


Running Head: ISE 690 e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e
e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e 1
Milestone 3: Incident Management Simulation Tabletop Training Exercise
ISE 690 Cyber Security Capstone
SNHU

ISE 690 e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e
e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e 2
Introduction
In Callego, there is a need to implement a robust incident management
simulation tabletop training exercise so that the risks and issues relating to the
Intelligent Virtual Assistant (IVA) could be effectively tackled. The Sonya Project could
be beneficial for the organization but it could also increase the vulnerability of the firm
and its customers. The implementation of a tabletop exercise could play a key role and
help the organizational personnel to consider varying risk scenarios that could jeopardize
the Information technology infrastructure (Six Scenarios to Help Prepare Your
Cybersecurity Team, 2019, p 3).
The tabletop training program has been designed so that it would help the organization
to effectively manage cybersecurity incidents. In addition to this, it would help to
identify the existing gaps relating to response procedures, information security controls,
or mitigation tactics.
Security issue relating to Intelligent Virtual Assistants
The installation of an intelligent virtual assistant in Callego could give rise to
numerous security challenges. Since the engineered entity would be able to interact with
the customers, directly, it is necessary to give high priority to the security concerns that
could arise in the business backdrop (The Virtual Personal Assistant and Its Security
Issues, 2017). Some of the main security issues and risks include the privacy of the
customers and clients and security breach incidents. Since the IVA technology is still
evolving, other kinds of security and privacy risks could arise that could increase the
vulnerability of Callego and its customers.
The tabletop training exercise has been designed so that the organization would
be able to leverage the latest technology without compromising its security. The two-
hour exercise would help the employees of the business to come across different kinds

ISE 690 e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e
e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e 3
of security and privacy issues that could arise in the practical setting (Emergency
Management Institute (EMI) Virtual Table Top Exercise (VTTX), 2019). Simulated
scenarios would be presented and the employees would be expected to react
appropriately so that the risks could be effectively tackled. Before expecting the
employees to know how to act in the situation, training materials would be provided to
them so that they could get an insight into what is expected of them in a tense
situation.
The objective of the tabletop exercise
Some of the main objectives of the designed tabletop training exercise have been
highlighted below:
❖ Intelligence and information sharing
❖ Handling complex cybercriminals and online hacker attackers
❖ Cyber coordination
❖ Recovery coordination
A holistic training plan has been designed so that the employees of Callego would
be able to manage security concerns after the Sonya project would be implemented. The
tabletop exercise would allow the participants to engage with one another and adopt an
integrated approach to mitigate or minimize a security issue.
Incident management team roles and responsibilities
All the responsibilities would be clearly defined so that there would be no
confusion among the participants during the exercise. The key team roles and
responsibilities have been highlighted below:
Employees – A majority of the participants would play the role of the employees who
would have restricted knowledge about IVA and security concerns. They would be

ISE 690 e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e
e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e 4
responsible to identify suspicious or malicious activity in the IVA system. Then they
would intimate the Network Administrator about the concern.
Network Administrator – He would act as the gatekeeper and ensure that the IT system
of the entity including the IVS system is not invaded by any unauthorized individual or
party. His strategic actions could prevent theft or loss of data of Callego (IT Security
Management: Roles and Responsibilities, 2019).
IVA security manager – The IVA security manager would be responsible to ensure that
all the updated security policies are implemented throughout the organization so that the
customer service is not compromised n any manner. In the exercise, he would be
responsible to lock down the entire IVA system so that the scope of the security
incident could be restricted.
Customer or clients – A few participants of the program would play the role of the
customers or clients of Callego whose privacy would be at stake. Their involvement
would be necessary for the tabletop training exercise as they would be made aware of
the actions that they could take to minimize their vulnerability.
Elements to be tested
The designed tabletop training program would test a diverse set of security
elements of the Callego organization such as security principle, security policy, technical
control measure and, incident response tactic. All these elements would be given high
consideration as they are likely to have a direct impact on the security and privacy
aspect of the users. A diverse range of potential attacks would be carried out in the
training exercise so that the employees, especially the IT team could identify the
vulnerable areas and the security gaps in Callego’s IT system.
Security principle

ISE 690 e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e
e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e 5
The security principle that would be tested in the training program is layering.
Presently, the layering technique is employed in Callego to strengthen the level of
security of the organization and its clients or customers. It basically involves the
application of different security controls at different levels so that the digital assets can
be protected in the best way possible (What is Layered Security? - Definition from
Techopedia, 2019). The training would emphasize on a threat that could arise in the
internal business context. So in such a situation, the existence of multiple security layers
would not serve any purpose to safeguard the IT ecosystem of the organization.
Security policy
The scenario that would be presented in the tabletop training exercise would test
the security policy relating to the proper awareness of the staff of the organization to
the IVA technology. For instance, the program would help to get an insight into how
well the employees are able to respond to hardware failure or software errors. The
exposure to such simulated scenarios in the training program would help the staff
members to face similar situations in the real-life setting (Gibb, 2019).
Technical control measure
The technical control measure that would be potentially exploited in the tabletop
training exercise relates to the use of an old version of antivirus software. Antivirus
software is used as a vital security tool in every organization including Calloga. The
testing of this security aspect would show how the vulnerability of the IT system could
increase if the IVA technology has redundant antivirus software in place. The training in
this area would be extremely vital for all the participants as they would understand the
significance of antivirus to strengthen the security posture.
An incident response tactic

ISE 690 e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e
e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e 6
An incident response tactic that involves the use of an intrusion detection system
(IDS) would also be tested or exploited in the tabletop training exercise. The actual
effectiveness of the system could be ascertained by putting the system through the
rigorous test. It would help the participants of the program to understand how effectively
and efficiently they are able to detect unauthorized behavior or actions in the IT system
of the organization including the IVA system. A potential attack on the deployed IDS
would enable the Network Administrator and IVA security manager to understand how
the security tool can be strengthened in the future.
Exercise timeline
The timeline of the tabletop training exercise has been highlighted below:
30/01/2020 – Initial Attack Vector
The first stage would basically involve the attack that would have the potential to
compromise the Intelligent Virtual Assistant of Callego along with the entire IT
infrastructure.
7/02/2020 – Framing for an initial response
In this stage, a framework of the response would be employed so that relevant
policies, principles, and controls could be checked. For example, the team would ensure
that all the security elements of the layered security are functioning properly.
14/02/2020 – Branching scenarios
The decisions that would be taken by the participants and team members of the
exercise would have direct implications on the future actions and consequences. For
example, the decision to update the knowledge and education of the staff members
would ensure that they are well prepared to identify suspicious activities in the internal
setting of the organization, especially the IVA system. Thus the probability of the attack
could be curtailed to a substantial extent. In case, the IT team of Callego would fail to

ISE 690 e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e
e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e 7
update the antivirus software that is used in the new Intelligent Virtual Assistant, the
attack could have a major impact on the IT ecosystem of the firm. Thus there would be
a significant interlink between the actions that would be taken by the firm and the
consequences that would be faced by it. e
22/02/2020 – Three injects that could shift the attack vector or introduce new
information regarding the business
The three elements that could alter or shift the pattern of the attack include the
compromise of the security of the clients and customers of the organization, the theft of
the financial data of the business undertaking and the intention to shut down the IT
system of the entire organization.
03/03/2020 – Frames for responding to the injects
In this stage, suitable methodologies and methods would be employed to tackle
the three different infects that would be presented in the tabletop program. In order to
safeguard the confidential details of the clients and customers, proper encryption
practices would be employed. For effectively dealing with the theft of the financial data
of the business, the layers of security would be updated and the security policies would
be based on General Data Protection Rule (GDPR). Ultimately, for responding to the
attempt to shut down the IT system of Callego, the technical security controls would be
upgraded and tested on a regular basis.
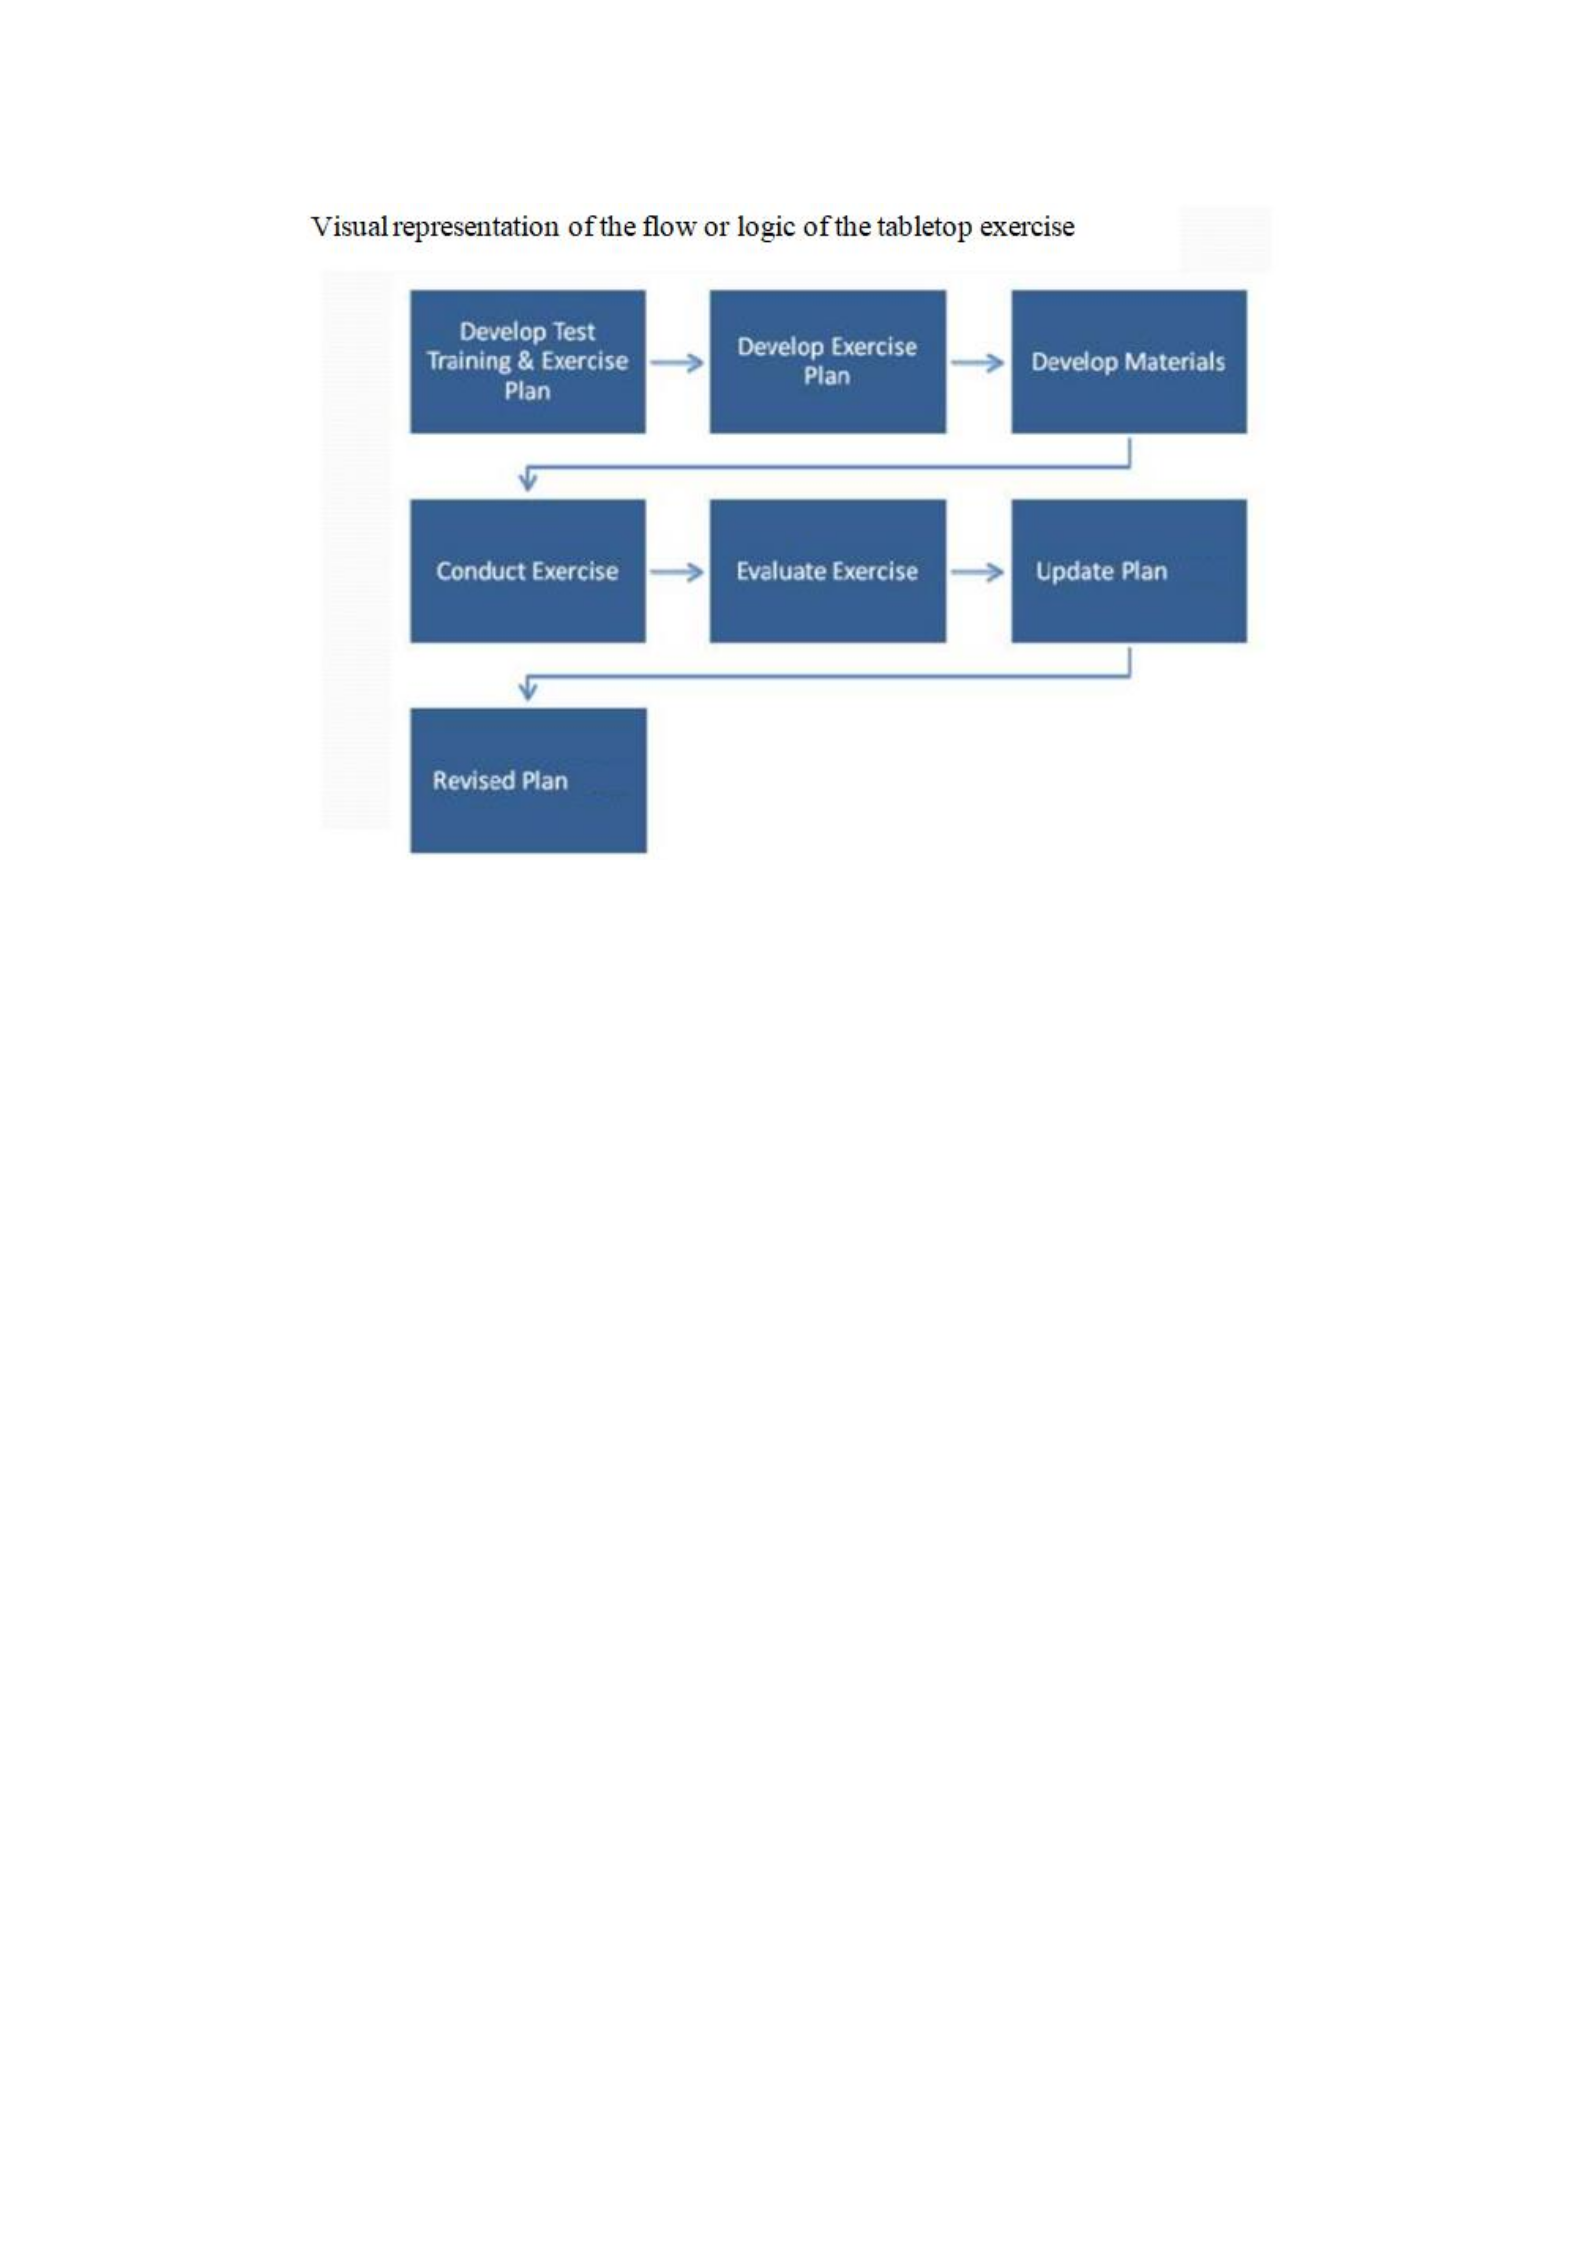
Visual representation of the flow of exercise
The flowchart that has been presented below shows how different processes of
the tabletop training program would be conducted in the organizational context. All the
activities would play an integral role to help the employees become aware of different
risk scenarios that could compromise the IT ecosystem of the firm due to the use of
Intelligent Virtual Assistant technology.
ISE 690 e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e
e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e 8
Source: (Shaurette, 2017)
Projects of lessons learned
The tabletop training exercise that would revolve around IVA would be of high
value for the employees of Callego. It would make the participants aware of the security
gaps that exist in the system. The IT team would get a detailed insight into the gaps
that exist in its current Technical controls thus it could introduce necessary
improvements in them.
Similarly, the simulated risk scenario would help the team to employ a
streamlined communication procedure so that proper engagement could be possible
among the relevant parties simultaneously. The other areas and aspects that need to be
covered in other training and awareness campaigns include the proper education on the
technical elements of Intelligent Virtual Assistants. The technical know-how will
empower the staff to understand how vulnerability can arise and intensify. The training
laid high emphasis on the regulatory and legal elements that govern the industry such as
the GDPR. There is further scope to expand the knowledge on the updated regulations
and legal components. A robust and systematic documenting of risk is necessary. It

ISE 690 e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e
e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e 9
would help the upper management of Callego to review these documents and introduce
suitable corporate policies to enhance security relating to IVA technology.
Conclusion
The tabletop training exercise would help Callego to strengthen the preparedness
of its employees to handle risky situations that could arise because of the Sonya project.
A diverse range of scenarios would be presented which would give them an idea about
how to tackle cyber threats and risks. The core areas that the program would focus on
include real-time intelligence and information sharing, handling complex cybercriminals
and online hacker attackers, effective cyber coordination and robust recovery
coordination. The role of all the participants in the program would be critical to ensure
that it would add value for them.
ISE 690 e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e
e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e 10
References
Emergency Management Institute (EMI) Virtual Table Top Exercise (VTTX). (2019).
Retrieved December 13, 2019, from https://training.fema.gov/programs/emivttx.aspx
Gibb, K. (2019). GDPR - Information Security Policy. Retrieved December 13, 2019,
from https://stjosephs.southwark.sch.uk/en/home/terms-privacy/1366-gdpr-
information-security-policy.
IT Security Management: Roles and Responsibilities. (2019). Retrieved December 13,
2019, from https://www.edology.com/blog/computing-it/it-security-management-
roles-responsibilities/.
Six Scenarios to Help Prepare Your Cybersecurity Team. (2019). Retrieved December
13, 2019, from https://www.cisecurity.org/wp-content/uploads/2018/10/Six-tabletop-
exercises-FINAL.pdf.
Shaurette, K. (2017). Surviving a Mock Disaster. Retrieved December 13, 2019, from
https://secure360.org/wp-content/uploads/2016/05/Surviving-a-Mock-
Disaster_KenShaurette.pdf.
The Virtual Personal Assistant and Its Security Issues. (2017, May 31). Retrieved
December 13, 2019, from https://resources.infosecinstitute.com/virtual-personal-
assistant-security-issues/#gref.
What is Layered Security? - Definition from Techopedia. (2019). Retrieved December
13, 2019, from https://www.techopedia.com/definition/4005/layered-security.

