


Running Head: ISE 690 g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g 1
Final Project
ISE 690 Cyber Security Capstone

ISE 690 g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g 2
Table of Contents
Milestone 1: Memo of Recommendation on IVA ......................................................... 4
Summary of Intelligent Virtual Assistant ........................................................................... 4
Underlying technology with security implications .............................................................. 5
Security Risks ........................................................................................................................ 6
Examples of possible adversarial attacks ............................................................................ 7
Control Measures .................................................................................................................. 8
Evaluation of control measures ............................................................................................ 9
Milestone Two A: Privacy Statement for GDPR compliance ..................................... 10
Revised Privacy Statement .................................................................................................. 10
Explanation ........................................................................................................................... 11
Justification .......................................................................................................................... 12
Impact on organization ....................................................................................................... 13
Top-Three Policy List: Annotated ................................................................................ 14
Milestone Two B: Technical Controls recommended for GDPR due care ............... 15
Introduction .......................................................................................................................... 15
Recommended control measures ......................................................................................... 15
Intrusion detection and prevention system – ................................................................... 16
Firewalls – ........................................................................................................................... 16
Malware scanners ................................................................................................................ 16
Present state and future state description ........................................................................ 16
Recommended measures will function systematically ....................................................... 17
Principle for information security ..................................................................................... 18
Justification .......................................................................................................................... 18
Milestone Three: Incident Management Simulation ................................................... 19
Security issue relating to Intelligent Virtual Assistants .................................................. 19
The objective of the tabletop exercise .............................................................................. 20
Incident management team roles and responsibilities ...................................................... 21
Elements to be tested ......................................................................................................... 22
Security principle ................................................................................................................. 22
Security policy ..................................................................................................................... 22
Technical control measure .................................................................................................. 23
An incident response tactic ................................................................................................ 23

ISE 690 g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g 3
Exercise timeline .................................................................................................................. 23
Visual representation of the flow of exercise .................................................................. 25
Projects of lessons learned ................................................................................................. 26
Framing Statement ........................................................................................................ 27
Consulting Problems ............................................................................................................ 27
Top three policies and procedures for GDPR compliance ............................................. 28
Framing Statement for Consulting Collection Components ............................................ 28
References ..................................................................................................................... 30

ISE 690 g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g 4
Milestone 1: Memo of Recommendation on IVA
To: Management, Callego
From: Mr. Jack Ray
Subject: Security risks and control measures relating to Intelligent Virtual Assistant
Date: November 12, 2019
Technology is evolving like never before. The concept of Intelligent Virtual
Assistant (IVA) has captured everyone’s attention as it has the ability to interact
with humans in a human way. But IVAs give rise to numerous security concerns
that need to be addressed promptly. In Callego, there is scope to introduce an IVA
as it can make the customer service leaner and more efficient. But the technology-
driven approach could give rise to security concerns that must be handled efficiently.
Summary of Intelligent Virtual Assistant
An Intelligent Virtual Assistant can be defined as an engineered entity that
resides in software. It has the ability to interface with human beings in a human
manner. This innovative technological tool primarily encompasses elements relating to
interactive voice response and various other latest Artificial Intelligence projects. The
objective is to make sure that an IVA can deliver full-fledged ‘virtual identities’ that
can have a conversation with the users (What Is an Intelligent Virtual Assistant? -
Definition from Techopedia, 2019). IVAs have brought about revolutionary changes
in a customer service setting. Some of the major benefits include the scalable and
efficient nature of the Virtual assistants to resolve the concerns of the customers,
and the improved customer and brand experience (Gray, 2019). In the case of the
Callego firm, the intention of introducing Sonya is to solve the most difficult or
complex customer issues for clients in an innovative and secure way.

ISE 690 g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g 5
Underlying technology with security implications
As per Knote and Eigenbrod, Intelligent Virtual Assistants have a certain
degree of intelligence and interaction that makes them highly useful. IVAs are
designed as security agents that are capable of performing tasks and activities by
simply receiving command or questions (Knote et al., 2018). These smart virtual
assistants work by identifying, processing and using contextual information. If a
context-adapted system is integrated into an IVA, it helps to detect as well as react
to the context by taking necessary actions. The context detection is enabled by
optical and/or optical sensors like cameras or microphones. The data that is
communicated to the Virtual Assistant can be said to be context information (Knote
et al., 2018, p 6). Intelligent Virtual Assistants are designed to deliver an automated
and intuitive experience for the users. The underlying technology of IVAs supports
intelligent and human-like dialogue with the customers. Sonya would act like a lean
and efficient project that would enable the business to work intelligently and marshal
its resources and safeguard the data assets of Callego and its clients. But it could
have some security implications as well.
A number of security concerns have been raised due to the increase in the
use of Intelligent Virtual Assistants. Some of the most common security concerns
that are being raised in the current times include attack by malicious attackers and
accidental voice recordings. In addition to this, there is also an increase in concern
relating to the openness of customers to security and privacy risks due to the data
processing involving Virtual Assistants. As the technology relating to Intelligent
Virtual Assistants is still evolving, numerous risks and uncertainties might surface
which can adversely affect the customers as well as the organizations. Chung and
Iorga in a NIST article have identified numerous IVA security and privacy risks

ISE 690 g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g 6
which can compromise the purpose of the technology-based system (Chung et al.,
2017).
Security Risks
The degree of risk gets enhanced when complex and free-flowing
conversations take place between people and intelligent and adaptive machines. IVAs
basically open an entirely new world where humans can talk to a machine as if it
is a fellow human being. The interaction gives rise to a number of security
vulnerabilities. As per Chung and Iorga, since IVAs use actual voices of people
which are ‘Personally Identifiable Information’ (PII) the user privacy might be a
major security concern. In addition to this, the vendors of Intelligent Virtual
Assistants store voice data which increases the level of vulnerability of the users
(Chung et al., 2017, p 3). This is because; it might be possible for unauthorized
entities to gain access to the stored voice data of the customers. There is a
possibility that the voice data can be used by unauthorized individuals or parties to
construct ‘voice artifacts’ that can be utilized for impersonating the users. These are
some of the most vital security scenarios that can give rise to serious security
problems. g
In the current times, cybercriminals and online hackers are making use of
sophisticated equipment so that they can compromise the security posture of the
victims. Since the IVA technology is yet to mature, there is a need to have a
robust security framework in place so that the vulnerability and risks of the users
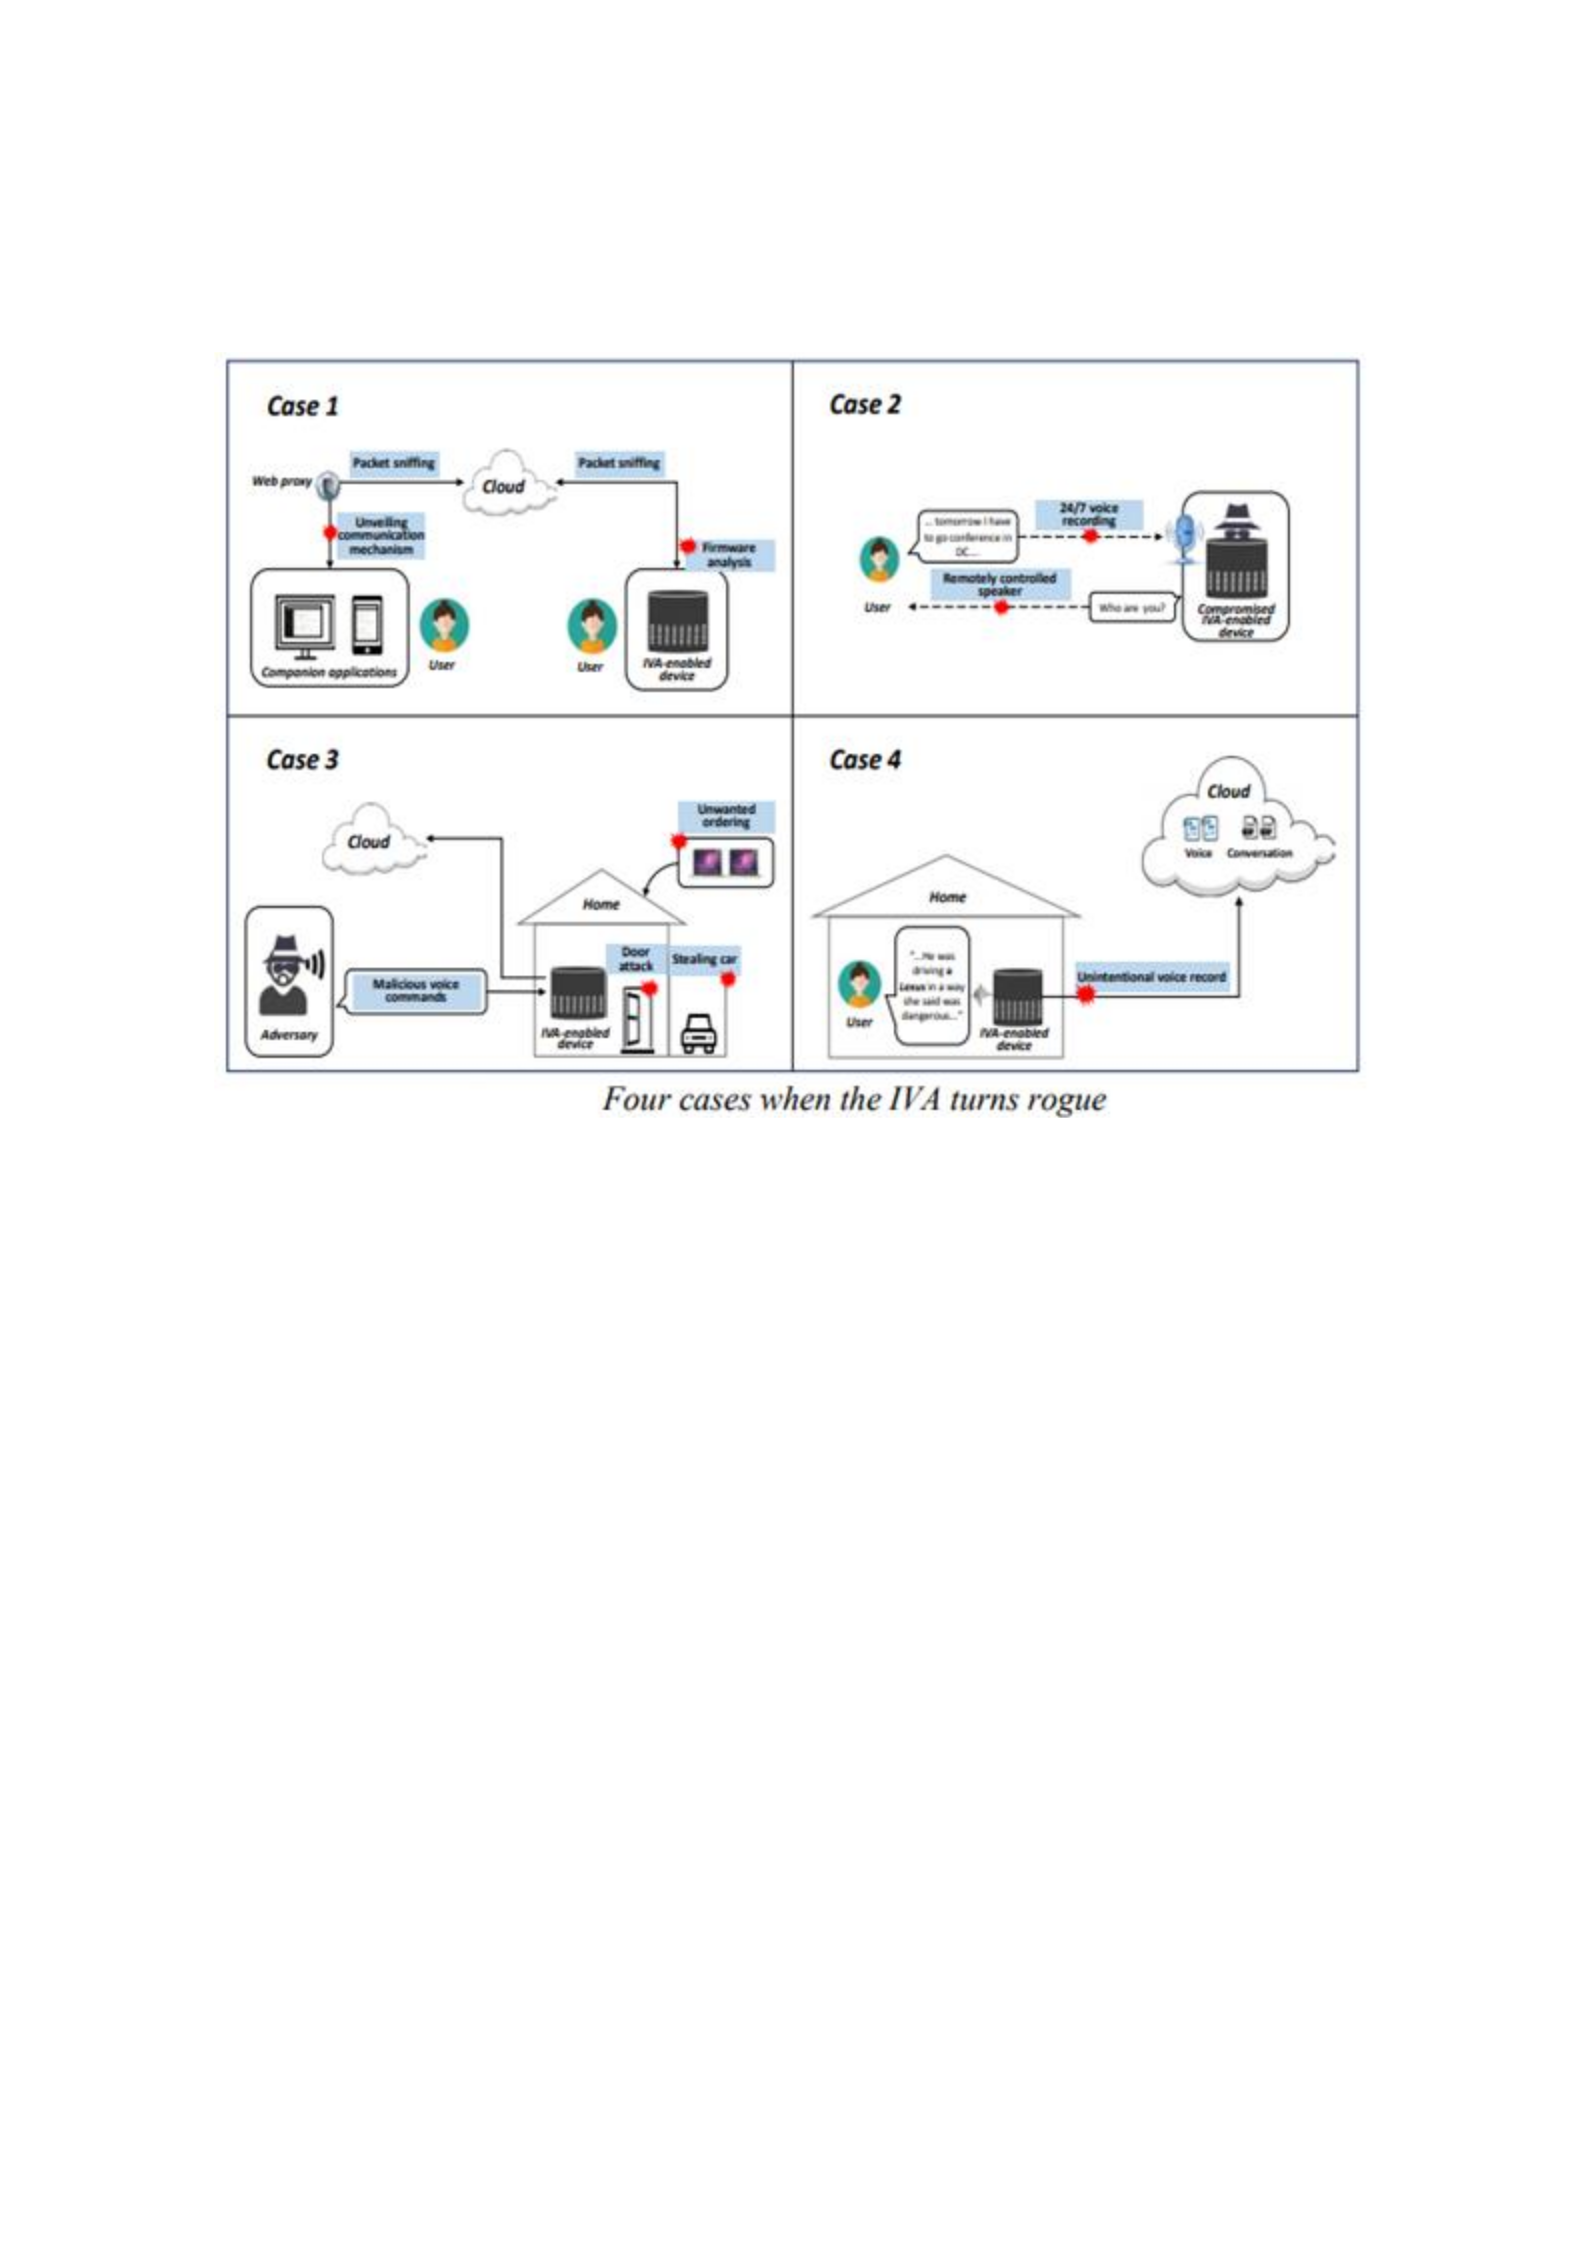
can be mitigated to a possible extent. Chung and Iorga have identified a number of
IVA security and privacy risks namely wiretapping, compromised end devices,
malicious voice commands, and unexpected voice recordings. Since Sonya would
ISE 690 g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g 7
work on the lines of a new technological concept, the area of vulnerabilities for the
organization would be high.
Source: (Chung et al., 2017, p 5)
Examples of possible adversarial attacks
A number of possible adversarial attacks might target or involve Sonya and
compromise the security of the organization as well as the clients. For instance,
voice-activated digital assistants such as Echo and Alexa open up a wide range of
vulnerabilities by issuing commands that might not be audible to the human ear.
Such commands could exploit the accessibility setting that has been activated by the
digital assistants. One of the primary functions of the smart assistants is to connect
the users to services by using an easy-to-use voice interface. But these innovative
tools could make the job for online hackers simpler. In the case of Sonya, the same
vulnerabilities can arise and the system might be bypassed on the locked Windows
computer or other smart devices. Thus, due to system availability, the hackers can

ISE 690 g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g 8
get a detailed insight into the lives of the users which could be a major security
threat. g
Voice hacking or voice recording is another possible adversarial attacks that
might target Sonya, Callego’s Intelligent Virtual Assistant. As per Chung, IVAs
might be controlled or manipulated by the individuals who are pretending to be in
proximity to the Intelligent Virtual Assistant device (Chung et al., 2017, p 7). They
can basically access the speaker and breach the security of the user. Thus in the
case of Sonya, malicious users could record the voice of the users without their
knowledge. They could also give voice commands which could negatively affect data
integrity. The online hackers with suspicious and malicious intentions could use such
approaches to compromise the security and privacy of the users.
Control Measures
In order to address the possible adversarial attacks that might target Sonya, it
is necessary to create a robust security posture so that the technology cannot be
invaded or exploited by unauthorized users or cybercriminals. The platform where
the interaction takes place between a user and an Intelligent Virtual Assistant needs
to be designed with multiple relevant controls. These controls must operate within
the digital and voice applications so that the conversation will not be accessed by
any unauthorized party or individual. It is necessary to ensure that the interaction
takes place in a sound and safe environment which respects the confidentiality and
integrity of the users (Chung et al., 2017, p 7). Voice recording and voice hacking
are major concerns that could compromise the security of the users. In order to
control the security risk, there is the need to create a robust Intelligent Virtual
Assistant (IVA) infrastructure. It must be equipped to identify various kinds of threat
vectors that might compromise the security of the users and the organization. Such a

ISE 690 g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g 9
control measure can come into play and safeguard the users. Sonya must be
designed in a lean and efficient manner so that it could handle complex problems of
the clients without compromising their security.
Even though Intelligent Virtual Assistants have the potential to bring about
revolutionary changes where they are applied, they also give rise to numerous
security risks and challenges. In order to safeguard the confidentiality and privacy of
the users while interacting with IVAs, various security techniques can be introduced
such as real-time data blocking, log encryption, and sensitive redaction. Such
techniques can restrict the scope of cybercriminals and online hackers to compromise
the security framework of the system. g In addition to this, it is necessary to upgrade
the security system on a regular basis so that hackers will not be able to use
sophisticated tools and techniques in order to pose additional security threats and
risks
Evaluation of control measures
In the organization, Sonya would act as the Intelligent Virtual Assistant which
could increase the security risks. In order to mitigate security risks, there is a need
to deploy robust control measures in the organizational context. Firstly, a voice
biometrics system needs to be introduced so that the level of security and
confidentiality could be strengthened. Such a measure would basically allow users
or clients to have an additional factor of authentication. Similarly, an additional layer
of security needs to be introduced so that the interaction that takes place between
Sonya and the customers would be stored in an encrypted format. Such a control
measure would basically ensure that the stored voice data could not be retrieved in
the original format by any unauthorized parties.

ISE 690 g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g 10
The IVA concept could help the organization to streamline customer service
activities. But it is necessary for Callego to carefully take into account the security
implications that would arise by introducing Sonya, the Intelligent Virtual Assistant
(IVA) of Callego. A robust and secure security infrastructure must be introduced in
place so that the various kinds of threats and risks could be mitigated in the most
effective manner. The control measures must be introduced on high priority so that
the IVA model could function in a secure manner without adversely affecting the
confidentiality, privacy and security aspects. A functional control measure would
ensure that Sonya could effectively interface with the customers on phone calls by
using AI technology and natural language processing, without compromising their
security.
Milestone Two A: Privacy Statement for GDPR compliance
Revised Privacy Statement
Callego would adopt a robust privacy and security model so that the use of
the Intelligent Virtual Assistant – Sonya would not compromise the security of its
clients or other stakeholders. The conversation that Sonya has with the clients of
Callego must be encrypted and stored in the cloud servers of the firm for better
safety and security. The customers and clients of the firm would be intimidated
about how the data relating to the customers would be collected, used, gathered and
processed in a secure manner. In addition to this, the customers of the outsourced
customer service provider would also be informed on why the data would be
processed by the business undertaking (PrivacyPolicies.com, 2019). The organization
would make sure to explain to its customers in a clear and understandable manner
why their data would be processed by it and how its security would be ensured at
all the levels.

ISE 690 g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g 11
The role of the Data Controller and Processor would be of paramount
importance to ensure that the proper security and privacy model is in place. Thus
there professionals would be identified as they would have the ownership to take
care of the security and privacy aspects of the sensitive and confidential data
(PrivacyPolicies.com, 2019). The privacy approach of the business undertaking would
be based on fairness, lawfulness and transparency so that the personal data of clients
and customers could be processed by the organization in a lawful manner. The latest
technology-driven tools and techniques would be implemented in the business context
so that it would have genuine control over the data.
Callego would ensure to introduce and implement more straightforward and
accessible privacy policies so that it would be in a position to effectively promote
the fundamental rights of individuals. The firm would focus on data minimization
(The 6 GDPR privacy principles you must know - now, 2018). In other words, the
personal data of the customers and other stakeholders that would be vital for the
business function would be collected. In case any data is no longer required by the
organization, it would be removed in a safe and secure manner so that the privacy
aspect would not be compromised.
Explanation
The privacy statement that has been devised for Callego is in sync with the
security principles of the General Data Protection Regulation (GDPR). A high degree
of emphasis has been laid on the safety and privacy of the customer data. The
thinking, as well as the work process, relating to the revised privacy statement
revolves around the security principles of the General Data Protection Regulation
(The 6 GDPR privacy principles you must know - now, 2018). The organization
would make sure to inform the customers about why it needs their data and how it

ISE 690 g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g 12
intends to use and process it. This knowledge would ensure that the individuals
know how the organization plans to take care of their privacy and safety. It would
also lay emphasis on the accuracy and privacy aspects of the customer data. GDPR
privacy principles act as the fundamental framework that would guide Callego to
ensure that the introduction of the Sonya project would not jeopardize the privacy of
the customers and clients of the business.
The privacy statement shows that the organization would place the customers
in the central position so that their data could be securely and safely handled by it
(Microsoft's commitment to GDPR, privacy and putting customers in control of their
own data, 2018). It would act as a critical step forward that would strengthen the
privacy rights of the customers of the outsourced customer service provider.
Justification
The revised privacy statement that has been designed for the Callego business
entity exhibits privacy principles and standards of due care that adheres to the
General Data Protection Regulation. This is evident from the fact that high emphasis
is being given to the level of transparency and confidentiality of customer data.
GSPR lays a high emphasis on individuals and their knowledge of how their data is
being used and processed by a business undertaking. The revised privacy statement
of Callego would ensure that the customers would be informed about how their data
would be collected, used, and processed by the business entity in a safe and secure
manner.
One of the core privacy policies of GDPR highlights the significance of data
minimization. As per the regulation, the personal data relating to the customers
would be collected which would be a necessity for the purpose of the business
function. So Callego would ensure that it would gather minimum data relating to the

ISE 690 g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g 13
customers that would be a fundamental necessity for it. The core principles of
GDPR would ensure that Callego would establish a robust privacy model that would
act as the foundation of trust for its customers (General Data Protection Regulation
(GDPR): The paradigm shift in privacy, 2018). It would ensure that the organization
takes necessary care to makes sure that the privacy and security aspects of its
customers are taken care of in an effective and optimum manner. g
Impact on organization
Callego is a well-known provider of outsourced customer service that has
clients in various industries such as healthcare, insurance, and the financial sector.
One of the core elements that impact its sustainability and reputation in the
operational business climate is its ability to take care of the needs and wants of its
clients and customers. The revised privacy statement that has been designed for the
business undertaking would have a significant implication on its mission, operations,
and organizational culture. g Since the privacy statement is based on the principles of
GDPR, the business would give top priority to the safety and privacy aspects of its
customers. In addition to this, the business firm would make sure to intimate the
customers about how it plans on collecting using, processing and storing their data
in a safe and secure manner. The core security and privacy principles would help
Callego to build the organizational culture that gives high importance to privacy and
security. The leaders of the firm would play an active role to ensure that a highly
functional security framework is in place that supports the Intelligent Virtual
Assistant project – Sonya. Thus the firm could imbibe the security element in its
core business processes and values so that the privacy and security of the customers
could be taken care of.

ISE 690 g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g 14
Top-Three Policy List: Annotated
Information Security As Part Of Data Protection. (2019). EU General Data
Protection Regulation (GDPR), Third Edition, 111–126. doi:
10.2307/j.ctvr7fcwb.9
The first policy that would be introduced in Callego relates to the appointment
of a competent Data Protection Officer (DPO). As per Osterman research white
paper, organizations need to appoint a DPO if they are involved in the processing
of personal data. Since the customer service entity deals with personal data of its
clients and customers, the role of DPO would be integral to ensure that it is
complying with GDPR.
Figure 2f from: Irimia R, Gottschling M (2016) Taxonomic revision of Rochefortia
Sw. (Ehretiaceae, Boraginales). Biodiversity Data Journal 4: e7720.
https://doi.org/10.3897/BDJ.4.e7720. (n.d.). doi: 10.3897/bdj.4.e7720.figure2f
The data relating to the customers that are collected by Callego needs to be
collected and stored in such a manner so that it will be easier for the company to
comply with the “new data subject rights”. As per Delloite, the individuals and
teams that a5re responsible for information management need to focus on various
areas such as data storage, journey and overall lineage. It would ensure that they
have a better grasp of customer data and information.
Urquhart, L., & McAuley, D. (2018). Avoiding the internet of insecure industrial
things. Computer law & security review, 34(3), 450-466.
There is a substantial rise in security issues and risks in the business arena.
According to Urquhart and McAuley, the instances of hacking can be avoided by

ISE 690 g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g 15
organizations only if they adopt a robust It infrastructure. In Callego, the IT
ecosystem must be strengthened so that security loopholes can be addressed and
existing security concerns can be managed in an efficient and prompt manner.
Milestone Two B: Technical Controls recommended for GDPR due
care
Introduction
In Callego, there is a need to introduce three robust technical control
measures so that it can be aligned with the privacy protection expectations of the
General Data Protection Regulation and the organization’s emerging revised privacy
statement. The control mechanisms that have been designed taking into account the
firm’s mission relating to customer service, the budgetary constraints, and the
advanced time frame. The objective is to ensure that the security posture of the
organization would not get compromised in any manner and the confidential data
relating to the clients, customers and the business could not be accessed by
unauthorized individuals or parties.
Recommended control measures
The three control measures that have been recommended for the Callego
organization so that its networks could be secured include the application of
intrusion detection and prevention system, firewalls and malware scanners to
strengthen the network security. GDPR states that it is necessary to introduce
appropriate technical and organizational measures” so that its principles can be
adhered to (Know Your Compliance, 2019). By introducing these recommended
control measures, the cybersecurity framework of the firm could be strengthened, and
the requirements of the regulations could be met.

ISE 690 g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g 16
Intrusion detection and prevention system –
By introducing a functional intrusion detection and prevention system, Callego
would be able to safeguard against external risks. The tool would help the firm to
comply with the GDPR principles and safeguard the confidential data that it has
relating to the clients and its business (3 Things You Need to Know About GDPR
and Intrusion Detection, 2019).
Firewalls –
The use of a network firewall would be extremely vital for the business
undertaking as it could help the firm to protect the customer data. One of the most
vital elements that have been highlighted in GDPR relates to ‘preventing data
breaches’ (Zeichick, 2018). BY installing network firewalls, Callego would be able to
prevent data breaches in the enterprise networks. In addition to this firewall would
also help to limit data exfiltration, i.e. the removal of data through an internet
download by malware or outsiders.
Malware scanners
In order to ensure that the firm complies with GDPR, robust malware
scanners must be deployed. It would help to conduct thorough threat analysis and
help to identify suspicious elements such as malware that could compromise the
security of the organization’s network (Is Your Cloud-based Anti-Malware Solution
GDPR Compliant, 2019).
Present state and future state description
The Capability Maturity model has been used to get a detailed insight into
the present state and the future state of the recommended control measures.
Currently, the Intrusion detection and prevention system that is deployed in the firm
is in the initial stage as it is disorganized and not completely functional (Rouse &

ISE 690 g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g 17
Jayaram, 2019). It would have to move to the optimum level so that the detection
and prevention process could be optimally strengthened. It is necessary to make
significant progress so that the control measure could create value for the
organization.
Callego has employed network firewalls that play a vital role to improve the
safety posture of the organization. But there is scope to strengthen the control
measure so that it could safeguard the firm’s network against sophisticated threats
and attacks. Its current level is “repeatable” as it carries out the basic functions. But
there is scope to take it to the “optimizing” level so that consistent improvements
can be introduced.
The role of malware scanners is restricted in the organizational context. So, it
is necessary to define the software process and gradually make progress so that it
would act as a vital control measure for Callego.
Recommended measures will function systematically
The control measures that have been recommended primarily focus on the
security of the organizations’ network. The three approaches would work together
and complement one another in a systematic manner. This would be possible as the
firewall, Intrusion detection and prevention system and malware scanners would offer
integrated safety of the firm’s network which acts as a pathway for outsiders. The
tools would function in a uniform manner so that comprehensive security of the
system network would e possible so that the instances of a data breach could be
restricted and mitigated. By complying with the General Data Protection Regulation
and Callego’s emerging revised privacy statement, the security posture of the firm
could be upgraded to a substantial degree.

ISE 690 g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g 18
Principle for information security
The recommended control measures that have been selected for Callego use
the least privilege principle for information security to support GDPR conceptions of
privacy as well as the revised Callego privacy statement. The control measures
would ensure that the users would have access to sensitive data or information that
is relevant for their functions and work (The principle of least privilege: A strategy
of limiting access to what is essential, 2018). The ‘least privilege’ principle is
considered to be one of the most effective security practices that ensure that
unauthorized users do not gain entry into the system. The recommended control
measures would help the business undertaking to keep a check on the users as well
as their accessibility rights so that the instances of a data breach could be restricted.
Justification
The security measures that have been designed have been selected by taking
into consideration the practicality, value or cost-effectiveness, and the available time.
The control measures such as firewalls and intrusion detection and prevention
systems have become a basic necessity in the unpredictable technology-driven times.
So, by strengthening these models in the organization setting, Callego would be able
to abide by the GDPR principles and fight against the instances of data breach
incidents. Similarly, it is also necessary for the business firm to deploy malware
scanners so that it would be able to keep a tab on suspicious or malicious elements
such as malware. The identification of such harmful elements would help the firm to
take suitable measures so that its vulnerability could be minimized, and the security
breach incident could be managed in the most effective and efficient manner. It

ISE 690 g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g 19
would be simple for the firm to introduce these control measures within the
restricted time frame.
In the evolving technological setting, the control measures that have been
recommended for Callego would play a key role to safeguard the confidential data
and information that it has relating to the business, clients, and customers. By
implementing these control measures, the firm could strengthen its security
framework. g
Milestone Three: Incident Management Simulation
In Callego, there is a need to implement a robust incident management
simulation tabletop training exercise so that the risks and issues relating to the
Intelligent Virtual Assistant (IVA) could be effectively tackled. The Sonya Project
could be beneficial for the organization, but it could also increase the vulnerability
of the firm and its customers. The implementation of a tabletop exercise could play
a key role and help the organizational personnel to consider varying risk scenarios
that could jeopardize the Information technology infrastructure (Six Scenarios to Help
Prepare Your Cybersecurity Team, 2019, p 3).
The tabletop training program has been designed so that it would help the
organization to effectively manage cybersecurity incidents. In addition to this, it
would help to identify the existing gaps relating to response procedures, information
security controls, or mitigation tactics.
Security issue relating to Intelligent Virtual Assistants
The installation of an intelligent virtual assistant in Callego could give rise to
numerous security challenges. Since the engineered entity would be able to interact
with the customers, directly, it is necessary to give high priority to the security

ISE 690 g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g 20
concerns that could arise in the business backdrop (The Virtual Personal Assistant
and Its Security Issues, 2017). Some of the main security issues and risks include
the privacy of the customers and clients and security breach incidents. Since the
IVA technology is still evolving, other kinds of security and privacy risks could
arise that could increase the vulnerability of Callego and its customers.
The tabletop training exercise has been designed so that the organization
would be able to leverage the latest technology without compromising its security.
The two-hour exercise would help the employees of the business to come across
different kinds of security and privacy issues that could arise in the practical setting
(Emergency Management Institute (EMI) Virtual Tabletop Exercise (VTTX), 2019).
Simulated scenarios would be presented, and the employees would be expected to
react appropriately so that the risks could be effectively tackled. Before expecting
the employees to know how to act in the situation, training materials would be
provided to them so that they could get an insight into what is expected of them in
a tense situation.
The objective of the tabletop exercise
Some of the main objectives of the designed tabletop training exercise have been
highlighted below:
❖ Intelligence and information sharing
❖ Handling complex cybercriminals and online hacker attackers
❖ Cyber coordination
❖ Recovery coordination
A holistic training plan has been designed so that the employees of Callego
would be able to manage security concerns after the Sonya project would be

ISE 690 g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g 21
implemented. The tabletop exercise would allow the participants to engage with one
another and adopt an integrated approach to mitigate or minimize a security issue.
Incident management team roles and responsibilities
All the responsibilities would be clearly defined so that there would be no
confusion among the participants during the exercise. The key team roles and
responsibilities have been highlighted below:
Employees –
A majority of the participants would play the role of the employees who
would have restricted knowledge about IVA and security concerns. They would be
responsible to identify suspicious or malicious activity in the IVA system. Then they
would intimate the Network Administrator about the concern. g
Network Administrator –
He would act as the gatekeeper and ensure that the IT system of the entity
including the IVS system is not invaded by any unauthorized individual or party.
His strategic actions could prevent theft or loss of data of Callego (IT Security
Management: Roles and Responsibilities, 2019).
IVA security manager –
The IVA security manager would be responsible to ensure that all the
updated security policies are implemented throughout the organization so that the
customer service is not compromised n any manner. In the exercise, he would be
responsible to lock down the entire IVA system so that the scope of the security
incident could be restricted.
Customer or clients – A few participants of the program would play the role of the
customers or clients of Callego whose privacy would be at stake. Their involvement

ISE 690 g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g 22
would be necessary for the tabletop training exercise as they would be made aware
of the actions that they could take to minimize their vulnerability.
Elements to be tested
The designed tabletop training program would test a diverse set of security
elements of the Callego organization such as security principle, security policy,
technical control measure and, incident response tactic. All these elements would be
given high consideration as they are likely to have a direct impact on the security
and privacy aspect of the users. A diverse range of potential attacks would be
carried out in the training exercise so that the employees, especially the IT team
could identify the vulnerable areas and the security gaps in Callego’s IT system.
Security principle
The security principle that would be tested in the training program is
layering. Presently, the layering technique is employed in Callego to strengthen the
level of security of the organization and its clients or customers. It basically
involves the application of different security controls at different levels so that the
digital assets can be protected in the best way possible (What is Layered Security? -
Definition from Techopedia, 2019). The training would emphasize on a threat that
could arise in the internal business context. So in such a situation, the existence of
multiple security layers would not serve any purpose to safeguard the IT ecosystem
of the organization.
Security policy
The scenario that would be presented in the tabletop training exercise would
test the security policy relating to the proper awareness of the staff of the
organization to the IVA technology. For instance, the program would help to get an

ISE 690 g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g 23
insight into how well the employees are able to respond to hardware failure or
software errors. The exposure to such simulated scenarios in the training program
would help the staff members to face similar situations in the real-life setting (Gibb,
2019).
Technical control measure
The technical control measure that would be potentially exploited in the
tabletop training exercise relates to the use of an old version of antivirus software.
Antivirus software is used as a vital security tool in every organization including
Callego. The testing of this security aspect would show how the vulnerability of the
IT system could increase if the IVA technology has redundant antivirus software in
place. The training in this area would be extremely vital for all the participants as
they would understand the significance of antivirus to strengthen the security posture.
An incident response tactic
An incident response tactic that involves the use of an intrusion detection
system (IDS) would also be tested or exploited in the tabletop training exercise. The
actual effectiveness of the system could be ascertained by putting the system through
the rigorous test. It would help the participants of the program to understand how
effectively and efficiently they are able to detect unauthorized behavior or actions in
the IT system of the organization including the IVA system. A potential attack on
the deployed IDS would enable the Network Administrator and IVA security
manager to understand how the security tool can be strengthened in the future.
Exercise timeline
The timeline of the tabletop training exercise has been highlighted below:
30/01/2020 – Initial Attack Vector

ISE 690 g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g 24
The first stage would basically involve the attack that would have the
potential to compromise the Intelligent Virtual Assistant of Callego along with the
entire IT infrastructure.
7/02/2020 – Framing for an initial response
In this stage, a framework of the response would be employed so that
relevant policies, principles, and controls could be checked. For example, the team
would ensure that all the security elements of the layered security are functioning
properly.
14/02/2020 – Branching scenarios
The decisions that would be taken by the participants and team members of
the exercise would have direct implications on the future actions and consequences.
For example, the decision to update the knowledge and education of the staff
members would ensure that they are well prepared to identify suspicious activities in
the internal setting of the organization, especially the IVA system. Thus, the
probability of the attack could be curtailed to a substantial extent. In case, the IT
team of Callego would fail to update the antivirus software that is used in the new
Intelligent Virtual Assistant, the attack could have a major impact on the IT
ecosystem of the firm. Thus, there would be a significant interlink between the
actions that would be taken by the firm and the consequences that would be faced
by it. g
22/02/2020 – Three injects that could shift the attack vector or introduce new
information regarding the business
The three elements that could alter or shift the pattern of the attack include
the compromise of the security of the clients and customers of the organization, the

ISE 690 g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g 25
theft of the financial data of the business undertaking and the intention to shut
down the IT system of the entire organization.
03/03/2020 – Frames for responding to the injects
In this stage, suitable methodologies and methods would be employed to
tackle the three different infects that would be presented in the tabletop program. In
order to safeguard the confidential details of the clients and customers, proper
encryption practices would be employed. For effectively dealing with the theft of the
financial data of the business, the layers of security would be updated and the
security policies would be based on General Data Protection Rule (GDPR).
Ultimately, for responding to the attempt to shut down the IT system of Callego,
the technical security controls would be upgraded and tested on a regular basis.
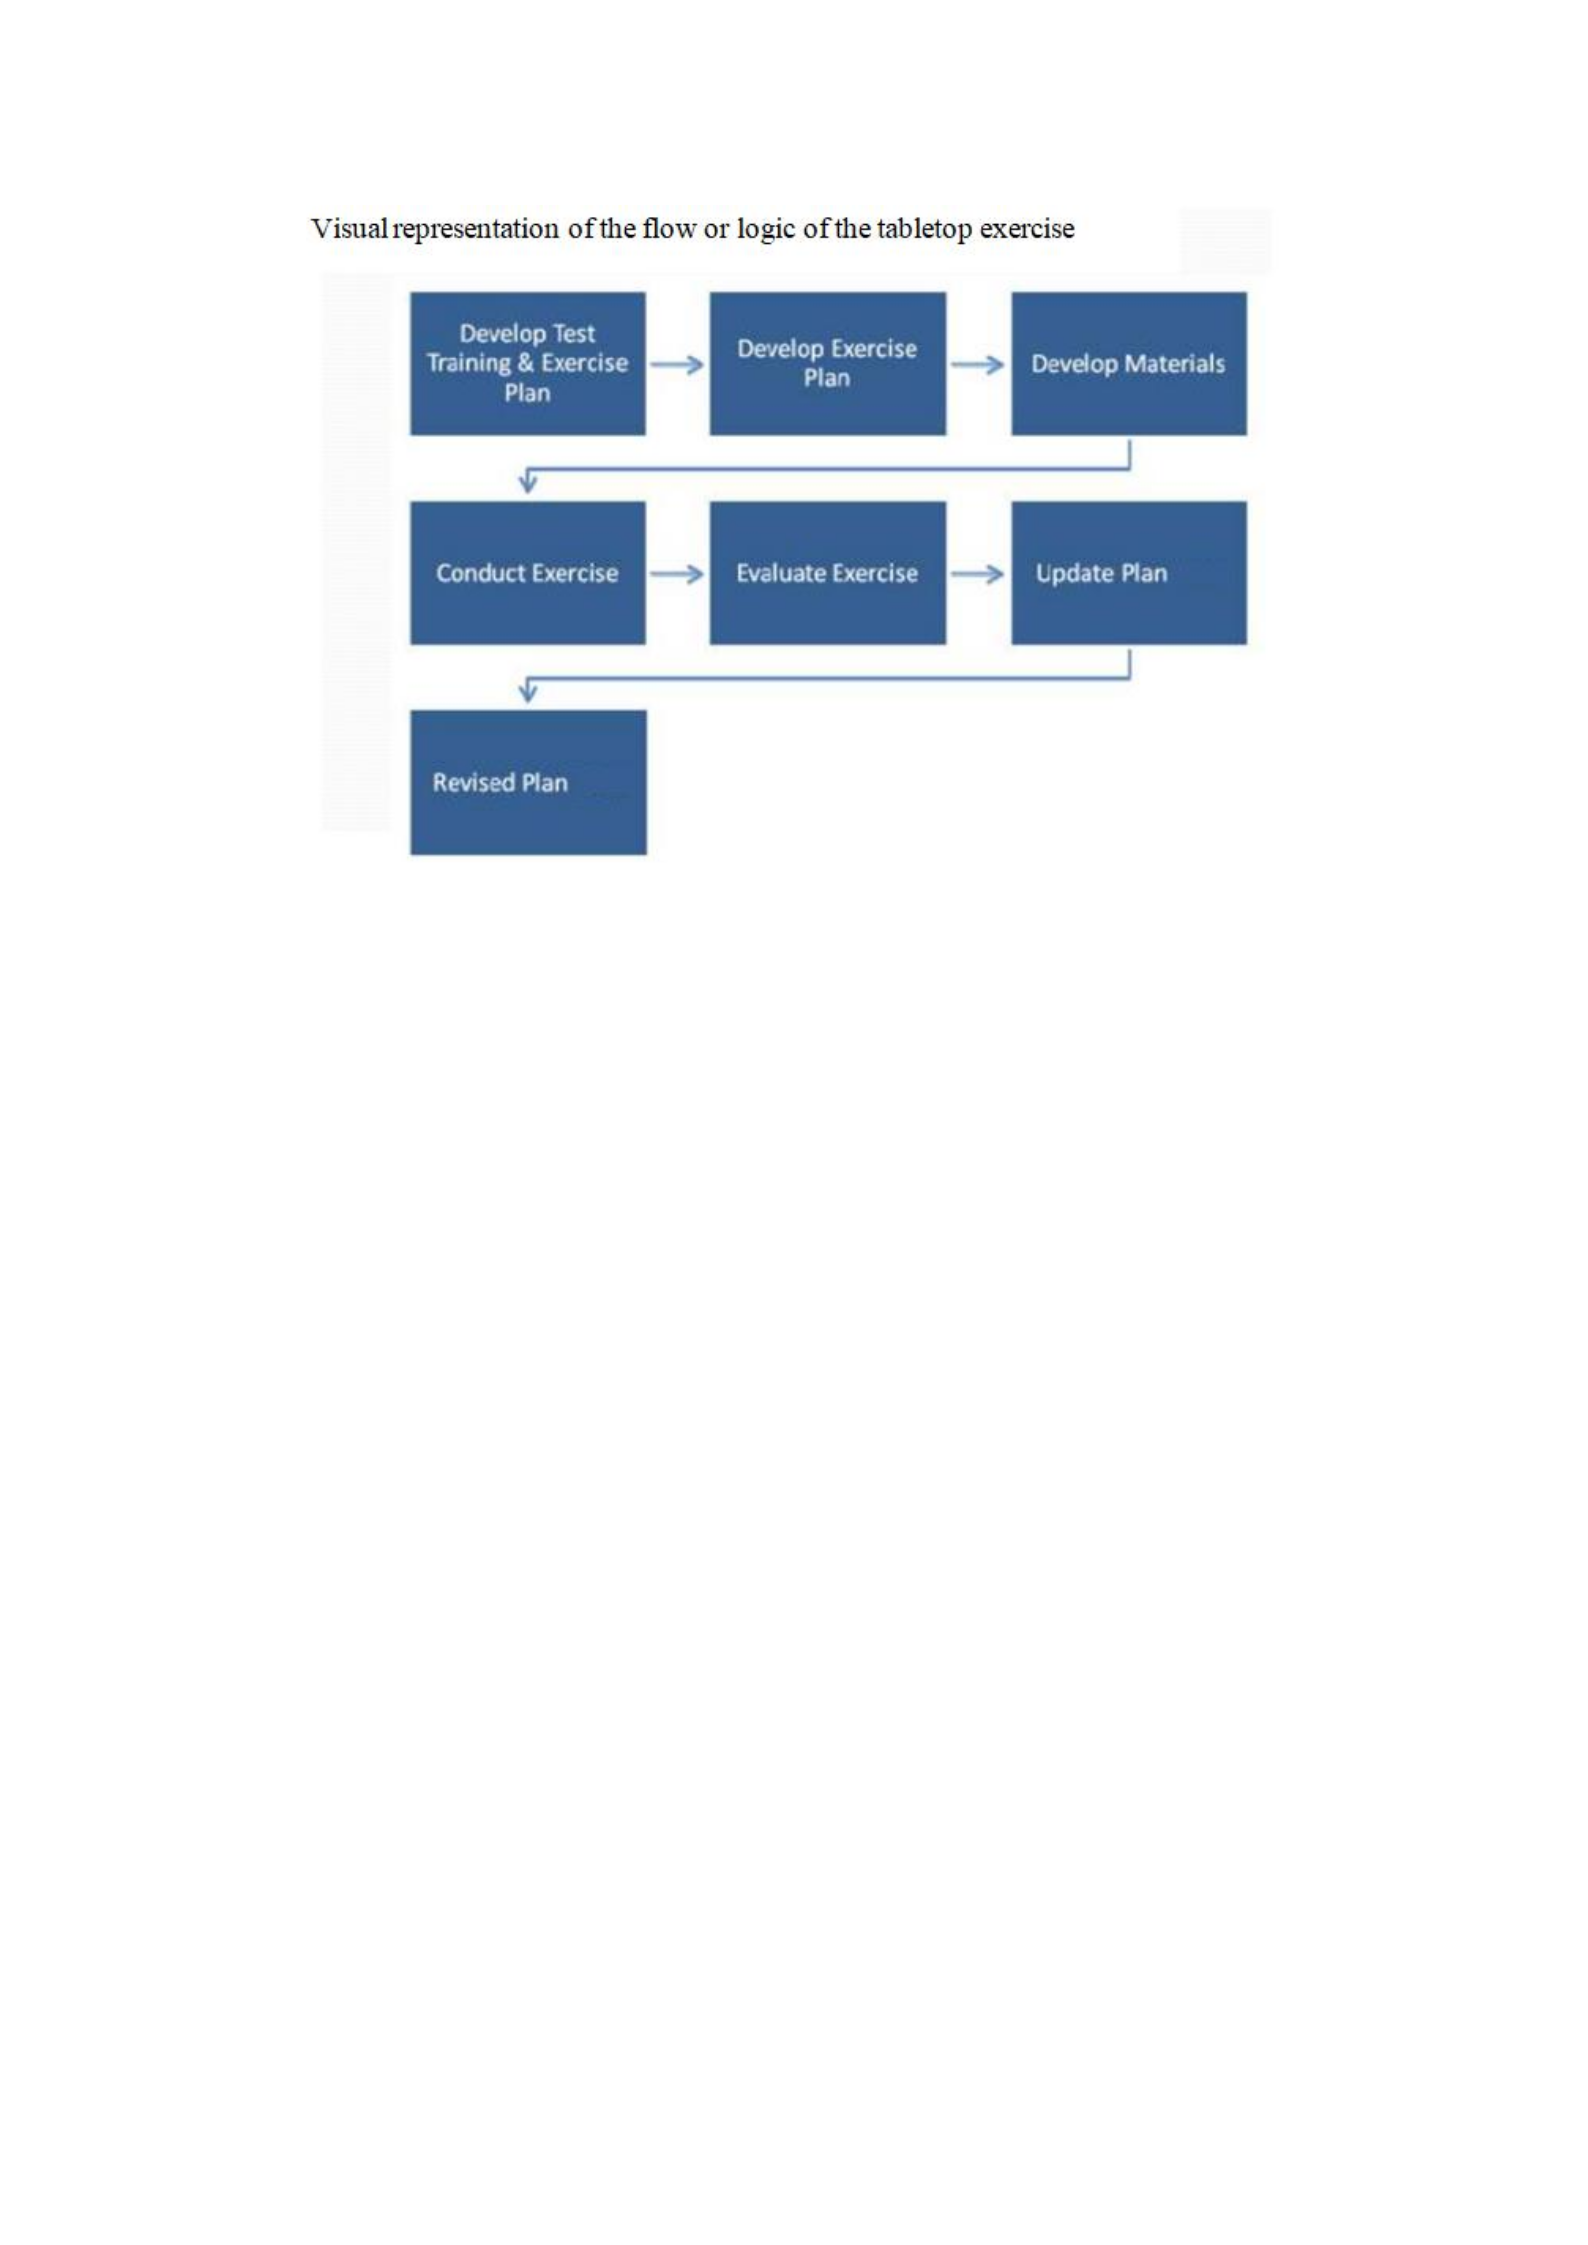
Visual representation of the flow of exercise
The flowchart that has been presented below shows how different processes
of the tabletop training program would be conducted in the organizational context.
All the activities would play an integral role to help the employees become aware
of different risk scenarios that could compromise the IT ecosystem of the firm due
to the use of Intelligent Virtual Assistant technology.
ISE 690 g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g 26
Source: (Shaurette, 2017)
Projects of lessons learned
The tabletop training exercise that would revolve around IVA would be of
high value for the employees of Callego. It would make the participants aware of
the security gaps that exist in the system. The IT team would get a detailed insight
into the gaps that exist in its current Technical controls thus it could introduce
necessary improvements in them.
Similarly, the simulated risk scenario would help the team to employ a
streamlined communication procedure so that proper engagement could be possible
among the relevant parties simultaneously. The other areas and aspects that need to
be covered in other training and awareness campaigns include the proper education
on the technical elements of Intelligent Virtual Assistants. The technical know-how
will empower the staff to understand how vulnerability can arise and intensify. The
training laid high emphasis on the regulatory and legal elements that govern the
industry such as the GDPR. There is further scope to expand the knowledge on the

ISE 690 g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g 27
updated regulations and legal components. A robust and systematic documenting of
risk is necessary. It would help the upper management of Callego to review these
documents and introduce suitable corporate policies to enhance security relating to
IVA technology.
The tabletop training exercise would help Callego to strengthen the
preparedness of its employees to handle risky situations that could arise because of
the Sonya project. A diverse range of scenarios would be presented which would
give them an idea about how to tackle cyber threats and risks. The core areas that
the program would focus on include real-time intelligence and information sharing,
handling complex cybercriminals and online hacker attackers, effective cyber
coordination and robust recovery coordination. The role of all the participants in the
program would be critical to ensure that it would add value for them.
Framing Statement
In the evolving industrial context, Callego is likely to face a number of
consultation problems relating to the Intelligent Virtual Assistant (IVA), GDPR
Principles and building an Incident Management Capability. In order to effectively
manage these issues, there is a need to deploy a transparent and effective
communication and engagement approach.
Consulting Problems
The introduction of the Intelligent Virtual Assistant named Sonya could
improve the overall efficiency and consistency in the quality of customer service that
is provided by the organization. But it could also give rise to a number of privacy
and security challenges as the firm handles a huge volume of customer information.
Similarly, the firm must ensure that it complies with the GDPR Principles and gives
high priority to the safety of the clients and customers. The ultimate consulting

ISE 690 g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g 28
problem revolves around building a robust Incident Management Capability by using
a Tabletop Simulation Exercise. These concerns need to be addressed in a
comprehensive manner so that the ultimate purpose of the innovative approach of the
business undertaking would not be defeated. g
Top three policies and procedures for GDPR compliance
Adopting a systematic approach to collect personal data from the customers
which are not shared by any unauthorized third-party
The appointment of a Data Protection Officer (DPO) and incorporating his
contact information in the privacy policy of the organization
Resolving security issues and complaints within a stipulated time frame in a
prompt and professional manner is necessary (PrivacyPolicies.com, 2019).
Revisions have been made so that Callego could comply with the General
Data Protection Regulation (GDPR) in a better way and the quality of security
infrastructure of the firm could be strengthened.
Framing Statement for Consulting Collection Components
Since Callego operates in a highly dynamic and evolving market setting, it is
necessary to give high priority to the security posture and security policies that are
followed by it. The consulting issues that have been highlighted could have a major
implication on its sustainability.
In order to get a holistic insight into the consulting aspects of the business
entity, a systematic process has been implemented. Some of the key areas that have
been highlighted in the consultation collection relate to how the security framework
would get altered after the introduction of the new Intelligent Virtual Assistant. This
technology-based concept is emerging in the market setting. Its application in the

ISE 690 g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g 29
Callego firm could simplify its processes but it could also increase security and
privacy concerns. A holistic assessment of the security setting has been carried out
to capture the exact issues that could jeopardize the business undertaking. g
The firm needs to give high emphasis to GDPR regulations so that the
personal data and information pertaining to the clients and customers would not get
compromised. In order to abide by the rules and regulations, the high focus has
been given to lawfulness, transparency, and fairness. These basic elements would
ensure that the consulting problem relating to the compliance to the General Data
Protection Regulation could be effectively managed in the organizational setting. A
Tabletop Simulation Exercise has been devised so that the involved participants
would be aware of how they need to react to threatening situations that could
compromise the level of security of the technological setting. A holistic assessment
of the Information Technology setting of the business undertaking has been carried
out to devise suitable technical controls. The controls that have been devised are
firewalls, intrusion detection and prevention systems and malware scanners. These
elements would play a vital role and strengthen the effectiveness of the IT security
of the business entity. In addition to these approaches, a simulation program has
been devised by Callego that focuses on various participants. Callego has adopted
such an approach so that the Network Administrator, organizational personnel,
Intelligent Virtual Assistant Security Manager and customers would be well prepared
to deal with contingency situations.
In order to minimize the security and consulting concerns of Callego, an in-
depth and thorough assessment of the entire situation was carried out. This
systematic approach sheds light on various important aspects relating to IT security.
All the components relating to the consulting collection have been assessed in great
ISE 690 g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g 30
detail so that the firm would be able to deliver quality customer service by
introducing the IVA technology.
The communication has been designed in a simple manner so that the audience from
the non-technical background could understand the consulting collection components
of the firm.
References
3 Things You Need to Know About GDPR and Intrusion Detection. (2019).
Retrieved November 30, 2019, from
https://www.insightsforprofessionals.com/it/security/need-to-know-gdpr-intrusion.
Chung, H., Iorga, M., Voas, J., & Lee, S. (2017). Alexa, can I trust you?.
Computer, 50(9), 100-104.
Emergency Management Institute (EMI) Virtual Table Top Exercise (VTTX). (2019).
Retrieved December 13, 2019, from
https://training.fema.gov/programs/emivttx.aspx
Gibb, K. (2019). GDPR - Information Security Policy. Retrieved December 13, 2019,
from https://stjosephs.southwark.sch.uk/en/home/terms-privacy/1366-gdpr-
information-security-policy.
Gray, P. (2019, September 16). The Rise of Intelligent Virtual Assistants. Retrieved
November 13, 2019, from https://www.interactions.com/blog/intelligent-virtual-
assistant/rise-intelligent-virtual-assistants/.
General Data Protection Regulation (GDPR): The paradigm shift in privacy. (2018).
Retrieved November 20, 2019, from.

ISE 690 g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g 31
Is Your Cloud-based Anti-Malware Solution GDPR Compliant? (2019). Retrieved
November 30, 2019, from https://www.opswat.com/blog/cloud-based-anti-malware-
solution-gdpr-compliant.
IT Security Management: Roles and Responsibilities. (2019). Retrieved December 13,
2019, from https://www.edology.com/blog/computing-it/it-security-management-
roles-responsibilities/.
Know Your Compliance. (2019, November 7). GDPR Appropriate Technical and
Organisational Measures. Retrieved November 30, 2019, from
https://www.knowyourcompliance.com/gdpr-technical-organisational-measures/.
Knote, R., Janson, A., Eigenbrod, L., & Söllner, M. (2018). The what and how of
smart personal assistants: Principles and application domains for IS research.
Microsoft's commitment to GDPR, privacy and putting customers in control of their
own data. (2018, June 7). Retrieved November 20, 2019, from
https://blogs.microsoft.com/on-the-issues/2018/05/21/microsofts-commitment-to-gdpr-
privacy-and-putting-customers-in-control-of-their-own-data/.
PrivacyPolicies.com. (2019). Retrieved November 20, 2019, from
https://www.privacypolicies.com/blog/gdpr-privacy-policy/.
Rouse, M., & Jayaram, M. N. (2019). What is Capability Maturity Model (CMM)? -
Definition from WhatIs.com. Retrieved November 30, 2019, from
https://searchsoftwarequality.techtarget.com/definition/Capability-Maturity-Model.
Six Scenarios to Help Prepare Your Cybersecurity Team. (2019). Retrieved December
13, 2019, from https://www.cisecurity.org/wp-content/uploads/2018/10/Six-tabletop-
exercises-FINAL.pdf.
ISE 690 g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g 32
Shaurette, K. (2017). Surviving a Mock Disaster. Retrieved December 13, 2019, from
https://secure360.org/wp-content/uploads/2016/05/Surviving-a-Mock-
Disaster_KenShaurette.pdf.
The Virtual Personal Assistant and Its Security Issues. (2017, May 31). Retrieved
December 13, 2019, from https://resources.infosecinstitute.com/virtual-personal-
assistant-security-issues/#gref.
The 6 GDPR privacy principles you must know - now. (2018, January 25).
Retrieved November 20, 2019, from http://techgenix.com/6-gdpr-privacy-
principles/.
The principle of least privilege: A strategy of limiting access to what is essential.
(2018, July 3). Retrieved November 30, 2019, from
https://www.welivesecurity.com/2018/07/02/principle-least-privilege-strategy/.
What is Layered Security? - Definition from Techopedia. (2019). Retrieved December
13, 2019, from https://www.techopedia.com/definition/4005/layered-security.
What Is an Intelligent Virtual Assistant? - Definition from Techopedia. (2019).
Retrieved November 13, 2019, from
https://www.techopedia.com/definition/31383/intelligent-virtual-assistant.
Zeichick, A. (2018). GDPR Should Change Your Thinking About Network Firewalls.
Retrieved November 30, 2019, from
https://www.securitynow.com/author.asp?section_id=716&doc_id=743272.

