



OPM Data Breach
Amanda Shears
Liberty University
HLSC 500

Who is the Office of Personnel
Management (OPM)?
Serves as chief human resources agency and personnel policy manager
for the Federal Government
Directs multiple programs such as:
Human resources and employee management services, administers
retirement benefits, manages healthcare/insurance programs, oversees merit-
based and inclusive hiring into the civil service, and provides a secure
employment process
Responsible for the management of security clearances for the U.S.
Government
About the Breach
OPM receives at least 10 million attempts of cyber breach every month
Unclear when incidents amounting to cyber breach started; believed that attempts began in 2013
Series of attacks happened allowing hackers to slowly gain access and implement controls
NOV 2013, a group of hackers (X1) carried out an attempt of a cyber-breach and despite failing were
able to break out details on IT manuals with architecture information
MAR 2014, OPM was hacked but access was no gained to personal information; Hackers information
was retained for purposes of monitoring them
OPM were able to hinder theft by using IDS; no confidential information was lost during the breach
MAY 2014 a hacker group (X2) had successfully introduced malware into OPM’s network, IDS did not
notice this incident and therefore could not stop the execution of the malware plan; creating a back
door in the system
JUN 4th, 2015 data breach
OPM reported on the largest cases of the breach in history which was investigated by DHS through
the Einstein system.
This is an (IDS) intrusion detection system that operates by evaluating federal internet for any suspicious
activity that could be a threat to cybersecurity

About the Breach (Cont.)
Over 2.4 million people both current and former employees information
was compromised
Data compromised involved confidential information for former and current
employees, dignified contractors and all the employees connected to the
agency through and queries or forms
Information about applicants into the organization containing their residential
and marital statuses, user names, passwords, fingerprints was stolen and this
constituted to about 1.1 million
Further damage was registered later and information for about 21.5 million
people was stolen
About the Breach (Cont.)
OPM, in turn, notified over 15 federal agencies about the unfortunate
incident and notified all personnel who were possibly affected
DHS, in conjunction with the U.S. Computer Emergency Readiness Team,
opened an investigation to conceptualize the nature and the scope of
the attack
OPM Director Katherine Archuleta admitted that information breach occurred
because of the encryption systems in OPM database were outdated
Director of OPM resigned amidst judgment from various critics around the
world on the fact that the agency failed to keep securely sensitive employee
information
Phase of Emergency Management
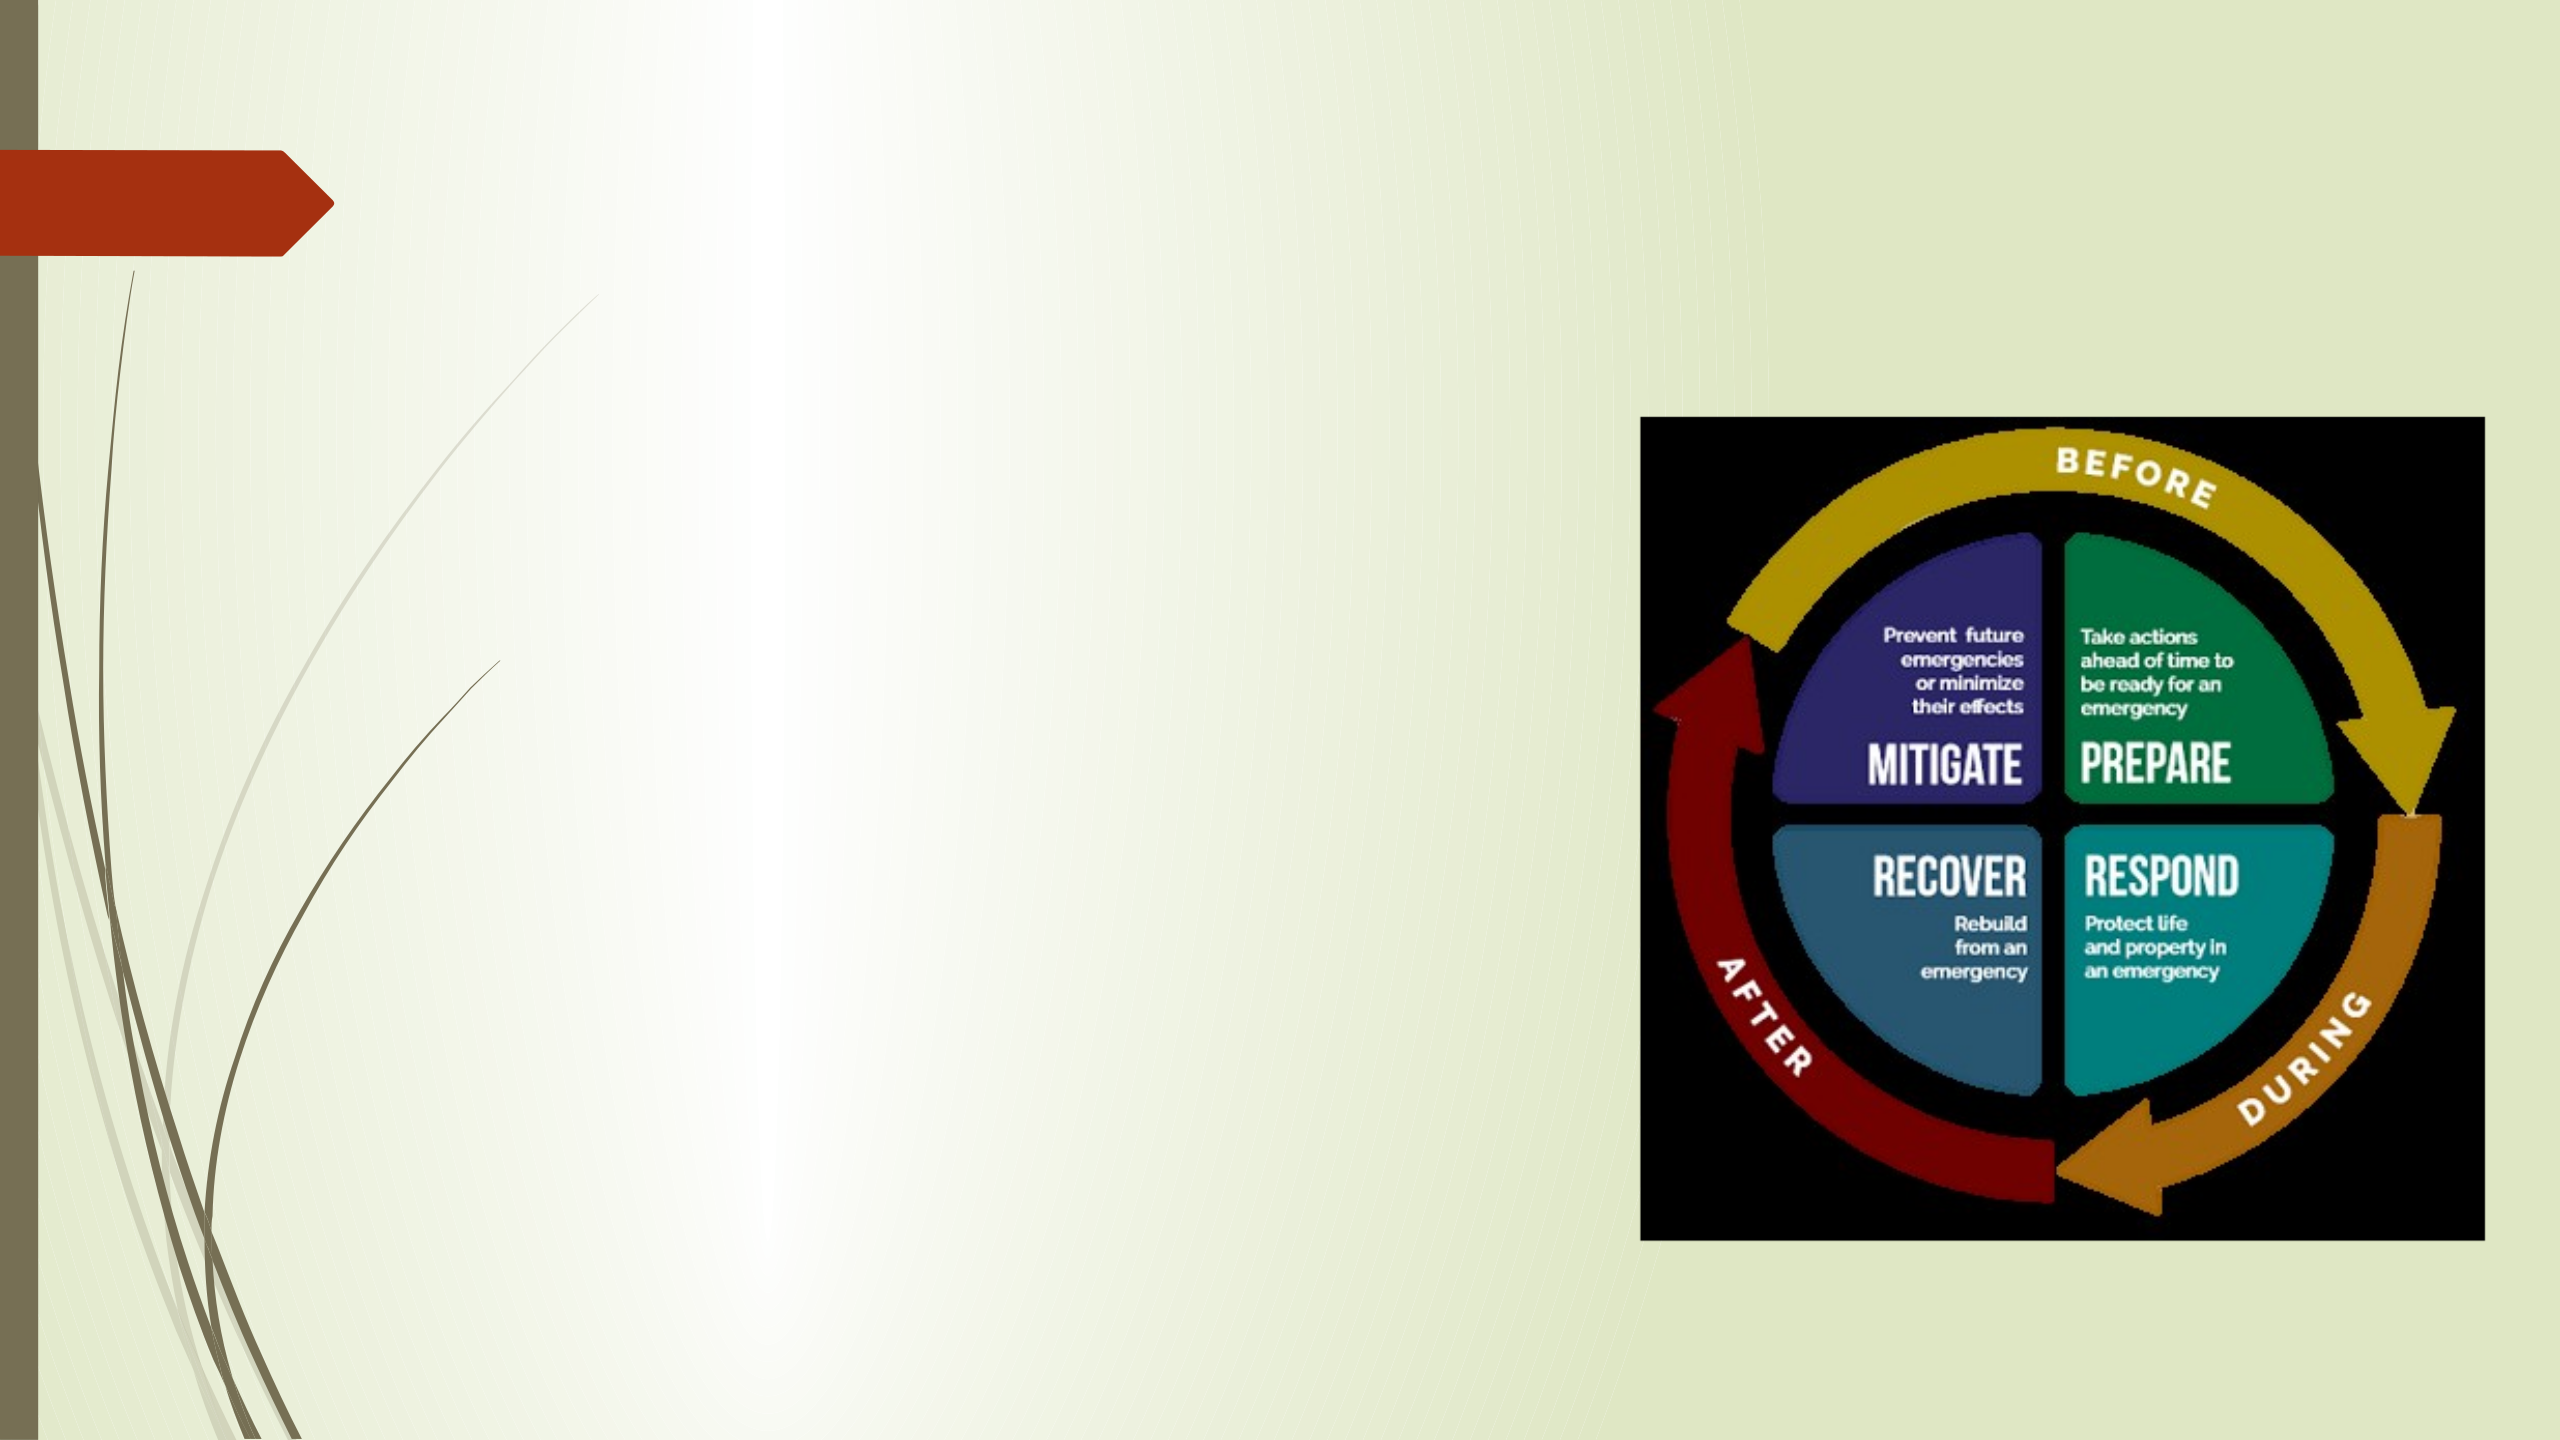
Emergency management is identified by four
distinct phases in the United States
Mitigation
Preparedness
Response
Recovery
Emergency management is majorly associated
with actions that are directed towards combating
and preventing both natural and human-induced
calamities
Robustly decentralized with activities that combine
services of the non-government organization,
private sector and any other agencies in the
country

Phase of Emergency: Mitigation
Identification of the probable risks that would be faced by the country to
devise means on how they can be eliminated before they cause adverse
damage in the country
Mitigation measures can either be from a long term goal or in the
aftermath of a catastrophic occurrence
According to the official report from DHS cyber strategy, the major
objective:
Assess the risk to determine the magnitude of exposure
Set priorities from different areas depending on their vulnerability levels

Phase of Emergency: Preparedness
Focuses on how the affected agencies will respond to the circumstances
of cybersecurity
Involves planning and training personnel on how to overcome these
challenges
Intelligence surveillance systems are also incorporated in this activity
together with resource allocation for the different sectors
Presidential Policy Directive as reported by DHS, is in charge of national
preparedness and therefore strategizes on behalf of the nation

Phase of Emergency: Response
Activities that drive towards reacting to stimuli that and this to mean the
activities that have been executed against the goodness of the people in
the US
Involves impulsive actions drawn to save property, lives and important
information in the nation through the use of various resources,
stockpiles, and command centers and so much more
DHS, through the NCCIC, is responsible for all aspects of response
Uses all gathered information about cyber breaches and causes public
awareness to protect people from any such incidences

Phase of Emergency: Recovery
Activities of restoration that are driven towards vanishing up the
damages that were a result of the unfortunate circumstances
Possible amendment of the government's constitutional duties and
activities, rebuilding of stockpiles and reallocating resources
Federal Government directs its response to activities of cyber-crime
through federal agencies in conjunction with the Cyber Unified
Coordination Group

Wrap-Up
Incidences of cybercrime will never cease because the world today is
transiting through an era that is digitalized and full of technology
New ideas paired together with new technologies and developments
that can either be employed for the better good of humanity or used by
malicious personnel who either wish to gain political power, money,
supremacy, and all the other intentions
Care must be taken to fully protect and keep sensitive information away
from malicious people and hackers so that the safety of information is
guaranteed
Improve the trust that the people put in the government and federal
organizations at large.

References
Baird,HM.HE. (2010). The “Phases” of Emergency Management.
Bisson,HD. (2015). The OPM Breach: Timeline of a Hack. Retrieved from
https://www.tripwire.com/state-of-security/security-data-protection/cyber-security/the-opm-
breach-timeline-of-a-hack/
Finklea,HK., Christensen,HM.HD., Fischer,HE.HA., Lawrence,HS.HV., & Theohary,HC.HA. (2015,). Cyber
Intrusion into U.S. Office of Personnel Management: In Brief.
Fruhlinger,HJ. (2018). The OPM hack explained: Bad security practices meet China's Captain
America. Retrieved from https://www.csoonline.com/article/3318238/the-opm-hack-explained-
bad-security-practices-meet-chinas-captain-america.html
Koerner,HB.HI. (2016). Inside the OPM Hack, the Cyber attack That Shocked the US Government.
Retrieved from https://www.wired.com/2016/10/inside-cyberattack-shocked-us-government/
Lindsay,HB.HR. (2012). Federal Emergency Management: A Brief Introduction.
U.S. DEPARTMENT OF HOMELAND SECURITY. (2018). U.S. DEPARTMENT OF HOMELAND SECURITY
CYBERSECURITY STRATEGY.

