


1
SNHU
ISE 510 Security Risk Analysis & Plan
Week 8 HW
Developing a Risk Remediation Plan
30 points
2
Read Chapter 10 and 11 in our textbook first.
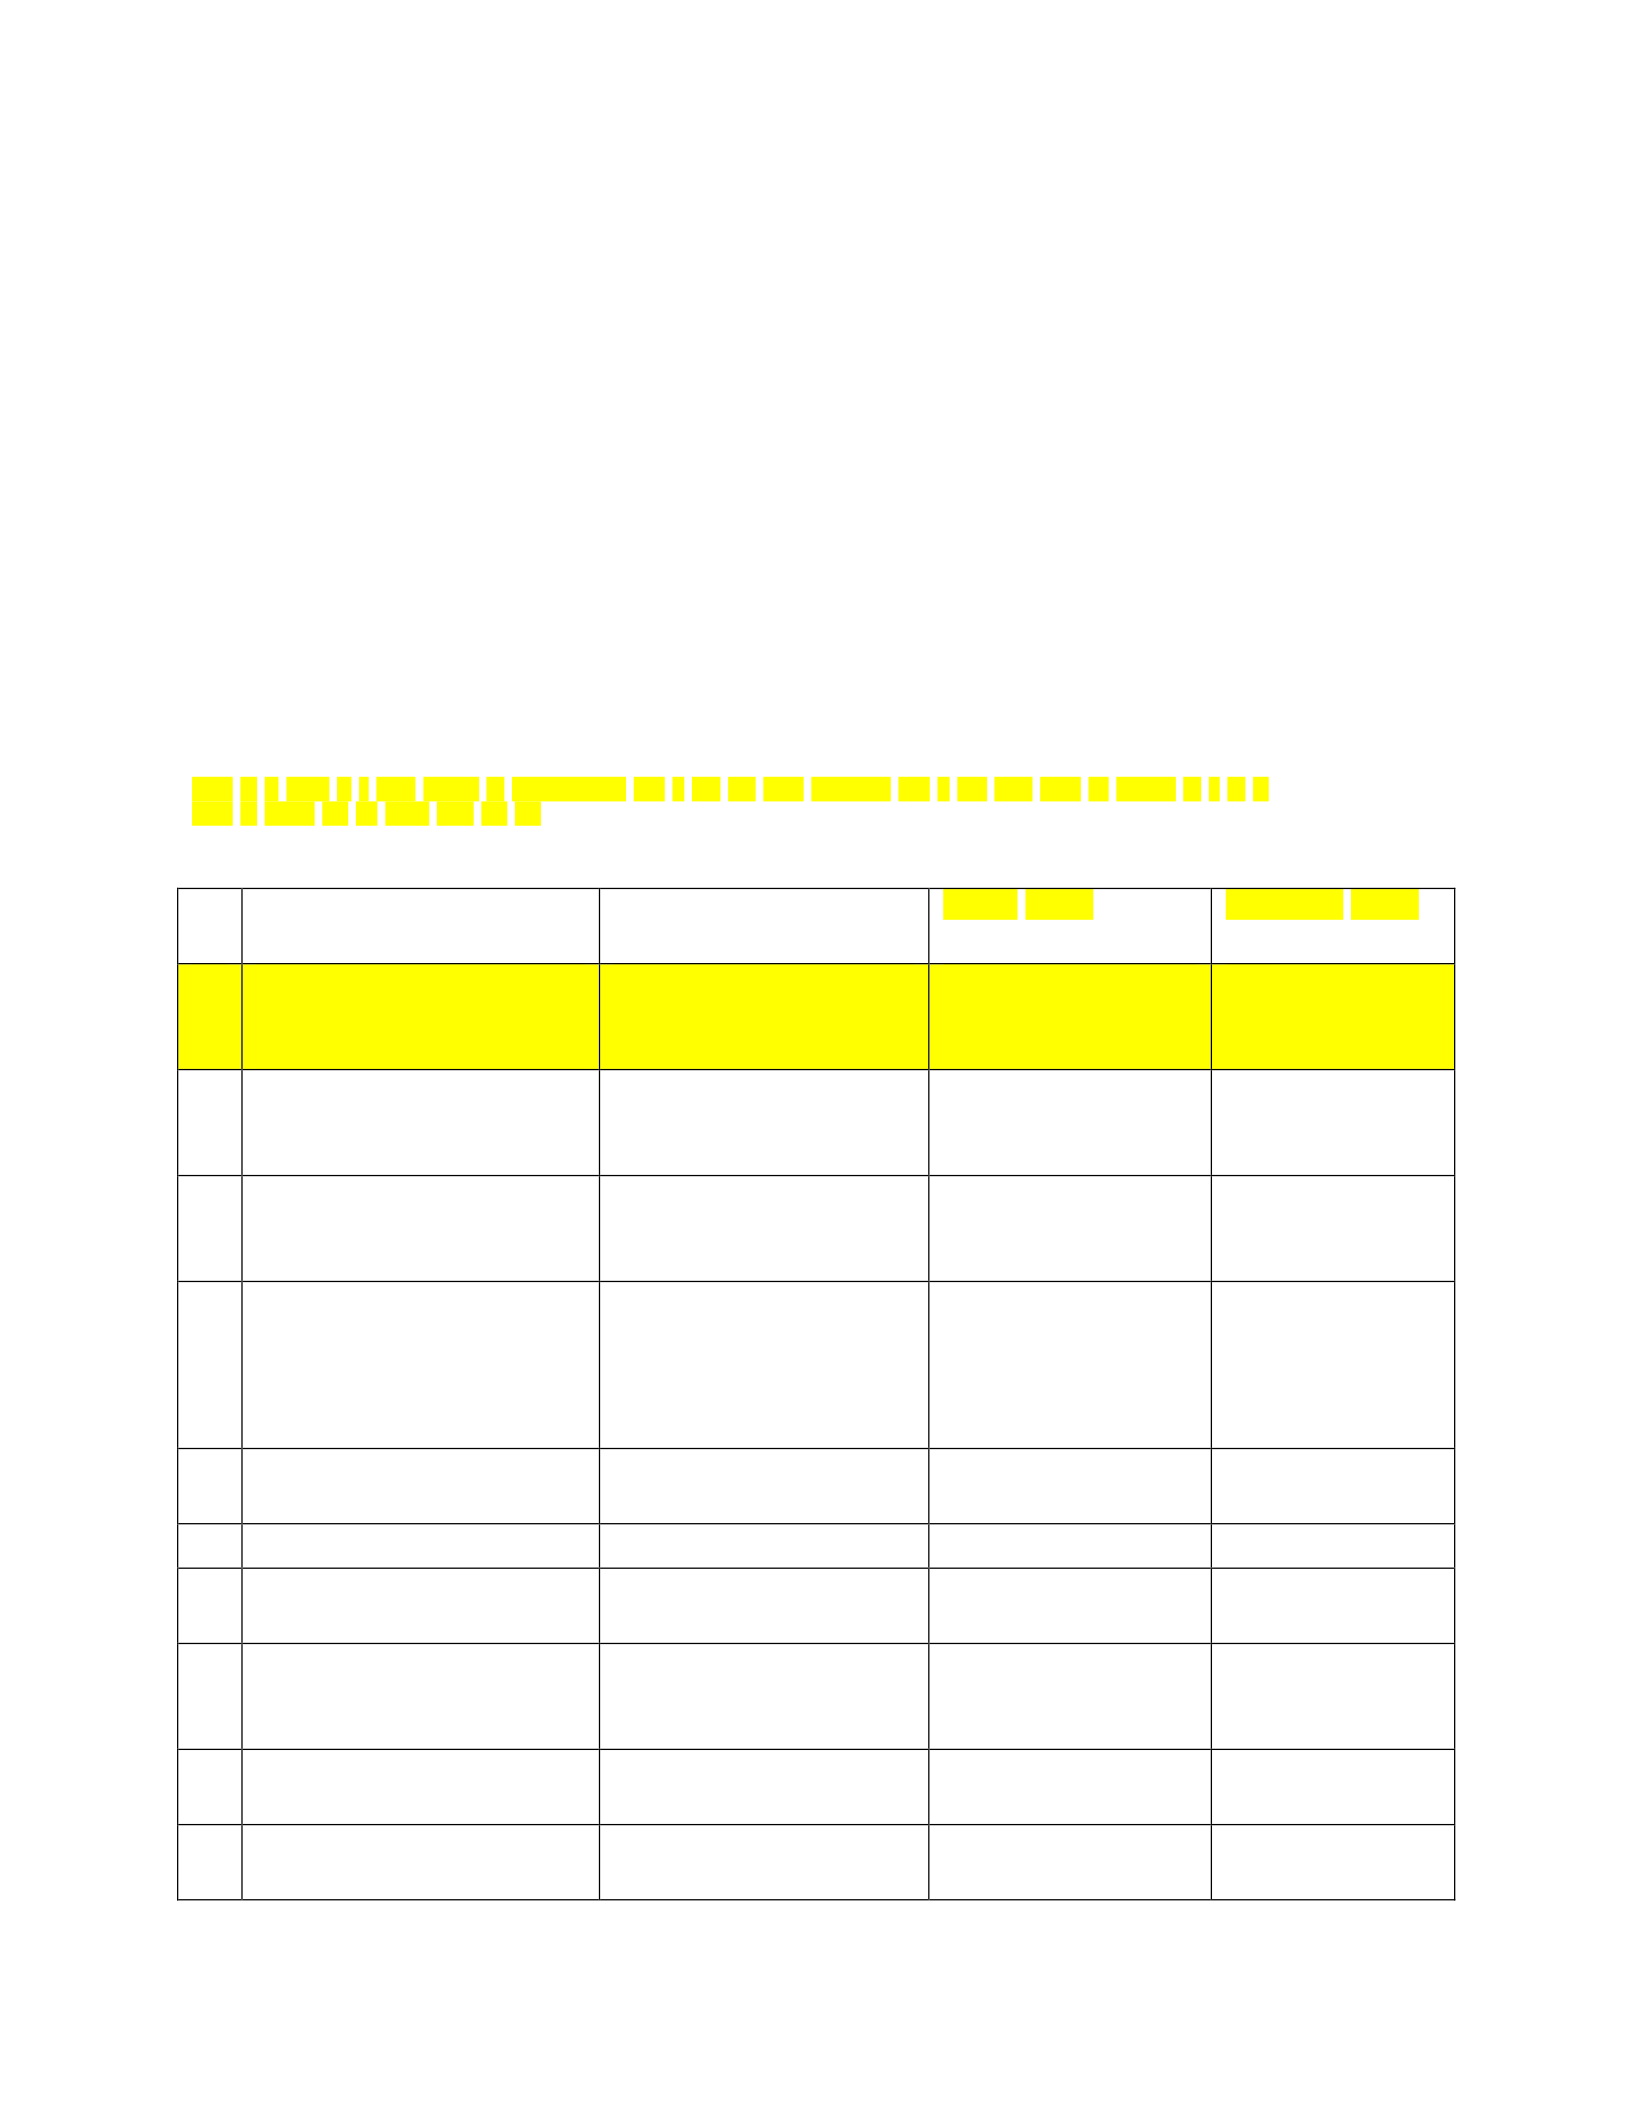
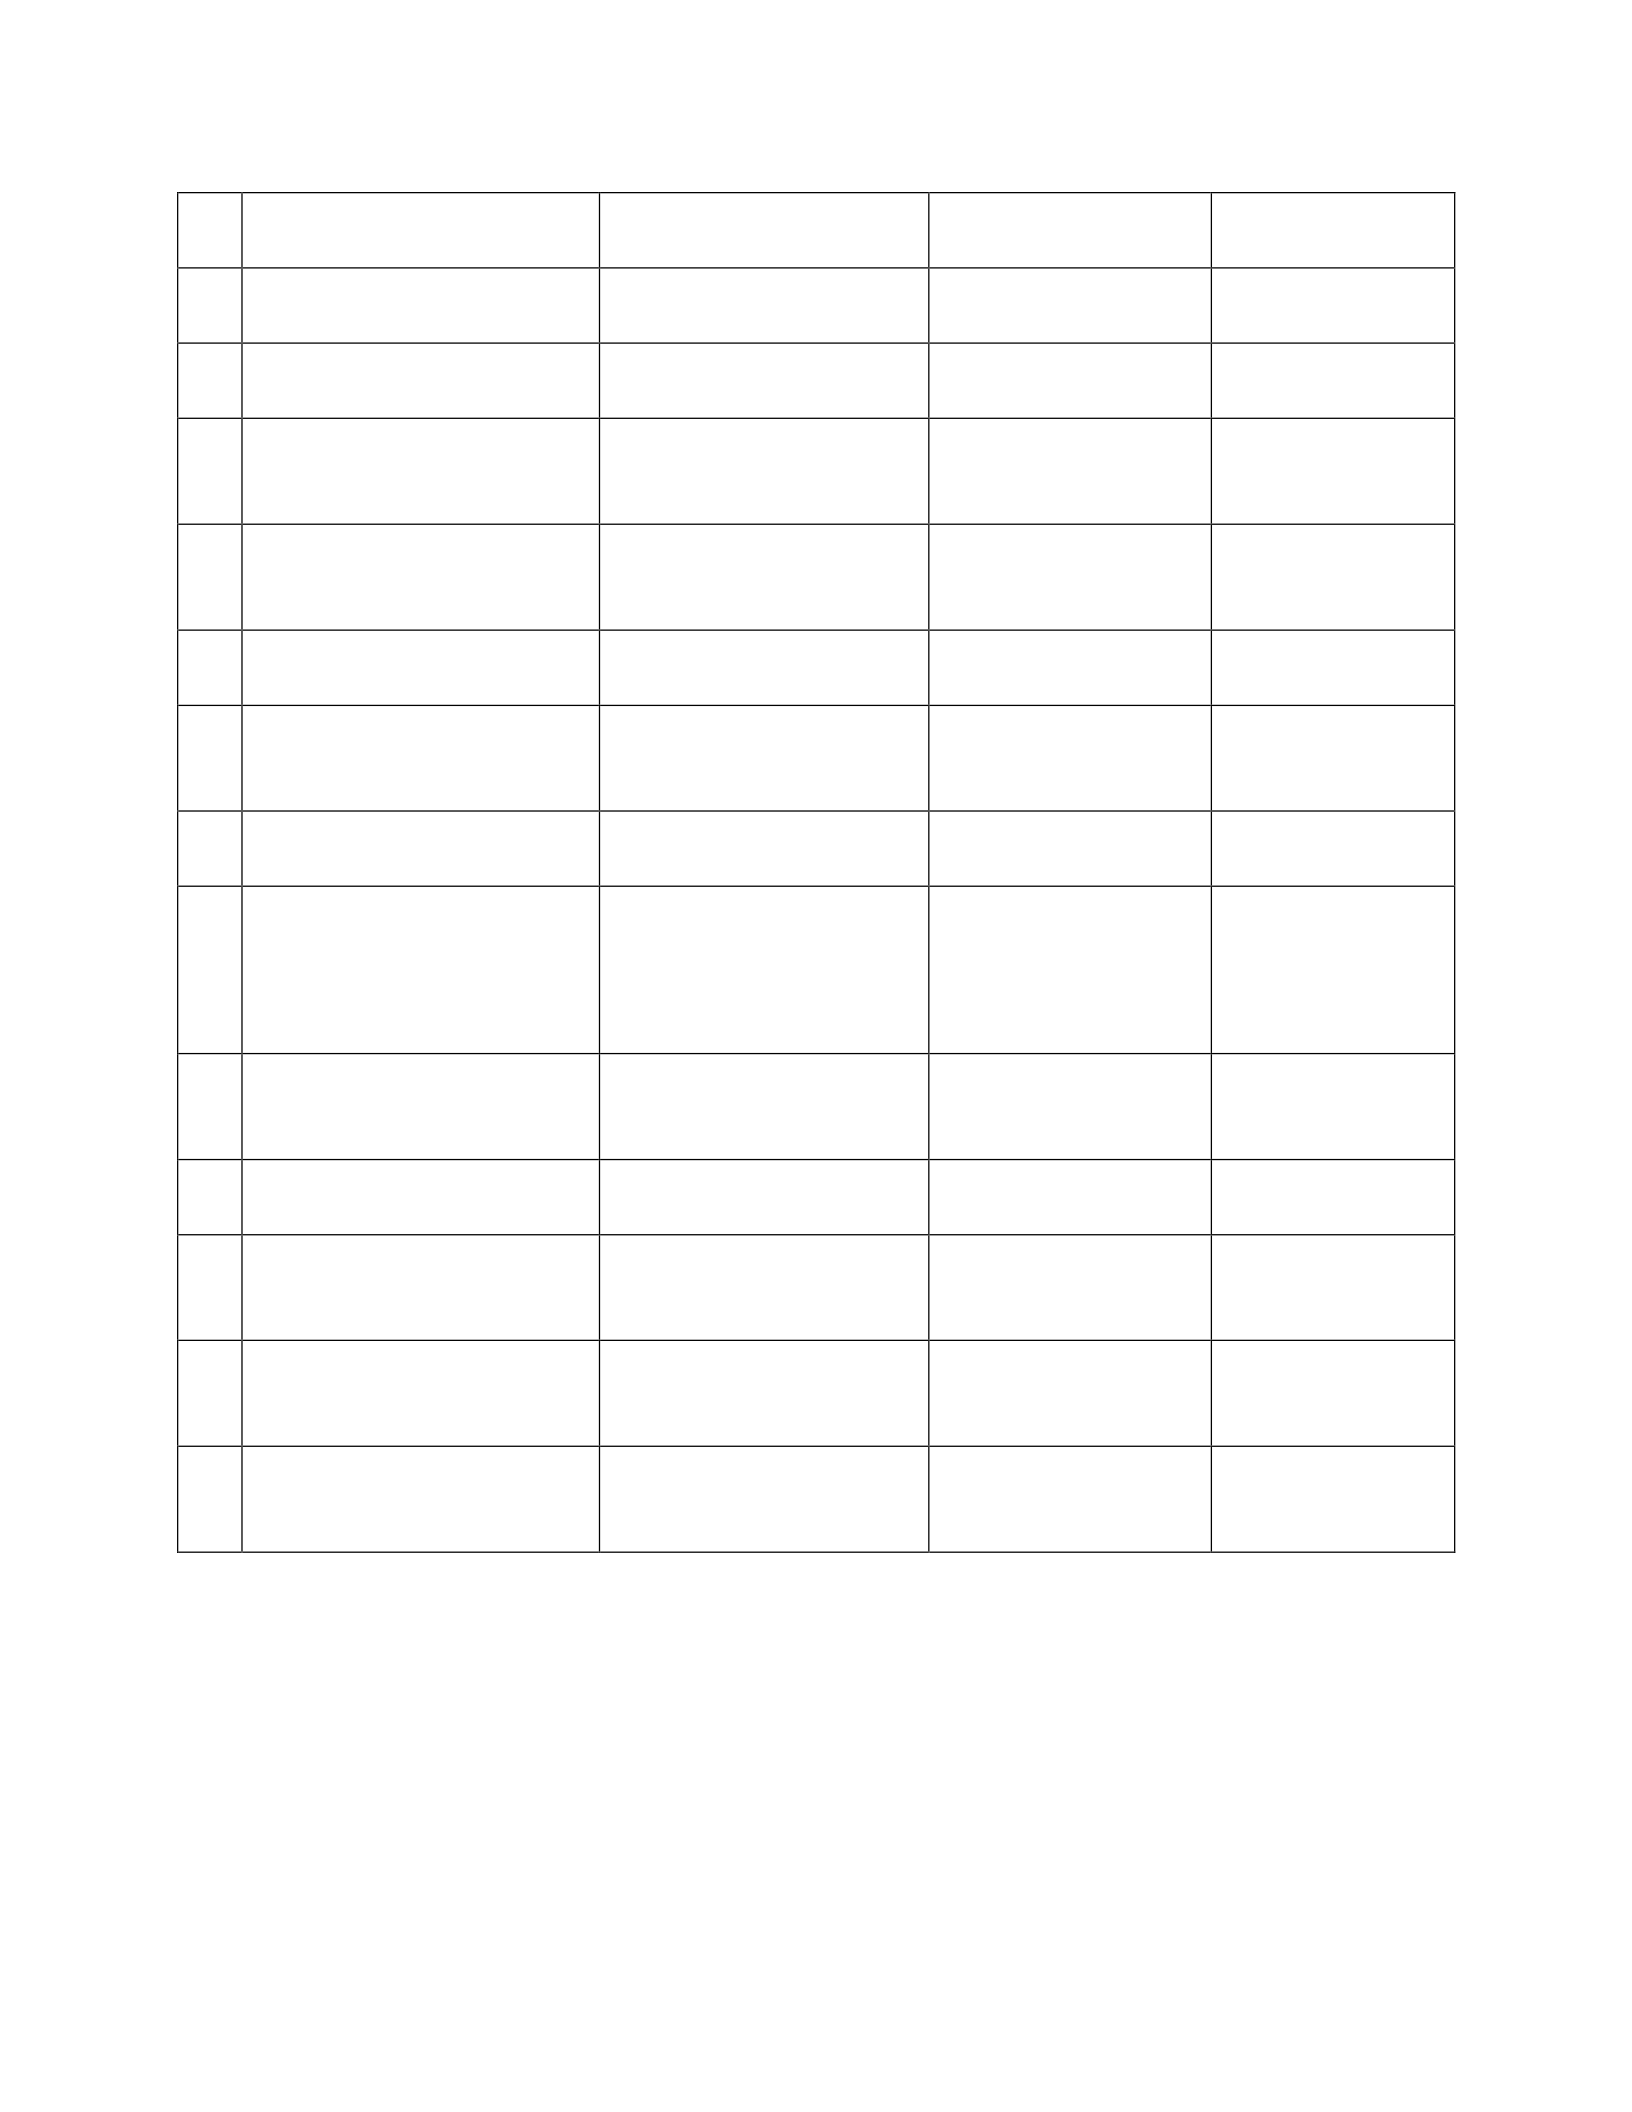
1) The table below has a list of LIMETREE’s Risks Threats and Vulnerabilities. The primary
Domain is listed in the third column. You are to place the Impact Factor based on the definitions
below, and then place a likelihood factor (Low, Medium, High) based on your experience,
research or insight.
1 = Critical: A risk, threat or vulnerability that impacts compliance (privacy laws requirements for securing
privacy data and implementing proper security controls) and places the organization at increased liability
2 = Major: A risk, threat or vulnerability that impacts confidentiality, integrity or availability of the organization’s
intellectual property assets and IT infrastructure
3 = Minor: A risk, threat, or vulnerability that impacts user or employee productivity or availability of the IT
infrastructure.
The first row is completed as an example.
Rule 1: If there is a Risk Threat or Vulnerability and it has not been exploited yet, it can only have an Impact of 2 or 3.
Rule 2: There are no more than ten 1’s
#
Risks Threats and
Vulnerabilities
Domain (primary)
Impact Factor
Likelihood Factor
EX
Technician (user) uses P2P
file sharing on company
owned PC
#1 - USER domain
2
high
1
Unauthorized access from
Internet to corporate servers
and applications
#7 - Remote Access
Domain
1
high
2
User destroys data in
application and deletes all
files she has access too.
#6 Application domain
2
low
3
Hacker penetrates your IT
infrastructure and gains
access to your internal
network because default
password is left on router
#4 LAN-to-WAN domain
1
high
4
Two employee’s share
usernames and passwords
#1 - USER domain
2
high
5
Fire destroys data center
#6 Application domain
1
medium
6
Workstation OS has known
vulnerabilities
#2 Workstation domain
2
medium
7
Internet Service provider has
2% loss of service which is
below the SLA.
#5 WAN Domain
3
low
8
Hacker penetrates IT system
by a phishing attach
#1 - USER domain
1
high
9
LAN switch has default
username and password
#3 - LAN Domain
2
high
3
10
Denial of service attack on
email server
#5 WAN Domain
1
high
11
User turns off screensaver on
PC
#1 User domain
3
low
12
Corporate Data server has no
backups
#6 Application domain
2
high
13
VPN tunneling between
remote computer and
ingress/egress router
#4 LAN-to-WAN domain
2
medium
14
Internet Service Provider has
major outage; no employees
can access Internet
#5 WAN domain
2
low
15
Web browser vulnerabilities
exist on client machines
#2 Workstation domain
3
low
16
A general-purpose sniffer is
found on organization-
controlled client PCs
#2 Workstation domain
2
high
17
System admin has found
DNS cache poisoning attack
#5 WAN Domain
1
high
18
The Telecommunications
closet where the switches and
routers reside is unlocked and
open because the AC is
broken.
#3 - LAN Domain
2
medium
19
Attacker tries brute force
attack against Corporate
Portal
#7 - Remote Access
Domain
2
medium
20
DDoS attack from the
WAN/Internet
#5 WAN Domain
1
high
21
WLAN access points are
needed for LAN connectivity
within warehouse
#3 - LAN Domain
3
low
22
WLAN access points need to
be protected from
eavesdropping
#3 - LAN Domain
1
medium
23
Weak ingress/egress traffic
filtering degrades
performance
#4 LAN-to-WAN domain
3
low
4
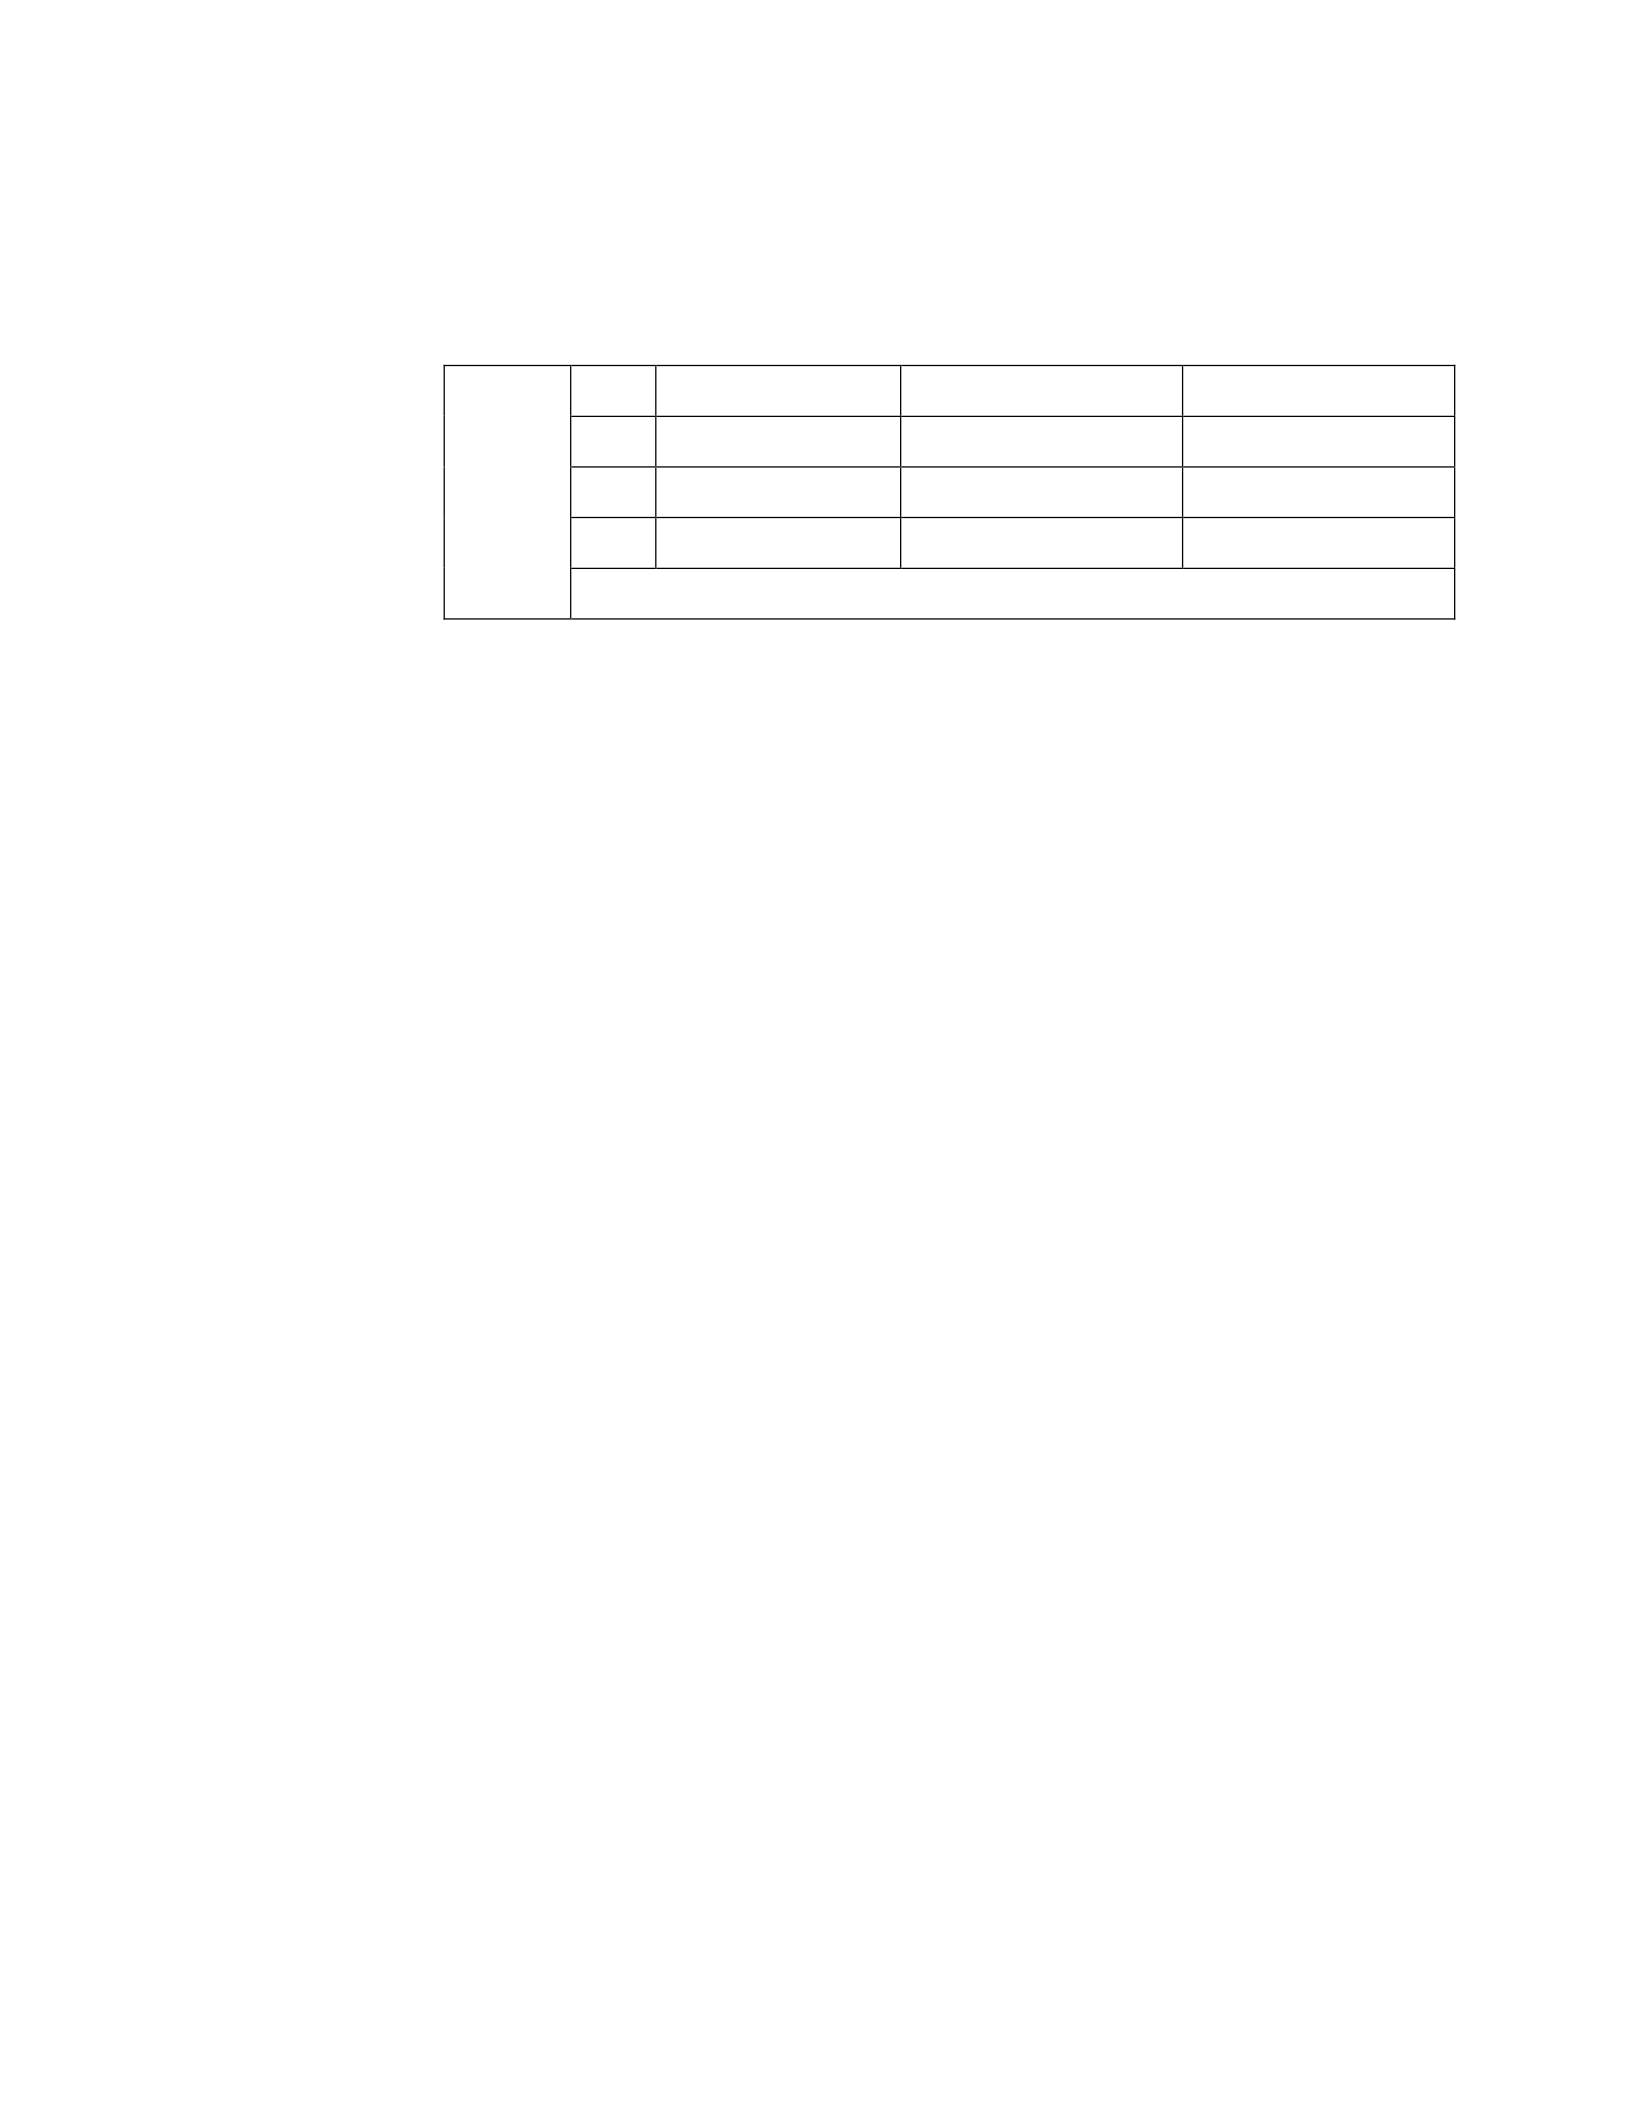
2) Frequency Table
Looking at your table above, count the number of “High-1” and place the number in cell High-1;
then High-2, High-3, Med-1 etc. repeat for all cells. The total of all the cells will be 23.
Impact
1
0
1
6
2
2
4
5
3
5
0
0
Low
Medium
High
Probability
What can you observe about the distribution? Is this company in trouble or are they close
to being secure?
I can understand that the company is in a bad position through looking at chart. However, I understood
that the company will surpass all the hurdles if it is given proper help and support. We already
understood the level of threat in front of the company by looking at the table. By looking at the table, the
control should be determined by us so that the risk could be avoided in the days to come. Mitigation of
risk would enable the company to achieve its proper growth. By bringing control over the operation,
certain changes should be entertained in this regard. The risk would be mitigated by taking wise control
by lowering the influence of threats. By taking control over the risk, we can consider to what extent the
risk can be acceptable. In this situation, some benefits can be achieved from CBA as it enables us to take
control ri ofsk and what control can be implemented in this situation. We are much benefitted by it on
deciding what kind of investment should be made or needed to achieve this control over mitigating the
risk. All the controls must be reviewed, however, only one system cannot be focused for it. It must be
wide, aiming to reduce the security controls. A mixture of broad as well as narrow security controls must
be used by us for achieving the best result.
3) Remediation plan
For the top 3 most critical risks, threats, or vulnerabilities, give a primary and an alternate
remediation course of action (COA). The primary course of action is what you recommend to
Management, and the alternatives are usually different in terms of effectiveness, cost,
compliance, and labor. Be sure to consider cost in your recommendation to Management. Use
references on each.
3-1. Hacker infiltrate the f IT infrastructure and gets access to our internal network
because default password is left on router
Primary: Create a DMZ to keep hackers out
Alternate: Discussed at end
3-2. DDoS attack coming from the WAN/Internet

5
Primary: Create DMZ to protect data. Up to date software to prevent the attack
Alternate: Discussed at end
3-3. Non-Approval access from Internet to corporate servers
Primary: Create DMZ to protect data to maintain PCI compliance
Alternate: Discussed at end
The public is kept separate by the DMZ (demilitarized zone) from sensitive data or internal
network. One of the main purposes of DMZ is to provide untrusted, trusted, and external sources
with strict access as necessitated to the releasable information during barricading the internal
networks from the attacks made from outside. In order to accomplish this, we are required to use
the firewall for separating the networks that must be internal and are used for housing our
important resources, the DMZ and the internet (Yoon, Weiss & Cho, 2018). During establishing
the communication between these areas, it is necessary to move through the firewall first. The e-
mail servers, servers, DNS servers, and other service types that will be needed access to the
world outside are included in the DMZ. The goal of the DMZ would be that the attacker should
obtain, and they will only be given access to that area. They will be separated from other
network areas.
We are required to ensure that our rules are performed and allow the traffic between the internal
network and DMZ to be linked as frequent as possible, aiming to secure the DMZ (Yoon, Weiss
& Cho, 2018). There should be specifications of the firewall rule to the servers, and that
specification should be on particular ports. It should maintain still daily business operation. We
must ready all the time and make sure that all the systems of DMZ are entirely patched, aiming
to deal with the new vulnerabilities. The firewall application layer should be more than the filter
of the port. That means, it will ensure that all the inspections closely performed. To cover all
this, we must buy a good firewall. There is a good option named Sonicwall, which would be
beneficial for us.
The price of Sonicwall hovers between $250 and $10,000. The pricing of this fully depends on
its features such as company scale, hardware, the requirement of the license, time-period of
subscription.
Alternatives to all three risks: The network should be segregated by us, aiming to make it
difficult for the intruder who tries to get in. As per the PCI standard, we physically need to
separate this. There are many advantages over the separation, such as obtaining better access
control, improve the security, improvement of monitoring the system, and many more. Some
investments should be made in IDS aiming to monitor our networks. There are many options
where we can choose the best one.
Suricata: it is free, and the source is open
Snort for Windows: it is free means does not bear any cost

6
The Bro Network Security Monitor: this is a high-performance network, and it is free.
Malware Defender: this free system can give us monitoring over the intrusions along with
malware detection (Yoon, Weiss & Cho, 2018).

7
References
Yoon, J. L., Weiss, P. S., & Cho, N. J. (2018). Envisioning Scientific Innovation in Korea’s
Demilitarized Zone: A Step toward Economic Progress and Global Peace.
8
Appendix
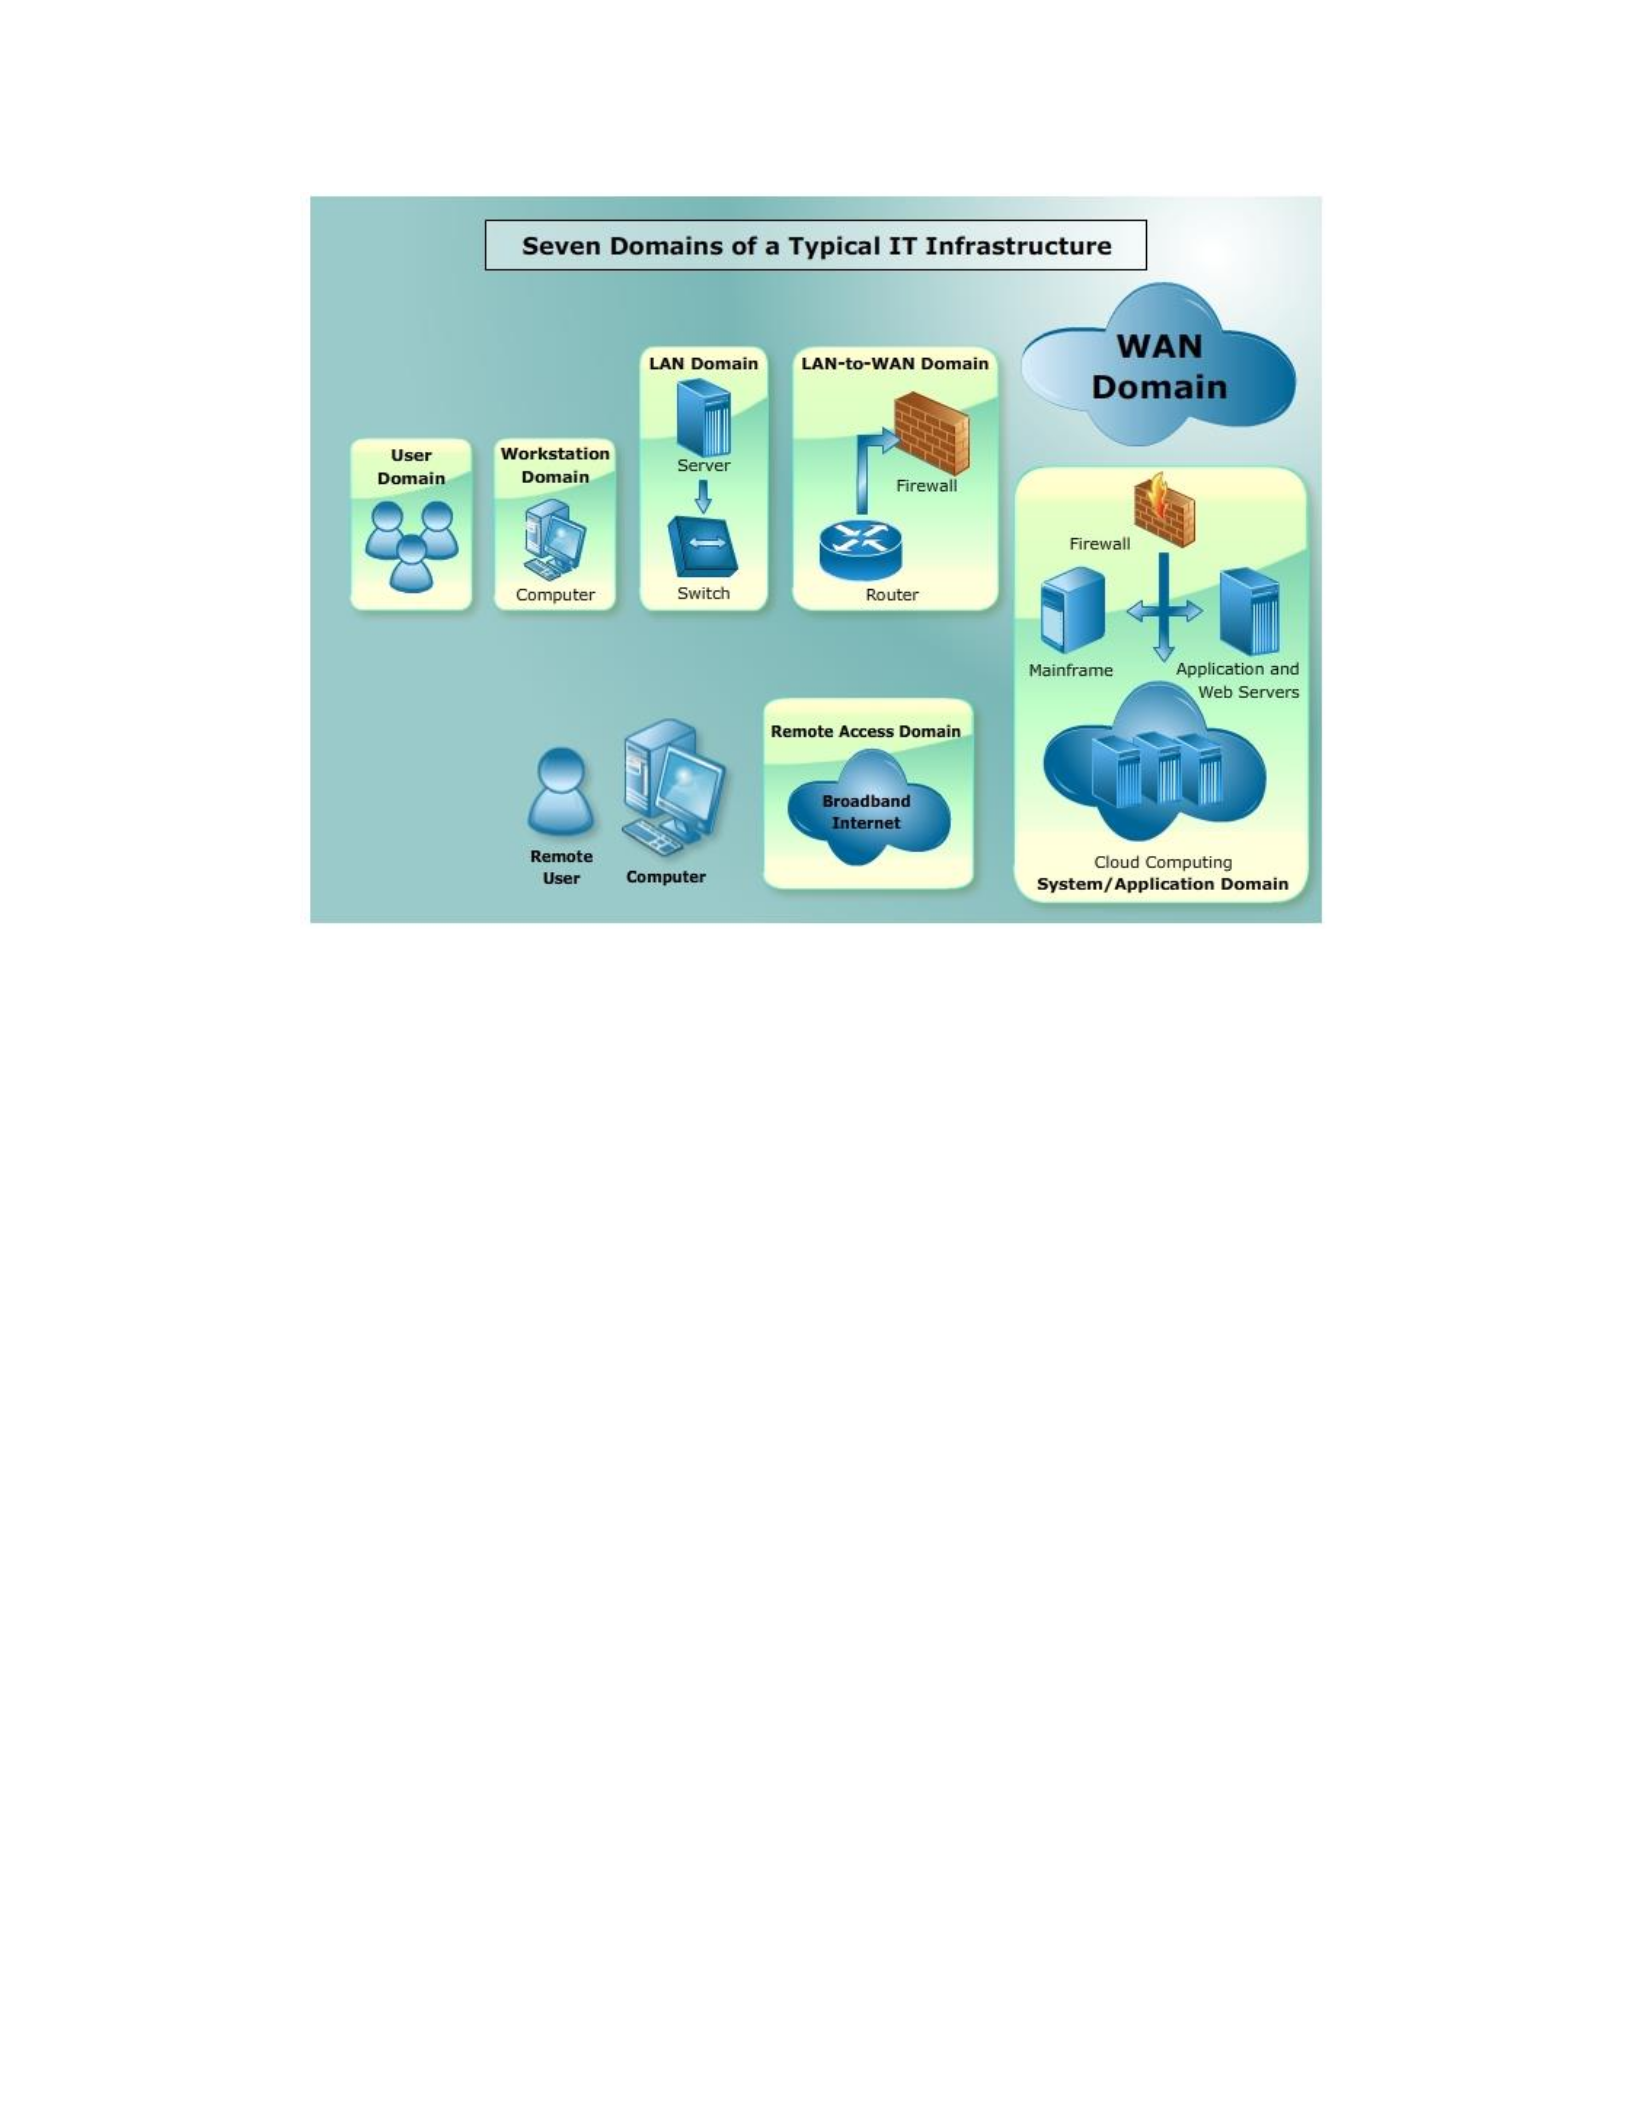
- Seven major areas of risk in IT infrastructure
From: Jones and Bartlett Learning, TOPIC 1.
Q: What are the major areas of risk in IT infrastructure? See Image below.
A: The seven domains of the typical IT infrastructure are the major areas of risk.
1. USER: The user domain risk areas include user names, passwords, biometric or other
authentication, and social engineering.
2. WORKSTATION: In the workstation domain, the risk areas include end user systems,
laptops, desktops, and cells phones. The “desktop domain” where most users enter the IT
infrastructure
3. LAN: In the local area network (LAN) domain, the risk areas include the equipment required
to create an internal LAN, such as hubs, switches, and media. Small network organized by
function or department, allowing access to all resources on the LANs.
4. LAN-to-WAN: The risk areas in the LAN-to-wide area network (WAN) domain include the
transition area between the LAN and the WAN, including the router and the firewall. The point
at which the IT infrastructure joins a WAN and the Internet
5. WAN: The WAN domain risk areas include the routers and circuits connecting the WAN. The
point at which the WAN connects to other WANs via the Internet
6. APPLICATION: In the system, or application, domain, the risk areas include the applications
you run on your network, such as e-mail, database, and Web applications. Holds all of the
mission-critical systems, applications, and data
7. REMOTE ACCESS: The risk areas in the remote access domain include applications, such as
a virtual private network (VPN) to guide remote or travelling users. Connects remote employees
and partners to the IT infrastructure
9
Seven major areas of risk in IT infrastructure

