


SNHU
ISE 510 Security Risk Analysis & Plan
Week 6 HW
Create an CIRT Response Plan for a Typical IT infrastructure
Same as “LAB Manual Create a CIRT Response Plan for a Typical IT Infrastructure”
30 points
Delapaz,Carlos
Due September 22,2019
Submitted on September 22,2019
If late let me know why:
1
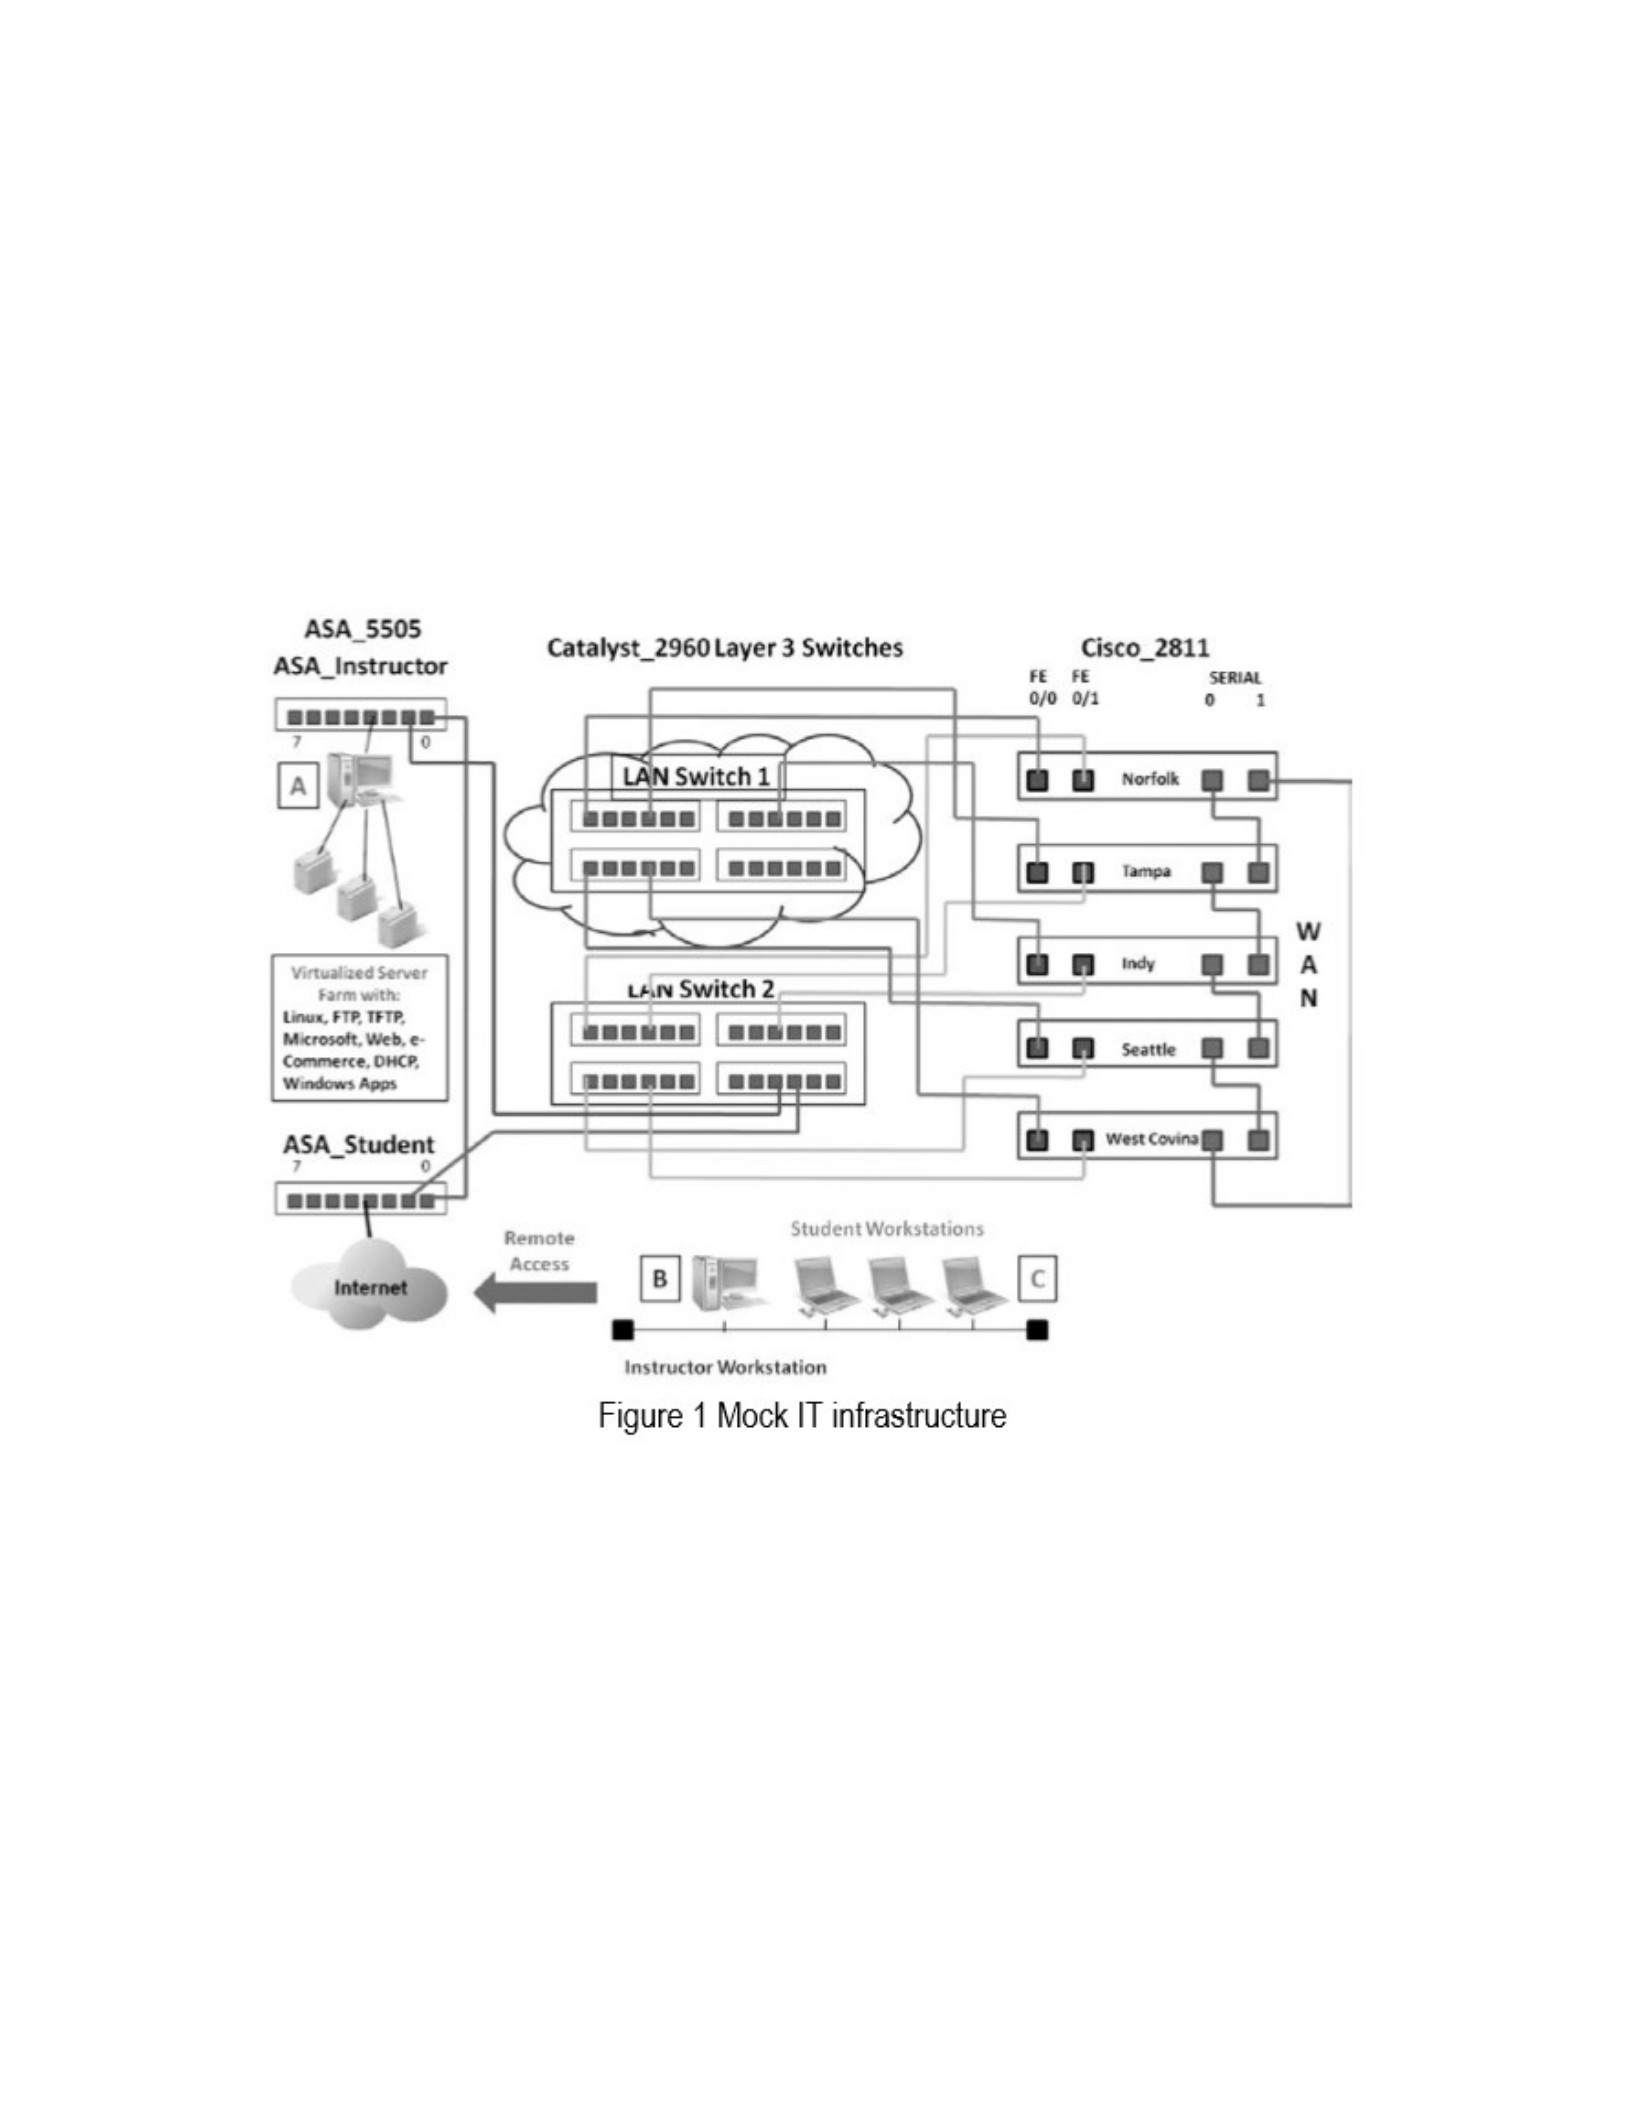
The figure below is a Mock IT infrastructure of “ASA Schools online” where they
provide learning content to remote students that sign-up over the Internet. The
student workstations can be anywhere in the world, but mostly they are from the
US. You don’t have to be a CISCO Architecture to do this assignment. The point
here that each of the 7-Domains are present (user, workstation, LAN, WAN-to-
WAN, WAN, application, and remote access). These are shown in Appendix.
Figure 1: Mock IT Infrastructure - Copied from JBL LAB Manual
2

PART I
1. Build a CIRT Plan
a. Purpose
CIRT refers to a computer incident response team that consists of a group involved in the
handling of events of threats related to security breaches of the computer. The purpose of the
CRT plan is to help the different organizations in the identification of probable computer
incidents and in preparation for dealing with the same. The plan will include all computer
incident related policies and the ways of handling them effectively. The CIRT will enable the
creation of a link with the Disaster Recovery Plan (DRP) (Cichonski et al., 2013). The
implementation of the CIRT plan will assist you in applying your critical thinking to the
potential problems related to computer incidents.:
b. Roles and Responsibilities of the CIRT Plan.
A key requisite of the CIRT is a team having a group of people with diverse skill sets from
different areas of the organization for ensuring an optimum balance of skills. This enables the
fulfillment of the multiple roles in an organization by the team members.:
The different roles that need to be filled up by the CIRT members include::
Human Resource
Team Leader
Communication
Information Security Members
Physical Security
Network Administrators
Legal:
The member of CIRT needs to take charge of the different responsibilities for the successful
development of the plan. The different responsibilities of the CIRT plan are:
Conduct inquiry of the incident
Find out the potential cause of the incidents
Develop effective procedures for incident response
3

Secure the collected evidence
Employ the Chain of custody
Suggest ways or control measures to prevent incidents in future
c. Proposed CIRT Plan:
1) Preparation
The preparation phase involves the designing of the CIRT plan where the computer incidents
will be defined and the plan will be created. The team members of CIRT are assigned particular
roles and responsibilities and are provided with appropriate training to enable them to execute
their part effectively and efficiently (Cichonski et al., 2013). The employees associated with the
CIRT plan are well prepared to help them recognize, contain, as well as mitigate the arising
incidents. The approval and funding of the plan are also ensured in the preparation stage of the
CIRT plan. The use of methods like drill can be helpful in the evaluation of the effectiveness of
the plan. (Davis Ellis)
2) Identification
The identification phase of the CIRT plan is also referred to as the detection and analysis phase.
This phase includes the use of different controls for the detection of probable incidents. The
phase evaluates the events to find out whether the actual events are false or false positive. The
identification phase involves the application of AV software and intrusion detection systems
(IDS).
The important questions that need to be raised by the CIRT group members in this phase are:
When did the actual event take place?
How was the event located?
By whom was it discovered?
What are the different areas that are impacted by the event?
What are the potential scopes of the event?
How will the event affect the different operations of the organization?
Has the team been successful in discovering the point of entry of the incident? (Davis
Ellis)
3) Containment
4

After the detection and analysis phase of the CIRT plan, the next phase is containment where the
detected incident is contained. This phase includes the removal of the threat causing devices
from the internet and network connections of the organization. It also includes the updating of
the systems and restoration of the organizational operations with the help of effective back-up
systems. The credentials related to the administration and user access are changed. The
containment of the incident helps in ensuring that the spreading of the threat is stopped, thus
eliminating the chances of more damage to the organization. In this stage, the CIRT members
also review the current policies, passwords, and remote access protocols for ensuring enhanced
authentication.:
The questions to be raised by the CIRT in this phase are:
What has been done by the team for the containment of incidents in the short-term and
long term?
Has any of the discovered malware been detached from the other networks?
What are the effective backup systems in the current scenario?
Does the remote access necessitate true multi-factor authentication?
Have the team hardened, reviewed, and changed the access credentials?::
Has the team been successful in implementing the recent patches and updates? (Davis
Ellis)
4) Eradication
The detection of the incident leads to its eradication. In the eradication phase, it is important to
cross-check that all the traces of malware have been removed to ensure the optimum security of
the systems of the organization (Gibson, 2014). The process of detection and removal continuous
until all the malicious elements are cleaned.:
The potential questions to be answered during this phase are:
Has the CIRT group been successful in removing all the malware securely?
Has all the patches and updates been applied?
Is the re-imaging of the system possible? (Davis Ellis)
5) Recovery
The recovery phase involves the process of getting back the devices and systems of the
organization to their operational condition. It includes the restoration of the functioning of the
affected systems and eliminating the occurrence of another incident.:
5

The questions that should trigger in this phase are:
When is it possible to return the devices and systems to their original environment?
What are the possible ways of testing, hardening, and patching the systems?
Is it possible to trust and restore the system through a backup?
What effective tools can be used to avoid a particular incident in the future? (Davis Ellis)
6) Lessons Learned
After the recovery process, an after-review meeting is held to determine the lessons learned. This
phase aims to find out the effective response for the incidents and the possible ways for
improvement. The lessons learned can help in the enhancement of the CIRT plan that can be
documented for future use.:
The questions to be answered during this phase are:
What changes can be made to ensure enhanced security?
What are the possible ways of training employees differently?
What were the weaknesses of the organization that led to the incident?
What are the ways of ensuring that the same incident does not get repeated in the future?
(Davis Ellis)
d. The Incident Response Process
The incident response process begins immediately after the occurrence of an incidence. It starts
with the preparation phase where the security policies are identified, establishes and recovered.
The employees are prepared through proper training and the available tools are effectively used.
Then comes the Identification phase where the actual incident is identified. It involves the
assessment of the affected systems for malicious activities. The Containment phase includes the
containment of the incident. It involves restricting the incident from spreading more and causing
further damage to the organization. The Investigation phase includes the determination of the
ways how and when the incident happened. In this process, all the policies and processes are
reviewed as well as documented properly. The Eradication phase includes the elimination or
cleaning up of the malicious software from the network and systems. The Recovery phase
restores the original functioning of the systems. The Follow-Up phase involves a discussion
regarding the changes to be made in the entire process and implementation as well as
documentation of the same.
6

PART II Answer these questions about CIRT Plans
1. How might ASA Schools know if they were being attacked over the network or
Internet?
The possible ways of knowing about the attack are:
1. Unwanted Toolbars: The emergence of toolbars on the browsers that you do not know is
a potent symbol of attack.:
2. Frequent pop-ups are another signal that must not be ignored.
3. Ransom Message: This is a kind of malware that restricts your access to some data and
demand payment for its access. On rebooting, the malware goes away. It can be restored
by making the payment of the ransom or with a backup system.:
4. Redirection: Getting continuously redirected to another website during your internet
searches is another signal of a possible attack.
5. Fake Anti-virus software messages: This message attracts users to buy the anti-virus
package and extracts their credit card information.:
6. Unexpected Software Installations: In addition to desired software, another software may
be installed without your knowledge.:
7. Disablement of Antimalware, registry editor, and task manager is a symbol or potential
attack.:
8. The DDoS attack that prevents the effective functioning of services is a common attack
for schools.:
9. Using the right online password yet seeing the account not working is an attack signal.
Automatic moving of mouse and making selections is another attack symbol
2. Inappropriate usage incidents occur when users violate internal policies. Give
two examples of this from our textbook (and page number):
The two examples are:
the copying of the proprietary data of a secured system to access an insecure system
Visiting a malicious website which is already identified as off-limits (Gibson, p. 402).
3. One of the important steps when handling an incident is to identify the impact
and priority of the incident. How does Gibson (2004) address that?
7

The rating system can be implemented through the use of a numerical value. The effect rating
definitions stated in Table 15-1 will assist in figuring out the rating and the table will help in
finding the critical level of the attack.:
The formula to be used is::
(Current Effect Rating x.25) + (Projected Effect Rating x.25) + (Criticality Rating x.50):
10 x .25 + .50 x .25 + .50 + .50
2.5 + 12.5 + 25
Incident Impact Score = 40
This will be helpful for rating the incident’s impact. The score will range from 0-100. The
minimal value is 0 and critical value is 100.:
8

References
Cichonski, P., Millar, T., Grance, T., & Scarfone, K. (2013). Computer Security Incident
Handling Guide.:International Journal of Computer Research,:20(4), 459.
Gibson, D. (2014).:Managing risk in information systems. Jones & Bartlett Publishers.
Appendix - Seven major areas of risk in IT infrastructure
9

From: Jones and Bartlett Learning, TOPIC 1.
Here are the seven major areas of risk in IT infrastructure: (See Image below).
1. USER: The user domain risk areas include user names, passwords, biometric or other
authentication, and social engineering.
2. WORKSTATION: In the workstation domain, the risk areas include end user systems,
laptops, desktops, and cells phones. The “desktop domain” where most users enter the IT
infrastructure
3. LAN: In the local area network (LAN) domain, the risk areas include the equipment required
to create an internal LAN, such as hubs, switches, and media. Small network organized by
function or department, allowing access to all resources on the LANs.
4. LAN-to-WAN: The risk areas in the LAN-to-wide area network (WAN) domain include the
transition area between the LAN and the WAN, including the router and the firewall. The point
at which the IT infrastructure joins a WAN and the Internet
5. WAN: The WAN domain risk areas include the routers and circuits connecting the WAN. The
point at which the WAN connects to other WANs via the Internet
6. APPLICATION: In the system, or application, domain, the risk areas include the applications
you run on your network, such as e-mail, database, and Web applications. Holds all of the
mission-critical systems, applications, and data
7. REMOTE ACCESS: The risk areas in the remote access domain include applications, such as
a virtual private network (VPN) to guide remote or travelling users. Connects remote employees
and partners to the IT infrastructure
10
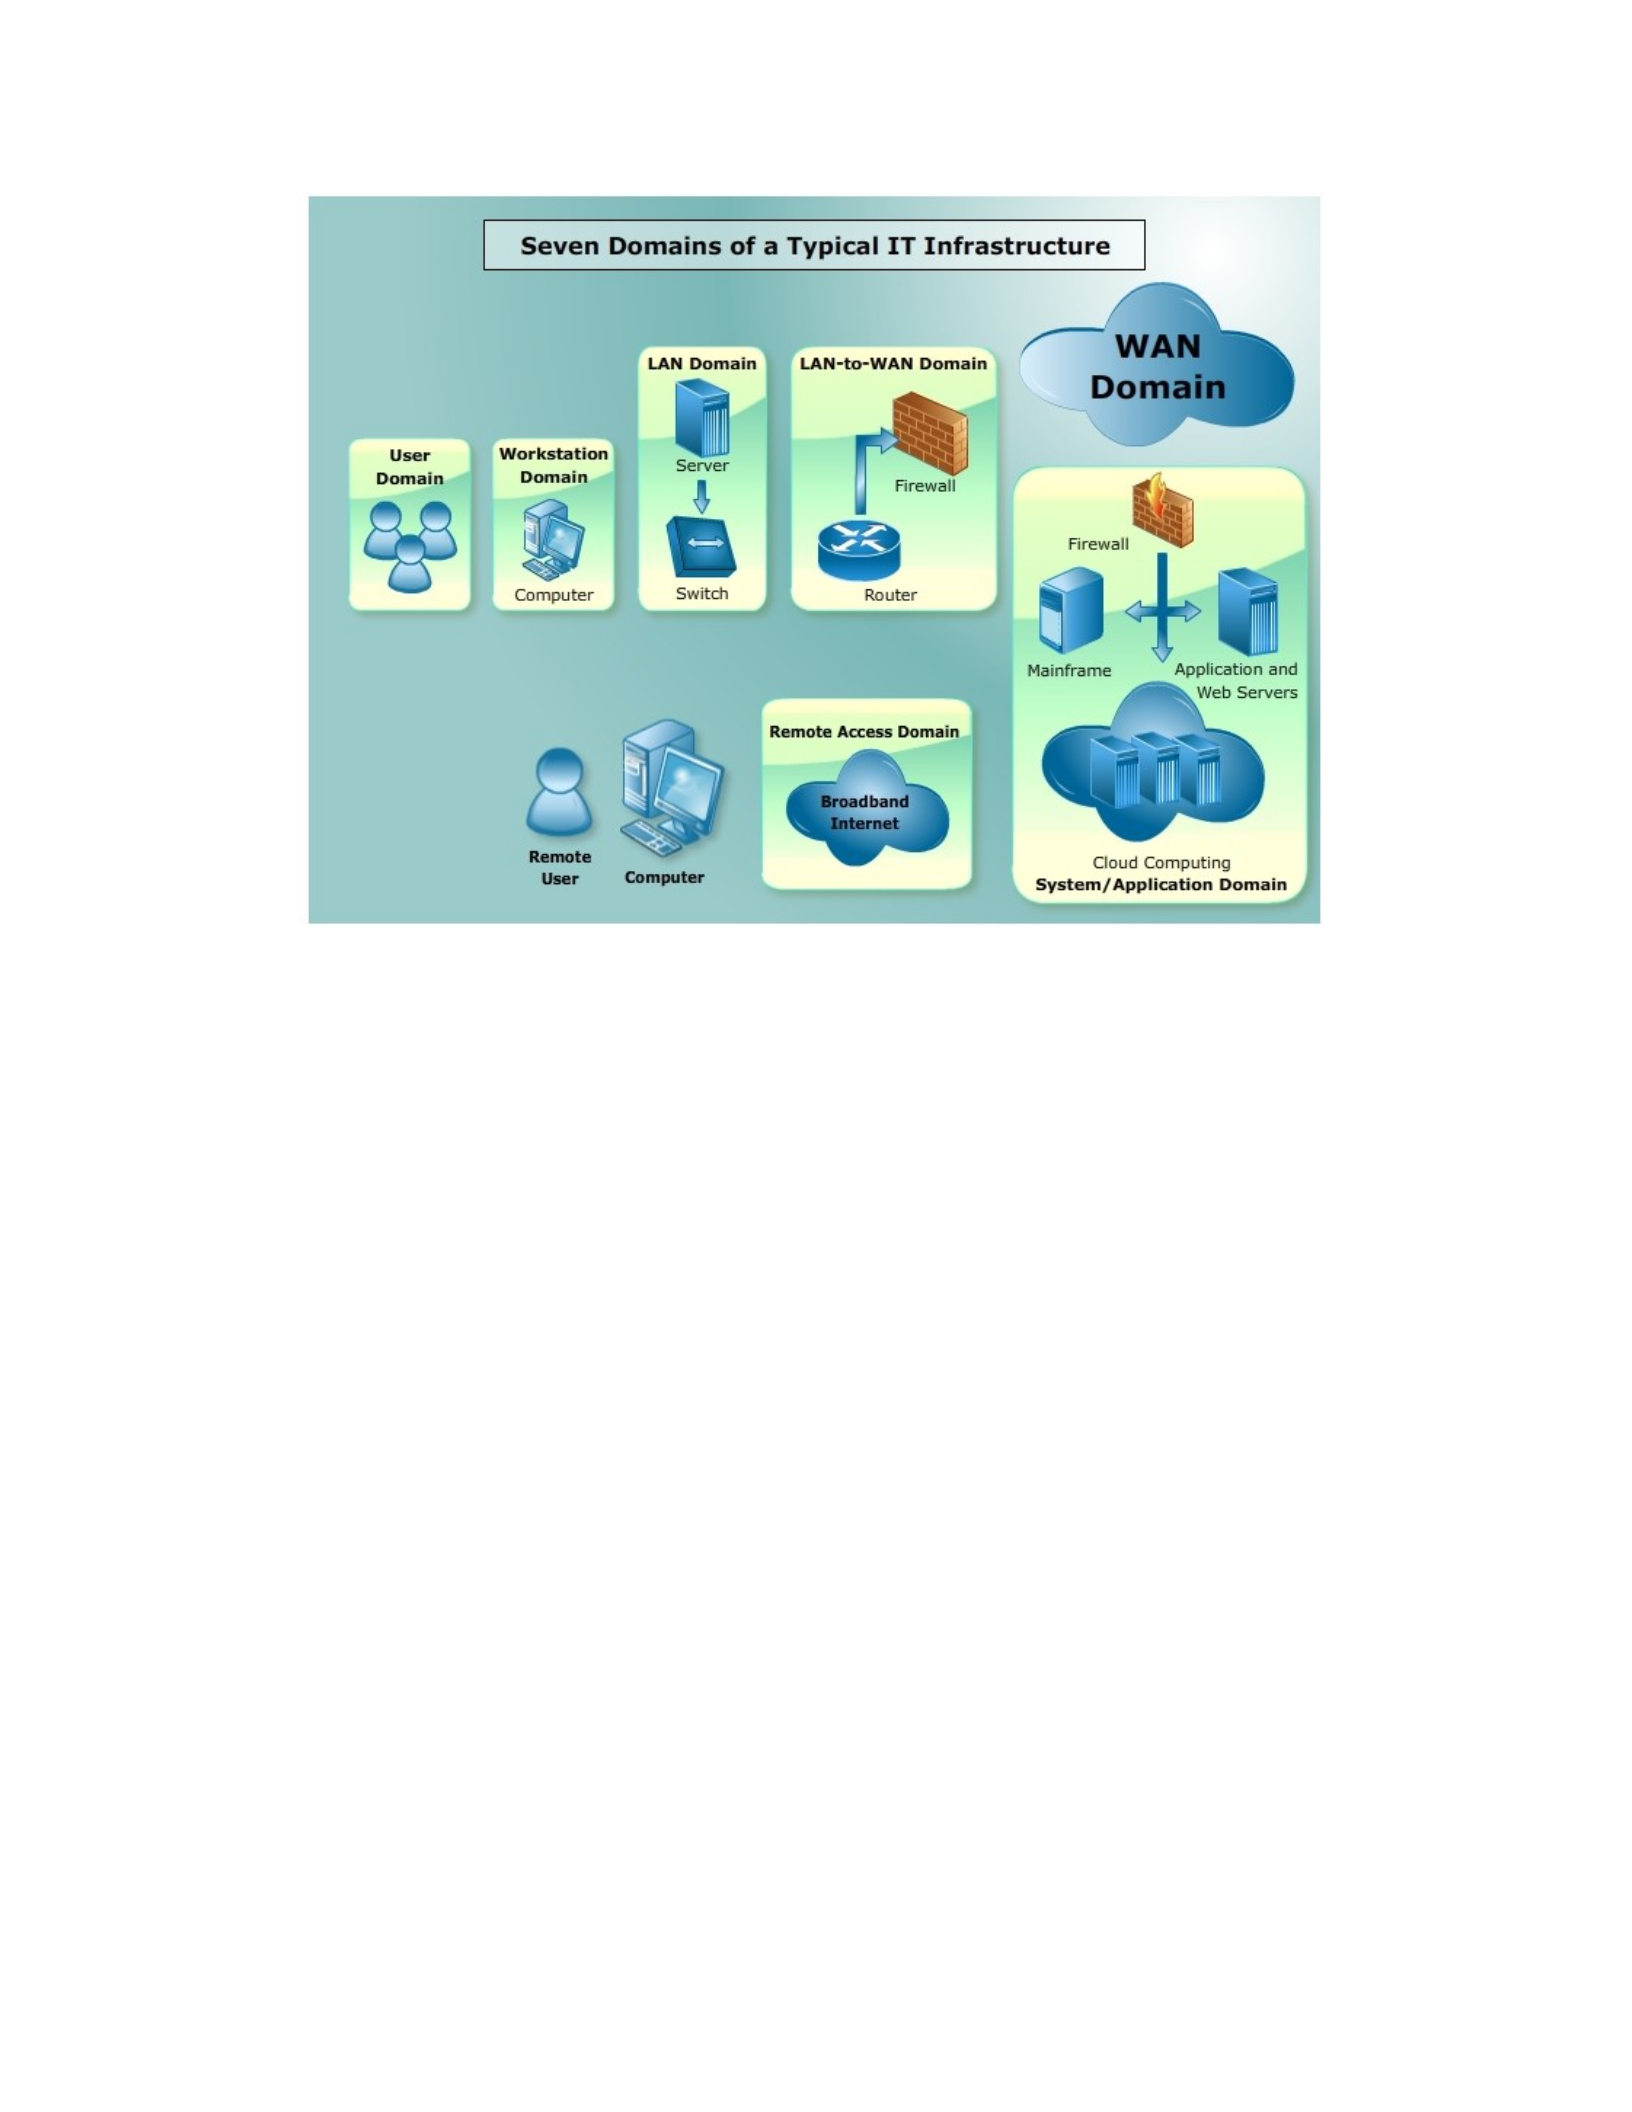
Seven major areas of risk in IT infrastructure
11

