


IT Infrastructure
Designing Lan networks Assignment
School of Business Administration, Liberty University
BMIS 520: IT Infrastructure (B02)
Honesty Statement Instructions
Completed by Hoang Le on <Feb 18, 2024>
IT Infrastructure 1
Honesty Statement
I, Hoang Le, did not copy any of the following writing or designs or configurations or code from
any source. I did not use any automated tools, artificial intelligence, or person to assist in any
way in completing this work. All writing, design work, configurations, and code is 100% my
own, original, and created solely for this class. Less than 5% of this work contains direct quotes
or paraphrases. I agree to receive an academic violation if TurnItIn and/or SafeAssign matches
exist of over 10% or I have copied existing Packet Tracer solutions in any form from any person
or source.
Packet Tracer Version
IT Infrastructure 2
Part 1: Network design
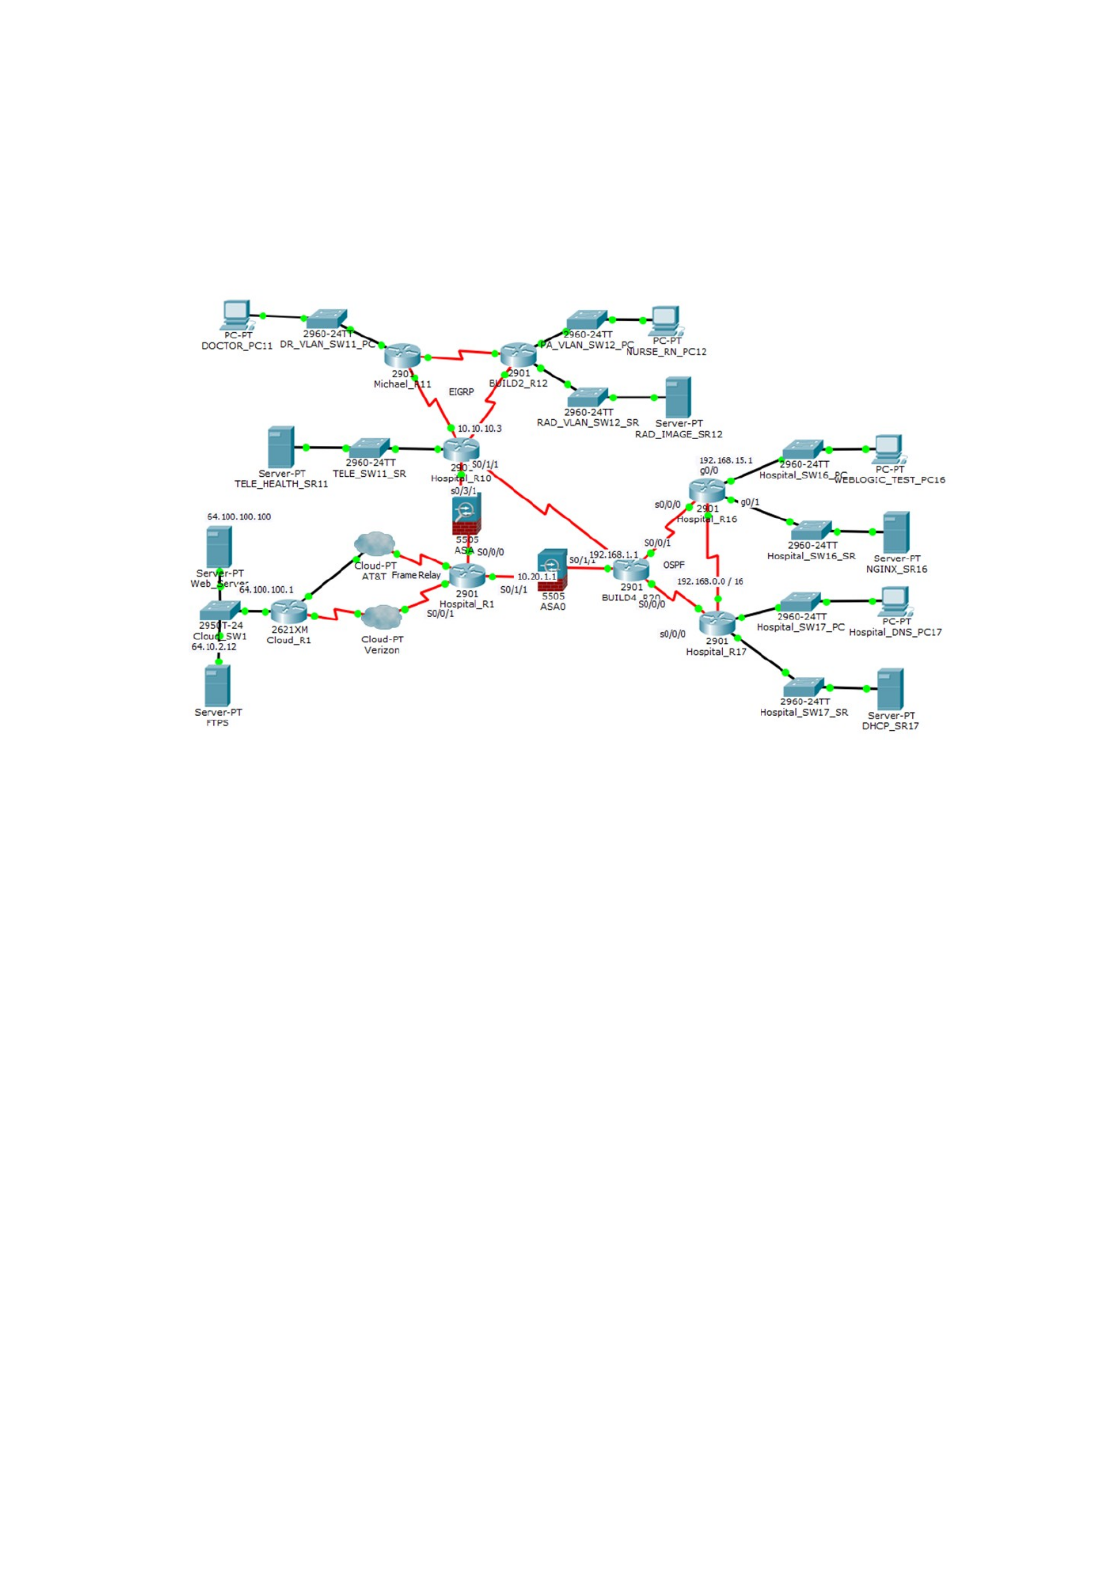
Original LAN Network
Recommendation:
As the current network, the weakness is as below.
Routing: The current routing configuration is suboptimal, with a single router (R16) connecting
the two campuses to the Internet. This creates a single point of failure and can lead to
performance bottlenecks. A more robust routing configuration would involve using two routers,
each with its own connection to the Internet. This would provide redundancy and improve
performance.
Security: The current security configuration is also suboptimal. The ASA firewall is only located
at the edge of the network, leaving the internal networks vulnerable to attack. A more secure

IT Infrastructure 3
configuration would involve placing firewalls at multiple points throughout the network,
including between the two campuses. This would create a more layered security posture.
VLANs: The current network is not using VLANs. VLANs can be used to segment the network
into different logical groups, which can improve security and performance. For example, the
network could be segmented into separate VLANs for different departments or types of traffic.
Some specific recommendations for improving the two campus LANs
Routing: Add a second router to the network and connect it to the Internet. Configure the router
to use a routing protocol such as RIPv2, OSPF or EIGRP to exchange routing information. This
will create a more robust and reliable routing configuration.
Security: Add firewalls to the network between the two campuses and between the campuses and
the Internet. Configure the firewalls to allow only necessary traffic to pass through. This will
improve the security of the internal networks.
VLANs: Implement VLANs to segment the network into different logical groups. For example,
you could create separate VLANs for the administration department, the nursing department, and
the patient care department. This would improve security and performance.
In addition to the above recommendations, you may also want to consider the following:
Upgrading the network infrastructure: The network switches and routers are relatively old.
Upgrading to newer equipment can improve performance and reliability.
Implementing QoS: QoS (Quality of Service) can be used to prioritize different types of traffic.
For example, you could give higher priority to voice and video traffic than to web browsing
traffic. This can improve the performance of critical applications.
Implementing network monitoring: Network monitoring tools can be used to detect and
troubleshoot network problems. This can help to improve the overall reliability of the network.
IT Infrastructure 4
By implementing these recommendations, you can significantly improve the performance,
security, and reliability of the two campus LANs.
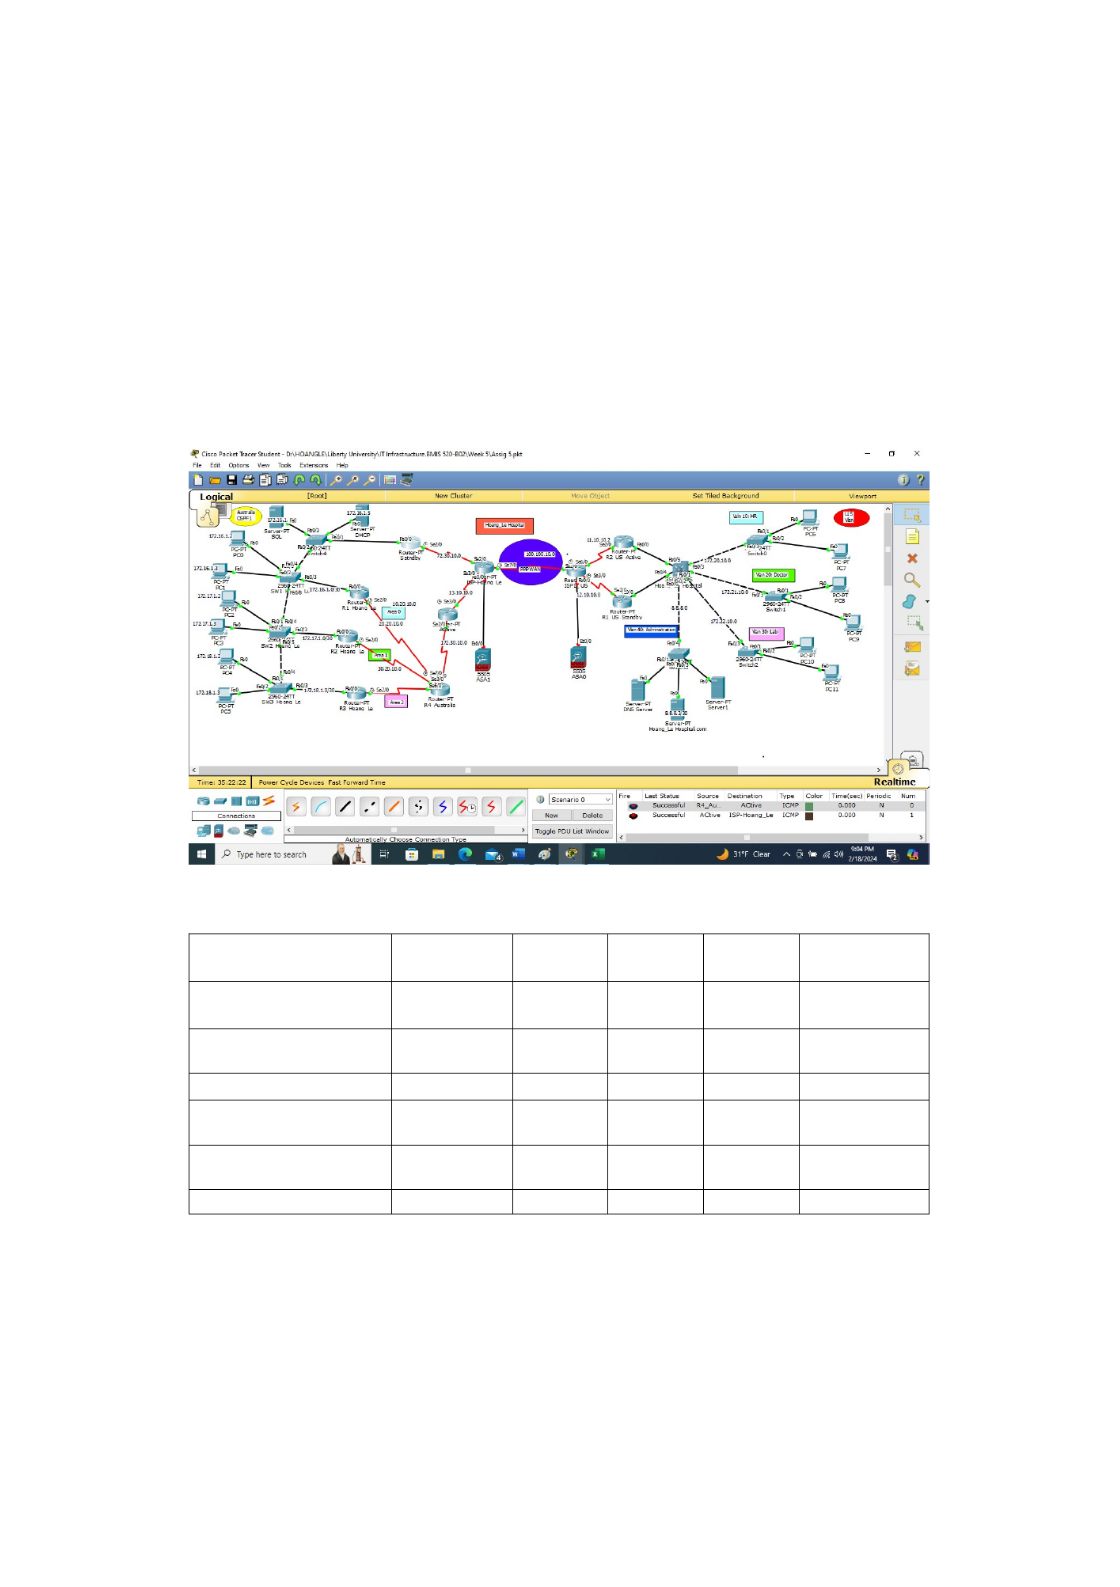
The suggested LAN Network
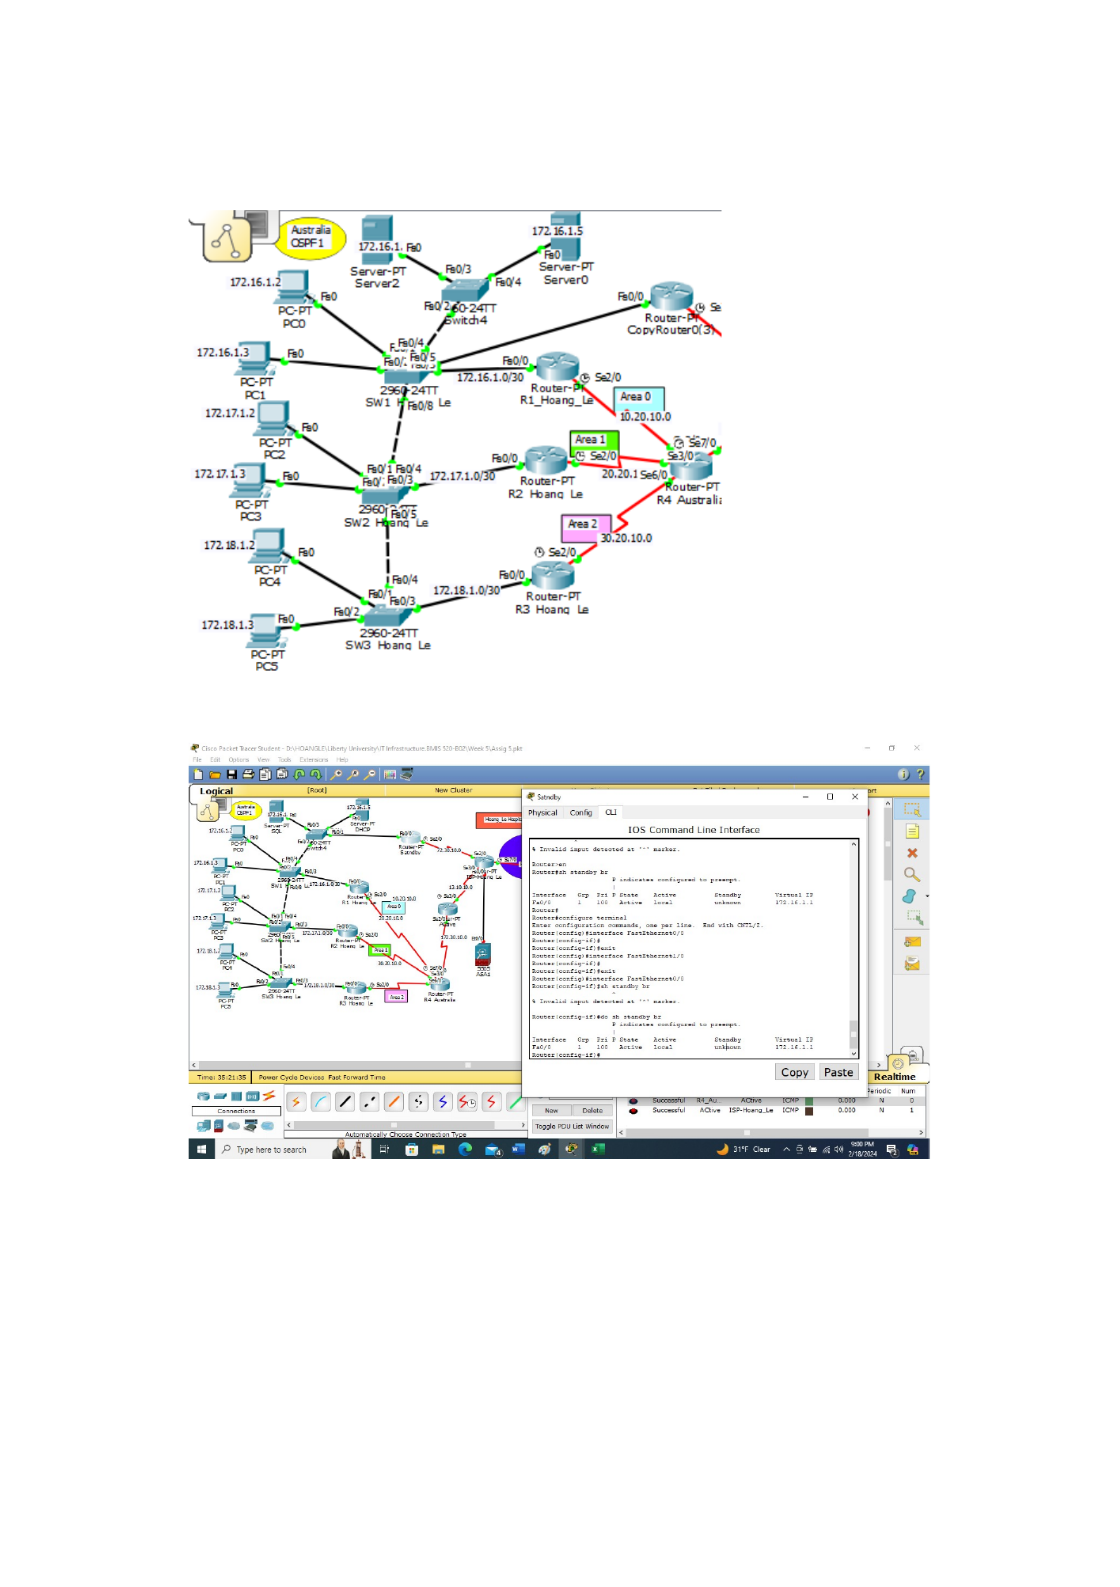
OSPF routing method will be used to configure on this LAN network for Australia area.
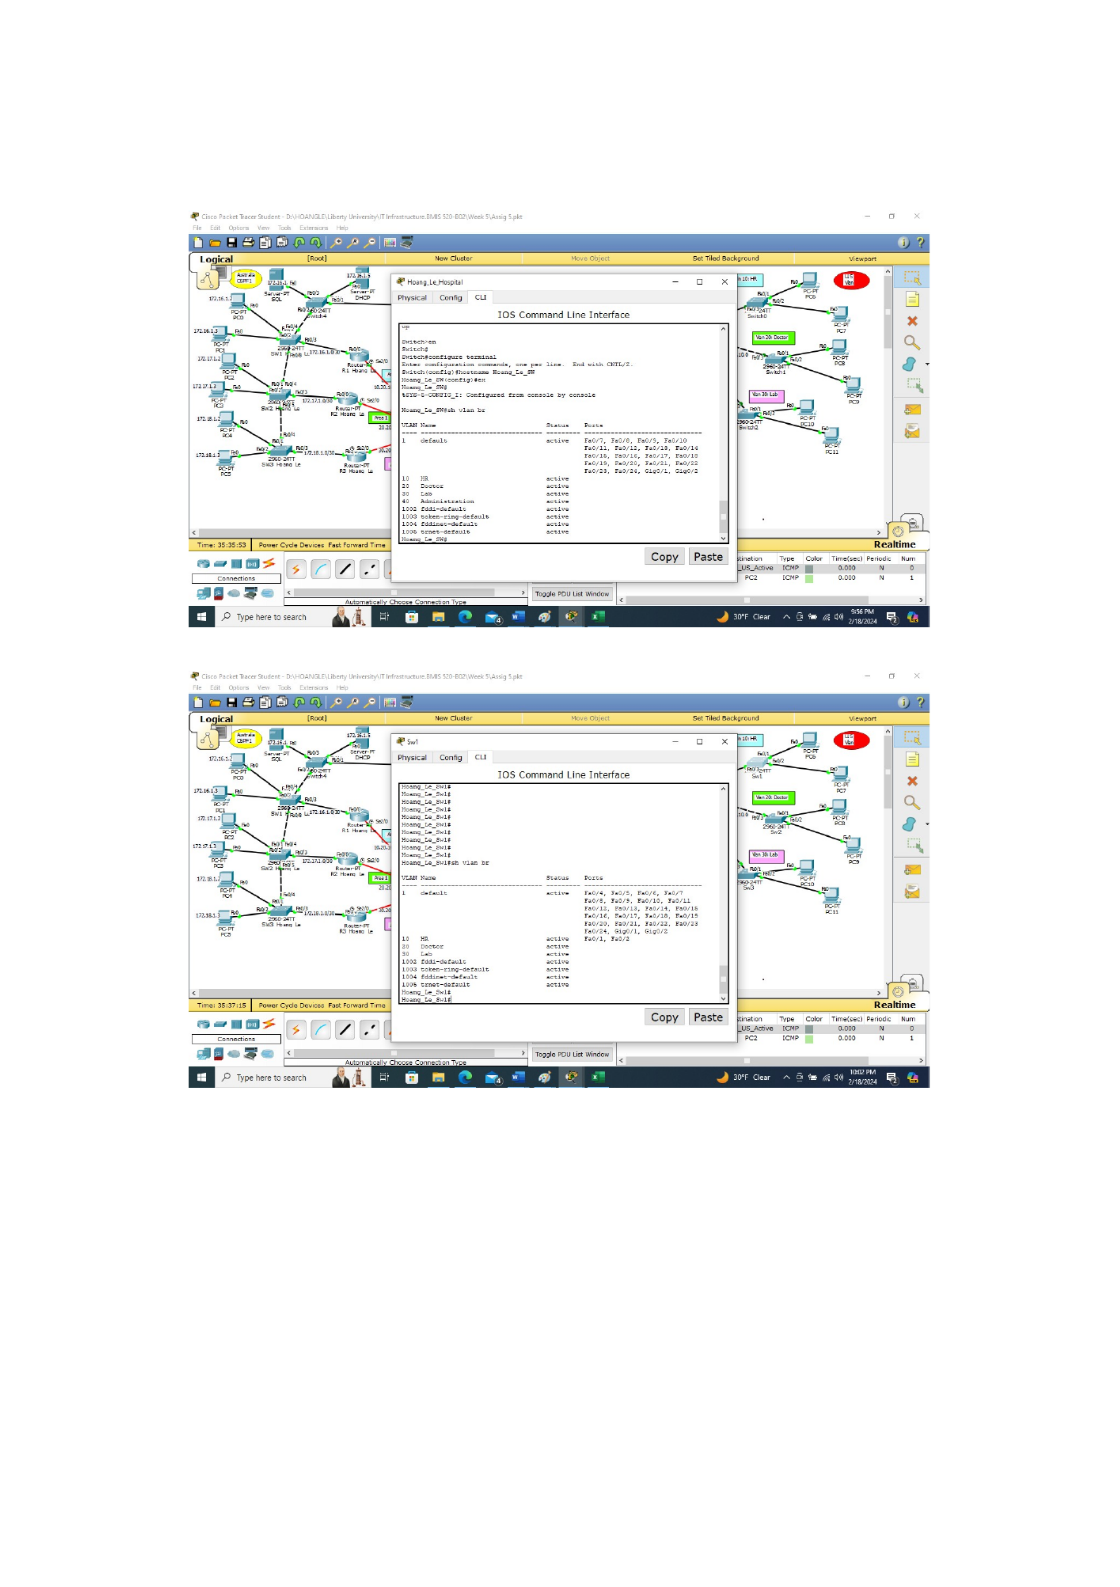
Vlans routing method will be used to configure on U.S network area.
Network topology redesign
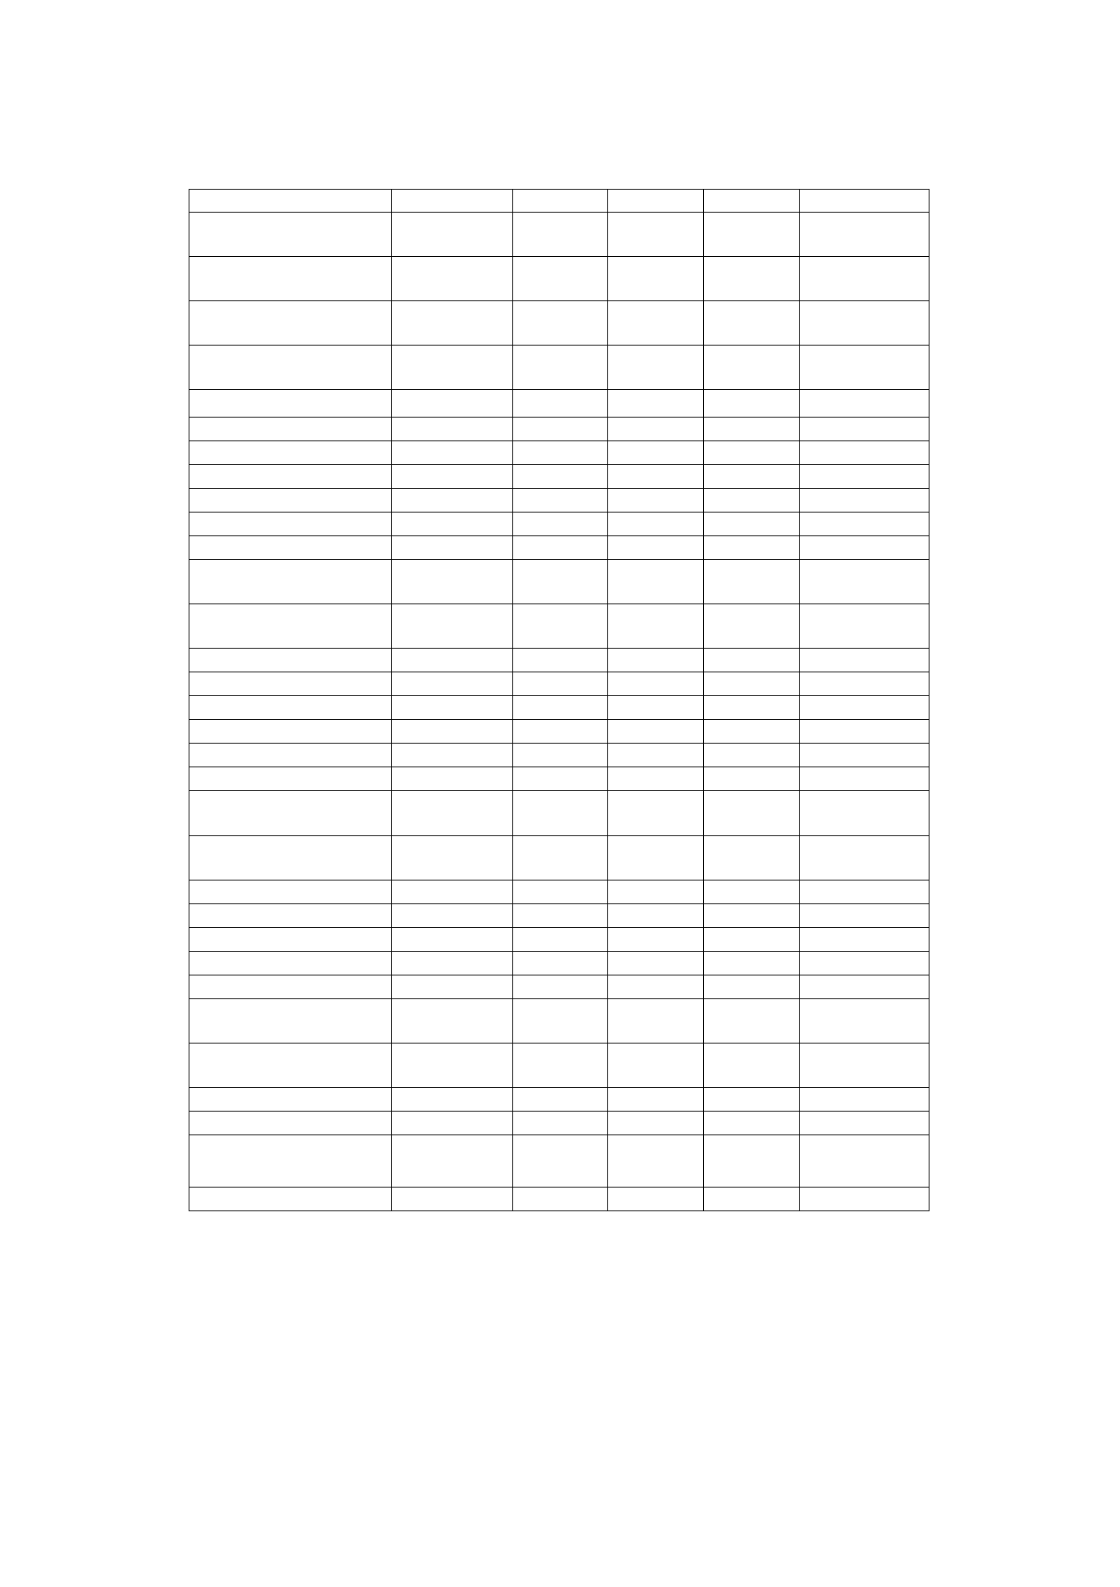
IP Address table
Device Interface IP
Adress
Subnet
Mask
Wildcard
Mask
Defaul
Gateway
Australia Network
R1 S2/0 10.20.10.
2/30
255.255.2
55.0
0.0.0.255 N/A
F1/0 0.0.0.255 N/A
F0/0 172.16.1.
1/30
255.255.2
55.0
0.0.0.255 N/A
R2 S2/0 20.20.101
2/30
255.255.2
55.0
0.0.0.255 N/A
F0/0 172.17.1. 255.255.2 0.0.0.255 N/A
IT Infrastructure 5
1/24 55.0
R3 G2/0 30.20.10.
2/30
255.255.2
55.0
0.0.0.255 N/A
F0/0 192.168.2
.1/24
255.255.2
55.0
0.0.0.255 N/A
R4 G2/0 12.10.10.
2/30
255.255.2
55.0
0.0.0.255 N/A
F0/0 172.17.1.
1/24
255.255.2
55.0
0.0.0.255 N/A
R5_Standby
SW1 Area 0 N/A N/A N/A N/A
F0/1 Trunk N/A N/A N/A
F0/2 Trunk N/A N/A N/A
F0/3 Trunk N/A N/A N/A
F0/4 Trunk N/A N/A N/A
f0/8 Trunk N/A N/A N/A
PC0 NIC 172.16.1.
2/30
255.255.2
55.0
0.0.0.255 172.16.1.1
PC1 NIC 172.16.1.
3/30
255.255.2
55.0
0.0.0.255 172.16.1.1
SW2 Area1 N/A N/A N/A N/A
F0/1 Trunk N/A N/A N/A
F0/2 Trunk N/A N/A N/A
F0/3 Trunk N/A N/A N/A
F0/4 Trunk N/A N/A N/A
F0/5 Trunk N/A N/A N/A
PC2 NIC 172.17.1.
2/30
255.255.2
55.0
0.0.0.255 172.17.1.1
PC3 NIC 172.17.1.
3/30
255.255.2
55.1
0.0.0.255 172.17.1.1
SW3 Area 2 N/A N/A N/A N/A
F0/1 Trunk N/A N/A N/A
F0/2 Trunk N/A N/A N/A
F0/3 Trunk N/A N/A N/A
F0/4 Trunk N/A N/A N/A
PC4 NIC 172.18.1.
2
255.255.2
55.0
0.0.0.255 172.18.1.1
PC5 NIC 172.18.1.
3
255.255.2
55.0
0.0.0.255 172.18.1.1
SQL server
Backup Server
U.S Network
R1 F0/0 172.20.10 255.255.2 0.0.0.255 N/A
IT Infrastructure 6
.1/30 55.0
172.21.10
.1/30
255.255.2
55.1
0.0.0.255 N/A
172.22.10
.1/30
255.255.2
55.0
0.0.0.255 N/A
R_Stanby F0/0 172.20.10
.1/30
255.255.2
55.0
0.0.0.255 N/A
172.21.10
.1/30
255.255.2
55.0
0.0.0.255 N/A
172.22.10
.1/30
255.255.2
55.0
0.0.0.255 N/A
255.255.2
55.0
0.0.0.255 N/A
Multi SW Vlan N/A N/A N/A N/A
F0/1 Trunk N/A N/A N/A
F0/2 Trunk N/A N/A N/A
F0/3 Trunk N/A N/A N/A
F0/4 Trunk N/A N/A N/A
F0/5 Trunk N/A N/A N/A
F0/6 Trunk N/A N/A N/A
SW0 Vlan 10 N/A N/A N/A N/A
F0/1 Trunk N/A N/A N/A
F0/2 Trunk N/A N/A N/A
F0/3 Trunk N/A N/A N/A
SW1 Vlan 20 N/A N/A N/A N/A
F0/1 Trunk N/A N/A N/A
F0/2 Trunk N/A N/A N/A
F0/3 Trunk N/A N/A N/A
SW2 Vlan 30 N/A N/A N/A N/A
F0/1 Trunk N/A N/A N/A
F0/2 Trunk N/A N/A N/A
F0/3 Trunk N/A N/A N/A
PC6 NIC 172.20.1.
2/30
255.255.2
55.0
0.0.0.255 172.20.1.1
PC7 NIC 172.20.1.
3/30
255.255.2
55.0
0.0.0.255 172.20.1.1
PC8 NIC 172.21.1.
3/30
255.255.2
55.0
0.0.0.255 172.21.1.1
PC9 NIC 172.21.1.
3/30
255.255.2
55.0
0.0.0.255 172.21.1.1
PC10 NIC 172.22.1.
3/30
255.255.2
55.0
0.0.0.255 172.22.1.1
PC11 NIC 172.22.1.
3/30
255.255.2
55.0
0.0.0.255 172.22.1.1
IT Infrastructure 7
DNS Server F0 8.8.8.2 255.255.2
55.0
0.0.0.255 8.8.8.1
Web server F0 8.8.8.3 255.255.2
55.0
0.0.0.255 8.8.8.1
SQL server F0 8.8.8.4 255.255.2
55.0
0.0.0.255 8.8.8.1
Part 2: Network configuration
Network configuration
The popular network routing designed for wired networks is Open Shortest Path First
(OSPF). Australia continental will be configurated with OSPF Routing. According to Almutairi
and Zhang (2024), OSPF allows the network to be divided into small areas to create a routing
hierarchy that implies the top-level routing area. The top level is the backbone area of the whole
network. It is connected to other network areas to create a routing traffic. Routing information is
exchanged through a group of nodes known as an Autonomous System (AS) (Almutairi &
Zhang, 2024). As its name Open Shortest Path, the routing will look for the shortest road to
deliver the packet to its destination and if the source and destination are in the same area, then
intra-area routing will be used. If they are positioned in different areas, then inter-area routing
will be used. In addition, to establish a neighbor relationship, “Hello” message will be
periodically sent each note on the network. The most advantageous routing of OSPF is
automatically updated whenever changes happen with the network.
The U.S continent network will be designed and routing as vlan network. Vlan routing
provides security on larger network and improves network performance by grouping together
devices that communicate frequently. It allows users accessing only the network they are
assigned as their role.
IT Infrastructure 8
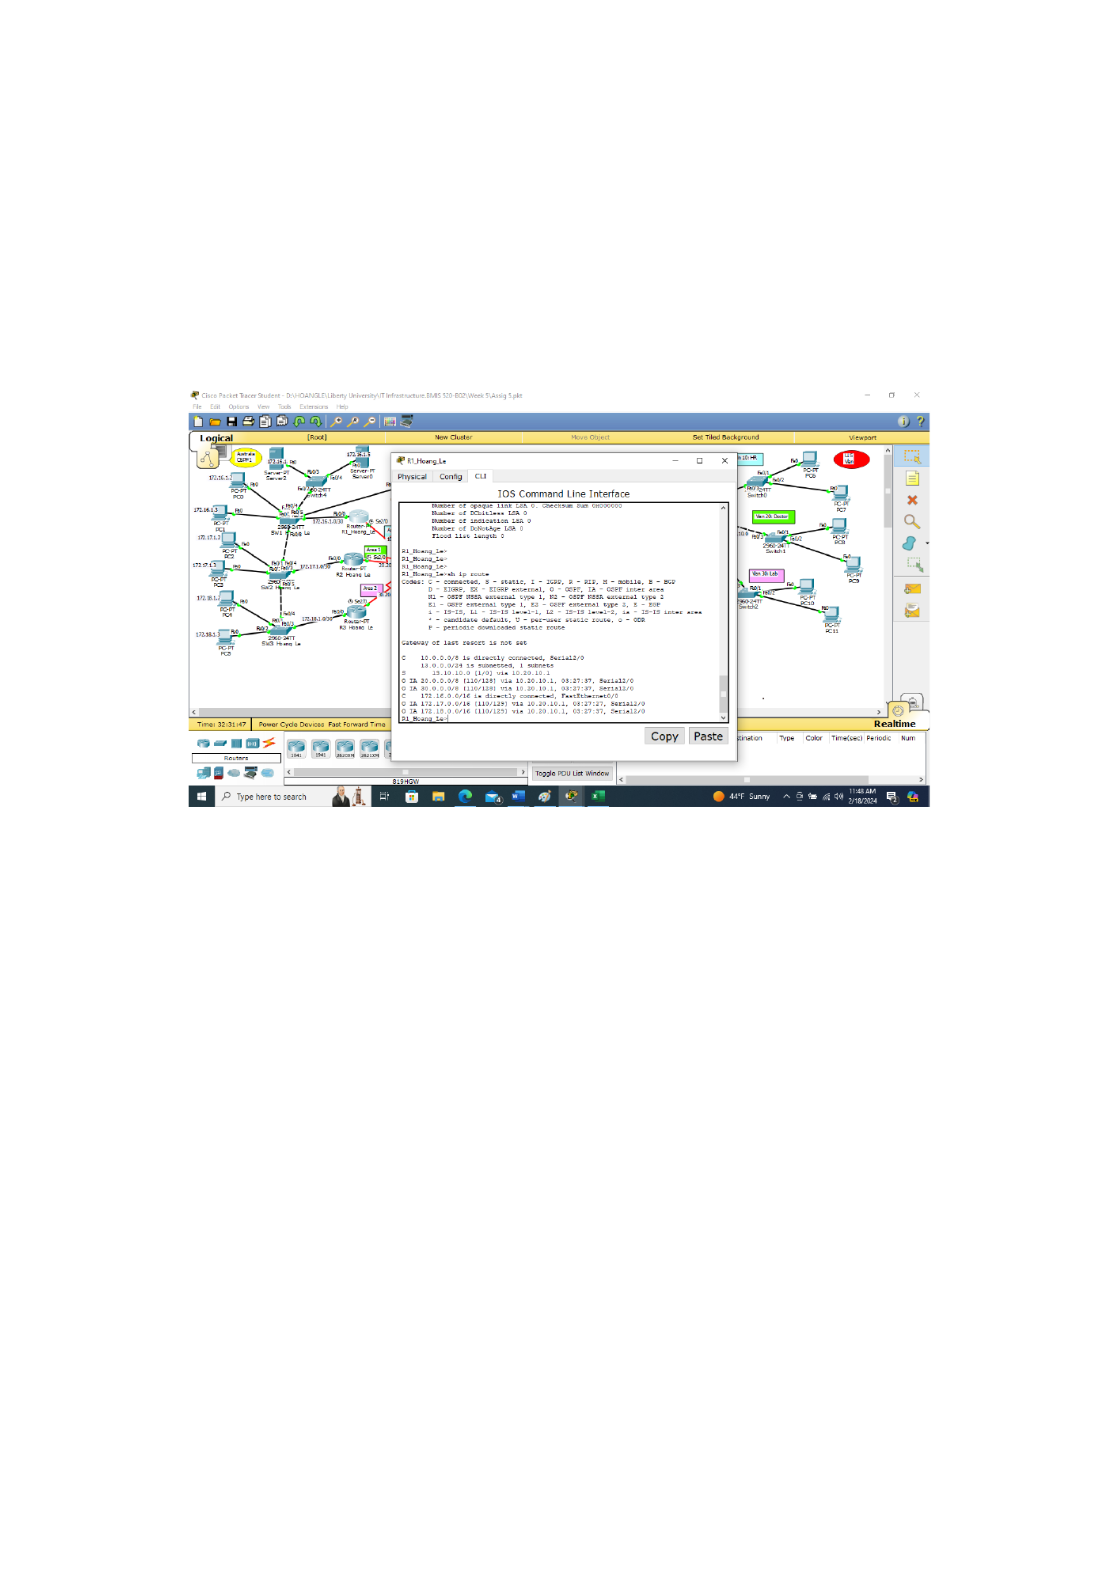
Network routing
Australia network
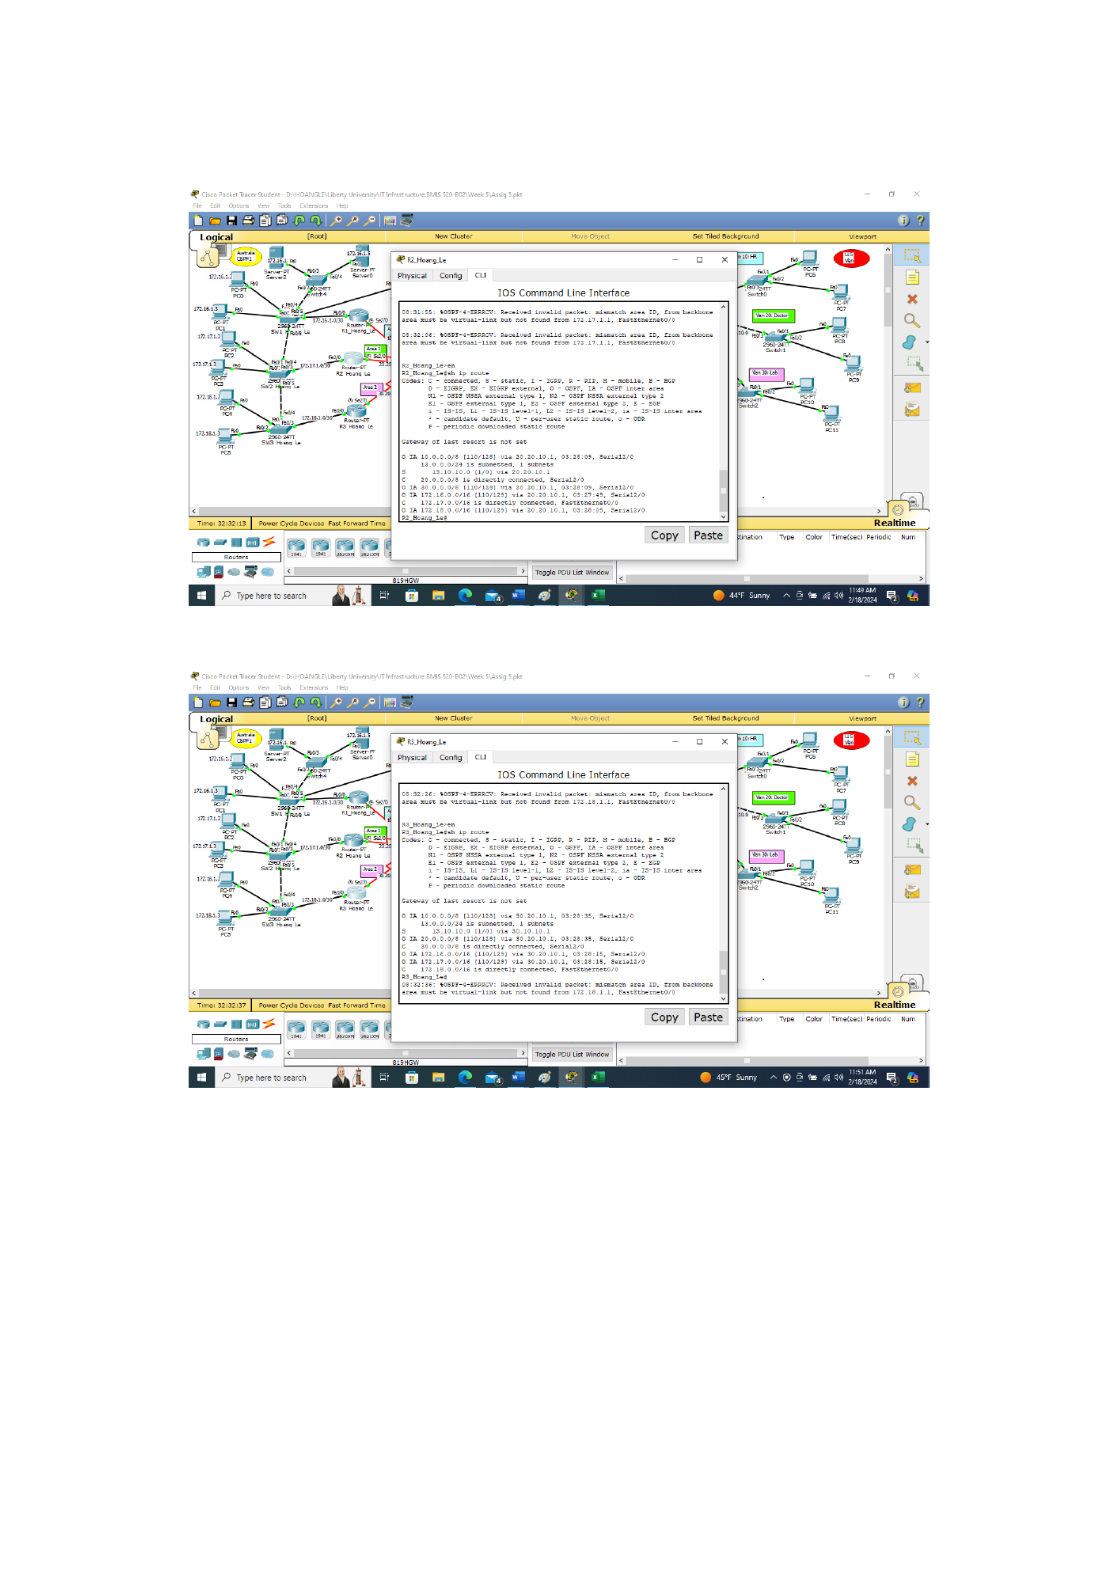
OSPF routing
R1
R2
IT Infrastructure 9
R3
IT Infrastructure 10
OSPF Areas
HSRP configure.
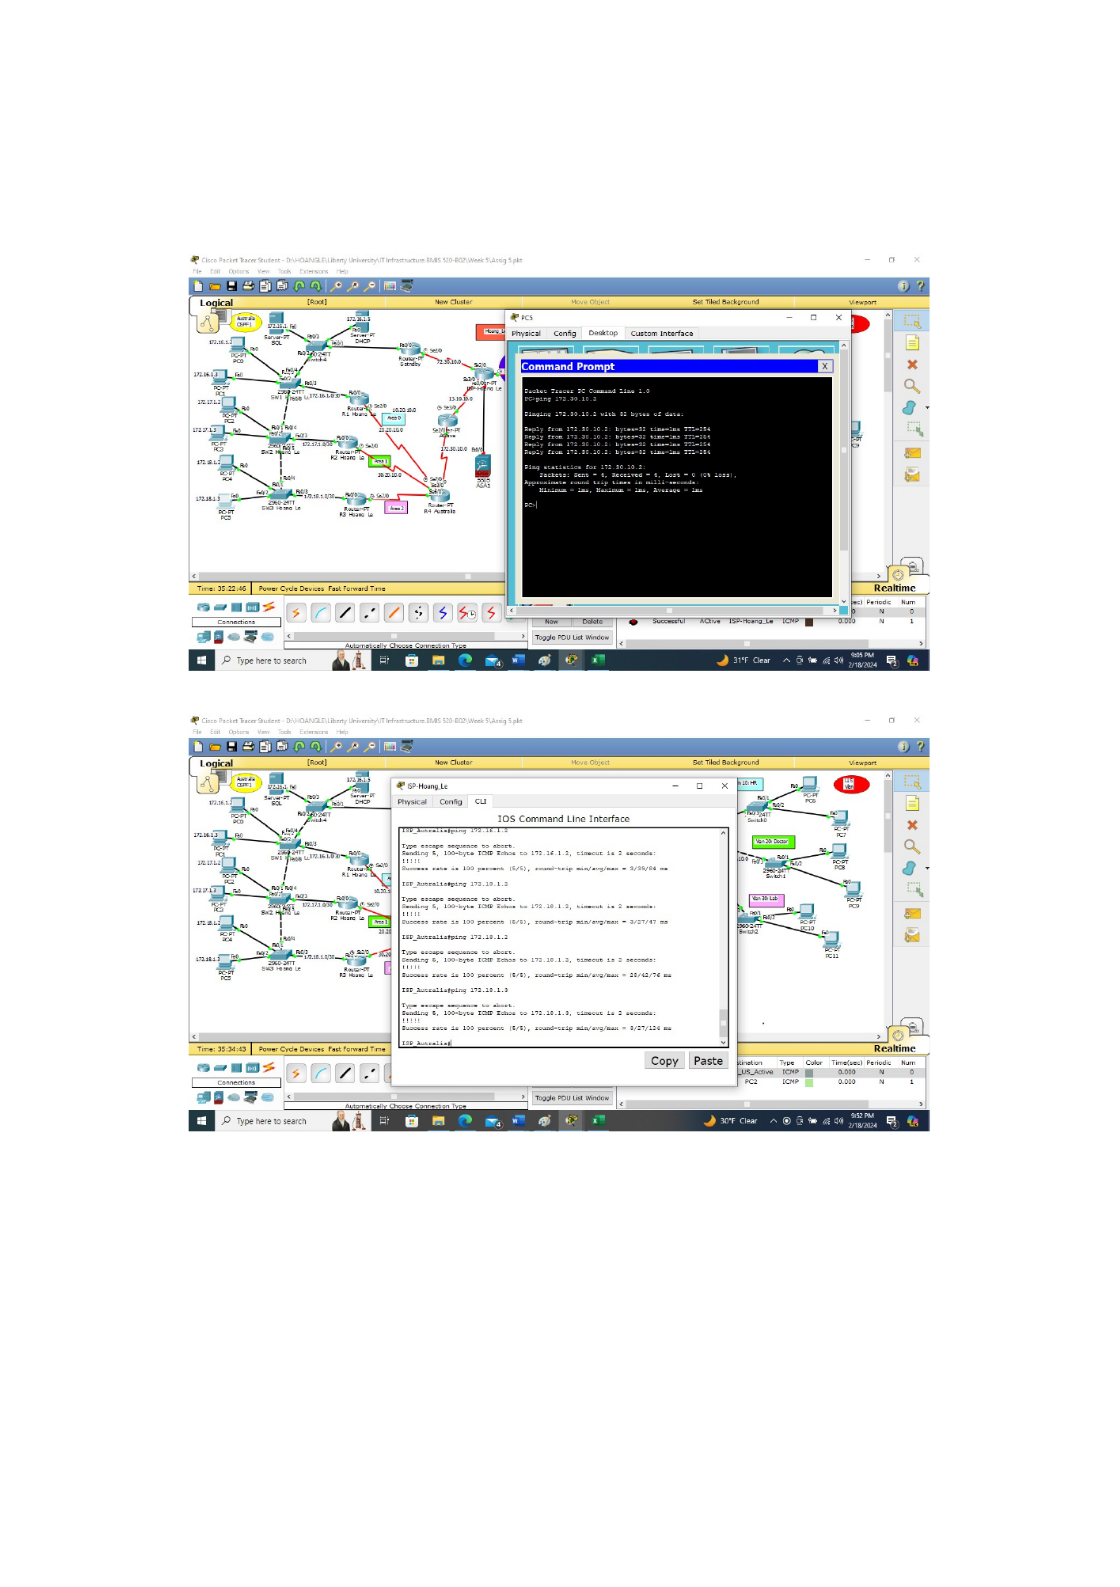
Testing and Verifying
Ping commands
IT Infrastructure 11
Ping PC5 to HSRP Active router
Ping from IPS router to OSPF network
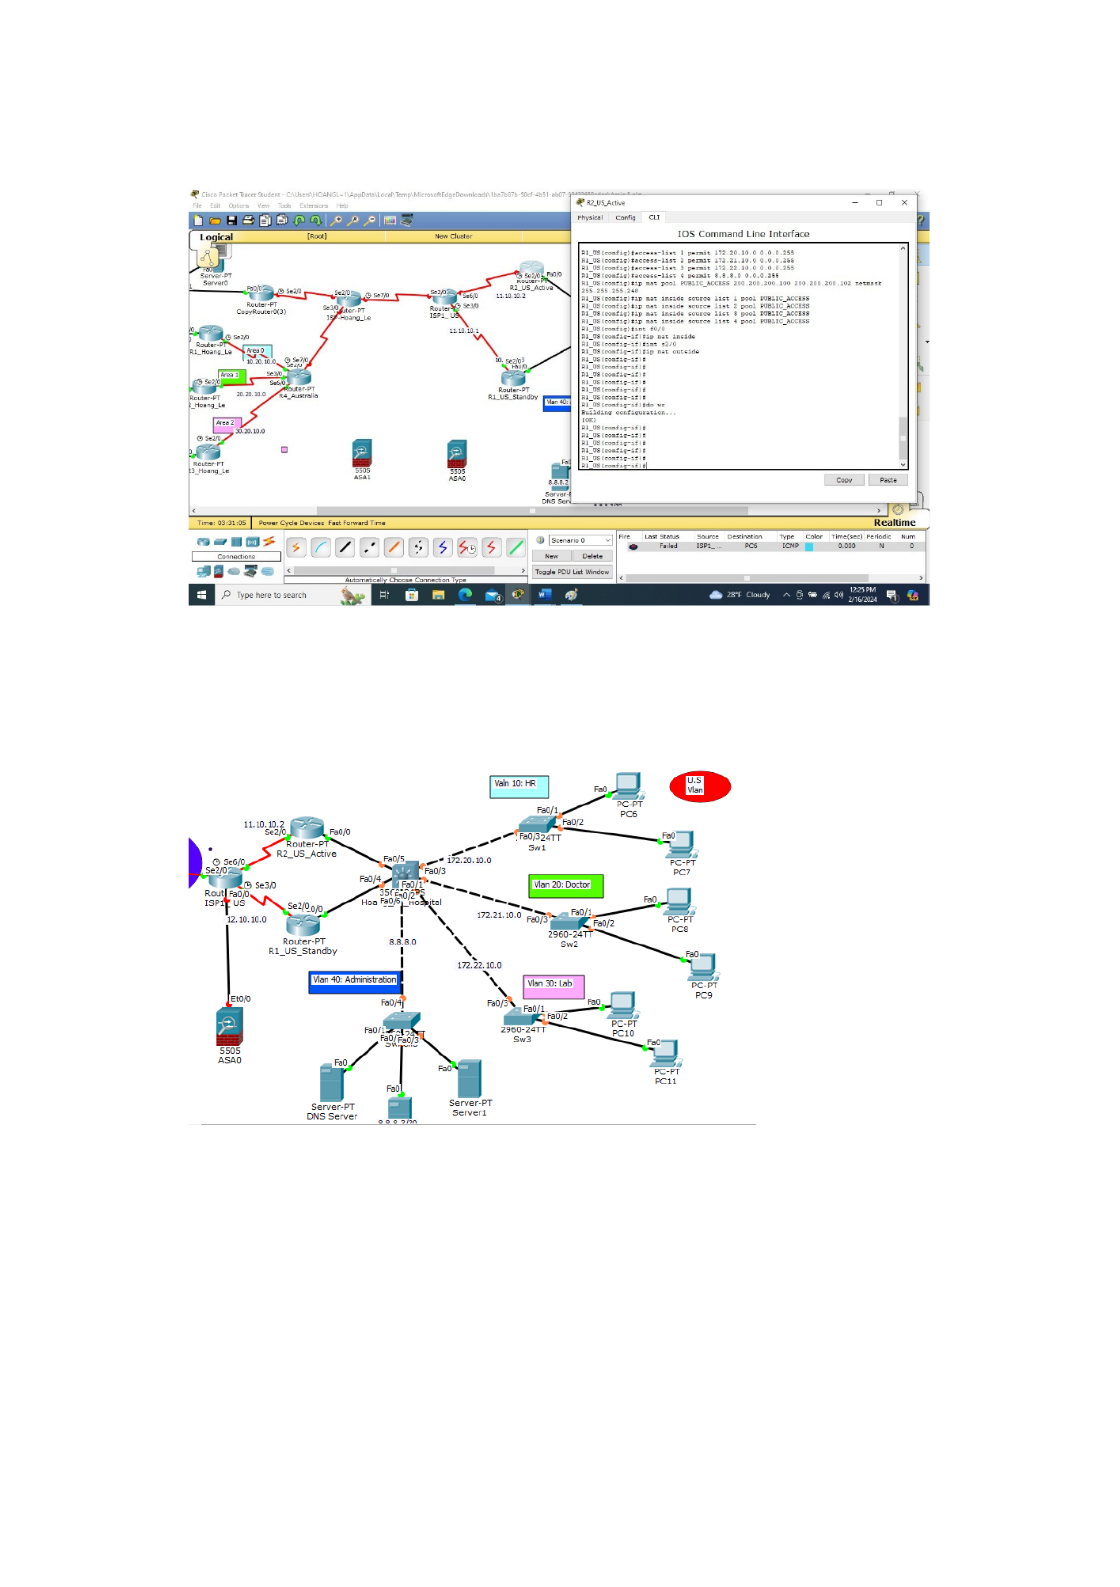
PPP WAN configuration
IT Infrastructure 12
U.S network configurations.
Vlan configurations
Vlan network design
Multi SW vlan configurations
IT Infrastructure 13
SW1
SW2
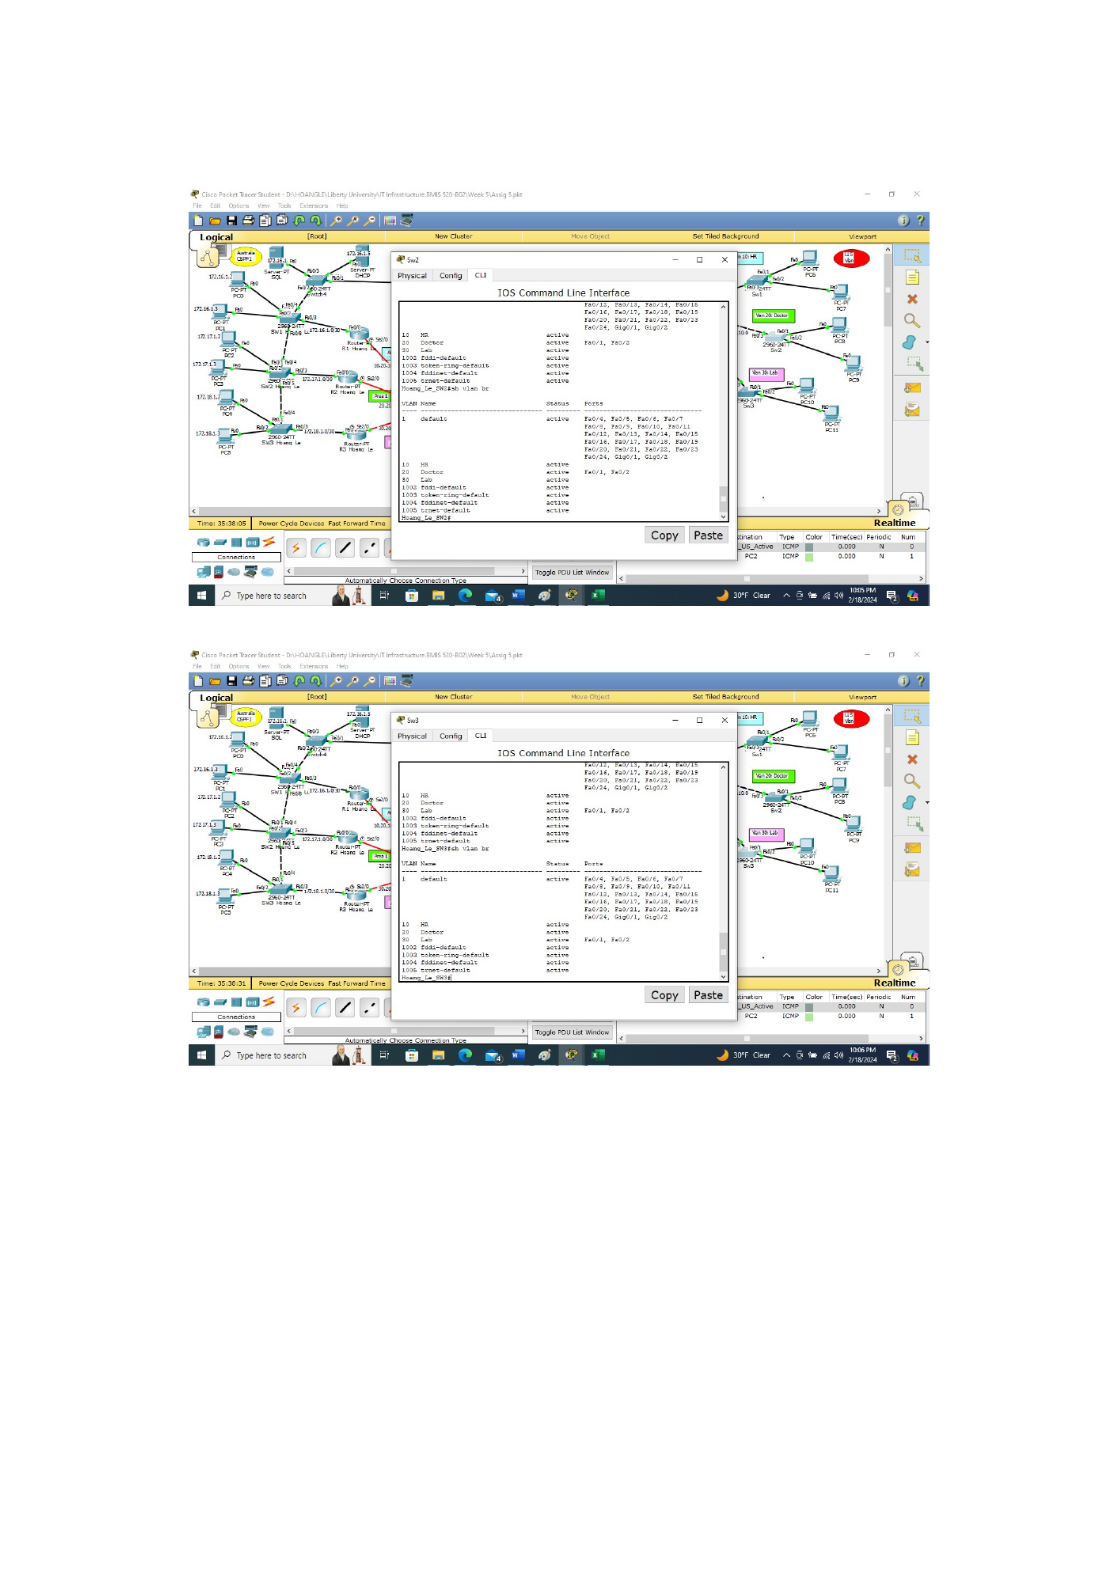
IT Infrastructure 14
SW3
HSRP configure.
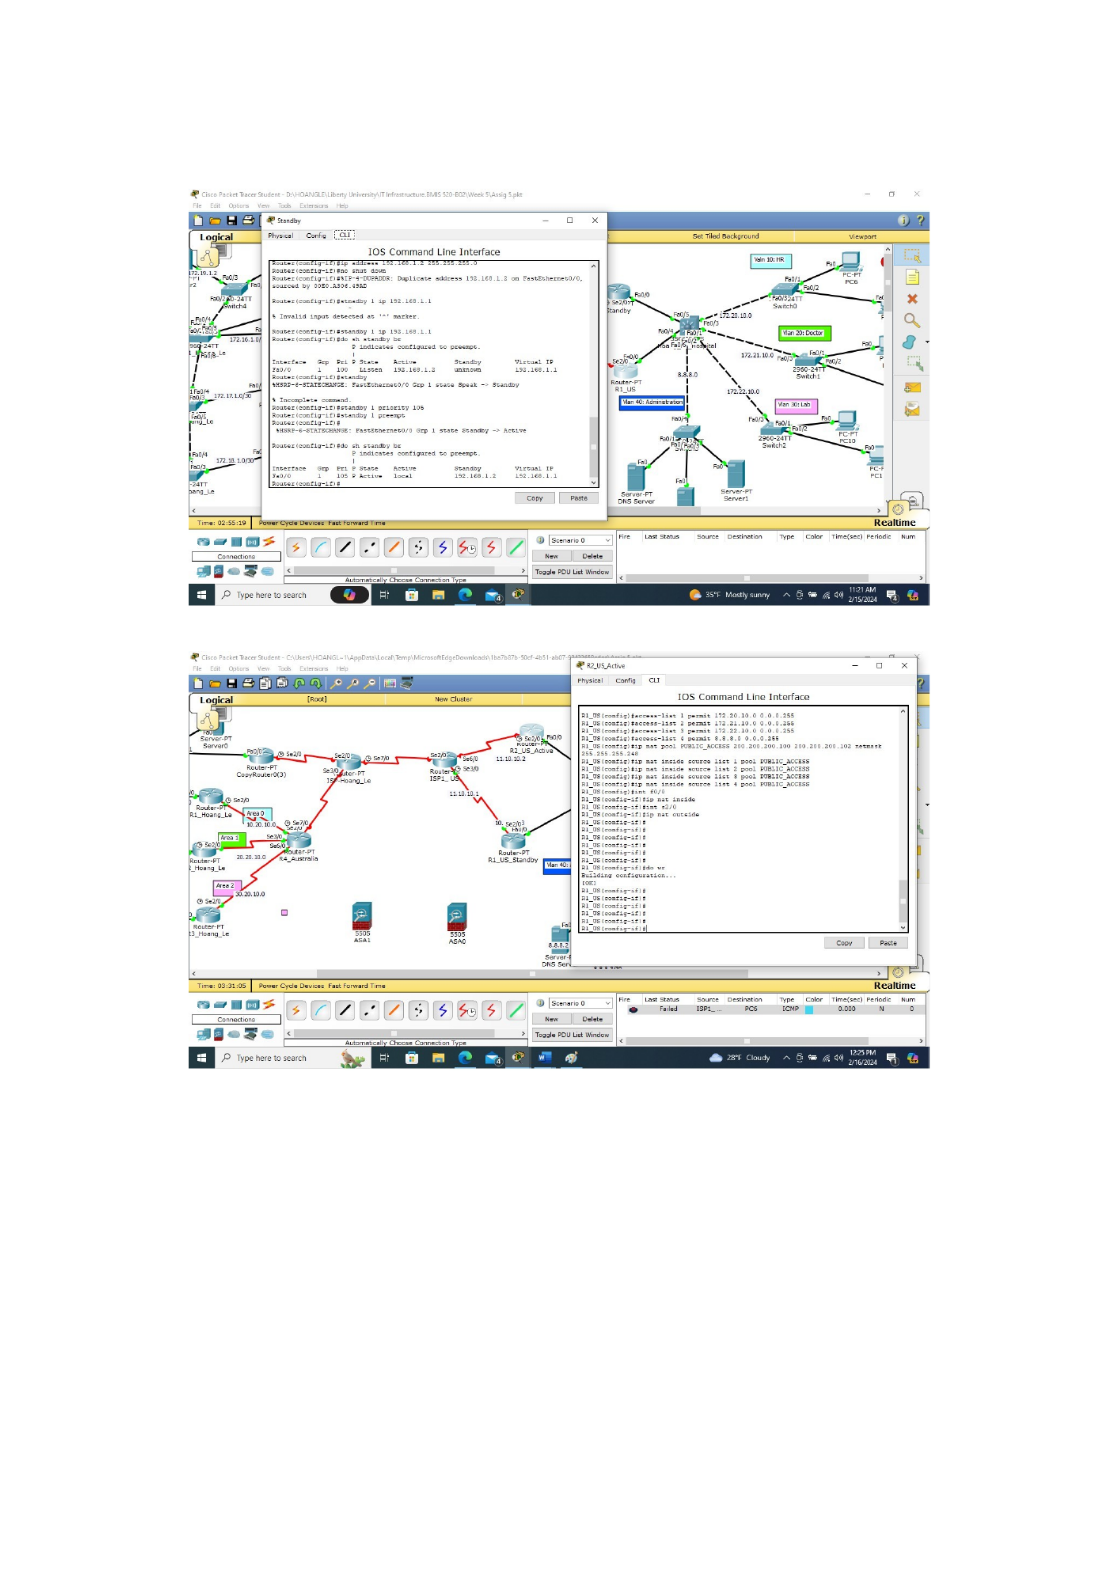
IT Infrastructure 15
Create and call access list.
PPP WAN configuration
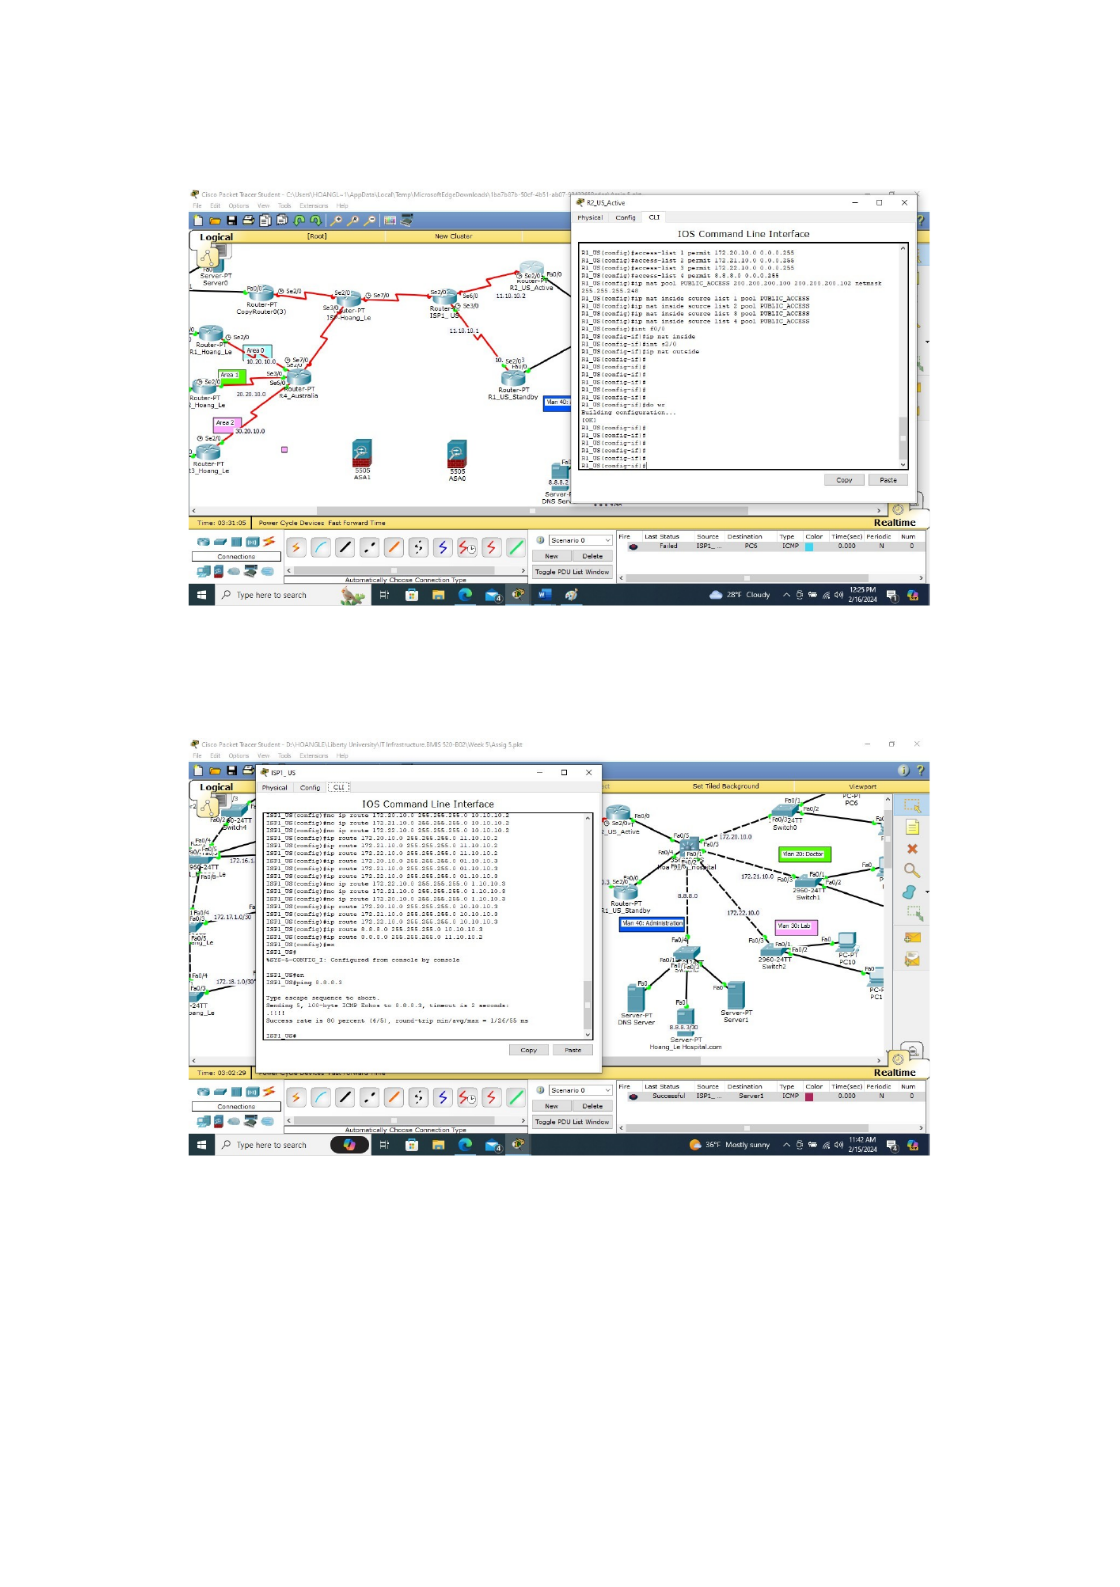
IT Infrastructure 16
Testing and verifying
Ping Commands
Ping from ISP router to Web server
Web Access
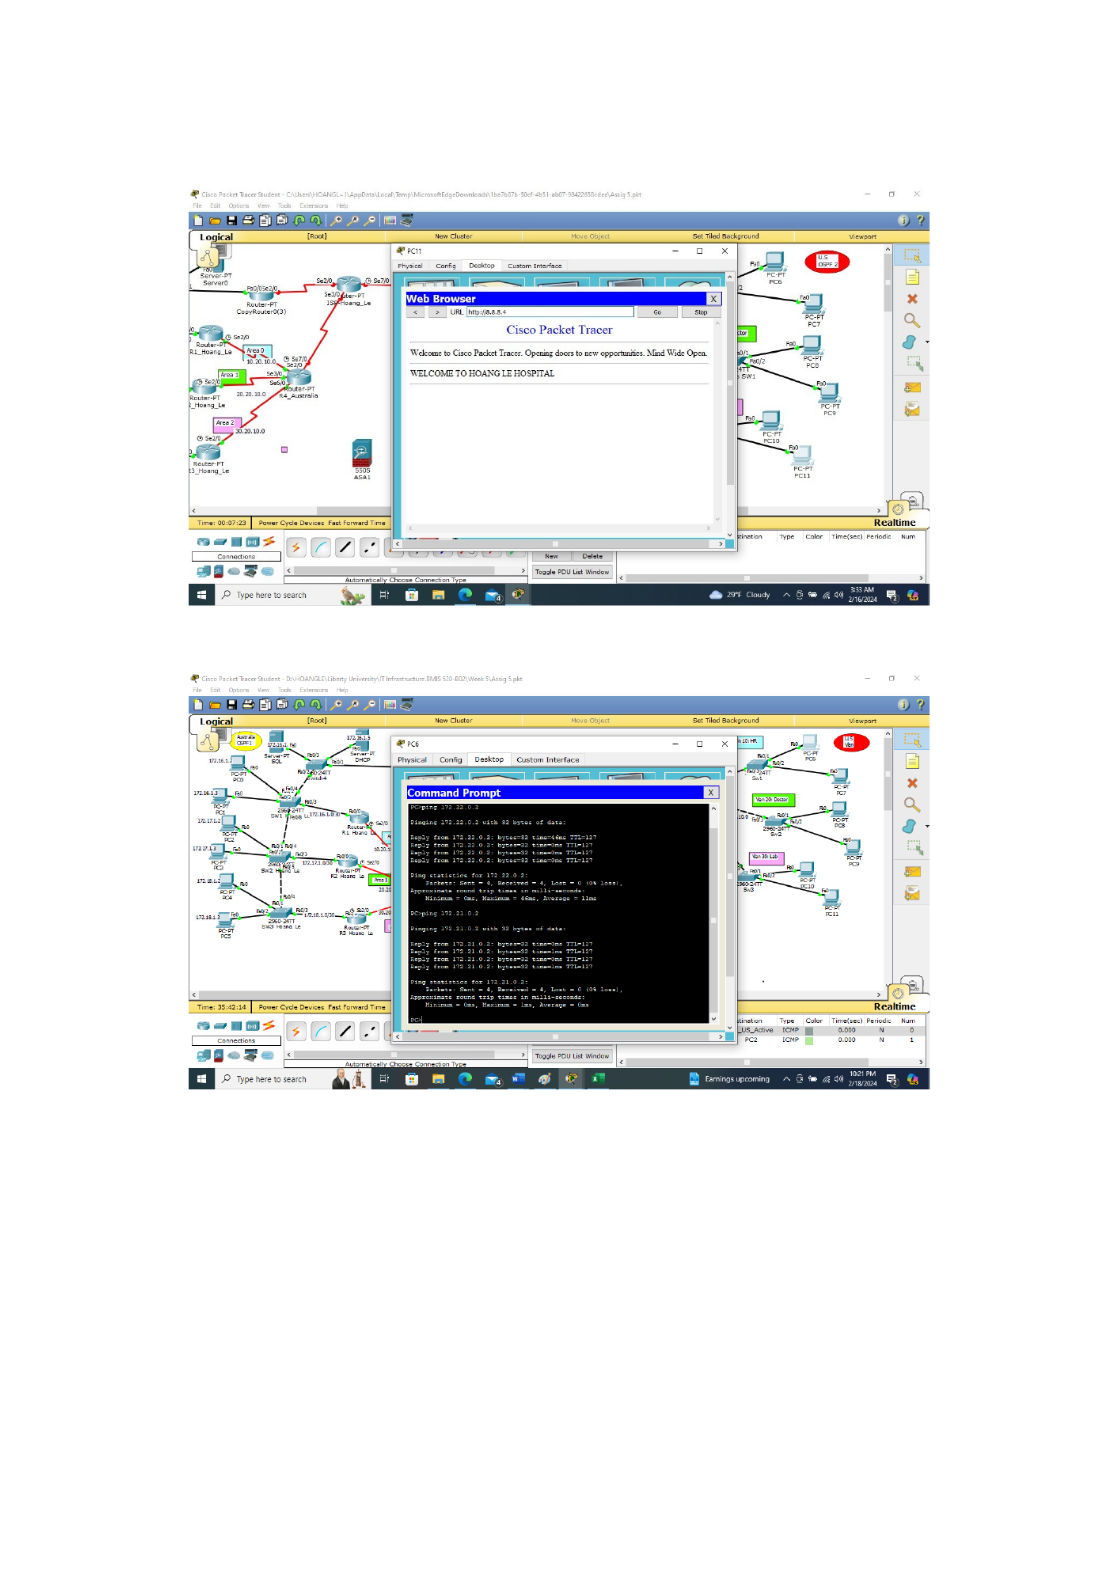
IT Infrastructure 17
Ping PC to PCs

IT Infrastructure 18
Conclusion
As the project progresses, the LAN network is designed to satisfy the requirements of the
hospital that expanded to Australia connected through WAN network. The LAN network above
is designed for both LANs, U.S and Australia. With the optimal configuration, the LAN is
configured with OSPF method on the stimulate Cisco packet tracer and successfully tested. The
future project should be set up and configurated the WAN network for both LANs, U.S and
Australia network.
IT Infrastructure 19
References
Diaz, L. (2018). . Packt Publishing. CCNA Routing and Switching 200-125 Certification Guide
ISBN-13: 978-1-78712-788-3.
Bruno. A & Jordan. S. (2021). CCNP Enterprise Design ENSLD 300-420 Official Cert Guide:
Designing Cisco Enterprise Networks. Cisco Press. ISBN-13: 978-0-13-657519-1
Cengage Learning. ISBN: 978-1-337-09904-29th ed.
Almutairi. H.& Zhang, N. A (2024). Survey on Routing Solutions for Low-Power and Lossy
Networks: Toward a Reliable Path-Finding Approach. Network 2024, 4, 1–32.
https://doi.org/10.3390/network4010001

