


Assignement introduction Some small business leaders lack
internal control
Internal control systems are policies, plans, and procedures to protect business assets while
reducing ethical and criminal violations (Hazzaa et al., 2022). Internal control systems also
mitigate the internal risk affecting profit margins. According to Setyawan et al. (2021),
internal control is essential to a company’s development and growth because it improves
financial and business processes. In the first section of the study, I will provide a
background of the problem, problem and purpose statement, nature of the study, research
questions, and conceptual framework. The first section also includes a review of the
professional and academic literature.
Background of the Problem
Public and private organizations are left vulnerable and open to the risk of
fraudulent activity when there is a lack of an internal control systems program. According
to Bunn et al. (2019), small business owners lack the financial expertise to run a business
effectively, develop internal controls, and recognize discrepancies or unusual transactions
of manipulated financial records. Developing internal controls to counter fraudulent
activities is essential to developing and implementing reliable systems and uncovering
fraudulent activity (Jachi & Yona, 2019). The cost to a company exposed to fraud is
detrimental and may lead to a company's demise.
According to Jachi and Yona (2019) and Othman and Ali (2014), fraud prevention
is an effort to emphasize the importance of internal controls to ensure operating

efficiencies, produce reliable financial data, and comply with applicable laws and
regulations. For example, misappropriating funds or property, followed by falsifying
accounts to conceal this act, may make it more difficult to detect, and an investigation is
necessary (Hazami-Ammar, 2019). Abdullah et al. (2018) stressed the need to identify
internal control components, specifically detecting and preventing accounting fraud.
According to Nazarova et al. (2020), the need for preventative audits and internal controls
is more in demand from equity holders and stakeholders.
Problem and Purpose
Some small business leaders lack the financial expertise and knowledge of internal
controls to run a business effectively (Bunn et al., 2019). According to the Association of
Certified Fraud Examiners (Almalki, 2016), small business leaders can expect to lose about
$150,000 due to fraud. The general business problem was that some small business leaders
were experiencing a loss of business assets or profitability. The specific business problem
was that some small business leaders lacked internal control system strategies to protect
business assets or profitability.
The purpose of this qualitative multiple-case study was to explore successful
internal control system strategies that small business leaders use to protect business assets
and profitability. The targeted population included five small business leaders in the
Western region of the United States with 2 years of experience who have successfully
developed and implemented internal control system strategies. Developing and
implementing internal control system strategies for small businesses may aid in protecting

business assets and profitability. The findings in this study may be used by small businesses
to successfully expand their business to different geographic venues in the Western region
of the United States.
Population and Sampling
Small business leaders who successfully operated a business in the Western region
of the United States were the population for this study. I used purposeful sampling for this
study. Purposeful sampling results in sampling that better match the sample to the research
aims and objectives, improving the study's rigor and the trustworthiness of the data and
results (Campbell et al., 2020). Eligible participants for this study were small business
leaders who have successfully operated a business in the Western Region of the United
States over 2 years and successfully developed and implemented internal control system
strategies to protect business assets and profitability. Data sources used in this study
consisted of transcripts of business leader interviews, archival data, reports, and documents
that the organization’s leadership deemed fit to share, which included business plans,
annual and quarterly financial statements, standards of procedures manuals, organizational
charts, employee handbooks, employee hiring procedures, interview protocols, and internal
control systems strategies manuals.
Nature of the Study
When conducting a study, the three methodologies are qualitative, quantitative, and
mixed methods (Siponen et al., 2021). Babones (2016) stated that researchers use
quantitative approaches to examine relationships or differences among variables. Overby

et al. (2022) stated that quantitative research is useful for obtaining numerical data. A
quantitative method's statistical implications for defining the relationships and differences
among variables were unsuitable for this study. The mixed-method research design
approach combines quantitative and qualitative methodologies when using either method
as a standalone study is insufficient (Stoecker & Avila, 2021). Therefore, a mixed method
for this study was inappropriate because of time and cost constraints. The quantitative
(statistical) method of data analysis is not necessary for the data collection process (Benoit
et al., 2017). Qualitative researchers focus on ordinary events in their natural settings to
grasp real life in an everyday environment (Gioia, 2019; Hamilton & Finley,
2019). Therefore, a qualitative method was appropriate for this study. Guercini
(2014) and Lê and Schmid (2022) discussed that in qualitative methodology, the approach
may be related to the researcher's experience. Kruth (2015) outlined five types of
qualitative research: narrative, case study, phenomenology, grounded theory, and
ethnography. In this section, I will discuss four types of qualitative research:
phenomenology, ethnography, grounded theory, and case study because they aligned
closely with my study. Exploring participants' lived experiences through a
phenomenological approach was inappropriate for the study because exploring the
meaning of the lived experiences by controlling participants' situations and environments
is not the study's goal (Kruth, 2015). Kruth also stated that ethnographic designs focus on
identifying the values and beliefs of the entire cultural group's shared patterns, which was
inappropriate for this study. The grounded theory is used to develop sociological theory

from textual data to explain social phenomena (Hennink & Kaiser, 2022). In a case study
design, researchers ask questions such as what, how, or why. Yin (2018) added that a case
study focuses on contemporary instead of historical phenomena. The case study approach
was appropriate for identifying and exploring strategies small business leaders use in
developing internal control systems to protect small business assets and profitability.
Research Question
The overarching research question for this study was: What internal control system
strategies do small business leaders use to successfully protect business assets and
profitability?
Interview Questions
The following were the research questions that I used to address the overarching research
question:
1. What internal control system strategies do you use to protect business assets and
profitability?
2. What framework did you use to develop and implement your internal control
system program?
3. How did you assess benefits of internal control system program implementation?
4. What were the key challenges to implementing your strategies for internal control
system elements?
5. How did you overcome the key challenges in the implementation of internal control
system elements?

6. How, if at all, has your internal control systems program helped your business
reporting functions?
7. What additional information would you like to share that we did not cover during
this interview that you used to protect business assets and profitability?
Conceptual Framework
The conceptual framework for the qualitative multiple case study was the
Committee of Sponsoring Organizations of the Treadway Commission (COSO) 2017
internal control-integrated framework. The commission established a framework for
developing efficient internal control systems (Frazer, 2016; Park et al., 2021). The COSO
framework includes five major components: (a) control environment, (b) risk assessment,
(c) control activities, (d) information and communication, and (e) monitoring that
strengthens the efficiency of management for organizations (Dolghi & Petreanu, 2021;
Frazer, 2016; Park et al., 2021). The COSO framework elements include a relationship
between the COSO framework's components and objectives on organizational internal
control systems. Braun (2015) also analyzed how each component contributes to applying
the COSO framework to internal control system development and may provide a system
of checks and balances to mitigate corporate fraud and risk for public and private entities
regardless of the business size. Each component aligns with the different functional and
operational activities of the various departments of a corporate body. Implementing the
framework should help organizations develop their internal controls for each department.
Small business leaders may benefit from the framework in developing their internal

controls systems program to protect business assets and profitability. The framework
provides organizations with a conceptual framework to develop their internal control
systems. Aladejebi and Oladimeji (2019) and Braun (2015) noted that the COSO
framework provides a potential lens through which researchers can view and understand
the operational, reporting, and compliance objectives that corporate bodies can use to
develop their internal control systems.
Operational Definitions
The operational definitions section below contains some terms referenced in this
doctoral study. Four key vocabulary words used in this study are defined below.
Business assets: Business assets are the total of a business entity's tangible and
intangible assets (Reilly, 2018).
Internal control systems: An internal control system is a process intended to provide
reasonable assurance to achieve control objectives of operations, the reliability of financial
reporting, and compliance with applicable laws and regulations (Hari, 2016; Kabuye et al.,
2019).
Risk assessment: Risk assessment is a security strategy and roadmap to evaluate an
organization (Gritzalis et al., 2019).
Small business: The U.S. Small Business Administration (SBA) defines a small
business with less than 500 employees (SBA, 2020).
Assumptions, Limitations, and Delimitations

Assumptions
Assumptions are the underlying premise and expectations that would affect the
study’s findings if invalid (Marshall & Rossman, 2016). Assumptions are a necessary
component of a study that a researcher accepts as valid and accurate (Valentin, 2014). My
first assumption was that participants would have knowledge and expertise in developing
internal control systems strategies. My second assumption was that participants provided
honest and detailed responses to the interview questions.
Limitations
A study area's limitations are outside the researcher's control (Helmich et al., 2015;
Theofanidis & Fountouki, 2018). A limitation of this study was the geographic region of
the study. This study was limited to the sample of participants in the Western region of the
United States, primarily focused on the State of Hawaii. The limitation of sample size and
geography limited data collection findings and established conclusions.
Delimitations
Delimitations are the scope and boundaries within the researcher's control
(Theofanidis & Fountouki, 2018). The first delimitation was the business size. I invited
only small business leaders with a minimum of 10 employees to participate in the study.
The second delimitation was business longevity. I also only used small businesses that have
operated for at least 2 years.

Significance of the Study
Small business leaders may be able to use the findings from this study to develop
strategies for developing internal control systems at a lower cost. Small business leaders
will have a tool to better protect their business assets and profitability by developing and
implementing their internal control systems program. Society may benefit from the study’s
findings by encouraging up-and-coming entrepreneurs to become small business owners
because they have the necessary tools and confidence to uplift commerce in the local
community.
Contribution to Business Practice
Small business leaders may benefit from the study because the results include
examples of strategies to develop internal control systems. By protecting small business
leaders' assets, the business's value may also create opportunities for small businesses to
open new locations. Internal control systems also increase efficiencies in accounting and
finance controls and other areas such as management, inventory, cash, purchase, sales, and
budget (Frazer, 2016). Small business leaders with internal control systems safeguard small
business leaders' assets and promote operational efficiencies (Frazer, 2016; Park et al.,
2021). Small business leaders can review and adapt the study's findings to develop
strategies to protect small business owners' assets and profitability.
Implications for Social Change
Society may benefit from the study's findings because of improved small business
financial stability from using internal control system strategies. Strategies to develop an

internal control systems program are essential to protect business assets and profitability.
According to Frazer (2016), small business owners may be able to develop and implement
an internal control systems program that may address those of a public corporation but at
minimal costs. The rationale for small business owners to consider developing a system
that may potentially protect business assets in the short and long term will benefit the
owners and the business to continue offering employment in communities. Internal control
systems stability may contribute to expansionary efforts that encourage more small
businesses to succeed and increase tax revenues for local communities.
A Review of the Professional and Academic Literature In this
qualitative case study, I explored small business leaders' strategies to develop internal
control systems to protect business assets and profitability. I applied a framework that
public organizations use in developing an internal control systems program.
Organizational leaders used the details of the framework to create a robust internal control
systems initiative. Small business leaders will use the framework to develop internal
control system strategies. A thorough review of prior studies was necessary to identify
strategies used by other business leaders in developing, implementing, and assessing
internal control systems for small business management. In the first part of the
literature review, I reviewed the relevance of the current COSO internal control-integrated
framework to this study, including the five major components and 17 principles and the
conceptual framework's makeup; an in-depth discussion of applying the COSO framework
in public organizations; and supportive models and contrasting theories, Sarbanes-Oxley

(SOX) Act, SOX Section 404, and management accounting information systems of the
COSO framework. The second part of the literature review discussed internal control
systems, corporate governance, organizational fraud in public and private entities, SOX
section 404, and the importance of organizations developing and implementing an internal
controls systems program. In this section, I define strategies for small business leaders to
develop and implement internal control systems to protect business assets and
profitability. In the final section of the literature review, I explained the cost of developing
and implementing an internal control systems program while applying the COSO
framework as the foundation for developing the program and the various features of
developing and implementing an internal control systems program for a public entity
versus a private one.
Strategy for Searching the Literature
The doctoral study literature included peer-reviewed journal articles, seminal
sources, and government documents. I found journal articles for the literature review by
using the following keywords and a combination of keywords included: business assets,
internal control, internal control systems, risk assessment, small business, small business
leaders, profitability, fraud, COSO, {COSO} 2017 Internal Control-Integrated framework,
small business profitability, SOX, SOX Section 404, corporate governance, financial
reporting, public entities, Securities and Exchange Commission (SEC) and internal control
system strategies. I used the Walden University Library databases to locate relevant
scholarly resources. The databases included ABI/INFORM Collection, Academic Search
Complete, Business Source Complete, Emerald Insight, ERIC,
Education Source Combined Search, JSTOR, SAGE Journals, ScienceDirect, and Thoreau
Multi-database Search. The list is not exhaustive and included Google Scholar and Ulrich
Web Global Serials Directory, confirming peer-reviewed sources. Ninetyseven percent of
the resources were peer-reviewed or governmental. In contrast, 29% of the resources I
included in sections 1, 2, and three literature review sections were published within 5 years
of my graduation, as shown in Table 1.
Table 1
Literature Review Sources
Reference type Total references 2019 2018 2019
and newer
and older and newer
Peer-reviewed journals
129
38
91
29%
Governmental references
2
1
1
50%
Non-peer-reviewed journals
1
0
1
0
Total references
132
39
93
29%
Application to the Applied Business Problem
In this qualitative case study, I explored small business leaders' strategies to develop
internal control systems to protect business assets and profitability. The conceptual
framework for this study was the COSO internal control-integrated framework {COSO,
2017}. The COSO framework elements address the relationship between the framework
components and the organization's internal controls systems objectives.

Conceptual Framework: COSO Internal Control-Integrated Framework
The COSO internal control-integrated framework was updated to align with current
organizational activities. Wilson et al. (2014) stated that the commission issued a report
defining a theoretical basis for internal controls. The members of the commission worked
on developing the foundation for the framework. The COSO framework originally included
only three categories of objectives: operations, reporting, and compliance {COSO, 2017}.
The five major components from the original framework include (a) control environment,
(b) risk assessment, (c) control activities, (d) information and communication, and (e)
monitoring that strengthens the efficiency of management for organizations (Dolghi &
Petreanu, 2021; Frazer, 2016; Park et al., 2021). Furthermore, to allow flexibility for
corporate leaders to interpret, align, design, and implement departmental organizational
activities, 17 principles were added {COSO,
2017}.
The articulation of internal controls is an essential aspect of the COSO framework.
The principles represent the fundamental concepts for each component. Public and private
sector organizations can achieve effective internal control by applying all the principles.
According to Dickins and Fay (2017), five significant components are the principles that
provide clarity and enhance understanding of the COSO framework. Executive leaders use
the principles to guide the development of a well-designed internal controls system for
small, medium, and large organizations operating in the public and private sectors.
Organizations change during their lifetime; therefore, organizational leaders adjust the five

major components of internal controls to align with the seventeen principles of
organizational change (Nurhayati, 2016).
Small businesses and public and private organizations use the COSO framework to
develop, implement, and assess internal control systems. According to Savitri et al. (2020),
business leaders use internal control systems to develop proper financial accounting and
management systems. Internal control systems are critical to developing policies and
procedures for operational planning. Mutnuru (2016) stated that small organizations need
internal controls to maintain a high-level assurance to achieve operational, financial
reporting, and compliance objectives. The executive leadership uses the COSO framework
in developing the firm's internal control systems program on the operational and functional
levels. Wilkins and Haun (2014) also mentioned that the newly developed and implemented
internal control systems strategies contributed to organization leaders experiencing a
positive, revenue-generating stream and strengthened weak control systems that may be
counterintuitive to the overall goal of positive capital inflows. Researchers have claimed
that businesses benefit from internal control systems because the activities developed also
maintain compliance with regulatory practices. Creating a culture of accountability with
clearly defined activities at different levels of the organization may also strengthen control
systems and address the changing business environment.
The COSO framework's function has organically changed the business landscape
with oversight to protect business assets while keeping with industry standards in financial
reporting. Adherence to SOX is also essential to consider when developing internal control

systems. Martin et al. (2014) stated that the interrelationship between the COSO framework
and SOX strengthens a business's checks and balances activities to deter fraud and money
mismanagement. The relationship between the five essential components, the framework's
17 principles, and SOX creates a potential future for a global and universal set of business
standards (Dickins & Fay, 2017). Therefore, the connection between the COSO framework
and governmental legislation creates a healthy regulatory environment to decrease
fraudulent activities. Government regulation provides a means to strengthen the COSO
framework and further develop control systems surrounding operational performance
practices (Rae et al., 2017). Government and external auditing council regulations are
essential to managing the organization leaders' ongoing financial malpractices.
Dragos (2015) discussed developing and implementing internal control systems
within public entities. Managers administer and communicate the objectives of an entity's
internal control system to organizational employees. Employees are also responsible for
implementing an internal control system, while managers oversee the organization's
policies and procedures. Public entities incorporate the COSO framework as a guide to
developing their internal control systems program. Internal controls are a continuous
process that requires ongoing assessments to ensure the activity aligns with the
organization's objectives. Public entities in Romania used the COSO framework to allow
management better activities, leading to organizational objectives' success (Dragos, 2015).
Organizational leaders in public entities using the COSO framework to develop internal
control activities will benefit from my study. The COSO framework illustrates the

applicability and flexibility of its five major components in an international setting.
Bilgi et al. (2017) discussed applying internal control systems and the five main
components of the Committee of Sponsoring Organizations of the Treadway Commission
(COSO) frameworks. The quantitative study by Bilgi et al. included questionnaires and
descriptive statistics to address small Turkish companies' internal control systems. Bilgi et
al. developed improvement guidelines for a company's internal control systems. The
questionnaires included questions that would address the five main components of the
COSO framework. The statistical component of the study evaluated the effectiveness of
the Turkish company's internal control activities. The COSO framework's five significant
components were included in Bilgi et al. questionnaire to add authenticity to the study. The
details of the data extracted from the questionnaires also provided relevant information; if
applied adequately, internal controls will be practical and efficient (Bilgi et al., 2017).
Subscales provided further details on the effectiveness of the five major components that
align with an organization's different areas. The overall results showed that Bilgi et al.
showed that participants rated the five major components and subscales higher, validating
the effectiveness of the COSO internal control system framework.
Yap Kiew Heong and Yap Saw (2016) also discussed that the lack of a controlled
environment could result in business failures. The business strategies for maintaining
external stakeholder trust in a company derive from adopting an internal control system to
assist future risk management planning. Creating a culture of accountability with clearly
defined activities at different levels of the organization may also strengthen control

systems. Wilkins and Haun (2014) state that internal control systems help maintain internal
and external stakeholders' health and welfare. The COSO internal control-integrated
framework contributes to a high-level and comprehensive overview of the importance of a
stable environment for the organization.
COSO Framework Components
The COSO framework's five components are essential to developing and designing
an effective internal control system. According to Cropanzano et al. (2017), Figure 1
represents the five major components of the COSO framework that are interrelated and
includes the (a) control environment, (b) risk assessment, (c) control activities, (d)
information and communication, and (e) monitoring that strengthens the efficiency of
management for organizations (Frazer, 2016; Park et al., 2021). Boyle and Applegate
(2016) stated that researchers tested all five COSO control components and found a
consistent baseline for achieving COSO criteria, ensuring that the objectives align with the
framework's five significant components. Rae et al. (2017) also uncovered direct
connections with the components, while others found indirect relationships. It is essential
to its vulnerability to monitor the control environment, information and communication,
and risk assessment to oversee internal operations. Therefore, when designed and
functioning effectively together, the five major components of the framework can maintain
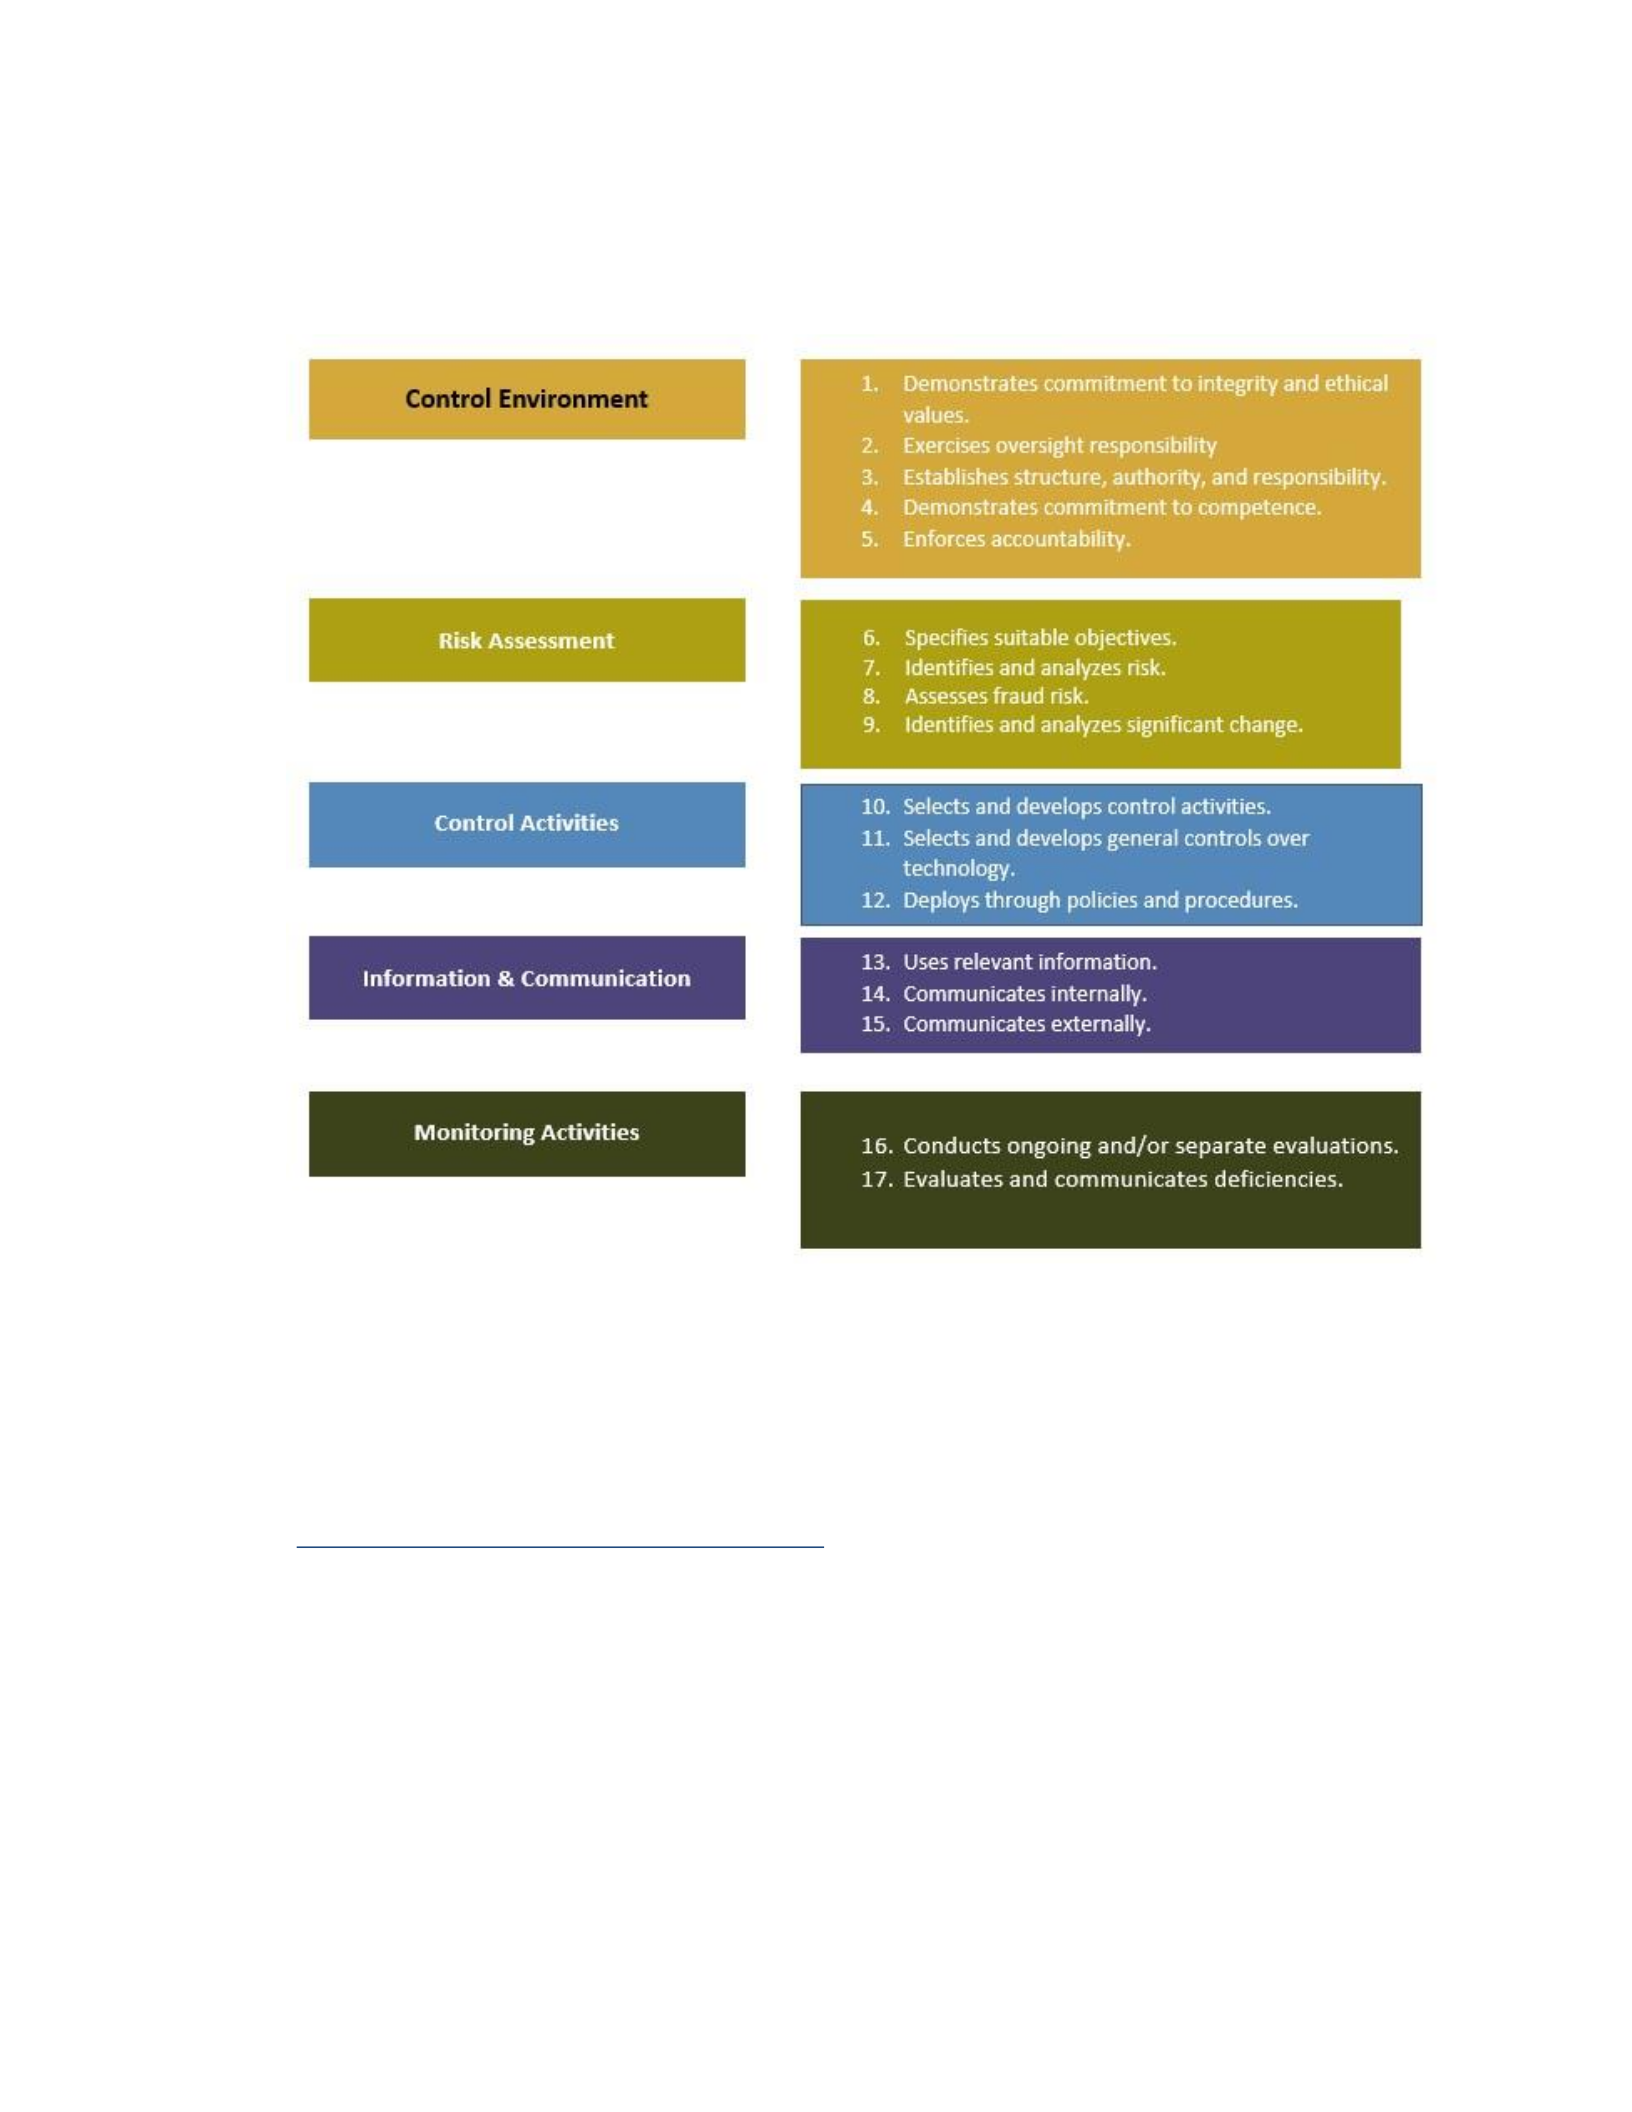
an organization's internal controls systems program. Figure 2 outlines the 17 principles that
make up each of the five main sections of the COSO Cube.
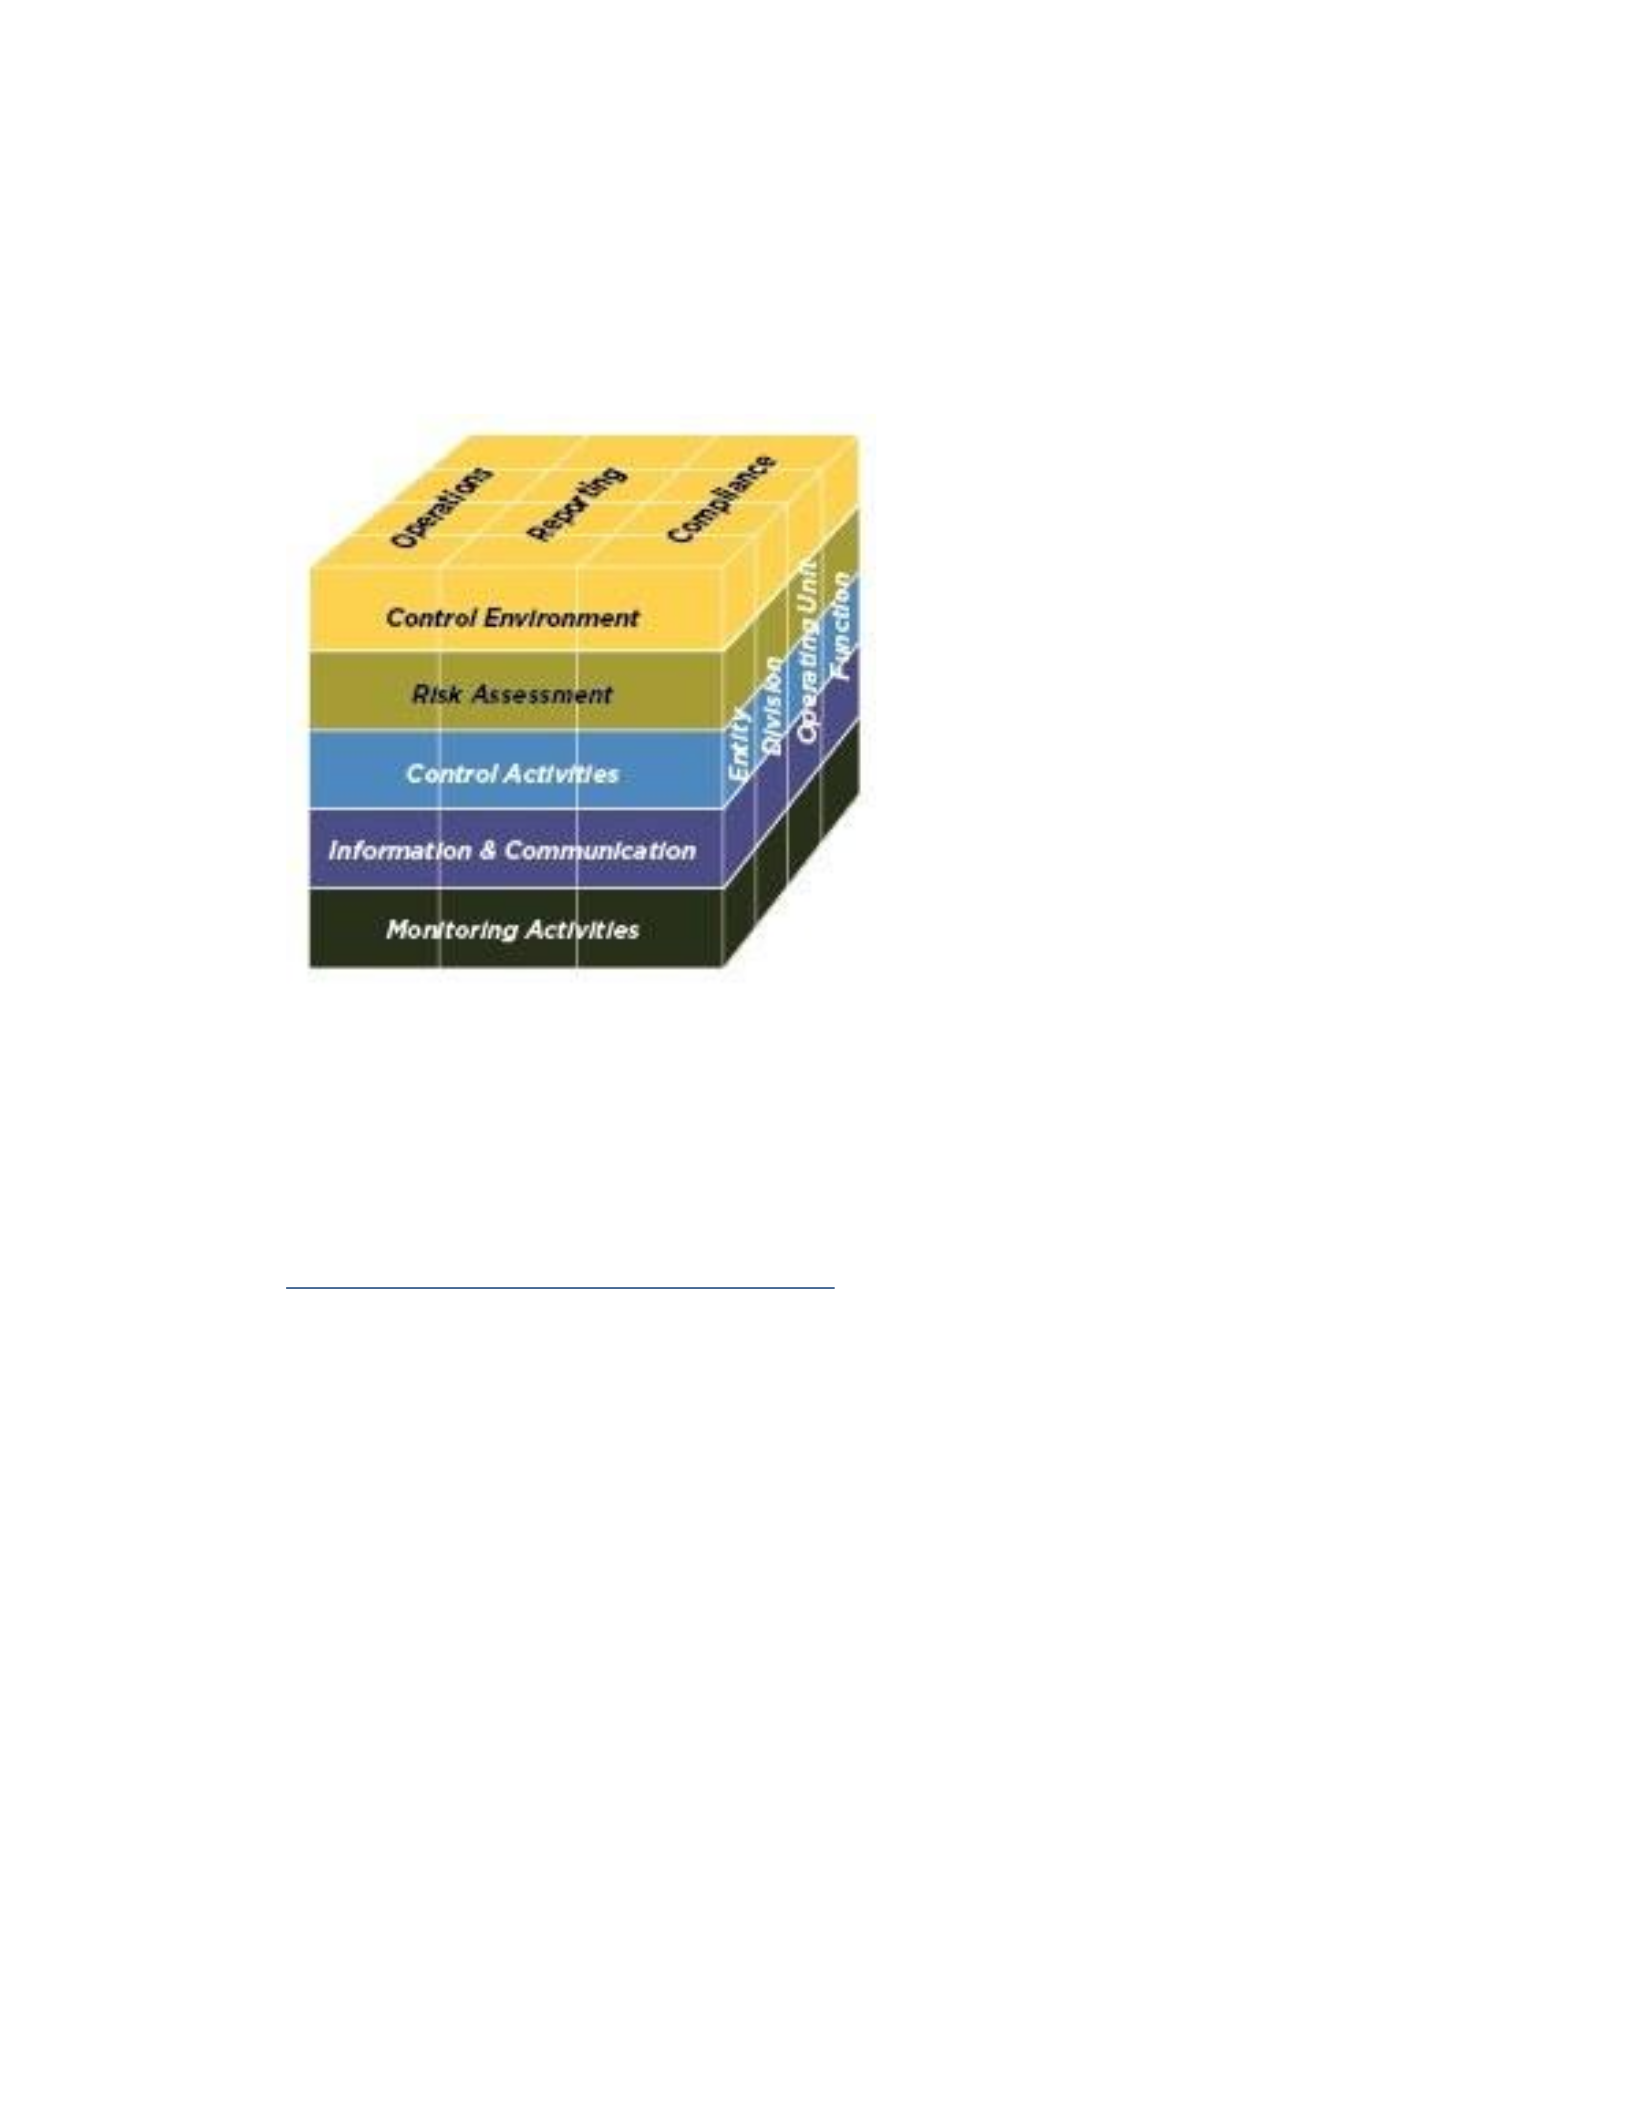
Figure 1
COSO {2017} Cube (2013 Edition)
Note. Adapted from “Social Exchange Theory: A Critical Review with Theoretical
Remedies,” by R. Cropanzano, E. L. Anthony, S. R. Daniels, and A. V. Hall, 2017,
Academy of Management Annals, 11(1), p.1–38
(https://doi.org/10.5465/annals.2015.0099). Adapted with permission (see Appendix E).
Figure 2
Social Exchange Theory
Note. Adapted from “Social Exchange Theory: A Critical Review with Theoretical
Remedies,” by R. Cropanzano, E. L. Anthony, S. R. Daniels, and A. V. Hall, 2017,
Academy of Management Annals, 11(1), p.1–38
(https://doi.org/10.5465/annals.2015.0099). Adapted with permission (see Appendix E).
Control environment
The control environment is the first significant component of the COSO framework.
According to COSO {2017}, the component's design focuses on the organization's internal
control systems' standards, processes, and structure. The board of directors and senior

management are in charge of setting the tone at the top by reinforcing the importance of
internal controls and standards. The control environment comprises the firm's ethical
values and integrity, which involves developing and implementing a systemic structure on
the functional and operational levels. Also, it provides a framework for organizational
leaders to attract, develop, and assess a cadre of human resources to accomplish its
functions to meet or exceed objectives. The control environment aims to have accurate
systems and human capital resources to impact and strengthen its internal controls systems
{COSO, 2017}.
Organizational leaders use the first five principles of the control environment to
develop and deepen the control environment's relationship at all organizational levels.
According to COSO {2017}, the first principle calls for the organization to demonstrate a
commitment to high ethical values and integrity. The board of directors uses the second
principle as a guide to demonstrate management and exercise oversight over developing
and implementing internal controls. The third principle is a design for management and the
board to communicate standards of procedures to meet organizational objectives.
Management will use the fourth principle to determine the organization's responsibility to
seek out, train, and retain competent individuals to ensure their objectives. The fifth
principle of the control environment is that the individuals responsible for organizational
activities are accountable for internal controls striving to meet organizational objectives.

Risk assessment
Risk assessment is the second major component of the COSO framework.
According to COSO {2017}, organization leaders experience internal and external
influences of risk that may impede the business from meeting organizational objectives.
Determining business risk tolerance will allow organizational leaders to set up processes
to mitigate the risk of achieving its objective. Risk assessment systems are essential for
organizations to have in place to determine how the organization will manage risk.
Managers at all levels of an organization require objectives to manage the risk and
minimize disruption to the business. The risk assessment component allows management
to develop operations, reporting, and compliance objectives when considering risk
assessment systems. The processes must be clear and concise, with management
opportunities to communicate the organization's systems and objectives for awareness and
ongoing implementation by all business members. The changes occurring within the
organization require external considerations, as the changing business landscape could
render the organization's internal control program ineffective {COSO, 2017}.
The next set of guiding principles of the COSO framework is a design of risk
assessment activity for management to understand, determine, and mitigate the different
levels of organizational risk. According to COSO {2017}, the sixth principle is a guide for
identifying and assessing potential risks. The seventh principle is used by leadership to
effectively communicate the organizational standards to identify and assess risks that may
impede an objective from success. The eighth and ninth principle addresses identifying risk

and determining how the organizational leaders will manage any organization's risks. Also,
organizational awareness of identifying potential risks to mitigate present and future issues
could cost the business unnecessary capital loss. Ensuring organization leaders consider
fraud potential when assessing risks to achieve organizational objectives is essential for
success. Risk assessment is essential in determining appropriate measures to combat
potential weaknesses in a vulnerable organizational system.
Control activities
Control activities are the third major component of the COSO framework.
Management involves carrying out objectives by setting up and managing policies and
procedures to mitigate risk. Management control activities are systems developed and
implemented at all levels of the organization. All organization members in charge of
business and technology processes carry out these control activity systems. The processes
require clear definitions to manage or detect risk activities with appropriate policies to
address human resource-related issues. Also, the segregation of duties is vital to the
organization's control activities. If segregation is not feasible, the organization will
implement alternative methods {COSO, 2017}.
The third set of principles guides the control activities of the COSO framework. The COSO
{2017} framework states that organizational leaders use the tenth principle with oversight
in selecting and developing processes to mitigate against the potential risk that may impede
the success of objectives acceptable to the managers and board of directors. The eleventh
principle addresses the selection and development process of practical control activities

over technology to ensure the chosen technology achieves organizational objectives. The
twelfth principle addresses the development and directs the implementation of control
activities regarding policies and procedures to effectively communicate the organization's
standards of action procedures to its employees. The technology control activities within
an organizational setting provide an organization with external system infiltration. It also
ensures that the internal use of technology is for the sole purpose of organizational activities
to achieve organizational objectives and not of a personal nature.
Information and communication
Information and communication are the fourth major component of the COSO
framework. COSO {2017} stated that information is critical to internal control activities.
Communication is the dissemination or the flow of information throughout the
organization. The quality of information within the organization between internal and
external sources supports the other internal control components. Personnel and senior
management communication require explicit information exchange so everyone knows
activities and issues. External communication is vital for organizational success; however,
the degree of information and how the information will be valid for the organization. The
flow of information and communication requires processes and systems to handle external
sources and the organization.
Management uses the fourth set of principles to determine an organization's inflows
and outflows of communication. According to COSO {2017}, the thirteenth principle is a
foundation for organizational members to use relevant quality information to support

internal control system functions. Organizational leaders benefit from the framework's
fourteenth principle of information and communications. The principle addresses
developing and implementing an internal communication system. The type of
communication includes but is not limited to the objectives and internal control
responsibilities necessary to support an internal controls systems program. The fifteenth
principle addresses that organizations effectively communicate with external parties,
affecting internal controls.
Monitoring
The fifth major component of the COSO framework included monitoring activities.
The COSO {2017} framework is a guide for management to prepare for ongoing
assessments to ensure each of the five components of internal control and the principles is
essential in maintaining the consistency and reliability of the framework. Assessments
should be ongoing and built into the business processes at different levels of the
organization. However, separate evaluations are also necessary periodically depending on
the scope and frequency of any issues from risk, assessments, and management's ability to
reach objectives. The outcome of the assessments is reviewed by industry regulators,
standard-setting regulators, the management, or the board of directors when deemed
appropriate.
The final set of principles addresses the importance of ongoing and separate
evaluations to determine if all five major components and their principles are present and
functioning. According to COSO {2017}, the sixteenth principle addresses that the

organization selects, develops, and performs ongoing internal and external assessments to
ensure that present internal control systems function. Managers use the seventeenth
principle to evaluate and communicate internal control deficiencies promptly and
responsibly, ensuring organizational leaders, including the board of directors, know the
activities and any corrective action. Lestari et al. (2019) conducted a study to provide
empirical evidence regarding the effects of the internal control system. One of the
conclusions states that continuous monitoring with optimal supervision in managing village
funds minimizes occurrences of fraud activities on Bangka Island. However, the
implementation of internal control systems harmed managing village funds because of
weaknesses in its implementation with factors like low understanding of village
government, overlapping rules, and changes in managing village funds (Lestari et al.,
2019). The lack of monitoring may weaken an organization's internal control system
(Wilkins & Haun, 2014). Therefore, the monitoring activities principles act as a means for
organizations to ensure that the organization maintains a reliable system of internal controls
that may weaken over time.
Sarbanes-Oxley
The SEC has designated the COSO framework as a regulatory policy, adding depth
to its SOX audit program. Internal control system programs in public organizations require
adherence to SOX and COSO Internal Control-Integrated framework for internal and
external auditing standards {COSO, 2017}. Organizational leaders can develop internal
control systems by implementing COSO and SOX standards. Auditors use the

COSO structure to organize a corporate environment's required processes and procedures
(Rae et al., 2017). The auditor's use of the COSO framework contributes to framework
reliability by providing a more structured environment for reliable internal reporting
standards (Martin et al., 2014). However, voluntary adoption of the COSO framework and
SOX auditing programs enables company leaders to set minimum external audit control
regulations (Martin et al., 2014). According to Wilkins and Haun (2014), communicating
information to internal and external stakeholders about the organization's financial health
is a transparent organization's essential practice. Internal stakeholders adhere to strict
policies and procedures that guide the business to achieve defined revenue-generating
strategies. Other factors, such as risk assessment, control activities, and monitoring
activities, contribute to its ability to deliver consistent revenue generation (Wilkins &
Haun, 2014).
Braun (2015) analyzed the COSO framework's contribution and applicability to an
organization's internal control systems. The internal control framework specifies
operational, reporting, and compliance objectives for corporate bodies to develop internal
control systems (Domnisoru and Dragomir et al., 2017; Rashid et al., 2022). Rae et al.
(2017) discussed the COSO internal control-integrated framework. They stated that the
framework among organizational stakeholders offers a universal language. Organizations
can achieve goals if efficiently communicated at all stakeholder interest levels. The COSO
framework elements included the control environment, risk assessment, control activities,
information and communication, and monitoring activities. The COSO framework's five

components of interrelatedness are a direct, indirect, and reciprocal association among the
components, and when adequately implemented in a business's internal control system
strategic plan and strengthens a business's corporate governance program (Rae et al., 2017;
Rashid et al., 2022).
The COSO framework contains five major components. Rae et al. (2017) identified
a positive interrelationship between the five COSO framework components. Each of the
components measures the effectiveness of the other four. The results reflected further
implications that the five elements functioned as a continuous network and were not
independent of each other. The five elements align with the various department's functional
and operational areas, with each department assigned a specific internal control system
(Rae et al., 2017). The COSO framework elements reflect a relationship between the COSO
framework's components and objectives on organizational internal control systems.
Public and private organizations use the COSO framework in developing,
implementing, and assessing internal control systems. Dickins and Fay (2017) provided
information about the reliability of internal control systems over financial reporting on
dependable financial statements. Kimbell (2017) stated that the SEC recognizes the
interrelationship between the COSO framework and the SOX auditing programs as a
regulatory standard. The COSO integrated framework of internal control systems is the
backbone of corporate governance practices worldwide (O. Braun, 2015). Kimbell (2017)
stated that the SEC found that adopting terms from a private sector entity developing a
framework for internal controls provides procedural due process. Dickins and Fay stated

that the SEC required managers to design, maintain, and regularly evaluate their internal
control systems over financial reporting. Organizational leaders and small business owners
should use the COSO framework to develop and implement an internal control system.
SOX Section 404 and Management Accounting Information System
Internal control systems are critical policies and procedures to consider in
operational planning. According to Martin et al. (2014), the COSO framework identified
five significant components and the 17 guiding principles that lay the foundation for an
internal control systems program structure. However, the cost of developing a robust
internal control auditing system that follows the 17 principles of the COSO framework and
SOX audit programs is challenging. Also, the policies that govern the external auditor's
ability to validate the internal auditor's programs pose another challenge if the activities
become standard regulatory practices. Dorsey (2015) stated that only 83% of public entities
bound by SOX Section 404 adopted the COSO framework. The remaining 17% did not
understand the newly introduced framework but became compliant 2 years after the
framework's update. The business's size determines how minimal or robust an internal
auditing system business will adopt using the COSO framework and SOX auditing
program mechanism for full integration. The COSO framework on internal control system
development provides checks and balances to mitigate corporate fraud and risk for public
and private entities regardless of the business size. Lawson et al. (2017) added that the
COSO framework's improvements provided more stability and strength to the conceptual
framework.

Small business owners with ten or more employees may consider developing and
implementing an internal control systems program to mimic a massive corporation at
minimal costs. Dimitrijevic et al. (2015) stated that an efficient management system is
necessary for achieving company goals. The rationale for small business owners to
consider developing a system that may potentially protect business assets in the short and
long term will benefit the owners and the business to continue offering employment in the
community. Also, internal control systems may increase efficiencies in accounting and
finance controls and other areas such as management, inventory, cash, purchase, and sales
and budget. The systems allow organizations to deter fraudulent activity and minimize risk
factors that will cost the company money and potential shutdown. Klein (2015) provided
insight into what small business owners and organizational leaders should look for to
minimize the risk of fraud exposure. Klein further discussed red flags that leadership and
owners should be aware of in detecting fraudulent activity. Also, Klein discussed the
importance of having an internal control system to protect the business and organization
from fraudulent activities. According to Lawson et al. (2017), the COSO framework
allowed business owners to evaluate their internal controls' design and effectiveness.
Organizational executives design internal checks and balances to deter fraud in their
risk management planning and internal controls systems program (Gavrys et al., 2020).
The control environment, one of the five major components of the framework, contributes
to strengthening an organization's internal control systems program. According to Welch et
al. (2016), an internal control systems program's importance validated its effectiveness in

protecting business assets. Organizational leaders use the COSO framework because
researchers showed detailed information about its effectiveness in different departments. It
provides a model for developing and implementing its internal control systems program.
Frazer (2016) pointed out that internal control systems are essential in a small business
environment to keep track of costs and overall organizational planning to safeguard
business assets. However, the costs involved in implementing an internal control systems
program are costly, and knowledge of developing systems to protect business assets may
lack on the business owners' side. Therefore, further research is necessary to show other
small business owners that developing an internal control systems program is possible.
Using the COSO framework to develop and implement internal controls promotes
the effectiveness and efficiency of functional and operational operations within an
organization. Wilson et al. (2014) stated that internal control policies and procedures guide
employees to safeguard organizational assets, management practices, inventory
procedures, operational efficiency, information systems, and financial reporting functions.
Liu et al. (2017) further discussed how employees influenced the quality of an
organization's internal control systems in China and how employees contributed to
designing and implementing an organization's internal control systems. Liu et al.
introduced the input-process-output and agency theories to highlight employee quality and
its relation to internal control quality. The agency theory addresses employee development
to minimize conflict by monitoring employees. Monitoring employee satisfaction may

increase productivity and employee buy-in on internal control systems when issues
between managers and employees are tense.
Napitupulu et al. (2016) found that using a management accounting information
system (MAIS) relates to an organization's internal control systems program. The quality
of MAIS depends on an organization's data and information, culture, and shared values
within an organization. Internal control systems allow organizations to deter fraudulent
activity and minimize risk factors that may cost the company money and existence
(Napitupulu et al., 2016). Dimitrijevic et al. (2015) discussed the importance of internal
control systems and the goals and constraints of a system. The history and purpose of
internal controls within a business safeguard internal and external stakeholders
(Dimitrijevic et al., 2015). Internal controls protect corporate assets and check the accuracy
of managerial policies. Developing policies and procedures to maintain stakeholder
interests is essential in meeting strategic goals focusing on revenue generation. Wilson et
al. emphasized the importance of internal controls to ensure that a business's operations are
practical and efficient, reliable financial reporting, and compliance with applicable laws
and regulations for activities.
The COSO framework application further emphasized the importance of keeping
information and support systems fit the company's needs (Napitupulu et al., 2016).
Dimitrijevic et al. (2015) stated that an organization is proactive in monitoring activities to
detect and quickly respond to data manipulation and fraud, stating that a company can
benefit from internal controls. However, public and private entities can benefit from

monitoring internal control activities to strengthen an organization's checks and balances
system. The results of Dimitrijevic et al. study to develop reporting systems in
organizations and businesses are essential deterrents to protect business assets and
profitability. Also, utilizing the COSO {2017} framework as a template to develop more
robust corporate governance through an organization's internal controls program
strengthens an organization's overall reporting system for financial and non-financial
information. Protecting a company from financial fraud due to a single perpetrator or
collusion scheme is a factor in developing internal controls. Internal control systems are
necessary to manage corporate governance (Paletta & Alimehmeti, 2018).
Moreover, Abdullah et al. (2018) and Hazzaa et al. (2022) stated that the lack of
efficient corporate governance and internal controls makes a firm vulnerable to risks,
including improper recording of accounting transactions, losses, and uncertainty. The data
may suggest that small business leaders develop and strengthen their internal control
system strategies, deter mismanagement of assets, and ensure transparency in financial
recording activities. The results of this study may also positively impact small business
sustainability, asset protection, and profits.
Corporate Governance
Corporate governance is the foundation for public entities to conduct business
ethically and transparently. The Organisation of Economic Co-operation and Development
(2015) defined corporate governance as relationships between management, directors,
shareholders, and other stakeholders. Corporate governance also provides leaders with

guidelines for attaining the organization's objectives and monitoring overall performance.
According to Nerantzidis and Filos (2014), corporate governance is the cornerstone of a
public entity's position to be transparent, ethical, trustworthy, accountable, and risk
management supporting investments with integrity. Public entities with a substantial
corporate governance program develop mechanisms to sustain the organization's
transparency and integrity (Nerantzidis & Filos, 2014). Public entities use the COSO
{2017} framework as a guide to developing activities to strengthen an organization's
corporate governance program with stable internal control systems. COSO focuses on
operations, reporting, and compliance objectives to guide organizational leaders in
implementing and evaluating internal controls. In Greece, Nerantzidis and Filos found that
the organization's corporate governance and management control system improved by
incorporating the COSO framework. Smaili and Labelle (2016) stated the importance of
separating corporate ownership and control so groups and individuals in power cannot take
advantage of powers to manipulate financial accounting information. After the United
States passed SOX, several market authorities regulated corporate governance and
enforcement actions against single perpetrator or collusion schemes. The internal control
system mechanism assures executive leaders' responsibility and financial statements'
reliability (Oussii & Boulila Taktak, 2018). Therefore, internal controls ensure
management manages objectives reported under the COSO framework by an organization's
board of directors and executive leaders. It also monitors organizational risk, ensures

published financial statements are dependable, and assures the organization complies with
all applicable federal, state, and local laws.
Financial Reporting
Organization leaders must identify internal control components, specifically
accounting fraud, and detect and prevent fraud. The cost to a company exposed to fraud is
detrimental and may lead to a company's demise. Developing internal controls to counter
fraudulent activities is essential to developing and implementing systems relevant to
accounting and uncovering fraudulent activity (Dimitrijevic et al., 2015). COSO {2017}
stated that management sets the tone for the functioning of an internal control system.
Dimitrijevic et al. outlined the several types of fraudulent activity that can affect a company.
Reporting activities and financial statements were the standard and reported fraud
activities. The details of the different activities can provide managers and owners with
information to develop their internal control systems. The qualitative study by Napitupulu
et al. (2016) proved that internal control effectiveness influenced MAIS quality in SOEs.
Napitupulu et al. also stated that internal controls were associated with the quality of MAIS
reporting on financial and non-financial information used for decision-making purposes.
Therefore, the objective of internal controls is to minimize the risk and ensure the security
of the company assets, accuracy, and appropriateness of the information presented by the
information system to support company goals and objectives.

Corporate Fraud
Corporate fraud cases continue to increase even after the United States established
legislation to deter fraudulent activities. In a study, researchers used a sample group of 152
U.S. criminal corporate fraud cases within the U.S. Department of Justice and found
employees engaged in unethical and fraudulent activities for ten years (Harjoto, 2017). The
study showed a connection between a weak corporate ethical culture resulting in fraud in
public entities. According to Peters and Maniam (2016), corporate fraud and employee theft
within 20th-century businesses are common occurrences. Organizations that lack the
proper mechanisms to deter fraudulent activity expose themselves to capital, information,
or material losses (Aytac & Cabuk, 2020). The dynamic nature of business underscores the
importance of active risk management in developing and implementing internal controls to
decrease business risk. According to Margret and Hoque (2016), the opportunity for
fraudulent behavior is apparent; however, a well-developed and implemented internal
control system is necessary to decrease less good behavior. Accounting standards are rules
and regulations set by accounting regulators to regulate an organization's financial
transactions and accounting statements (Ndekugri & TwumDanso, 2019). Mechanisms to
deter these actions are required to protect internal and external clientele from experiencing
losses. The perception from internal and external stakeholders following corruption
allegations was that stakeholder trust was significantly violated (Eberl et al., 2015).
Weaknesses in an organization's internal control system program can cause distrust and

damage its reputation. The framework's adoption suggests its use to deter future financial
fraud and unethical activities.
Regulations – SEC Adoption and SOX
The SEC was formed in response to the stock market crash. Public confidence in
the markets declined, and the SEC is an established administrative agency with the passing
of the Securities Act and the Securities Exchange Act. The SEC continues to be a consistent
regulatory agency for internal and external activities for public organizations and further
strengthens SOX's effectiveness. The SEC regulates public entities while keeping investor
confidence in organizations secure. The SEC adopted the COSO framework, which may
increase investor confidence in organizations with a welldeveloped internal control systems
program.
Executive leaders falsifying financial reports and mismanaging organizational
records caused Enron and WorldCom's company leaders to be guilty and charged with
obstruction of justice for destroying documents (Ozdagli, 2018). The executive leaders of
these companies engaged in unethical and fraudulent activities. Audits conducted
uncovered the financial mismanagement activities of these companies. The COSO
framework requires public organization leaders' compliance with SEC rules and SOX
procedures. SOX and portions of the law indicate public entity leaders' requirements to
certify internal control effectiveness, with external auditors attesting to its authenticity
(Kimbell, 2017). SOX Section 404 requires public entity leaders to choose an internal
control framework and annually report their internal controls' design and effectiveness

(Barlas, 2015). Internal control compliance is critical to maintaining and deterring
fraudulent activity in organizations.
Executives use the COSO {2017} framework to guide the development,
implementation, and assessment of an organization's internal control systems program.
According to Kimbell 2017, the SEC adopted the COSO {2017} framework because it
allowed regulators to measure procedural due process. The five parts of the framework and
17 guiding internal control principles further strengthen the framework's effectiveness.
SOX requires public organizational executives to establish and maintain adequate internal
control procedures for financial reporting (Addy & Berglund, 2019;
Karakoc & Özdemir, 2016; Zhao et al., 2017). In conjunction with SOX and COSO, the
SEC's three standards are critical to organizations when leaders develop, maintain, and
assess their risk mitigation efforts. The COSO frameworks can also be used outside the
U.S. and adopted in a global business environment to combat corruption and fraudulent
activity (Trautman & Kimbell, 2018). Therefore, the framework's flexible nature to operate
in all business environments allows small businesses to adopt the COSO framework in their
business planning efforts or incorporate it into an existing business. Implementing an
internal control system program in a small business environment is costly. However, risk
mitigation planning is essential to reduce financial losses due to fraudulent crimes.
Transition
In Section 1, I included a discussion of the background of the problem, problem
statement, purpose statement, nature of the study, and a rationale for choosing a qualitative

and multiple case study. In Section 1, I also shared the interview questions, conceptual
framework, assumptions, limitations, delimitations, the study's significance, and details of
the COSO internal control-integrated framework used in this study. Section 1 also
contained peer-reviewed and seminal research on the conceptual framework, parallel and
contrasting views, its application in public and private organizations, and a discussion on
internal control systems strategies for small business leaders to create and implement.
I included descriptions detailing the data collection processes and instruments for
the study, and the steps necessary for ethical research, limiting bias, and protecting the
participant's identity in Section 2. Also included were the reliability and validity data
components I used during member checking and methodological triangulation to reach data
saturation.
Section 3 included the classical data method and the NVivo 12 qualitative software
analysis used to code and validate the data analysis process. Information extracted during
the data analysis helped me author Section 3 of the study. Section 3 also contained my study
findings and professional recommendations on applying the results and addressing social
change implications to conclude the study.

Section 2: The Project
The purpose of this qualitative multiple-case study was to explore successful
internal control system strategies that small business leaders use to protect business assets
and profitability. In this section, I explored project details, including the researcher's role,
the rationale for using a qualitative research method and multiple case study designs, data
collection instruments and analysis, and the specific population and sample group in
Section 2. I also critically analyzed my data collection activities and organization
techniques to conclude the study. I defended the research's reliability and validity.
Purpose Statement
The purpose of this qualitative multiple-case study was to explore successful
internal control system strategies that small business leaders use to protect business assets
and profitability. I interviewed small business leaders in the Western region of the United
States from five small businesses who have successfully used internal control system
strategies to protect business assets and profitability. The implications for positive social
change include increased internal controls to protect business assets while enabling small
businesses to succeed and potentially expand their business to different geographic venues
in the Western region of the United States. The opportunity for small businesses to grow
could also provide more employment opportunities in the community. The increase in
employment could allow small business leaders to succeed and the possibility to contribute
proceeds from their sales to local charitable foundations in the Western region of the United
States.

Role of the Researcher
The primary role of the researcher was to develop narratives and a space for
interaction among participants' views, grasp the material and analyze multiple perspectives
(Karagiozis, 2018). I captured each participant's views, knowledge, and deep understanding
of developing internal control systems strategies and their perspectives during the
interview. Through ongoing and active engagement, researchers can gain insightful
information by strengthening research-participant relationships (Yin, 2018). I encapsulated
the multiple viewpoints and connected them back to the purpose of the study and the
overarching research question by the end of the study. Yin (2018) stated that the qualitative
researcher should follow a rigorous path of formal and explicit procedures to protect against
the threats to validity and rival test explanations of case study research. Therefore, my role
as the primary researcher required a certain degree of knowledge and understanding of
internal control systems, small business leaders, and strategy development.
My relationship with the topic, study participants, and area of research is essential
to address the overarching research questions. According to Moon (2015), the researcher’s
role in collecting data involves knowledge, skills, and influence to make sound judgments
and decisions when conducting research. My professional experience working with small
business leaders spans professional and academic arenas. Also, my expertise includes
management, accounting, finance, marketing, advertising, risk management, and
insurance. These areas of practice mentioned were in my experiences as a leader in a public
organizational setting, private business setting, and academic institution of higher learning.

The interaction with the different individuals at the different venues allowed me to connect
my experiences with the particular research area focusing on internal control systems and
strategy development. Also, my experiences with individuals and groups in both settings
allowed me to connect with my study. Due to my experiences in practice, I have developed
an interest in developing strategies for internal control systems in public and private
settings and small business environments.
Ethics is a vital part of a research study, and a researcher must be aware of their
ethical role throughout the survey (Marshall & Rossman, 2016). The National
Commission for the Protection of Human Subjects of Biomedical and Behavioral Research,
in its 1979 Belmont Report, provided ethical guidelines that include three guiding
principles that focus on respect for persons, beneficence, and justice. In addition to
maintaining an ethical environment, I followed a strict protocol to protect the study
participants and guarantee that the benefits of the education outweigh the potential risks to
a participant's involvement with a research study. Therefore, I followed The Belmont
Report.
The ethical principles included in The Belmont Report are respect for persons,
beneficence, and justice (National Commission for the Protection of Human Subjects of
Biomedical and Behavioral Research, 1979). I maintained timely and consistent
engagement during each phase of my study. First, to ensure respect for persons, I reached
out via in-person, phone, email, or letter in the mail when making first and subsequent
contact with each participant. Second, to safeguard each participant's beneficence and

protect the research participants' identities, I assigned each participant an anonymous letter
and number combination. Also, in my interview protocol, I outlined Walden
University’s policies and procedures for my participants. Third, I provided consent forms
(Appendix E) via email to voluntary participants to maintain justice. I provided participants
with full disclosure of the research study and how their participation impacted it. Also, in
my consent forms (Appendix E), I provided participants with information regarding the
study's voluntary nature and that, at any time, the participant could withdraw from the study
without any consequence. Furthermore, I remained mindful of the geographic region's laws
and regulations and was bound to each phase of the data collection process. Therefore, I
followed all applicable federal, state, and local laws and regulatory guidelines in the
Western region of the United States, where my research study’s geographic region resided.
Qualitative researchers must be aware of and mitigate personal bias by carefully
assessing and disseminating data throughout the research process (Malone et al., 2014;
Stone et al., 2019). I might become personally involved with the subject matter and varying
personal viewpoints during the study. A researcher's comprehensive knowledge of the topic
by connecting with prior research may be another means to mitigate bias (Bryman, 2012).
Therefore, I addressed bias by exercising daily self-reflection and selfdialogue to identify
personal bias contrary to my research. I engaged in these exercises during each research
study phase, ensuring I remained objective. Also, I paired other mechanisms to mitigate
bias and avoid the data through my perspective lens by using interview protocols, member
checking, data saturation, and thematic analysis of the research data.

I used an interview protocol to remain consistent with all interviews to minimize
inconsistencies and reduce biases during my interviews. My interview protocol and
questions (see Appendix A) outlined the details of each stage of the interview process for
added consistency and rigor. I also provided participants with the details of their
participation in the interview portion of the study. Marshall and Rossman (2016) stated that
interview protocols provide consistency and rigor throughout the study of each interview
procedure. Researchers use an interview protocol to keep interviews as short as possible
with the help of procedures and keeps consistency for the number of interviews scheduled
during the interview process (Benia et al., 2015; Siedlecki, 2022; Yin, 2018). Consistency
with each interview is essential during the interview process and ensures the same
information from my participants.
Participants
The target participants of my study included five small business leaders in the
Western region of the United States. According to Yin (2018), researchers must target
qualified participants based on the researcher's prescribed eligibility criteria to gain quality
data. I used a sample size of five small business leaders from five small businesses
participating in the study. The criteria for participants included (a) five small business
leaders who have successfully operated their business in the Western region of the United
States for over 2 years and (b) five small business leaders who have successfully developed
and implemented internal control systems strategies. Hays et al. (2016) also suggested that
researchers consider validity, trustworthiness, and goodness as criteria for the study's

participants' eligibility. Researchers need to develop specific strategies to gain access to
participants for the study. According to Powell et al. (2016), identifying recruitment
strategies for study participants may positively affect the study's reliability, cost, and length.
I have a working knowledge of the topic to connect with potential study participants.
According to Marshall and Rossman (2016), sample sizes are small, and qualitative
researchers aim for depth and crafting relationships with the study participants.
Gatekeepers are people or entities who could allow or deny access to potential study
participants (Whicher et al., 2015). Gaining access to participants may be challenging.
Gatekeepers may be a potential roadblock for researchers in gaining access to participants.
The gatekeepers will be the small business leaders for the study. Once participants meet the
eligibility criteria, researchers send letters of invitation to potential participants for the
study (Powell et al., 2016).
Potential participants must possess the knowledge and experience in developing
internal control strategies to participate in the study. I compiled a list of the top 50 small
businesses in the Western region of the United States. I visited each place of business,
whether the owners were past acquaintances or a cold lead from my list, to shake hands
with potential participants to discuss the possibility of their participation in my study. When
visiting the potential participant's office, I briefly discussed the nature of the study and its
benefits. Zhang and Jiang (2015) stated that participants might be more willing to
contribute when they understand their role in the study and its benefits.

After visiting places of business, I sent a letter of solicitation to a confirmed
business mailing address and participant's email address (see Appendix B). I asked
participants if they would participate in my study with a letter of solicitation to each
participant. I mailed the letter via the United States Postal Service (USPS). I also emailed
participants a consent form (Appendix E) from my Walden University email address. I
asked that all potential participants send me their desire to participate through my Walden
University email address. I also sent each participant a confidentiality agreement
(Appendix C) via USPS which contained a self-addressed stamped envelope to mail the
form back to me. I also asked participants to reply with “I consent” electronically via email
upon receipt of the consent form (Appendix E). The two options provided flexibility for
small business leaders.
One week after sending out the informed consent form (Appendix E) and
confidentiality agreement (Appendix C), I followed up with each small business leader via
phone and email to confirm receipt of a hard copy and an electronic copy of the forms. The
five small business leaders reviewed the study's nature and reason for the arrangements
with me. I also answered any questions that participants had during the phone call. I offered
to pick up the letter if they preferred to sign the hardcopy, remind them to use the self-
addressed stamped envelope, or electronically sign the email attachment with “I consent.”
I found it essential to establish rapport with participants so they were willing to
participate in my study. McGrath et al. (2019) stated that building rapport and establishing
comfortable interactions in the qualitative interview should be done well before the

interview. The in-person meeting, letters, emails, and follow-up phone calls established
rapport and allowed me to build trust between the participants and me. According to
Stühlinger and Hackl (2014), participants will become trusting and confident in the
research by building a relationship at the start of the study. Participants may often share
detailed and personal information; therefore, establishing trust between the researcher and
participant is vital from the beginning of the study (Olsen et al., 2016).
Building a trusting relationship encourages open participation with the participants
for this study. If the participant's identity remains confidential throughout the review, trust
may strengthen between the researcher and the participant. Encouraging participants to
cooperate and considering trustworthiness as a priority while staying ethical at this study
stage helped the researcher gain access to potential participants (Marshall & Rossman,
2016).
Transparency by the researcher further leads to a more accessible and valuable
interview activity and willingness to participate (Stühlinger & Hackl, 2014). I established
a working relationship with participants by providing a clear and detailed background, the
study's benefits and risks of their participation, and reviewed the consent form (Appendix
E) and confidentiality agreements (Appendix C). I also ensured that each participant
understood and thoroughly knew the study's activities before becoming a participant.
Small business leaders were my study participants. They are the policy and
decision-makers for the business who possess characteristics that address the overarching
research question for the study. During the data collection process, small business leaders

provided the necessary information by stating facts about their strategies for developing
and implementing internal control systems to protect business assets and profitability.
The participants' characteristics aligned with the overarching research question, so the data
I collected addresses other small business leaders in developing their internal control
systems programs.
Research Method and Design
A researcher's methodology encompasses the processes and procedures to address
an overarching question. There are three types of research methods. The research methods
are qualitative, quantitative, and mixed (Almalki, 2016; Siponen et al., 2021). The choice
of research design is dependent on the research method. I used the qualitative research
method for my study because of the exploratory nature of the research question: What
internal control system strategies did successful small business leaders use to protect
business assets and profitability? In the following paragraphs, I discuss the three different
methodologies in detail, the method for my study, my research method's appropriateness
and design, and how my research method and design affected the overall study.
Research Method
The appropriateness of qualitative, quantitative, or mixed methods depends on the
information needed to answer the research question. Qualitative researchers engage in
individual and focus group interviews, participant observations, ethnography, and several
other approaches by describing how things are (Gioia, 2019; Hamilton & Finley, 2019).
The overarching research questions I used for my study focused on small business leaders

from the Western region of the United States. Steen et al. (2018) also added that qualitative
researchers focus on participants sharing their experiences. I asked participants to share
their experience developing and implementing internal control systems and small business
leaders' strategies. Lê and Schmid (2022) added that qualitative researchers use
semistructured interviews and archival data while reflecting on familiar themes for their
research. Therefore, my participants' experiences during the individual interview made a
qualitative research method appropriate for the study.
In contrast, quantitative researchers test hypotheses to understand the relationship
between variables (Christenson & Gutierrez, 2016). I had no intention of testing a
hypothesis to understand a relationship between several variables because the study would
not engage in numerical or statistical values. According to Bristowe et al. (2015),
quantitative methods include extrapolating numeric data, quantifying, or conducting
statistical analysis. Developing statistical relationships will not address the overarching
research question for my study. Therefore, a quantitative method focusing on numerical
values was inappropriate.
The mixed-method research approach combines quantitative and qualitative
methodologies when using either method as a standalone study is insufficient to study a
research problem (Christenson & Gutierrez, 2016; Doyle et al., 2016). Although I used a
qualitative research method, I did not combine a qualitative and quantitative method
design; therefore, a mixed method was inappropriate for my study.

The choice of research method could have an impact on the research study. The
quantitative approach was inappropriate for this study because numeric and statistical data
did not address my research question. Likewise, the mixed-methods approach did not apply
to this study because the method engaged both qualitative and quantitative methods.
Furthermore, the method only addresses the qualitative approach of my study and leaves
the quantitative approach without data. The two-sided approach of the mixed method made
it inappropriate for this study. Therefore, the qualitative method was appropriate because
the method focuses on addressing the participants' experiences in developing strategies in
internal control systems.
Research Design
The research designs considered for my study included case study, phenomenology,
and ethnography. According to Yin (2018), a case study design is appropriate when the
primary research questions ask what, how, or why the researcher has little or no control
over conditions. A multiple case study research design was appropriate for my research
study. Small business leaders will use the findings and recommendations to develop and
implement internal control systems to protect small business assets and profitability. Also,
other small business leaders will use my research findings to strengthen their internal
control system strategies to deter internal criminal activity and ensure transparency in
financial reporting activities.
The researcher explored participants' lived experiences (Kruth, 2015; Marshall &
Rossman, 2016). Ellis (2016) stated that phenomenology provides an understanding of a

defined context through a researcher's lens by observing participants within their natural
settings. According to Marshall and Rossman, participants of a phenomenological study
have experienced similar experiences, which is the focus and essence of a study. The
phenomenological approach was inappropriate for this study because I reviewed
organizational strategies to develop and implement internal control systems, not the
participants' lived experiences.
The researcher addressed entire cultural groups' values, beliefs, and shared patterns
(Kruth, 2015). Marshall and Rossman (2016) stated that ethnographic researchers study
participants in social interactions and settings. Also, ethnographic researchers can immerse
themselves in culture, leading to extended periods of conducting fieldwork and increased
study costs (Bristowe et al., 2015; Marshall & Rossman, 2016; O'Byrne, 2016).
Ethnography was inappropriate for this study because I will not study cultural or social
patterns.
Data saturation is when the researcher collects data from informants so that no
further information can be collected, assuring validity and credibility by saving researchers
time and energy in collecting the same data (Mwita, 2022). Fusch and Ness (2015) stated
that validity and credibility are invalid if data saturation is unmet. After interviewing five
small business leaders who successfully developed and implemented internal control
systems strategies in the Western region of the United States, I achieved data saturation
after no new data was available.

Population and Sampling
My targeted population was small business leaders in the Western region of the
United States who had successfully used internal control system strategies to protect
business assets and profitability. Participants for my study possessed the knowledge in
developing internal control systems strategies with the following criteria: (a) five small
business leaders who have successfully operated their business in the Western region of the
United States for over 2 years, (b) five small business leaders who have successfully
developed and implemented internal control systems strategies.
According to Moser and Korstjens (2017), a sampling plan for qualitative research
describes the number of observations, interviews, focus group discussions, or necessary
cases to ensure that findings contribute rich data. I used the purposive sampling method for
my study. The sampling method aligned with the research purpose and the predetermined
target group (Marshall & Rossman, 2016; Nikolaos & Panagiotis, 2016). Purposive
sampling is a selection of participants based on the researcher's judgment about the
potential participant's ability to be informative (Moser & Korstjens, 2017). Purposive
sampling increased the likelihood of obtaining participants who qualified for my study by
selecting small business leaders who have developed and implemented internal control
systems strategies.
Gentles et al. (2016) suggested that the main objective of a systemic methods
overview on sampling is to provide a more productive and in-depth understanding of
sampling strategies, data saturation, and other methods related to qualitative research. I

solicited five small business leaders to interview to participate in this multiple-case study.
The participants for my research had the necessary experience and knowledge of internal
control systems. Data saturation is the next step, following identifying the population and
sample method for a multiple case study to be successful. Qualitative researchers use a
multiple case study design to gain compelling and robust data (Yin, 2018).
Qualitative researchers acknowledge reaching data saturation when the researcher
has exhausted all available resources for a study. However, some resources or interviews
are not indicators of data saturation but the depth of data in which enough data is present
to replicate the study in the future (Fusch & Ness, 2015). I interviewed five small business
leaders using a semistructured interview with seven open-ended questions. According to
Pourmovahed et al. (2018), a researcher meets data saturation when no new data is
available from the study participants. The interview process, transcribed interviews, and
coding validated my study’s data. The data quality ensured data saturation, and the
researcher met the study (Hancock et al., 2016). No new data ensured enough data was
collected to replicate and ensured data saturation.
The interview setting appropriate for the study was face-to-face, via
videoconferencing, or by telephone. The participants chose the interview time and venue.
Interviewees respond strongly to face-to-face interviews (Hilgert et al., 2016). The
participants answered seven open-ended questions during the semistructured interviews
and focused on internal control systems strategies. Upon receipt of IRB approval, I set up
the interviews. Data collection began when I received an “I consent” email reply from the

participant acknowledging small business leaders’ participation. According to McVey et al.
(2016), researchers should aim for balanced inner and outer listening to gain insight into
their thoughts and the participants to succeed in the interview process. I also created a
comfortable and safe environment for each interview for each participant to prevent any
unnecessary interference of video-conferencing or in-person audio-recording during
faceto-face and telephone interviews.
Ethical Research
The informed consent process was essential before the data collection process. In
qualitative studies, federal law mandates researchers to receive Institutional Review Board
(IRB) approval to communicate the study participants' risks and benefits (Figueroa, 2016).
Upon IRB approval, Figueroa advised that a researcher share the study's potential risks and
benefits with potential participants through informed consent. I used an informed consent
form (Appendix E) to ensure my compliance with applicable ethical requirements. The
form included the following information for the participant to review: (a) purpose of the
study, (b) study procedures, (c) voluntary nature of the study, (d) risks and benefits of the
study, (e) payment, (f) privacy of the participant's identity, (g) my contact information, and
(h) participants acknowledgment of participation in the study.
Participants had the option to withdraw from the study without reason. Robinson
(2014) advises on policies, procedures, and withdrawal from a study. If they wish to
withdraw from the study, I asked participants to notify me in person, by phone, or by email.
Also, the participant's identity remained anonymous upon withdrawing as a study

participant. I did not provide any incentives for participation in the study. Incentives may
significantly impact the outcome of the research study (Batorsky et al., 2016). However, I
reminded participants that participation did not provide any incentives for their
participation and was entirely voluntary. The required forms included the informed consent
(Appendix E) and confidentiality agreement (Appendix C). Before setting up and
conducting interviews with participants, I visited small businesses to ask for small business
leaders' permission and approval, ensuring their participation in the study.
The National Commission’s guidelines list the Protection of Human Subjects of
Biomedical and Behavioral Research in The Belmont Report. According to the report,
researchers should treat autonomous agents anonymously. Also, individuals with
diminished autonomy are entitled to protection (National Commission for the Protection
of Human Subjects of Biomedical and Behavioral Research, 1979). The three parts of the
report outline the importance of respect for persons, beneficence, and justice for
researchers. I ensured respect for persons by reaching out via in-person meetings, phone
conferences, email correspondence, or physical letters in the mail when making first and
subsequent contact with each participant. I assigned an anonymous letter and number
combination—also my interview protocol (see Appendix A) with the policies and
procedures of Walden University. I did this to safeguard each participant's beneficence by
protecting each participant's identity. The participants' identities remained confidential to
ensure proper protection during the study (Bromley et al., 2015; Yin, 2018). Yin also stated
that the participant's identities remained anonymous and confidential throughout the study

and were complete. Therefore, I labeled each participant as P1, P2, P3, P4, and P5 to protect
the study participants' identities.
Regarding maintaining justice, I emailed each participant an informed consent form
(Appendix E) who voluntarily participated in the study. I also ensured full disclosure about
the research study and how participants' participation impacted it. I outlined in my consent
form (Appendix E) information regarding the study's voluntary nature and how each
participant could withdraw from the study at any time without any consequence.
I stored electronic data collected on a password-protected external hard drive. I used
hardcopy documents for the study and the password-protected external hard drive in a
safety deposit box under lock and key at a local financial institution for 5 years. The safety
deposit box is secure, and access to the vault requires a biometric scan and hand and facial
recognition. Security was vital in protecting participants' identities and sensitive
information connected to the study. After 5 years, I will destroy all electronic data and
hardcopy documents with a local shredding agency to protect participants' confidentiality.
I included Walden University's Institutional Review Board (IRB) approval number 09-21-
22-0737476; the study's expiration date will be September 20,
2023.
Data Collection Instruments
I served as the primary data collection instrument as the researcher for the study.
According to Yin (2018), the researcher serves as a qualitative case study's primary data
collection instrument. The findings and recommendations from my study explored internal

control system strategies small business leaders use to protect business assets and
profitability. I used semistructured interviews to collect data by engaging five small
business leaders in the Western region of the United States.
Semistructured interviews allowed the researcher to ask follow-up questions to
clarify interviewee responses (Bryman, 2012). After I received a signed or electronic
consent confirming small business leaders’ participation with “I consent” of the informed
consent (Appendix E) and confidentiality agreements (Appendix C), I set up my interviews.
Hardcopy or electronically signed forms were sufficient to confirm participant consent. I
set up the date and time of the interview with each participant. I used seven open-ended
interview questions addressing small business leaders' strategies for developing internal
control systems to protect business assets and profitability.
In addition to interviews, I used supplemental resources. I reviewed audio-video
recordings, archival records comprising written internal control systems procedures,
business plans, standards of procedures manuals, financial reporting records, and other
relevant internal documents and interview transcripts as primary data sources. Berazneva
(2014) stated that audio recordings ensure the consistency and quality of the data collected.
Also, Bristowe et al. (2015) stated that data analysis sources are verbatim interview
transcripts and fieldwork notes.
I offered three format options for the interview. I followed an interview protocol
and questions (see Appendix A) to provide consistency for each participant interview.

Interview protocols ensured the case study's process (Benia et al., 2015; Yin, 2018).
According to Heath et al. (2018), flexibility in participating in qualitative research may
improve participant access to research, recruitment, and response rate. The participants
chose between a face-to-face, video-conferencing, or telephone interview format. The
interviews lasted no more than 75 minutes. Face-to-face and video-conferencing interviews
allowed the researcher to build trust through rapport with participants and increase the data
quality. In contrast, telephone interviews may provide social desirability bias (Nandi &
Platt, 2017).
The advantage of face-to-face, telephone, and video conferencing interviews was
that participants chose the option that fits their schedules and gathered data for the study.
However, according to Zhang et al. (2017), telephone interviews provide participant
openness when responding to questions when the interviewer is absent. However, an
increase in social desirability bias may exist. According to Bryman (2012), a researcher's
comprehensive knowledge of the topic by connecting with prior research may be a means
to mitigate bias to curtail social desirability bias.
The interviews were audio-recorded, if in-person, or video-recorded via a
videoconferencing tool like Zoom, Microsoft Teams, Skype, or software to ensure the
interviews are quality when under review. I also took detailed notes and observed the
participant's body language, the intonation of the interviewee's voice, and breaks in
speaking when interviewees responded to my interview questions. In-person and
videoconferencing interviews were helpful in post-interview review and transcription.

Interviews that use in-person or video recordings were my primary data sources.
Before the interview, I reminded participants of the audio-video recording, and they
consented. Also, participants received copies of the signed informed consent form
(Appendix E) before starting the interview to confirm their understanding of their
participation. In order to ensure rigor, qualitative researchers need to develop interview
guides (protocols), consent forms, and coding frameworks (McMullin, 2021). I used an
interview protocol (Appendix A) and questions outlining the details of each stage of the
interview process for added consistency and rigor.
I used member checking, thematic analysis, and transcript review. These different
actions enabled the data collection process's reliability and validity. Member checking
enhanced the rigor and validity of information collected during the interview process (Birt
et al., 2016; Marshall & Rossman, 2016). According to Marshall and Rossman, the
member-checking process followed: (1) the researcher reviewed and interpreted interview
transcripts; (2) summarized a brief synthesis of one-paragraph data summaries for each
interview question; (3) provided participants with a readable and preferably printed copy
of synthesized response for each interview question; (4) confirmed the accuracy of
synthesis with participants, or gathering additional input and disclosure for accurate
understanding; and finally, (5) continued the member checking process until the study
participant provided no new information.
I scheduled a post-interview meeting with each participant. The post-interview
meeting also increased the trust and rapport between the researcher and participants, thus

ensuring the continued reliability and validity of the data collection process and the data
itself. Also, the post-interview assisted me in validating the data and allowed me to ask
follow-up questions to add to the data.
Data Collection Technique
The data collection technique helped the researcher collect the necessary data for
the study participants (Yin, 2018). This study's data collection techniques included access
to semistructured interviews and archival documents. I used semistructured interviews to
collect data. Semistructured interviews allowed follow-up questions and clarifying
information on interviewees' responses (Bryman, 2012). One advantage of semistructured
interviews is that I had access to the participant who developed and implemented the
internal control systems to address my research question. The disadvantage of
semistructured interviews is the likelihood of participant and researcher bias. Qualitative
researchers must be aware of personal biases and find ways to mitigate bias by assessing
and disseminating data throughout the study (Malone et al., 2014; Stone et al., 2019). After
I received IRB approval, I conducted a practice interview with my friends and colleagues
who were not directly involved in the study. The practice uncovered unforeseen roadblocks
I worked on before the actual interviews. Also, address any challenges that I may encounter
during the actual interviews.
I followed an interview protocol and questions for each interview activity for this
case study. The interview protocol and questions introduced the study's details, seven open-
ended questions to address the overarching research question, interview wrap-up, and

scheduling a follow-up member checking session with each participant. The interview
protocol outlines the processes and procedures while keeping the researcher consistent
during the interview process (Benia et al., 2015; Yin, 2018). The advantage of an interview
protocol is that it creates a structured process, consistency of the experience for each
participant, and ease of assessing each participant in the same way, to minimize bias during
the interview process.
I used archival documents during my data collection process. Archival documents
are an advantage because I will use the information from these documents to enrich the
data from the semistructured interviews. The archival documents included company files
such as business plans, standards of procedures manuals, and written artifacts outlining
their internal control systems policies and procedures. According to Marshall and Rossman
(2016), archival documents supplement other qualitative methods further, and the
researcher will use the information from archival documents as preliminary data for the
study. Also, information was available regarding how, why, and strategies the participants
used to develop and implement internal control systems. Marshall and
Rossman stated that archival documents should be supplemented with other techniques to
corroborate the company information used for the study. Relying on only company documents
could be a disadvantage because I could not substantiate their authenticity. Therefore, I used
semistructured interviews to gain insight from small business leaders regarding their strategies
for developing and implementing internal control systems, while the archival documents

supplemented the data collected from the interviews. I combined the two strategies, which aided
in the data analysis process and strengthened the overall data for the research study.
Member checking is another process that I used in my research. According to
Marshall and Rossman, the member-checking process followed the following:
(1) The researcher reviewed and interpreted interview transcripts.
(2) Marshall and Rossman summarized a brief synthesis of one-paragraph data
summaries for each interview question.
(3) Member checking provides researchers and participants with a readable, preferably
printed, copy of the synthesized response for each interview question.
(4) Confirmed synthesis accuracy with participants or gathered additional input and
disclosure for accurate understanding.
(5) Continue the member-checking process until the study participant provides no new
information.
Member checking enhanced the rigor and validity of data collected during the
interview process (Birt et al., 2016; Marshall & Rossman, 2016). I conducted member
checking via Zoom conferencing with each study participant to discuss further their data
input. The advantage of meeting each participant post-interview also increased trust and
rapport for more data to collect for the study. Also, member checking corroborates archival
documents that I used while interpreting the interview transcribed data. The review process
was essential in confirming and validating the accuracy of the data collected.

Data Organization Technique
Data organization techniques supported my research data’s validity and reliability
for my research study. According to Yin (2018), data organization techniques are essential
for accurate analysis, review, and reporting. I created a case study database to organize and
document the data collected. During each interview, I hand-wrote notes to supplement the
audio-recording activity.
I used two primary audio-recording options. The first was a Sony – XU series digital
voice recorder with a Sony – omnidirectional condenser microphone for clear digital voice
recording and hands-free use. Also, I used a SanDisk – ultra plus 32GB
MicroSDHC memory card for storing the media. I also used a Toshiba laptop and iPhone
7 as backup recording devices for the interviews. Both devices were my personal property
and were password protected. The second option was a video-conferencing application. I
used Zoom to video and audio record interviews when an in-person option was unavailable.
The COVID-19 pandemic imposed the use of this method for the health and safety of the
researcher and participant. I also used computer-assisted qualitative analysis tools,
Microsoft Office: Word and Excel. The tools helped arrange the narrative and numeric
data separately (Yin, 2018). For example, I used Microsoft Office: Word to keep daily logs
and journals for the study.
After each interview, I used reflective journaling to identify and minimize
researcher bias that became apparent from the data collection process. I journaled before
and after each interview to capture my pre- and post-interview experiences. According to

Malone et al. (2014) and Stone et al. (2019), qualitative researchers need to be aware of
their biases and help mitigate bias through careful assessment and data dissemination
throughout the research process. The reflective journals also addressed my awareness of
impending biases post-interview. This process also complemented pre-interview exercises
of self-reflection and self-dialogue; according to Mecca et al. (2016), cognitive errors
influence decision-making. The researcher's comprehensive knowledge of the topic
connected with prior research was another means to mitigate bias (Bryman, 2012). I also
considered this study's storage and protection of sensitive data.
I added the interviews to a password-protected external hard drive and stored the
device in a locked and secured safety deposit box at a local financial institution for 5 years.
After 5 years, I will use a local shredding agency to destroy all electronic data and hardcopy
documents to protect participants' confidentiality. The 5-year requirement aligned and
adhered to Walden University's standard to protect the data's integrity, identity, and
personal information. Therefore, according to Yin (2018), the participants' identities will
remain anonymous. I labeled each participant as P1, P2, P3, P4, and P5 to ensure proper
protection during the study.
Data Analysis
I used methodological triangulation for my data analysis process. Triangulation
ensured that a case study rendered data accuracy from the participant's perspective through
multiple data sources (Denzin & Lincoln, 2017; Marshall & Rossman, 2016; Yin, 2018). I
reviewed transcripts from semistructured interviews, audio recordings, and archival

records. The archival documents I used comprised written internal control systems
procedures, business plans, standards of procedures manuals, financial reporting records,
and other relevant internal documents as primary data sources. Yin stated that
methodological triangulation used multiple sources.
Member checking and thematic analysis were part of my study's data analysis
procedures addressing the development and implementation of small businesses' internal
control systems. I used the NVivo 12 qualitative software analysis to code and validate data
for a qualitative study. Qualitative research software packages provide the following
process support (a) organizing data; (b) systematizing and analyzing data; (c) defining
codes and themes; and (d) providing a visual representation model of the data from the
research (Freitas et al., 2017). I also used Microsoft Office software programs to organize
my study's data.
The classical data analysis method utilizes computer software to sort and organize
the data during the study's analysis phase. Marshall and Rossman (2016) stated that using
multiple cases, multiple informants, and more than one data-gathering method can increase
the chances of replicating the design in another setting. Member-checking interviews
allowed me to ask the interviewees to review the transcribed material for the study's
credibility and validity. During the member-checking interview, I focused on confirming,
modifying, and verifying interview transcripts (Birt et al., 2016). According to Marshall
and Rossman, the member-checking process followed the following:
(1) The researcher reviewed and interpreted interview transcripts.

(2) Marshall and Rossman summarized a brief synthesis of one-paragraph data
summaries for each interview question.
(3) Member checking provides researchers and participants with a readable, preferably
printed, copy of the synthesized response for each interview question.
(4) Confirmed synthesis accuracy with participants or gathered additional input and
disclosure for accurate understanding.
(5) Continue the member-checking process until the study participant provides no new
information.
I conducted member checking either in-person, over the phone, via a
videoconferencing application, or via email with each study participant to discuss further
their data input. Meeting each participant post-interview increased trust and rapport for
more data to collect for the study. Fusch and Ness (2015) also added that additional coding
would be necessary for the study if new data emerged during the member-checking
interview. I provided the small business owners with copies of the transcripts to review
during the member-checking interview activity.
I also used thematic analysis to further find patterns and themes from the transcribed
semistructured interview to strengthen the data's reliability and validity. Yin (2018)
suggested that researchers use coding to uncover themes and patterns from a study's data.
I transcribed each interview, reviewed the synthesized data during the member-checking
process, and reviewed any similarities and differences. I also determined themes from each
participant's responses during the interview. The process ensured that critical themes from

my data analysis correlated with my literature to corroborate my findings. Crowe et al.
(2015) stated that qualitative research methods understand meanings and experiences with
thematic analysis.
Crowe et al. (2015) and Marshall and Rossman (2016) stated the use of Thematic
analysis to interpret qualitative data and find patterns in the meaning of the data collected
(Crowe et al., 2015; Marshall & Rossman, 2016). Braun and Clarke (2006) outlined six
phases of thematic analysis as follows (a) familiarization with the data, (b) generating
initial coding, (c) searching for themes, (d) reviewing themes, (e) defining and naming
themes, and (f) producing the report from the data analysis. I correlated the key themes and
results to align with the literature and conceptual framework throughout the study by cross-
referencing the interview data and member-checking process. Organizing themes focusing
on the conceptual framework increased the study's reliability, credibility, and validity. I
added new research when it became relevant to the literature review to maintain the study's
consistency and alignment with the conceptual framework. My data collection instruments
included the following (a) interview protocol and questions (see appendix A), (b)
transcribed interviews and (c) thematic analysis in the appendices and the table of contents
of the study.
Reliability and Validity
In a qualitative research study, reliability and validity are the foundation of a
research study. Lincoln and Guba’s (1985) criteria discussed dependability, credibility,

transferability, and confirmability. The following sections discussed reliability and validity
and how each related to the research study.
Reliability
Reliability depends on a researcher's ability to use various processes and procedures
effectively to ensure a qualitative study's rigor. At the same time, trustworthiness describes
the reliability of a qualitative study. I used member checking, methodological triangulation,
interview protocol, and a case study database to enhance the trustworthiness and reliability
of this study. Member-checking interviews can support the dependability of a study.
According to Birt et al. (2016) and Marshall and Rossman (2016), member checking
enhances the interview process's rigor. According to Marshall and Rossman, the member-
checking process followed the following:
(1) The researcher reviewed and interpreted interview transcripts.
(2) Marshall and Rossman summarized a brief synthesis of one-paragraph data
summaries for each interview question.
(3) Member checking provides researchers and participants with a readable, preferably
printed, copy of the synthesized response for each interview question.
(4) Confirmed synthesis accuracy with participants or gathered additional input and
disclosure for accurate understanding.
(5) Continue the member-checking process until the study participant provides no new
information.

Denzin and Lincoln (2017) stated that triangulation could ensure a case study is
accurate when a researcher uses several data sources. I will use methodological
triangulation using various sources, including written internal control systems procedures,
business plans, standards of procedures manuals, financial reporting records, and other
relevant internal documents and interview transcripts as primary data sources. I will also
use an interview protocol for consistency with each interview and benefit me by lessening
my biases during the interview stage of the research study. According to Benia et al. (2015)
and Yin (2018), interview protocols help researchers develop procedures and consistency
for the interview process. Also, interview protocols lessened my bias during the interview
phase of the study.
Validity
My trustworthiness addressed the study's credibility, transferability, confirmability,
and data saturation. Credibility is believability and accuracy based on the research process
(Hays et al., 2016). The researcher's member checking, methodological triangulation,
interview protocol, and case study database can provide a qualitative research study
(Marshall & Rossman, 2016; Yin, 2018). Member checking enhances the interview
process's rigor and validity and helps with data saturation for a qualitative study (Birt et al.,
2016; Marshall & Rossman, 2016). I used the process of member-checking interviews to
confirm the information during the initial interview. I also confirmed the study's data by
cross-referencing business documents from the initial interviews, member-checking

interviews, methodological triangulation, personal notes, and reflective journaling
activities.
Transferability enables another researcher to replicate a study like the original study
(Hays et al., 2016). The data collection and analysis provide details for the different parts
of the study, from instruments, population, and methods for replicating a similar study.
Future researchers' tasks are the main idea addressing transferability for the study (Fusch
& Ness, 2015; Marshall & Rossman, 2016). Future researchers can use the research
findings and recommendations to replicate future studies. According to K. Moon et al.
(2016), transferability can be critical in applying research findings. Developing strategies
may depend on applying the data, conclusions, and recommendations from a single or
multiple case study design.
Confirmability is the accuracy of the data free of researcher bias (Hays et al.,
2016). NVivo 12 qualitative software analysis to code data and mitigate researcher bias.
Yin (2018) stated that reliability reduces errors and biases in a study. V. Braun and Clarke
(2006) outlined six phases of thematic analysis as follows (a) familiarization with the data,
(b) generating initial coding, (c) searching for themes, (d) reviewing themes, (e) defining
and naming themes, and (f) producing the report from the data analysis. I correlated the
key themes and results with the literature and conceptual framework throughout the study
by cross-referencing the data from interviews and member-checking interviews.
Data saturation is when the researcher exhausts the resources to replicate the study
in the future (Fusch & Ness, 2015; Hancock et al., 2016). Fusch and Ness say failure to

reach data saturation can negatively impact the study's validity. I ensured data saturation
by utilizing semistructured interviews with small business leaders structured with open-
ended questions until study participants provided no new data. According to Pourmovahed
et al. (2018), a researcher meets data saturation when no new data is available from the
study participants. The interviews, member checking, transcripts, business documents, and
coding validated the data and were sufficient for replication and data saturation.
Transition and Summary
Section 1 of this study included the problem statement, purpose statement, nature
of the study, and the rationale for choosing the qualitative research method and multiple
case study design. Section 1 also contained the overarching research question and interview
questions; details of the COSO framework; and the study's assumptions, limitations, and
delimitations. In Section 1, I reviewed the professional and academic literature on critical
analysis and synthesis to develop and apply internal control systems strategies for small
businesses.
I presented a comprehensive account of the qualitative research study process and
the foundation for a qualitative methodology and case study in Section 2. I restated the
purpose statement and explained the researcher's roles, participants, population, and
sampling group that align with the research study. Section 2 included ethics and the
mechanisms to collect, organize, and analyze the data from interviews conducted during
data collection. I presented the significance of reliability and validity in Section 2 of my
study.

In Section 3, I presented the findings and recommendations from the data collected
from semistructured interviews with five small business leaders for the qualitative multiple
case study research. I used seven interview questions for participants during the interview
process. I comprehensively assessed the data collected during the interviews, including
member checking, methodological triangulation, and business documents. Also, I coded
the data and developed themes that further supported and addressed my research question.
Moreover, I concluded future studies' reflections and recommendations in Section 3. The
study results may positively impact small business sustainability, asset protection, and
profits.

Section 3: Application to Professional Practice and Implications for Change
Introduction
The purpose of this qualitative multiple-case study was to explore successful
internal control system strategies that small business leaders use to protect business assets
and profitability. I conducted five semistructured interviews and collected data from small
business leaders in the Western region of the United States with 8 years of experience and
knowledge in developing and implementing strategies for internal control systems. I used
small business documents, including business plans, financial statements, standards of
procedures manuals, organizational charts, employee handbooks, employee hiring
procedures, interview protocols, and internal control systems strategies manuals to enrich
the data collected via semistructured interviews. I also reviewed the small businesses
website for information regarding safeguarding and protecting client-sensitive information.
I used thematic analysis, member checking, methodological triangulation, and
NVivo 12 analysis software. I transcribed and coded the audio interviews and identified
four themes: (a) internal control systems and procedures, (b) benefits of internal control
systems, (c) challenges of developing internal control systems strategies, and (d) internal
and external data, communication, and assessment.
In the remaining paragraphs, I presented information regarding the presentation of
findings, application to professional practice, social change implications, recommendations
for action and research, and my reflections and conclusion of my study.

The findings from this study showed strategies that small business leaders used to develop
and implement their internal control system strategies.
Presentation of the Findings
The overarching research question for this study was: What internal control system
strategies do small business leaders use to successfully protect business assets and
profitability? Owusu-Ansah (2019) stated that internal control systems are a significant
part of an organization's governance, management, and other areas of personnel provided
that reasonable assurance of achieving an entity’s objectives regarding financial reporting,
effectiveness and efficiencies of operations, and compliance with applicable laws and
regulations. I used the interview questions to explore strategies small business leaders used
to develop internal control systems, and they aided me in analyzing and coding the data for
my study.
I interviewed five small business leaders of privately owned small businesses. I
used semistructured interviews with open-ended questions. Due to the COVID-19
pandemic, participants opted for videoconference meetings via the Zoom
videoconferencing application. My primary data came from well-established small
business leaders, each with over 8 years of business experience and knowledge in business
and developing strategies for internal control systems. The data from each participant were
adequate and accurate and outlined in detail for this part of my study, which addressed the
interview and overarching research questions. I assigned alphanumeric codes to each

participant as P1, P2, P3, P4, and P5 to protect the participants' identities throughout the
study.
Based on each participant's responses during the semistructured interview, I
identified four themes: (a) internal control systems and procedures, (b) benefits of internal
control systems, (c) challenges of developing internal control systems strategies, and (d)
internal and external data, communication and assessment. The interview contained seven
open-ended questions. I used the Zoom video-conferencing application to capture video
and audio recordings of our discussion, which lasted no more than 75 minutes. To ensure
consistency for each interview, I used an interview protocol (Appendix A) to keep me on
track. The interview protocol outlined the details of each stage of the interview process. I
used the same process for each interview for added consistency and rigor. Throughout the
interviews, I also asked follow-up questions for clarification on my part of that of part of
the participant. I ensured data saturation when the study participants provided no new data.
The NVivo 12 software transcribed the audio-video recording at the end of each interview
into a Word document. I used the transcribed material during my member-checking meeting
to clarify information and collect any other relevant data that the participant did not share
during our initial interview. I also used the NVivo 12 software to analyze the data and
organize the information into themes.
In addition to interviews, I used supplemental resources. I reviewed audio-video
recordings, archival records comprising written internal control systems procedures,
business plans, standards of procedures manuals, financial reporting records, and other

relevant internal documents and interview transcripts as primary data sources. The findings
from this study suggest that small business leaders in the Western region of the United
States use comparable internal control system strategies to protect small business assets
and profitability.
The COSO framework was the conceptual framework for this qualitative multiplecase
study. Organizational leaders used the framework with reasonable assurance regarding
achieving the organization's objectives. Small business leaders used the framework to
develop their internal control strategies to achieve their objectives and safeguard assets and
profitability. Four themes become apparent after analyzing the data. The themes in Figure
3 represent the internal control systems and procedures, benefits of internal control
systems, challenges of developing internal control systems strategies, internal and external
data, communication, and assessment. Each theme aligned with the five main parts of the
COSO framework, ensuring the relevancy to small business leaders' strategies in
developing their internal control systems are: (a) control environment, (b) risk assessment,
(c) control activities, (d) information and communication, and (e) monitoring.
Figure 3
Emerging Themes
Theme 1: Internal Control Systems and Procedures
Internal control systems and procedures were the first identified theme from the
interviews. Internal control systems help with managerial decisions regarding the business
plan, the organization, and organizational structure, and the delegation of duties to
structures and individuals involved in the organization's activities (Tamas et al., 2022).
There are also seven internal control procedures: separation of duties, access controls,
physical audits, standardized financial documents, periodic trial balances, periodic
reconciliation, and approval authority. Each participant shared that understanding the
importance of internal control systems and their procedures helped them develop strategies
for their business. Table 2 represents Interview Questions 1, 2, and 6. After analyzing the
data from these interview questions, member checking, and methodological triangulation,
I Contr Sys
Procedur
B of Int
C Sy
C of Developi
I Contr Sys
S
I and External
D , Communication
Assessment
Emerging
Themes

I used thematic analysis to indicate the first emerging theme. Table 2 also represents the
number of times each participant referenced the first emerging theme during their
interviews.
P1 stated, “Internal control systems are important to have in place because it
provides me with a process and procedure to monitor what is happening within my
business.” P2 stated, “Internal control systems showed me where we needed to change or
pivot from our current process.” P2 stated, "At the start of business, I separated duties
between the manager and lead server and the rest of my employees with financial control
with my manager and lead server to minimize loss or error.” P3 stated,
As a small business owner, you have many things on your plate at any given time,
so in order to mitigate financial losses or errors on my part and my employees, we set up a
system to monitor what is going on within all facets of my business. P3 further added, “we
outsource our financial bookkeeping to my accountant, and I am very involved in the
process of understanding my financial outlook.” P4 stated, I developed internal controls
on paper when I started my business to keep track of transactions, financial statements, and
waste; as the years passed, I am using a software program to track what I did in the past on
paper.
P5 stated,
I used the same processes of internal control systems with this business as I do with
my other one, but the only difference is this business has more employees and
moving parts that I need to ensure I keep a tight rein all aspects of the business.
All participants stressed the importance of developing and implementing an internal
control system. They all agreed that because they are in charge of all facets of the business,
having processes and procedures in place can mitigate any unforeseen risk or loss to their
business. According to Kabuye et al. (2019), internal control systems consist of all the
measures taken by the organization to protect against waste, fraud, and inefficiency; ensure
accuracy and reliability of accounting and operations; comply with organizational policies;
and evaluate the level of performance in all units of the organization. Reviewing their
business plans, internal control systems procedure manual, and employee handbook
outlined the strategies for internal control, separation of duties, and employees
understanding their responsibilities within the business. The company documents also
showed alignment with the framework's five main areas, further validating and supporting
the literature and the importance of internal control systems.
Table 2
Internal Control Systems and Procedures
Interview
Total
Questions
References
Participant 1 1,2,6
15
Participant 2 1,2,6
30
Participant 3 1,2,6
21
Participant 4 1,2,6
24
Participant 5 1,2,6
16
Theme 2: Benefits of Internal Control Systems
The benefits of internal control systems were the second identified theme from the
participants’ responses. Internal control systems provide management to keep track of

profitability and mission achievement, minimize risk and management respond quickly to
an issue; ensure efficiency and effectiveness, reduce risk of loss of assets; help establish
confidence in financial statements and overall compliance with applicable rules and
regulations (Boghean & Chihai, 2021). The benefits provide management with specific
areas to focus on so the organization can experience the benefit of an internal control
system. During the interviews, participants shared with me their internal control systems
strategies and how the business benefitted from having a system like this in place. Table 3
represents Interview Questions 3 and 7. After analyzing the data from these interview
questions, member checking, and methodological triangulation, I used thematic analysis to
designate the second emerging theme. Table 3 also represents the number of times each
participant referenced the second emerging theme during their interviews.
P1 stated,
We found the benefits of internal controls were the business passed its break-even
point, which meant we experienced a return on our investment in the first year of
opening. We also experienced return customers month after month, and the increase
in the volume of new customers leading up to the pandemic and after
COVID guidelines were relaxed was due to having a system of internal controls.
P2 said,
The benefit of having a system of internal controls was how we kept track of our
daily accounting, mainly on employee salaries, food costs, food waste, financial
forecasting, and our marketing efforts. Also, we set up a training program for our
employees in all capacities to understand the daily front and back of the house

operations and the policies and procedures required of each employee to fulfill the
job.
P3 stated,
I needed first to understand internal control systems, which I shared with you
earlier. Then, I asked myself how I would benefit from such a system. At the same
time, I wanted to be involved in everything. As we expanded the business, I better
understood human resources, hiring contractors, working with other business
owners, hiring employees, accounting, finance, marketing, etc. Developing and
implementing an internal control systems program made keeping track of my
profits and losses easier as the years went by.
P4 and P5 summed it up, and both stated,
Business 1 and 2 benefited because I could not be in two places at once, so having
written policies, procedures, and processes and effectively communicating
expectations to employees made it easy for me. Also, with the help of financial
software, I could track the incoming and outgoing of monies with the help of my
management staff.
Each of the participants shared the benefits that applied to their specific needs.
They also added the importance of communicating first-hand the expectations of the
business owners and management staff via written policies and during staff meetings. I
reviewed each small business leader’s version of the written standards of procedures
manual, internal control system policies, and financial statements to confirm increases in
sales. I also reviewed documents that noted employees in charge of different areas of the
business, their job descriptions, and specifications to ensure those employees were
performing their duties. If any issues regarding accounting discrepancies were present in a
report, the issue was quickly addressed, discussed, and fixes made so that the issue would
not occur again. Participants shared that compliance with applicable accounting and
financial reporting laws was an essential benefit of internal control systems. The business
owners were able to make sure their overall reporting of financial data were accurate so
they could track profits and allocate capital appropriately, mainly in marketing and product
development, to increase their overall business sales in any given month.
Table 3
Benefits of Internal Control Systems
Interview
Total
Questions
References
Participant 1 3,7
20
Participant 2 3,7
25
Participant 3 3,7
27
Participant 4 3,7
30
Participant 5 3,7
19
Theme 3: Challenges of Internal Control Systems
The third theme that emerged from the interviews was internal control system
challenges. Internal control systems benefit public and private organizations because they
provide organizational leadership with a detailed framework for developing, implementing,
and assessing its effectiveness on all levels of the organization. Challenges to developing
strategies for internal control systems could be a lack of knowledge of internal controls, the

cost and time required for developing and implementing a system, consistently
communicating the importance of a system of internal controls between management and
subordinates, and assessing its reporting effectiveness in a small business setting. A
material weakness is a deficiency in internal control over financial reporting, which may
cause a delay in detecting the company’s financial misstatement (Nasir et al., 2021). Small
businesses may not have the accounting and financial capacity to discover misstatements
or knowledge of best practices in accounting and finance. Also, small business leaders may
not understand how to build out robust policies and procedures to address internal control
system issues and identify potential threats to the small business.
P1 stated,
The challenge at first was getting on the same page with the key players of the
business. Also, knowing where to start, even to set up any system, policies, or
procedures. As a new business owner, I had many questions that needed to be
answered. Regarding internal control systems, the main challenge was where to
start.
P2 stated,
We started with all new employees; young employees (high school and college students)
made it easier to train to understand the goals and expectations of the business. However,
at the same time, I was finalizing my policies and procedures for my understanding so I
could better communicate them to my employees was challenging. Regarding internal
control systems, I adopted strategies from my old job and used what applied to my

business. In the end, I developed a system of internal controls that you reviewed in our
standards of procedures manual and employee handbook.
P3 stated,
The first challenge was building this business, and I had to learn the business from
the inside out. Internal control systems were on the radar, and looking back on our
accomplishments, I am happy we put a system in place to track the accounting and
financial parts of the business. Also, accuracy is important to me, so knowing the
financial welfare of my business helped me make informed decisions when the time
came.
P4 stated, “I have owned many successful businesses in the past, and developing systems
was something I was familiar with from the start. Internal controls were a priority because
of the activities involved in business 1.”
P5 stated,
Business 2, on the other hand, was a larger business with many moving parts.
Internal control systems were a key indicator of where my money was being spent
and catch any monetary discrepancies immediately to avoid further issues in the
long run.
Each small business owner shared many challenges in starting a business. However,
one thing remained certain: the challenge was communicating and keeping track of the
different areas of the business. Consistency is vital in overcoming the challenges of setting
up, implementing, and addressing issues that may affect the business. For example, owner
and employee learning curves differ, and consistently communicating expectations will
enhance the employee experience, leading to their and the business's success. The training
process was another means of maintaining business success and employee accountability
for their contributions to the business. The small business leaders all shared that leading
with integrity is crucial in maintaining internal control systems. I referred to training
manuals, business plans, income statements, and standards of procedures manuals. I cross-
referenced the material used with the data from my interviews and literature review to
confirm the challenges organizational leaders face in developing internal control systems
strategies.
Table 4
Challenges of Internal Control Systems
Interview
Total
Questions
References
Participant 1 1,4,5
15
Participant 2 1,4,5
25
Participant 3 1,4,5
19
Participant 4 1,4,5
31
Participant 5 1,4,5
27
Theme 4: Internal and External Data, Communication, and Assessment The
fourth emerging theme was internal and external data, communication, and assessment.
Communication is vital in ensuring an organization's internal control systems program is
effective when managers can determine strengths, weaknesses, opportunities, and threats
to the internal and external organizational environment. Acquiring the necessary internal
and external data to assess the effectiveness of the organization's internal control systems

is a critical factor in assisting management in making decisions and allocating resources.
The COSO framework provides a detailed map of internal controls. The five principles
covered by the COSO framework are the control environment, risk assessment, control
activities, information and communication, monitoring activities concerning organizational
operations, reporting, and compliance with applicable laws and ordinances. The practical
business practice relies on the areas outlined in the COSO framework to mitigate potential
risk, safeguard assets, and maintain integrity with the reporting functions of the
organization.
P1 stated, “There is much communication between myself and my management
team, my accountant and financial consultant.” P1 added, “The data from the different
software applications we use help us determine our next move and see if any discrepancies
are present.” P1 stated, “We also rely on historical data to assess the effectiveness of our
systems and procedures.” P2 stated, “Standards of procedures, daily and past experiences,
and historical data will help us determine our business practices.” P2 added, “I created
consistency through the information on a daily and by communicating my expectations
from each employee as well as my expectations for the team.” P3 stated, “I receive my data
from software applications and outsourced accounting activities to develop strategies, for
example, marketing, then assess the necessary statements to determine the most need in
my business.” P3 added, “I communicate with my employees daily regarding expectations
and job responsibilities.” P3 stated,
In addition to daily communication, upon hiring a new employee, I provide them
with the tools necessary to be successful, for example, employee handbook and,
depending on their role within the business, standards of procedures manuals, and
other pertinent information that applies to their role.
P4 and P5 stated, “I collect historical data and review the information to assess better where
I am presently at and determine where I want to go.” P4 and P5 added, “I take that data I
gathered from the different software programs to make a better, more educated decision.”
P5 stated, “I use internal control systems for risk mitigation planning, minimizing potential
losses by going through the data monthly to identify any discrepancies.”
Each participant agreed that relying on historical data was critical in identifying
discrepancies in reporting to pivot internal and external activities. Also, communication
was another critical factor in maintaining consistency with new hires and existing
employees. Participants relied on their internal control systems to make informed
operations, reporting, and compliance decisions. The COSO framework in Figure 1 of the
literature review represents the strategies used in each participant's place of business. The
data from the literature review indicates that the participants have reliable strategies for
other small businesses to develop their internal control systems.
Table 5
Internal and External Data, Communication, and Assessment
Interview
Total
Questions
References
Participant 1 1,2,7
16
Participant 2 1,2,7
22
Participant 3 1,2,7
27
Participant 4 1,2,7
21
Participant 5 1,2,7
19
Applications to Professional Practice
The applicability of the findings from this study is to aid small business leaders
with detailed strategies to develop, implement, and assess internal control systems within
their businesses. The general business problem stated that small business leaders were
experiencing a loss of business assets or profitability. At the same time, the specific
business problem was that some small business leaders lacked internal control system
strategies to protect business assets or profitability. The results of the study provided small
business leaders with information to (a) understand internal control systems, (b) the
benefits of developing internal control systems, and (c) strategies to develop effective
internal control systems.
The data I collected and the themes presented in my study supported preliminary
findings from my literature review. A finding from my study was for small business leaders
to understand internal control systems. According to Zheng and Liu (2021), the internal
control system is an internal self-management method formulated by managers to ensure
the reliability and correctness of internal financial information to achieve business goals.
Small business leaders develop, implement, communicate, monitor, and assess a small
business’s operational and functional areas with sound internal control systems. An
adequate system of internal controls is also a reliable mechanism to mitigate business risk
and respond immediately to internal and external issues. Small business leaders rely on
their employees to conduct their daily functions. Tahriri and Hasanzadeh (2022) stated that

internal control systems need the supervision and attention of the company’s management
and leadership. With a built-in system of internal controls, small business leaders can
oversee and respond to issues that arise effectively and efficiently. Managers can also use
the results of internal control systems in long-term strategic planning.
The second key finding from my study was the benefits of an internal control
systems program. Mutnuru (2016) states that small organizations need internal controls to
maintain a high-level assurance to help achieve operational, financial reporting, and
compliance objectives. These three key objectives show the benefits of internal control
systems. Also, internal control systems safeguard small business leaders' assets and
promote operational efficiencies (Frazer, 2016; Park et al., 2021). The specific areas of
increased efficiencies are in accounting and finance controls and other areas such as
management, inventory, cash, purchase, and sales and budget. Weaknesses or lack of
internal control systems can cause distrust and damage a business’s reputation. Internal and
external stakeholders are also affected because the business is left open to the possibility
of financial fraud and unethical activities. The most important driver is the presence of
internal control systems; small business leaders need to understand the importance of
internal control systems, the potential downside of a weak or absence of one, and how it
will benefit both internal and external stakeholders in the short and long term.
The final key finding from my study was the strategies small business leaders used
to develop internal control systems. My study participants provided in-depth knowledge of
their internal control systems strategies. Through trial and error, each shared the challenges

of developing a system of internal control to align with their current business conditions. A
significant requirement for the control system is to be costeffective, whereas the cost to
implement should not exceed the benefits of having a control system. Bilgi et al. (2017)
stated that an essential requirement for the control system is to be cost-effective, whereas
the cost to implement should not exceed the benefits of having a control system. All
employees are responsible for carrying out the system of internal controls. My study
participants shared the benefits of having a mechanism to assist in planning daily, weekly,
monthly, and annual activities to respond to the business’s needs. Therefore, strategies
aligned with developing a robust internal control systems program for a small business are
in the control environment, risk assessment, control activities, communication and
information, and monitoring. The COSO framework’s five main areas and the associated
seventeen principles are a detailed guide for small business leaders to develop or strengthen
their existing internal control system.
Implications for Social Change
The results from this study may contribute to positive social change by promoting
enterprises' sustainable development through the strategies that small business leaders use
to develop internal control systems to protect business assets and profitability. Small
business leaders may use strategies in implementing internal control systems and
developing or enhancing current policies and procedures regarding operations, reporting,
and compliance efforts. The strategies are interchangeable and may apply to different types
of businesses, such as restaurants, retail shops, and boutiques. The themes identified in this

study will allow small business leaders to mitigate potential risks, identify and respond
quickly to risk-averse issues, and communicate within the organization consistently and
effectively while maintaining financial statement compliance. The factors mentioned may
contribute to increased commerce and employment opportunities, decreasing the
unemployment rate, and decreasing fraudulent activity, which may increase productivity
and profits for small businesses, creating a positive social change.
Recommendations for Action
Small business leaders continue to provide employment opportunities and
commerce and support larger public organizations in different capacities. Small business
leaders must be aware of protecting their assets and profit margins and develop strategies
to protect them. I recommend four actional items based on the results of my study, as
outlined in Figure 4. The four recommendations were: Review the COSO framework's five
components and seventeen principles, review internal and external communications
strategies, review current software applications concerning accounting and financial
management systems, and review current business practices, processes, and procedures.
Small business leaders can use internal control systems to communicate, assess, and
develop processes and procedures to increase business assets and profits.
The first recommendation is for small business leaders to review the COSO
framework's five components and seventeen principles. The five components of the COSO
framework include the control environment, risk assessment, control activities, information
and communication, and monitoring activities. The five components focus on a small

business's operational, reporting, and compliance areas. Also, small business leaders will
use the COSO framework and the seventeen principles connected to each of the five
principles with details and actionable items to develop and implement strategies for internal
control systems. The COSO framework may contribute to small business leaders'
foundation to develop internal control systems.
The second recommendation is for small business leaders and managers to review
internal and external communications strategies. Effective communication starts from the
top and trickles down through management, subordinates, and vice versa up the
hierarchical chain. Consistent communication from small business leaders upon hire,
reinforcing expectations, and encouraging openness may garner employees who lead with
integrity. Internal and external communication requires all small business leaders,
managers, and employees an opportunity to provide necessary feedback if issues arise.
Also, training opportunities to make sure employees are on the same page allow for another
platform for communication. Empowering employees to contribute to external
communication can also lead to trust between small business leaders and employees,
further minimizing fraudulent issues. Small business leaders must consistently, clearly, and
concisely communicate messaging internally and externally so employees and customers
understand their brand.
The third recommendation is for small business leaders and, if applicable,
accountants and financial planners to review current software applications concerning
accounting and financial management systems. Small business leaders need to understand

the capabilities of accounting and financial systems used to leverage better their use for
tracking and assessing profit margins or identifying discrepancies on a statement or report.
In terms of a business having an accountant or financial planner, small business leaders
need to build a positive working relationship with them. Also, both parties must understand
each other's expectations to strengthen a working relationship. Working with these
individuals may build trust and enhance small business leaders' confidence that they do
their job with integrity and accountability.
The fourth recommendation is for small business leaders to review their current
business practices, processes, and procedures. Knowing business practices, processes, and
procedures is crucial for small business leaders to understand and plan to integrate
strategies for internal control systems. Small business leaders with a detailed account of
these areas can add the necessary information to the foundation built using the COSO
framework. Also, there may be an opportunity to add, delete, or consolidate operational
and functional practices to better align with the goals and expectations of the business.
The findings from this study are essential to small business leaders, managers,
supervisors, and subordinates within a small business. My findings will help small business
leaders understand internal control systems, the COSO framework, current policies and
procedures, business processes, and the importance of consistent and ongoing internal and
external communication. I will share my results at conferences, through peer-reviewed
journals, with small business leaders in my community, and as an opportunity to teach in
the classroom at the current university where I am employed. I would also like to bring
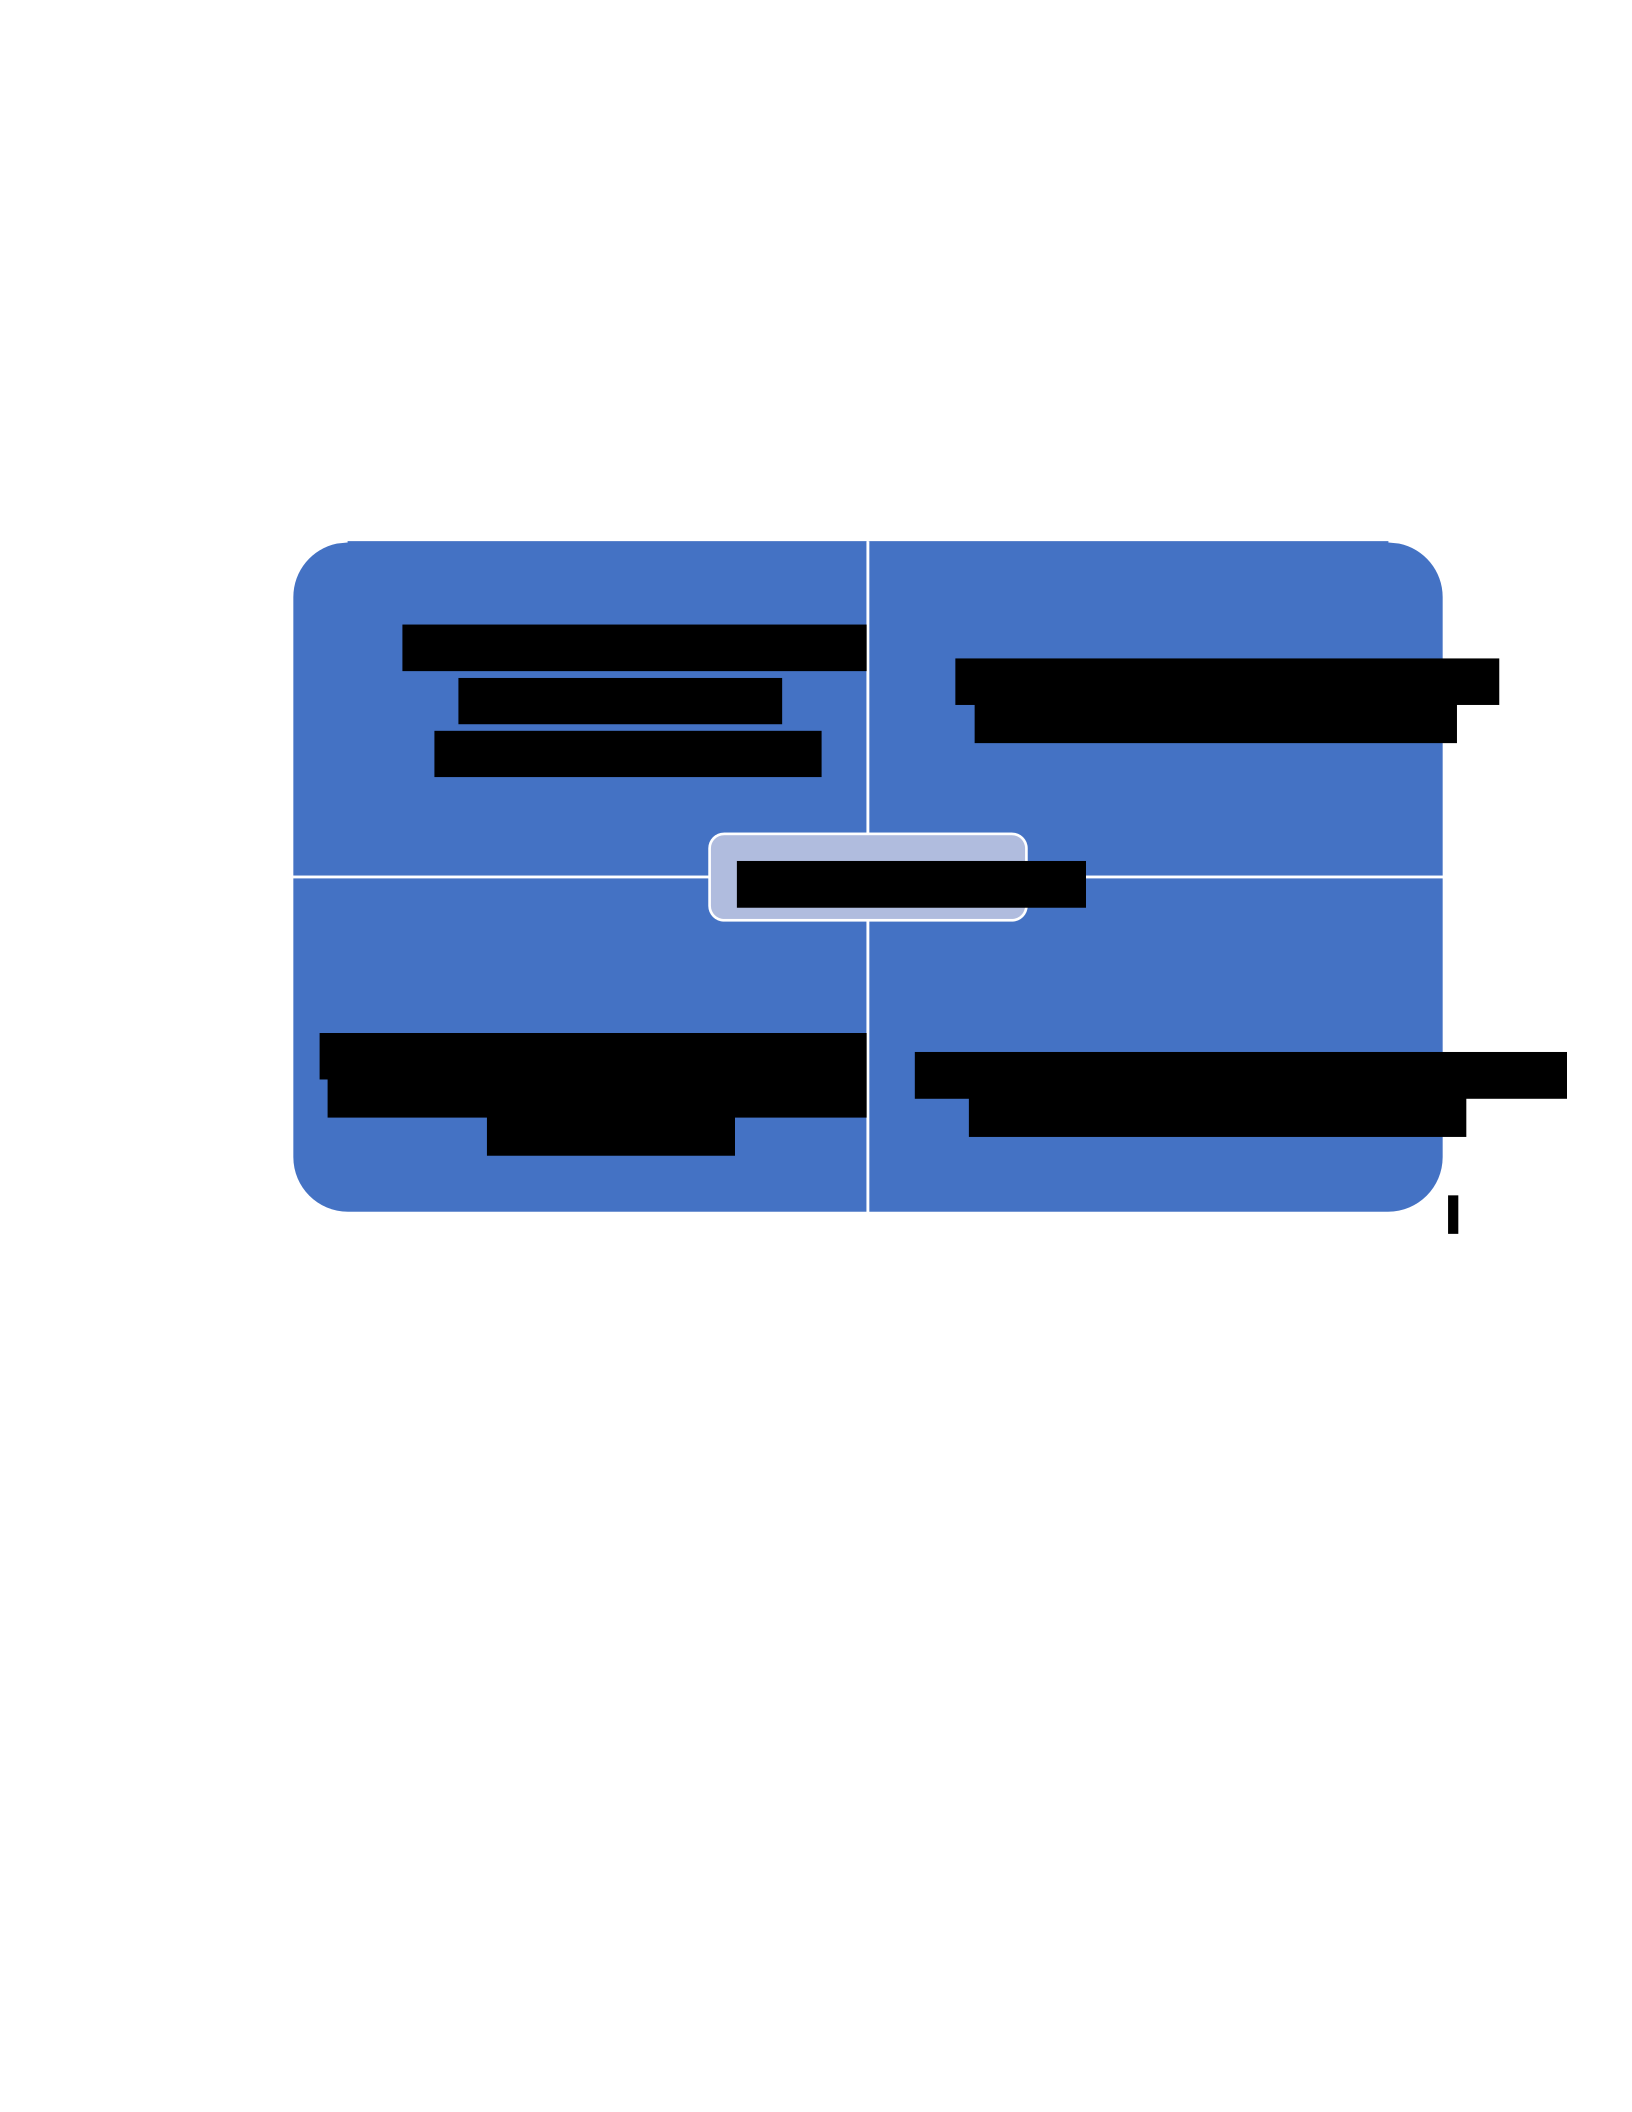
small business leaders into the classroom to work with students in developing areas of
internal control systems, risk management, and mitigation planning.
Figure 4
Recommendations for Action
Recommendations for Further Research
The purpose of this qualitative multiple-case study was to explore successful
internal control system strategies that small business leaders use to protect business assets
and profitability. I interviewed five small business leaders from the Western region of the
United States who have experience developing strategies for internal control systems. A
study area's limitations are outside the researcher's control (Helmich et al., 2015;
Theofanidis & Fountouki, 2018). A limitation of this study was the geographic region of
the study. This study was limited to a sample of participants in the Western region of the
R COSO Fr
F Components
S Principl
R internal and external
s
R current software applica
accounting and financial
R curren busines pr ,
, and procedur
Recommendations

United States. Also, the limitation of sample size and geography limited data collection
findings and established conclusions.
I recommend that researchers have a larger region of study, as my study was limited
to one region of the United States. Another recommendation is for researchers to conduct
a study with a larger pool of participants. My study consisted of five participants. The larger
region and sample size may generate more results of strategies that small business leaders
use to develop internal control systems. Another recommendation is that in addition to
conducting studies in other regions, I would compare the results of the different regions
and identify comparisons of strategies by region and even further to the types of businesses
to determine effective strategies for each business type.
Reflections
The Doctor of Business Administration degree will allow me to be a practitioner in
business academics and a positive role model for my students to aspire to complete their
college education. The second opportunity this degree will have on my professional career
is to assist organizations enduring undue distress for whatever reason and knowing
I can assist organizational leaders in resolving issues. Finally, this degree will address the
Native Hawaiian community's voice in recognizing our people’s values and the diversity
we can share with others from our ideas and culture. The beliefs and cultural values can
quickly transfer to the business and academic setting when well-planned with clearly
defined goals and manageable activities to achieve them.

This process allowed for self-reflection and how the fruits of my journey will one
day contribute to the solution facing the Native Hawaiian community. I hope my research
will benefit small businesses in Hawaii by providing small business leaders with a
framework to develop, implement, and assess internal control systems at an affordable cost.
I will continue working with small business leaders in the community. I also teach at the
University of Hawaii West Oahu as a full-time business instructor in areas covering risk
management, insurance, and marketing. The relationship built between myself and my
peers in the industry where I identified at the start of this study. I thought their information
would be false because they wanted me to complete this degree. However, during the
process and understanding first-hand their business, that notion was let go because, in the
end, the data collected aligned with my study.
Ultimately, my doctoral journey was the most challenging feat for me to endure. I
learned more about myself by navigating adversity and connecting with my chair once I
had a consistent one. I admit I probably gave up several times because a doctorate is not
for the faint of heart. I also can relate better with small business leaders now because the
information provided by my participants was deep and rich. I believe in building and
engaging relationships whenever opportunities present themselves. I have also deepened
my level of patience and understanding, and appreciation for the hard work researchers do,
especially my committee having to review and recommend changes to my work.
Whatever the future brings, I am confident that my study can help small business leaders
implement the strategies required to develop internal control systems.

Conclusion
The purpose of this qualitative multiple-case study was to explore successful
internal control system strategies that small business leaders use to protect business assets
and profitability. Small businesses provide employment opportunities and support to larger
public organizations in the U.S. Public organizations use internal control system programs
that adhere to SOX and COSO Internal Control-Integrated framework, which identifies
required internal and external auditing standards {COSO, 2017}. The converse is that
increased fraudulent activities targeting small businesses can harm commerce in any
region. Developing internal controls to counter fraudulent activities is essential to
developing and implementing reliable systems and uncovering fraudulent activity (Jachi &
Yona, 2019). Frazer (2016) pointed out that internal control systems are essential in a small
business environment to keep track of costs and overall organizational planning to
safeguard business assets. Therefore, internal control systems in the public and private
sectors are essential, especially in small businesses.
I used seven open-ended questions to explore strategies small business leaders used
to protect business assets and profitability. Also, to observe COVID-19 guidelines for social
distancing, I used the Zoom video-conferencing application to capture video and audio
recordings. To ensure consistency for each interview, I used an interview protocol
(Appendix A) detailing each stage of the interview process. I ensured data saturation when
the study participants provided no new data. I used the NVivo 12 software to transcribe the
audio-video recording at the end of each interview into a Word document. I also used

member checking and methodological triangulation, and thematic analysis during my
study. The data also came from archival records comprising written internal control systems
procedures, business plans, standards of procedures manuals, financial reporting records,
and other relevant internal documents and interview transcripts as primary data sources.
In conclusion, the four themes identified were: (a) internal control systems and
procedures, (b) benefits of internal control systems, (c) challenges of developing internal
control systems strategies, and (d) internal and external data, communication, and
assessment. The themes aligned with the five components of the COSO framework and the
overall recommendations for this study. The findings of this study’s primary purpose are
for internal controls to safeguard organizational objectives. Also, minimize risk and protect
assets, ensure records' accuracy, promote operational efficiency, and encourage adherence
to policies, rules, regulations, and laws.

