


Cybersecurity Barriers in Agriculture 4.0: A Study of Michigan Family Farms
Chapter 1: Introduction
Technology has reshaped global industries through the Industry 4.0 revolution, and Bour
et al. (2023) stress that “ongoing digitalization across all industries will revolutionize the way
critical infrastructures operate.” Industry 4.0 is a "primarily IT-driven" manufacturing system
with a cyber-physical system (CPS) merging the physical and digital worlds (Lasi & Fetke,
2014). Additionally, Industry 4.0 utilizes the Internet of Things (IoT), cloud and edge computing,
artificial intelligence (AI), machine learning (ML), data, and 5G networks (Schume, 2020). As
technology has changed industry, it has also begun shaping agriculture through the fourth
agricultural revolution, called “Agriculture 4.0” (Frankelius et al., 2017). The central tenets of
Agriculture 4.0 are technology, data, data-driven decision-making, smart and precision
agriculture, and many other tech-focused advancements within farming operations (Araújo et al.,
2021).
Automation, reliance on Information Technology (IT) systems, and data-driven
decisionmaking introduce a new type of risk to the farm: cyber risk. In January 2024, Jen
Easterly, the Director of the U.S. Cybersecurity and Infrastructure Security Agency (CISA),
highlighted that the technology base underpinning critical infrastructure is inherently insecure
and leaves our critical infrastructure vulnerable to attack (CISA, 2024). Thus, introducing
cybersecurity concepts to Michigan's family farm operators and fostering their adoption of these
practices will help ensure that their operations are secure and that farmers can prevent
cyberattacks, device failure, and loss of information to the best of their ability. Further,
increasing cybersecurity awareness will enhance the resiliency of farms.

While many of the 16 critical infrastructure sectors in the United States have focused on
implementing cybersecurity practices and training their workforce for some time (Obama, 2013),
agriculture has traditionally been less digitally connected to infrastructure than many other
sectors and has not focused on cybersecurity requirements. No longer isolated from the internet,
the U.S. Food and Agriculture (FA) Sector added smart and precision agriculture technology and
practices to move to Agriculture 4.0. Those now connected within the sector to the digital world
are thus at risk of cyberattacks or risk impacts due to the failure of their IT systems, which can
result in non-malicious impacts such as hard drive failures.
Additionally, farmers face challenges regarding cybersecurity as they may be unsure of
the cybersecurity practices and frameworks they should utilize (Syafrizal et al., 2022), even as
researchers stress that farmers should use established security frameworks (Barreto & Amaral,
2018). Farmers may not be familiar with the various aspects of technology they are trying to
secure, and they may lack knowledge of whom to ask or where to seek assistance and lack a
helpline (Pfluger, 2023). Farmers may also fail to recognize that their operation has a digital
aspect, even if they have not fully adopted Agriculture 4.0 technologies. Therefore, cybersecurity
research must focus on farm operators and understand the barriers preventing them from being
cyber-aware and secure. Focusing on the best methods and practices to reach farmers and
encouraging the adoption of cybersecurity will be essential to ensuring FA sector security and
resilience.
Chapter One highlights the background of cybersecurity applied to farming operations
and Agriculture 4.0, including the increasing levels of risk in the 2020s. This chapter also
outlines the purpose of the study and the problem statement guiding this research and addresses
the hypotheses of this research. Additionally, this chapter introduces the application of the

Technology Acceptance Model (TAM) to frame farmers' understanding of cybersecurity, its ease
of use, and perceived usefulness to inform better ways to educate farmers and overcome the
cybersecurity adoption barriers they face.
Background
Cyber-related issues continue to grow as farmers seek to increase efficiency and
overcome resource and labor scarcity. Integrating data and data-driven decision-making along
with technology and automation have become central tenants of change on the farm as operations
move towards Agriculture 4.0 (Bešić et al., 2021). At the core of Agriculture 4.0 are data and
connected IT, both in the field and the office, applied across all stages of decision-making on the
farm. While these modern systems seek to improve and enhance operations on the farm through
data-driven decision-making, they also introduce increased risk to individual farm operations as
increased technology use leads to increased cyber security vulnerabilities (Kjønås & Wangen,
2023). These vulnerabilities may be through cyberattacks, data loss, or failure of the IT systems
and devices, or possibly all three simultaneously. While not every cyber event is malicious, they
can all impact farmers similarly, as they may lose access to their critical systems or data.
Farmers' increased reliance on technology exposes them to the same longstanding risks
traditional businesses have faced for years. Modern farm equipment connected to the internet
erodes a farm's digital isolation. Additionally, as farm operations generate more significant
volumes of data, that data grows in value. However, storing it in internet-connected locations
increases its vulnerability to new risks.
In 2022, the U.S. Federal Bureau of Investigation (FBI) underscored this risk with a
Private Industry Notification (PIN). The PIN warned that farms face a growing threat of
cyberattacks timed to disrupt critical farm activities (FBI, 2022). Malicious actors may target

essential systems at specific times of the year. The PIN highlighted recent attacks: six grain
cooperatives targeted during the fall 2021 harvest and two further attacks aimed at seed and
fertilizer supplies during the 2022 planting season (FBI, 2022).
These attacks highlight the vulnerability of the FA supply chain, with potential negative
consequences for individual farms. The FBI also noted a rise in ransomware attacks across the
farm-to-table spectrum (FBI, 2022). Therefore, farmers cannot depend solely on other entities for
cybersecurity. They must actively work to secure their operations.
With the Agriculture 4.0 shift towards connected technology and data, farm operators
must adopt cybersecurity practices to protect their operations from cyberattacks, data theft, and
loss of operational capability due to IT system failure. Identifying critical farm IT infrastructure,
connected equipment, and data is crucial due to their importance to continued farm operations
and the risks associated with damage or loss of any of these farm components.
General Problem Statement
Cybersecurity is a complex and diverse concept requiring in-depth knowledge and
technical capability to implement best practices successfully and secure an IT system effectively
(CompTIA, 2021). Family farm operators encounter many issues they must be proficient in, and
cybersecurity adds another layer of knowledge that farmers must obtain. Additionally, as
technology advances and farms transition towards Agriculture 4.0 and data-driven
decisionmaking, the risks of a cyber-attack increase along with the potential for a significant
negative impact on their operation, such as the loss of critical operational data (Gupta et al.,
2020).

As the industrial sector transitioned to Industry 4.0 through the addition of IoT,
automation, big data, AI, and immutable ledgers, such as Blockchain technologies, so too has
agriculture with Agriculture 4.0 utilizing these technologies to move towards real-time farm
management with automation and data-driven decision-making (Liu et al., 2021). Introducing
new internet-connected equipment and technologies, Agricultural IoT (Ag-IoT) devices, creates
new cybersecurity dilemmas for farmers: Should farmers invest in self-education about
cybersecurity, outsource by hiring an external professional, or transition to Agriculture 4.0
without accounting for the potential risks (Kristen et al., 2021)?
Specific Problem Statement
An understanding and adoption of cybersecurity by family farm operators in Michigan is
paramount if they wish to proactively mitigate cyber risks to their IT systems and Agriculture 4.0
devices instead of working retroactively to remediate following an attack (Lauver, 2022). For
farm operators to become cyber aware and cyber secure, they must understand the concepts of
cybersecurity and how to implement a cybersecurity framework to protect their farms. Farmers
must also prioritize the time and financial investments required to ensure their operation is secure
(Drape et al., 2021). Existing cybersecurity frameworks, such as the NIST Cybersecurity
Framework, may be challenging to understand, and implementing good cybersecurity practices
and cyber hygiene or hiring an external consultant (Kristen et al., 2021) may present a significant
challenge for small farming operations. Therefore, to best educate farm operators, the
cybersecurity community must understand the existing barriers that prevent farm operators from
adopting cybersecurity practices.

Purpose of Dissertation
The quantitative study aims to identify specific barriers, such as knowledge gaps and
financial considerations, preventing Michigan family farmers from adopting cybersecurity
practices. The resulting recommendations for tailored outreach and awareness of cybersecurity
adoption barriers aim to foster increased cybersecurity adoption. Applying TAM by Davis
(1986), the study will examine farm operators' perceptions of cybersecurity's usefulness and ease
of use. It will also examine their familiarity with applicable best cyber practices and their
perceptions of and uses of technology.
Cybersecurity research has focused on other critical infrastructure sectors, with limited
research on agriculture, especially farmers’ perspectives and knowledge about cybersecurity
(Kjønås & Wangen, 2023). Kjønås and Wangen (2023) highlighted this knowledge gap in current
research, lacking focus on farmers’ knowledge and perspectives on cybersecurity, and stated the
need for research to examine farmers’ perspectives. While Agriculture 4.0 literature explores the
uses and benefits of technology, it frequently lacks a focus on protecting the farm from
cybersecurity risks introduced by the technology and the increased value of farm data generated
by these new technologies. This study addresses the knowledge gap of family-owned farms
regarding Cybersecurity and Agriculture 4.0, particularly within Michigan, which continues to
exist as of early 2024.
Findings will aid cyber advocates and researchers in understanding barriers to adoption.
This deeper understanding will inform more effective approaches to better educate family
farmers on the importance of cybersecurity and the threats they face. These findings will
ultimately foster Michigan family farmers’ adoption of cybersecurity and improve their
operational security.

Significance of Study
The significance of this study is establishing cybersecurity leadership in Michigan's
agriculture sector by identifying barriers that prevent farm operators from securing their
operations. This understanding will ultimately improve cybersecurity adoption within this critical
infrastructure sector. This study also expands the TAM (Davis, 1986) with its cybersecurity
application to agriculture, focusing explicitly on Michigan's family-owned farms. With the
transition to Agriculture 4.0 and an ever-increasing reliance on technology and data, it is critical
that farm operators in Michigan and across the United States implement cybersecurity practices
or are at least familiar with the associated risks and where to obtain information (Drape et al.,
2021), such as from their local farm bureau, and this study seeks to help inform this process.
Hazrati et al. (2022) also highlighted that presenting information through national farm
associations would likely increase the adoption of security practices as farmers have trust and
long-standing relationships with these organizations.
Additionally, as Agriculture 4.0 increases the potential attack surface for a farm and as
malicious actors target the FA sector, farmers must be proactive rather than reactive regarding
cybersecurity (CISA, 2022). Farmers must think about cybersecurity, like how farmers treat
fields to prevent weeds before they occur. Waiting until a problem occurs is too late. Therefore,
applying TAM to understand farmers' attitudes toward cybersecurity and the barriers preventing
them from becoming secure is crucial to crafting a cybersecurity strategy to educate farmers
effectively. Information, antecedent stories, and strategies to encourage cybersecurity adoption in
one industry or critical infrastructure sector may not work similarly in the FA sector. Instead,
advocates should present cybersecurity information tailored to the agricultural industry (Orloff,
2022).

Further, as of early 2024, cybersecurity awareness and implementation within family
farms lacked thorough study. Kjønås and Wangen (2023) identified this as one of the most
significant gaps in the literature. The results of this study offer further opportunities for research
regarding the identified knowledge gaps for farmers about cybersecurity. The findings from this
study will also provide knowledge enabling entities and individuals who seek to increase the
cybersecurity of family farms in Michigan and likely those across the United States.
Additionally, the recommendations from this study enable further efforts to increase
cybersecurity acceptance within family farm operations in Michigan and the United States.
Research Questions
The research question details the phenomena studied, who comprised the study, and what
problem will be addressed (Connelly, 2015). This study seeks to answer the following central
research question (CRQ) using the associated research questions following the CRQ.
CRQ: What factors hinder the successful adoption of cybersecurity measures among
family-owned farms in Michigan?
Associated Research Questions (RQ):
1. How do knowledge gaps and digital connectivity influence cybersecurity adoption
among family farms in Michigan?
2. How do size, resources, and technological expertise shape the cybersecurity
landscape for Michigan's family farms?
3. How do assessed impact, risk perception, and decision-making influence
cybersecurity adoption among family farms in Michigan?
4. How do financial constraints and perceived ROI impact cybersecurity adoption
among family farms in Michigan?

5. Does geographical location in the State of Michigan influence the adoption of
cybersecurity measures among family farms in Michigan?
6. What are the most effective ways for government agencies, extension services, or
industry associations to collaborate to inform family farms in Michigan about the
value of cybersecurity and improve cybersecurity adoption among these farms, and
how do trusted agents influence the effectiveness of these efforts?
This research uses a quantitative method to collect and analyze data. This study will
utilize a quantitative survey to gain insight into family farmers' understanding of cybersecurity
principles and practices of farm owners and operators and their perceptions regarding
cybersecurity's ease of use and usefulness.
Hypothesis
A hypothesis predicts the relationship between two or more variables and predicts the
specific nature of the results of a study (Connelly, 2015). This study examined the relationship
between farms' views of and adoption of cybersecurity practices, their relationship with
Agriculture 4.0 technologies, and what barriers to adoption exist. The researcher used the
following hypotheses for each associated RQ to answer the CRQ.
Null (H0): There is no difference in the use and perceived usefulness of cybersecurity practices
by farm operators in Michigan who have or have not adopted Agriculture 4.0 technologies.
Alternative (H1): There is a significant difference in the use and perceived usefulness of
cybersecurity practices by farm operators in Michigan who have or have not adopted Agriculture
4.0 technologies.
Theoretical Framework / Conceptual Framework
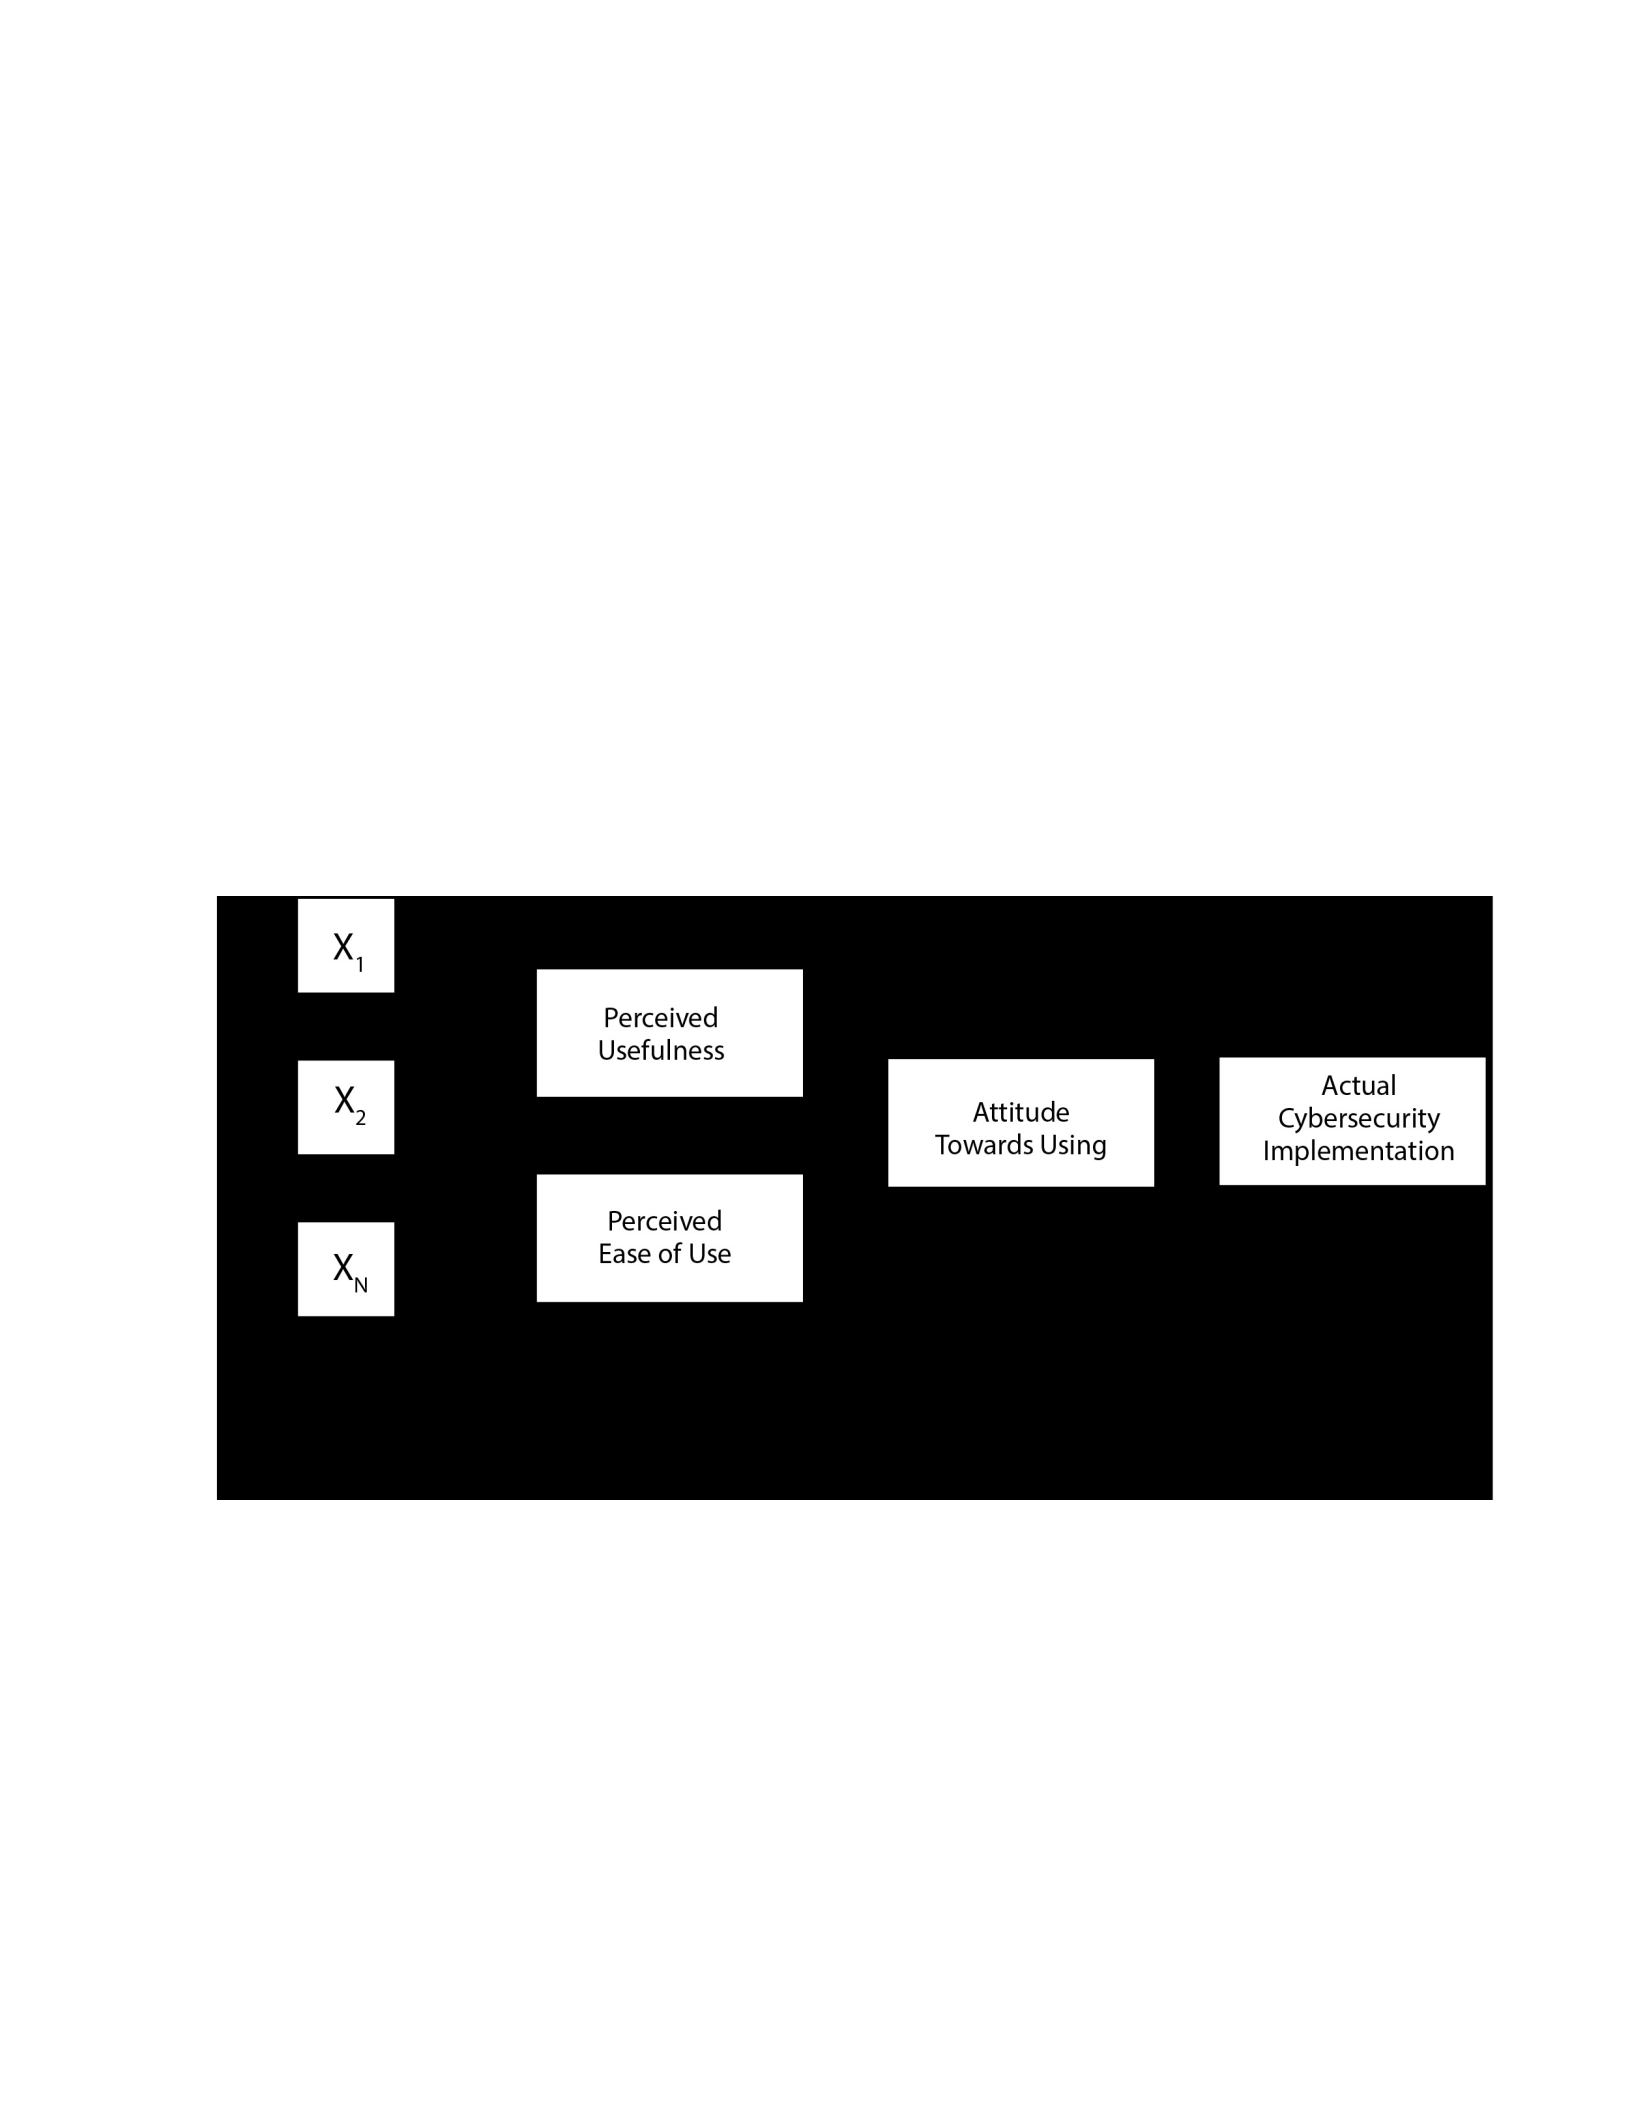
The conceptual framework for this study is the TAM and the key aspects of user attitude
towards a system, in this case, cybersecurity frameworks and best practices. Davis (1986) created
TAM to understand how influencing a user's attitude by the perceived usefulness and ease of use
of a system determines if a user will adopt the system. In the case of applying TAM to
cybersecurity, cybersecurity practices will substitute for the idea of a system (Figure 1). TAM
notes that individuals will avoid using a product because it is not used or easily comprehended.
Figure 1
TAM Cybersecurity
Note. Adapted from the TAM designed by Davis (1986).
Definitions
Terminology within Cybersecurity and Agriculture 4.0 can vary between researchers and
practitioners and from country to country. Ramirez and Choucri (2016) reiterated the benefit of

using standardized cyber terminology in research. Therefore, to ensure clarity within this study,
the relevant terms utilized by this researcher are detailed in this section.
Agriculture 4.0 – is farming characterized by sensors and satellite-based precision,
hightech construction materials, digital technology, advanced communication, working
environment optimization, niches, and new business models (Lejon & Frankelius, 2015).
Additionally, it includes servitization, where traditional product-based companies add services to
their offerings, such as seeking to create value through new products derived from data generated
by the physical product (Kim et al., 2023).
Big Data – refers to extremely large and diverse collections of structured, unstructured,
and semi-structured data that continue to grow exponentially over time. These datasets are so
vast and complex in volume, velocity, and variety that traditional data management systems
cannot store, process, and analyze them (Google, n.d.).
Cyberattack – any intentional effort to steal, expose, alter, disable, or destroy data,
applications, or other assets through unauthorized access to a network, computer system, or
digital device (IBM, n.d.-a).
Cybersecurity – the art of protecting networks, devices, and data from unauthorized
access or criminal use and the practice of ensuring confidentiality, integrity, and availability of
information (CISA, 2021).
Machine Learning – is a branch of artificial intelligence (AI) and computer science that
focuses on using data and algorithms to enable AI to imitate how humans learn, gradually
improving its accuracy (IBM, n.d.-b).
Precision Agriculture – involves the integration of new technologies, including

Geographic Information Systems (GIS), Global Positioning Systems (GPS), and Remote Sensing
(RS) technologies, to allow farm producers to manage within-field variability to maximize the
cost-benefit ratio rather than using the traditional whole-field approach (Brisco et al., 1998).
Smart Farming – is a development that emphasizes using information and
communication technology in the cyber-physical farm management cycle (Wolfert et al., 2017).
Scope of Research
Cybersecurity awareness and its perceived use and usefulness among Michigan family
farm operators lacks thorough study as of the beginning of this research in mid-2022. The goal of
this study is to examine these factors and barriers to the adoption of cybersecurity within the
study's population group.
The sample population of 146 survey participants aged 18 or older who are either owners
or operators of a family farm in Michigan limited the scope of this research. This sample
comprised the data to conduct correlation analysis to determine if a relationship exists between
the independent and dependent variables. Additionally, utilizing G*Power software, the statistical
power analyses were calculated a priori (Faul et al., 2009).
The survey recruitment period was from October 2022 to February 2023. The researcher
chose this period to reach farmers between the end of harvest and the start of the 2023 planting
season. Research on agricultural surveys by Pennings et al. (2002) found that farmers prefer to
receive surveys during January and February, with November and December as the second-best
periods. Each participant completed a survey regarding their perceptions of cybersecurity, its
usefulness, and its use within their farm, as well as their adoption of Agriculture 4.0
technologies.

Limitations
Limitations are a potential weakness in the study that is outside the study's control
(Simon, 2011). This study assumes that survey respondents provided honest and complete
answers; however, it lacks a method to validate the provided data. A survey respondent may be
hesitant to note that they have been the victim of a cyberattack or are not keeping their data and
IT systems secure, so they may have changed their response to protect themselves. These types
of actions are outside of the control of the survey instrument, and this study assumes the survey
respondents' noble intent.
Additionally, with limited research conducted regarding Michigan family farm operators
and their perceptions regarding the ease of use and usefulness of cybersecurity, there are no
known Michigan-specific datasets against which to compare this new data set. Therefore, this
study assumes that trends within the data represent the overall landscape of family farm
operations across Michigan. Additionally, this study relies on a survey that allows respondents to
remain anonymous to encourage honest responses through anonymity. The study must then make
assumptions based on respondents' honesty about their cybersecurity knowledge and the nature
of their family farm operations.
Chapter Summary
As the potential for a cyberattack increases for Michigan's family farm operators,
implementing cybersecurity best practices will be essential to securing data, IT systems, and
Agriculture 4.0 devices. Chapter 1 has introduced the increased risk of a cyberattack against
family farms and how research can apply the TAM to farm operators' views and perceptions of
cybersecurity to overcome barriers to adoption.

Chapter 2: Literature Review
Five areas of focus comprise this literature review: 1) how agriculture has evolved
towards Agriculture 4.0, 2) the digitization of agriculture and transition to Agriculture 4.0 and
beyond, 3) the increased cybersecurity threat and concerns that result, 4) issues facing farmers
regarding the adoption of cybersecurity and information security practices, and 5) the TAM
created by Davis (1986) which seeks to understand the “determinants of perceived usefulness
and perceived ease of use and predict adoption of IT systems” (Venkatesh & Bala, 2008).
Searches and Peer-Reviewed Articles
The literature review for this study relies primarily on peer-reviewed journals and
nonpeer-reviewed sources. While peer-reviewed articles are the desired primary source of
information, the rapid rate of change and knowledge creation within the cybersecurity
community, along with the constantly evolving threat space, create a body of knowledge outside
of peer-reviewed publications that helps inform cybersecurity professionals and researchers at a
much faster rate than traditional publication methods. According to Gernhardt and Groš (2022),
researchers and professionals trust many non-peer-reviewed sources and use them at conferences.
Researchers should view these as sources of trustworthy computer security information
(Gernhardt & Groš, 2022). Gernhardt and Groš (2022) also highlight the quicker publication
timeline following the discovery of incidents in cyberspace in non-peer reviewed sources. At the
same time, peer-reviewed publications require a potentially long period before publication
(Gernhardt & Groš, 2022). While not fully vetted by peers, non-peer-reviewed sources remain
valid sources of information and, therefore, included in this review.

Literature Review
Evolution of Farming from Agriculture 1.0 to Agriculture 4.0
Often, research detailing driving factors for the evolution of agriculture from Agriculture
1.0 to modern Agriculture 4.0 includes a reference to the statistic from The Food and Agriculture
Organization (FAO) of the United Nations that the world population will reach 9.1 billion in
2050 and require food production to increase by 70 percent at the same time (FAO, 2009).
According to Jha et al. (2019), agriculture will continue to face pressure due to the expansion of
the human population, which has increased the importance of agricultural technologies and
precision farming. Therefore, to increase production and meet this goal, agriculture must increase
efficiency and productivity while overcoming a decreasing labor force in a sector where
individuals typically do not transition into seeking employment (Charlton & Castillo, 2021).
Additionally, while changes in farm methodologies are not new, the rate of change has
accelerated as the technology and data applied to the farm have evolved faster (ERS, 2022).
The descriptions of the stages of evolution in agriculture are similar to the evolution of
industry from Industry 1.0 to Industry 4.0 and the even more recent definition of Industry 5.0,
which includes a “sustainable, human-centric and resilient industry” focused on organizations
serving people and ensuring their well-being. Stages of industrial evolution directly translate into
agriculture as Agriculture 1.0, 2.0, 3.0, and 4.0. Zambon et al. (2019) described these stages in
the following way: Agriculture 1.0, which is still practiced by smaller farms today, began with
humans farming and animals assisting them; Agriculture 2.0 saw the addition of the combustion
engine; Agriculture 3.0 started to bring technology to the farm with guidance systems and early
precision farming via GPS; and; Agriculture 4.0 brings more technology and data to the farm in

addition to the use of the internet and cloud computing to connect devices and data as well as
process data from the farm and inform decision making and remote management.
While Beluhova-Uzunova and Dunchev (2022) explained that there is no globally
accepted definition of Agriculture 4.0 and that the idea is shifting towards sustainability and
inclusion, the actual term Agriculture 4.0 is still developing and evolving. As the definition of
Agriculture 4.0 evolves, Zhai et al. (2020) noted that it includes the IoT, Big Data, AI, Cloud
Computing, Remote Sensing, and others. Additionally, an outcome of Agriculture 4.0 is
increased efficiency to address the issue of reduced available labor as farm workers leave for
other industries (Ghobadpour et al., 2022). While the average age of farmers increases, so do the
demands on those farm workers that remain (Ghobadpour et al., 2022). The lack of available
labor and increased demands on farmers drive the need to increase productivity and efficiency
using technology and data. Therefore, as farmers adopt technology to pursue their production
goals, they also increase their cybersecurity risk profile and must address this risk through a
cybersecurity risk management program (NIST, 2019).
For this research, the researcher views Agriculture 4.0 and the more commonly used
terms in the United States of smart farming, precision agriculture, and Decision Agriculture or
Digital Agriculture (Katamreddy et al., 2019) as synonymous and interchangeable. Throughout
this study, Agriculture 4.0 is the preferred reference.
Agriculture 4.0 Digitization and Transformation
According to Dimitri et al. (2005), technological developments within agriculture are
driving change within the farm sector. Those who have remained in the agricultural sector have
increased efficiency by expanding their operations or becoming more specialized to take
advantage of economies of scale (Dimitri et al., 2005). Alternatively, they may identify a niche

market to maintain profitability (Dimitri et al., 2005). Demonstrating this trend, according to the
USDA, within Michigan, there were more than 1,700 farms in 2022 that generated an income of
more than $1 million per year, and the average size of Michigan farms continued to increase,
reaching an average of 208 acres, and a median size of 50 acres (NASS, 2023 and NASS, 2024).
While Agriculture 4.0 benefits large farms, it also benefits small farms; however, farmers
have not always adopted technology at the same rate across the FA Sector (ARS/USDA, 2022).
Previous researchers also noted that “the adoption of new technologies in agriculture is rarely
immediate” (Pierpaoli et al., 2013). Validating this idea, according to Dr. Philip Owens of the
USDA’s Agricultural Research Service (ARS), even though small farms make up 85% of the
U.S. farm totals, very few have adopted precision agriculture, meaning Agriculture 4.0
(ARS/USDA, 2022). Owens emphasized the need to identify appropriate Agriculture 4.0
technologies that can have positive impacts across all scales of farming and believes that small
farms have the most significant potential for adoption (ARS/USDA, 2022). Because this impacts
the most considerable number of farms, the ARS is promoting “big data for small-scale farmers”
(ARS/USDA, 2022).
Industry 4.0, ultimately adopted in the agricultural field as Agriculture 4.0, brings
technology and data together in a linked space (Zambon et al., 2019), which the authors note
both small and medium farms must invest in to keep up with the evolution of farming. Liu et al.
(2021) pointed out that the Agriculture 4.0 goals of sustainability and intelligent industrial
agriculture are achievable through real-time data collection, processing, and analysis of
spatiotemporal data in all aspects of the agricultural industry, from production to processing,
distribution, and ultimately, the customer experience. Additionally, Agriculture 4.0 interconnects
different technologies through the fusion of precision agriculture and the internet with the

common goal of improving yield, increasing sustainability, and improving the quality of the
process (Zamon et al., 2019). Overall, the transition to Agriculture 4.0 is the digital
transformation of agriculture and can benefit most farms. Demonstrating this point, Vij et al.
(2020) highlighted that a smart farming approach could benefit farms of all sizes, from largescale
industrial farms to small-scale farms, even down to a household gardener.
Another critical component is that Agriculture 4.0 generates large volumes of data that
serve as the foundation for decision-making (Araújo, 2021). Data-driven decision-making
changes the focus of agriculture from beliefs and intuition to one based on mathematics
(Beluhova-Uzunova & Dunchev, 2022). As a result, farmers move from the more traditional
decision-making based on “touch and feel” and personal observation of the field, described by
Eastwood et al. (2019) as being experiential, to data-driven insights that are based on data and
are near-real-time, and predictive rather than reactive. Farmers can also make decisions on a
micro-scale rather than a macro-scale across an entire field (Kour & Arora, 2020). At CES 2024,
Doug Sauder, Director of Product Management & User Experience at John Deere, summed up
the focus of Deere’s technology advancements by saying, "You really want to be a micromanager
and give every seed its most optimal potential" (Wolny, 2024).
One way to view this shift in the decision-making scale is to consider the soil within a
farm field. Most soils are not homogonous; they consist of variations within types and properties
across the field. In previous generations of agriculture, farmers made decisions about the field as
a single unit, with fertilizers and pesticide treatments applied consistently across the land. With
the shift to higher resolution data (i.e., micro versus macro), more frequent sampling during the
season, and access to a variety of remotely sensed data, farmers can make decisions down to
individual sections of the field or individual plants (Lambert, 2023). In farming terminology, an

example that farmers are familiar with this practice is variable rate application (Grisso et al.,
2011). An example of this new technology in use as of mid-2023 is the John Deere See &
Spray™ sprayer, with control of each sprayer nozzle and the ability to turn them on and off
individually as the sprayer moves through the field (Deere & Company, 2024). Deere highlights
the increased productivity of the technology, along with a reported approximately 66% reduction
in herbicide use (Lambert, 2023). Thus, Agriculture 4.0 technologies enable these micro-level
management decisions.
Further, Ghobadpour et al. (2022) highlighted that the future of agriculture envisions
more intelligent farms that are more efficient and sustainable, blending sensors, machines,
robots, and IT into the farm. These changes will allow farmers to monitor these parameters in
real time (Araújo, 2021).
Agriculture 4.0 further introduces precision agriculture principles on the digitally enabled
farm. Systems generate large amounts of data, which are then processed to allow farmers to
make strategic and operational decisions (Ghobadpour et al., 2022). Precision farming or
precision agriculture are two more familiar terms used in the United States, and they denote the
blending of technology with data to digitize operations and increase yield (Misra et al., 2020).
One of the issues highlighted by Zambon et al. (2019) is that modern farms produce data that
farmers must interpret, which requires infrastructure, training, and the willingness to adopt the
new technologies. Agriculture 4.0 transformations have also introduced additional concepts
regarding the need for cybersecurity, cloud technology, and big data.
Additionally, farmers may now collect data continuously and in near-real time, making
decisions based on analysis almost as soon as the data is collected. This shift increases
productivity and yield while increasing efficiency. The key is creating data and using the

technology to “collect, store, process, manage, and share such data” (Araújo et al., 2021). In their
research, Liang and Shah (2023) stressed that the IoT is at the forefront of the agricultural
revolution, enabling precision monitoring and providing a wealth of data to farmers to enable
data-driven farming. With Agriculture 4.0, it is possible to think of a shift in farming from
farmers farming a crop to now “farming data,” with the outcome being the crop. Agriculture 4.0
is a more efficient process that ideally leads to greater yields.
While Agriculture 4.0 is a connected system of sensors, external consultants, data
services, and cloud platforms working to optimize agricultural processes, Mühl and de Oliveira
(2022) believe that human intervention is essential to key decision-making. This idea changes in
future stages of digital transformation. While very nascent as of 2024, the next phase of
transformation, Agriculture 5.0, will bring autonomous systems to agriculture and rural
environments (Zambon, 2019). This revolution of farming leverages integrated systems with
self-learning capabilities and a high degree of autonomy, removing the human operator from the
immediate operating environment.
For example, John Deere has set a goal for the company to have a fully autonomous
production cycle for corn and soybeans by 2030 (Lambert, 2023). In this system, Deere will
utilize AI to enable autonomous planting, spraying, and harvesting in conjunction with robotics,
sensors, data, and connectivity (Lambert, 2023). Another example of this next-generation
technology is the Monarch Tractor MK-V tractor, which has full self-driving capability and
Monarch’s proprietary WingspanAI technology (Monarch Tractor, 2023). Farmers can program
the Monarch tractor to perform tasks on the farm, and it can be remotely monitored and
controlled, and the tractor collects crop data that it can use to make real-time adjustments
(McIntyre, 2023; Suarez, 2023).

Adopting these technologies will increase the farm's cyber risk profile, and farmers must
become aware of and educated about cybersecurity. Further, as farming becomes more digital
and advanced, data is essential, and data protection becomes equally important (Dennison, 2023).
Connecting the Farm -- Agricultural Internet of Things (Ag-IoT)
The IoT is the term used to describe the connectivity between the physical and digital
world with standard and interoperable communication protocols (Araújo et al., 2021). When
applying and utilizing IoT devices within agriculture, these systems are known as AgricultureIoT
(AG-IoT) (Uddin et al., 2017), and the application of Ag-IoT to Agriculture 4.0 has the potential
to contribute to greater efficiency in agriculture (Araújo et al., 2021).
Additionally, integrating Ag-IoT into farming operations empowers farmers with decision
tools and automation technologies, integrating knowledge, products, and services to help achieve
high productivity, quality, and profits (Abbasi et al., 2022). Another benefit of Ag-IoT is that big
data analytics can analyze the vast amounts of created data, and the results help make farm
decisions (Araújo, 2021).
Jha et al. (2019) explain that IoT devices transfer the information they generate without
human involvement, and the devices can improve efficiency, productivity, and the global market
and reduce human intervention, time, and cost. They also noted that IoT in agriculture, referring
to Ag-IoT, leads to smart farming. Annosi et al. (2019) also note that Agriculture 4.0 leads to
higher efficiency and better-quality production and has extensive benefits and potential economic
impacts while working to make farm systems more sustainable, efficient, and resilient. These
advancements also allow farmers to increase yield, detect problems earlier, reduce inputs, and
monitor and control farm machines and equipment, all while providing new inputs to farm

management decision-making (Annosi et al., 2019). Thus, Agriculture 4.0 helps farmers make
better-informed decision-making promptly.
Connected equipment and machines containing networks of Ag-IoT sensors within a
platform, for example, a combine or tractor, are not necessarily Ag-IoT and may even be
controlled by the Ag-IoT devices (Kovács & Husti, 2018). Alternatively, Ag-IoT devices can
provide input that controls the devices. One of the many, but perhaps most common, examples
would be John Deere tractors and combines that connect to wireless networks and generate vast
amounts of data as they operate, which then integrates the data into the John Deere Operations
Center™ (John Deere, 2023). At CES 2024, Deere demonstrated this capability via a remotely
controlled tractor operating in another state (Lee, 2024). Using Ag-IoT, Deere works to create a
fully integrated ecosystem in their platform, from the field to the office.
Beyond Ag-IoT are the infrastructure and components that enable the digital age, referred
to as information and communication technology (ICT) (Awati & Pratt, 2023). Within
agricultural contexts, the integration of information and communication technologies (ICTs) is
termed ICT-for-agriculture (ICT4Ag) (Steinke et al., 2022). ICT4Ag includes “all the devices,
networking components, applications, and systems” that, when combined, allow farmers and
farms to interact in the digital world (Awati & Pratt, 2023). While ICT is valuable to farms, it
also creates new potential access vectors for cyber actors to exploit, especially if not secured
(Hughes et al., 2017). These systems will require cybersecurity investment to protect them as
they become more central to farm operations.
Creating and Managing the Data
As farms move towards Agriculture 4.0, data becomes the main constituent, acting as a
base and catalyst throughout the production process (Kour & Arora, 2020). The data creates and

informs the data-driven loop within Agriculture 4.0 and can deliver great value for farmers
(Katamreddy et al., 2019). Javaid et al. (2019) believe that the true potential of Agriculture 4.0 to
increase production is not only the data itself but the “capacity to gather, use, and exchange data
remotely.”
As previously highlighted, the systems that comprise Agriculture 4.0 generate large
amounts of data, known as big data, and make the entire production chain more competitive and
lucrative (Javaid et al., 2022). The massive volumes of data “captured, analyzed, and used for
decision-making” drive Agriculture 4.0 and the contained digital agriculture (Himesh et al.,
2018). Javaid et al. (2022) also noted that digitizing agriculture lowers transition costs, improves
communication, and can revolutionize farming and the entire FA Sector.
Once farms begin creating these big data sets, they must store and manage the data to
utilize it in the follow-on processes, i.e., data analytics, that inform their decision-making.
Farmers can store data locally on the farm or via a third-party platform utilizing cloud
technology, streaming continuously into what is known as a data lake (Misra et al., 2020). By
design of Agriculture 4.0, the farm operator and their consultants and advisors can assess this
data and leverage it for insights (Misra et al., 2020). It can also be accessed for processing by
algorithms or ML techniques to generate actionable insights (Misra et al., 2020). Additionally,
because the data must be accessible from anywhere, analysis and utilization rely on connectivity
to the storage location, such as internet or cellular systems, through whichever means are
available.
Analysis and Data-Driven Decision-Making
Data alone does not power the revolution of Agriculture 4.0. To harness the potential of
this digital agriculture revolution, farmers or consultants must complete data analysis, identify

insights, and then use them to inform decision-making. Agriculture 4.0 utilizes the
decisionmaking analytical framework created by U.S. Air Force Colonel John Boyd, known as
the Observation, Orientation, Decision, and Action (OODA) loop (Zager & Zager, 2017), to
determine a location, detect a feature, do an action, and collect data (Zhai et al., 2020).
Agriculture 4.0 relies on this feedback loop to benefit the farm (Misra et al., 2020).
Central issues within the Agriculture 4.0 system also include the ability to forecast and
predict more effectively. According to Palanivel and Surianarayanan (2019), estimating yields
before harvest is an important issue in agriculture as these changes influence international
business, the food supply, and prices. Further, early yield prediction is helpful to policy planners
(Palanivel & Surianarayanan, 2019).
Another shift within agricultural management is the ability for decision-makers on the
farm to access data via computers and smartphones from any location, provided they have
connectivity. Eastwood et al. (2019) noted that cloud-based data storage and internet-accessible
decision support tools create remote management opportunities. Additionally, Agriculture 4.0
will leverage AI in decision-making. Liu et al. (2021) detail that AI-enabled predictive analytics
will enable forecasting and modeling and that the seamless transition from agricultural problems
to decision-making models is crucial for the successful adoption of AI in agriculture.
Another technology that can help drive decision-making on the farm is virtualization and
digital twins, which are virtual representations of physical objects or systems (Slob & Hurst,
2022). Decision support and analysis systems use this digital replica, and one example of a
system that can be a digital twin is a CPS (Slob & Hurst, 2022). According to Rad et al. (2015),

CPS is a technology comprising three layers: the physical, network, and decision layers. CPS are
smart systems with hardware, software, and physical components that seamlessly integrate and
closely interact to sense changes in the real world.
Agriculture 4.0 is an application of a CPS, according to Rad et al. (2015), and they
seamlessly integrate and interact to sense the changing state of the physical world, in this case,
the farm and its components. Abbasi et al. (2022) label CPS directly connected to agriculture as
agricultural cyber-physical systems (ACPs), combining advanced electronic technologies and
agricultural facilities to build integrated farm management systems. These systems then interact
with the physical environment, optimizing the growing environment for crops (Abbasi et al.,
2022).
For example, in Denmark, researchers have been working to transform the horticulture
greenhouse industry using digital twins to simulate and evaluate the physical greenhouse
performance and production processes (Howard et al., 2021). Utilizing the Agriculture 4.0
devices and data from the greenhouse systems, greenhouse operators use modeling and
simulations, which ultimately support the greenhouse operators in decision-making, and the
resulting information is used within Agriculture 4.0 control systems to optimize the greenhouse
processes (Howard et al., 2021).
Another benefit of digital twins is that they can identify potential problems before they
become critical (Singh et al., 2021). Identifying that a piece of farm equipment has developed a
fault, and if the farmer does not attend to it, the equipment may fail and impact their operation
(Pylianidis et al., 2021) is one example. Identifying the problem earlier allows farmers to save
money on costly repairs and ensure they can continue their operations without interruption.

Another benefit of Agriculture 4.0 technologies is the reduced time required to obtain
information about the farm. In one instance, Lukowska et al. (2019) detailed a mobile soil
sampling platform capable of roaming a farm’s field, collecting and processing soil samples in
situ, and storing the resulting data. Thus, the platform could ultimately survey the field more
quickly and efficiently than before adopting Agriculture 4.0 technologies (Lukowska et al, 2019).
In addition to crops, precision livestock farming (PLF) is an additional aspect of
agriculture modernized via Agriculture 4.0. PLF applies process engineering principles and
techniques to livestock farming to automatically monitor, model, and manage animal production.
This real-time animal health monitoring makes farmers rapidly aware of potential issues (Li et
al., 2020). Like decisions in crop farming, the sooner a livestock farmer receives notification of a
problem, the less impact the problem may have on their operation.
Optimizing costs and time, farms must adopt technology and move beyond only using the
traditional techniques of farming (Kour & Arora, 2020). The authors note that precision
agriculture, and thus Agriculture 4.0 by extension, seeks optimization and improvement of
processes, ensuring farms achieve the best production. However, Dorairaju (2021) noted in a
case study about technology in modern agriculture that the increased reliance on technology and
its associated processes increases the need for the farm to secure the IT systems and data in ways
they may have been unfamiliar with before its adoption.
Cyber Threats to Agriculture 4.0
The U.S. CISA defines cybersecurity as “the art of protecting networks, devices, and data
from unauthorized access or criminal use and the practice of ensuring confidentiality, integrity,
and availability of information.” As agriculture transitions into Agriculture 4.0, cybersecurity
must become a central farm operation and management tenant. In the ‘‘Promoting Precision

Agriculture Act of 2023’’ introduced by U.S. Senators Thune and Warnock, they propose that the
Secretary of Agriculture consider “the cybersecurity challenges facing precision agriculture,
including cybersecurity threats for agriculture producers and agriculture supply chains,”
highlighting that increased availability of advanced precision agriculture technologies has
increased the vulnerabilities of the agriculture industry (Thune, 2023). Additionally, cyber
hygiene, which applies basic cybersecurity practices to an operation, including multifactor
authentication, strong passwords, and employee training (Cain et al., 2018), must also become a
standard operating procedure on the farm.
Even though cybersecurity has become critical for businesses, the U.S. FA Sector lacks
the resources, expertise, and government support to protect the sector and its products from
rapidly expanding cybersecurity threats (Geller, 2023). According to Janos Botschner, the
principal investigator for the Cyber Security Capacity in Canadian Agriculture, digital agriculture
cybersecurity is still in its infancy across the globe as of 2022, which Botschner believes is both a
weakness and an opportunity to build cyber capacity within the FA sector (Bueckert, 2022).
Without a focus on securing digital, connected devices and farm data, operations will face cyber
risk from actions that could be malicious or simply a failure and lead to potential disruptions.
To help farm operators understand cybersecurity and its fundamental principles,
agricultural cybersecurity training can borrow from well-established terms and frameworks
already utilized by other sectors, such as the U.S. National Institute of Standards and Technology
(NIST) Cybersecurity Framework (CSF) 2.0 (NIST, 2024). For many years, the cybersecurity
community has used the CIA triad as the information security model, referring to Confidentiality,
Integrity, and Availability as the fundamental elements of security controls within information
systems (Samonas & Cross, 2014). In recent years, the CIA triad has expanded to include

authentication and non-repudiation of user data, described as the Five Pillars of Cybersecurity or
Pillars of IA (Information Assurance) (USNA, n.d.).
The CIA triad and NIST Framework for Improving Critical Infrastructure Cybersecurity
(NIST, 2018) have coupled to further cybersecurity frameworks. This framework provides a way
to organize cybersecurity activities into Identify, Protect, Detect, Respond, and Recovery. While
these two are some of the most common references to cybersecurity principles and frameworks,
they are not the only ones. Regardless of the terminology and framework, the core principles of
cybersecurity are important to Agriculture 4.0 as we advance.
Regardless of the size of a farm, cybersecurity needs to be a focus of the business. Many
businesses believe that cyber threats will not impact their farm due to their size, location, or
industry; however, regardless of size, “all organizations must understand the importance of
cybersecurity protection” (Lahiri, 2023). In one example, security company Barracuda (2022)
found that email attacks did not discriminate based on the size of an organization and that an
employee of a company with less than 100 employees received 350% more social engineering
attacks than an employee at a larger business. Barracuda (2022) highlighted that small and
medium-sized businesses (SMBs) are attractive targets for cyber actors because, collectively,
they have substantial economic value and often lack security resources or expertise. Barracuda
stressed that small businesses should not overlook investment in security in both technology and
user education.
Next, shifting to the threat of cyber-attacks, in 2010, the world saw a dramatic
cyberattack against industrial control systems (ICS) via a specialized, targeted attack known as
the
Stuxnet worm, designed to cause physical damage to specific Programmable Logic Controllers

(PLCs) (Karnouskos, 2011, November, and Langer 2011). Karnouskos (2011, November) noted
that Stuxnet targeted a network not directly connected to the Internet, referred to as being
airgapped; however, Karnouskos highlighted that emerging industrial infrastructure will be a
system of systems that relies on connected communications infrastructure for command and
control which will expose those systems to cyber risks. Utilizing its tailored malicious code,
Stuxnet could propagate within the network to run attacks against the targeted PLCs and cause
damage by issuing malicious commands. While this attack was very specialized, it demonstrated
the severe impacts that a cyber-attack can have against critical infrastructure.
Karnouskos (2011, November) also noted that Stuxnet came at a critical time for modern
ICS as they adopted Internet-based technologies and architectures and the interconnection of
enterprise IT systems and ICS. Further, these modern systems include CPS, which, according to
Karnouskos (2011, July), “monitor, share and manage information, and control actions on the
business as well as the real world” while blurring the lines between the physical and virtual
worlds, and represent systems that are part of critical infrastructure. As indicated earlier, CPSs
are a part of the FA sector, especially when considering systems within Agriculture 4.0, and the
modernization of systems within critical infrastructure sectors will further introduce cyber risk.
Agriculture in the Cyber Crosshair
Abbasi et al. (2022) highlighted that cybersecurity “is a major challenge that needs to be
addressed within the context of smart farming.” From the late 2010s into the early 2020s,
cyberattacks against agriculture and its supply chain have increased rapidly. In 2021, malware
detections against agriculture rose by 607% (Malwarebytes, 2021).
When considering cyber threats to Agriculture 4.0, there may be some debate regarding a
specific attack that researchers point to as the watershed moment when a cyber-attack directly

changed the course of history within the FA sector. While the attacks may not be as specific as
Stuxnet and identified as “the moment” agriculture became a target of cyber attackers, there are
several incidents that occurred in 2021 and 2022 that led the U.S. FBI to issue a PIN in April
2022 detailing the timing of attacks against agricultural cooperatives that can match critical
seasons (FBI, 2022). The FBI warned that well-timed attacks against the essential aspects of that
part of the season could have wide-ranging impacts across the sector. For example, a threat actor
may choose to attack agricultural cooperatives during critical planting and harvest seasons,
which would cause direct effects on farmers (FBI, 2022). The disruption to supplies during
planting or a co-op unable to accept harvested crops during harvest would have direct and
immediate negative repercussions for farm operations.
Cyber Attacks on the Rise
In March 2023, a report highlighted that agriculture was the “second-largest target of
cybercrime because farming and food,” i.e., the FA sector, are critical infrastructure
(McCullough, 2023). Special Agent Byron Franz of the Milwaukee Division of the FBI
highlighted that cyber actors increasingly target the FA sector because of the critical nature of
food and that attacks have worsened due to the increased attack surface that results from farms
adding connected devices (McCullough, 2023). More information about attack surfaces is in the
next section.
Over the past several years, cyberattacks against agriculture have increased. Kouloufakos
(2022) detailed some of the more significant agricultural cyberattacks that had ripple effects
across the supply chain. Farms rely on supply chains to enable their operations, and farms are
also part of the supply chain. Therefore, cyberattacks against farms or other supply chain
segments directly impact everyone relying on that specific chain portion. A challenge that

prevents a more complete understanding of the overall cyber threat to the FA sector is that the
United States does not require reporting for cyberattacks in all instances. Instead, most
knowledge about attempted or actual attacks comes from voluntary reporting. In 2022, President
Biden signed into law the Cyber Incident Reporting for Critical Infrastructure Act of 2022
(CIRCIA), which will require covered cyber incident and ransomware payment reporting once
the final rule implementing CIRCIA goes into effect. Until then, CISA encourages critical
infrastructure owners and operators to report cyber incidents voluntarily (CISA, 2023). It is of
concern that this rule, once implemented, will not require many farms to report cyber incidents as
they may not qualify as covered entities. While a step in the right direction, voluntary
ransomware payment reporting should still be encouraged for those not required to report a
payment.
Examples of cyberattacks focused on the FA sector include:
•In May 2021, a ransomware attack against JBS USA Holdings Inc., the U.S.
subsidiary of Brazil-based JBS, the world’s largest meat processor, forced JBS to
shut down operations across the United States and JBS subsidiaries in Canada and
Australia. JBS is responsible for processing one-quarter of the beef in the U.S.,
and the shutdown could impact the beef supply if it went on for some time
(Durbin & Bajack, 2021). Additionally, JBS USA paid the attackers $11 million in
ransom to mitigate the attack's impact (Nair, 2021).
•In September 2021, Crystal Valley, a farm supply and grain marketing cooperative
with customers in southern Minnesota and northern Iowa, was the victim of a
targeted ransomware attack that left it unable to maintain daily operations (Crystal

Valley, 2021). Also, in September 2021, a Russian-linked ransomware attack
against New Cooperative, an Iowa grain cooperative, disabled
the co-op’s automated control systems and disrupted operations. Around the same
time, another ransomware group attacked the Iowa-based Farmers Cooperative
Elevator Company, and the group threatened to release sensitive data from the
company (Ernst, 2021).
•In October 2021, the United States saw a cream cheese shortage timed with the
increased holiday season demand after Wisconsin-based Schreiber Foods was the
victim of a cyberattack, forcing it to stop production for several days (Maruf,
2021). As a result, the demand for cream cheese from downstream producers and
consumers could not be fulfilled (Maruf, 2021).
•From late February 2022 into March, Bob’s Red Mill Natural Foods, Inc., was the
victim of a data scrape attack that stole customers’ personal information and credit
card numbers—Bob’s notified customers of the breach and their disrupted online
ordering (Schroeder, 2022).
•In March 2022, H.P. Hood Dairy in Massachusetts, the largest producer of milk
used in school lunches in New England, suffered a cyberattack that disrupted its
ordering and delivery services and impacted school lunch programs throughout
New England (Sudborough, 2022).
•March 2022, an unidentified multi-state grain company providing seed, fertilizer,
and logistics services was the target of a Lockbit 2.0 ransomware attack (Gates,
2022).

•In late February 2023, Dole disclosed that it was the victim of a ransomware
attack (Dole, 2023). The attack forced Dole to shut down plants in North America,
causing delays and shortages in products, and ultimately, Dole revealed that the
attackers accessed employee data (Umawing, 2023).
The increase in attacks and timing led the FBI to issue the PIN to the FA sector,
highlighting the impact that the loss of Agriculture 4.0 technologies could have on the farm. Paul
Main, the owner of Main Farms in Six Lakes, Michigan, noted that technology has been the
future of agriculture. However, if their GPS and satellite are unavailable, they cannot operate or
do many tasks (Galloway, 2023). Main stressed that technology was excellent, but there were no
backups for them (Galloway, 2023) – highlighting the critical importance of technology to the
modern farm and the impact of the loss of these technologies due to a cyberattack. Further,
attacks may not be explicitly against agriculture; instead, they may be against the critical systems
relied upon by agriculture. However, the result of attacks on another sector or even an act of war
against the U.S. may still be the same: that loss of availability directly impacts the FA sector.
Increased Attack Surface, Increased Vulnerabilities
Before the digital transformation of agriculture, farms typically had to deal with the
security perimeter consisting of the physical boundaries of their farm along with access to their
buildings, barns, and equipment. In general, threats to the farm had to physically be present at the
farm to launch an “attack.” As farms move towards and into Agriculture 4.0, they expand their
security perimeter from the physical world into the digital world. Each Ag-IoT or
internetconnected device increases the farm’s attack surface and vulnerabilities (M. Gupta et al.,
2020). Rizvi et al. (2020) reported that the attack surface of a network is the sum of all

penetration points known as attack vectors, and attackers or unauthorized users can exploit these
attack vectors to penetrate a network and change or extract data from the targeted environment.
Another issue with the modernization of the farm, according to Botschner, is that an
attack could impact both the farm business and the farm family because of the lack of network
segregation between the home and agricultural operation (Bueckert, 2022). The result is that an
attack on either side of the network could impact the other. Therefore, it is also vital that farms
secure their home devices, as they can provide a gateway into the business network. Because of
the increased vulnerabilities from connected devices on the farm or data stored outside their
control, farms face new potential access vectors accessible to threat actors.
The Human Attack Surface
Within cybersecurity, the weakest link is often considered humans (Hennessey, 2022),
and the totality of all exploitable security holes created through the activities and vulnerabilities
of personnel is known as the “human attack surface” (Cuchta et al., 2019). Therefore, employee
training is vital for a farm to achieve a robust cybersecurity strategy (Macri, 2023). Hence, to
increase an organization's cybersecurity awareness and resilience, tailored cybersecurity training
is essential to instill knowledge and capability into the personnel (Nagarajan et al., 2012).
Further, to reduce the risk due to the human attack surface and improve the farm cybersecurity
posture, regular security awareness training is critical for all employees, providing them with the
understanding and methods to implement security practices and minimize the risk of a
cyberattack (Rende, 2023). This training teaches employees about potential cyberattack methods
and ways to prevent attacks (Rende, 2023).
The 2016 ransomware attack on Lansing, Michigan’s Board of Water and Light (BWL)

highlights the impact that a single user can have on critical infrastructure, even unintentionally.
To launch this attack, ransomware actors targeted employees via a phishing attack, sending a
malicious link via email, and an employee clicked the link on April 25, which then encrypted the
employee’s computer and the BWL email and accounting systems (Reed, 2016). To unlock
BWL’s systems and recover from the attack, BWL paid a $25,000 bitcoin ransom, cleaned and
tested 700 to 800 pieces of computer equipment, replaced the infected server, and completed
$400,000 in cybersecurity upgrades, resulting in a total cost of $2.4 million to remediate this
single cyber-attack (Reed, 2016). BWL noted that the attack was successful due to the
employee’s lapse of awareness and the sophistication of the attacker (Reed, 2016). This attack
demonstrated one action's cascading impact across a critical infrastructure network. While
BWL’s network is much more extensive than most farm networks, it highlights the costs incurred
by an operation to recover, which could be more than a farm can afford. Therefore, recurring
cybersecurity training for all employees is an important defense mechanism.
Threats to Access
One of the most frequent cyber-attacks impacting IT systems or data access is
ransomware, highlighted in several recent attacks in this literature review. Ransomware is a form
of malware designed to encrypt data on a device, rendering it and systems that rely on the data
unusable until the data is decrypted, if possible (CISA and MS-ISAC, 2020). Threat actors
typically demand a financial ransom for the key to decrypt the data. However, failure to pay the
ransom may lead to the threat actor selling or leaking the data. According to the Palo Alto
Networks Unit 42 Threat Intelligence unit, as of late 2022, threat actors engaged in data theft in
70% of ransomware cases and often threaten to leak stolen data onto the dark web (Unit 42,
2023).

Due to the potential for an attack to have already occurred and gone unnoticed, the
cybersecurity community has introduced the concept of zero trust. In zero trust architecture
(ZTA), one assumes that a cyber incident has already occurred and that the devices within a
network should not be inherently trusted (Lopez, 2022). Zero trust moves the security perimeter
from the network's edge into the local network. In this model, authentication of every action
occurs at every session, and authorization to access one resource does not automatically grant
access to another (Rose et al., 2020). With authentication no longer occurring just at log-in, the
threat actor’s inability to authenticate each session or event should prevent them from moving
throughout the network or accessing data (Rose et al., 2020).
Additionally, it is critical to ensure that employees have the lowest level of access
required to complete their duties. The lowest required access prevents compromised credentials
from allowing someone to access large network sections (Rose et al., 2020). It also prevents
insider threats from gaining access to information they should not have access to (Rose et al.,
2020). It is possible to explain this concept to a user by using the example of a hotel. The room
access key allows access to the patron’s room and shared amenity areas but not every room
within the building. Only those spaces, i.e., areas of the network that management has
determined accessible to customers, are accessible via their credentials. Zero trust and ensuring
employees do not have unnecessary access to resources could have limited the impact
demonstrated in the BWL attack above.
As noted above, on the human attack surface, it is crucial that the IT system enforces
cybersecurity practices and that employees cannot easily circumvent them. For example,
requiring employees to use strong passwords or two-factor authentication (2FA) or multifactor
authentication (MFA) is a good practice. Still, the system must also require security features by

default rather than as an option (West, 2018). Farms should implement free or low-cost network
security measures, such as MFA or 2FA, as a standard cyber practice for immediate security
improvement (NIST, 2023).
Threats to Connected Devices
In 2017, Lin et al. detailed that precision agriculture at the time, and by extension
Agriculture 4.0, increased the national security threat levels for a nation’s FA sector by exposing
it to data theft, hacking via vulnerabilities, and tactics specially used with the intent to steal
farmlevel data in bulk. Additionally, the centralized management platforms of Agriculture 4.0
expose farms to vulnerabilities as they are a single point of failure if attacked. Ag-IoT also
increases cyber risk as using connected devices to gather data on and analyze agricultural
processes creates a vulnerability as many of these technologies and their data are not secure
(Drape & Murch, 2022). Bour et al. (2023) also stressed that the security of IoT solutions is a
critical concern in adopting Industry 4.0 and, by extension, Agriculture 4.0 technologies due to
their lack of basic security mechanisms and vulnerability to cyberattacks.
When organizations undertake digital transformation projects, such as the shift to
Agriculture 4.0, adding emerging technologies to legacy IT systems increases the complexity of
the digital environment and cybersecurity risk (WEF, 2023). The World Economic Forum (WEF)
(2023) also reported that leaders struggle to balance the value of new technology with the
potential increased cyber risk for their organization. In one example, Lennon, the general
manager of the Ontario Federation of Agriculture (OFA), highlighted that she could not
remember the last time she met a farmer who did not have a cell phone, including a smartphone
(Bueckert, 2022). Lennon has seen an increasing amount of technology and data on farms and

noted that farms become targets for cyberattacks as farm equipment becomes more advanced and
connected to the internet, putting the FA sector at risk (Bueckert, 2022).
As an example of the threat faced due to connected devices, in April 2023, farmers in
Israel received warnings to turn off remote connections for the water controllers of irrigation
systems on their farms due to the threat of cyberattack (Kovacs, 2023). Nearly one dozen farms
failed to follow the recommendation, resulting in hacked water controllers, and then their
automated irrigation systems were disabled, forcing farmers to rely on manual irrigation (Ikeda,
2023). Leaving passwords set to the default and not disconnecting the vulnerable ICS systems
allowed hackers to gain access and disrupt the irrigation controllers (Kovacs, 2023). This
preventable cyberattack took advantage of the farmers’ failure to implement basic cybersecurity
practices and cyber hygiene and their failure to heed cyber threat warnings.
Another example of a feature of Agriculture 4.0 that could potentially become a
vulnerability is remotely accessible or controlled tractors. During the beginning of the Russia and
Ukraine conflict in 2022, Russian forces stole $5M worth of John Deere tractors from a
dealership in Ukraine and shipped them to Chechnya (Fylyppov & Lister, 2022). Using their
proprietary technology, John Deere tracked the equipment, remotely disabled it, and rendered it
useless to the recipients (Fylyppov & Lister, 2022). While this capability benefits the owner, it
also creates a vulnerability if leveraged by threat actors. In 2022, a hacker known as Sick Codes
demonstrated that he could exploit vulnerabilities within certain John Deere tractors through their
touch screens and take control of them (Newman, 2022). While Newman (2022) highlights that
this attack required physical access to the tractors, she also points out that this vulnerability is an
insecurity that could be combined with other vulnerabilities, allowing threat actors to attack the
connected tractors, and Sick Codes claimed it would be possible to develop a remote tool.

Threats to Data
“Data is power — financial, economic, and military power,” according to Trent
Emenecker, a member of the U.S. Pentagon’s Defense Innovation Unit (Tegler, 2024). Javaid et
al. (2022) warned that data security in agriculture is still a relatively new idea. The threat of
cyber-attacks will increase as industrial systems become more complicated, according to Javaid
et al. (2022), even more so as Agriculture 4.0-enabled devices rely on secure and timely transport
and data exchange. Additionally, as the volume of data generated by the farm increases, so does
the value of the data as it becomes a high-value asset and increases the potential value to third
parties or threat actors (Rawat et al., 2021). According to Monteiro et al. (2021), the control and
use of this farm data can be problematic as companies can monetize the data for commercial
benefits. Further, big corporations can collect, use, and sell data from farmers, leading to tension
between the corporations and farmers over the misuse of their data (Monteiro et al., 2021). Thus,
farmers must pay attention to the data use policies of devices they introduce to their operations,
and they must also be aware of the potential for threat actors to target this data for exploitation.
One example of this potential conflict is John Deere's release of a fully autonomous 8R
tractor in 2022, which incorporates AI to process the data generated by the tractor. Then, Deere’s
AI uses the data to improve tractor performance and inform the farmer (Knight, 2022). The issue,
highlighted by Santa Clara University professor Christopher Kitts, is that the data has the
potential to be so helpful that John Deere may charge farmers to access it (Knight, 2022). Knight
(2022) also quoted agricultural engineer Kevin Kenney, who believes these tractors could make
farmers more reliant on John Deere and less able to make decisions as John Deere tries to
become “the Facebook of farming.” This model ultimately means farmers turn their data over to

John Deere, allowing John Deere to use the data as they see fit per the user agreement. Deere
wants farmers purchasing their products, but John Deere will retain data ownership (Dey, 2022).
Deere can then sell the data to anyone, including the farmer who created it (Dey, 2022).
Threats to data exist both within the farm's IT and externally as operators transfer data
into the cloud. As the data resides outside the farm’s local IT, offsite cloud storage poses risks;
instead, the external vendor manages the cloud storage, and farms rely on their security (Yang et
al., 2020). While this may offer levels of protection more significant than those of local storage,
such as resilience, since the cloud provides some restoration capability, there are still risks that
come with cloud storage. Misconfiguration of cloud storage has led to data leaks and breaches in
the past. According to the Cloud Security Alliance (2022), of the top 11 threats they identified to
cloud computing, number 3 is “Misconfiguration and Inadequate Change Control.” Further
discussion of additional threats to the cloud occurs in the following section.
Additionally, protecting data stored locally is important as threats are not only from
external cyber actors. Hard drive or storage device failures can lead to the loss of critical farm
data and, without appropriate and frequent backups, crippling operations as they no longer have
data to drive decision-making or have the data available for regulatory requirements such as
taxes. Additionally, should disclosure of farmers' sensitive data to third parties through a leak or
hack occur, they could suffer financial loss and negative emotional impacts (Liu et al., 2021).
The Cloud
Storage of Agriculture 4.0 data generated by Ag-IoT, along with other processes and
record keeping on the farm, must be in a manner that allows it to be readily accessible. In many
instances, proprietary data storage has moved from locally stored on a computer or external
storage device to a cloud-based data storage platform called a cloud service provider (CSP).

While private clouds exist, a third party, such as Amazon Web Services (AWS), more often owns
and manages the CSPs, and these are a lower-cost option for farms. When farm operators move
their data outside their control, they expose it to potential risks. Risks could be data loss or theft
due to a data breach of the platform. Misra et al. (2020) indicated that the new challenges
resulting from the digitization of agriculture create new cybersecurity challenges and that a data
security breach could be fatal for companies due to the loss of business reputation.
According to the IBM “Cost of a Data Breach Report 2022,” 45 percent of data breaches
reported in their study population occurred in the cloud. According to Achar et al. (2022), CSPs
and their users have responsibilities regarding cloud security. The CSP secures the cloud
platform, and the user is responsible for security within the cloud using the security controls
offered by the CSP (Achar et al., 2022). This responsibility presents a potential vulnerability for
farmers as they may not know how to configure their security settings appropriately. Achar et al.
(2022) highlight that incorrectly configured cloud security settings are the most significant
security risks that can result in cloud data breaches. One option to increase data security within
the cloud is to encrypt the data before transmitting it to the CSP (Arora & Parashar, 2013), an
additional technique with which users must become familiar. Ultimately, it is incumbent on
farmers to ensure that their data stored within the cloud is secure.
Another instance of threats to data occurs when transmitting or exchanging data if these
actions are not secure or if they are not timely enough for decisions made on the farm. Thus, data
security is an issue for Agriculture 4.0.
Threats to Privacy
The digital transformation of farms results in farms being at risk of losing confidentiality
if threat actors breach their systems and access, steal, or leak their information (Osborne, 2023).

Additionally, as more information about individuals is made available on the internet, the threat
to privacy increases. Threat actors collect readily available data, using the scraping process to
tailor cyberattacks to individuals or organizations, using social engineering to trick or manipulate
a person to complete an action or provide information to the threat actor (Gupta et al., 2016,
April). One example is a phishing attack where threat actors attempt to have a victim conduct an
action, such as clicking on a link in an email and then providing information to the threat actor,
enabling them to compromise the user’s credentials, data, and system.
One of the most influential trends in modern agriculture is the rise of consumer influence
in agricultural production (Dimitri et al., 2015). Today’s consumers seek to connect with farms
they patronize, learning about them on social media and interacting on various platforms such as
Instagram, Facebook, and YouTube. To achieve this interaction, farms increase their digital
footprint to gain online exposure and interact with their customers. A negative effect of this
increased presence is that farms increase the risk of cyber-attacks or privacy threats, as
individuals may inappropriately use information.
Several adverse effects have occurred to farmers leveraging social media to increase their
farm business. In August 2022, Laura Carlson of Laura Farms admonished her YouTube viewers
to respect the privacy of her and her family as people had been showing up at her relatives’
houses looking for Laura (Laura Farms, 2022). Similarly, Cole Langenbau, known as Cole the
Cornstar, returned to his farm late one evening in September 2020 and found an individual who
drove from out of state uninvited to meet Langenbau (Cole the Cornstar, 2020). Langenbau noted
that people feel they know him from watching his videos, but he does not know them and
requests that people respect his privacy and not travel to his farm uninvited (Cole the Cornstar,

2020). While both examples have individuals approaching them in the physical world, their
digital exposure created vulnerability, resulting in their loss of privacy and a potential threat.
In another example where threat actors leveraged this public-facing connection, Mike
Morgan of Outdoors With The Morgans warned his viewers in January 2023 that “scammers and
spammers” were using the comments sections of their videos to conduct cyberattacks via the
comments and poisoned links, or through impersonation of their social media (Outdoors With
The Morgans, 2023). The cyber actors were impersonating Morgan online to trick followers into
providing personal information. Additionally, they placed links into authentic videos' comments
sections to redirect viewers to malicious websites.
These are a few examples in which threat actors can use publicly available information to
violate farmers' online privacy. They may harass the individual farmer, attempt to extort them, or
even impersonate them to conduct an attack. These attacks can impact the farm's reputation, just
as data leaks may, and erode the trust of the farm’s social media following. Both of which can
have a negative financial impact on the farm. Therefore, warnings like that from Morgan aim to
prevent followers from exploitation from cyber actors, presenting a new type of customer
protection that farmers must become familiar with as they enter the cyber realm.
Threat Intelligence
Cyber Threat Intelligence (CTI) is the cybersecurity domain in which “data is collected,
processed, and analyzed to understand a threat actor’s motives, targets, and attack behaviors”
(CrowdStrike, 2023). Additionally, CTI provides insight to support cyber defenders to help
inform decision-making (Sakellariou et al., 2022). Thus, CTI is critical in cyber defense and
shifting an organization’s cybersecurity from reactive to proactive (Kotsias et al., 2022).

While CTI can be broad and help businesses in any sector, specific threat information
companies share within an industry benefits everyone (Norton & Sachs, 2023). Norton and Sachs
(2023) highlight that a proven way to share information is through an Information Sharing and
Analysis Center (ISAC); however, they noted at the time of their writing that the FA Sector was
the only U.S. critical infrastructure sector without an ISAC. The FA Sector first created an ISAC
in 2002. According to Sachs, the ISAC disbanded in 2008 due to members being unwilling to
share information at the time and fearing they may lose competitive advantage and become
exposed to regulatory action (Geller, 2023). To counter this idea, Norton and Sachs (2023) noted
that information within an ISAC is protected from Freedom of Information Act (FOIA) requests
and shared only with other members of the ISAC. Norton and Sachs (2023) stressed that the FA
Sector must form a new ISAC, given the increased cyber threats against the global food system.
Following renewed interest in an ISAC, Congressman August Pfluger from Texas
introduced the Food and Agriculture Industry Cybersecurity Support Act in February 2023 that
proposed a requirement for the U.S. Government to study the advantages and disadvantages of
creating a food and agriculture industry-specific ISAC (Pfluger, 2023). Before this study moved
forward, the food-focused information-sharing subgroup within the Information Technology
ISAC (IT-ISAC) then separated to re-create the Food and Agriculture-Information Sharing and
Analysis Center (Food and Ag-ISAC) in May 2023 (Starks, 2023).
While the re-created ISAC will reportedly have board members “from the entire farm-
totable supply chain” (Starks, 2023), it is vital to represent farms of all sizes. All farms should be
encouraged to join the ISAC so that cybersecurity may increase across the entire supply chain.
The re-establishment of the Food and Ag-ISAC demonstrates the recognition “that threat
intelligence, analysis, and effective security practices help food and agriculture companies detect

attacks, respond to incidents, and share indicators so they can better protect themselves and
manage risks to their companies and the sector” (Food and Ag-ISAC, 2023).
Agricultural Supply Chain
Agriculture supply chains are the system or systems encompassing all the activities,
organizations, actors, technology, information, resources, and services involved in producing
agri-food products for consumer markets, according to the Organisation for Economic
Cooperation and Development (OECD) of the FAO of the United Nations (OECD/FAO, 2016).
These supply chains include upstream and downstream sectors, from agricultural inputs (seeds,
fertilizers, feeds, medicine, or equipment) to production, post-harvest handling, processing,
transportation, marketing, distribution, and retailing (OECD/FAO, 2016). Also included are
supply chain support services, which include extension services, research and development, and
market information (OECD/FAO, 2016). Organizations within the agricultural supply chain
include farms of all sizes, farmers’ organizations, co-operatives, companies providing services to
or buying from the farms, government organizations, financial services, and private foundations
(OECD/FAO, 2016).
As technology digitizes agriculture, so has technology digitized supply chains. As the
agricultural supply chain components implement many of the same technologies that drive
Agriculture 4.0, they become data-driven and predictive (Lezoche et al., 2020). According to the
WEF (2023), supply chain risk indicates the risk shared across a particular sector, multiple
sectors, or countries, and cyber incidents impacting the supply chain demonstrate how
technologies that support business, infrastructure, and societies are increasingly interdependent
and vulnerable. Boyes (2015) highlighted that the increased use of technology in supply chains
increases cybersecurity risks that affect the cyber-resilience of the supply chain. Boyes (2015)

further noted that supply chains had received insufficient attention, creating cybersecurity and
cyber-resilience vulnerabilities, and this continues to be an issue for agriculture as supply chain
attacks have increased into the 2020s.
With connected digital agricultural supply chains vulnerable to the same cyber threats
that farms face, cyberattacks against the supply chains can also impact farms. In a 2022 PIN, the
FBI highlighted the potential for supply chain attacks to disrupt the FA Sector, addressing
ransomware attacks on agricultural cooperatives timed to match critical seasons (FBI, 2022). As
discussed earlier, the FBI highlighted several cyberattacks in 2021 and 2022 against agricultural
cooperatives, demonstrating a significant disruption to grain production and noting that it could
impact the entire food chain since grain is a crucial input in multiple parts of the agricultural
supply chain (FBI, 2022).
Barriers to Cybersecurity Adoption and Farmer Education
Farm owners are the chief executive officer (CEO) of their operation and, in this role,
face a wide variety of decision-making challenges that present themselves on the farm, including
those regarding Agriculture 4.0 technology adoption and implementing cybersecurity practices
and the farmers are often the central decision-maker (Annosi et al., 2019). Annosi et al. (2019)
found a significant limitation in the agricultural sector, and thus, by extension, the entire FA
sector is that awareness of innovations and their potential benefits is low. Additionally, farmers
may be reluctant or unable to use newer technologies (Monteiro et al., 2021).
As such, and as highlighted by the WEF’s Global Cybersecurity Outlook 2023,
information must “translate cyber-risk issues into communication that C-suites and boards of
directors can use effectively.” The WEF noted that “awareness of cyber-risk issues, at the
executive level, has gone up” (WEF, 2023). Within the FA sector, especially farms, the

cybersecurity community must work to make agricultural CEOs aware of cyber-risk issues and
how they must protect their operations.
Farmers need to understand cybersecurity before understanding why they must
implement cybersecurity into their farming operations. Additionally, farmers may think their
operation is not digital or connected because they have not added Agriculture 4.0 technologies.
However, Nikander et al. (2020) defined agricultural cybersecurity as “the activities and
processes whose goal is to provide the farm with a cyber-physical system that can be trusted to
work as planned.” Further, the authors also highlight that for many small-to-medium farms,
external attacks are not the probable threats; instead, human error and the physical environment
of the farm are the most common problems (Nikander et al., 2020). While Nikander et al. (2020)
found these issues to be the most common for small-to-medium farms, the risk of a cyberattack
has increased in the years following their research.
Cybersecurity awareness is not a priority among most farmers. Still, it should be,
according to Botschner, and governments and major technology companies should work to help
farmers improve their cybersecurity while protecting critical infrastructure from threats
(Bueckert, 2022). The shift of the cybersecurity burden from the individual farm to the
companies providing Ag-IoT, data platforms, and other Agriculture 4.0 services aligns with the
new U.S. National Cybersecurity Strategy released in March 2023. The core areas of focus are
the moves to require that companies create devices and platforms that are “Secure-by-Design”
and “Secure-by-Default” rather than relying on the end user to be solely responsible for the
cybersecurity of their devices (The White House, 2023). Additionally, the updated strategy
emphasizes securing critical infrastructure, including the FA sector.

Is Cybersecurity Our Responsibility?
Farmers may also question why they, instead of providers, are responsible for
cybersecurity. One of the issues is that most user networks tend to be heterogeneous and are not
closed ecosystems that use only one company’s products (Zhang & Zhu, 2019). The composition
of many farm networks is devices and software from many manufacturers, each with different
vulnerabilities and values to the network (Zhang & Zhu, 2019). For example, Zhang and Zhu
(2019) note that a home network may have laptops, routers, smart speakers, cameras, and more;
some devices contain sensitive information that may inflict higher losses once compromised.
Additionally, each manufacturer must continue to update their products to mitigate newly
discovered vulnerabilities, referred to as patching the device or program. Larger companies, such
as Apple, Google, Microsoft, and John Deere, have large workforces dedicated to testing their
products, identifying new vulnerabilities, and creating a patch to close the hole. Smaller
companies are less likely to have the necessary resources to conduct penetration testing of their
products (Rittman, 2022). As a result, they may have vulnerabilities that remain undiscovered for
a long time, creating an opportunity for threat actors to use this vulnerability to access their
network.
Therefore, farmers must actively participate in their networks' cybersecurity, understand
their potential risks, and take a Defense-in-Depth approach. To improve cybersecurity within the
FA Sector, cyber professionals must also overcome potential skepticism and lack of awareness
(Hussain et al., 2020, March). Ultimately, it is incumbent upon cyber advocates to convince the
farmers that cybersecurity practices are not a burden but an incentive that helps protect against
possible cyberattacks and data breaches (Hussain et al., 2020, March). Further, farmers need the
required information to convince them to invest a portion of their limited resources into

cybersecurity for their operation with a demonstrated return on investment (ROI) (Watkins,
2022).
Cybersecurity is a complex field ranging from basic principles to those that are very
advanced (McDonough, 2024). Further, farming in the Agriculture 4.0 era has also become more
complex as farmers must learn new technologies and methodologies to leverage the opportunities
of Agriculture 4.0. Farmers are unlikely to become cybersecurity experts because of the required
combination of skills. Instead, farmers need exposure to cybersecurity concepts, why they are
essential, and where to seek additional information and assistance. While not being cybersecurity
experts, farmers must have basic cybersecurity skills as they digitize their farms. These can be
basic levels of cybersecurity skills, including basic cyber hygiene. Research by Such et al. (2019)
highlights “The Cyber Essentials” produced by the United Kingdom as an effective solution for
SMBs. Then, when a more complex issue or situation arises, farmers know that they have experts
they can reach out to for help.
Additionally, much of the existing research has not focused on the focus of
implementation stage regarding the determinants of IT adoption in SMBs (Annosi et al., 2019).
Annosi et al. (2019) also highlight that mainstream literature reports note that many SMB owners
and managers do not take part in formal learning activities, have limited peers or role models
within the company (i.e., farms), have limited time or financial resources available, and rely on
external contacts. Therefore, Annosi et al. (2019) highlighted that it is necessary to deepen the
understanding of how factors influence owners’ and managers’ adoption of new IT solutions,
which in the case of this research is Agriculture 4.0 and cybersecurity practices.

Ease of Use
Once farmers have decided to digitize their operations and adopt Agriculture 4.0
technologies, cyber advocates must also convince them to learn and adopt cybersecurity
practices. An initial barrier to adoption will be that farms tend to use systems that are simple,
easy to understand, and easy to operate (Li et al., 2020). Cybersecurity complexity will challenge
farmers’ willingness to adopt it into their operations. Also, the design of platforms and systems
should be user-friendly for farmers worldwide, considering their ethnic and linguistic
backgrounds, so the platforms will be more understood to overcome the reluctance to adopt the
technology (Kour & Arora, 2020). Cybersecurity platforms and tools are no exception; we
should consider these factors.
Farmers may also see the addition of cybersecurity and Agriculture 4.0 technology as
another potential nuisance in accessing their systems and data. Over the last several years,
farmers have been challenging John Deere regarding the “right-to-repair” (Carrier, 2023). As
John Deere has added technology to their equipment, they have restricted the owner’s ability to
repair their equipment, instead requiring owners to take their equipment to a certified John Deere
technician with access to proprietary data (Keeler, 2022). Following litigation of this issue, in
late 2022, John Deere agreed to allow owners to access the same manuals as technicians and
repair their equipment (Tomko, 2023). This years-long battle has led to a mistrust of John Deere
and technologically advanced equipment, raising the value of older models that are not locked
down and do not require a computer to repair them (Wiens, 2015). The preference for older, less
technologically advanced equipment may solve the issue of the right to repair and be less
vulnerable to cyber vulnerabilities. Still, it also means that farmers may be unable to take
advantage of the advances in Agriculture 4.0 and its potential benefits.

Cost of Entry
Digital technologies require substantial financial investment (Javaid et al., 2022), and the
costs associated with adopting Agriculture 4.0 technologies are a significant deterrent to the
digitization of the FA sector (Abbasi et al., 2022). Research has previously identified that the
monetary cost or the cost of difficulty directly impacts attitudes toward Agriculture 4.0 (Pierpaoli
et al., 2013). The cost of cybersecurity to secure the FA Sector is another facet of operational
business expenses that depends on the level of protection a farm wishes to achieve (Gadient,
2023). While there is no set dollar value of investment into cybersecurity to provide to farmers,
the key is that they should spend some amount on cybersecurity. The amounts vary across
sources, ranging from 5.6% to 20% of a company’s total IT spend (Rinaldi, 2023). Some
cybersecurity options are free or low cost and increase in price based on selected and adopted
cybersecurity technologies. Each farm operation should have its needs evaluated based on its risk
level, IT investment, and individual cybersecurity needs. For example, choosing an email service
such as Google Gmail offers free built-in cybersecurity protections not provided by other
providers but at the cost of using a fee-based third-party provider (Walker, 2021).
Another financial challenge is that small and medium-sized farms may not have the free
capital to invest in Agriculture 4.0 technologies and cybersecurity protections, so they may adopt
the technology without fully understanding or mitigating potential risks. Annosi et al. (2019)
noted that studies have found that cost-benefit trade-off relates to perceived usefulness and ease
of use, which relates directly to TAM and affects decision-making strategies. Without an
understanding of the usefulness and ease of use, it is possible for a farm that invests in either
Agriculture 4.0 or cybersecurity to see one become a barrier to entry for the other. Farmers often

will invest in Agriculture 4.0 before investing in cybersecurity due to the perceived return on
their investment, the direct impact on their operation, and their desire for more immediate returns
(Eckelkamp, 2021). Farmers should not have to sacrifice cyber safety in exchange for
modernization.
Data Challenges
The ability to generate data is vital to Agriculture 4.0 decision-making and the digital
transformation of agriculture to reduce manual work and improve productivity; however, Liu et
al. (2021) highlight that most agricultural machines are still predigital and, therefore, do not
create data for Agriculture 4.0 decision-making platforms to leverage. Additionally, the right-
torepair issues highlighted previously push farmers away from technologies that could benefit
their bottom line with increased yields, productivity, and efficiency.
According to Liu et al. (2021), farmer participation is essential to big data success in
agriculture. Because of this, it is necessary to demonstrate the benefits for farmers so that they
are willing to participate in agricultural data exchange (Liu et al., 2021). Additionally, as data
sharing was an issue for the previous agricultural ISAC, farmers must be convinced that sharing
data benefits their operation.
One issue with Agriculture 4.0 is that the functions may be imprecise, leading to lessthan-
optimal agricultural activities and production chains, according to Muhl and Oliveira
(2022). When this happens, digital systems can generate large volumes of erroneous data (Muhl
& Oliveira, 2022). It is also an issue in agriculture that the various systems collecting data do not
have a mechanism to co-relate it, making monitoring and analyzing agricultural data challenging
(Katamreddy et al., 2019).

Ron Baruchi, CEO of Agmatix, said that a significant challenge for the agricultural
industry is that the number of data solutions and the number of data points generated per acre on
a farm have grown exponentially, and connecting these data points into meaningful results for
farmers is a challenge (Gray, 2023 March). Additionally, due to the number of digital modeling
tools creating siloed data, Baruchi believes data standardization standards would increase
collaboration (Gray, 2023 March). Ultimately, he believes that “open data is the future” (Gray,
2023 March). One platform that seeks to integrate data from disparate sources is Esri. This GIS
software company highlights that its ArcGIS platform can “collect, maintain, analyze, and share”
agriculture data to inform decision-making through its ability to bring various data sets together
to create maps and visualize farm data (Esri, 2023).
Microsoft’s Project FarmVibes
Third-party platforms are another option that allows farmers to store, manage, and
analyze their data. Through Microsoft’s Project FarmVibes, Microsoft indicates that their goal is
to help farmers adopt sustainable agricultural practices, which includes the application of
Agriculture 4.0, to address climate change; however, Microsoft highlighted that the lack of data
from farms makes it difficult to make progress towards new agricultural practices (Microsoft,
2023). Thus, the goal of Project FarmVibes “is to enable researchers, practitioners, and data
scientists to build affordable digital technologies to help farmers (1) estimate the emissions in
their farms, (2) with climate adaptation by predicting weather variations, and (3) determine the
right management practices that can be profitable and help improve soil health” (Microsoft,
2023).

Connectivity
Connectivity to digital networks, highlighted as those technologies that are part of
ICT4Ag, is vital to utilize Agriculture 4.0 and learn about new technologies and how to apply
them to the farm, including cybersecurity. Jahmy Hindman, Senior Vice President and Chief
Technology Officer at John Deere, noted that a challenge for rural farmers is that terrestrial
cellular service is not always available, or when it is, it is insufficient to enable Agriculture 4.0
technologies (Brennan, 2023). Researchers have also highlighted the issue of connectivity.
Beluhova-Uzunova and Dunchev (2022) identified connectivity and digital infrastructure as
barriers and challenges to Agriculture 4.0 and the lack of digital competencies in rural areas.
To solve the communications gap, Deere has sought to partner with companies in satellite
communications to enable their Agriculture 4.0 services (Brennan, 2023). While Deere had not
previously mentioned Starlink by SpaceX, in January 2024, Deere announced an agreement with
SpaceX to provide satellite communications (SATCOM) to farmers to overcome rural
connectivity challenges and enable rural farmers to leverage precision agriculture technologies
fully (Deere, 2024). Starlink provides high-speed, low-latency satellite internet in rural areas that
traditionally lack this quality of broadband internet (Starlink, 2023). In the press release,
Hindman highlighted that this SATCOM solution brings satellite communications to farmers at
scale to maximize the value of connectivity (Deere, 2024).
Education and Outreach
The need to educate everyone involved in the FA Sector, especially those related to
Agriculture 4.0, about cybersecurity has increased as the digital transformation has taken hold.
Annosi et al. (2019) found that a significant problem related to adopting new digital technology
is that many decision-makers do not have the relevant knowledge, which hinders strategic

actions and may limit the ability to act on perceived opportunities and incentives. Research has
also found that hurdles to adopting cybersecurity are a lack of farmer awareness of cybersecurity,
a lack of expertise in IT, a lack of resources, and connections to outside experts who could help
farmers (Nikander et al., 2020). Additionally, Agriculture 4.0 increases the learning load for
farmers (Eastwood et al., 2019). This learning burden can apply to Agriculture 4.0 technologies
and the principles and practices of cybersecurity.
Recognizing the need to improve agricultural cybersecurity, the 2022 South Dakota
Legislature passed House Bill 1092, which appropriated $1.25 million to create the precision
agriculture cybersecurity CyberAg partnership initiative between South Dakota State University
and Dakota State University (South Dakota HB 1092). The partnership aims to develop
“undergraduate and graduate curricula, engaging in research, and providing associated outreach
programming and communication to address agricultural security threats” (South Dakota HB
1092). To address vulnerabilities in agriculture and cyber threats, both universities planned to
work together to increase communication between each other and the agricultural industry and to
understand what farmers are worried about (Maruri, 2022). The South Dakota State University
Extension director highlighted that “communication, research, and education are needed to
strengthen the relationship between agriculture and cybersecurity (Elkins, 2022). The CyberAg
partnership will educate farmers about cyber threats impacting Agriculture 4.0 technologies
(Elkins, 2022).
This state-level partnership is a model that other states and universities can use to
increase cybersecurity awareness and preparedness within their FA Sector. College programs
focused on agriculture and agribusiness must also add cybersecurity training into their
curriculum (Clemens, 2022). According to Doug Jacobson, University Professor of electrical and

computer engineering (ECpE) and the director of the ISU Center for Cybersecurity Innovation
and Outreach, the goal of the program at Iowa State University is to add a cybersecurity context
into courses where cybersecurity is relevant (Clemens, 2022). The focus on developing
educational curricula will lead to new graduates with cyber skills who will have an advantage
over their peers who do not have the same level of awareness. Farm operations will hire
graduates of these programs, and they will have essential cybersecurity awareness and be able to
bring this information to the farm, helping to strengthen cybersecurity protection within the FA
sector.
Another way that farmers learn is by relying on their social networks to gain awareness
about new technologies, techniques, and information (Chaudhuri et al., 2021). Rust et al. (2022)
found that farmers trusted other farmers most to learn new information. In their study, Rust et al.
(2022) found that farmers were less trusting of traditional experts from academic and
government institutions. Additionally, farmers rely on advisors from companies they interact
with and those in agricultural education and outreach efforts that are known for their
collaboration with farmers (Rust et al., 2022). The need for cybersecurity information has led
Iowa State University to conduct training and outreach to educate farmers, companies, and
organizations about cybersecurity (Iowa State University of Science and Technology, 2024). For
farmers to educate one another, cybersecurity education and awareness must be implemented
across all aspects of farming. For example, when farmers attend a trade show or seminar and
learn something new, they often return home and share the information with their peers.
Therefore, those instructing or advising farmers must educate themselves in cybersecurity and
cyber hygiene practices to pass the information on to farmers.

Education will also help apply cybersecurity practices to farms, but the information
presented must be easy for farmers to understand. Those working in the cybersecurity field must
close the communication gap with non-technical audiences so the audience understands the
importance of their recommendations and applies them to farm operations (WEF, 2023). The
WEF noted that cyber professionals must use less technical jargon when communicating their
message (WEF, 2023), and in farming communities where cyber awareness may be deficient, it is
even more important that information be understandable and related to agriculture.
The Need for Advisors
Advisors are an essential source of support for farmers regarding further changes in farm
management practices (Eastwood et al., 2019). Shang et al. (2021) reported that consultants,
meaning advisors, are significantly associated with technology adoption by farms. Advisors act
as “sense makers” to help farmers understand the Agriculture 4.0 innovation system and achieve
more value from these technologies rather than being just promoters or barriers to technology
uptake (Eastwood et al., 2019). Eastwood et al. (2019) identified a research gap in the
farmeradvisor relationship, advisors and farm data and technology, and the ability to identify
priorities to enable advisors to be successful components of the Agriculture 4.0 future. Eastwood
et al. (2019) also noted that Agriculture 4.0 presented a unique innovation challenge due to the
influence of commercial technology companies and the new knowledge demands for farmers in a
“highly dynamic, technology-driven environment.” In the overall technology adoption process,
advisors are critical to support farmers learning about the nature of the digital data created by
Agriculture 4.0 and how to interpret the data (Eastwood et al., 2019). Additionally, many people
rely on advisors to gain cybersecurity awareness and training, and this needs to be an additional
focus area for advisors in a digital agriculture era.

Another reason advisors are critical is that most farmers do not understand the
significance of Agriculture 4.0 technologies, how to implement them, and which technologies are
suitable for their farm and specific requirements (Abbasi et al., 2022). They are also likely to
need assistance understanding these technologies' cybersecurity requirements. Therefore, it is
incumbent on farm advisors to educate farmers on why they need Agriculture 4.0, as well as
convince farmers that new methodologies are beneficial and that these changes have a positive
effect (Gray, 2023 April). Kelly Klosterman, an advisor with Wright Implement, noted that some
farmers are not aware of the tools available to them or that they are overwhelmed by the
technology, and it is her role as an advisor to communicate information effectively and help
farmers become comfortable with the new technology (Gray, 2023 April).
The importance of the ability to consult an advisor was highlighted by Cole the Cornstar
(2023) as he used Agriculture 4.0 technologies to map the boundaries of his farm fields for use
with his precision agriculture planter. Not realizing that a setting was incorrect for the GPS data
collection, Cole spent hours mapping the boundaries of his farm (Cole the Cornstar, 2023). When
he attempted to use the data, Cole learned that he had set the GPS differential source to WAAS
(Wide Area Augmentation System) and EGNOS (European Geostationary Navigation Overlay
System) instead of the correct setting for TerraStar-X real-time kinematic positioning (RTK)
(Cole the Cornstar, 2023). After mapping the fields again, Cole learned that an error had
occurred. After another investment of his time, he learned that his high-resolution GPS
subscription had expired, forcing Cole to map his fields for a third time (Cole the Cornstar,
2023).
Additionally, the errors were more costly as Cole and his family’s farm is 1,700 acres
spread across several locations, which increased the time required to correct the mapping error.

While Cole is a young, technologically adept farmer, he still makes several errors that cost him
time and resources. He highlighted the value of an Agriculture 4.0 advisor who can help ensure
proper configurations before wasting resources. These errors highlight the challenges of adopting
Agriculture 4.0 technologies and the importance and value of trusted advisors.
Another area farmers will rely on advisors is cyber insurance, a recent addition to
insurance options that can offer some protection to mitigate the damage from a cyber incident
(WEF, 2023). According to the WEF (2023), 48% of smaller organizations examined did not
have cyber insurance, and the WEF believes this is a critical gap in cyber resilience. Additionally,
WEF (2023) highlighted that smaller organizations are less likely to have the resources necessary
to respond to cyber-attacks. Agriculture-focused cyber insurance advisors and agents must advise
the FA sector on the benefits of cyber insurance and the proper policy for the farm.
Labor Challenges
Globally, there is a shortage of approximately 3.4 million cybersecurity workers ((ISC)2,
2022). According to the WEF (2023), recruiting and retaining cyber talent continues to be
challenging, and expanding the talent pool will require “time, thought, and investment.”
Many farms, especially small and medium-sized farms, do not have the budget to hire a
full-time cybersecurity worker; instead, they may rely on an outside consultant to provide
cybersecurity training or services to their farm (Aucott, 2023). If an agricultural operation is
large enough to hire a cybersecurity employee, it will compete against all other organizations
looking to hire the same talent. Additionally, finding cybersecurity talent with a background in or
familiarity with agriculture and Agriculture 4.0 technologies will further compound the
challenge.

Skilled workforce: Consultancies and advisorships must have enough cyber-focused
talent and be knowledgeable about cybersecurity (Uche, 2024) and agriculture. On the farm side,
they may not be large enough to have internal IT or cyber talent, and they will rely on either
being made aware of the issues for themselves to deal with or perhaps they will receive
cybersecurity information but are not experts. On the college front, programs must ensure
cybersecurity exposure to agricultural program graduates and make them aware of the issues they
should be familiar with, as detailed in the education section of this literature review.
The Technologist Farmer
The modern farmer must be familiar with technology, develop skills to take advantage of
Agriculture 4.0 and be aware of cybersecurity principles to protect their operation. Monteiro,
Santos, and Goncalves (2021) highlight that a commercial farmer, and by extension any farmer
using technology on the farm, needs to become an IT manager able to operate in an office or at a
computer screen rather than solely in the field controlling a machine by hand and adjusting
equipment manually. Previous research has found that confidence in computer use is one of the
most important drivers affecting agricultural technology adoption (Pierpaoli et al., 2013). This
lack of confidence leads to another challenge: farmers may not be familiar with computer
knowledge. They would rather not spend too much time learning to use Agriculture 4.0 decision
support systems (Zhai et al., 2020). Instead, Zhai et al. (2020) found that farmers want the
systems to inform them how to perform agricultural activities efficiently. This challenge is also
present for farmers to invest time to learn about cybersecurity.
Additionally, the farmer's age is not always a barrier to technology adoption, as Nikander
et al. (2020) found that older farmers are not the only ones requiring support. They also cited
research that younger tech-savvy farmers require help. They note that a barrier to small and

medium farms adopting agricultural cybersecurity is a lack of trained staff or cybersecurity
experts (Nikander et al., 2020). The digitization of agriculture, therefore, brings a new set of
problems to the farm that they may be unable to manage (Nikander et al., 2020), thus creating a
barrier to adoption.
Farmers must become technologists, at least at a basic level of competency, to maintain a
competitive advantage, leverage the benefits of Agriculture 4.0, and understand the farm's
required cybersecurity needs. To facilitate adoption, stakeholders must recognize the value
proposition of Agriculture 4.0 technologies and robust cybersecurity practices.
Farm-Focused Research
To best benefit the FA Sector, researchers focused on cybersecurity must tailor their work
towards the sector and those operating in this space, such as the “Cybersecurity for Smart
Agriculture” effort by Iowa State University of Science and Technology (2024). Because of the
unique and very diverse environment presented by agriculture and the diverse knowledge levels
of those within the FA Sector, researchers should focus on understanding each component better
and more broadly (Nikander, 2020). Further, it is not enough to tell farmers they should
implement Agriculture 4.0 and cybersecurity on their farms in tandem; researchers should
identify information addressing specific knowledge needs and use cases. Legislation introduced
in 2023 would increase this focus by establishing five research centers focused on agricultural
security (Opsahl, 2023). With research focused on the FA Sector, the perceived ease of use and
perceived value will be better, leading to higher adoption rates. Additionally, as the threat
landscape has continued to evolve with more threat actors focused on the FA Sector, research
must examine how cybersecurity can benefit it and how to encourage its adoption best.
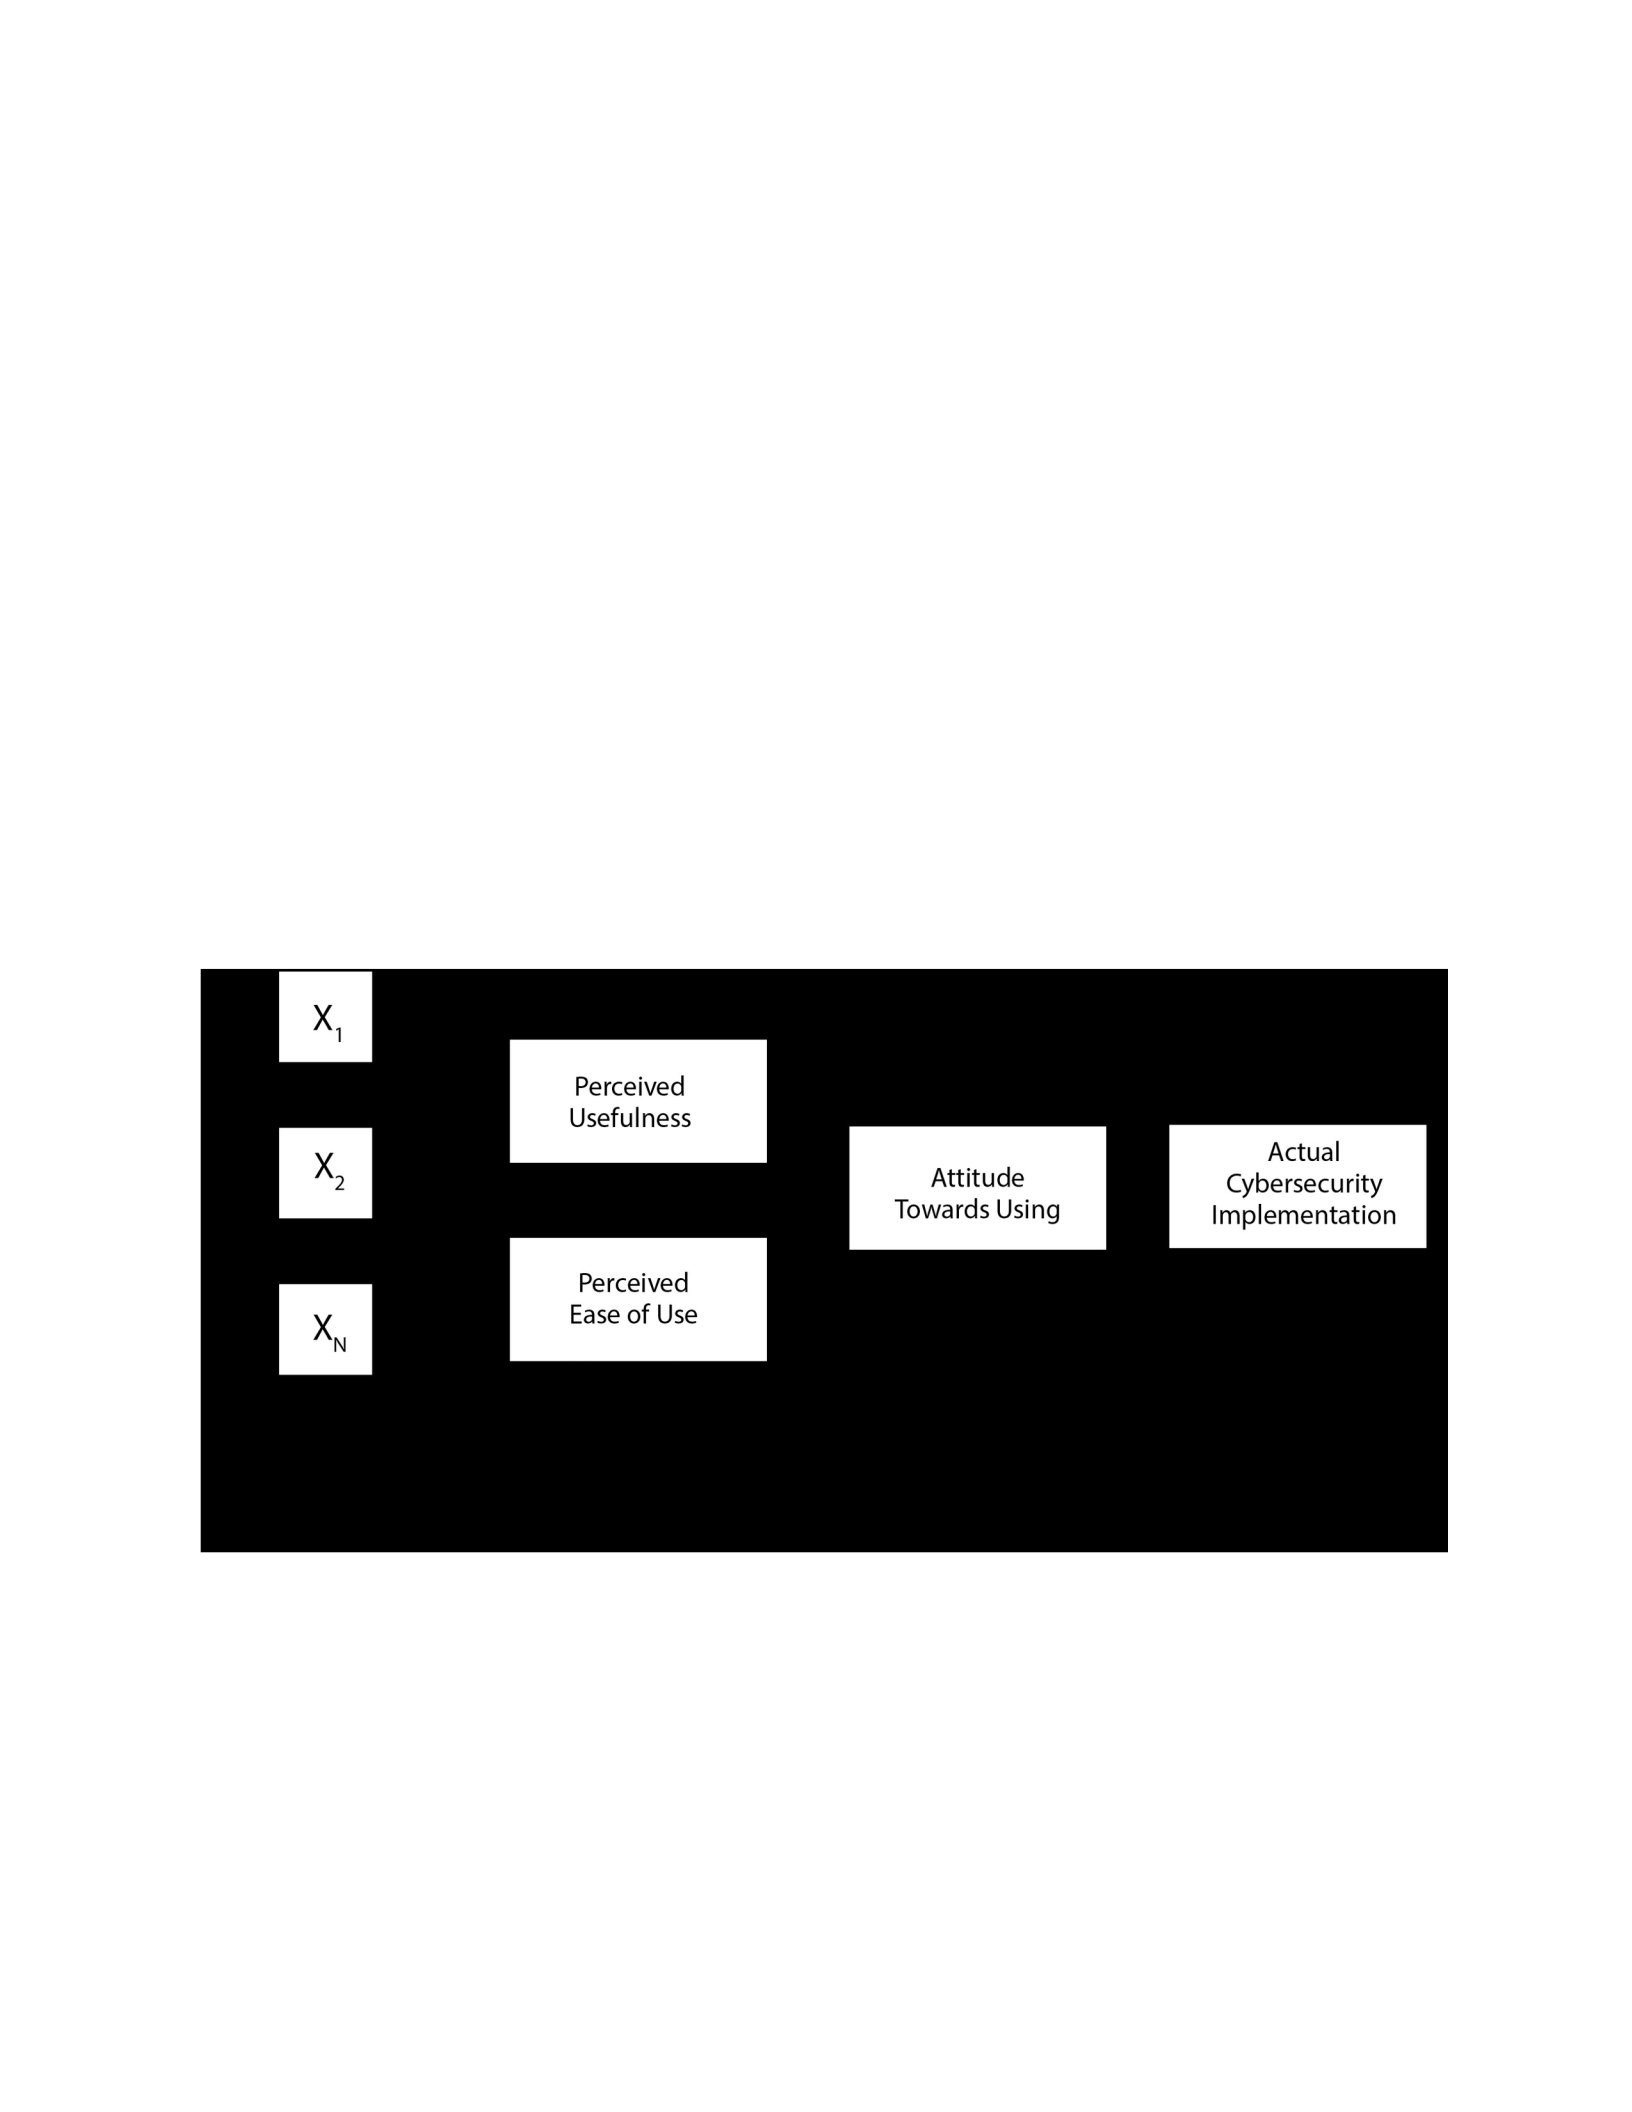
Technology Acceptance Model (TAM)
The conceptual framework for this study is the TAM and the central aspects of perceived
usefulness (PU) and perceived ease of use (PEU) that impact a user’s attitude towards a system,
in this case, cybersecurity principles and best practices as applied to Agriculture 4.0. Davis
(1986) created TAM to understand the influence of a user’s attitude by the PU and PEU of a
system to determine if a user will adopt the system. In the case of applying TAM to
cybersecurity, cybersecurity practices will substitute for the idea of a system (Figure 2). TAM
notes that individuals will avoid using a product because it is not easily understood or used.
Figure 2
TAM Cybersecurity
Note. Adapted from the TAM Designed by Davis (1986)
Previous studies utilized TAM to understand factors influencing adopters of precision
agriculture technologies. They found that PU and PEU significantly affect one’s attitude toward
using precision agriculture technologies (Pierpaoli et al., 2013). According to Pierpaoli et al.

(2013), a deficiency in one of these constructs will negatively affect the adopter’s attitude toward
using or adopting these technologies. Research also found that while usefulness and ease of use
are central aspects of technology adoption, these factors become negative if they cause a
significant increase in the cost of production (Pierpaoli et al., 2013). While these studies have
examined factors related to adopting Agriculture 4.0 technology alone, studies have not utilized
TAM to understand the factors that impact the attitude toward cybersecurity in conjunction with
Agriculture 4.0 technologies.
Additionally, while Pierpaoli et al. (2013) detailed research has shown that farm size is
also a factor influencing technology adoption, more recent publications highlighted earlier in this
literature review have demonstrated that Agriculture 4.0 technologies can be helpful when
adopted by farms of all sizes. Farms must adopt cybersecurity in conjunction with Agriculture
4.0 technologies. Therefore, TAM will help understand farmers' attitudes towards adopting
cybersecurity and Agriculture 4.0 technologies in Michigan.
Summary
Reviewing literature focused on the digital transformation of agriculture into Agriculture
4.0, research has identified many new technologies and techniques based on sensors, data, and
analysis driving agriculture toward a micro-level management system with data-driven
decisionmaking. Many of the works highlighted here note that Agriculture 4.0 brings increased
efficiency and productivity to the farm but at the risk of increasing attack surfaces and
opportunities for cyber-attacks and device failure to impact the farm negatively. Additionally,
many farmers are reluctant to add new technologies to their farms, and when they do, they do not
fully understand the introduced cybersecurity risks.

Thus, there is a knowledge gap between research focused on Agriculture 4.0, the
associated need for cybersecurity, and how America’s farmers, specifically farmers in Michigan,
view these changes. This dissertation addresses this knowledge gap and provides insight into
Michigan family farm views regarding cybersecurity and Agriculture 4.0. Additionally, this work
seeks to inform the cybersecurity community on ways to overcome barriers to adopting
cybersecurity practices within farms in Michigan and, ultimately, the United States by identifying
the knowledge gaps in the farm community.
Chapter 3: Methodology
This chapter provides an overview of the research methodology utilized in this
quantitative non-experiential study. This study specifically utilized survey research to gather
primary data across a broad population of Michigan family farm owners or decision-makers.
Additionally, this chapter elaborates on the guiding research paradigm of postpositivism, the
reasoning behind the selected research methodology, the identification of the target population,
sampling method, and sample size, details the data collection instrument and outlines the data
analysis methods.
Research Methodology
First, the overarching research paradigm chosen for this study is postpositivism, also
called the scientific method, which replaced positivism after World War II (Mackenzie & Knipe,
2006). Positivism relies on the view that a scientist works with observable reality within society,
leading to generalizations (Alharahsheh & Pius, 2020). Positivism research also focuses on
discovering observable and measurable facts, and the researcher seeks to find causal
relationships between the collected data (Alharahsheh & Pius, 2020).

Creswell and Creswell (2018) detailed that postpositivism assumptions represented the
traditional form of research and held true more for quantitative research. Postpositivism also
develops knowledge based on observation and measurement; studying individuals’ behavior is
paramount (Creswell & Creswell, 2018, p. 7). Additionally, postpositivism sees the researcher
begin with a theory, collecting data that supports or refutes the theory, then making necessary
revisions and conducting additional tests. Finally, this paradigm relies on a researcher collecting
information on instruments based on measurements completed by the study participants
(Creswell & Creswell, 2018, p. 7). With this study's reliance on a survey instrument to quantify
individuals' views on cybersecurity within modern farm operations, the postpositivism paradigm
is best suited to guide this research.
Next, this study utilized quantitative research methodology with a non-experimental
design to discover relationships between independent and dependent variables within a
population (Mohajan, 2020). Further, quantitative research utilizes numbers and accuracy
(Rutberg & Bouikidis, 2018) collected via instrument-based questions through a survey to
measure attitudes or opinions of a population with the “intent of generalizing from a sample to a
population” and test a hypothesis (Creswell & Creswell, 2018).
Creswell and Creswell (2018) explained that a survey design provides a quantitative
description of a population's attitudes and opinions and can test for associations among variables
of a population by studying a sample of that population. Additionally, survey designs help
researchers answer descriptive questions about the relationship between variables (Creswell &
Creswell, 2018). Two further reasons to utilize quantitative research methods are that a lack of
research exists on a topic or there are unanswered research questions (Rutberg & Bouikidis,

2018). These reasons further support postpositivism’s use of an instrument to collect data
supporting this research study.
Initial reviews of existing literature indicated research is lacking on family farmers’
attitudes and perceptions of cybersecurity ease of use and usefulness in the era of Agriculture 4.0.
Therefore, utilizing a quantitative research study to examine a sample of the family farm
population in the State of Michigan research setting is the best method to understand their views
and attitudes towards cybersecurity and using Agriculture 4.0. Additionally, this method allowed
closed-ended questions to obtain large amounts of data from a greater sample size than would
have been possible in the same amount of time utilizing qualitative methods (Asenahabi, 2019).
This research collected data using a cross-sectional study using a non-experimental design, with
observations of each survey participant collected at one point in time (Asenahabi, 2019).
Research Questions, Data Collection, Instrumentation, and Data Analysis
To investigate the barriers to cybersecurity adoption among Michigan family
farms, the researcher crafted a central research question to define the study's overall purpose and
developed six sub-questions to investigate the relationships among the variables. Each sub-
question relies on hypotheses to predict expected outcomes and utilizes statistical analysis to test
each hypothesis (Creswell & Creswell, 2018, p. 136). The null hypothesis (H0) predicted that no
relationship existed between the variables, while the alternative hypothesis (HA) predicted that a
significant relationship existed between the variables (Creswell & Creswell, 2018, p. 137). The
results of each sub-question inform the findings supporting the central research question.

Research Questions
Central Research Question:
What specific factors hinder the successful adoption of cybersecurity measures among
family-owned farms in the State of Michigan?
Associated RQ:
1. How do knowledge gaps and digital connectivity influence cybersecurity adoption
among family farms in Michigan?
2. How do size, resources, and technological expertise shape the cybersecurity
landscape for Michigan's family farms?
3. How do assessed impact, risk perception, and decision-making influence
cybersecurity adoption among family farms in Michigan?
4. How do financial constraints and perceived ROI impact cybersecurity adoption
among family farms in Michigan?
5. Does geographical location in the State of Michigan influence the adoption of
cybersecurity measures among family farms in Michigan?
6. What are the most effective ways for government agencies, extension services, or
industry associations to collaborate to inform family farms in Michigan about the
value of cybersecurity and improve cybersecurity adoption among these farms, and
how do trusted agents influence the effectiveness of these efforts?
The Population and Sample
Researchers aim to study the entire target population, but recruiting the population is
often not feasible, so instead, the investigator will recruit a sample from the target population
(Majid, 2018) to create generalizations. The target population for this research is family-owned

farms in the State of Michigan. According to the USDA National Agricultural Statistics Service
(NASS) (2023), in 2022, the total number of farms in Michigan was 44,300, and the 2017
Census of Agriculture reported that 96% were family-owned farms (NASS, 2017). Based on this
information, the estimated target population eligible for this study is 42,528 farms. From this
population, eligibility criteria for study participants required that they be 18 years or older and
the farm owner or decision maker of a family farm in the State of Michigan.
Also, for the first time, the USDA included a question regarding adopting precision
agriculture in the 2022 census. While the data was unavailable until February 2024, according to
the 2022 USDA Census of Agriculture, 5,965 Michigan farms reported adopting precision
agriculture practices (USDA NASS, 2024). This number of farms equals a reported adoption rate
of 13.09% for precision agriculture practices in Michigan.
The sample size is essential “to generalize from a random sample and avoid sampling
errors or biases” (Taherdoost, 2017). According to Creswell and Creswell (2018), a larger sample
will provide more accuracy in the inferences made, but larger samples are more costly and
timeconsuming. For the sample in the study to be representative of the target population, the
ideal sample size would be 381 participants; the researcher calculated this sample size using
Qualtrics sample size calculator with a population size of 42,528, a 95% confidence level, and a
5% margin of error (Qualtrics, 2023). Even though the sample population for this study did not
reach the ideal sample size, the sample was large enough to result in a confidence level of 99%,
and participants’ views were statistically significant within the sample population. This
significance was determined using the required sample size calculated with OpenEpi Version
3.01, an opensource calculator. See Table 1.
Table 1 Sample Size for Frequency in a Population
Population size (for finite population correction factor or fpc)(N): 42258
Hypothesized % frequency of outcome factor in the population (p): 95%+/-5
Confidence limits as % of 100(absolute +/- %)(d): 5%
Design effect (for cluster surveys-DEFF): 1
Sample Size(n) for Various Confidence Levels
Confidence Level(%) Sample Size
95% 73
80% 32
90% 52
97% 90 99% 126
99.9% 205
99.99% 286
Equation
Sample size n = [DEFF*Np(1-p)]/ [(d2/Z21-α/2*(N-1)+p*(1-p)]
https://www.openepi.com/SampleSize/SSPropor.htm
Further, a statistical power analysis conducted using G*Power 3.1.9.7 determined the
required sample size for Pearson r correlation and Chi-square tests. According to Faul et al.
(2007), “the power of a statistical test is the probability that its null hypothesis (H0) will be
rejected given that it is in fact false.” Deciding which power analysis to use, Erdfelder et al.
(1996) consider a priori power analysis the ideal type of power analysis, as it allows researchers
to specify the effect size, alpha level (significance), and desired power level of the test.
Therefore, using a priori analysis, for a Person r correlation, G*Power calculated a required
sample size of 134 participants using the following parameters: test family, t-tests; statistical test,
correlation: Point biserial model; input parameters: tails, two; Effect size 0.3, α err prob = 0.05,
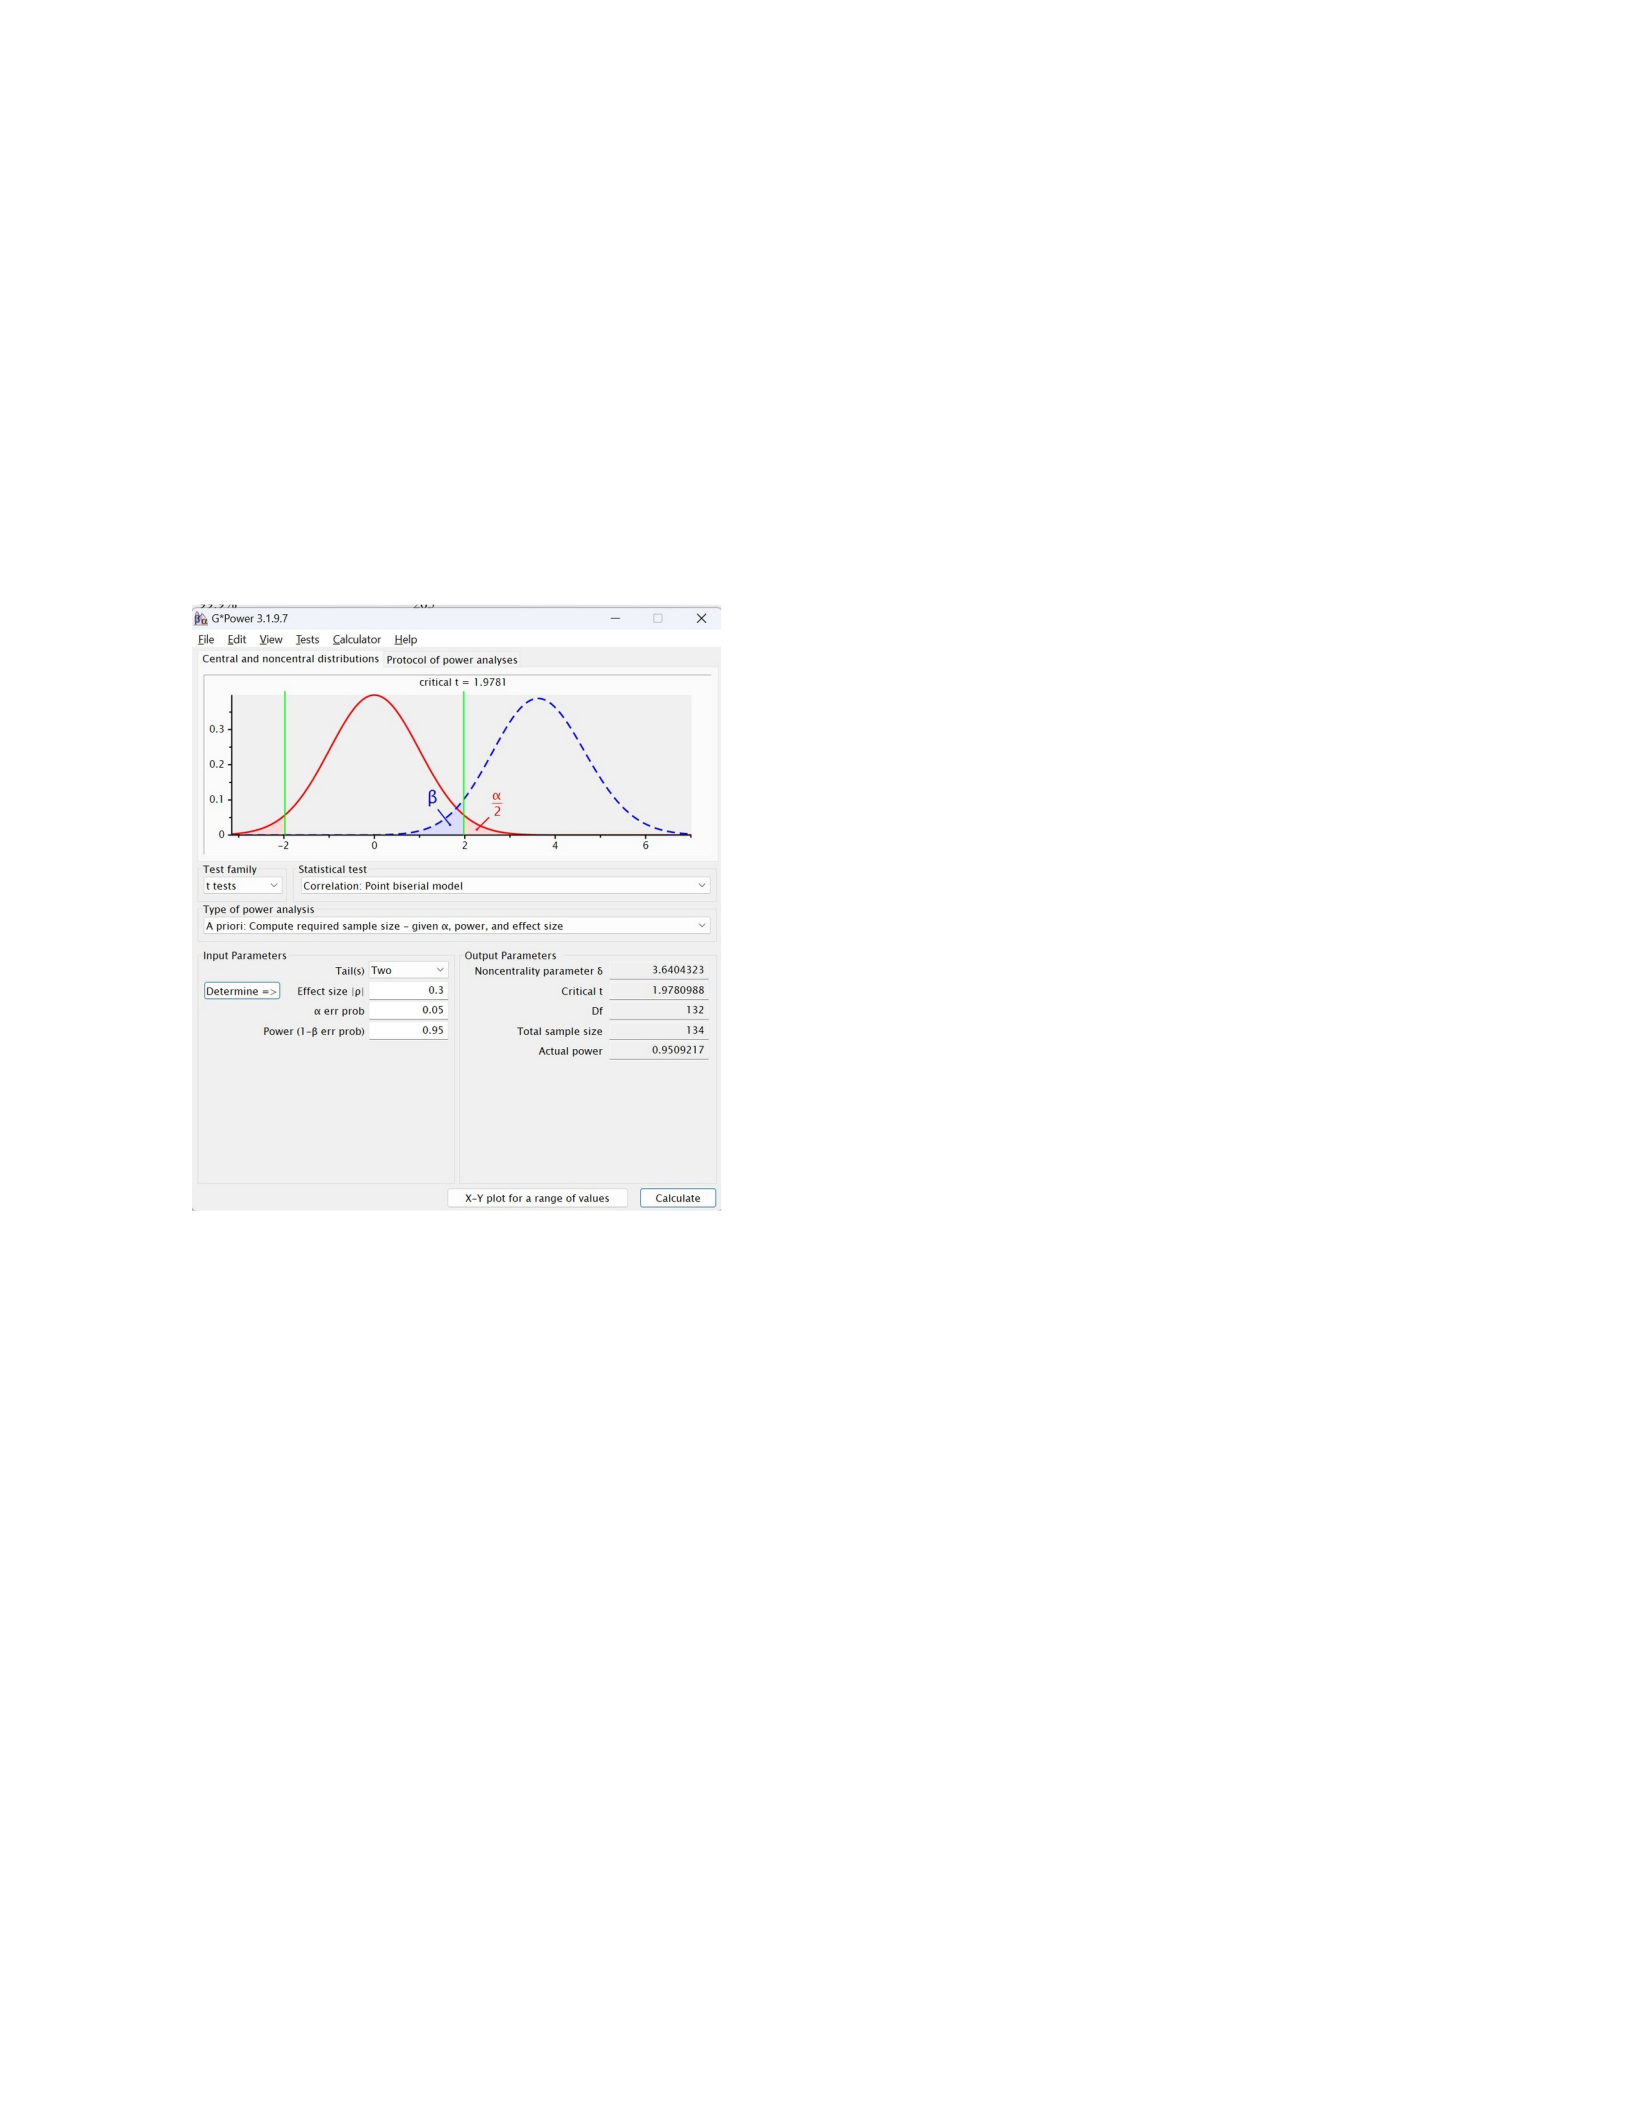
Power (1-β err prob) = 0.95, Correlation ρ H0 = 0 (Faul et al., 2007). See Figure 3. According to
these results, if the study samples 134 participants, there is a 95% chance of a significant result;
alternatively, there is a 5% chance that the result will not be significant.
Figure 3
G*Power for Pearson r correlation
For Chi-square tests, G*Power calculated a required sample size of 317 participants when
the Df = 16 and 405 participants when the Df = 32, with the following parameters: Test family x2
tests: Goodness-of-fit tests: Contingency tables, Effect size 0.3, α err prob = 0.05, Power (1-β err
prob) = 0.95, Df = 16 or 32. Decreasing the Power to 0.80 means that the chance that a
significant result will be determined decreases to 80%, and G*Power determined a required
sample size of 215 participants when Df = 16 and 280 participants when Df = 32. A discussion of
the sample size for this study compared to the G*Power sample size is in the Limitations section
of Chapter 5.
Figure 4
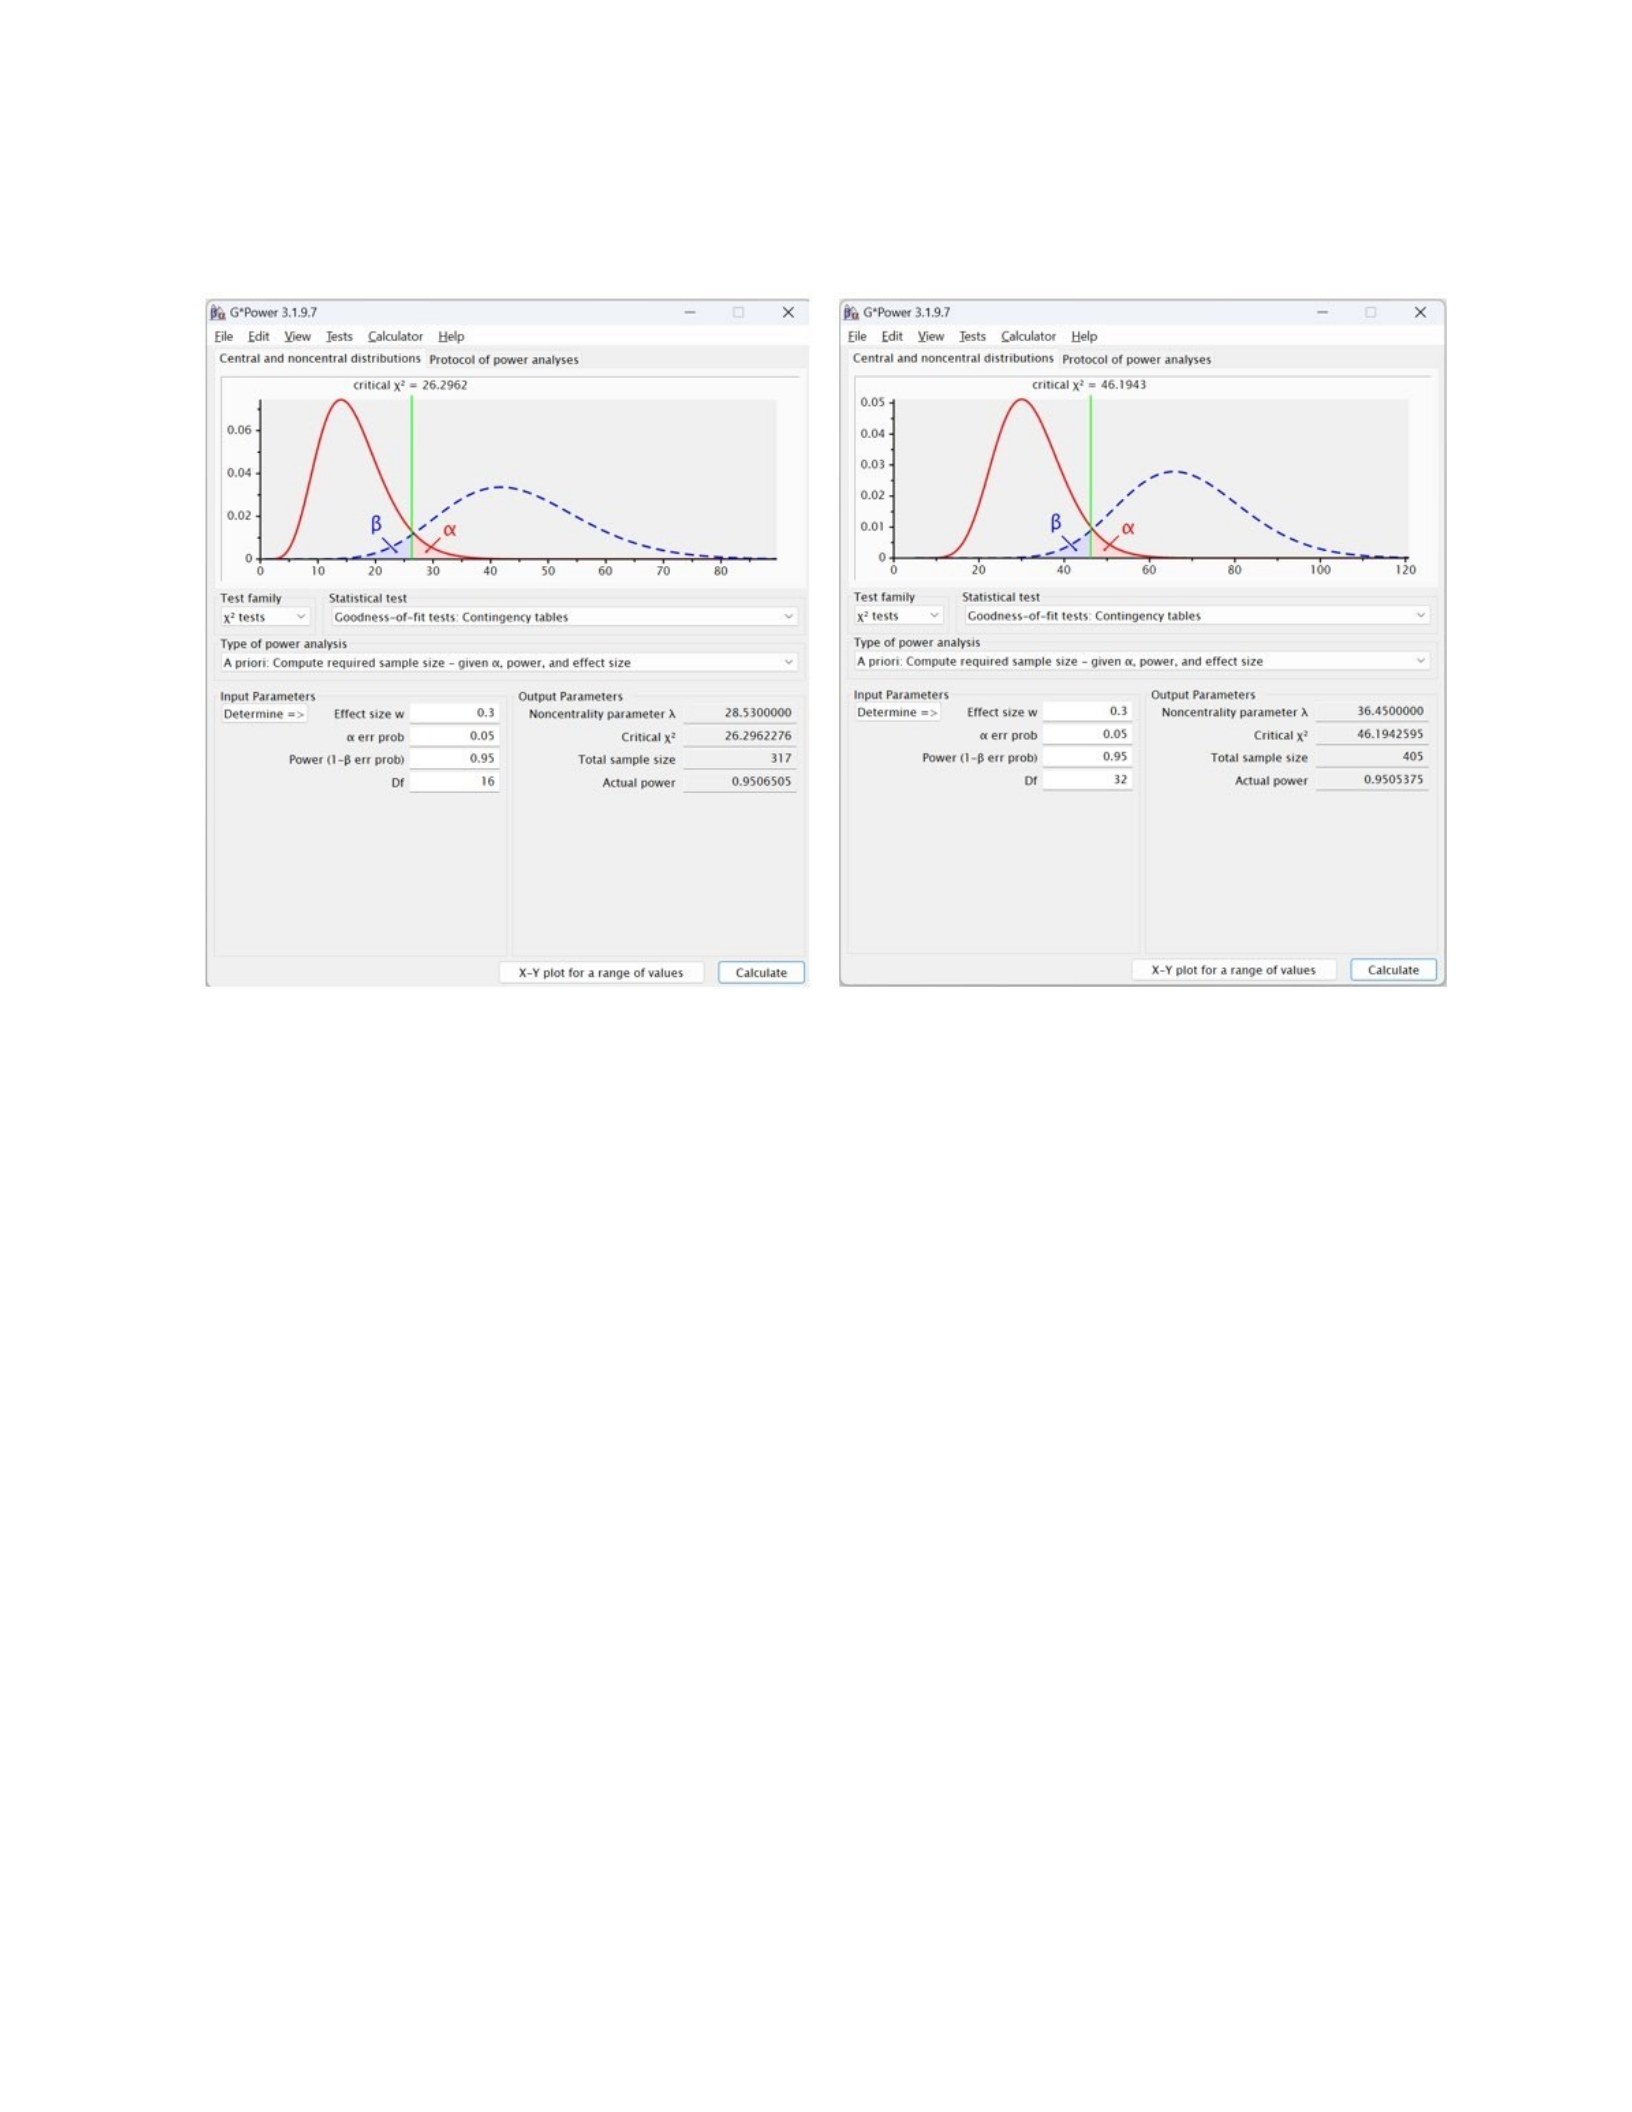
G*Power for Chi-Square Tests
Sampling Methodology
Before identifying survey candidates and attempting to recruit them, the researcher
sought review and approval from the Capitol Technology University Institutional Review Board
(IRB). See Appendix A. The researcher's employment with the Department of Defense (DoD)
necessitated additional IRB approval; however, the DoD does not sponsor this research. All the
views expressed are solely those of the researcher and not representative of the DoD.
Studying the entire target population is not always possible or practical in research
studies; the researcher will choose a population subset via a sampling method (Acharya et al.,
2013). The researcher used a simple random sampling method for this research. This method is a
probability sampling methodology to help ensure the generalizability of the results to the target
population (Acharya et al., 2013). This method ensures equal selection probability for every
family-owned farm in Michigan, the target population for this study.
While the reported target population is large, challenges exist in identifying individuals
and their electronic contact information within the population. Without public access to a
complete list such as that controlled by the USDA Farm Service Agency (FSA), the researcher
utilized internet research to identify individuals within the population who may be candidates for
the study. The researcher also conducted internet searches to identify trade groups within the
target population, such as the Michigan Soybean Association, and utilized publicly available lists
of their members. Additionally, the researcher conducted social media searches to identify farms
publicly identifying their operations on platforms such as Instagram and Facebook by Meta
Platforms, Inc., and a list of Michigan farms curated by Taste the Local Difference®, a
Michigan-based food consulting, media, and marketing agency
(https://www.localdifference.org/find-food-farms/).
Having identified the farms, the researcher sent introductory letters and invitations via
USPS mail and email to those farms identified through internet research. The letters introduced
this researcher, the reasons behind the research, and the survey instrument (see Appendix B). The
researcher instructed volunteers to access the survey and offered them the opportunity to
complete it if they met the eligibility criteria outlined earlier. Creswell and Creswell (2018)
highlighted that study participants should benefit from participating. Pennings et al. (2002) found
that most farmers expected compensation for surveys with an average of $15 and a median of
$10. So, upon completing the survey, participants could select a $10 gift card to Amazon,
Walmart, or Tractor Supply if they chose to do so. Participant names were not collected to protect
participant anonymity. However, participants provided email addresses where they could receive
their gift cards. The researcher emphasized that email addresses would be used solely for gift
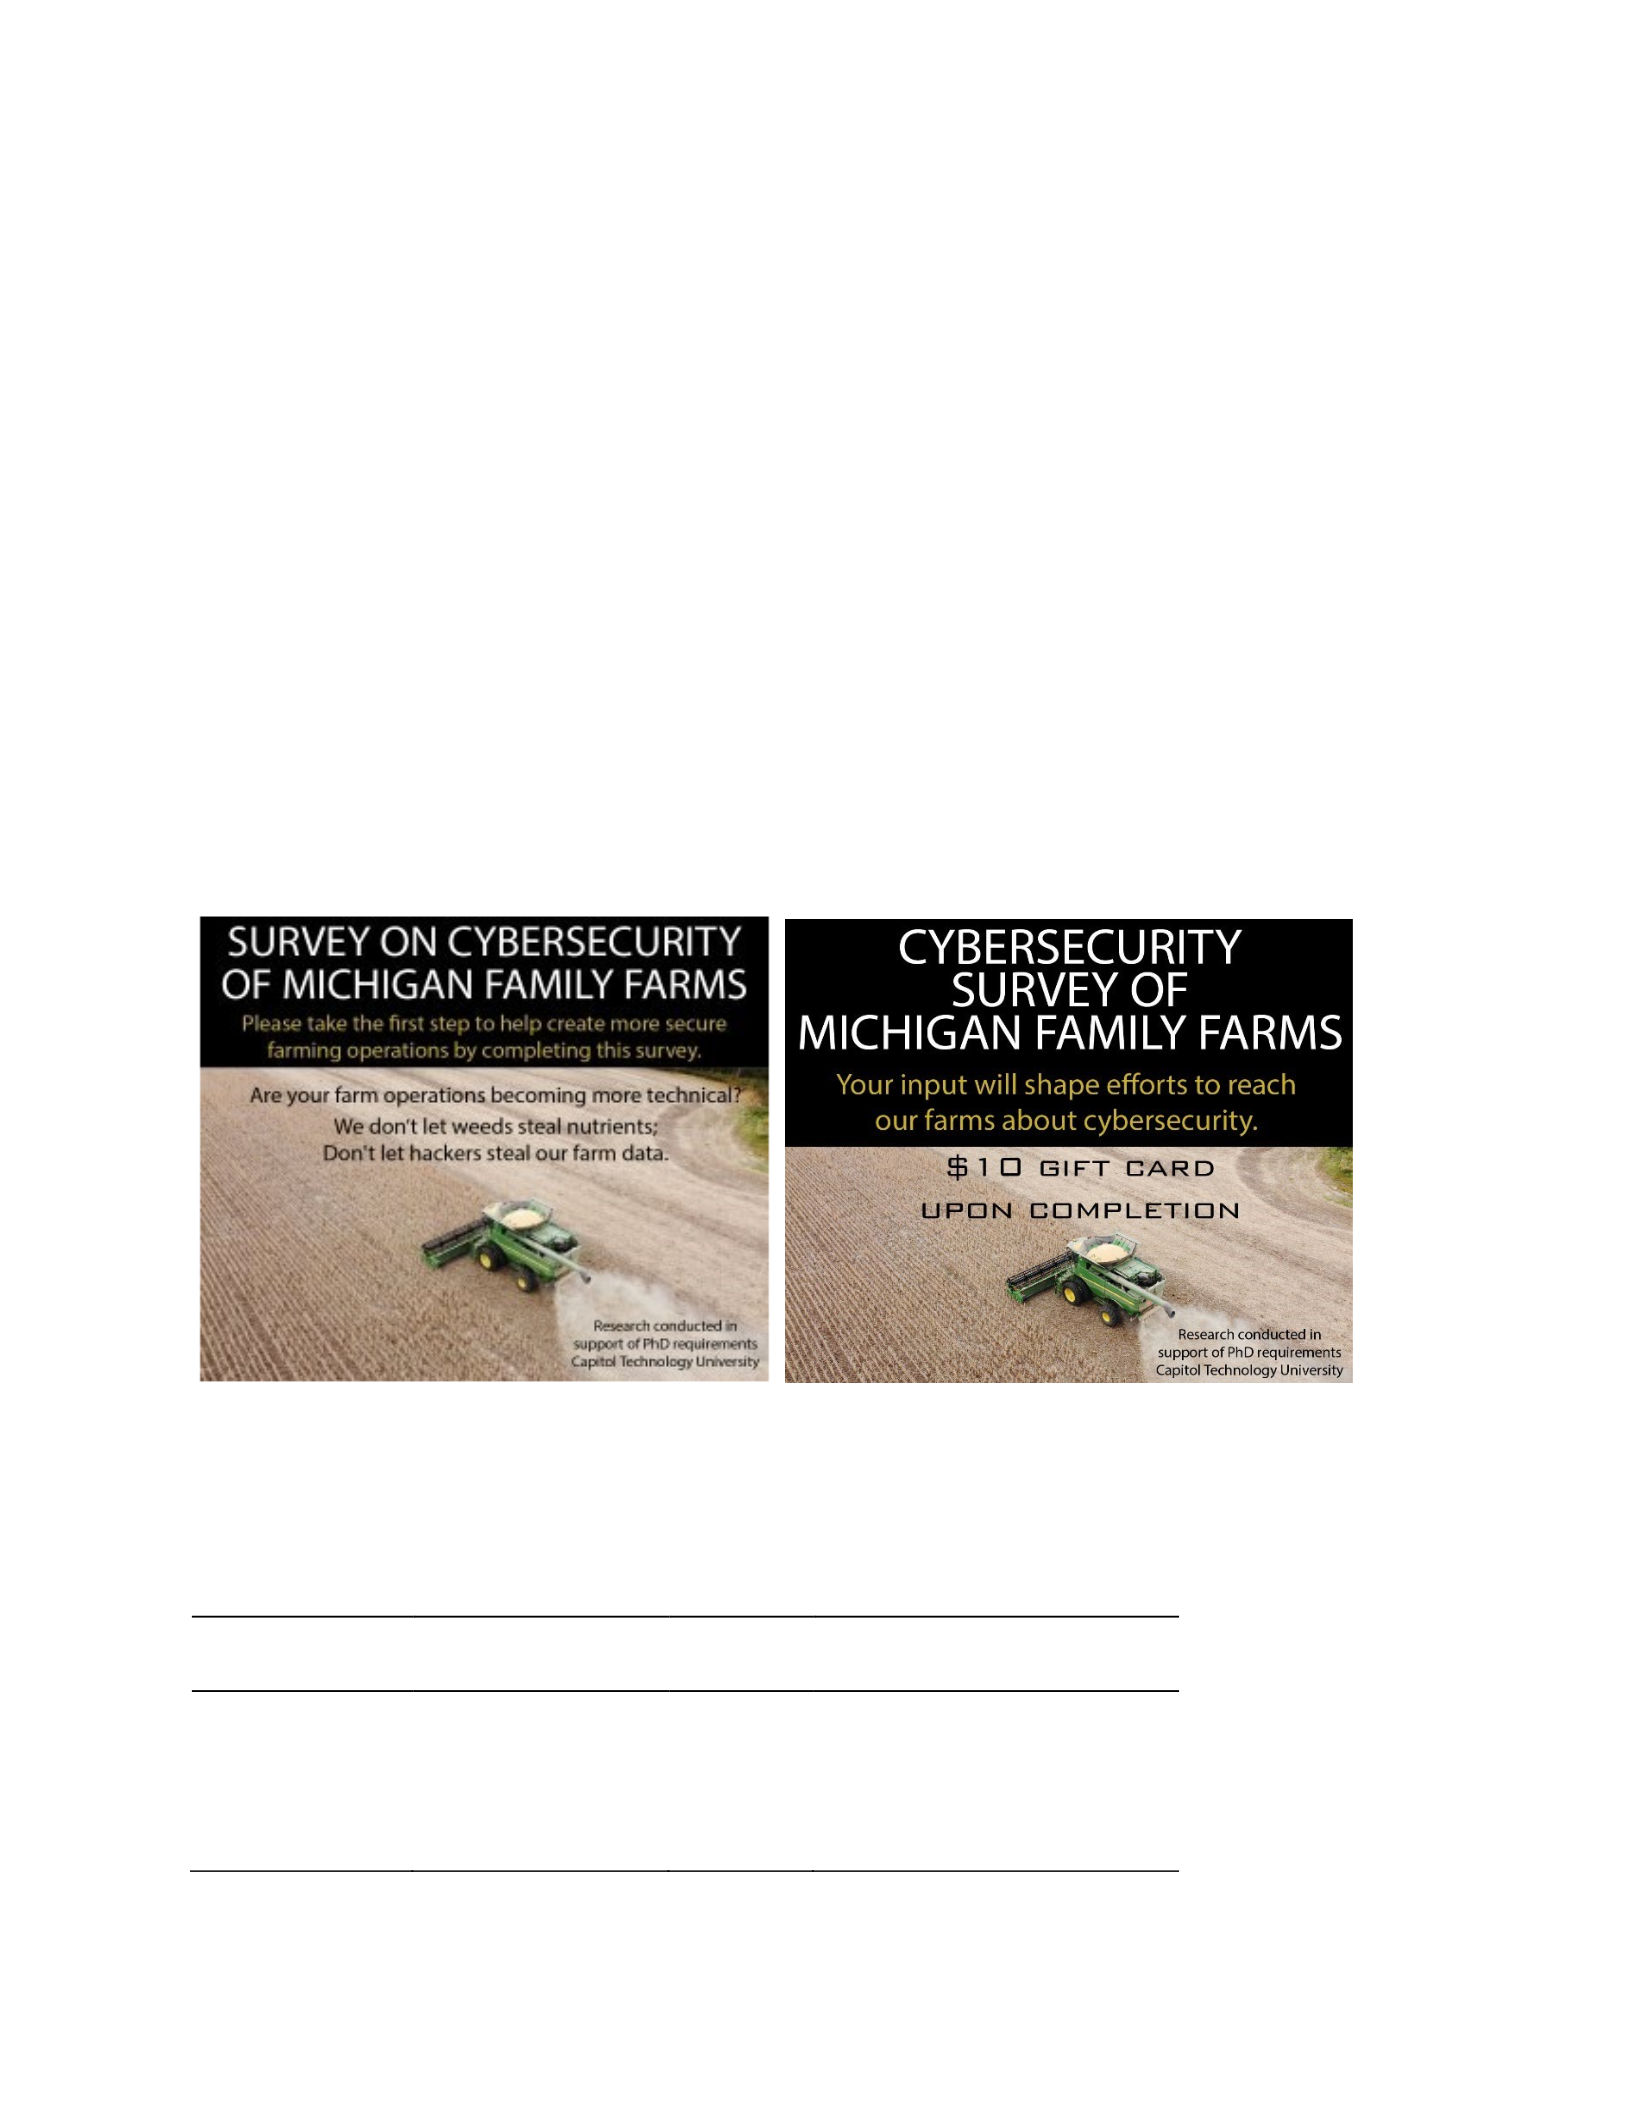
card distribution and would not be sold or used for any other purpose. Additionally, email
addresses did not restrict participant eligibility further.
In addition to the invitations, the researcher placed a digital advertisement for the survey
in the Michigan Farm News, a daily newsletter published by the Michigan Farm Bureau (see
Figure 5). This advertisement ran throughout October and November 2022 and February 2023.
Clicking on the digital advertisement re-directed individuals to the landing page for the survey
on the Qualtrics platform. For click-through rate (CTR), see Table 2.
Figure 5
Survey Advertisements
Table 2
Advertisement Click Through Rate
Total Ad Click-through rate Month Impressions
Clicks (CTR)
October 2022
November
538,864 129 0.024%
2022 509,508 139 0.027%
February 2023 500,122 196 0.039%

As previously stated, this methodology was designed to yield a simplified random sample
of individuals from the Michigan family farm population, ensuring that each farm had an equal
likelihood of being selected. Initially, the researcher did not delineate farms based on factors
other than requiring their location in Michigan because of the lack of demographic data about the
farm operators. Since the demographic characteristics of the individuals in the sample were
unknown until after survey completion, stratification, a method of dividing the sample into
subgroups based on shared demographic characteristics (Acharya et al., 2013), was not
employed. The resulting sample may not proportionally represent each Michigan family farm
population stratum.
When determining the sample size for this study, the ideal sample size was 381 farms,
which would lead to the survey being representative of the total population; however, the ability
to reach individuals and ensure their participation in a timely manner meant that achieving this
number was challenging and unlikely. Consequently, the researcher decided to employ multiple
distribution methods to reach a wide range of participants and increase the sample size, thereby
enhancing the accuracy of inferences drawn from the survey results (Creswell & Creswell,
2018). The resulting sample population size was 146 qualified study participants.
Instrumentation
The survey instrument designed for this study was a modified instrument adapted from
the Canadian cybersecurity awareness survey conducted in 2022 by the Canadian Community
Safety Knowledge Alliance (CSKA). The CSKA conducted their survey as part of their Cyber
Security Capacity in Canadian Agriculture project funded by Canada’s Minister of Public Safety
and Emergency Preparedness (Public Safety Canada, 2021). The researcher modified the

instrument to focus on Michigan farms and sought to apply the principles of TAM to this specific
topic and population. See Appendix B for a sample of the survey.
Content of the Instrument
The instrument comprised the following sections: Cover Letter, Demographics,
Selfassessment, Perceptions of Risks and Priorities, Cybersecurity Practices, Risk Management,
Experience with and Impacts of Cyber Attacks, and Closing Section.
This study utilized several scales in the survey instrument to measure participants’ views
and opinions. Likert scales measured survey participant assessment of their familiarity and
understanding of technology, cybersecurity, and Agriculture 4.0. The purpose of a Likert scale is
to rate participant agreement with the statements (Sullivan & Artino Jr, 2013) and for this study
to understand the self-assessed level of understanding of the studied topics.
This survey included closed-ended multiple-choice questions where respondents could
choose one or more options from a predetermined list, along with single-answer and
multipleanswer questions. A benefit of using closed-ended questions is that they obtain structured
responses that produce clean data for analysis (SurveyMonkey, 2023).
The survey collected demographic data using dropdown questions with pre-defined
responses, categorized based on the USDA Economic Research Service (ERS) categories. The
reason for applying the USDA demographics was to allow future research to utilize a standard
USDA category and to allow potential references to other USDA data.
The researcher chose not to ask participants about their gender or age to avoid potential
negative impacts, such as decreasing the number of respondents, when collecting demographic
data for this survey (Hughes et al., 2016). As highlighted by Vanderbilt University, surveys often

force people to choose between limited options that do not include their identities and can make
individuals feel invalid, and this can cause surveyors to collect inaccurate data (Vanderbilt
Student Affairs, 2023). Vanderbilt University further encourages researchers to consider asking
about sex, gender, or sexuality when it is necessary. The researcher decided not to ask about
these demographics based on the lack of previous research on this topic and population.
Data Collection / Administering the Survey
The instrument was delivered utilizing the online survey platform Qualtrics. The
Qualtrics platform allowed for more efficient survey delivery utilizing a custom URL:
http://www.miagcyber.com, a shortened URL, and a QR code, each option redirecting
participants directly to the survey.
The researcher collected data throughout the survey in a single phase, keeping the
instrument open for the entire period. Upon completion, the researcher closed the survey and
downloaded all Qualtrics responses to the researcher’s computer. Per the American
Psychological Association (APA) Ethical Standard 6.01 (Berenson, 2018), the researcher will
retain and delete the data after five years. Only the researcher handled the collected data,
maintaining the strict confidentiality of the participants.
Data Cleaning
Data cleaning occurred on the survey data before conducting the analysis. The primary
cleaning method was to remove incomplete responses from the sample population. The study
received a total of 178 survey responses. However, 32 of these responses had participants initiate
the survey but were abandoned and not completed or only partially completed. Some surveys
appeared incomplete initially because those participants chose to remain completely anonymous
and opted not to select a gift card and provide their email address. Otherwise, these surveys were
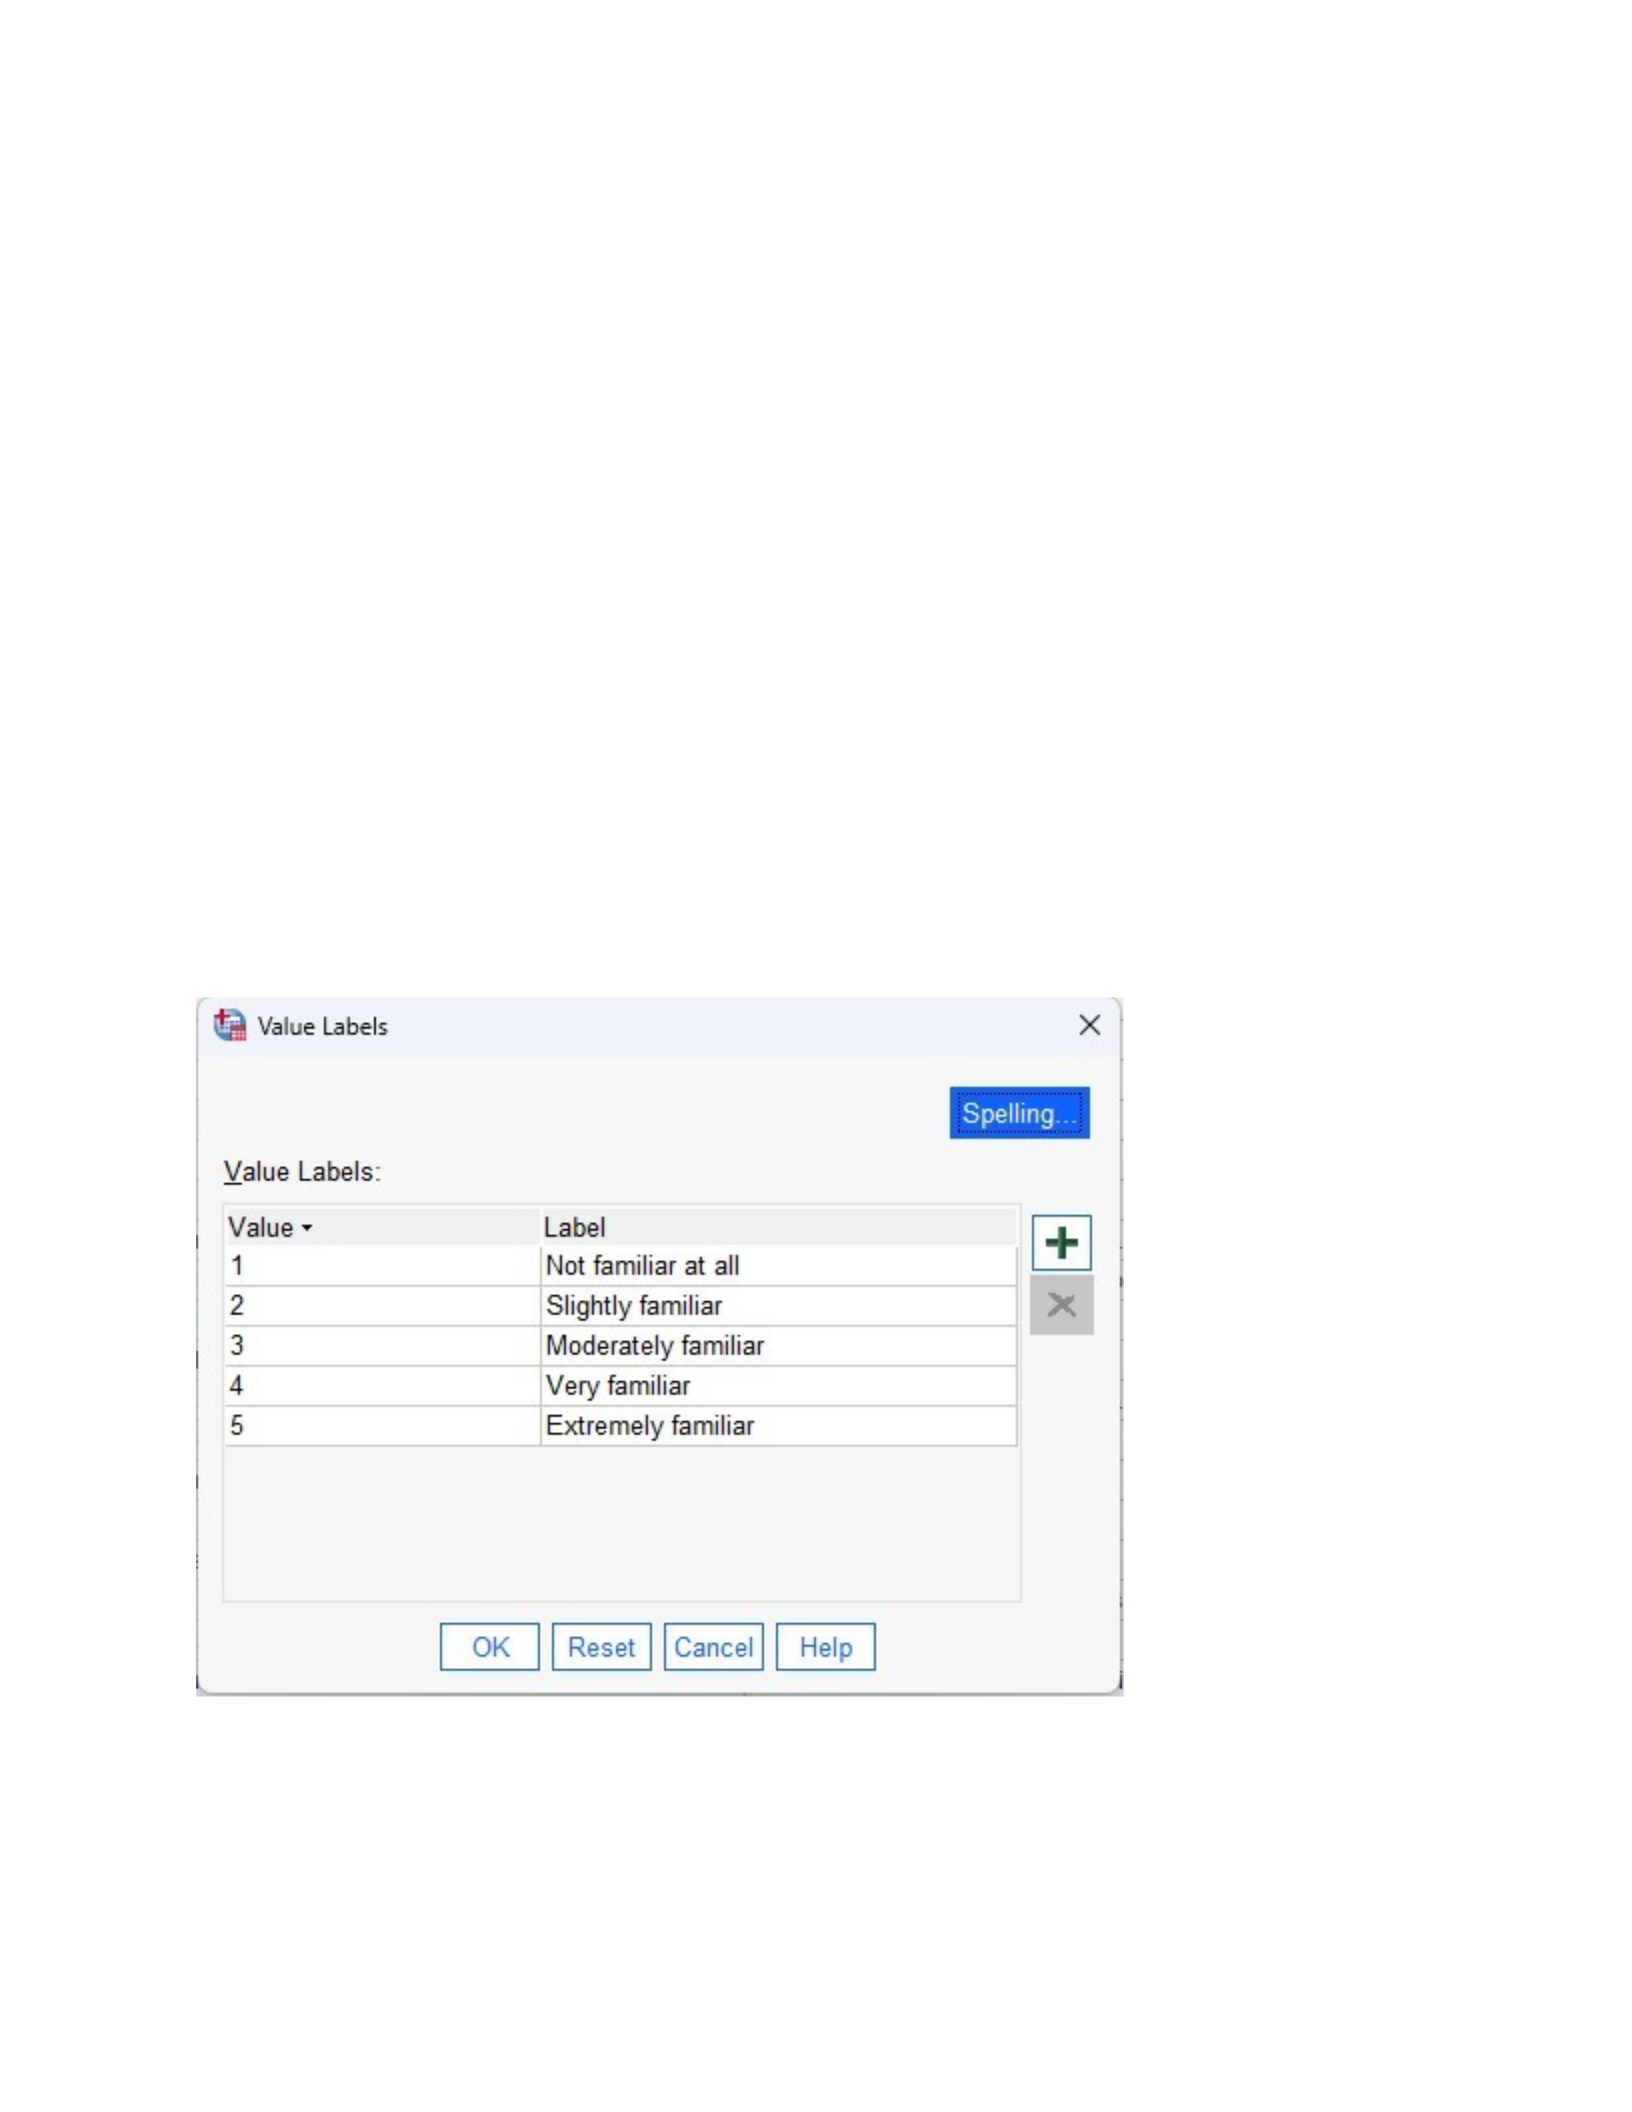
complete and retained in the sample. The researcher retained responses in the sample even if
participants skipped some questions, provided they completed most of the survey. Once the
cleaning was complete, 146 responses remained in the sample, which resulted in an 82%
completion rate. This group became the final sample population for use in the data analysis.
Additionally, in preparation for the analysis to enable statistical analysis, Qualtrics
transforms survey responses into numerical answers. For example, a question assessing the
participant's cybersecurity knowledge presented five response options in the table’s label field,
and Qualtrics automatically assigned corresponding values in the value field (Figure 6).
Figure 6
Example Value and Label
Data Analysis Procedures
After exporting the survey results from Qualtrics, the researcher saved them on the
password-protected computer owned by the researcher. The researcher utilized IBM SPSS

Statistics software version 29.0.1.0 to conduct statistical data analysis to test hypotheses for each
research sub-question. Additionally, utilizing Microsoft Excel, the researcher created the graphs
and tables presented in Chapter 4, Results.
The researcher generated descriptive statistics for the sample population to begin the data
analysis. These statistics included role, years of experience, USDA ERS category, farm size in
acres, use of connected digital technologies, whether the farm had been the victim of a
cyberattack, and location by the district in Michigan. Table 3, Table 4, and Table 5 (in
Descriptive Statistics for Sample Population, Chapter 4) present each variable's total N and
percentages. Furthermore, the researcher calculated descriptive statistics – including the total
number of responses (N), mean, standard deviation, and standard error of the mean – to measure
participants' familiarity with technology, the concept of cybersecurity, and Agriculture 4.0.
During data analysis, the researcher utilized the Chi-square test to determine if there is a
relationship between two categorical variables. The Chi-square test is based on comparing
frequencies observed in certain categories to the frequencies that one might expect to obtain by
chance (Field, 2018, p. 613). For the expected frequency values, they are calculated using the
column and row totals for each cell, divided by the total number of observations that could have
contributed to the cell (Field, 2018, p. 614). When utilizing IBM SPSS, the expected values are
calculated by the software as it processes the input data for the Chi-square test. In situations
where values of the contingency table are not as robust or when samples are small, the
Likelihood Ratio Test is utilized in place of the Chi-square test (Field, 2018, p. 615).
Hypothesis Testing
To test the hypothesis for RQ1, the researcher conducted a Pearson correlation test
between cybersecurity knowledge gaps and the sample population’s belief that a cybersecurity

incident would occur. Pearson’s correlation coefficient “is a standardized measure of the strength
of the relationship between two variables, scored from -1 to 1” (Field, 2018, p. 748). A Chisquare
test will be employed to investigate the relationship between the variables. This test assesses the
independence of categorical variables (Field, 2018, p. 737).
To test the hypothesis for RQ2, the researcher used Chi-square tests to examine how the
relationship between the size of the farm, its resources, and technological expertise shapes the
cybersecurity landscape for Michigan’s family farms. This research aims to analyze whether
these variables influence adopting cybersecurity practices on farms.
To test the hypothesis for RQ3, the researcher conducted Pearson correlation tests to
investigate the relationship between a farm’s assessed cybersecurity impact, risk perception, and
the farm’s decision-making and cybersecurity adoption to determine if the independent variables
influence the outcome.
To test the hypothesis for RQ4, the researcher conducted Pearson correlation tests to
investigate the relationship between farms regarding their available resources to invest in
cybersecurity and their decision to invest in cybersecurity or other aspects of the farm.
Additionally, the researcher conducted Pearson correlation tests to investigate the relationship
between perceived return on investment (ROI) and investment in cybersecurity.
The researcher conducted a Chi-square test to test the hypothesis for RQ5, which
examines the relationship between a farm’s location in the State of Michigan and cybersecurity
familiarity. Due to limitations in the contingency table, with the percentage of cells with an
expected count of less than 5, the Likelihood Ratio was employed to assess the strength of this
association.

To test the hypothesis for RQ6, the researcher conducted a correlation analysis between
the size of the farm in acres, and the preferred kind of cybersecurity support a farm would like to
receive. Additionally, the researcher conducted a correlation analysis between farm acreage and
each dependent variable to determine if there is a significant relationship between the acreage of
the farm and the preferred learning method. Finally, the researcher conducted a correlation
analysis between farm size by income and each dependent variable to determine if there is a
significant relationship between the size of the farm and the preferred provider of information.
Assumptions, Limitations, & Delimitations
Assumptions
Assumptions are items within the study that are outside of the researcher’s control, but
according to Simon (2011), if they were to disappear, then the study would become irrelevant.
Simon (2011) further noted that one must not just state assumptions but must justify them as
probably true. This study assumed that survey participants would answer screening questions and
survey questions truthfully, given that they could remain anonymous, and any identifying
information would remain confidential (Simon, 2011). Additionally, this study assumed that the
sample population is representative of the target population. This study also assumed that the
survey instrument was reliable and valid and that it measured the intended phenomena
(Kimberlin & Winterstein, 2008).
Limitations
Limitations are potential weaknesses, usually outside of the researcher’s control, that are
associated with the selected research design, statistical models, and funding constraints and may
affect the results and conclusions of the study (Theofanidis & Fountouki, 2018). One limitation
of this study was using an online platform to deliver the survey instrument. While cybersecurity

and technology are closely linked, not all potential participants may have access to the internet to
participate in the survey. Further, Theofanidis and Fountouki (2018) highlighted that quantitative
statistical analysis models could easily determine the correlation between variables but not
causation.
Furthermore, the sample size for this survey may not be representative of the target
population due to the required large sample size. Consequently, the researcher cannot generalize
the findings of this study across the target population. While this does not diminish the value of
the results obtained from the sample population, it is important to acknowledge the potential
limitations arising from an inadequate sample size.
It would be necessary to increase the sample size to understand the target population
more thoroughly, but this is costly in terms of time and budget (Bartlett et al., 2001). Therefore,
to address this issue, Bartlett et al. (2001) recommend that researchers note both the appropriate
sample size and the sample size used in the study, the reasons for the inadequate sample size, and
the effect it may have on the results. Chapter 5 provides a comprehensive analysis of these
aspects.
Finally, this study was self-funded to cover expenses related to utilizing the Qualtrics
platform, advertising the survey, printing and mailing invitations, and compensating the survey
participants. This self-funding limited the potential reach of the survey and potentially limited
access to the total population.
Delimitations
Delimitations are limitations set by the researcher to set boundaries or limits on the work
so that the study’s aims and objectives are achievable (Theofanidis & Fountouki, 2018). This

researcher sought to understand the barriers to family-owned farms adopting cybersecurity in the
State of Michigan and how they impact decision-making in terms of the TAM. To make the study
achievable, the researcher delimited the study to individuals aged 18 or older and the owner or
operator of a family farm in Michigan. Additionally, while the Canadian survey included farms
across Canada, this research study was delimited to only the State of Michigan rather than the
entire United States. This researcher decided to create an accessible sample within the time frame
of this degree program and available personal funding.
Chapter Summary
This chapter presented the research methodology used in this research study and the
methods and assumptions, limitations, and delimitations applied to this study. Chapter Four
presents the results of the survey conducted in support of this study, applying the methods
detailed in this chapter.
Chapter 4: Results
Introduction
This chapter presents the data analysis results of this research study. This quantitative,
non-experimental, exploratory research study explored the barriers to adopting cybersecurity
practices by family-owned farms in Michigan. The study also sought to provide insights into the
understanding of cybersecurity and the factors, or barriers, that impact its adoption. Additionally,
this study sought to provide information to those attempting to reach family farmers and present
cybersecurity information that will resonate with farmers to enable them to better connect with
their intended audience. The target population of this study was family farm owners and
operators, age 18 and older, located in the State of Michigan.

CRQ:
What specific factors hinder the successful adoption of cybersecurity measures among
family-owned farms in the State of Michigan?
Associated RQs:
1. How do knowledge gaps and digital connectivity influence cybersecurity adoption
among family farms in Michigan?
2. How do size, resources, and technological expertise shape the cybersecurity
landscape for Michigan's family farms?
3. How do assessed impact, risk perception, and decision-making influence
cybersecurity adoption among family farms in Michigan?
4. How do financial constraints and perceived ROI impact cybersecurity adoption
among family farms in Michigan?
5. Does geographical location in the State of Michigan influence the adoption of
cybersecurity measures among family farms in Michigan?
6. What are the most effective ways for government agencies, extension services, or
industry associations to collaborate to inform family farms in Michigan about the
value of cybersecurity and improve cybersecurity adoption among these farms, and
how do trusted agents influence the effectiveness of these efforts?
Results
Descriptive Statistics for Sample Population
This non-experiential study treated survey participants as representatives of their farm
operations; therefore, the researcher did not collect age and gender data. Instead, the farm
demographics collected include the Michigan County, USDA ERS category of operation size
based on income, commodity produced, total acres, and respondents’ years as decision-makers
for the operation.
The average respondent is the primary decision-maker for a small farm; they own an
average of 50 to 179 acres and have more than five years but less than 20 years of experience.
Most farmers, 80%, have connected devices and use the same network for personal and business
use. To their knowledge, they have not been the victims of a cyber-attack. See Table 3, Table 4,
and Table 5 for the demographic information gleaned in this study.
Table 3
Descriptive Statistics of Survey Participants (N=146)
Demographic Item N %
Role:
Primary owner/operator and decision-maker 97 66.40%
Part of the group of people who make decisions 48 32.90%
Missing 1 0.70%
Years of Experience:
1 year or less 1 0.68%
More than 1 year and less than 5 years 24 16.44%
More than 5 years and less than 10 years 29 19.86%
More than 10 years and less than 20 years 31 21.23%
More than 20 years 61 41.78%
USDA Economic Research Service Category:
Retirement Farms (Small farms whose principal operators
report having Retired)
Off-farm occupation farms (Small farms whose principal
14 9.59%
operators report a primary occupation other than farming)
Farming-occupation farms. Small farms whose principal
41 28.08%

operators report farming as their primary occupation. Low-sales
farms. Farms with GCFI less than $150,000
Farming-occupation farms. Small farms whose principal
operators report farming as their primary occupation. Moderate-
36 24.66%
sales farms. Farms with GCFI between $150,000 and $349,999
Midsize Family Farms (GCFI between $350,000 and
16 10.96%
$999,999) 9 6.16%
Large-Scale Family Farms (GCFI of $1,000,000 or more)
Large-Scale Family Farms with GCFI between $1,000,000
12 8.22%
and $4,999,999
Very Large-Scale Family Farms with GCFI of $5,000,000 or
11 7.53%
more 6 4.11%
Missing 1 0.68%
Farm Size in Acres:
1 to 9 acres 29 19.86%
10 to 49 acres 25 17.12%
50 to 179 acres 36 24.66%
180 to 499 acres 27 18.49%
500 to 999 acres 9 6.16%
1,000 acres or more 20 13.70%
Use Connected Digital Technologies:
None of my farm business devices are connected to a
network or to the internet
Some of my farm business devices are connected to a network
or to the internet; I use the same network for my
15 10.27%
business and personal devices 118 80.82%
Table 5
Location by Districts of Survey Participants (N=146)
Michigan Agricultural Statistics District N %
Some of my farm business devices are connected to a network
or to the internet; I use separate networks for my
business devices and personal devices
Table 4
Participant Victim of Cyberattack
Victim of a Cyberattack:
13 8.90%
My farm business has been a victim of a cyber attack
Attempted cyberattacks were made against my farm business but were not
6 4.11%
successful 10 6.85%
As far as I know, my farm business has not experienced any cyberattacks 121 82.88%
I don’t know/I’m not sure/Would rather not say 9 6.16%
1. Upper Peninsula 17 11.64%
2. Northwest 24 16.44%
3. Northeast 6 4.11%
4. West Central 6 4.11%
5. Central 7 4.79%
6. East Central 8 5.48%
7. Southwest 30 20.55%
8. South Central 24 16.44%
9. Southeast 21 14.38%
Missing (Not provided) 3 2.05%
Data Analysis
To begin the survey instrument, participants rated their level of familiarity with
technology, familiarity with the concept of cybersecurity, and familiarity with Agriculture 4.0.
The rating of each concept is on a scale of 1 to 100. While there were 146 survey responses in
the sample, some participants did not rate their familiarity with each concept, resulting in values
less than 146. For a summary of the results, see Table 6.
Table 6
Participant Concept Familiarity
Concept N Mean Std Deviation Std Error of Mean
Familiarity with technology, being
able to maintain devices, upgrade, and
add new technology 142 60.69 24.62 2.06
Familiarity with the concept of
cybersecurity (what it is, why it is
important, how to secure devices and
networks, etc.) 142 58.09 26.07 2.18
Familiarity with Agriculture 4.0 99 35.67 38.51 3.87
Analysis of the participant responses for self-assessment of familiarity with the concept
of cybersecurity revealed that the median response was 58.50, with a mean of 58.09. This result
indicates that more participants in the sample population rated themselves lower than the median
score. Reviewing the group’s familiarity with cybersecurity, as defined in the subsequent
question, reinforces this self-assessment.
The researcher further provided a specific definition of cybersecurity to assess the sample
group’s familiarity with cybersecurity. The definition noted that cybersecurity refers to
techniques to protect the integrity of networks, programs, and data from attack, damage, or
unauthorized access. The researcher asked the participants to rate their familiarity with
cybersecurity from unfamiliar to extremely familiar. The sample population had a slight to
moderate familiarity with cybersecurity (M = 2.77, SD = 0.987). See Table 6 for a summary of
the results, N = 142, missing = 4.
Figure 7
Participant Familiarity with Cybersecurity
11
48
54
21
8
0
10
20
30
40
50
60
Not familiar at
all
Slightly familiar Moderately
familiar
Very familiar Extremely
familiar
Count

To examine the relationship between the two cybersecurity familiarity ratings, the
researcher conducted a correlation analysis to determine if there was a significant correlation
between the two measures. The null hypothesis is that there is no relationship between the two
ratings of cybersecurity familiarity. The alternative hypothesis is that a significant relationship
exists between the two ratings. The results show a significant positive correlation between
familiarity with cybersecurity as a concept and familiarity with cybersecurity, as defined above (r
= 0.652, p < 0.001), and reject the null hypothesis. On average, the farms in this sample
population are moderately or less familiar with cybersecurity, thus exposing farmers to
cybersecurity risks through ignorance.
Interpretation of Results for RQ1
RQ1: How do knowledge gaps and digital connectivity influence cybersecurity adoption among
family farms in Michigan?
To test the hypothesis for RQ1, the researcher conducted a correlation analysis on
cybersecurity knowledge and digital connectivity variables, seeking a significant relationship
between them and cybersecurity adoption. The null hypothesis is that there is no significant
relationship between knowledge gaps and digital connectivity and cybersecurity adoption among
family farms in Michigan. The alternative hypothesis is that there is a significant correlation
between knowledge gaps, digital connectivity, and cybersecurity adoption among family farms in
Michigan.
First, to test the correlation between knowledge gaps and the sample population's belief
that a cyber security incident would happen to their farm, the researcher conducted Pearson’s
correlation analysis to examine the relationship between familiarity with cybersecurity and the
belief that a cyberattack would happen against their farm. The null hypothesis is that these two
variables have no significant relationship. The Pearson correlation coefficient (r) between
familiarity and belief that an attack will happen is -0.006, p = .941. This result indicates a weak
negative relationship; however, the researcher does not reject the null hypothesis due to the p
value > .05, and the null hypothesis is accepted. A possible explanation for this relationship may
be that the sample population is somewhat overconfident that they will not be the victim of a
cyberattack, even though increased familiarity should likely result in increased awareness of the
potential threat level.
Examining graphs of the two variables, the researcher determined that while most
participants were unfamiliar with cybersecurity, as shown in Figure 7, the graph for the belief
that an attack will occur indicates that almost half (N=69, 47.3%) believe an attack will happen.
See Figure 8. A slightly lower amount (N=50, 34.2%) does not have enough information to guess
the likelihood of an attack. The sample population has a knowledge gap regarding the likelihood
of a cybersecurity incident.
Figure 8
Belief Cybersecurity Incident Will Happen
50
5
19
3
69
0
10
20
30
40
50
60
70
80
I do not know
enough about
this
A cyber security
incident will not
happen to my
farm business
A cyber security
incident is
unlikely to
happen to my
farm business
A cyber security
incident is likely
to happen to my
farm business
A cyber security
incident will
happen to my
farm business
Count
Belief a Cybersecurity Incident Will Happen
Further examining the relationship between these two variables, the researcher used a
Chi-square test to analyze the relationship between cybersecurity familiarity and the belief that a
cyberattack was likely to occur on their farm. The null hypothesis is that there is no relationship
between the two variables, and the alternative hypothesis is that there is a relationship between
the two variables. According to the Likelihood Ratio Test, a significant relationship exists
between familiarity and belief that a cyber-attack will happen (λ (16) = 28.971; p = .024).
Therefore, the researcher rejects the null hypothesis. See results in Table 7.
Table 7
Chi-Square Test Between Cybersecurity Familiarity and Belief Attack Will Happen
Test Value df
Asymptotic
Significance (2-sided)
Pearson Chi-Square 37.413a 16 0.002
Likelihood Ratio 28.971 16 0.024
Linear-by-Linear
Association 0.005 1 0.941
N of Valid Cases 142
a. 16 cells (64.0%) have an expected count of less than 5. The minimum expected
count is .17.
Since the relationship between cybersecurity familiarity and belief that a cybersecurity
incident is likely to occur is significant, the strength of the association between familiarity and
belief is determined by Cramer’s V. The Cramer’s V coefficient is .257 (p = .002) (Table 8),
which indicates based on this effect size that these variables are moderately associated. These
findings indicate that as the farmers surveyed become more familiar with cybersecurity, they are
more likely to believe that a cyberattack may occur.
Table 8
Symmetric Measures
Value
Approximate
Significance
Nominal by Nominal Phi 0.513 0.002
N of Valid Cases
Cramer's V 0.257 0.002
142
Second, the researcher examined the relationship between digital connectivity and cybersecurity
goals for the farm. Prevention was the number one goal selected by participants (N = 90,
61.6%), either on its own or with detection and/or response (Figure 9). Of note, 14% of the
participants (N = 22) did not know enough to select a goal. The null hypothesis is that no
significant relationship exists between digital connectivity and cybersecurity goals. The
alternative hypothesis is that there is a significant relationship between the two variables.
Following a correlation analysis between the two variables to test the hypothesis, the Pearson
correlation coefficient (r) between digital connectivity and cybersecurity goals is .139, p = .094
(Table 9). The results indicate a weak positive relationship; however, the researcher did not
reject the null hypothesis due to the p value > .05 and found no significant relationship.
Figure 9
Participant Cybersecurity Goals
Table 9
Correlation Between Digital Connectivity and Cybersecurity Goals
Q16
Q9 Pearson Correlation 1 0.139 Sig. (2-
tailed) 0.094
Sum of Squares and
Cross-products 27.973 16.863
Covariance 0.193 0.116
N 146 146
Q16 Pearson Correlation 0.139 1
Sig. (2-tailed) 0.094
Sum of Squares and
Cross-products 16.863 525.315
Covariance 0.116 3.623
N 146 146
While participants rated themselves as slightly familiar with cybersecurity on average,
there is a belief among the sample population that a cybersecurity incident will happen to their
22
69
18
7
15
41
10
0
10
20
30
40
50
60
70
80
N
Count
Goal
Cybersecurity Goals
Don't know
Prevention
Detection
P+D
Response
P+R
D+R
P+D+R
Q9
farm. Additionally, a knowledge gap exists about cybersecurity that prevented 47.3% of the
population from being able to guess if a cyber incident will happen. While knowledge and belief
were not significantly correlated, these two variables are moderately associated. Additionally, the
digital connectivity of the farm was not correlated with the farm's cybersecurity goals. It is worth
noting that while there is no significant correlation between digital connectivity and
cybersecurity goals, most farms in the sample population are aware that preventing cybersecurity
incidents should be a central goal for their operation.
Interpretation of Results for RQ2
RQ2: How do size, resources, and technological expertise shape the cybersecurity landscape for
Michigan's family farms?
To test the hypothesis for RQ2, the researcher conducted Chi-Square tests to determine
the role of the size of the farm in acres and income (resources) and the farms' technological
experience impact cybersecurity practices on the farms of the sample population.
To examine the effect of farm size in terms of acreage and income, the researcher ranked
the cybersecurity protection items utilized by the sample population farms by the total number of
responses (N) for each choice, selecting the top five items for further analysis. Table 10
summarizes these results.
Table 10
Ranked Cybersecurity Practices
Rank Cybersecurity Practice N %
1 A password for your WiFi router 94 64.38%
2 Basic access/user controls (passwords or PIN codes) for computers and
tablets used for farm business
90 61.64%
3 Software protections (examples: antivirus/malware, firewalls) 81 55.48%
4 Different passwords for multiple platforms and applications 77 52.74%
5 Regular back-ups of important information 70 47.95%
6 Automatic software and application updates 50 34.25%
7 Off-site data storage 32 21.92%
8 More advanced access/user controls (i.e., 2FA) 30 20.55%
9 The default passwords for all network capable devices have been changed 24
16.44%
10 Different network segments for personal and business use 11 7.53%
11 Physical protections (e.g., locked server cabinets, video surveillance of 11 7.53%
critical areas)
12 Data encryption (e.g., storage, in-transit) 9 6.16%
13 Threat monitoring and detection 9 6.16%
14 Endpoint security within connected devices 8 5.48%
15 Cybersecurity insurance 8 5.48%
16 There are currently no cybersecurity steps being taken in our farming 6 4.11%
operations, that I know of
17 An up-to-date list of the important software and applications needed to 5 3.42%
run your farm business
18 Periodic audits from external technical experts 3 2.05%
19 Business response/recovery plan (e.g., back-up systems, redundant and 3 2.05%
segregated environmental controls for livestock facilities)
20 A diagram that maps your on-farm network of connected devices 2 1.37%
21 Threat-risk assessment/threat management plan developed by external 2 1.37%
technical expert
22 Maintain detection logs 0 0.00%
23 Cyber threat intelligence 0 0.00%
Next, the researcher conducted a Chi-square test to examine the relationship between the
size of the farm in acres and the number of top five cybersecurity measures implemented by a
farm, using the following hypotheses: The null hypothesis is that there is no relationship between
the size in acres and the number of the top five cybersecurity measures implemented. The
alternative hypothesis is that there is a relationship between the size of the farm in acres and the
number of the top five cybersecurity measures implemented. According to the Likelihood Ratio
Test, there is no significant relationship between acreage and cybersecurity measures (λ (25) =
19.661; p = .764). Therefore, the researcher accepts the null hypothesis since the p value is >
0.05. See results in Table 11.
Table 11
Chi-Square of Farm Size in Acres and Top Five Cybersecurity Measures
Value
18.091a
df
Asymptotic
Significance
(2-sided)
Pearson Chi-Square 25 0.838
Likelihood Ratio 19.661 25 0.764
Linear-by-Linear
Association 0.527 1 0.468
N of Valid Cases 146
a. 22 cells (61.1%) have an expected count of less than
5. The minimum expected count is .80.
The researcher then conducted the same test to test the relationship between the income
of the farm and the number of top five cybersecurity measures implanted by a farm. The
researcher conducted a Chi-square test with the following hypotheses: The null hypothesis is that
there is no relationship between the size of a farm by income and the number of the top five
cybersecurity measures implemented. The alternative hypothesis is that there is a relationship
between the size of a farm by income and the number of the top five cybersecurity measures
implemented. As shown in Table 12, the researcher utilized the Likelihood Ratio Test because
more than 20% of the cells have an expected count of less than five. The results show a
significant relationship between income and cybersecurity measures (λ (35) = 53.055; p = .026).
Therefore, the researcher rejects the null hypothesis and accepts the alternative hypothesis.
Table 12
Chi-Square of Farm Income and Top Five Cybersecurity Measures
Value df
Asymptotic
Significance (2-sided)
Pearson Chi-Square 50.881a 35 .040
Likelihood Ratio 53.055 35 .026
Linear-by-Linear
Association
3.604 1 .058
N of Valid Cases 145
a. 40 cells (83.3%) have an expected count of less than 5. The minimum expected
count is .54.
Since the relationship between income and the top five cybersecurity measures is
significant, the strength of the association between income and the number of top five
cybersecurity measures chosen is determined by Cramer’s V. The Cramer’s V coefficient is .265
(p = 0.04) (Table 13), which indicates based on this effect size that income and the top five
cybersecurity measures are moderately associated.
Table 13
Symmetric Measures of Chi-Square of Farm Income and Top Five Cybersecurity Measures
Approximate
Value Significance
Nominal by Nominal Phi .592 .040
Cramer's V .265 .040
N of Valid Cases 145
Technological Expertise
The researcher also questioned participants on how they manage IT on their farms, with
the choices of being self-managed, an internal employee, or a third party. Most farms selfmanage
their IT resources, N=125, 86.2% (Figure 10).
Figure 10
Person Responsible for IT Management on the Farm
To test the relationship between farm size in acres and the person responsible for IT
management, the researcher conducted a Chi-square test with the following hypotheses: The null
hypothesis is that there is no relationship between farm size in acres and the person responsible
for IT management. The alternative hypothesis is that there is a relationship between farm size in
acres and the person responsible for IT management. According to the Likelihood Ratio Test, a
significant relationship exists between acreage and cybersecurity measures (λ (10) = 22.296; p
= .014). Therefore, the researcher rejects the null hypothesis and accepts the alternative
hypothesis.
125
812
0
20
40
60
80
100
120
140
Self-managed Employee Third Party
Count
Person Responsible for IT Management
See results in Table 14.
Table 14
Chi-square Text of Farm Size in Acres and Person Responsible for IT Management
Value
24.153a
df
Asymptotic
Significance
(2-sided)
Pearson Chi-Square 10 0.007
Likelihood Ratio 22.296 10 0.014
Linear-by-Linear
Association 12.001 1 <.001
N of Valid Cases 145
a. 12 cells (66.7%) have an expected count of less than
5. The minimum expected count is .50.
Since the relationship between farm size in acres and the person responsible for IT
management is significant, the researcher used Cramer's V to determine the strength of this
association. As shown in Table 15, the Cramer’s V coefficient is .289 (p = 0.007), which
indicates that based on this effect size, size in acres and IT management are moderately
associated.
Table 15
Symmetric Measures of Chi-square Test of Farm Size in Acres and Person Responsible for IT
Management
Value
Approximate
Significance
Nominal by Nominal Phi 0.408 0.007
N of Valid Cases
Cramer's V 0.289 0.007
145
The researcher conducted a Chi-square test to test the relationship between the income of
the farm and the person responsible for IT management, with the following hypotheses: The null
hypothesis is that there is no relationship between farm income and the person responsible for IT
management. The alternative hypothesis is that there is a relationship between farm income and
the person responsible for IT management. According to the Likelihood Ratio Test, there is a
significant relationship between income and IT management (λ (14) = 41.286; p < .001).
Therefore, the researcher rejects the null hypothesis and accepts the alternative hypothesis. See
results in Table 16.
Table 16
Chi-square Test of Farm Income and Person Responsible for IT Management
Value
48.413a
df
Asymptotic
Significance
(2-sided)
Pearson Chi-Square 14 <.001
Likelihood Ratio 41.286 14 <.001
Linear-by-Linear
Association 27.295 1 <.001
N of Valid Cases 144
a. 12 cells (66.7%) have an expected count of less than
5. The minimum expected count is .33.
Since the relationship between farm income and the person responsible for IT
management is significant, Cramer’s V determines the strength of the association between size
and the person responsible. The Cramer’s V coefficient is .410 (p < .001), which indicates that
income and IT management are moderately associated based on this effect size.
While the farm's acreage does not have a significant relationship with the number of
measures selected, the farm's income plays a greater role, as noted by Cramer’s V, being .410 for

income versus .289 for acreage, and a more significant result. Given the cost of hiring an
employee or external consultant for IT management, it makes sense that farm income plays a
greater role.
Interpretation of Results for RQ3
RQ3: How do the assessed cybersecurity impact, risk perception, and decision-making influence
cybersecurity adoption among family farms in Michigan?
To examine how these factors impact cybersecurity adoption among family farms in
Michigan, the researcher conducted a correlation analysis between the independent variables of
assessed cybersecurity impact, risk perception, and decision-making and the dependent outcome
of cybersecurity adoption. For each of these, the null hypothesis is that there is no significant
relationship between the independent variable and cybersecurity adoption. The alternative
hypothesis is that there is a significant relationship between the independent variable and
cybersecurity adoption.
First, the researcher investigated the correlation between farmers' perceived impact of a
potential cyberattack and their subsequent cybersecurity investments. For this analysis, the
researcher conceptualized investment in cybersecurity as adopting protective measures. The
Pearson correlation coefficient (r) between the assessed impact of a cyber-attack and investment
in cybersecurity was -.033, p = .689. The results indicate a weak negative but not statistically
significant relationship; however, the researcher rejects the alternative hypothesis due to the p
value > .05, and does not reject the null hypothesis. There is no significant relationship between
an attack's assessed impact and investment into cybersecurity among the sample population. A
possible explanation for the negative correlation is that a farm may view the impact of an attack
as being less serious to their operation if they have invested in cybersecurity.

Next, the researcher conducted a correlation analysis between how well the farm would
be able to manage a cyber incident (risk) and cybersecurity adoption. The Pearson correlation
coefficient (r) between the ability to manage a cyber-attack and investment in cybersecurity
was .221, p = .007. This value indicates a positive relationship between the variables, and the
researcher rejects the null hypothesis due to the p value < .05. There is a significant relationship
between a farm’s perceived ability to manage a cyber incident and the farm’s adoption of
cybersecurity via investment.
Finally, the researcher conducted a correlation analysis between the farm's IT
management method and the adoption of cybersecurity. The Pearson correlation coefficient (r)
between IT management and the adoption of cybersecurity was .213, p = .01. This indicates a
positive relationship between the variables. The researcher rejects the null hypothesis due to p
value < .05. There is a significant relationship between the method by which a farm manages its
IT and the adoption of cybersecurity via investment.
Based on the results, farms that perceive they can manage a cyber incident are more
likely to invest in cybersecurity measures. Additionally, those farms with dedicated IT employees
or external consultants are more likely to invest in cybersecurity measures.
Interpretation of Results for RQ4
RQ4: How do financial constraints and perceived ROI impact cybersecurity adoption among
family farms in Michigan?
To test the hypothesis for RQ4, the researcher conducted a correlation analysis between
the answers of the farms regarding their available resources to invest in cybersecurity and their
decision to invest in cybersecurity or other aspects of the farm. For those farmers who noted they

were investing in other priorities on the farm, the researcher assessed this to equal a low
perceived ROI of cybersecurity investment compared to other investments. According to Watkins
(2022), a farmer and consultant on farm technology adoption and value creation, farmers think of
ROI as the increase in yield and revenue expected from adopting a product or practice. Thus,
farmers are more likely to invest in aspects of the farm operation that have an immediate impact
on farm production and yield, thus, a more significant ROI.
The null hypothesis is that there is no significant correlation between financial constraints
and perceived ROI and cybersecurity adoption among family farms in Michigan. The alternative
hypothesis is that there is a significant correlation between financial constraints and perceived
ROI, and cybersecurity adoption among family farms in Michigan.
First, to test the correlation between resource constraints and cybersecurity adoption, the
researcher considered participants resource-constrained if they selected the response that they
could not address cybersecurity at the time due to resource constraints of time, money, or
resources (Figure 11). The Pearson correlation coefficient (r) between resource constraint and
investment in cybersecurity was -.034, p = .688. This value indicates a slightly negative
relationship between the variables, and the researcher rejects the alternative hypothesis due to p
value > .05. There is no significant relationship between resource constraint and investment in
cybersecurity within the sample population.
Figure 11
Distribution of Farm Resource Status
For the main barriers to strengthening cybersecurity on the farm, it is essential to
highlight that the sample population has a knowledge gap regarding where to start or get help. As
shown in Table 17, 21.92% of the sample population did not know where to start, and 11.64%
identified that they needed help but did not know where to obtain assistance.
Table 17
Participant Responses About Where to Obtain Cybersecurity Assistance
I don't know where to start 32 21.92%
I need help, but I don't know where to get it 17 11.64%
Figure 12
Farm Investment in Cybersecurity Since January 2020
Resource
Constrained
45%
Not
Constrained
55%
Resource Status (N=146)
Issue N %
Next, the researcher conducted a correlation analysis between ROI and investment in
cybersecurity. To identify farms with a lower perceived ROI for investment in cybersecurity, the
researcher selected those farms that answered that they had other priorities on the farm and/or
cybersecurity was not important. As farms are likely to invest resources into items that will
increase their income, lack of priority for cybersecurity was viewed as low perceived ROI
(Figure 13). The Pearson correlation coefficient (r) between resource constraint and investment
in cybersecurity was -.167, p = .044. This value indicates a slightly negative relationship between
the variables, and the researcher rejects the null hypothesis to p value < .05. There is a significant
relationship between perceived ROI and investment in cybersecurity within the sample
population.
Figure 13
Farms Viewing Cybersecurity as Low Return on Investment
97
49
0
20
40
60
80
100
120
No Yes
Investment in Cybersecurity since Jan 2020
For this correlation, the negative value indicates that those who did not identify
cybersecurity as having a low perceived ROI are more likely to invest in cybersecurity than those
who identify it as having a lower perceived ROI. Figure 14 demonstrates the relationship, where
8 farms invested in cybersecurity even though they identified cybersecurity as a lower ROI
compared to 41 farms investing in cybersecurity when not identifying cybersecurity as a low
ROI.
Figure 14
Summary of Cybersecurity Investment vs Perceived Return on Investment
107
39
0
20
40
60
80
100
120
Not Selected Perceived Low ROI
View Cybersecurity as Low ROI (N=146)
Based on the correlations for the sample population, there is no significant correlation
between resource-constrained farms and those that did not choose to invest in cybersecurity.
However, perceived ROI significantly correlates to those who invest in cybersecurity in the
sample population. When a farm views cybersecurity as having a lower ROI for its operation, it
is less likely to invest in cybersecurity.
Interpretation of Results for RQ5
RQ5: Does geographical location in the State of Michigan influence familiarity with
cybersecurity measures or the view that a cyber incident will occur among family farms in
Michigan?
To test the hypothesis for RQ5, the researcher conducted a Person’s Chi-Squared test and
the Likelihood Ratio Test, examining the relationship between location in the State of Michigan
based on Agricultural Statistics Districts and farmers' familiarity with cybersecurity and their
view that a cyber incident may occur on their farm.
31
8
66
41
0
10
20
30
40
50
60
70
No Yes
Sum of N by Investment and ROI
Low
Not Selected
The null hypothesis is that there is no significant relationship between location and
familiarity with cybersecurity. The alternative hypothesis is that there is a significant relationship
between location and familiarity with cybersecurity. See results in Table 18.
The Chi-Squared test assumes that the expected frequencies in each contingency table
cell will be greater than five for more than 80% of the cells (McHugh, 2013). For the analysis
results conducted below, both instances violated the assumption and resulted in more than 20%
of the table having cells with values fewer than five. Therefore, the researcher selected the
Likelihood Ratio Test to determine if there is a significant relationship between the variables.
According to the Likelihood Ratio Test, there was not a significant relationship between
location and familiarity with cybersecurity (Question 11) (λ (32) = 39.719; p = .164).
Table 18
Chi-square Test Between Location and View a Cyber Incident May Occur
Test Value df Asymptotic Significance (2-sided)
Pearson Chi-Square 37.852a 32 0.22
Likelihood Ratio 39.719 32 0.164
Linear-by-Linear
Association 0.138 1 0.711
N of Valid Cases 139
a. 35 cells (77.8%) have an expected count of less than 5. The minimum expected count
is .35.
According to the Likelihood Ratio Test, there was not a significant relationship between
location and the view that a cyber incident may occur on their farm (Question 12) (λ (32) =
29.337; p = .602) (Table 19).
Table 19
Chi-square Test Between Location and View a Cyber Incident May Occur
Value
28.483a
df
Asymptotic
Significance
(2-sided)
Pearson Chi-Square 32 0.645
Likelihood Ratio 29.337 32 0.602
Linear-by-Linear
Association 0.575 1 0.448
N of Valid Cases 143
a. 35 cells (77.8%) have an expected count of less than
5. The minimum expected count is .13.
Based on the results of the Likelihood Ratio Test being p value > .05 for both tests
conducted, the researcher did not reject the null hypothesis. Within the sample population, there
was no significant relationship between location in the State of Michigan and a farmer’s
understanding of cybersecurity and the view that a cybersecurity incident may occur. The
findings may result from information disseminated across digital means, thus removing a
geographic factor where, in the past, those who were closer to physical resources were more
likely to have access to the information.
Interpretation of Results for RQ6
RQ6: What are the most effective ways for government agencies, extension services, or industry
associations to collaborate to inform family farms in Michigan about the value of cybersecurity
and improve cybersecurity adoption among these farms, and how do trusted agents influence the
effectiveness of these efforts?
Regardless of farm size, the most popular cybersecurity support was farm-focused tips
via a trustworthy website (N=82) and then help from a trusted technical support service (n=46).
See Figure 15.
Figure 15
Preferred Cybersecurity Support By Farm Size in Acres
The researcher conducted a correlation analysis between the size of the farm in acres, and
the preferred kind of cybersecurity support a farm would like to receive. The researcher
calculated correlation values between the acreage category and each dependent variable to
determine if there is a significant relationship between the size of the farm and the preferred kind
of support. The null hypothesis for each variable is that a significant relationship between acres
and the variable does not exist. Of the dependent variables, only tips and resources have a
significant relationship with the size of the farm. Pearson correlation coefficient (r) between
acres and farm-focused tips and resources posted on social media was -.845, p = .034 (Table 20).
This value indicates a strong negative relationship between the variables, and the researcher
rejects the null hypothesis due to p value < .05. In this relationship, as the farm acreage
increases, the preference for support via social media decreases.
Table 20
0
2
4
6
8
10
12
14
16
18
20
1 9 to 10 to 49 50 to 179 180 to 499 500 to 999 1,000+
Preferred Type of Cybersecurity Support by Farm
Size in Acres
Printed trustworthy websitepodcasts social media trusted technical support
Correlation Between Farm Size in Acres and Preferred Cybersecurity Support
Acres Printed
Trustworthy
Website Podcasts
Social
Media
Trusted
Technical
Support
Acres Pearson
Correlation 1 -0.332 -0.690 -0.639 -.845* 0.096
Sig. (2-tailed) 0.52 0.129 0.172 0.034 0.856
N 6 6 6 6 6 6
Printed Pearson
Correlation
-
0.332 1 0.639 0.617 0.374 0.638
Sig. (2-tailed) 0.52 0.172 0.192 0.466 0.173
N 6 6 6 6 6 6
Trustworthy
Website
Pearson
Correlation
-
0.690 0.639 1 0.728 0.576 0.367
Sig. (2-tailed) 0.129 0.172 0.101 0.231 0.474
N 6 6 6 6 6 6
Podcasts Pearson
Correlation
-
0.639 0.617 0.728 1 0.683 0.652
Sig. (2-tailed) 0.172 0.192 0.101 0.135 0.160
N 6 6 6 6 6 6
Social
Media
Pearson
Correlation
-
.845* 0.374 0.576 0.683 1 -0.048
Sig. (2-tailed) 0.034 0.466 0.231 0.135 0.929
N 6 6 6 6 6 6
Trusted
Technical
Support
Pearson
Correlation
Sig. (2-tailed)
0.096
0.856
0.638
0.173
0.367
0.474
0.652
0.160
-0.048
0.929
1
N 6 6 6 6 6 6
* Correlation is significant at the 0.05 level (2-tailed).
Preferred Delivery Method to Receive Information
The preferred delivery method to learn about cybersecurity, regardless of the size of the
farm in acres, is via email, as shown in Table 21 and Table 22.
Table 21
Preferred Learning Delivery Method
Delivery Method
Email N
85 58.22%
Newsletter 47 32.19%
Online Training 42 28.77%
Internet Search 39 26.71%
In-person seminars 28 19.18%
Newspaper, magazine 21 14.38%
Blog
Mentoring from
1 0.68%
Professional 1 0.68%
TV news 0 0.00%
Table 22
Preferred Learning Delivery Method by Acreage
Preferred Method
Newspaper,
Internet Magazine, Online In-Person Total Email
Newsletter Search Print Sources Training Seminars (N)
Total 1 to 9 acres 15 8 11 1 7 4 27
10 to 49 acres 17 6 10 3 9 2 25
50 to 179 acres 20 15 9 6 8 6 35
180 to 499 acres 19 10 6 7 9 4 26
500 to 999 acres 5 0 1 0 1 3 9
1,000 acres or more 9 8 2 4 8 9 19
%
Total (N) 85 47 39 21 42 28 141
The researcher conducted a correlation analysis between size and each dependent variable
to determine if there is a significant relationship between the size of the farm and the preferred
learning method (Figure 16). The null hypothesis for each variable is that a significant
relationship between acres and the variable does not exist. Of the dependent variables, only
internet search has a significant relationship with the size of the farm. Pearson correlation
coefficient (r) between acres and internet search was -.948, p = .004. This value indicates a
strong negative relationship between the variables, and the researcher rejects the null hypothesis
due to p value < .05. In this relationship, as the acreage of the farm increases, the preference for
internet search as a preferred method decreases.
Figure 16
Preferred Learning Delivery Method by Farm Size in Acres
0
5
10
15
20
25
1 to 9 10 to 49 50 to 179 180 to 499 500 999 to 1,000+
Preferred Delivery Method to Learn About Cybersecurity
by Size of Farm in Acreage
Email Newsletter
Internet Search Newspaper, magazine, print sources
Online Training In-person seminars
The preferred method to learn about cybersecurity, regardless of the farm's income, is
email based on its selection by 84 study participants (Figure 17). The researcher conducted a
correlation analysis between income and each dependent variable to determine if there is a
significant relationship between the income of the farm and the preferred learning method. The
null hypothesis for each variable is that a significant relationship between income and the
variable does not exist. Of the dependent variables, only the newsletter has a significant
relationship with the size of the farm. Pearson correlation coefficient (r) between acres and
internet search was -.832, p = .01. This indicates a strong negative relationship between the
variables, and the researcher rejects the null hypothesis due to p value < .05. In this relationship,
as the income of the farm increases, the preference for a newsletter decreases.
Figure 17
Preferred Learning Delivery Method by Farm Size in Income
0
5
10
15
20
25
12345678
Preferred Delivery Method to Learn About Cybersecurity by Size
of Farm in Income
Email Newsletter
Internet Search Newspaper, magazine, print sources
Online Training In-person seminars
Preferred Provider of Cybersecurity Information by Acreage
Reviewing the top selections of the providers of cybersecurity information of the sample
population, agricultural magazines and newsletters, farmer-run organizations, state universities,
farm-focused training organizations, and insurance companies were the most frequently selected
(Table 23). Most survey respondents selected the organizations with which the farms have
existing relationships. Government organizations were some of the least selected within this
sample population. Only 6% of survey participants selected the Federal Government. For further
details, see Table 23.
Table 23
Preferred Provider of Cybersecurity Information by Farm Size in Acres
Provider N %
Agricultural magazines and newsletters 65 44.52%
Farmer-run organizations 65 44.52%
State Universities 54 36.99%
Farm-focused training and cultural
organizations 45 30.82%
Your insurance company 34 23.29%
A national not-for-profit organization
supporting small businesses 20 13.70%
Your local phone/ISP 17 11.64%
Digitally enabled farm equipment and data
service vendors 15 10.27%
Your government commodity associations 14 9.59%
Your local government 11 7.53%
A national network from the publicprivate-
academic sectors that supports cyber
security capacity
11 7.53%
A local computer network service company 10 6.85%
The federal government 9 6.16%
Local libraries 4 2.74%
Other 3 2.05%

The researcher conducted a correlation analysis between farm size in acres and each
dependent variable, determining if there is a significant relationship between the size of the farm
and the preferred provider of information. The null hypothesis for each variable is that a
significant relationship between acres and the variable does not exist. Of the dependent variables,
several have a significant relationship with the size of the farm. First, the Pearson correlation
coefficient (r) between acres and a national not-for-profit organization supporting small
businesses was -.932, p = .007. This value indicates a strong negative relationship between the
variables, and the researcher rejects the null hypothesis due to p value < .05. In this relationship,
as the farm's acreage increases, the preference for information via a not-for-profit decreases.
Next, the Pearson correlation coefficient (r) between acres and local government
was .869, p = .025. This value indicates a strong negative relationship between the variables, and
the researcher rejects the null hypothesis due to p value < .05. In this relationship, the preference
for local government decreases as the farm's acreage increases. Finally, the Pearson correlation
coefficient (r) between acres and farm-focused training and cultural organizations was -.829, p
= .04. This indicates a strong negative relationship between the variables, and the researcher
rejects the null hypothesis due to p value < .05. In this relationship, as the acreage of the farm
increases, the preference for farm-focused training and cultural organizations decreases. For
additional information regarding the preferred providers by farm size, see Figure 18.
Figure 18
Preferred Provider of Cybersecurity Information by Farm Size in Acres
Preferred Provider of Cybersecurity Information by Income
Again, reviewing the top selections of the providers of cybersecurity information of the
sample population by farm income, farmer-run organizations, agricultural magazines and
newsletters, state universities, farm-focused training organizations, and insurance companies
were the most frequently selected. Table 24 provides further details.
Table 24
Preferred Provider of Cybersecurity Information by Farm Size in Income
N
Farmer-run organizations 65 44.52%
Agricultural magazines and newsletters 64 43.84%
State Universities 54 36.99%
0 10 20 30 40 50 60 70
Agricultural magazines and newsletters
Your government commodity associations
Farmer-run organizations
The federal government
Your local government
State Universities
Local libraries
Your insurance company
Farm focused training and cultural…
Digitally enabled farm equipment and data…
Your local phone/ISP
A local computer network service company
A national network from the public-…
A national not-for-profit organization…
Other
Preferred Provider by Farm Size in Acres
to 91 10 to 49 50 to 179 180 to 499 500 to 999 1,000+
Provider %
Farm-focused training and cultural
organizations 45 30.82%
Your insurance company
A national not-for-profit organization
34 23.29%
supporting small businesses 20 13.70%
Your local phone/ISP
Digitally enabled farm equipment and
16 10.96%
data service vendors
Your government commodity
15 10.27%
associations 14 9.59%
Your local government
A national network from the publicprivate-
academic sectors that supports
11 7.53%
cyber security capacity
A local computer network service
11 7.53%
company 10 6.85%
The federal government 9 6.16%
Local libraries 4 2.74%
Other 3 2.05%
The researcher conducted a correlation analysis between farm size by income and each
dependent variable to determine if there is a significant relationship between the size of the farm
and the preferred provider of information. The null hypothesis for each variable is that a
significant relationship between income and the variable does not exist.
Of the dependent variables, several have a significant relationship with the size of the
farm. First, the Pearson correlation coefficient (r) between income and local libraries was -.8735
p = .007. This value indicates a strong negative relationship between the variables, and the
researcher rejects the null hypothesis due to p value < .05. In this relationship, as the farm's
income increases, the preference for local libraries as information providers decreases.
Next, the Pearson correlation coefficient (r) between income and local phone company or
ISP was -.756, p = .03. This indicates a strong negative relationship between the variables. The

researcher rejects the null hypothesis due to p value < .05. In this relationship, the preference for
local phone companies or ISPs as information providers decrease as the farm's income increases.
Based on the results of the analysis for RQ6, farms within the sample population have
preferred organizations to serve as information providers, likely those organizations they already
have an established relationship with, or in this case, serve as their trusted agents. The sample
population preferred email to receive cybersecurity information but is open to other delivery
methods, such as newsletters and online training. Additionally, farms prefer receiving
farmfocused cyber tips through trusted websites or cyber help from technical support.
Summary
This study explored the views of Michigan family farms regarding cybersecurity and
technology and their understanding of the value of cybersecurity to their operations. The study
examined barriers to farms adopting cybersecurity principles and how the demographics of farms
factor into the understanding and adoption of cybersecurity. The analysis identified several
factors that are important for those organizations and people seeking to provide cybersecurity
education to Michigan family farms. This chapter presented the results obtained from the
analyses used to test the hypotheses for this study, applying them to six research questions that
each contribute to the central research question. The next chapter discusses the interpretations of
the findings, recommendations, and implications for those involved in cybersecurity outreach.
Chapter 5: Discussion, Recommendations, And Conclusions
Introduction
The transition from traditional agriculture to a digital, connected farm that has adopted
Agriculture 4.0 technologies changes how farmers operate and make decisions. Agriculture 4.0
farms strongly emphasize data-informed decision-making and connected technologies across the

operation. This researcher believes that Agriculture 4.0 farms are beginning to “farm data” as
opposed to the traditional method of farming based on “touch and feel.” This shift to a reliance
on technology and data improves efficiency and resource utilization; however, the farm's
adoption of Agriculture 4.0 introduces a new type of risk: cyber risk. With the potential for
malicious cyber-attacks, device failure, or data loss, farmers must become aware of the
importance of cybersecurity and choose to adopt it into their operations. Effective education and
outreach about cybersecurity information must be provided to farm operators to encourage
adoption.
This study sought to identify the barriers to family farms' adoption of cybersecurity in
Michigan. The goal is to understand how to encourage farm decision-makers to realize the need
to implement cybersecurity protection in the digital aspects of their operation as they adopt
Agriculture 4.0 technologies and increase the volume of information the farm creates. The
reliance on technology without a plan to protect their investment may lead to severe financial
losses for the farm. This study also aimed to provide cybersecurity professionals, researchers,
and educators with information about the barriers farmers face and how they may better approach
farmers with information about cybersecurity so that it resonates with them and leads to higher
adoption rates of cybersecurity practices.
This study investigated how to apply the TAM (Davis, 1986) to the decision-making
calculus farm operators use when deciding whether to invest in cybersecurity. Decision-makers
must understand the need for cybersecurity and the concept's usefulness and ease of use.
Addressing knowledge gaps, resource constraints, and the need for tailored outreach is critical
for overcoming barriers to adoption. Otherwise, as TAM highlights, farm operators will likely

remain reluctant to adopt cybersecurity, leaving their operations vulnerable to various cyber
risks.
This quantitative, non-experimental, exploratory research study aimed to identify and
understand the barriers hindering cybersecurity adoption among family-owned farms in
Michigan through the CRQ of "What specific factors hinder the successful adoption of
cybersecurity measures among family-owned farms in the State of Michigan?" The researcher
analyzed unique survey data across six RQs, tested hypotheses, and brought forward insights
among the sample population to inform the CRQ. The researcher will discuss the implications
later in this chapter. This information can help inform methods and processes to understand
better how to reach the target population and provide meaningful information about
cybersecurity in agriculture. Further, this study highlights the need for additional research into
and overcoming the barriers to adopting cybersecurity to improve U.S. agriculture's protection.
Chapter Five presents the key findings of this study, addresses its limitations and
implications, and provides recommendations for practice and future research. Ultimately, this
work contributes to the field of cybersecurity as it relates to efforts to improve cybersecurity
adoption by a portion of the U.S. critical infrastructure FA sector.
Summary of Findings
This section reviews the key results of this research study and provides the analysis
results for each research question. The CRQ focused on identifying barriers to cybersecurity
adoption by family farms in Michigan. Related research questions analyzed survey data to
determine specific obstacles these farms face. This section will present a synopsis of these
findings.
First, it is essential to understand the digital nature of the sample population. Upon reviewing
the survey results, the researcher found that almost 90% of the sample population self-reported
that their farm was digitally connected. This result approximates the USDA-reported statistic that
88% of Michigan farms have internet access (Figure 19). Thus, most of the sample population of
this study has a digital aspect to their farm operation and should be applying cybersecurity
practices.
Figure 19
Percentage of Michigan Farms Reporting Access to the Internet
At the same time, the average response for self-assessed familiarity with technology and the
concept of cybersecurity was approximately 60 out of 100. Further, only 68% of the sample
population responded to the self-assessment question regarding familiarity with Agriculture 4.0
and, on average, rated their familiarity as 35 out of 100. The researcher will further address the
lack of answers to this question in the implications section. The researcher utilized the results to
view the sample population as slightly to moderately familiar with technology and cybersecurity,
potentially leaving them vulnerable to cyber-related issues as they adopt Agriculture 4.0 into
their operations.
67%
%70
%71
%81
%84
%88
%65
70%
75%
%80
%85
%90
2013 2015 2017 2019 2021 2023
Percentage of Farms Reported Having
Access to the Internet
National Michigan

RQ1: How do knowledge gaps and digital connectivity influence cybersecurity adoption
among family farms in Michigan?
The analysis results supporting this question revealed no significant correlation between
digital connectivity and cybersecurity goals within the sample population. The null hypothesis
was that these two variables have no significant relationship. The researcher retained the null
hypothesis due to the p value > .05. However, on average, the sample population demonstrated a
knowledge gap regarding the likelihood of a cybersecurity incident happening to their farm.
Additionally, most farms in the sample population indicated that preventing cybersecurity
incidents should be a central goal for their operation. The analysis also revealed a significant
relationship between cybersecurity familiarity and the belief that a cybersecurity incident is
likely to occur, with the two variables being moderately associated. The survey revealed a
knowledge gap among the sample population, as 47% of the respondents did not know enough to
guess if a cyber incident would happen.
RQ2: How do size, resources, and technological expertise shape the cybersecurity
landscape for Michigan's family farms?
The analysis revealed that half of the sample population applies basic cybersecurity
practices such as password protection for their router, IT access control, firewalls, or antivirus,
and regularly backing up important information. However, as the technical complexity of
cybersecurity practices increases, their adoption decreases. Practices such as network
segmentation, threat monitoring, and endpoint security are examples of those practices that fell
below a 10% adoption rate. Examining how the size of the farm in acres impacted the adoption
of cybersecurity, this study found no significant correlation between the size of the farm in acres
and the adoption of practices. There was a significant relationship and moderate association

between the size of the farm based on income and the top five cybersecurity measures
implemented. Additionally, most farms in the sample population self-manage their IT resources.
However, the study found that larger farms are likelier to have a dedicated employee or external
consultant for their IT management.
RQ3: How do the assessed cybersecurity impact, risk perception, and decision-making
influence cybersecurity adoption among family farms in Michigan?
For this study, the results found for the sample population that there was not a significant
association between a farm's assessed impact of a cyber-attack and its investment into
cybersecurity. A positive, significant relationship existed between how well a farm would be able
to manage a cyber incident and cybersecurity adoption. As farms become more familiar with
cybersecurity, they are more likely to believe that they will be able to manage a cyber incident.
Finally, for this question, the analysis revealed that for the sample population, there was a
positive significant relationship between the method by which a farm manages its IT and
investment in cybersecurity. Farms with a dedicated IT employee or an external consultant are
more likely to invest in cybersecurity than those who self-manage their IT resources.
RQ4: How do financial constraints and perceived ROI impact cybersecurity adoption
among family farms in Michigan?
When analyzing the results for this question, survey participants responded that they
could not address cybersecurity at the time due to resource constraints of time, money, or
resources, which were then considered resource-constrained. For the sample population, 45% of
the farms fell into this category. The results found no significant relationship among the sample
population when examining the relationship between resource constraints and investment in

cybersecurity. The study found that the participants again faced a knowledge gap as 59 farms,
34%, either did not know where to start or where to obtain help for cybersecurity.
This study investigated the correlation between ROI and investment in cybersecurity.
Results indicated that a significant relationship between perceived ROI and investment in
cybersecurity existed within the sample population. The Pearson correlation coefficient (r)
between resource constraint and investment in cybersecurity was -.167, and the negative value
indicates that those who did not identify cybersecurity as having a low perceived ROI are more
likely to invest in cybersecurity than those who identify it as having a lower perceived ROI.
Ultimately, when a farm views cybersecurity as having a lower ROI, they are less likely to invest
in cybersecurity.
RQ5: Does geographical location in the State of Michigan influence familiarity with
cybersecurity measures or the view that a cyber incident will occur among family farms in
Michigan?
This study investigated if a farm's location in Michigan impacted its familiarity with
cybersecurity and its perception that a cyber incident may occur on the farm. The results showed
no significant relationship between location and a farmer's understanding of cybersecurity and
the view that a cybersecurity incident may occur. Therefore, this research indicates that the
sample population will likely have a similar view of cybersecurity regardless of their proximity
to population centers within Michigan.
RQ6: What are the most effective ways for government agencies, extension services, or
industry associations to collaborate to inform family farms in Michigan about the value of

cybersecurity and improve cybersecurity adoption among these farms, and how do trusted agents
influence the effectiveness of these efforts?
This study found that for the sample population, regardless of farm size, the most
preferred cybersecurity support is farm-focused tips via a trustworthy website, followed by help
from a trusted technical support service. Examining the correlation between the size of the farm
and the preferred type of support, the Pearson correlation coefficient (r) between acres and
farmfocused tips and resources posted on social media was -.845, p = .034. This value indicates a
significant strong negative relationship between the variables, and as the acreage of the farm
increases, the preference for support via social media decreases.
Additionally, the preferred delivery method to learn about cybersecurity, regardless of the
size of the farm in acres, is via email. However, when examining the correlation between size
and each dependent variable of the preferred delivery method, only internet search had a
significant relationship with the size of the farm. The Pearson correlation coefficient (r) between
acres and internet search was -.948, p = .004, indicating a strong negative relationship between
the variables. In this relationship, as the acreage of the farm increases, the preference for internet
search as a preferred method decreases. When examining the correlation between the income of
the farm and the preferred learning method, only the newsletter had a significant relationship
with the size of the farm. The Pearson correlation coefficient (r) between acres and internet
search was -.832, p = .01, indicating a strong negative relationship between the variables. When
examining income as the independent factor, as the income of the farm increases, the preference
for a newsletter decreases.
Next, the study analyzed the correlation between the size of the farm and the preferred
provider of information. For the sample population, the Pearson correlation coefficient (r)

between acres and a national not-for-profit organization supporting small businesses was -.932, p
= .007. In this relationship, as the acreage of the farm increases, there is a decreasing preference
for information via a not-for-profit. The study also found that the Pearson correlation coefficient
(r) between acres and local government was -.869, p = .025, indicating that the preference for
local government decreases as the farm’s acreage increases. Finally, the Pearson correlation
coefficient (r) between acres and farm-focused training and cultural organizations was -.829, p
= .04, indicating that the preference for farm-focused training and cultural organizations
decreases as the farm acreage increases.
Finally, the study investigated the correlation between the size of the farm by income and
the preferred provider of information. Several dependent variables had a significant relationship
with farm income. First, the Pearson correlation coefficient (r) between income and local
libraries was -.8735 p = .007, indicating a strong negative relationship between the variables. In
this relationship, as the income of the farm increases, the preference for local libraries as
information providers decreases. Next, the Pearson correlation coefficient (r) between income
and local phone companies or ISPs was -.756, p = .03, indicating a strong negative relationship
between the variables. In this relationship, as the income of the farm increases, the preference for
local phone companies or ISPs as information providers decreases.
Additionally, the analysis of RQ6 found that farms within the sample population have
preferred organizations to serve as information providers. This researcher believes they are likely
those organizations with whom they already have an established relationship, or in this case,
serve as their trusted agents. As noted in Chapter 4, the sample population preferred email to
receive cybersecurity information but will accept other delivery methods, such as newsletters and

online training. Additionally, farms prefer receiving farm-focused cyber tips through trusted
websites or cyber help from technical support.
Limitations
It is essential to acknowledge that studies have strengths and weaknesses; their limitations
must also be considered (Connelly, 2013). Connelly (2013) further noted that the analysis of
limitations is a subjective process, and it can also be an opportunity to suggest future research to
address these issues, which this researcher will do in the recommendations section below. This
study faced several limitations outside of the researcher's control. Despite these challenges, the
results of this study provide an opportunity for additional research. Further research could
investigate the barriers to family farms adopting cybersecurity within Michigan and the United
States.
First, the sample size is smaller and thus more limited than is ideal for Chi-square tests.
This study comprises 146 participants, less than the required 317 to 405 responses to be
statistically significant results according to the G*Power calculation. With a sample size smaller
than 317 to 405 responses, the study results might not accurately represent the target population,
potentially accepting or rejecting hypotheses incorrectly. Even though this limitation exists, it is
essential to highlight that the barriers identified within this study are not unique to agriculture.
Therefore, it is likely that these barriers to adoption exist outside of the sample population and
within the target population, and the hypotheses were probably accepted or rejected
appropriately. Further research into this population will allow researchers to generate statistically
significant conclusions and determine if these barriers exist.
Additionally, there is a lack of existing research on this specific topic. The lack of
research into this population in the United States further increases the value of this study, as it

contributes to the initial body of work. Because there is a knowledge gap about this topic, the
exploratory nature of this research impacts the cybersecurity field applied to agriculture.
Exploratory research provides an opportunity to gain initial insight into an issue and learn about
the motivations and incentives of the people involved in the study (Jain, 2021). This study is
important as it examines family farmers’ barriers to investing in and adopting cybersecurity
practices and highlights areas of concern. Without an existing dataset about the target population
for this study, the collected survey data provided an opportunity to begin to understand the target
population and highlights several issues that further research should address. This study also
contributes to the body of knowledge on agricultural cybersecurity, especially as agriculture has
begun to face a more significant cyber threat over the past several years, and the adoption of
cybersecurity has become more important.
Another limitation of this study was access to the target population. While the researcher
utilized several methods to contact and invite family farm operators to participate in the study,
there were challenges in identifying and reaching the population. Using digital communication
methods and mailed letters, the researcher attempted to reduce the potential for bias towards
those with an online presence; however, this method required respondents to navigate to the
survey via the Internet. At least one potential participant found it a challenge to navigate to the
survey and took the time to write a letter to request a survey by mail to participate (See Appendix
D). Further, at least one potential participant expressed skepticism about the survey invitation
(see Appendix E). The accidental sending of multiple invitations prompted the participant to
write a letter questioning the survey's legitimacy and expressing concern about a potential
cybersecurity threat. They questioned whether this was an attempt to convince an unsuspecting
farmer to connect their network to a malicious web server. While this individual took time to

hand-write a letter to the researcher, other participants may have also had concerns but did not
express them.
Additionally, online directories were not always up to date, and some of the digital farm
presences were out of date as well. To reduce the potential for future bias and increase the
response rate, having greater access to current lists of farms comprising the target population
would be ideal. These farm lists exist, and agencies such as the USDA maintain them.
Researchers would likely need to form a partnership with the agency to obtain access to these
databases and be funded for research, as these databases are not publicly available. During the
participant identification process for this study, in December 2022, the researcher contacted the
USDA National Agricultural Statistics Service Great Lakes Region office to inquire if lists of
farms were available from the NASS. A statistical analyst within the office replied that the USDA
does not give out farmer information and protects farmers’ information as required by law.
Another challenge limiting the survey was possibly survey fatigue. Pennings et al. (2002)
documented that survey fatigue is a barrier to survey responses. Additionally, Pennings et al.
(2002) highlighted that many farmers received many study participation requests, and they may
not open the mail without sufficient interest, such as if the item is a bill or an important
document.
Implications
Overall
This study breaks new ground in cybersecurity research by examining the unique barriers
to adoption faced by family-owned farms in Michigan. Additionally, it aims to identify these
barriers to inform future solutions.

This study sought to identify barriers to cybersecurity adoption in family-owned farms in
Michigan and to expand the field of cybersecurity through the initial study of this topic and
population. This work also informs cybersecurity professionals, researchers, and policymakers
seeking to secure this critical infrastructure sector. Additionally, this study provides insight into
how these barriers may prevent the successful implementation of cybersecurity, as viewed
through the TAM. The findings of this study highlight the need for further research into the topic
of agricultural adoption of cybersecurity practices due to the existence of research gaps in this
specific topic.
As agriculture continues to modernize towards a digitally enabled Agriculture 4.0
ecosystem, the threat of cyberattacks increases along with the potential for failure of Agriculture
4.0 devices or data loss. As other critical infrastructure sectors harden defenses, the FA sector
becomes a potentially softer, more lucrative target to threat actors seeking to exploit valuable
farm data and malicious actors seeking to disrupt critical agriculture infrastructure and supply
chains. Even non-malicious failures, such as hard drive loss or corruption, can severely impact
the modern farm.
Bringing cybersecurity practices to the modern farm is more important than ever, as
Abbas et al. (2022) and McCullough (2023) highlighted. This study identified barriers to
adopting cybersecurity within the sample population and highlights that tailored outreach and
education efforts should communicate cybersecurity information to farm decision-makers clearly
and effectively. Farmers must understand the potential risks associated with adopting Agriculture
4.0 technology, the impact of losing access to critical systems and data, and how and where they
can seek cybersecurity information. Otherwise, decision-makers will likely invest their limited
resources into other parts of the farm.

The threat to U.S. agriculture has increased in recent years. Industry groups have
reinvigorated the Food and Ag-ISAC along with a focus on cybersecurity as part of the National
Security Memorandum on Strengthening the Security and Resilience of United States Food and
Agriculture (NSM-16) issued in 2022 by the President of the United States. Farms of all sizes
and resource levels must become aware of the need to adopt cybersecurity practices and protect
their operations. Famers must also be able to bring the best practices into their operation without
experiencing a large financial or time burden.
The remainder of this section will provide insight into the identified barriers and the
implications this research has for cybersecurity as applied to agriculture in Michigan and beyond.
Additionally, this study seeks to encourage continued dialogue between cyber professionals and
farmers and spur additional research into this topic.
Knowledge Gaps Impact Adoption
For farmers to assess the value and necessity of cybersecurity, they need to understand
the concept and reasons why they need to adopt cybersecurity. Without this information, farmers
are likely to avoid the adoption of cybersecurity as they have limited time and resources to invest
across all facets of their farm, and cybersecurity will fall below other priorities that are perceived
to be more important for the farm. The results of this study identified knowledge gaps in several
areas surveyed. Whether it is a knowledge gap about cybersecurity or how or where to obtain
help, these are barriers to adopting cybersecurity.
Further, cybersecurity is a diverse concept that may challenge farmers' understanding of
exactly what it is, what aspects they need to adopt, and if the lack of a readily apparent return on
investment makes sense. Additionally, a lack of standardization of the language that describes
cybersecurity and Agriculture 4.0 technologies can lead to additional confusion. For this study,

only 99 out of 146 participants evaluated their familiarity with Agriculture 4.0. This may be due
to the lack of common terminology to describe Agriculture 4.0, the digital transformation of the
farm, and the need to apply cybersecurity practices to secure their farm. Precision agriculture is
frequently used in the U.S. to describe digital and connected technologies applied to the farm;
however, this does not truly capture the full Agriculture 4.0 ecosystem. In the 2022 Census of
Agriculture, the USDA surveyed farmers regarding the adoption of precision agriculture
practices for the first time and reported an overall adoption rate of 11.89% of farms, 226,092 out
of 1,900,487 (NASS, 2024). The reported adoption rate for Michigan was 13.08%, 5,965 out of
45,581 (NASS, 2024). The low reported adoption rates may also align with participants skipping
this question out of lack of adoption or familiarity.
Confusion among the target population likely leads to additional barriers to adoption.
While this study did not address the various terminologies used and which is the most understood
by the sample population, this researcher believes that the lack of familiarity with Agriculture 4.0
as a concept prevented participants from assessing their level of understanding. Therefore, they
skipped the question.
The finding of knowledge gaps in this study mirrors those noted in the literature review
of this study. It highlights the need for education on both Agriculture 4.0 technology and
cybersecurity. This phenomenon extends beyond agriculture; literature documents that a lack of
understanding of cybersecurity hinders adoption across various sectors. While Agriculture 4.0
technology can introduce new vulnerabilities and risks to the farm, so can the lack of
understanding of the technology and cybersecurity practices to help secure their farm. Therefore,
it is essential to stress the need to include cybersecurity training and education for farms.

Value to the Farm
Operating a modern farm is an expensive, resource-intensive endeavor. Farmers must
make smart investments to ensure their operations continue the following year because farm
income fluctuates yearly due to external factors, such as commodity market pricing. For
example, a 2024 John Deere S760 combine that is Agriculture 4.0 ready with premium
technology and connectivity packages starts at a list price of over $600,000 (Deere & Company,
2023). This machine must demonstrate ROI for the farm. Otherwise, farmers are likely to avoid
the adoption of technologically advanced equipment. Costs will continue to be a barrier to
adoption as the ERS (2024) predicts that 2024 net farm income will decrease by 25.5% compared
to 2023, placing further pressure on farmers to spend resources on items with the best ROI.
In the same way, a cybersecurity investment made by the farm must also show some
value, at least in terms of the value of the protected IT and data. Cybersecurity will always be a
cost center for a farm business, and farmers may hesitate to invest in something they do not
understand as a concept or as a service to their farm. Unfortunately, many farmers may not
appreciate the expense of cybersecurity until they have suffered a cyber event. Understanding the
importance of cybersecurity in a data-dependent operational environment will help farmers move
towards adoption. As found within the sample population of this study, when farmers view
cybersecurity as having a low value for the farm, they are less likely to invest. Therefore,
cybersecurity education must demonstrate the intrinsic value of cybersecurity and the potential
cost savings of investment into proactive rather than reactive cybersecurity services.
There are lessons to carry over to the findings of this study from Purdue University’s
demonstrating the barriers of ROI and perceived value in precision agriculture investment, which
are likely to be like an investment in cybersecurity for agriculture (Erickson &

LowenbergDeBoer, 2022). As the Purdue University report indicates, farmers are interested in
precision services, but pressure on farm income limits their use. Additionally, precision
agriculture dealers reported that the perception that the cost of precision services is greater than
the benefits farmers receive, and dealers face challenges demonstrating the value of precision
services to farmers (Erickson & Lowenberg-DeBoer, 2022). Purdue University also noted that
farmers require additional services to add significantly more value to their operation, meaning
greater ROI, and dealers have challenges creating a program that adds more value than
traditional programs. Additionally, dealers reported that interpreting and making decisions with
precision information takes too much of the farmer’s time (Erickson & Lowenberg-DeBoer,
2022). They also reported that the fees they can charge farmers are insufficient to make precision
services profitable (Erickson & Lowenberg-DeBoer, 2022). It is likely that adding cybersecurity
consulting to their services, or for services of a specifically farm-focused cyber business, would
also cause issues for either business to charge prices that ensure they are profitable while still
being affordable to family farms.
Additionally, larger farms have greater resources to apply to problems. They thus may be
more likely to adopt cybersecurity as they have dedicated IT employees or consultants who can
bring cybersecurity to the farm. For smaller farms, greater resource constraints mean they will
need to receive cybersecurity information and training through less costly means. Having
seminars offered by MSU Extension, the USDA FSA, or at trade events will help introduce the
topic to decision-makers at no or low cost.
Closing the Access Divide
With the sample population of this study nearing 90% internet connectivity and the
USDA statistic noting 88% of all Michigan farms have internet, this access to information

bridges the access divide within the digital divide (Van Dijk, 2006), more readily bringing
information and knowledge to the farm. While in the past, less available internet would mean
that farmers had to travel for information or receive it via slower means, now they can access
information wherever they are in Michigan. This digital access to information lessens the
knowledge divide of the past. It increases opportunities for farmers to learn about new
technologies and how to better apply them to their operations, especially as they are made more
aware of the need to seek out cybersecurity information.
As farms gain access to high-speed internet with greater bandwidth, the opportunity to
connect their farm operation and bring more robust capabilities of Agriculture 4.0 technology to
bear will increase. Industry, consultants, and advocates should capitalize on farmers' growing
ability to leverage access and learn cybersecurity fundamentals. This increased connectivity
presents an opportunity to connect with farmers effectively. For example, online seminars and
newsletters already existing through the Beginning Farmer program offered by Michigan State
University (MSU) Extension are opportunities to add education about Agriculture 4.0 and
cybersecurity and the importance of protecting digital information and technology.
Ideal Methods of Outreach
In an era of constant advertisements and sales pitches, individuals can miss valuable
information as it becomes lost in the noise. In 2022, 48% of emails sent were identified as spam
(Griffiths, 2023). Therefore, cyber professionals must utilize ideal methods to contact and
connect with family farmers so that the messages about cybersecurity are not lost or overlooked.
As shown by the sample population for this study, farmers prefer contact via email almost twice
as much as their next preferred method of newsletters or online training. Organizations such as

MSU Extension and the Michigan Farm Bureau often email important information and
newsletters in Michigan.
Traditional communication methods, such as printed sources or TV news, resonate less
with the farm population studied. Additionally, 'cord-cutting' generations are unlikely to benefit
from these forms of advertisement and communication (Tefertiller, 2020). Farmers in this sample
also preferred to receive information through trusted websites. Identifying the websites the
broader target population utilizes will be critical to reaching farmers. Failure to communicate
information effectively will slow or even negatively impact further cybersecurity adoption.
Further, when deciding which organizations to utilize to approach farmers, it is also
essential to use those they have identified as their preferred choice. The sample population of this
study preferred agricultural magazines and newsletters, farmer-run organizations, State
universities, and their insurance company. Within Michigan, farmers tend to have strong
relationships with MSU Extension, the Michigan Farm Bureau, the farm credit agricultural
cooperative GreenStone Farm Credit Services, and their local cooperative. These organizations
offer information and training to farmers, and cybersecurity professionals should seek to form
partnerships with them to identify opportunities to reach out to farmers and provide
cybersecurity information. Opportunities already exist within these organizations to add
cybersecurity information, and it could be a reasonably easy way to begin educating farmers,
adding more specialized training over time. The Crawl, Walk, Run approach is commonly used
for this type of implementation (Ohrt et al., 2021; Campbell, 2023).

Technology Acceptance Model (TAM)
For farmers to adopt cybersecurity practices, according to the TAM, they must be able to
view the principles and practices of cybersecurity and perceive that they are useful and easy to
use. This point is the cognitive response stage of TAM. Once farmers have these perceptions,
they can move on to the affective response stage, developing attitudes toward using
cybersecurity. If the perceptions are positive, farmers will move into the behavioral response
stage and adopt and implement cybersecurity. The issues highlighted by this study’s findings are
that barriers exist between cybersecurity and the farmer’s perceived usefulness and ease of use.
These barriers are like the initial barrier to adoption highlighted by Li, Ren, and Zang (2020),
which is that farms adopt systems that are simple, easy to understand, and easy to operate. For
farmers to formulate a cognitive response about cybersecurity, they must have the appropriate
information presented to them or readily discoverable, and the information must be
understandable. Alternatively, farmers must have employees, consultants, or advocates who
present cybersecurity information and demonstrate its usefulness and ease of use to the farmer so
that they can invest their limited resources.
The results of this study also highlight that farmers are adopting technology into their
operations in Michigan. However, they do not always understand the risks associated with the
technologies. Farmers may be able to understand and evaluate Agriculture 4.0 technologies more
readily due to potential increased efficiencies, cost savings, or increased yields; therefore, they
can move along the TAM to implementation. It is imperative that farmers can perceive the
benefits of cybersecurity practices as well, even though there may not be an immediately
demonstrable return on their investment, and overcome the barriers preventing them from
moving forward on the TAM to adopt cybersecurity. The impact of ROI on adoption was also

noted in research by Pierpaloi et al. (2013), where monetary costs or the costs of difficulty
directly impact attitudes towards Agriculture 4.0. Without the correct information presented
through the best channels by the preferred organizations, farmers will avoid adopting
cybersecurity, as demonstrated by the TAM.
The research results, highlighted in the next section, identify key barriers to farmer
adoption of cybersecurity. Additionally, they outline best outreach practices to bring farmers into
the cognitive response stage and enable the successful outcomes of farmer adoption of
cybersecurity.
Recommendations
Recommendations for Practice
Educators and commercial vendors should ensure that they use farmers' preferred
outreach methods to reach family farms best and educate them about cybersecurity and the need
to implement it within their farm operations. As highlighted by the sample population of this
study, participants indicated a preference for specific contact methods over others. They
preferred email and newsletters. Additionally, providing farmers with the appropriate information
that resonates with them will also improve outreach efforts. Using industry-relevant anecdotes
such as the Canadian cyber “fire drill” how-to provides farmers with familiar language and
concepts tailored to their existing knowledge. It adds cybersecurity concepts to these efforts
(CSKA, 2022).
Additionally, equipment manufacturers and third-party vendors encourage farmers to
adopt Agriculture 4.0 technologies and promote benefits such as increased efficiency, improved
decision-making, and more. However, they do not always present the potential impacts of
adopting Agriculture 4.0 technologies, such as increased cyber risk, the costs of protecting the

new digital side of their operation, and other issues highlighted in Chapter 2. While there are
benefits, the information shows that farmers do not fully understand the potential value of
Agriculture 4.0 practices. They are often unsure of what to do with the generated data. The
CropLife-Purdue Precision Agriculture Dealership Survey highlights this issue further.
The push towards Agriculture 4.0 also brings increased cyber risk to farms, and those
promoting Agriculture 4.0 should also highlight the need to protect investment into digital
technologies and data. Thus, they should include information about the need for cybersecurity.
Further, entities such as university extension organizations or farm-focused organizations should
increase cybersecurity education for farmers. As identified by this study, farmers prefer to
receive information from organizations they trust and those they view as trusted agents.
Therefore, these organizations can help begin to create cyber-secure Michigan agriculture in a
meaningful way.
Further, while the U.S. Government continues to highlight the existence of cybersecurity
threats and the need to secure digital resources, it must work to overcome the skepticism of the
government that can exist with the agricultural community. Messaging through agencies such as
the FSA may be more impactful for farmers than through others such as CISA or the FBI because
there is a pre-established relationship between farmers and the FSA. The U.S. Government
should also increase data collection regarding cybersecurity in agriculture to inform
policymakers, such as the U.S. Congress, as they author new farm bills. Funding to enable the
USDA to expand the Agricultural Census to include more questions about Agriculture 4.0 and
cybersecurity awareness and practices would create a large, regularly collected dataset to enable
research and inform policymakers. The 2022 Census of Agriculture asking about precision

agriculture is a starting point that researchers should expand in the coming years. An example of
the value of data about internet connectivity collected by the census is the study “The Case for
Rural Broadband” and the tracking of rural connectivity, as highlighted previously in the
Summary of Findings section. Through this expanded dataset, additional reports could be
generated on cybersecurity and technology adoption by farms. Finally, research funding from
U.S. government agencies to study cybersecurity in agriculture further would strengthen
cybersecurity in the FA sector.
Recommendations for Future Research
As cyber threats and attacks against agriculture continue to increase, the lack of research
into the U.S. agricultural population and its adoption of cybersecurity should justify this topic as
a focus of research efforts. While this study has a limited sample population, the implications
highlighted above demonstrated that Michigan family farmers need additional information
regarding the importance of and how to adopt cybersecurity within their farm operations. Further
research will help illuminate barriers to adopting cybersecurity as technology and the threat
landscape change.
Additionally, conduct further quantitative research to obtain survey results representative
of the target population. Through increased funding and partnerships with Federal or State level
agricultural organizations or industry associations, researchers will reach the target population
better and may achieve a statistically significant sample size. This researcher also recommends
an improved survey instrument that requires participants to answer questions before moving
forward to the next. However, the survey should be shorter to avoid the potential for survey
fatigue. Due to the lack of existing research, this study was very broad, but a more tailored and
focused survey should improve the response rate. Future research should also utilize a survey

validated through pilot testing (Creswell & Creswell, 2018, p. 154). Additionally, future research
efforts should be even better seasonally timed to reach farmers when they are less preoccupied
with farm operations by avoiding periods such as planting or harvest season, as highlighted by
Pennings et al. (2023). This study has illuminated that knowledge gaps exist about cybersecurity
within Michigan family farms, and a better understanding of how to address these gaps within
this population and, more broadly, across the United States will help to secure this segment of the
FA sector better.
Another recommendation by this researcher is for researchers to conduct a qualitative
study focused on representative farms from the target population. Quantitative studies do not
provide the flexibility for in-depth, open-ended questions that can reveal the reasons behind
farms' lack of cybersecurity adoption. Qualitative interviews would allow researchers to tailor
questions to individual participants and gain deeper insights into adoption barriers.
Understanding the security landscape through in-depth interviews will provide richer, more
significant insight.
Additionally, it is important to understand how to best educate farmers about
cybersecurity's usefulness and ease of use, applying the idea of the TAM to increase the
cybersecurity adoption rate. Further, the qualitative methodology would also allow researchers to
understand where the farm sits regarding technology adoption. Besides identifying methods to
enable them to perceive cybersecurity as useful and easy to use, it is important to understand
whether they are innovators, early technology adopters, early or late majority, or laggards
(Moore, 2014). Once we know a farmer’s position on the technology adoption curve, we can ask
tailored questions to identify what would help them move forward and cross the chasm to adopt
cybersecurity (Moore, 2014). Also, spending time in-person or virtually with the study

participants would allow a better understanding of their views and positions on technology and
cybersecurity.
Finally, additional research should focus on ways to best integrate cybersecurity
education into college degree programs, farm-focused training, and consultant operations. One
example is the Digital Agriculture program in the College of Agriculture, Purdue University,
where they highlight digital agriculture, and thus, by extension, Agriculture 4.0, “to reach its full
potential, the success of digital agriculture is highly dependent on outreach and education”
(Purdue University, n.d.). There is a focus on bringing digital technology and data-driven
decision-making to agriculture, but a specific focus on securing these additions is not readily
apparent.
The study identified additional gaps regarding training for the trusted agents that farmers
rely on to gain information about new technologies or practices they should adopt when
reviewing the literature for this research study and the focus of other education programs. Future
farm decision-makers should be cyber-aware as they enter the workforce. Much of the focus of
Agriculture 4.0 is to improve farm efficiency; the potential risks and vulnerabilities introduced
by these technologies often receive less attention. Research identifying ways to improve
education across this sector would benefit farms and help increase adoption rates of
cybersecurity practices.
Conclusions
As agriculture in the United States continues integrating technology into operations and
moves towards Agriculture 4.0, the increased reliance on technology, connectivity, and data
presents increased cyber risks for farms. Adopting Agriculture 4.0 brings a new challenge to the
farm as cybersecurity becomes more critical to the operation to protect the various facets of

Agriculture 4.0, as presented previously in Chapter 2. Farmers will face new threats and
challenges that they have not had to address traditionally in a less digital farm operation.
Therefore, researchers and those fostering the adoption of cybersecurity must be aware of the
barriers farm operators face to adopting cybersecurity. The cyber community should also know
how to best inform farmers of the need to protect their IT and data.
As this chapter also highlights, barriers exist to adopting cybersecurity, and farmers must be
able to obtain information and training about cybersecurity and the risks associated with
technology adoption. Farmers also need to understand the value of cybersecurity. The cost of
protecting the digital farm components and data is an expense that will not show an immediate
ROI for the farm but could prove invaluable when the farm faces a cyberattack or catastrophic
data loss. Finally, when the cybersecurity community attempts outreach and engagement with the
farm community, they must utilize the preferred methods of communication.
Lastly, as demonstrated by this study, there is a lack of research and peer-reviewed literature
focused on the agricultural community and barriers to adopting cybersecurity practices. While
efforts are underway to address agricultural cybersecurity through the re-established Food and
Ag-ISAC in the United States and through the Canadian CSKA ag-focused cybersecurity
research effort, additional research is needed to understand the barriers to farmers' adoption of
cybersecurity. Research providing further insight into the mindset of the Agriculture 4.0 farmer,
the barriers to cybersecurity adoption and ways to overcome them, and how to facilitate farmers'
understanding of the ease of use and usefulness of cybersecurity to increase its adoption becomes
even more important as cyber threats aimed at agriculture increase. The ideal end state is
adopting cybersecurity practices by farms of all sizes in any location and a strengthened, resilient
FA sector in the U.S. and globally.


