


Threat Assessment
Foundations of Security CYB110
University of Phoenix
Shelby Hoke

Introduction
Confidentiality, integrity, and availability is the foundation of information security. More
commonly known as CIA Triad, it is a model designed to determine how data is handled when it
is stored, transmitted, or processed by an organization. Confidentiality ensures that only
authorized parties have access to data on the system. Integrity conveys that data shall not be
modified or compromised in any form. Finally, availability suggests that data should be ready
and easily accessible when the appropriate party sends a request for the data. Every cyber-attack
attempt to violate at least one, if not more, of these attributes. The table below provides a few
examples of which attack violates what attribute, and suggestions on how to mitigate the issue.

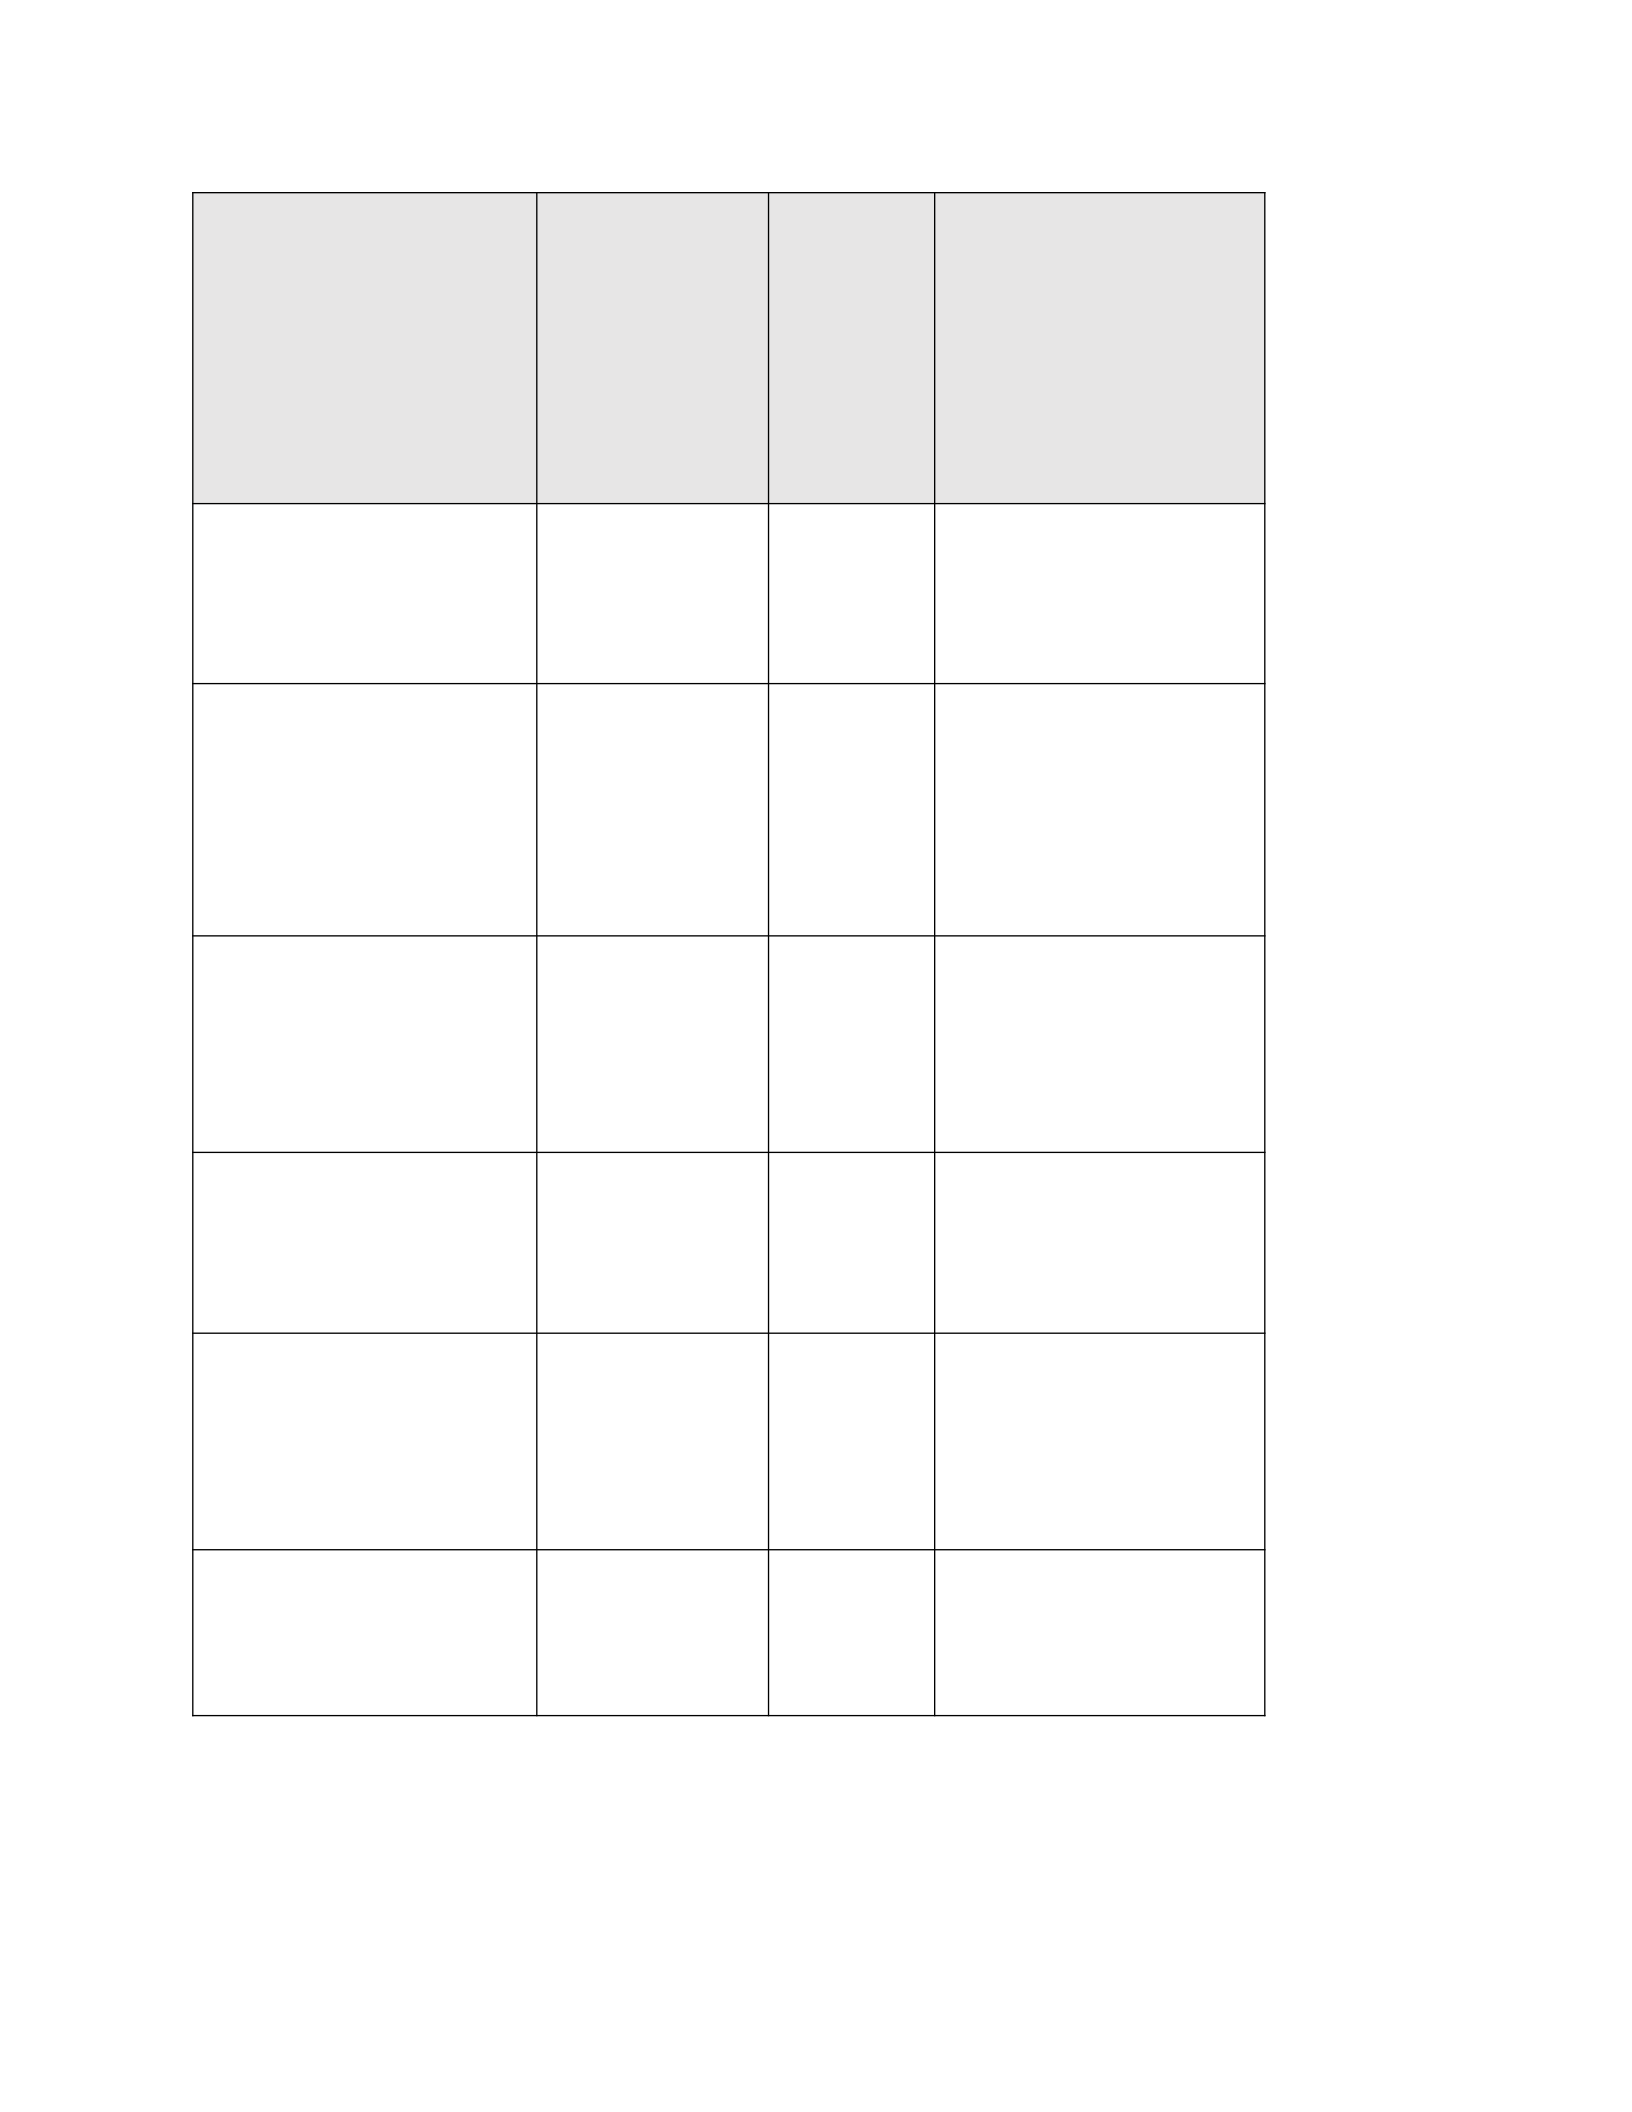
Threat Threat to
type of data
Confide
ntiality/
Integrity
/
Availabil
ity
Mitigation
Theft/Physical Intrusion Data-at-rest I & A
-Set up firewalls
-Install trusted antivirus
-install perimeter
security
Human Error
Data-at-rest
Data-in-transit
Processing
C & I & A
-Regularly provide
security awareness
training
-Have regular audits
-Encourage open
communication
-
Ransomware Data-at-rest I
-Train employees
monthly
-Install antivirus
-Make sure all hardware
and software are
updated regularly
Spyware Data-in-transit C
-Install pop-up blocker
-Enable anti-spyware
-Limit employees
personal use of company
computers
Keylogger Data-in-transit C & I
-Instruct employees to
keep computers locked
when not in use
-Enable firewalls
-Use a password
manager
Trojan Horse Data-at-rest C & I
-Enable firewalls
-Ensure all hardware and
software stay up to date
-Use anti-virus


Access Control Techniques
The term Access Control defines security techniques which regulate access to certain data on a
system. Additionally, it is a method a system uses to verify the identity of a user and
authenticates the permission this user must access the data. There are three main access control
policies: Mandatory Access Control (MAC), Discretionary Access Control (DAC), and Role
Based Access Control (RBAC). The strictest of these policies is Mandatory Access Control
(MAC), which the government uses. MAC provides every resource with security labels that
include a classification and a category. Likewise, each user on the system has security labels that
coincide with the security labels of the resources. These security labels control how much user
access the system data has. Unlike MAC, Discretionary Access Control (DAC) leaves a certain
amount of access control at the users' discretion. However, DAC is known to be inherently weak
for two reasons. Granting read access is transitive and DAC policies are vulnerable to Trojan
Horse attacks.
REFERENCES
Election security spotlight – cia triad. CIS. (2021, June 15). Retrieved December 1, 2022, from
https://www.cisecurity.org/insights/spotlight/ei-isac-cybersecurity-spotlight-cia-triad
EC-Council . (n.d.). Certified secure computer user. BibliU. Retrieved December 1, 2022, from
https://bibliu.com/app/#/view/books/9781635671070/pdf2htmlex/index.html#page_1

