


Running Head: EQUIFAX CYBER ATTACK g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g 1
IT-549 Final project Submission

EQUIFAX CYBER ATTACK g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g 2
Contents
I Introduction ............................................................................................................................. 3
II The role of the key leaders within the Equifax organization ............................................... 5
III. Risk Assessment: Equifax ................................................................................................... 7
IV. Statements of Policy ......................................................................................................... 11
V. Conclusion: ......................................................................................................................... 15
VI. References ......................................................................................................................... 18

EQUIFAX CYBER ATTACK g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g 3
I Introduction
Equifax Inc. is a reputed business undertaking that specializes in data analytics and
technology. In the year 2017, cyber attackers had gained access into the system of the
business entity and compromised secretive data and information of around 143 million
American consumers (Equifax Says Cyberattack May Have Affected 143 Million in the
U.S, 2019). They had compromised confidential details such as name, address, birth date,
driver’s license number and Social Security Number. The incident had gained a lot of
attention for all the wrong reasons. In fact, the cyber-attack on the business entity was
considered to be one of the largest risks relating to the personal and sensitive information
of the 21st century (Deanne, 2019).
Overview of the goals and objectives
The information assurance plan has been designed with the intention to get an
insight into the importance of the confidentiality, integrity, and availability of information.
The incident which jolted the business organization arose as the business was using an
open-source framework known as Apache Struts for the purpose of addressing the online
disputes relating to its web application. It had a number of loopholes which exposed its
vulnerability to cyber hackers (Deanne, 2019).
The unfolding of the cyber breach indicated that the attack has taken place two
months prior to the disclosure of the vulnerability of the business entity. In case a robust
cybersecurity model was in place, such an unfateful cyber occurrence could have been
avoided by Equifax Inc. The business undertaking failed to upgrade its existing systems
which ultimately resulted in one of the most severe cyber-attacks in the history of mankind
(Deanne, 2019).
In order to avoid history from repeating itself, there is a need for Equifax Inc. to
learn from the mistakes and understand the significance of maintaining the confidentiality,

EQUIFAX CYBER ATTACK g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g 4
integrity, and availability of information. The creation and maintenance of a robust and
well-designed information assurance plan is beneficial to safeguard the confidential data
and information.
Assessment of confidentiality, integrity, and availability of information
The cybersecurity model of Equifax Inc. was of an inferior quality which was in
place to safeguard the privacy of its stakeholders including the customers. Even though the
business undertaking was one of the most reputed customer credit reporting agencies, the
cyber security complacency at the business organization was poor and obsolete. In fact, the
cyber-attack that took place could have been prevented only if the business concern had in
place an upgraded version of the security system (Solomon, 2019).
The business concern miserably failed to implement and execute some of the basic
security protocols like the file integrity monitoring technique and the network segmentation
practice. The focus on confidentiality, integrity and availability of information was
negligible due to which the cyber attackers were able to take advantage of the poor
security model of the business entity (Solomon, 2019).
The assessment of the confidentiality, integrity, and availability of information
within the organization has revealed that the CIA triad was weak which allowed the online
attackers to infiltrate sensitive and confidential at relating to millions of people. The digital
certificate which allowed the company to monitor the encrypted network traffic that flew
through its environment had expired almost 19 months prior to the security breach
incident.
Current protocols and policies of the Equifax Inc. organization
The business undertaking believes that it is its primary responsibility to protect and
safeguard consumer reports. On the official website of the business, it has claimed to
protect the proprietary information including accounting information, subscriber code, and

EQUIFAX CYBER ATTACK g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g 5
all the other non-public business details. The business has, in fact, introduced a number of
procedures and policies that its clients need to abide by in order to access, obtain or
distribute the firm’s information (Exhibit A - Internet Security Requirements, 2019).
Even though the business has made claims about safeguarding confidential
information pertaining to its clients and customers by encrypting the same, it is not clear to
what extent the procedure is followed by the concern (Fortune.com, 2019). In spite of the
heavy claims that the business has made about its cybersecurity approach, it has been
involved in a serious of obvious errors and it has failed to find any fixes for the same.
Some of the potential barriers that hinder the implementation of a new information
assurance plan in the business undertaking include the absence of a strict security protocol
and the presence of a weak internal defense mechanism (Staff, 2019).
II The role of the key leaders within the Equifax organization
The leaders of an organization play an extremely critical role to make sure that the
security infrastructure is robust and up-to-date. In the case of the Equifax concern, when
the cyber attack took place, the CEO of the entity was Mr. Richard Smith. Soon after the
security breach incident had occurred, he was the third senior executive to have retired
from the business undertaking. The other members who had previously left the
organization soon after the cyber incident were Susan Mauldin and David Webb (Equifax
hack: two executives to leave company after breach, 2019). They were the top security
officer and the chief information officer respectively. The leaders resigned as it was their
responsibility to take care of the security environment of Equifax but they failed to
implement a robust security system. Due to their poor approach, the security breach
incident took place which compromised the confidential data and information of almost
143 million American consumers (Equifax hack: two executives to leave company after
breach, 2019).

EQUIFAX CYBER ATTACK g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g 6
The core leadership members of Equifax had not been capable enough to safeguard
the online data and information pertaining to their customers and clients. So new leaders
were appointed where Mr. Paulino do Rego Barros, Jr served as the new CEO and Mark
Feidler was selected as the Non-executive Chairman. The main reason for the change of
leadership in the organization was due to the poor responsiveness of the former leaders to
strengthen the security model firm’s information (Equifax CEO Richard Smith suddenly
decides to ‘retire’, 2019). Richard Smith failed to design a full proof security model for
Equifax due to which a number of vulnerabilities of the entity were exploited by online
hackers. Similarly, Susan Mauldin and David Webb who were holding vital leadership
positions in the organizational context were not capable enough to upgrade and strengthen
the security system that was at par with the industry standards.
The key ethical and legal considerations related to information assurance
A number of key ethical and legal considerations relating to information assurance
must be taken into account by the leaders in the evolving organizational context. In the
case of the Equifax entity, the cyber breach exposed the catastrophic mismanagement of
the security infrastructure by its leaders (Equifax CEO Richard Smith suddenly decides to
‘retire’, 2019). The leaders had failed to take an ethical and legal stance while designing
the security framework. This is evident from the fact that they had failed to patch a well-
known security loophole which is the main reasons why the online hackers were able to
gain access into the organizational system.
The main legal and ethical considerations that the new leaders of the entity took
after the cyber attack include the introduction of the TrustedID Premier services. This new
technique will basically enable the customers to the business entity to determine whether
they have been adversely affected by an incident or not. In case robust ethical and legal
elements are not taken into account by organizations, adverse implications can be faced by

EQUIFAX CYBER ATTACK g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g 7
the affected organization especially, the leaders (Rep. Correa Reiterates Need For Federal
Data Breach Laws, 2019). For instance, federal law has been designed in California after
the data breach incident which crippled the Equifax business entity. Businesses must notify
the Federal Bureau of Investigation (FBI), Federal Trade Commission (FTC) and other
agencies about the data breach incident. g g
The key components of information assurance
In order to establish a robust security system in the organizational context, business
undertakings need to have proper and updated security policies that revolve around
confidentiality, integrity, and availability of information. In the Equifax entity, the security
policy was not well designed. In fact, the business undertaking failed to match the security
model with its market growth (Bloomberg - Are you a robot?, 2019). The organization did
not have clear lines of authority due to which a number of gaps existed in the security
system. Similarly, the organization that specialized in data analytics and technology failed
to modernize its technology-based security model with the evolving times and changing
the technological landscape. As per reports, if the business organization would have been
able to take suitable actions against the observable security loopholes prior to the cyber
incident, the data breach accident could have been totally prevented.
On the highly dynamic and unpredictable technological business setting, business
undertakings need to focus on the confidentiality aspect, integrity aspect and availability
aspect of technology. These key components of information assurance must be ingrained
so that a safe and secure It infrastructure can be created by a business entity.
III. Risk Assessment: Equifax
The term ‘risk assessment’ can be defined as the process of identifying hazards,
negative influences or risk factors are identified. These elements have the potential to
cause harm in a specific context such as a business organization. A proper risk assessment

EQUIFAX CYBER ATTACK g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g 8
process is necessary so that a business concern can effectively function in a dynamic and
uncertain environment (Risk Assessment, 2019).
In the information technology context, a wide range of risks and threats can arise
and have an adverse implication on the manner in which a firm functions. Thus there is a
need to do a thorough risk assessment and devise a suitable information assurance plan.
The risk assessment process acts as the core foundation which can help an entity to
identify the various sources of risks and uncertainties that have the ability to jeopardize the
sustainability of the business (National Research Council, 2007).
The main goals of the risk assessment process are as follows:
❖ Identify the risks and gaps and monitoring the performance against the
requirements.
❖ Identify and prioritize the IT-related risks to the business concern.
❖ Design an effective and robust IT inventory model that can strengthen the
Information Technology infrastructure of the business undertaking.
❖ Mitigate the identified risks that face the business undertaking by implementing
suitable plans (Monahan & Skeem, 2016).
The environment in which Equifax operates
The Equifax business is primarily involved in the data analytics and technology-
based processes. It enables its clients including business organizations and individuals to
make informed decisions. The customers of the business are enabled to connect with a
wide range of equipment so that they can connect to a network. All these aspects are
necessary so that the business undertaking can offer the best possible credit reference and
data intelligence services in the market (Corporate Social Responsibility | ABout Equifax |
Equifax UK, 2019).

EQUIFAX CYBER ATTACK g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g 9
The business undertaking understands that the environment in which it functions
plays a critical role to impact the ultimate service that is offered to its clients. The current
policy of Equifax stresses on the privacy aspects as well as the security aspects so that the
consumers can avail the offerings in a safe and secure environmental setting. Due to the
high level of uncertainty that exists on the IT platform, the business has introduced an
effective online privacy and Cookie policy which will keep the private information of its
clients in a safe manner. In order to secure the clients in the unpredictable business
environment, Equifax has introduced in place a number of security and confidentiality
procedures relating to the storage and the disclosure of the customer information.
Treat Environment of Environment
The information technology environment in which a majority of the business
processes and activities of Equifax are conducted is highly dynamic and unpredictable in
nature. One of the core elements that can endanger the network of the organization is the
‘bring your own device’ BYOD concept. According to an article by Sally Ewalt, even
though this feature can enhance the quality of service for the clients, it is necessary for an
organization like Equifax to take into account the data security aspects (Bring Your Own
Device - But Don't Endanger the Network - Equifax Insights Blog, 2019).
A wide range of security issues can arise that need to be addressed on priority to make
sure that the BYOD model does not hamper the security model of the organization
(Privacy & Cookie Policy | Equifax UK, 2019). The main issues that must be addressed
are as follows:
❖ The strong authentication process could be compromised by introducing an outside
device.
❖ Theft of the device with sensitive organizational information
❖ The issues relating to the overall control of the BYOD in the organizational context.
EQUIFAX CYBER ATTACK g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g 10
Best approaches for implementing information assurance principles
The privacy policy of the Equifax organization does not exactly elaborate on the
specific IT security approaches that are implemented at various levels of the entity. But in
order to implement the information assurance principles in the organizational setting,
Equifax must get a detailed understanding of the specific requirements. The business must
carefully select the IT assets that would contain digital information relating to the clients in
a safe and secure manner (Schou & Hernandez, 2014).
The job description relating to the position of the security risk assessment analyst in
Equifax must be elaborately captured. It would enable Equifax to employ suitable
personnel to take care of the IT security infrastructure. There is the need to focus on the
environmental as well as the physical security control measures so that a holistic
information assurance model could be designed for Equifax. The backup and restoration of
the digital information need to be carefully planned so that the organization could have
proper control over the sensitive data and information relating to its clients and customers.
Threats to and vulnerabilities of Equifax – Risk matrix
Since the Equifax business undertaking mainly deals with sensitive and confidential
data relating to its clients, it is extremely necessary to mitigate the dangers that arise in the
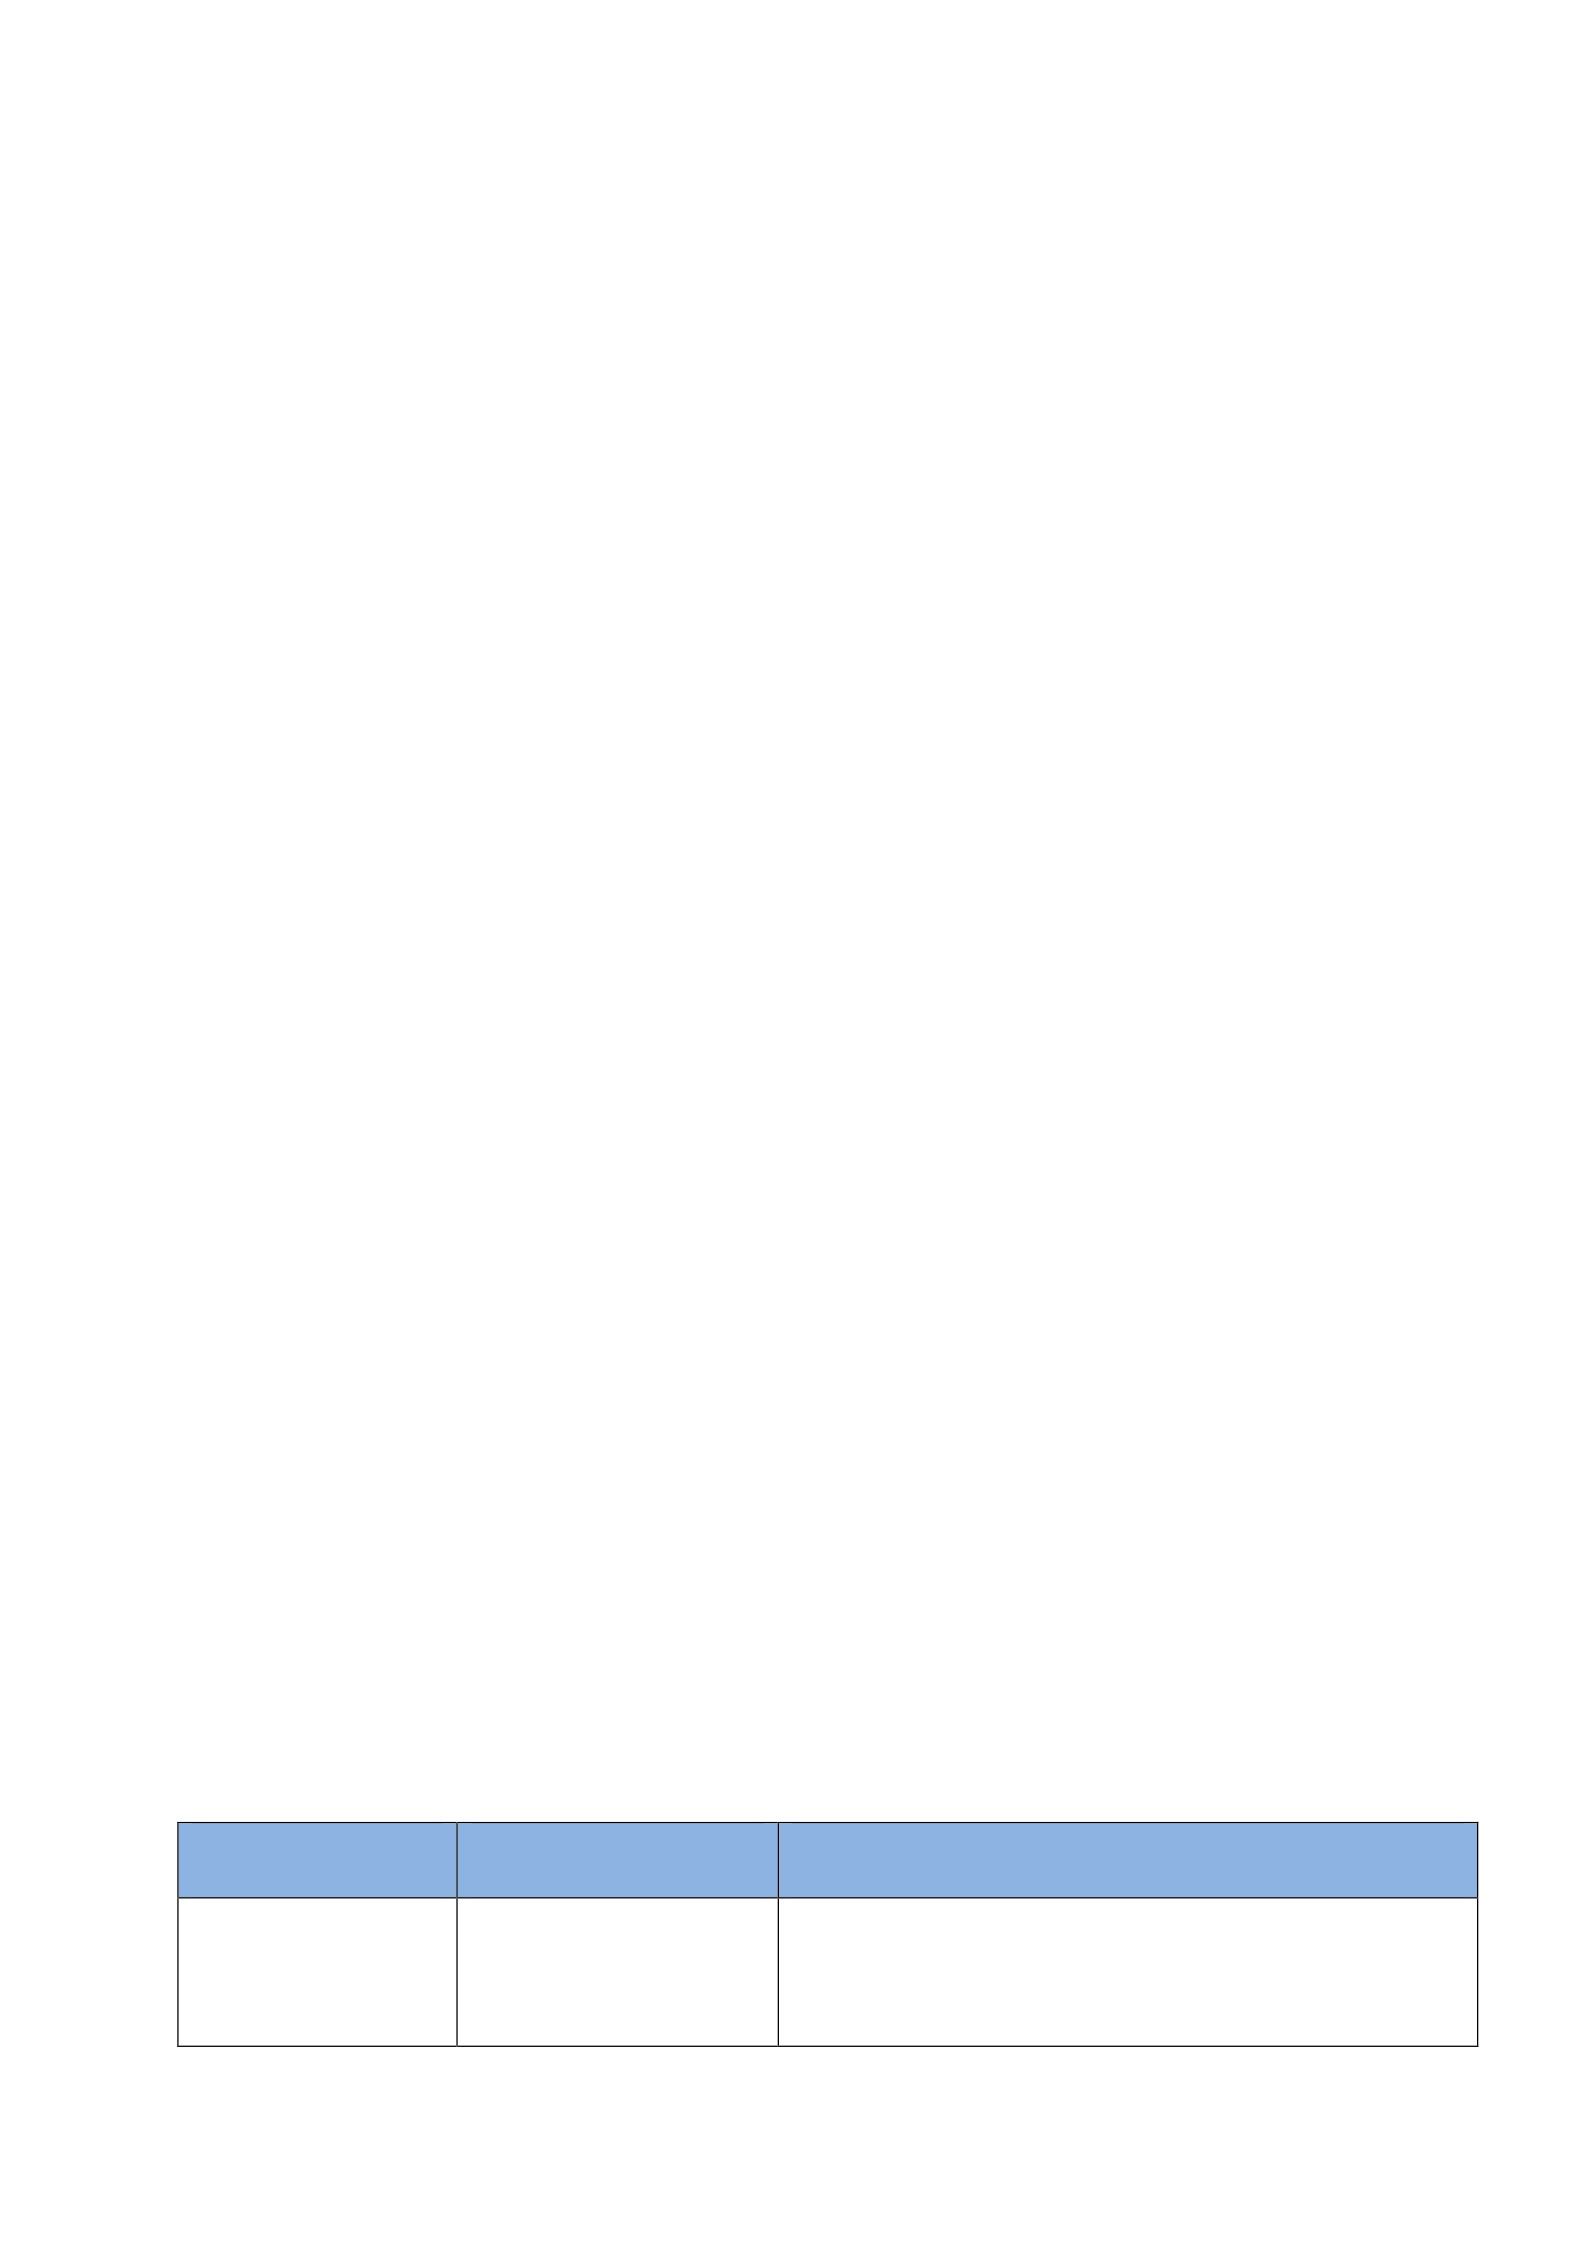
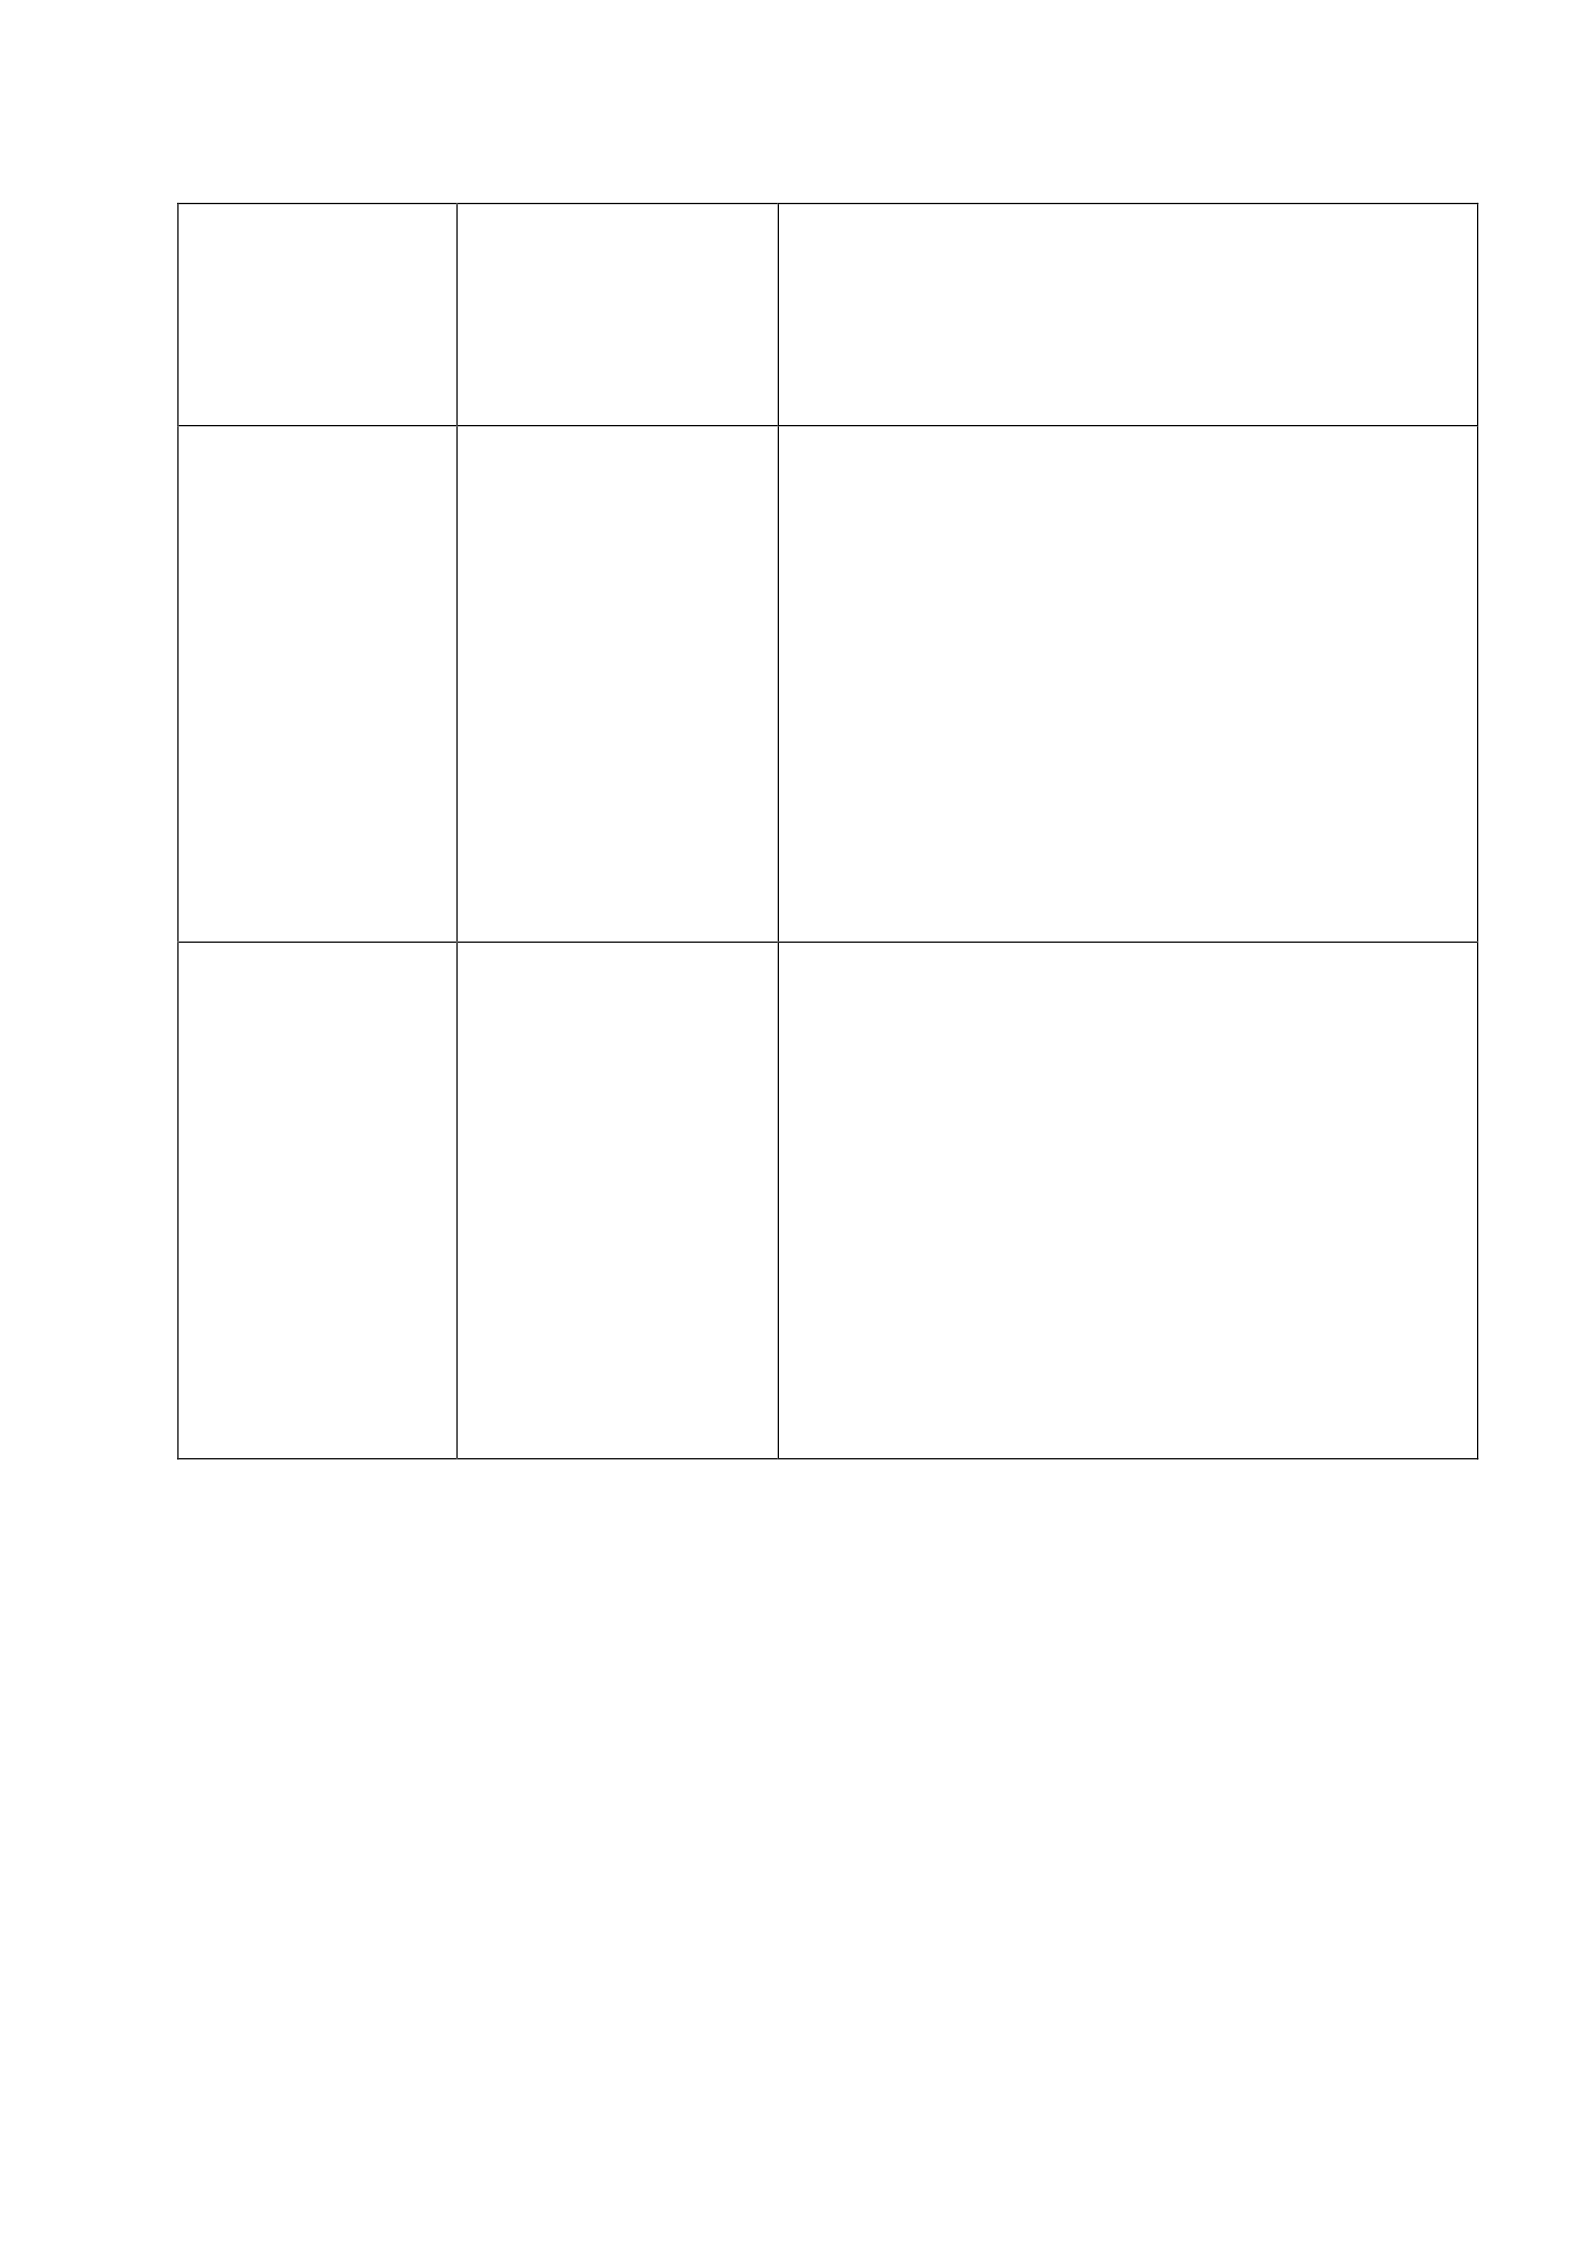
digital arena. The risk matrix that has been presented below captures the threats to Equifax
and the vulnerabilities of Equifax in the dynamic technological environmental setting. The
intention is to outline the threats and vulnerabilities that could adversely impact the
business. Similarly, suitable mitigation strategies have also been presented that would help
to mitigate the identified dangers.
Threats
Risk of impact
Mitigation strategy
Loss of data or
leakage of data
High
Equifax can make sure that all the sensitive and
confidential data and information relating to its
EQUIFAX CYBER ATTACK g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g 11
clients are securely encrypted. This method would
make sure that even if the data is compromised by
an unauthorized party, it cannot be decoded.
Malware
High
The Equifax organization must focus on
establishing robust cybersecurity hygiene. In order
to do so, the business entity needs to employ
proper firewalls, antiviruses and malware software
in place. This holistic technique would help to
identify malware that could compromise the
security mode of the organization.
Phishing
High
Phishing awareness workshops and training must
be designed so that the employees of Equifax
could get a proper understanding of the security
threat. Such a mitigation strategy would enable
them to identify phishing emails that could
adversely affect the security system of the
business organization.
Source: (Security Think Tank: 10 control areas to mitigate against malware attacks,
2019)
IV. Statements of Policy
Lately, a large number of business undertakings have fallen victims to cyber-
attacks. One of the most well-known cyber incidents that had jolted the business setting
involved the Equifax firm. A number of protocols have been recommended for the firm.
Similarly, various mitigating factors to the organization have been highlighted as well. The
main protocols that have been captured here are the Incident Response protocols, Disaster

EQUIFAX CYBER ATTACK g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g 12
Response protocols, Access control protocols, and maintenance plan. The intention is to
design a robust information assurance plan so that such kinds of cyber incidents can be
managed and effectively tackled in the future by Equifax.
Incident Response protocols
The incident response protocol would enable the firm to properly respond and react
to such kinds of events in case they arise in the future. In order to do so, it is extremely
vital to involve organizational personnel in the security process. Equifax must implement a
functional incident response protocol so that the employees will be empowered to respond
to such an event. It would also allow them to take the necessary steps to minimize the
extent of the damage (Incident Response Protocol: Information Technology - Northwestern
University, 2019).
Some of the key stages that are involved in the incident response protocol include
the preparation by the response team, the identification of the environment, the
containment of the damage, the eradication of the threat from the system, recovery and
learning lessons from the incident (Response, 2019).
Justification of the Incident Response protocols
The protocol is necessary as it can help an organization to be ready to face a cyber
threat. Today, such threats can arise before any firm. The protocol will make sure that the
firm and its employees know the steps that they need to take so that they can tactfully
respond to the situation and control the damage. g g
Disaster Response protocols
The business undertakings that work in the global context such as Equifax must
devise suitable disaster response protocols. These protocols will primarily help to devise a
coordinated plan across the various business units which will help to face the danger in the

EQUIFAX CYBER ATTACK g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g 13
cyber setting. Equifax conducts its data analytics and technology function in almost 24
nations (Myers, 2019).
Some of the main elements that can be introduced by Equifax in the Disaster
Response protocol include segregating the authority among professionals to close a site.
Similarly, all the security criteria must be clearly defined so that the leaders can act in an
independent manner. The firm must make sure that there exists no ambiguity while
distributing responsibilities among the organizational personnel of Equifax. In various
locations in which Equifax functions, it must implement streamlined and uniform disaster
response protocols. It would enable the firm to respond in an integrated manner to tackle
vulnerabilities in the cyber setting.
Justification of the Disaster Response protocols
The relevance of proper disaster response protocol would be extremely vital for the
Equifax concern. This element of the security policy would make sure that all the
individuals are aware of their exact roles and responsibilities when a threat in the cyber
setting arises. It would enable them to get a detailed insight into various angles from where
the threat could loom such as the attack on cloud services, mobile device attack, and
ghostware attack (Emergency Management for Cyber Attacks, 2019).
Access control protocols
Equifax would have to establish a number of access control protocols on its policy
so that specific individuals would have the authority to have access to certain areas of the
IT ecosystem. This protocol would ensure that professionals would be able to meet certain
criteria before they gain access to the system. This control mechanism would enable the
business to introduce innovative elements such as PIN, fingerprints identification model or
iris identification model.

EQUIFAX CYBER ATTACK g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g 14
The access control protocol of Equifax must be developed so that the firm could be
well equipped to defend itself from internal threats as well as external threats. The protocol
would facilitate the business concern to involve the appropriate team members in the attack
mitigation plans (my Social Security | Social Security Administration, 2019). A vital
practice that the business undertaking must keep in mind relates to the regular drafting,
implementing and upgrading of the cybersecurity plan. Such an approach would play an
extremely critical role to prepare the firm to face uncertain cyber events. g
Justification of the access control protocols
Equifax needs to introduce the access control protocols in the security policy as it
would strengthen its security model in the uncertain cyber setting. These protocols would
safeguard the firm from internal threats as well as external risks. It would make sure that
power to have access to certain sensitive IT areas is in the hands of a few individuals.
Such an approach could minimize the vulnerability of the business in the dynamic cyber
setting.
Recommendation for maintaining the information assurance plan
In order to maintain the robust information assurance plan, Equifax must make sure
that the appropriate policies, practices, standards, and guidelines are always followed by
the organizational personnel.
The policies and security component must be matched with the firm’s risk profile.
A robust risk assessment model must be designed comprising of implementation,
monitoring, testing, and reporting elements. It would help to maintain the information
assurance plan of Equifax firm. g
In addition to the firm’s information security policy, Equifax must also follow the
security standards that are applicable at the industry level. For example, in case the firm

EQUIFAX CYBER ATTACK g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g 15
deals with branded credit cards from the clients, it must make sure to follow the Payment
Card Industry Data Security Standard (PCI DSS).
Since the information security policies and protocols would act as the backbone of
Equifax’s information assurance plan. It is necessary to follow the recommendations so
that the maintenance of the assurance plan could be possible (How to Develop & Maintain
Information Security Policies & Procedures, 2019).
Justification of the maintainable plan
The maintenance plan has been designed to make sure that the information
assurance plan of Equifax would play a vital role and defend the firm and its Information
Technology ecosystem in the unpredictable cyber setting. By properly following the
security model, the vulnerability of the firm could be controlled in a better manner. The
proper maintenance of the assurance plan by the business undertaking would play a vital
role to strengthen its stance against cyber attackers and hackers who could exploit the
vulnerabilities of the business concern. The proper maintenance of the information
assurance plan would help the firm to know the current status of the security system. Thus
it could strengthen, upgrade and maintain the quality of the information assurance plan. In
the unpredictable cyber setting, the role of the assurance plan would be indispensable in
nature for Equifax. It would help the business undertaking to prevent similar kind of attack
that had previously affected its brand reputation and crippled its business activities.
V. Conclusion:
Need for information assurance plan:
Information assurance is the process of ensuring appropriate management of
specific data and risks pertaining to them in various aspects of application usage,
transmission, processing and storage. Information assurance is ensured by taking care of
different aspects such as integrity, confidentiality, availability, authenticity and non-

EQUIFAX CYBER ATTACK g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g 16
repudiation. The importance of information assurance plan is clearly observed in the
necessity for safeguarding user data in transit stages as well as with storage. Therefore,
information assurance is accounted as a significant component of data security because
business processes and transactions are prominently associated with digital management
practices.
Equifax has experienced considerable issues in information security due to the
hacking attack on its database which compromised many crucial details of consumers such
as name, birth date, social security number, driver’s license number and address. This
served as the primary background for reflecting on the need for a proper information
assurance plan for Equifax. From the basic viewpoint, Equifax is legally as well as
ethically obliged to safeguard user information with appropriate security measures in place
for digital information as well as physical information. It can also be pointed out that
information assurance not only deals with preventing external attacks on the information
systems of Equifax but also putting measures in place to ensure recovery of the
compromised information.
An outline of the legal and ethical responsibilities of Equifax for information
security could provide a reliable impression of the need for an information assurance plan
for the organization. In terms of legal responsibilities, the organization has to comply with
the federal law in California that clearly states the need to report immediately to the
Federal Bureau of Investigation (FBI) and the Federal Trade Commission (FTC) as well as
other agencies about the incident of data breach. The organization has also made claims in
its official business description about protecting confidential information related to clients
and customers through encrypting the information. This points out towards the ethical
responsibility of Equifax to invest maximum efforts in protecting customer information.
Another ethical responsibility that can be identified in context of information assurance

EQUIFAX CYBER ATTACK g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g 17
plan of Equifax is to monitor the BYOD (Bring Your Own Device) use in organizational
context for preventing any information leaks. The TrustedID Premier services introduced
by Equifax in the aftermath of attacks on its information systems can be accounted as a
formidable component in the information assurance plan of Equifax as it can let customers
know if their information has been compromised or not. This provides a certain level of
autonomy to the clients for safeguarding the confidentiality, integrity and availability of
their information. Hence, Equifax has brought customers in the scope of its information
assurance measures that can help it in safeguarding its ethical obligations for information
security.
Key elements of information assurance plan:
The key stakeholders that have to be taken into consideration for the information
assurance plan of Equifax include the CEO, Chief Information Officer, Chief Technology
Officer and Chief Security Officer alongside employees, customers and agencies such as
the Federal Bureau of Investigation (FBI). Each of these stakeholders has a different role
in safeguarding the elements of confidentiality, integrity and availability (CIA triad) of
information at Equifax. Confidentiality refers to the protection of access to information and
this can be the responsibility of the Chief Information Officer and the Chief Technology
Officer. They are responsible for designing the information security framework for the
organization with appropriate policies and procedures in place for ensuring that
unauthorized agents are not able to access sensitive information.
Employees as well as customers can also be held responsible for confidentiality as
they should not engage in disclosure of information access methods to external agents. For
examples, employees practicing the BYOD model should not allow external agents to
access their device and customers should protect their login id and details from disclosure.

EQUIFAX CYBER ATTACK g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g 18
Integrity of the data is under the responsibility of the CEO, CIO and CTO as they
have to employ the necessary policies for establishing data accessing privileges and the
necessary penalties for violations thereby preventing any sort of unauthorized modification
in the information at Equifax. The CEO, CTO and CIO are also answerable for availability
element of information as they have to make sure of recovery systems that can bring back
the compromised information for use by clients. Hence, a clear estimate of the need for
information assurance plan for Equifax as well as the outline of responsible stakeholders
for different aspects of information assurance was able to provide a conclusion to the
design of a functional information plan highlighted in this assessment. g g g g g g g
VI. References
Bloomberg - Are you a robot?. (2019). Retrieved from
https://www.bloomberg.com/news/articles/2018-12-10/equifax-failed-to-adjust-
security-to-rapid-growth-report-says
Bring Your Own Device - But Don't Endanger the Network - Equifax Insights Blog.
(2019). Retrieved from https://insight.equifax.com/bring-your-own-device-but-dont-
endanger-the-network/
Corporate Social Responsibility | ABout Equifax | Equifax UK. (2019). Retrieved from
https://www.equifax.co.uk/about-equifax/corporate-social-responsibility/en_gb/
Deanne, M. (2019). The Equifax Cyber Attack - How It Happened and How to Protect
Yourself. Retrieved from https://interwork.com/equifax-cyber-attack-happened-
protect/
Emergency Management for Cyber Attacks. (2019). Retrieved from
https://safetymanagement.eku.edu/blog/emergency-management-for-cyber-attacks/
EQUIFAX CYBER ATTACK g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g 19
Equifax hack: two executives to leave company after breach. (2019). Retrieved from
https://www.theguardian.com/technology/2017/sep/15/equifax-hack-susan-mauldin-
david-webb
Equifax CEO Richard Smith suddenly decides to ‘retire’. (2019). Retrieved from
https://www.engadget.com/2017/09/26/equifax-ceo-retires-after-massive-data-breach/
Exhibit A - Internet Security Requirements. (2019). Retrieved from
https://www.equifax.com/eport/internet-security/
Equifax Says Cyberattack May Have Affected 143 Million in the U.S. (2019). Retrieved
from https://www.nytimes.com/2017/09/07/business/equifax-cyberattack.html
Fortune.com. (2019). Retrieved from http://fortune.com/2018/09/07/equifax-data-breach-
one-year-anniversary/
How to Prepare For and Respond To A Cyber Attack: Have A Disaster Recovery Plan |
OlenderFeldman LLP. (2019). Retrieved from https://www.olenderfeldman.com/how-
to-prepare-for-and-respond-to-a-cyber-attack-have-a-disaster-recovery-plan/
How to Develop & Maintain Information Security Policies & Procedures. (2019).
Retrieved from https://www.bankinfosecurity.com/webinars/how-to-develop-maintain-
information-security-policies-procedures-w-135
Incident Response Protocol: Information Technology - Northwestern University. (2019).
Retrieved from https://www.it.northwestern.edu/policies/incident.html
Monahan, J., & Skeem, J. L. (2016). Risk assessment in criminal sentencing. Annual
review of clinical psychology, 12, 489-513.
Myers, L. (2019). How many people outside the US are affected by the Equifax breach? |
WeLiveSecurity. Retrieved from https://www.welivesecurity.com/2017/09/15/many-
people-outside-u-s-affected-equifax-breach/
EQUIFAX CYBER ATTACK g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g 20
My Social Security | Social Security Administration. (2019). Retrieved from
https://www.ssa.gov/myaccount/
National Research Council. (2007). Scientific review of the proposed risk assessment
bulletin from the Office of Management and Budget. National Academies Press.
Privacy & Cookie Policy | Equifax UK. (2019). Retrieved from
https://www.equifax.co.uk/About-us/Privacy_policy.html
Rep. Correa Reiterates Need For Federal Data Breach Laws. (2019). Retrieved from
https://medium.com/congressman-lou-correa/rep-correa-reiterates-need-for-federal-
data-breach-laws-22bacdc57348
Risk Assessment. (2019). Retrieved from
https://www.ccohs.ca/oshanswers/hsprograms/risk_assessment.html
Response, T. (2019). The Six Stages of Incident Response. Retrieved from
https://www.cso.com.au/article/600455/six-stages-incident-response/
Schou, C., & Hernandez, S. (2014). Information Assurance handbook: Effective computer
security and risk management strategies. McGraw-Hill Education Group.
Security Think Tank: 10 control areas to mitigate against malware attacks. (2019).
Retrieved from https://www.computerweekly.com/opinion/Security-Think-Tank-10-
control-areas-to-mitigate-against-malware-attacks
Solomon, H. (2019). Congress report: Equifax breach ‘entirely preventable,’ blames
‘culture of cyber security complacency’. Retrieved from
https://www.itworldcanada.com/article/congress-report-equifax-breach-entirely-
preventable-blames-culture-of-cyber-security-complacency/412857
Staff, T. (2019). The Equifax breach: consequences, implications, and sequelae. Retrieved
from https://thecyberwire.com/articles/the-equifax-breach-consequences-implications-
and-sequelae.html

EQUIFAX CYBER ATTACK g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g g
g g g g g g g g g g g g g g g g g g g g g g g g g g g g 21

