


Running Head: ISE 510 e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e
e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e 1
SNHU
ISE 510 Security Risk Analysis & Plan
Security Breach Analysis and Recommendations
FINAL PROJECT

ISE 510 e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e
e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e 2
2
I. Introduction
Limetree Inc. is a well-known research and development business entity that
specializes in research projects in various areas such as biotechnology, healthcare, and other
cutting-edge industries. It works with private corporations as well as the federal
government. Lately, the business undertaking has been experiencing substantial growth in
the operational industry but it is concerned about the rising security breach incidents that
are taking place in the unpredictable industrial setting. One of the core objectives of the
business undertaking is to strengthen its information security program so that it can achieve
its business goal.
The Limetree Inc. organization has been facing significant security breaches lately. It
believes that confidential information was stolen from it including Personal Health
Information (PHI) that were utilized in a research study. The existing security protocols and
policies are inadequate as they do not adhere to the existing industry standards. The
security breach incident could adversely impact the survival and sustainability of Limetree
Inc. in the operational industry. Malicious cybersecurity incidents had cost the United States
economy between USD 57 billion and USD 109 billion in the year 2016 alone. Both large
and small businesses need to identify their security vulnerabilities and strengthen their
cybersecurity framework so that security breach incidents can be prevented or avoided.
The paper captures the security breach incident that took place in Limetree Inc and
compromised the quality of security of the firm. The key vulnerabilities of the entity have
been identified and a robust incident response plan has been designed so that similar kinds
of security incidents could be prevented in the future. A security test plan has been
designed and suitable recommendations have been designed to strengthen the security
infrastructure of the organization.
II. Security Breach
Some of the likely causes of the breach include the poor security posture of the
organization, the lack of proper documentation of the security policies and the lack of
proper training of employees on security awareness. At present Limetree does not have a
robust security framework in place which could give cyber attackers an upper hand to
exploit the vulnerabilities of the organization. The low security posture of the firm is a
major IT concern that could have led to the security breach incident.
A. Attack Location:
The attack that took place in Limetree impacted all the employees of the research
organization especially the research team. This is because personal health information (PHI)
that was used in a recent research study was stolen by the attackers. The physical and IT
environment of Limetree has a number of gaps that could have given access to online
hackers to invade the system and compromise the security.

ISE 510 e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e
e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e 3
3
B. Attack Method and Tools:
In order to carry out the security breach attack, the insider data theft attack is a
probable method that could be used by an attacker. In such an attack, sensitive information
relating to the company could be stolen without the knowledge of the employees. As the
employees lack proper training on security awareness, this method must have been used to
conduct the security breach in Limetree.
C. Vulnerabilities:
As per Jack Sterling, the Security Manager of Limetree Inc, even though the firm has
faced security incidents before, no previous documented history of incidents was stored
which could be used to identify the corrective measures that were taken to deal with the
incidents. Similarly, the process of sharing information on a computer incident is quite
lengthy. For instance, the administrators escalate the incident to the IT manager, who
reports incidents to the security manager if they are considered to be relevant. These were
the two major vulnerabilities that were exploited to affect the attack as per John.
The physical vulnerabilities that Jack Sterling has identified include:
• Users are not given training on security awareness
• Visitors just sign in at the front desk and are allowed to walk in to see employees
at their respective offices.
• The users are generally allowed to bring in their own laptops and connect to the
corporate system.
The vulnerabilities that Jack Sterling has identified in the Administrative Office
workstations include:
• The low level of security setting of the Internet Explorer browser and the absence of
a standard browser for the environment.
• The low disk space for the SQL database log which is overwritten with new
information when it is full.
• No segmentation or authentication between the wireless and wired LAN. Visitors are
given access code to use the wireless network of the company.
• Absence of logging of network activities on any of the switches.
• The public-facing web server is a part of the LAN and it acts as the key point
where internet users get information on the company.
• Absence of documented security policy, or computer use policy.
• Lack of a properly documented process for changes to the system.
• Absence of any contingency plan.
The vulnerabilities that Jack Sterling identified regarding the Wi-Fi was that the
Wireless network was available with clearly advertised SSID, and it was a part of the local
area network (LAN). There was no segmentation or authentication between the wireless and
wired LAN which was a major security blunder. Visitors are given access code to the
wireless network at the front desk which increases the vulnerability of the firm’s network.

ISE 510 e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e
e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e 4
4
III. Incident Response
The purpose of the incident response plan is to help the research and development
organization to be prepared in case any security incidents arise. It would strengthen the
security infrastructure of the organization and minimize its vulnerability on the cyber
platform.
The current Incident Response Plan at Limetree is very ineffective and weak. I case any
security incidents arise, the system administrators are notified of the same and they escalate
the issue to the IT Manager. He is then responsible to report the incident to the Security
Manager if it is considered to be an actual incident. Currently, there exists no
documentation process so there is no record of previous security incidents.
A. Purpose of the Incident Response Plan
The purpose of the incident response plan is to help the research and development
organization to be prepared in case any security incidents arise. It would strengthen the
security infrastructure of the organization and minimize its vulnerability on the cyber
platform.
B. Incident Response
A new Incident Response Plan has been proposed that could be introduced at Limetree
to upgrade its security posture. The process has been designed so that the Incident
Response Team could take necessary measures to deal with the security issue and make
sure that the extent of the damage can be curbed to the best possible extent. The main
phases that would be involved in the plan have been highlighted below.
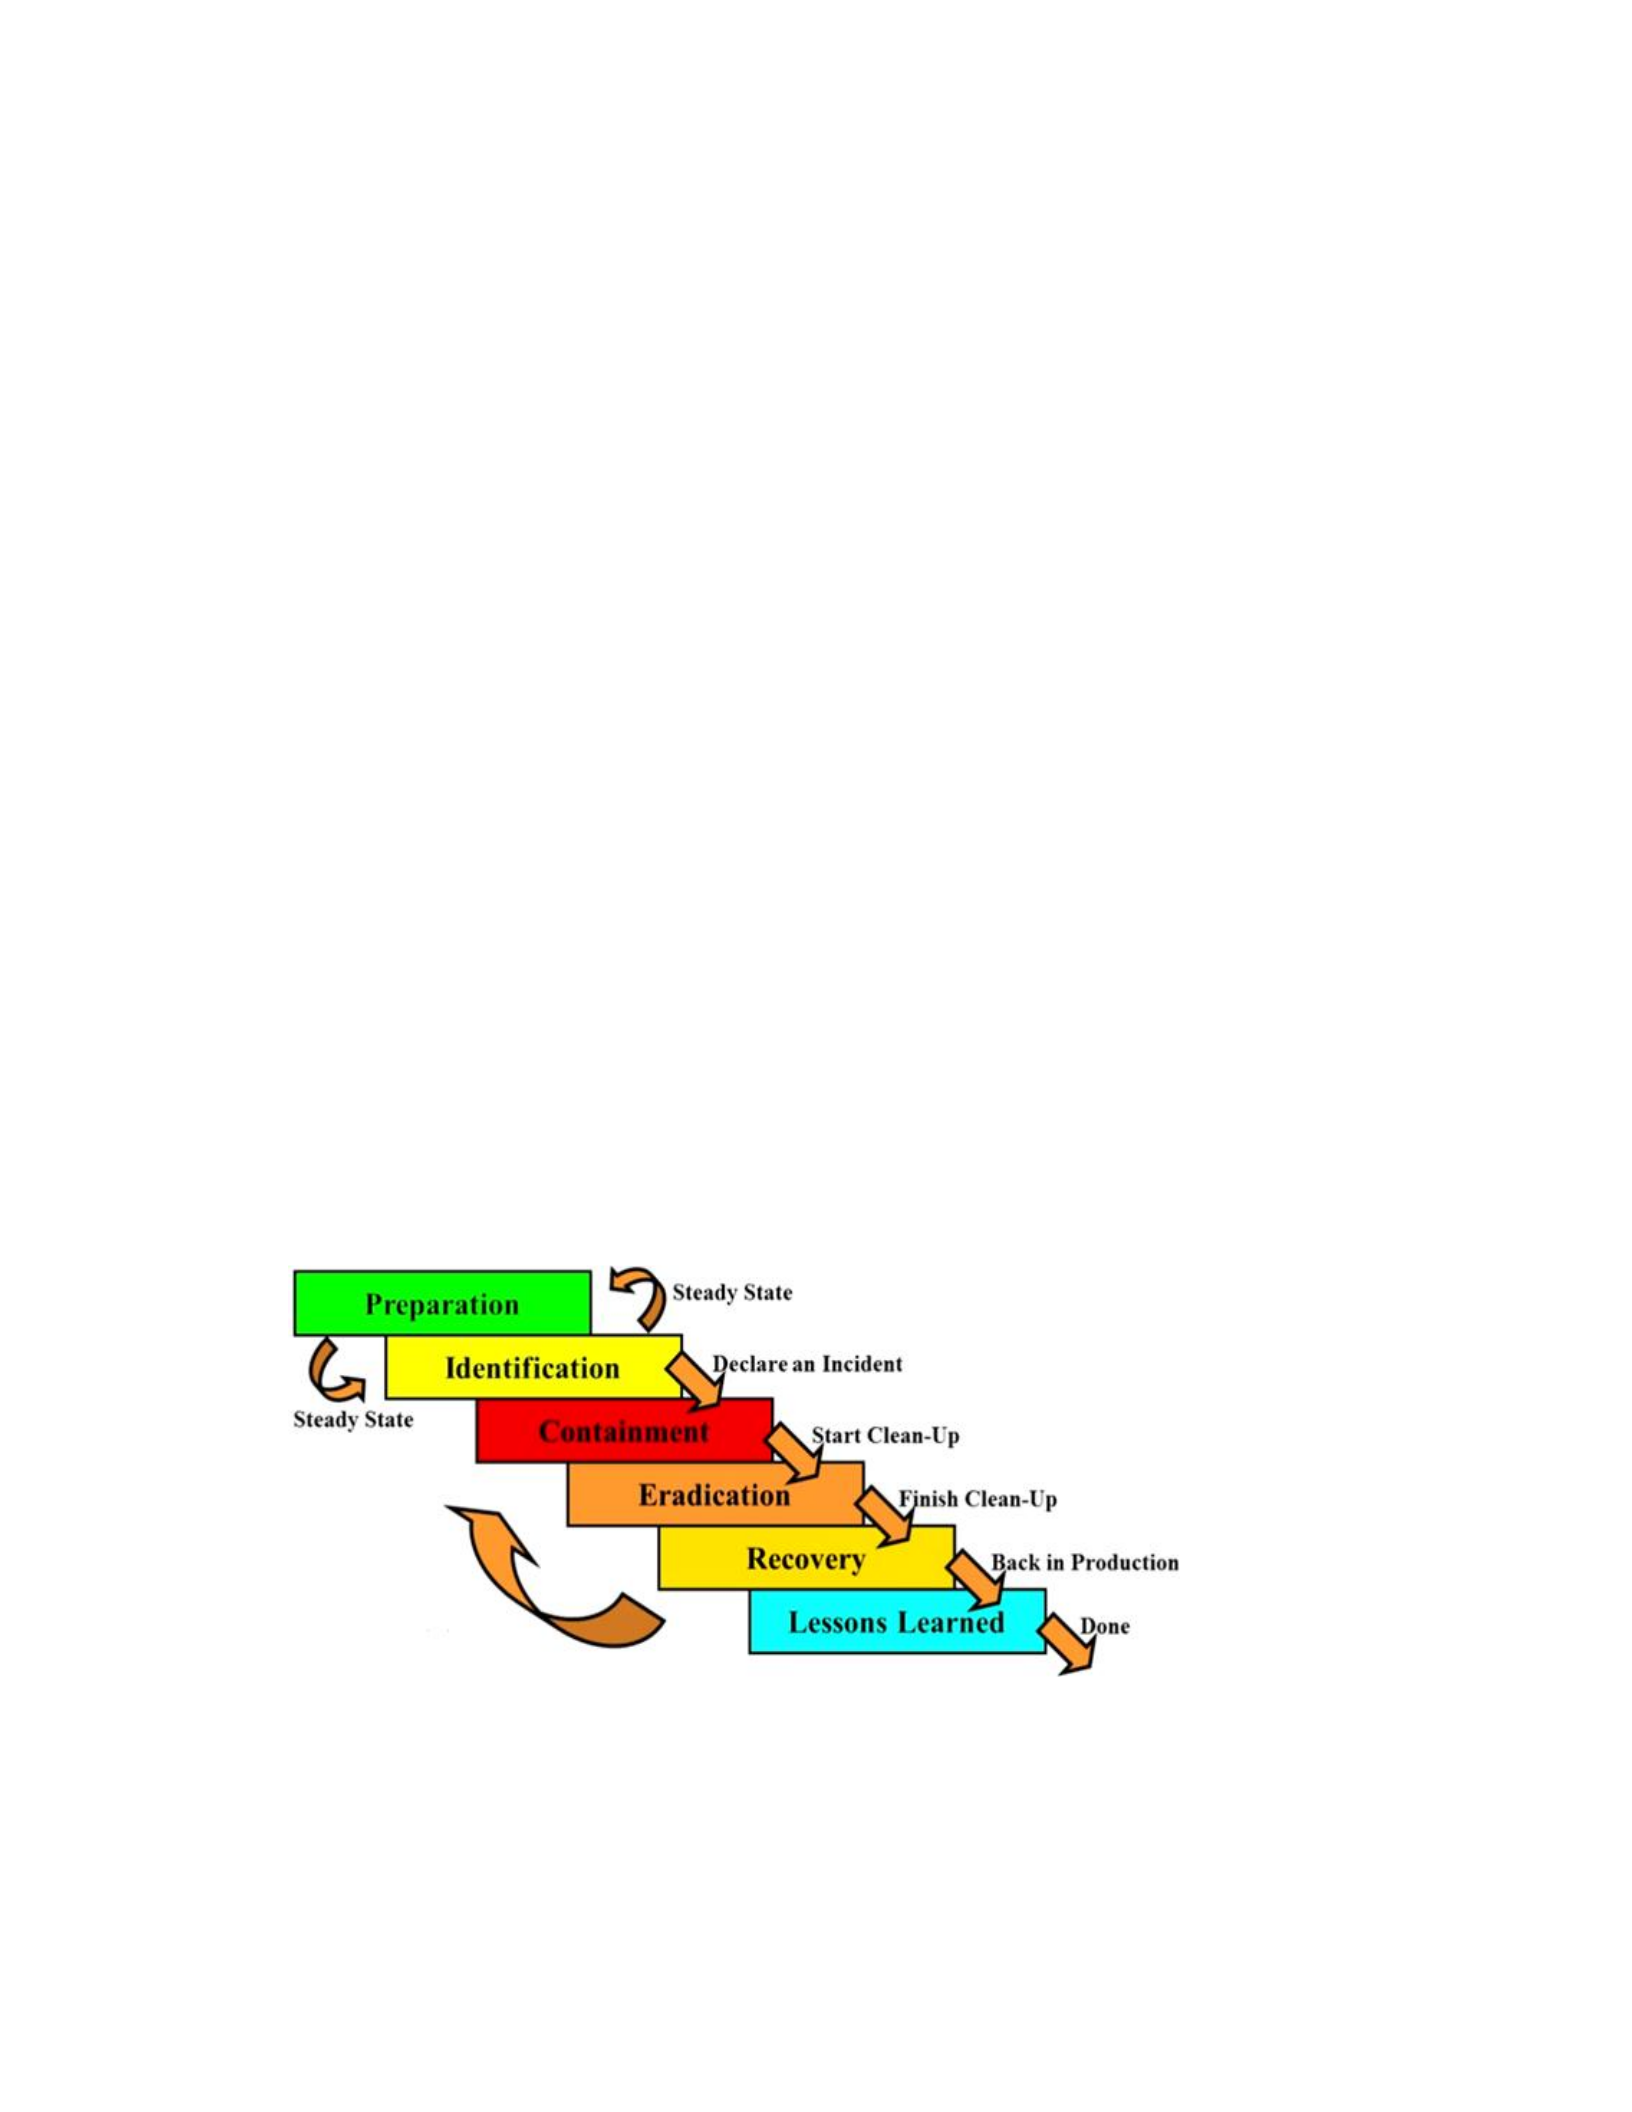
1) Preparation - In the preparation stage, Limetree must make sure to develop suitable
capabilities so that security incidents could be prevented in the future. So the research and
development organization must ensure highly-functional and effective networks, systems,
hardware, and applications are employed.
2) Identification - Limetree has to confirm, categorize, determine the scope and prioritize
various kinds of risks that could arise in the IT ecosystem. Such an approach would enable
the business to get a better insight into the threats and risks that could affect the business
in the cyber setting.
3) Containment - Necessary steps have to be in place so that the damage can be
minimized or mitigated to a possible extent. Limetree has to ensure the affected devices are
disconnected from the internet so that the spreading of the breach could be restricted
(Supplement to ISE510 Security Risk and Planning, 2019).
4) Eradication - In order to eliminate the cybersecurity threat, Limetree has to ensure that
the root cause of the issue is dealt with. So, all malicious elements have to be securely
removed and the system would have to be hardened and patched.
5) Recovery - Limetree has to assess the incident to get a detailed insight into the
procedural and policy implementations (CRR Supplemental Resource Guide, 2019). At this
stage, the business undertaking would have to restore the affected systems so that they
could be restored and brought back into the business environment. The firm must ensure to
ISE 510 e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e
e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e 5
5
document each and every process so that in the new future it could prepare itself in case a
similar security breach incident arises (Blair, 2015).
6) Lessons Learned – After the in-depth investigation relating to the cybersecurity incident
has been completed, a post-action meeting must be conducted by the Incident Response
team at Limetree. All the members would get the opportunity to discuss the learning from
the data breach incident. This meeting would allow them to assess and document every
little aspect relating to the security incident. Some of the main questions that need to be
addressed relate to the following areas:
• The changes that need to be introduced in the security model of Limetree so that
its security posture can be strengthened.
• The training process that must be implemented for the employees of the firm so
that their security awareness can be improved
• The exact weaknesses and vulnerabilities that were exploited by the cyber attackers
• The steps that must be taken to avoid similar kinds of security breach incident in
the future
C. The Incident Response Process:
The new Incident Response Process that would be implemented at Limetree
encompasses a number of procedures that will help to minimize the impact of the security
incident and make a solid recovery. The figure that has been highlighted below shows that
a number of processes of the response plan would be carried out interchangeably so that
proper measures could be introduced to deal with the security issue. After a security
incident has been identified and corrective actions have been taken, the recovery procedure
must be initiated. As highlighted in the figure, in case fresh malicious elements have been
identified, the team can go back to the containment stage so that suitable measures can be
deployed to contain the extent of damage that might be caused by the IT security breach
incident. e e e
The team would have to actively assess the Information Technology ecosystem of
Limetree so that it could be able to identify any kind of malicious behavior in its network
or system. All the phases of the Incident Recovery Plan must be followed in a disciplined
manner. The logging records must be critically analyzed to identify any potential security
incident. IT would help to classify the incident that could arise before the research and
development entity and compromise its security posture.

ISE 510 e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e
e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e 6
6
The IT staff members and personnel would be playing an active role throughout the
cybersecurity incident in the organizational setting of Limetree so that all traces of
malicious elements could be effectively identified and suitable actions could be taken
against them. Throughout the process, the roles of communication among the team members
would be of paramount importance. Such an approach would make sure that the proper
flow of information and details takes place among the organizational personnel on a real-
time basis. The knowledge of the professionals on the latest cybersecurity incidents must be
upgraded on a regular basis so that they could play an active role throughout the incident
response process within Limetree Inc.
IV. Impact
A. Application
Limetree Inc. is a reliable research and development organization that conducts research
activities in various curing edge fields for both the federal government as well as private
corporations. As it has a close link with the federal government, and its research projects,
the R&D firm has to abide by the latest federal legislation as well as industrial regulations
and standards so that it can keep a robust security framework in place. There are a number
of Acts and laws that the organization must give special attention to so that a strong
security posture can be maintained. For instance, the business undertaking must comply
with the Health Insurance Portability and Accountability Act (HIPAA) which relates to data
privacy and security provisions. The objective is to safeguard the confidential medical
information (Rouse & Biscobing, 2019).
Limetree must also adhere to the Health Information Technology for Economic and
Clinical Health Act. This act was initiated to encourage the implementation of electronic
health records (EHR) and strengthen the use of technology in the United States of America.
The HITECH Act was introduced in the year 2009 so that the exchange of electronic
protected health information (ePHI) between hospitals, physicians and other bodies could be
simplified (What is the HITECH ACT?: What HITECH Compliance Means, 2019).
Limetree Inc. has to ensure that the security model that is implemented throughout the
organization is in sync with the regulations and legislation that exist in the industrial
setting. The National Institute of Standards and Technology (NIST) must be considered as
the main body which would provide proper guidelines so that the IT security infrastructure
of the organization could be strengthened.
B. Impact
The regulations and industry standards that have been introduced by NIST would
playa vital role and help Limetree to strengthen the IT security framework of the
organization. It must make sure to adhere to NIST guidelines, HIPAA and HITECH so that
the confidentiality and integrity of the sensitive business information would not get
compromised. The regulations would basically guide the research and development firm to
introduced robust and appropriate security controls in place which could upgrade the
effectiveness of the security system. The inability to comply with the security legislation
and standards would have a negative impact on the business reputation of Limetree. In

ISE 510 e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e
e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e 7
7
addition to this, legal action could be taken by its clients in case a security breach incident
is extremely serious in nature.
C. Financial and Legal Implications
The implications that Limetree Inc. would face if it fails to adhere to the regulations
and a security breach incident occurs would affect it legally and financially. The
trustworthiness of the business in the market environment could be adversely affected which
would affect its credibility before its clients and customers. If clients would lose trust, they
would shift to Limetree’s competitors and its profitability could drastically decline. In case
Limetree gets involved in a major security breach incident where confidential and highly
sensitive information of the clients gets leaked then it could be taken to the court of law.
V. Security Test Plan
The security test plan primarily captures the scope of the security test, the key
resources that would be used to strengthen the security posture of the organization. The
resources that have been highlighted in this section include the people resources. In addition
to this, the hardware and software of Limetree Inc. have also been captured as they make
up the Information Technology infrastructure of the organization. The special tools that
would be required by the ACME Cybersecurity, based on Limetree’s hardware and software
have also been highlighted in the security test plan.
A. Scope:
The scope of the project is to conduct a thorough assessment of the information security
system of Limetree Inc. so that the security breach incident can be evaluated. In order to
carry out a comprehensive check, there is the need to forensically analyze all the 250
computers that are used in Limetree Inc. Based on the thorough analysis, suitable
recommendations would be made for the research and development business so that the
security posture of its IT system can be strengthened. The various risks and threats that the
business undertaking is currently exposed to because of its security loopholes will be
identified and accordingly, a roust security model will be planned for the firm.
The risk assessment will help Limetree to get an in-depth idea about the effectiveness
or ineffectiveness of the existing security approach. The ACME Cybersecurity Consulting
Team would enable the research and development entity to understand the IT vulnerabilities
that exist in the business undertaking which give an edge to cybercriminals and attackers.
The security test plan has been designed with the intention to identify the threats and
vulnerabilities so that suitable strategies can be introduced in order to mitigate the same.
The team of experts that have been hired would play a vital role to execute the project
security plan. They would help to develop robust secure network solutions, safeguard the
firm’s confidential data and design suitable cybersecurity strategies across the organization.
B. Resources:
ISE 510 e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e
e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e 8
8
People resources would be of chief importance to make sure that security issues, risks
and vulnerabilities in Limetree Inc. can be effectively identified and the overall quality of
the security posture can be strengthened.
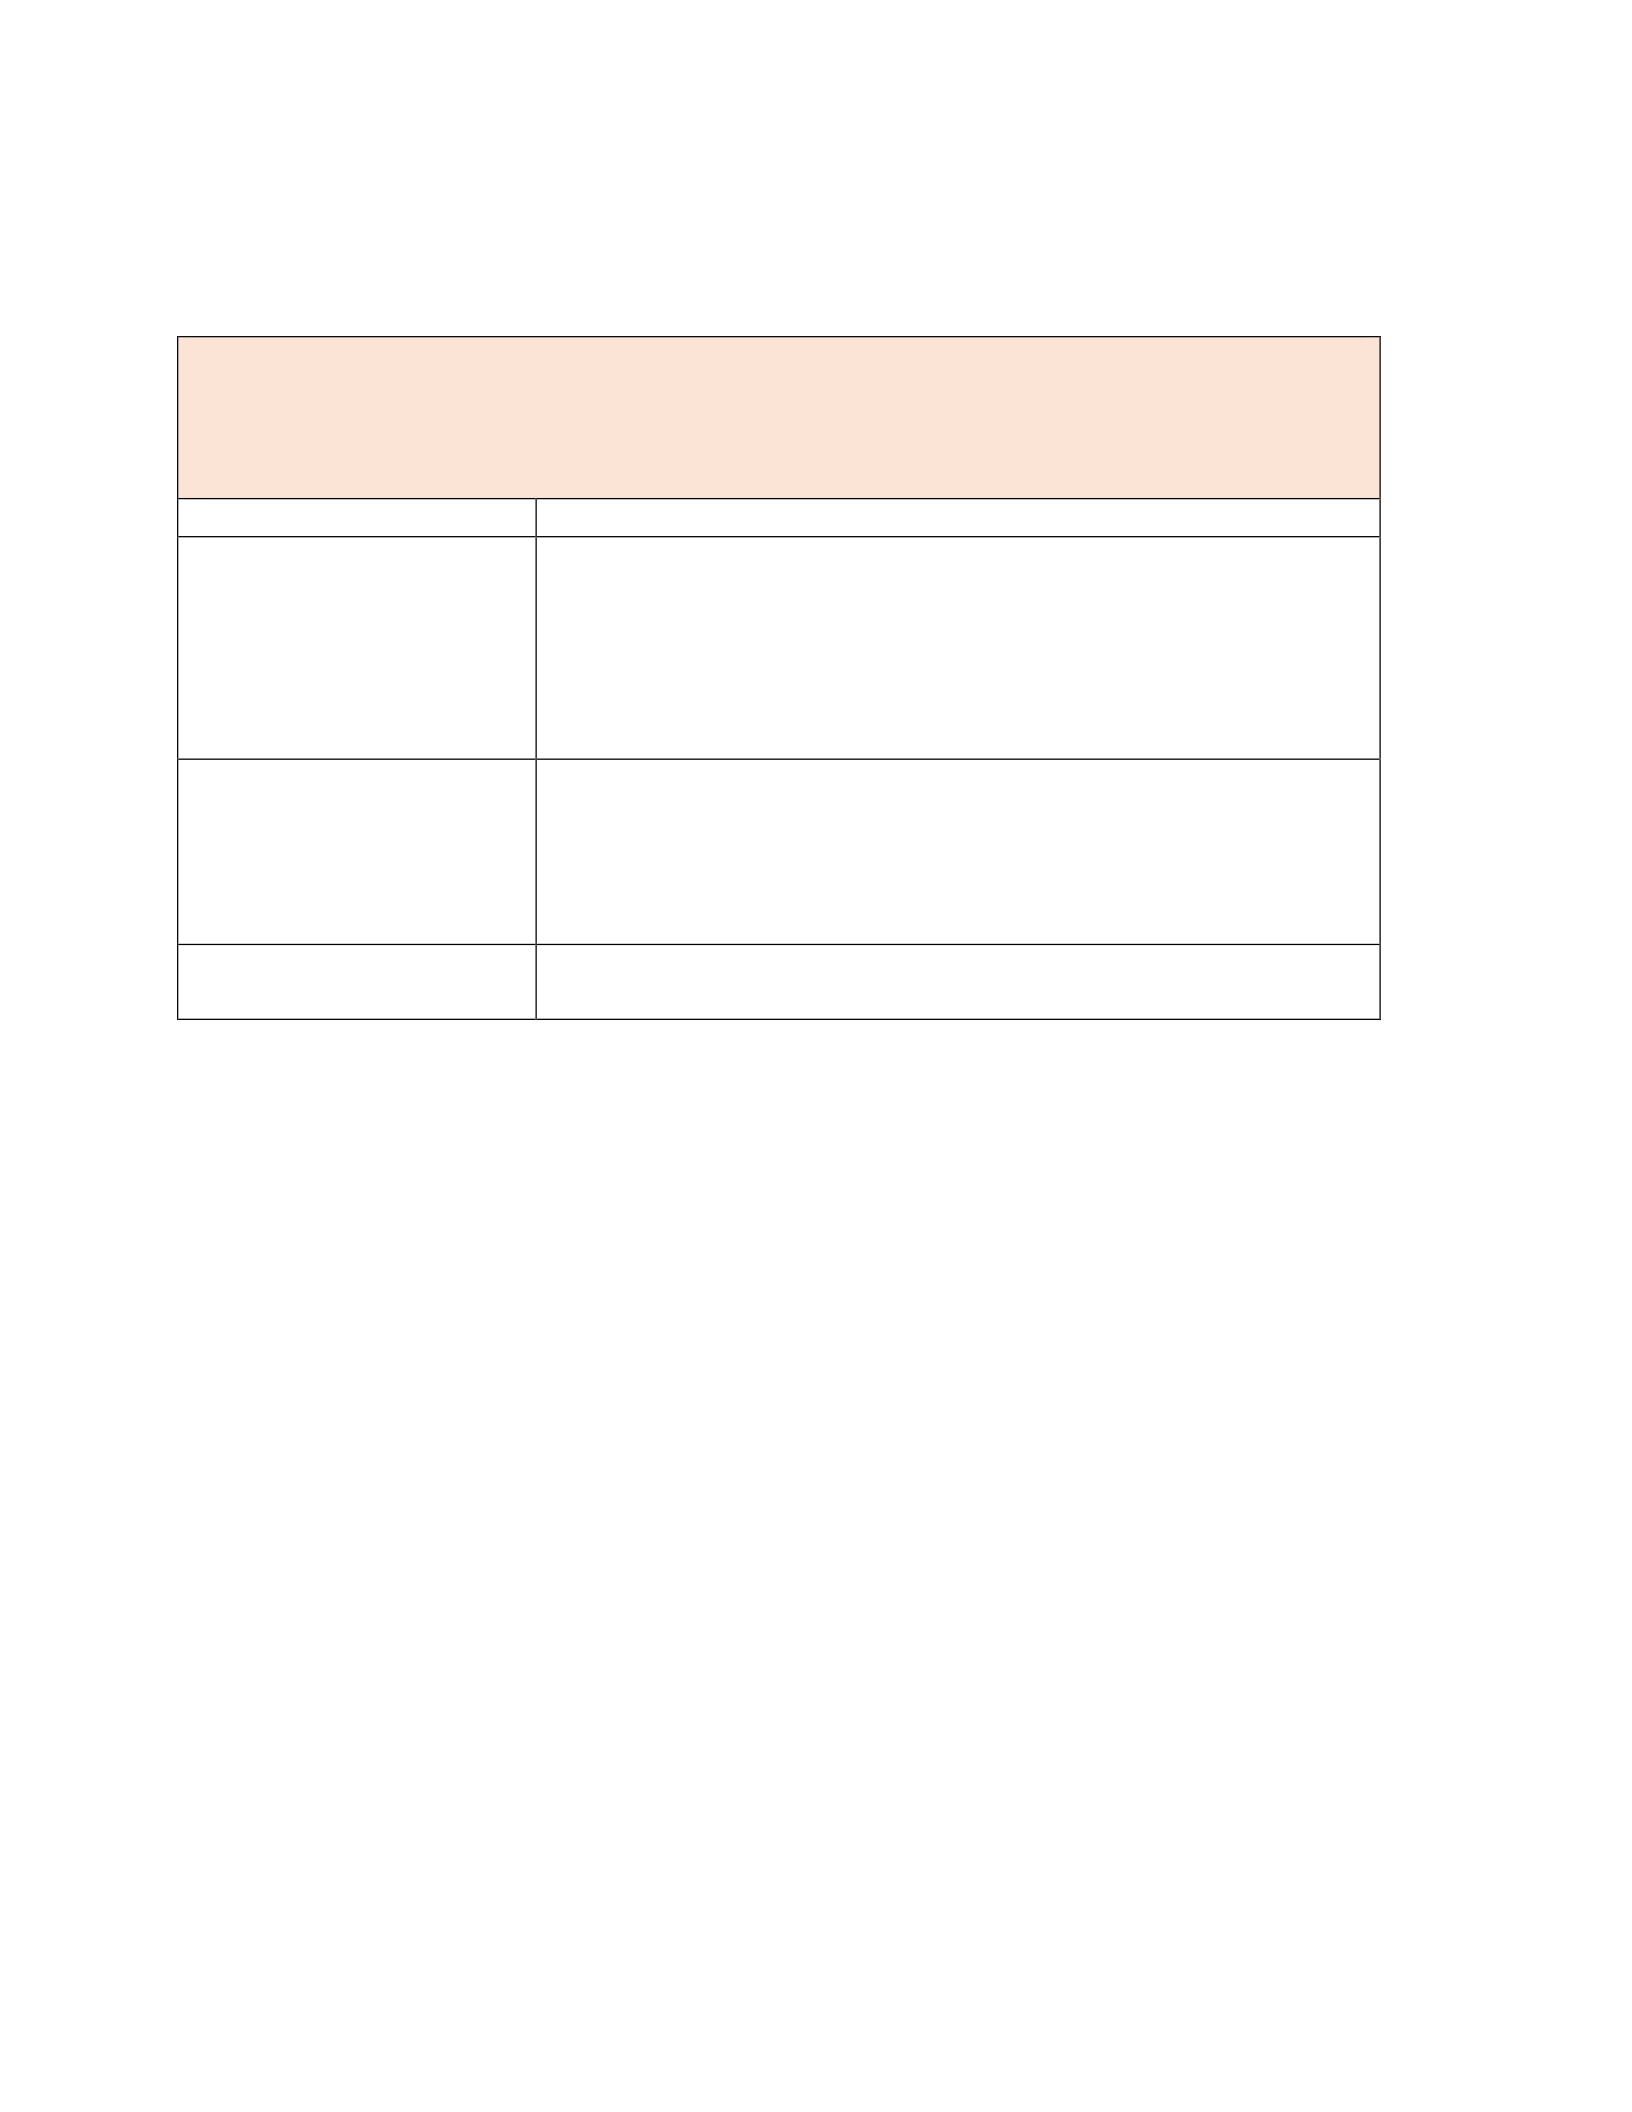
Table 1
ACME Team Members - Titles and Roles
Team Member Title
Role
Lead Cyber Security
Engineer
The role would include the development of secure network
solutions, performing network scans, conducting risk
assessments, and penetration testing. He would also manage
the firm’s security technology, implement the Security
Technical Implementation Guidelines (STIG) throughout the
entity.
Chief Information
Security Officer (CSO)
His primary responsibility is to safeguard Limetree’s data
and intellectual property. In addition to this, he has to
strategize and employ IT security strategies so that adequate
security could be given to the research and development
business from potential risks, threats, and cyberattacks.
Security Consultant
He would be responsible to design effective cybersecurity
strategies across the Limetree organization.
C. Hardware and Software:
Currently, Limetree Inc. has in place numerous hardware and software that make up
its Information Technology ecosystem. The firm has a medium-sized network which enables
it to carry out the online activities. The key components of Limetree’s network include 250
desktops, 7 remotely manageable Cisco switches, 5 file and printer servers, 3 email servers,
3 web or applications servers, 3 wireless access points, 3 firewall devices, 2 proxy servers,
and 1 gateway device to the internet (router).
The software or applications that are used in the research and development entity
include Google Chrome, Firefox, Internet Explorer, Microsoft Office, Adobe Flash, and
Adobe Acrobat. But there exists no standard browser that is used in the business
environment. These browsers even permit the remote installation of applets which impacts
the security posture of the business. The virus software that is employed in the business
undertaking is MacAfee. It is locally deployed on the computer systems of each and every
user. The antivirus needs to be updated every month mandatorily in all the systems of the
organization.
The Structured Query Language (SQL) Database is used in the IT setting of Limetree.
But the total disk space for the SQL database log that is available is quite small. In fact, it
is overwritten with new information whenever it gets full.
e
ISE 510 e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e
e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e 9
9
D. Tools:
For conducting a thorough security test in Limetree Inc., the ACME team would
require a number of tools and resources so that a critical risk assessment procedure could
be conducted which would help to get an insight into the security posture of the research
and development organization. Firstly, a team of experienced and qualified IT professionals
would be required so that they could assess the existing IT ecosystem of the firm. At
present, Limetree already has an efficient Security Manager Jack Sterling. The team
members would assist the firm’s Security Manager so that a holistic risk assessment could
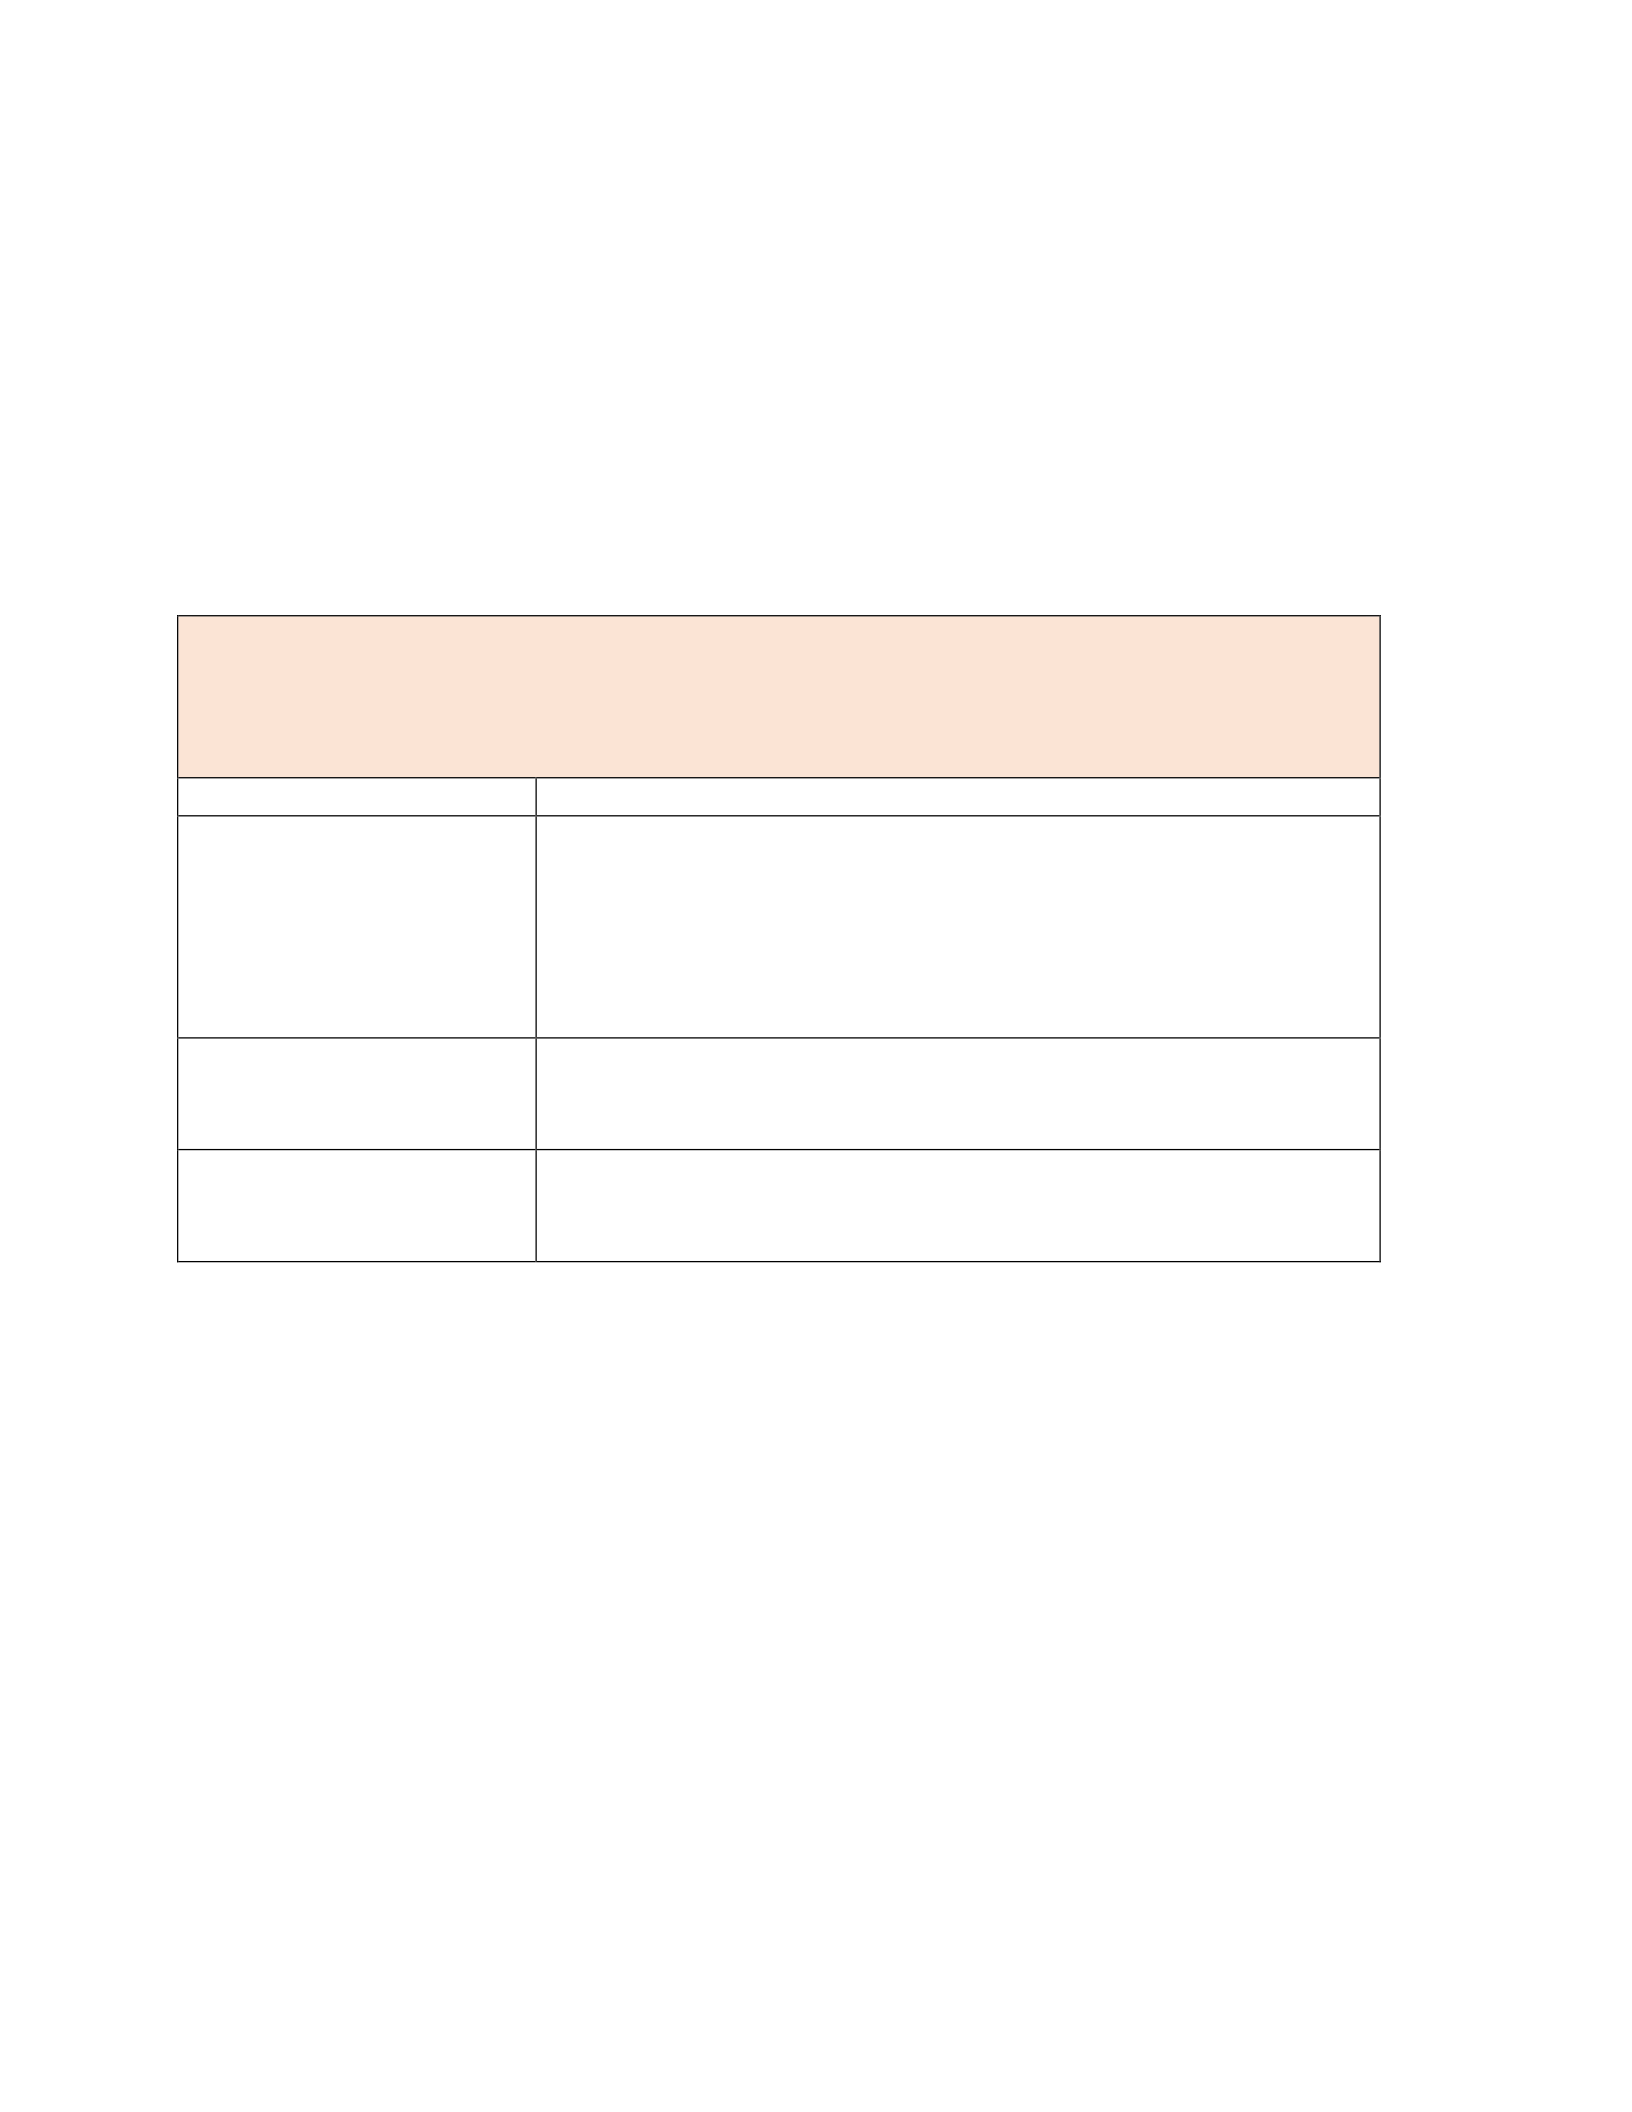
be carried out. The tools that the specialized team would need for conducting the risk
assessment have been highlighted in the table.
Table 2
ACME – Software Resources for Breach Analysis
Software
Description
Wireshark
The free and open-source packet analyzer would be used
for various purposes such as network troubleshooting,
software, and communication protocol development,
analysis, and education. The data traffic could be
effectively analyzed and abnormal behavior could be
identified.
Varonis
Varonis is a robust security software platform that would
help to track, visualize, evaluate and safeguard the
unstructured data of Limetree.
Suricata
Suricata is a fast open-source privacy breach detection
software that could perform intrusion detection on a real-
time basis.
VI. Risk Mitigation:
Risk mitigation is a vital strategy that would be necessary for Limetree Inc. so that it
could minimize the impact of threats and risks that could arise in its online setting. Suitable
security controls would be introduced which would ensure that similar breach incidents
would not reoccur in the future and compromise the security posture of the research and
development entity. Some of the core elements that have been captured in the section
relates to security controls, mitigation of vulnerabilities and evaluation of the effectiveness
of the controls (Rouse & Sullivan, 2019).
A. Security Controls at Limetree Inc:
1. Access control (for transmission medium) – Limetree must control the physical
access to the telecommunication medium by enclosing them in the rigid conduit that
is sealed with tamper-resistant epoxy and locking pull and drop boxes.
Risk – If a malicious actor were to get physical access to network cabling, they
could acquire unauthorized access and Limetree would never know without a
physical inspection or audit.

ISE 510 e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e
e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e 10
10
Impact – The most significant impact would be financial due to loss of contracts or
leaked proprietary information.
Likelihood – Low. Before implementing the recommended controls in this
document, there were many easier opportunities to exploit, and after Limetree
implements this control, a malicious actor would be detected due to the metal
conduit encasing the unencrypted cabling would obviously show the signs of
tampering.
2. Awareness and Training (Security Awareness Training) – Limetree must provide
necessary training to the employees so that they would be aware of the basic
security elements. While making changes to the firm’s information system model,
proper training would be vital to make sure the personnel are skilled to identify any
kind of abnormality in the firm’s network (Nvd - Control - At-2 - Security
Awareness Training, 2019).
Risk – In case any abnormal behavior would appear in the network, for example,
receipt of hundreds of spam emails, the employees could intimate the network
administrator about it so that appropriate actions could be taken. e
Impact – The main impact on the human factors as they would be empowered to
strengthen the security posture of the business organization.
Likelihood – High. This control would be of paramount importance that could
upgrade the overall effectiveness of the security model of the entity.
3. Incident Response Control (Incident Reporting) – A proper reporting protocol must
be in place in Limetree so that the employees would be able to use them in case
they come across a possible security breach incident (Nvd - Control - At-2 -
Security Awareness Training, 2019).
Risk – The employees of Limetree would know the exact steps that they can take at
the individual level to report any suspected security incident to the firm’s incident
response capability. One of the main risks includes the receipt of suspicious or
malicious communication mails on a frequent basis.
Impact – This security control would impact the entire IT system of Limetree Inc.
and help to address formal incident reporting requirements as well as specific
incident reporting requirements.
Likelihood – High. The likelihood of introducing the security control is High in
Limetree Inc. as it could be well prepared to deal with any unpredictable security
incident that could arise at any time.
4. Physical and Environmental Protection Control – Limetree must design proper
procedures to facilitate the implementation of functional physical and environmental
protection rules so that the documents could be properly disposed of and
unauthorized personnel would not gain access into the office premises (Nvd -
Control - At-2 - Security Awareness Training, 2019).
Risk – No outsider or guests would be able to loiter inside the office premises. This
security control would help to ensure that such unprofessional behavior is controlled
and the official documents are safe from inaccessible to outsiders.

ISE 510 e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e
e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e 11
11
Impact – The control would have a direct impact on the human resources as they
would have to entertain outsiders such as clients and guests outside the office
premises.
Likelihood – Moderate. The likelihood of introducing the control is moderate but it
would play a key role to strengthen the security infrastructure of Limetree. e
5. Risk Assessment Control – Limetree must conduct a regular risk assessment of the
IT infrastructure so that it could get a detailed insight into the magnitude of harm
from any unauthorized users (Nvd - Control - At-2 - Security Awareness Training,
2019).
Risk – Any kind of threats or vulnerabilities that would exist in the IT setting of
the business undertaking could be identified. Thus, the scope of cyber hackers could
be restricted to a significant degree.
Impact – The impact of the security control would be technical in nature as the
assessment would inspect the IT infrastructure of the business entity.
Likelihood – High. The likelihood of the security control is high s it would enable
Limetree to conduct a thorough risk analysis to identify any kind of suspicious or
malicious activity within its organizational network.
6. Maintenance control – Limetree has to maintain the robust nature of the IT
security so that unauthorized actors would not get the chance to exploit the
vulnerabilities of the research and development entity (Nvd - Control - At-2 -
Security Awareness Training, 2019).
Risk – The regular upgradation of antivirus would enable the strengthening of the
IT infrastructure and thus it could safeguard itself from infiltration by online
hackers.
Impact – The impact would be financial in nature as Limetree Inc. would have to
make significant financial investments to upgrade, install and maintain the security
level of the IT system.
Likelihood – Moderate. The likelihood of implementing the maintenance control in
the organizational setting is moderate. This is because it could introduce more
important security measures in place to strengthen the IT security posture.
7. System and Information Integrity (Information System Monitoring) – Limetree
Inc. has to ensure that regular and timely Information System Monitoring is carried
out so that no abnormality could be ignored by the team (Nvd - Control - At-2 -
Security Awareness Training, 2019).
Risk – Any kind of attacks or potential attacks could be identified by introducing
the control relating to Information System Monitoring.
Impact – The impact of the security control would be technical as a thorough
monitoring process would be carried out in the technical environment of the
organization.
Likelihood – Moderate. The likelihood of conducting the Information System
Monitoring is moderate as Limetree would have to implement other vital security
controls to strengthen its security posture.
8. Personnel Security Control (Access Agreements) – Limetree must make sure to
introduce access agreements with certain employees so that the accessibility of the
confidential information could be strengthened (NVD - Family - Personnel Security,
2019). e

ISE 510 e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e
e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e 12
12
Risk – No unauthorized personnel would be able to gain entry into the location or
the IT folders where sensitive and confidential information has been stored. Prior
approval would be required from the respective managers for doing so.
Impact – The impact would be felt on the human factors as their accessibility in the
organizational setting would be restricted.
Likelihood – Moderate. There is a moderate likelihood of Limetree to introduce
access agreements so that the confidentiality of the data and information could be
strengthened (Force e & Initiative, 2013).
B. Vulnerabilities:
The security controls that have been designed for Limetree Inc. would play a critical
role to strengthen the overall effectiveness of the measures that could be introduced to
minimize the extent of the harm or threat. For instance, the introduction of physical and
environmental protection policy would ensure that a professional and secure work
environment can be established where the internal business information would not be leaked
to the outsiders. Similarly, access control for transmission medium would prevent
unauthorized access to telecommunications lines so that the risk due to electronic
eavesdropping can be reduced.
B. Evaluation:
A thorough assessment of the security controls is necessary to ensure they add value to
the quality of security of Limetree. A number of criteria must be introduced for measuring
the controls to make sure that they are properly implemented in the organizational setting.
Limetree Inc. organization must carefully review its telecommunication wiring diagrams,
and carry out tests to ensure that the telecommunications media is encased in rigid conduit
which is sealed with tamper-resistant epoxy and locking pull and drop boxes. Similarly, the
CTV cameras must be used to assess the office environment and ensure that no
unauthorized individuals have been given access to the office premises. Such evaluation
techniques would help to ensure that the security controls have been effectively
implemented throughout Limetree Inc.
VII. Conclusion
A number of recommendations have been made for Limetree Inc. relating to the
administrative aspects, technical features, organizational personnel, and physical
environment. The objective is to help the research and development entity so that it can
strengthen its security infrastructure.
A. Administrative Recommendations – All the administrative and regulatory policies
must be designed in a simple and understandable manner so that the organizational
personnel of Limetree Inc. would be able to get a detailed insight into the actions or
measures that could be taken by them at the individual level to improve the
effectiveness of the security model. The guidelines must be able to convey the
information relating to Limetree Inc.’s security model with both technical as well as
the non-technical audience. Frequent workshops could be conducted so that all the
administrative guidelines could be shared with the employees of Limetree in a
transparent manner.

ISE 510 e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e
e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e 13
13
B. Technical Recommendations – Limetree must deploy a robust Host Intrusion
Detection System (HIDS) so that it would be able to identify and block common
attacks that could arise in the online environment of the business undertaking. In the
current times, cyber attackers are using a broad range of sophisticated techniques to
gain unauthorized access into the networks of businesses (Intrusion Detection System
(IDS) - GeeksforGeeks, 2019). So, Limetree could strengthen the IT security
infrastructure and technical ability by introducing the IDS which would enable the
firm to monitor the online traffic that is present in its network. The Network
Administrator of the Research and Development entity would also be able to receive
alerts in case any suspicious or malicious activity has been detected in its network
or online infrastructure.
C. Personnel Recommendations – Technical training must be provided to the
organizational personnel of Limetree Inc. so that they would be well aware of the
latest security approaches and techniques. The organizational personnel are one of
the most vital parts of each and every business entity including Limetree Inc. They
are also known to be the weakest link when it comes to the security system of the
IT ecosystem of an organization. In the case of the Research and Development
undertaking, there is the need to ensure that the technical know-how and expertise of
the organizational personnel is constantly upgraded so that their basic awareness of
IT security can be improved. Such a step would be vital as it would empower the
employees to take necessary action in case any abnormal or suspicious behavior is
observed in the network of the organization.
D. Physical Recommendations – Strict guidelines and rules need to be introduced in
Limetree Inc. relating to the work setting and the physical environment of the
organization. The management must ensure that outsiders, guests or unauthorized
individuals are not given access to enter the official premises where the employees
carry out the day to day official work. Such a step would be extremely vital to
ensure that they would not gain an access to confidential business information. The
physical environment in which the employees of Limetree operate must be
thoroughly secured. The security personnel must ensure that the official premises
cannot be accessed by anyone other than the current employees of the organization.
Such a security measure would play a critical role to safeguard the confidential and
sensitive business information of Limetree Inc.
ISE 510 e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e
e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e e 14
14
References
Blair, M. A. (2015). Computer Security Incident Response Plan. Retrieved October 12,
2019, from
https://www.cmu.edu/iso/governance/procedures/docs/incidentresponseplan1.0.pdf.
CRR Supplemental Resource Guide. (2019). Retrieved October 12, 2019, from
https://www.us-
cert.gov/sites/default/files/c3vp/crr_resources_guides/CRR_Resource_Guide-IM.pdf.
Force, J. T., & Initiative, T. (2013). Security and privacy controls for federal information
systems and organizations. NIST Special Publication, 800(53), 8-13.
Intrusion Detection System (IDS) - GeeksforGeeks. (2019). GeeksforGeeks. Retrieved 12
October 2019, from https://www.geeksforgeeks.org/intrusion-detection-system-ids/
Nvd - Control - At-2 - Security Awareness Training . (2019). Nvd.nist.gov. Retrieved 12
October 2019, from https://nvd.nist.gov/800-53/Rev4/control/AT-2
NVD - Family - Personnel Security . (2019). Nvd.nist.gov. Retrieved 12 October 2019, from
https://nvd.nist.gov/800-53/Rev4/family/Personnel%20Security
Rouse, M., & Biscobing, J. (2019). What is HIPAA (Health Insurance Portability and
Accountability Act) ? - Definition from WhatIs.com. Retrieved October 12, 2019,
from https://searchhealthit.techtarget.com/definition/HIPAA.
Rouse, M., & Sullivan, E. (2019). What is risk mitigation? - Definition from WhatIs.com.
Retrieved October 12, 2019, from
https://searchdisasterrecovery.techtarget.com/definition/risk-mitigation.
What is the HITECH ACT?: What HITECH Compliance Means. (2019, September 16).
Retrieved October 12, 2019, from https://compliancy-group.com/what-is-the-hitech-act/

