


RISKASSESSMENT: PART 3 1
Risk Assessment: Part 3
Elliott J. Clemente
The Helms School of Government, Liberty University
HLSC720
Author Note
I have no known conflict of interest to disclose.
Correspondence concerning this article should be addressed to
Email:
RISK ASSESSMENT: PART 3 2
Abstract
Critical infrastructure plays a critical role in the life of every American life. The country’s day-
to-day function relies on having access to such things as electricity or portable drinking water on
demand. The ability of the United States to protect itself from domestic or foreign adversaries
makes the protection of the country’s infrastructure critical project power both here and abroad.
For over four decades, Presidents of both parties have understood the importance of the
interdependence system that compose the critical arrangement. Critical infrastructure
encompasses many aspects of life in the United States, which includes transportation hubs or
centers like airports. The popularity of airports has also increased its vulnerability. It must be
under constant security assessment, which includes conducting studies to improve the balance of
security and access for the public. The study investigates the connection between security,
access, and critical infrastructure protection (CI). This study used cross-sectional analysis to
analyze the complex interconnection and intended system measured from 2000-2022 against
similar research conducted during the same period. Further studies are required to establish a
causal relationship and develop countermeasures.
Keywords: Critical infrastructure, Key resources, Presidential Directives, Homeland Security, risk
assessment.
RISK ASSESSMENT: PART 3 3
What is risk assessment, vulnerability analysis, and critical Infrastructure?
Risk assessment
Risk Assessment is a careful examination to ascertain the probability of an attack
occurring and causing harm to critical infrastructure, key resources, or key assets (Bennett,
2018). The assessment justifies security resources to prevent or limit an adversarial event against
a facility. A crucial part of the risk assessment is the extensive review of the security scheme
employed by a facility that highlights any vulnerabilities that an adversary can manipulate to
produce destruction. The goal of understanding risk is understanding, or lack of understanding
with the fundamental focus being clarity. In both aspects, the common denominator and
indecision are the vital components of risk.
Assessment of risk should be conducted based on three different impact criteria: human,
economic, and political /social consequences; quantitative for the first two categories, such as
number of deaths/injuries cost, and with a qualitative scale for the third (Theocharidou &
Giannopoulos, 2015). The universal illustration for security risk is Risk=Consequence x
Vulnerability x Threat. Where consequence is specified as the maximum credible loss,
vulnerability is characterized by the expression of overall vulnerability in the equation, and the
threat is the annual rate of hazard occurrence for the asset (Zio, 2016). Risk assessments are
implemented in all sectors regardless of their funding sources. As the coordinator of the security
programs, the public sector mandates the private sector as the holder of 80% of the critical
infrastructure in the United States to stay updated with the current security protocols.
vulnerability analysis
Vulnerabilities analysis is the analysis of the security state of a system based on system
information collected on demand (Bace & Sinchak, 2014). Vulnerability analysis draws its
RISK ASSESSMENT: PART 3 4
foundation in the continuum of possibility. Potential vulnerabilities are quantified based on asset and
threat analysis, and existing security countermeasures are tested for effectiveness (Bennett, 2018). The concept
of vulnerability analysis as a systemic application has allowed security analysts and emergency managers to
focus on all vulnerabilities of their facilities’ physical and virtual aspects that may provide an exploitable point.
The theme of vulnerability analysis is to devise a classification or set of classifications that enable the analyst
to abstract the information desired from a set of vulnerabilities (Bishop, 1999). In recent decades, the number
of threats directed at America’s critical infrastructure system has increased exponentially, mandating the nation
to understand the Modis Operandi of their adversaries, thus better protecting their vital assets.
Critical Infrastructure
The current global environment has spotlighted protecting the designated structures and
facilities critical to the public and private sectors. Successive Presidents of the United have
prioritized the nation’s interconnected system as vital or critical to national security.
Prioritization is evident in the legislation and executive orders signed into the law. A critical
infrastructure component is a collection of indispensable assets necessary to maintain our
standard of living. An asset of a critical infrastructure component is something of high
importance or high value or an information system (Bennett, 2018).
Historically, the protection of infrastructure can trace its roots back to the Second World
War when allies strategized attacking adversaries’ infrastructure systems to weaken their ability
to continue to support and supply the war effort. The methodology of attacking a nation’s critical
infrastructure continued into the Cold War era. The world’s remaining superpowers have
understood the destruction or damage of the country’s vital electrical, financial, and health
systems.
The securitization of critical infrastructure is pre-eminently about the protection of
objects. Critical Infrastructure protection is generally held to have emerged as a security issue in
the mid-1990s (Aradau, 2010). In 1996, the then President Clinton used the for the first-time
RISK ASSESSMENT: PART 3 5
used to refer a system of interdependent systems and its importance to the American way of life.
Modern society relies upon the functionality of such virtual infrastructures as the Internet. These
virtual network infrastructures are playing an ever-increasing role in the primary function of the
global community. The ability to participate in the global community depends on a country’s
infrastructure system or the lack of such a system. Underdeveloped countries are lagging.
However, this seeming deficit has allowed.
Each interdependent system(s) somehow affects the lives of everyday Americans in some
way. Any disruption of any systems considered critical can cause cascading events that may end
in the total denial of use and place the entire infrastructure system in peril. The more the
American society becomes more advanced and complex, the more it relies on critical
infrastructure to support the American lifestyle and existence (Taylor & Swanson, 2019). The
terrorist attacks of September 11, 2001, brought to focus the vulnerabilities of the system and the
need to harden them from terrorist attacks and natural disasters.
Portfolio-level VS. Asset-level Analysis
The general purpose of the analysis is to identify the various threats posed by an
adversary that could adversely impact a critical asset (Bennetts, 2018). Two particular risk
assessments primarily focused on the portfolio and asset levels. Portfolio level assessment is an
analysis conducted to identify the various known threats and focus on vulnerabilities to a
structure and the ability to apply security countermeasures and improve resilience. All portfolios,
whether defined by a particular function or composed of otherwise unrelated elements, are
defined by their assets. Asset-level analysis provides the basic information needed to assess risk
at higher levels of abstraction (Ayyub et al., 2007). Both assessments are similar in that they
measure a loss at some level but have disenable differences. Both assessments also view risk and
RISK ASSESSMENT: PART 3 6
threat reduction as their primary goal. View Asset-level assessment involves an estimated loss
concerning the asset(s). Portfolio-level assessment deals directly with the losses involving
several aspects of analysis, including physical, geographic, cyber, and logical interdependencies.
Interdependencies can be internal to the portfolio or arise from external interactions between
portfolio assets in the external world (Ayyub et al., 2007).
FEMA's community perspective on mitigation
For decades, the Federal Emergency Management Agency (FEMA) has promoted the
benefits of community participation in mitigating and preparedness of their states, cities, towns,
and tribal areas. The better citizens understand the National Preparedness Framework, the greater
the cooperation they will have with the public and private sectors. The cooperation also allows
for a quicker response to natural disasters and man-made events. Quicker response is also cost-
effective to mitigate damage and recover from events. Resilience depends on the whole
community, individuals and communities, the private and nonprofit sectors, faith-based
organizations, and all levels of government. Inclusiveness and partnership throughout these
levels can ensure the best use of available knowledge, resources, and efforts (FEMA, 2016).
Communities have proven to be an indispensable part of information and knowledge of
the local landscape, showing that well-organized groups promote collective action. They often
promote and mitigate actions without an official governmental title or authority.
Communities advancing mitigation can include social and community service groups and
institutions, neighborhood partnerships, communities representing and including those with
disabilities and others with access and functional needs, online communities, hazard-specific
coalitions, and communities of practice (FEMA, 2016).
What is the role of government and the Private sector in conducting risk assessments?
RISK ASSESSMENT: PART 3 7
Risk assessments are significant in protecting a facility and its personnel while ensuring
its optimal operational function. The assessment provides a security analyst or emergency
manager with a significant starting point to review vital aspects of the organization. The public
and private sectors often collaborate to harden the critical infrastructure and protect the United
States’ national security.
The public sector is responsible for conducting and identifying threats to the nation’s
critical infrastructure and national security. The federal government devised a plan to combat the
growing specter of threats from domestic and foreign adversaries. It established the
Cybersecurity Infrastructure Security Agency (CISA) to coordinate sector-specific agency efforts
to protect themselves from virtual and physical threats.
The best practices used for critical infrastructure identification.
The concept of identifying is a challenging endeavor. The evaluation methodology used
to value the critical infrastructure may differ from country to country and organization to
organization. Identifying critical is various national and international laws that regulate and
mandate process. The European Union (EU) countries must identify areas considered as critical
infrastructure. Within national Critical Areas/Sectors, framework, record and evaluate their
systems or component record and evaluate interdependencies between the identified CIs
(Petrakos & Kotzanikolaou, 2019). The counties within the coalition are mandated by treaty to
develop and update an Operator Security Plan and An Emergency action plan to protect their
national CIs.
The United States Homeland Security Presidential Directive-7 (HSPD-7) was signed into
law on December 17, 2003, by George W. Bush as the Critical Infrastructure Identification and
Prioritization and Protection. This directive requires that the Department of Homeland Security
RISK ASSESSMENT: PART 3 8
and other federal agencies collaborate with appropriate private sector entities in sharing
information and protecting critical infrastructure (Bennett, 2018).
Analyze tools and techniques used to identify critical infrastructure.
The federal government has developed specialized assessment tools and techniques to
identify critical infrastructure. The Cybersecurity and Infrastructure Security Agency (CISA) is
responsible at the federal level for conducting various security and resilient assessments on the
nation’s critical infrastructure (CI). These assessments are not mandatory. However, they are
recommended to assist their partners at all levels of government (federal, state, local, tribal, and
territorial) and the private sector to better understand the risk management paradigm. A joint
assessment includes infrastructure vulnerabilities, interdependencies, capability gaps, and the
consequences of disruption. CI operators use a Geographical Information System (GIS) to
manage and visualize spatial data. Geographical Information Science (GIScience) is the research
field that studies methods, techniques, concepts, theories, and questions related to using GIS
(Arvidsson et al., 2021).
Geographical Information Systems Data and Mapping
Geographical information systems (GIS) are designed to store, retrieve, manipulate,
analyze, and map geographical data. The primary feature of the program is its ability to use the
geographical of an object(s) and its corresponding data about other objects. The applicant allows
for commonly utilized bilateral global coordinating systems (Church, 2002). Because
information is stored, retrieving one system in conjunction with another is often seamless,
allowing newly entered data to be combined and warehoused for referencing. The expansion and
utilization of the
RISK ASSESSMENT: PART 3 9
Global Positioning System (GIS) has enhanced the collection ability to capture attributes
regarding
location at a relatively low cost to the customer.
GIS is a commonly used software application within public and private sector agencies. It
has become popular among agencies that utilize large amounts of geographical data and must
work within budgetary constraints. The federal government is the largest consumer of the
software program. Agencies like the US Forest Service, Bureau of the Census, transportation
services, and various contractors all utilize the program.
National Preparedness and Homeland Security Directives Affect Critical
Infrastructure Assessments
Preparedness is the shared responsibility of our entire nation. The whole community
contributes, beginning with individuals and communities, the private and nonprofits sectors,
faith-based organizations, and all governments (Department Homeland Security, 2015). Through
the core capabilities the United States can achieve what is understand what is required to reach
the national goal of protecting the nation’s infrastructure.
The core capabilities serve as both preparedness tools and a means of structured
implementation. All manner of incidents across the whole community have proven the
usefulness of the core capabilities and the coordinating structures that sustain and deliver them
(Department Homeland Security, 2015). The concerns brought forth by the modern infrastructure
and the vulnerabilities presented by such attacks forced planners to look at infrastructures, not
just physical structures, as key systems that require protection. The USA PATRIOT Act defines
critical infrastructure as systems and assets, whether physical or virtual, so vital to the United
RISK ASSESSMENT: PART 3 10
States that the incapacity or destruction of such systems and assets would have a debilitating
impact on security (Humphreys, 2019).
National Infrastructure Protection Plane (NIPP)
The federal government of the United States devised a plan in which it will be able to
protect the critical infrastructure system that is so vital to the everyday life of the average
citizen and the national security of the nation. The National Infrastructure Protection Plan aims
to build a safer, more secure, and more resilient America by preventing, deterring, neutralizing,
or mitigating the effects of deliberate efforts by terrorists (Murray & Grubesic, 2011). The
legislation’s primary focus is to prevent the destruction, incapacitation, and exploitation of the
nation’s Critical Infrastructure Key Resources (CIKR).
Recently, in the United States, a petroleum supplier was hacked and held hostage
(RANSOMWARE) in exchange for monetary compensation, disrupting fuel distribution
throughout the eastern seaboard and spotlighting the importance of protecting such
infrastructure. Because critical infrastructure networks are vital yet so vulnerable to damage and
disruption, it is recognized that a system can benefit from the strategic protection/fortification of
network elements (Murray & Grubesic, 2011).
Under the National Infrastructure Protection Plan, the federal government established
specific components within the protection plan to minimize the probable offensive action by
adversaries in a coordinated strike against a target(s) because it is almost impossible to protect
every aspect of a facility or network it imperative that security analysts or emergency managers
prioritize assets that require the highest level of security and allocate resources according to the
prioritization.
RISK ASSESSMENT: PART 3 11
The National Infrastructure Protection Plan outlines many of the roles and responsibilities
of all levels of government (federal, state, local, and tribal) involved in the protection plan’s risk
management aspect. As the program coordinator, the federal government also serves as a
regulatory monitor for the compliance of all aspects of the program. The US government has
generally pursued a hands-off approach to regulating critical infrastructure systems. Approxi-
85% of the CIKR in the United States is privately held (Murray & Grubesic, 2011).
Homeland Security Act of 2002
As a result of the 9/11 attacks, President George W. Bush passed the Homeland Act of
2002, which created the Department of Homeland Security (DHS) and placed the protection of
the nation’s infrastructure under its preview. The Homeland Security Act 2002 and other
administrative documents have assigned the Department of Homeland Security specific duties
associated with coordinating the nation’s efforts to protect its critical infrastructure (Moteff,
2005).
As is often done in the federal government, the responsibility of leading the nation’s effort to
protect its critical infrastructure was \assigned to the Information Analysis and vulnerability
infrastructure Protection Directorate (IA/IP). In particular, the IA/IP Directorate integrates threat
assessments to identify and manage the risk of possible terrorist attacks on the
Presidential Policy Directive 7
President George W. Bush signed Homeland Security Presidential Directive-7 into
legislation on December 17, 2003. The directive identifies the cabinet-level agency responsible
for identifying, prioritizing, and protecting critical infrastructure. HSPD-7 was established as a
preventive measure to keep terrorists from using the nation’s critical infrastructure against itself.
The directive directly references the 9/11 skyjackers using commercial aircraft as guide missiles
RISK ASSESSMENT: PART 3 12
to target domestic infrastructures.
Homeland Security Presidential Directive-7 mandates the cooperation between the public
and private sectors to establish synergy between the two sectors. Homeland Security Presidential
Directive-7 supersedes Homeland Security Presidential Directive-63. Homeland Security
Presidential Directive-7 expands coverage of additional critical infrastructure and key resources
(CI/KR).
HSPD-7 adopts, by reference, the definitions of “critical infrastructure” and ‘key
resources” in the Homeland Security Act. It adopted the critical infrastructure and key asset in
the National Strategy for the Physical Protection of Critical Infrastructure and Key Assets
(Moteff & Parfomak, 2004).
Presidential Policy Directive 21
On October 21, 2013, the Obama administration replaced HSPD-7 with Homeland
Security Presidential Directive-21. This directive updated the nation’s security envelope and
realigned and expanded critical infrastructure sectors from seven to sixteen. The realignment and
expansion provided a clear line of responsibility throughout the federal government. It also
included a national guide and a national plan with areas of responsibility according to the
expertise and capabilities involved, including subject-specific agencies (SSA), state, local, tribal,
and territorial (SLTT) entities, and critical infrastructure owners and operators.
HSPD-21 provides for integrating the physical and virtual infrastructure systems to
exchange information between the public and private sectors seamlessly. The goal is to enable
efficient information exchange by identifying requirements for data and information formats and
accessibility, system interoperability, redundant systems, and alternate capabilities should there
be a disruption in the primary systems (Bennett, 2018). All information-sharing functionalities
RISK ASSESSMENT: PART 3 13
conducted by the federal government must balance privacy and security. This balance must be
within applicable laws, policies, and procedures.
Stafford Act
As the world deals with global warming and the associated side effects of increased
weather-related events, the federal government has seen the number of individuals and
businesses, cities, and states applying for disaster relief. Recently, the number of multi-billion-
dollar disasters has shown the need for the federal government to intercede and aid as requested
by that state’s leadership (Governor). The Robert T. Stafford Disaster Relief and Emergency
Assistance Act, or the Stafford Act, has been the most critical legislation in this area.
The Robert T. Stafford Disaster Relief and Emergency Assistance Act was established to
provide local and state governments with continuity of operations during and after a natural and
man-made disaster. Its stated goal is to provide an orderly and continuing means of assistance by
the Federal Government to state and local governments in carrying out their responsibilities to
alleviate the suffering and damage that result from such disasters (Hunter, 2017). The sector-
specific agency (SSA) with overall responsibility for coordinating the program is the Federal
Emergency Management Agency (FEMA). FEMA may distribute tens and sometimes hundreds
of millions to states and individuals to recover from various disasters.
Governors must declare an emergency and apply with the federal government to begin
the application process. Due to the disaster’s severity, the application process may often occur
after the declared event(s). For the state government to receive Stafford Act assistance, the event
must qualify as defined by FEMA. The Stafford Act enables multiple forms of assistance to flow
to states, localities, and individual victims of catastrophic loss. It creates two primary categories
of events that qualify for such aid. Major and emergencies (Hunter, 2017). A major disaster is a
RISK ASSESSMENT: PART 3 14
naturally occurring incident in which the severity has reached the level that will overwhelm state
and local resources, or the President deems the affected state requires federal intervention. An
emergency is any event, determined by the President, that requires supplement resources and
assistance to save lives, protect property, and aid in the well-being of the public health system.
The
Robert T. Stafford Disaster Relief and Emergency Assistance Act remains one of the
government’s
most utilized disaster-related legislation. The law and its use will only increase in the future.
Principle of Protective Security and effective countermeasures.
The are five individual principles that are interconnected to provide and assist prioritizing
a facility’s defensive countermeasures. The principle of countermeasures are Protective Security,
Cyber Security, Personnel Security, and Information Security. The security plan of the operator
owning a critical infrastructure is one of the instruments for measuring, analyzing, and recording
the values of the factors that directly or indirectly contribute to the level of criticality of the
designated infrastructure (Roman, 2016).
Countermeasures as a system must be intended to prevent, mitigate, and deter any attacks
that affect the physical structure and its virtue network(s). This idea is consequential regarding
terrorism and terrorist networks. For many terrorist and terrorist groups, they have developed
specific characteristics that identify them in the same manner as fingerprints Malevolent actors
can adapt their strategies to the security measures taken; thus, their actions are complicated to
anticipate (Pettersen & Bjorskau, 2014).
Differentiate between a pure risk assessment model and a security vulnerability analysis.
Pure risk is a threat beyond human control with only one possible outcome: loss (Bennett,
RISK ASSESSMENT: PART 3 15
2018). An example of pure risk is evident in acts of God (natural disasters, fire, and deaths). For
clarification, pure risk is placed into three groups (personal risk, property pure risk, and Liability
pure risk). The title of the classification defines each category. The classifications provided
security analysts with a straightforward section into which to enter information.
Security Vulnerability Assessment (SVA) is the process of measuring and prioritizing
this risk associated with network and host-based systems and devices to allow rational planning
of
technologies and activities that manage business risk (Nath, 2011). Each assessment serves to
identify security issues that an adversary may exploit. However, they accomplish the goals in
different ways. Pure risk is often Acts of God that include natural disasters, fires, or death. These
occurrences are beyond human control. At the same time, Security Vulnerability Assessment
(SVA) allows decision-makers to identify and quantify security vulnerabilities within a facility.
Overall assessment of the area
The overall assessment of the critical infrastructure facility provides an overall situational
awareness of the area of responsibility (AOR) that includes the physical and the virtual
environment. Bradley International Airport’s overall security profile is satisfactory; however,
some areas require attention. A specific area of concern is the parking lot located directly in front
of the main passenger terminal. A terrorist attack involving a Vehicle Borne Improvised
Explosive Device (VBEID) will create a mass causality situation that will also incapacitate the
airport for further operations. The parking lot has been plagued with petty crimes for some time
now. Additional Surveillance cameras should be installed along with 24-hour armed security
with the parking garage. This controls access to and from the area reducing the probability of it
being used as platform a lone wolf attack.
RISK ASSESSMENT: PART 3 16
The area is vulnerable to exploitation by an adversary with unrestricted access to the
passenger pick and drop off areas directly in front of the terminal entrance. This area provides a
terrorist to enter the terminal prior to mandated security checks. Moving security process prior to
designated area outside the terminal. Transportation Security Administration officers (TSA)
would have an improved opportunity to intercept any threats outside.
Taxi stands should be located outside the immediate airport area. Waiting areas for both
share rides (uber& Lyft) and meter taxi should be required to be in an area designated as a
waiting car and drivers. Ft. Lauderdale/Hollywood International Airport is a designated area for
share rides, and metered taxi services away from the main terminal area. Commuter bus service
is also
directed to areas that are away from the main terminal area.
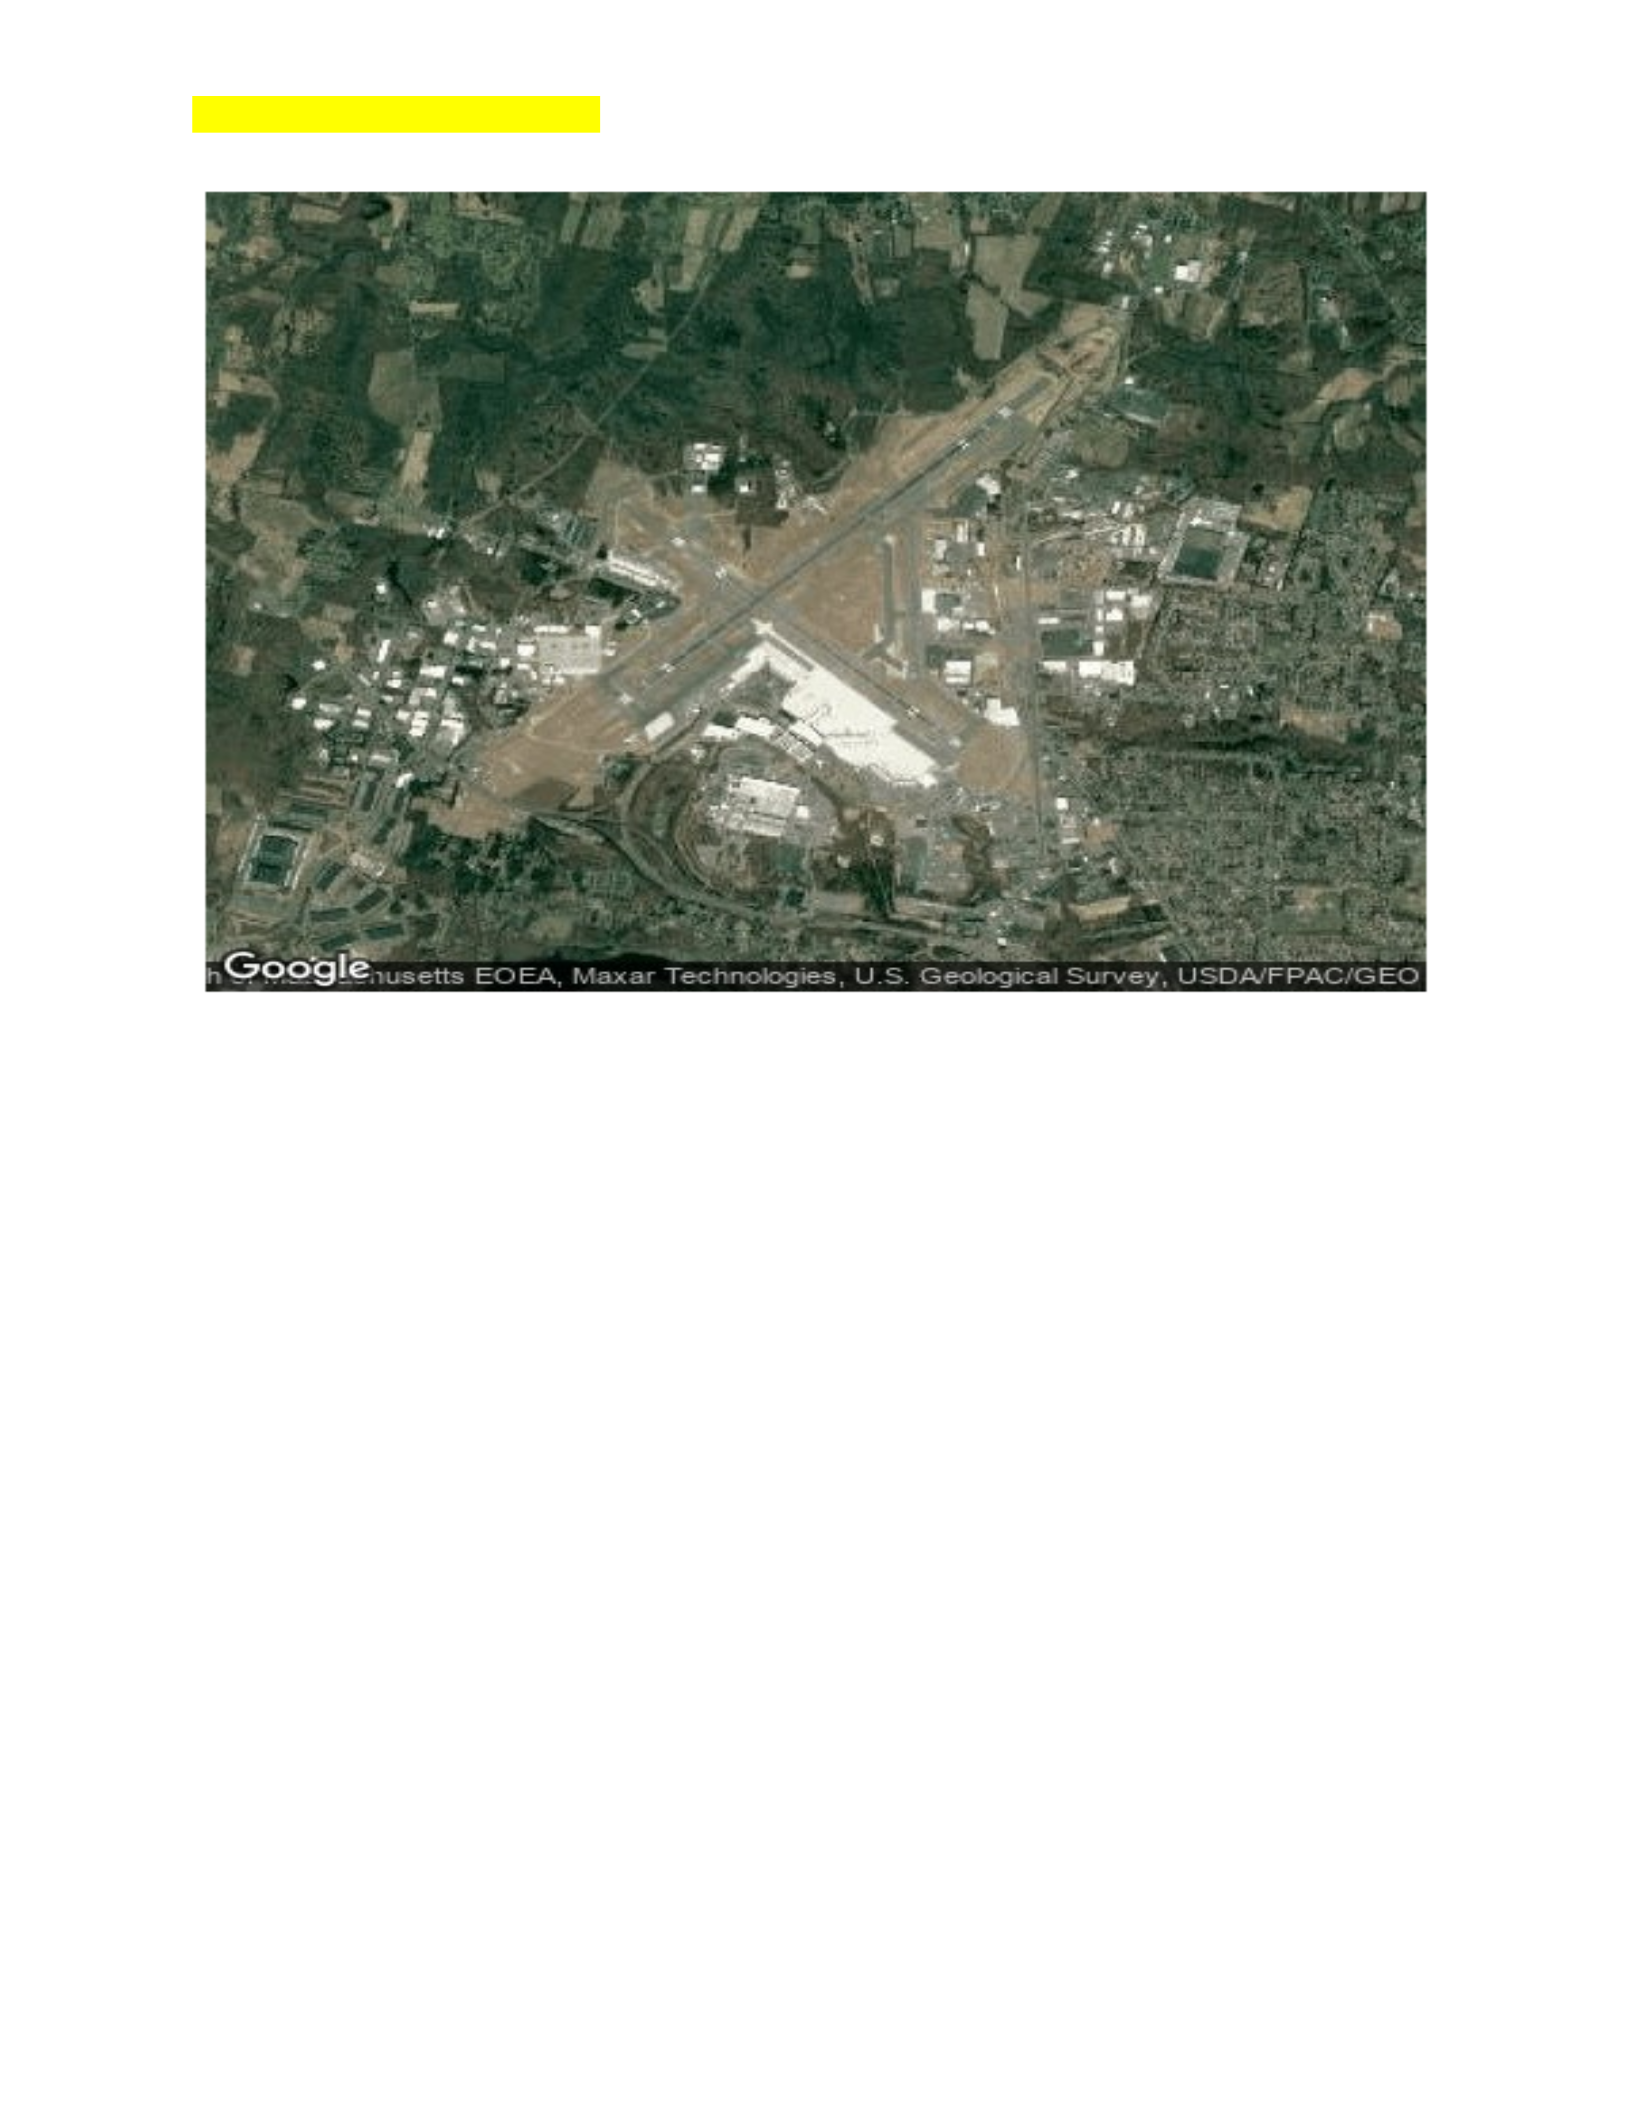
Bradley International Airport (BDL)
Bradley International Airport second busiest airport in New England in the Northeast
region second only to Boston’s Loggan Airport. It is estimated that some seven million travelers
utilize the airport annually. The Bradley Airport serves as a secondary airport for the three major
airfields in the area (John F. Kennedy International, LaGuardia, and Newark International).
Bradley international airport service the lower New England region.
The airport borders the Town of Winsor Locks to the West, and East Granby to its East.
The City of Hartford, CT is located 15 minutes South of the airport down Interstate 91. The
Connecticut River is also located to the East of the airport. The Connecticut River separates the
Town of Windsor Locks and the airport from the other towns like Enfield, and Suffield. The
cities of Springfield and West Springfield, MA is also served by Bradley International airport.
RISK ASSESSMENT: PART 3 17
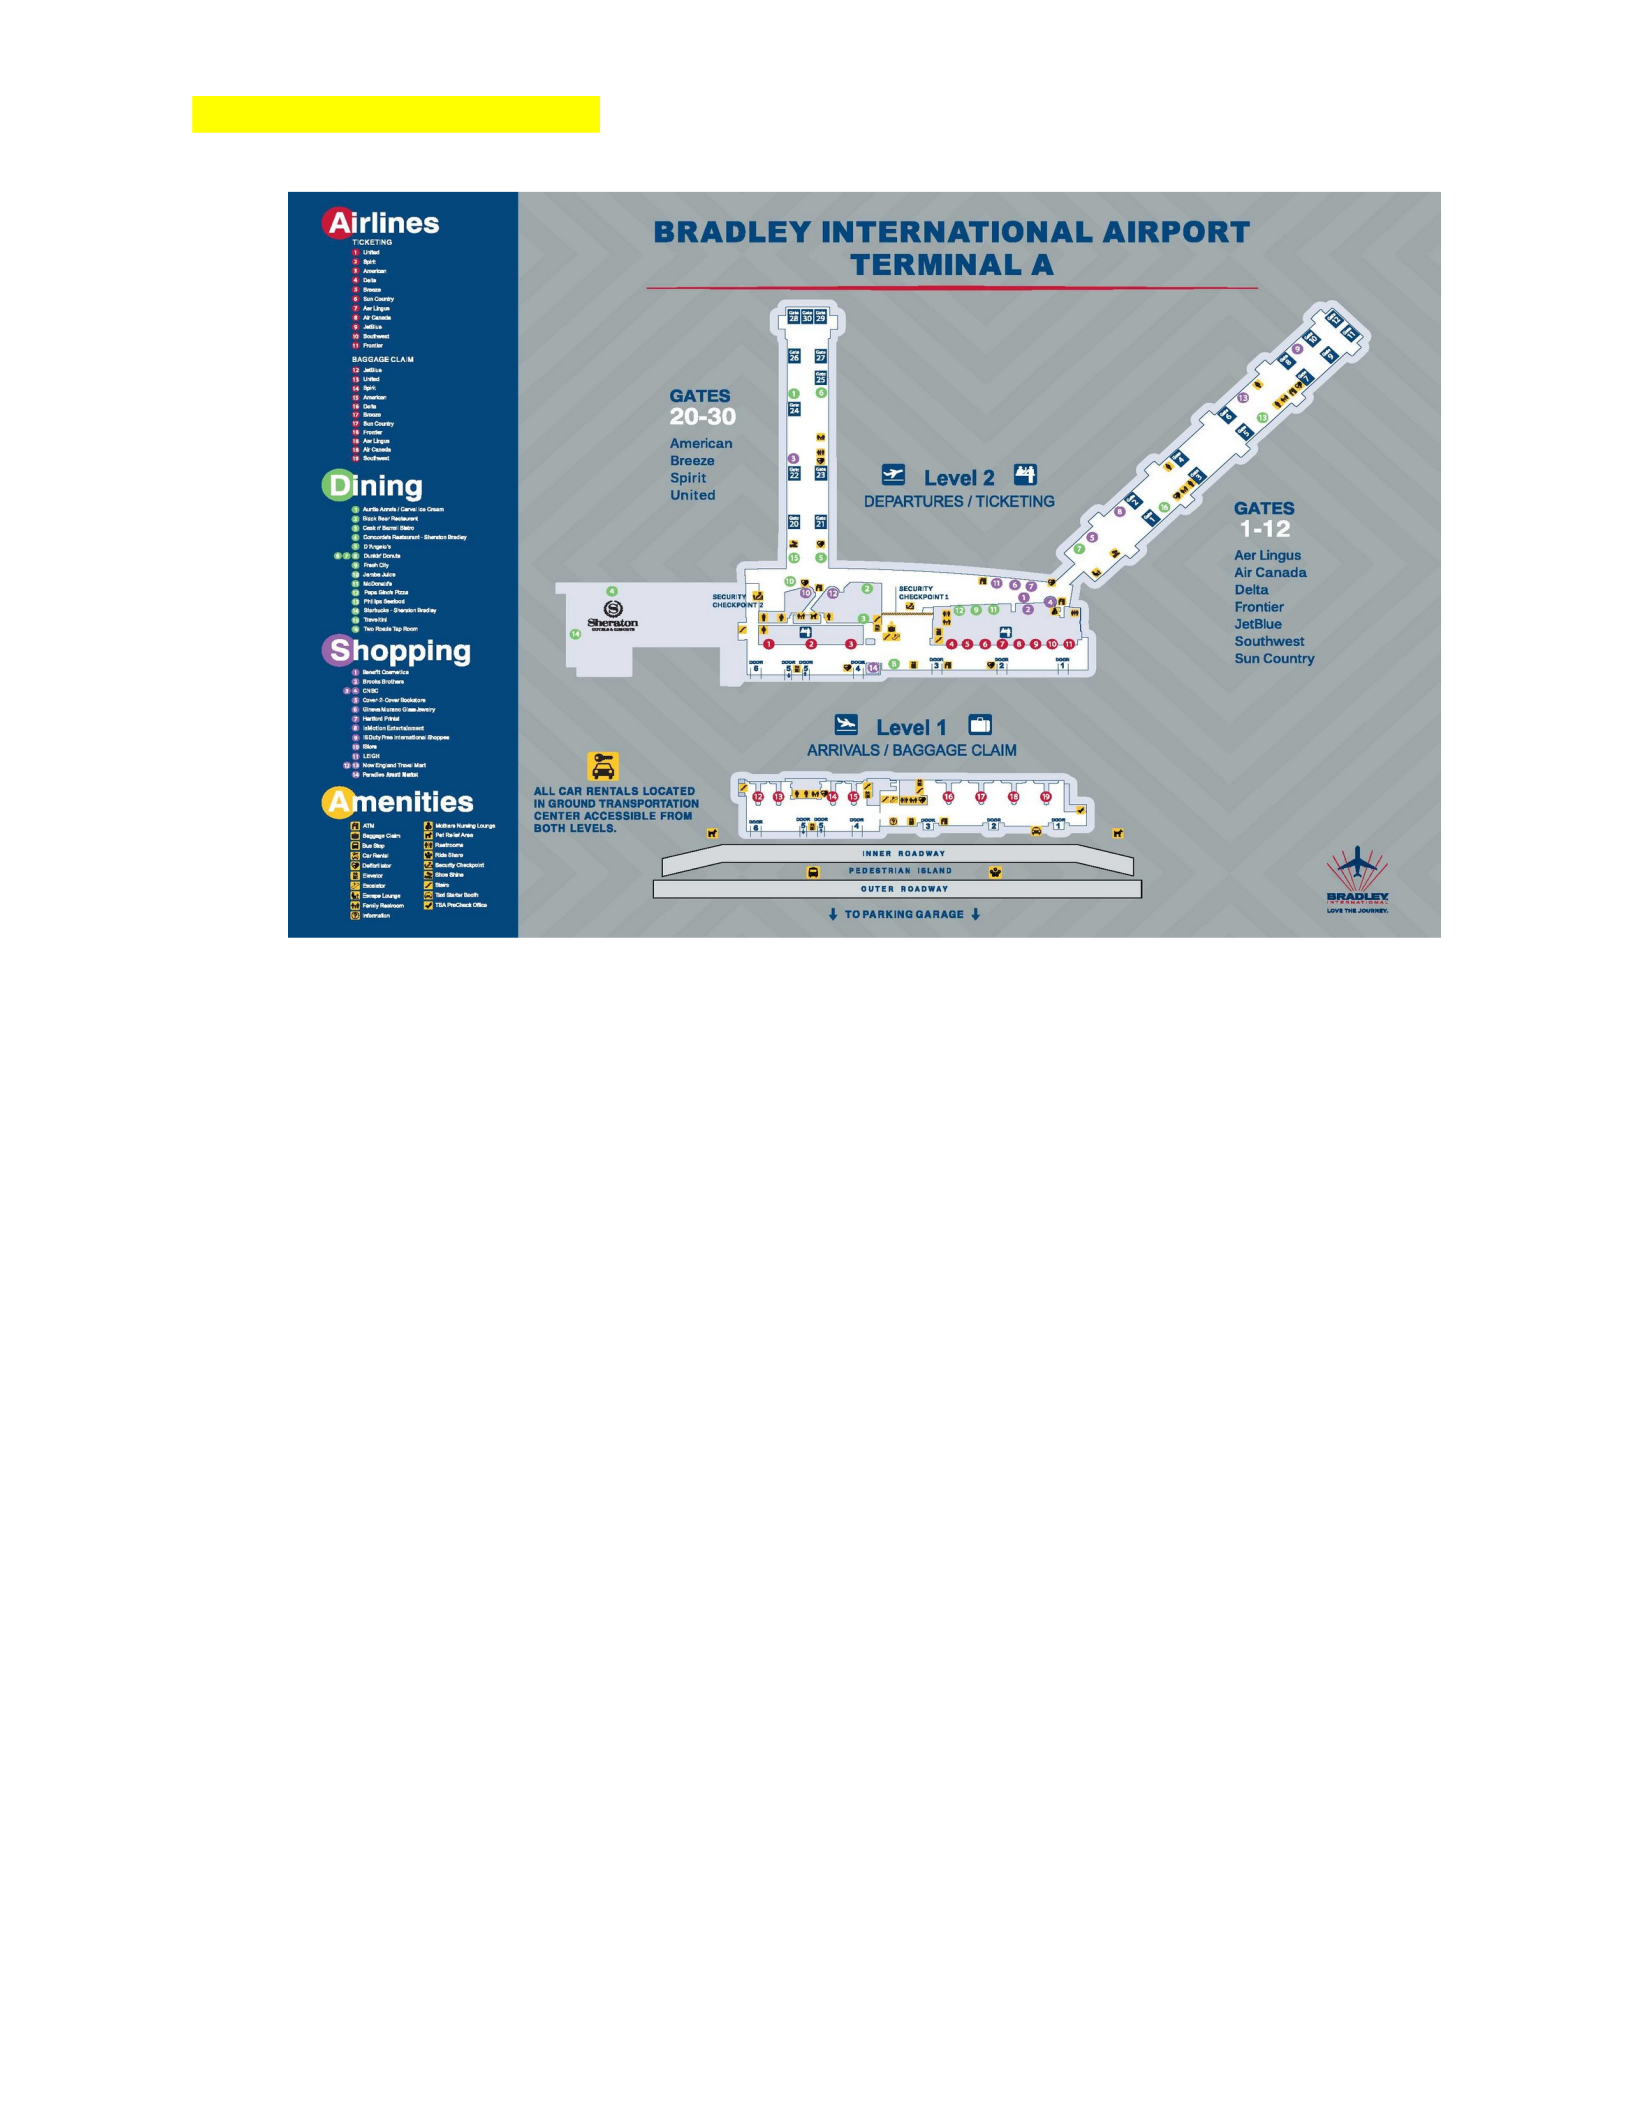
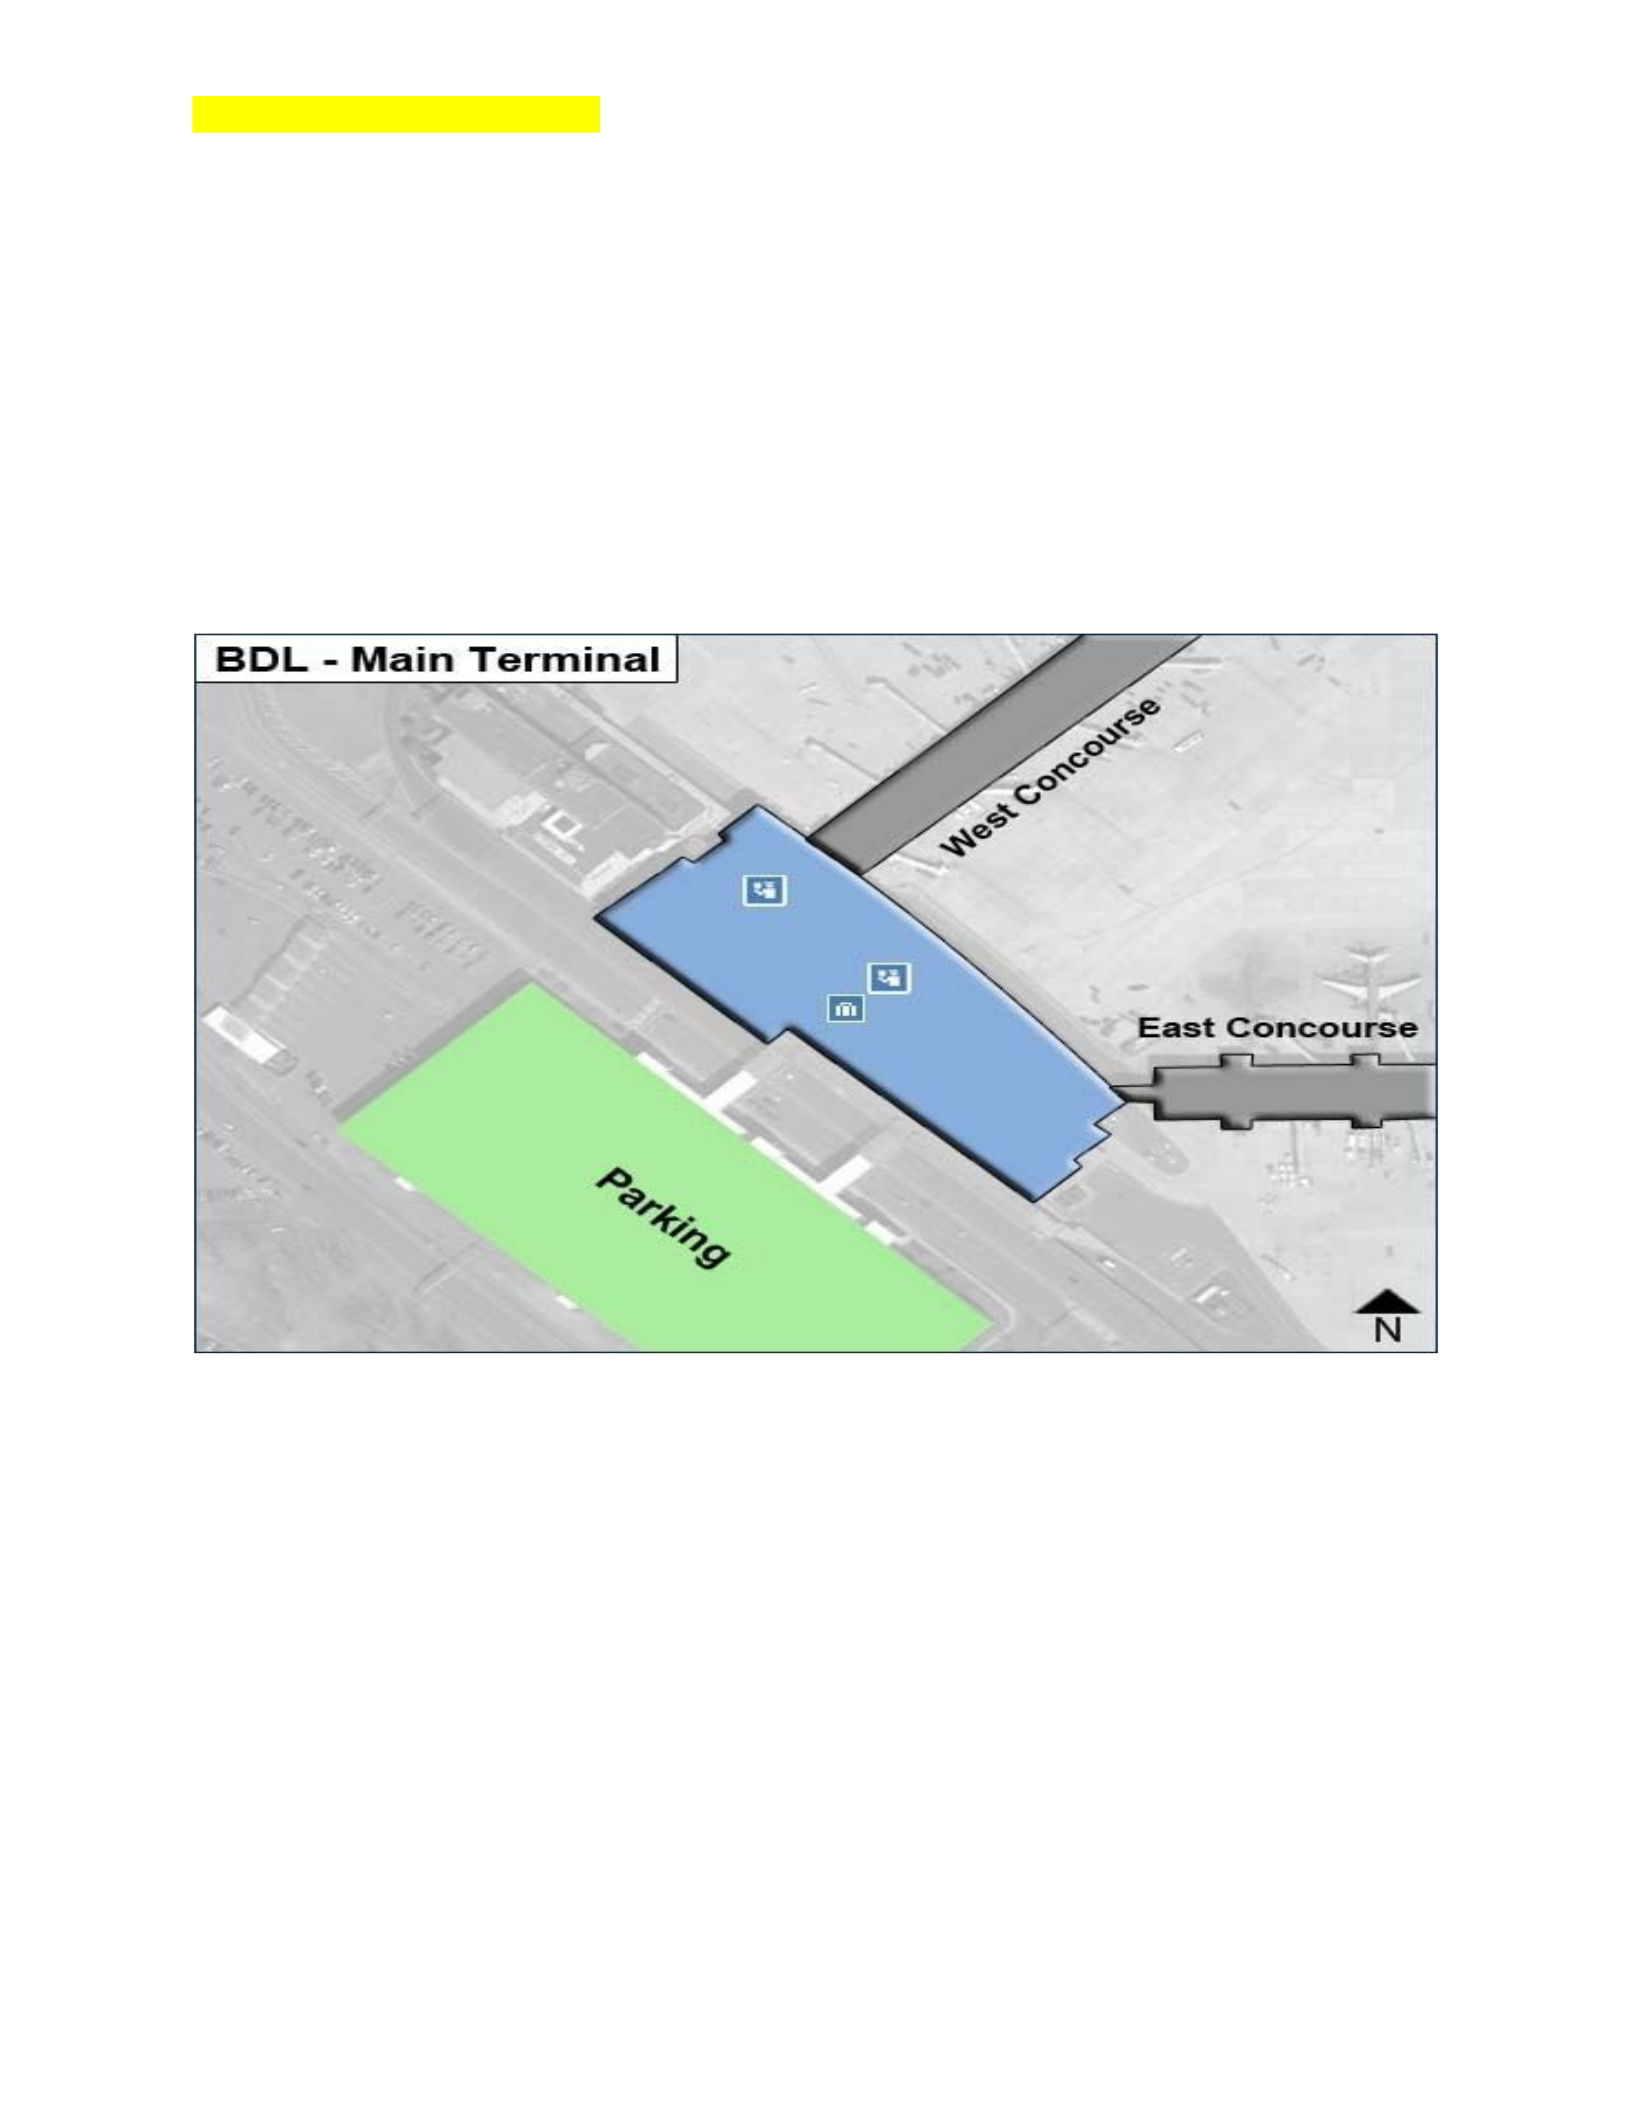
Terminal A
Terminal A serves as the main passenger terminal for the airport. This structure is a split
facility with departures on the upper level and arrivals on the lower level. Both levels serve as
passenger drop-off and pick-up areas. Both terminals have equal gates, with even-numbered
gates on the left side and odd-numbered ones on the right.
RISK ASSESSMENT: PART 3 18
The drop-off and pick areas are in front of the terminal doors, designed in all glass, with
no mechanisms to mitigate attack(s) involving Vehicle Borne Improvised Explosive Devices
(VBIED). Such an attack will have secondary injuries and deaths created by the shattered glass.
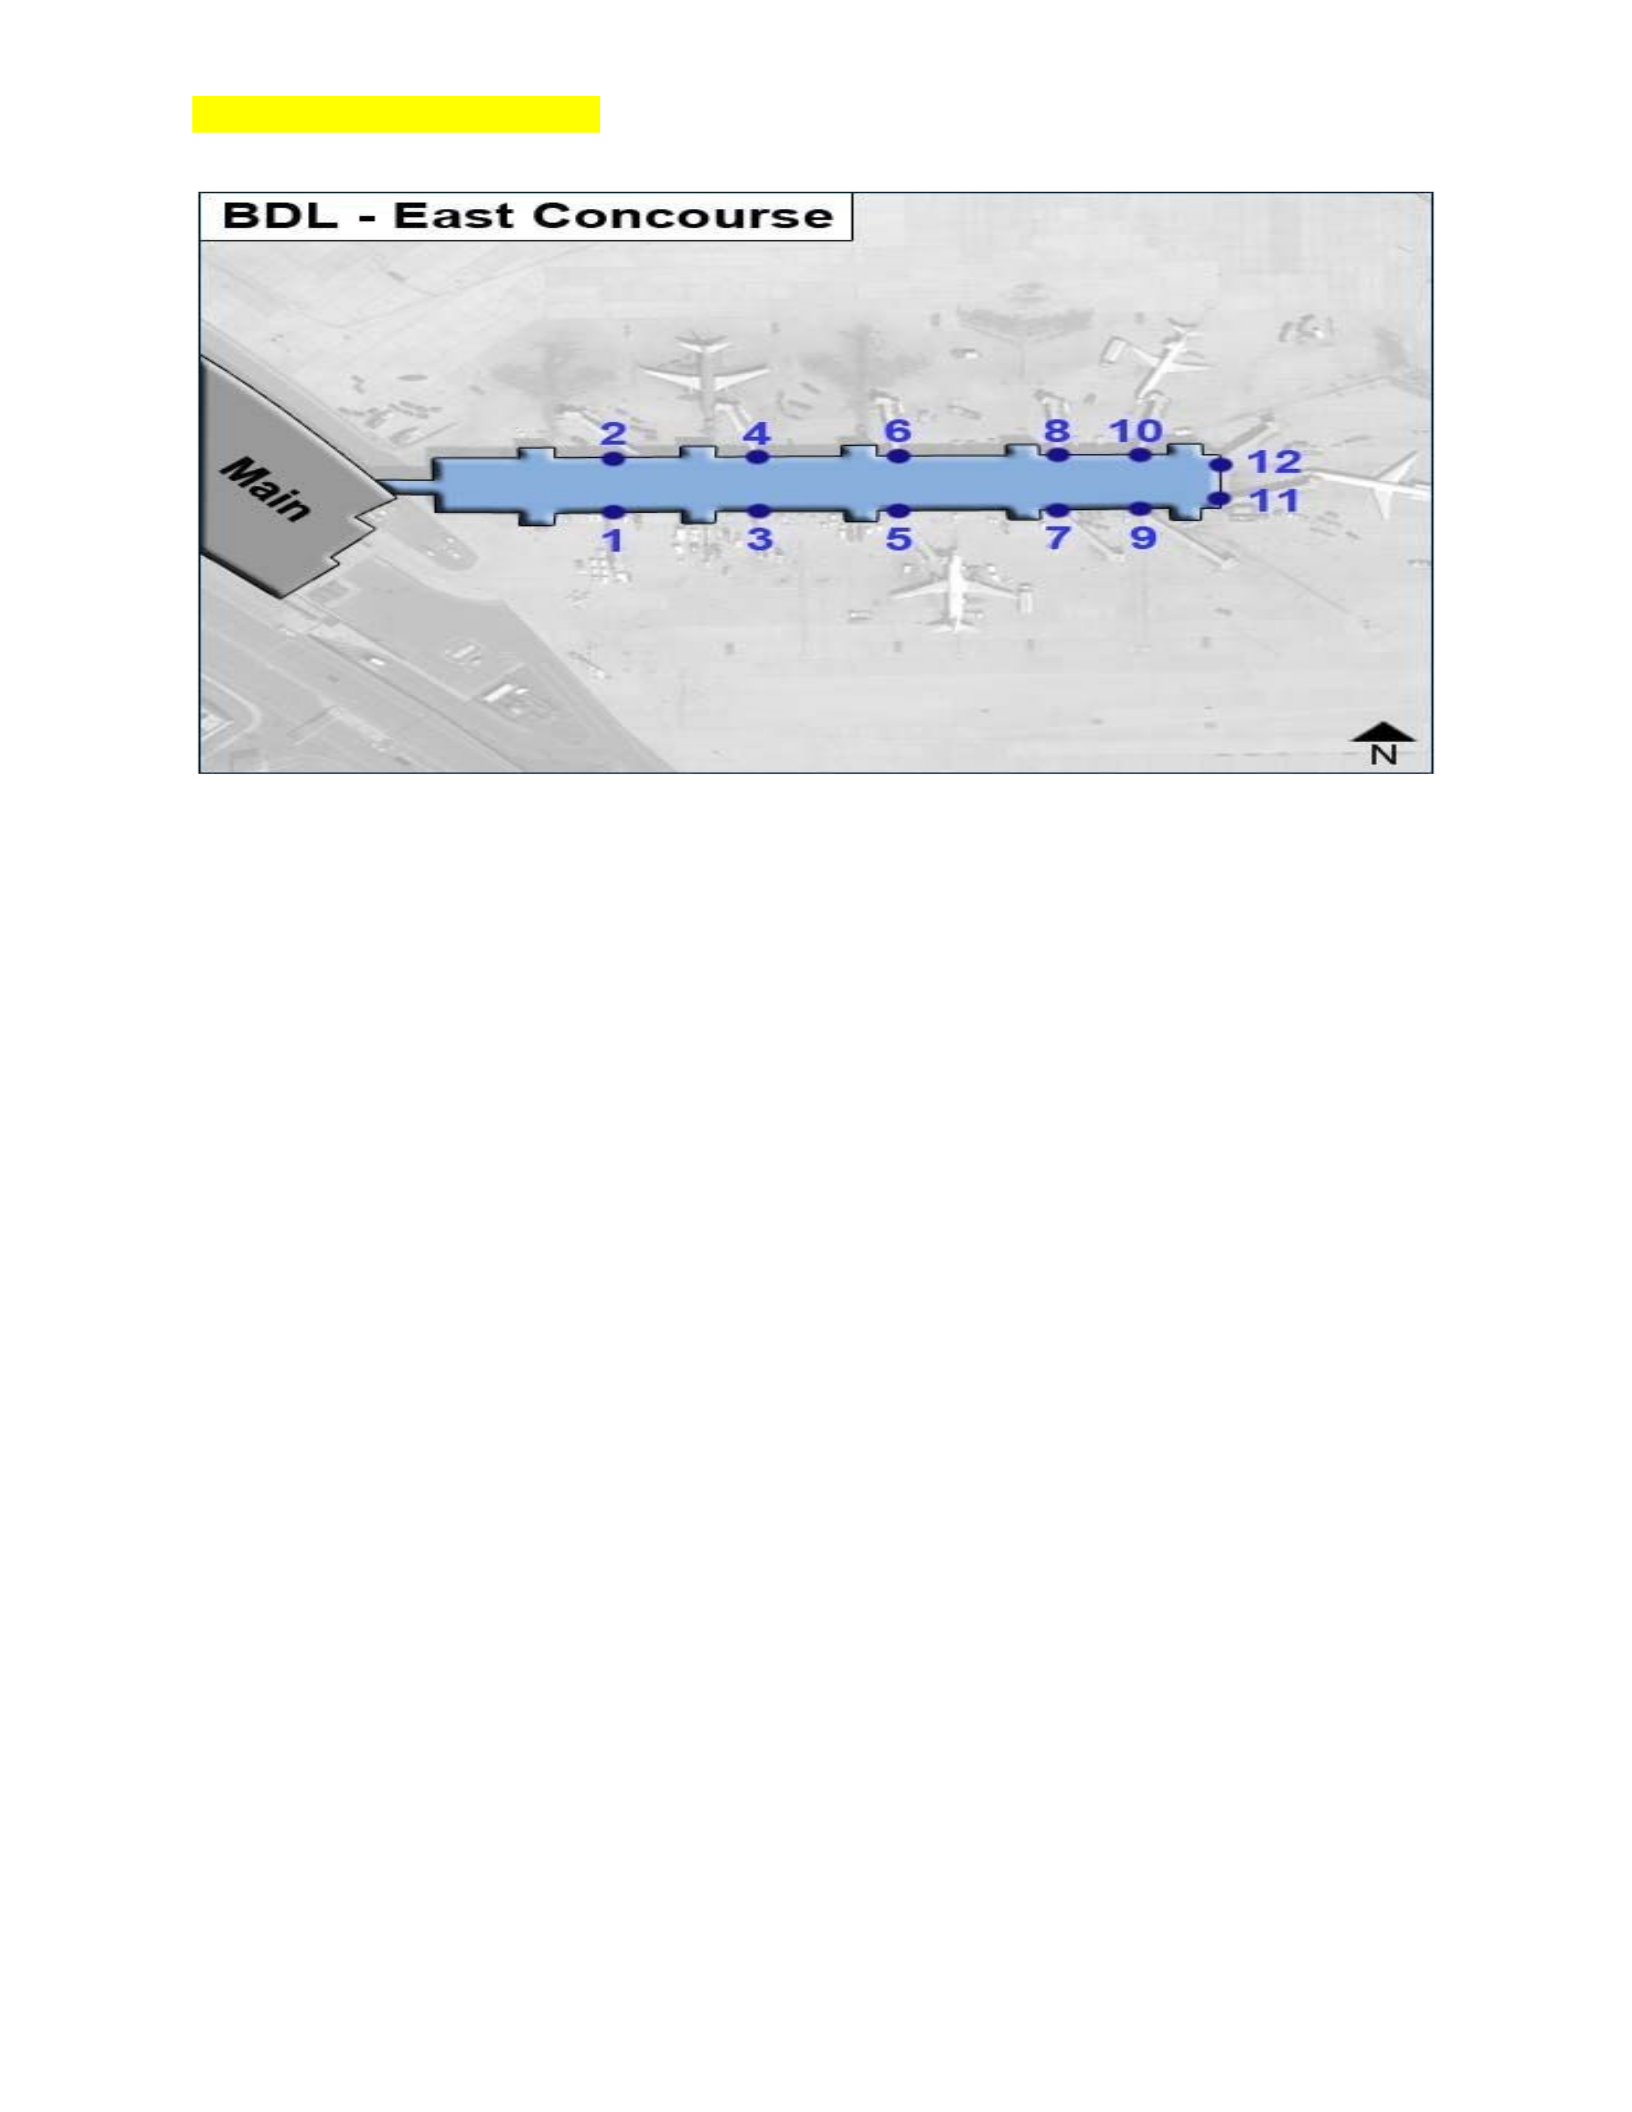
East Concourse
The concourse has seven airline carriers (Aer Lingus et al.) that make Bradley Airport
and gates 1-12 home all year round. The northern half of the concourse houses all even-number
gates. In contrast, the western half houses the odd-number gates in the southern half. Delta
Airlines is
the only primary air carrier establishing a permanent home base at Bradley International Airport.
With the addition of various air carriers, the number of aviation personnel fluctuates widely.
RISK ASSESSMENT: PART 3 19
The East Concourse of the main terminal has several businesses spread throughout the
wing of the structure. The businesses range from Dunkin Donuts to the International duty-free
store on the furthest end of the concourse. These stores serve as a gathering point for numerous
travelers searching for comfort items for their travelers. However, they serve as accessible places
where they can be attacked with little room to maneuver to avoid such an incident. The narrow
design of the concourse will serve as a funneling action, providing staff, airport personnel, and
travelers getting pushed to the end of the concourse where there is limited ability for individuals
to move or escape from an attack initiated from the main passenger terminal.
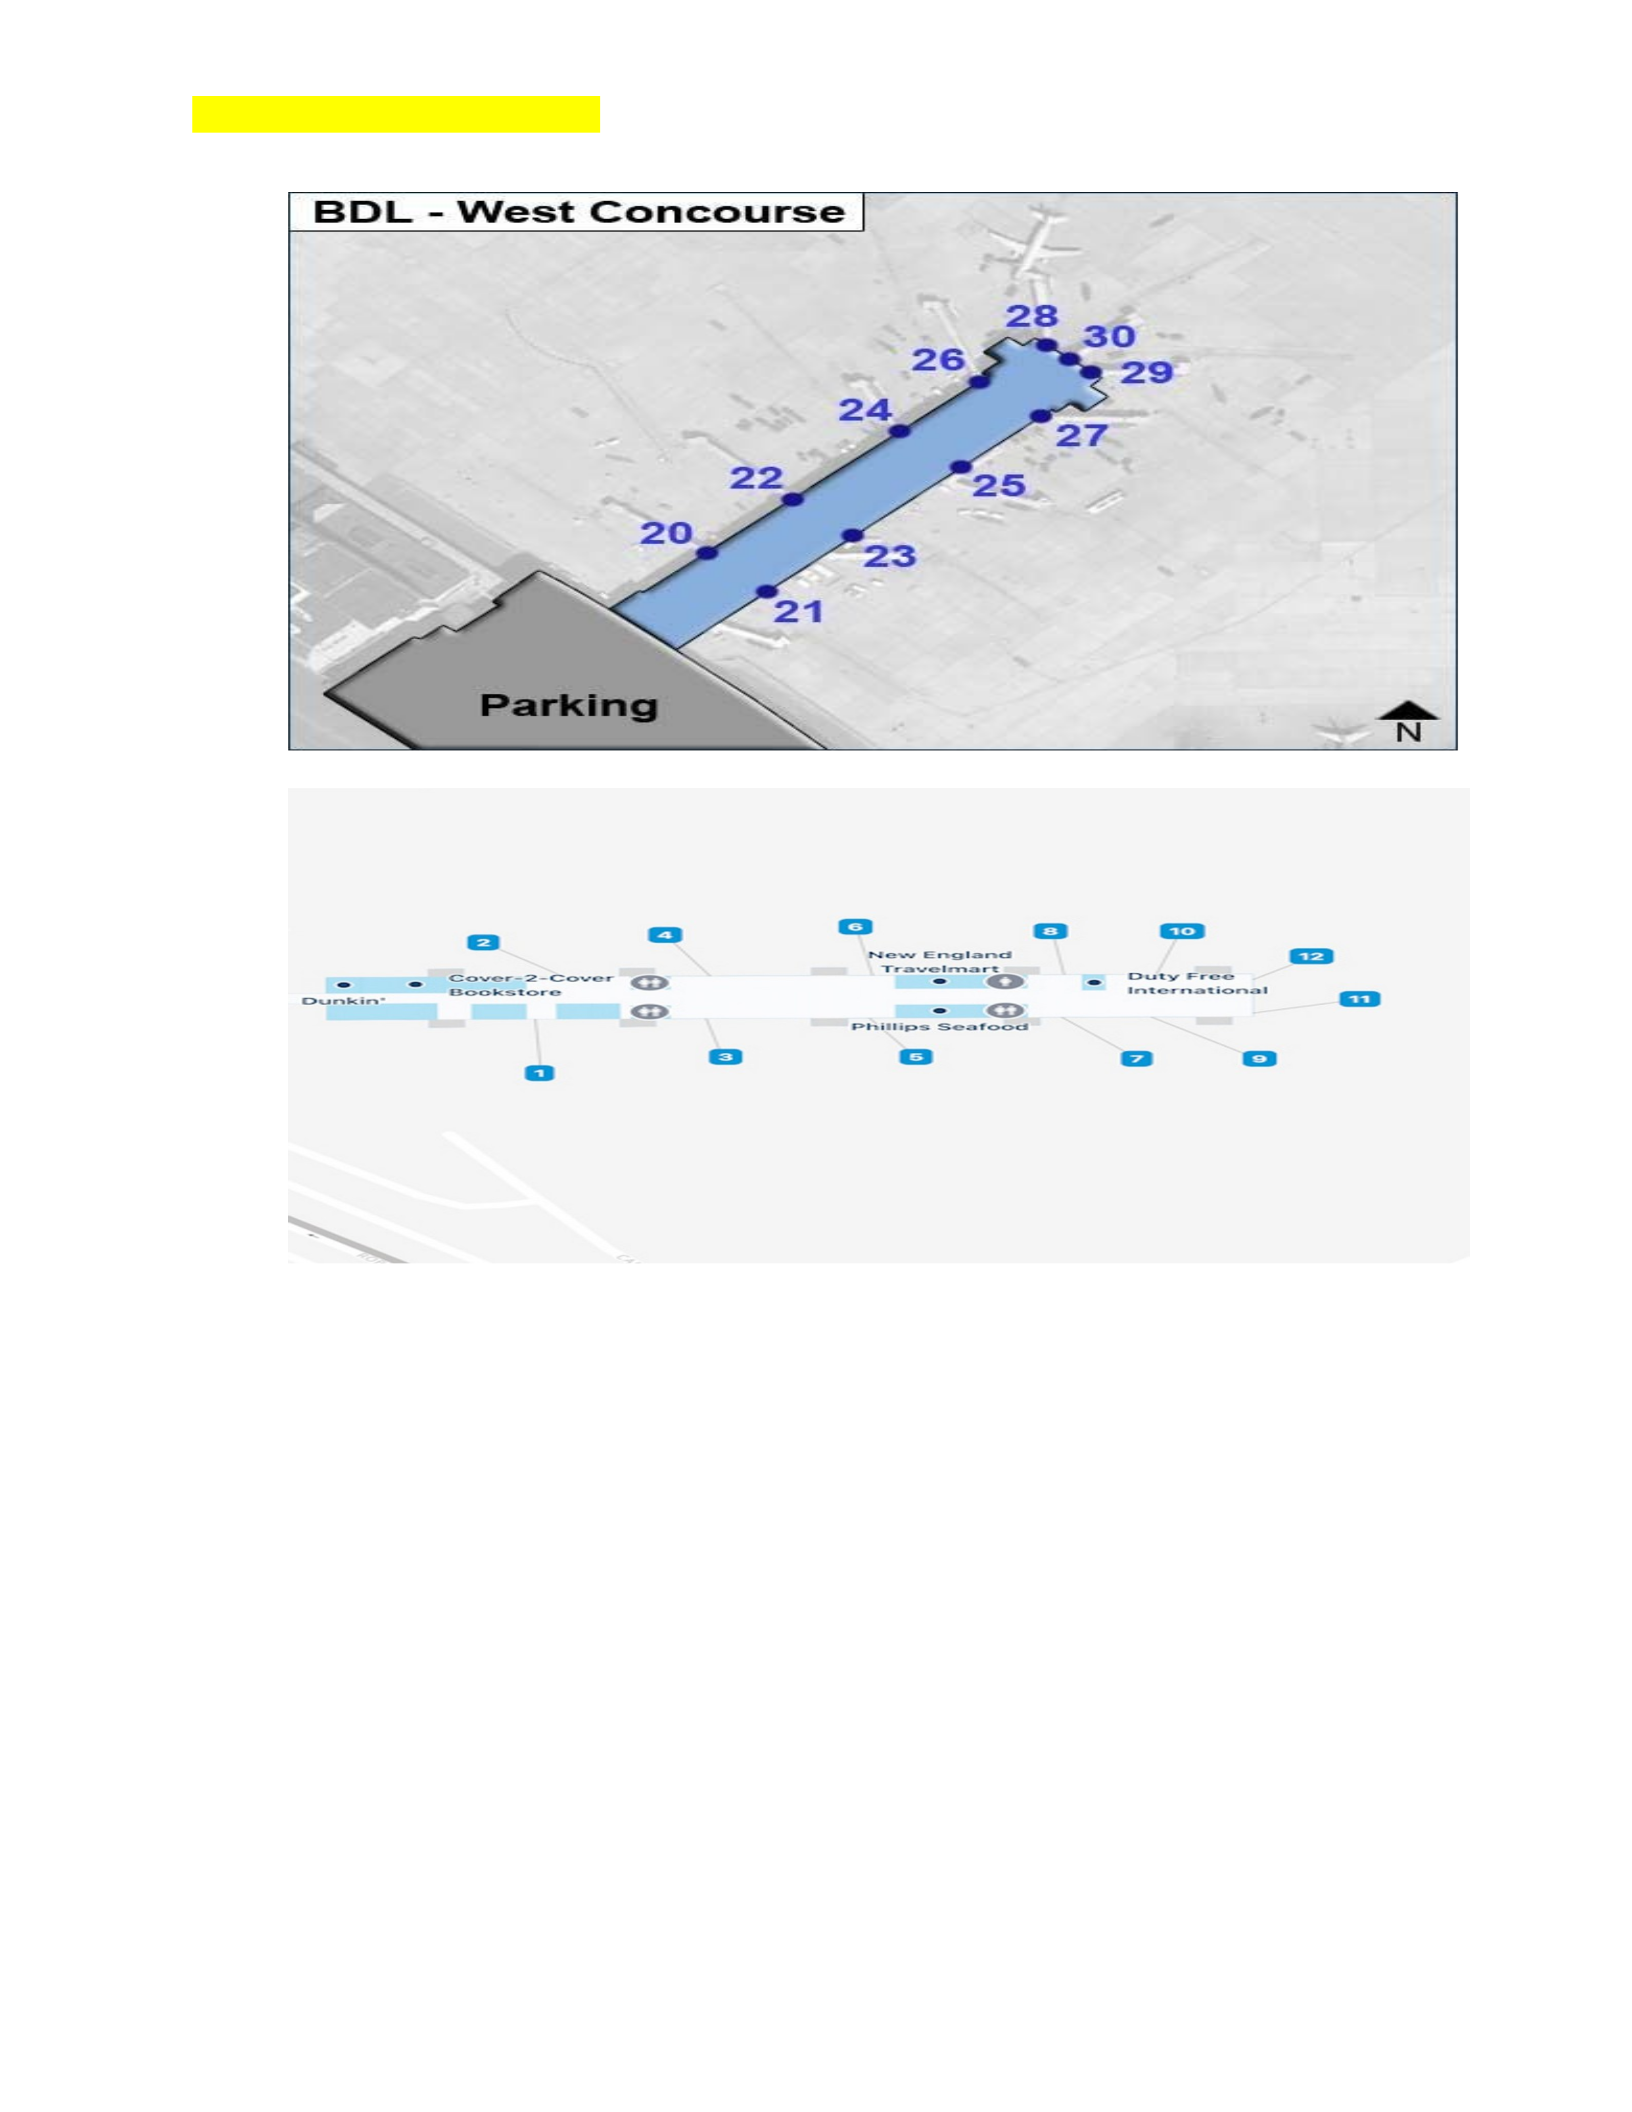
West Concourse
The Western Concourse is similar in design to the Eastern Concourse. Gates 20-30 is in
the Western Concourse. Similarly, all the even gates numbers are on the left side, and the odd
numbers of gates are on the right. The Admiral’s Club, CNBC News, and D’Angelo’s restaurant
are on the West Concourse.
RISK ASSESSMENT: PART 3 20
Parking Lots
The indoor self-service parking lots directly across from the main terminal are a safety
concern. The location has direct access to the terminal for travelers using this facility. The lack
of security cameras in the parking lot has been of concern for some time. The lack of security
cameras has produced low-level crimes like theft and vandalism. The few surveillance cameras
available are pointed at travelers’ and vehicles’ entrances and exits, leaving blind spots that
adversaries can take advantage of such a vulnerability.
RISK ASSESSMENT: PART 3 21
Its proximity to the terminal glass entrance explosion of any significant size would have
limited shielding from the blast. A Vehicle-Borne Improvised Explosive Devised (VBIED)
parked with hundreds of explosives vehicles near its entrance closest to the main terminal
entrance, directing its blast to the street and the glass doors and windows. The explosion will kill
individuals in the pickup and drop-off area. The blast will create glass shrapnel, creating
additional casualties, cutting off the road and thus access to the main passenger terminal.
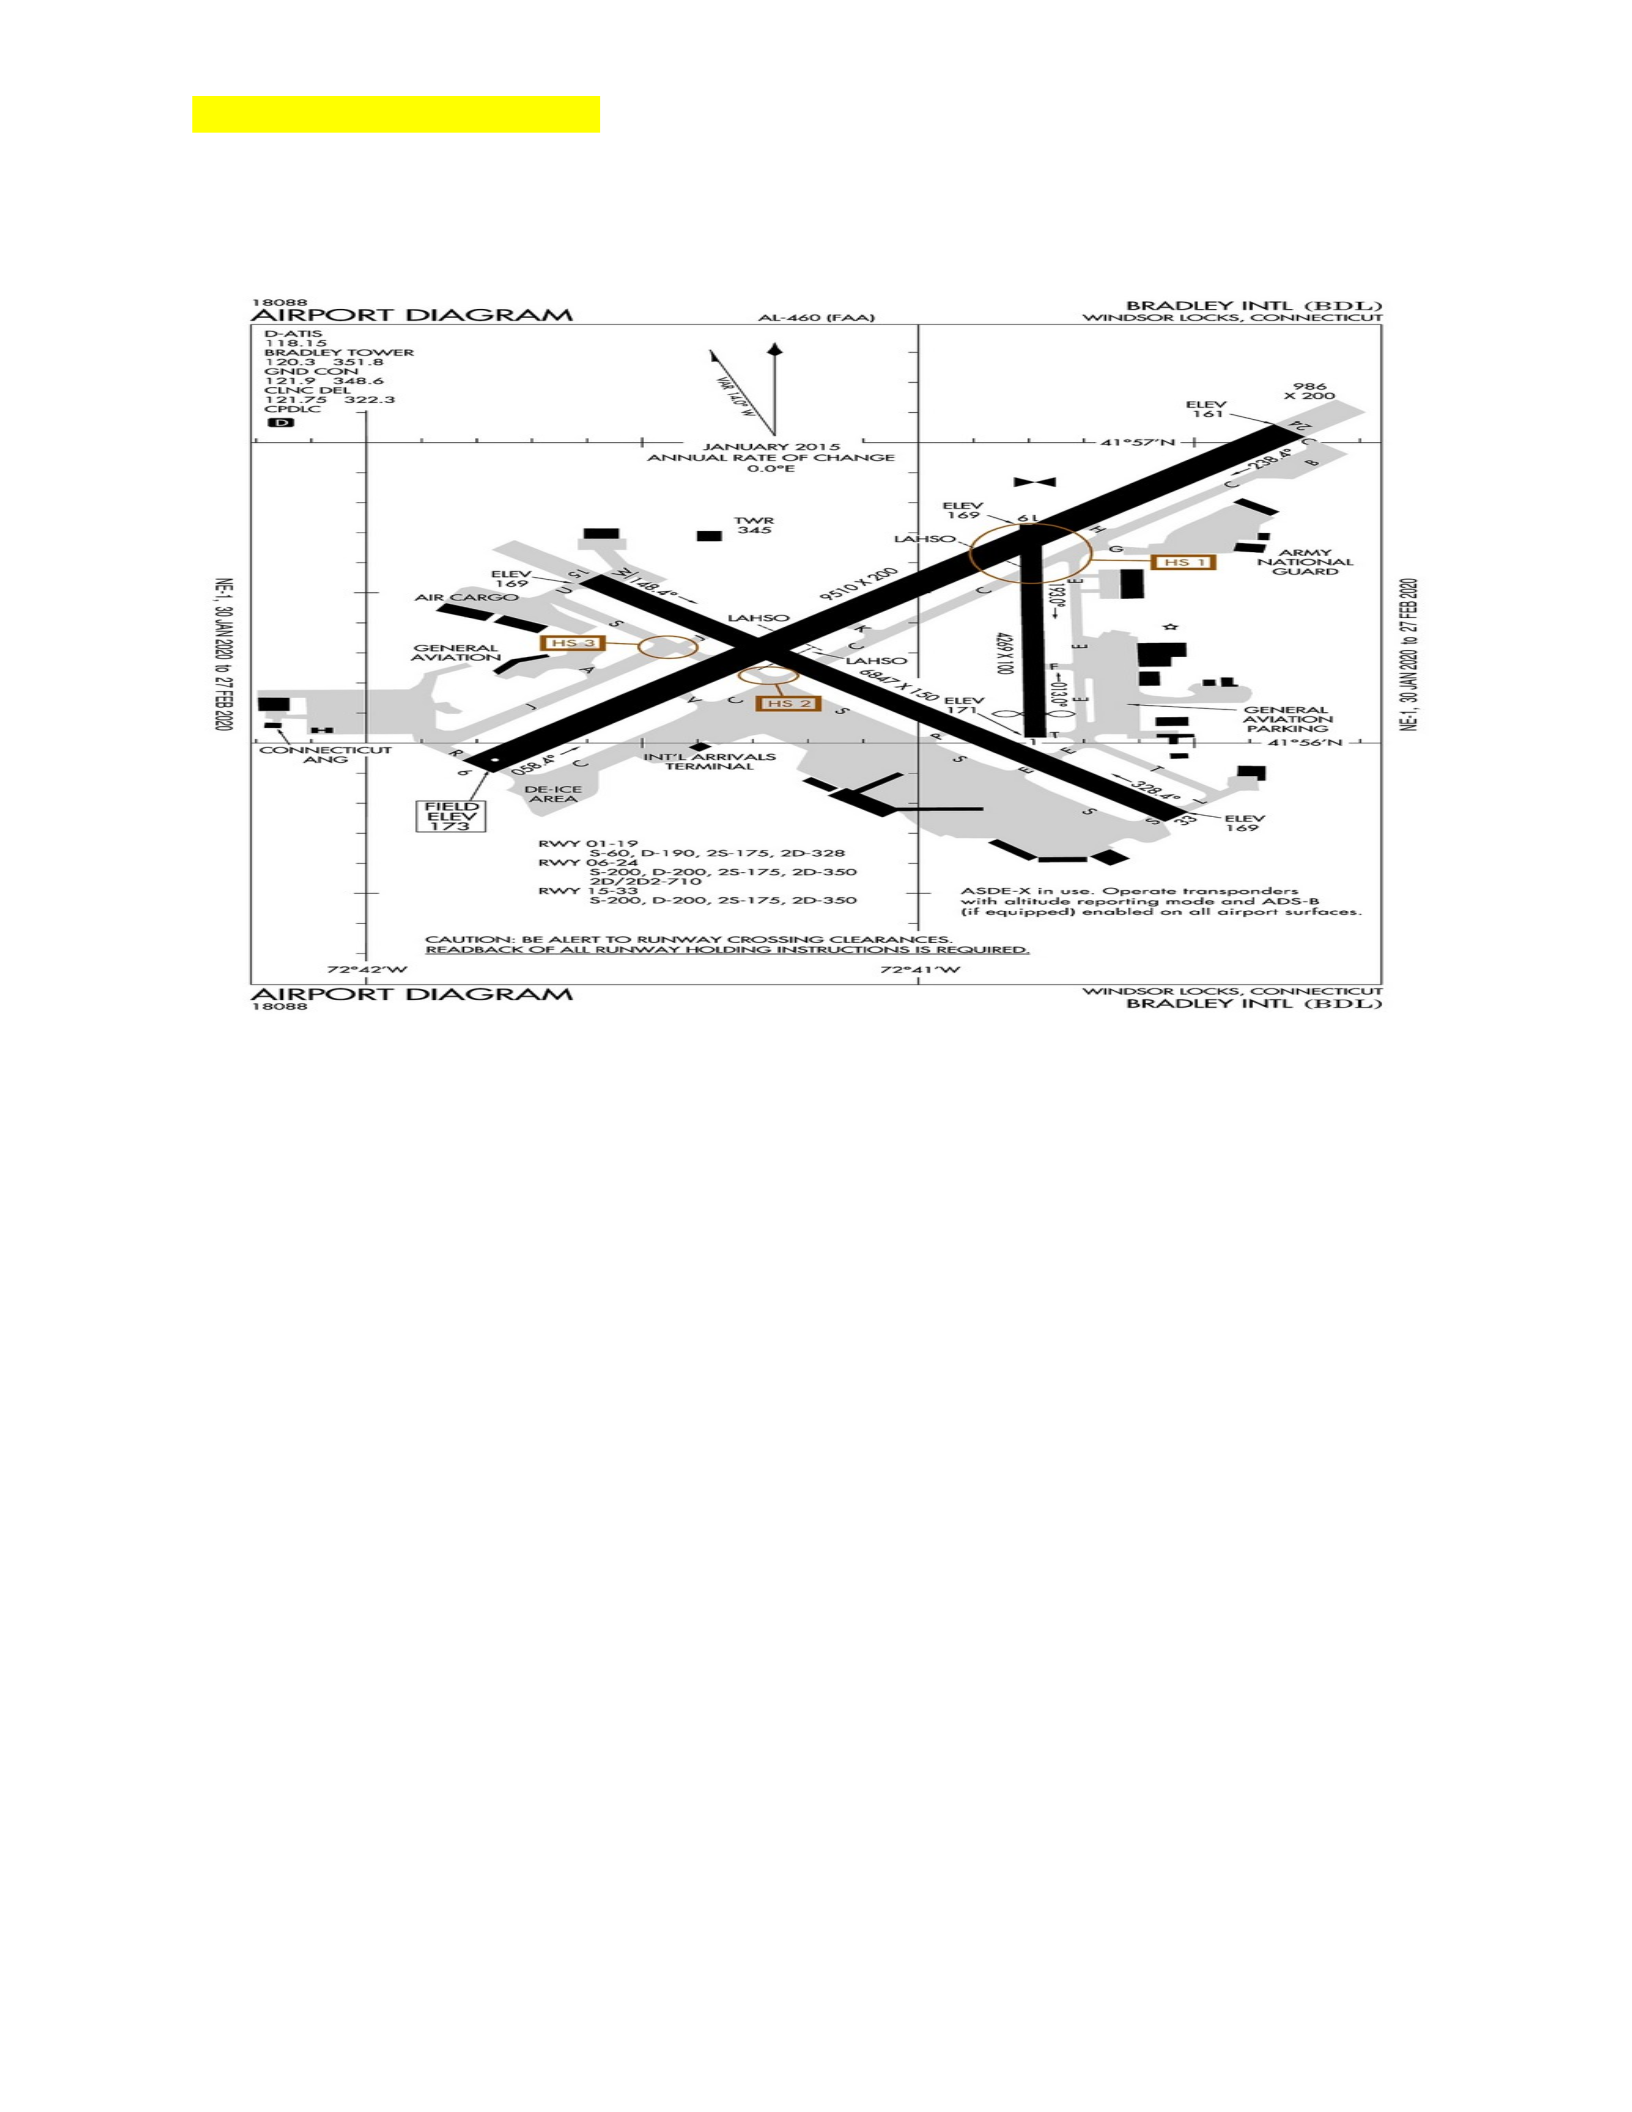
Airport Runways
Airport runway Light Systems (RLS) are vulnerable to attacks initiated from the outer
edges of the runways. Adversaries can turn lights on an approaching aircraft while shining a light
into the cock pit of an aircraft, temporarily blinding the flight crew and creating a possible
catastrophic situation. Many airports have deployed backup emergency lighting systems in case
of sudden loss of power. The system automatically provides enough light to assist an
approaching.
RISK ASSESSMENT: PART 3 22
aircraft with landing.
Demographics of Windsor Locks, CT
The town of Windsor Locks has a population of 12,559, with the largest ethnic population
non-Hispanics making up about 76.9%, African-American (non-Hispanic), Asian (non-
Hispanic) 7.14%, Hispanic 3.16%, 7.82% of the town’s population biracial is 2.46%. The
average annual income for the town’s population is about $79,000. However, the total population
has declined between 2020-2021 from 12,732 to 12,559 a population decline of 1.36% in the past
three years.
Single Station Assessment (SSA)
Single station Assessment is a category of assessment conducted on the nation’s critical
infrastructure. It is conducted either voluntarily or in a non-regulatory manner. This type of
assessment assists the Critical Infrastructure Security Agency (CISA) and its private sector
RISK ASSESSMENT: PART 3 23
partners in identifying vulnerabilities, interdependencies, capability gaps, and consequences of
any disruptions.
In 2013, the Government Accountability Office (GAO) conducted a Joint Vulnerability
Assessment (JVA) in conjunction with the Transportation Security Administration (TSA) and
Federal Bureau of Investigation (FBI) at 81 of 437 or 19% of commercial airports throughout the
nation. TSA was the lead agency for the assessment, with the other agencies playing a support
role. The small sample size used by the General Accounting Office (GAO) was due to budgetary
and resource constraints.
Bradley International Airport Terminal A is the main passenger terminal that connects the
lower level where baggage claims and passenger pickup and drop off. The terminal also has a
direct connection to the service parking lot. Concourse East and West are also connected through
the main terminal. Within the East Concourse, various businesses are located that stretch the
length of the concourse.
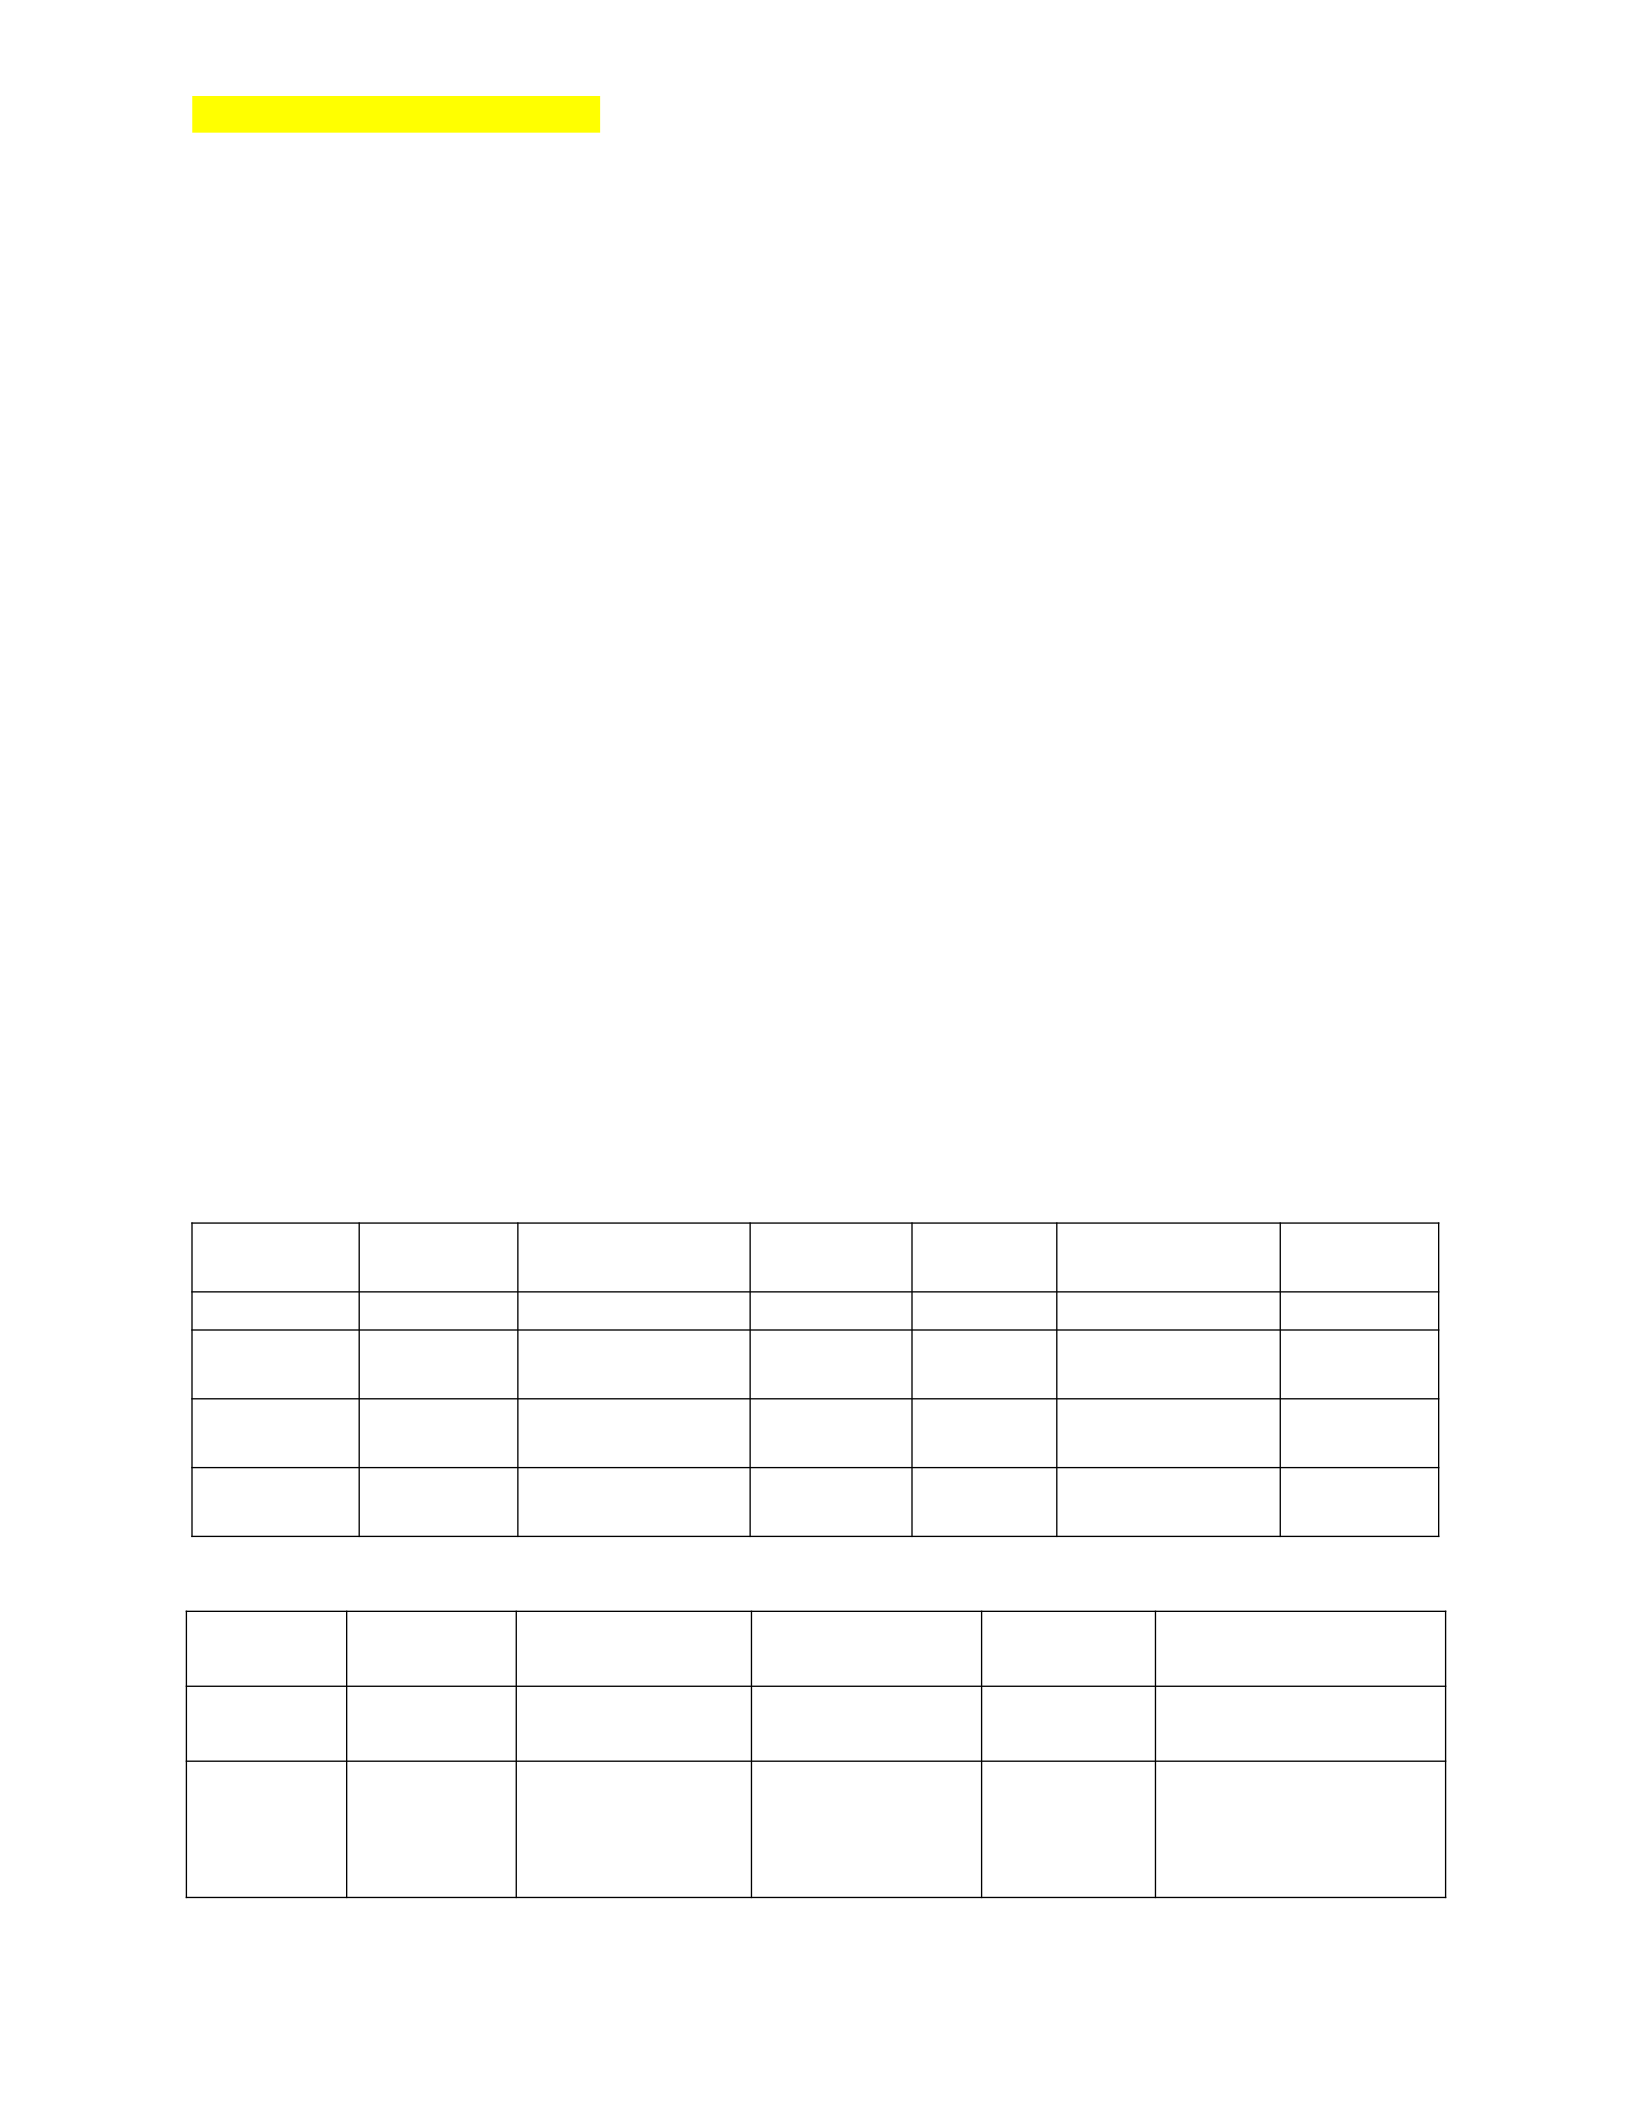
Assessment Tables
Casualties Environmental
Impact
Economic
Impact
Business
Impact
Infrastructure
Impact
Weighted
Score
Structure 3 2 2 3 2 37
Terminal
A
3 0 2 2 2 27
East
Concourse
0 1 1 1 1 10
West
Concourse
0 0 1 1 3 8
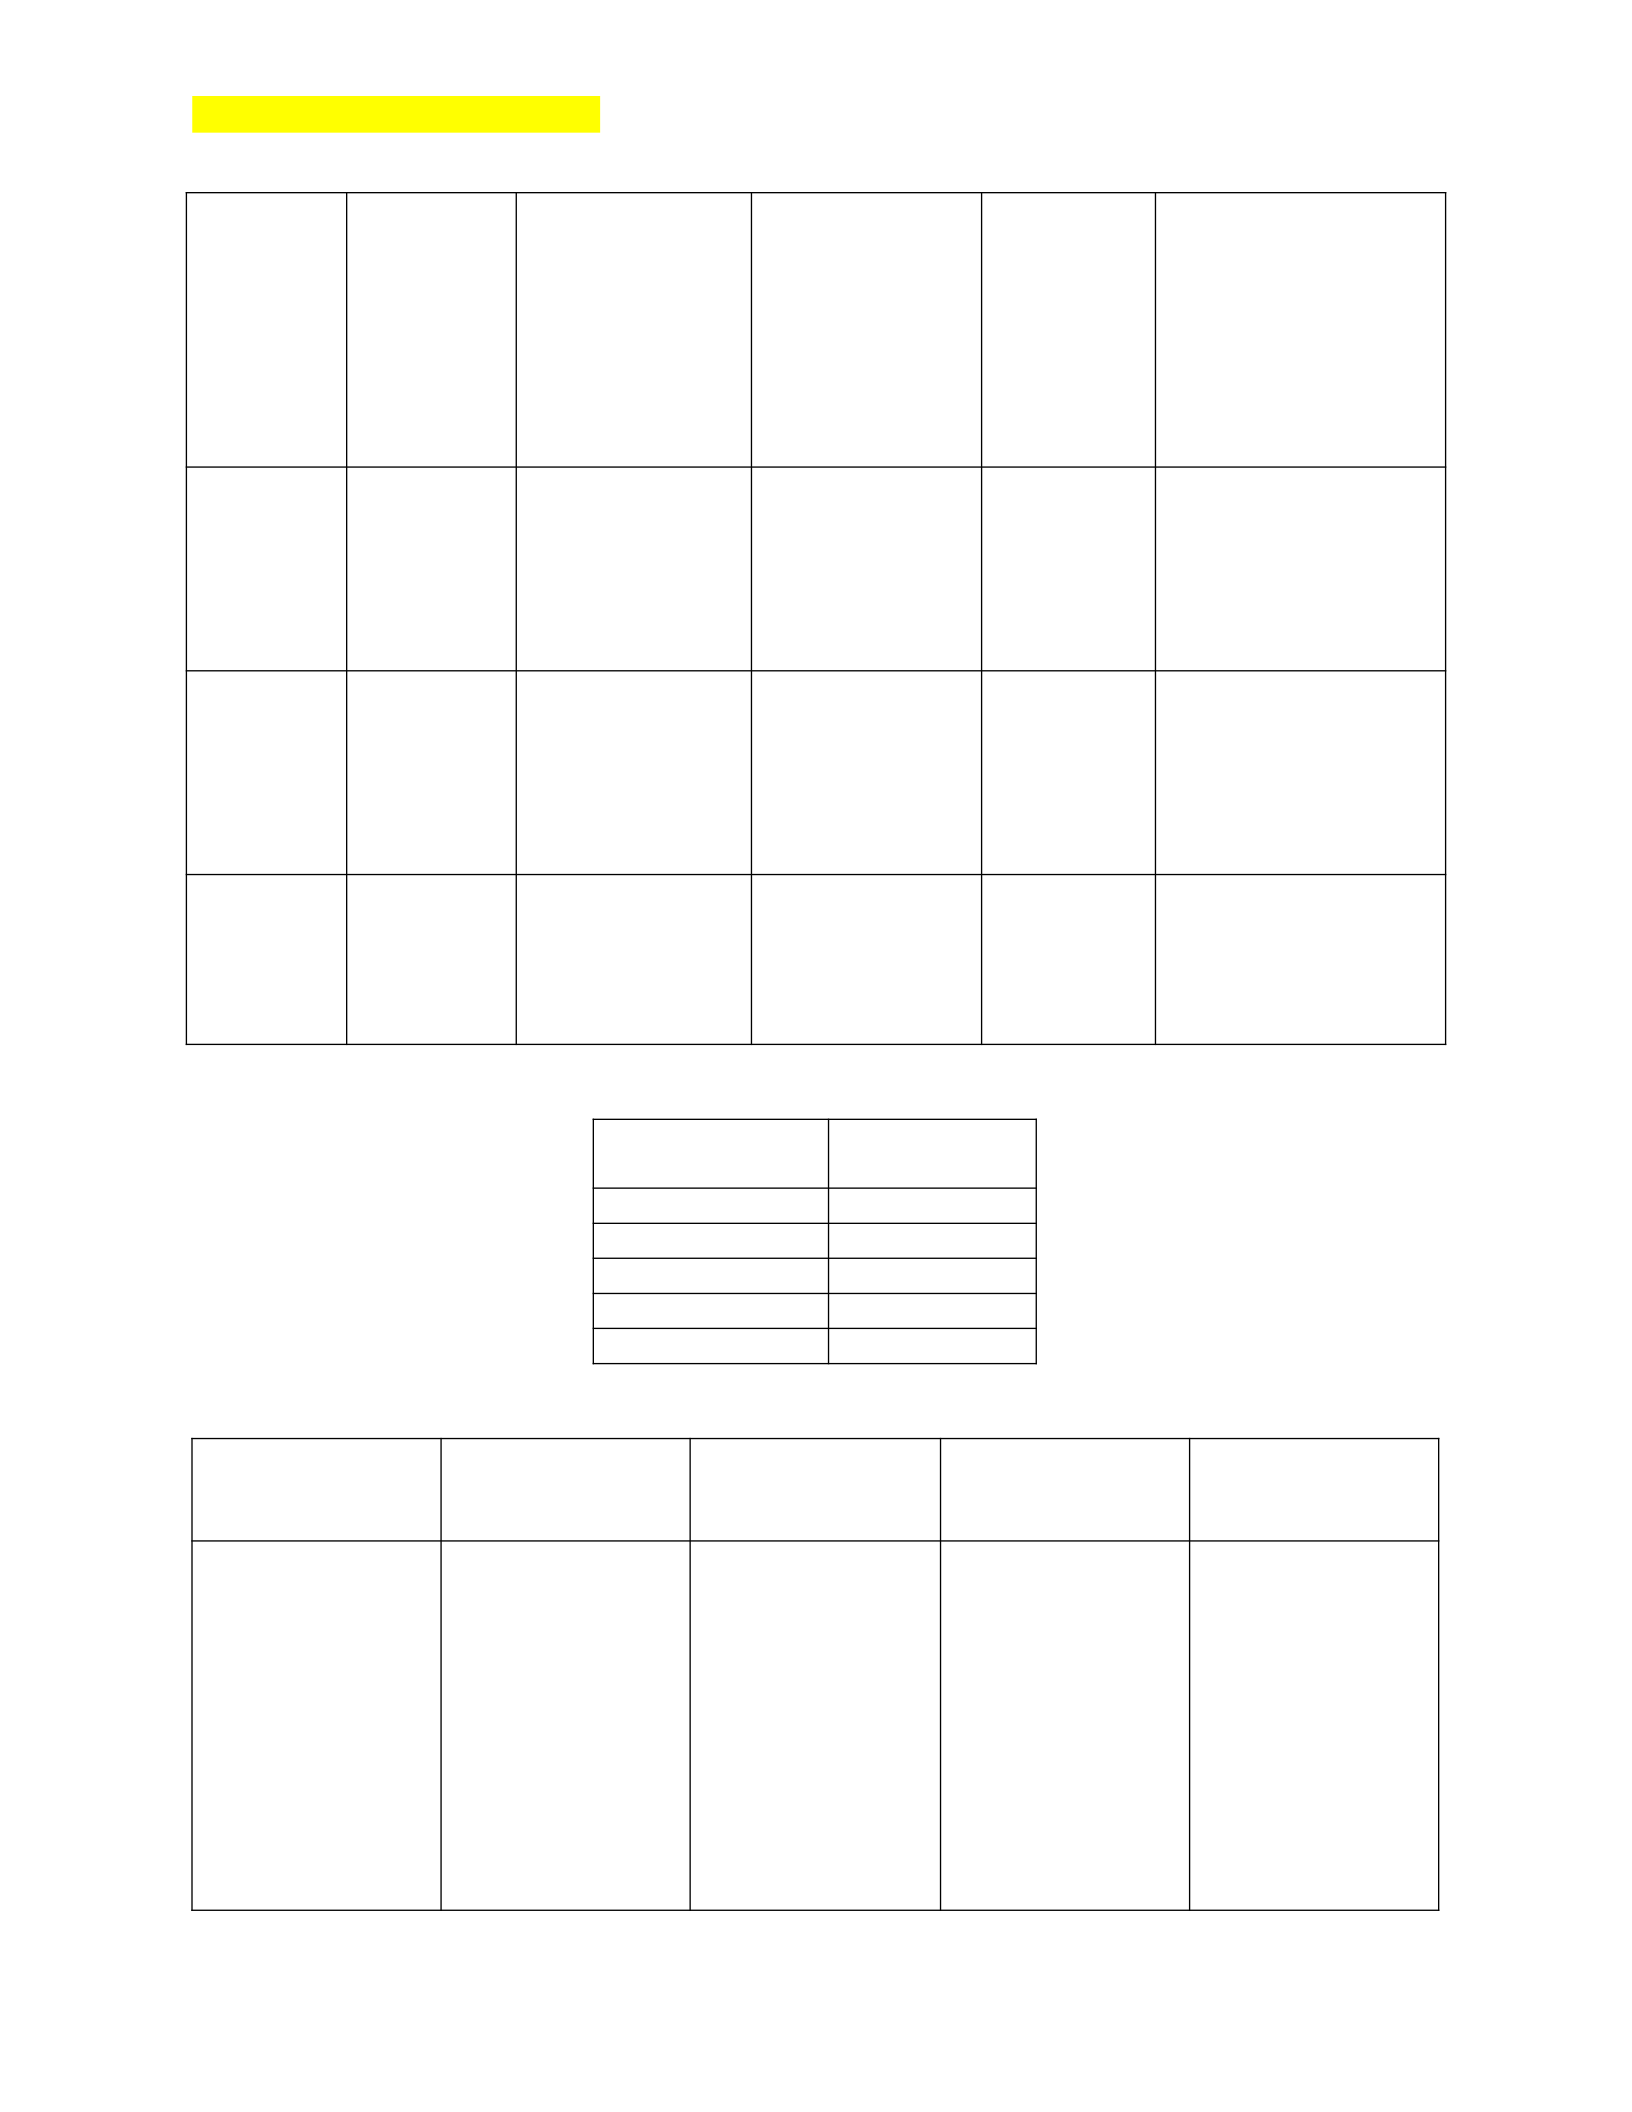
Score Casualty Environmental
Impact
Economic
Impact
Business
Impact
Infrastructure
Impact
Structur
e
0None
Expected
Not applicable No significant
effect likely
Startup
facility with
minor
changes
No effect on
operations
RISK ASSESSMENT: PART 3 24
1Non-life
threating
injuries
projected
off the
property
Not applicable No significant
effect likely
>10%
Terminal
shut down
and unable
to provide
services for
less than 1
month.
Damage restricted to
the identified building
2Life
threating
injuries
both on off
the
property
Will not leave
the key asset’s
property
Impact on
corporate
profitability
>10%
Terminal
shut down
and unable
to services
less 6
months.
Damage to terminal
support systems and
utilities
3On-site
Fatalities
likely
Impact of
United States
economy
Terminal
shut down
and unable
to services
less than 1
year
Damage to other
production or
maintenance aviation
service facilities
4Off-site
fatalities
Like to leave the
key asset
property;
persistent
Income on the
world economy
Terminal
destroyed
and not
expected be
rebuilt
Damage to the entire
terminal
Impact Weighting
Factors
Casualty Rating x 5
Environmental Rating x 4
Economic Rating x 3
Business Rating x 2
Infrastructure Rating x 1
Problem Risk Existing
Countermeasure
s
Recommendation Priority
Fire Structural
damage, casualties
Pull alarms,
warning lights,
smoke detectors,
sprinklers, fire
extinguishing, lit
exit signs,
visibility marked
FDC, terminal
coordinator, call
center
Create clear
signs indicating
location of fire
extinguishers,
promotes fire
drills’
with airport fire
department,
update directory
maps for
3
RISK ASSESSMENT: PART 3 25
accuracy, clear
display terminal
evacuation route
maps, install exit
signs
Explosion Casualties,
structural damage,
secondary
explosions
Evacuation,
deploy Bomb
Squad, warning lit
exit signs,
visibility marked
FDC, terminal
coordinator, call
center
Create clear
signs indicating
locations of fire
extinguishers,
promote
fire/bomb drills’.
4
Terrorist attack Casualties,
explosion, fire
damage to the
structure
Evacuation,
deploy, law
enforcement
Promote terrorist
attack drills
4
Active Shooter Causalities Evacuation,
deploy, law
enforcement
Promote active
shooter drills
4
Risk assessment and Countermeasures
Table six indicates the security action plan required to establish a minimal threat
reduction. At the same time, it provides resiliency and mitigation in a successful attack terrorist
attack at a commercial airport like Bradley International Airport. A high security level has
become the standard operation procedures (SOP) required to keep the facility secure and safe.
Facilities require redundant systems as fail-safe operations in the case of disruptions
caused by natural or man-made events. It protects a vehicle used to drive through a glass entrance
and then explode inside the facility, maximizing the death and damage. Bollards of different
materials have been constructed and placed in front of terminal doors at airports like John F.
Kennedy in New
New York City and act as effective countermeasures for Vehicle Borne Improvised Explosive
Devices (VBIED). Hardened obstacles like bollards will not stop a heavy truck from ramming
through but can keep a small vehicle from ramming into a facility.
RISK ASSESSMENT: PART 3 26
Bradley International Airport has various issues that the airport administration can
address. The first issue is that of the parking lot and the location. While the parking lot is
convenient for the public, it is a cause for concern. After the first World Trade Center bombing
attempt, the truck filled with explosives parked in the parking garage. An explosion from a
similar explosive(s) can render the main terminal and the access road unusable for months. The
actual damage of such an attack is the loss of consumer confidence. No one will fly; they do not
feel safe doing so. The decrease in individuals flying was evident in the days and months
following the 9/11 attacks when a significant segment of the population refused to fly.
Security
Action
Parking Lot Main
Terminal
Concourse
East
Concourse
west
Perimete
r
Fence
Airport
Roadway
Airport
runway
Passenger
pickup &
drop off
Risk
planning
&
assessment
Mount
additional
surveillance
cameras.
Establish
standard
evacuation
procedures
Establish
announcement
system for all
staff, and
airport
personnel
Establish
announcement
system for all
staff, and
airport
personnel
Add
sensors
Build
steel
bollards
Install
sensors
throughou
t the back
& sides of
the
runways
and taxi
ways
Establish
passenger
pick up &
drop areas
away from
terminal
entrance
Post 24hr
armed security
guard
Establish
Active
shooter
drills
Establish gate
lock down
policy
Establish gate
lock down
policy
Establish
roving
Security
watch
Situate
concreate
staggered
barriers
Leading
to the
terminal
Establish
emergency
runways
power
stations
Establish
designated
taxi and
share ride
stand
areas
Build Blast
proof walls
Establish Active
shooter drills
Establish Active
shooter drills
Station law
enforcement
perched
stations in all
parking open
air parking
lots
Build panic
buttons for all
merchants
Establish a
larger
police
presence
Establish a larger
police presence
Establish a larger
police presence
RISK ASSESSMENT: PART 3 27
Conclusion
A critical infrastructure is a collection of indispensable assets necessary to maintain our
standard of living (Bennett, 2018). Current and historical events have shown the need to protect
the critical infrastructure (CI) of the United States. Public and private sectors designated these
structures or facilities vital to the United States’ national security. Security analysts and
emergency managers are directly involved with public and private sectors in protecting facility
personnel, business staff, and travelers.
Since the September 11, 2001, attacks, the civil aviation community has continuously
focused on transportation safety and the renewed effort to secure airport airlines’ concerns
updated newly implemented security procedures. In recent years, the policies have been driven
mainly by occurrences at international airports and reported near misses on airliners. These
reported near misses almost always involved individuals attempting to smuggle on board
explosive materials into and through airport baggage checking points.
Bradly International Airport in Windsor, CT, has similar issues balancing safety with
access. The airport has an estimated 4.6 million travel transits through its facility each year,
making it the second busiest airport in New England. Boston’s Logan Airport is the largest and
busiest in the New England region. An estimated 10 million travelers traveled through its facility
during the same period in 2022.
RISK ASSESSMENT: PART 3 28
Bradley International Airport is a critical infrastructure and a key resource that must be
protected and its operations prioritized. A successful attack on the airport would cause a loss of
confidence in the safety of the facility by the public, which would cause an economic turn for the
facility and create a cascading chain of events scrutiny from the various government agencies
that oversee airport operations.
Bradley International Airport is invaluable to Northern Connecticut and southern
Massachusetts. It provides the state, town, and city’s economy and pride to the area’s residents.
Christian Worldview
Because you have the Lord your dwelling place- the highest, who is my refuge -no evil
shall be allowed to befall you, no plague comes near your tent. For he will command his angels
concerning you to guard you in all your was (English Stand Version, Psalm 91:9-11).
RISK ASSESSMENT: PART 3 29
References
Aradau, C. (2010). Security that matters: Critical Infrastructure and Objects of Protection.
Security dialogue 41(5), 491-514.
https://dx.doi.org/10.1177/0967010610382687
Ayyub, B. M., McGill, W. L., & Kaminskiy, M (2007). Critical Asset and Portfolio Risk
Analysis: An All-Hazards Framework
Risk Analysis: An International Journal, 27(4), 789-801
http://doi.org/10.1111/j.1539-69.2007.00911.x
Bennett, B. (2018). Understanding, Assessing, and Responding to Terrorism: Protecting Critical
Infrastructure and Personnel. (2nd ed.).
Wiley & Sons.
Bishop, M. (1999). Vulnerabilities analysis. In Proceedings of the Recent Advances in Intrusion
Detection pp 125–136.
Church, R. L. (2002). Geographical Information Systems and Location Science.
Computer & Operations Research 29(6), 541-562
htttps://doi.org/10.1016/S0305-0548(99)00104-5
Fischoff, B., Watson, S. R., & Hope, C. (1984). Defining Risk.
In Readings in Risk,
RFF Press pp.30-42
Hunter, N, D. (2017). The law of emergencies: public health and disaster management.
Butterworth-Heinemann.
Moteff, J., Library of Congress Washington DC Congressional Research Service. (2005,
January). Critical Infrastructure Protection: The 9/11 Commission Report and
Congressional Response. Congressional Research Service, Library of Congress, Library
of Congress.
Moteff, J., & Parfomak, P. (2004, October). Critical Infrastructure and Key Assets: Definition
and Identification
Washington: Congressional Research Service, Library of Congress
https://apps.dtic.mil/sti/pdfs/ADA454016.pdf
Murray, A. t., & Grubesic, T. H. (2012). Critical infrastructure protection: The vulnerability
conundrum
Telematics and informatics, 29(1), 56-65.
http://doi.org/10.1016/j.tele.2011.05.001
Ronczkowski, M. R. (2018). Terrorism and Organized Hate Crime: Intelligence Gathering,
Analysis, and Investigations. (4th ed.).
CRC Press
Taylor, R. W., & Swanson, C. R. (2019). Terrorism, Intelligence & Homeland Security. (2nd ed.).
Pearson Education
The English Standard Version Bible. (2001). Crossway.
Theocharidou, M., & Giannopoulos, G. (2015). Risk assessment methodologies for critical
infrastructure protection. Part II: A new approach.
Scientific and Technical Research Reports.
Zio, E. (2016). Challenges in the vulnerability and risk analysis of critical infrastructure.
Reliability Engineering & System Safety 152, 137-150.
https://dx.doi.org/10.1016/j.ress.2016.02.009

