


CSIS 343 – Cyber security
Week 8
15th August
Assignment 8: Securing a Global Biotechnology and Life Sciences Company
Instructions:
You are a cybersecurity consultant working with a global biotechnology and life sciences company that
specializes in genetic research, pharmaceutical development, and healthcare solutions. Write a seven to nine-page
paper addressing the following questions:
1. Develop a comprehensive cybersecurity strategy for the biotechnology and Life Sciences Company.
Discuss measures to secure genetic research data, protect intellectual property related to pharmaceutical
development, and prevent cyber threats to critical life sciences infrastructure. Address the unique
challenges associated with managing sensitive health data and complying with healthcare industry
regulations.
2. Evaluate the security of the company's genetic research and laboratory systems. Recommend measures to
secure these systems, prevent unauthorized access, and ensure the confidentiality and integrity of genetic
research data. Discuss the importance of compliance with biotechnology and healthcare industry
cybersecurity standards and regulations.
3. Assess the security of the company's pharmaceutical development systems, including drug formulation
databases and research collaboration platforms. Propose strategies to secure these systems, prevent
unauthorized access, and ensure the confidentiality and integrity of pharmaceutical development data.
Discuss the importance of secure coding practices and compliance with industry-specific cybersecurity
standards.
4. Propose measures to secure communication channels within the biotechnology and life sciences
Company, especially those involving sensitive information related to genetic research findings,
pharmaceutical development, and patient health data. Discuss strategies for secure data exchange,
encryption, and identity verification to prevent unauthorized access to critical life sciences information.
5. Develop an incident response plan specifically tailored for cybersecurity incidents affecting the
biotechnology and life sciences company. Discuss communication strategies with regulatory bodies,
government health agencies, and the public, as well as steps to minimize the impact of incidents on life
sciences operations and public trust.
Given the sensitive nature of genetic and pharmaceutical research, emphasize the need for a proactive and robust
cybersecurity posture to protect intellectual property and maintain the trust of patients and stakeholders.
Ensure that your papers provide practical recommendations and considerations for the specified scenarios. Use
relevant industry standards, best practices, and case studies to support your analysis and suggestions.
Your assignment must follow these formatting requirements:
Be typed, double spaced, using Times New Roman font (size 12), with one-inch margins on all sides;
citations and references must follow APA or school-specific format. Check with your professor for any
additional instructions.
Include a cover page containing the title of the assignment, the student’s name, the professor’s name, the
course title, and the date. The cover page and the reference page are not included in the required
assignment page length.
The specific course learning outcomes associated with this assignment are:
Compare and contrast the methods of disaster recovery and business continuity.
Explain risk management in the context of information security.
Use technology and information resources to research issues in disaster recovery.
Write clearly and concisely about disaster recovery topics using proper writing mechanics and technical
style conventions.
Grading for this assignment will be based on answer quality, logic / organization of the paper, and language and
writing skills, using the following rubric.
Points: 75 Assignment 8: Securing a Global Biotechnology and Life Sciences Company
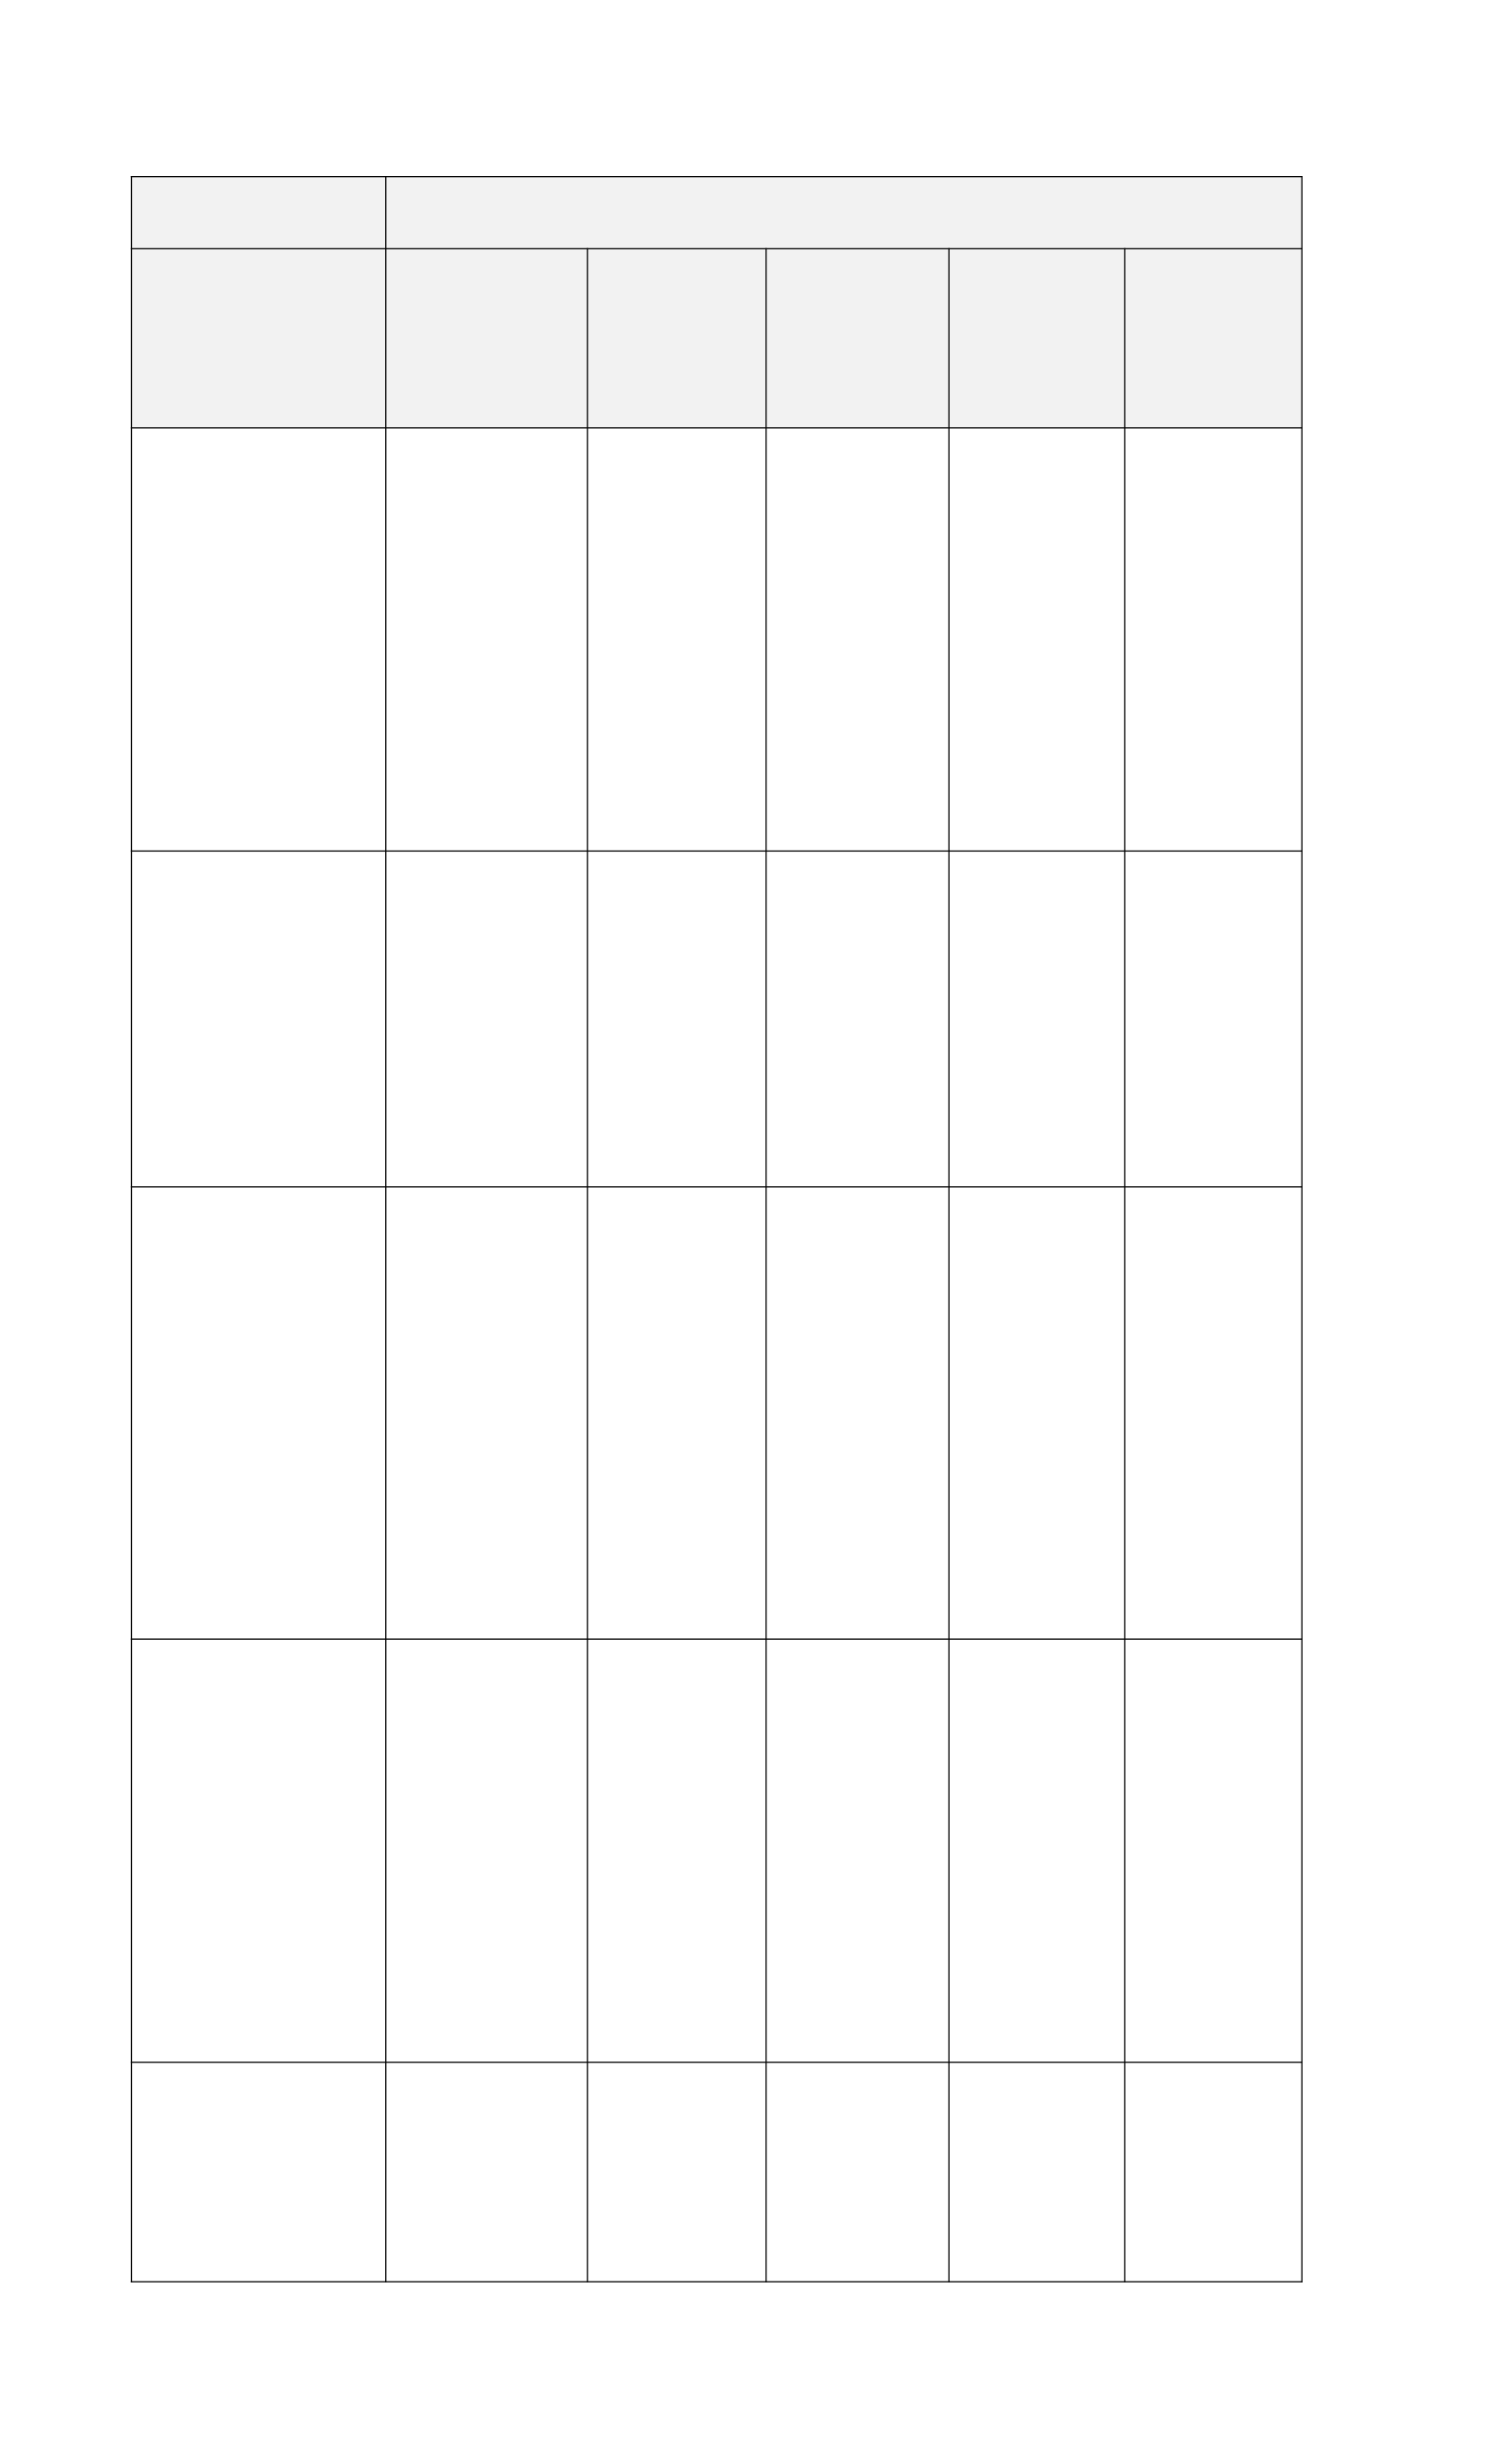
Criteria Unacceptable
Below 60% F
Meets
Minimum
Expectations
60-69% D
Fair
70-79% C
Proficient
80-89% B
Exemplary
90-100% A
1. Explain the basic
primary tasks, ongoing
evaluations, and major
policy and procedural
changes that would be
needed to perform as
the BC lead / manager.
Weight: 20%
Did not submit or
incompletely
explained the
basic primary
tasks, ongoing
evaluations, and
major policy and
procedural
changes that
would be needed
to perform as the
BC lead /
manager.
Insufficiently
explained the
basic primary
tasks, ongoing
evaluations,
and major
policy and
procedural
changes that
would be
needed to
perform as the
BC lead /
manager.
Partially
explained the
basic primary
tasks, ongoing
evaluations,
and major
policy and
procedural
changes that
would be
needed to
perform as the
BC lead /
manager.
Satisfactorily
explained the
basic primary
tasks, ongoing
evaluations,
and major
policy and
procedural
changes that
would be
needed to
perform as the
BC lead /
manager.
Thoroughly
explained the
basic primary
tasks, ongoing
evaluations,
and major
policy and
procedural
changes that
would be
needed to
perform as the
BC lead /
manager.
2. Provide insight on
how to plan the
presentation to garner
management and
Board buy-in for those
who are skeptical.
Weight: 20%
Did not submit or
incompletely
provided insight
on how to plan
the presentation
to garner
management and
Board buy-in for
those who are
skeptical.
Insufficiently
provided
insight on how
to plan the
presentation to
garner
management
and Board buy-
in for those
who are
skeptical.
Partially
provided insight
on how to plan
the
presentation to
garner
management
and Board buy-
in for those who
are skeptical.
Satisfactorily
provided
insight on how
to plan the
presentation to
garner
management
and Board
buy-in for
those who are
skeptical.
Thoroughly
provided
insight on how
to plan the
presentation to
garner
management
and Board buy-
in for those
who are
skeptical.
3. Discuss the first four
(4) high-level activities
that would be
necessary in starting
this initiative in the
right direction and
describe the potential
pitfalls of each.
Weight: 25%
Did not submit or
incompletely
discussed the
first four (4) high-
level activities
that would be
necessary in
starting this
initiative in the
right direction and
did not submit or
incompletely
described the
potential pitfalls
of each.
Insufficiently
discussed the
first four (4)
high-level
activities that
would be
necessary in
starting this
initiative in the
right direction
and
insufficiently
described the
potential pitfalls
of each.
Partially
discussed the
first four (4)
high-level
activities that
would be
necessary in
starting this
initiative in the
right direction
and partially
described the
potential pitfalls
of each.
Satisfactorily
discussed the
first four (4)
high-level
activities that
would be
necessary in
starting this
initiative in the
right direction
and
satisfactorily
described the
potential
pitfalls of each.
Thoroughly
discussed the
first four (4)
high-level
activities that
would be
necessary in
starting this
initiative in the
right direction
and thoroughly
described the
potential
pitfalls of each.
4. Speculate on the
most comprehensive
and / or critical
challenge(s) in the
infancy of this initiative
and explain how to
overcome that
challenge(s).
Weight: 20%
Did not submit or
incompletely
speculated on the
most
comprehensive
and / or critical
challenge(s) in
the infancy of this
initiative and did
not submit or
incompletely
explained how to
overcome that
challenge(s).
Insufficiently
speculated on
the most
comprehensive
and / or critical
challenge(s) in
the infancy of
this initiative
and
insufficiently
explained how
to overcome
that
challenge(s).
Partially
speculated on
the most
comprehensive
and / or critical
challenge(s) in
the infancy of
this initiative
and partially
explained how
to overcome
that
challenge(s).
Satisfactorily
speculated on
the most
comprehensive
and / or critical
challenge(s) in
the infancy of
this initiative
and
satisfactorily
explained how
to overcome
that
challenge(s).
Thoroughly
speculated on
the most
comprehensive
and / or critical
challenge(s) in
the infancy of
this initiative
and thoroughly
explained how
to overcome
that
challenge(s).
5. 3 references
Weight: 5%
No references
provided
Does not meet
the required
number of
references; all
references
poor quality
choices.
Does not meet
the required
number of
references;
some
references poor
quality choices.
Meets number
of required
references; all
references
high quality
choices.
Exceeds
number of
required
references; all
references
high quality
choices.
6. Clarity, writing
mechanics, and
formatting
requirements
Weight: 10%
More than 8
errors present
7-8 errors
present
5-6 errors
present
3-4 errors
present
0-2 errors
present
1. Develop a comprehensive cybersecurity strategy for the biotechnology and life sciences
company. Discuss measures to secure genetic research data, protect intellectual property
related to pharmaceutical development, and prevent cyber threats to critical life sciences
infrastructure. Address the unique challenges associated with managing sensitive health data
and complying with healthcare industry regulations.
Developing a comprehensive cybersecurity strategy for a biotechnology and life sciences company
involves addressing the specific challenges associated with managing sensitive genetic research data,
protecting intellectual property related to pharmaceutical development, and preventing cyber threats to
critical life sciences infrastructure. Additionally, compliance with healthcare industry regulations and
safeguarding sensitive health data is crucial. Here's a step-by-step approach to creating such a strategy:
Risk Assessment and Asset Inventory:
Conduct a thorough risk assessment to identify potential threats and vulnerabilities.
Create an inventory of all critical assets, including genetic research data, intellectual property, and life
sciences infrastructure.
Data Classification and Encryption:
Classify data based on its sensitivity and importance.
Implement encryption for both data in transit and data at rest to protect against unauthorized access.
Access Controls and Identity Management:
Implement robust access controls to ensure that only authorized personnel have access to sensitive data.
Utilize strong identity management practices, such as multi-factor authentication, to enhance access
security.
Network Security:
Segment the network to isolate critical systems and data from non-essential areas.
Employ firewalls, intrusion detection/prevention systems, and regular network monitoring to detect and
mitigate suspicious activities.
Phishing Awareness and Training:
Conduct regular training programs to educate employees on the risks of phishing attacks.
Implement email filtering solutions to detect and prevent phishing attempts.

Endpoint Security:
Ensure that all endpoints (computers, mobile devices) are equipped with up-to-date antivirus and anti-
malware software.
Implement device management controls to monitor and secure all endpoints.
Incident Response Plan:
Develop a comprehensive incident response plan outlining the steps to take in case of a cybersecurity
incident.
Regularly test and update the plan to ensure its effectiveness.
Intellectual Property Protection:
Implement data loss prevention (DLP) solutions to monitor and control the transfer of intellectual
property outside the organization.
Utilize digital rights management (DRM) tools to protect proprietary information.
Supply Chain Security:
Assess and enhance the security posture of third-party vendors and partners involved in the supply
chain.
Establish contractual obligations for security standards in vendor agreements.
Regulatory Compliance:
Stay informed about healthcare industry regulations (e.g., HIPAA, GDPR) and ensure compliance.
Regularly audit and update security measures to align with changing regulatory requirements.
Employee Awareness and Training:
Educate employees on the importance of cybersecurity and their role in safeguarding sensitive
information.
Conduct regular security awareness training sessions.
Continuous Monitoring and Auditing:
Implement continuous monitoring tools to detect and respond to security incidents in real-time.
Conduct regular internal and external audits to assess the effectiveness of cybersecurity measures.
Secure Software Development Practices:
Integrate security into the software development lifecycle to identify and address vulnerabilities in
applications.
Insurance and Legal Counsel:

Consider cybersecurity insurance to mitigate financial risks associated with potential breaches.
Consult legal counsel to ensure that the cybersecurity strategy complies with relevant laws and
regulations.
Collaboration with Industry Peers:
Participate in information-sharing initiatives within the biotechnology and life sciences industry to stay
updated on emerging threats and best practices.
Remember, cybersecurity is an ongoing process, and it's essential to regularly review and update the
strategy to adapt to evolving threats and technologies.
16. Data Backup and Recovery:
Regularly back up critical data, including genetic research and intellectual property, and ensure that
backups are stored securely.
Develop and test a robust data recovery plan to minimize downtime in case of a cyber incident.
17. Secure Collaboration Tools:
Implement secure communication and collaboration tools to facilitate information sharing among
researchers and teams.
Encrypt communications and data shared through these platforms to maintain confidentiality.
18. IoT Security for Laboratory Equipment:
Secure Internet of Things (IoT) devices used in laboratories by changing default passwords, applying
patches promptly, and segmenting IoT networks.
Monitor IoT devices for any unusual behavior that may indicate a security compromise.
19. Biometric Security Measures:
Implement biometric authentication for accessing sensitive systems and laboratories.
Biometric measures, such as fingerprint or retina scans, can add an extra layer of security to access
controls.
20. Blockchain for Data Integrity:
Explore the use of blockchain technology to ensure the integrity and immutability of genetic research
data.
Implementing blockchain can provide a transparent and secure way to track and verify changes made to
research data.
21. Cloud Security Best Practices:

If utilizing cloud services, apply best practices for cloud security, including strong authentication,
encryption, and continuous monitoring.
Ensure that cloud service providers comply with relevant industry regulations.
22. Physical Security Measures:
Secure physical access to laboratories, data centers, and other critical infrastructure.
Install surveillance systems and implement access controls to monitor and restrict entry.
23. Red Team Testing:
Conduct periodic red team exercises to simulate cyber-attacks and identify potential weaknesses in the
cybersecurity defenses.
Use the findings to continually improve the security posture.
24. International Collaboration and Threat Intelligence Sharing:
Engage in international collaborations to share threat intelligence and best practices with other
organizations in the life sciences and biotechnology sectors.
Stay informed about global cyber threats that could impact the industry.
25. Secure DevOps Practices:
Integrate security into the DevOps processes to identify and address vulnerabilities early in the
development lifecycle.
Utilize automated security testing tools to ensure the security of code and applications.
26. Audit Trail and Monitoring for Compliance:
Implement robust audit trail capabilities to track and monitor access to sensitive data for compliance
purposes.
Regularly review audit logs to detect and respond to any unauthorized access.
27. Crisis Communication Plan:
Develop a crisis communication plan to effectively communicate with internal and external stakeholders
in the event of a cybersecurity incident.
Establish clear communication channels and messaging protocols.
28. Employee Offboarding Security Protocols:
Implement thorough security protocols when employees leave the company to prevent unauthorized
access after their departure.
Revoke access credentials promptly and conduct exit interviews to address potential insider threats.

29. Continuous Training and Simulation:
Regularly conduct cybersecurity training sessions for employees and simulate various cyber threat
scenarios to ensure preparedness.
Keep the workforce informed about the latest cyber threats and attack techniques.
30. Government and Law Enforcement Collaboration:
Collaborate with government agencies and law enforcement to report and investigate cyber incidents.
Stay abreast of any relevant threat intelligence provided by government cybersecurity agencies.
Remember that cybersecurity is a dynamic field, and a proactive and adaptive approach is crucial to
staying ahead of evolving threats. Regularly reassess the cybersecurity strategy and update it to address
emerging risks and technologies in the biotechnology and life sciences industry.
31. Cybersecurity Training for Researchers:
Provide specialized cybersecurity training for researchers, emphasizing the unique risks associated with
handling genetic and pharmaceutical data.
Foster a culture of security awareness within research teams.
32. Secure Software Development Lifecycle (SDLC):
Integrate security into the entire software development lifecycle to identify and mitigate vulnerabilities
at every stage.
Conduct regular code reviews and security assessments during development.
33. International Data Transfers:
If the company operates globally, ensure compliance with international data transfer regulations.
Utilize encryption and secure data transfer mechanisms when moving data across borders.
34. Secure Collaboration with External Partners:
Establish secure channels for collaboration with external research partners, ensuring the confidentiality
and integrity of shared data.
Use secure file-sharing platforms and employ encryption for data in transit.
35. Biological Threats and Biosecurity:
Develop a biosecurity plan to protect against biological threats, both physical and cyber.
Implement access controls and monitoring systems for biological laboratories and facilities.
36. Simulation and Red Teaming for Physical Security:

Conduct physical security simulations and red teaming exercises to identify vulnerabilities in the
company's physical infrastructure.
Evaluate the effectiveness of security measures in place, including surveillance systems and access
controls.
37. Zero Trust Security Model:
Implement a zero-trust security model, where trust is never assumed, and strict access controls are
enforced.
Authenticate and authorize every device and user attempting to connect to the network, regardless of
their location.
38. Threat Hunting and Continuous Monitoring:
Proactively hunt for potential threats within the network by utilizing threat intelligence and behavioral
analytics.
Implement continuous monitoring to detect anomalies and potential security incidents.
39. Regulatory Liaison Officer:
Designate a regulatory liaison officer responsible for staying informed about changes in healthcare
regulations and ensuring compliance.
Foster a collaborative relationship with regulatory bodies to address cybersecurity concerns.
40. Biometric Data Privacy Considerations:
If biometric data is utilized for authentication, ensure compliance with data privacy regulations.
Implement measures to protect the privacy and security of biometric information.
Gain insights into the tactics and techniques used by adversaries through the analysis of honeypot data.
These advanced considerations can help a biotechnology and life sciences company build a highly
resilient and adaptive cybersecurity strategy. Keep in mind that staying ahead of cyber threats requires
continuous innovation and a proactive approach to security. Regularly reassess the strategy to
incorporate emerging technologies and address evolving risks.
2. Evaluate the security of the company's genetic research and laboratory systems. Recommend
measures to secure these systems, prevent unauthorized access, and ensure the confidentiality
and integrity of genetic research data. Discuss the importance of compliance with
biotechnology and healthcare industry cybersecurity standards and regulations.

Securing a company's genetic research and laboratory systems is crucial to protect sensitive data, ensure
research integrity, and comply with industry regulations. Here are several recommendations to enhance
the security of genetic research and laboratory systems:
Access Control:
Implement strict access controls to limit the number of individuals who can access the genetic research
and laboratory systems.
Use role-based access control (RBAC) to assign permissions based on job roles, ensuring that
individuals have the necessary access for their specific responsibilities.
Regularly review and update access permissions, revoking access for employees who no longer require
it.
Authentication and Authorization:
Enforce strong authentication mechanisms, such as multi-factor authentication (MFA), to prevent
unauthorized access.
Utilize strong encryption for user credentials to protect against credential theft.
Implement robust authorization processes to ensure that users can only access the data and systems
relevant to their roles.
Data Encryption:
Encrypt sensitive genetic research data both in transit and at rest to protect it from unauthorized access
and tampering.
Employ end-to-end encryption to secure communications between different components of the
laboratory systems.
Network Security:
Segment the network to isolate the genetic research and laboratory systems from other corporate
networks, reducing the attack surface.
Regularly update and patch network infrastructure components to address vulnerabilities and ensure a
secure network environment.
Regular Security Audits and Penetration Testing:
Conduct regular security audits and penetration testing to identify and address vulnerabilities in the
genetic research and laboratory systems.
Engage with third-party security experts to perform comprehensive assessments and provide insights
into potential security weaknesses.
Incident Response Plan:

Develop and regularly update an incident response plan to address security incidents promptly and
effectively.
Conduct regular drills and simulations to ensure that the response team is well-prepared to handle
various security incidents.
Compliance with Industry Regulations:
Stay informed about and comply with relevant biotechnology and healthcare industry cybersecurity
standards and regulations.
Regularly assess and update security measures to align with evolving compliance requirements.
Include security requirements in vendor contracts and agreements to hold them accountable for
maintaining the security of their products.
Monitoring and Logging:
Implement robust monitoring tools to detect and alert on suspicious activities within the genetic research
and laboratory systems.
Maintain comprehensive logs of system activities for forensic analysis and auditing purposes.
Secure Data Transmission:
Use secure communication protocols (e.g., TLS) for transmitting genetic research data to prevent
interception and eavesdropping.
Consider implementing virtual private networks (VPNs) for secure data transfer between different
locations or collaborating institutions.
Biometric Access Control:
In high-security areas, consider implementing biometric access controls, such as fingerprint or retina
scans, to ensure only authorized personnel gain physical access to sensitive laboratories and equipment.
Disaster Recovery and Business Continuity:
Develop and regularly test a comprehensive disaster recovery plan to ensure minimal disruption in case
of system failures or catastrophic events.
Consider redundant systems and offsite data backups to enhance business continuity.
Regular Security Training for Researchers:
Researchers should undergo specialized security training to understand the importance of protecting
sensitive genetic data and complying with security protocols.
Secure Collaborative Research Practices:
Establish secure methods for collaborative research, including secure file-sharing platforms and
encrypted communication tools to protect shared data.

Regulatory Compliance Audits:
Conduct regular internal audits to ensure ongoing compliance with industry regulations.
Engage with external auditors to perform independent assessments and verify compliance with
applicable standards.
Crisis Communication Plan:
Develop a communication plan for addressing security incidents, ensuring transparency with
stakeholders, and mitigating reputational damage.
Technological Trends and Emerging Threats:
Stay informed about the latest technological trends and emerging cybersecurity threats in the
biotechnology and healthcare sectors.
Proactively adapt security measures to address new challenges posed by evolving technologies and
threats.
Security Information and Event Management (SIEM):
Implement SIEM solutions to aggregate and analyze security event data in real-time, enabling rapid
detection and response to security incidents.
Legal and Ethical Considerations:
Ensure that all security measures align with legal and ethical considerations, especially when dealing
with human genetic data, to protect individual privacy and maintain ethical research practices.
Remember, cybersecurity is an ongoing process, and a holistic approach is necessary. Regularly
reassessing and updating security measures, staying informed about industry developments, and
fostering a security-centric culture among employees are key elements in maintaining a robust security
posture for genetic research and laboratory systems.
Insider Threat Mitigation:
Implement strategies to mitigate insider threats, which could arise from employees, researchers, or
collaborators.
Conduct periodic background checks on personnel with access to sensitive data.
Monitor user activities for unusual behavior that might indicate malicious intent.
Red Team Exercises:
Conduct red team exercises where security professionals simulate real-world cyberattacks to identify
vulnerabilities and weaknesses in the security infrastructure.
Use the findings to improve incident response capabilities and enhance overall security.
Supply Chain Security:

Assess and ensure the security of the entire supply chain, from the procurement of laboratory equipment
to third-party services and software.
Verify that suppliers adhere to security standards and regularly update their products to address
vulnerabilities.
Incident Documentation and Analysis:
Document and analyze security incidents thoroughly to understand the root causes and improve incident
response procedures.
Use incident data to refine security policies and enhance preventive measures.
International Data Transfer Compliance:
If conducting international research, be mindful of data transfer regulations and ensure compliance with
international data protection laws.
Implement data anonymization and pseudonymization techniques to protect the privacy of research
subjects.
Continuous Security Training:
Provide ongoing security training for all employees, including updates on the latest cybersecurity threats
and best practices.
Foster a culture of cybersecurity awareness to encourage proactive reporting of security concerns.
Zero Trust Security Model:
Adopt a Zero Trust security model, where trust is never assumed, and verification is required from
everyone trying to access resources.
This model helps prevent lateral movement of attackers within the network.
Blockchain for Data Integrity:
Explore the use of blockchain technology to enhance the integrity and traceability of genetic research
data.
Blockchain can provide an immutable and transparent record of data transactions.
Security Metrics and Key Performance Indicators (KPIs):
Establish security metrics and KPIs to measure the effectiveness of security controls.
Regularly review and analyze these metrics to identify trends, potential weaknesses, and areas for
improvement.
Secure DevOps Practices:

If employing DevOps practices in software development, integrate security measures into the
development lifecycle.
Implement automated security testing tools to identify and fix vulnerabilities early in the development
process.
Cloud Security Best Practices:
If utilizing cloud services for genetic research, adhere to best practices for cloud security.
Implement robust identity and access management, encryption, and regular security assessments for
cloud-based systems.
Threat Intelligence Sharing:
Engage in information sharing and collaboration with other research institutions, industry partners, and
cybersecurity organizations to stay informed about emerging threats.
Participate in threat intelligence sharing platforms to exchange information about potential risks.
Biometric Data Protection:
Implement strict controls and encryption mechanisms for the storage and processing of biometric data,
ensuring compliance with privacy regulations.
Collaboration with Cybersecurity Researchers:
Collaborate with cybersecurity researchers and experts to identify and address potential vulnerabilities in
genetic research and laboratory systems.
Engage in responsible disclosure practices to address any security issues discovered.
Quantum-Safe Cryptography:
Anticipate the future threat of quantum computing by considering the adoption of quantum-safe
cryptographic algorithms to protect sensitive data in the long term.
Regulatory Advocacy and Participation:
Actively participate in industry forums, conferences, and regulatory discussions to stay abreast of
changes in regulations and contribute to the development of security standards.
Remember that security is a dynamic and evolving field, and staying proactive is key to adapting to
emerging threats. Regularly reassess the security posture, engage in ongoing education, and
continuously refine security measures to address the evolving landscape of genetic research and
laboratory systems.
AI and Machine Learning Security:
If employing AI or machine learning in genetic research, ensure the security of these algorithms and
models.

Implement security measures to prevent adversarial attacks and unauthorized access to machine learning
systems.
Quantified Risk Assessment:
Conduct quantified risk assessments to prioritize security efforts based on potential impact and
likelihood of security incidents.
Use risk assessments to allocate resources effectively and focus on the most critical security areas.
Secure Data Disposal:
Establish protocols for the secure disposal of data storage devices and laboratory equipment to prevent
unauthorized access to sensitive information.
Ensure compliance with data disposal regulations and standards.
International Collaboration Considerations:
When collaborating internationally, understand and adhere to data protection laws in different countries.
Establish clear data sharing agreements that address security and privacy concerns.
Secure Mobile Devices:
If researchers use mobile devices for data access, implement strong mobile device management (MDM)
policies.
Encrypt data on mobile devices, enforce strong authentication, and enable remote wipe capabilities in
case of loss or theft.
Biological Threats and Lab Biosafety:
Integrate cybersecurity practices with biosafety protocols to address both cyber threats and potential
biological threats.
Establish measures to prevent unauthorized physical access to laboratory facilities.
Security Information Sharing Platforms:
Participate in industry-specific security information sharing platforms to exchange threat intelligence
with peers and stay informed about emerging threats.
Ethical Hacking and Bug Bounty Programs:
Consider implementing ethical hacking programs or bug bounty programs to allow external security
researchers to identify and report vulnerabilities.
Establish clear guidelines for responsible disclosure to encourage collaboration with the security
community.
Employee Behavioral Analytics:

Leverage behavioral analytics to monitor and identify anomalous behavior among employees.
This can help detect potential insider threats or compromised accounts based on deviations from normal
user behavior.
Privacy-Preserving Technologies:
Explore privacy-preserving technologies such as homomorphic encryption or federated learning to
conduct collaborative research without compromising individual privacy.
Implement anonymization techniques to de-identify sensitive data.
International Standards and Frameworks:
Familiarize yourself with international cybersecurity standards and frameworks relevant to genetic
research and healthcare, such as ISO/IEC 27001, NIST Cybersecurity Framework, or ENISA guidelines.
Blockchain for Consent Management:
Utilize blockchain for secure and transparent consent management, ensuring that individuals' consent for
genetic research is recorded and cannot be tampered with.
User Awareness Training for Social Engineering:
Provide training on social engineering tactics, as researchers may be targeted through phishing or other
social engineering methods.
Conduct simulated phishing exercises to test and reinforce awareness.
Legal Review of Security Measures:
Regularly review and update security measures in collaboration with legal experts to ensure alignment
with evolving laws and regulations.
Securing Research Protocols:
Implement security controls for research protocols to ensure the integrity of experiments and the
authenticity of research results.
Protect against manipulation of experimental data.
Environmental Controls:
Implement environmental controls to safeguard laboratory equipment and systems from physical threats,
such as temperature fluctuations or power outages.
Cross-Functional Collaboration:
Foster collaboration between IT, security, legal, compliance, and research teams to ensure a
comprehensive and unified approach to security.
Securing IoT Devices:

If using Internet of Things (IoT) devices in laboratories, apply security measures to protect against
potential vulnerabilities associated with these devices.
Data Sovereignty:
Understand and adhere to data sovereignty requirements, especially when conducting research in
multiple jurisdictions with different data protection laws.
Public Relations Strategy:
Develop a public relations strategy to address potential security incidents, ensuring transparent
communication with the public, research participants, and stakeholders.
Continuous improvement and adaptation to new challenges are essential in the ever-evolving field of
cybersecurity. Regularly assess the security landscape, embrace new technologies responsibly, and
remain vigilant to protect genetic research and laboratory systems effectively.
3. Assess the security of the company's pharmaceutical development systems, including drug
formulation databases and research collaboration platforms. Propose strategies to secure these
systems, prevent unauthorized access, and ensure the confidentiality and integrity of
pharmaceutical development data. Discuss the importance of secure coding practices and
compliance with industry-specific cybersecurity standards.
Securing pharmaceutical development systems, especially drug formulation databases and research
collaboration platforms, is crucial to protect sensitive data, intellectual property, and ensure the integrity
of research efforts. Here are strategies and considerations for enhancing the security of these systems:
Access Control and Authentication:
Implement strong access controls to limit user access based on roles and responsibilities.
Use multi-factor authentication (MFA) to add an extra layer of security.
Regularly review and update user access privileges.
Encryption:
Encrypt sensitive data both in transit and at rest to prevent unauthorized access.
Utilize strong encryption algorithms to protect the confidentiality of pharmaceutical development data.
Regular Auditing and Monitoring:
Implement logging and monitoring systems to track user activities and detect any suspicious behavior.
Conduct regular audits to ensure compliance with security policies and identify potential vulnerabilities.
Network Security:

Employ firewalls, intrusion detection and prevention systems to safeguard the network.
Segment the network to isolate critical systems from less secure areas.
Secure Coding Practices:
Train developers on secure coding practices to minimize vulnerabilities in the software.
Regularly conduct code reviews and static/dynamic analysis to identify and rectify security flaws.
Incident Response Plan:
Develop and regularly test an incident response plan to ensure a timely and effective response to security
incidents.
Define roles and responsibilities for incident response team members.
Regular Software Updates and Patching:
Keep all software, including operating systems, databases, and applications, up-to-date with the latest
security patches.
Regularly perform vulnerability assessments to identify and address potential weaknesses.
Collaboration Platform Security:
Secure communication channels within collaboration platforms using encryption.
Ensure proper user authentication and access controls for collaborative research tools.
Employee Training and Awareness:
Conduct regular training sessions to educate employees about security best practices.
Raise awareness about phishing attacks and social engineering tactics.
Compliance with Industry Standards:
Adhere to industry-specific cybersecurity standards and regulations, such as Good Automated
Manufacturing Practice (GAMP) and standards set by regulatory bodies like the FDA.
Regularly assess compliance and update security measures accordingly.
Data Backup and Recovery:
Implement a robust data backup and recovery plan to prevent data loss due to accidental deletion or
malicious activities.
Regularly test data restoration processes.
Vendor Security:
Assess and ensure the security measures taken by third-party vendors providing services or tools for
pharmaceutical development.

Include security clauses in contracts with vendors to enforce security standards.
In conclusion, a comprehensive approach that combines technical measures, employee training, and
adherence to industry standards is essential to secure pharmaceutical development systems effectively.
Regular testing, monitoring, and adaptation of security measures are key components of maintaining a
robust cybersecurity posture in this highly sensitive industry.
Secure Development Life Cycle (SDLC):
Threat Modeling: Conduct threat modeling sessions to identify potential security threats and
vulnerabilities in the early stages of the development life cycle. This helps in designing security controls
proactively.
Code Review: Regularly review code for security vulnerabilities and compliance with coding standards.
Automated tools and manual reviews by experienced security professionals can identify and address
potential issues.
Security Training: Provide ongoing security training for developers, emphasizing secure coding
practices and awareness of common vulnerabilities.
Data Protection and Privacy:
Data Masking/Anonymization: Implement data masking or anonymization techniques in non-production
environments to protect sensitive information during testing and development.
Data Classification: Classify pharmaceutical development data based on sensitivity. Apply stricter
controls and encryption to highly confidential information.
Privacy by Design: Incorporate privacy considerations into the design and architecture of systems,
ensuring that data protection is an integral part of the development process.
Cloud Security:
Cloud Access Security Broker (CASB): If using cloud services, employ CASBs to monitor and control
data transfers between on-premises and cloud environments, ensuring data security and compliance.
Identity and Access Management (IAM): Implement robust IAM policies to manage user access and
permissions in cloud environments.
Cloud Compliance: Ensure compliance with industry regulations and standards specific to cloud
security. Regularly review and update cloud security configurations.
Research Collaboration Platforms:
Secure File Sharing: Implement secure file sharing mechanisms with encryption and access controls to
prevent unauthorized access to research data.
Collaboration Policies: Establish clear policies for data sharing and collaboration. Define roles and
responsibilities for collaborators and ensure adherence to security protocols.

Secure Communication Channels: Use secure communication channels such as encrypted messaging
and virtual private networks (VPNs) for collaborative discussions and data sharing.
Regulatory Compliance:
FDA Compliance: Ensure that security measures align with the FDA's guidelines for computer system
validation, data integrity, and electronic records.
GxP Compliance: Adhere to Good Automated Manufacturing Practice (GAMP) standards, ensuring that
systems are validated, and data integrity is maintained throughout the development life cycle.
Periodic Audits and Assessments: Conduct regular internal and external audits to assess compliance
with industry regulations and standards.
Continuous Improvement:
Incident Response Drills: Conduct regular incident response drills to test the effectiveness of the
response plan and identify areas for improvement.
Threat Intelligence Integration: Stay informed about the latest cybersecurity threats and vulnerabilities
specific to the pharmaceutical industry. Integrate threat intelligence into security measures.
Feedback Loop: Establish a feedback loop for continuous improvement by analyzing security incidents,
conducting post-incident reviews, and updating security policies accordingly.
Securing pharmaceutical development systems is an ongoing process that requires a combination of
technological solutions, organizational practices, and a proactive mindset. By integrating security into
every phase of the development life cycle and staying vigilant against evolving threats, organizations
can better safeguard their critical pharmaceutical data and intellectual property.
Insider Threat Mitigation:
Employee Awareness Programs: Regularly educate employees about the risks associated with insider
threats. Encourage a culture of security awareness to help prevent unintentional security breaches.
User Behavior Analytics (UBA): Implement UBA tools to monitor and analyze user behavior for
anomalies. This can help detect potential insider threats or compromised accounts.
Privileged Access Management (PAM): Implement PAM solutions to tightly control and monitor access
to critical systems and data, especially privileged accounts with elevated permissions.
Physical Security:
Data Center Security: If applicable, ensure that physical data centers housing pharmaceutical
development systems are secure. Implement access controls, surveillance, and environmental controls to
protect against physical threats.
Endpoint Security: Implement endpoint protection measures, including device encryption, antivirus
software, and endpoint detection and response (EDR) solutions to safeguard against threats originating
from individual devices.

Threat Intelligence and Information Sharing:
Participate in Information Sharing Communities: Engage with industry-specific information-sharing
communities to stay informed about emerging threats and vulnerabilities. Collaborate with peers to
enhance collective cybersecurity defenses.
Continuous Monitoring: Implement continuous monitoring of external threats and vulnerabilities
relevant to the pharmaceutical industry. Regularly update security controls based on the latest threat
intelligence.
Disaster Recovery and Business Continuity:
Regular Testing of Backup and Recovery Processes: Periodically test data backup and recovery
processes to ensure that critical pharmaceutical development data can be restored in case of data loss or
a cyber incident.
Business Impact Analysis (BIA): Conduct BIAs to identify critical systems and processes. Develop and
maintain a comprehensive business continuity plan to minimize downtime and data loss in the event of
disruptions.
Secure Supply Chain:
Vendor Risk Management: Assess and manage the cybersecurity risks associated with third-party
vendors. Perform due diligence on the security practices of suppliers and ensure they adhere to similar
standards and protocols.
Secure Development Practices for Third-Party Applications: If using third-party applications or
software, ensure that they follow secure coding practices and adhere to industry-specific security
standards.
International Standards and Frameworks:
ISO/IEC 27001: Consider adopting the ISO/IEC 27001 standard for information security management
systems. This internationally recognized framework provides a systematic approach to managing and
securing information.
NIST Cybersecurity Framework: Implement the NIST Cybersecurity Framework to assess and enhance
the security posture of pharmaceutical development systems. It provides a risk-based approach to
cybersecurity.
Incident Communication and Coordination:
Communication Plan: Develop a clear and comprehensive communication plan to inform stakeholders,
including employees, customers, and regulatory bodies, in the event of a security incident.
Coordination with Authorities: Establish protocols for cooperating with law enforcement and relevant
regulatory authorities in the event of a significant security incident.
Ethical Hacking and Red Team Exercises:

Penetration Testing: Conduct regular penetration testing to identify vulnerabilities in pharmaceutical
development systems. Address and remediate the identified issues to improve overall security.
Red Team Exercises: Engage in red team exercises where external security experts simulate real-world
cyber-attacks to evaluate the effectiveness of security measures and response capabilities.
Documentation and Policy Management:
Security Policies and Procedures: Develop and maintain comprehensive security policies and procedures
tailored to the pharmaceutical industry. Regularly review and update these documents to reflect changes
in technology and threat landscapes.
Employee Acknowledgment: Ensure that employees acknowledge their understanding of security
policies and procedures, emphasizing the importance of compliance.
Long-Term Security Planning:
Technology Roadmap: Develop a technology roadmap that includes long-term security planning.
Consider future technologies, industry trends, and evolving cybersecurity threats in the pharmaceutical
sector.
Regular Security Reviews: Periodically review and update the security strategy based on changes in the
pharmaceutical landscape and advancements in cybersecurity.
By implementing these additional considerations and best practices, pharmaceutical companies can
establish a robust and adaptive cybersecurity framework to protect their development systems,
intellectual property, and sensitive data. Continuous improvement, collaboration, and a proactive
approach are key elements in maintaining a resilient security posture in the evolving landscape of
cybersecurity threats.
Threat Hunting and Advanced Analytics:
Threat Hunting Teams: Establish dedicated threat hunting teams to actively search for and identify
advanced threats within the pharmaceutical development systems. This involves proactively seeking out
anomalies and potential security incidents.
Advanced Analytics and Machine Learning: Implement advanced analytics and machine learning tools
to analyze large datasets for patterns indicative of security threats. These technologies can help identify
subtle and sophisticated attacks that may go unnoticed with traditional security measures.
Zero Trust Architecture:
Zero Trust Principles: Adopt a Zero Trust security architecture, where trust is never assumed, and
verification is required from everyone, both inside and outside the organization. This approach involves
continuous verification of user identity and device security status.
Micro-Segmentation: Implement micro-segmentation to divide the network into smaller, isolated
segments. This limits lateral movement for attackers, even if they gain access to one segment.

Blockchain for Data Integrity:
Blockchain Technology: Explore the use of blockchain technology for ensuring the integrity of
pharmaceutical development data. Blockchain can provide a tamper-proof and transparent record of
transactions and changes, enhancing data trustworthiness.
Smart Contracts: Utilize smart contracts within a blockchain to automate and enforce security policies,
ensuring that data access and modifications adhere to predefined rules.
Quantum-Safe Cryptography:
Post-Quantum Cryptography: Given the potential future threat posed by quantum computing to
traditional cryptographic methods, consider adopting post-quantum cryptography algorithms to protect
sensitive data.
Quantum Key Distribution (QKD): Explore quantum key distribution as a method for secure
communication. QKD leverages the principles of quantum mechanics to enable secure key exchange
between parties.
Cyber Threat Intelligence Sharing:
Private and Public Threat Intelligence Sharing: Engage in both private and public threat intelligence
sharing forums. Collaborate with other pharmaceutical companies, industry associations, and
government agencies to stay ahead of emerging threats.
Automated Threat Intelligence Integration: Integrate automated tools to consume and analyze threat
intelligence feeds. This ensures that the organization is continuously updated on the latest threat
landscape.
DevSecOps Integration:
DevSecOps Practices: Integrate security into the DevOps process from the beginning (DevSecOps). This
involves automated security testing, continuous monitoring, and collaboration between development,
operations, and security teams throughout the development life cycle.
Container Security: If using containerized environments, ensure the security of container images,
orchestration platforms, and the overall containerized infrastructure.
Quantum-Safe Communication:
Quantum Key Distribution (QKD): Consider implementing QKD for securing communication channels.
QKD provides a quantum-resistant method for secure key exchange, protecting against potential future
advancements in quantum computing.
Post-Quantum Secure Protocols: Explore the use of post-quantum secure communication protocols to
protect against quantum-based attacks on current encryption standards.
Threat Simulation Exercises:

Red Team Operations: Conduct advanced red team exercises simulating sophisticated cyber-attacks.
This involves using real-world tactics, techniques, and procedures to evaluate the effectiveness of
security measures.
Purple Team Collaboration: Foster collaboration between red and blue teams (security defenders). This
ensures a holistic approach to security testing, with the red team simulating attacks, and the blue team
defending against them.
Continuous Compliance Monitoring:
Automated Compliance Tools: Utilize automated tools to continuously monitor and assess compliance
with industry-specific regulations and standards. This helps in ensuring that pharmaceutical
development systems adhere to the necessary cybersecurity requirements.
Regulatory Reporting: Establish streamlined processes for reporting and documenting compliance status
to regulatory authorities. This includes maintaining records of security measures, audits, and risk
assessments.
Quantum-Safe Encryption:
Post-Quantum Encryption Algorithms: Research and implement post-quantum encryption algorithms to
protect sensitive data. As quantum computing capabilities advance, traditional encryption methods may
become vulnerable, making it essential to transition to quantum-safe alternatives.
Encryption Key Management: Enhance encryption key management practices to ensure the secure
generation, storage, and distribution of cryptographic keys, especially in a post-quantum encryption
environment.
Continued investment in cutting-edge technologies, collaboration with the broader cybersecurity
community, and a commitment to staying ahead of emerging threats are essential for pharmaceutical
companies looking to maintain a high level of security for their development systems. Regular
assessments, updates to security protocols, and a proactive approach to cybersecurity will contribute to
the resilience of the overall security posture.
4. Propose measures to secure communication channels within the biotechnology and life sciences
company, especially those involving sensitive information related to genetic research findings,
pharmaceutical development, and patient health data. Discuss strategies for secure data
exchange, encryption, and identity verification to prevent unauthorized access to critical life
sciences information.
Securing communication channels within a biotechnology and life sciences company is crucial to protect
sensitive information related to genetic research findings, pharmaceutical development, and patient
health data. Here are some measures and strategies to enhance security:

End-to-End Encryption:
Implement end-to-end encryption for all communication channels, ensuring that data is encrypted from
the sender's device and only decrypted on the recipient's end. This prevents unauthorized access to
sensitive information during transmission.
Secure Email Communication:
Use secure email protocols (such as S/MIME or PGP) to encrypt email communications. This ensures
that email content, including attachments, remains confidential and can only be accessed by authorized
personnel.
Virtual Private Network (VPN):
Encourage the use of VPNs for remote access to the company's network. This helps create a secure and
encrypted connection, reducing the risk of data interception during transmission over public networks.
Multi-Factor Authentication (MFA):
Implement multi-factor authentication for access to communication and collaboration tools. This adds an
additional layer of security, requiring users to verify their identity through multiple means (e.g.,
password and a mobile authentication app).
Secure File Transfer:
Use secure file transfer methods, such as SFTP (Secure File Transfer Protocol) or SCP (Secure Copy
Protocol), for sharing large datasets, research findings, and other sensitive documents. This ensures data
integrity and confidentiality during transit.
Access Controls:
Implement strict access controls to limit who can access sensitive information. Role-based access
control (RBAC) can be utilized to grant permissions based on job responsibilities, ensuring that only
authorized personnel can access critical data.
Regular Security Audits:
Conduct regular security audits and vulnerability assessments to identify and address potential
weaknesses in the communication infrastructure. This includes reviewing encryption protocols, access
controls, and monitoring for any suspicious activities.
Employee Training and Awareness:
Provide regular training sessions to employees on security best practices, emphasizing the importance of
safeguarding sensitive information. Create awareness about social engineering attacks and phishing
attempts that could compromise communication channels.
Secure Collaboration Platforms:

Use collaboration tools with built-in security features that support end-to-end encryption, secure file
sharing, and access controls. Ensure that these platforms comply with industry regulations and
standards.
Incident Response Plan:
Develop a robust incident response plan to address any security breaches promptly. This plan should
include steps for communication, containment, eradication, recovery, and post-incident analysis to
continuously improve security measures.
By implementing these measures, a biotechnology and life sciences company can significantly enhance
the security of its communication channels, safeguarding sensitive information from unauthorized access
and potential breaches.
Data Loss Prevention (DLP) Solutions:
Deploy DLP solutions to monitor and control the transfer of sensitive data. These systems can identify
and prevent the unauthorized sharing of confidential information, helping to mitigate the risk of data
leaks.
Regular Security Training and Awareness Programs:
Conduct ongoing security training sessions and awareness programs for employees. This helps keep the
workforce informed about the latest security threats, social engineering tactics, and best practices for
maintaining a secure communication environment.
Secure Mobile Device Management (MDM):
Implement MDM solutions to secure mobile devices used for communication and data access. This
includes enforcing security policies, implementing device encryption, and remotely wiping data from
lost or stolen devices.
Secure Video Conferencing:
Use secure video conferencing platforms with end-to-end encryption to protect discussions involving
sensitive information. Additionally, implement access controls to ensure that only authorized
participants can join virtual meetings.
Regular Software Patching and Updates:
Keep all communication-related software, including operating systems, email clients, and collaboration
tools, up to date with the latest security patches. Regularly patching vulnerabilities helps protect against
potential exploits.
Secure Cloud Services:
If utilizing cloud services, choose reputable providers with a strong focus on security. Encrypt data both
in transit and at rest, and ensure that the cloud service complies with industry-specific regulations for
data protection.

Secure Voice Communication:
Employ encrypted voice communication tools for sensitive discussions. This is particularly important
for any communication that involves discussing research findings, patient health data, or proprietary
information.
Regular Security Assessments:
Conduct periodic security assessments, including penetration testing and vulnerability assessments, to
identify and address potential weaknesses in the communication infrastructure. Regular assessments
help stay ahead of evolving security threats.
Collaboration with Cybersecurity Experts:
Establish partnerships with cybersecurity experts or firms specializing in the life sciences industry. This
collaboration can provide valuable insights, threat intelligence, and recommendations to enhance the
overall security posture.
Continuous Monitoring and Incident Response Automation:
Implement continuous monitoring solutions to detect and respond to security incidents in real-time.
Automation can play a crucial role in responding to threats promptly, minimizing the impact of potential
security breaches.
Data Backups:
Regularly back up critical data and ensure that the backup systems are secure. In the event of a security
incident or data loss, having reliable backups allows for quick recovery without compromising sensitive
information.
Regulatory Compliance:
Stay updated on relevant regulations and compliance requirements in the biotechnology and life sciences
industry. Ensure that communication practices align with these standards to avoid legal issues and
maintain stakeholder trust.
By adopting these additional measures, a biotechnology and life sciences company can create a
comprehensive and robust security framework for its communication channels, reducing the risk of
unauthorized access and ensuring the confidentiality and integrity of sensitive information.
Blockchain Technology:
Consider leveraging blockchain technology for securing and validating data transactions. Blockchain
provides a decentralized and tamper-resistant ledger, enhancing the integrity and transparency of data
related to genetic research, pharmaceutical development, and patient health.
Homomorphic Encryption:

Explore the use of homomorphic encryption, which allows computation on encrypted data without the
need for decryption. This can be beneficial when performing computations on sensitive genomic or
pharmaceutical data while keeping the information encrypted.
Secure APIs (Application Programming Interfaces):
Implement secure APIs for seamless integration between different systems and applications. Ensure that
APIs are protected with authentication mechanisms, access controls, and encryption to prevent
unauthorized access or data exposure.
Container Security:
If using containerized applications, prioritize container security. Implement measures such as image
scanning, runtime protection, and secure orchestration to mitigate potential vulnerabilities in
containerized environments.
Quantum-Safe Encryption:
Stay informed about developments in quantum computing and considers implementing quantum-safe
encryption algorithms. As quantum computers pose a potential threat to traditional encryption, preparing
for quantum-resistant cryptographic methods is essential for long-term security.
Cyber Threat Intelligence Integration:
Integrate cyber threat intelligence feeds into the security infrastructure. This enables the organization to
proactively identify and respond to emerging threats specific to the biotechnology and life sciences
sector.
Zero Trust Network Architecture:
Adopt a Zero Trust model, where no user or system is inherently trusted. Implement strict access
controls, continuous authentication, and least privilege principles to ensure that access is granted based
on real-time verification of user and device trustworthiness.
Red Team Exercises:
Conduct red team exercises to simulate real-world cyber-attacks. This helps identify vulnerabilities, test
incident response capabilities, and improve the overall resilience of the communication infrastructure.
AI-Powered Anomaly Detection:
Implement artificial intelligence (AI) and machine learning (ML) algorithms for anomaly detection.
These technologies can analyze patterns of user behavior and network activities, quickly identifying
deviations that may indicate a security threat.
Biometric Authentication:
Consider incorporating biometric authentication methods for highly sensitive systems or applications.
Biometrics, such as fingerprint or retina scans, provide an additional layer of identity verification
beyond traditional authentication methods.

Immutable Audit Trails:
Implement immutable audit trails to record and monitor all communication activities. This ensures a
comprehensive record of data access, modifications, and transfers, facilitating forensic analysis in the
event of a security incident.
Cross-Functional Security Teams:
Establish cross-functional security teams that include experts in biotechnology, life sciences, and
cybersecurity. This collaboration ensures a deep understanding of the specific security challenges faced
by the organization and promotes a holistic approach to security.
Regular Security Drills:
Conduct regular security drills and tabletop exercises to test the effectiveness of incident response plans.
This proactive approach helps teams refine their response strategies and enhances overall preparedness
for security incidents.
International Data Security Compliance:
If the organization operates globally, ensure compliance with international data security standards and
regulations. This includes understanding and adhering to data protection laws specific to each region
where the company conducts business.
By incorporating these advanced measures, a biotechnology and life sciences company can elevate its
security posture, adapt to emerging threats, and foster a culture of continuous improvement in
information security practices. It's important to stay agile and proactive in the ever-evolving landscape
of cybersecurity.
Supply Chain Security:
Assess and enhance the security of the entire supply chain, including third-party vendors and partners.
Implement vetting processes, contractual obligations for security standards, and regular security
assessments for third-party services involved in the communication ecosystem.
Threat Intelligence Sharing:
Engage in collaborative threat intelligence sharing with industry peers and relevant cybersecurity
forums. This can provide valuable insights into the latest threats, attack vectors, and mitigation strategies
specific to the biotechnology and life sciences sector.
Data Classification and Labeling:
Implement a robust data classification and labeling system. Classify data based on sensitivity levels, and
ensure that communication channels apply appropriate encryption and access controls based on the
classification of the information being transmitted.
Real-Time Monitoring and Incident Response Automation:

Enhance real-time monitoring capabilities with advanced security information and event management
(SIEM) systems. Implement automation in incident response processes to swiftly detect and mitigate
security incidents, reducing the response time to potential threats.
Physical Security Measures:
Integrate physical security measures to protect communication infrastructure. This includes secure
server rooms, access control systems, surveillance cameras, and environmental controls to prevent
unauthorized physical access to critical communication components.
Compliance with Industry Standards:
Ensure compliance with industry-specific standards and regulations, such as HIPAA (Health Insurance
Portability and Accountability Act) for healthcare data or GDPR (General Data Protection Regulation)
for data protection in the European Union. Regularly audit and update security measures to meet
evolving compliance requirements.
Dynamic Identity Management:
Implement dynamic identity management systems that adapt to changing roles and responsibilities
within the organization. This ensures that employees have the appropriate level of access based on their
current responsibilities, reducing the risk of unauthorized access.
Behavioral Analytics:
Utilize behavioral analytics to identify abnormal user behaviors that may indicate a security threat. By
analyzing patterns of behavior, the system can detect deviations and trigger alerts or automated
responses to potential security incidents.
International Collaboration on Cybersecurity Research:
Foster collaboration with international research institutions and organizations focused on cybersecurity
in the life sciences and biotechnology domains. This collaborative approach can contribute to shared
knowledge, best practices, and collective defense against global cyber threats.
Security Awareness and Culture:
Cultivate a strong security awareness culture within the organization. Encourage employees to be
vigilant, report suspicious activities promptly, and actively participate in ongoing security training
programs.
Data Resilience and Disaster Recovery:
Develop a comprehensive data resilience and disaster recovery plan. Regularly test backup and recovery
processes to ensure the organization can quickly recover from data loss or system failures, maintaining
continuity of operations.
Legal and Ethical Considerations:

Stay abreast of legal and ethical considerations related to the collection, storage, and transmission of
sensitive data. Ensure that communication practices align with ethical standards and legal requirements
to avoid regulatory penalties and reputational damage.
User Behavioral Training:
Provide specialized training on recognizing and responding to phishing attempts, social engineering
attacks, and other tactics that exploit human vulnerabilities. User awareness is a critical component of
overall cybersecurity resilience.
Continuous Improvement:
Establish a continuous improvement process for cybersecurity measures. Regularly review and update
security policies, conduct post-incident analyses, and stay informed about emerging threats and
technologies to adapt the security posture accordingly.
By incorporating these additional aspects, a biotechnology and life sciences company can create a
comprehensive and adaptive security strategy that addresses evolving threats and safeguards critical
communication channels and sensitive information effectively.
5. Develop an incident response plan specifically tailored for cybersecurity incidents affecting the
biotechnology and life sciences company. Discuss communication strategies with regulatory
bodies, government health agencies, and the public, as well as steps to minimize the impact of
incidents on life sciences operations and public trust.
Developing an incident response plan for a biotechnology and life sciences company requires a thorough
understanding of the industry's unique challenges and risks. Below is a tailored incident response plan,
including communication strategies and steps to minimize the impact on operations and public trust:
Incident Response Plan for Cybersecurity Incidents in Biotechnology and Life Sciences:
1. Preparation:
a. Risk Assessment: - Identify critical assets and systems related to research, development, and
intellectual property. - Assess potential impact on patient safety, regulatory compliance, and public trust.
b. Incident Response Team (IRT): - Assemble a cross-functional IRT with expertise in IT, cybersecurity,
legal, regulatory affairs, and public relations.
c. Incident Response Plan Documentation: - Develop a detailed incident response plan, outlining roles,
responsibilities, and communication protocols. - Regularly update the plan based on emerging threats
and industry changes.
2. Detection and Analysis:

a. Continuous Monitoring: - Implement advanced threat detection systems for real-time monitoring. -
Establish anomaly detection for unusual activities in the network.
b. Incident Analysis: - Rapidly analyze and assess the scope and nature of the incident. - Determine the
potential impact on research, patient data, and regulatory compliance.
3. Containment, Eradication, and Recovery:
a. Isolation and Containment: - Isolate affected systems to prevent further damage. - Contain the
incident to minimize the impact on critical operations.
b. Eradication: - Identify and eliminate the root cause of the incident. - Implement security patches and
updates to prevent future occurrences.
c. Recovery: - Restore affected systems and data from secure backups. - Verify the integrity of restored
data and systems.
4. Communication Strategies:
a. Internal Communication: - Establish a secure and dedicated communication channel for the incident
response team. - Keep internal stakeholders informed about the situation, progress, and recovery
timelines.
b. Regulatory Bodies and Government Health Agencies: - Notify relevant regulatory bodies promptly,
providing detailed information on the incident. - Collaborate closely with government health agencies to
share intelligence and receive guidance.
c. Public Communication: - Develop a coordinated communication strategy with public relations teams.
- Craft transparent and accurate messages to address the incident's impact on public safety and research
integrity.
5. Minimizing Impact on Operations and Public Trust:
a. Alternate Operations: - Identify backup systems and facilities to ensure critical research and
operations continue. - Implement contingency plans to minimize disruptions.
b. Collaboration with Partners: - Communicate with research partners, vendors, and collaborators to
mitigate shared risks. - Share best practices for cybersecurity to strengthen the overall ecosystem.
c. Rebuilding Public Trust: - Establish a public relations campaign emphasizing the company's
commitment to cybersecurity. - Engage with the public, patients, and stakeholders to rebuild trust
through transparent communication and proactive measures.
6. Post-Incident Analysis and Improvement:
a. After-Action Review: - Conduct a comprehensive analysis of the incident response process. - Identify
areas for improvement in policies, procedures, and technologies.
b. Continuous Training and Awareness: - Provide ongoing training to employees on cybersecurity best
practices. - Foster a culture of awareness and accountability.

By following this tailored incident response plan, the biotechnology and life sciences company can
effectively navigate and mitigate the impact of cybersecurity incidents while maintaining public trust
and regulatory compliance. Regular testing and updates to the plan will ensure its effectiveness in the
face of evolving cyber threats.
Communication Strategies:
a. Internal Communication:
Establish clear channels for internal communication to ensure timely and accurate information sharing
among the incident response team and key stakeholders.
Hold regular briefings to keep employees informed about the incident, its impact, and the ongoing
response efforts.
Emphasize the importance of confidentiality to prevent the spread of misinformation.
b. Regulatory Bodies and Government Health Agencies:
Develop pre-established relationships with regulatory bodies and government health agencies.
Create a dedicated liaison role within the incident response team to facilitate communication with
regulatory authorities.
Provide regular updates to regulatory bodies and agencies, demonstrating transparency and cooperation.
c. Public Communication:
Craft a well-defined public communication plan that includes designated spokespersons and
communication channels.
Tailor messages to different audiences, addressing concerns related to patient safety, research integrity,
and the company's commitment to cybersecurity.
Utilize social media, press releases, and the company website for official communication.
Minimizing Impact on Operations and Public Trust:
a. Alternate Operations:
Develop a business continuity plan that outlines procedures for maintaining critical operations during
and after a cybersecurity incident.
Identify backup facilities, equipment, and personnel to ensure minimal disruption to ongoing research
and development activities.
b. Collaboration with Partners:
Establish communication protocols with research partners and collaborators to share threat intelligence
and coordinate response efforts.
Conduct joint cybersecurity exercises with partners to enhance collective readiness and resilience.

c. Rebuilding Public Trust:
Engage with the public through transparent and empathetic communication.
Highlight the company's commitment to cybersecurity measures, investment in technology, and ongoing
efforts to strengthen security protocols.
Implement visible and proactive measures to address vulnerabilities identified during the incident.
Post-Incident Analysis and Improvement:
a. After-Action Review:
Conduct a thorough analysis of the incident response process, including strengths and areas for
improvement.
Document lessons learned and update the incident response plan accordingly.
Use the insights gained to enhance incident detection and response capabilities.
b. Continuous Training and Awareness:
Provide ongoing cybersecurity training for employees at all levels of the organization.
Conduct simulated exercises and drills to test the effectiveness of the incident response plan and
improve the team's response capabilities.
Foster a culture of cybersecurity awareness and accountability, encouraging employees to report
suspicious activities promptly.
Legal and Compliance Considerations:
a. Legal Counsel:
Involve legal counsel in the incident response process to ensure compliance with data protection and
privacy laws.
Navigate any potential legal implications and obligations associated with the incident.
b. Regulatory Compliance:
Regularly audit and update policies and procedures to align with evolving regulatory requirements.
Ensure that the incident response plan addresses industry-specific regulations governing the protection
of sensitive data.
Technological Measures:
a. Threat Intelligence Integration:
Integrate threat intelligence feeds to stay informed about emerging threats specific to the biotechnology
and life sciences industry.

Use this intelligence to proactively enhance security controls.
b. Advanced Endpoint Protection:
Implement advanced endpoint protection solutions to detect and mitigate sophisticated cyber threats.
Regularly update and patch systems to address vulnerabilities.
By addressing these additional considerations, the incident response plan becomes more comprehensive
and adaptable to the unique challenges faced by a biotechnology and life sciences company. Regular
testing, training, and updates are crucial to maintaining the plan's effectiveness in the dynamic landscape
of cybersecurity threats.

