


Running head: PASSIVE RECONNAISSANCE 1
Passive Reconnaissance
Carla Ginart
Liberty University
Ethical Hacking
CSCI 632
Dr. Allen Harper
PASSIVE RECONNAISSANCE 2
Passive Reconnaissance
Part 1: Explore Google Hacking Techniques
Step 5
Step 7
Google
Google
google.com/search?q=!
563
Anytimes.comAisca_esv=6798127eb681991781sca_upy=18ei=0YpQZoKALqueSNoPuda
10AU8ved=OahUKEwjC1Oq6p6aGAxUrD1kFHTIrD
link-nytimes.com
x
$a2aQ
‘All
News
Images
Videos
Shopping
More
Tools
“The
New
York
Times
hitpsihepnyimas.com>
ens»
atlas
»
15014893...
Linking
to
NYTimes.com
-
Help
-
The
New
York
Times.
‘No.
We
encourage
links
from
other
sites.
When
your
readers
visit
NYTimes.com
by
clicking
a
rUntitled-Note.
-
OO xX
link
on
your
blog
or
site,
that
article
(or
video,
side
show,
etc.)
File
Edit
Format
View
Help
Carla
Ginart
05/24/2024,
People
also
ask
How
do
I
link
my
NYTimes
account?
v
10C
Windows
(CRLF)
—_UTF-8
What
is
The
New
York
Times
URL?
v
What
is
a
NYTimes
gift link?
v
How
do
|
activate
my
NYT
subscription?
v
Feadboce
The
New
YorcTimes
hpstawanyimes
com
gas
connections
Play
Connections
and
more
in
the
NYT
Games
app.
[Group
words
that
share
a
commen
thread.
Wiant
fo
access
al of
our
games?
Pay
Connections
and
more
in
the
NYT
Games
app
©
The
NewYork
Times
hitps:tmyaccount
nytimes.com»
inks
homedelvery.
{
Welcome
to
The
New
York
Times,
Log
in
or create
a
New
York
Times
account
to
access
the
All
Access
portion
of
your
Home
Delivery
subscription.
Login
or
Create Account.
Need
Help?
Contact
our
ge
TeNew
orc
Tines
hipelwanyimes
com
$
The
New
York
Times
-
Breaking
News,
US
News,
World
News
Live
news
investigations,
opinion,
photos
and
video
by
the
journalists
of
The
New
York
Times
from
more
than
150
counties
around the
works
Connections
Today's
Paper:
International
Worl
News
google.com/search?q=related%3Anytimes.coméisca_esv=6798
127eb681991781sca_upv=18lei=S4IQZp-zitCISNoPtpGykAgSived
=
0ahUKEwjfhNWXpqaGAxXQEIkFHbalDI
related:nytimes.com
x
£ana
All
News
Images
Videos
Shopping
More
Tools
@
The
New
York
Times
httpsi/www.nytimes.com>
spotight>
race
$
‘unitied-Noe.
—-
OX
Race/Related
File
Edit
Format
View
Help
Carla
Ginart
‘Welcome
to
Race/Related,
a
weekly
newsletter
focused
on
race,
identity
and
culture.
0724/2024
Page
9
Page
8-
10-
Page
4
100
Windows
(CRLF)
—_UTF-8
|
THe
New
york
Times
httpsi/www.nytimes.com
newsletters
racerelated
Race/Related
Newsletter
Race/Related.
Explore
the countless
ways
race
affects
our
lives,
with
provocative
reporting
and
discussion.
Sent
to
Your
Inbox
Weekly;
Read
the
Latest.
&
The
New
York
Times
https://www.nytimes.com
»
newsgraphics
»
race-related
Race/Related
Anewsletter
exploring
race
with
provocative
reporting
and
discussion.
We
want
to
stir
up
conversation,
with
The
Times
and
with
you.
Race
matters,
and
it's
People
also
ask
:
Who
owns
nyt?
v
PASSIVE RECONNAISSANCE 3
PASSIVE RECONNAISSANCE 4
Step 9 Describe the differences as directed?
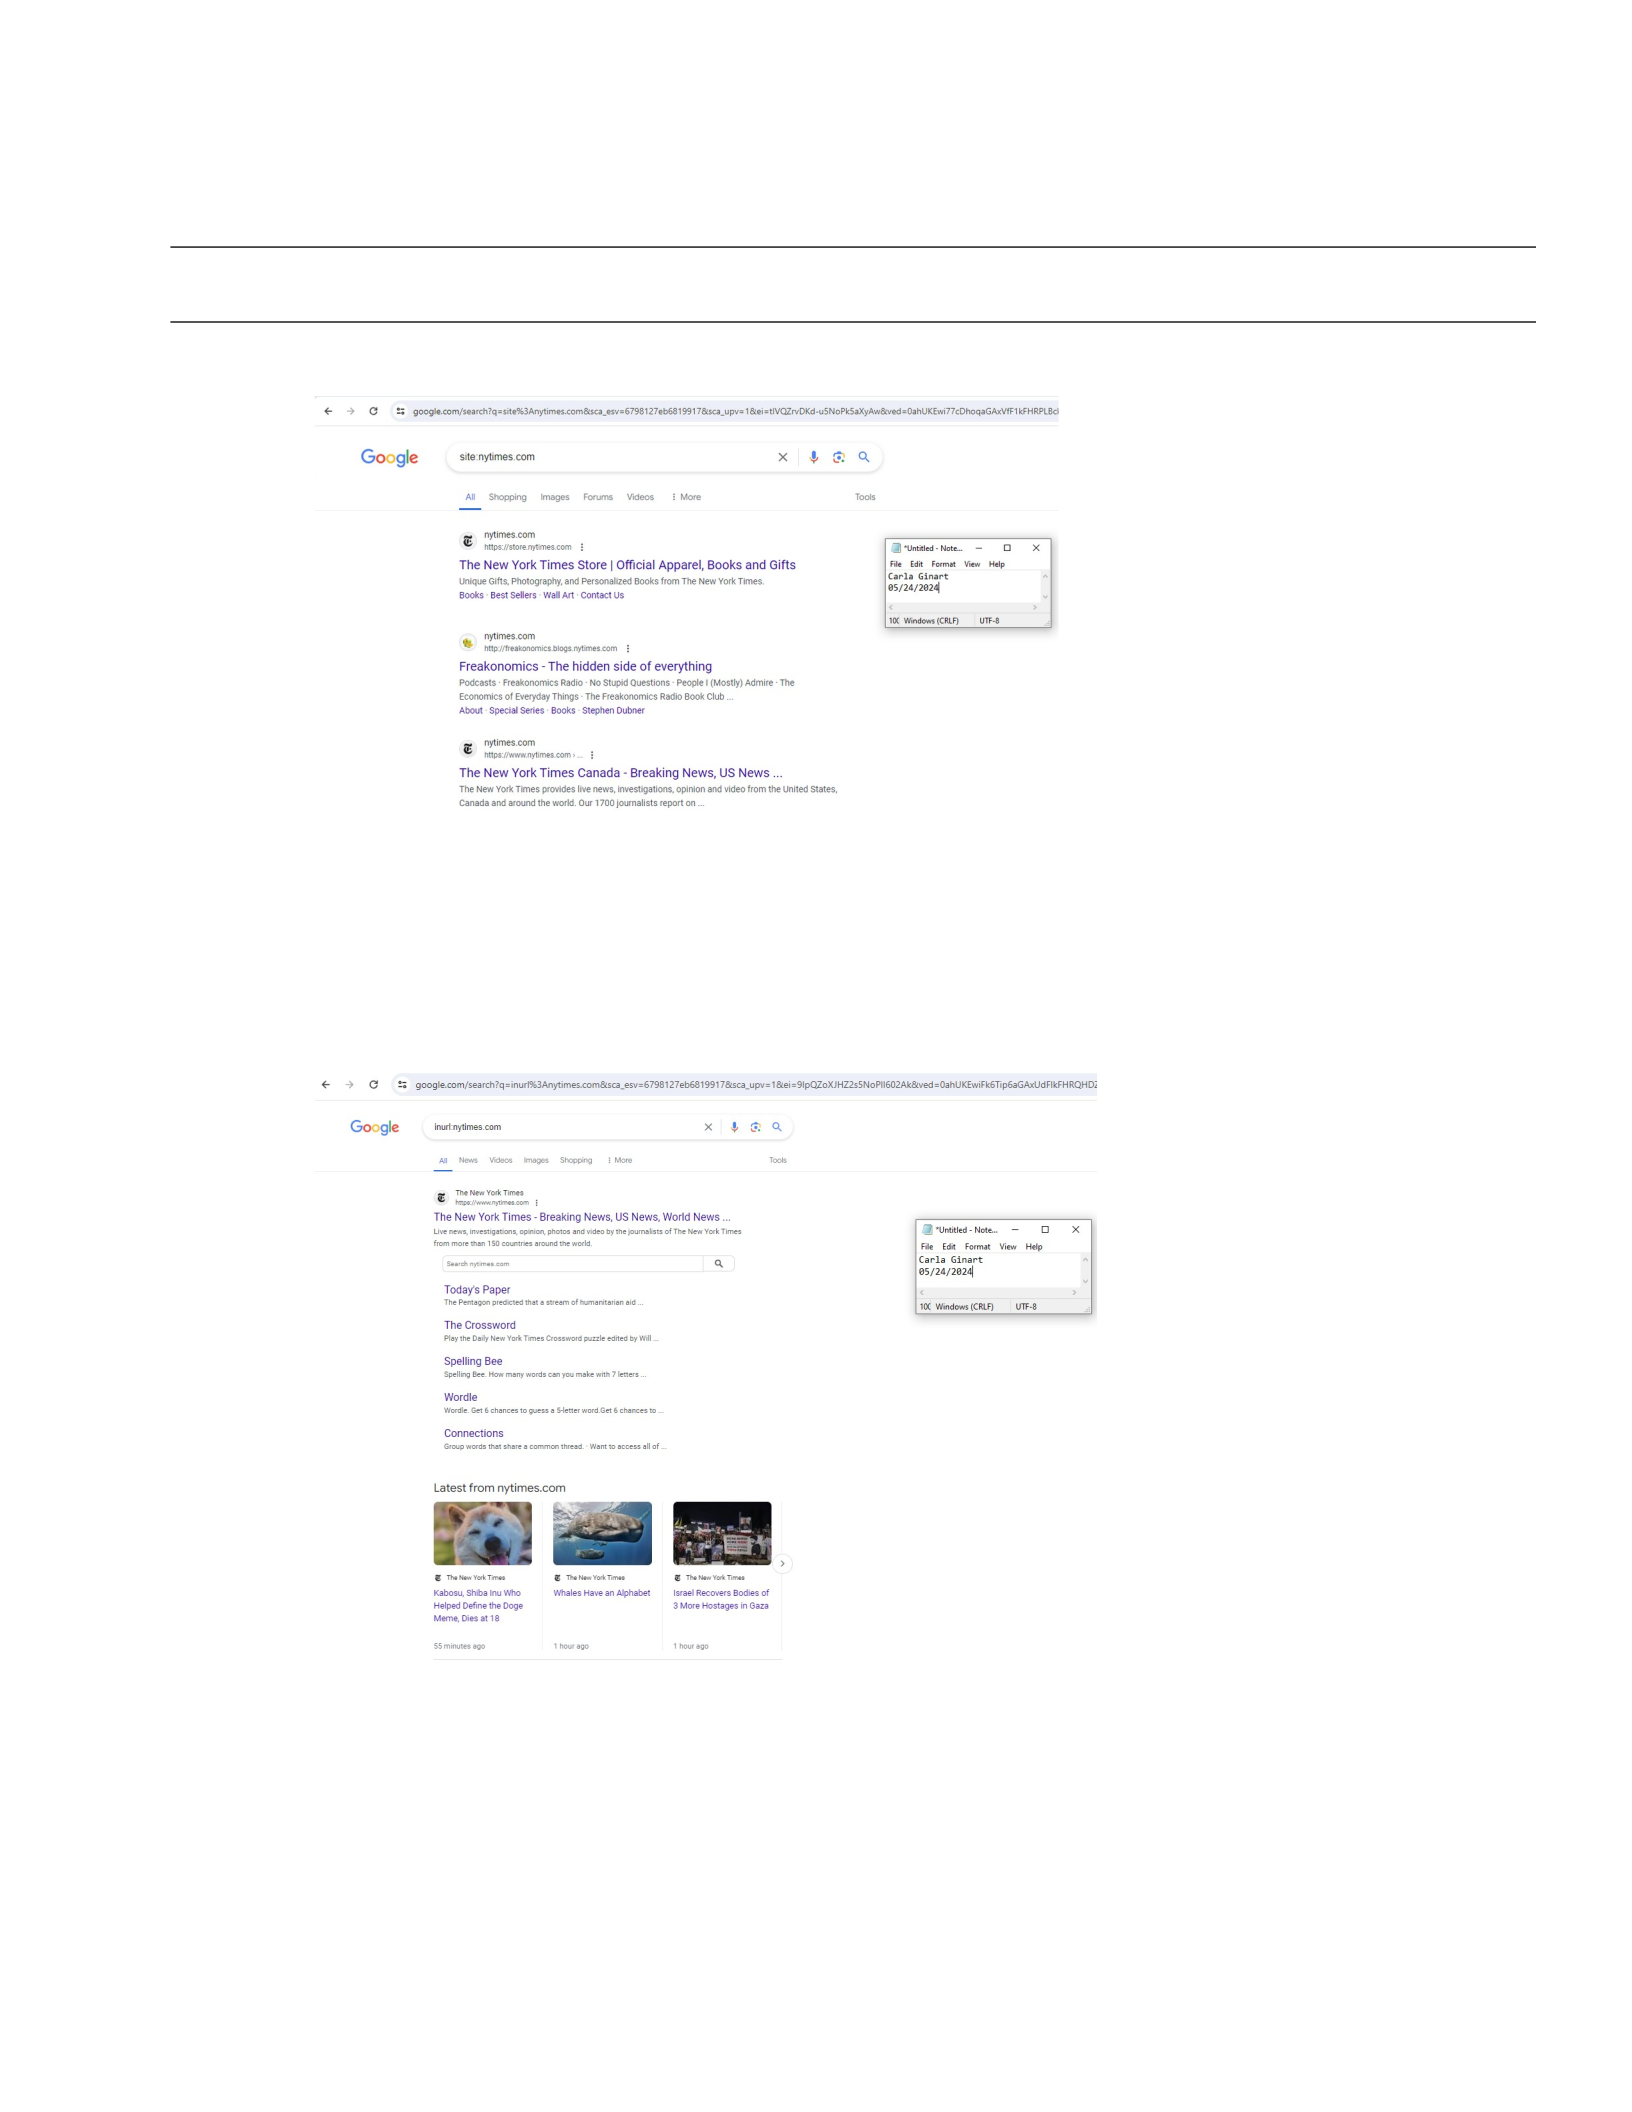
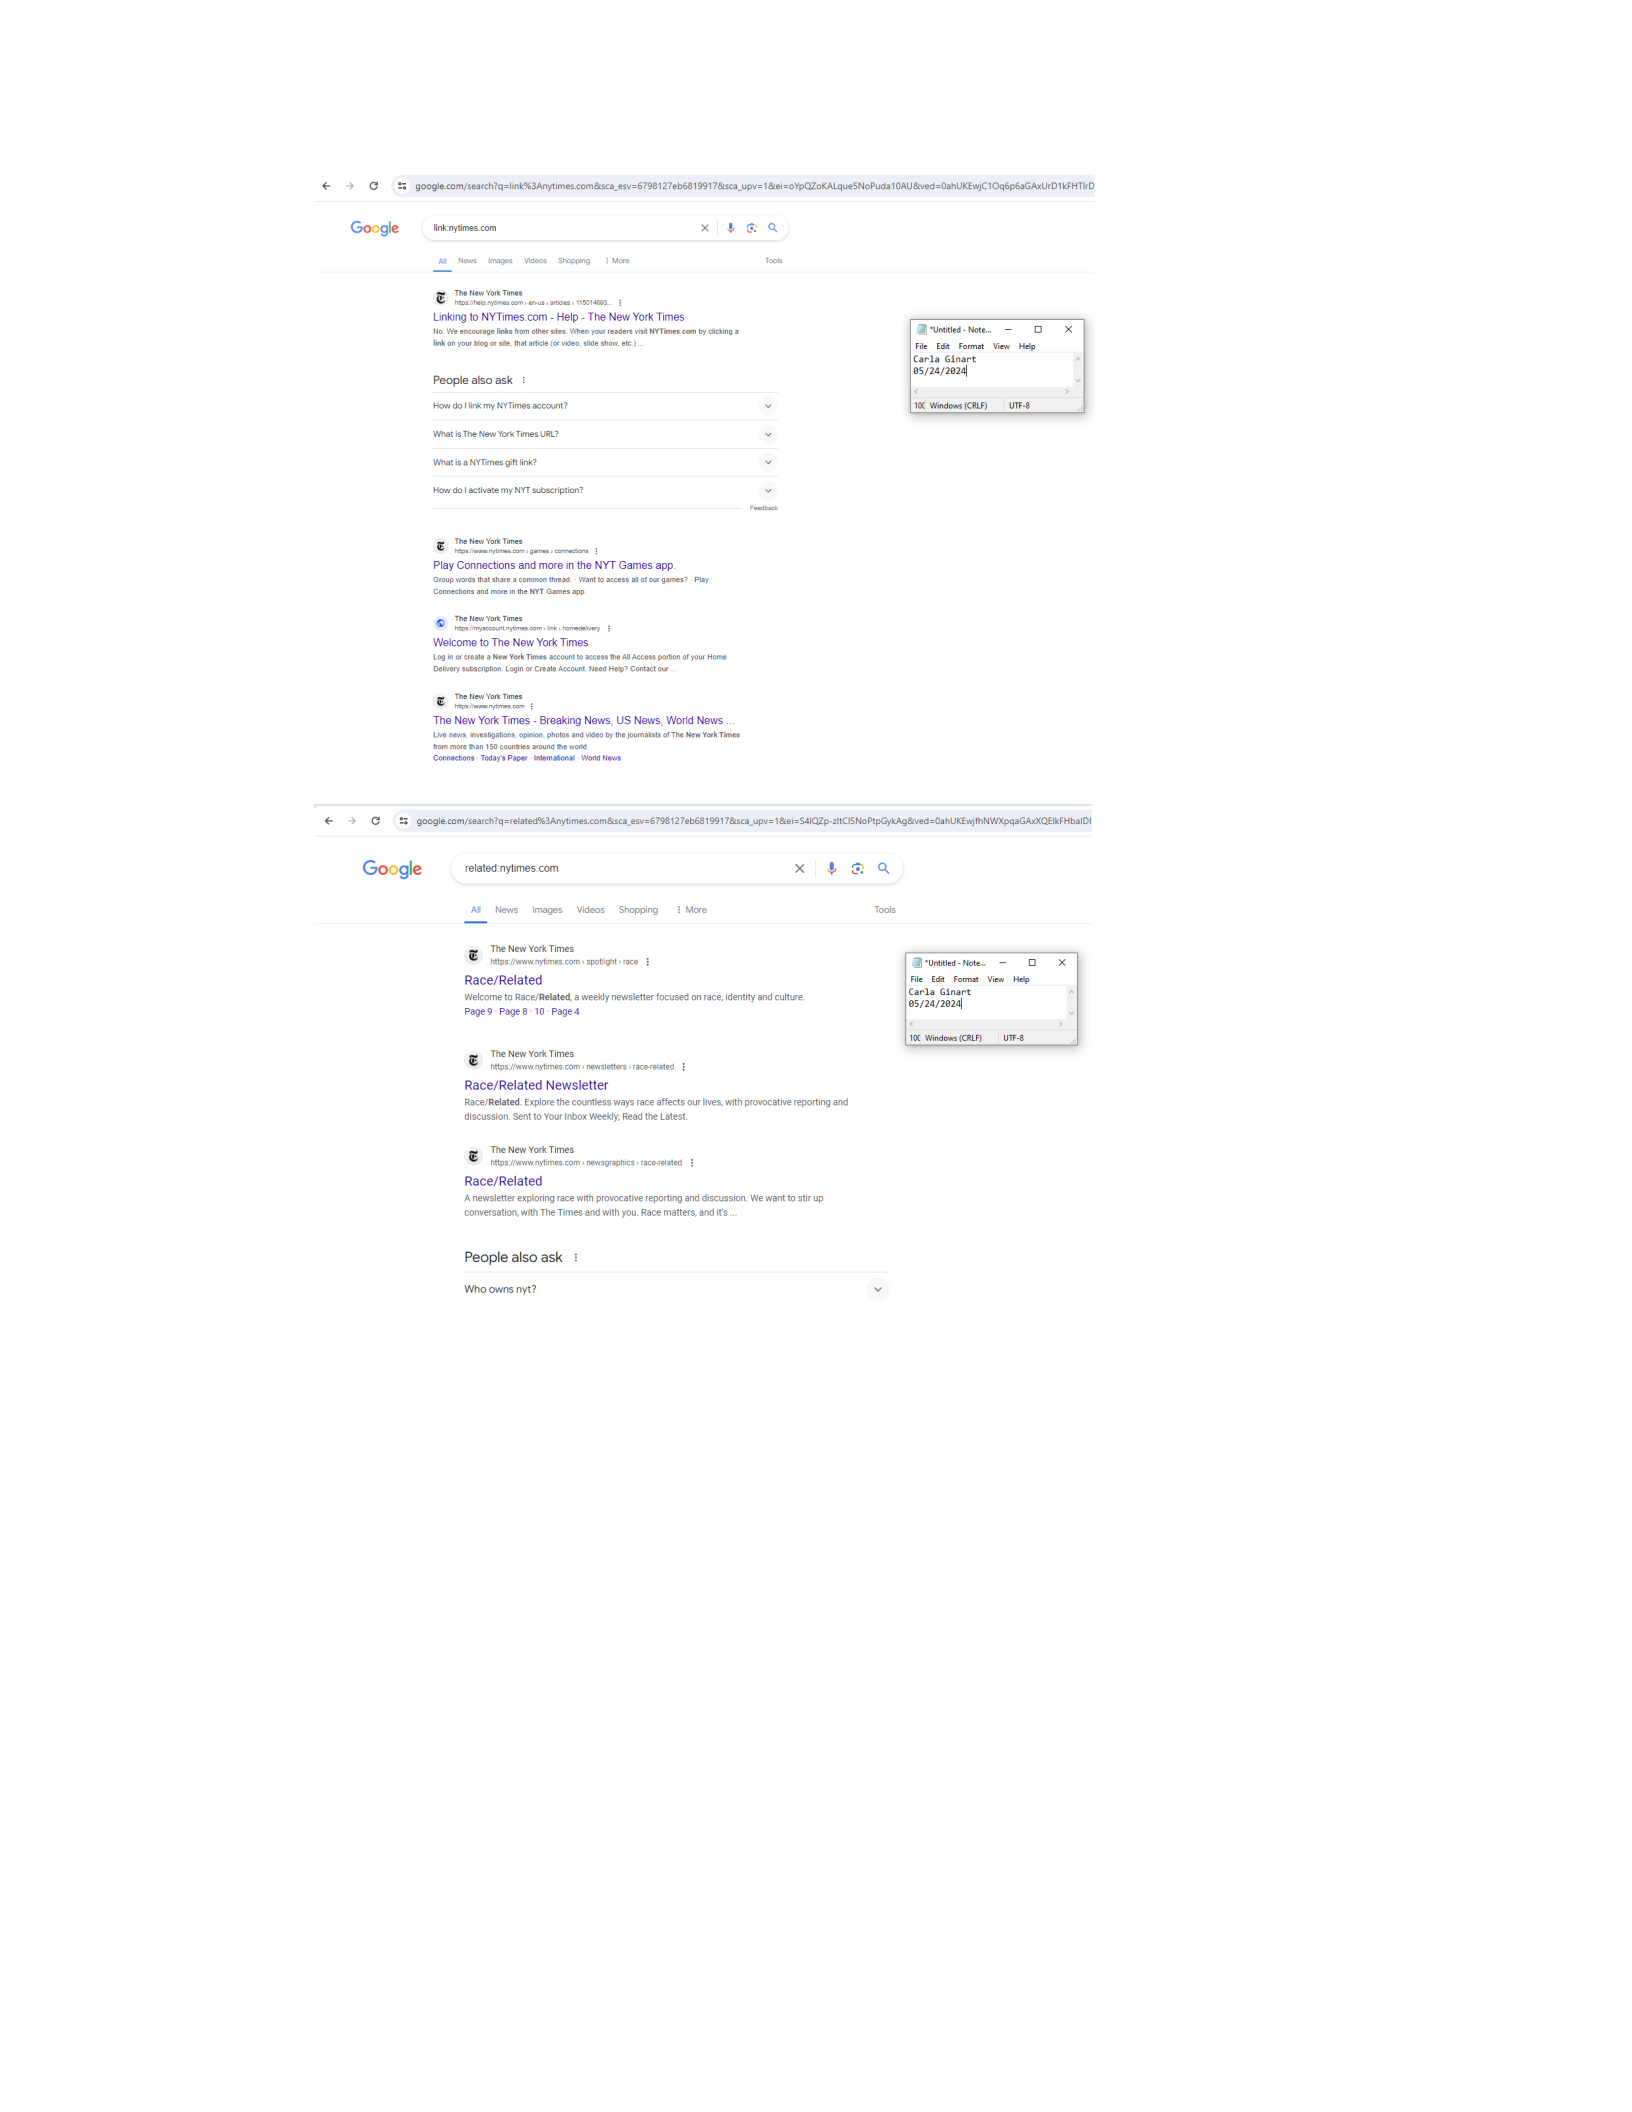
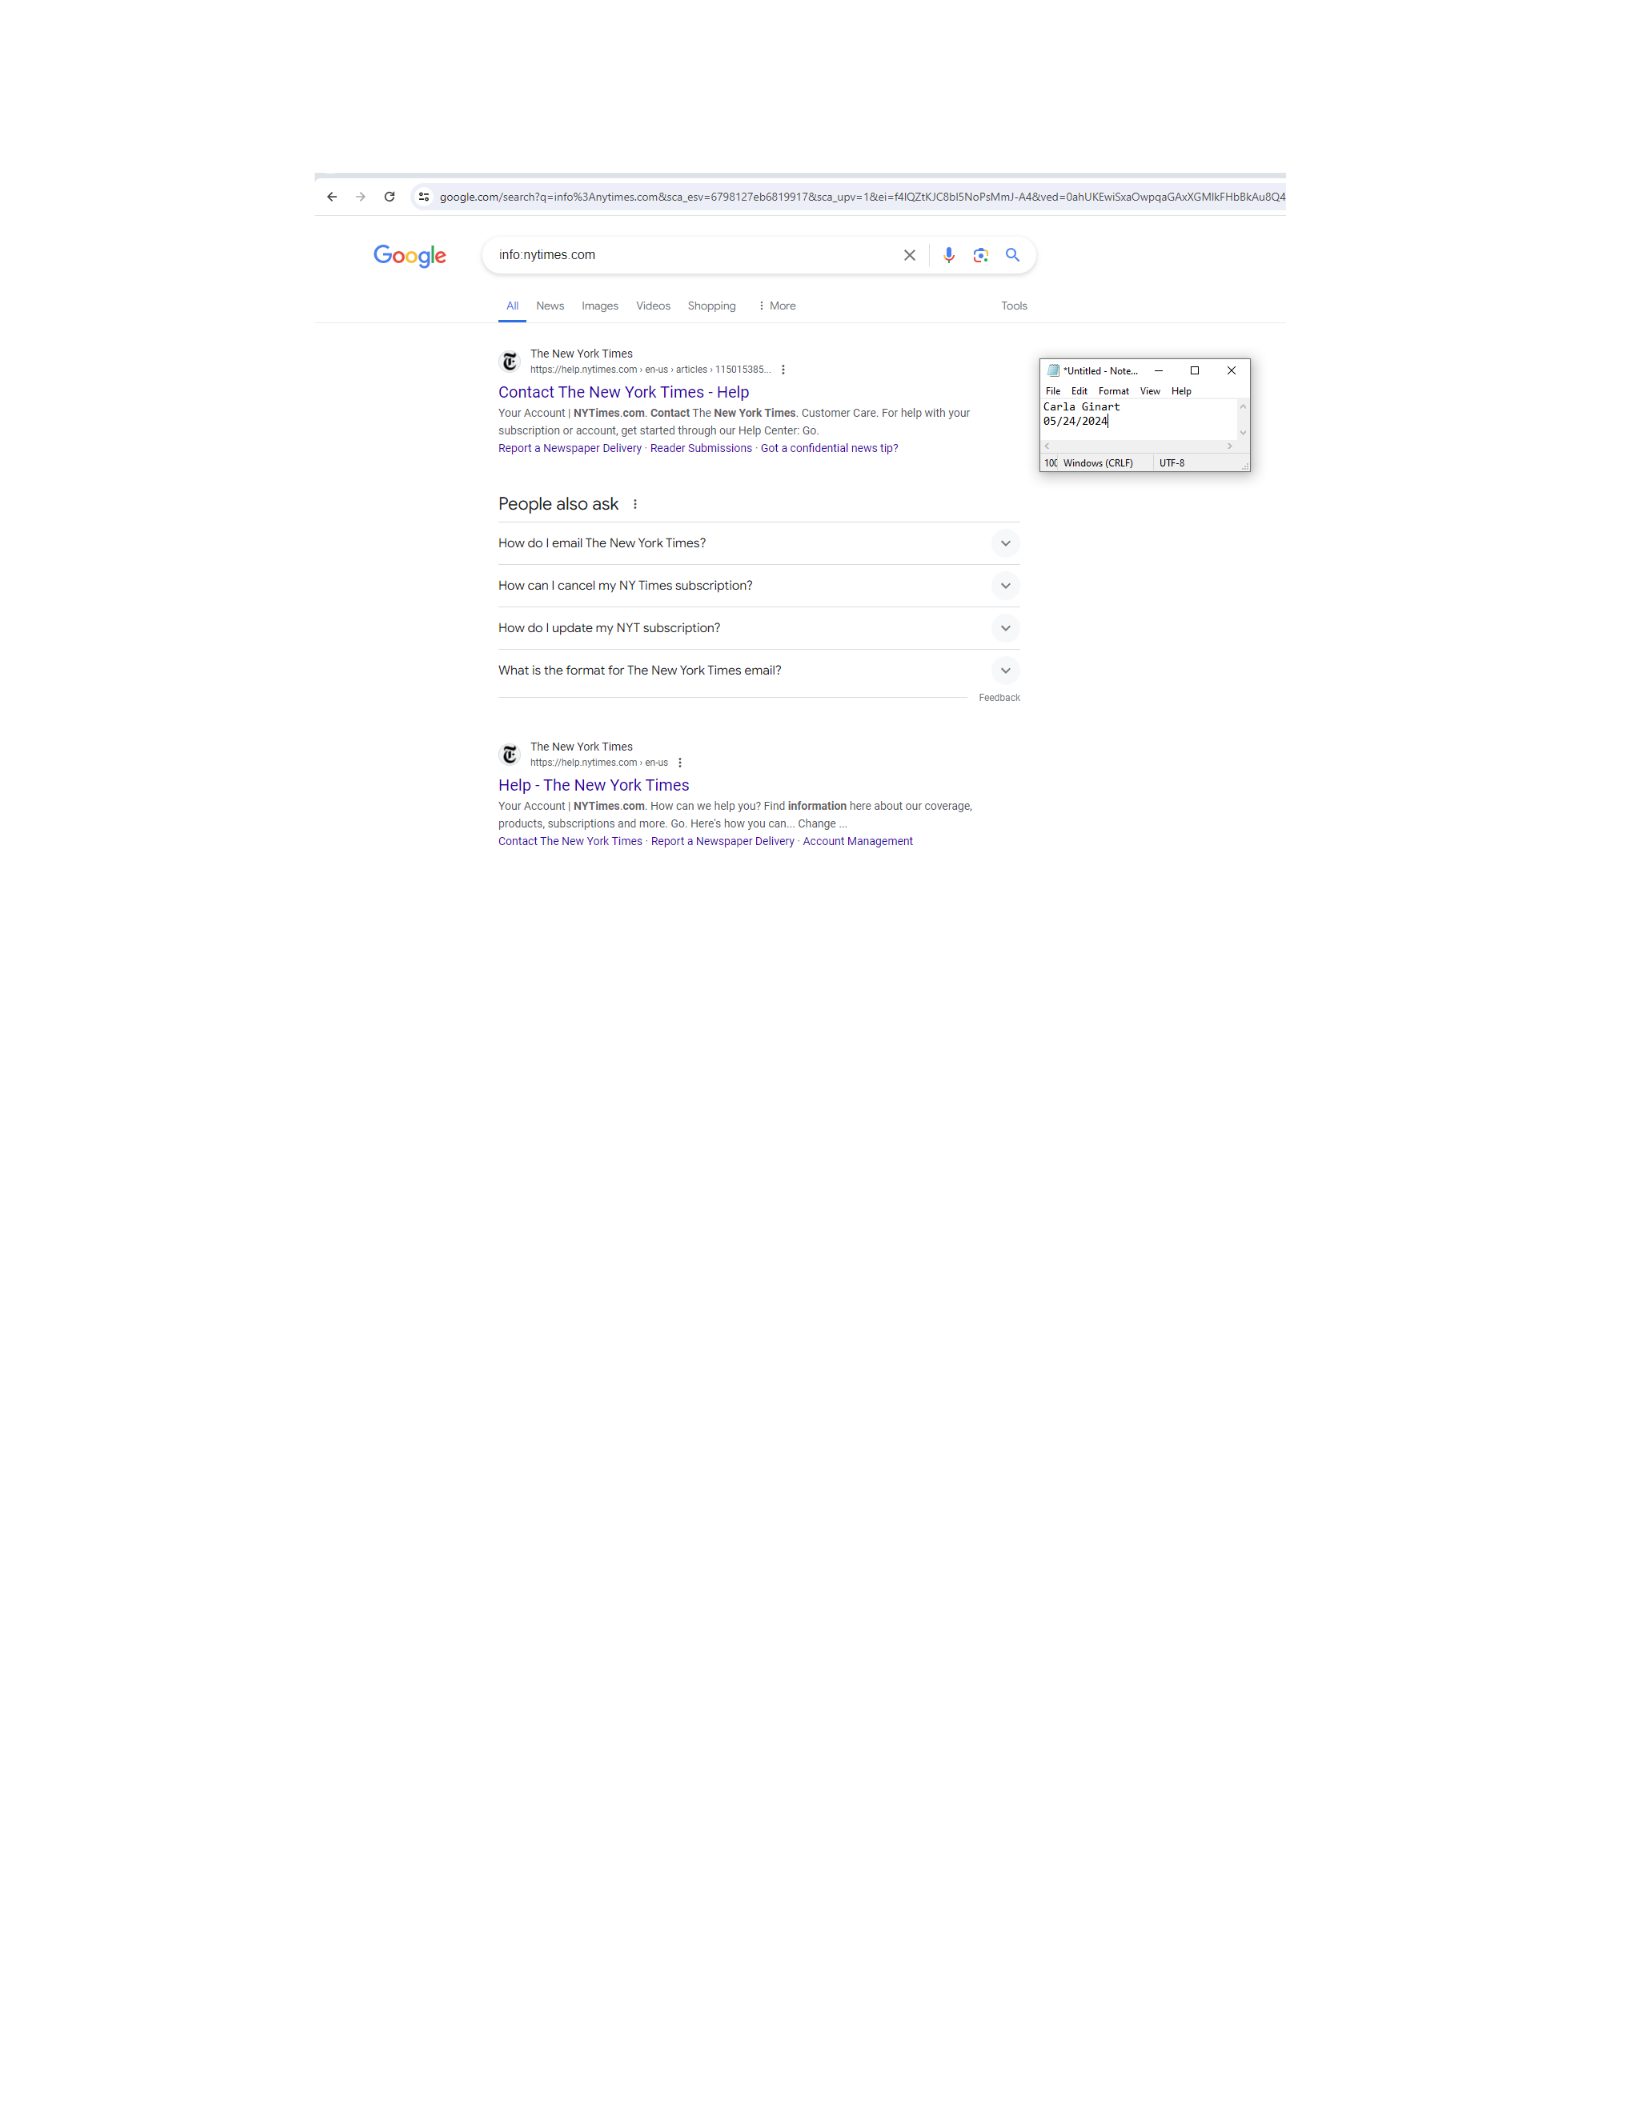
Just typing New York times shows all the top sites connected to the nytimes.com domain.
Doing site:nytimes.com shows pages for the NYTimes holding nytimes.com . Doing
inurl:nytimes.com shows pages with the nytimes.com string in the title. Doing
link:nytimes.com displays linked pages based on the nytimes.com. Doing info:nytimes.com
displays information Google stores about the page itself. Doing relate:nytimes.com shows
web pages similar to nytimes.com.
PASSIVE RECONNAISSANCE 5
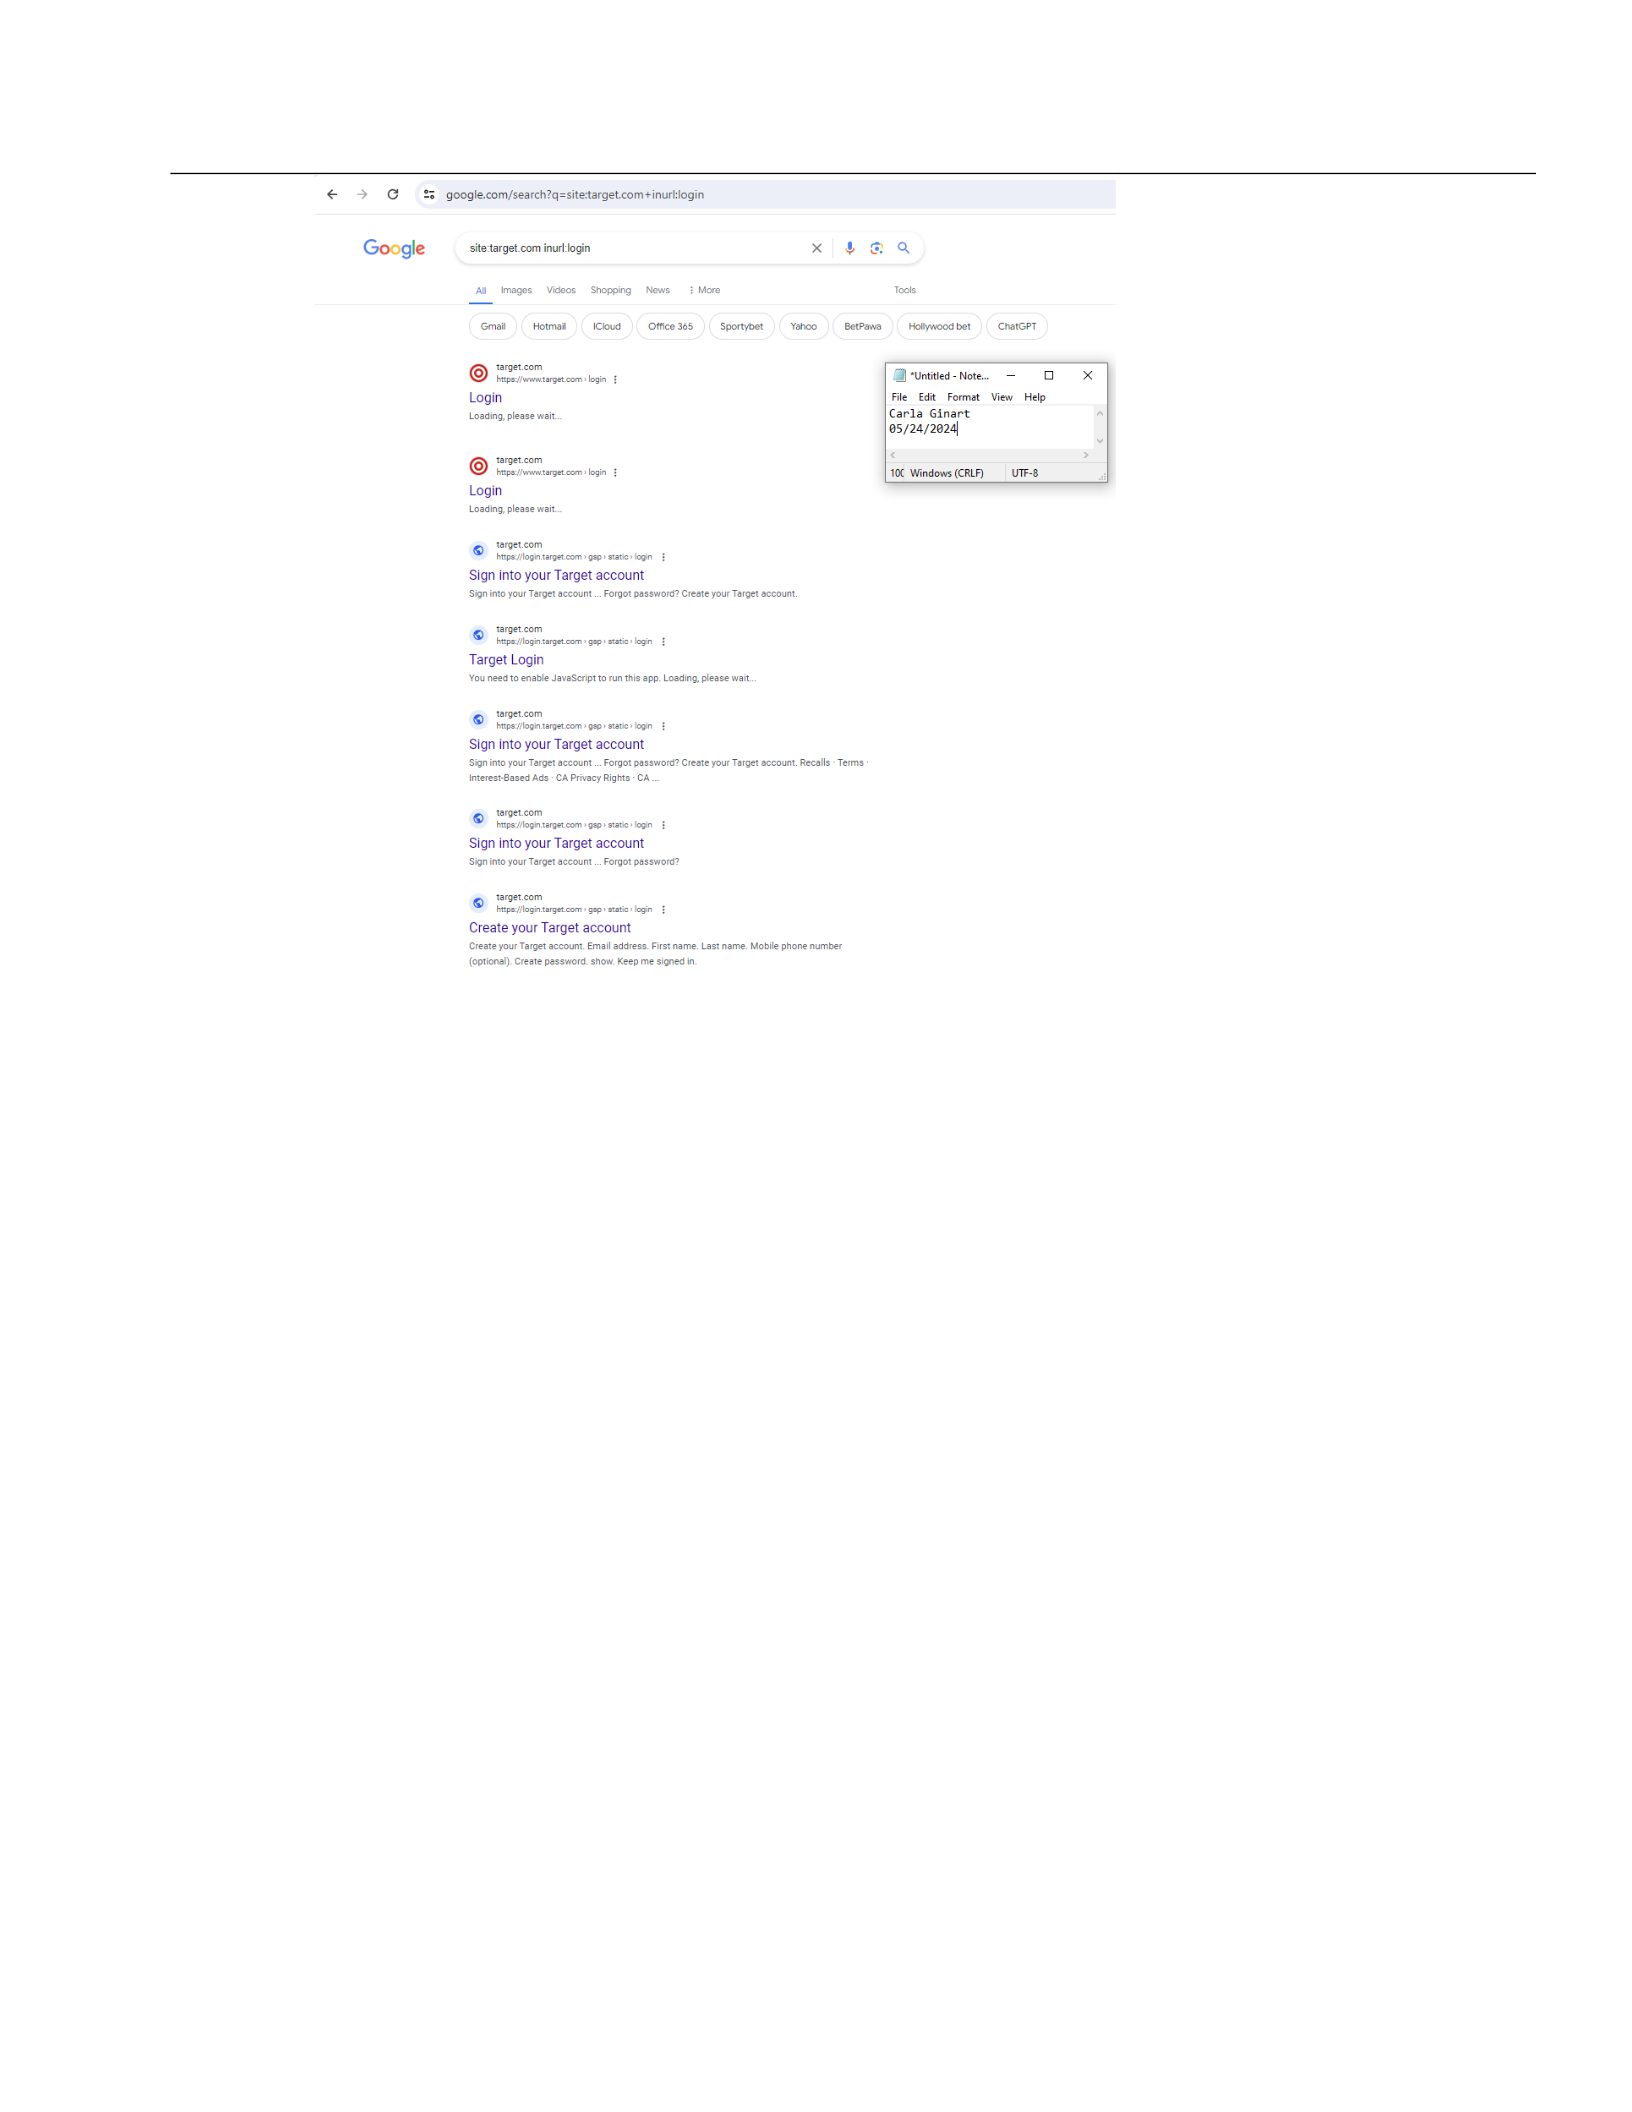
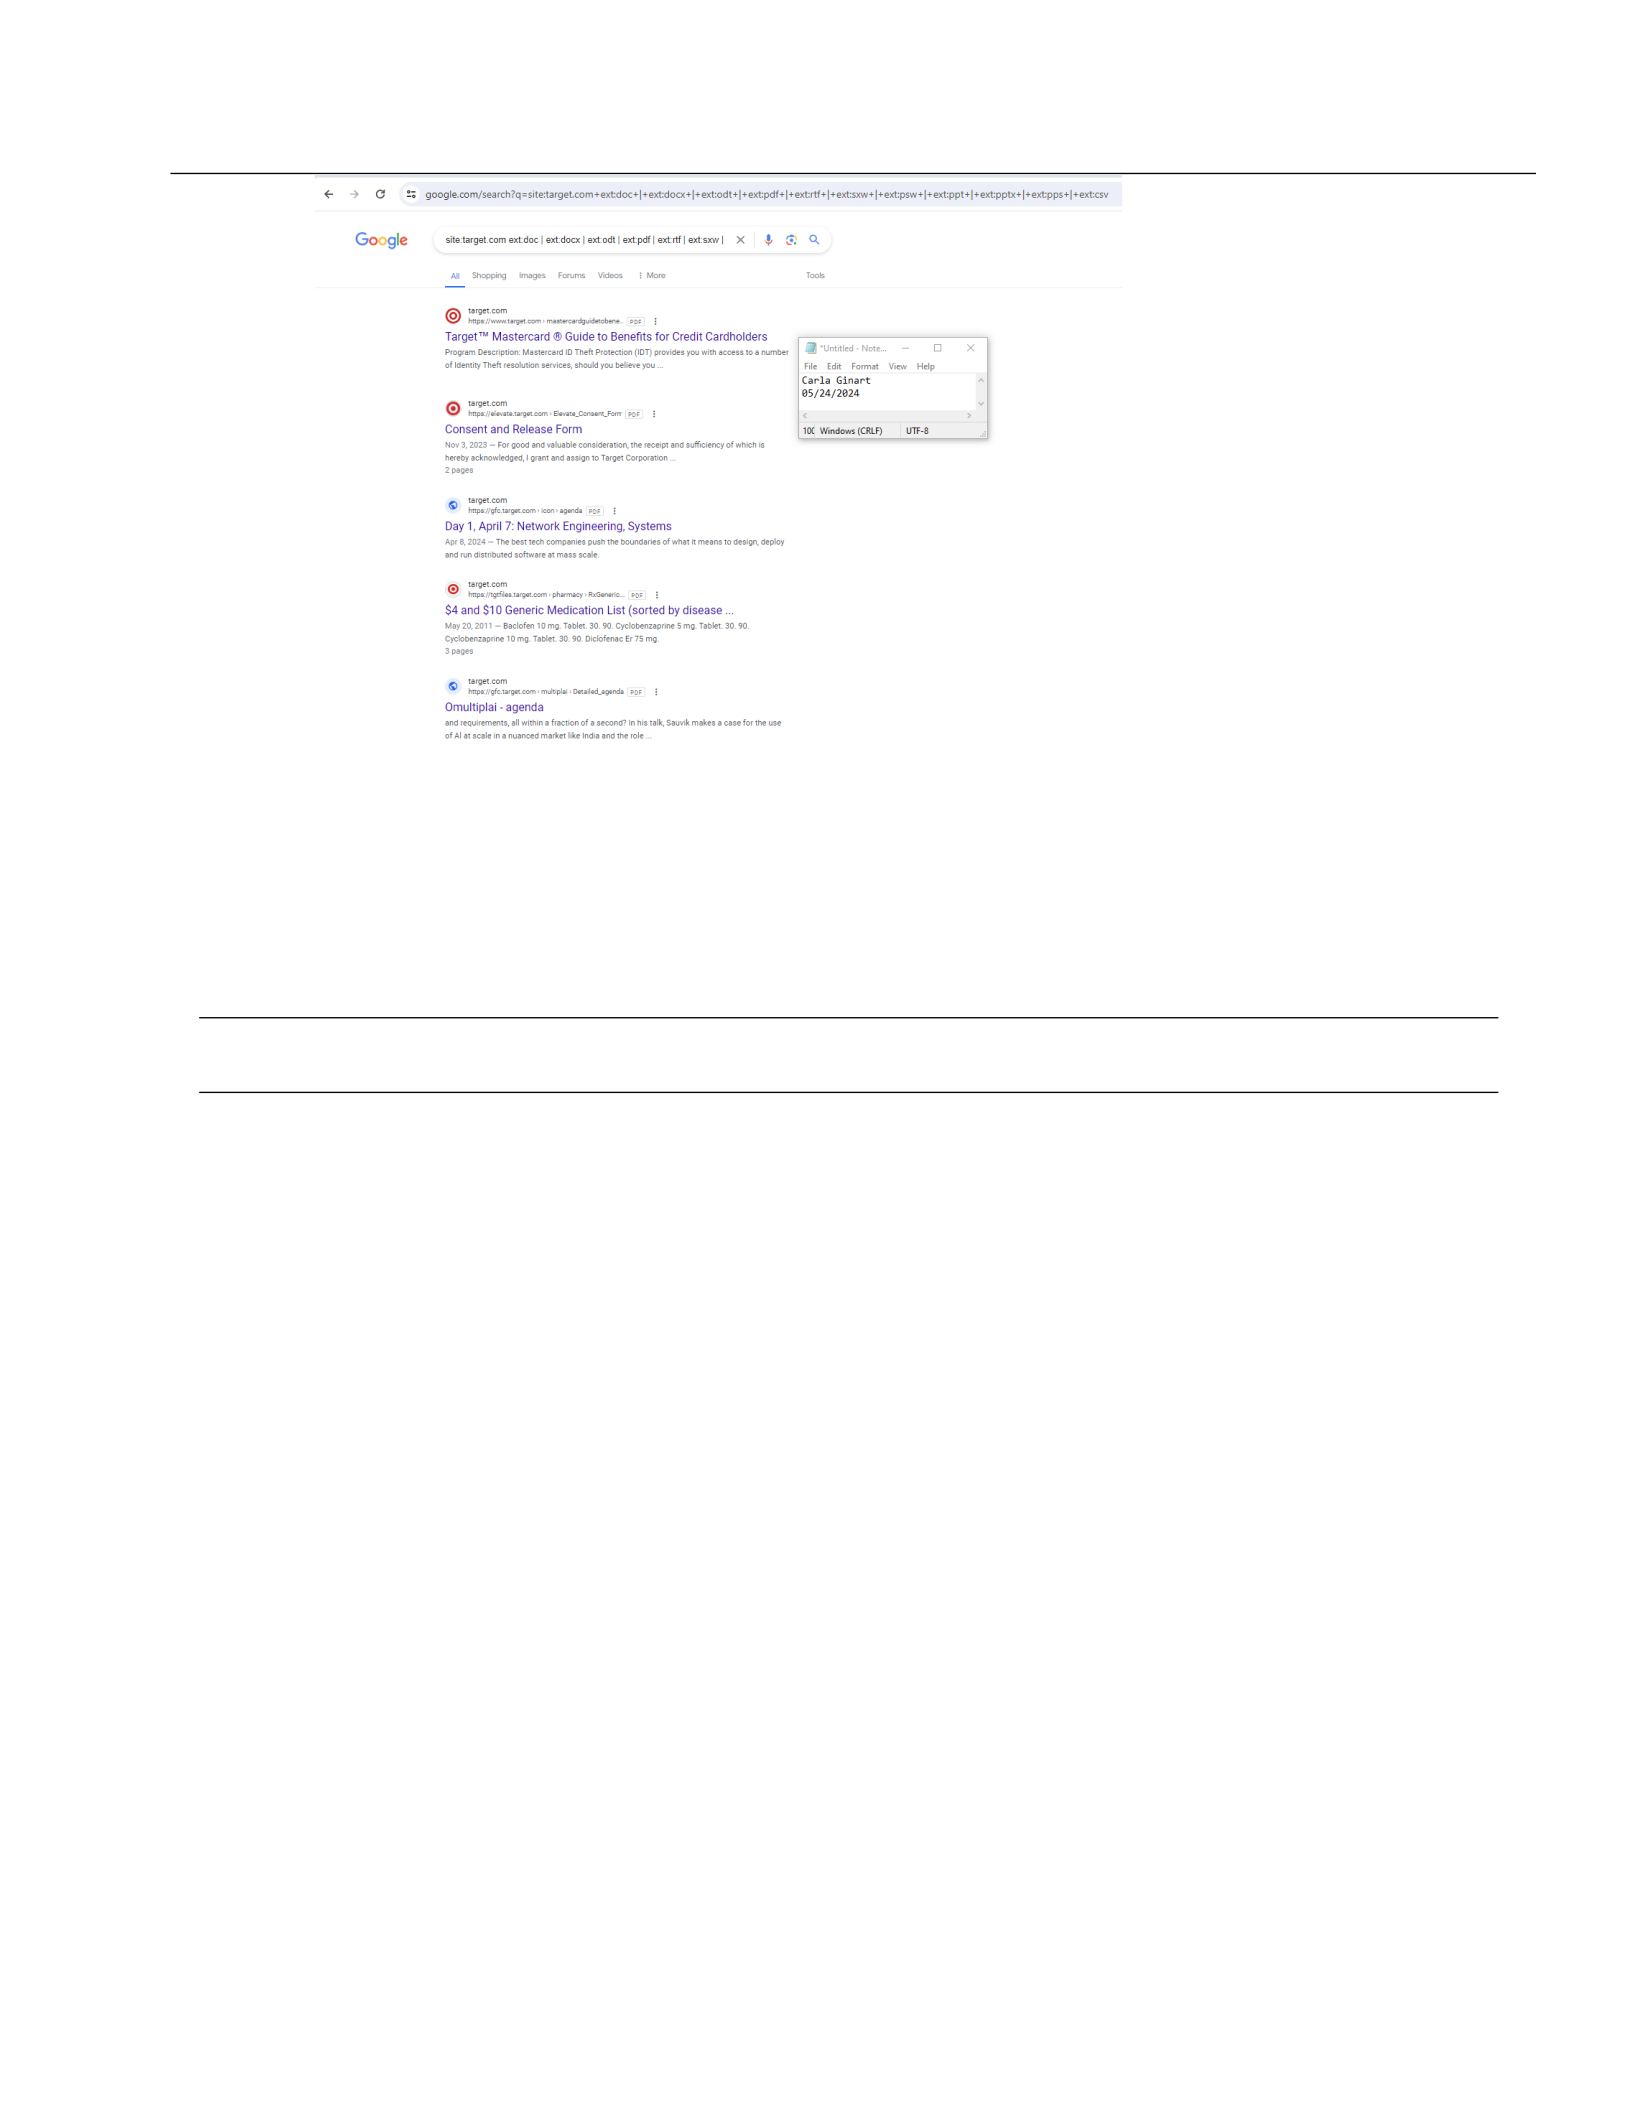
Part 2: Experiment with Google’s Advanced Search Operators
Step 5
Step 6
D)
PASSIVE RECONNAISSANCE 6
F)
PASSIVE RECONNAISSANCE 7
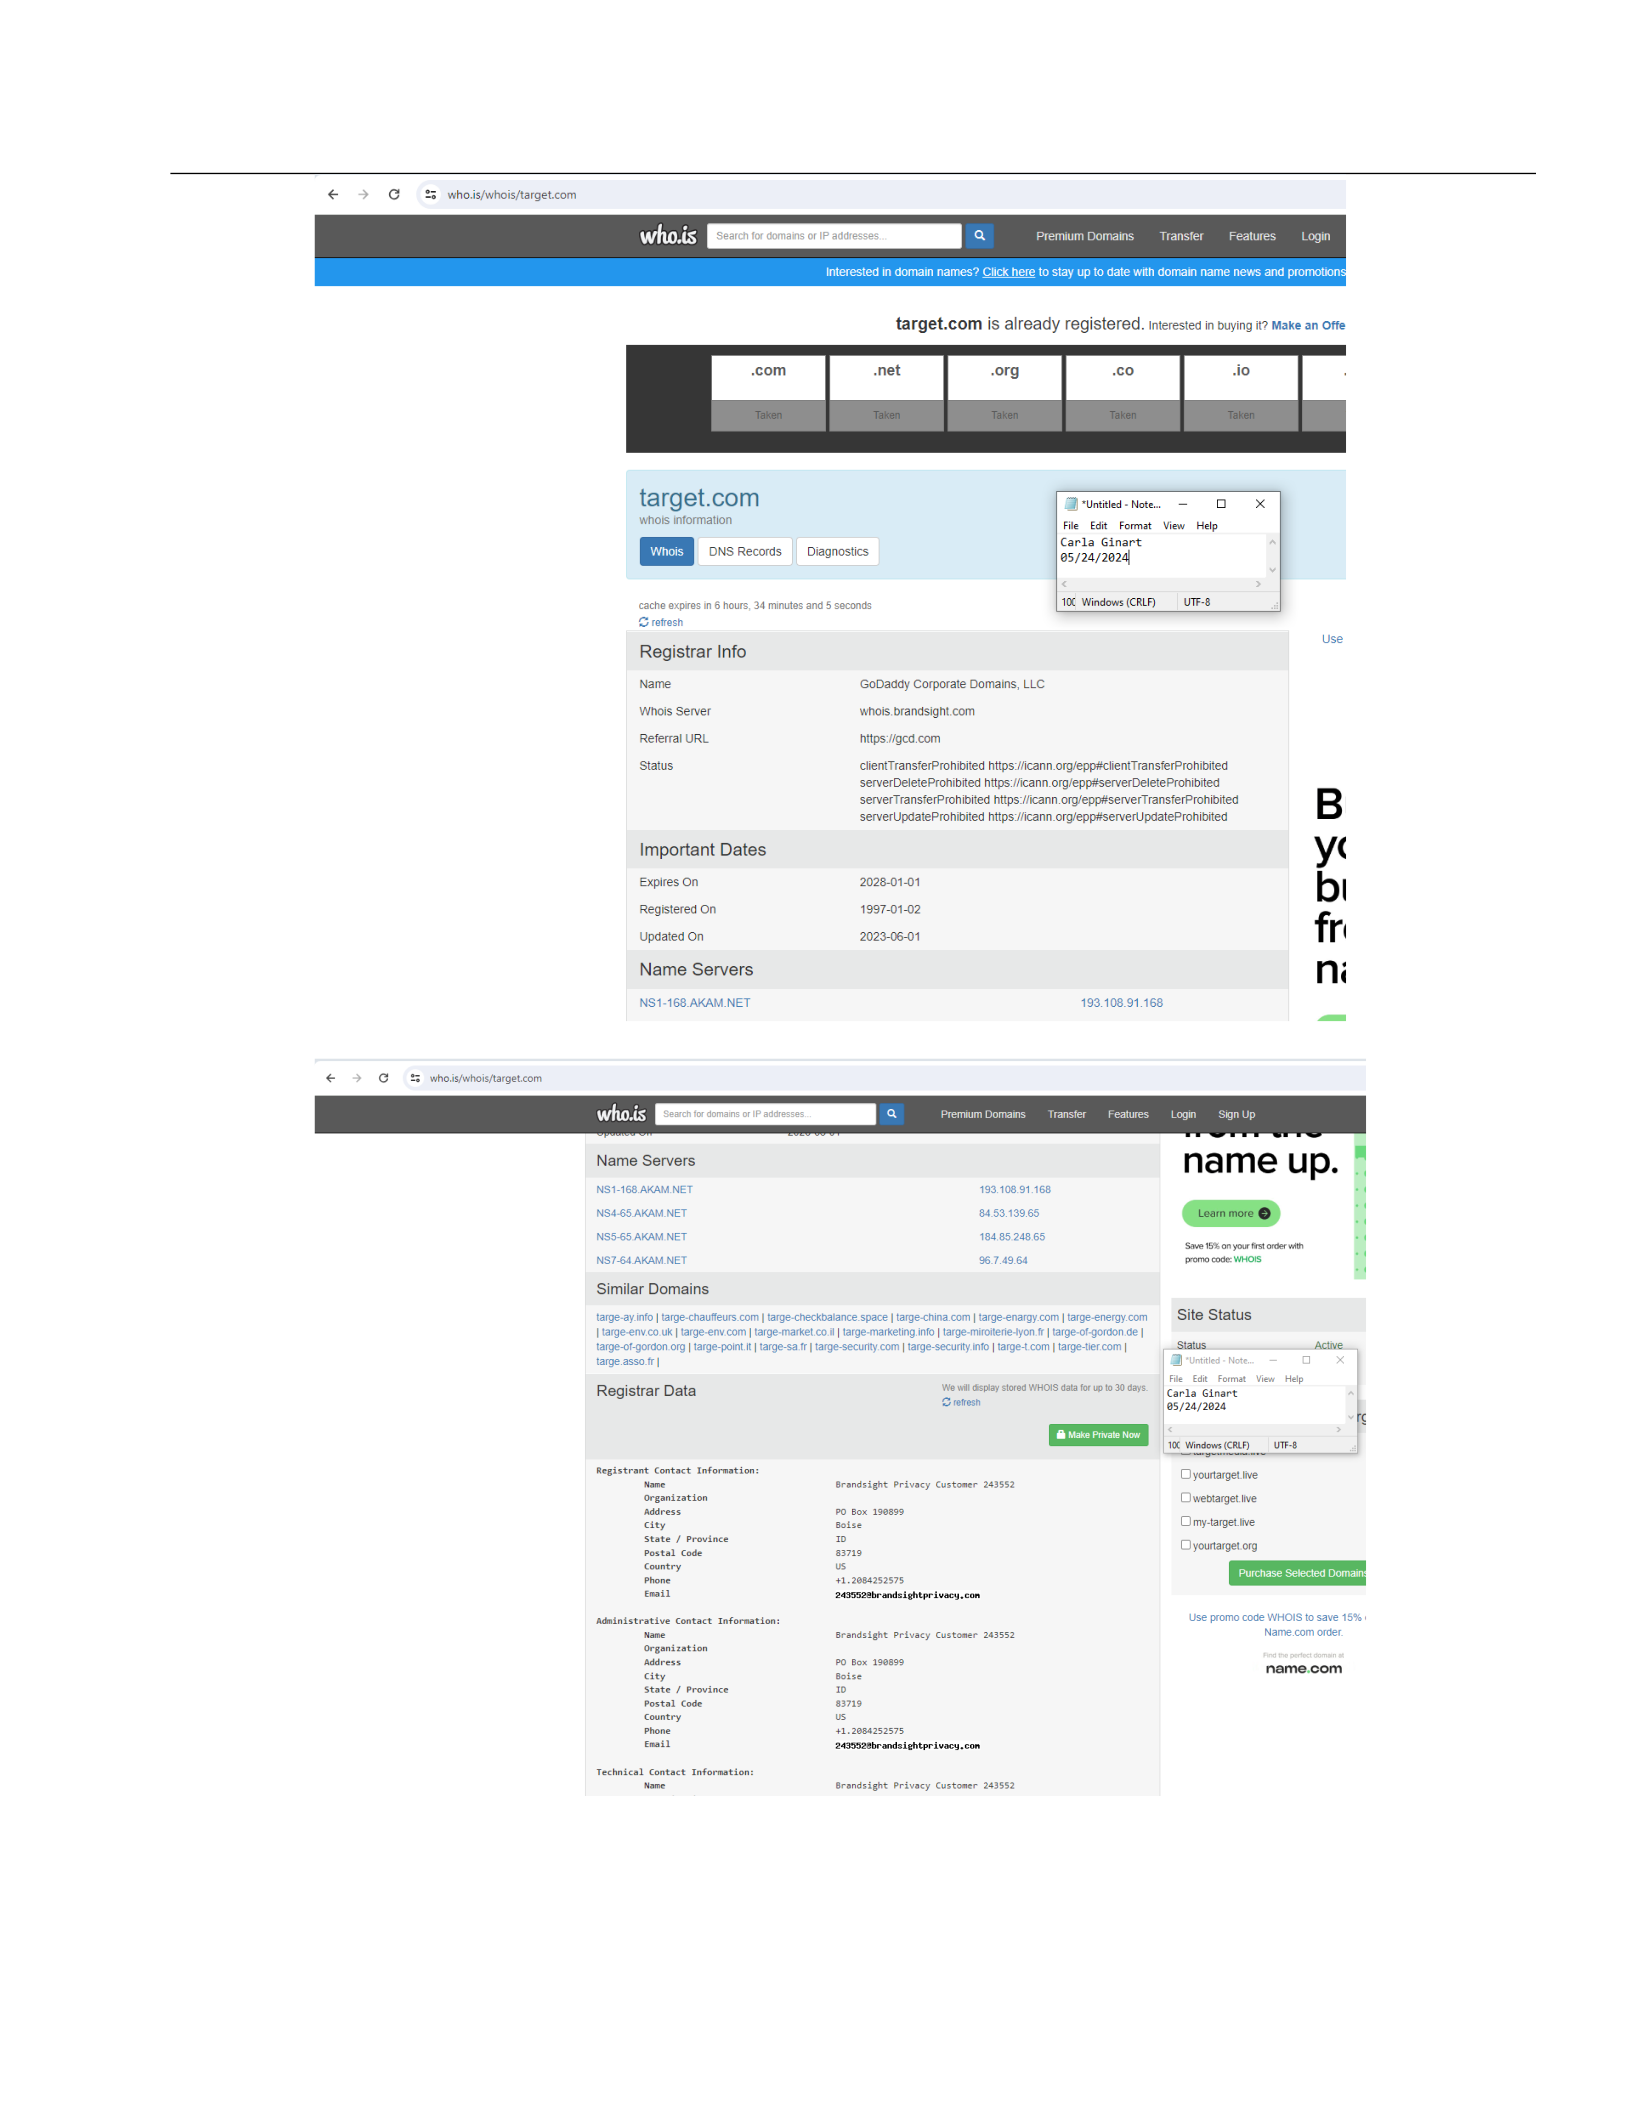
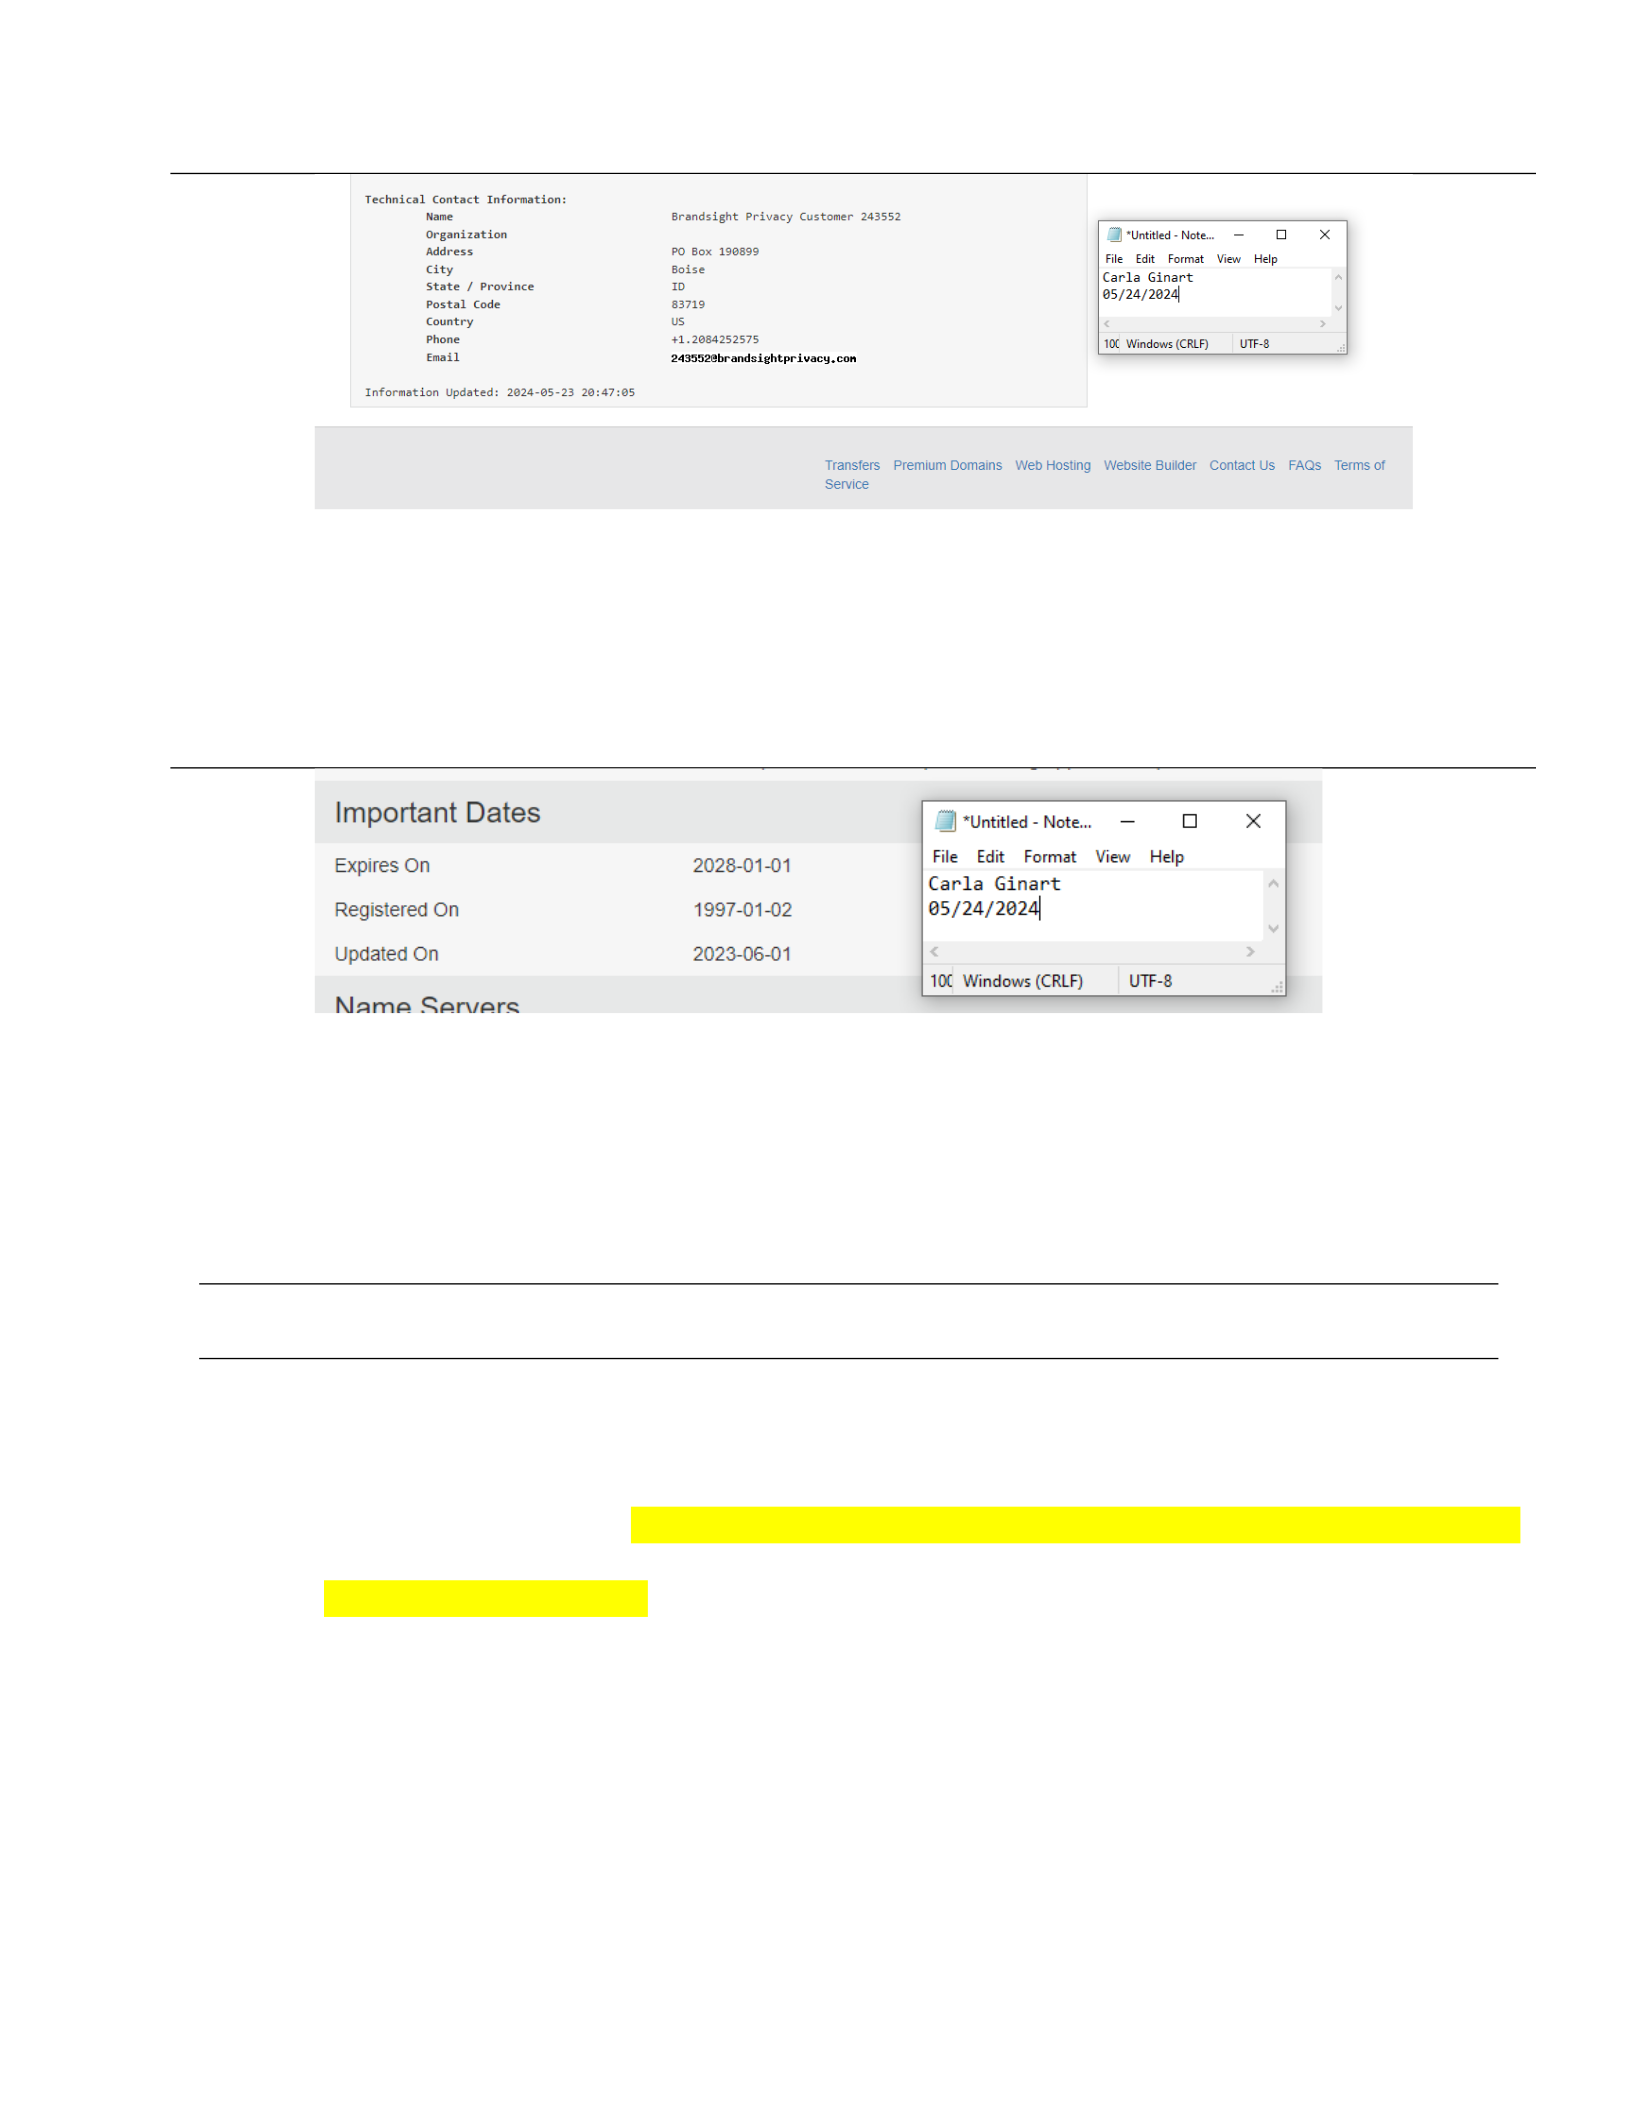
Part 3: Explore the WHOIS Database
o-
<3
who.is/whois/target.com
&3
who.is/whois/target.com
Search
for
domains
or
IP addresses...
Premium
Domains
Transfer
ere
|W
f=te)
Login
Interested
in
domain
names?
Click
here
to
stay
up
to
date
with
domain
name
news
and
promotions
target.com
whois
information
DNS
Records
Diagnostics
cache
expires
in
6
hours,
34
minutes
and
5
seconds
target.com
is
already
registered.
interested
in
buying
it?
Make
an
Offe
)
*Untitled
-
Note...
—
a
x
File
Edit
Format View
Help
Carla
Ginart
05/24/2024
10C
Windows
(CRLF)
UTF-8
S
refresh
Registrar
Info
Name
Whois
Server
Referral
URL
Status
Important
Dates
Expires
On
Registered
On
Updated
On
Name
Servers
N331-168.AKAM.NET
Search
for
domains
or IP
addresses__
Tash
Name
Servers
NS1-168.AKAM.NET
NS4-65.AKAM.NET
NS5-65.AKAM.NET
NS7-64.
AKAM.NET
Similar
Domains
GoDaddy
Corporate
Domains,
LLC
whois.
brandsight.com
https://gcd.com
clientTransferProhibited
https://icann.org/epp#clientTransierProhibited
serverDeleteProhibited
https://icann.org/epp#serverDeleteProhibited
serverTransferPronibited
nttps://icann.org/epp#servertransferPronibited
serverUpdateProhibited
https://icann.org/epp#serverUpdateProhibited
2028-01-01
1997-01-02
2023-06-01
193.106.91.168
CMM
Be]
CTL}
193.108.91.168
84.53.139.65
184.85.248.65
96.7.49.64
targe-ay.info
|
targe-chauffeurs.com
|
targe-checkbalance.space
|
targe-china.com
|
targe-enargy.com
|
targe-energy.com
|
targe-env.co.uk
|
targe-env.com
|
targe-market.co..il
|
targe-marketing
info
|
targe-miroiterie-lyon ‘r
|
targe-of-gordon.de
|
targe-of-gordon.org
|
targe-point
it
|
targe-sa.fr
|
targe-security.com
|
targe-security.info
|
targe-t.com
|
targe-tier.com
|
targe.asso.fr
|
Registrar
Data
Registrant
Contact
Information:
Name
Organization
Address
city
State
/
Province
Postal
Code
Country
Phone
Email
Administrative
Contact
Information:
Name
Organization
Address
city
State
/
Province
Postal
Code
Country
Phone
Email
Technical
Contact
Information:
Name
‘We
will
display
stored
WHOIS
data
for
up
to
30
days.
refresh
Brandsight
Privacy
Customer
243552
PO
Box
190899
Boise
ID
83719
us
+1.
2084252575
2435528br
andsightprivacy,con
Brandsight
Privacy
Customer
243552
PO
Box
198899
Boise
ID
83719
us
+1.
2084252575
243552ebr
andsightprivacy.con
Brandsight
Privacy
Customer
243552
Login
Sign
Up
name
up.
©
ew
+4
Gz
H
ae
“4
ea
Save 15% on
your first
order
with
promo
code:
WHOIS
Site
Status
Status.
Active
@)
“untitled
-
Note...
—
Oo
x
File
Edit
Format
View
Help
Carla
Ginart
05/24/2024
iA
10¢
Windows
(CRLF)
UTF-8
0
yourtarget
live
webtarget
live
U
my-target.live
O
yourtarget.org
Use
promo
code
WHOIS
to
save
15%
Name.com
order.
name.com
PASSIVE RECONNAISSANCE 8
Step 3
PASSIVE RECONNAISSANCE 9
Step 4
Part 4: Collect Information with theHarvester
Step 2 Provide a screenshot as directed.
Your answer goes here. Include a small text editor or command prompt with your typed name
visible, in the screenshot.
PASSIVE RECONNAISSANCE 10
Step 4 Provide a screenshot as directed.
Your answer goes here. Include a small text editor or command prompt with your typed name
visible, in the screenshot.
Step 6 Provide a screenshot as directed.
Your answer goes here. Include a small text editor or command prompt with your typed name
visible, in the screenshot.
Step 8 Provide a screenshot as directed.
Your answer goes here. Include a small text editor or command prompt with your typed name
visible, in the screenshot.
Part 5: Collect Information with Maltego
PASSIVE RECONNAISSANCE 11
Step 8 Provide a screenshot as directed.
Your answer goes here. Include a small text editor or command prompt with your typed name
visible, in the screenshot.
Step 17 Provide a screenshot as directed.
Your answer goes here. Include a small text editor or command prompt with your typed name
visible, in the screenshot.
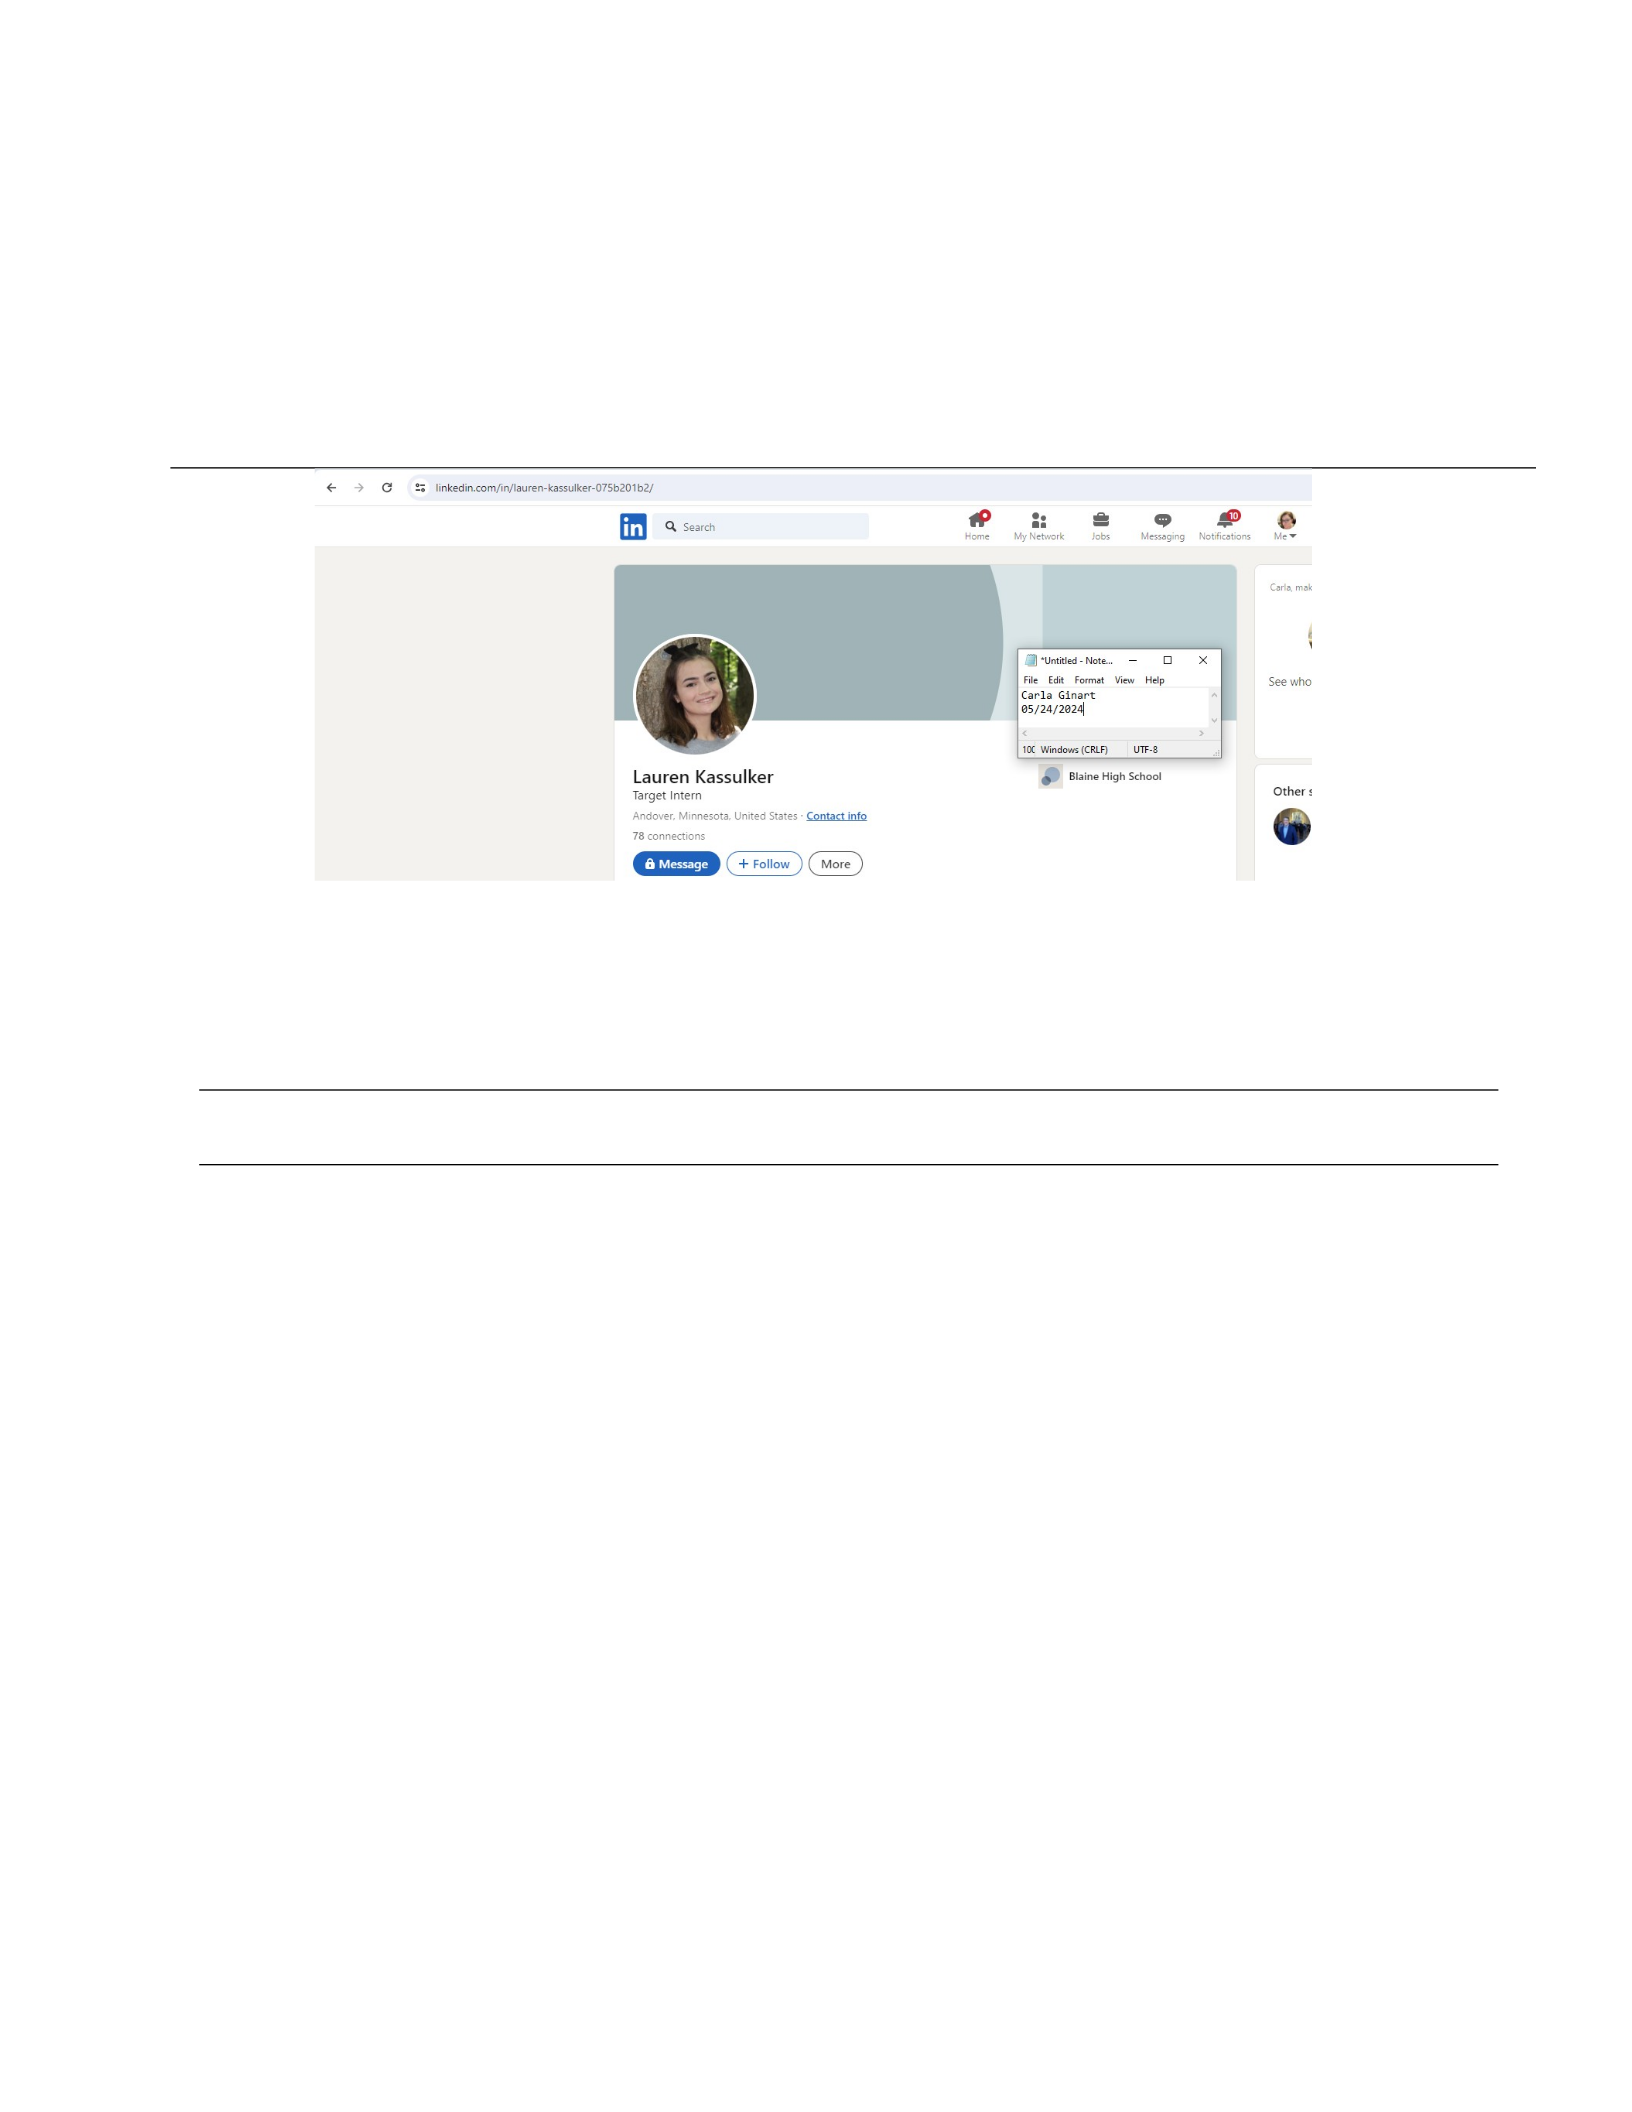
Part 6: Gather Social Engineering Data with LinkedIn
Step 7
PASSIVE RECONNAISSANCE 12
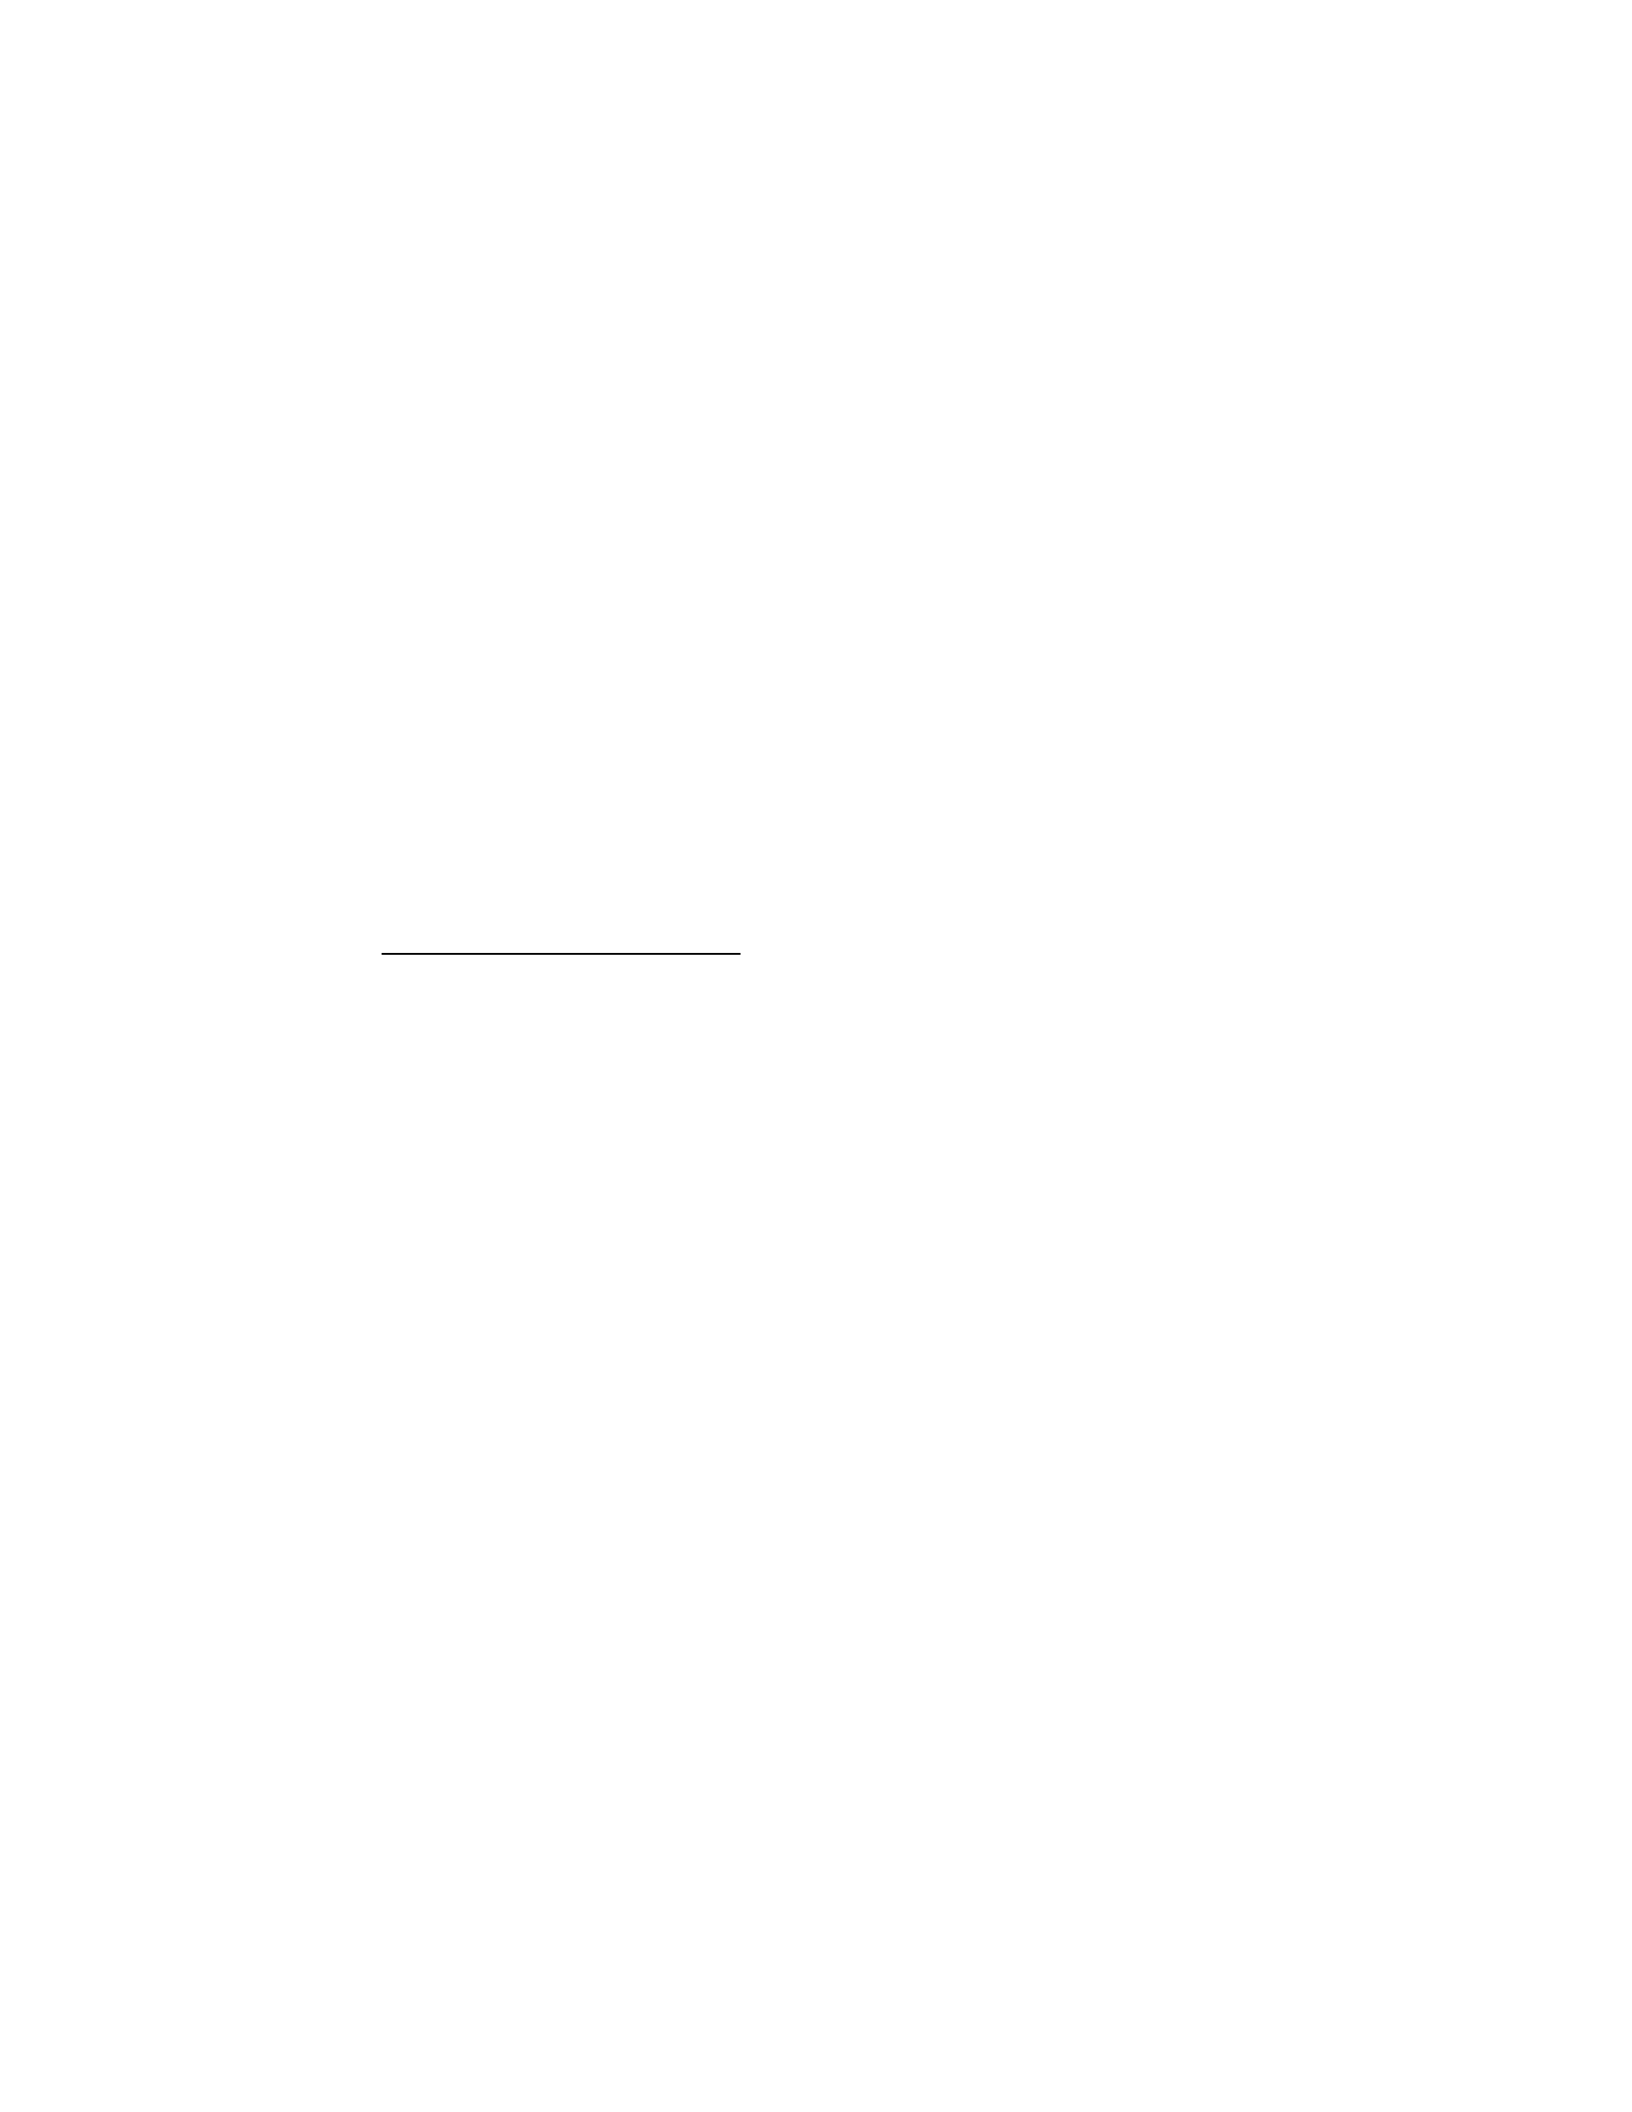
Step 16
Part 7: Going Deeper
Passive Reconnaissance Essay
Passive Reconnaissance
The goal of passive reconnaissance is to learn as much as possible about computers and networks
that are being targeted without actively interacting with the systems. It is information collection
done without warning the victim. Security against the attack is significantly increased if the
victim host is informed. In network penetration testing, having a clear passive reconnaissance
procedure is essential. This first stage, despite its seeming simplicity, establishes the framework
for the entire evaluation. Taking a methodical and organized approach guarantees that no
important details are missed or ignored. It acts as a tactical road map, assisting the tester in
navigating the complex network of IP addresses, domain names, and possible attack vectors.
(Scott, 2024) While it is hard to protect against passive reconnaissance since it is almost

PASSIVE RECONNAISSANCE 13
impossible to detect, there are some ways to help protect against it. One method to not only help
prevent passive reconnaissance but other types of network reconnaissance are MultiRHM. Each
of the numerous cyber agility and cyber deception strategies that make up MultiRHM works in
concert with the others to defeat distinct forms of network reconnaissance without creating
conflicts. MultiRHM thwarts reconnaissance by disguising or masking network hosts' identity.
By distributing the IP and MAC addresses of the hosts at random and anonymizing their
fingerprints across phony machines that have the same fingerprints, this obfuscation is
accomplished. To obstruct the reuse of information and lateral movements, MultiRHM also
randomizes these parameters throughout time and space. (Jafarian,2023) Some other ways to
help prevent passive reconnaissance from being successful would be to keep as much code,
network data, IP addresses, usernames, and other information private as you can. Update the
packages in the repository. Make lengthy passwords and switch them out frequently. Make sure
that any code and endpoints that are visible to the general public are secure and require
authentication. To keep API and security keys hidden from the public, use secret managers or
key vaults. Having engineers conduct passive reconnaissance on their systems to see what they
can find is probably the best method to keep sensitive data private. They can regenerate and
make private whatever they uncover that they don't want to be public, including IP addresses,
domain names, and keys. Although it is difficult to stop passive reconnaissance, regular self-
reconnaissance activities can identify any weaknesses and address them before they become
serious issues. (Proctor, 2023)
Search Operators
One person who helped popularize the practice of footprinting a target was Johnny Long, a member of the
IT security team at his place of employment, in late 2004. He began observing how Google's search
strings functioned while conducting pen testing and ethical hacking. There have always been extra
PASSIVE RECONNAISSANCE 14
operators in the search engine that let you customize your search query. All Mr. Long did was use that
reasoning for a more sinister end. In order to find vulnerabilities, Google hackers manipulate a search
string using extra operators. You can get assistance with Google hack strings from a plethora of sources
(not to mention Google provides multiple support pages for each operator in use). Some examples of
search operators that can be used include the following:
Info:string like info:nytimes.com (shows information google stores about the page itself)
Inurl:string like inurl:nytimes.com (displays pages with the string in the url.)
Link:string like link:nytimes.com (displays linked pages based on a search term)
Site:domain or webpage like site:nytimes.com (displays pages for a specific website or domain
holding the search term)
To add another example of what you could do with a google search, you can use the Google
search syntax, site:exploit-db.com firefox, to search the site exploit-db.com for Firefox exploits.
(Shields, 2024)
theHarvester
The Edge-Security team created theHarvester, a command-line program (whose initial 't' is
intentionally spelled lowercase). It's a Python-based application designed to help identify an
organization's online external danger landscape in the early phases of an inquiry by utilizing
open source intelligence (OSINT).The tool's original intended use was during the early phases of
a red team or penetration test engagement. But depending on the circumstance, the Harvester's
passive scouting skills also make it appropriate for blue or purple teams. (Borges, 2024) Two
command switches that can be used when using theHarvester is -d and -b. These are used to
search for the domain (-d) and using Google as the data source (-b).
Maltego
Maltego is the all-in-one tool for link analysis. Maltego offers real-time data mining and
information gathering, as well as the representation of this information on a node-based graph,

PASSIVE RECONNAISSANCE 15
making patterns and multiple order connections between said information easily identifiable.
Maltego compiles and arranges data according to a domain name, similar to theHarvester. In
addition to email addresses, Maltego can gather data on groups of individuals, organizations, and
the network itself. But it accomplishes this by graphically representing the objects and their
relationships to one another. The Maltego program was used to offer rich graphical data. When
target.com was put into the domain name of Maltego it showed a detailed map of ip addresses
tied to the target domain.
LinkedIn
LinkedIn is the world's largest professional network on the internet. You can use LinkedIn to
find the right job or internship, connect and strengthen professional relationships, and learn the
skills you need to succeed in your career. Since it is so popular it makes for a good site to use
for when doing passive reconnaissance, since so many people having profiles on it. Sometimes
when you search for a member for a certain company to find employees that may work there,
you will see LinkedIn Member instead of that person’s first and last name. This means that that
person is outside of your network. To get around this you can go to a recruiting site, like
recruitin.net, then press the LinkedIn button and then you can paste that user’s job title and
location into the search box. Then you can click on open in Google and you can uncover the
first and last name of that user’s profile. It also allows you to click the link in Google to take you
to that persons LinkedIn profile.
Passive Reconnaissance and the Bible
Passive reconnaissance and satan’s attack can be linked in Biblical worldview, because just like you
would do searches with public information to gain information about a target, Satan will do the same
thing to launch an attack against you. “Be sober-minded; be watchful. Your adversary the devil prowls

PASSIVE RECONNAISSANCE 16
around like a roaring lion, seeking someone to devour. Resist him, firm in your faith, knowing that the
same kinds of suffering are being experienced by your brotherhood throughout the world.” -1 Peter 5:8-9
As company if you want to protect yourself against a passive reconnaissance attack you need to try to
keep as much of your company information as private as possible. As a Christian we must do the same
thing as well. “And to aspire to live quietly, and to mind your own affairs, and to work with your hands,
as we instructed you,” -1 Thessalonians 4:11. The less we tell others about our lives the better. Satan
will use others to attack you, without you even realizing it. A close friend could easily turn into an
enemy. “And no wonder, for even Satan disguises himself as an angel of light.” -2 Corinthians 11:14.
Satan can attack in any disguise including a friend that you have shared information with. Passive
reconnaissance in the same way. A simple post somewhere or a profile created with information that the
public can access can cause a hacker to be able to attack your company.
Lab Assignment
In this lab I learned how easily it is to find information on a company and how easy it is to find
out information about someone that works there, even if they feel they have hidden their
information well. There are many tools available to help you gather that information. My
favorite part of the lab was the section using LinkedIn. I have a LinkedIn account and I had
never really thought about how someone could use that information to try and gain access to the
network at the company that I worked for. So it was really nice to be able to do something that
can tie in with my actual life and shows me how easy it is to get around privacy settings. The
steps that I had challenges with was Part 2 Step 6 because a lot of the links that I was trying to
use would keep throwing an error that told me no information was available. Other than that
everything worked really well and made a lot of sense when doing the lab and I learned a lot
doing this lab. I don’t think I would change anything about this lab, it was very informative and
taught me a lot of things that I wouldn’t trade. I am looking forward to seeing what else I learn
throughout this course.
PASSIVE RECONNAISSANCE 18
References
Borges, E. (2024, April 28). SecurityTrails | theHarvester: A classic open source intelligence
tool. Security Trails Blog. https://securitytrails.com/blog/theharvester-tool
Jafarian, J. H., & Niakanlahiji, A. (2023). MultiRHM: Defeating multi-staged enterprise
intrusion attacks through multi-dimensional and multi-parameter host identity
anonymization. Computers & Security, 124. https://doi.org/10.1016/j.cose.2022.102958
Proctor, A. (2023, March 27). Passive reconnaissance: What you need to know. Firewall Times.
https://firewalltimes.com/passive-reconnaissance/
Scott, J. (2024, January 16). Pentesting 3: Passive reconnaissance. Cyber Hacktics.
https://cyberhacktics.com/pentesting-3-passive-reconnaissance/
Shields, D.(2024). Ethical Hacking. McGraw-Hill Create.
https://bookshelf.vitalsource.com/books/9781307881974

