


1
Tech LandscapeRisk Mitigation Strategy.
Student Name
Professor
Unit Code
Date

2
Introduction
Risk assessments and mitigation involve implementing processes to effectively regulate,
eliminate, or significantly limit the impact of potential impediments, hence reducing their
severity. They avert potential dangers from escalating into unmanageable catastrophes.
Management is tasked with not only formulating and implementing the strategy but also
overseeing its advancement and assessing the need for any modifications. The process of
developing a risk mitigation plan consists of several stages, namely risk identification, risk
assessment, risk periodization, risk mitigation proposal, and risk residual and review.
1. Risk Identification:
Risk identification is an essential initial stage in the risk management process, vital for
foreseeing potential obstacles that may affect the smooth functioning of a firm. Essentially, it is
the systematic investigation and categorization of potential risks and weaknesses across many
aspects of an organization's operations. This procedure is not limited exclusively to adverse
occurrences; it also includes favorable circumstances that, if identified and utilized, might
improve the company's performance (De Bruin & Goulart, 2020). The goal is to develop a
thorough and sophisticated comprehension of the business environment, ensuring that potential
risks are not only recognized but also acknowledged and assessed. Within the Tech Landscape,
the risk identification division plays a crucial role in revealing the wide range of dangers that
could potentially jeopardize its operations. The hazards encompass technological, financial, and
legal compliance aspects, illustrating the complex nature of the modern company landscape. The
risk identification process establishes the foundation for further assessments by outlining
prospective obstacles, including cyber security concerns, market swings, and regulatory

3
compliance issues. Every detected risk acts as a fundamental component of the comprehensive
risk management plan, facilitating the development of specific and efficient methods to minimize
or eliminate the risks.
The efficacy of the risk identification phase depends on its comprehensiveness, ensuring that no
substantial risk is disregarded. This requires cooperation and the exchange of information among
different departments within the organization. By cultivating a culture that promotes vigilance
towards risks and openness in communication, firms can improve their capacity to tackle
obstacles proactively. In essence, the process of identifying risks is not a singular event but
rather a continuous and iterative undertaking that corresponds to the ever-changing nature of the
corporate environment. It serves as a guiding tool for organizations to take a proactive approach
to handling uncertainty, therefore strengthening their ability to withstand challenges and
maintain long-term viability.
2. Risk Assessment:
Risk assessment is the second step and crucial step in the risk management process that entails a
systematic review of the identified risks to ascertain their potential impact and probability of
occurrence. This approach aims to measure and assess the risks by assigning numerical numbers
to both their potential impact on the business and the likelihood of their occurring. The objective
is to offer a systematic and measurable foundation for decision-making, enabling companies to
allocate their efforts and resources towards the most notable dangers (Zhang, 2021). By doing a
thorough risk assessment, firms acquire valuable information about the possible outcomes of
each risk scenario and can then customize their tactics for minimizing those risks. Within the
Tech Landscape, the risk assessment component functions as the analytical foundation of the risk

4
management plan. An exhaustive examination is carried out for every detected risk, taking into
account the particular circumstances and weaknesses of the online technology marketplace. The
organization obtains a comprehensive comprehension of its most significant vulnerabilities by
providing numerical values to both effect and likelihood.
The justifications provided with these evaluations serve to explain the reasons behind the given
values, promoting clarity and helping stakeholders understand the complexities of the risk
landscape. Assumptions and dependencies are essential components of risk assessment. It is
crucial to document these elements since it helps to put the risk evaluations into context and
serves as a basis for future changes. As the potential dangers change over time, the assessment of
those dangers also adapts, resulting in a flexible and ongoing procedure. Ultimately, risk
assessment serves as the guiding principle for decision-makers, allowing them to efficiently
allocate resources and implement focused risk mitigation methods that match with the company's
overarching goals.
3. Prioritization of Risks:
Risk prioritization is a strategy process in risk management that sorts known risks by how likely
they are to happen and how bad they could be if they do. This lets resources be put toward the
most important threats. When companies take this important step and think about how to divide
up prevention efforts, they can make a more focused and effective risk management plan. Risk
grids and other visual aids are used to show which risks are high, medium, and low priority to
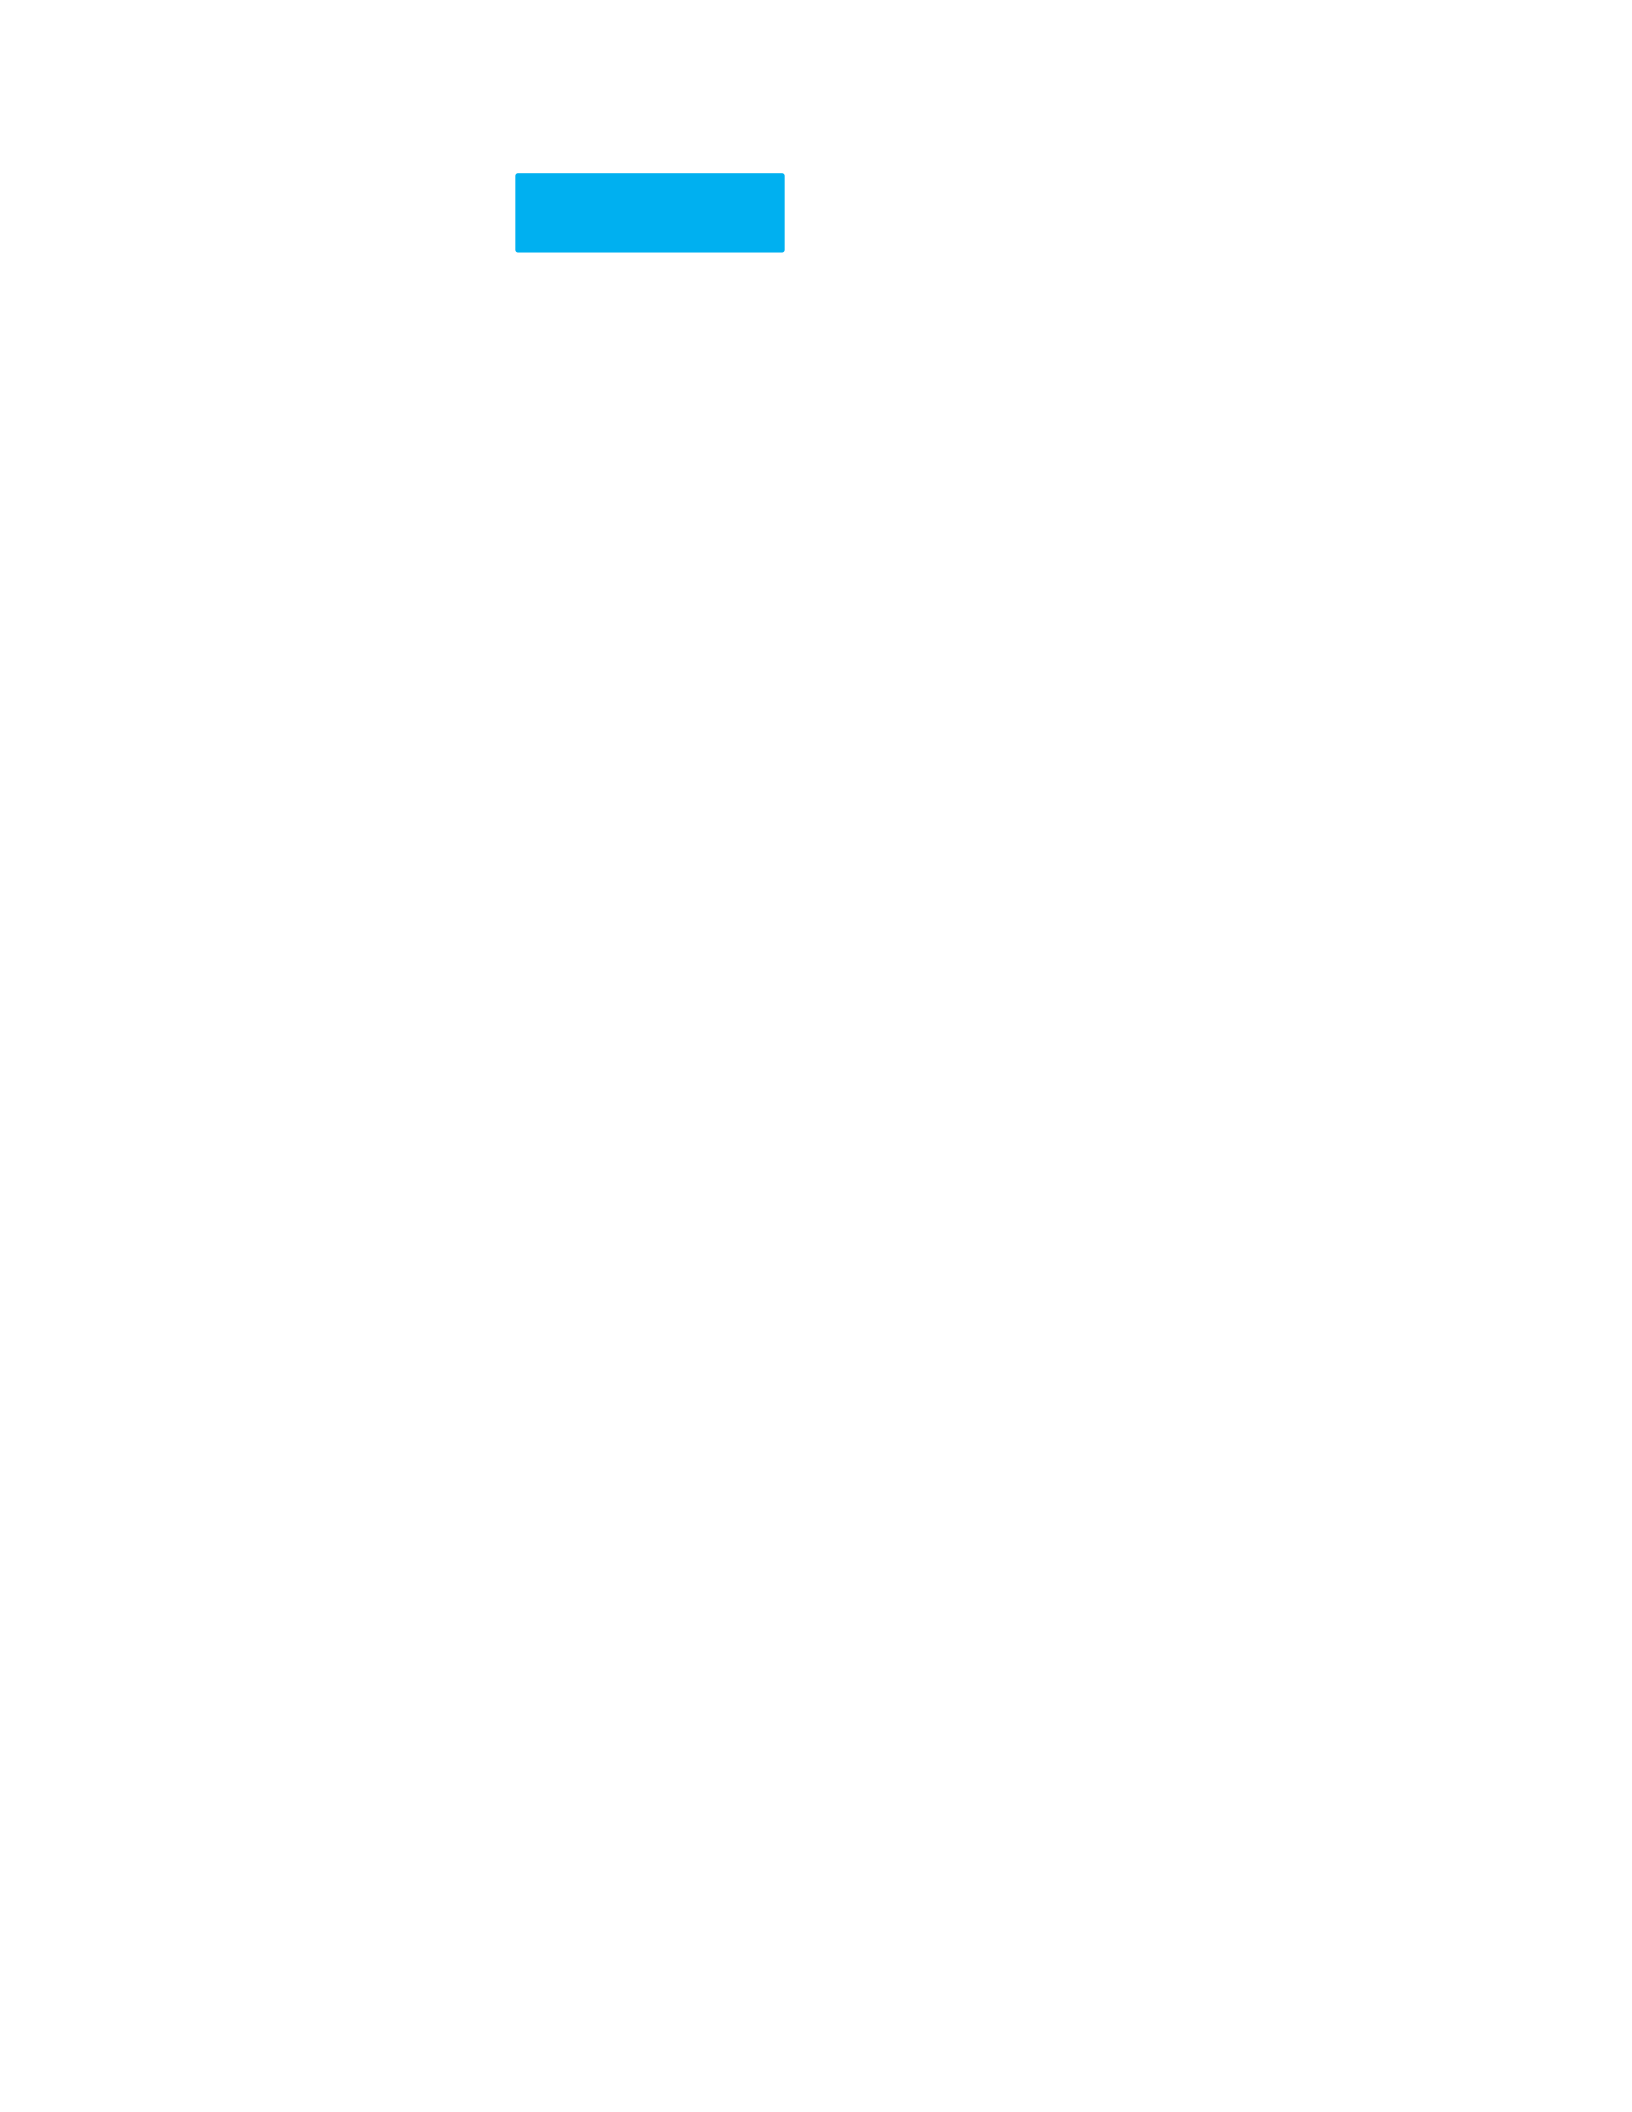
help people understand how important each risk is (Zhang, 2021). In a scale of 1-5 represent high
risk 6 to 8 represent medium and low priority are represent by 9 -10. The main goal of risk
5
priority is to make the best use of resources to protect against the most likely and damaging risks.
This helps the business deal with the most important issues first. There are a lot of technical,
financial, and legal compliance risks in the tech landscape. When hazards are carefully ranked by
how important they are, efforts and resources can be better distributed (Feng & Yang, 2020).
This method ensures a slow and preventative response, which fits with Tech Landscape's main
goals. This creates a risk management plan that is strong and flexible. To keep the plan adaptable
to changing business conditions, the risk priorities need to be looked at and changed on a regular
basis.
Risk Assessment Matrix
Risk High Medium Low Priority
System Downtimes
Cyber attacks
Credit and Liquidity
risk
Market and
Fluctuations
Contractual Risk
Key
High Risk 1-5
Medium 6-8
6
Low 9- 10
4. Risk Mitigation Proposal:
The Risk Mitigation Proposal is a thorough plan created to manage and reduce the potential
consequences of recognized risks on a firm. This important part of risk management is all about
dealing with uncertainties ahead of time to make sure the organization's processes run smoothly
and successfully. This part goes over the different types of risks that have been found and the
specific, individualized steps that will be taken to deal with them (Guzik & McInnes, 2020).
These steps will cover the physical, financial, and legal aspects of following the law. The Risk
Mitigation Proposal for Tech Landscape is implemented through a comprehensive and complex
strategy. The plan highlights the importance of taking urgent actions to address technological
threats, such as deploying state-of-the-art cyber security solutions and upgrading infrastructure.
Diversification and planning for the worst are two ways to lower your financial risk with market
volatility and keep your finances stable during tough times. We deal with legal and compliance
problems in a number of ways, including short-term steps like keeping you up to date on changes
in the industry and long-term steps like setting up a strong system for monitoring compliance.
The idea surpasses mere risk control by integrating risk financing solutions, guaranteeing that the
organization not only mitigates or reduces the likelihood of hazards but also possesses the
capacity to manage potential financial consequences through initiatives such as contingency
funds. The emphasis on both immediate and future initiatives demonstrates a comprehensive and
flexible approach to risk management in accordance with Tech Landscape's overall goals in the

7
constantly changing online technology sector. The Risk Mitigation Proposal acts as a proactive
plan, directing the company towards resilience and sustainability in response to various and ever-
changing risks.
5. Assessment of Remaining Risk and Evaluation
The Residual Risk and Review Proposal is an important part of risk management because it finds
threats even after protective measures have been put in place. To keep a full picture of the risk
environment, it is important to find these last few threats. The plan stresses the need for a full
evaluation of how tolerable these remaining risks are. An in-depth study that looks at the
possible outcomes of remaining risks and how well the measures put in place are working is
needed for this (Feng & Yang, 2020). Tech Landscape finds out if the remaining risks are
acceptable based on its risk tolerance levels or if more needs to be done by checking to see if
these threats are acceptable.
The idea also stresses the importance of setting up ways to keep an eye on things all the time.
This preventative approach needs to be constantly watched to make sure that the measures put in
place continue to work. Tech Landscape can quickly find new risks or changes in the working
environment and take action because it is constantly monitoring. In addition, the risk
management strategy is now being evaluated on a regular basis. This gives a structured way to
look at and change the present strategies. It is very important to keep the risk management
strategy up-to-date and adaptable so that it can work in the constantly changing online IT market.
With the Residual Risk and Review Proposal, Tech Landscape improves its ability to deal with
future risks strongly and strategically. It also takes care of pressing issues.

8
References
De Bruin, & Goulart, M. (2020). Initial impacts of global risk mitigation measures taken during
the combatting of the COVID-19 pandemic.?Safety Science,?128, 104773.
Zhang, Y

9
. (2021). Improving risk identification of adverse outcomes in chronic heart failure using
SMOTE+ ENN and machine learning.?Risk management and healthcare policy, 2453-
2463.
Guzik, & McInnes, I. B. (2020). COVID-19 and the cardiovascular system: implications for risk
assessment, diagnosis, and treatment options.?Cardiovascular research,?116(10), 1666-
1687.
Feng, L., & Yang, W. (2020). Disruption risks in supply chain management: a literature review
based on bibliometric analysis.?International Journal of Production Research,?58(11),
3508-3526.

