


Effective Internal Control Strategies for an
Enterprise Resource Planning System
Section 1: Foundation of the Study
Businesses have seen advances in accounting information systems that improve
operations, reduce errors, and enhance productivity (Jasim & Raewf, 2020). Recent
advancements in accounting information systems are the enterprise resource planning
(ERP) system that integrates accounting and business functions and allows for real-time
processing and information generation (Trunina et al., 2018). Management information
technologies are an integral part of an organization’s risk management strategy
(Vovchenko et al., 2017). With the implementation of an ERP system, risk managers
have the opportunity to enhance internal controls (Elbardan et al., 2016).
Background of the Problem
Financial institutions and organizations have been at the forefront of adopting
strategies to prevent fraud. One of the measures that can be used to achieve this milestone
is data-driven auditing (Singh et al., 2019). According to Chen et al. (2016), external
monitoring can play an instrumental role in preventing financial fraud within business
organizations. ERP systems, databases, and the internet are the new form of organizing
operations that will integrate activity types and control them in real-time (Trunina et al.,
2018). Despite the large volume of research on ERP systems, the impact of ERP systems
implementation on the internal control system and subsequently on the IAF remains
poorly understood. ERP systems are built from interdependent modules, and their

business risks and audit risks significantly differ from traditional computer systems
(Privitera & Ahlgrim-Delzell, 2018). External monitoring involves coordinated efforts
with key stakeholders to develop a robust anti-fraud system. Financial organizations
focused on developing plans for fraud prevention are likely to experience an increase in
operations. When a business uses an external monitoring technique, it prevents financial
resource loss (Chen et al., 2016). Internal audits are also instrumental in business
operations, preventing possible financial fraud (Yigzaw et al., 2017). In this study, I
explored the effective internal control strategies for business leaders' ERP systems to
reduce risk reporting and erroneous transactions.
Problem Statement
Without an effective internal control strategy, the implementation of an ERP
system is a source of risk exposure to an organization (Messabia et al., 2020).
According to Eker and Eker (2018), there is a significant positive correlation between
financial reporting quality and ERP-internal controls (β = .495; t = 6.836, p = .000).
The general business problem was without an active internal control structure in an
ERP system, organizations are susceptible to fraudulent and erroneous transactions and
reporting. The specific business problem was that some business leaders lack effective
internal control strategies for ERP systems to reduce risks from reporting and erroneous
transactions.
Purpose Statement
In this study, I explored effective internal control strategies for ERP systems
business leaders use to reduce risks from reporting and erroneous transactions. The

target population for this study included seven participants at one business in Mississippi
who have successfully implemented effective internal control strategies for their ERP
systems. The positive social change implication is that the resident’s benefit may be
enhanced community stability where employment opportunities increase, thereby
increasing the betterment of the community.
Nature of the Study
There are three types of studies: quantitative, qualitative, and mixed studies.
Quantitative researchers use statistical data collection techniques to measure variables
and test hypotheses about variables’ relationships or groups’ differences (Zyphur & Pieri-
des, 2019). Qualitative researchers use semistructured interviews to understand the mean-
ing of a phenomenon (Yin, 2018). Mixed-method researchers use qualitative and quanti-
tative methods in the same study (Sahin & Öztürk, 2019). I chose a qualitative method for
this study.
Principal qualitative research designs include phenomenology, ethnography, and
case study (Goldman et al., 2015). Researchers use a phenomenological design to explore
participants’ lived experiences (Yin, 2018). My goal was not to explore the lived
experiences of participants. Thus, a phenomenological design was not suitable.
Researchers use ethnography to explore the characteristics of an intact culture (Dhar,
2014). The ethnographic design is inappropriate for my study as I was not exploring a
cultural phenomenon. Researchers use a case study design defined by Yin (2018) as a
detailed exploration using multiple data collection techniques to explore a bounded
system in its place and time (Marshall & Rossman, 2016). I selected a single case study

design to gather and gained in-depth knowledge and rich data to explore a bounded
system in its natural setting. A single case study is appropriate when the researcher is
interested in a concentrated holistic understanding of a single unit (Gaya & Smith, 2016).
Research Question
What effective internal control strategies for ERP systems do business leaders use
to reduce risk reporting and erroneous transactions?
Interview Questions
1. What internal control strategies for your ERP system did you use to reduce
fraudulent reporting and erroneous transaction risks?
2. What key barriers to implementing your internal control strategies for your
ERP system did you encounter to reduce fraudulent reporting and erroneous
transaction risks?
3. How did you address the key challenges to implementing your strategies for
internal controls for your ERP system to reduce fraudulent reporting and
erroneous transaction risks?
4. How have you measured the effectiveness of your ERP internal control
strategies for fraudulent reporting and erroneous transaction risks?
5. How has your organization used internal controls processes, from the
strategies to monitor activity to fraudulent reporting and erroneous
transaction risks in your ERP system?

6. What additional information can you provide about your internal control
strategies in your ERP systems to mitigate reporting and erroneous
transaction risks?
Conceptual Framework
In 1994, the Committee of Sponsoring Organizations of the Treadway Commis-
sion (COSO) developed a model for evaluating internal controls (COSO, 2017). Business
leaders use the COSO framework to develop effective internal controls (Moeller, 2014).
Business leaders use the COSO model for guidance when developing internal controls to
achieve organizational objectives. According to Altheebeh and Sulaiman (2016), the
COSO model encompasses (a) control environment, (b) risk assessment, (c) control activ-
ities, (d) information and communication, and (e) monitoring. The foundation of internal
sound controls within an organization includes leadership, shared values, and a culture
that emphasizes accountability. I expected the COSO model to be appropriate for this
study as the model contains holistic and functional components applicable to the develop-
ment of ERP system internal controls.
Operational Definitions
Accountability: An organization or an individual who shows or accepts the
responsibility of engaging in specific activities or processes and remaining
transparent when disclosing the results (Fernandes et al., 2018).
Enterprise resource planning (ERP): A software system used to unify data
and business processes, including accounting and finance, HR, management,
customer relationship management, and supply chain management (Moldof, 2015).

Fraudulent reporting: An act where management or an individual
intentionally misrepresents financial statements to give a false impression to the
investors about a company's performance (Moeller, 2014).
Integrated framework principles: A tool used to manage data movement
between applications and organizations and contains important standards in the
integration policies and their acceptance in the organization (Binder, 2016).
Internal control: internal controls are mechanisms, procedures, and rules that a
firm will adopt and implement to allow for the integration of accounting and financial
activities to prevent fraud and promote accountability (Rodgers et al., 2015).
Assumptions, Limitations, and Delimitations
Assumptions
An assumption is an assertion accepted as truthful (Johnson, 2015). The following
assumptions impacted this study. The first assumption was that effective internal controls
reduce the risk of fraud or errors. The second assumption was that participants would
provide honest answers. The last assumption was that a qualitative single case study is
appropriate for exploring the research question.
Limitations
Yin (2018) described limitations as the characteristics of a research design or
methodology outside researchers' control. Researchers must pay attention to existing
limitations and consider them in their research design (Clark & Vealé, 2018). The first
limitation was of this study is that participants can withdraw at any point in the study.
Second, the results of this study were limited by the honesty and thoroughness of

participants ‘responses. Third, the participants ‘changes in technology may affect the
implementation of internal controls in an ERP system. The last limitation was the results
might be limited by the participants’ knowledge of the subject.
Delimitations
Delimitations are choices that researchers made to frame study boundaries
(Theofanidis & Fountouki, 2018). Delimitations of this multiple case study involved the
geographic location, sample size, and sample group. I studied business leaders in
Mississippi. I restricted the participants from a single business that may impact my
results. The selected participants have the same approaches and face similar challenges.
The adoption of the ERP systems and internal control will solely depend on internal
factors in the business. Thus, the selection criteria affect the pattern, trend, and type of
information acquired in the business. The delimitations provide areas for potential future
research identified in Section 3 of this study.
Significance of the Study
Contribution to Business Practice
Small business owners and managers may benefit from the results of this study by
understanding the relationship or the lack of relationship between an internal control sys-
tem, segregation of duties, and attitude toward internal control. Business leaders could
benefit from the study results by increasing their understanding of internal controls ERP
systems. This study could benefit business leaders by informing them on how to realign
their internal controls best and help create an effective ERP system. A framework of in-

ternal controls could improve accountability and profitability by reducing fraudulent re-
porting and erroneous transaction risks.
Implications for Social Change
The results and findings of this study could benefit society by adding to the strate-
gies that business leaders can use to detect and prevent fraudulent reporting and errone-
ous transaction risks. The successful involvement of the business leaders might contribute
to the effectiveness of handling the internal controls (Brucker & Rebele, 2014; Chen et
al., 2016; Kulikova & Satdarova, 2016). When an organization has strong internal con-
trols, it may increase the business's success and improve the surrounding community's
economic well-being; business leaders who develop effective internal controls could im-
prove communities' social and cultural well-being by providing consistent employment
opportunities. Consistent employment opportunities enhance the stability of local com-
munities by empowering residents to focus on community betterment (Brown & Baker,
2019).
A Review of the Professional and Academic Literature
A literature review is a systematic analysis of prior research on the subject. The
literary works audit survey papers, journals, and other appropriate publications for a
specific research topic. The preceding work needs to be enumerated, defined,
summarized, critically assessed, and explained. A literature review comprises theoretical
and methodological presentations toward a specific topic of study. The purpose of a
literature review is to survey literature, synthesize information, critically analyze
information, and present literal material in an organized manner (Nakano & Muniz,

2018). Mock et al. (2016) referred to the literature review as an essential topic of study.
Readers can use a well-developed literature review to gain a firm understanding of the
research topic, providing a starting point for new ideas and recommendations.
Effective internal control systems in business can reduce the risks of fraudulent
reporting and erroneous transactions, hindering the achievement of ERP business
objectives. My approach in this literature review was to report varied research
perspectives from an ERP internal control lens. The research findings are significant as
they provide insight to business management on how to mold their internal control
environment to better ERP performance.
I searched for recent literature references published within the last five years of
my expected graduation. I searched for relevant articles from repositories, including
ProQuest, EBSCOhost, business websites, Emerald Journals, Walden University Thesis,
Dissertation Collection Sage Journals, and Google Scholar. Search terms included
COSO, internal controls, ERP, enterprise risk planning, and financial statement quality.
The primary source of information is peer-reviewed articles relevant to the topic,
constituting 95% of the total review. In comparison, 5% of the sources were from
books and Walden University Thesis and Dissertation collection.
I conducted a critical analysis of literature related to ERP internal control
functions. In this literature review, I explain scholarly contributions to the
conceptual framework. The literature review structure starts with reviewing my
conceptual framework and then alternative theories to the conceptual framework. In
this case, I relied on the trends, patterns, and assertions made from previous studies

about ERP internal control from articles, books, research papers, and peer-reviewed
journals.
The COSO Framework
The COSO framework was introduced by the Committee of Sponsoring
Organizations of the Treadway Commission in 1992 as a standard framework for
evaluating internal function (COSO, 2017). COSO (2017) described an internal control
as a process effected by an entity’s board of directors, management, and other personnel,
designed to provide reasonable assurance of achieving objectives in an organization.
According to Vovchenko et al. (2017), auditors use the COSO internal control
framework to focus on the effectiveness and efficiency of internal operations, integrity
and transparency of financial reporting, and policy and procedure compliance standards.
COSO (2017) acknowledges that developing an ‘optimal fit’ internal control system can
be challenging. Thus, there is a need to evaluate and assess the internal operations and
aspects of the organization while adhering to an outlined compliance standard.
Organization leaders use the COSO internal control framework to achieve a
standard of enhancing their internal control system (COSO, 2017). Due to the various
changes occurring in the business environment and the need to equip businesses with
robust strategies to respond to the changes, COSO updated its model in 2013 (COSO,
2017). According to Länsiluoto et al. (2016), COSO model updates share the same
framework and are mutually compatible. Organization management experienced many
gaps in their operations, creating opportunities for fraud and errors in financial systems
(COSO, 2017). Organization leaders use the implemented internal control changes in

achieving transparency and accountability of systems to ensure that businesses achieved
objectives and mitigated risks to an acceptable levels. By including a system of guidelines
and requirements for organizations to follow, COSO introduced a practical approach to
internal control that is responsive to changes in the business environment (COSO, 2017).
The updated model applies a principle-based approach centered on the various
dimensions of internal control, expanding the need for internal control in financial and
nonfinancial operations (COSO, 2017). While the traditional model focused on
external reporting, the updated model provides clearer guidelines to support reporting
in both external and internal financial and nonfinancial reporting. COSO expanded its
reporting capacity with the updated model to cover the broader spectrum of business
activities involved in the internal control system. Länsiluoto et al. (2016) stated that
the model emphasized the importance of technology in challenging complex business
changes and improving control over internal control tools.
The COSO model enhances the governance concepts by encouraging the use of
judgment and decision-making by the various organizational managers in internal control
strategies (Länsiluoto et al., 2016). Organizational managers, including the board of
directors and other managers, are designated to design, implement, and regulate internal
control structures. According to Martin et al. (2014), the COSO model's guiding principle
is for leadership to demonstrate a commitment to integrity and ethical conduct.
Monitoring is a critical element of an internal control strategy. Thus, effectiveness
should be monitored using continuous and separate evaluations to ensure that all internal
control elements are functioning as expected (Murphy & Free, 2016). COSO's control

activities include an internal control system. Länsiluoto et al. (2016) stated that the model
emphasized the importance of technology in challenging complex business changes and
improving control over internal control tools.
The COSO model enhances the governance concepts by encouraging the use of
judgment and decision-making by the various organizational managers in internal control
strategies (Länsiluoto et al., 2016). Organizational managers, including the board of
directors and other managers, are designated to design, implement, and regulate internal
control structures within an organization. According to Martin et al. (2014), the COSO
model’s guiding principle is for leadership to demonstrate a commitment to integrity and
ethical conduct. Monitoring is a critical element of an internal control strategy. Thus,
effectiveness should be monitored using continuous and separate evaluations to ensure
that all internal control elements are functioning as expected (Murphy & Free, 2016).
COSO’s control activities component is a part of management’s organizational policies
and procedures (Dorsey, 2015; Verschoor, 2015). Management should ensure that there is
deployment, modification, and replacement of control activities at all stages of the
organization to reduce risk and meet operation objectives (Urbanik, 2016 ).
There are recent enhancements to the COSO framework. In a 2017 COSO update,
the report covered the development of managing risks and the necessity for companies to
enhance their risk-management strategy to keep up with the changing economic
environment’s requirements. The new information emphasizes the significance of taking
risk into account throughout the strategy-setting phase and while driving ability. COSO
released new guidelines towards the end of 2020, “Risk Appetite–Critical to

Achievement,” to assist boards, executive officers, and management staff in
acknowledging how an improved comprehension and information exchange of risk
appetite might aid their companies to grow. The guideline focuses on how companies
could perhaps encourage risk appetite as an essential form of decision-making. Risk
appetite is linked to goals and plans, and appetite is used as a component of managing the
company for performance regarding the abundance of risk that the company is prepared
to accept. It’s important to highlight in the report that a company’s risk appetite should be
adaptable enough to keep up with changing circumstances. It is easier to accept the
transformation and be more flexible in difficult situations when one anticipates and
understands one’s risk.
Managers use the COSO framework to develop a control system within an
organization. According to COSO (2017), the internal control system is the heart of the
firm; the purpose of internal controls is to provide life to multiple aspects of the business.
COSO outlines internal awareness and expertise among management as the underlying
factors behind the internal control. The use of the COSO framework creates insights into
areas in which management should aim to build internal awareness and control the
internal control tools. Davis et al. (2017) suggested that the framework provides
management and the board of directors with a principle-based approach to internal
control. COSO is appropriate for any organization as its. The framework provides a
criterion for the executive management to identify and analyze risks, leverage
opportunities in the business environment, and allow for more accountability and
transparency of financial systems (Machado et al., 2017).

Integrated Framework Principles
Committee of Sponsoring Organizations (2013) framework helps organizations
achieve a reliable, timely, transparent, and professional financial reporting system that
adheres to organizational and international reporting standards. COSO presents the
internal control framework as a cube model with three central dimensions: operations,
reporting, and compliance (see Figure 1). Internal controls are a part of the integrated
system involving the three dimensions (COSO, 2017). According to Rae et al. (2017), the
framework provides organization leaders support towards achieving organizational goals.
Reporting objectives are the quality of financial reporting, both internal and external (Rae
et al., 2017). Compliance objectives relate to an organization's ability to conform to the
laws and regulations it is subject to (COSO, 2017). By setting a platform for better
performance, efficiency, and professionalism, an organization can adhere to stipulated
rules and regulations.
Figure 1
The COSO Cube
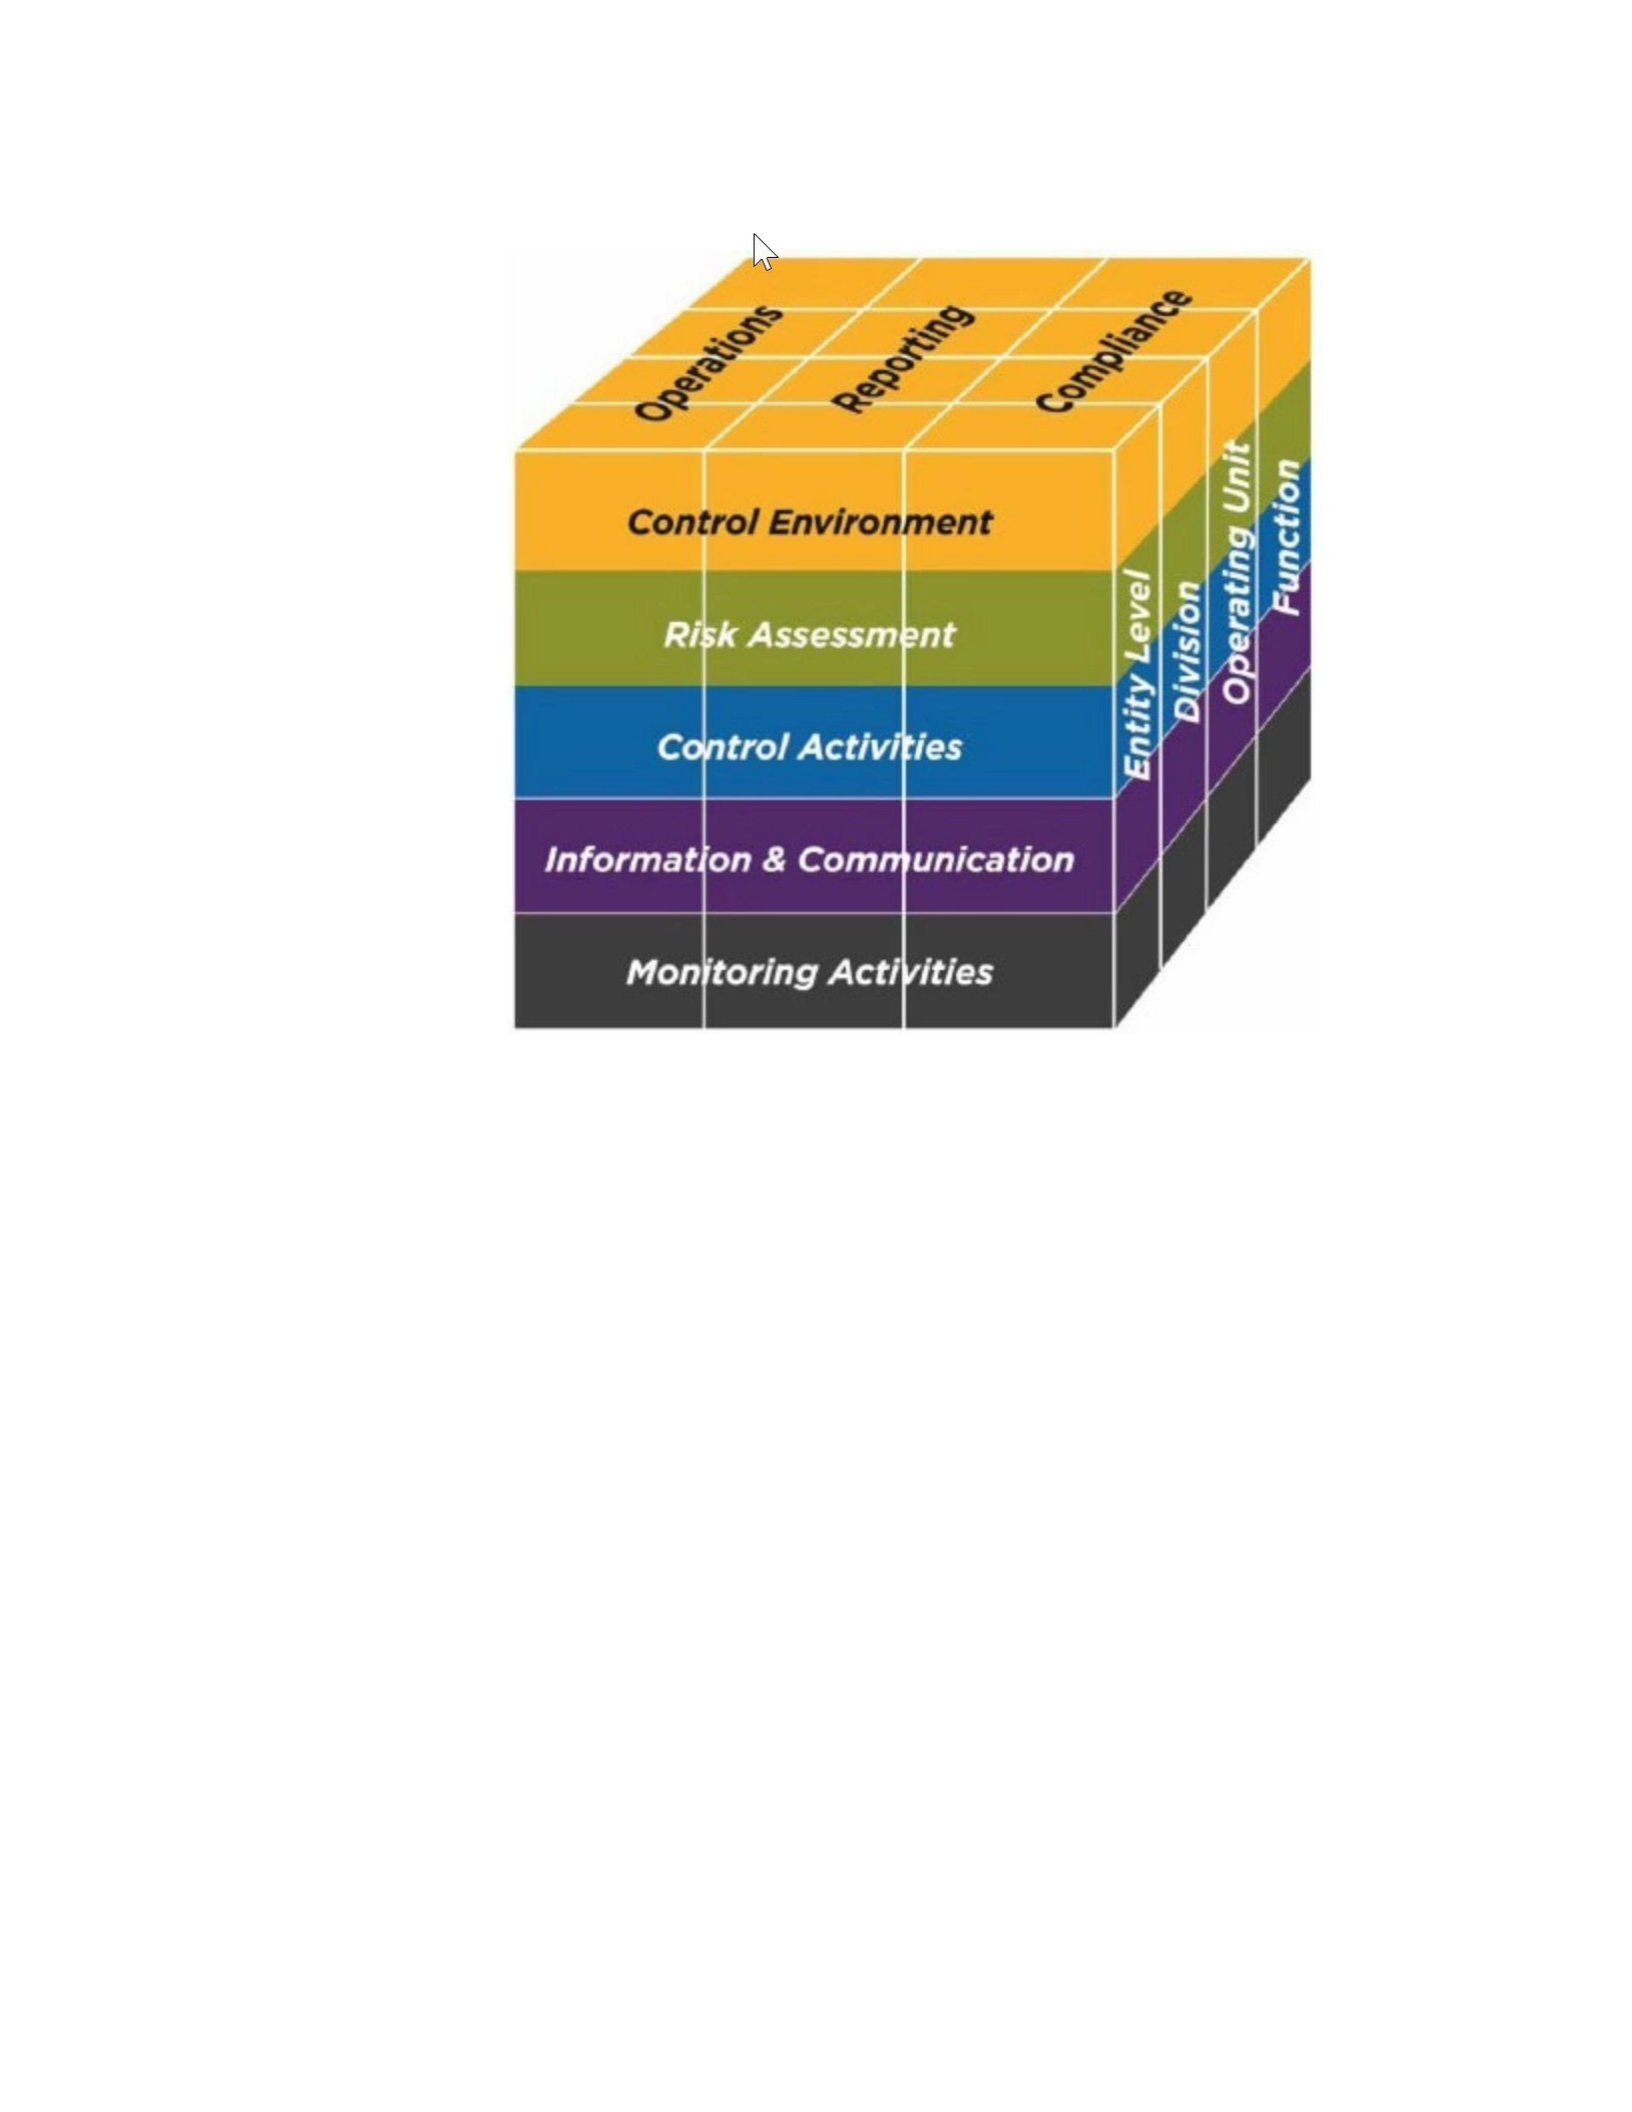
COSO. (2017). An integrated framework of the COSO cube.
The COSO model defines the different functions and levels within organizations
that the internal control function seeks to protect. According to COSO (2017), the
entity- level signifies internal control that influences the entire organization. Machado et
al. (2017) stated that the control tools emphasize creating and maintaining a good
culture within the entire organization. Organizations implement entity-level controls to
influence actions and decision-making throughout the organization to improve the
internal environment's quality (COSO, 2017). The goal of entity-level internal controls
is to standardize internal controls throughout the organization.

The next level of control is at the divisional level. COSO (2017) stated that some
internal controls must reflect unique environmental issues within divisional levels.
Depending on the organization's structure, some controls are specific to only certain
divisions (Davis et al., 2017). The coverage area extends beyond the physical areas of
operation to include the various focused activities in which an operating unit is engaged.
Each operation unit requires specific designs and internal control tools to generate
optimal results (Machado et al., 2017). Therefore, management must decide on the
design, implementation, and monitoring of internal controls at operational levels. The
final area of coverage is the functional level (Machado et al., 2017). An organization
includes various functional units, each bringing a unique contribution to the overall
performance. Management must determine the optimal fit internal control approach to
enhance functional units' performance within the organization.
The final two elements of the organizational structure include operating unit and
function. Operational objectives are concerned with the effectiveness and efficiency of
organizational operations, including production, financial performance, and asset
management (Rose et al., 2015). Functional operations with an organization require
specific controls (Frazer, 2016). Management develops controls for various operations
and functions based on the unique activities of the department or workgroup. Examples of
controls include segregation of duties, authorization, and physical controls
(Kamaruddin & Ramli, 2017). An organization's policies and procedures reflect the
operation of these internal controls (COSO, 2017). The controls become a part of the
components of the COSO model.

The Five Components of the COSO model
An effective control system encompasses five key components. These five
components of internal controls embedded in the COSO cube (see Figure 1) include the
control environment, risk assessment, information and communication, and monitoring
activities (COSO, 2017). According to COSO (2017), an effective system of control must
be operational. All the components of internal control must be present. To be termed
‘present,’ the internal control component must be incorporated into the internal control
system's design and implementation (Davis et al., 2017). To be termed operational, the
component must be realized as part of the system and continue to exist as part of its
internal control system. For management to define the internal control system as
effective, the five components must work together on an integrative basis.
The system is not effective if an individual component is not functioning. All
components must complement one another in an integrative manner to help build an
effective internal control system (COSO, 2017). A deficiency existing in any component
of the internal control system can contribute to the entire system's inefficiency, thus
impeding the achievement of internal control objectives. According to COSO (2017), a
deficiency occurs when management concludes that an objective has not been achieved
due to a missing or non-functional component. Thus, managers must critically assess each
component of the COSO model
The five components work together to establish a robust internal control function
for the organization (COSO, 2017). The COSO framework corresponds with this
research's objectives. The model guides business managers to optimize their internal

control functions to ensure more efficient operations using the ERP model (Rae et al.,
2017). The control environment refers to the structures, procedures, and processes that
define its internal control (COSO, 2017). The acting board of directors and executive
management set the internal control function's tone by defining employees' expected
standards and requirements (Li et al., 2015). Management strengthens the expectations of
the executives in the various functional levels of the enterprise. The control environment
defines the management philosophy and operating style adopted to run the organization
(King, 2016).
Control Environment
The control environment plays a significant role in shaping the internal control
function. Internal controls frame the ethical conduct and values that define the
organization's interactions and behavior (COSO, 2017). In addition, the control
environment consists of the parameters that assist the executive management and board of
directors in overseeing their responsibilities and defines the internal structure on which
authority and responsibilities are defined (King, 2016). The control environment outcome
has a pervasive impact on the internal control system as it helps create efficiency,
favorable work environments, and rigor around productivity measures.
Risk Assessment
Risk assessment refers to internal control involved in evaluating potential risks to
an organization due to performance activities (COSO, 2017). Risks are influences or
events whose occurrence leads to potential losses within an organization. Risks can occur
from the internal or external organizational environment, warranting the need to develop

strong risk assessment measures to identify and prevent potential risks (Moeller, 2014).
Primarily, risk management is an internal control that defines how an organization
manages risks (Li et al., 2015). As a precondition, risk management involves setting
objectives, which an organization links to various levels within the entity. The objectives
are defined at the management level against different categories, including operations,
reporting, and compliance, to ensure they specifically address the organization's various
activities (Feng et al., 2015). Management's responsibility is to review the set objectives
and gauge their suitability for the organization. Management then determines appropriate
activities to help achieve the specific objectives and evaluate possible risk management
changes. Management must ensure that the risk management strategies do not create
inefficiency in the internal control function (Akinleye & Kolawole, 2020). Risk
assessment helps identify the various risks impeding achieving an optimal internal
function and creates opportunities for improved efficiency and control.
Control Activities
The control activities refer to the actions developed through policies and
procedures and contribute to the mitigation of organizational risks that undermine
the achievement of objectives. According to Light (2014), control activities ensure
that organizations identify and mitigate errors and biases in financial reporting.
Light (2014) states that control activities can either be preventative or directive.
Preventive activities are programmed to prevent the occurrence of future events that
may expose an organization to loss. Furthermore, directive activities evaluate and

monitor processes that identify occurring events that require management to take
corrective measures (Light,
2014).
Management identifies and implements standard control activities over technology
to help achieve organizational objectives at acceptable levels. The policies are established
to define the expectations and procedures that stimulate policies to work. The control
activities are implemented at all levels of the organizations to influence a more coherent
internal control system. The COSO framework depends on management decision-making
and judgment to design and implement control activities that benefit the organization at
minimal costs (Boyle & Applegate, 2016). To ensure the efficiency and effectiveness of
the control activities, implemented activities must be cost-effective and based on the
probability and impact of the risks involved (Länsiluoto et al., 2016). In addition, the
application of activities should be applied in modality since too much control could
interfere negatively with productivity. According to Feng et al. (2015), some of the most
used control activities include verification, reconciliation, physical security of assets,
training and development, performance planning, and evaluation and authorization.
Information and Communication
The fourth component of the COSO model is information and communication.
Information and communication systems generate relevant and quality data to support
the functioning of the internal function's different components (COSO, 2017).
Furthermore, the information and communication systems ensure that an organization

communicates with external stakeholders on issues affecting the functioning of the
internal control system (Boyle & Applegate, 2016).
Monitoring Activities
Monitoring activities is the fifth component of the COSO model. Monitoring
activities define the strategies adopted by an organization to assess internal control
systems' quality over time (COSO, 2017). Internal control is affected by changes in the
organizational environment, constantly creating inadequacies in the control system.
Monitoring activities act as a basis for strengthening and understanding factors
influencing different internal control strategies (Pett et al., 2015). The monitoring
activities can determine the effectiveness and efficiency of implemented controls to
protect the organization from fraud and errors (Länsiluoto et al., 2016). To maintain up-
to-date activities and operations, organizations monitor activities that identify weaknesses
and create opportunities for improvements. According to Dorsey (2015), monitoring
activities should be systematic and allow for change opportunities.
Transitioning into the COSO Framework
COSO (2017) outlined that an internal control system is only effective if the
various components are present and functional. An organization must be involved in an
effective collaborative change management process to achieve functional internal
controls. The following framework outlines the five steps of transitioning into the COSO
internal control framework that adds value to the organizations at the most cost-effective
level.

The first step of the transitioning process is building knowledge by developing
internal awareness, expertise, and alignment. Developing awareness, expertise, and
alignment occurs by understanding how the COSO model applies to an organization
(COSO, 2017). According to COSO (2017), the second step is to conduct a preliminary
impact assessment to understand how the transition will affect the organization.
According to Dorsey (2015), in this stage, it is essential to consider the ability of
management to design and implement organizational fit control systems and the ability of
the organization to adapt. Management should map the current internal control system
against the updated COSO model (COSO, 2017). The assessment allows management to
understand what needs to be done to achieve the updated COSO control framework.
The third step is to enhance a broad awareness, training, and comprehensive
assessment. The third step is critical as it communicates the vision of the employees'
transition to avoid resistance (Babkin et al., 2017). The employees are educated on the
COSO framework's skills and methods to empower them into the transitioning process.
The employees are also coached and mentored on the right behavior and attitudes to
support the transitioning process. The ethical and compliance conduct framework
should be present and functioning to support management awareness and training
efforts
(Länsiluoto et al., 2016).
The fourth stage of the transitioning process involves developing and
implementing appropriate internal controls (Länsiluoto et al., 2016). Building knowledge
and awareness in previous stages act as a foundation for the organization to embrace the

transition. Implementing the COSO transition plan sees the various components of the
framework integrated into the internal control system. The system of internal control is
updated to encompass the various components at a functional level. The organization sets
realistic objectives that align with the business strategy (COSO, 2017). The various
activities involved in the implementation stage include documentation, validation testing,
gap remediation throughout the project's life cycle, and external review and testing to
assess adopted methods' effectiveness.
The final stage is to drive continuous improvement in the adoption of the COSO
framework. Ensure continuous improvement is essential in ensuring that the appropriate
ethical tone is at the top. The model's effectiveness requires management to adjust
internal tools and processes to create an optimal fit system of internal control (King,
2016). Therefore, the framework's effectiveness through time rests on continuous
improvement by management to adapt to the business's changes and requirements
(COSO, 2017). Responsibility for internal control is a part of the fabric of the company’s
culture, business processes, and procedures. This way, the internal control becomes the
entire organization's responsibility for more sustainability (Länsiluoto et al., 2016).
Management must also ensure continuous communication and reporting on the
performance of the framework. Continuous reporting and communication help inform
stakeholders of the model's strengths and weaknesses, creating opportunities for an
informed approach to improvements (King, 2016).
Strengths and Weaknesses of the COSO Model

The COSO model has gained a high level of acceptance and applicability in
organizations. In their review, Pett et al. (2015) stated that the COSO model is a leading
framework for designing, implementing, and coordinating internal controls. According to
Babkin et al. (2017), the model is flexible and allows an organization to mitigate risks at
reasonable levels and facilitate efficient decision-making and leadership. King (2016)
stated that the COSO model allows organizations to report their financial information in
conformance to relevant laws, regulations, and acceptable standards. King stated that the
model highly involves management decision-making, planning, and judgment, allowing
management and the board of directors to control the processes (King, 2016).
Limitations may impede the full applicability of the COSO model. According to
Länsiluoto et al. (2016), the COSO framework heavily depends on human judgment,
which is vulnerable to bias and processing errors that may lead to poor judgment. The
COSO model depends on judgment to design, implement, monitor, and control for more
effectiveness. Weaknesses in human cognitive processing can therefore lead to risks in
internal control. According to Kaya (2018), several organizations have also termed the
model to be too complex. For the model to be effective, management must apply
judgment to help develop suitable objectives that fit a specific organization.
Based on Länsiluoto et al. (2016), management's ability to handle internal control
responsibility is affected by poor judgment or decision-making and external factors.
Company risk assessment research is currently centered on the executive board and senior
management's function throughout the development and implementation of risk
mitigation systems that define, evaluate, handle, and track risks that impact the company.

In keeping with these standards and the ERM concept of COSO, the company and
executive leadership assume a leading function at the organization's tier. Focusing on the
governing board's position and leadership is an essential component of current
advancements in risk regulation and an effective catalyst for analysis into the function of
directors and executives in ERM implementation and firm financial condition (Tavakoli
et al., 2016).
Reporting of intelligence levels for ERM modules was achieved utilizing the
functionality configuration Model methodology. ERM is a system addressed,
developed, and implemented by individuals, and the human resource system drives its
success (COSO, 2017). Factors such as misguided cultural assumptions and fiscal
pressures can cause an ERM system to fail (Agarwal & Ansell, 2016).
Alternative Theories
To appropriately frame my research study, I also considered alternative
theoretical frameworks. In this section, I consider two additional conceptual
frameworks. The first framework is systems theory, as developed by von Bertalanffy. I
considered the second framework is the compliance objectives and related technologies
(COBIT) model containing best practices for internal controls over information systems.
Systems Theory
Systems theory is a multidisciplinary approach that allows researchers to evaluate
phenomena from a holistic perspective. Systems theory is based on the presumption that
phenomena are best understood by looking at the broader picture. Tops et al. (2014)
suggested that systems do not exist in isolation, meaning interdependence exists between

systems. Building on the COSO framework, von Bertalanffy developed systems theory,
suggesting that any system is complex with different elements (von Bertalanffy, 1972).
Knowledge about a system is built by understanding how the interconnected parts
contribute to the whole system's functioning (Länsiluoto et al., 2016).
System theorists focus on the interconnectivity of complex elements. According to
systems theorists, all system elements are rationally connected and complement one
another to build an optimally functioning system (Tops et al., 2014). Under this vision,
internal control is a system involving the interaction of a variety of components. In
systems theory, the critical components, interdependency, relationships, and objectives
comprise a system integral to the operation of the firm, which culminates in its overall
odjectives (Hughes et al., 2015). Each component of the internal control system works to
create value in its capacity, thereby leading to a more efficient internal control system
(Tops et al., 2014).
The systemic thinking conception of the internal control function aligns with the
COSO model, as both emphasize the need to improve individual components'
performance for the entire system to work (Alles et al., 2006). From both perspectives,
the internal control system involves interacting with various components whose value and
contribution enhance internal processes for better ERP management in business
organizations. Structures can also be open or closed. Available organizations share
information, resources, or services within their ecosystems, while secure facilities do not.
Since no social systems could be closed or opened, they are generally described as wholly
closed or accessible.

The difference between closed and open structures is defined by the degree of
external environmental exposure. Secure facilities are resistant to ambient anomalies,
while available systems are receptive to environmental conditions (Tops et al., 2014). The
solution to the programs is an institutional norm that evaluates efficacy developed on
long-term expansion or viability. If an organization, which comprises preservation and
development, can maintain homeostasis, the model is efficient.
Compliance Objectives and Related Technologies (COBIT)
COBIT is a structure used for IT governance as well as strategic planning. The
system is built to be a manager-friendly tool and bridges the critical gap across technical
problems, company uncertainties, and command standards. Ultimately, COBIT
guarantees consistency, monitoring, and efficiency of an organization's information
technology and is the most predominant element of any corporate practice. COBIT is an
acknowledged standard that could be implemented in any field to any company (Andry &
Hartono, 2017).
The COBIT model is a framework for IT to improve organizational processes.
According to Audit and Control Association (ISACA), lucrative organizations
understand the value created by information technology (Andry & Hartono, 2017). IT
professionals use the framework to create more optimized internal processes to drive
shareholder value. The model allows managers to close the gaps between control
requirements, technical requirements, and business requirements at large by enabling the
development of clear policies and procedures. Like the COSO model, the COBIT

framework has five functional components: framework, process description, control
objectives, management guidelines, and maturity models (Machado et al., 2017).
The COBIT framework helps managers develop systematic IT internal controls.
Montenegro and Flores (2015) stated that the COBIT framework encourages management
to use best practices and standards to shape IT processes and infrastructure. The approach
recommends management develop a strategic IT plan that helps businesses align their
internal control goals to their overall business goals (Montenegro & Flores, 2015). IT can
be applied in governance areas to support informed decision making, audit to promote
more efficient processes, and financial reporting to ensure the accuracy and effectiveness
of the methods used (Machado et al., 2017). The process descriptions define the process
model and standard language adopted by everyone in an organization. The process
description defines the roles, responsibilities, areas, and building mechanisms required to
develop robust IT systems to guide internal control. Control objectives are the third
component of the COBIT model (Machado et al., 2017).
Management objectives define management’s responsibility of allocating
responsibilities, objectives, measures of performance, and the relationships between
processes. Control objectives define the set of high-level requirements that
management must engage in to support IT systems' optimal functionality (Machado et
al., 2017). The final component of the COBIT model is the maturity model, which
involves: the need to assess the maturity and capability of an organization to
implement IT infrastructure, implement the right processes to complement the

functioning of the IT processes, and develop objectives that link the use of IT to
improved internal control processes
(Montenegro & Flores, 2015).
The COBIT model aligns with the COSO framework. Like the COSO model,
COBIT provides a rationale for organizations to control their internal functions and align
internal control objectives to the overall business strategy in business operation (COSO,
2017). However, COBIT emphasizes the role IT plays in enhancing internal control tools
such as governance, audit, and financial reporting. The COBIT framework suits
organizations that use multiple frameworks to provide complementary support systems
beyond those involving IT (Fernandes et al., 2018).
Effective Internal Control Strategies in ERP Model
An ERP system forms the basis of integrating diverse elements of an organization.
Due to changing business models, technological advancements, globalization, and other
business demands within the contemporary business environment (Altheebeh &
Sulaiman, 2016). ERP systems have become requisite for modern businesses as part of
their strategy to achieve sustainable and value-creating operations. ERP operates a single
database that integrates functional groups such as planning, purchasing inventory, sales,
marketing, finance, and human resources (Kaya, 2018). The ERP system forms a basis
for integrated business operations in real-time; it supports the free flow of information
between diverse business departments.
The ERP system is a critical business tool due to its ability to create efficiency by
supporting integrated organizational systems. According to Germann and Manasseh

(2017), ERP systems consolidate business transactions available to all enterprise staff.
ERP systems eliminate human interaction with data flows, thereby enhancing security,
accuracy, and transparency of operation (Jagoda & Samaranayake, 2017). According to
Geiger et al., 2015), as business managers invest in information system resources, the
degree of efficiency and value to an organization is determined by the system's success or
failure. Business managers must develop strategies to increase the successful integration
of an ERP system.
An internal control system is a crucial tool ensuring the successful functioning of
business ERP systems. According to Ballas and Demirakos (2018), internal controls
might be overlooked as factors to consider when implementing ERP. Jagoda and
Samaranayake (2017) suggested that a control framework must conceptualize internal
control features within an IT context. Parker and Nielson (2016) defined internal controls
as an integral mechanism that supports an organization’s operational efficiency, achieving
operational goals, organizational competitiveness, and reinforcing the corporate role. An
effective internal control system ensures the smooth running of routine organizational
operations and a significant reduction in organizational risks, thereby forming an integral
component of the ERP system (Ballas & Demirakos, 2018). Thus, internal controls must
be a part of the overall ERP process.
An essential advantage of an ERP is the consolidation of business processes
within a single system. Geiger et al. (2015) suggested that ERP systems effectively
integrate internal resources and business processes to increase organizational efficiency
and effectiveness. Ettish et al. (2017) suggested that the internal control system

complements the ERP system's function and determines its ability to benefit the
organization. An internal control system can help an ERP gather, analyze, and report
information in a changing context (Ettish et al., 2017). Ballas and Demirakos (2018)
suggested that a functional internal control system requires organizations to go beyond
the standard adherence to policies and procedures. The internal system helps articulate
the social, human, and cultural factors that affect an ERP system's operation.
An internal control structure of an ERP system must incorporate elements of the
COSO framework. Management and involved stakeholders must use decision-making
tools, judgment, and strategic opportunities to ensure that the internal control function
supports the optimal performance of various business areas (Babkin et al., 2017). ERP
systems have embedded structures and institutional logic that collide with various internal
control tools (Chen & Keung, 2018). These internal control tools can be strategically
placed to leverage opportunities for success in ERP, allowing the organization to reap
maximum benefits.
According to Chen and Keung (2018), inadequate internal controls threaten ERP
systems' legitimacy if the controls do not support all individual business functions
covered. Moldof (2015) suggested that many organizations have suffered losses because
of poorly designed internal control systems. Issues within the context of internal control
attach significant input to the ERP process, which cannot be realized if control systems
are weak. The mold stated that the streamlined performance of routine operations and
successful mitigation of operational risks occur with the successful implementation of
sound internal control systems.

A focus on internal controls is a critical component of the successful operation of
ERP systems. Fitzgerald et al. (2018) established that of the organizations that
implemented ERP systems, 78% of these organizations credited internal control systems
as positively affecting ERP system operations. In another study conducted among 500
organizations operating in Hong Kong, Cheng et al. (2018) sought to establish an
organization's quality variables for information systems to influence an organization's
benefits. Cheng et al. (2018) found that 65% of all organizations were aware that quality
variables in internal control significantly influenced an organization's management level
on their ERP systems. The internal controls determine the coherence of business
processes and procedures, which are factors that underpin the successful implementation
of ERP systems in organizations (Jagoda & Samaranayake, 2017).
A corporate governance structure influences internal control systems that support
the success and effectiveness of ERP systems. Corporate governance is an essential
aspect of internal control that significantly affects how an ERP system operates in an
organization. Geiger et al. (2015) defined the role of corporate governance in internal
control from a contingency theory perspective, stating that organizations are different and
therefore require different management styles. Corporate governance determines the type
of contingency an organization adopts to achieve its objectives (Fitzgerald et al., 2018).
Corporate governance provides an oversite of internal controls.
Fitzgerald et al. (2018) argued that corporate governance principles describe the
rules, regulations, and procedures that achieve the best protection of and balance
between the interests of corporate managers, shareholders, and other stakeholders.

Corporate governance oversees the control activities, risk assessment, information,
communication, and monitoring and evaluation, shaping the internal control system
(Cheng et al., 2018).
Corporate governance can influence internal control in three significant aspects:
management control, strategy, structure, and management support.
Cheng et al. (2018) defined corporate structure as the outline of organizational
roles and responsibilities related to different parts of the organization. The structure
determines how information flows in the organization and how responsibilities and
activities are allocated at different levels of the organization. The structure also
determines the degree of integration and differentiation in an organization (Khani &
Noroozian, 2018). The integration aspect of the structure refers to the level at which
authority is decentralized, while the integration refers to the rules and operating
procedures. Khani and Noroozian (2018) noted that organizations with more
decentralized authority and well-established rules and operational procedures perform
better. Highly decentralized and integrated organizations also develop better control of
internal processes, increasing the probability of successful ERP system operations.
Strategic corporate governance forms the basis for effective internal control
systems (Akinleye & Kolawole, 2020). Strategy in corporate governance is the tools and
methods management chooses to adopt to influence organizational elements such as
control, internal systems, technology, or risk management. Strategies act as a guiding
tool for management to enhance control and decision-making to ensure more optimized
outcomes. Strategies are not standard but differ among different organizations due to

differences in environmental requirements. Parker and Nielson (2016) highlighted failed
corporate governance as the main contributing factor to fraudulent scandals. Corporate
governance oversees the design and implementation of internal control systems that fit
the organization and promote the optimal functionality of ERP systems.
Corporate governance is a comprehensive organizational process. According to
Geiger et al. (2015), corporate governance includes planning, control activities, risk
assessments, authorizations, segregation of duties, and reconciliations, all of which form
the internal control system's components. More strategic judgment and control from
corporate governance can create tighter internal controls that facilitate ERP functioning.
Based on information by Altheebeh and Sulaiman (2016), corporate governance provides
oversight over a company’s processes and procedures to ensure they leverage
opportunities and minimize risks at acceptable levels. The governance processes monitor
the organizational risks and ensure that the organizational controls are efficient enough to
mitigate future risks (Graham, 2015). The governance processes ensure accountability,
transparency, and professionalism in internal control, which support sound internal
control systems. Graham (2015) states that the corporate governance framework
comprises organizational policies, measures of performance, and controls established to
align operational goals to organizational strategy. For an enterprise to leverage the ERP
system's full benefits, the internal control must align to corporate governance (Graham,
2015).
An ongoing ERP system requires appropriate monitoring controls. According to
Elbardan et al. (2016), management ensures the system's continuous improvement and

functionality. Corporate governance works to streamline internal processes to support the
continuous functioning of the ERP system. The governance processes focus not only on
the financial aspect of internal control but on the holistic development of internal
systems, ensuring that the internal control system supports ERP (Rubino et al., 2017).
Factors guiding corporate governance include employees understanding the system's
technical capabilities and relevance to the organization (Jagoda & Samaranayake, 2017).
Corporate governance is constantly engaged in information synthesis and
regular updating of the internal control systems to respond to the changing
organizational requirements (Haislip et al., 2015). The management is further engaged
in articulating how changes in internal systems can directly impact the functioning of
ERP systems. Thus, management can tell whether the existing internal control systems
sufficiently support the organization's current needs concerning ERP operation.
Altheebeh and Sulaiman (2016) added that corporate governance shapes the work
environment by implementing core standards and values on which employees base
behavior and interaction. By designing an organization's ethics and compliance
standards, corporate governance influences a positive culture that supports a positive
internal environment (Geiger et al., 2015).
Management support occurs by supporting organizational performance and
employee participation. For change to occur in an organization, the tone must come
from the top down to the employees (COSO, 2017). Given the role of leadership,
managers provide strategic opportunities to support organizational change, behavior,
and culture (Haislip et al., 2015). Control activities and processes' effectiveness

depends on the level of engagement, motivation, and collaboration of employees.
Corporate governance promotes a positive work environment by building strong
communication systems, work arrangements, employee relations, and training and
development opportunities to improve employees’ capacity for productivity. According
to Khani and Noroozian (2018), corporate governance developed transformational and
charismatic leadership roles that help lead organizations in changing times. Khani and
Noroozian, 2018) suggested that transformational and charismatic leaders can embed
the change process as a part of organizational culture and promote employee attitudes
that positively encourage a favorable internal control atmosphere. This way, effective
corporate governance plays an essential role in ensuring the development of internal
control systems that support the implementation and effectiveness in businesses
(Germann & Manasseh, 2017).
Audit influences internal controls over the effective use of an ERP system.
Effective internal audit processes in businesses create better opportunities for better
internal control systems (Germann & Manasseh, 2017). Auditing is an independent,
visional assurance and consulting activity designed to add value to an organization’s
processes (Shaiti, 2014). The internal audit function was traditionally focused on the
independent assessment of financial information but has expanded to encompass the
nonfinancial elements of internal control affecting businesses. Internal audit creates a
platform for more effective governance, risk management, and control activities
(Naheem, 2016). Effective audit processes help identify weaknesses in the internal
control system, allowing for improved processes (Moldof, 2015). The auditors’ role is to

assess the control environment operated by an organization regarding how various
individuals conduct their roles and responsibilities within the organization (Germann &
Manasseh, 2017). From this perspective, an auditor identifies weaknesses in corporate
governance and recommends improvements to ensure that management is more
accountable and transparent in their oversight and control duties.
Based on information from Cheng et al. (2018), the legitimacy of the audit process
is the ability to evaluate, monitor, and identify strategies to improve an organization's
internal control system. According to Germann and Manasseh (2017), the audit function
positively affects an organization's quality of control processes. Graham (2015) identified
one major internal control pitfall as the lack of consistency and inadequate internal
control measures that fail to identify internal control weaknesses. The lack of a control
process contributes to the inability to achieve organizational objectives. The audit
function determines the contours involved in internal controls and relates these to the
business strategy and risks (Cheng et al., 2018). Any misalignment between strategy and
business requirements is identified and corrected for more consistency in performance.
The audit process contributes to building organizational value, building effective business
operations, and allowing for more accountable financial reporting. According to Babkin
et al. (2017), the audit process links to improved systems implementation. The auditor
acts as a strategic internal control assessment tool to minimize organizational risks.
Internal auditors assess and opine on the effectiveness and adequacy of controls.
According to Babkin et al. (2017), the audit opinion forms the basis for corporate
governance activities, information technology operations, and a reference point for the

transparency and accountability of the financial systems in an organization. The audit
function evaluates the effectiveness of the control environment, risk assessment
strategies, management controls, communication activities, and monitoring activities
in place (Gramling & Schneider, 2018).
The legitimacy of the audit process depends on the auditor's independence,
objectivity, and professionalism (Gramling & Schneider, 2018). The audit should reflect
the various aspects of the control environment that influence business performance in
multiple areas and improve them to provide more value for the organization (Ballas &
Demirakos, 2018). The management depends on the auditors’ opinion to formalize the
risk management strategies adopted by an organization. Therefore, the opinion must
reflect quality and transparency to support effective management decisions (Ballas &
Demirakos, 2018).
The internal audit function should also be effective enough to act as a governance
mechanism for evaluating the introduction of different technology (Altheebeh &
Sulaiman, 2016). Following the adoption of ERP systems, the control activities,
environment, and internal control mechanisms continually evolve. The internal audit
function identifies and evaluates emerging risks and provides a basis for preventative and
detective control activities (Gramling & Schneider, 2018). Preventative control activities
reduce the risks of an organization. On the other hand, the detective control activities aim
to recommend existing events that pose significant risks to an organization. The internal
auditors must focus on providing reliable assurance on the quality of control activities in
the organization, both in financial and nonfinancial aspects of operation (Germann &

Manasseh, 2017).
Effective Change Management in ERPs
ERP research by Haislip et al. (2015) also sought to uncover the dynamics of the
change process and how effectively the change can settle as a part of the organization.
ERP systems bring new logic into the organization that can conflict with the existing
logic. To promote the success of ERP systems and for the organization to reap full
benefits, the institutional reason must change to accommodate the ERP systems' logic.
According to Germann and Manasseh (2017), ERP involves implementing broad changes
in business processes and significant alterations in business models, structures, and
individual responsibilities. Cumming et al., 2017) agreed that several risks are involved
with ERP systems, including implementation, technicality, and functionality. These risks
demand that organizations respond by reengineering and customizing new organizational
processes, which are pivotal in ensuring the system’s success.
Implementing an ERP system requires changes to almost all activities throughout
the organization. Chen and Keung (2018) stated that reengineering and customizing
processes to accommodate ERP implementation and improvements could cause resistance
to change, which significantly impedes ERP functionality. Stakeholders must think about
a new way of working and interacting with organizational networks to achieve
operational objectives. The new methods may accelerate misunderstanding and
misinformation, resulting in increased financial errors and fraud (Cumming et al., 2017).
Significant risks are associated with the ERP system implementation. Chalmers et
al. (2018) identified the main risks as the poor technical skills required to identify and

understand how a system operates and underutilization of system capabilities to build
organizational efficiency. The interdependent nature of the ERP system means the system
implementation may cause disruptions in other organizational operations (Jagoda &
Samaranayake, 2017). Managers must recognize how each process changes with an ERP
system. The change management process determines the employees' capacity to interact
and cooperate with the new methods and systems, further determining the compatibility
of the ERP system to the organization (Chen & Keung, 2018).
Change management plays a significant role in shaping the ERP systems' success.
According to Chalmers et al. (2018), change management refers to the approach adopted
by an organization to ensure that newly designed methods, ideas, techniques, and
resources are successfully implemented in an organization. Change management is a vital
tool in internal control since it ensures that an organization can successfully implement
innovations and adapt to the changes as part of its strategic processes (Ifinedo, 2015).
A successful change management process occurs in three distinct stages:
unfreezing, changing, and refreezing (Machado et al., 2017). The freezing stage involves
identifying a need for change and then cultivating the organizational ground to
implement the transition successfully. During the freezing stage, management focuses on
eliminating barriers to change, such as employee resistance to change, by creating a
good awareness and knowledge about the change process. The change process is
considered a collaborative and stakeholder-engaging process that gives stakeholders
time to adopt the right behaviors, skills, attitudes, and perceptions required to facilitate
the change (Saxena & McDonaga, 2016). During this stage, the organization also

projects the potential impact of the change to ensure the change process aligns with the
achievement of the business objectives (Machado et al., 2017). After the unfreezing
process, the organization transitions to the changing phase, which implements the actual
change. During the change process, uncertainty and fear concerning the new methods
can affect the organization.
The change process requires planning and leadership to ensure sustainability.
Management has a critical role to play at this stage by reinforcing information, providing
new strategies, and helping employees develop the right behaviors toward the change
process (Cumming et al., 2017). Education, communication, and leadership support are
critical inputs at this stage. The final stage of the change management process is the
refreezing process. In the final stage, management seeks to consolidate the skills,
knowledge, and behaviors acquired for the change to occur (Saxena & McDonaga, 2016).
The change will now be a part of the organizational culture to ensure that employees fully
understand their role in ensuring a sustainable change process (Cumming et al., 2017). An
effective change process may tighten internal control and create a positive impact on ERP
operation in businesses.
Existing tensions, attitudes, and perceptions can undermine the successful use of a
system in an organization. The organizational culture is an essential internal control tool.
According to Altheebeh and Sulaiman (2016), the organizational culture highly
determines the effectiveness and success of ERP in organizations. The organizational
culture refers to the system of values, beliefs, and attitudes possessed by the organization
members (Alvesson & Sveningsson, 2015). The organizational culture is shaped by the

management's ethics and compliance standards as a strategy for internal control. The
organizational culture determines the level at which an organization can adapt to changes
created by ERP processes (Lee & Kramer, 2016). The changes affected by ERP have the
potential to affect the social environment of the organization, which can lead to either a
positive or negative outcome, depending on the nature of organizational culture. Rae et al.
(2017) stated that ERP redefines the social-technical atmosphere of the organization by
introducing new information infrastructures and methods. The ERP process welcomes
considerable social forces that may create opportunities for promoting or opposing the
change. Given that ERP is an agent of change, a favorable organizational culture provides
an empowering environment where ERP is more readily absorbed and more sustainably
accepted as a part of the organizational processes.
Lee and Kramer (2016) stated that there always exists a gap between system
capabilities, contextual requirements, and the nature of an organization to which a system
is implemented. The organizational culture equips employees with the right values,
beliefs, and behavior to support a change process that could benefit the organization
(Alvesson & Sveningsson, 2015). The favorable values and belief system supports a
collaborative approach to the change process, which gives leaders a strategic opportunity
to educate, train, coach, and mentor employees, auditors, and other personnel into
embracing the use of ERP (Bolman & Deal, 2017).
According to Rae et al. (2017), one of the internal control tools underpinning the
success of an ERP system is the communication system that is present and functional in
an organization. Hsiung and Wang (2014) referred to communication as the effective

exchange of information, ideas, opinions, and feelings between different people or
entities. Bolman and Deal (2017) defined the communication strategy or system as the
effective approach an organization adopts to provide information to all relevant users
quickly and appropriately. Communication strategies are established to influence quality
decision-making, enhance mutual understanding among staff, boost positive employee
relations, enhance teamwork, and build awareness of an organization’s vision (Helms-
Mills & Mills, 2017). The communication system determines the flow of information and
how different users can make decisions timely and relevant.
The quality of communication is positively correlated to the functioning of the
ERP systems, as it determines the level of understanding the various stakeholders have of
the ERP system. Rae et al. (2017) argue that an information system that its users do not
understand is redundant and cannot influence the intended objectives aimed at
organizations. Several communication exchanges take place between ERP employees and
other employees from other departments. Communication also takes place between the
ERP project groups (Germann & Manasseh, 2017). ERP personnel engage with the ERP
system need a technical understanding of the system to ensure they adopt a system-
thinking approach on compliance and operation of the system (Ballas & Demirakos,
2018). Such deep knowledge can ensure that the ERP consultants tailor the right
strategies to help meet ERP objectives. Communication fosters this connection and
ensures that ERP personnel understand what is required for optimal system functionality
(Helms-Mills & Mills, 2017).

Germann and Manasseh (2017) suggested that through effective communication
systems, management can educate, coach, and mentor employees on the need for ERP
systems, allowing for a successful implementation of ERP in an organization. The
continuous improvement of ERP in an organization is also shaped by communication
strategies adopted by an organization since it ensures information is available to the ERP
project team for more practical decision-making (Gramling & Schneider, 2018). Through
effective communication, the ERP personnel can monitor changes and patterns in both the
internal and external environment, thereby adapting the ERP system to remain responsive
to changes in the environment. Geiger et al. (2015) provided the example of auditors who
operate ERP systems to identify the strengths and weaknesses within organizations’
operations. A poor understanding of the ERP system because of poor communication
methods impedes the auditors’ ability to control the ERP system and use the system as a
risk management tool (Binder, 2016). Quality communication eliminates
misunderstandings, clarifies vision, techniques, and helps to build trust among auditors,
empowering them to use their professional knowledge in risk assessment (Gramling &
Schneider, 2018). An organization can also gain more control of the ERP system when
awareness is built around it and when employees understand their role in supporting it.
Therefore, communication helps maintain the connections needed for an ERP to work
efficiently and ensures a favorable working environment that fully supports the ERP
objectives (Shao et al., 2017).
Internal Control Strategy Barriers

From the context of the study, it is essential to understand the key barriers
preventing businesses from implementing effective internal control strategies to support
more efficient ERP system operations. Audit and inspection challenges affect the ability
of the auditor to identify weaknesses and risks associated with ERP (Ardi & Nazaripou,
2015). The implementation of ERP systems or improvements generates new systems and
approaches to business processes. The new business models and processes create a new
risk, given that the framework is different from the original system.
Boyle and Applegate (2016) suggested that ERP systems are also constantly
reengineered to respond to changes in the business environment and ensure that the
business continually gets the optimal benefits from operating the system. The changes
in the system create significant modifications in network security, system
interdependencies, interruptions, employee roles and responsibilities, and overall
control activities (Kaya, 2018). The changing fundamentals of the risk environment
pose a challenge to effective internal control from an internal audit perspective. The
internal auditor may not adequately comprehend the basic architecture and technicality
of the system, creating a risk of a non-quality assurance of internal controls (Boyle &
Applegate, 2016).
Additionally, Alles et al. (2006) stated that an internal auditor is highly
vulnerable to loss of independence. The manager selects them, unlike the external
auditor, who has no connection to the organization. The lack of independence reduces
objectivity and risks the possibility of distorted opinions, which misinform governance,
IT-related decisions, and overall internal control strategies. According to Altheebeh and

Sulaiman (2016), the auditor may also lack professional competence to form a quality
assurance from the audit operation due to a lack of professional training. Inadequate
professional competence can also be caused by a lack of continuous training and
improvement to ensure that the auditor is conversant with updated organizational
processes or requirements (Ballas & Demirakos, 2018). Low competence levels mean
that the auditor does not adopt the right processes and procedures in research and
reporting, undermining the opinions provided. Ardi and Nazaripou (2015) argued that to
overcome the challenge created by poor quality auditing, an organization must select
auditors with strong professional and academic backgrounds in the auditing process.
Management must ensure continuous training and development that address new or
changing processes (Binder, 2016). Knowledge increases auditors' operational capacity
and provides they can apply the correct methods and techniques to the right internal
control processes. Alles et al. (2006) also recommended the internal auditors be
constantly changed to help reduce the probability of conflicting interests or lack of
objectivity in the auditing role.
Lack of understanding of corporate governance's scope and functionality
affects the effectiveness of internal control processes, thereby affecting the quality of
ERP systems realized (Ballas & Demirakos, 2018). Management failure from a poor
understanding of scope and functionality creates gaps in internal control. Management
decision-making determines the effectiveness of control activities. The complex and
dynamic organizational environment requires managers to engage in complex, flexible,
and contingent mechanisms, which may not always be possible. Inability to develop

strong cognitive processes to support decision-making in areas of structure, strategy,
management control, and management support leads to undesirable effects for the
internal control system, undermining the ability of the internal system to support ERP
effectiveness (Binder, 2016). Poor management decisions because of poor
understanding of scope and functionality mean that some areas of internal control are
underrepresented and may therefore perform in coherence with other internal control
components. According to Kaya (2018), management lacks professionalism and
accountability to carry out their roles in other cases. This can be defined from an
agency theory perspective. Agency theory states that managers play a unique role in
representing shareholders and stakeholders in decision-making to ensure that every
decision creates value for the various shareholders (Parker & Nielson, 2016).
Management acts as an agent for shareholders to ensure shareholders optimize their
value from the business. However, the problem of agency theory emerges when
managers lack incentive and subjectivity to represent the interests of shareholders
(Kaya, 2018). Therefore, management may engage in poor decision-making or engage
in unethical activities for self-gain at the expense of shareholders’ interests. This
provides a reasonable explanation for the many corporate managers involved in
corporate scandals. As a solution, Ardi and Nazaripou (2015) recommended using
incentives to motivate managers to perform their roles. Incentives can be financial or
nonfinancial, such as recognition, empowerment, job security, and trust. Incentives can
build a management culture in which managers feel a direct individual responsibility
towards ensuring the internal controls support organizational performance. Kakabadse

et al. (2017) also recommended the use of continuous training and development to
continually reinforce the skills and behavior required for managers to contribute
optimally to effective internal control systems.
The practicability of risk management strategies and compliance standards has
also been identified as a challenge to effective internal control. According to Geiger et al.
(2015), risk management strategies and compliance standards have only been
implemented at a hypothetical level. Thus, organizations face uncontrolled risks that
could significantly lead the organization to face loss or collapse. Risk management and
compliance standards are sometimes viewed as an extra burden to organizations, causing
the two important aspects to receive low attention (Kaya, 2018). Poor decision-making by
management, such as developing inappropriate compliance standards, may lead to poor
organizational culture, employee behavior, and relationships that undermine the
development of effective internal control systems. The ineffective risk and compliance
standards have led to financial errors, scandals, and business-oriented inadequacies. Yin
(2018) recommended using legal standards to affect risk management and compliance
standards to promote effective internal control systems. According to Geiger et al. (2015),
management should embrace their role in protecting and guiding the interests of
shareholders and, thus, practice risk management and compliance management at an
organizational level.
Kaya (2018) attributed poor internal control systems to poor change management
processes. Some organizations have adopted coercive, and directive change strategies
that are highly consistent with resistance. Resistance from employees creates

ineffectiveness in change processes and leads to inadequate internal controls. New
methods and processes affect the social aspect of organizational life (Lee & Kramer,
2016). Therefore, management must provide employees with enough time to accept and
adopt the change as part of their work culture. According to Kaya (2018), change
management should be systematic and collaborate with employees to realize the
necessary change in the institution.
Transition
Section 1 included the foundation of research associated with effective fraud risk
mitigations strategies. In addition, Section 1 had the background of the problem as well, a
statement of the proposed qualitative single case study is to explore effective internal
control strategies for ERP systems business leaders use to reduce risks from reporting and
erroneous transactions. The nature of the study, research question, and a description of
the COSO framework were included in Section 1. This section also included the
assumptions, limitations, delimitations, and anticipated social change, as well as a review
and synthesis of the academic literature related to the COSO framework, fraud theories,
and internal control.
Section 2 includes a background of research methodologies and designs related to
the study. In addition, the study population and sampling, the role of the researcher, as
well as the data collection instruments, technique, and organization is outlined. Section 2
concludes with a discussion of data analysis, reliability and validity techniques. Section 3

contains an overview of the study. This section includes a presentation of findings,the
application of findings to professional practice, as well as implications for social change.
Recommendations for further research are also included in this section.

Section 2: The Project
In Section 2, I restate the purpose of the study and describe the role of the
researcher in the data collection process and research methods used in this study. The
section includes details regarding the target population, selection process, research
ethics, and data collection techniques and instruments that I used to analyze the
research findings. I conclude Section 2 with a discussion of the reliability and validity
of the research instruments, a transitional summary of topics in Section 2, and an
overview of
Section 3.
Purpose Statement
This purpose of this qualitative single case study was to explore effective internal
control strategies for ERP systems business leaders use to reduce risks from reporting
and erroneous transactions. The target population for this study included seven
participants at one business in Mississippi who have successfully implemented effective
internal control strategies for their ERP systems. The positive social change implication
is that the resident’s benefit may be enhanced community stability where employment
opportunities increase, thereby increasing the betterment of the community.
Role of the Researcher
Researchers have the mandate to formulate research questions, select an
appropriate research method, collect relevant data, and later use appropriate data analysis
methods (Marshall & Rossman, 2016). My role as the researcher included selecting the
appropriate research method and designing, recruiting potential participants, deciding on
the instrument, collecting the data, analyzing the data, and describing the results. As the

primary data collection instrument, I engaged prospective participants who met the
criteria for the targeted population. I also interviewed qualified research participants to
answer the research question, used member checking to ensure data accuracy, and
organized, interpreted, and analyzed the data collected from all sources. Data collection
occurred only after approval was obtained from Walden University’s Institutional
Review
Board (IRB).
Interviewing business leaders and retrieving ERP implementation documents
were the data collection techniques in this study. My role as a researcher in the data
collection process was limited to four activities. First, I developed an interview protocol
to maintain the consistency of questions in the interviews. Second, I sought Walden
University’s IRB approval before interviewing participants. Third, I interviewed
multiple business leaders after securing informed consent from the interviewees. Finally,
I (a) recorded the interviews, (b) transcribed the interviews’ recordings and summarized
each interview, (c) conducted member checking, and (c) stored transcriptions in a
computer- assisted qualitative data analysis software to create a case study database. As
a researcher, I was also responsible for conducting an ethically sound study and
preventing any harm to the participants.
Researchers struggle to avoid bias. McCusker and Gunaydin (2015) argued that
researchers might embed their prior beliefs in the research process. I have worked in the
business industry and have worked with the implementation and operation of ERP
systems. However, my background in the business industry did not bias my research in

selecting participants or interpreting data; I incorporated strategies to limit potential
biases including bracketing and using an interview protocol.
Bracketing assists researchers in maintaining objectivity, consciously
maintaining a distance from the research project. Researchers put aside their individual
biases through bracketing while collecting data (Petty et al., 2012). The researcher uses
bracketing to develop a deeper understanding of their work while at the same time
maintaining an objective approach all through the research process by operating non-
judgmentally (Sorsa et al., 2015). In this study, I used the bracketing technique to reduce
bias.
According to the ethical guidelines of The Belmont Report (National Commission
for the Protection of Human Subjects of Biomedical and Behavioral Research, 1979), a
researcher must understand the ethical issues inherent in research involving human
subjects. To comply with these guidelines, I followed the basic ethical principles in The
Belmont Report, including: (a) respect for persons, (b) beneficence, and (c) justice. I
demonstrated respect for participants by requesting written informed consent from all
participants to confirm their voluntary participation in the study. The informed consent
form included (a) an explanation of potential risks and benefits, (b) confirmation of the
voluntary nature of the study, and (c) a description of measures to ensure participants’
privacy, confidentiality, and anonymity. I waited for Walden University’s IRB approval
before engaging the participants.
Participants
There were seven participants in this study. Qualitative researchers choose
participants based on the eligibility criteria (Jagoda & Samaranayake, 2017). The

selected participants met the following criteria: (a) willingness to participate in data
collection, (b) business leaders Mississippi, and (c) have successfully implemented
business strategies to sustain their operations in business management. I identified
business leaders working with one business who are appropriate gatekeepers. I reached
out to these executives to find one who agrees to participate in the study. After the
gatekeeper in the observation (Powell et al., 2016). Obtaining participant responses
specific to the research question was at the forefront of this study. As the researcher, I
established the criteria necessary for participation.
After IRB approval of the study, I began reaching out to potential participants
via email. I introduced myself and the study and strived to garner interest in
participation in the study. I did not conduct on-site recruitment. The targeted population
was appropriate for this study because business leaders are controlled strategies for
ERP systems business leaders use to reduce risks from reporting and erroneous
transactions.
Gaining access to participants requires a specific strategy (Gülmez et al., 2016).
Researchers can explain the interview process, the purpose of the study, and the research
value through e-mail to establish trust and compatibility with the participant (Auer et al.,
2015). Confidence and a good working relationship between the participants and the
researcher help get positive feedback (Johnson, 2015). To build a positive working
relationship with participants and ensured person-centered while collecting data. I was
able to build on social networks and accrue social capital with the participants. In the
data collection, I involved in the participants' daily activities in the research. Once
researchers have identified eligible participants, they invite them to participate in the

study (Powell et al., 2016). As an additional strategy, I collected my data using an
interview protocol to minimize the participant's anxiety, time commitment, and
reluctance. I ensured that the participants perceived that they were valued, appreciated,
and comfortable. Having the interview in an environment familiar to the participant will
more likely help participants feel at ease.
Research Method and Design
Research Method
The research method for this study was qualitative. Researchers have the option
of using quantitative, qualitative, and mixed methods for their studies (Strijker et al.,
2020). Quantitative researchers use statistical data collection techniques to measure
varia- bles and test hypotheses about the relationships between variables or the
differences be- tween groups (Zyphur & Pierides, 2019). A quantitative method was not
suitable for this study as I was not testing a hypotheses. A mixed-method researcher uses
qualitative and quantitative methods in a single study (Sahin & Öztürk, 2019). I did not
use the mixed method as the quantitative aspect was not a part of my study. Qualitative
researchers use semistructured interviews to understand and meaning a phenomenon
(Yin, 2018).
Researchers analyze the relationships between variables using a quantitative ap-
proach (Zyphur & Pierides, 2019). Quantitative researchers use numeric data to examine
a phenomenon's nature (Bristowe et al., 2015). Researchers use quantitative research
methods to examine quantities, support judgments, and test hypotheses (Bell et al.,
2018).
Researchers use quantitative research methods to examine quantities, support judgments,

and test hypotheses (Bell et al., 2018). A quantitative research approach was not appro-
priate for this analysis, as I did not produce any ideas or test hypotheses. Researchers
use a mixed research method to integrate quantitative and qualitative research
approaches (Strijker et al., 2020).
A mixed research method is harder to carry out (Yin, 2018). Researchers use
qualitative and quantitative methods to understand the research issues (Brannen, 2017).
Researchers use a mixed approach to achieve a complex understanding of a phenomenon
(Hamilton & Finley, 2019). I did not select a mixed method because I did not include
nu- merical data in this study. I did use the qualitative method of study to analyze and
explain participant interactions. Hence, the qualitative method was more appropriate for
this study compared to the quantitative and mixed methods.
Research Design
The qualitative research designs include phenomenology, ethnography, and case
studies (Goldman et al., 2015). Phenomenology design refers to a qualitative research
method that focuses on how humans’ character and describe the experiences of human
beings. At the same time, ethnography is the scientific study of people based on their
cultural beliefs and perspectives (Marshall & Rossman, 2016). Unlike phenomenology
and ethnography, the case study design uses multiple data collection techniques to
explore a bounded system in place and time (Yin, 2018). This study will employ design
to gather and gain in-depth knowledge and ample data to explore a bounded system in its
natural setting.
Researchers using an ethnography design to understand the culture of a
particular group (Cincotta, 2015). Ethnographic researchers must become part of a

group to study individuals of that culture (Yusop & Correia, 2013). Ethnographic
research focuses on understanding a culture's behavior (Bailey & Bailey, 2017). An
ethnographic design was not appropriate for my research because I did not intend to
explore cultural values.
Data saturation depends on the purpose of the study, participants, and the
research method and design (Viet-Thi et al., 2016). The sample should be large enough
for the re- searcher to obtain redundancy of responses or saturation (Yin, 2018). The
research meth- odology, research question, and design will dictate when and how
researchers attain data saturation (Viet-Thi et al., 2016). Researchers conducting
qualitative research use data saturation to evaluate the study's quality (Hancock et al.,
2016). If the researcher fails to attain data saturation in a study, the study's quality and
content validity may be hindered (Fusch & Ness, 2015). To attain data saturation, I
continued interviews until I fail to iden- tify new themes, categories, insights, or
perspectives for coding.
Population and Sampling
The purpose of this qualitative single case study was to explore effective internal
control strategies for ERP systems. The sample population for this study consisted of
business leaders selected from one business in Mississippi. Researchers use this form of
purposeful criterion sampling as a guide to obtaining information pertinent to the issue
under investigation (Marshall & Rossman, 2016). Purposeful criterion sampling is
relevant for qualitative research, such as case studies (Moss et al., 2014). I used criterion
sampling to select the business leaders as my focus will be to identify the businesses

using ERP systems or internal control strategies (Robinson, 2014). I followed the criteria
established from my population as the criterion I used to pick my sample.
Researchers' sampling technique must align with the goals and assumptions of
the study. Researchers use sampling to maximize efficiency and validity (Hamilton &
Finley, 2019; Robinson, 2014). Criterion sampling in this study will enhance the
selection of experienced and knowledgeable business leaders who have implemented
strategies to reduce risks from reporting and erroneous transactions.
Data saturation occurs when the data collected does not add new information or
coding to a study, and the data collected can replicate the study (Fusch & Ness, 2015).
Data saturation increases the reliability and validity of a study's results (Fusch & Ness,
2015). Qualitative researchers refrain from interviewing more participants when
additional interview information does not generate new insight into a phenomenon
(Cleary et al., 2014; Roy et al., 2015). I continued to interview additional participants
who met the criteria for this study until there were no new concepts or codes that
emerged. The study will be qualitative and will entail the selection of leaders from
several businesses in Mississippi. Yin (2018) suggested that researchers can reach data
saturation with a small sample. Christenson et al. (2016) reached data saturation after
interviewing 7 participants. The sample size of this study was seven experienced
business leaders. At the conclusion of my interviews I reached data saturation.I
continued to collect data until I reach data saturation.
Researchers can use interview settings to increase the quality of the participant's
information (Cairney & St Denny, 2015). I conducted in-depth online interviews.

Participants for my study will choose a comfortable and safe environment for the
interview. When participants feel comfortable and safe in an online interview, they
share more information relevant to the study phenomenon (Bowden & Galindo-
Gonzalez, 2015; Deakin & Wakefield, 2014). Participants are more focused in an
environment free of distractions, thus providing higher quality audio recording (Deakin
& Wakefield,
2014).
Ethical Research
All participants must provide their informed consent by signing the consent form
before participating in the proposed study. An essential step for the researcher is to en-
sure that all participants have provided their informed consent (Alshenqeeti, 2014).
Where audio recording was used, verbal consent was also obtained. Once participants
ex- pressed interest in participating in the study, the consent form was sent by email to
allow participants ample time to review the content. I also reviewed the consent form
with each participant at the start of the interview process to ensure each participant
understood the intent of the study. The IRB has three main purposes: (a) enabling
researchers to conduct scientific processes by which new data and knowledge are
rigorously acquired that may benefit the public and society as a whole, (b) ensuring
voluntary participants within hu- man studies are adequately protected, and (c) limiting
exposure of litigation to institu- tions (Balon et al., 2019). Participation by an individual
in research is voluntary, and the right to withdraw is a core principle of research ethics
(LaRossa & Bennett, 2018).

The process of withdrawal will be a failure to attend the interview or failure to
give information. No participants of this study will receive any compensation for their
participation. I sent the participants a summary of the results. All collected data will re-
main in a password-protected external hard drive for five years before disposal of infor-
mation. The disposal will occur through the deletion of data and all accounts linked with
the data. The participants’ identities are confidential. Each participant will receive a
unique number to maintain confidentiality in the study. The details of the participants
were limited to a code, P1, P2, P3, P4, P5, P6, and P7, which will change with each par-
ticipants. The IRB approval number for this study is 03-24-220566476.
Data Collection Instruments
As a qualitative researcher, I was the primary data collection instrument for this
proposed study. Qualitative researchers collect data through observations, document
reviews, and observations (McCusker & Gunaydin, 2015). Qualitative researchers
interpret data to make the data meaningful (Lynch et al., 2016). I conducted
semistructured interviews using open-ended questions using Zoom. Researchers using
semistructured interviews have a predefined list of questions (Hedlund et al., 2015). In
this study, I used six predetermined open-ended questions that focus on exploring the
main phenomenon of the study. The semistructured interviews include six predetermined
open-ended questions that target exploring the relevant phenomenon of the observation.
Each semistructured interview will be 45 minutes, and the interviews was audio
recorded. When undertaking semistructured interviews, I intended to have firm expertise
in the study question, ask precious interview questions, live adaptively, and avoid biases.

During the interviews, I took notes of my observations of the surrounding envi-
ronment and participants’ reactions to questions, including facial expressions and voice
tones. Also, I reviewed internal documentation and make notes of relevant information
related to internal controls I collected relevant documentation associated with
information obtained from the participants during the interview process from publicly
available sources online. These notes are part of a journal. The combination of
interviews with other data sources enhances the study's validity (Yin, 2018). Each
semistructured inter- view will last no more than 45 minutes.
Qualitative researchers use semistructured interviews to gather data (Stevens,
2017). I gathered data by conducting zoom interviews with participants, reviewing
internal documents, and making information available publicly. Researchers will use
interview protocols as a gradual process to guide them through the interview process
(Benia et al., 2015). Researchers can use interview questions to achieve access to key
participants and create precise schedules of activities required to finish the data
collection procedure at a given time (Yin, 2018). Researchers can use interview
protocols to reduce the risk of researcher bias by selecting participants (De Ceunynck et
al., 2013). I used semistructured interviews open-ended questions to elicit
comprehensive responses from participants. Using an interview protocol (see Appendix
A), I standardized the interviews to minimize bias and improve the accuracy of
information.
Member checking is a procedure used by qualitative researchers to enhance a
study's skill (Marshall & Rossman, 2016). Researchers use member checking to
validate the data collected from participants (Dubois & Gadde, 2014). In a qualitative

investiga- tion, member checking can take place during the interview process, at the end
of the study, or both to increase credibility and validity (statistics). The interviewer
restates or summarizes information and questions the participant. To improve the data
collection process's reliability and validity, a qualitative researcher can employ member
checking. I employed member checking to enhance the reliability and validity of the
data collection process in this study.
A qualitative researcher is the primary data collection instrument and must avoid
researcher bias (Cope, 2014). A researcher can use interview protocols to gain access to
key participants and make precise schedules of activities needed to complete the data
col- lection procedure at a given time (Yin, 2018). A researcher can use interview
protocols to reduce the risk of researcher bias (De Ceunynck et al., 2013). I used
semistructured inter- views using open-ended questions to elicit comprehensive
responses from participants. I asked for clarity when needed throughout the interview
process to ensure that my inter- pretations of the participants’ responses were correct. By
using an interview protocol, I standardized each interview and thus reduce researcher
bias.
Data Collection Technique
I used three data sources for this study: interviews, archived data, and publicly
available records from an organization. I explained to participants the purpose of the re-
search, how the interview process works, and how I want to collect their consent. A pro-
tocol was followed when conducting each interview (see Appendix A). Public data
sources were consulted and generally agreed with data gathered during interviews with
the participants.

The archival data and organizational records were very helpful in understanding
the interview data. Archived data and organizational records can help confirm the accu-
racy of responses given by participants during an interview. Another benefit of using a
randomized trial is that the results are more reliable. The main limitation of digital data
from computer software is that the user is often limited by the context provided by the
data provider, which can limit their interpretive capacity. Other potential disadvantages
of using data from a study may include retrieving information that is not richly detailed
or that fails to capture a range of perspectives within the context of the research question.
Nevertheless, the type of interview questions may be detrimental to the quality of
information gathered. The disadvantage of semistructured phone interviews is that it is
challenging to communicate and establish relationships with participants (Agran et al.,
2016). Another advantage of semistructured phone interviews is the option to arrange or,
in some instances, reschedule interviews with the participants with fewer interruptions
(Agran et al., 2016). Casual observation enables researchers to access real-world events
of participants. Researchers are likely to intrude on these real-world participants’ activi-
ties (Yin, 2018). Therefore, during the research, I acknowledged the potential discretion
of the interview procedure. Andraski et al. (2014) claim that a qualitative researcher can
use member checking to allow participants to respond to how they interpret the collected
information. This strategy helps in ensuring the credibility of the data collected. I sent
copies of my interpretation to the participants via email to confirm the accuracy of my
in- terpretation of the information gathered.
Data Organization Technique

There are several ways to track, code, and store data for analysis. I used the
NVivo 12 Plus software to manage, organize, and analyze the data. While NVivo lacks
the ability to fully stage the data analysis process, it does provide exceptional data man-
agement and data retrieval capabilities that support data analysis and reporting. As tech-
nology advances, the use of electronic filing is common and efficient (Maher et al.,
2018;
Swanier, 2016).
Researchers may use software applications to organize and store electronic data
(Rajesh & Ramesh, 2016). The comments will assist as I arrange the information gath-
ered. Also, I store and organize electronic data using a software application. Moreover, I
applied the coding technique for information retrieval and organization. The hardcopy
documents will be kept in a secure cabinet. I stored electronic information documents in
a computer that is protected by a stronger password. My security structure will help
ensure the confidentiality of the participants and protect the information from
unauthorized per- sons. After five years of secure storage, I will permanently delete the
documents stored in the computer and shred the documents stored in the cabinet.
Data Analysis
Researchers can use multiple data sources in a qualitative study, including data
from semistructured interviews, to explore a research question (Yazan, 2015). Data anal-
ysis includes compilation, disassembling, and reassembling data (Yin, 2018). Consider-
ing my research question, the naturalistic inquiry will be necessary since the question at
hand reflects a real-world approach to improving internal control strategies in business.

The major issue of concern in this research is negating manipulating the phenomenon of
interest, and accordingly, business leaders’ experiences within their organizations will
be informative (Thy et al., 2015).
In my qualitative data analysis, I incorporated semistructured interviews and doc-
umentary evidence. I used coding methods, a software application, and a reflective jour-
nal to organize data. While researchers often use the terms data triangulation and methodo-
logical triangulation interchangeably, data triangulation involves collecting data from multi-
ple sources using three inter-related data points: people, space, and time (Fusch et al., 2018).
Methodological triangulation involves using several sources of data and more than two data
collection methods that contribute to the reliability of results (Fusch et al., 2018; Houghton
et al., 2013). Second, I transferred all transcribed data to a computer-assisted qualitative
data analysis software to help transcribe all the information collected (Sutton & Austin,
2015). Afterward, I coded the data to help compress the information into understandable
con- cepts, properties, and patterns, thus ensuring the information creates meaning. The
last step will be to validate the data based on the accuracy of the design process and the
meth- ods used and then check for procedural consistency to improve reliability. The
robustness of data will be tested through sampling and chi-square tests. Researchers can
use a quali- tative data analytics application to locate and retrieve material related to
themes and codes (De Massis & Kotlar, 2014). Qualitative data analysis vendors include
NVivo, Hy- perRESEARCH, ATLAS.ti, and MAXQDA (Yin, 2018). Researchers utilize
qualitative data analysis applications to analyze, oversee, and increment speed for
organizing subjec- tive subjects (Blaney et al., 2014). These applications can increase the
effectiveness of thematic analysis (Blaney et al., 2014; Brennan & Bakken, 2015). I used

the NVivo 12 application in conjunction with Miles and Huberman’s (1994) data
reduction and display model to comprehensively analyze emergent themes and how the
resultant data was ap- plied to this study.
Researchers use thematic analysis to identify important and recurrent themes in
literature (Pascoal et al., 2016). Thematic analysis allows a researcher to extract
emergent themes from collected data and literature (Teruel et al., 2016). I triangulated
data from in- terviews with company documents. The identification of themes based on
repeated words, phrases, signs, or symbols is a popular method of qualitative data
analysis (Hen- nink & Kaiser, 2020). Researchers often use thematic analysis to read the
data several times and to identify and organize emerging themes related to the research
question (Rohlfing & Sonnenberg, 2016). Therefore, I used thematic analysis to detect
and organ- ize emerging themes.
Reliability and Validity
Reliability
Reliability is the qualitative measure used in the research that must ensure stabil-
ity in the research process as it must create equivalence in the data analysis. Eyisi (2016)
suggested that reliability improves the accuracy of the results. Ensuring credibility and
internal consistency will be critical to ensure that the results fit the objectives of the
study. Dependability is a key consideration during the study design phase. Qualitative re-
searchers include mechanisms for ensuring dependability in the design of their studies to
ensure the integrity of collected data and findings (Marshall & Rossman, 2016). The test
scores achieved must remain constant in the qualitative approach even when another test
or variable is introduced. When ERP questions are introduced in the qualitative ap-

proaches, it is important to ensure that the scores do not change but must be in line with
previous results from the qualitative approach. Connelly (2016) asserted the importance
of using an interview protocol during qualitative case studies in the business and
manage- ment fields to ensure study dependability.
Additionally, this also represents another avenue to ensure conformability in the
research. In this case, the interviews, survey questions, and structured recording must
show a high correlation with the results, and to help achieve this result, all the measures
will use different questions, but they must lead to the same outcomes (Heale &
Twycross, 2015; Johnson, 2015). However, for all these measures to show consistency in
results, the time scale is appropriately selected for the study while also incorporating the
appropriate methodology by considering the study characteristics. Data saturation is a
technique that safeguards that the researcher collectively acquired data (Viet-Thi et al.,
2016).
Reliability is enhanced when the researcher continues data collection until data
saturation occurs. Data saturation occurs when collecting additional data will add new
in- sights to the topic or issue being explored (Hancock et al., 2016). Thus, I continued
my interviews until I reach data saturation.
Validity
Albers (2017) referred to validity as the extent to which a concept is accurately
measured in a quantitative or qualitative study. Validity entails the credibility, transfera-
bility, and conformability of the collected data and research results. I used a combination
of data extraction methods to include methodological data triangulation and documented
audit trails of materials where available. In the following sections, I explained the proce-

dures to assure transferability, credibility, and confirmability of the findings of this
study.
Credibility
Credibility refers to the confidence that the qualitative researcher is truthful with
research study findings (Munn et al., 2014). Connelly (2016) recommended member
checking and reflective journaling as techniques to establish credibility in a finding. Re-
searchers use member checking to allow participants to validate, correct, or extend the
in- vestigator’s interpretation of their experiences as recorded in the interview transcript
(Marshall & Rossman, 2016). I used member checking and provided participants with
summaries of my interpretation of their responses during interviews to ensure the accu-
racy of interpretations. I implemented methodological triangulation to ensure credibility
by comparing the interpretation of interview responses with the analysis of the data col-
lected from reviewing related company documents.
Transferability
Transferability refers to the researcher’s ability to transfer research methods and
findings to other contexts, places, times, and people (Hallberg, 2013). Future researchers
increase the transferability to apply a study's findings to related research (Anney, 2014).
I provided information by evaluating the study results on the phenomenon to provide
read- ers and future researchers with transferable findings to their research.
Conformability
According to Elo et al. (2014), conformability entails reporting participants’ re-
sponses accurately and free of bias. Connelly (2016) indicates that researchers can
ensure conformability by auditing the techniques used to collect and analyze data. Also,

a re- searcher uses multiple data collection methods to explore a phenomenon (Greyson,
2018). The use of methodology triangulation increases the conformability of results
(San- tos et al., 2020). I maintained an audit trail during the research process and
illustrate the data collection process, the coding process, and clustering codes to form
themes. I used different sources of data collection, including zoom interviews,
documentary evidence, and casual observations in this study.
Data Saturation
Data saturation occurs when participant responses become repetitive (Morse &
Coulehan, 2015). Data saturation is critical in qualitative case study research (Yin,
2018). Data saturation arises when additional interviews do not add new information
(Adom et al., 2014; Onwuegbuzie & Byers, 2014; O’Reilly & Parker, 2014). Data
saturation in- volves employing diverse techniques to capture all possible data from
participants. Addi- tional interviews might be necessary to ensure that the researcher
achieves data saturation (Marshall & Rossman, 2016). I reached data saturation through
conducting semistruc- tured interviews, asking probing questions during interviews, and
using member check- ing. A researcher attains data saturation when additional data
collection does not result in additional themes (Morse & Coulehan, 2015). I continued to
collect data until no new themes or patterns emerge. I reached data saturation after
conducting four interviews and reviewing documents from seven participants, no new
themes emerged when analyzing the responses of the seventh interview.
Transition and Summary
In Section 2, I explained my role in the research, described the target population,
listed the participant selection criteria, and discussed the research method and design. I

explored the effective control strategies for ERP systems. I addressed the qualitative
research method and a case study design to analyze various business leaders' attributes
about applying effective internal controls for enterprise resource management. I closed
Section 2 with an explanation of the processes I implemented to ensure reliability and
validity of the study findings. In Section 3, I include the findings of my research, their
application to professional practice, and my recommendations for how applying internal
control strategies for ERP can avoid fraudulent transactions. Qualitative approaches are
different in various scenarios. The incorporation of qualitative techniques depends on the
type of information required. Crucial to create coherence and align all aspects of the
research project to improve focus and design. The research has established that the
research question will be structured so that the problems that tap into the concept under
review are internal control systems versus ERP systems. Section 3 concludes with
analysis of the implications for social change, my reflections, and a concluding
statement.
Section 3: Application to Professional Practice and Implications for Change
Introduction
The purpose of this qualitative single case study was to explore the effective
internal control strategies for ERP systems business leaders use to reduce risks from
reporting and erroneous transactions. I derived the data from semistructured interviews
with seven business leaders at one business in Mississippi who had successfully
implemented effective internal control strategies for their ERP systems. Through
methodological triangulation, I supplemented the interview data with documentary
evidence from internal documents. The COSO conceptual framework, the detailed

literature review, and the data collected and analyzed were crucial in this data analysis
leading to the emergence of three main themes. Using Yin’s (2018) 5-step data analysis
process, three themes emerged. The themes derived in the study were: (a) effective
internal control strategies, (b) overcoming barriers to implementing internal control
strategies, (c) addressing key internal control challenges.
Presentation of Findings
The main research question in this study was: What effective internal control
strategies for ERP systems do business leaders use to reduce risk reporting and
erroneous transactions? I interviewed seven business leaders that had experience in the
implementation of ERP systems in reducing risk reporting and erroneous transactions.
Furthermore, I accessed more data about the firm through observation and document
reviews. Thus, based on the information I accessed about the organization and the
responses of the interviewees in relation to the research questions was critical in
addressing and answering the research. Furthermore, I relied on NVivo 12, Miles and
Huberman’s (1994) data reduction, as well as the display model to help in
comprehensively analyzing the emergent themes.
Three main themes emerged from the analysis, including internal control
strategies, overcoming barriers to implementing internal control strategies, and
addressing the key internal control challenges. Recommendations from participants
included ways of using and measuring the effectiveness of internal control strategies and
the additional strategies to help safeguard the organizations.
Theme 1: Internal Control Strategies
The purpose of the internal control strategies for an ERP system is to reduce the
risk of fraudulent reporting as well as erroneous transactions. Applegate (2019)
suggested that organizations should create a robust COSO control environment to help
deter fraud and emphasize the importance of ethical behavior and adherence to internal
controls. Based on the interview data, participants had their preferred internal control
strategies. In this case, P6 preferred “to use the access reviews and the cash control by
trusted people as the main internal control strategies.” P3 stated, “I prefer automation
and password security as the key internal strategy.” P1 stated that, “it is effective to
apply the use of distributed control on the transaction, restricted control on company
credit card use, as well as monthly reconciliation of bank accounts.” P3 stated, “I am
comfortable with the application of frequent audits.” As displayed in Table 1, there were
a total of 17 references for the application of various internal control strategies.
Table 1
Internal Control Strategies (Frequency)
Source Number of thematic specific comments
P6 2
P3 5
P1 10
Total 17
To access review was a preferred internal control strategy that one business
leader found to be critical in the reduction of fraudulent reporting as well as erroneous
transactions. One participant felt that they have managed to ensure the internal control
strategy for the ERP system goes through the monitoring, which involves accessing the
reviews based on the job requirements. In this case, P6 reiterated that, “I have been using

regular access reviews to ascertain who has the authority to access what, and at which
level does their job requirement need them to have access right as a user.” The response
aligned with the COSO model component of control activities. The COSO model
outlines that control activities enables an organization to identify and mitigate the errors
and biases in the financial reporting (Shaiti, 2014).
P3 indicated that, “there is big need for automation and the application of password
security.” In this case, the strategy was found to be effective in controlling the access to
the accounting systems to ensure that it permits authorized individuals to access the
company’s information system. The participant maintained that access controls are a
critical control that must be embedded in the system. As such, P3 reiterated:
“Controlling the access to the accounting systems through strategies such as passwords,
lock-outs, and electronic access ensures authorized parties can only access the system.”
In this case, it is evident that the accounting system of an organization has to remain
intact, and as such, it has to apply various approaches. According to Moeller (2013), the
COSO model component of the control environment, which is considered effective and
reliable in shaping the internal control function, assists managers in overseeing their
responsibilities and defining authority as well.
P1 was involved in the implementation of distributed control on the transaction,
use of monthly reconciliation of bank account, and restricted control on company credit
card use. The participant found out that the three strategies were suitable for helping an
organization to manage fraudulent reporting as well as erroneous transactions. P1 opined
that, “one of the strategies I used is a checks and balances system to make sure that
nobody has control over all parts of a transaction.” The participant felt hat limiting

people on certain aspects of the transactions helps in reducing fraudulent reporting as
well as erroneous transactions. Furthermore, P1 stated that, “I reconciled the
organization’s bank accounts every month,” which is crucial in safeguarding the
proceeds of the bank accounts. The participant also clarified, “I implemented a
restriction on the use of the company’s credit cards and verified all the transactions made
using the credit cards to ensure they were business-related.”
P3 maintained that conducting frequent audits is vital in ensuring that an
organization remains safe and all the transactions are recorded well. The participant
mentioned, “Physical audits of assets involve bypassing electronic record-keeping
though the process may be carried out less frequently as it involves physically tracking
various physical assets.” The response aligned with the perspective of the COSO model
related to monitoring activities which help in defining the strategies that an organization
has adopted in assessing the internal system’s quality over time (Rubino et al., 2017). In
addition, P6 found out that trusted individuals need to be considered to have access to
the cash control center. P6 mentioned, “I have been using only a few trusted employees
to make our deposits and make them as frequently as possible.” Limiting the number of
people that access the cash reserve control center helps to limit the leaking of
information, passwords, and transactions that can lead to huge losses (Rose et al., 2015).
My assessment of the company documents supported the comments, responses,
and reactions of the participants about the infusion of internal controls in the ERP system
to reduce fraudulent reporting as well as promote erroneous transactions. Based on this
case, the firm adopted various strategies, such as the access reviews. These review audits
were crucial in ascertaining the authority that is mandated to access organizational

documents and operations. My document review also revealed that the application of
automated processes and password security helps in controlling access to the accounting
system. In addition, I realized that the firm trusts a few individuals to control the cash,
especially when making deposits. The firm has conducted frequent audits, which involve
physical assessment and evaluation of the electronic to keep the record.
Based on this assessment and results, I connected the them with previous
researchers. For instance, Rajesh and Ramesh (2016) argued that the adoption of
effective internal audit processes helps in creating better opportunities for better internal
control systems. Internal audit helps an organization in creating platforms that promote
effective governance and control activities. On the other hand, Pett et al. (2015) argued
that effective implementation of an ERP system requires an assessment of the workforce
to determine the most trustworthy individuals that will be responsible for the
improvement and implementation of the adopted strategies. A successful organization
needs to consider revising its workforce and offering the mandate to the trusted
individuals alone. The handling of duties and responsibilities like cash reserves requires
the management to have a long-term connection with the people responsible for the
work.
The participants discussed their views on the measured effectiveness of ERP
internal control strategies for fraudulent reporting and erroneous transaction risks by
finding out ways of measuring the effectiveness of internal control strategies. The united
workforce having an ethical conduct of the leaders and the workers and the assessment
of the current communication system used to make up the main ways a firm can measure
the effectiveness of an internal control strategy (Haislip et al., 2015). Based on the
responses of the seven participants, it became evident that different leaders had different
ways of measuring the effectiveness of internal control strategies. As such, as displayed
in Table 2 there were 11 leadership references for different ways to measure the
effectiveness of internal control strategies.
Table 2
How to Measure Effectiveness of Internal Control Strategies (Frequency)
Source Number of comments related to effective
measures
P7 1
P2 1
P5 3
P1 3
P4 3
Total 11
P1 offered three main suggestions on how to measure the effectiveness of
internal control strategies. First, it was the use of an assessment of the ethical conduct of
employees where the participant stated, “I assessed the control environment to ensure the
employee operated with ethical values and integrity.” The second suggestion was to
evaluate the available communication system, and he outlined, “I examined
communication and information systems to assess the accuracy and efficiency of
reports.” The last suggestion was based on evaluating the risk control system, and the
participant mentioned, “I evaluated the risk management to audit compliance and risks
internal controls are designed properly.” More so, P2 adopted the use of key
performance indicators where she mentioned, “Since ERP systems are fully integrated

with the system of reporting and dashboards, I used the key performance indicators for
measuring the efficiency of the control systems in place.”
Another participant maintained that the assessment of harmony among the
workers was an effective way. In this case, participant P7 stated, “In measuring the
effectiveness of ERP internal control strategies, the focus was to determine the
harmony and working relationship of workers in each department.” P5 relied on the
assessment of the proper functioning of systems as an evaluation measure. In this case,
the participant mentioned that “by determining the extent to which the stated control
measures fulfill proper functioning of the organization with regards to ERP’s control
environment, risk assessment, information and communication control activities, and
monitoring.” Regular auditing and review of fraudulent reporting were the two ways
that P4 found reliable to measure the effectiveness of internal control strategies. Thus,
P4 mentioned that “auditors regularly audit ERP system together with manual evidence
to ensure no fraudulent activity occurs” as well as “The ERP system conducts book
balancing for the casino. Unbalanced books were flagged as erroneous and fraudulent
using the system, requiring the responsible parties to adjust the books.”
The responses aligned with some of the findings from the current literature. For
instance, Alrobaish et al. (2022) found out that the ethical conduct of the workers has
been an integral aspect in assessing the effectiveness of an internal control strategy as it
helps in revealing the applied ethical values and integrity. In this study, the assessment
of the ethical conduct of the students was critical because it revealed that the
organization adheres to the goals, policies laid in place, and mission. More so, systems in
a firm tend to reveal the effectiveness of the management, plans, and ERP system (Ettish

et al., 2017). When an organization has reliable systems in place, it ensures that the
assessment of risks, communication, information, and control activities are well
structured and working out well.
Theme 2: Overcoming Barriers to Implementing Internal Control Strategies
The model assesses approaches for entering the market while remaining
sustainable. According to the notion of strategy, an organization functions in a
continually changing environment as society is essentially dynamic. It is the
responsibility of the business to evolve with the times (Mansaray, 2019). This includes
adapting to a variety of factors, including as shifting customer preferences, advances in
technology, shifts in political ideology, and globalization. A strategic company strategy
handles all of these functions simultaneously, ensuring that the majority's perspectives
are reflected. Thus, there are social, technological, financial, political barriers while
implementing internal controls.
The responses of the participants indicated that the adoption and implementation
of internal controls tend to have some key barriers in their implementation process.
When adopting the ERP system to reduce the fraudulent reporting and erroneous
transaction risks means that an organization may face challenges or barriers which come
in different ways, and there is no systematic number of barriers involved. A variation in
the operations, resources, and the number of workers is a major factor when developing
an internal control strategy (O’Reilly & Parker, 2014). Participant responses implied that
a firm will not lack any barrier in implementing internal control strategies. Thus, Table
3.
displas the frequency of the theme in identifying the various barriers to the
implementation of the internal control strategies.
Table 3
Barriers to Implementing Internal Control Strategies (Frequency)
Source Number of comments related to barriers
P3 2
P2 2
P6 2
P5 1
P1 5
P4 1
Total 13
Based on Table 3 there were 13 references to the identification of barriers that
ERP systems face in the implementation of internal control strategies. One business
leader relied on the achieving buy-in of all actors as a major barrier in implementing the
internal control strategies. Furthermore, each leader argued that the compliance of issues,
rob rotation, dealing with a lot of cash during the transaction, poor-data quality, the
requirement for constant system updates, and poor management skills were the main
barrier experienced. On the other hand, three leaders or participants found out that
resistance to change was a major barrier, with two clarifying that lack of human
resources and capacity and high cost of risk control was the major barriers encountered.
In this finding, P3 stated: “Mobilizing donors to facilitate the various protocols”
was the main challenge experienced in achieving the buy-in of all actors. Participants
referred donors as individuals or organization which can offer services which could help
them to overcome barriers. P3 further noted that “compliance and enforcement

challenges are significant as involved parties undertake the various protocols
effectively.” The participant was trying to address the issue of challenges that arise due
to the compliance issues. On the other hand, P2 noted, “It is more time consuming to
comply with available set standards and regulations as it is a multiple-step process” due
to the barriers related to the high risk of control. P6 found out that dealing with lots of
cash during the transaction is a major barrier and thus cited that, “A lot of cash
transactions resulted in having a lot of cash in the office at given times.” Furthermore,
the participant outlined that job rotation is a major hindrance to the implementation of
internal control strategies. The participant noted that “change in operational
responsibilities of my employees resulted in a challenge because new roles allocated had
to facilitate change in user rights every time there was a change.”
It is evident that different leaders highlighted different barriers as P5 found out
that lack of human resources and capacity was a major hindrance to implementing
internal control strategies. In this case, the participant noted, “Insufficient staff members
make segregation of duties difficult.” P4 further claimed, “The primary barrier while
implementing the system was the changing business environment requiring constant
updates for optimal results.” P1 managed to identify various barriers like the resistance
to change and claimed, “Resistance to change by some sections of the employees or
management” hindered some organizations in implementing the realization of internal
control strategies. Furthermore, poor management skills were found to be a major
concern as P1 cited, “poor project management and planning” made it difficult to
implement the internal control strategies.

In addition, my analysis of the firm in identifying the various barriers to
implementing internal control strategies was based on the ability of the different leaders
to identify the main challenges that they face. In this case, leaders like P1 found out that
poor management skills and poor data quality were the main barriers. The participants
affirmed the findings from previous literature. For instance, it was clarified that the
auditor might lack professional competence to form a quality assurance from the audit
operations because of a lack of professional training (Moeller, 2014). Al-Sady et al.
(2021) suggested that internal control training need to be completed at all level of the
organization. In this study, participants indicated that inadequate professional
competence could be caused by a lack of continuous training and improvements to
ensure that the auditor is conversant with organization to control environment, risk
assessment, information and communication, monitoring activities, and existing control
activities.
Theme 3: Addressing Key Internal Control Challenges
Participants in this study discussed the best ways to address and deal with the
challenges that the organization faces in implementing the internal control strategies for
the ERP systems with the aim of reducing fraudulent reporting as well as erroneous
transaction risks. As leaders, it is important to have an in-depth understanding of the
different ways of handling barriers that hinder smooth flow or implementation of internal
control strategies (Martin et al., 2014). The participants found different ways of handling
and dealing with the barriers. Table 4 below displays the frequency of the theme in
addressing the barriers to internal control strategies. The table shows that there were 16
comments of addressing the key challenges in internal control strategies.
Table 4
How to Address Key Challenges
Source Comments associated to challenges
P3 1
P2 1
P6 3
P5 1
P1 7
P4 3
Total 16
One key approach focused on by participants was the use of functional structure
and leadership. P3 stated: “Adopting a functional culture and leadership techniques” is
considered effective and reliable.” In addition, the approach to building capacity for the
staff members was found an appropriate way, and P4 opined: “I overcame lack of
leadership challenge by offering constant training and user support until the employees
were conversant with the system.” The study outlined that the use of another efficient
parallel system was considered reliable, and P2 stated: “I didn’t completely rely on the
sole system as I always kept another system which was more efficient and quicker.” P6
proposed the use the promotion of cash-less transactions and employee rotation. In this
case, the participant outlined “advocating for cashless transactions by the clients to
minimize the handling of a lot of cash in the office” as well as “I designed a policy
together with the management of specific periods of staff to change their roles.”
Participants suggested other methods like achieving widespread buy-in were
proposed. In this case, P1 explained, “I also obtained buy-in from stakeholders and
leaders across the department before the implementation process to prevent any form

of resistance that could arise.” The participant also proposed that efficient
communication was seen as a considerable approach. In this case, “timely two-way
communication” was preferable in dealing with barriers to the implementation of
internal control strategies. The other strategy outlined in this study was the reliance on
setting realistic goals and time frames. In this case, P1 reiterated, “To ensure proper
planning and management, it is important to set realistic milestones, timeframes, and
expectations, together with timely two-way communication.” P1 also found the
validation of data quality an important approach as the participant feels “that it
ensured data quality by validating and cleaning out duplicates and adding missing
information before transferring them to the ERP system.”
My review of this case scenario concluded that no approach is more important
than the other. In this case, P1 managed to outline four main ways of handling the
barriers affecting internal control strategies. Furthermore, I realized that the responses
affirmed the previous literature. According to Johnson (2015), management acts as the
agent for optimizing the value in an organization. The setting up effective management,
which is based on a working structure, offers a leeway in developing reliable
mechanisms for setting up an effective internal control strategy.
Furthermore, effective communication is considered a solution to aligning the
working mechanisms of an organization as it fosters a good understanding between the
different parties (Jagoda & Samaranayake, 2017). Other researchers have identified the
challenges of communication and how communication is embedded in the COSO
framework. Effective communication includes the transfer of information across the
entity to stakeholders (Edimo et al., 2022; Rubino et al., 2017). Embedded in the COSO

framework is management’s responsibility to provide a clear message throughout the
organization (COSO, 2017).
The participants discussed additional strategies that the organization can
implement in relation to the internal control strategies for an ERP system in mitigating
the reporting and erroneous transaction risks. The responses offered a deeper insight into
the existing strategies that can be adopted for ERP systems. There are many sources of
errors and challenges in the implementation of a reliable and smooth ERP system (Chen
& Keung, 2018). The two participants found out that apart from the current strategies
that the casino business is implementing, there are other strategies that are relevant for
ERP systems.
Participants identified additional strategies referenced in an ERP system when
handling internal control strategies in the organization. P6 noted that the auditing of
physical assets had been a major strategy in handling internal control strategies in ERP
systems to mitigate reporting and erroneous transaction risks. The participant clarified, "I
have also been using other internal control systems in my accounting departments like;
asset audits which we physical verification of assets in regard to the records." In
addition, cloud backup has been a major strategy that organizations can consider. As
such, P6 noted, "Data backups to the cloud are another method I use as an internal
control; when the computers are corrupted, or servers fail, we can easily retrace our
data." I also noted that the use of written policies and procedures had become an
important strategy. P5 clarified “that she develops written policies and procedures to
enhance awareness, ensure adequate staff training, identify potential areas of fraud and
risks concerning the system, and develop mitigation plans.”

My analysis of the company revealed that the casino business can still
incorporate more strategies in the ERP systems to mitigate reporting and erroneous
transaction risks. In this case, I managed to understand that the business usually conducts
an annual physical audit of all the assets. Such progress implies that the firm can still
make this a regular exercise. The use of physical asset assessment has been applied to
ensure that the company manages to understand all the available assets and their
implications on the operations. It has also enabled the firm to determine the status of the
assets to improve the performance of the organization. As such, the use of physical
documents and evaluation of the firm showed that the firm has been taking too long to
conduct such an assessment which needs to be done quite regularly.
The findings from the participants aligned with the previous literature. For
instance, the use of physical auditing assets has been implemented in the organization to
determine their value, uses, and effectiveness in promoting operations and working
(Chalmers & Khlif, 2018). The study noted that physical count and assessment of the
assets help an organization to understand its worth, capability, and aspects it can
improve on. Furthermore, the current business environment requires an organization to
back up its data, information, and internal controls to avoid losses and changes in the
configuration of the firm (Binder, 2016). It is one of the most effective ways to create a
better understanding of the business environment as it highlights the key issues and ways
of safeguarding the operations.
Application to Professional Practice
The findings from this study are critical for the leaders in a casino business to
understand better ways of developing internal control strategies that are crucial for ERP

systems to reduce fraudulent reporting as well as erroneous transactions. The finding
offers deeper insights that the various leaders at the casino have used to incorporate
internal control strategies in the ERP system. The emerging themes have been relevant in
ensuring that the casino businesses apply professional practices in implementing internal
control strategies. The thematic issues in the study have been crucial in ensuring that the
casino businesses understand better ways of reporting fraud as well as reducing errors
during transactions. Business managers are in a position to offer the best guidelines for
improving the business operations of the firm (Agarwal & Ansell, 2016). The leaders
helped in creating better ways to understand more about internal control strategies in the
firm, identifying the barriers that hinder the organizations in implementing the internal
control strategies, ways of addressing the key challenges, ways to measure the
effectiveness of internal control strategies, and ways of using the internal control
strategies.
The themes that emerged from the data analysis applies to professional practice.
The findings offer rich and diverse internal control strategies to different managers to
use in their ERP systems. It will help to understand the importance of having an internal
control strategy. The study findings will be relevant in ensuring that business owners and
managers find it critical to develop better internal control strategies that will be applied
in the ERP systems. The findings will also help in the reduction of reporting errors and
transactions for an organization. In addition, participants presented practical practices
and strategies that organizations can use to benefit from the implementation of ERP
systems. The goal of internal controls is to ensure that the adopted internal control
strategies align with the business needs, goals, mission, and vision. These controls will

improve the business operations and thus ensure that the reporting and handling of the
company operations are free of errors, which will lead to the seamless functioning of the
firm. The adoption of the internal control strategies will enable the businesses to improve
on the innovation, and this means that the leaders will understand the handling of
company affairs, especially when handling the finance department.
Small businesses and firms like the casino businesses need to find out the benefit
of having a smooth working relationship between the leaders and the workers. It reveals
the importance of having a closely-knit working relationship between the workers and
the leaders. The application of the findings like developing effective internal control
systems, developing the right attitudes towards the workers, and the segregation of
duties. It will ensure that the business leaders benefit by increasing their need to have a
deeper insight into ERP systems. Furthermore, it is evident that the study will be vital for
the leaders to realign their internal controls and ensure that they develop a reliable and
effective working ERP system. It also means that when an organization manages to
establish a reliable internal control strategy, it will be easier to promote facets of
accountability and profitability as it will lead to a reduction in the fraudulent business
deals and errors that occur during transactions.
Implications for Social Change
The casino business has played an important role in the promotion of the
economy. The business offers job opportunities to different people, from the waiters and
the managers to the supervisors. It is one of the best places that people can source
employment, although its functioning and management need to ensure that all the
departments are working closely with each. It also implies that the leaders have to devise

better ways of improving their performance (Adom et al., 2014). The working
relationship between the leaders and the employees needs to be flawless. As such, it will
help to align the perspectives that the workers and the community have towards working.
It will help to improve standards and character. It is a better way of ensuring that people
learn to focus on quality production. It is a better way of ensuring that organizations
remain sustainable as there will be a balance between the production and the needs of the
market or the community.
The findings from this study are quite relevant and important for the business
leaders as well as the community. It will depict the efficiency with which the business
leaders can identify and detect the presence of fraud during reporting as well as prevent
future erroneous transaction risks. Thus, when business leaders participate in the
implementation of the ERP system, it will be easier to promote the efficiency with which
they will manage to handle the internal controls. It means that when a business manages
to develop strong internal control strategies, it is easier to propel the business to rise and
attain success. It will also aim at promoting the economic wellbeing of the community.
As such, it means that leaders will be in a position to improve the economic wellbeing of
society. When the leaders manage to create and develop effective and reliable internal
control strategies, it is easier to improve the social and cultural wellbeing of the community
by creating a consistent source of employment. Thus, it means that developing consistent
working or employment opportunities will allow an organization to empower the residents
in a community, and this propels it towards becoming better.
Recommendations for Action

The findings from this study call upon the casino business leaders to consider
implementing internal control strategies in the ERP systems. It aims at ensuring that the
firm offers better production by reporting fraudulent transactions and reducing the
occurrence of errors during the transaction. The results offer deeper insights on the best
way to promote the better working of internal aspects of an organization. It also calls for
defining better strategies that can be applied to reducing errors and fraud. Fraud is very
damaging to any business but losing money to fraud in the nonprofit sector can be more
damaging as it undermines morale, tarnishes the organizations ‘reputation, and erodes
public confidence in such organizations (Ohalehi, 2019). The implies firm needs to
understand the need to have a flawless relationship between employees and the leaders.
Developing different internal control strategies enables an organization to develop
integrated ways of handling crises, fraud, and avoiding errors.
Based on the study findings, it was evident that handling internal control
processes may involve various strategies. In this case, the study proposed different
strategies like the improvement of the relationship of the employees. There is a need to
promote the working relationship of the workers. One way that can be applied is
through segregation of duties, as this will ensure that a single individual or department
has control over the complete business process (Pańkowska, 2022). The propel an
organization's departments to work closely to work together, and this boosts their
working relationships. It is a better way of ensuring that each employee is held
responsible for their work, duties, and responsibilities. Company employees can also be
trained on importance of practicing high level of ethics while performing their duties
through literature and conferences.

The second recommendation is management and Board of Directors review and
oversight. Purchases, expenditures, budgets, and monthly financial statements should all
be reviewed and authorized by the aforementioned. The third recommendation is
implementation of effective internal controls including restricted use of cash The
considerable fraud risk connected with the use/presence of cash on premises is the basis
for this idea. When possible, managers should try to reduce or eliminate the use of cash.
This can be accomplished by prohibiting the use of cash and requiring payment by credit
or debit card instead. In addition, managers may consider the implementation of a
whistleblower policy and segregation of critical duties whenever possible.
Reviewed literature and the findings within this study develop processes to
support decision-making in areas of structure, strategy, management control, and
management support leads to undesirable effects for the internal control system,
undermining the ability of the internal system to support ERP effectiveness.
Implementation of the recommended strategies may minimize fraud risk and reduce
financial loss associated with fraud incidents in organizations. I will provide the
study findings to managers in organizations via professional publications. In
addition, I plan to present study findings at conferences and training sessions.
Managers of organizations may increase their understanding and knowledge
regarding effective fraud risk mitigation strategies which may aid in the education of
financial loss due to a fraud incident.
Recommendations for Further Research
The findings from this study have revealed that there is a need to adopt more
internal control strategies. Participants suggested that developing internal control

strategies will be crucial in ensuring that firms like the casino businesses benefit more
from their operations. For instance, firms need to use cloud backup as a new strategy.
This approach will ensure that there is the involvement of new and traditional methods in
updating and promoting internal control processes. I would suggest that there is a need to
expand the exploration of digital platforms when handling internal control strategies as
well as ERP systems. The study adopted a single case study, and this limited the data
collection to a single business entity. A single case study is appropriate when the
researcher is interested in a concentrated holistic understanding of a single unit (Gaya &
Smith, 2016). This study was based on the different ways that the leaders use to handle
the issues related to ERP systems. Thus, I would suggest that future studies adopt
multiple case studies to ensure that we get a different insight into the way leaders can
handle internal control strategies in ERP systems to reduce the available errors and
report on transactions.
Reflections
My first impression during this study was that the participants would not be
cooperative and supportive. However, I later realized that the participants were willing to
offer a detailed explanation and description of their experience in handling the internal
control strategies. I was impressed with their personal insights on different issues, which
helped to develop three main themes.
I chose to research lack effective internal control strategies for ERP systems to
reduce risks from reporting and erroneous transactions. Throughout my professional
career I have worked with numerous organizations and witnessed the unique challenges
these groups face regarding fraud risk. My hope was to reduce risks from reporting and

erroneous transactions to similar organizations. Adoption of these strategies may help
organizations avoid fraud incidents and the associated reputational and financial loss.
My previous job in the organization sector as well as with internal controls
presented possible personal biases regarding the lack of effective internal control
strategies for ERP systems to reduce risks from reporting and erroneous transactions. I
had to set aside any preconceived ideas about the internal controls I believed to be
necessary or best for reducing risks. Reservation of my personal bias and ideas was
necessary in order to allow the findings of the study to reveal the actual effective reduce
risks from reporting and erroneous transactions.
The DBA doctoral study process provided an opportunity for me to develop
valuable research skills. I have gained an understanding of the research process as well
as an appreciation for data gathering coding and qualitative analysis. I would like to
expand upon my initial study and research to reduce risks from reporting and erroneous
transactions. In addition, I plan to continue writing and presenting findings with the hope
that it will help organizations avoid costly, damaging fraud incidents.
Conclusion
The purpose of this qualitative single case study was to explore the effective
internal control strategies for ERP systems for business leaders in reducing the risk
reporting and erroneous transactions. The target sample was seven business leaders
working in a casino in Mississippi. Based on the five-step thematic analysis recommend
by Yin (2018), three themes emerged, including (a) internal control strategies, (b)
overcoming barriers to implementing internal controls, and (c) addressing key internal
control challenges. The leaders gave various insights that supported each emergent

theme. The internal control strategies outlined by participants were straightforward.
While the themes have direct application to the implementation of an ERP in a casino,
the emergent themes provide guidance for other industry leaders.

