


CHAPTER 1
Introduction
The modern Smart Grid has two interwoven components, the cyber commu-
nication network and the physical components of the power grid. The duality of
the power grid creates a unique challenge to protect the grid from natural outages,
such as weather-related causes, as well as cyber or physical attacks. The cyber
and physical layers of the modern power grid rely on constant and accurate com-
munication to maintain a stable power grid. Many experts estimate that over the
next 20 years, the energy market will be flooded with millions of new wind farms,
photovoltaic plants and other distributed energy resources [11] along with the mas-
sive energy storage systems [12] required to balance the ever-increasing loads on
the grid [13]. The increasing popularity of electric vehicles will only intensify the
need for smart control of the power grid [14]. These energy resources and storage
systems will need to function in perfect harmony to maintain grid stability. As
computing solutions become cheaper and more powerful, the integrated systems
can be controlled and monitored in ways that were previously not thought to be
possible due to expense and required resources [15]. The development of smart
devices and the Internet of Things (IoT) has created the opportunity to monitor
and control Smart Grids in new ways. The Smart Grid will depend on a digital
communication between the power utility in the Smart Meters, commonly referred
to as advanced metering infrastructure (AMI). The Smart Grid will require pass-
ing immense amount of data from the distributed energy resources (DERs) to the
control station requiring better data networks [16]. The latest in embedded system-
on-chip and cloud-based computing servers allow the digital twin to overcome the
issue of processing the large amount of sensor data generated by the Smart Grids
1
[17].
The energy sector is identified as uniquely critical because it provides an en-
abling function across all infrastructure sectors [18]. It is estimated that the cost of
a single wave of cyber attacks on the US critical infrastructures could exceed
$
700
billion and every one of the 16 critical infrastructures relies on the energy sector to
function [19]. However, the critical nature of the power grid also makes it a target
for malicious attack, as reported in various references [20] [21] [22] [23]. The mod-
ern power grid requires increasingly complex methods to detect cyber-physical
anomalies in order to maintain and improve the resiliency of the cyber-physical
system. Without future advancements, the legacy Supervisory Control and Data
Acquisition (SCADA) system will continue to have difficulty responding to the
escalating cyber attacks [24].
As the modern power grid continues to morph into the future Smart Grid,
there is a need to develop new methods to leverage the emerging data that has
become available through the AMI and provide additional insight into the operat-
ing state of the power grid. One potential way to leverage this data is through the
use of Digital Twin technology coupled with advanced machine learning and data
processing techniques. The potential power of a fully deployed digital twin pro-
vides exciting possibilities for improving the cyber physical security of the future
grid as well as an avenue to visualize the response of the power grid when placed
under duress.
1.1 Background into Digital Twin Technology
1.1.1 What is a Digital Twin?
Over the last two decades, the concept of the digital twin has taken many
forms depending on the engineering need of the specific application. Digital twins
have been defined as ultra-high fidelity simulation environments to an evolving
2

product model to real-time dynamic representation of a physical system, as well
as many others. While there are many concepts that are accepted as digital twins,
this dissertation focuses on the digital twin as described by Dr. Michael Grieves in
his 2002 presentation for the formation of a Product Lifecycle Management (PLM)
center [25]. Originally called the “Conceptual Ideal for PLM”, this concept became
the framework of the modern digital twin architecture. The definition put forth
by Dr. Grieves was taken a step further to include “an integrated multiphysics,
multiscale, probabilistic simulation of an as-built vehicle or system that uses the
best available physical models, sensor updates, fleet history, etc., to mirror the
life of its corresponding flying twin” [11]. To accomplish this, the digital twin
needs to expand beyond the traditional modeling and simulation techniques by
incorporating sensor feedback in the simulation and even can close the loop by
feeding information from the simulation back into the physical model in real-time.
Digital twins have been found to be useful in many industries and as such the
research of digital twins has rapidly increased over the last decade. Figure 1 shows
the growth in IEEE journal publications in the field of Digital Twins from 2016
through 2022.
3
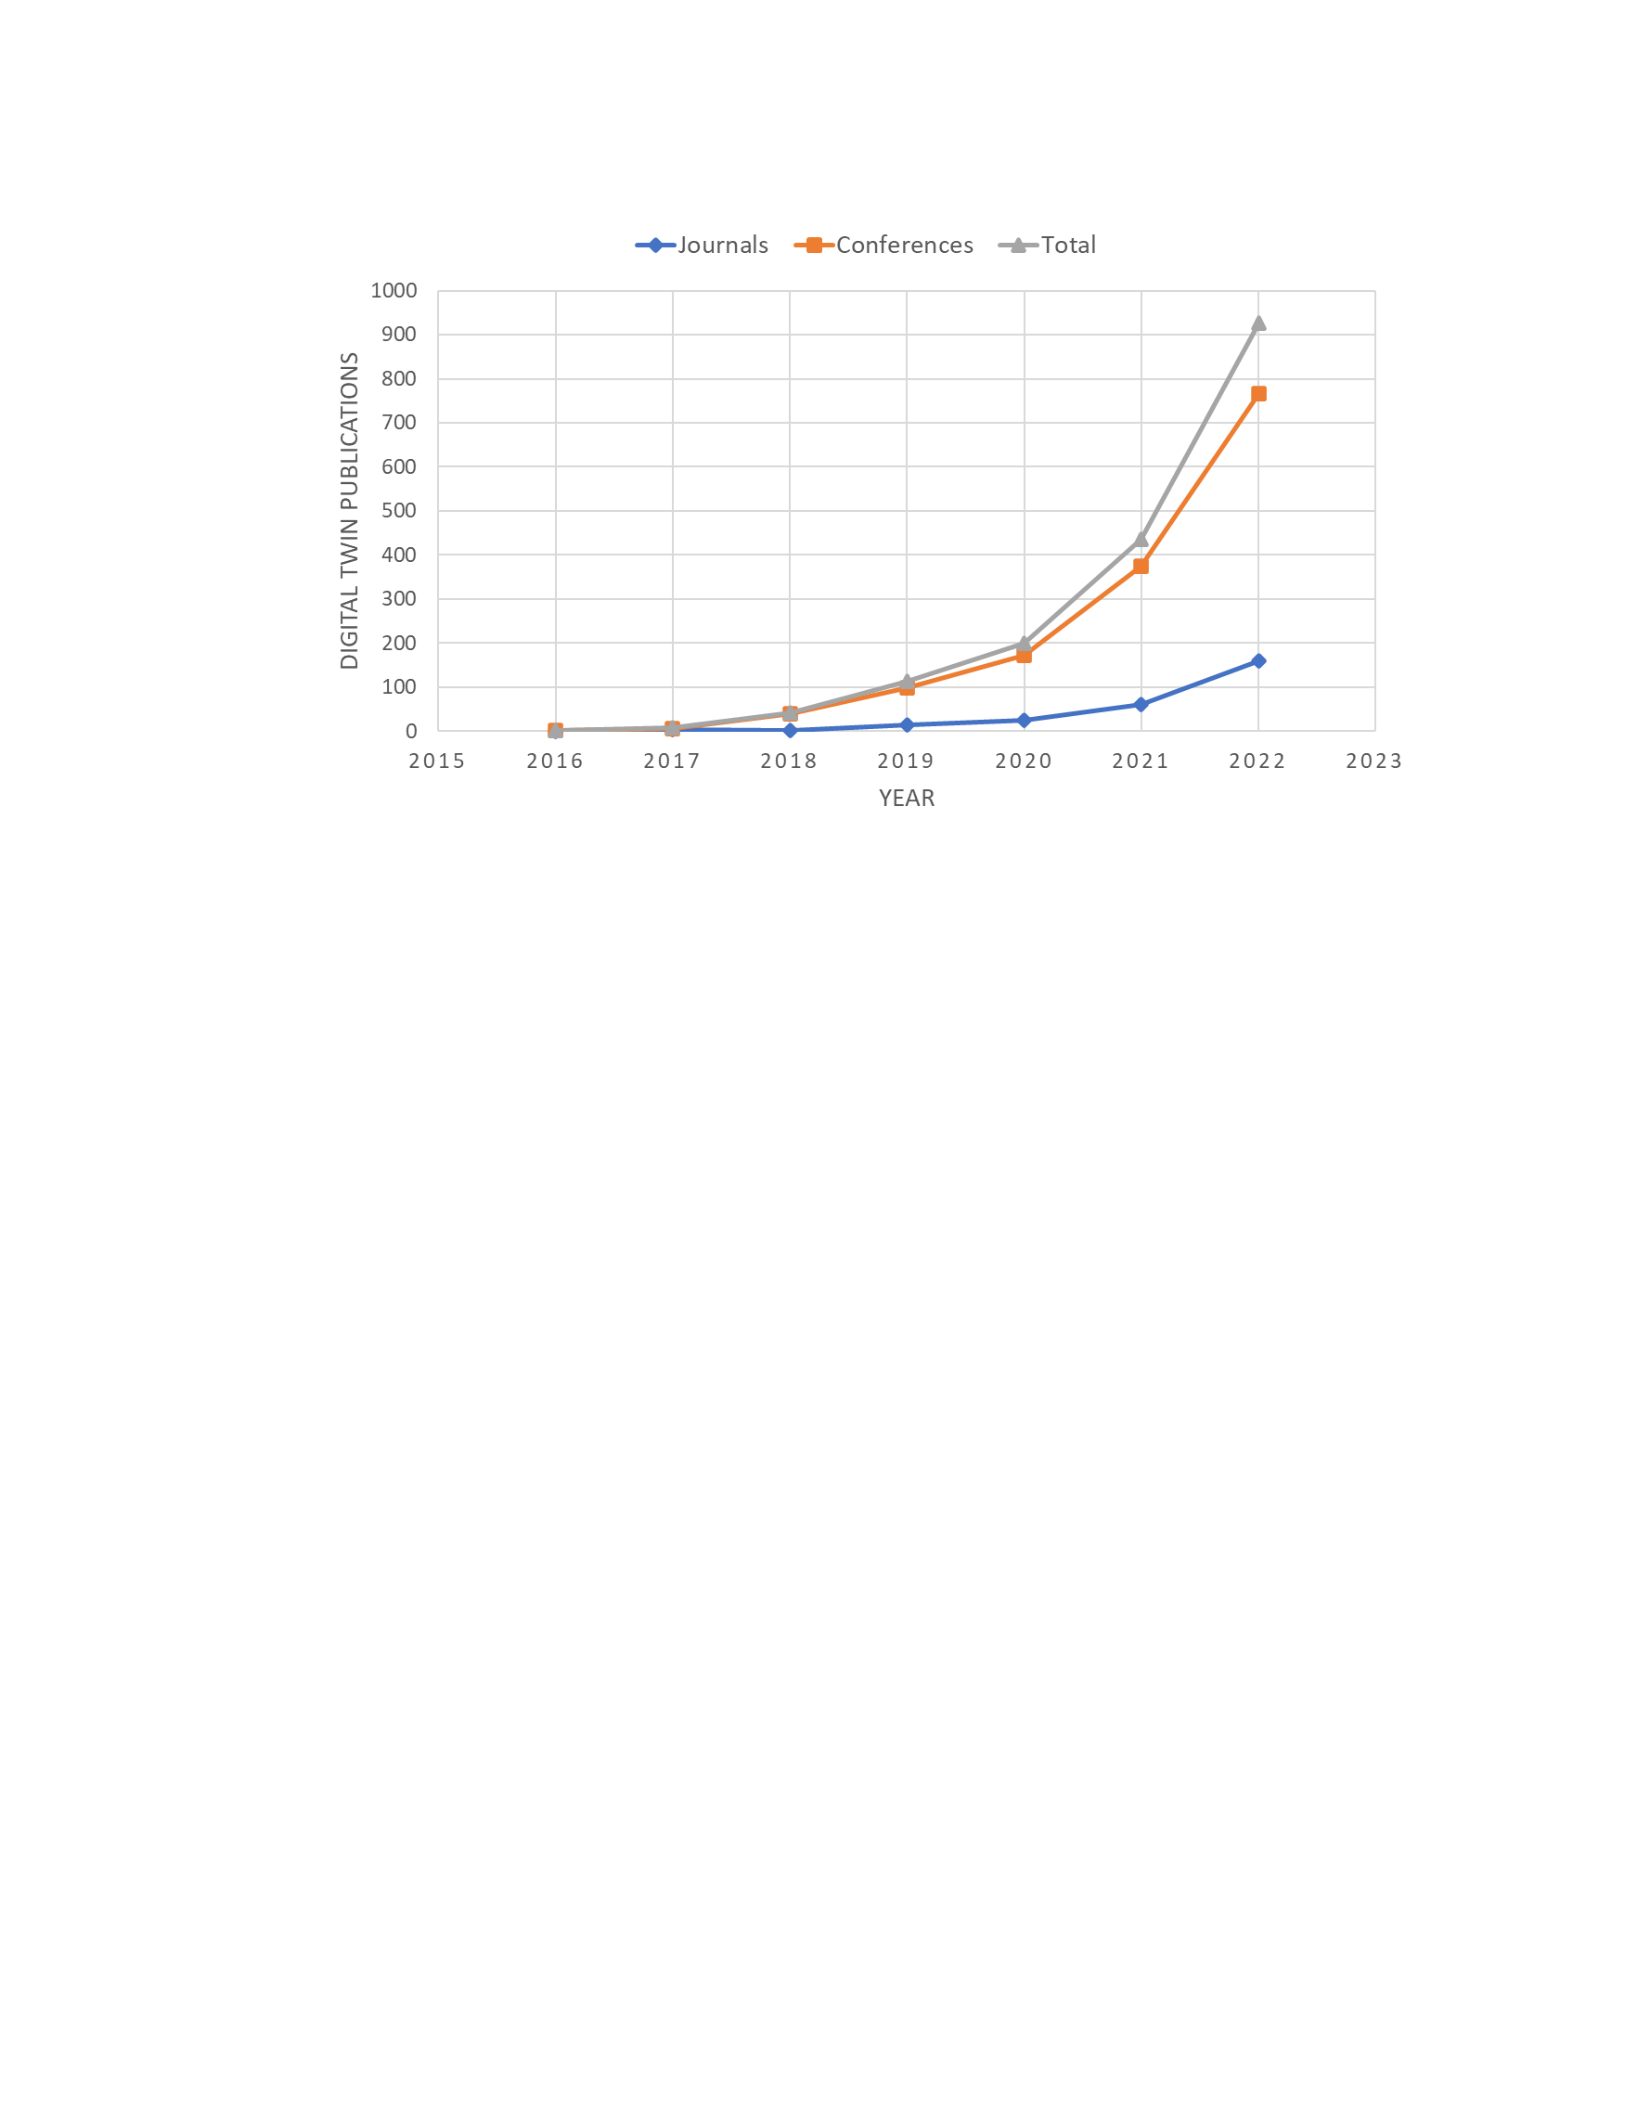
Figure 1. Number of Papers Published on IEEE Xplore using ”Digital Twin” as a
keyword
Different terms have been created to differentiate types of digital models and
the stage of development of the digital twin. These terms help to differentiate the
different levels of sophistication of the digital twin technology as well as separate
digital twins from modeling and simulation environments. Figure 2 shows the three
types of interaction between the physical system and the digital simulation [1]. The
digital model being a modeling and simulation environment. The Digital Shadow
being a one way coupling between the two entities. Lastly, the Digital Twin, having
a two-way coupling between the physical object and the digital object.
4
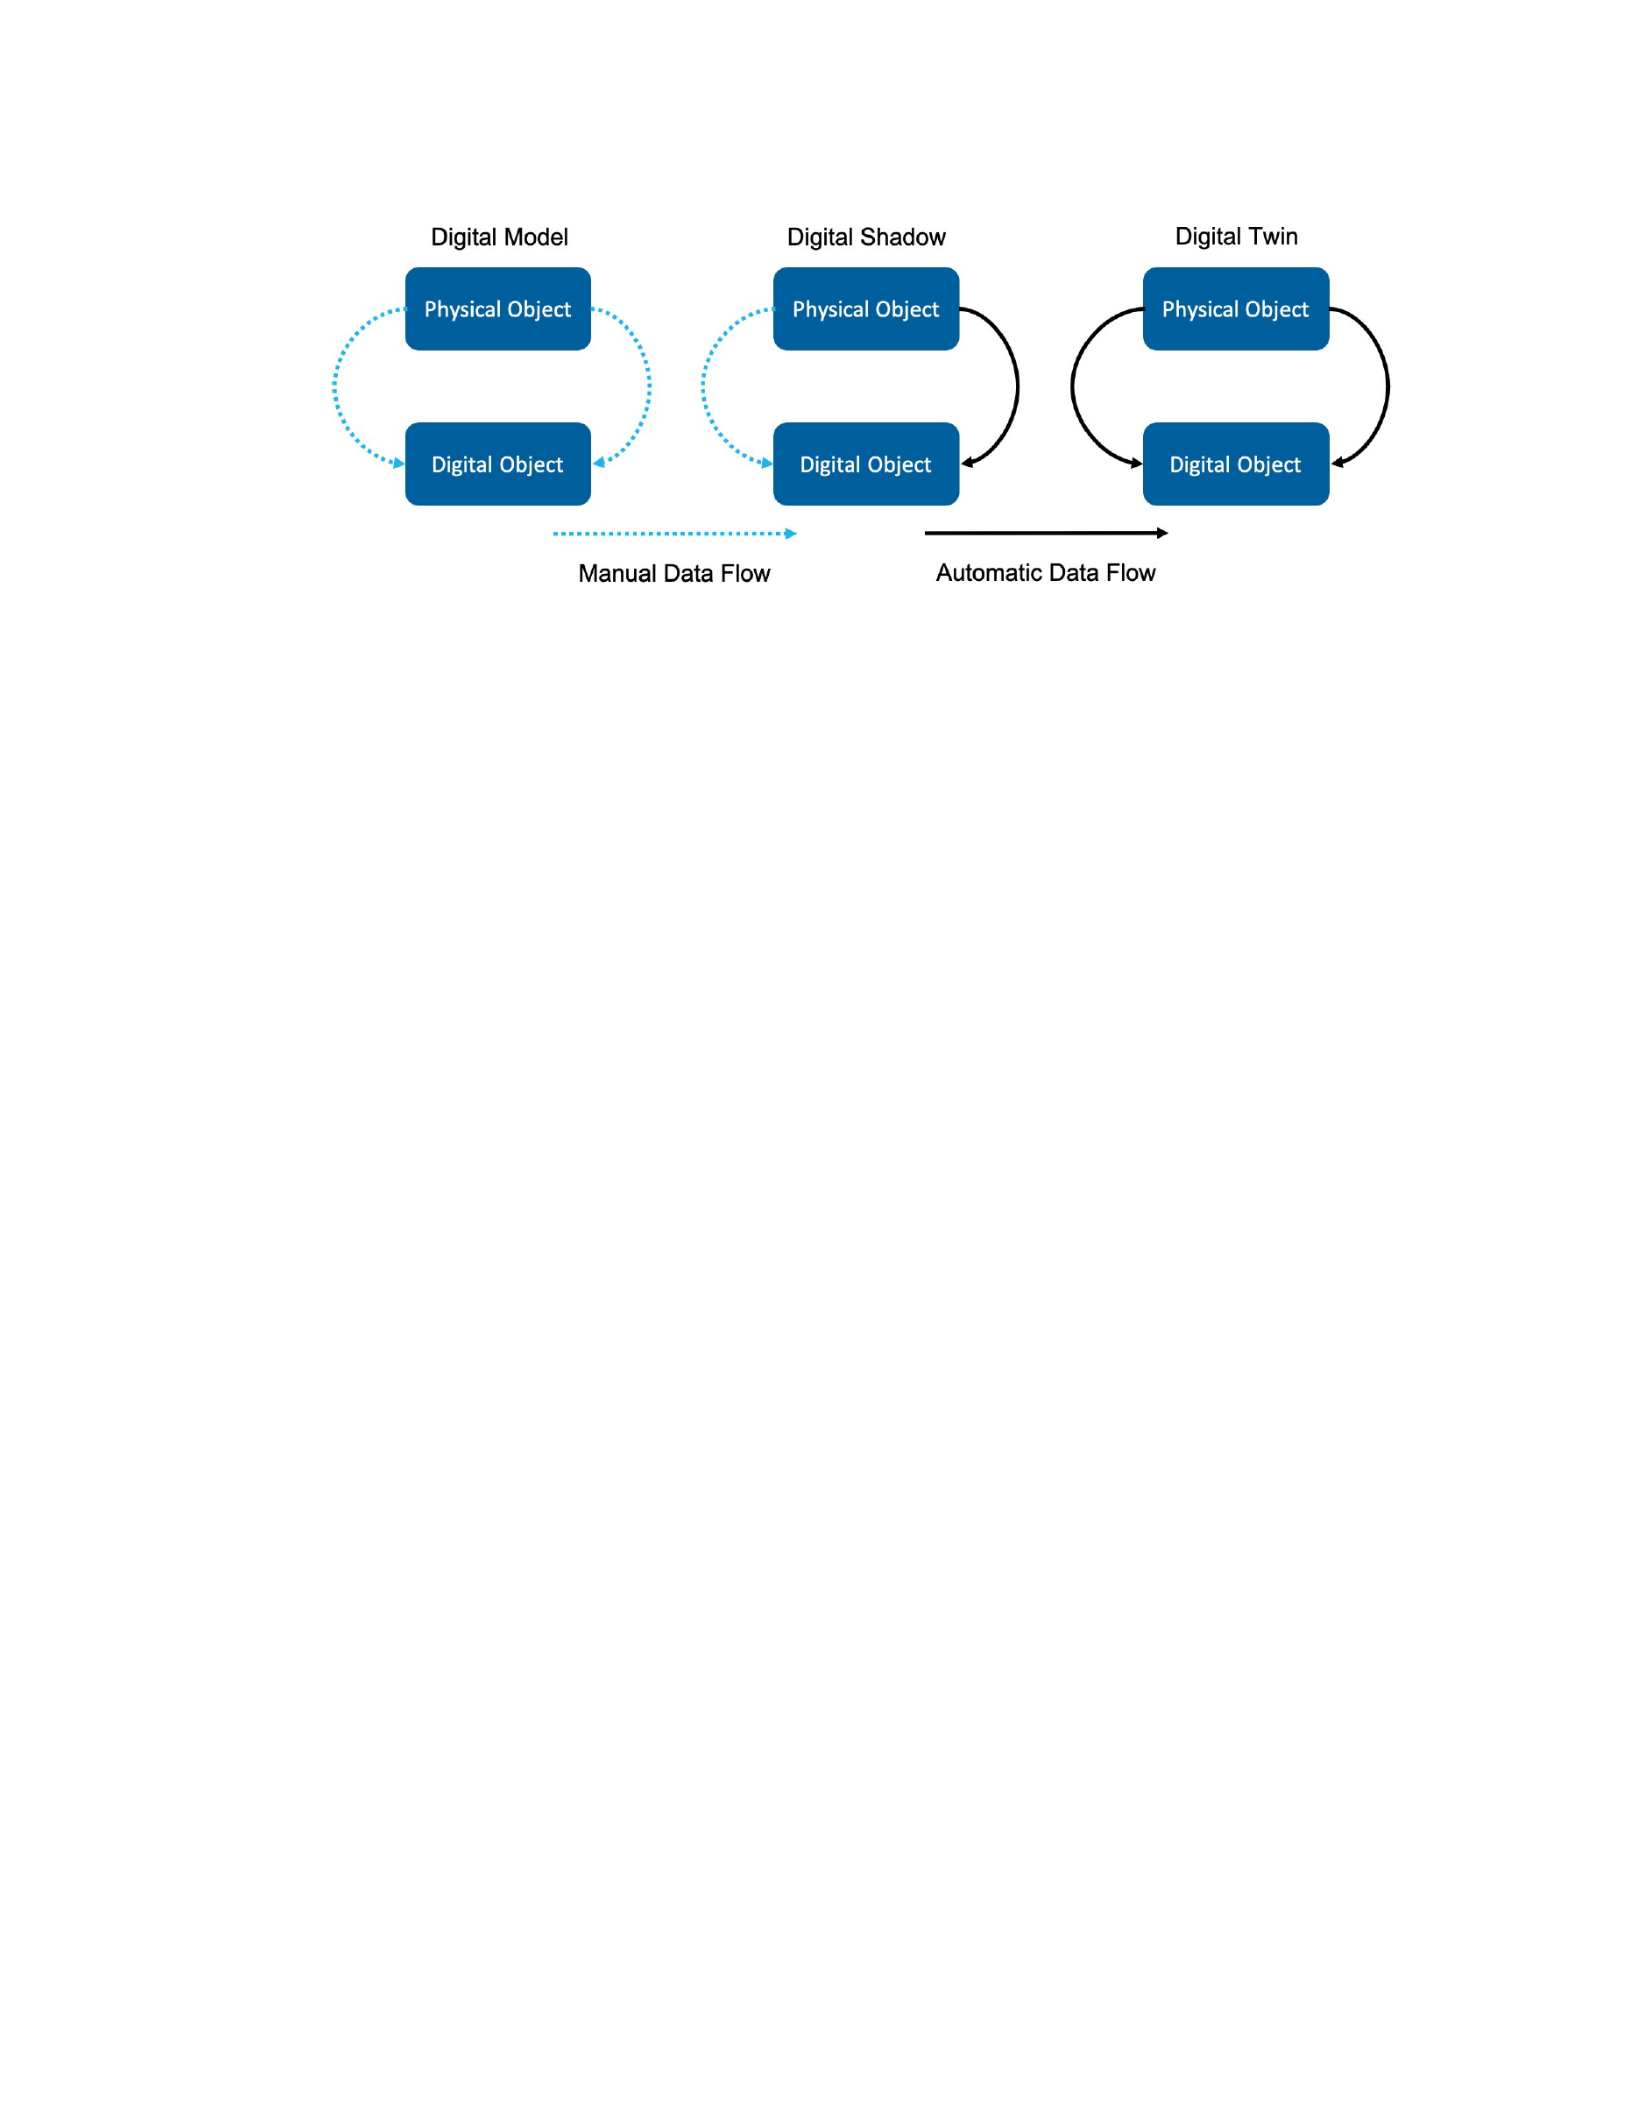
Figure 2. Interaction between the Digital Model and the Physical System [1]
Digital twin has become a hot keyword in recent years and a common mis-
conception is to describe digital modeling and simulation environments as digital
twins [26]. This often leads to confusion as to what exactly is a digital twin and ne-
cessitates a clear classification differentiating the sophistication of the digital twin
in question. To help alleviate this confusion, numerous papers have been published
attempting to explain the unique features contained in the digital twin environ-
ment that are not present in typical digital models or physics-based simulations
[26] [1]. However, these descriptions often leave out the machine learning (ML)
and computational intelligence (CI) algorithms that can be built into a fully de-
veloped digital twin. Building on the levels of digital twin sophistication proposed
by Madni et al. [27], the ANGEL digital twin framework proposes to categorize
the maturity of a digital twin into five levels of sophistication: Pre-Digital Twin,
Digital Twin, Adaptive Digital Twin, Intelligent Digital Twin and Autonomous
Digital Twin. The levels of Digital Twin sophistication is presented in Figure 3.
The Pre-Digital Twin encompasses all the design engineering tools that models
the physical system without communication to the physical system. These tools
are often used in the early stages of the design cycle before the construction of the
physical system and are also commonly referred to as virtual prototypes. The next
5
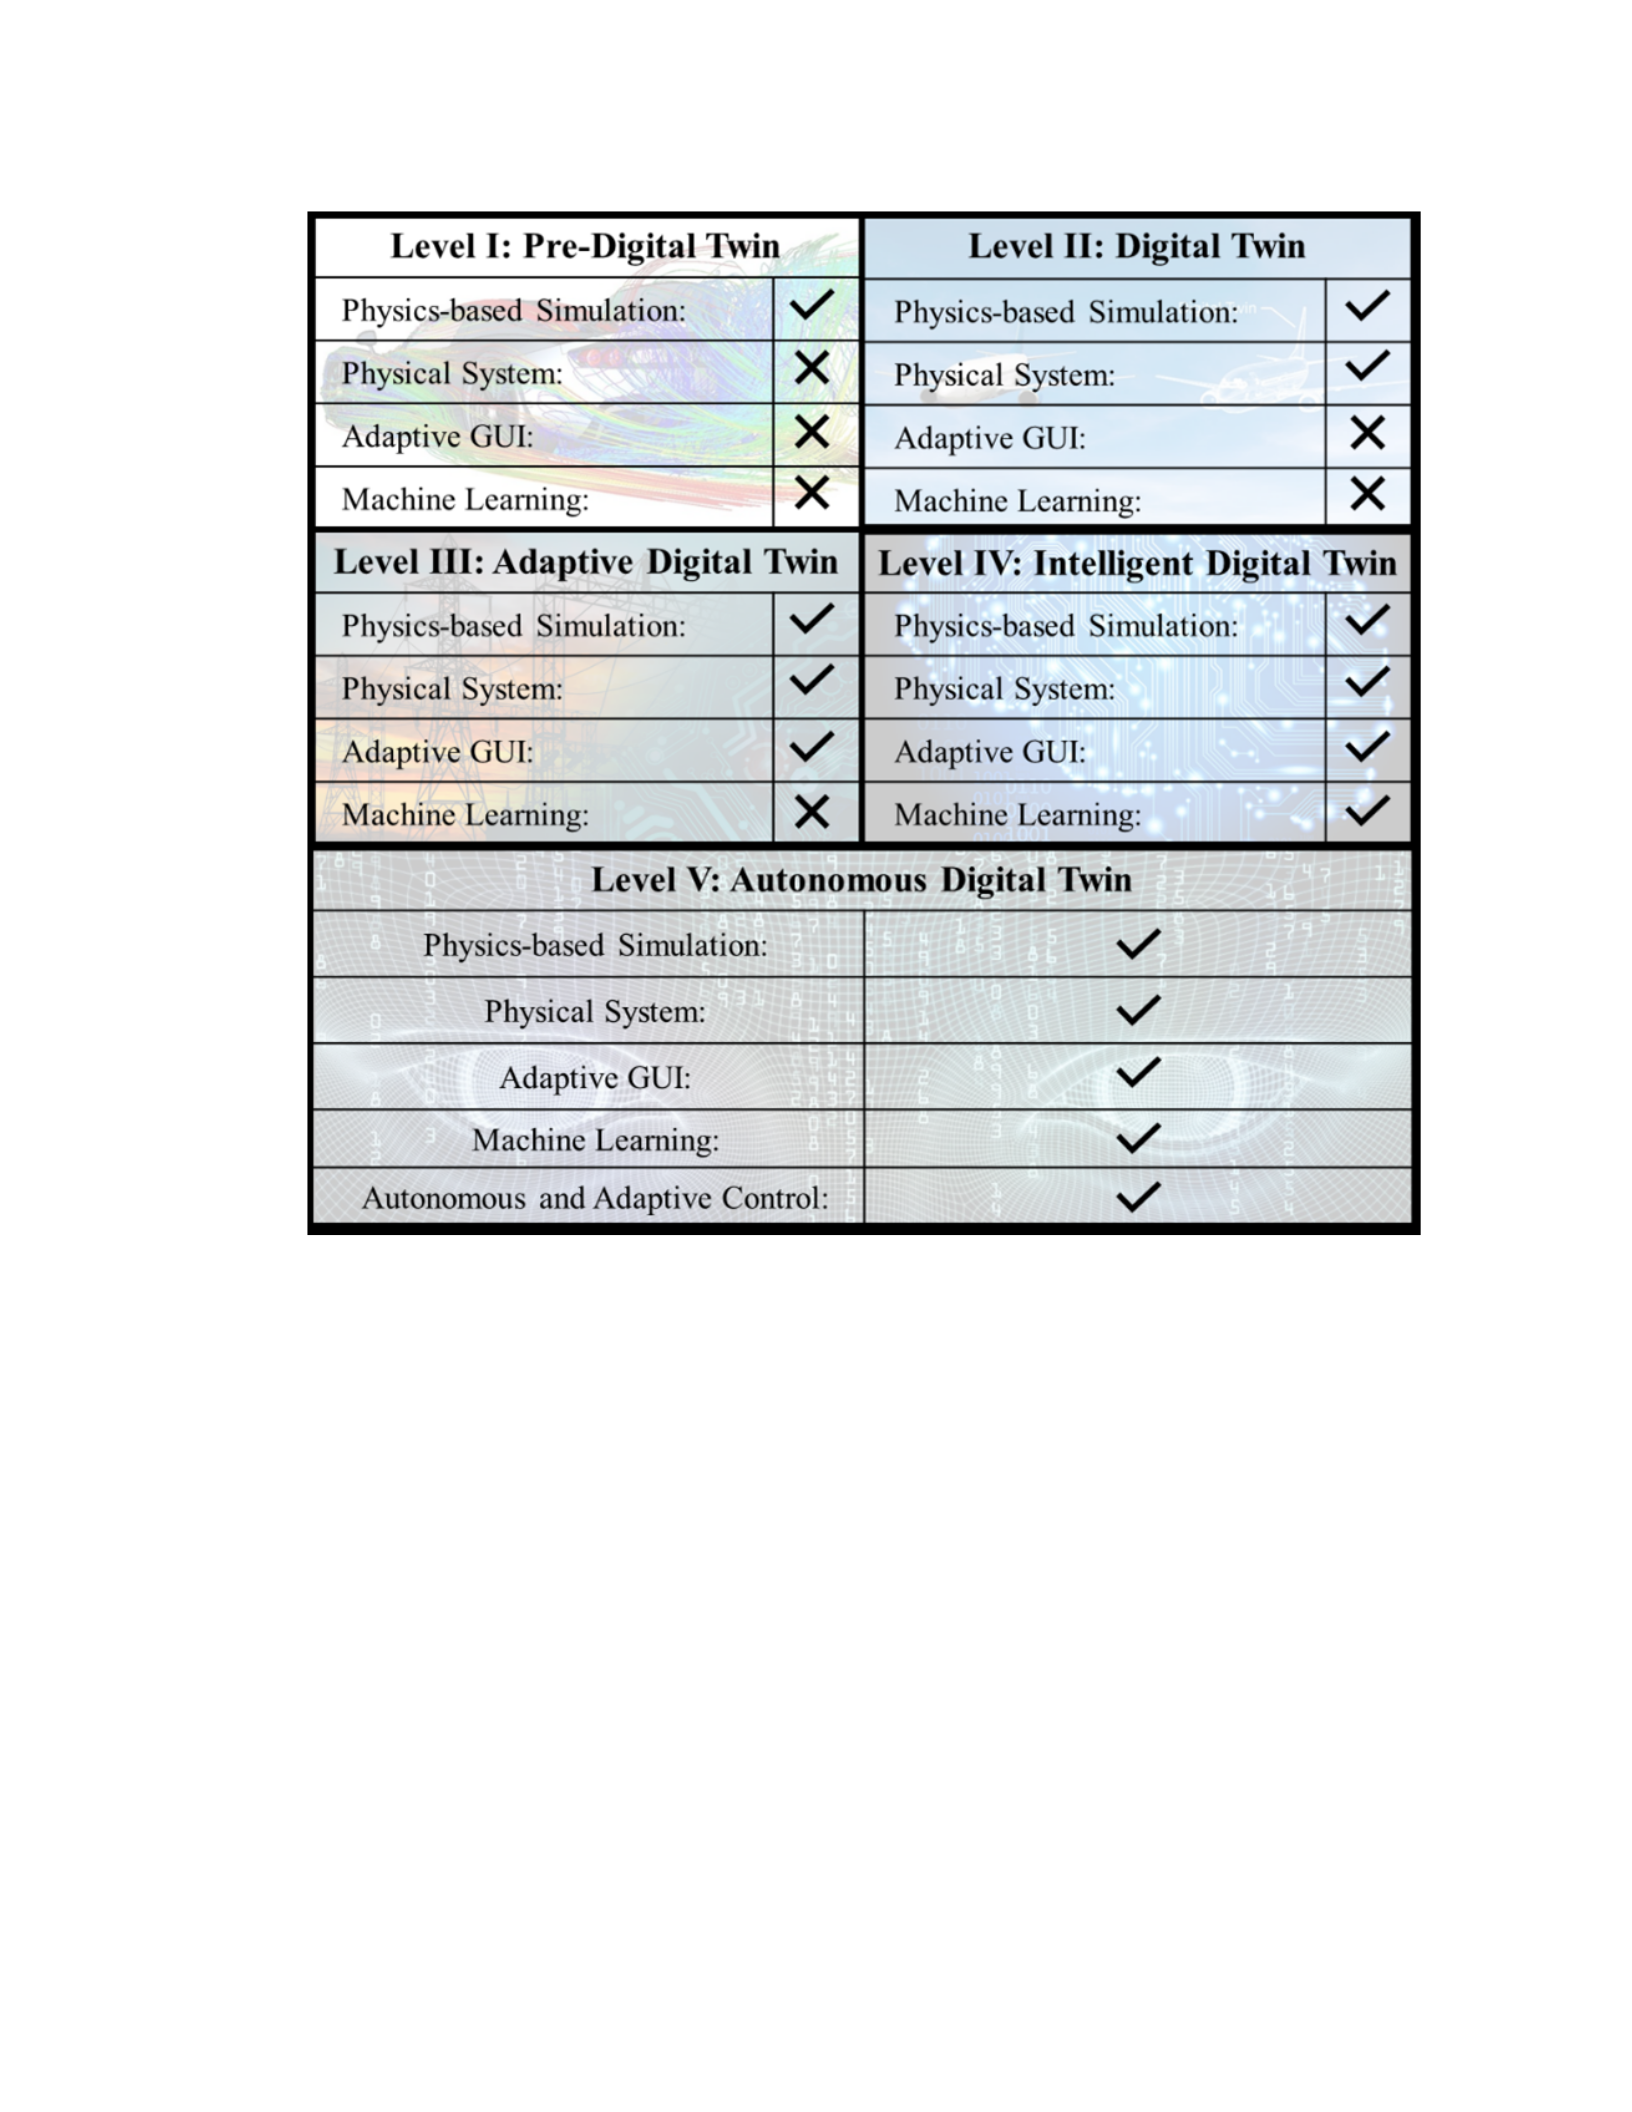
Figure 3. The levels of Digital Twin sophistication. [2]
level of maturity is the Digital Twin. At this level, the digital twin is capable of
communicating with the physical system in real-time. The digital twin collects data
from the physical system and incorporates the data into the simulation. The third
level of maturity is the Adaptive Digital Twin that is able to learn the preference
and priorities of the human operators. This level is focused on creating a human
interface that facilitates fast and accurate decision making by the system operator.
The fourth level of sophistication is the Intelligent Digital Twin which incorporates
machine learning capabilities to discern patterns and make control decisions [27].
6

The highest level of sophistication is the Autonomous Digital Twin which builds on
the previous levels of Digital Twins to allow the system to act autonomously with
limited, or possibly without, human operator interactions. Using the Digital Twin
simulation models and the machine learning algorithms outlined in the previous
stages, the Autonomous Digital Twin is able to direct the physical system to
optimal operating conditions using the state information from the physical system.
1.1.2 Recent Applications of Digital Twin Technology
Applications in Industrial and Manufacturing Systems
After its inception in the PLM center by Dr. Michael Grieves [25], the digital
twin took root and was initially developed in the manufacturing [28] and aviation
[11] industries. Since then, the digital twin has spread to a number of different
fields from full systems in the automotive [29] and medical fields [30] to tracking
wear in individual components in complex systems like wind turbines [31]. More
recently, the digital twin concept has been adopted by industries that are focusing
on the product lifecycle management (PLM) of consumer products such as the
automotive industry [29]. Other major companies have also started their own
research with General Electric [29] and Siemens [32] also placing themselves at the
forefront of developing Digital Twin technologies. Their reported applications are
for anything from Distributed Energy Resources (DERs), such as wind farms [33],
to cloud-based digital twin networks of multiple interconnected systems [34].
As a very active research field, the research and development of digital twins
has continued to increase in recent years. A selection of recent and interesting
digital twin applications are outlined in more detail below:
The field of digital twins has continued to be developed by researchers and
industry members that are attempting to improve their manufacturing processes.
In [35], the authors propose using a digital twin to improve the job-scheduling of
7

their production process. The Digital Twin implementation splits the problem into
two domains called the “virtual space” and the “physical space”. Using the virtual
space and multi-objective optimization methods, Fang et al is able to demonstrate
an improvement to the scheduling for the workshop. In [36], Gehrmann et al. take
Digital Twin technology a step further with the application of a digital twin based
industrial automation and control architecture. The paper develops a framework
for the security of a network connected physical system and demonstrates the per-
formance of the system on a software updated to a programmable logic controller.
In [37], Xu et al create a fault detection algorithm for manufacturing systems us-
ing a transfer learning technique. The authors proposed technique leverages the
simulation aspect of the digital twin to augment the available operating data to
provide additional information for the transfer learning algorithm. The proposed
framework allows for the digital twin to receive real-time data from the physi-
cal system and forecast the evolution of performance through the manufacturing
stages. In [38], Zhou et al proposes using digital twins to dynamically synchronize
objects during the manufacturing process. The objects can vary in size and this
paper specifically focuses on small object detection. The authors developed a hy-
brid neural network to identify the position and real-time status of the equipment,
product and the operator using surveillance video footage. In [39], Mortlock et al
proposes a graph learning framework for cognitive digital twins. The framework
is query-based that can potentially answer any type of query about the manufac-
turing system or resulting products. The authors demonstrate the ability of the
framework using three dimensional computer aided design models and used the
graph algorithm to produce classification labels for the products.
In recent years, mobile networking and edge computing has also begun using
digital twin techniques to improve system performance. In [40], Sun et al intro-
8

duce dynamic digital twins for wireless networks for supplemental capacity for
standard communication methods. The authors use digital twins to capture the
dynamic characteristics of the network in conjunction of a federated learning net-
work. Looking towards the future of mobile networks, there are a few researchers
that have proposed using digital twins as part of the 6th generation (6G) network.
In [41], Shen et al propose the use of digital twins to improve the end user vir-
tualization, as well as, holistic network virtualization. The digital twins would be
used to improve the quality of service to the end users by using network emula-
tions to improve network planning using synchronized real time data. Similarly,
in [42], Khan et al presents a 6G approach that uses digital twins to meet the re-
quirements of next generation networking. The authors propose both cloud-based
and edge-based digital twins. While a cloud-based digital twin has advantages
in computing power and storage availability, it could also result in high latency.
Conversely, an edge-based digital twin will offer low latency but might suffer from
high management complexity and lower resource availability.
The automotive industry has been at the forefront of digital twin develop-
ment. That trend has continued with many new development related to vehicle
management and autonomous driving. In [43], Hu et al develops a digital twin of
the human driver for the testing and development of human-vehicle interaction.
This approach allows the automated vehicle to adapt to the driver rather than
vice-versa. While the authors pose that the driver digital twin might one day
replace human drivers, the focus of the system is to comprehensively reflect the
behavior of the real driver in a synchronous fashion. Potentially, improving the
human-vehicle interaction for safer and more enjoyable operating conditions. In
[44], Hui et al propose a digital twin enabled collaborative autonomous driving
network for sharing the computational overhead of driving decisions. The pro-
9

posed architecture uses digital twins to replace the autonomous vehicles to make
the decisions on virtual networks in advance to limit the required data exchange
in frequently encountered conditions. In [45], Zhang et al. propose a novel ve-
hicular edge computing network based on digital twin technology and multi-agent
learning. The edge framework improves the learning efficiency of the agents and
improves the performance between the physical system and virtual counterpart.
The digital twin is used to reveal potential cooperation between the vehicles in
the network through the formation of learning groups. In [46], Hu et al presents a
digital twin application for traffic management using 5G-enabled vehicles. Using
a digital twin model of the traffic map, the algorithm is able to predict missing
traffic flow and velocity to augment missing or sparse traffic data. The authors
were able to demonstrate the effectiveness of this approach using existing traffic
data.
Applications in Power Systems
While digital twin technology was adopted early on in numerous other industries,
the energy sector was slow to develop digital twin applications for the power grid.
Some of the large players in the power system market, such as Siemens, have ex-
pressed interest in developing Digital Twin technologies for the power grid appli-
cation [32]. Using the legacy Supervisory Control and Data Acquisition (SCADA)
system that is already in place, the digital twin can access real-time data about
the physical system and provide guidance in real-time. While early adaptations
of the digital twin would likely include a human in the loop structure, the fully
realized digital twin could potentially analyze and control the power system with
virtually no human interaction.
The power grid continues to be modernized with devices that introduce small
10

time constants, such as High Voltage Direct Current (HVDC) and flexible alter-
nating current transmission system (FACTS), as well as, the phasor measurement
units (PMUs) that are able to report measurements with a high temporal resolu-
tion. This has created a strain on the legacy SCADA system that cannot deal with
the speed requirements of these high frequency elements [32]. Early in this research
effort, the Digital Twin for power systems was a relatively unknown space with
only a handful of other papers when our paper entitled “ANGEL: An Intelligent
Digital Twin Framework for Microgrid Security” was published in 2019 [2]. With
over 2,330 views and nearly 40 citations since publication, the ANGEL Digital
twin framework is having an impact on the community and many researchers are
using the paper for guidance on a power system Digital Twin framework. There
are a few interesting papers that have referenced our digital twin framework and
explored other aspects of power system digital twin technology.
In a recent survey paper of Digital Twin for Electric Power Systems [47] pub-
lished at the 2021 Power and Energy Society General Meetings (PESGM), the au-
thors reference the Digital Twin Evolution that was presented in the ANGEL Dig-
ital Twin Framework. The paper goes over many topics that was presented in the
ANGEL work including fault diagnosis, energy management systems and renew-
able energy resources. In [48], the authors use the Digital Twin Evolution to guide
the development of a Power-hardware-in-the-Loop (PHIL) assessment tool for dis-
tributed renewable energy sources (DRES). The paper presents a pre-integration
assessment method for DRES installations using PHIL and cyber-physical energy
systems.
In [49], Mark Karanfil et al. present the design and implementation of a
cyber-security monitoring tool based on the Network and System Management
(NSM) using a real-time microgrid being run in Hypersim. Using a hybrid machine
11

learning and rules based approach, the authors evaluated several detection schemes
included Long-short Term Memory (LSTM) and Gated Recurrent Units (GRU) for
detection of a cyber physical attack. The authors simulate three attack scenarios
on an islanded microgrid and evaluate the microgrid response and performance of
the detection algorithms.
In [50], Olivares-Rojas et al. evaluate the use of Digital Twins to provide
Cybersecurity to Smart Meter Systems and combat malicous attacks. The digital
twin system is able to successfully detect 98.8% of the data manipulation attacks
using their Digital Twin approach.
Wunderlich et al. works focus on the component level digital twins in power
electrics. In his 2021 work [51], he develops a new approach for real-time modeling
of power electronic converters using dynamic neural networks. The dynamic neural
network serves as the digital twin model and can be run on any platform, even in
edge computing environments. The paper proposes a Nonlinear AutoRegressive
eXogenous (NARX) network which contains memory blocks within the structure
of the neural network. The results of this approach is shown to be very good at
modeling a Boost converter. Dr Wunderlich also expands this work into applica-
tions of power and energy systems using analytical, data-driven and hybrid digital
twin models [52].
As digital twins will be connected to critical infrastructure, the issue of cyber
security of digital twins is a very important topic. The issue of security of the
digital twin is not only of the system itself but also expands to the integrity of
the data used by the digital twin. In [53], Alcaraz et al present the state of
research into digital twins as a cyber vulnerability. In the paper, the authors detail
the effects attackers can have on the cyber physical system including increasing
computational overhead, exfiltrating information from the digital twin model and
12

violate the fidelity of the digital twin models.
1.2 Research Methodology
In this research, a novel Digital Twin framework for Cyber Physical Systems
(CPS) is proposed. Using the Smart Grid as the representative CPS, this dis-
sertation includes the development of a Digital Twin framework along with novel
technology modules that expand the Digital Twin landscape and provide resiliency
to the Physical System as well as the Digital Twin.
1.2.1 Objectives
This dissertation details the approach taken into the research of the following
items:
1. The primary focus of this dissertation is the research of the Digital Twin
framework.
2. This dissertation also presents other technologies that improve the security
of the digital twin, as well as, digital twin modules that leverage the power
of the digital twin framework.
3. While models and algorithms can be developed as stand alone simulations,
the Digital Twin is required to be paired with a physical system. While
it is not feasible to build a full scale power system, a high-fidelity real-time
Hardware in the Loop (HIL) Smart Grid Testbed is presented for the research
into Cyber Physical Digital Twins.
While the definition of what constitutes a digital twin has evolved over time,
the basic idea and the required components have remained the same. In his recent
paper, Dr. Saddik expanded the digital twin concept to be “a digital replica of a
living or non-living physical entity. By bridging the physical and the virtual world,
13

data is transmitted seamlessly allowing the virtual entity to exist simultaneously
with the physical entity” [54]. While there is continuing discussion on what sepa-
rates a digital twin from it’s modeling and simulation roots, in this dissertation, a
digital twin is defined to have three fundamental components:
1. The first, and perhaps the most basic, item is a physics-based simulation of
the system.
2. Next, the Digital Twin needs a real-world counterpart that is intuitively
called the Physical Twin. The Physical Twin is the actual physical system
that is being monitored and analyzed. The Physical Twin is required to be
equipped with a large array of sensors to monitor all aspects of the system.
3. The third component required for a true digital twin is the passage of data
from the physical twin to the digital counterpart.
The proposed Digital Twin framework aims to do all of this with added com-
plexity of using machine learning techniques to monitor the system and detect
anomalies in the power system.
Almost any physical system can have a digital twin. While not all of the
digital twins have direct overlap with the proposed digital twin, the underlying
challenges of a digital twin infrastructure are often a commonality. Most notably,
all digital twins need to answer a few fundamental questions:
1. How to implement sensors on the physical system?
2. How to transmit sensor data from the remote sensor location?
3. Does the data transfer need to be secure? If so, how is the data secured?
4. How to update the simulation models with the data received from the phys-
ical system?
14

5. How does the Digital Twin improve the operation of the underlying physical
system, and perhaps most importantly, without adding vulnerabilities?
Using the legacy communication techniques already found in the SCADA and
wide area monitoring (WAM) systems, the digital twin framework is able to at-
tach itself to the control center environment and provide useful feedback to the
control system operator. The physical microgrid and grid communication network
feed data into the physics-based simulation, machine learning and data analysis,
as well as the user interface and visualization suite of the digital twin. While
analyzing additional data from the grid could be advantageous, using the legacy
communication protocols allow the digital twin to be deployed and tested on a
microgrid without significant modifications.
The ability to accurately model and simulate the physical system is critical to
being able to properly predict and assess the behavior of the Smart Grid. However,
while doing this the simulations have to be fast enough to provide feedback to the
Smart Grid in near real-time. The balance of fidelity and computational efficiency
is essential to successfully executing a digital twin.
1.3 Dissertation Organization
This dissertation describes the ANGEL Digital Twin Framework that is at
the core of this research effort as well as the associated modules that have been
developed to enable the digital twin to provide greater insight into the physical
system. The overall structure of the dissertation is show in Figure 3.
15
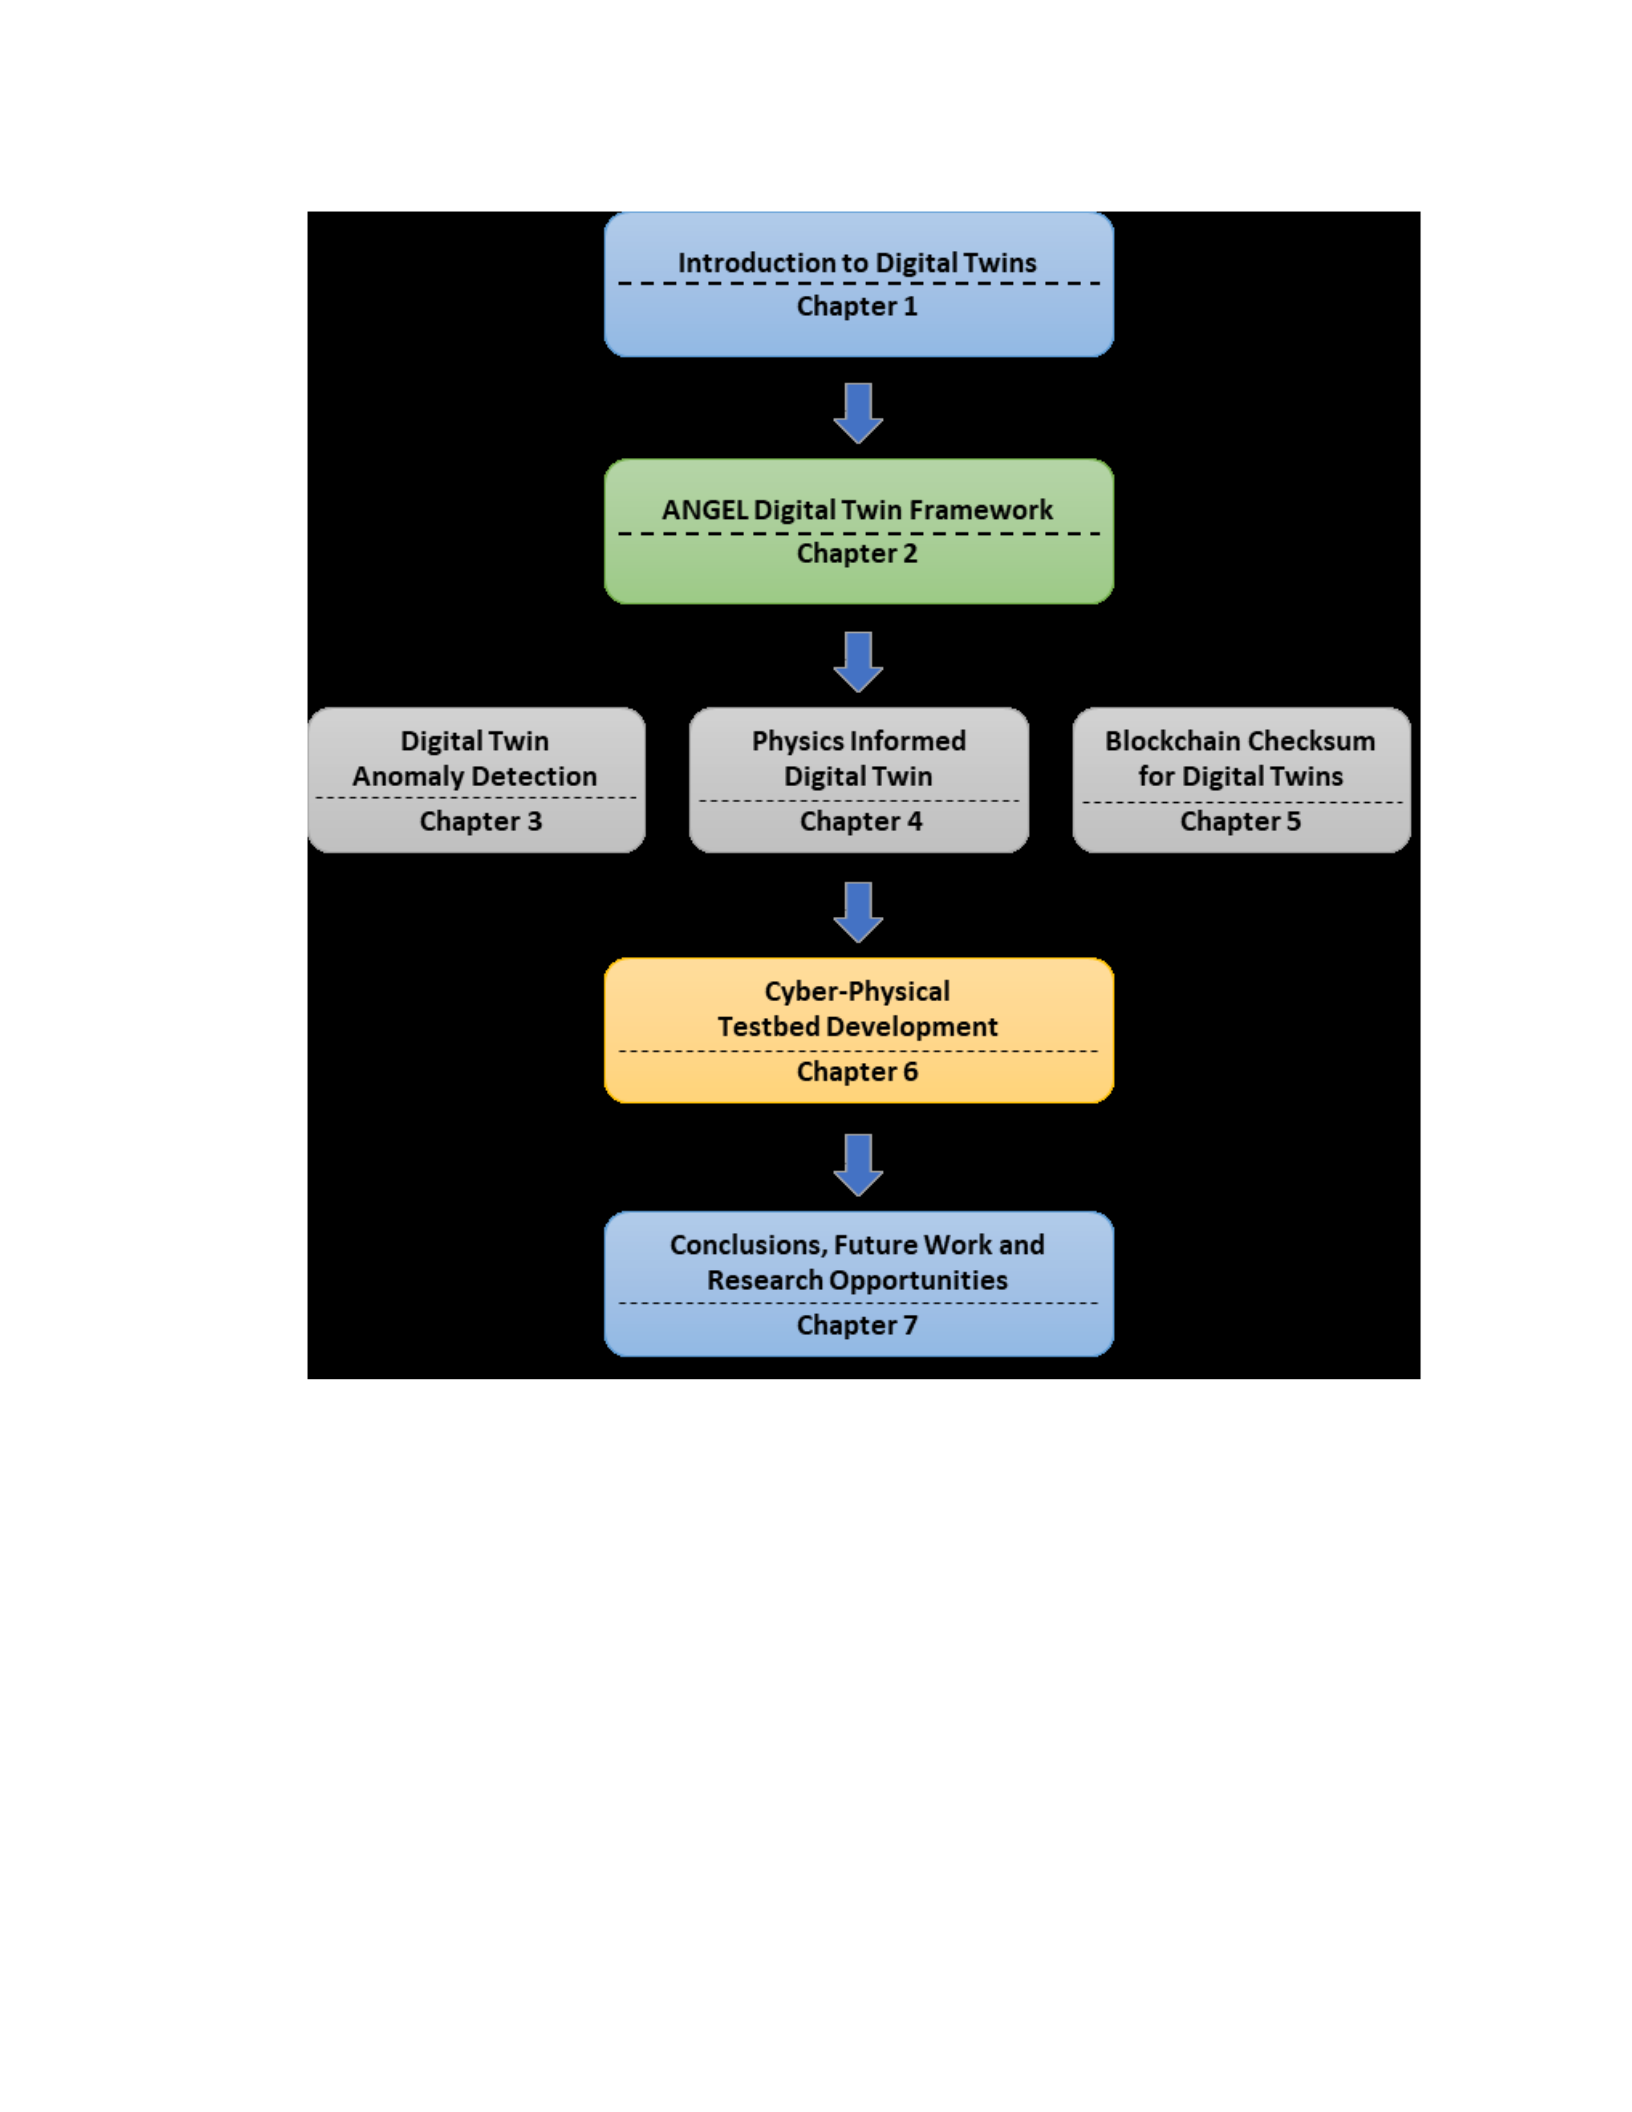
Figure 4. Structure of Dissertation
The ANGEL Digital Twin framework is presented in detail in Chapter 2. In
this chapter, the ANGEL system was developed to support anomaly detection in
cyber physical systems. This section presents the framework as first developed
in MATlab and the follow on functionality developed in Python. This section
also presents use cases of the ANGEL digital twin along with some computational
results.
16

Chapter 3 describes the digital twin anomaly detection modules that have
been developed as part of the ANGEL digital twin framework. The first algorithm
presented develops a Convolutional Neural Network (CNN) for anomaly detection
in a highly connected power system. The results are compared to other state of the
art machine learning algorithms. A secondary deep learning algorithm using a deep
Graph Convolutional Neural Network (GCN) with a temporal filter is presented
and compared to the original results of the CNN. The results from these works
are compared to the current state of the art fault detection algorithms in recent
literature.
A Digital Twin implementation is presented in Chapter 4 using a Graph Neu-
ral Network (GNN) to improve the physics based dynamic state estimation. The
algorithm was designed in response to traditional limitations and convergence is-
sues in state estimation and power flow solvers when presented with dynamically
changing system typologies. The GNN is able to encode the sensor output from
the physical system and provide it as an input into the physics based power system
simulation.
In Chapter 5, a blockchain checksum is presented for securing insecure com-
munications using digital twins. The implementation leverages the historical logs
stored by the Digital Twin and creates a novel Merkle tree architecture to provide
a dynamic checksum for the unsecured sensor readings. The algorithm is evalu-
ated using normal operating conditions along with data simulating the detection
of a false data injection attack. The proposed algorithm provides a cyber secure
verification method for digital twin communications using blockchain technology.
In Chapter 6, a detailed description of the cyber-physical Smart Grid Research
laboratory that was developed as part of this work is presented. Using state-of-
the-art Hardware-in-the-Loop simulation techniques, the lab is be able to simulate
17

sophisticated attack and defense strategies. With a four-seat control desk and large
video wall, the Smart Grid Research lab is designed to look and feel like a Power
Grid Control facility. The specialized HIL simulators are able to push simulation
techniques to real time for real time verification or rapid prototyping of control
algorithms. This implementation enables smart control systems and digital twins
to be deployed on a real cyber physical network to evaluate their effectiveness and
robustness in a realistic operating environment.
18

CHAPTER 2
ANGEL: An Intelligent Digital Twin Framework for Microgrid
Security
2.1 Chapter Overview
The Automatic Network Guardian for ELectrical systems (ANGEL) Digital
Twin for Cyber-Physical System Security is a novel approach for improving the
security of critical and non-critical infrastructure. Digital Twin technology, widely
used in the aviation, manufacturing and automotive industries, has the potential
to improve the security and resiliency of the microgrid. This chapter describes the
framework for adapting the Digital Twin to the application of microgrid research.
The Digital Twin is a real-time, physics-based simulation that runs alongside the
physical system providing for its constant monitoring and control. The ANGEL
system uses data from both the cyber and physical layers of the microgrid and
provide real-time data visualization. As a result, users are aided in assessing
the health of the physical plant and overall behavior over a range of operating
conditions. The ANGEL Digital Twin uses the real-time two-way coupling between
the simulation and physical system to update and evolve the simulation to provide
greater insight into the physical system. Ultimately, ANGEL provides the ability to
diagnose and heal the physical system, mitigating both component failures and the
effects of cyber attack. This chapter explains the methodology behind the design
of this digital twin and the advantages of such an approach. To demonstrate the
capabilities of the ANGEL framework as a Level III digital twin, a simulation
example is presented on the IEEE 39-bus benchmark.
The ANGEL framework, which is an adaptation of state-of-the-art Digital
Twin technology, bridges the gap between simulation and control leading to a safer
more secure power grid. The proposed ANGEL framework, explained in Section
19

2.2, represents a new approach to microgrid security using the data acquisition
techniques already applied in legacy SCADA system. A case study using the
ANGEL system is also presented in Section 2.2.1. Section 2.3 presents a discussion
of potential usage of the ANGEL digital twin for cyber defense. Finally, Sections
2.4 presents the expanded ANGEL framework in Python and Section 2.4.1 contain
a brief conclusion of the chapter and a summary of the development path of the
ANGEL framework.
2.2 ANGEL Digital Twin Framework
Power grid control centers have long relied on the legacy SCADA system to
protect and control the power grid. However, the new Smart Grid that will be a
fundamental building block for the future of Smart Cities could benefit from a more
sophisticated system for control and security. The Automatic Network Guardian
for Electrical (ANGEL) system has the ability to monitor the power system in
real time and provide insight into the inner workings of the grid dynamics. This
allows a digital twin to direct the physical “twin” when abnormal grid behaviors
are detected.
The modern power grid is a perfect application for the digital twin technology.
Using the legacy SCADA system that is already in place, the digital twin can
access real-time data about the physical system and provide guidance in real-time.
While early adaptations of the digital twin would likely include a human in the
loop structure, the fully realized digital twin could potentially analyze and control
the power system with virtually no human interaction.
Using the legacy communication techniques already found in the SCADA and
wide area monitoring (WAM) systems, the ANGEL digital twin is able to attach
itself to the control center environment and provide useful feedback. The phys-
ical microgrid and grid communication network feed data into the physics-based
20
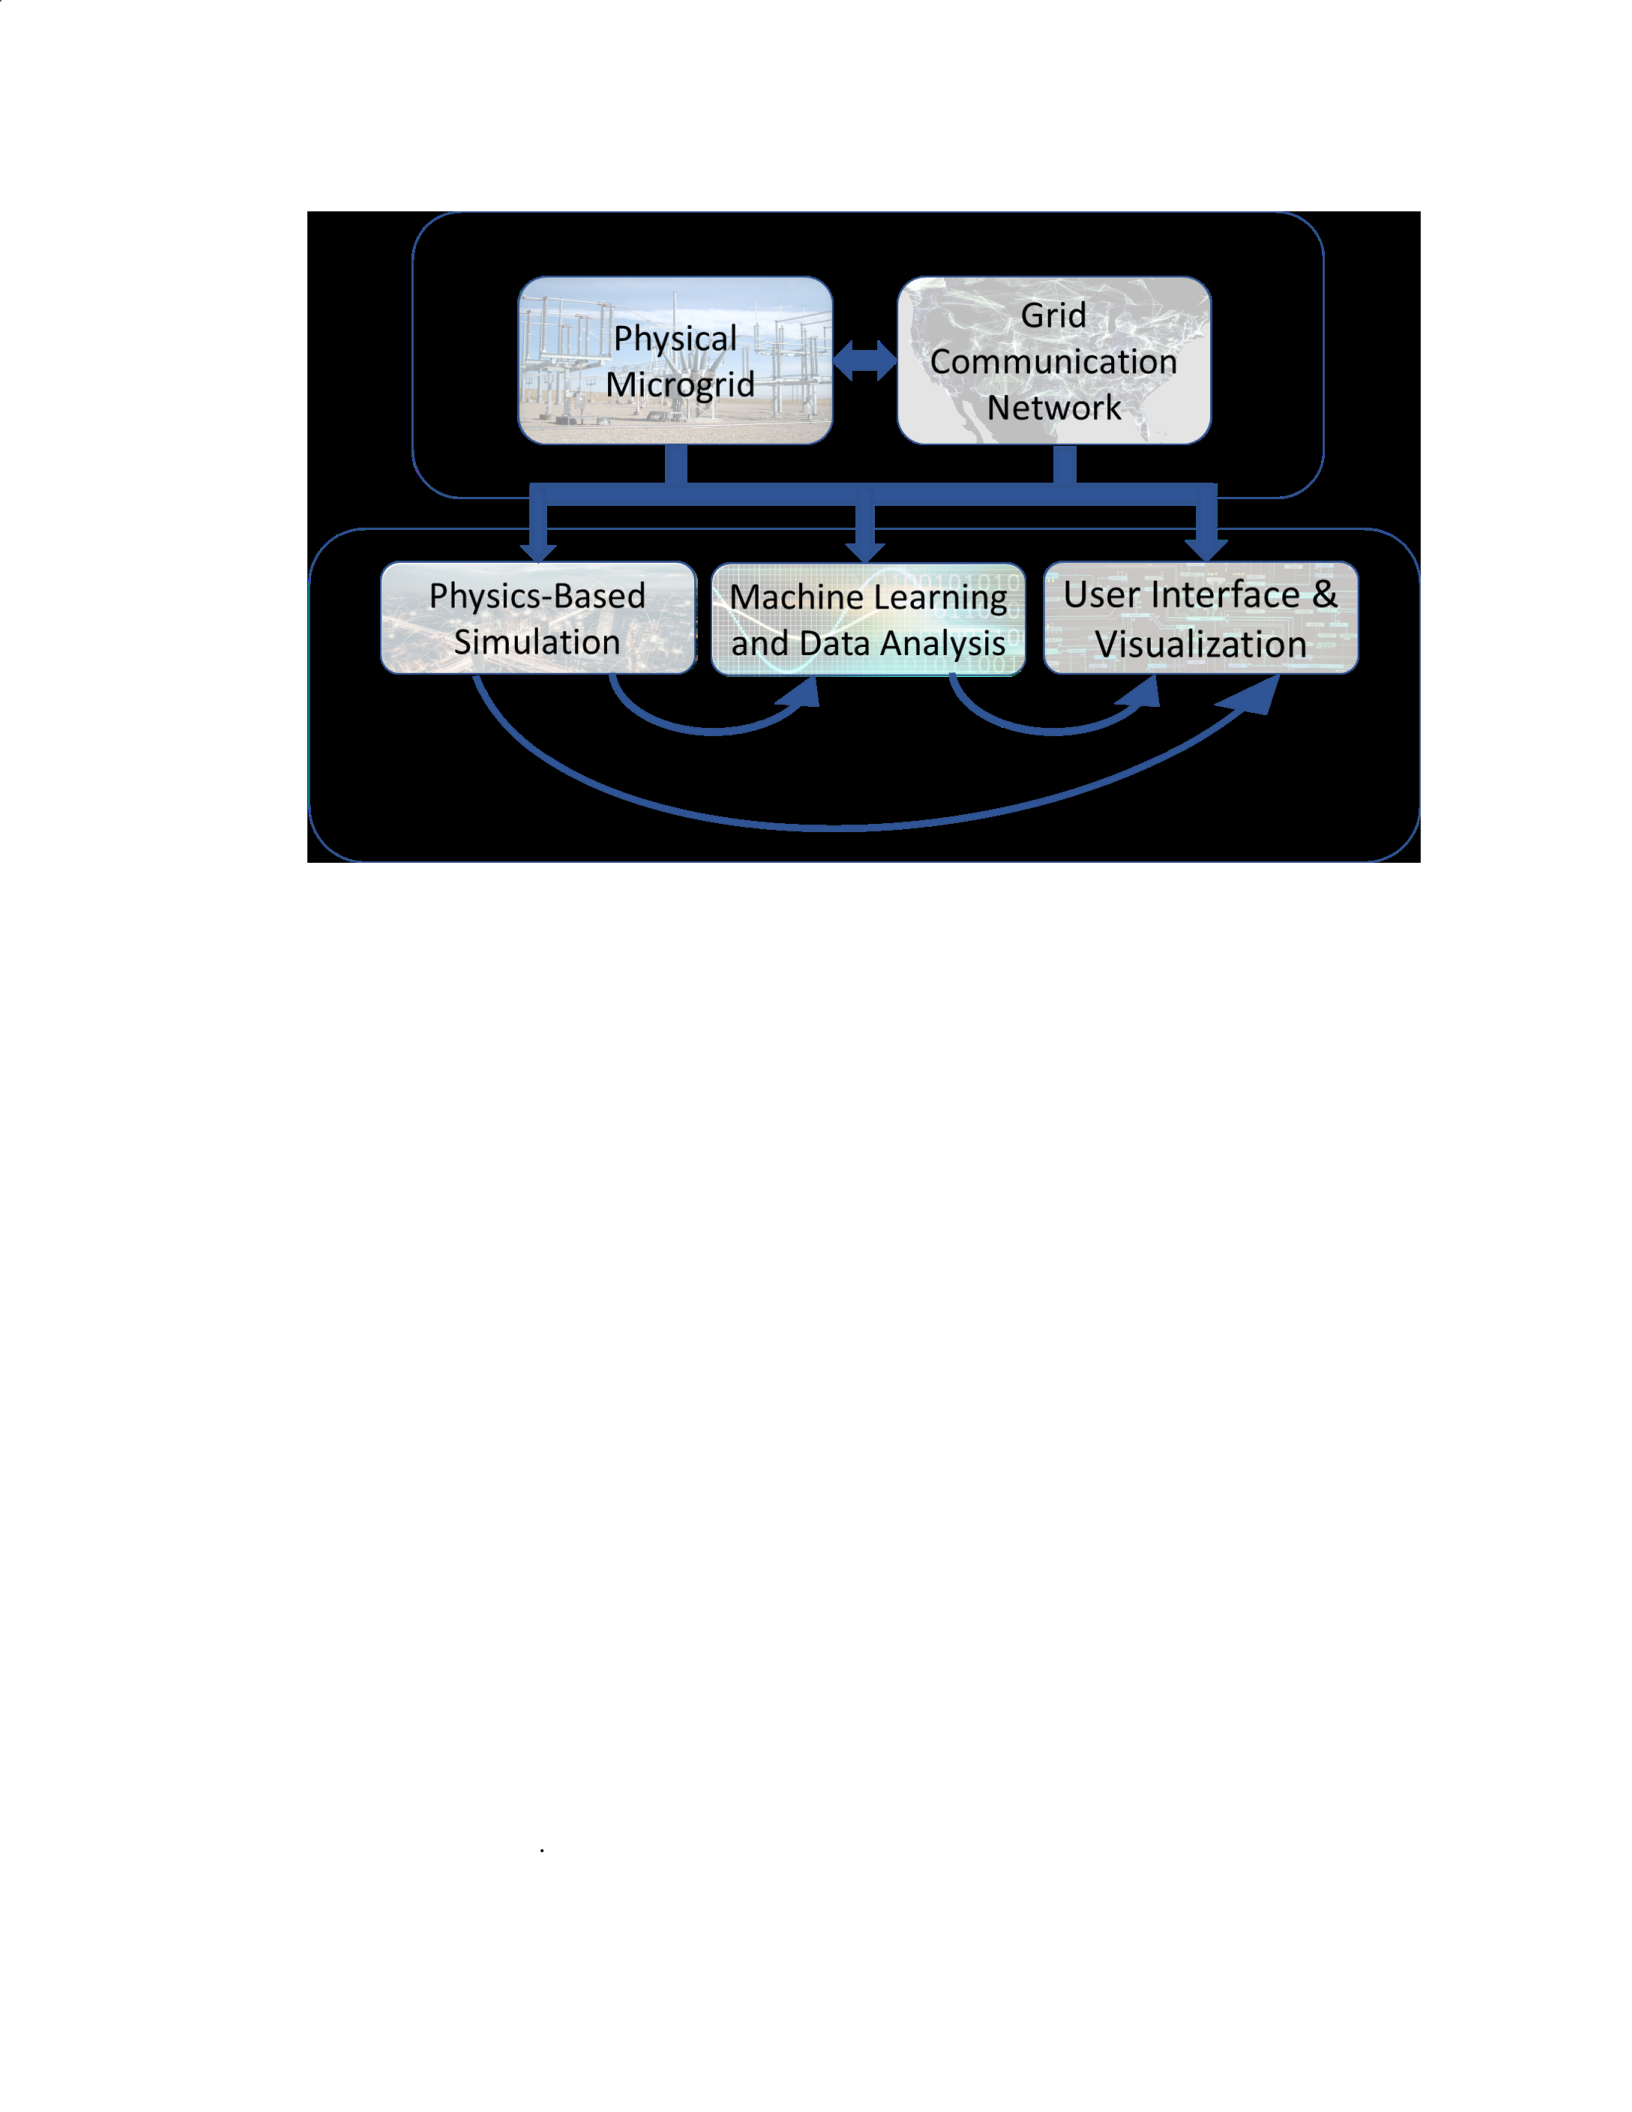
Figure 5. Overview of the ANGEL Digital Twin for Cyber Physical System. [2]
simulation, machine learning and data analysis, as well as the user interface and
visualization suite of the digital twin, Figure 5. While analyzing additional data
from the grid could be advantageous, using the legacy communication protocols
allows the digital twin to be deployed and tested on a microgrid without significant
modifications.
The digital twin is required to effectively model both the physical and cyber
layers of the Smart Grid. The ability to accurately model and simulate all aspects
of the physical system is critical to being able to properly predict and assess the
behavior of the Smart Grid. However, while doing this the simulations have to be
fast enough to provide feedback to the Smart Grid in near real-time. The balance of
fidelity and computational efficiency is essential to successfully executing a digital
twin.
The physical twin surrogate runs in real-time using the pacing feature in Math-
works Simulink
. Alongside the real-time simulation, the digital twin simulation
21

is run in a faster than real-time virtual environment. Since the digital twin sim-
ulation is able to run approximately five times faster than real time the ANGEL
digital twin is able to compare the data from the physical and digital systems and
flag any discrepancies.
As development of the ANGEL system continues, the power grid surrogate is
replaced with a state-of-the-art hardware-in-the-loop (HIL) simulation that mod-
els not only the physical aspects, including the high frequency components, of the
power grid but the cyber components as well. This research has focused on the
development of the ANGEL digital twin framework as well as the implementation
of computationally efficient but accurate simulation techniques. Using those sim-
ulation techniques, to research machine learning algorithms for the detection of
anomalies.
The digital twin prototype uses a memory-based co-simulation method to
pass data back and forth from the digital twin to the physical system. The co-
simulation method of communication allows for the prototyping of the physics-
based simulation methods. The Python-based digital twin, explained in further
detail in Section 2.4, is able to ingest real power grid communication protocols,
such as Modbus, DNP3 and IEC61850, via the lab-based SCADA system. Using
the working prototype, the methodology can be evaluated by comparing the digital
twin to the grid surrogate in the Matlab GUI environment.
The ANGEL digital twin aims to secure the modern cyber physical grid against
these types of attacks and exploits. Using real-time, physics-based modeling and
simulation techniques along with advanced stochastic methods, the ANGEL system
can identify a potential anomaly but evaluate the potential damage before it occurs.
This allows the system to adapt, creating a self-healing microgrid and ultimately
similar systems could be applied to Smart Grids. The useful application of the
22

self-healing aspects of the digital twin is not limited to malicious attacks. General
degradation due to age or operating condition can also be mitigated using the same
techniques.
Using parallel computing techniques, the digital twin is able to simulate many
system states concurrently. Using these simulations, the digital twin is able to
evaluate the current state of the physical twin against the simulations and make
intelligent judgments of the physical system state. Combining the simulation tech-
nique along with machine learning algorithms could create a first line of defense
that could potentially reduce grid vulnerabilities as well as lessen the time it takes
for a system infiltration to be detected.
2.2.1 Case Study using ANGEL Digital Twin
While the ANGEL digital twin framework is for a Level IV Intelligent Digital
Twin, as described in Figure 3, the case study presented here is using only limited
capabilities of the ANGEL system. This case study uses the IEEE 39-bus, com-
monly known as “the 10-machine New-England Power System”, as the initial test
case for the digital twin. First presented in 1970, the 39 Bus New England System
is a simplified model of the high voltage transmission system in the northeast of
the U.S.A. (New England area). It has since been often used for scientific research
and publications. The 39 Bus New England System consists of 39 buses, 10 gener-
ators, 19 loads, 34 lines and 12 transformers [3]. The 39-bus benchmark (Figure 6)
is commonly used in attack and defense scenarios due to its simplified nature and
relatively small size and therefore minimal computational expense.
The ANGEL GUI is fully interactive and can not only display the power grid
topography, but it is also able to display pertinent data from the grid. These visu-
alization techniques give the ANGEL system an ability to display any anomalies
that are detected in the physical system. The user is able to select the desired grid
23
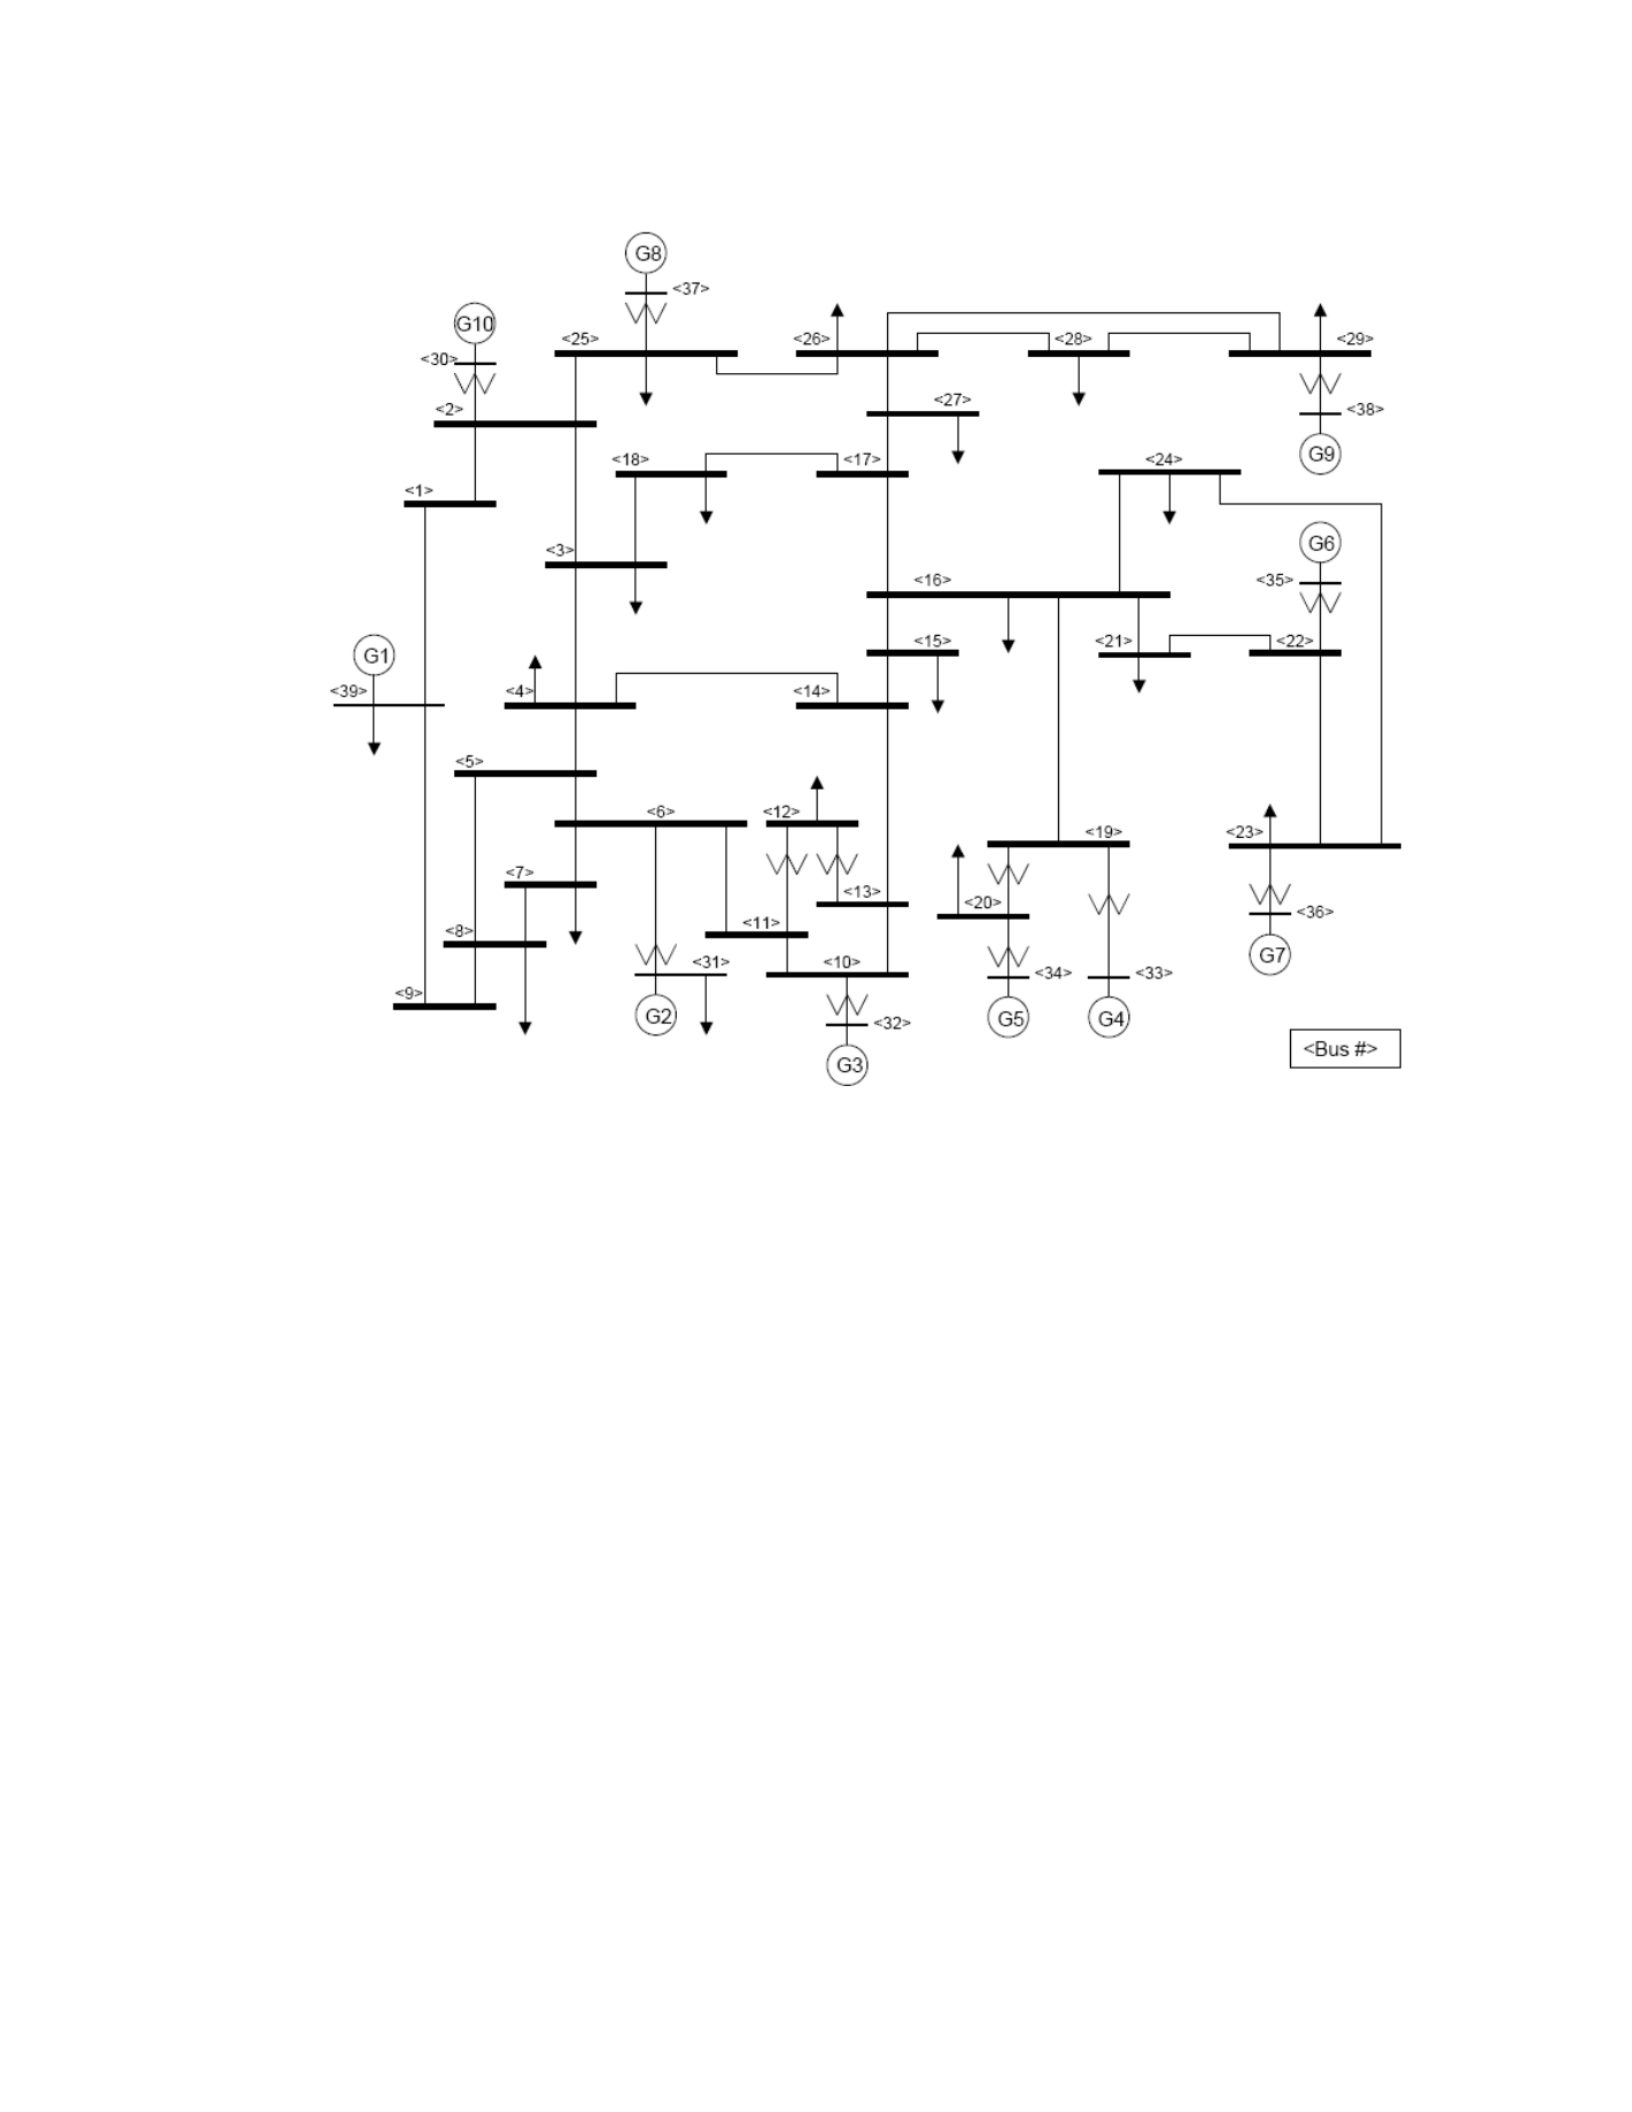
Figure 6. The IEEE 39-bus benchmark diagram. [3]
element to inspect the network and meter data being returned from the physical
system. In Figure 7, the user has selected a set of four buses, highlighted in blue, to
inspect the bus characteristic data for each bus. In Figure 7, the user has selected
the bus that encountered the fault, the Bus 39, as well as the two adjacent buses,
Bus 1 and Bus 9, and a bus far removed from the fault, Bus 23. For each bus
being inspected, data from the digital twin and the physical twin are able to be
compared on a single screen, shown in Figure 8, for the user to analyze.
The ANGEL digital twin models both the physical and cyber layers of the
Smart Grid. By modeling both layers the digital twin is able to evaluate the
performance of the grid as well as validate the data it is receiving from the power
24
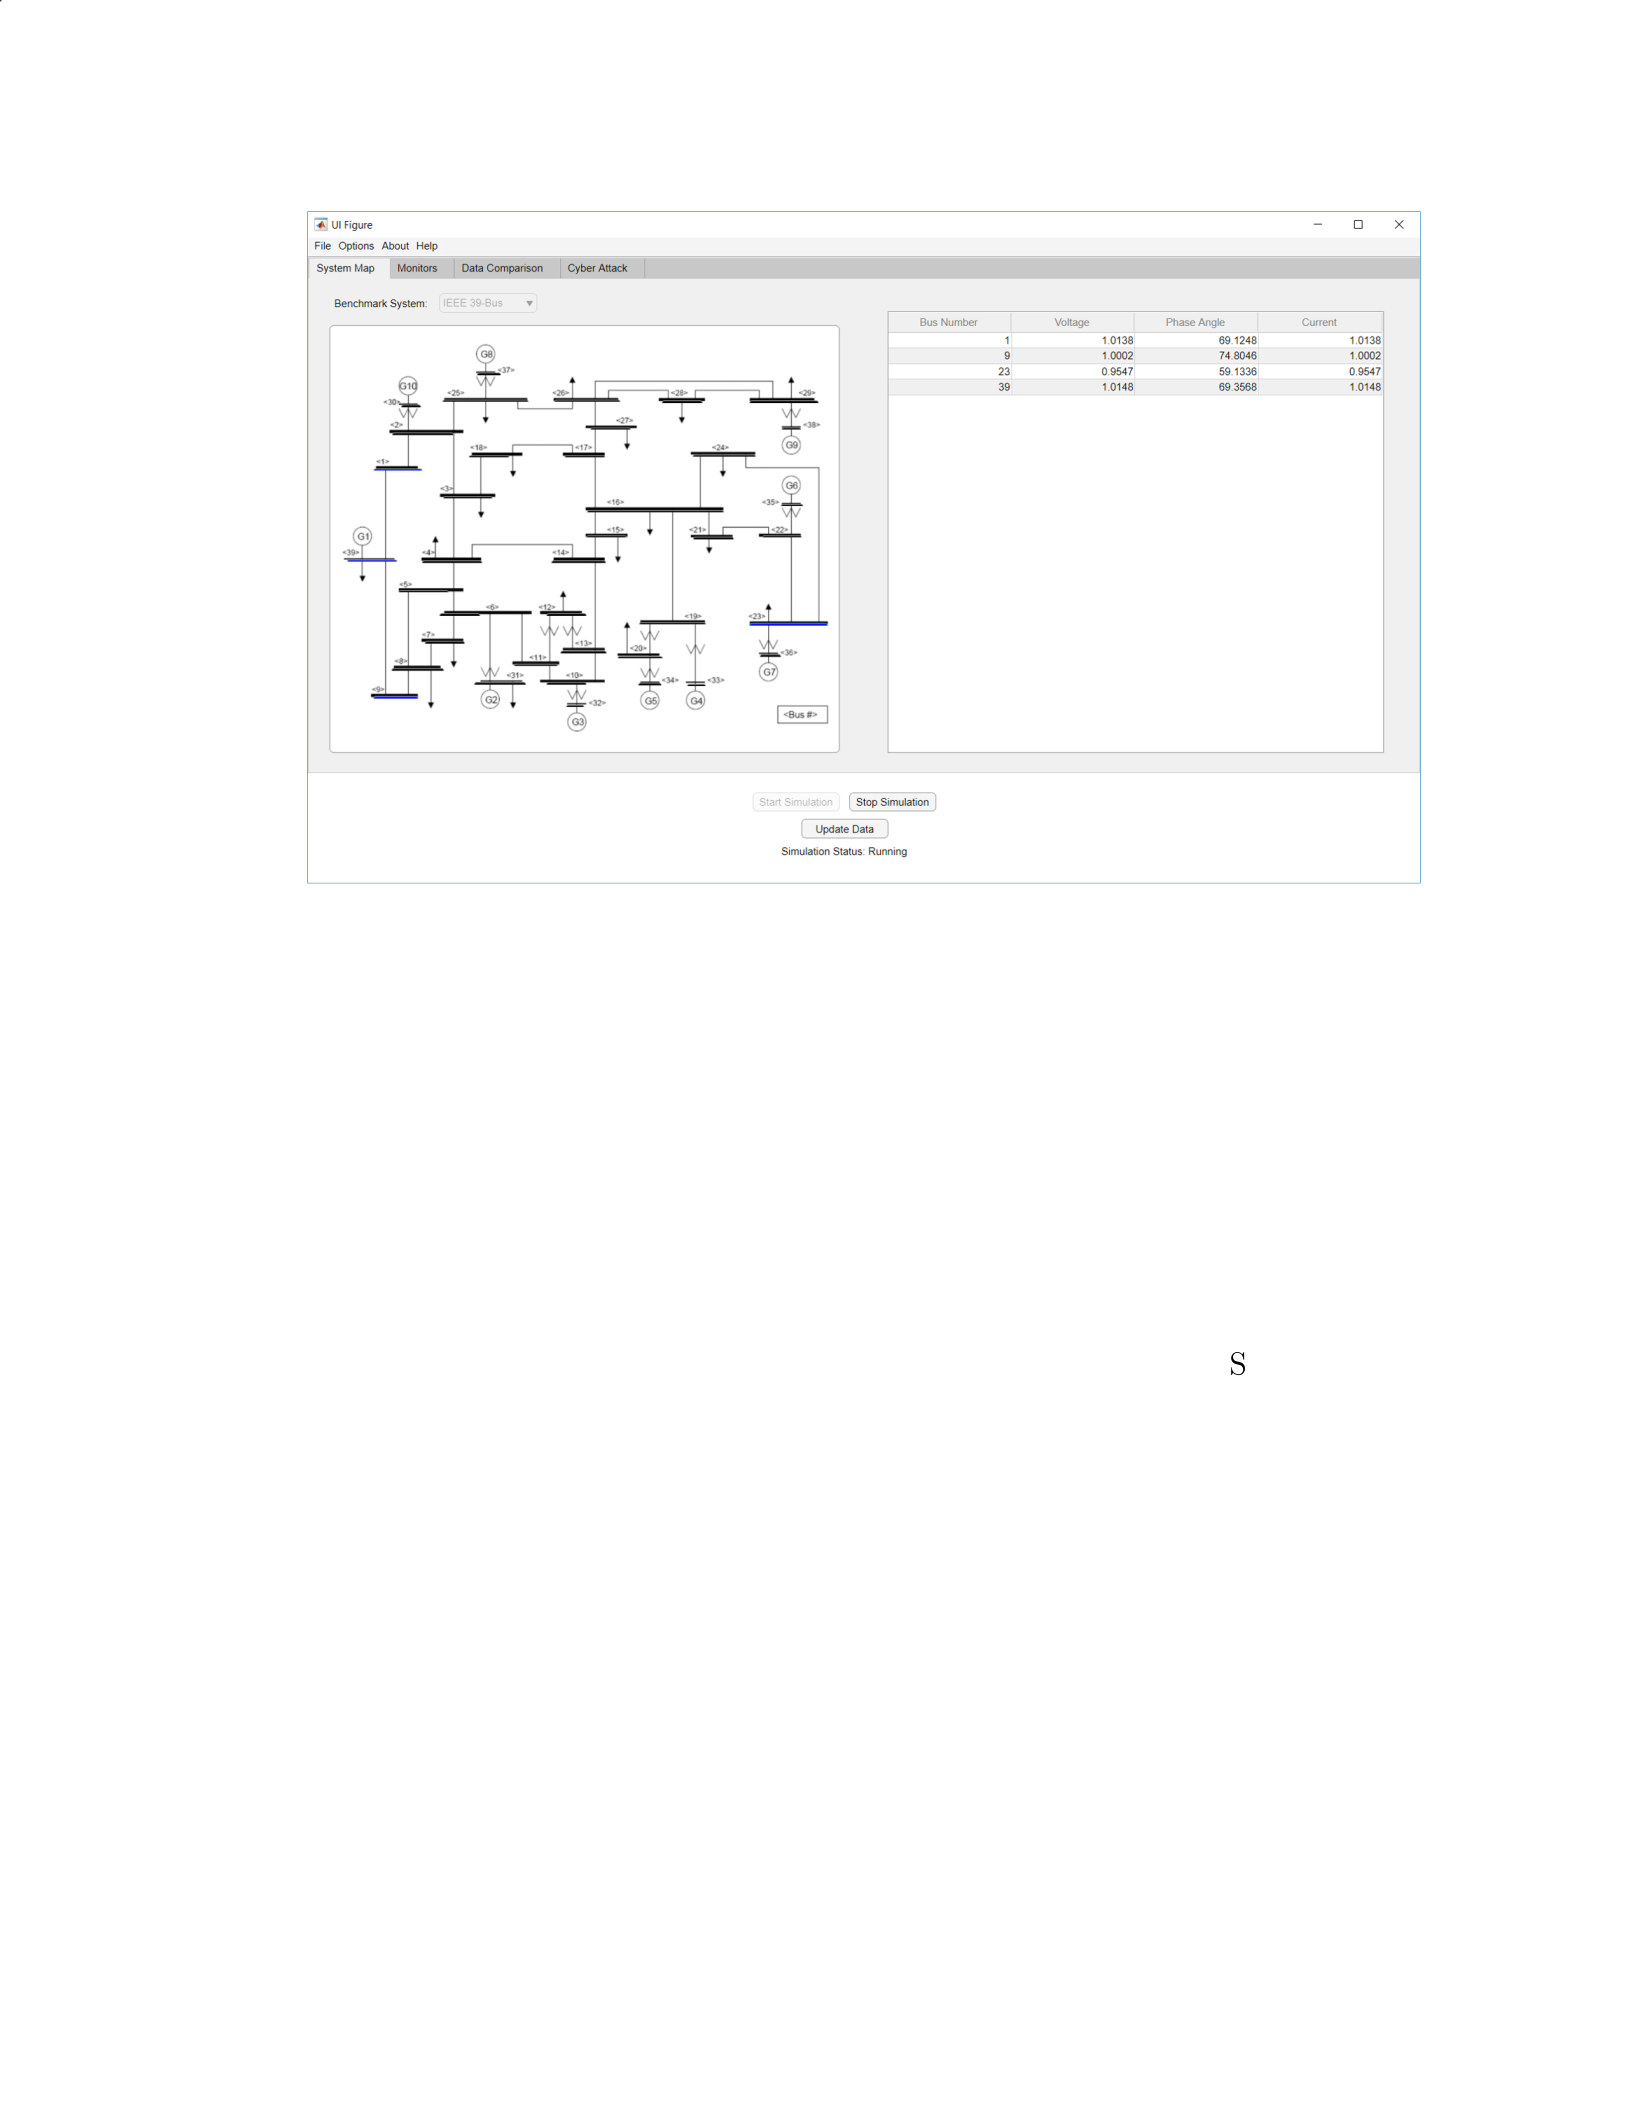
Figure 7. ANGEL Digital Twin displaying the typography of the IEEE 39-bus
benchmark (left) and characteristic data of the selected buses (Bus 1, Bus 9, Bus
23 and Bus 39) .
system. In the event a grid anomaly is detected the Angel system can direct the
physical system to a stable condition while also identifying the potential cause of
the anomaly.
The ANGEL digital twin GUI, shown in Figures 7, 8 and 9, is developed using
the Mathwork MATLAB App Designer and Mathworks Simulink
SimPowerSys-
tems as a surrogate for the power grid for the ANGEL prototype. The ANGEL
GUI runs alongside the benchmark system and extracts meaningful data from the
simulation model. The ANGEL system takes this data and displays the current
state of the physical system as well as feed the data into the digital twin simula-
tion. This structure allows future expansion the capabilities of the ANGEL system
to a full hardware-in-the-loop simulation and eventually a full microgrid without
requiring too much modification.
To show ANGEL in action, a simple demo case was set up to create a discrep-
25
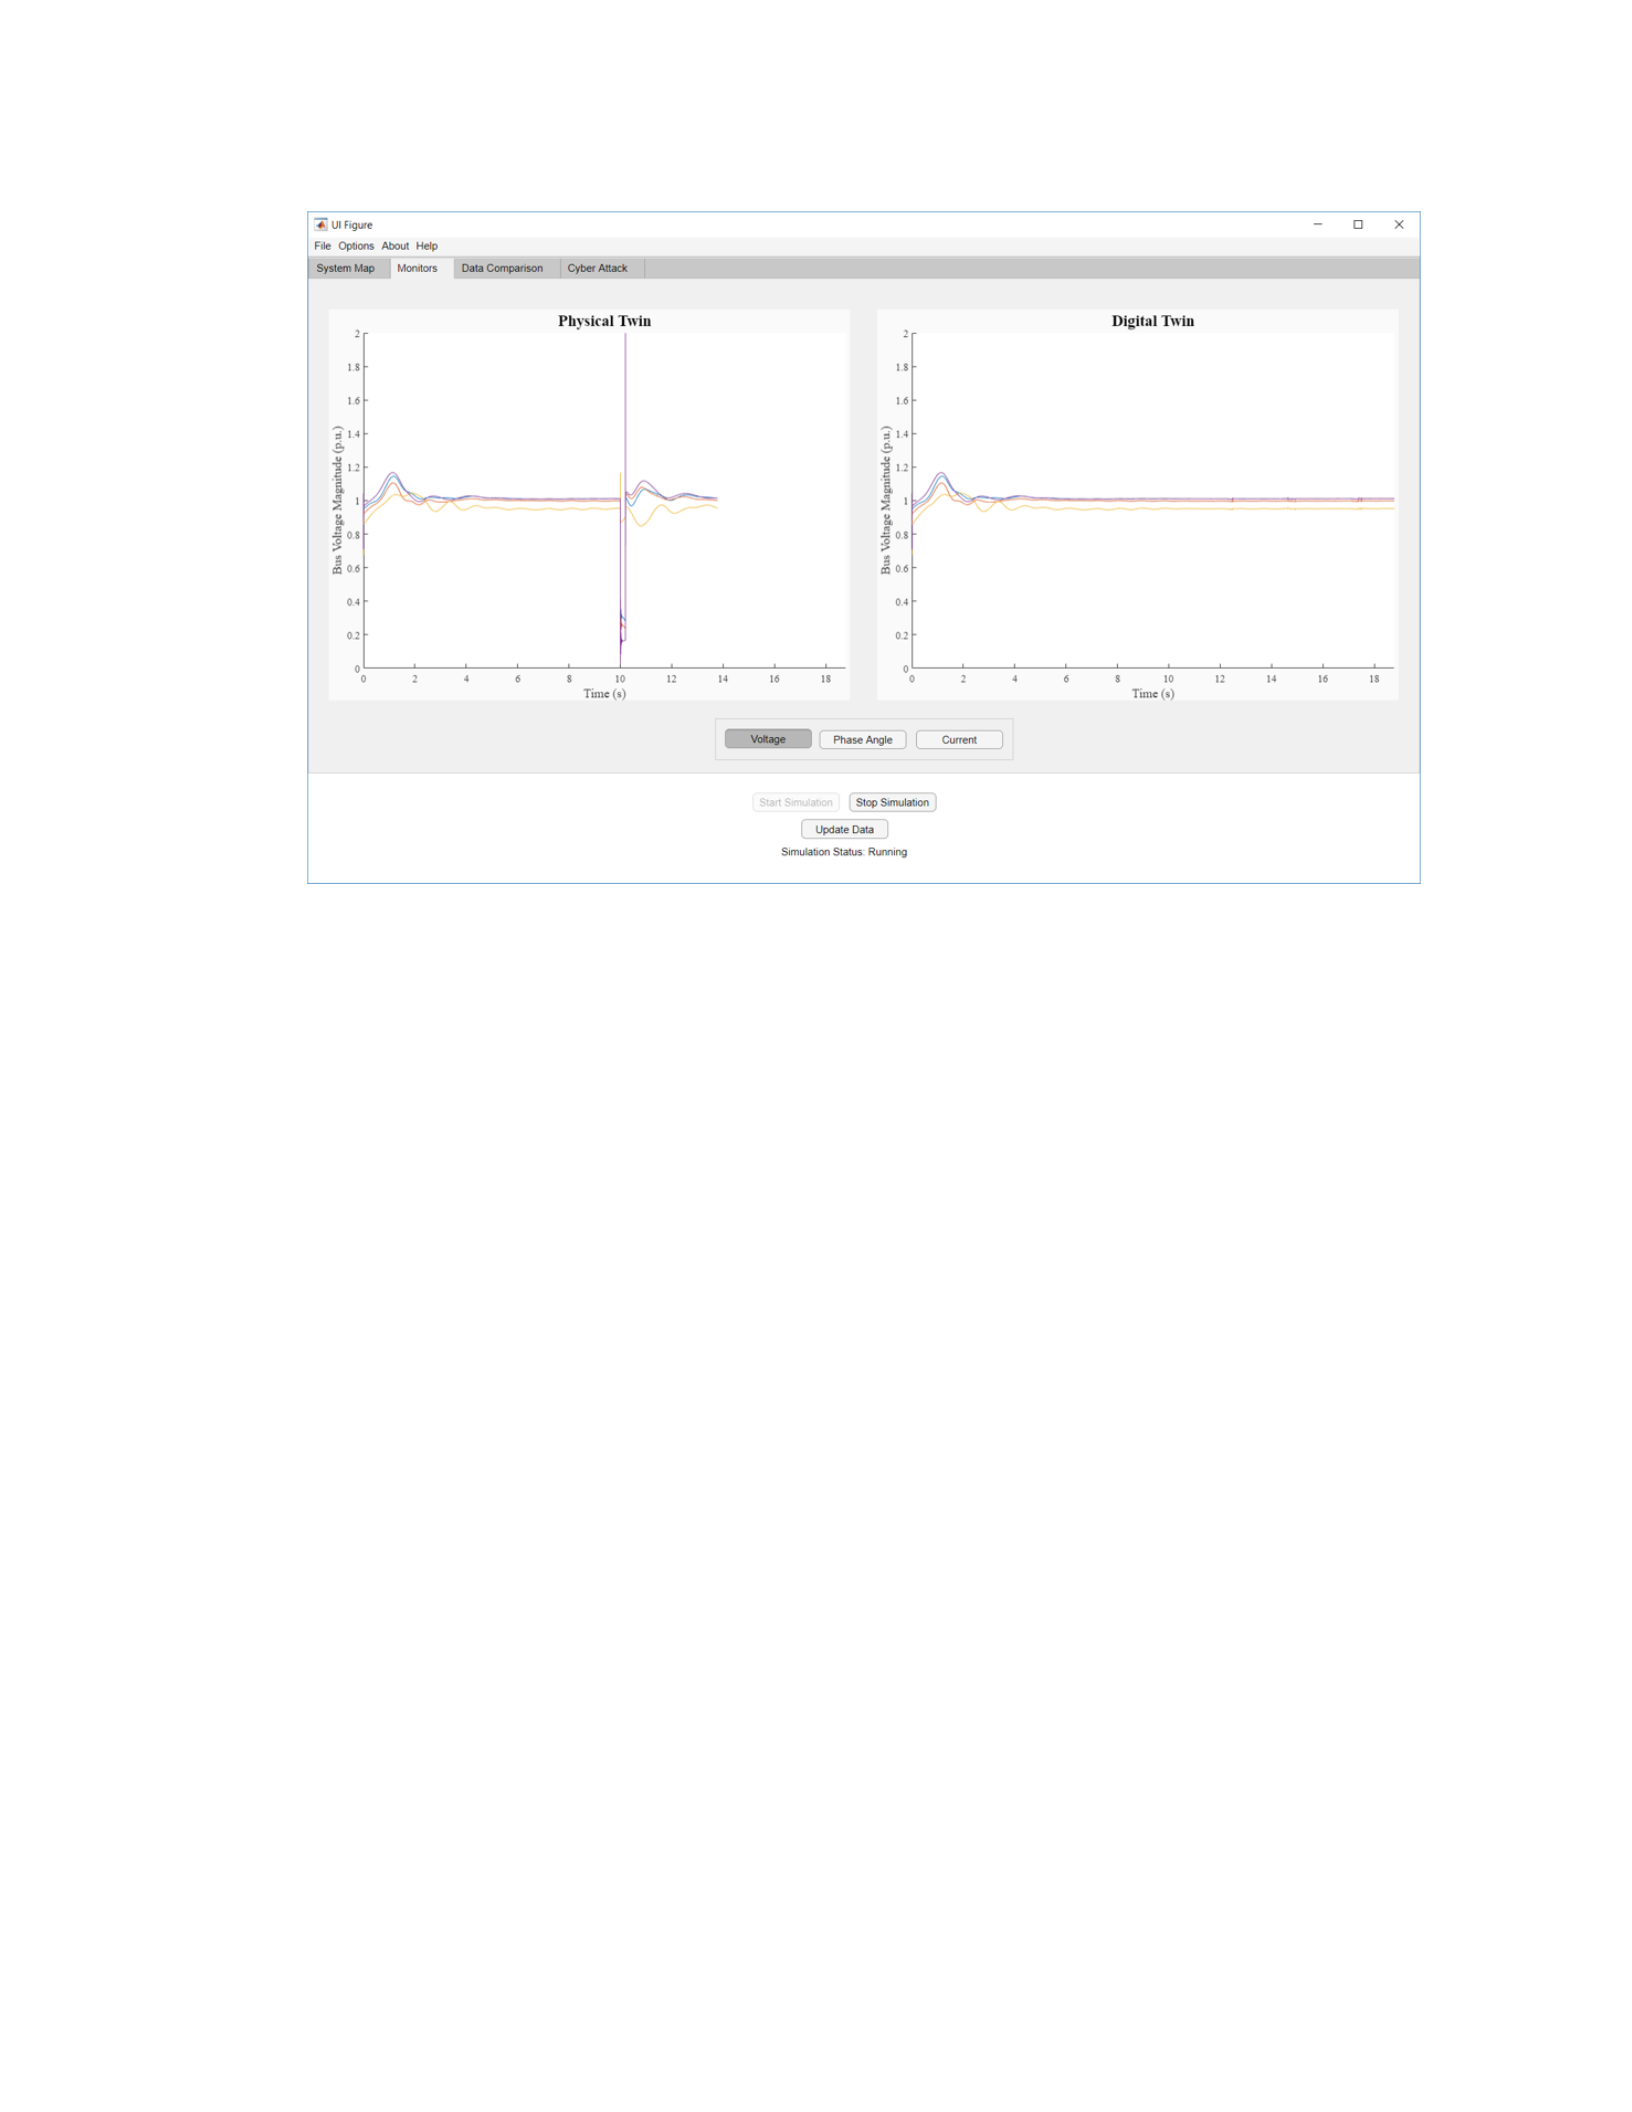
Figure 8. ANGEL Digital Twin plotting the voltage on Bus 39 received from the
physical twin (left) and digital twin (right).
ancy between the physical system and the digital twin. Similar to the methodology
used in [55], a three-phase fault is implemented on bus 39 in the physical twin at
the 10 second mark and the fault is cleared at 10.2 seconds.
An important part of the digital twin is the ability to visualize the data
acquired from physical and digital twins. The visualization is aimed to inform the
operator of the condition of the physical system and how well it is aligning with
the digital twin. The digital twin and physical twin align quite well for this demo
case up, shown in Figure 9 until the 10s mark when the fault is triggered. This is
to be expected because both systems are running in nearly identical environments
without any perturbations.
At the 10s mark the three-phase fault is triggered on bus 39 and the impact
of his fault reverberates throughout the system. As one would expect the response
is most severe on bus 39 which is displayed in Figure 6. The ANGEL digital twin
26
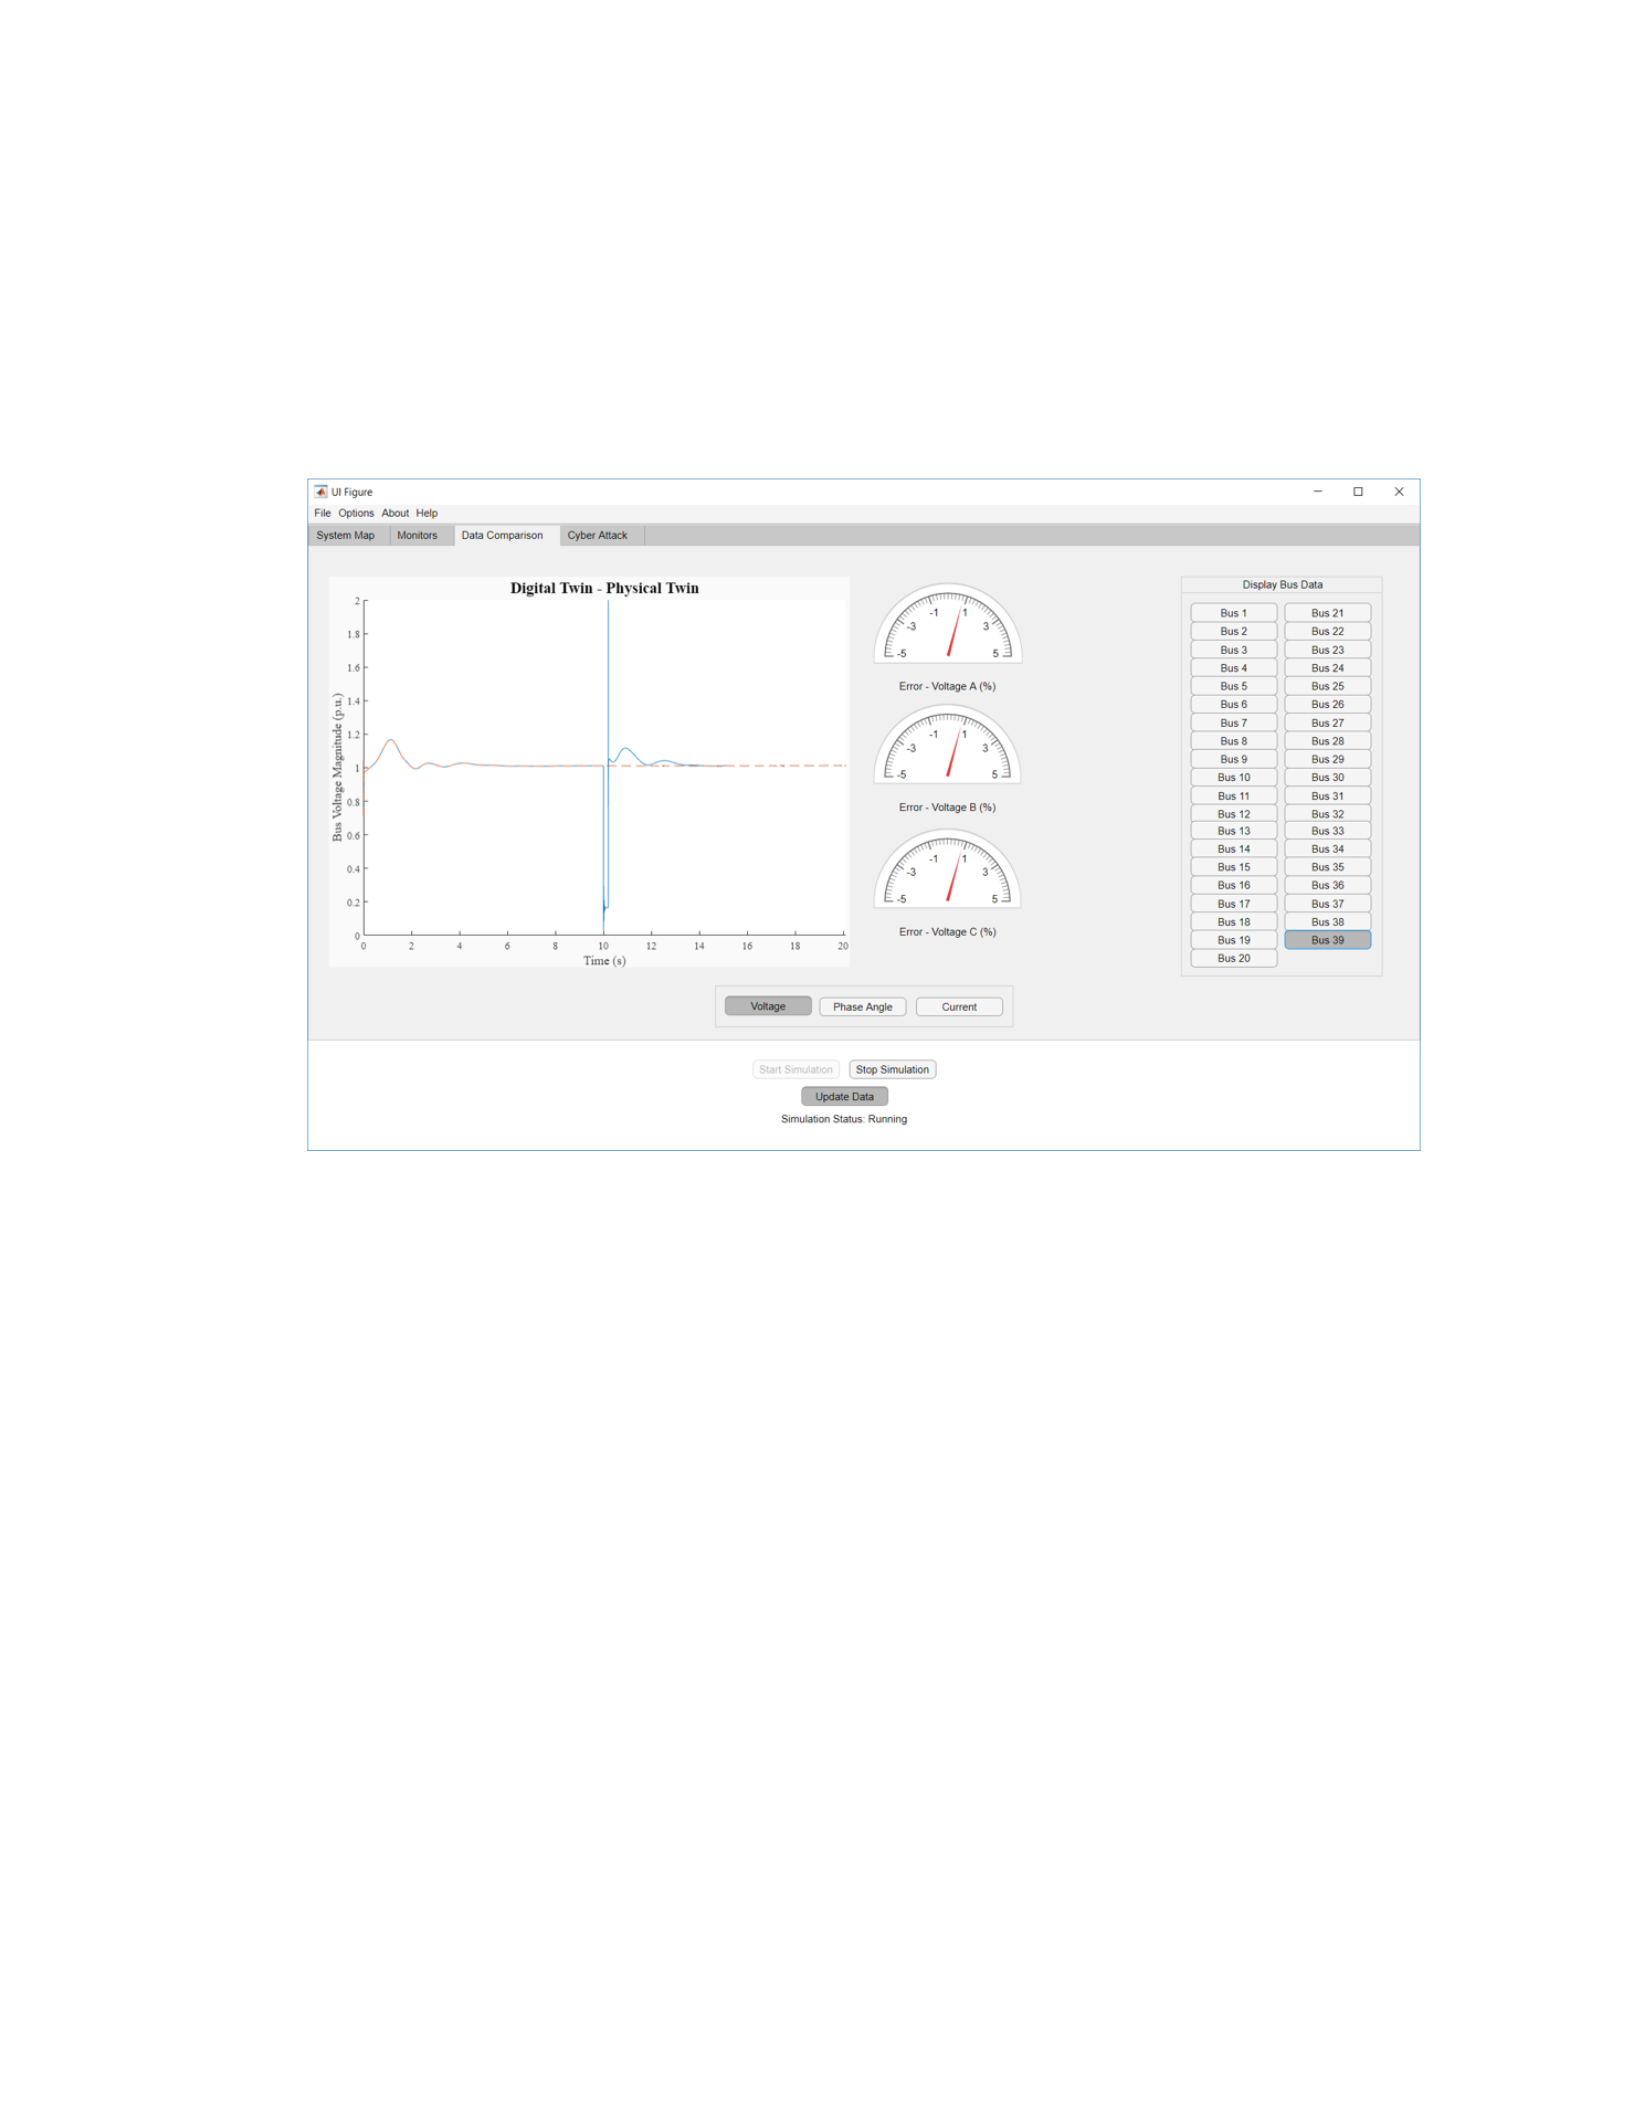
is able to capture the differences between the digital twin simulation which does
not have the fault and the physical twin which has a three-phase fault at bus 39.
When this divergence occurs, the ANGEL GUI detects the discrepancy and alerts
the user of the potential issue.
Figure 9. ANGEL Digital Twin displaying the voltage of Bus 39 of the physical
system as well as the expected data of the digital twin simulation.
2.3 Using a Digital Twin For Microgrid Resilience
The ability of the digital twin to not only model, but to influence the physical
system creates an extremely powerful entity that could defend the grid against
cyber-attack and exploit. The hybrid approach of the digital twin makes it very
well suited to evaluate the performance of the full power grid and make decisions
to protect the stability of the grid in real time. While digital twins are not cur-
rently used in modern power system monitoring and control, similar concepts have
become part of the discussion in recent years [32].
27

2.3.1 False Data Injection
The false data injection attack is the most obvious potential vulnerability
to the digital twin for Smart Grids. The digital twin is an integral part of the
Smart Grid that it is installed on. This tight two-way coupling makes it extremely
vulnerable to reacting to bad data. However, the physics-based simulation that is
the basis of the digital twin makes it more difficult for the attacker to inject data
that still aligns with a probable real-world solution. The simulation approach has
built-in redundancy due to the entire system being modeled not just an individual
node.
While false data injection attacks have proven successful against state estima-
tion techniques [56], the physics-based simulation environment of the digital twin
increases the difficulty of such attacks. Signal data that does not align with the
simulation-based system state is flagged and evaluated to determine the source
of the error. Using this type of approach, the Digital Twin can add layers of
protection to the traditional SCADA system.
2.3.2 Denial-of-Service
The Digital Twin relies on a constant stream of data to keep the simulation
model in lock-step with the physical twin. If the data received by the Digital
Twin is cut off or delayed the Digital Twin would not be effective in directing the
physical system because any control or guidance the physical twin receives from
the digital twin is no longer present. In this case, the physical system would default
to the traditional SCADA system. Likewise, the temporal accuracy of the sensor
information is important to the digital twin. If the sensor information is delayed
in a way that puts the digital twin out of sync with the physical Smart Grid,
the input provided by the digital twin could excite any grid instabilities that are
present in the physical system. Due to the importance of the temporal component
28

in digital twin’s dynamic simulation, the timestamp of the data would also need
to be analyzed in conjunction with the physical parameters of the system.
2.3.3 Topology Attack
The topology attack is a man-in-the middle attack where the attacker is able
to intercept network and meter data, modify them and forward the modified data
packets onto the control system [57]. While modern power systems have bad data
tests to compare the network and meter data, if both data set are changed to be
consistent the data check can not discover the change. Further, this type of attack
can be shown to be impossible for the traditional SCADA system to detect without
proper countermeasures in place [58]. One of the countermeasures suggested in [58]
is to lock down certain meters to prevent tampering with the meter data. While
this method would likely work, it could possibly be difficult to lock down a meter
with absolute certainty.
The digital twin presents another possible solution to the defense of this at-
tack. By providing an independent real-time simulation of the full topology of the
physical system, the digital twin can be able to detect any unnatural changes in
the data that the digital twin receives from the physical twin. Furthermore, the
digital twin is able to evaluate the likelihood of the recorded meter and network
data being accurate or bad data.
2.3.4 Digital Twin Vulnerability to Attack
The addition of more elements to any system creates a potential vulnerability
for attack and the digital twin is no different. The ANGEL framework attempts to
mitigate the inherent risks involved with a powerful system by designing the digital
twin with the capability to fall back on the SCADA system if required. However,
this is not enough to prevent the digital twin from becoming a potential single
29
point of failure for the system is installed on. It is imperative that the ANGEL
framework be designed with this vulnerability in mind and the ability to detect
and self-diagnose is critically important.
2.4 ANGEL Framework Expansion and Development in Python
While the Matlab implementation of the ANGEL framework was a good start-
ing point, the research into the ANGEL platform was moved into Python. The
flexibility of the Python development environment and large number of estab-
lished machine learning libraries was at the core of the decision. The Kivy library
is used to create a modern GUI for the ANGEL framework, shown in Figure 10.
Additionally, Kivy has cross-platform support which would potentially allow fu-
ture expansion to touch screen devices such as phones or tablets. While the GUI
and integrating software has moved to Python, the ANGEL framework continues
to leverage the MATlab modeling environment for the creation of physics-based
models.
The python platform is be central to much of the digital twin aspects of this
project and is the environment where the data from the physical system and the
physics-based model are compared and evaluated. This requires the python code
to support both the Simulink model and to be able to tie into the ElasticStack
database containing the data from the cyber layer of the physical system. The
python digital twin platform is required to update and launch the physics-based
simulations and return the outcome of those simulations into the semantic model
and decision making architecture.
The python environment is also a critical tool to calibrate and validate the
digital twin physics-based models with the physical system. The development of
the ANGEL system focused around two benchmark models:
IEEE 39 bus Benchmark System: The IEEE 39 bus model was chosen to be
30
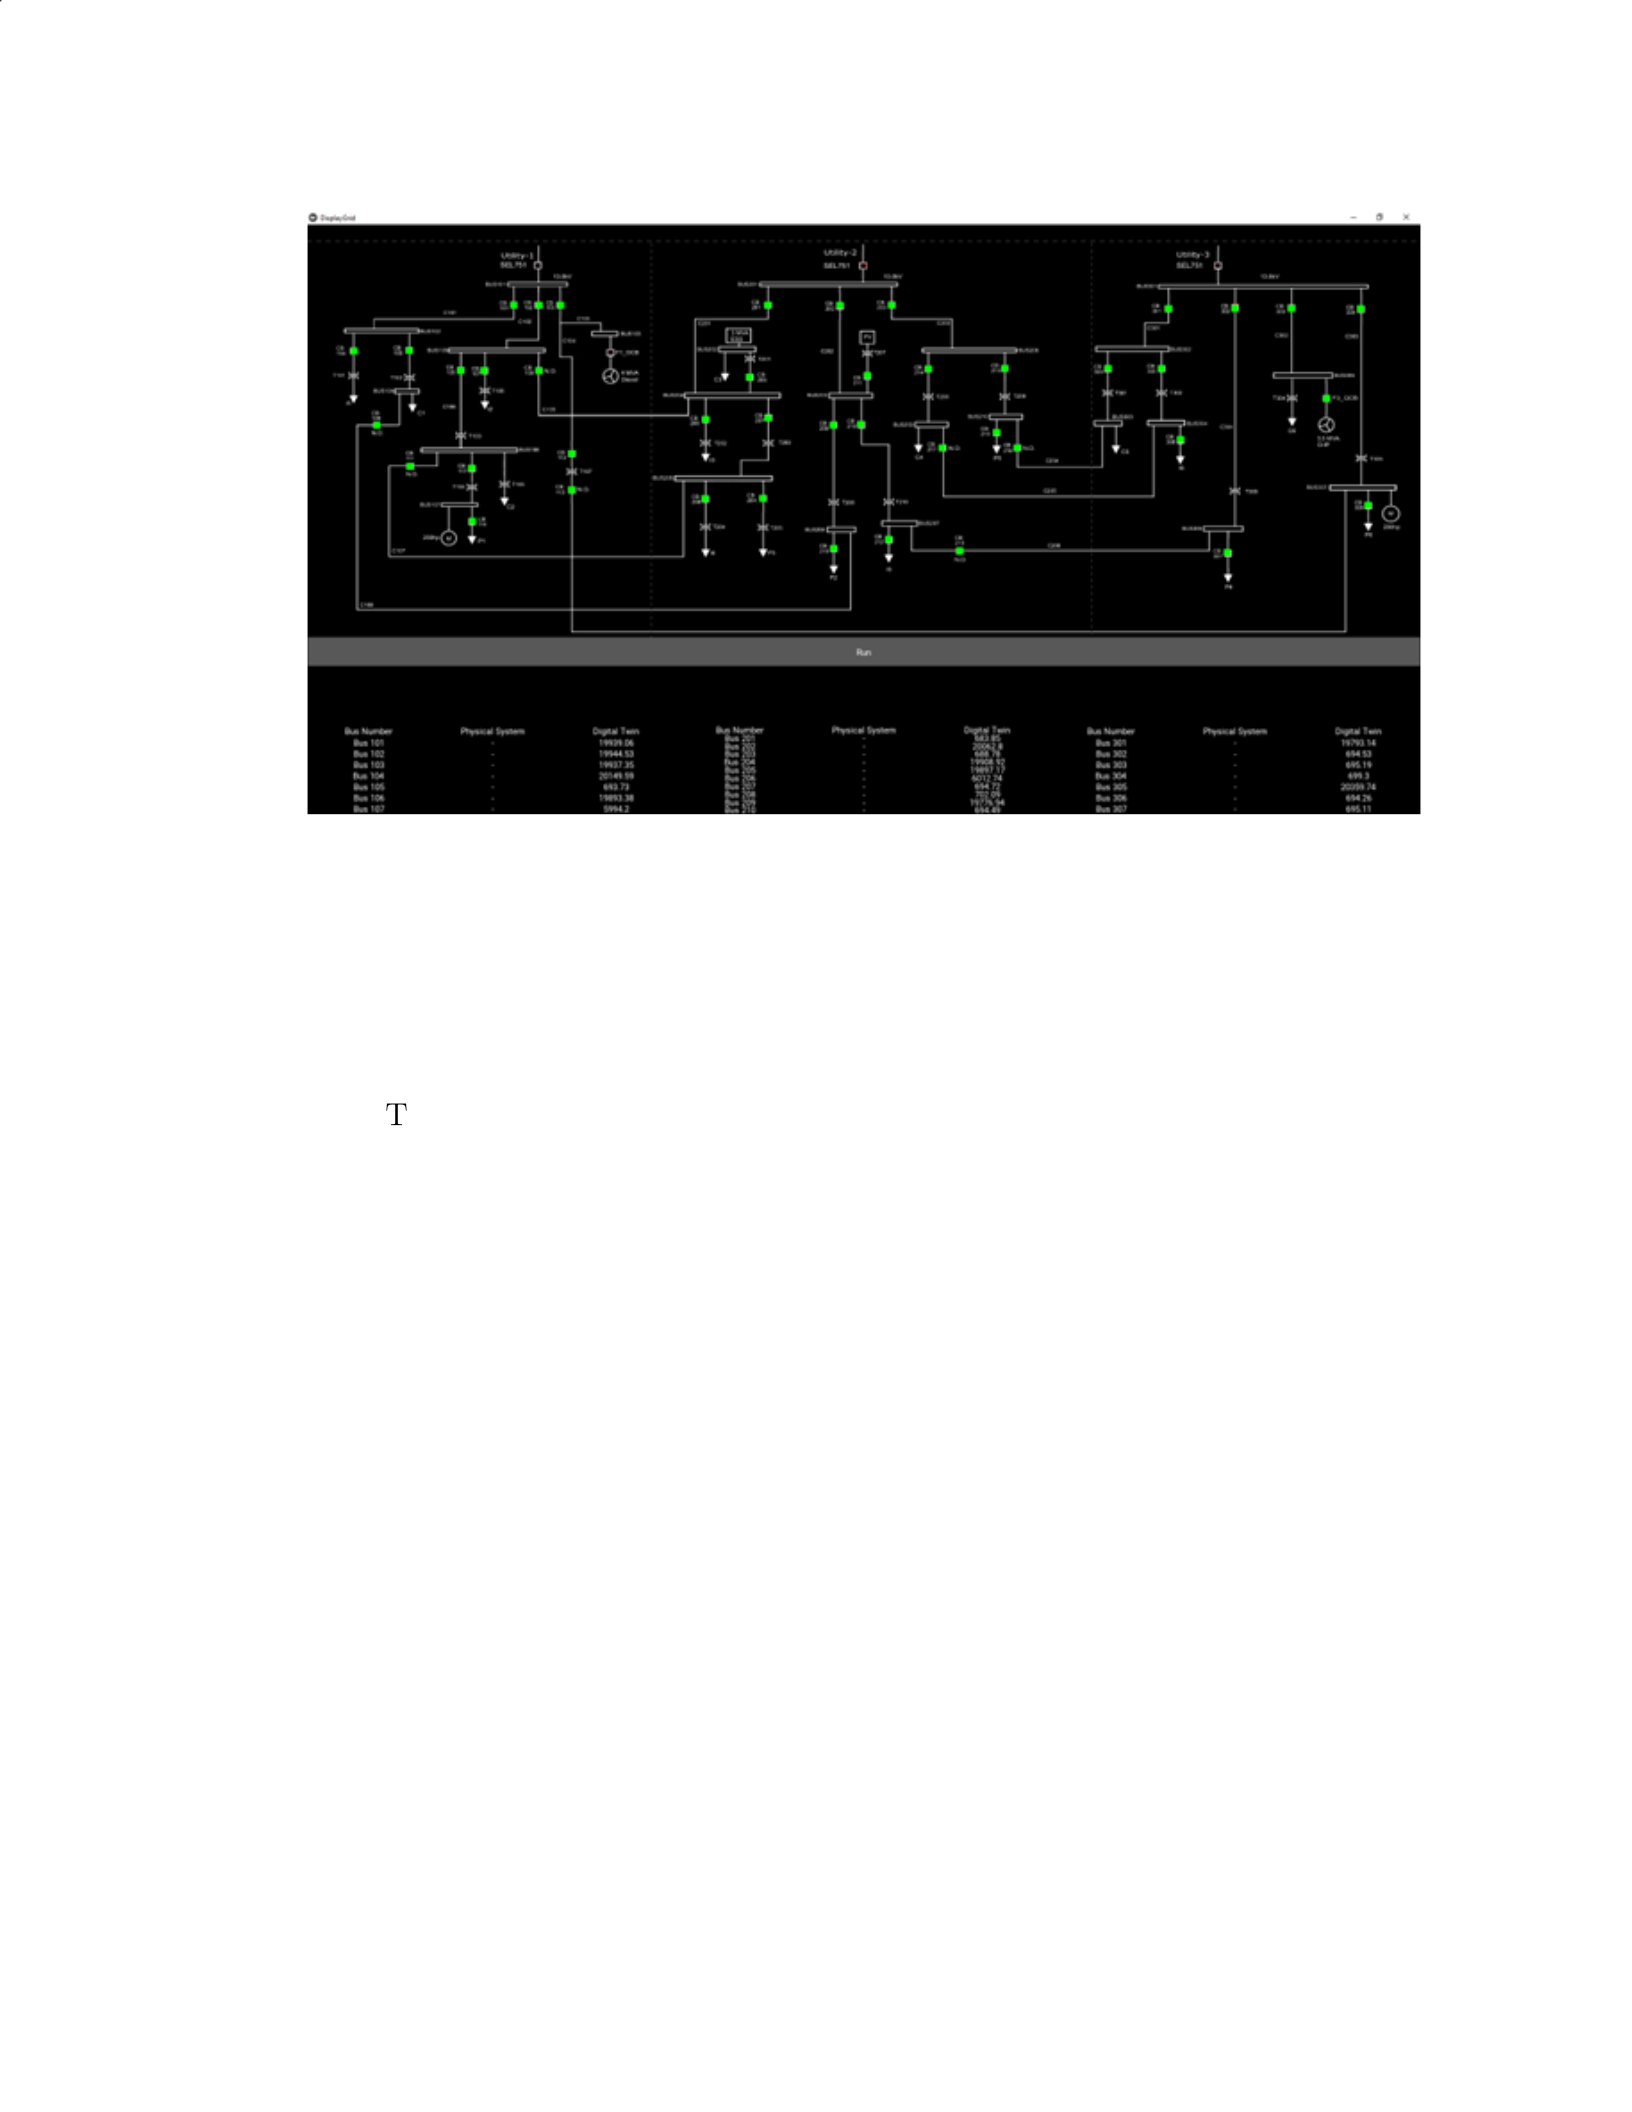
Figure 10. ANGEL Digital Twin v2.0 Running the GHOST Microgrid.
the benchmark and development system for the ANGEL development due to
it’s manageable size and widely published in literature.
The Grid Hardware Open Source Testbed (GHOST) Microgrid: The GHOST
microgrid was selected as a recently developed benchmark system that con-
tains modern sensors and control.
For more information on the benchmark system, refer to Chapter 6 which
contains a more detailed description of these power systems and how they were
implemented in the laboratory environment.
2.4.1 Chapter Summary
In this chapter, the ANGEL Digital Twin framework was presented along with
some use cases of the abilities of a cyber physical digital twin and how the ANGEL
framework can improve the resiliency of the power grid. The ANGEL system was
developed from the ground up to use digital twin technology to increase insight
into the operating state of the underlying power system.
31

While the power of the digital twin is beginning to be realized in other indus-
tries, the power distribution sector has been relatively slow to develop digital twin
technology. As Industry 4.0 and the Internet of Things (IoT) technologies continue
to infiltrate themselves into all industries, the potential applications and power of
digital twins continue to increase. Creating digital twins of individual devices or
components to determine maintenance cycles and service life is valuable; however,
the ability to leverage the digital twin to not only model the full physical system
but also to control, adapt and protect the physical system would be extremely
beneficial.
The ANGEL system is able to demonstrate its ability to gather system data
and to present anomalies to the operator. The ANGEL Digital Twin sets up an
advanced framework for the evaluation and control of cyber physical systems. The
ANGEL framework allows for the implementation of more sophisticated defense
of the power grid using real-time response and damage mitigation. The following
chapters will detail these uses cases and many more will be presented in the future
work section.
The ability to monitor, evaluate and control remote assets using physics-based
simulations and machine learning algorithms is able to improve smart control sys-
tems. The legacy SCADA system would still be valuable and can be used as a
safety net to prevent malicious actors from targeting the digital twin virtual envi-
ronment as a single point of failure. The ANGEL digital twin creates a framework
for a learning and self-healing cyber physical system to improve the resiliency of
perhaps the most essential piece of modern infrastructure, the power grid.
32

CHAPTER 3
Anomaly Detection Using a Deep Learning Digital Twin
3.1 Chapter Overview
Building on the ANGEL framework described in Chapter 2, in this chapter
a deep learning anomaly detection algorithm is presented. This algorithm is our
first step toward achieving a Level IV: Intelligent Digital Twin, see Figure 3 in
Chapter 1. This chapter focuses on applying deep learning algorithms to state-of-
the-art digital twin technology to assist in the detection of physical faults in a power
system. The proposed architecture would potentially allow greater understanding
into the status of the power grid by using deep learning (DL) to analyze the data
available to the Supervisory Control and Data Acquisition (SCADA) system of the
future Smart Grid.
Over the past few decades, the modern power grid has evolved into a large Cy-
ber Physical System (CPS) equipped with wide area monitoring systems (WAMS)
and distributed control. As smart technology advances, the power grid continues
to be upgraded with high fidelity sensors and measurement devices, such as mi-
cro phasor measurement units (µPMUs), that can report the state of the system
with a high temporal resolution. However, this influx of data can often become
overwhelming to the legacy Supervisory Control and Data Acquisition (SCADA)
system, as well as, the power system operator. This chapter proposes using a
deep learning (DL) convolutional neural network (CNN) as a module within the
Automatic Network Guardian for ELectrical systems (ANGEL) Digital Twin envi-
ronment to detect physical faults in a power system. The presented approach uses
high fidelity measurement data from the IEEE 9-bus and IEEE 39-bus benchmark
power systems to not only detect if there is a fault in the power system but also
applies the algorithm to classify which bus contains the fault.
33

By apply machine learning algorithms to detect the faults in a wide area
power distribution or transmission system, the power system would be able to
be continuously monitored and the faults could be detected and repaired before
any system damage is incurred. The analysis and control of the electric grid is a
critical issue in power systems [59]. As the power grid evolves to a Smart Grid, the
opportunities for distributed monitoring has increase significantly. However, the
legacy SCADA system is ill-equipped to process the plethora of real-time data that
is available from distributed sensors, such as Phasor Measurement Units (PMU)
and smart IECs [60].
Coupled with the deployment of high frequency sensors, the development of
software that can analyze the data and provide feedback to the system operator in
real time is required. Deep learning techniques have been deployed in a number of
different fields have the potential to do just that. Some of the recent successes of
modern deep learning architectures include ResNet [61], which was able to surpass
human accuracy in an image recognition task, and deep reinforcement learning
techniques, like AlphaGo [62], which have mastered complex games.
This work proposes a digital twin module that uses state-of-the-art deep learn-
ing techniques to detect and locate faults in a distributed smart grid infrastructure.
Section 3.2 presents a brief survey of other deep learning applications in power sys-
tems. Section 3.3 outlines the architecture of the deep learning algorithm and how
it was implemented in the power systems. In Section 3.4, the deep learning al-
gorithm is tested and the results of the tests are presented. Finally, Section 3.6
contains a brief conclusion and discription of how this fits into the research.
3.2 Related Work
While there are many approaches to fault detection in power systems, the
recent developments in big data and high fidelity wide area monitoring (WAM)
34

techniques using Phasor Measurement Units (PMU) have opened the possibility
of more detailed power system analysis [63]. Distribution and transmission power
systems are typically spread over wide areas and having precise diagnosis of fault
locations can help the utility engineer reach the fault location more quickly [64].
This not only saves time and money for the utility company, but will allow the
energy provider to reestablish power more quickly, which is especially important
for critical infrastructure, such as hospitals and water treatment facilities.
Many schemes have been proposed to detect faults in transmission lines as well
as larger power systems. These approaches include using dynamic state estimation
which has been used since the 1980s for anomaly detection in power systems [65] as
well as in individual transmission lines [66]. More recently, dynamic state estima-
tion has been applied to track the power system’s current state [67] and predict the
future states of the system. Similarly, state space observer-based control theory
has been applied to a Single Machine Infinite Bus (SMIB) power system to create
an online fault detection scheme for a power system [68].
In recent years, the investigation into wide-area fault detection and location
has increased. Using more classical techniques, such as a non-linear optimization
[69] and estimation [70], researchers have attempted to recreate missing sensor
data to assist in locating faults in the power grid.
Additionally, a number of machine learning based approaches have also been
investigated. The recent California fires have sparked new interest in fault detec-
tion in transmission lines [71]. Others have investigated using recurrent neural
networks (RNN) to detect cyber attacks launched on the physical power system
[72]. The use of discrete fourier transforms (DFT) [73] and discrete wavelet trans-
forms (DWT) [74] have been used for feature extraction in conjunction with artifi-
cial neural networks to locate faults. These methods focused on preprocessing the
35

data before passing it to a basic multilayer perceptron (MLP) for the deep learning
artificial neural network. Other researchers have investigated using a three layer
MLP network to detect faults in a power system [75]. In this paper, the researchers
were able to achieve a peak fault detection accuracy of 88.8% using current data
measured at a frequently of 1000 samples per hour.
With the expanding popularity of Digital Twin technology, some researchers
have begun exploring using this technology to improve the resiliency of the power
system [76]. Others have investigated using digital twins and deep transfer learn-
ing to manage maintenance cycles of a production line [77]. While others have
expanded this research into the field of power and energy to investigate faults in
individual components of the power system [78]. Another suggested power applica-
tion is to use artificial intelligence and machine learning to augment the traditional
SCADA control room [32].
While some of the machine learning methods are similar to the approach of
this dissertation, this method proposes to use state of the art machine learning
techniques as well as to expand the deep learning algorithm to encompass the
a full power system as a whole. Additionally, the techniques presented in this
method were developed to run in real-time to be able to function effectively as a
module of the ANGEL digital twin which focuses on the resiliency of the power
grid. Leveraging the advances in big data and machine learning and adding them
to the developing digital twin technology is a natural next step in creating a safer
and more secure power grid.
3.3 Approach and Methodology
As described in the previous section, there have been many proposed methods
for anomaly detection in power systems [79]. This deep learning approach analyzes
the whole power system simultaneously. Leveraging the advances made in the field
36
of deep learning for image recognition, a convolutional neural network (CNN) is
used to “view” the power system and detect anomalies in a similar fashion as it
would be used to detect objects in a picture. The three phases of voltage on the
bus is concurrent in time and space which is analogous to the three colors that
make up a pixel in an image. The proposed CNN methodology scans the time
series data for anomalies and passes the results to a feed forward network which
processes the features extracted by the CNN. To accomplish this, the sensor data
from the power grid model will need to be finite windows of data with a consistent
number of data samples. A time-window of 1000 samples at a sampling frequency
of 10,000 Hz, or equivalently 0.1s, is fed into the machine learning model. This
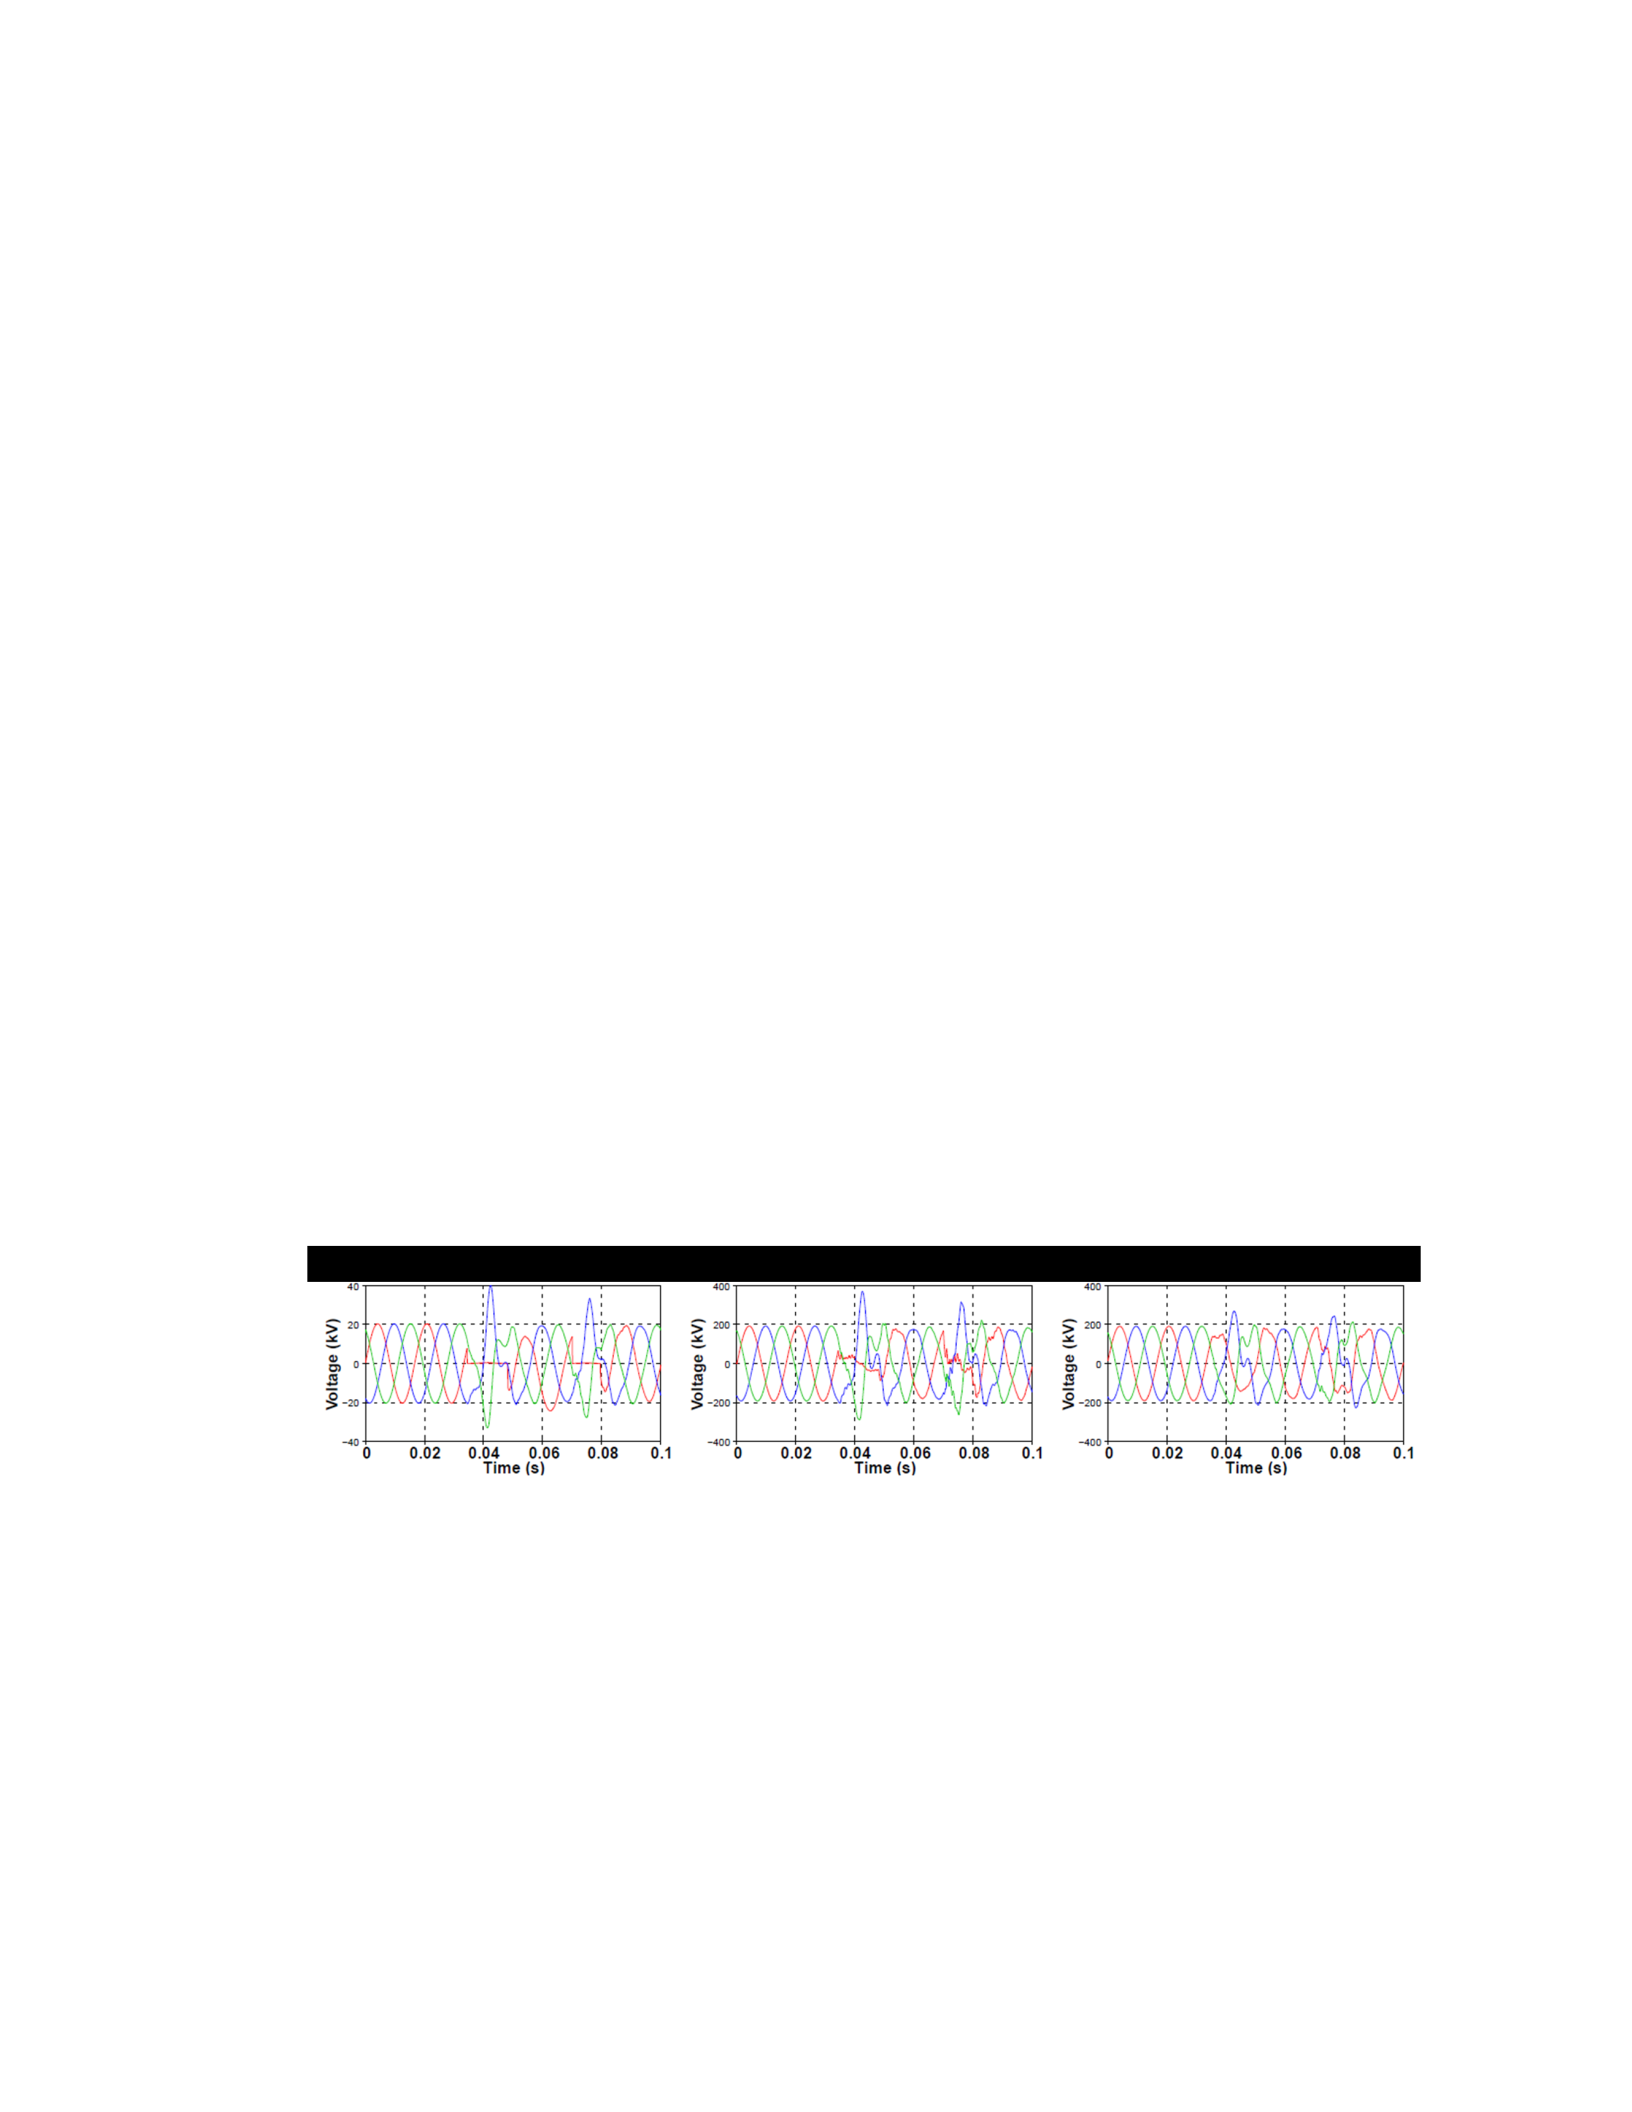
window represents about six cycles of the 60 Hz power. Figure 11 shows how a
full single phase ground fault on Bus 1 propagates through the IEEE 9-Bus power
system. It is worthwhile to note, that the data plotted represents a full fault and
the data does not include any noise for ease of visualization. In the following
research, many types of faults were used and all of the data included jitter, as
explained in more detail below.
Figure 11. Single phase to ground fault on triggered on Bus 1 can be seen on Buses
4 and 7.
The network is sampled at a frequency of 10 kHz which is comparable to
the data capture frequency of a µPMU [80]. While µPMUs are currently more
commonly used on distribution systems, the study assumes that as µPMUs become
cheaper and more prevalent in distribution systems their implementation will also
37

expand to transmission systems in the future smart grid. In machine learning, the
availability of high quality data is of the utmost importance and the underlying
assumption is that the logistical issues of transmitting the sensor data over the
network has been made possible in the future smart grid.
To increase the resiliency of the anomaly detection algorithm, artificial noise
or jitter was added to the training data [81]. As commonly done, the jitter was
added to the input as a randomized vector [82]. In this work, three percent input
noise was used to balance performance and training complexity. Adding noise to
the input of the network causes the algorithm to take more time to converge. To
account for this, each neural network was allowed to run for 50 epochs and the
iteration with the best results on the validation set was selected to be run on the
test dataset.
3.3.1 Convolutional Neural Network (CNN)
Inspired by neural cells of the visual cortex, CNNs are used for a multitude
of different applications, the most common of which is image classification [83].
However, there has been active research into using CNNs to analyze datasets such
as using a CNN for the prediction of the future price of a stock [84]. While this is
not anomaly detection, these methods can be applied to the analysis of the sensor
data from the benchmark power system.
The sensor data is passed to the CNN network as rows of data, for each of
the buses in the power system, and 1001 columns, one for each time sample, and a
depth of three, one for each voltage phase. This approach was taken because the
three phases of power are concurrent in time and space in the physical system. By
viewing the three phase power on a bus in this manner, allows the algorithm to
function similarly to the way an image is processed in a CNN.
The CNN architecture consists of two sets of three sequential CNNs each
38
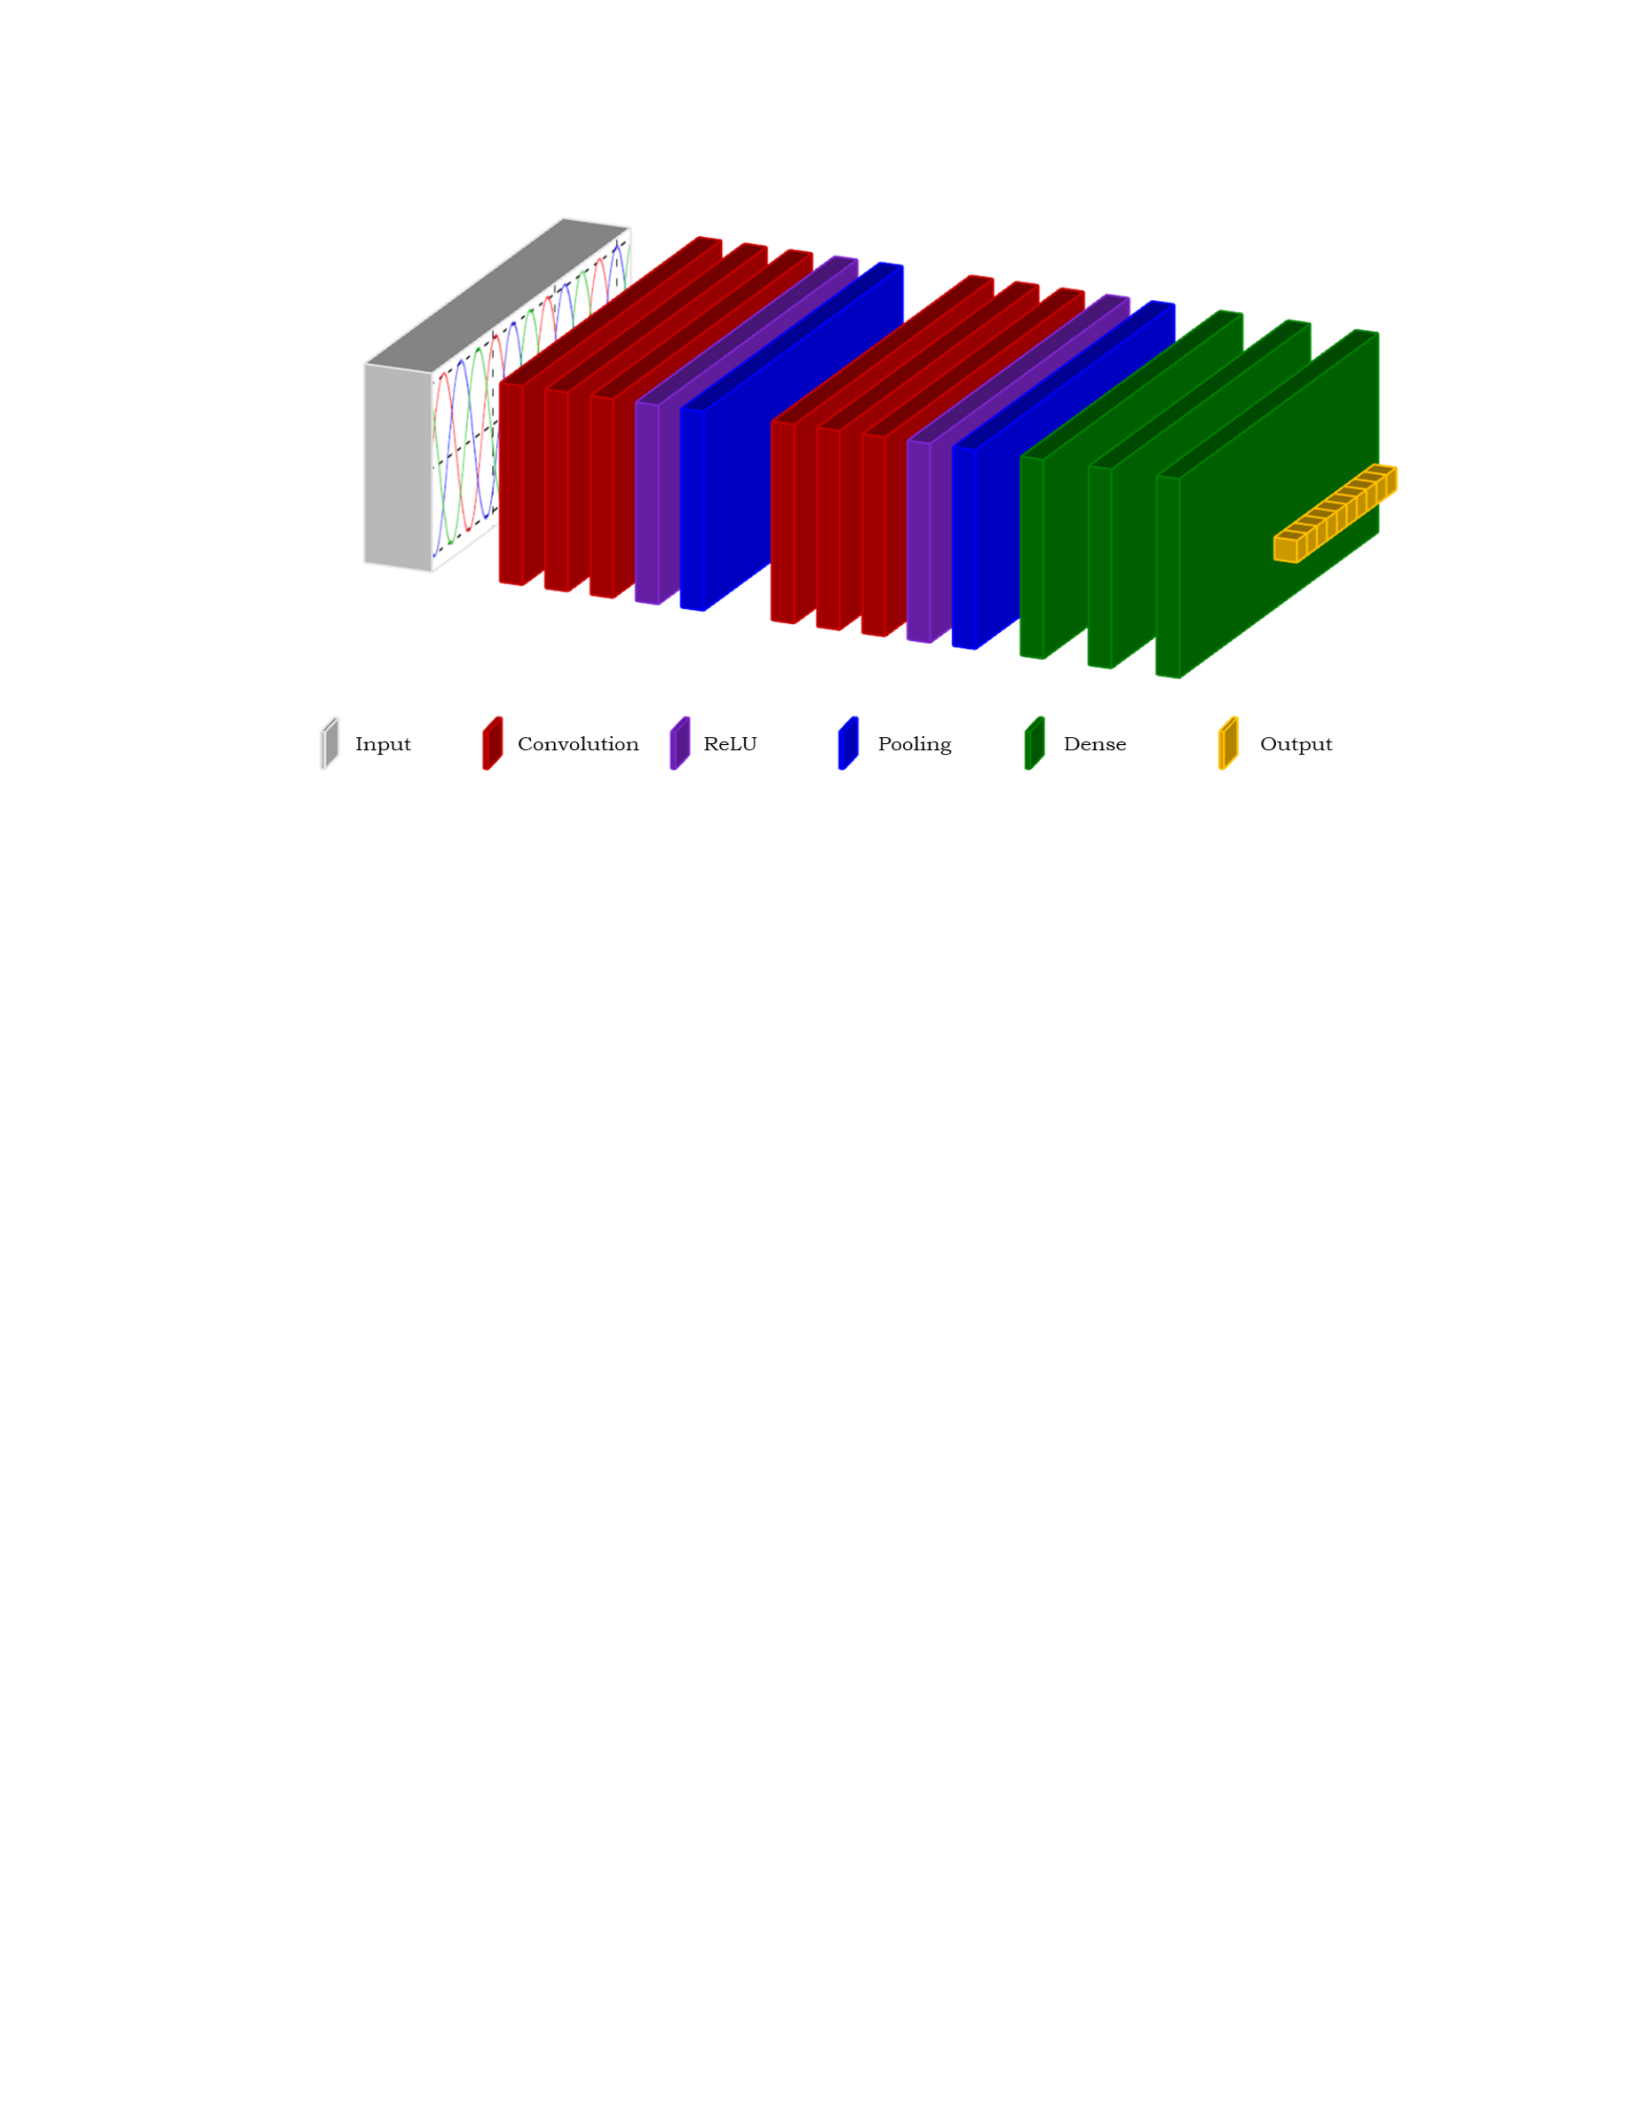
Figure 12. Deep Learning Architecture with two CNNs and three fully connected
linear layers.
having a kernel size of three, a stride of one and a single zero padding. The first
CNN has a output dimension of 16 and the second CNN has an output of 4.
Each CNN is followed by a Rectified Linear Unit (ReLU) activation and a pooling
unit. The network then passes the data through three fully connected layers and a
softmax classifier to create label for the data. The CNN architecture flow is shown
in Figure 12.
While a number of the hyperparameters, such as learning rate and batch size,
were tuned for each model, both of the models used the same network architec-
ture, cross entropy loss function and the ADAM optimization method for the back
propagation algorithm.
3.3.2 Graph Convolutional Neural Network (GCN)
The buses and lines of a power system can easily be thought of as nodes and
edges of a computational graph. In recent years, researcher have generalized the
CNN to work on arbitrarily structured graphs. This generalizing the formulation
of the CNN allows for the algorithm to “see” the underlying structure of the
39
system rather than relying on adjacency in the matrix which is a weakness of the
CNN in this application. In [85], Kipf and Welling present a method to adapt the
traditional CNN to a defined graph structure. Using a multi-layer GCN with the
rule:
H(l+1) =σ˜
D−
1
2˜
A˜
D−
1
2H(l)W(l)(1)
Where, the adjacency matrix of the power system, Ais defined as the bidirec-
tional graph along with each node being connected to itself and INis the identity
matrix. Dis the diagonal node degree matrix of A, Wis the trainable weights
matrix and σis the Rectified Linear Unit (ReLU) activation function.
˜
A=A+IN(2)
Dii =X
j
Aij (3)
In the proposed formulation, adjacency matrix is expanded using a diagonal
block matrix approach to connect all of the features or sensor readings through the
adjacency matrix. Similar to the CNN described above, the GCN formulation uses
two GCN layers with ReLU activation and three fully connected layers followed by
a softmax to classify the fault location. A graphical representation of the algorithm
structure is shown in Figure 13.
3.4 Experiments, Results and Analysis
3.4.1 Power System and Dataset Generation
The Anomaly Detection algorithm was implemented and tested on two IEEE
standard benchmarks. First, the IEEE 9-bus model was chosen for the develop-
ment of the anomaly detection system, shown in Figure 14. Then the application
40
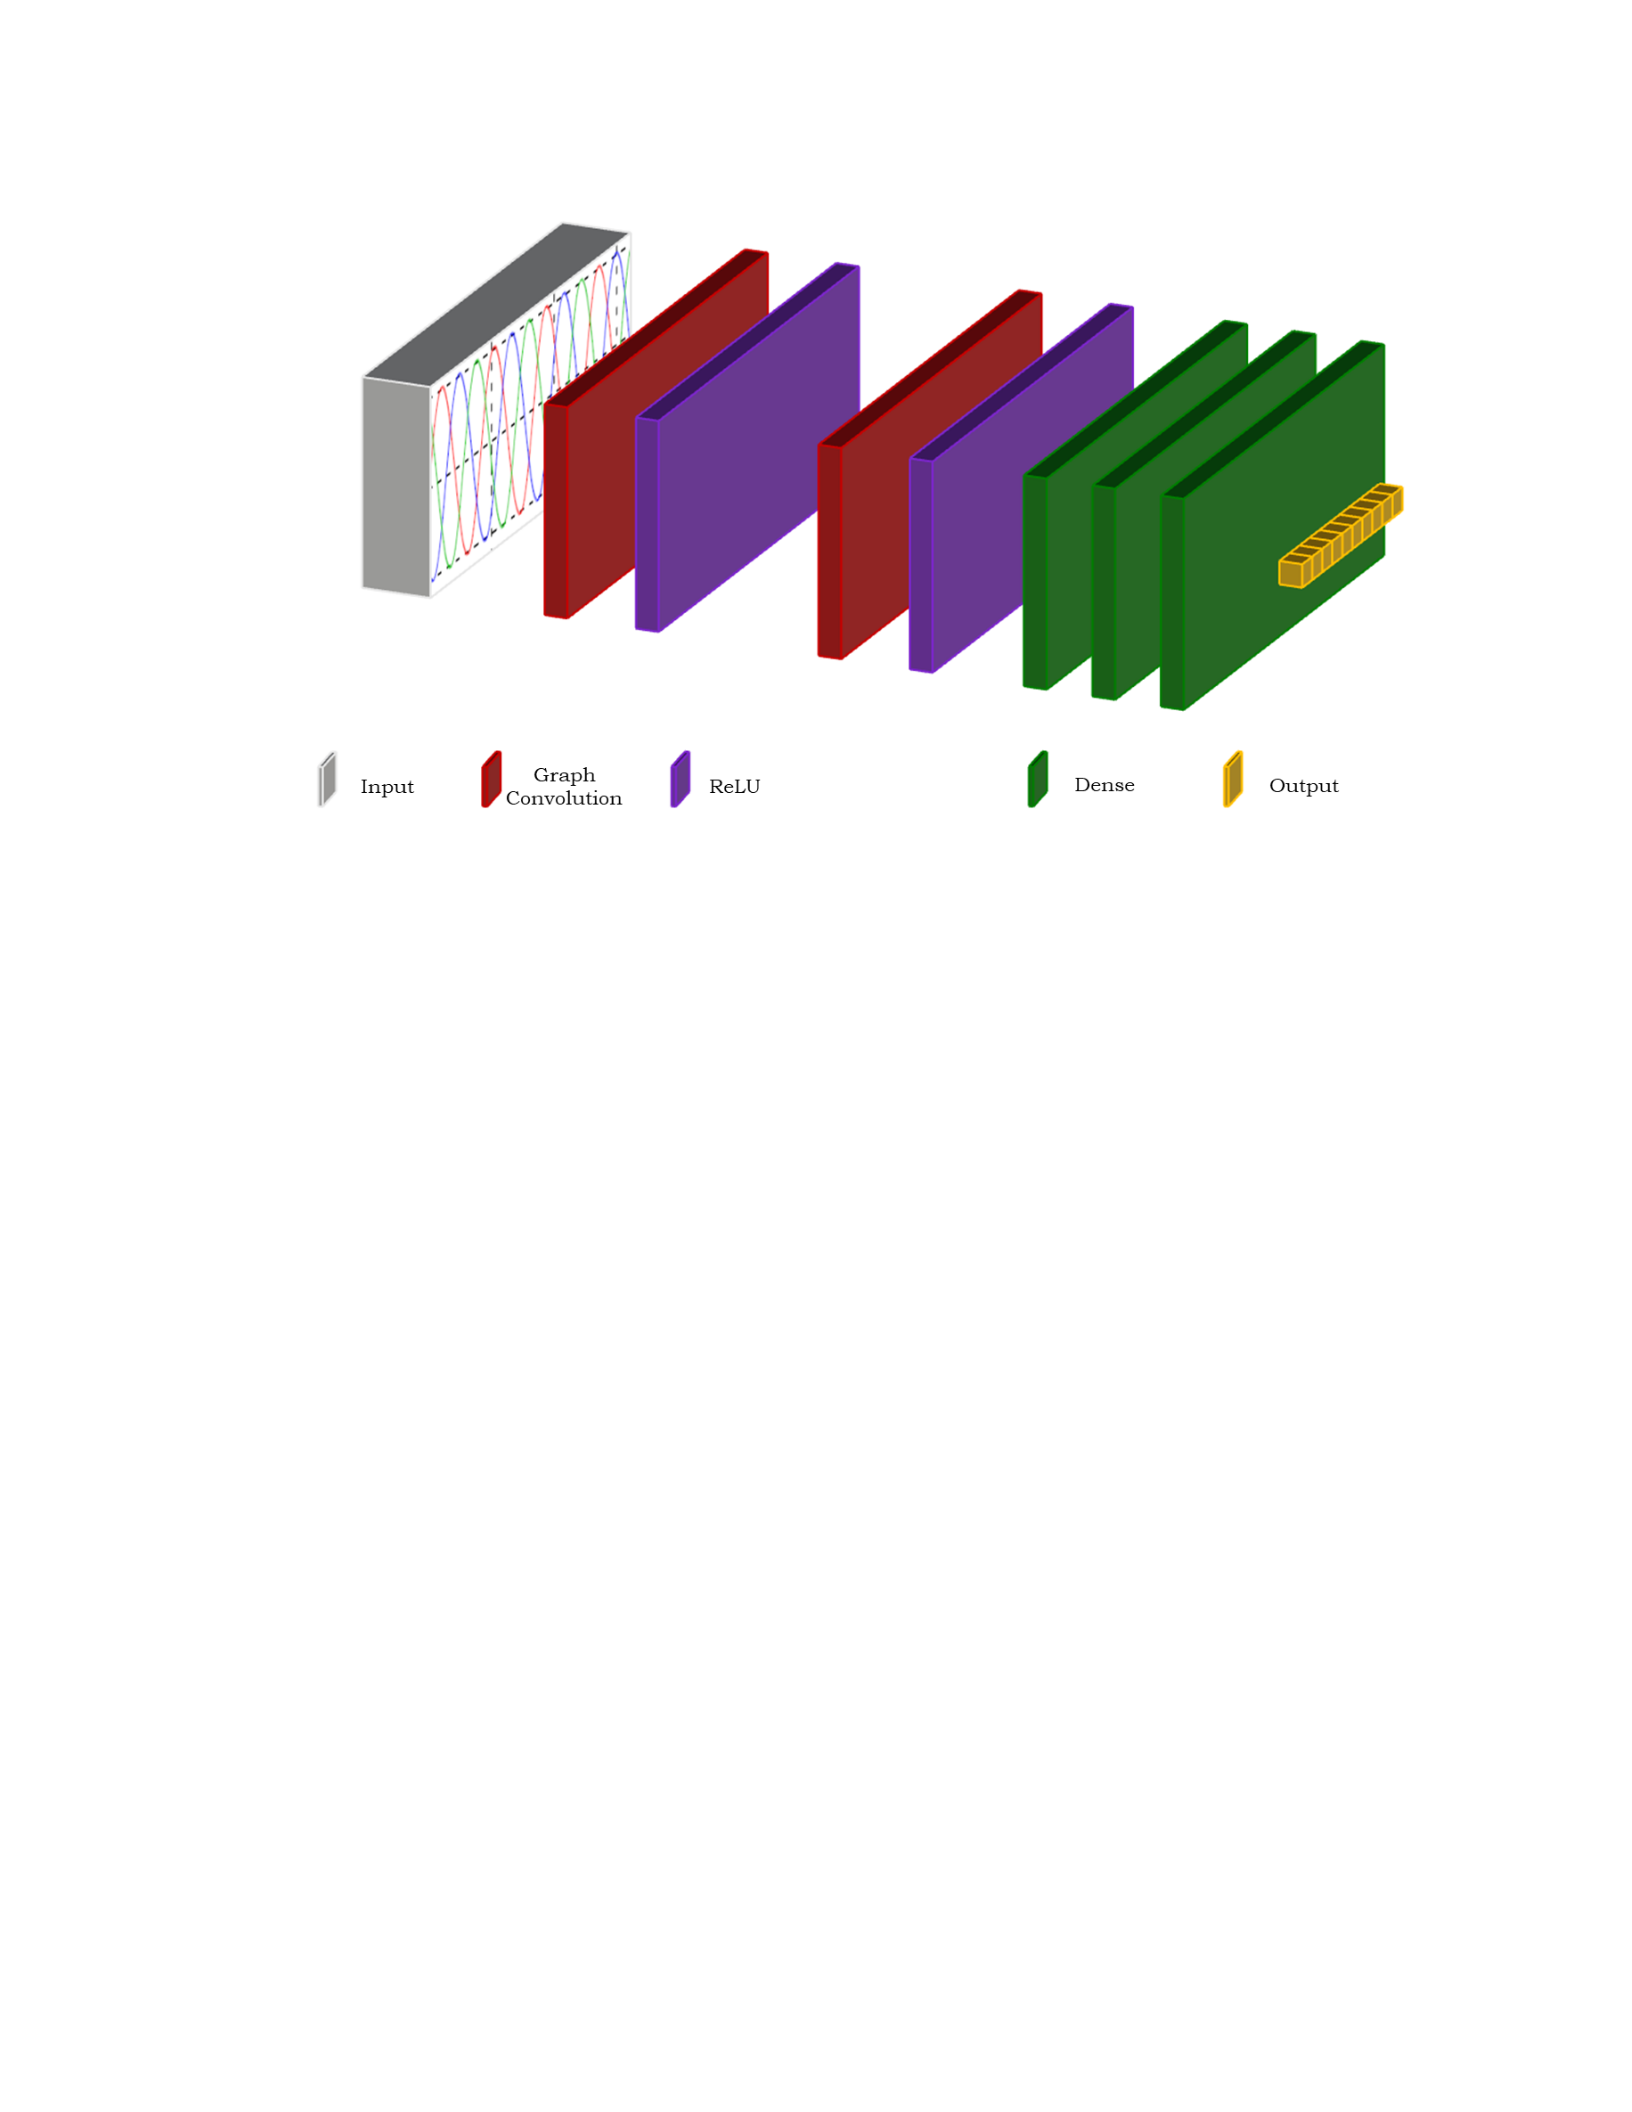
Figure 13. Deep Learning Architecture with two GCN layers and three fully con-
nected linear layers.
of the machine learning algorithm was expanded to the IEEE 39-bus system to
demonstrate the anomaly detection algorithm on a larger and more connected
power system. Both benchmark models, along with the other systems used for
this research, are explained in greater detail in Chapter 6.
Each benchmark system had unique challenges for the algorithm. The IEEE
9-bus is largely circular with three buses that spur off the network and are only
connected through a single other bus. The IEEE 9-bus model consists of three
synchronous machines, three transformers, six transmission lines, three dynamic
loads and nine buses.
Whereas the IEEE 39-Bus model, also known as “the 10-machine New-
England Power System”, contains ten machines, 34 transmission lines, 19 dynamic
loads and 39 three phase buses. The IEEE 39 bus system is much more intercon-
nected with many buses being attached to three or four other buses in the system.
Additionally, this interconnected nature creates a system where neighboring buses
41
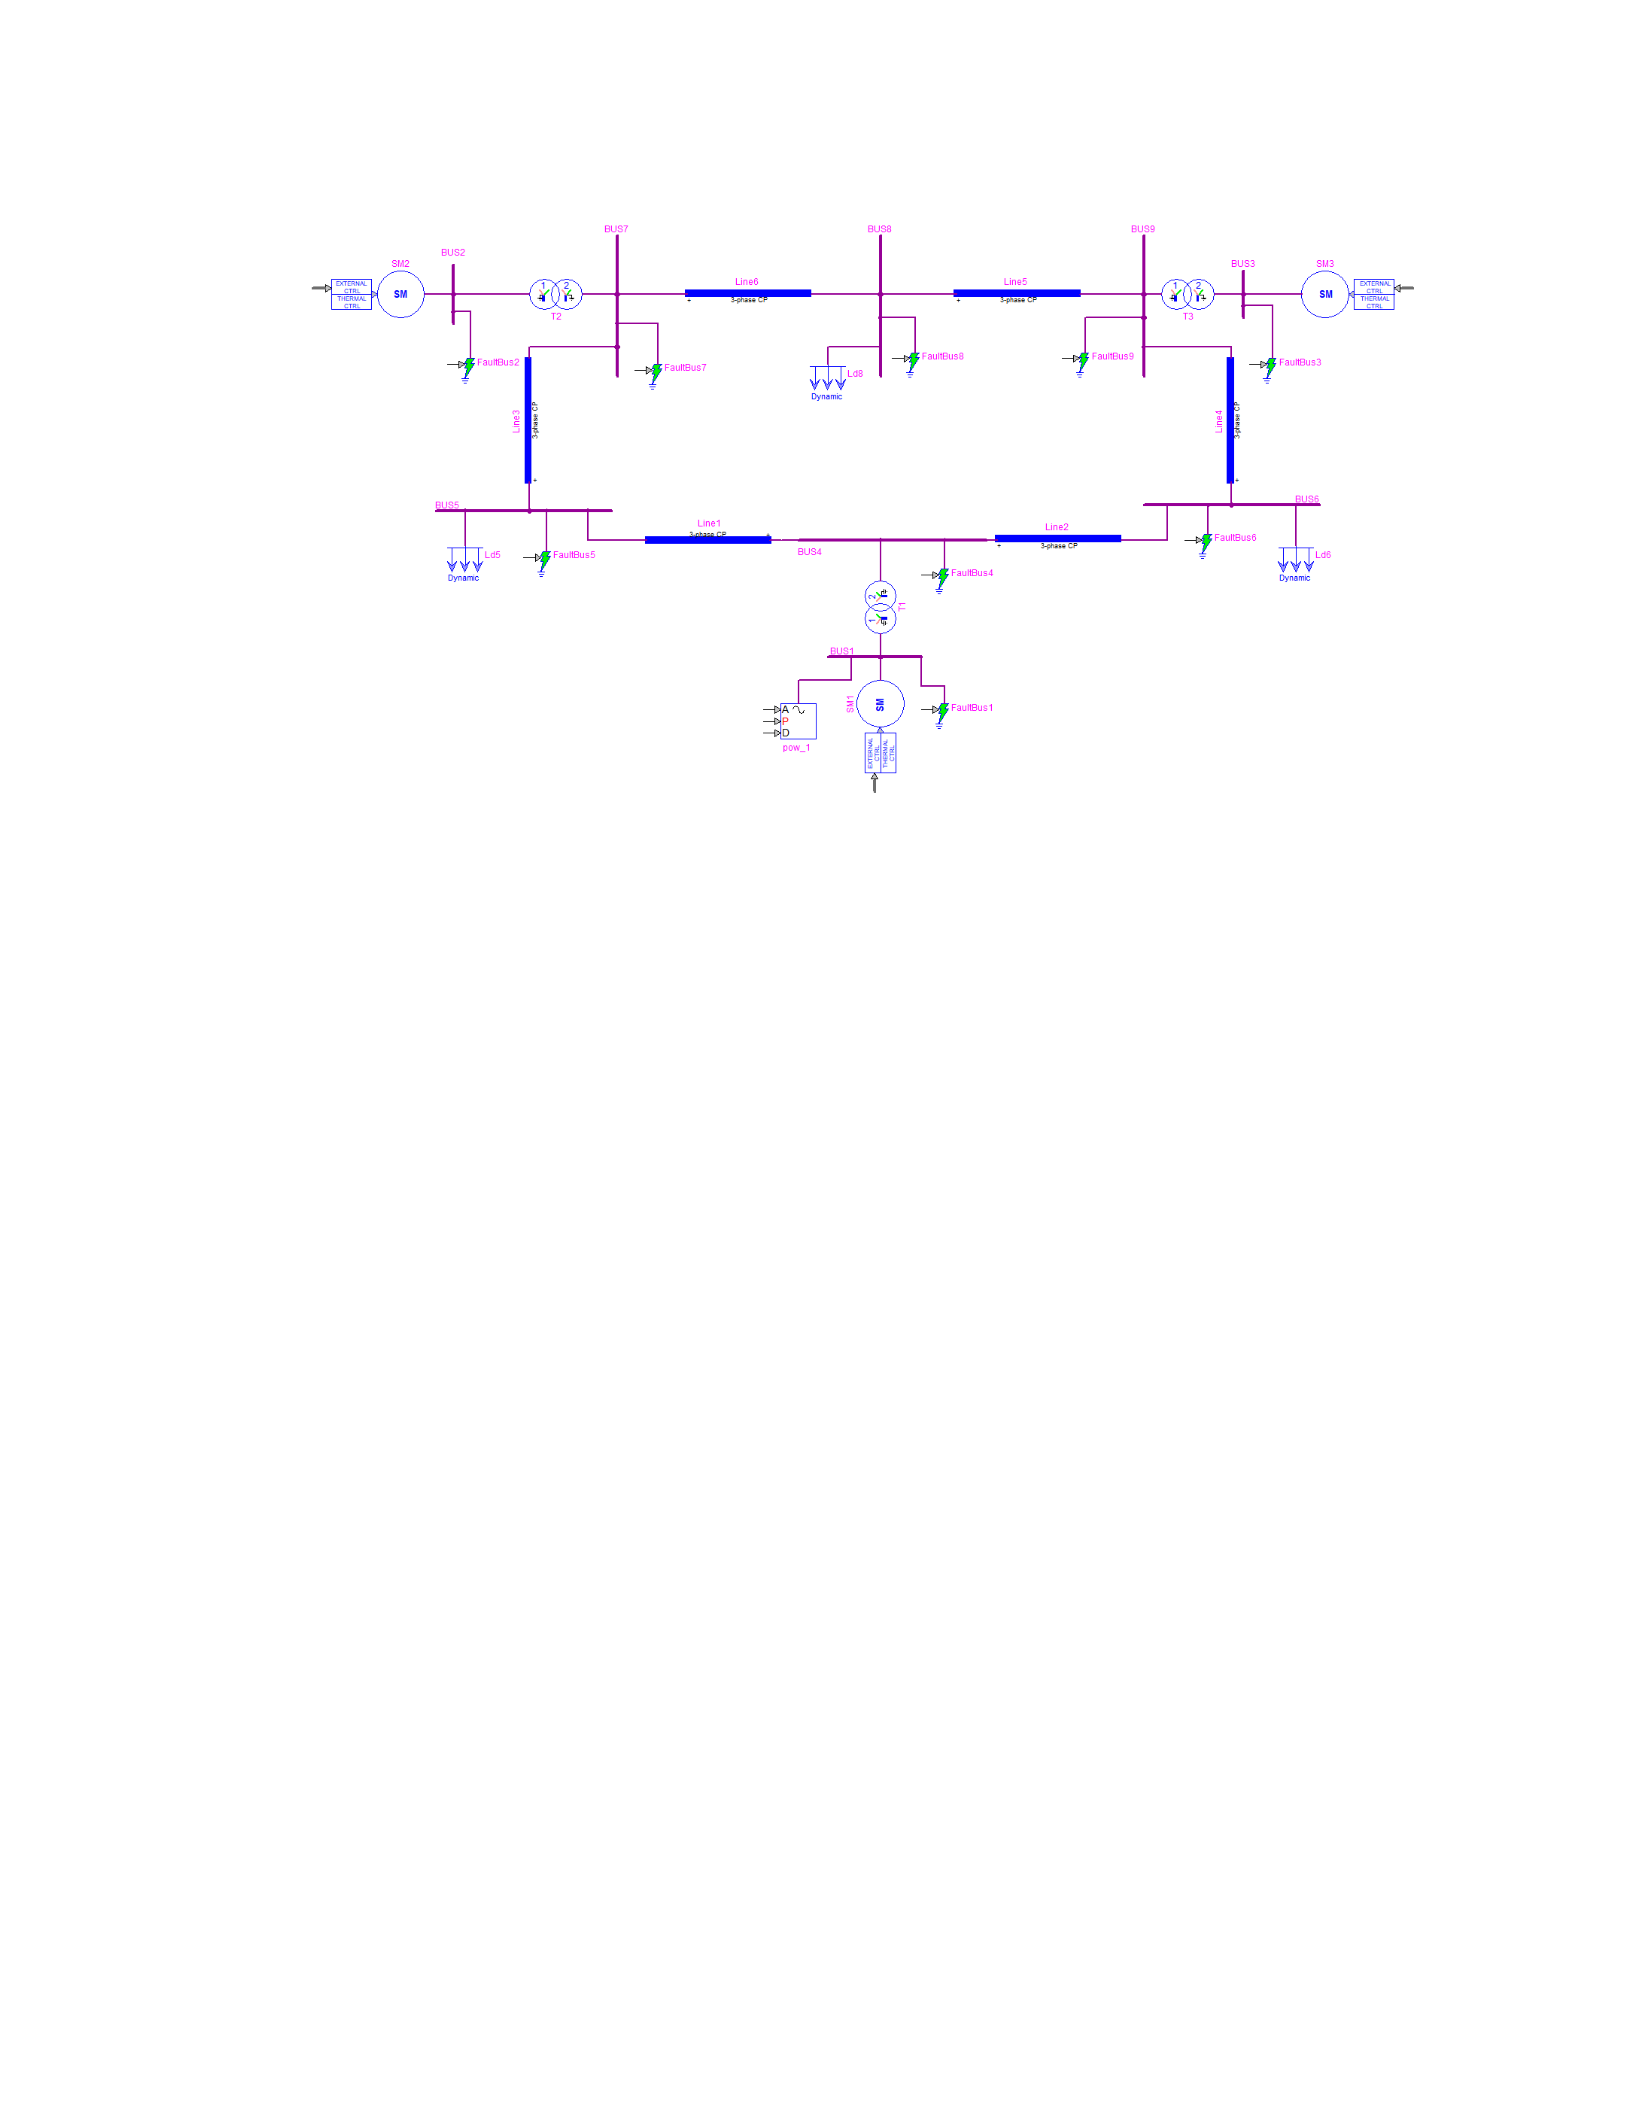
Figure 14. IEEE 9 Bus Model with faults added to every bus.
aren’t necessarily sequentially numbered. While the anomaly detection framework
was applied to the IEEE 9-bus and 39-bus models, the framework is expandable
to larger power systems with only minor adjustments.
The labeled dataset was created using HyperSim, a high fidelity hardware-in-
the loop simulation software developed by OPAL-RT [86]. The dataset includes a
total of 24000 simulations of 100-milliseconds duration. Each simulation contains
either a fault on one of the buses or the system operating a normal condition. The
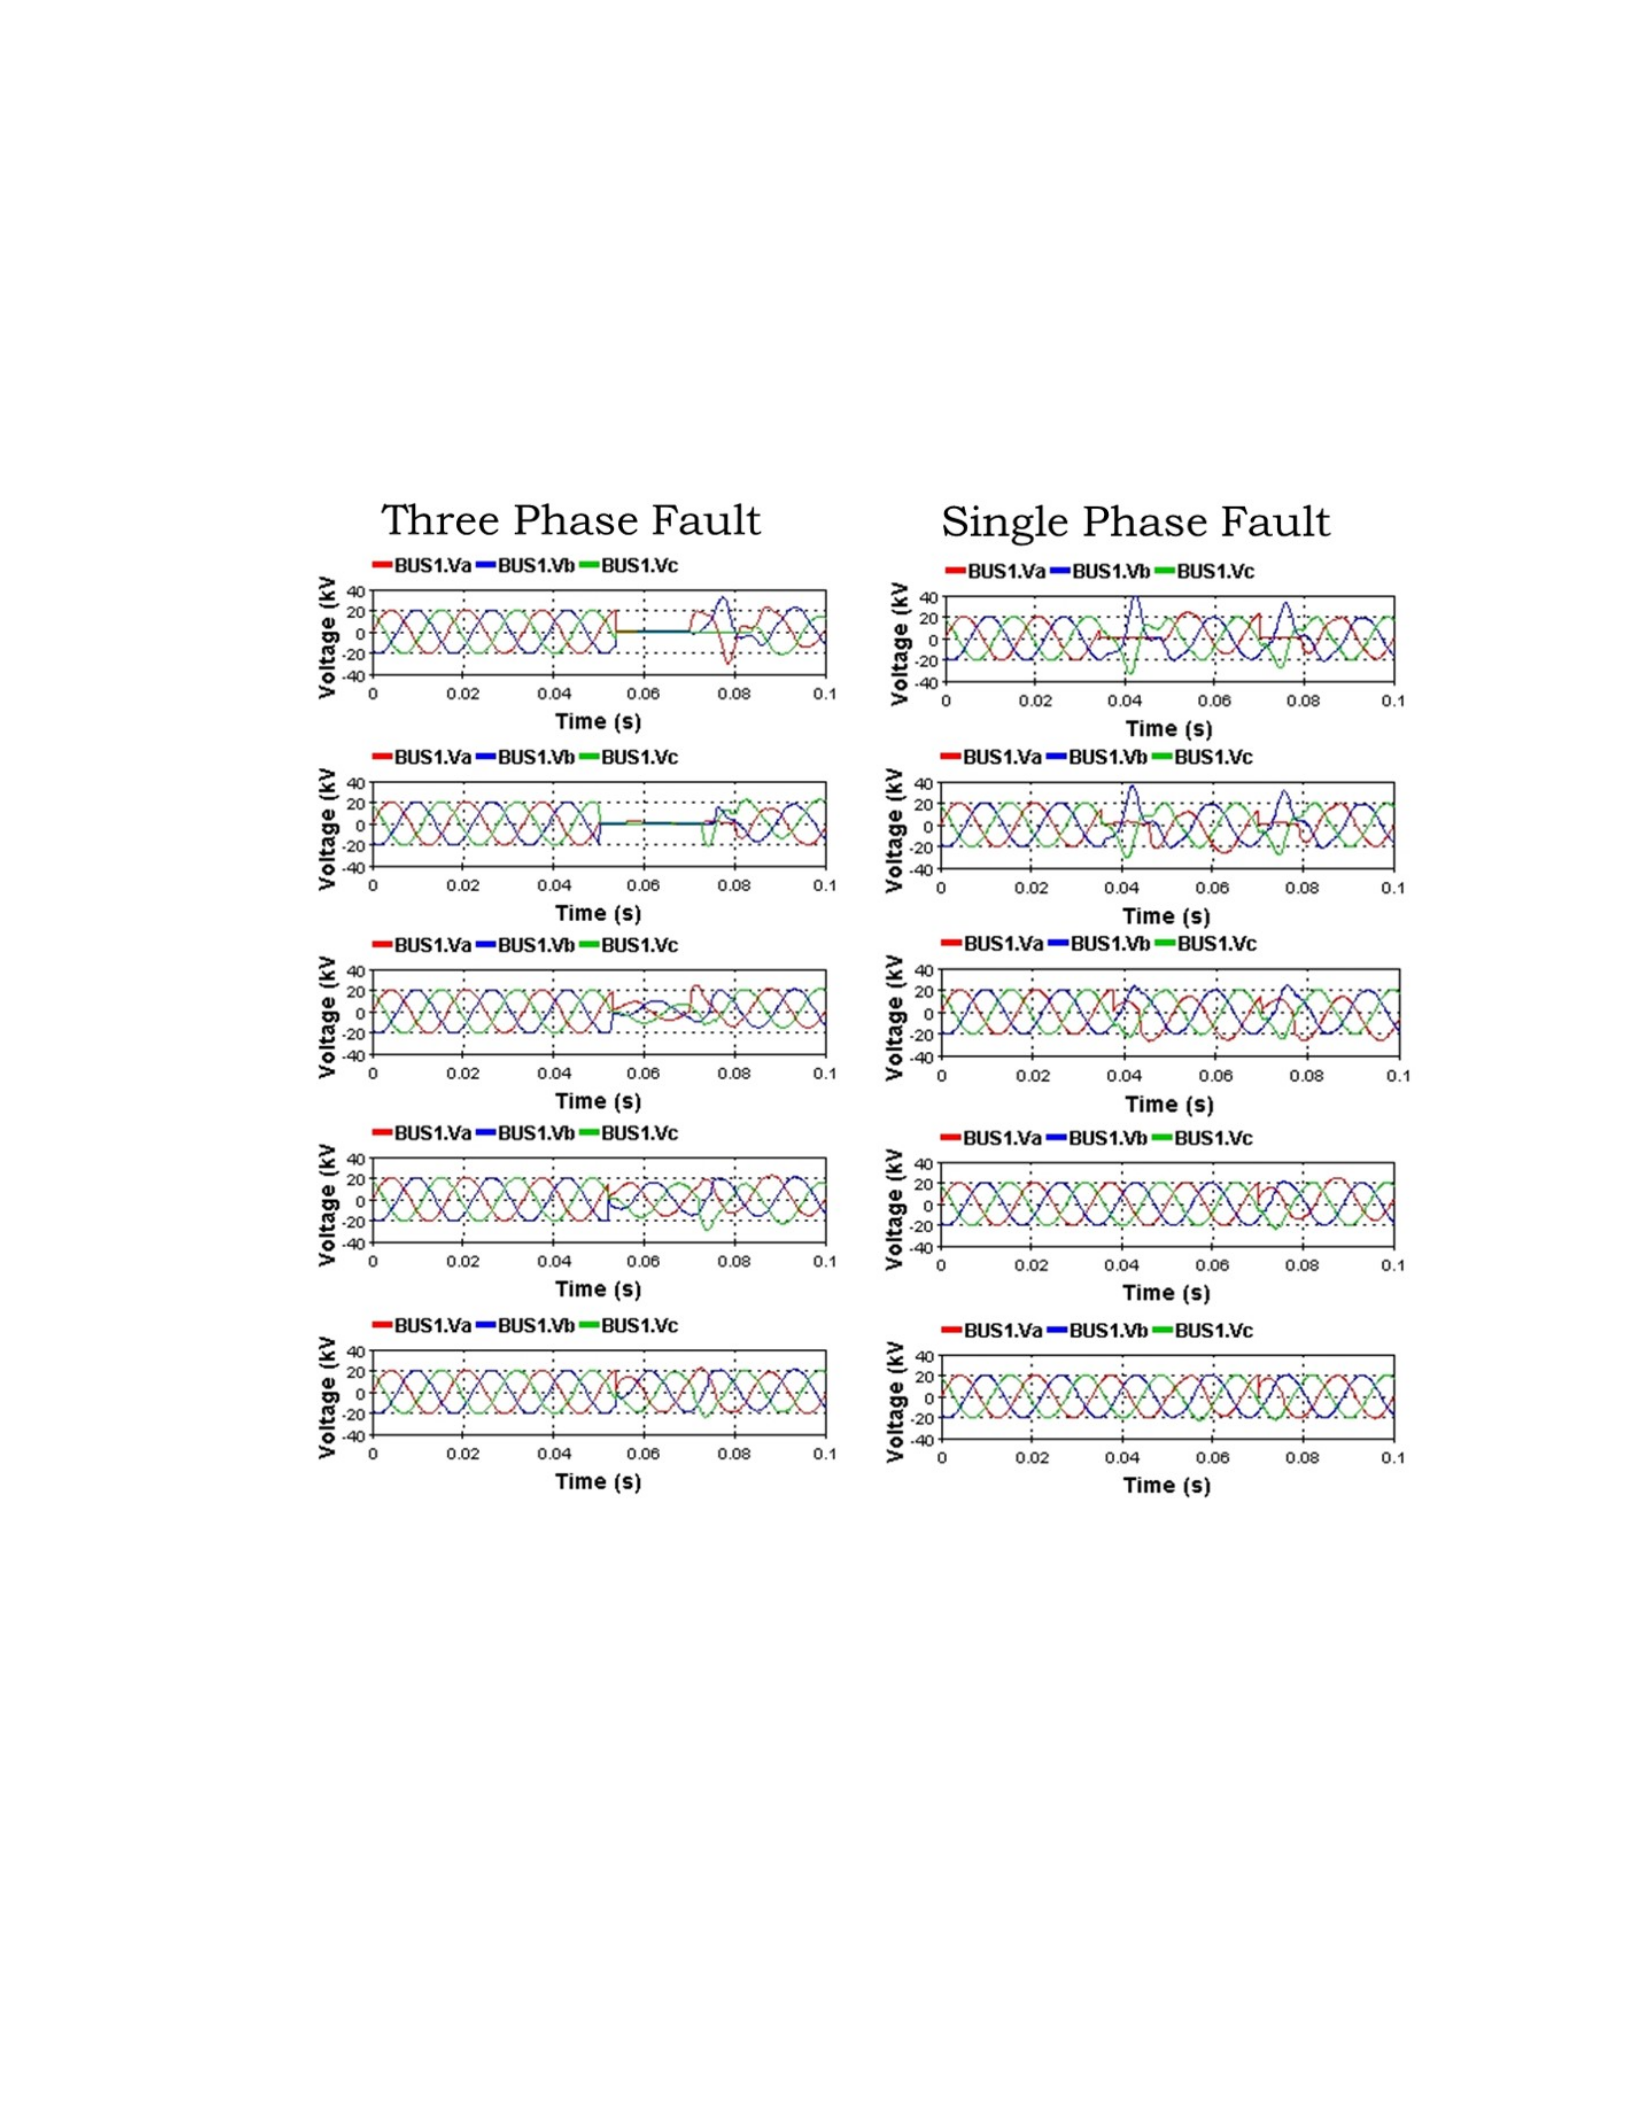
faults are either three phase or a single phase to ground and range from a full fault
with virtually no resistance to ground to faults with 0.01 Ω, 0.1 Ω, 0.25 Ω or 0.5
Ω of resistance to ground, shown in Figure 15. Each simulation takes about 10
seconds to generate and is the data is saved in the industry standard COMTRADE
data format.
The machine learning algorithm uses only the three phase voltage on each
bus for monitoring the network. It is assumed that the data from the distributed
sensor network is complete and is able to synchronized. While the algorithm is
42
trained on a clean dataset, white Gaussian noise was added to the testing dataset
to evaluated the resiliency of the anomaly detection module. The signal to noise
ratios tested were from 80 dB to 20 dB which falls within the range of noise often
seen in PMU data on power systems [87].
Figure 15. Power system simulation output of three phase voltage on Bus 1 with
a three-phase and single phase fault. From the top, plots show faults with a
resistance of 0.001 Ω, 0.01 Ω, 0.1 Ω, 0.25 Ω and 0.5 Ω on the IEEE 9-bus system
3.4.2 Results and Analysis
The anomaly detection CNN algorithm performed well for the detection por-
tion of in this study and was able to identify the existence of a fault with a near
43
perfect accuracy. However, for the classification task, the CNN was able to classify
the location of the fault with an accuracy of nearly 95% for both systems. The
results for each power system is shown in Table 1. It is also important to note the
inference speed on each network. The anomaly detection CNN performed quite
well in this regard as well with the ability to classify a single data window in about
8 milliseconds for the IEEE 9-bus model and about 40 milliseconds for the IEEE
39-Bus model. Achieving an inference time of about two to ten times faster than
real-time will be valuable in the overall Digital Twin environment.
Table 1. Accuracy in Fault Detection and Location Classification.
Power System Fault Detection Location Classification Inference Time
IEEE 9-Bus 100% 94.9% 0.008s
IEEE 39-Bus 99.5% 95.7% 0.041s
While other types of machine learning networks were evaluated, the CNN was
selected to be used due to its superior with regards to classification accuracy as
well as training and inference time. For reference, a Multilayer Perceptron (MLP),
and Long Short Term Memory (LSTM) Recurrent Neural Network (RNN) were
also developed and tested on the IEEE 9-bus system [88]. The MLP had an overall
accuracy on the independent test set of about 85%. Whereas, the CNN network
was able to achieve a 95% accuracy score. The LSTM was not as effective and was
only able to achieve a 57% accuracy score. While the MLP and CNN networks
are well suited for classification tasks the LSTM is more commonly used for time
series prediction and classification.
The high degree of connectivity of the 39-bus system causes some difficulty
for the algorithm to isolate some faults from neighboring buses. Bus 11, which is
centrally located in the system and connected to Bus 6, Bus 10 and Bus 12, is the
most difficult for the algorithm to correctly predict, as shown in Table 2. In the
44
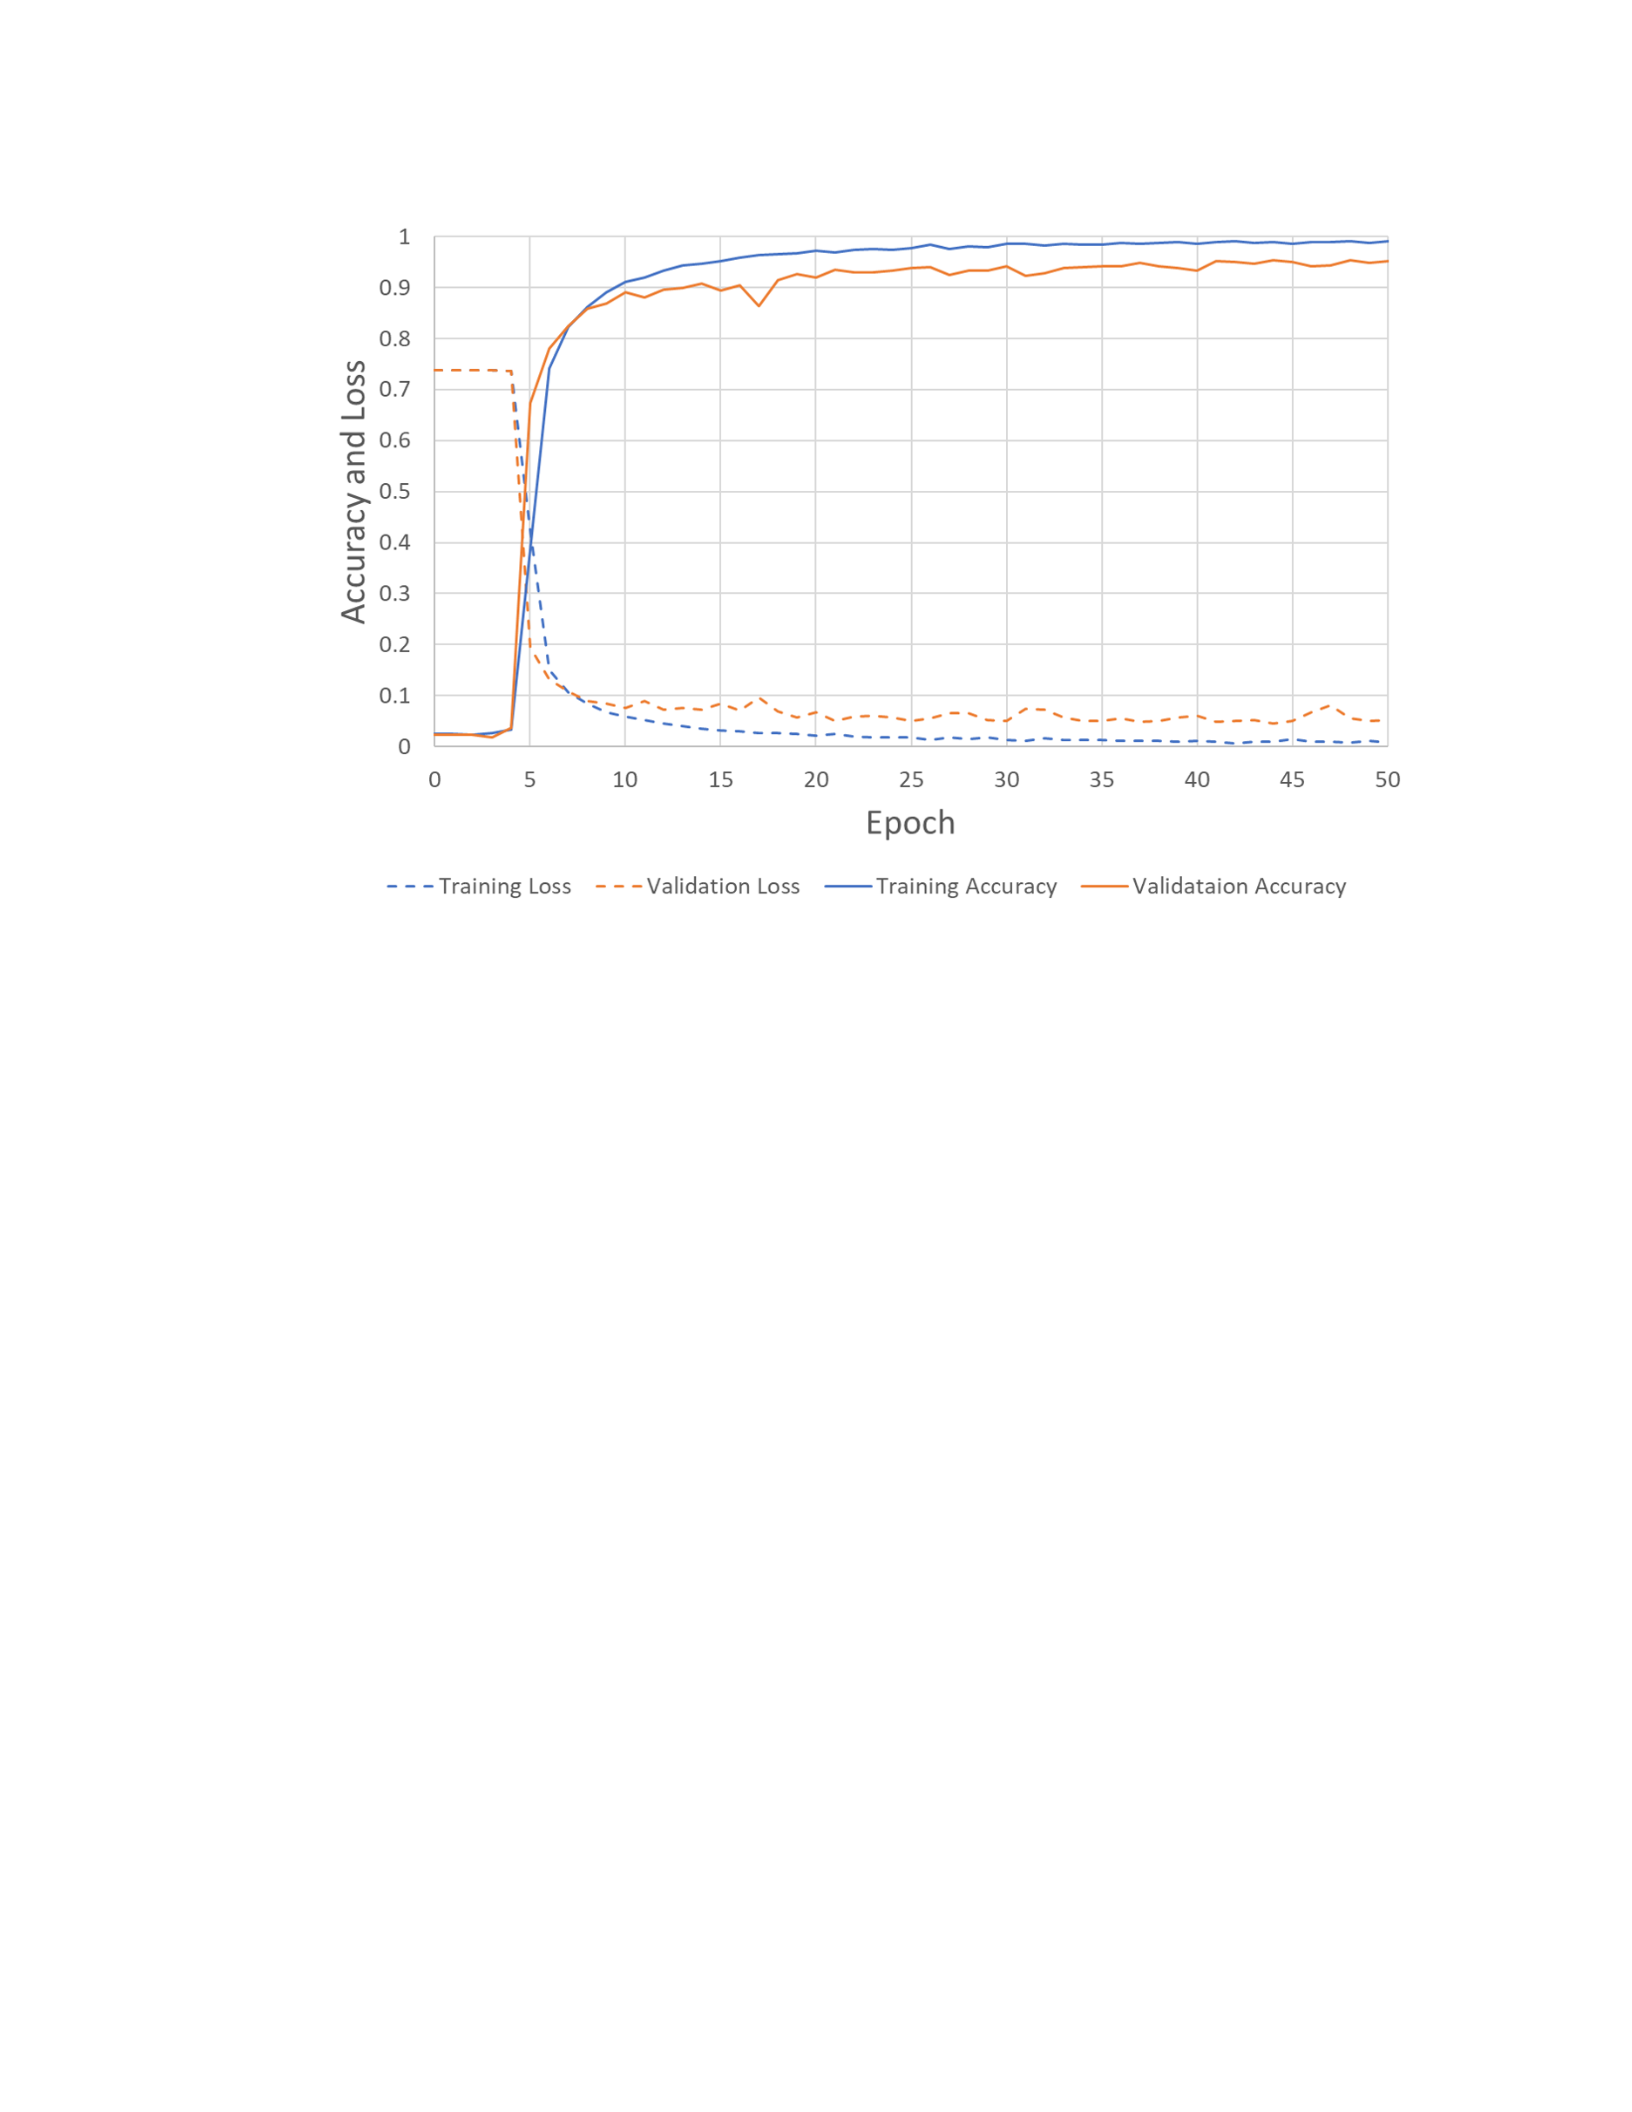
Figure 16. Training Accuracy and Loss for the CNN anomaly detection algorithm.
IEEE 9-Bus system, the most common incorrect classification is for neighboring
buses at the edge of the power system. For example Bus 9 and Bus 3 are often
incorrectly classified as each other. This makes sense because of the proximity in
the network and that the buses at the edge only have a single degree of connection.
Bus 9 is connected to three other buses while bus three is only linked to the network
via a single connection which reduces the amount of information that is available
to the anomaly detection algorithm.
The anomaly detection networks are able to detect and classify the faults on
the power system with a high level of accuracy with up to 30dB of signal noise,
as shown in Table 3. The signal noise, calculated from the standard devation
according to (4), is added to each data channel or bus voltage as a independent
random vector [82] with about 45 dB of noise being common in the power systems
[87].
45
Table 2. Classification Accuracy By Bus Fault
Bus Accuracy Bus Accuracy Bus Accuracy Bus Accuracy
None 99.5% 10 89.3% 20 97.3% 30 96.0%
1 93.0% 11 88.0% 21 99.0% 31 99.3%
2 94.3% 12 98.7% 22 94.0% 32 98.7%
3 96.0% 13 91.3% 23 96.7% 33 95.3%
4 95.0% 14 96.3% 24 97.3% 34 94.3%
5 95.0% 15 96.7% 25 98.3% 35 96.7%
6 89.3% 16 92.0% 26 93.3% 36 95.3%
7 93.7% 17 98.0% 27 98.0% 37 98.7%
8 91.3% 18 98.7% 28 98.0% 38 97.0%
9 98.0% 19 98.0% 29 96.0% 39 97.0%
SNRdB = 20log 1
σ(4)
The accuracy on both networks start to fall off with 20dB of noise due to the
fault being obscured in the signal noise. Additionally, when the high levels of signal
noise is present the algorithms begin to have a larger number of false positives.
Table 3. Classification Accuracy in the Presence of Signal Noise.
Network
Type
Signal to Noise
80 dB 40 dB 30 dB 20 dB
IEEE 9-Bus 94.9% 94.8% 95.2% 86.8%
IEEE 39-Bus 95.7% 95.5% 90.6% 73.1%
3.5 Temporal Graph Convolution Neural Network
While the anomaly detection approach works well in transmission level sys-
tems, it is also applicable to distribution systems where the likelihood of outage
is greater. In the distribution system, the electricity is stepped down to a lower
voltage and the power is provided to residential or business locations. The use of
46
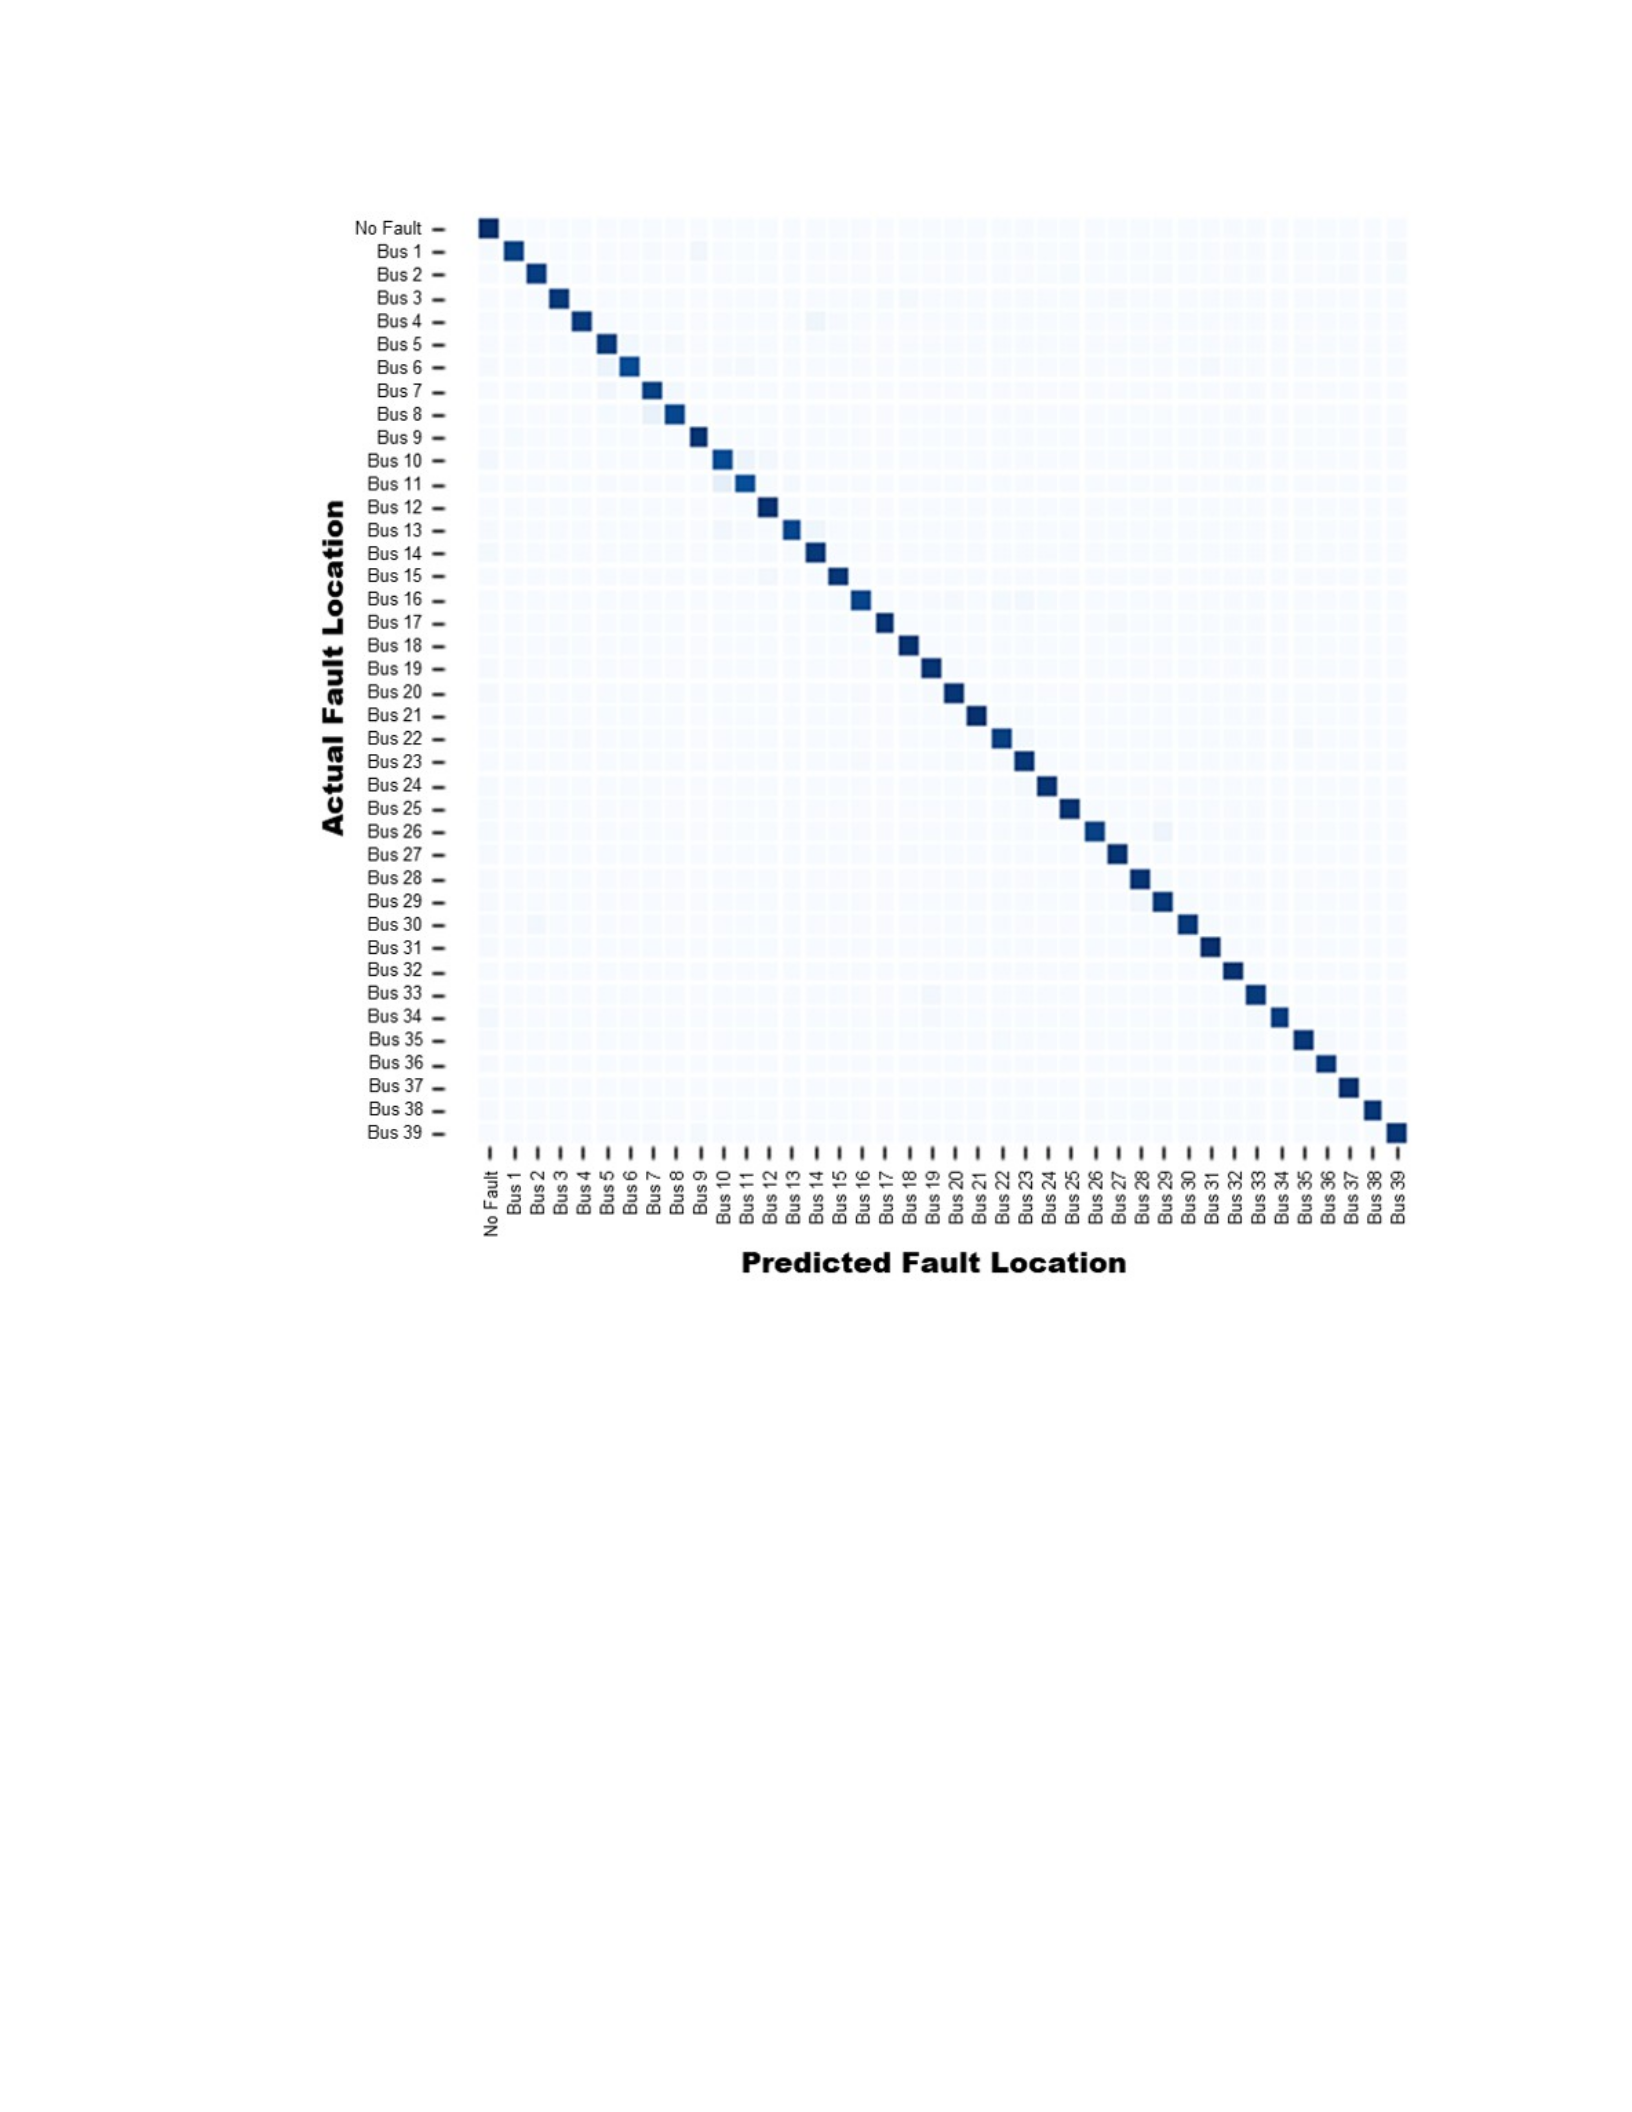
Figure 17. Confusion Matrix for the CNN Algorithm on the IEEE 39-Bus System
deep learning graph convolutional neural networks to distribution systems is an
active research area and has yielded positive results. In [89], the authors propose
a Deep Graph Convolutional Network to locate a fault in a distribution system.
The authors used OpenDSS, an open-source electric power distribution system
simulator, to simulate the bus faults in the distribution system. In this work, the
authors tested their GCN algorithm on two distribution systems, the IEEE 37-bus
benchmark and the IEEE 123-bus benchmark. The authors were able to create an
47

algorithm that predicted the location of the faulted bus with an accuracy of 97%
in both systems. However, there are a few key differences and limitations in this
study:
1. The dataset only included faulted systems. Therefore, the algorithm was not
required to detect if there was a fault present in the system.
2. The OpenDSS solver is a steady state solver and does not include the tran-
sients present in the real power system. Therefore, the faulted system is in a
steady state and does not have a temporial component. In this implementa-
tion, the fault would not permeate through the power system and all system
dynamics would be ignored by the OpenDSS solver. This simplifies the im-
plementation of the GCN because the algorithm does not have to account
for time in the formulation.
3. Both the IEEE 37-bus and IEEE 123-bus distribution systems have radial
configurations. In these radial distribution systems, there is one path for the
power to flow to each bus. Therefore, in this configuration, the impact of the
fault can be identified to be at the first bus to show signs of the fault.
In [90], the authors propose a spatiotemporal graph convolutional network
(STGCN) to analyze bus faults using time-domain data. The study uses MAT-
LAB/Simulink to generate the raw voltage data sampled at 1000 Hz. The authors
used two distribution systems, IEEE 33-bus and the IEEE 37-bus benchmark sys-
tems, to test the algorithm. Like the research discussed above, both distribution
system has a radial structure with single power flow paths. Adding the spatiotem-
poral element to the GCN vastly improves the results to nearly 100% accuracy.
However, there are a couple noteworthy differences to the implementation pre-
sented in this dissertation:
48

1. The fault occurrence is at a fixed time in the simulation, t = 0s, and, therefore
all of the data contains information about the fault. The algorithm was not
required to determine the presence of a fault but rather assumed that a fault
was present in all data. Additionally, the bus fault is not cleared in the
simulation so the system would likely reach steady state results similar to
the results presented in [89]
2. The algorithm uses the raw current and voltage readings at every bus as
features in the algorithm. The CNN and GCN presented only uses the raw
voltage but could benefit from the additional information contained in the
current data.
3. The radial distribution network could allow for the isolation of the fault due
to the singular path of the power flow. The paper does present results on a
modified mesh topology but it is unclear if that is the power system topology
or the computational graph.
4. For each specific bus fault, the same time fault history data is used. The
training and test samples are created by down sampling the data for a dif-
ferent window of time. By comparison, the high fidelity real-time simulators
allow us to generate fully independent data samples for both the training
and testing datasets.
The GCN presented in this section is able to process spacial and temporal
data from the high-fidelity real-time simulator. Similar to the works above, the
study assumes full observably of the system and full access to the raw µPMU data
stream. The algorithm was tested on the IEEE 39-bus benchmark and compared
to the previous results of the anomaly detection CNN.
The GCN anomaly detect algorithm is able to perform well, when the GCN
49
is provided PMU data for each bus in the system, Figure 18. When the GCN
algorithm is run on the same dataset used in the previous CNN studies, the GCN
is able to provide superior results than the published CNN algorithm in location
accuracy, 93% vs 90%, respectively, shown in Table 4
Table 4. Comparison of Classification Accuracy of CNN and GCN.
Network
Type
Signal to Noise
80 dB 40 dB 30 dB 20 dB
GCN 93.7% 93.1% 93.3% 93.6%
CNN 95.7% 95.5% 90.6% 73.1%
The GCN algorithm is able to better capture the high connectivity of the
IEEE 39-bus model and unlike the CNN, the GCN algorithm is not affected by
the signal noise in the system.
However, in many power systems, it is not practical or possible to have PMU
measurement devices on every bus. Using the optimal buses found in [10], the
model is reduced to contain PMU voltage data on only eight buses. The buses
that were selected are Bus 3, 8, 12, 16, 20, 23, 25, and 29. While reducing the
system into grouped regions would allow the algorithm to locate the fault to the
closest bus with a sensor, in practice this would also introduce a large search radius
for the operator. Instead, the algorithm was trained using the reduced sensor array
installed on the power system. In both cases, the raw three-phase data from the
PMU was used. However, the sensor data from the buses without PMU sensors
was removed from the dataset. This allowed the algorithm to maintain the graph
structure of the system to help determine the relationships between the buses.
As expected, when the number of PMUs is reduced to eight buses, the reduced
information on the system also reduces the accuracy of the model. The training
and validation results are shown in Figure 20. The GCN algorithm is able to
correctly identify the faulted bus with a 70% accuracy. However, the one-hop
50
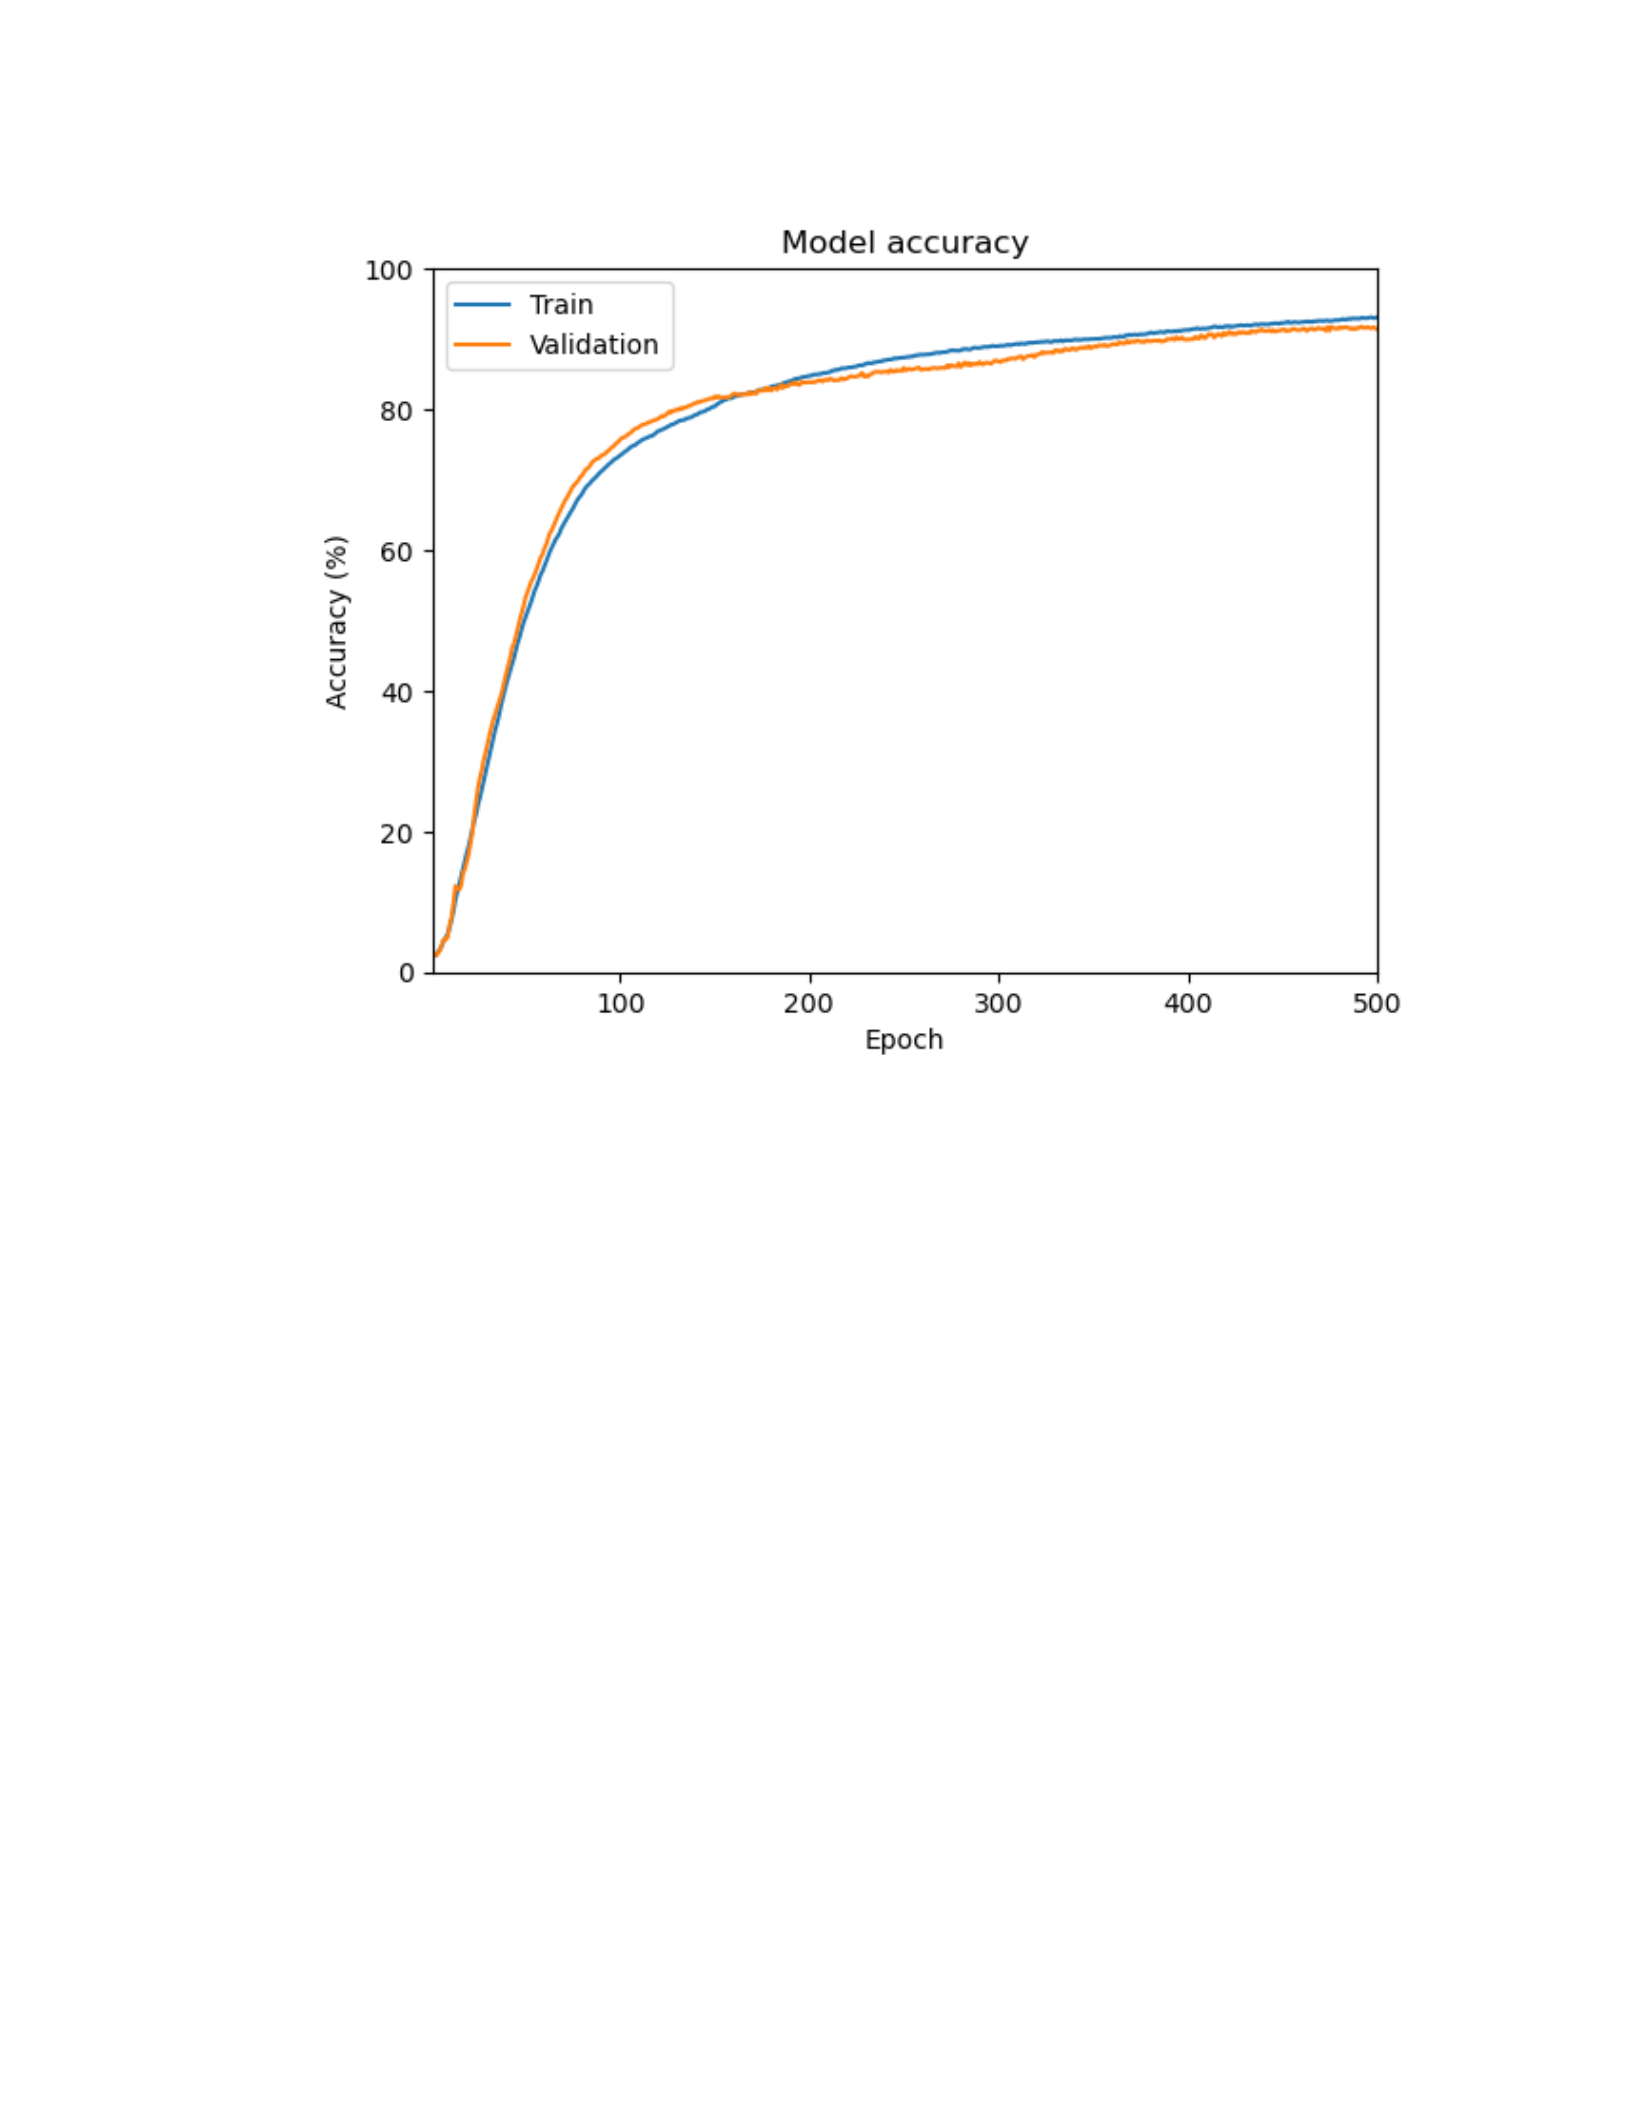
Figure 18. Accuracy of Anomaly Detection GCN with a PMU on Each Bus
and two-hop accuracy is significantly higher so the algorithm is able to correctly
identify the region with the underlying fault.
Looking deeper into the results, the accuracy issues with the algorithm is
largely due to confusion with highly connected buses. Figure 21 shows the confu-
sion matrix for the algorithm running with data from eight PMUs. While the GCN
is able to isolate the fault to a region, it is unable to discern the exact location of
the fault when the buses are highly connected.
The high connectivity buses, Buses 5-8 and Buses 10-13, show high levels of
confusion, shown in Figure 22. While many of the errors are still only off by a
single degree, there is room for improvement of the algorithm. In Chapter 5, the
addition of digital twin layers into the anomaly detection algorithm to improve the
51
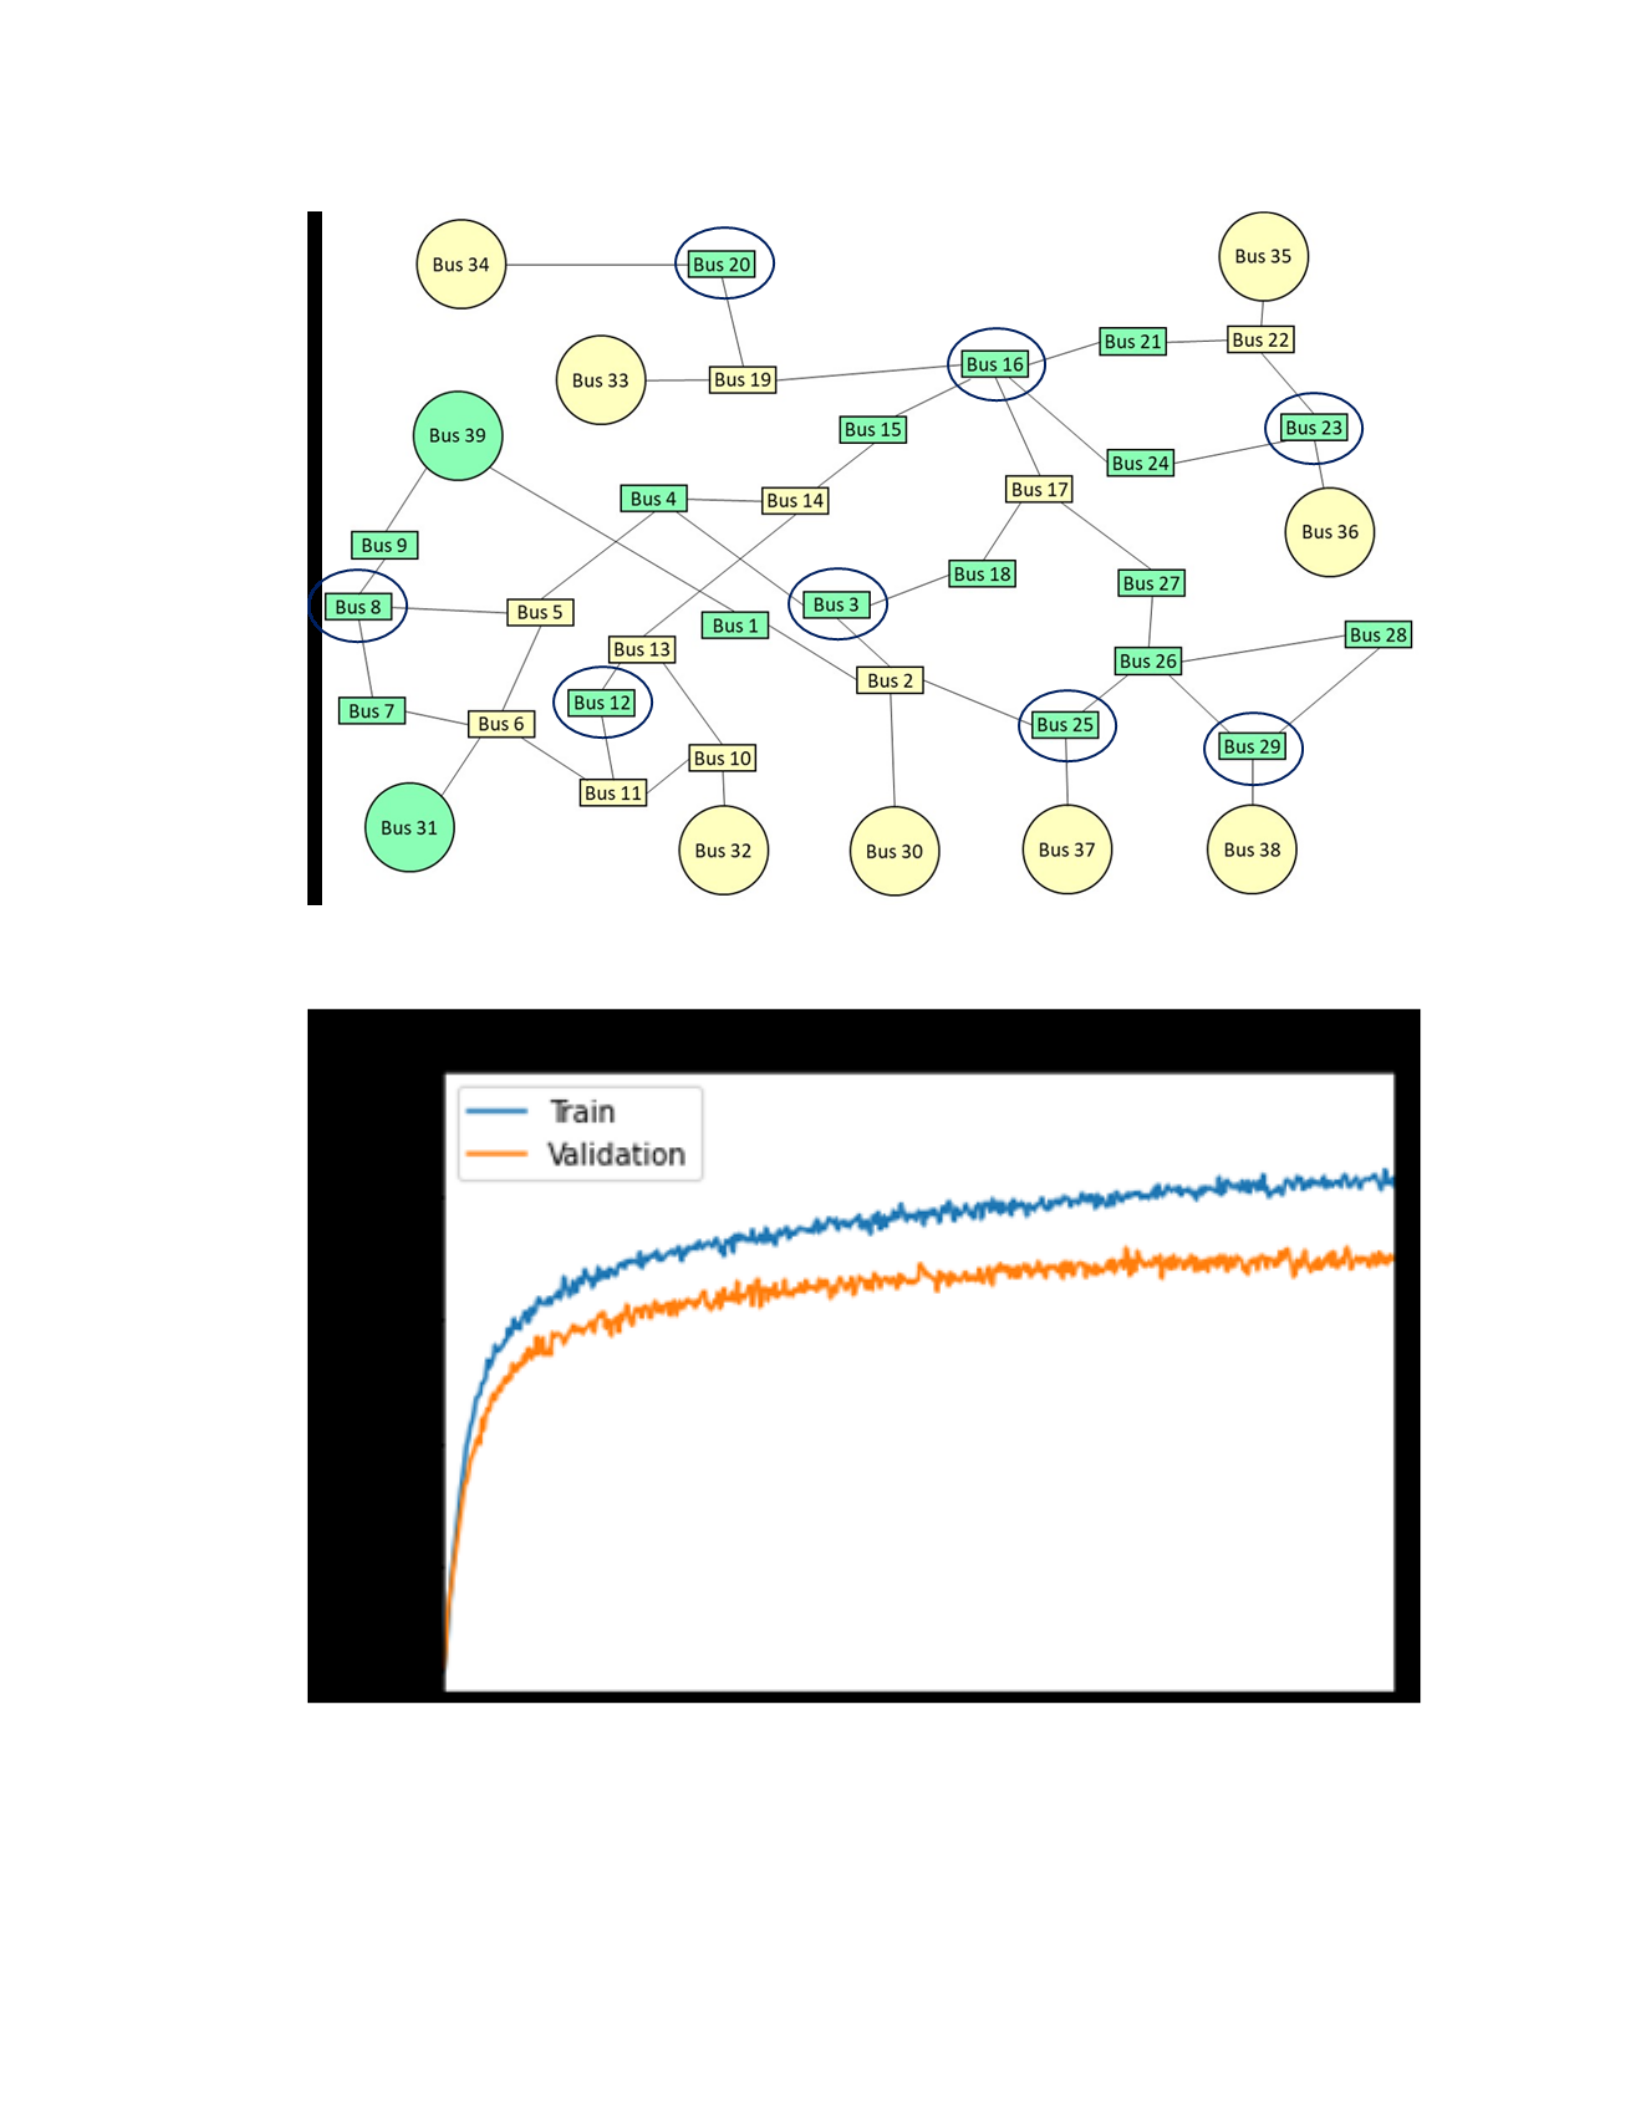
Figure 19. PMU Bus Locations for the System with Eight PMUs
Figure 20. Accuracy of Anomaly Detection GCN with Data from Eight PMUs
52
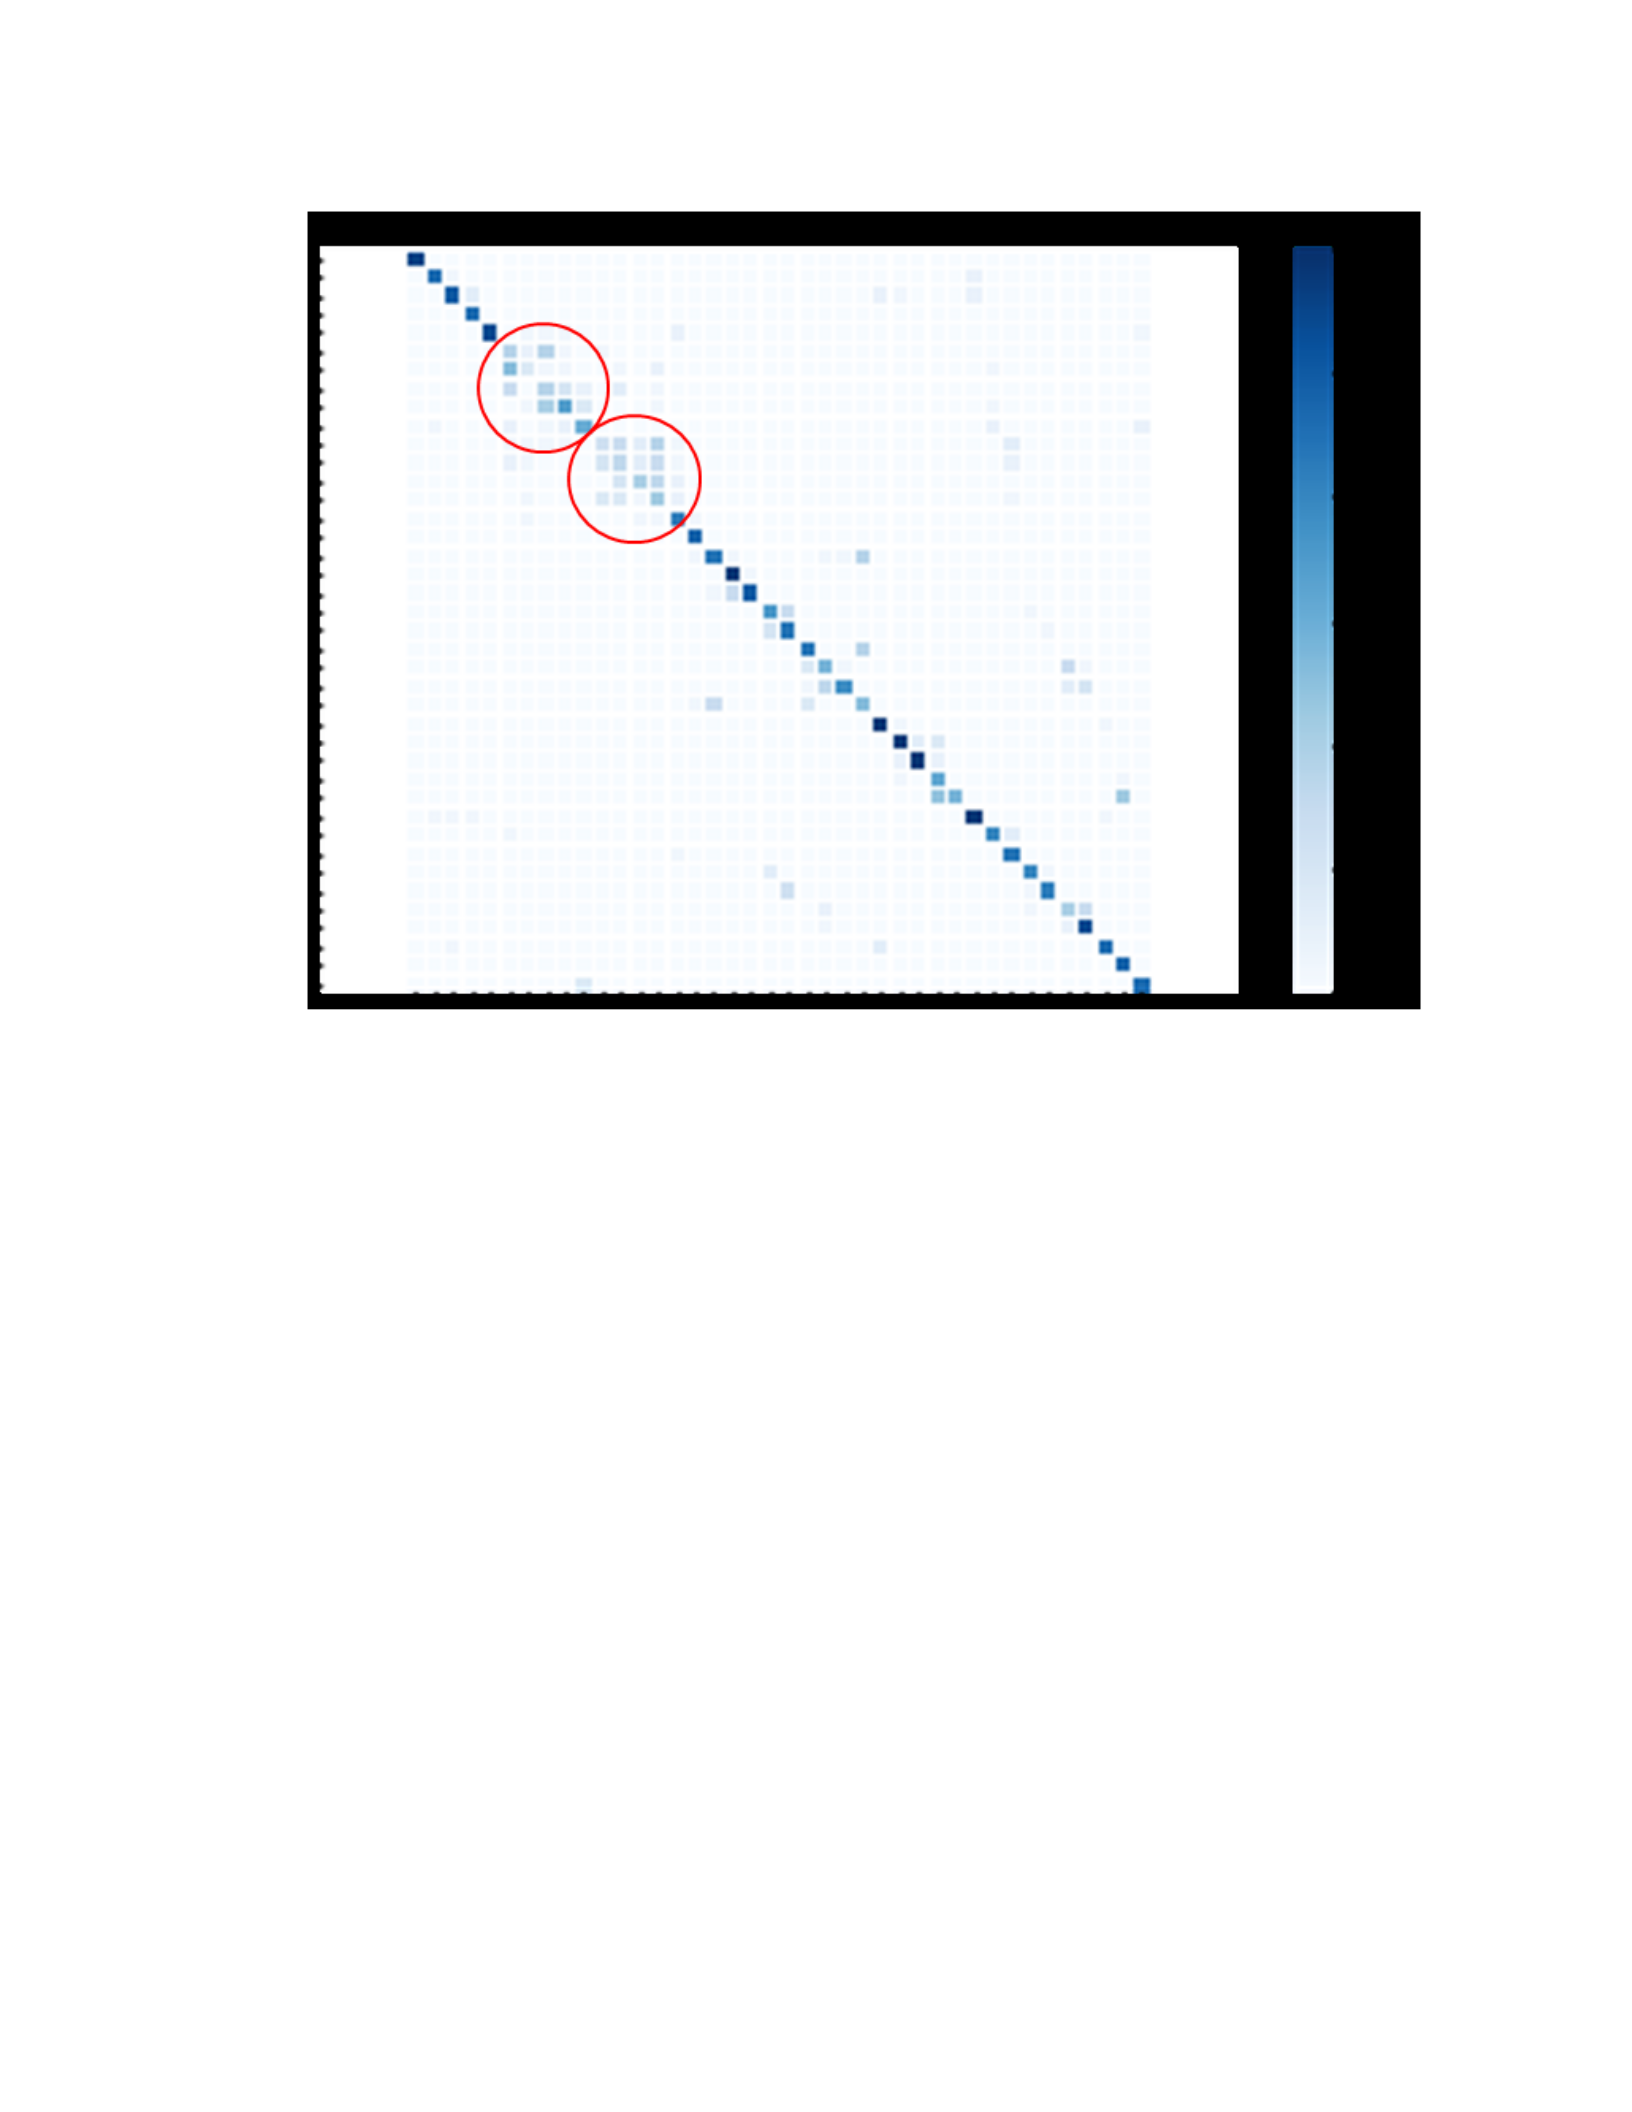
Figure 21. Confusion Matrix of Anomaly Detection Algorithm with Eight PMUs
location classification results is investigated.
3.6 Chapter Summary
This work presents a methodology for developing a deep learning architecture
for Anomaly Detection in a Smart Grid. By implementing a CNN to analyze the
distributed power system bus voltage data, the anomaly detection architecture was
able to correctly detect faults lasting only fractions of a second in a distributed
power system. Additionally, the CNN was able to locate the power fault within
the system with a high accuracy.
The deep learning algorithms show significant promise in the detection and
location of power system faults. Using these methods, along side traditional tech-
niques, can improve the performance and reduce the cost of power distribution. As
more advanced and complex energy resources continue to be integrated into the
53
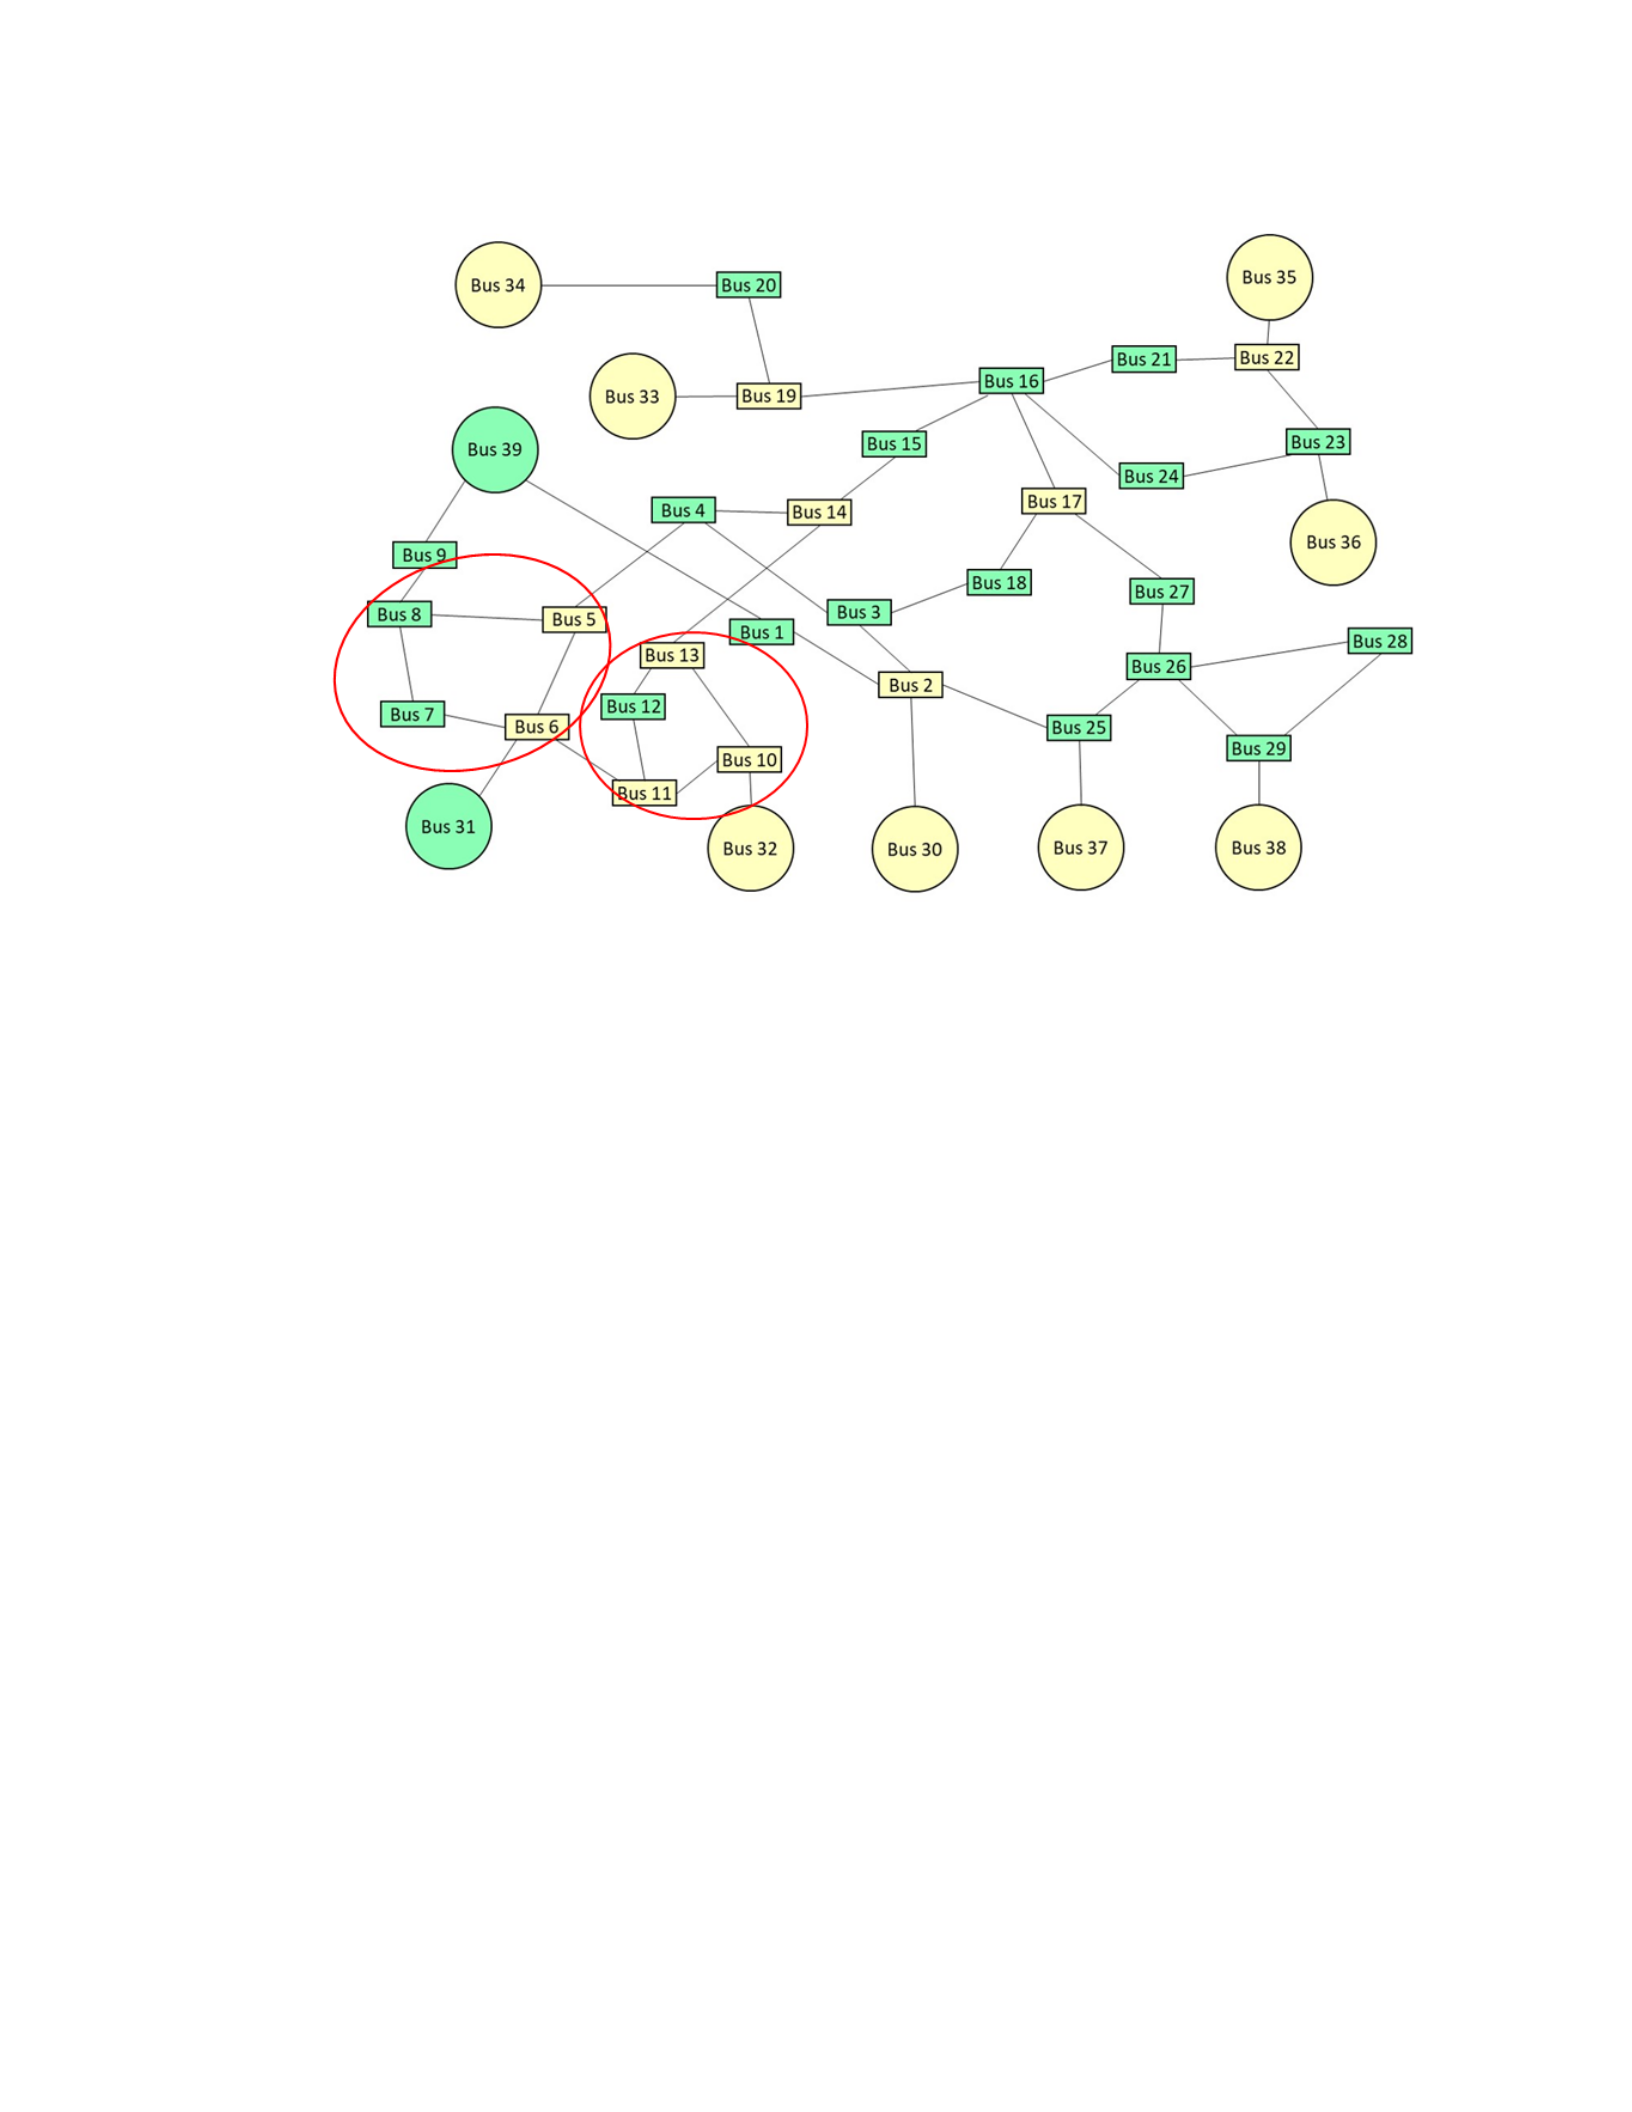
Figure 22. Commonly Incorrectly Classified Buses in GCN Algorithm
smart grid, the importance of high fidelity monitoring and control also increases.
The anomaly detection algorithm using the CNN deep neural network was able to
classify the faults with over a 95% accuracy.
The long term goal is to have the Digital Twin with the anomaly detection
CNN running along side of the physical smart grid. Since the detection algorithm
would then be required to run in real-time, the time required to train the model and
more importantly run the anomaly detection CNN algorithm and event classifier
becomes of critical importance. Therefore, as part of this effort, the computation
run time of the algorithms were also tracked and evaluated. While training and
inference was able to be achieved on a laptop device, for real time implementation
more powerful hardware would be beneficial to the overall performance of the
integrated system. Due to the extremely small timescales that are present in
power systems, the inference speed of this network will be of critical importance.
54

CHAPTER 4
Physics Informed Digital Twin using Graph Neural Networks
4.1 Chapter Overview
As stated in previous chapters, the modern smart grid contains Wide Area
Monitoring Systems (WAMS) composed of high fidelity sensors and Phasor Mea-
surement Units (PMU) that allow for constant monitoring of the system state.
However, the large amount of data provided by these smart devices can overwhelm
the legacy Supervisory Control and Data Acquisition (SCADA) system. Lever-
aging advances in machine learning, the proposed Digital Twin assisted Graph
Convolutional Neural Network can ease the burden on the SCADA system and en-
hance the capabilities of the trained operator. The proposed approach uses digital
twin technology to augment the PMU data provided by the physical system. The
augmented dataset, containing information from the digital twin and the physi-
cal twin, is processed by a graph convolutional neural network (GCN) to detect
physical faults in the power system and to classify the location of the system fault.
The proposed method is tested and evaluated on standard IEEE distribution and
transmission benchmark systems.
A significant development in the power grid has been the establishment of
Wide Area Monitoring Systems (WAMS) to allow greater insight into the current
system state. The monitoring devices are required to send the readings back
to the supervisory control and data acquisition (SCADA) system to increase the
situational awareness of at the central control center. This recently implemented,
and still developing, Cyber Physical System (CPS), commonly known as the Smart
Grid, has the potential to revolutionize the energy market. With the increased
proliferation of distributed energy resources (DER) and high implementation of
renewable energy, such as solar and wind, the monitoring and control of the Power
55

Grid has become increasingly difficult making it reliant on the WAMs to properly
function. However, this increased reliance on access to real-time data from the
remote assets can also introduce vulnerability to the power system.
Digital Twin technology has become an emerging topic in many fields. Digital
twins are simulations models that run along side physical system to provide greater
insight into the physical system state. Using real-time sensor data, the Digital
Twin is able to constantly update the simulation model to provide the useful
relevant information back to physical system. Digital twins have their origins in
the aviation industry and rapidly have expanded to be implemented in numerous
other industries such as automotive [29], manufacturing [91], cyber security [92],
and microgrids [93].
In this chapter, Section 4.2 outlines the Methodology for implementing the
GNN Digital Twin layer. In Section 4.3, the physical system and testbed is briefly
described. In Section 4.4, presents the conclusions and continuing research.
4.2 Approach and Methodology
In this chapter, a physics aligned deep learning digital twin is researched to
augment the data provided by the WAMs to add additional context to the sensor
data and to fill in the gaps when data is missing, whether it be by natural or
malicious reasons [94]. While classical methods like power flow analysis and state
estimation have been widely used but can encounter issues with convergence if
there is bad data present or line outages in the system. This chapter presents
a method to overcome those traditional limitations using a dynamically shifting
physics aligned graph neural network (GNN) [95].
Power system application lend themselves to graph-based implementation due
to the well known connected nature of the system elements. By viewing the buses
of a power system as the nodes, and the lines as connected edges. In Figure 23, the
56
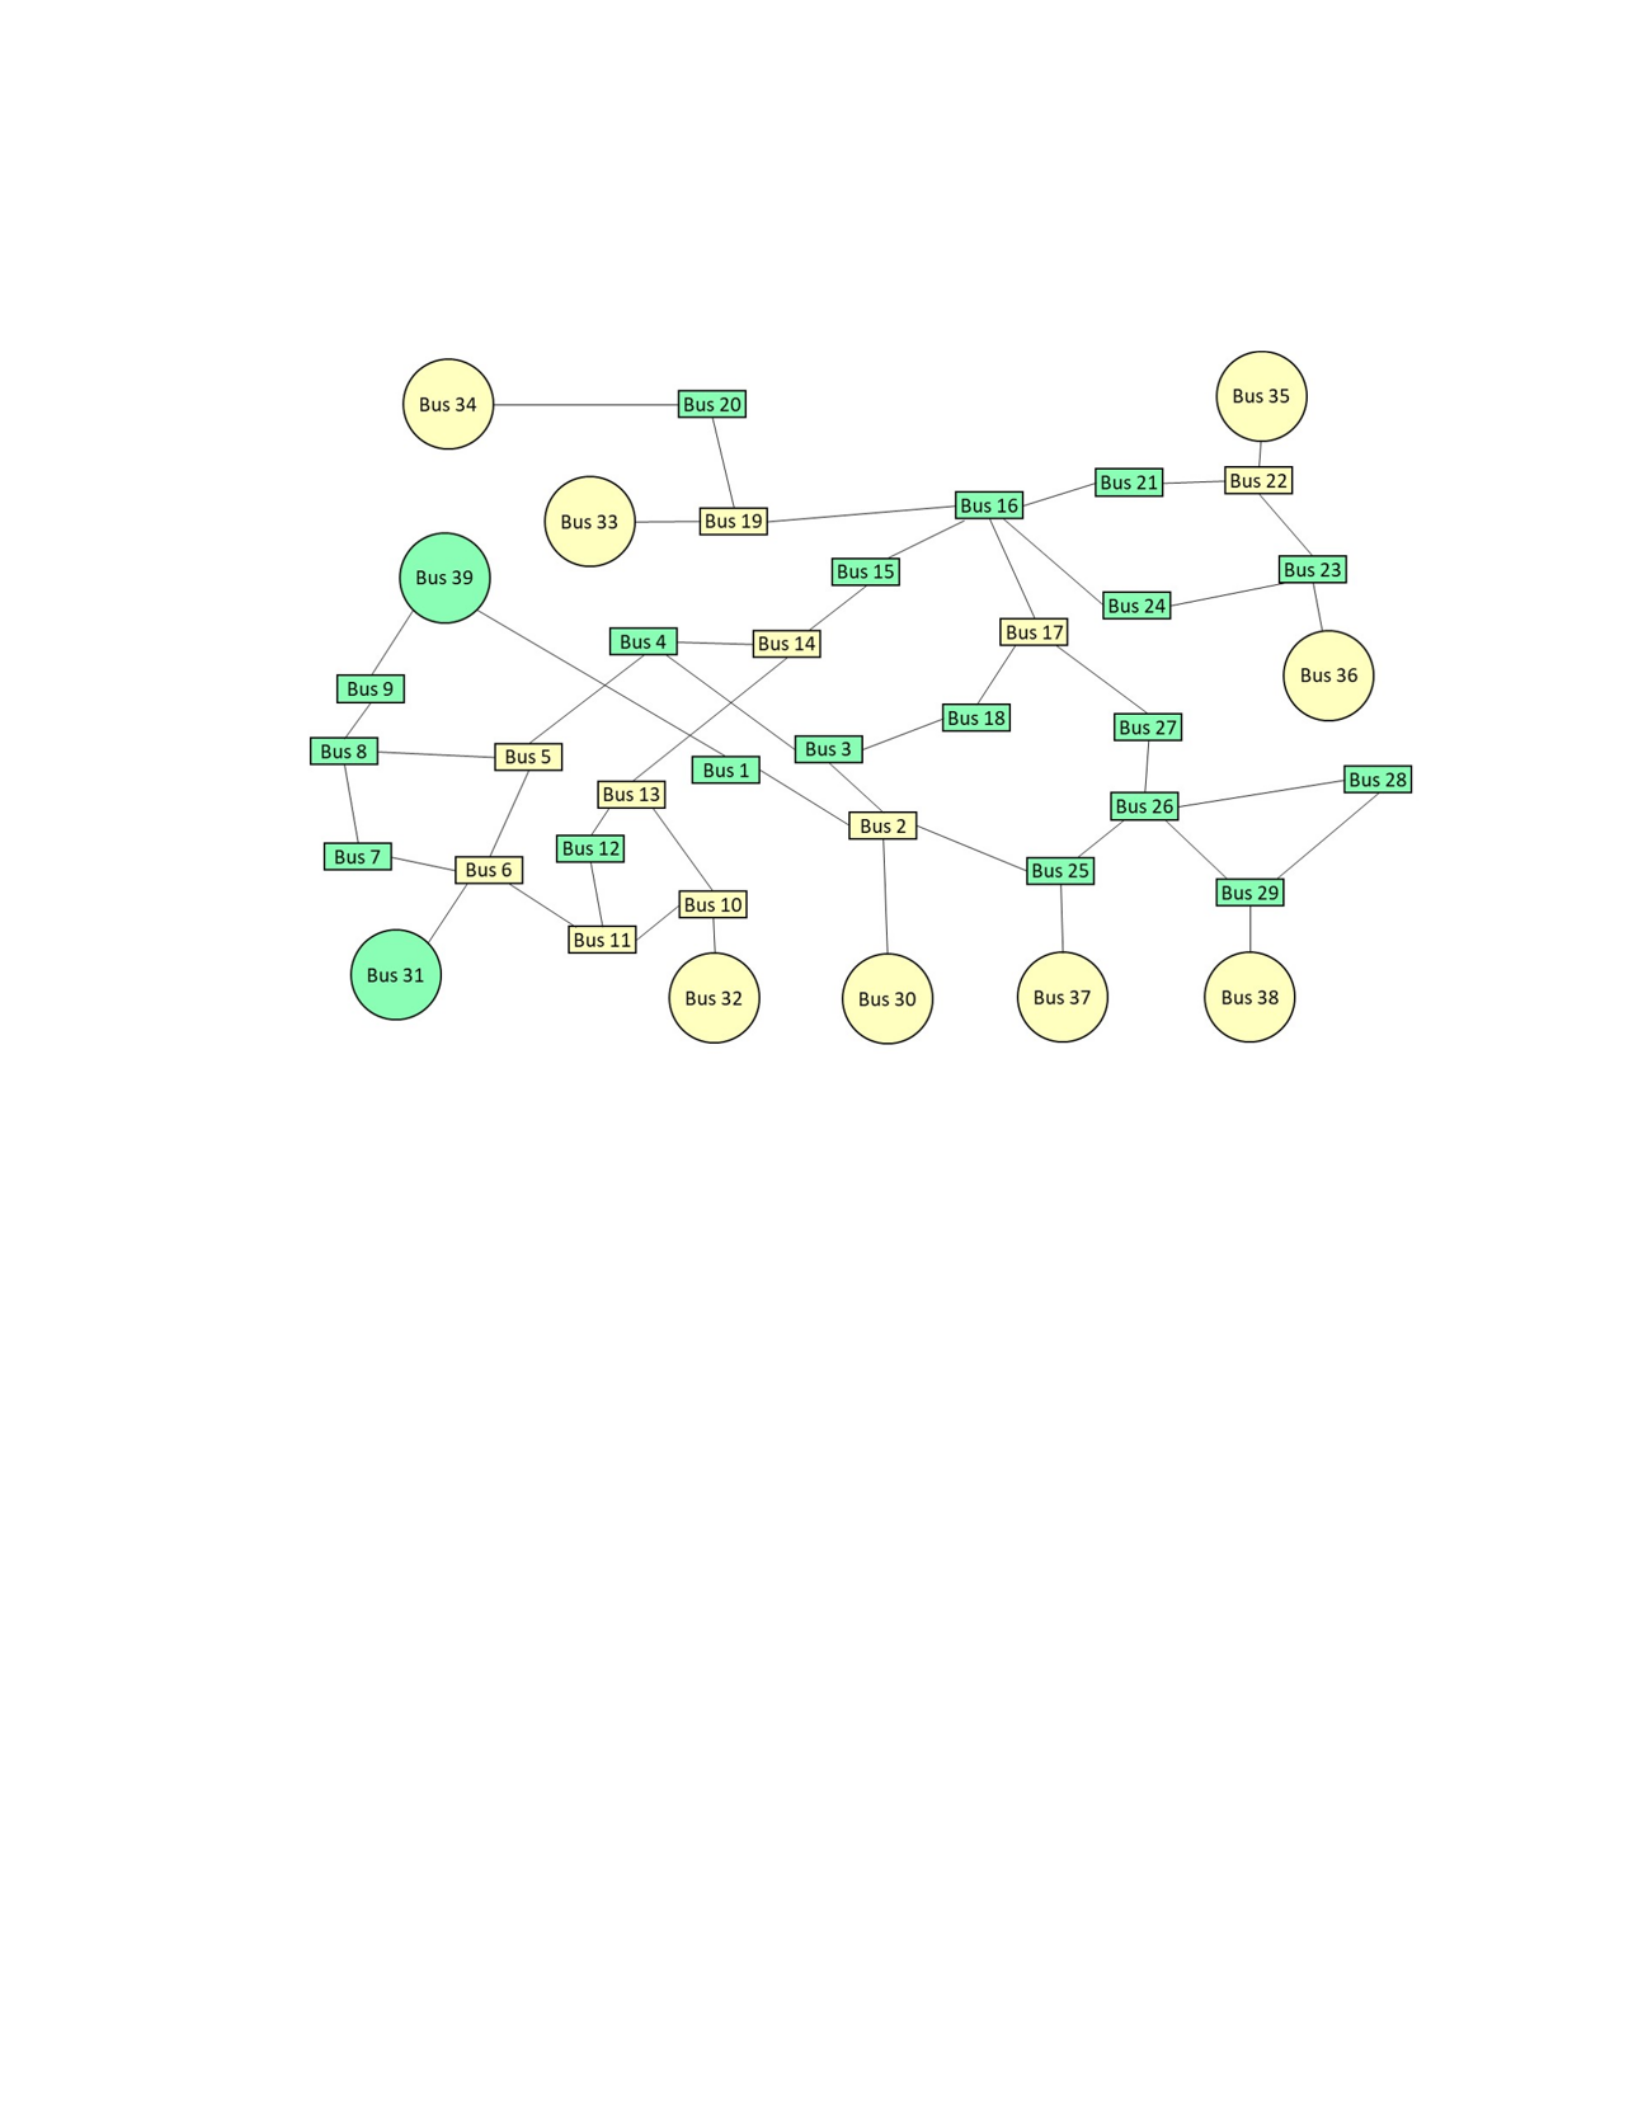
IEEE 39-bus model is represented as a graph network. The IEEE 39-bus model is
used to demonstrate the approach outlined in this paper.
Figure 23. IEEE 39-Bus Model shown as a connected graph. [4]
The GNN was designed to create a converged model of the physical system
in both normal and anomalous operating conditions [96]. A coordinated dropout
technique is used to improve the modeling of line faults in the system. Once
trained, the model will be evaluated in its ability to adapt to a changing system
topology without user input. While other approaches will be developed, the initial
approach will be to use a one shot approach to guess the state of the physical
system to align GNN model.
The GNN algorithm takes the PMU data (three-phase voltage, phase angle
and frequency) from 8 buses for a total of 56 input features. The inputs are
normalized to a range of -1 to 1. The normalized data is then fed through a single
graph layer and two fully connected layers. The output of the algorithm is the
57
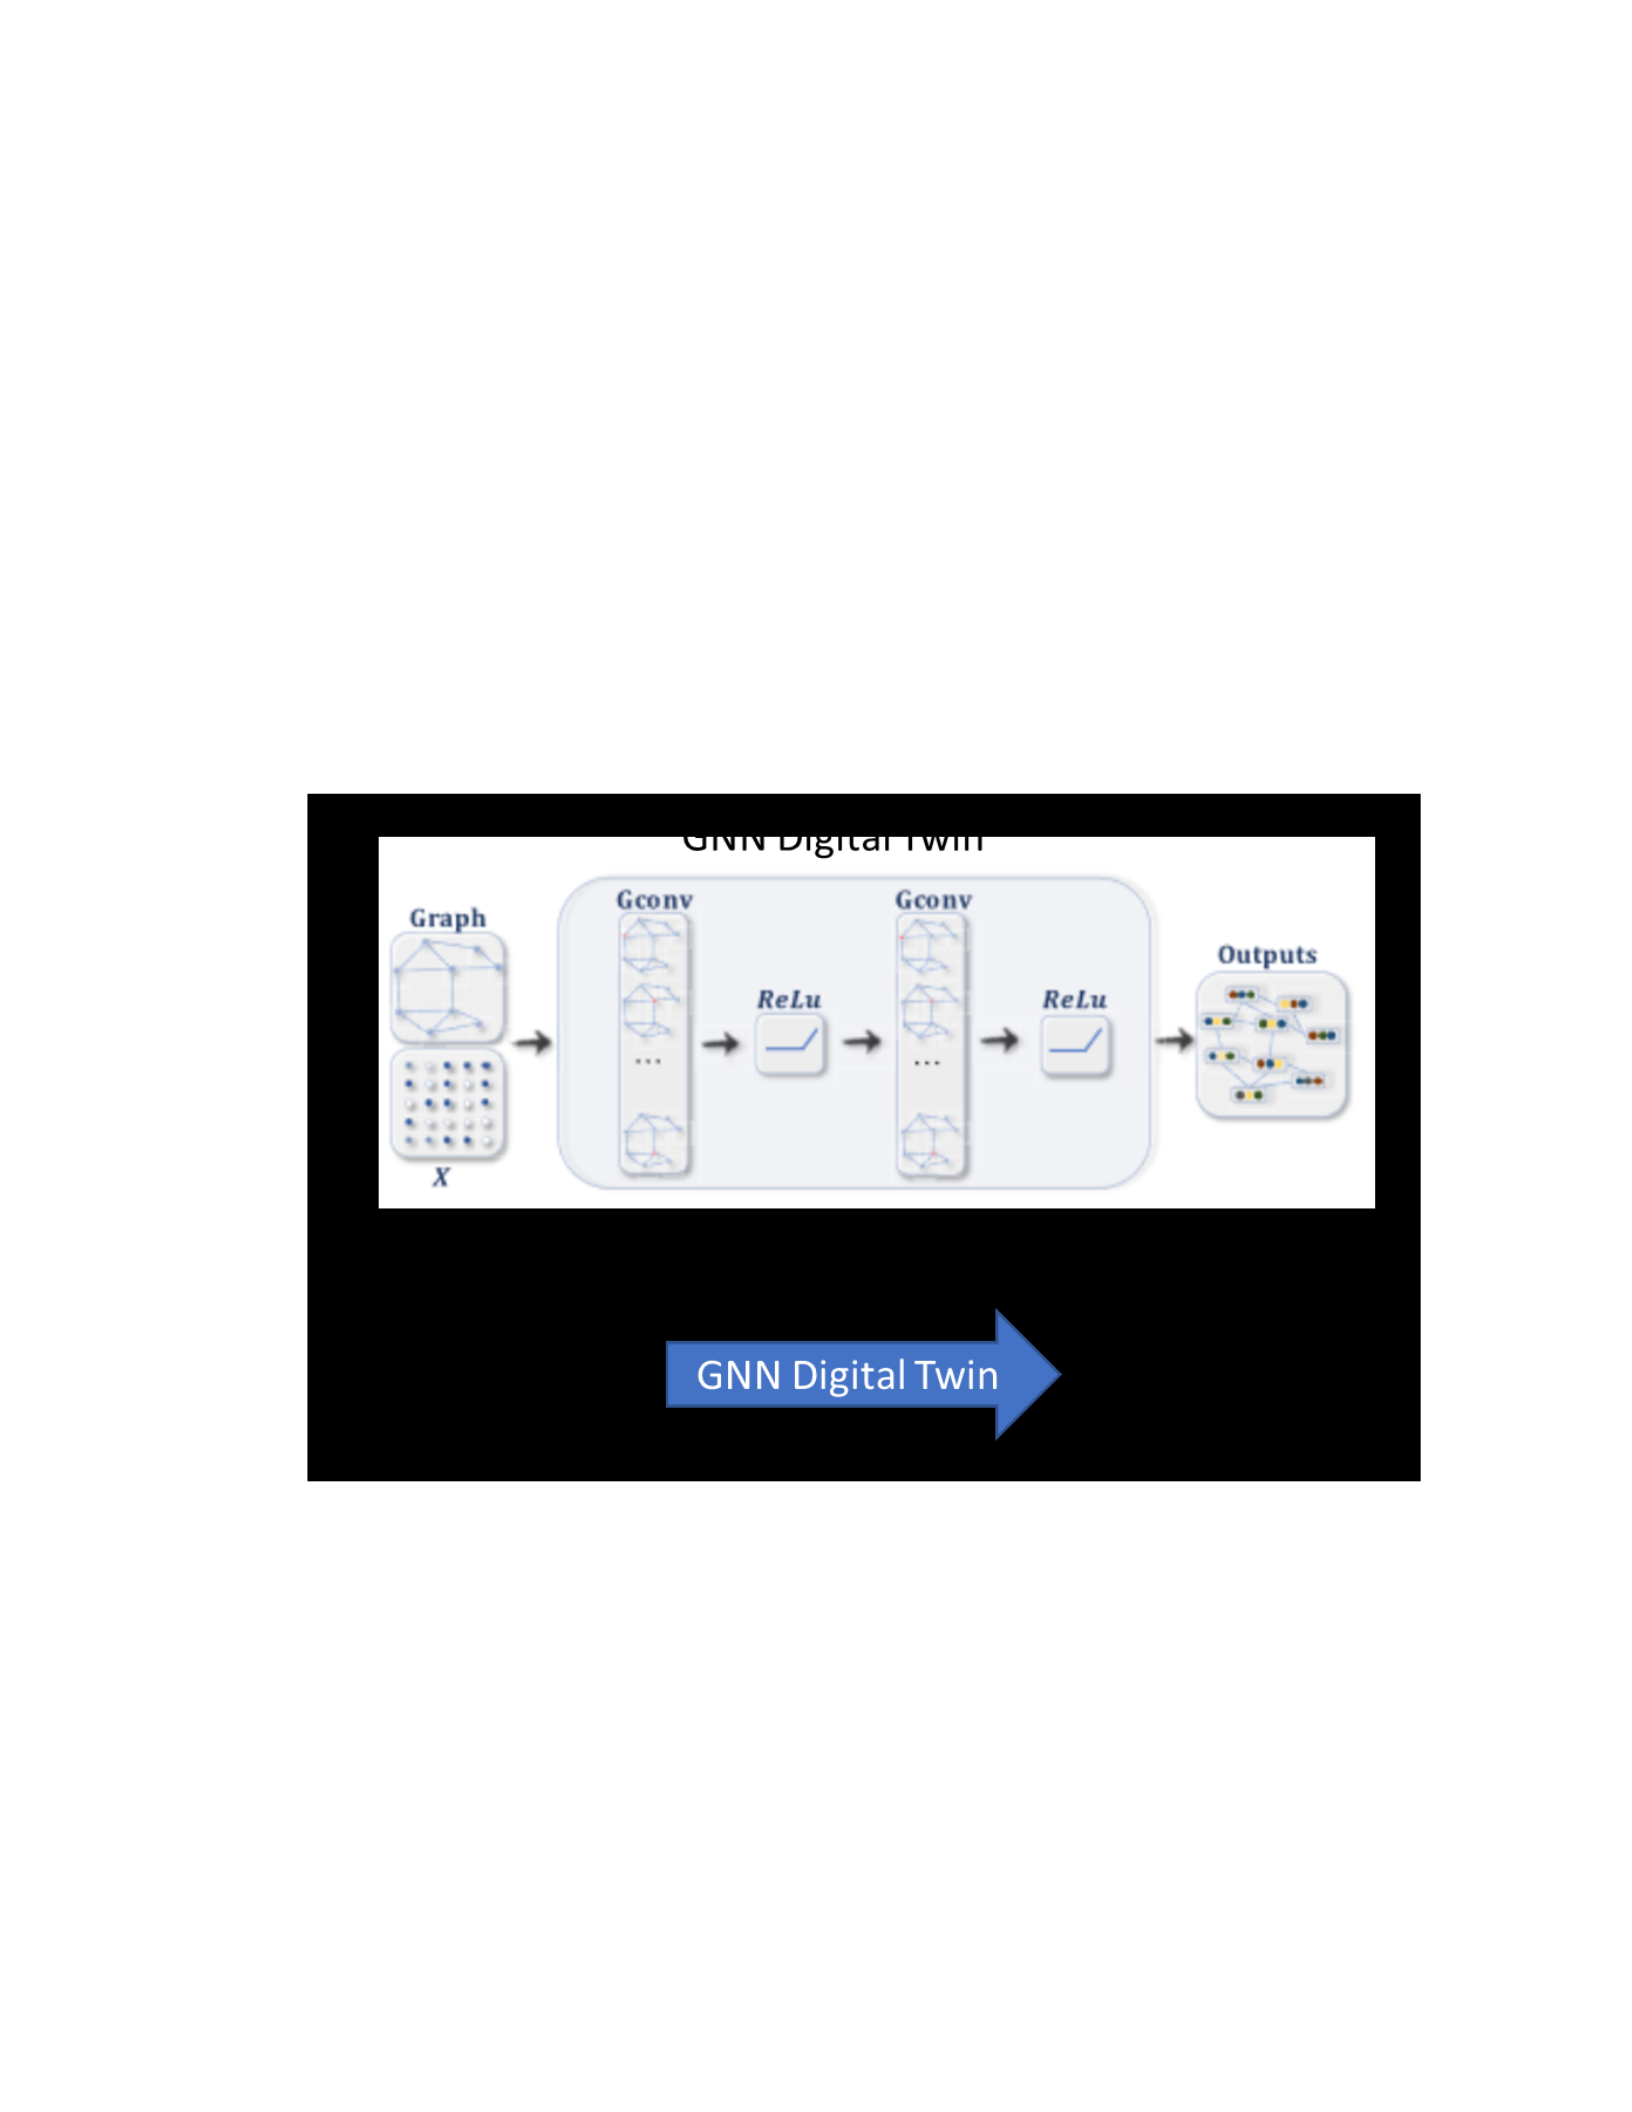
PMU features for all 39 buses. In the training loop, a L2 loss function, mean
square error, is used to compare the output features to the ground truth data.
As shown in Figure 24, the GNN works along side the Digital Twin layer to act
as a “decoder” of the reduced system state information and can recreate the full
system sensor array from the existing PMUs installed on the system. The PMU
data from the 8 active buses are passed to the GNN and the output is the full
system state. Using dropout, the connections to the faulted bus are eliminated in
the matrix representation of the system. The fault detection algorithm evaluates
the current system state and return any anomalies detected in the physical system.
Figure 24. General Topology of GNN Digital Twin Layer [5]
Lastly, the deep learning digital twin algorithm is combined with a deep graph
convolutional neural network (GCN) fault detection algorithm to improve detection
accuracy. The GCN is able to detect and locate the bus location of a fault with
a high degree of accuracy when given the PMU data for each bus in the full
system. However, when only given a limited subset of the bus information, the
58
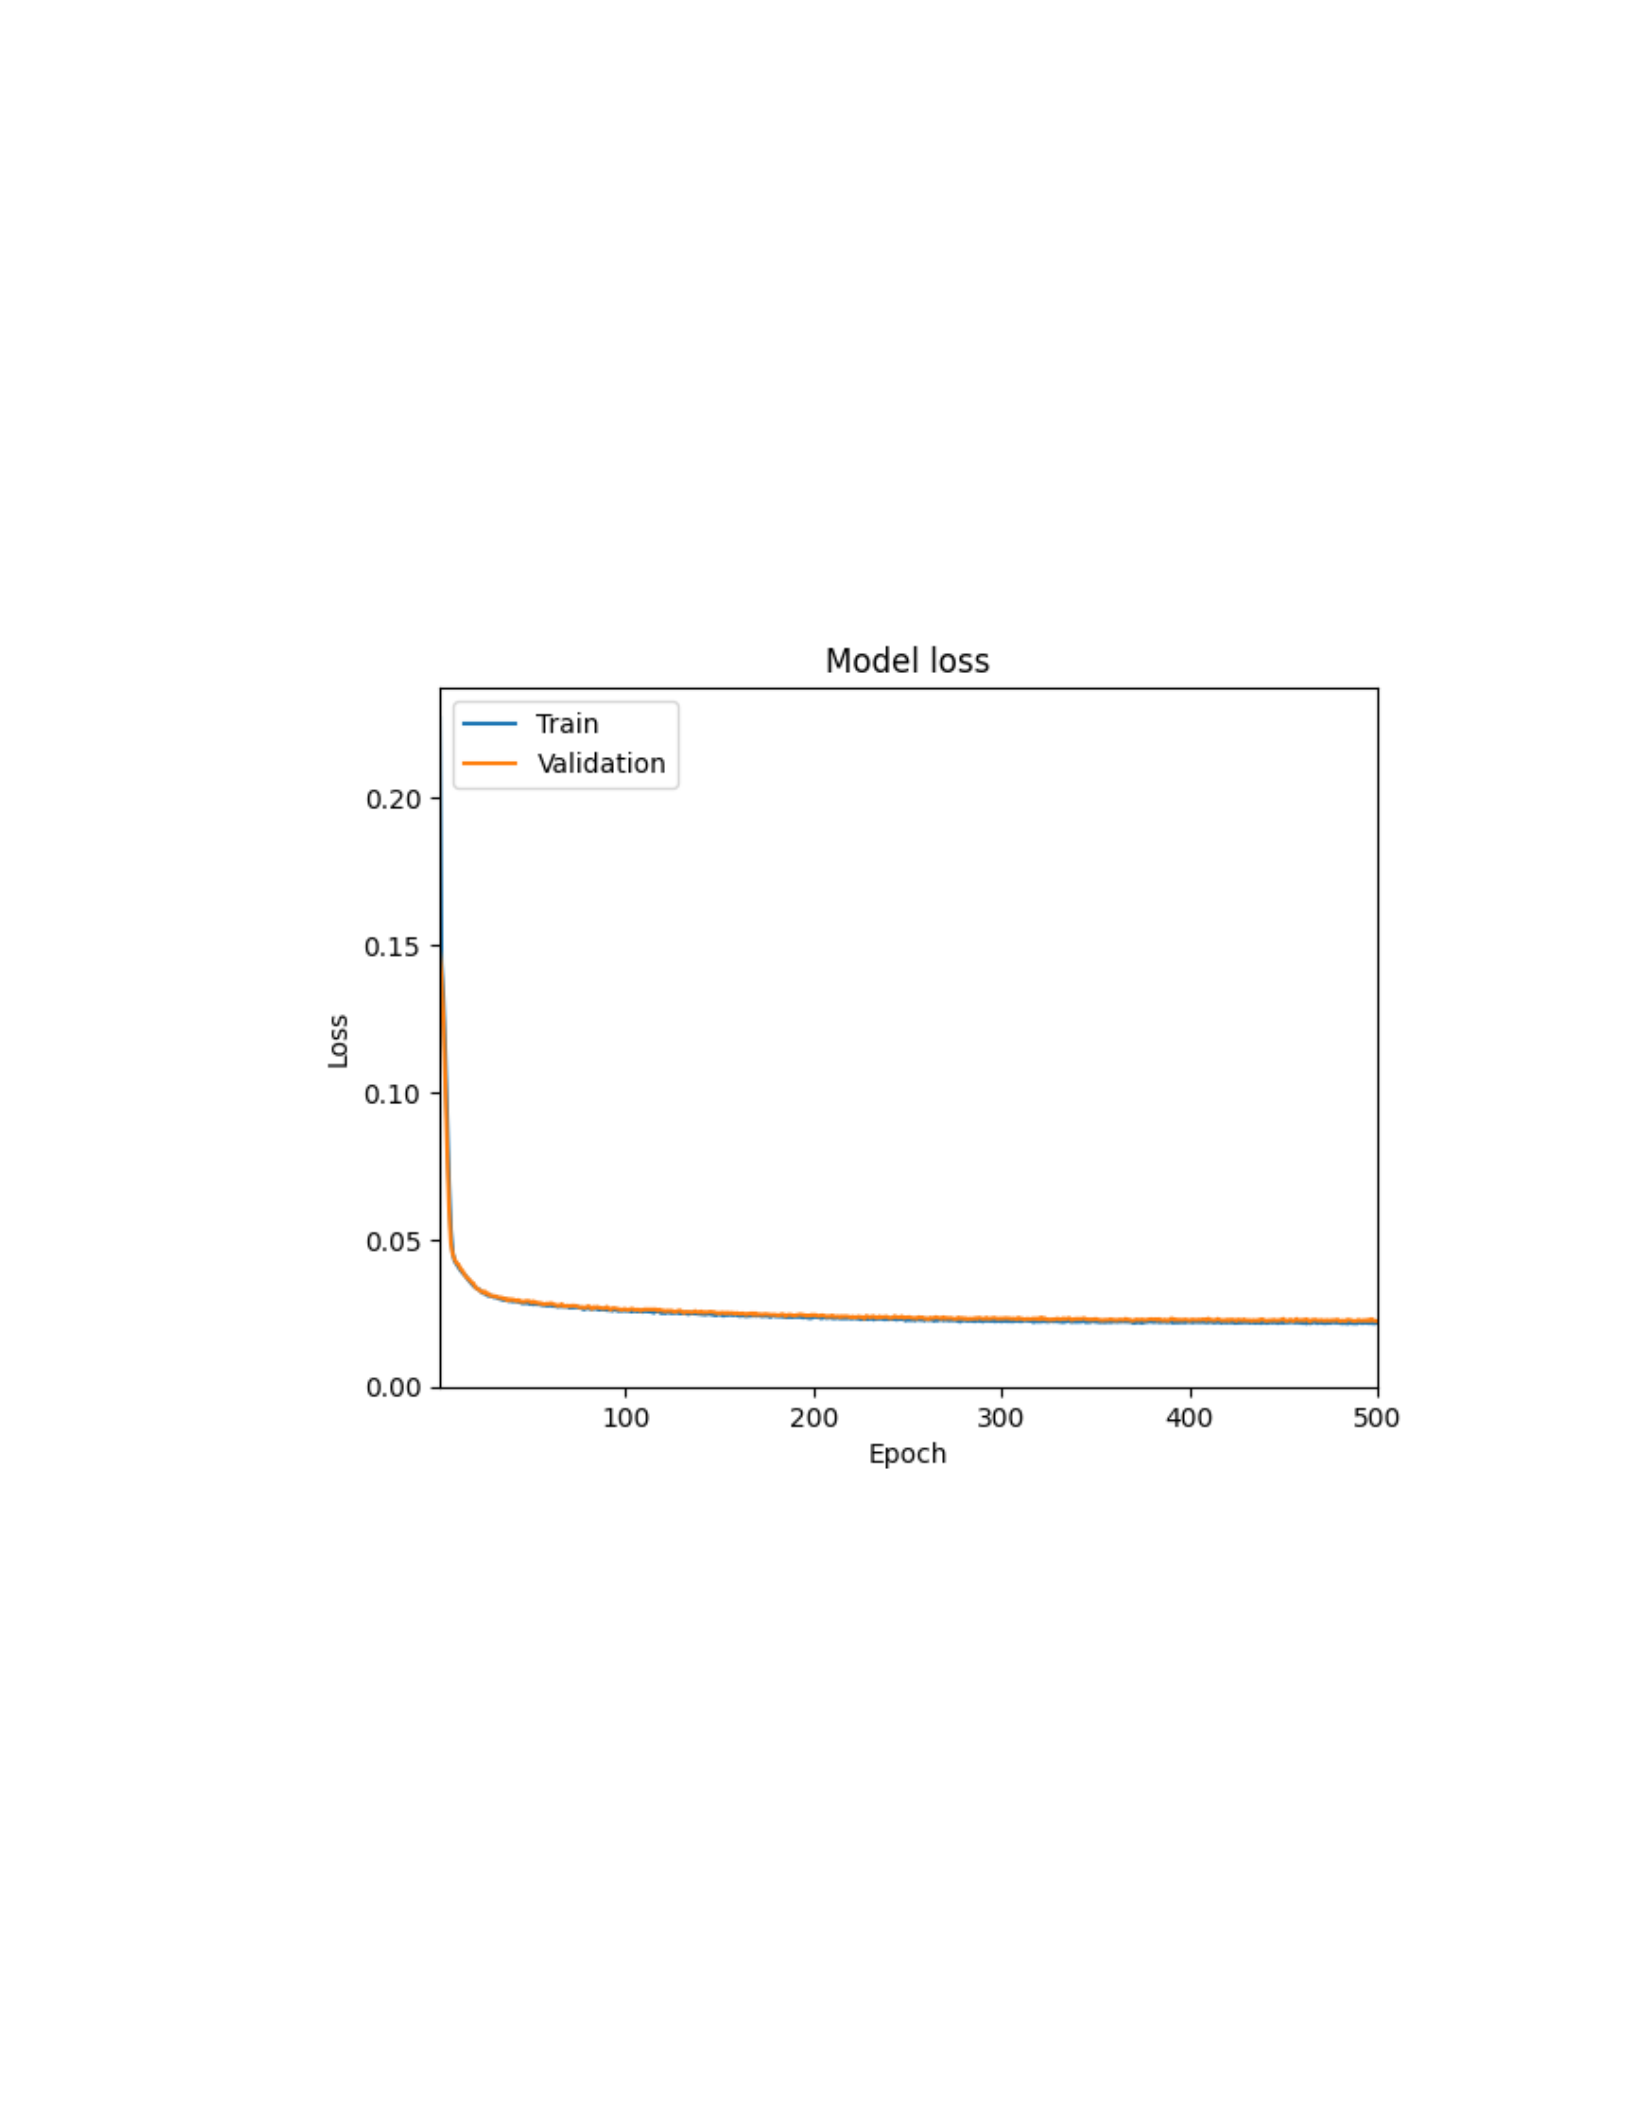
GCN algorithm doesn’t not perform as well.
4.3 Results and Discussion
The GNN algorithm converges to a reasonably accurate solution fairly quickly,
shown in Figure 25. After roughly 20 epochs, the loss in the GNN has begun to
converge. However, higher level details, such as the fault modeling don’t appear
to be captured until later in the training process.
Figure 25. Model Loss in the Training Process with L2 Loss Algorithm
Using the GNN state estimator, the algorithm was able to closely match the
output of the physical system across all 39 buses in the system, shown in Fig-
ure 26. The large discrepancy at bus 20 is due to a fault on that bus in the data
sample. The GNN has started to be able to recognize that as well as seen by the
discontinuity of the phase angle in the GNN state estimation at bus 20.
59
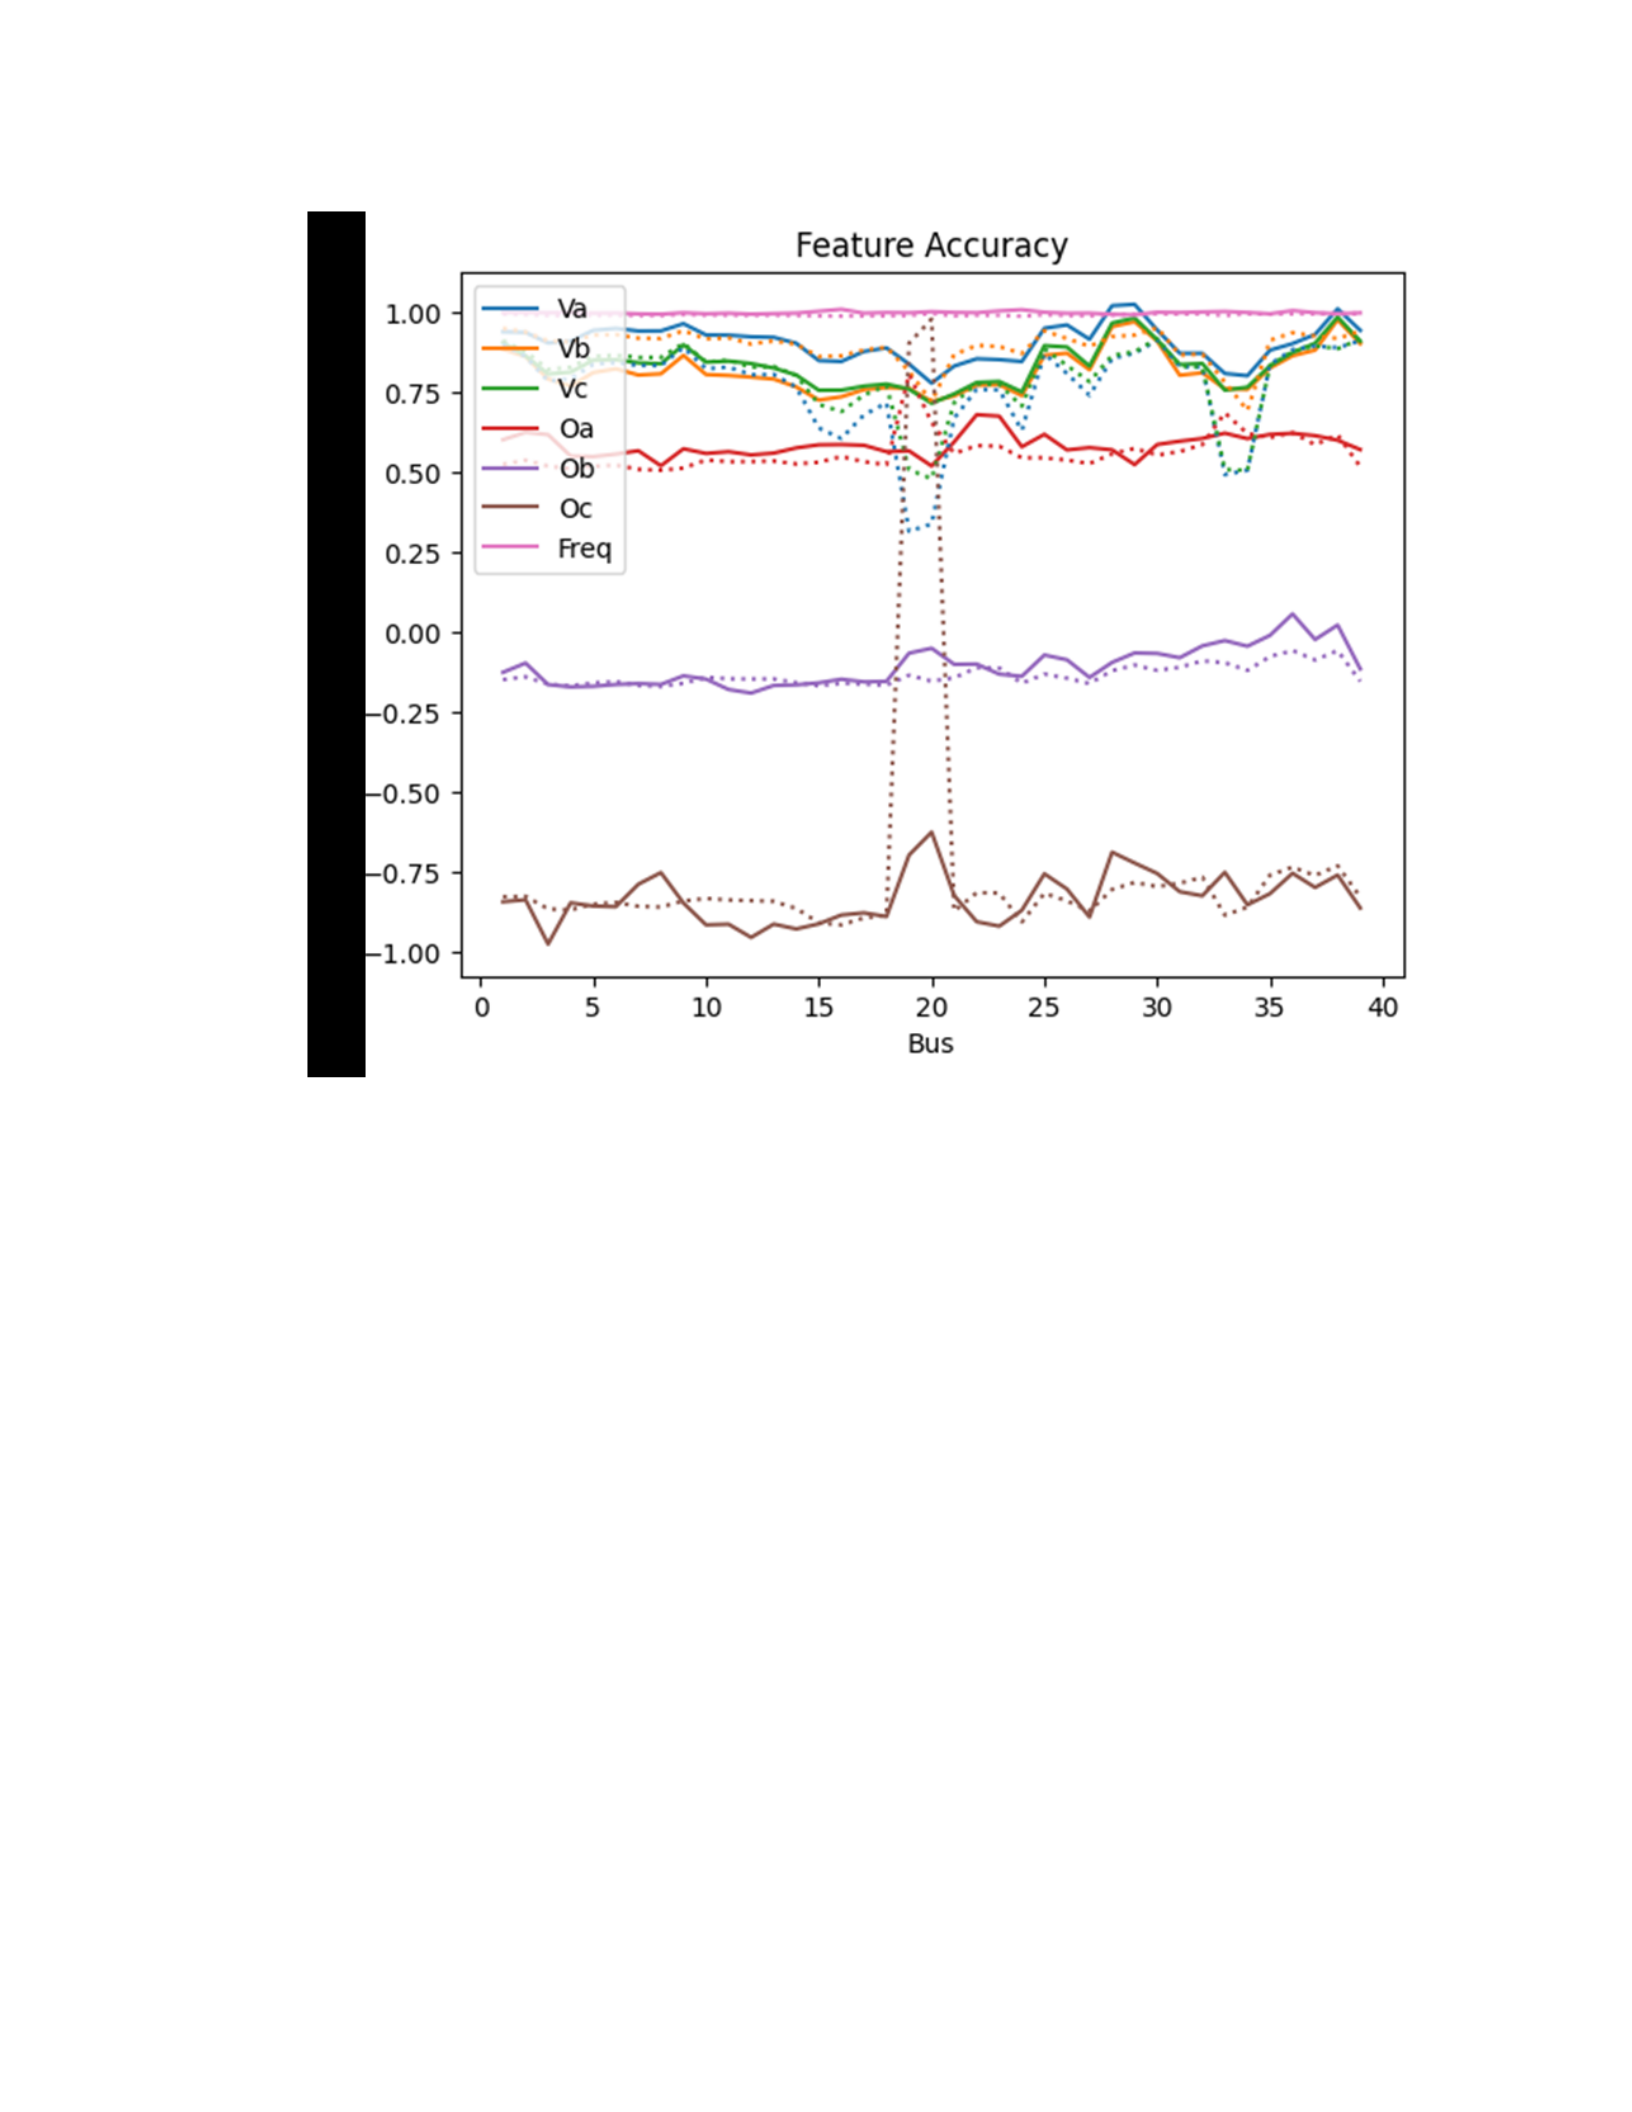
Figure 26. Comparison of GNN State Estimation Algorithm and True System
State
The Physics aligned GNN is able to show the deviations in bus voltage across
the power system and is able to capture some of the relationships between the
connected buses. It is worthwhile to note, while the nodes in the GNN are con-
nected in the same fashion as they are on the physical system, the physical line
characteristics are not passed to the GNN. However, the line characteristics are
likely learned by the GNN algorithm to align with the physical system.
When the algorithm is presented a partial fault, the algorithm is able to
capture the relationship between the buses but under predicts the impact of the
fault on the bus. In Figure 27, the impact of the fault on bus 38 is under predicted
by the algorithm.
60
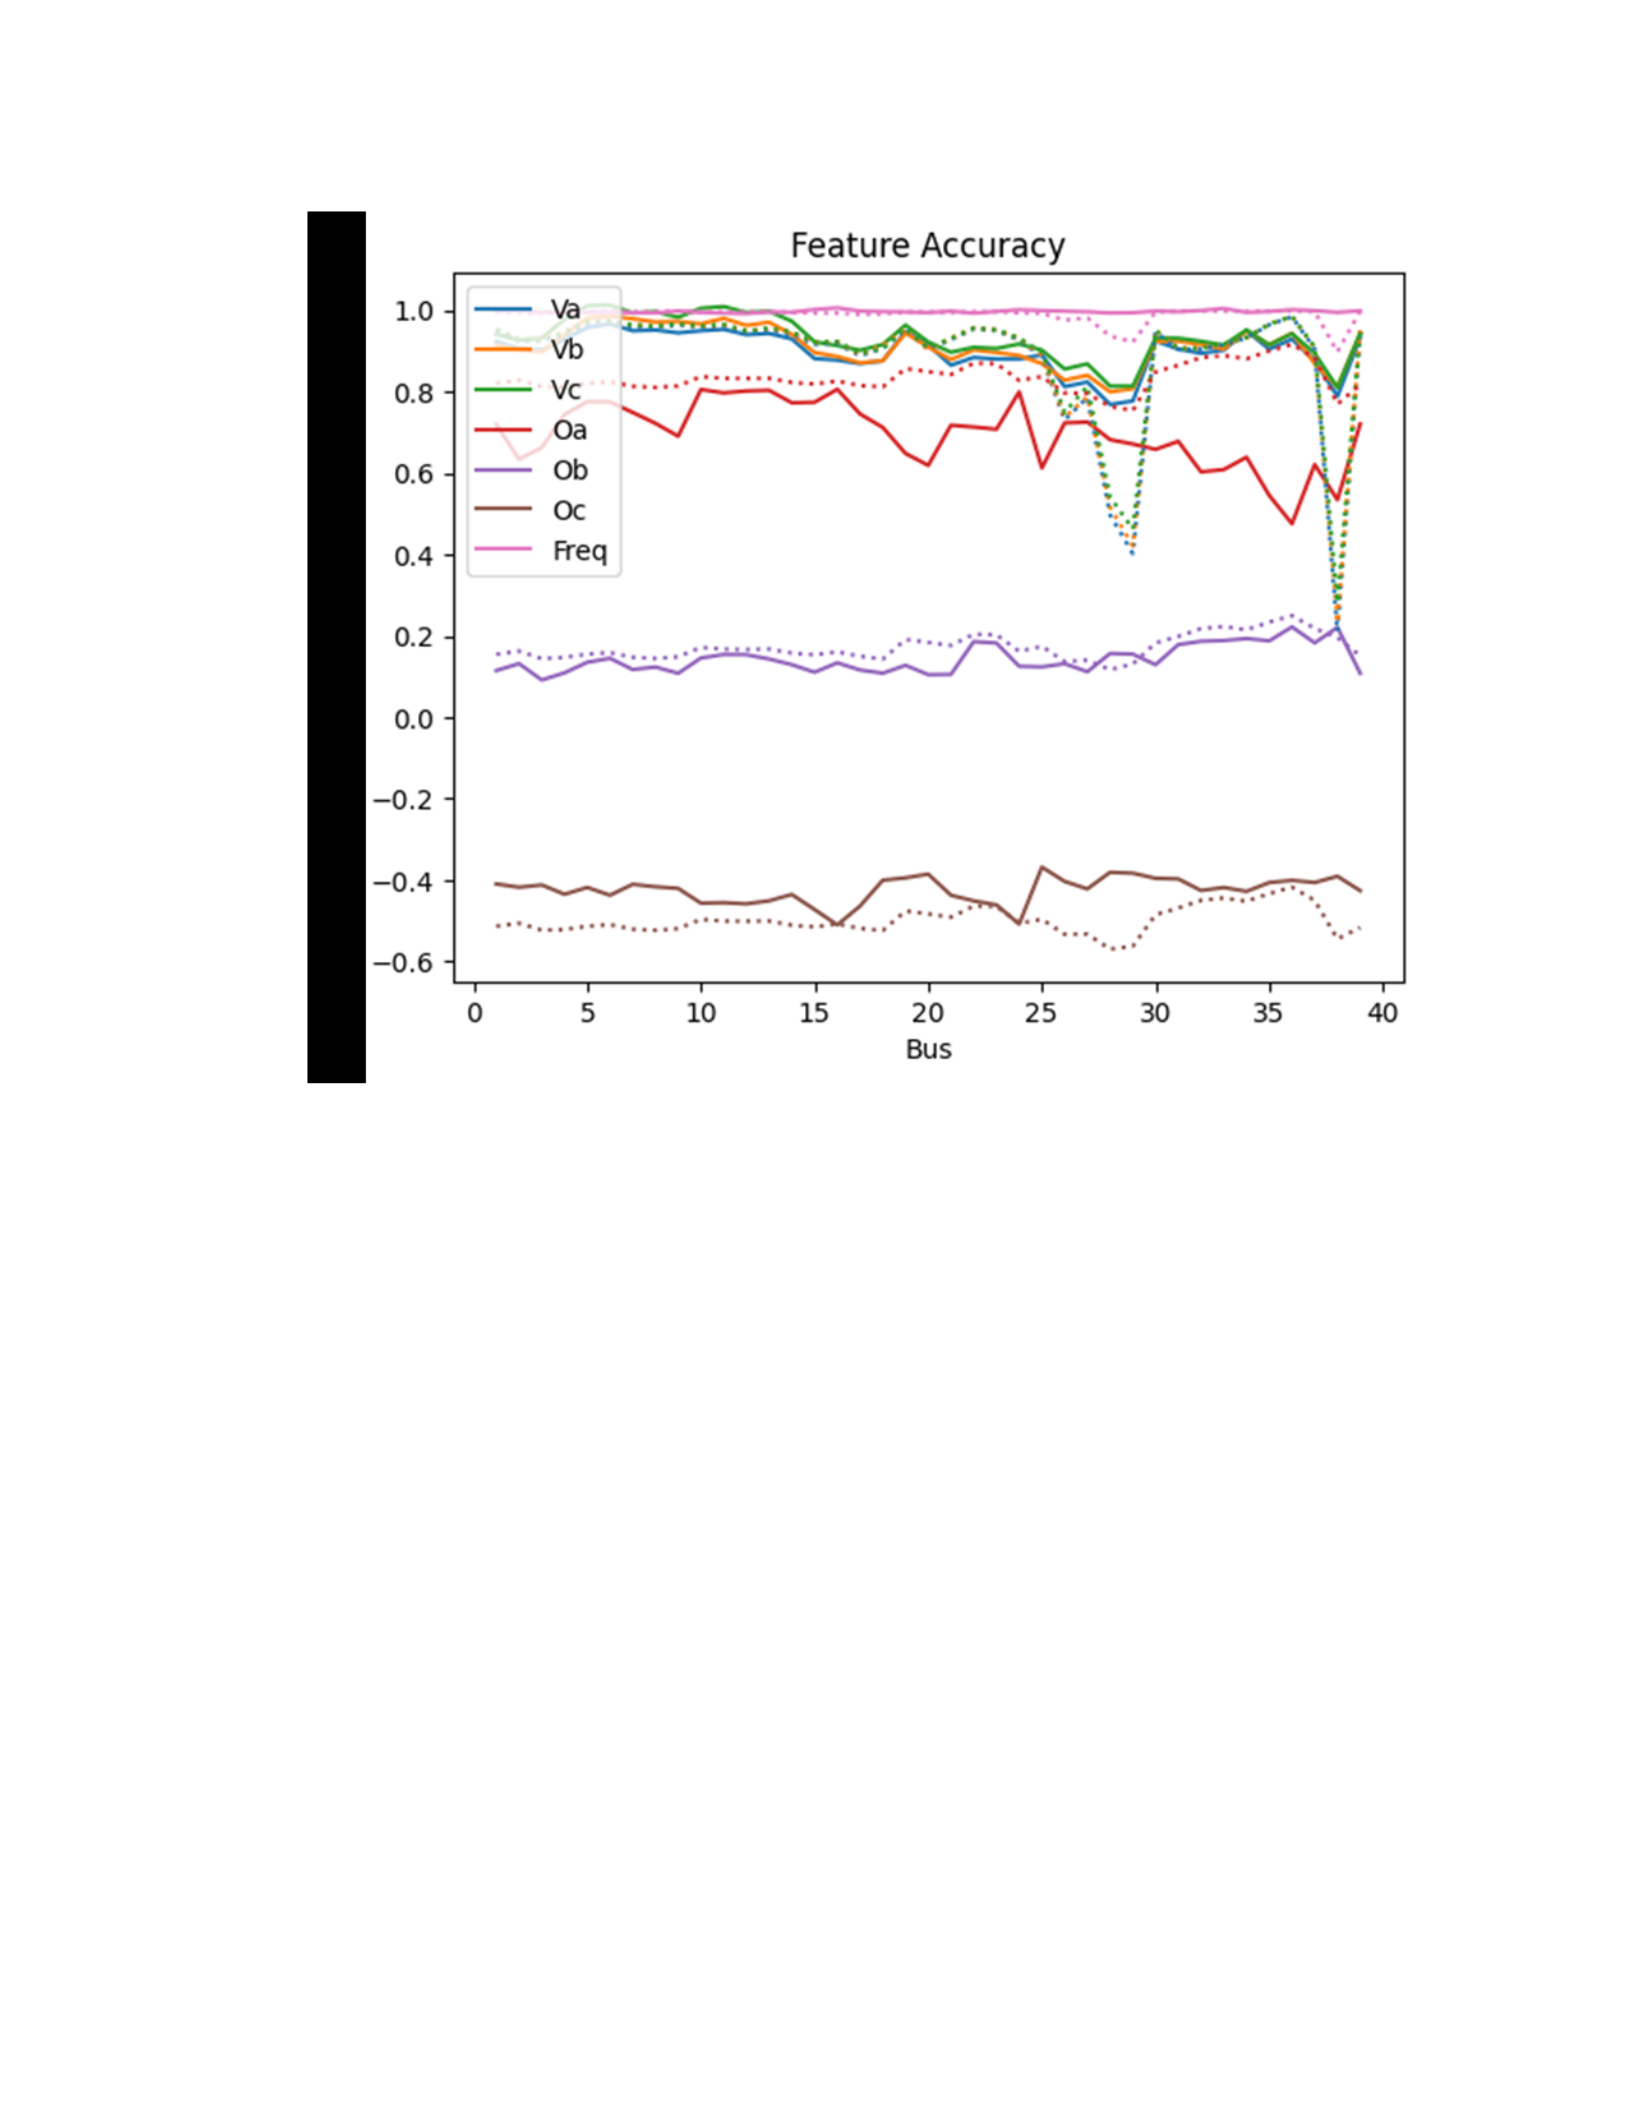
Figure 27. Comparison of GNN State Estimation Algorithm and True System
State
4.4 Chapter Summary
This chapter shows the ability to create a real-time Digital Twin implemen-
tation of a physical power system using a Physics Aligned Graph Neural Network.
The GNN-based Digital Twin power flow solver is able to fill in missing state in-
formation with limited PMU data and therefore less information about the system
state. The GNN is able to converge and provide a state estimation when a tradi-
tional power flow solver would not converge. The next steps in this research would
be to use the Digital Twin state estimation to assist in the anomaly detection and
location algorithm. Additionally, it would be interesting to add a recurrent layer
to the algorithm rather than the existing one shot approach.
61

CHAPTER 5
Blockchain Checksum for Establishing Secure Communications for
Digital Twin Technology
5.1 Chapter Overview
As Digital Twin technology continues to be developed for the power grid and
other high value applications, the security and accuracy of the remote sensor data
is of extreme importance. This chapter proposes a novel implementation of the
SHA-256 hash algorithm to create a blockchain of sensor readings. The implemen-
tation hashes the current sensor reading to the previous reading(s) from the sensor
through a chained checksum SHA-256 algorithm. The enhanced chained-checksum
is able to establish the trustworthiness of the communications between the con-
trol center and the remote sensor based on the length of the unbroken linked list.
The chain of sensor readings act as a sophisticated checksum for the middleware
communications used in the digital twin environment which often times are not
secure. While the concept is based on blockchain technology, this implementation
is specifically designed for two party communications, in this case the outstation
and the control center. To accommodate the two party communications, the im-
plementation allowed for the removal of some of the features commonly used in
blockchain, such as consensus polling or the proof-of-work algorithm, and replaced
them with historical values to establish the ground truth. To show the advan-
tages of the chained checksum, the SHA-256 algorithm has been implemented in
the IEEE 33-bus benchmark system in the Typhoon Hardware in the Loop (HIL)
real-time simulator.
The security of the power grid and other cyber-physical systems has gar-
nered global interest in recent years due to high visibility cyber attacks being
attempted on power grid both domestically and abroad. The 2015 cyber attack on
62

the Ukrainian power grid [97] is often referenced to show how a cyber attack on
physical asset can have wide ranging impacts. In the smart grid, securing the sen-
sor readings from remote meters and generators is important to have trustworthy
state information about the entire power system [98]. However, through methods
such as a man-in-the-middle [99] and false data injection attacks [94], the state
information from the distributed sensors can be incorrect and malicious data can
be specially crafted to harm the physical system.
Digital twin technology is an emerging technology that is being implemented
in many industries such as automotive [29] and aerospace [11], to provide greater
insight into the current state of the complete system. However, Digital Twins,
like many Industry 4.0 techniques, require large amounts of accurate and timely
data to allow for the cross analysis of the physical and digital domains [100]. More
recently, Digital Twin technology has garnered interest in Smart Grid applications
[32] [101] and cyber-physical security of power and energy installations [2]. With
cyber attacks on the rise globally and specifically targeting critical infrastructure,
it is of the utmost importance that the sensor data used by the Digital Twin is
trustworthy.
In recent years, blockchain has become a popular topic for many researchers,
including in the field of power and energy [102]. Blockchain technology is often
used as a distributed method to provide a secure and accurate ledger to all parties.
Perhaps the most famous use of Blockchain technology is in cryptocurrency such
as Bitcoin and Ethereum.
The lightweight method presented in this chapter is designed to increase the
trustworthiness of historically insecure communication methods, such as Modbus
or Distributed Network Protocol 3 (DNP3). This research introduces a hash check
field that is used to verify that no meter data has been changed while the data
63

was in transit to the control station [6]. Building on the blockchain technology,
the hash check is linked to previous sensor readings to create a linked list of data
increasing the difficulty of an attack without adding significant overhead. The
proposed hash algorithm uses previous sensor readings hashed with the current
sensor reading to increase the difficulty and computational overhead for malicious
attackers [6].
The proposed method increases the trustworthiness of the sensor data for
digital twin applications. The methodology uses a lightweight implementation of
the SHA-256 hash algorithm and builds on blockchain techniques to detect data
manipulation in a distributed smart grid infrastructure. Section II presents a brief
survey of other blockchain applications in the smart grid. Section III outlines
the architecture of blockchain hash sequence and real-time implementation in the
IEEE 33-bus distribution power system running in the Typhoon Hardware in the
Loop simulator. In Section IV, the blockchain algorithm is tested against a false
data injection attack and the results of the experiments are presented. Finally,
Section V contains a brief conclusion.
5.2 Related Work
In recent years, there has been significant interest in applying the Blockchain
technology, originally developed by Nakamoto in 2008 as an electronic currency
[103], to other applications including to the Future Smart Grid [104] [105]. There
has been a particular interest in using a distributed ledger to secure the energy
trading market [106]. Some papers attempt to leverage the distributed nature
of the ledger to create peer-to-peer trading platforms for energy, similar to what
exists in the current Bitcoin market [107] [108]. Others have developed private
blockchain networks to facilitate the energy transactions [109].
In [110], the author creates a trust model for wireless sensors using a smart
64

contract based on metadata indicator values. In this paper, the metadata is hashed
into a merkle tree to prevent tampering with historical data values. The Sensor-
Chain framework, presented in [111], is a spatiotemporal-based blockchain man-
agement system for Internet of Things (IoT) devices. The framework uses local
aggregator devices as miners to reset the blockchain at temporial trigger points to
reduce the memory burden on the IoT devices. In [112], Liang proposes to use the
blockchain to secure the data in the power system communications network using
consensus polling.
Blockchain and Digital Twins are emerging fields that can be used in conjunc-
tion to increase the resiliency of the Digital Twin applications. In [113], potential
use cases for the intersection of Blockchain and Digital Twin technology is ex-
plored for Industry 4.0 systems. Blockchain can be an enabling technology for
Digital Twin development to overcome cybersecurity concerns and establish trust,
security, and protection within the Digital Twin communications.
While many of the related works apply blockchain to the power grid, this
approach leverages the historical database inherent to the digital twin infrastruc-
ture to create a multi-layered temporial blockchain. As noted in [114], the uses for
blockchain are not limited to data transmission but also used in intrusion detection
systems (IDS) and establishing trust within a network. While the development and
implementation of an IDS is outside the scope, a large contribution of the frame-
work presented in this dissertation is to expand an attackers visibility to the IDS
through requiring historical knowledge of the system state.
In this research, the focus is using Blockchain to secure the middleware com-
munications of the remote sensors and power meters on the Smart Grid with a
centralized supervisory control and data acquisition (SCADA) system running a
digital twin. This implementation will help with each of the major secure infras-
65

tructure resiliency areas (secure communications, device security, security manage-
ment and awareness, cybersecurity evaluation and intrusion tolerance) presented
in [115] as well as addressing some of the emerging research challenges, such as risk
mitigation and trust management. While no one single technique will solve the se-
curity issues presented by the cyber-physical power grid, the blockchain checksum
could help be part of the solution.
5.3 Approach and Research Methodology
Blockchain implementations and smart contracts have been a popular research
topic. The distributed ledger provides a method for multiple parties to share
and update information. However, classical implementations of the Blockchain
technology are often plagued by the high energy and computational cost of the
proof-of-work algorithm [116].
The approach proposed in this research uses elements of the Blockchain process
to create a linked checksum to improve the security of an insecure communication
protocol, such as Modbus or DNP3. By linking the current sensor readings to
the previous reading, the system is able to create a linked list of sensor readings.
This method would increase the difficulty for an attacker to implement a false
data attack because the attacker would need to know the historical system data
to pass the blockchain check. In a traditional power system, a power meter is
only able to monitor the local state of system. Therefore, the meter is not able to
make judgment on the the other distributed meters making the proof-of-work and
consensus polling difficult, if not impossible, to implement. In this implementation
of a sensor data blockchain, the control center - outstation relationship does not
require distributed verification of the ledger. Therefore, the proof-of-work and
polling practices that are commonly used in other blockchain implementations are
also not required.
66

In a traditional blockchain implementation, the miner solving the proof-of-
work algorithm triggers the next block to be hashed. In this implementation, the
block trigger occurs when the data is compiled and sent to the SCADA system. For
a outstation-control center architecture, such as DNP3, the trigger would be the
control center’s request for the next reading. For a process bus-based middleware,
such as DDS or IEC 61850 Sampled Value, the block trigger would be clock-based.
The sensor data representing the current system state at the time of the request
is treated as the next individual block.
Similar to a traditional blockchain approach, the previous hash is also added
to the current block in the hash function, linking the current sensor data to all
previous data samples. Additionally, in this implementation, a historical hash
value is also appended to the end of the block and hashed using the SHA-256
algorithm.
The current sensor reading, x(t), is hashed with the previous sensor value, x(t-
1), and the historical sensor value, x(t-N). While it is not required, an additional
layer of security is added to the system by asserting that the attacker does not know
x(t-N). For simplicity, N=100 is chosen to demonstrate the idea of the blockchain
checksum. The three hashes, H(x(t)), H(x(t-1) and H(x(t-100)), are then hashed
together to get a final hash for the sensor reading. The final hash value is added as
the last field of the communication packet sent to the SCADA system. This hash
tree is shown in Figure 28.
This approach increases the security of the data being sent to the Digital Twin
in a few ways:
1. For an attack to go undetected, the attacker would be required to maintain
persistence on the network to be able to supply the correct Blockchain check-
sum to the Digital Twin and SCADA system. The attacker is required to
67
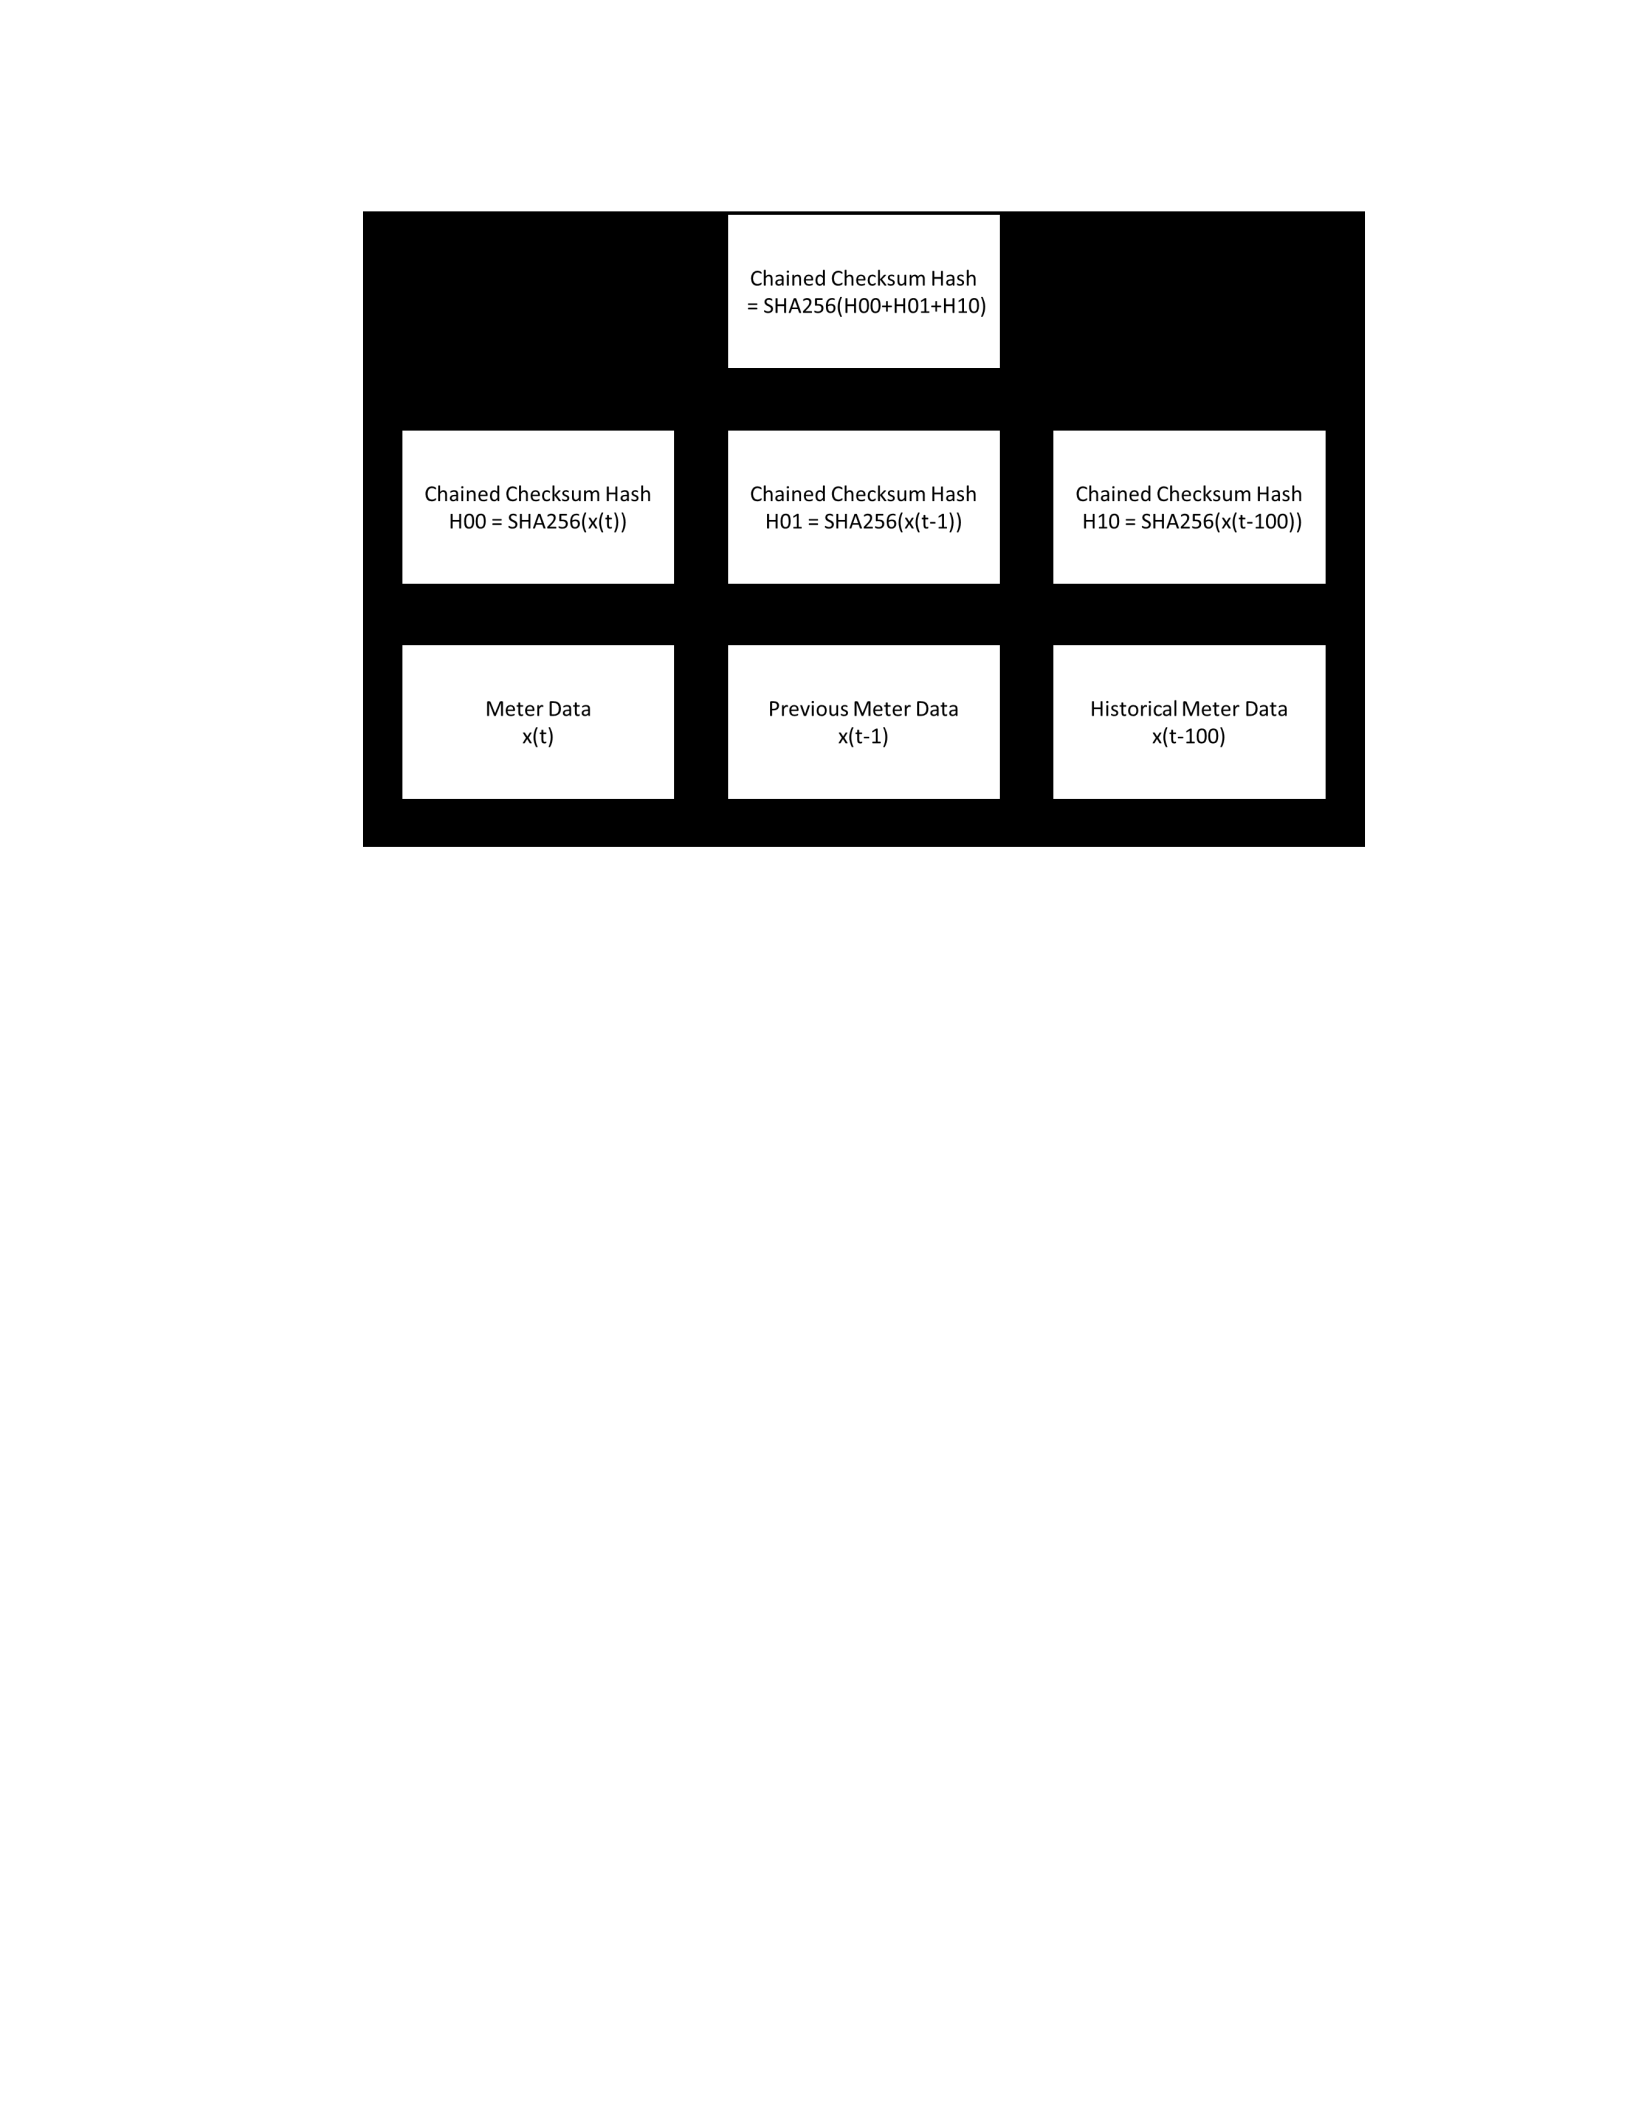
Figure 28. Modified Merkle tree for linking sensor readings to historical values
know not only the hash of previous data sample but also the hash of a second
historical data block that could be days or weeks in the past. It’s worth to
note, in the following examples, the Kerckhoffs’ Principle is used to assume
that the attacker knows the underlying system and algorithm. Therefore,
it is assumed that the attacker knows the historical loop back value, N, as
well as, the initial hash value. However, in practice, N may be chosen dy-
namically. For example, N can be based on a pre-determined secret shared
between sensors and the digital twin. Additionally, the initial hash can be
based on secure secret key, such as a one time pad.
2. In the event a man-in-the-middle attack was successful and the attacker is
able to reproduce the correct blockchain hash check, the attacker would be
required to maintain persistence to not be uncovered due to an inconsistency
in the checksum. Since the data is being altered, the hashed checksum would
differ from the value being produced by the meter. Since the SHA-256 al-
68
gorithm is distinct and difficult to reverse, explained in more detail below,
the attacker will be unable to cover the false data injection attack because
the blockchain hash functions will never converge once even a single data-
point is altered. Therefore, once the attacker stops supplying the altered
data, which satisfies the blockchain, and the connection to the real meter is
re-established, the blockchain hash check sent by the meter will no longer
match the hash calculated at the control center.
3. By linking the current data to the previous readings, all of the previous
hashes, and therefore data, is not able to be changed by an attacker without
rehashing all of the subsequent readings. This is of particular importance
to the Digital Twin which relies on not only the current system state but
previous system states to function. This feature of the methodology bridges
the gap between secure digital twin communications and the security of the
digital twin itself. Digital twins are inherently data driven and rely on using
historical data to evaluate the current system state [8] as well as future states
[2]. The Blockchain checksum can be used as a distributed data validation
technique to ensure the historical system state information being used by the
digital twin has not been altered.
5.3.1 Blockchain-based Hash
Cryptographic hash functions (CHF), such as SHA-256 [117], are mathemati-
cal algorithms that map data of arbitrary size to a fixed size bit array. Ideal hash
functions have a few notable characteristics:
They are one-way functions in that they are computationally infeasible to
invert.
They are deterministic in that the same input data maps to the same hash.
69
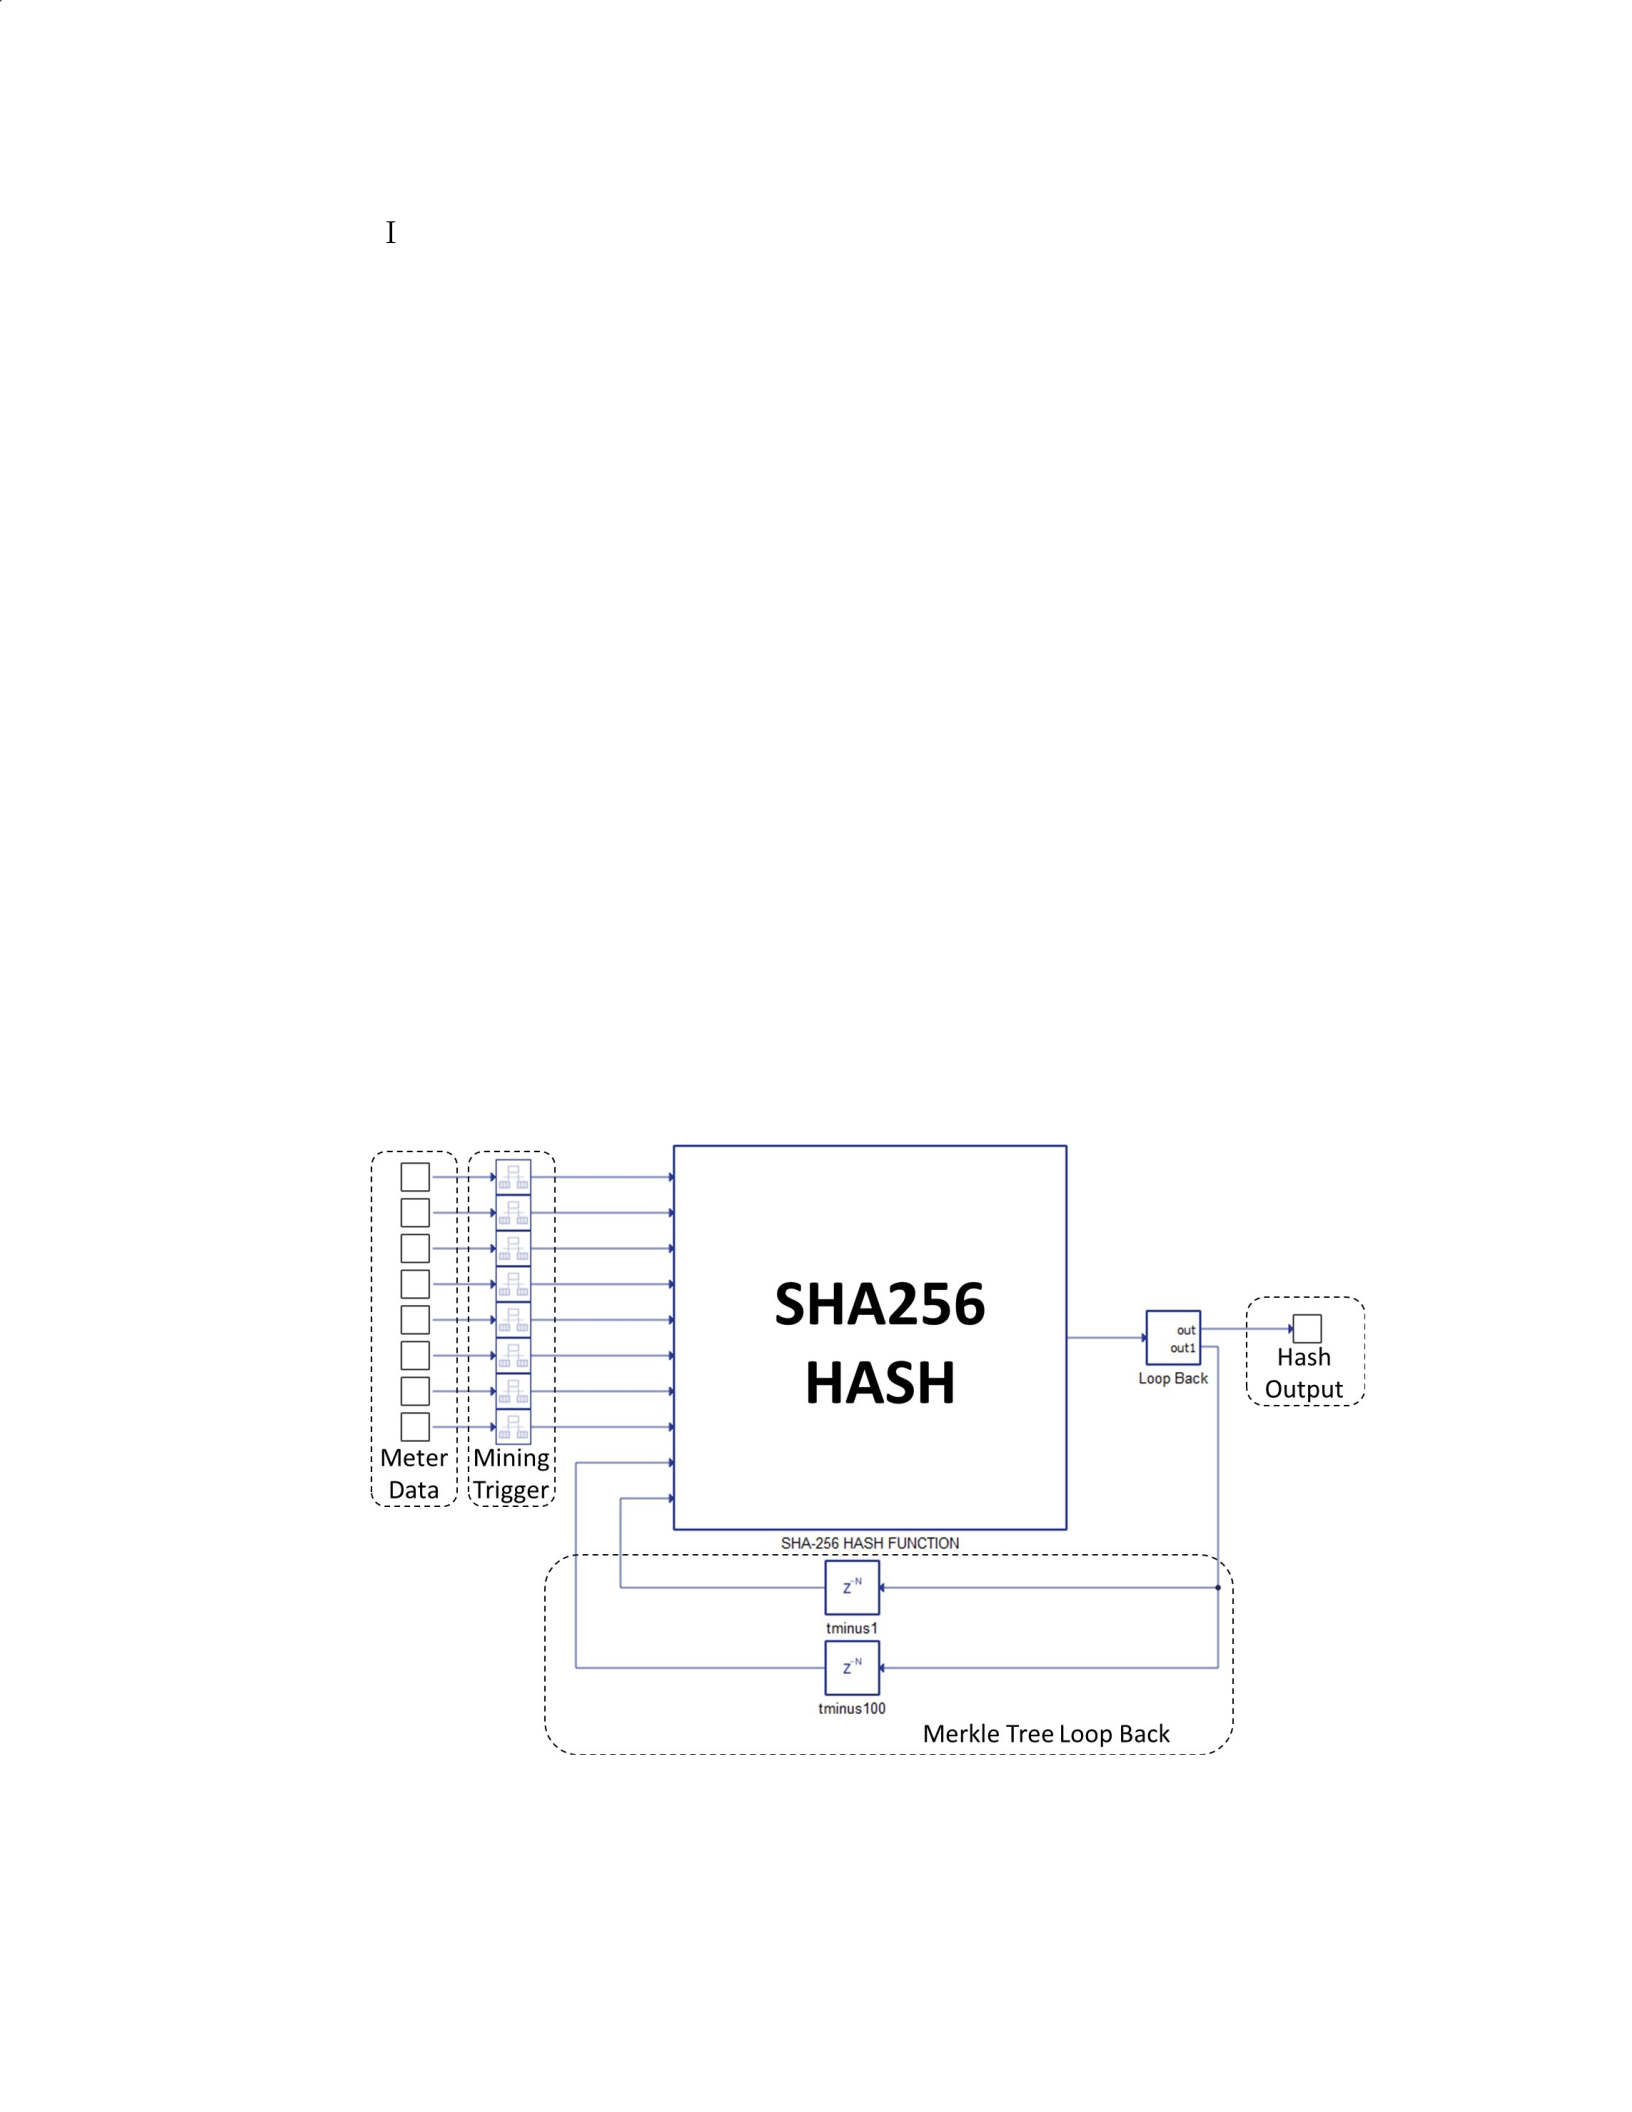
It is computationally infeasible to find two different inputs that result in the
same output hash.
The concept of a linked list of the sensor readings is leveraged to create a
secure history of sensor reading that would be difficult for an attacker to alter.
In the chained checksum, the current sensor readings are rounded to two decimal
places and then hashed along with the last hash and the historical hash value,
creating a link between the current reading and all prior sensor readings.
The SHA-256 hash algorithm is written in C and implemented directly in
the Typhoon HIL using the Advanced C code interface. The SHA-256 algorithm
takes the sensor readings and the hash output from the previous sensor readings
as inputs. The output of the hash is combined with the raw sensor data and
passed to the communication protocol compiler. The historic data is incorporated
in the Typhoon model using two loop back connections and with delay blocks. The
Typhoon implementation of the Blockchain checksum is shown in Figure 29.
Figure 29. Blockchain Implemented in the Typhoon HIL Model [6]
70
5.3.2 Limitation of Blockchain Approach
While this approach is not dependent on sampling rate, the calculation of
the hash does add a small amount of overhead to the network communications.
This could become an issue if the sensor on the physical system has a very high
sampling frequency such as a
µ
PMU or in systems with fast transient behavior
such as electromechanical or electromagnetic systems.
While the communication packets are not often dropped in the operational
technology (OT) network, it is possible that packets could be lost due to network
congestion or other non-malicious reasons. When a data sample is not reported, the
Blockchain will inherently be broken and trigger an alarm in the SCADA system.
The Blockchain will need to be reestablished so the checksum accompanying the
next data sample will be treated as an origin block for that sensor. This would
make it difficult for the control center to verify the next packet because it would
be lacking the hash from the previous state. If the chain was to be broken by
a dropped packet, the control center would likely be required to send an out-of-
cycle request for the missing data. More sophisticated methods to reestablish the
blockchain could also be developed such as using a secure seed to reestablish the
blockchain.
5.3.3 Establishment of Secure Baseline Hash
In the event that the hash is broken, an alarm would be raised in the control
system and the system operator would be notified or, in a smart system, the auto-
mated system response would be activated to investigate the cause of the broken
blockchain. The multi-level merkle tree allows for increased insight into the cause
of the broken checksum and the lost or incorrect sensor reading can be easily iso-
lated using the data available in the digital twin system. Once the communication
fault is cleared, the system will need to reset and re-establish a secure baseline
71

for the blockchain checksum. Using the investigative triage technique mentioned
above, the digital twin system triggers one or more of the follow responses in the
sensor unit.
1. In cases where the blockchain breakage is due to a simple dropped packet
or natural occurrence, a simple reset command would be sent to the remote
sensor. This would synchronize the digital twin with the remote asset with
minimal operational impact. It is worthwhile to note, in more advanced
systems, the ”time between outages” can be used as vector for a trust module.
2. In remote and vulnerable applications, persistent threats need to be elim-
inated and clean operation is required to be verified. In these situations,
the memory of the sensor is dumped and the asset is rebooted. The startup
routine verifies the unaffected safe operating condition using the established
technique of a Trusted Platform Module (TPM). The TPM is a hardward
chip that contains a storage root key that is embedded with the TPM hard-
ware. Using the checksum from the TPM as the baseline hash would be
effective to verify that the sensor hardware has not been compromised while
also establishing the first elements in the restarted blockchain.
5.3.4 Required Features for Sensors
This methodology requires the sensor to be able to compute the SHA-256 hash
in real time without a significant amount of additional latency. In the hardware in
the loop environment, the additional complexity of the SHA-256 algorithm did not
cause a computational delay and since there is not a proof-of-work requirement,
the SHA-256 algorithm is only required to be computed once per transmission.
The sensor is also required to have sufficient storage to maintain a cache of the
historical hash values. However, only the hash value is required to be saved, not
72
the raw sensor data, due to the hash only being used for data security and not as a
distributed ledger. Each hash value contains 256-bits of so 100 historical readings
represents roughly 25kb worth of data.
Figure 30. IEEE 33 Bus Benchmark Implemented in Typhoon HIL Simulator
5.4 Experiments, Results and Analysis
The IEEE 33-bus benchmark model, shown in Figure 30, originally presented
by Baran and Wu [118], is a small scale distribution system benchmark and con-
sists of 33 buses, 32 fixed lines and 5 switchable lines. While the IEEE 33-bus
model was used in the proof of concept demonstration, the methodology is fully
scalable due to the peer-to-peer nature of the outstation-control center commu-
nications. Using the Typhoon HIL, the IEEE 33-bus model is simulated in real
time enabling the evaluation of the sensor data blockchain implementation. The
real time implementation allows for the evaluation of the computational overhead
required and ensures the algorithm would work in a real world system setting.
The blockchain communication framework and SCADA communication block
73

was added to the IEEE 33-bus benchmark in the Typhoon Hardware in the Loop
(HIL) real time Simulator. The Blockchain checksum is implemented on each of the
nodes of the benchmark power system and each node runs the code independently.
While this blockchain checksum method would work using any digital twin com-
munication middleware, including Internet of Things (IoT) protocols such as Data
Distribution Service (DDS) and Message Queuing Telemetry Transport (MQTT),
or legacy power grid communication protocols, such as Modbus and DNP3, the
blockchain checksum was implemented in the Typhoon HIL SCADA system.
The Blockchain hash function calculated by the remote meter and the check-
sum calculated by the SCADA system is diplayed in the SCADA GUI for visual
verification, shown in Figure 31. When the two values match, a counter is updated
to reflect the number of data samples since the chain was last broken. This value
can serve as a rudimentary confidence measure which could be fed into a more
sophisticated trust algorithm. However, the trust evaluation is outside the scope.
Within the digital twin environment, the checksum of the sensor data is ver-
ified and the system state information is stored to be used in the digital twin
simulation environment. The historical checksums are also stored to be recalled
when required for the historical check.
To test the blockchain implementation, a series of False Data Injection (FDI)
attacks was created in the Typhoon system and the sensor data was manipulated
while in route to the SCADA system. FDI attacks are a type of cyber attack
where the attacker manipulates system or sensor data to mislead the control cen-
ter without being detected by the bad data detection algorithm [119]. In this
experiment, the FDI attack was not crafted to satisfy the state estimation and
bad data detection theory because they would have no effect on the outcome of
this method.
74
Figure 31. SCADA Display of the System State Under Normal Conditions
First, the network is run without the FDI attack and see that the hash check
is able to verify that the data is still consistent with the sensor data that was sent
by the relay Figure 31. With the system operating without an attack, the hash
values match up exactly and no alarm is triggered.
Next, the FDI attacks are added to the network and the data from the sensor
is altered before reaching the control center. In the FDI attacks, a simple scaling
is added to the voltages resulting in the control center to believe a higher voltage
is present at the bus. It is worthwhile to note, the FDI attack is executed as a
man-in-the-middle and the attacker does not have direct access to the sensor or
the control center.
In the first FDI attack, the attacker does not have access to the the historical
data readings. This could be due to the length of time required to capture the
historical data or the required memory allocate required to save the data. In
this case, the attacker is able to manipulate the voltage data transmitted to the
control station but unable to update the checksum due to the blockchain linking
the current checksum to the prior data readings.
75
Figure 32 shows the attacker is able to start manipulating the RMS voltage on
the bus at 1.5s and gradually increasing the voltage to ten percent higher than the
real RMS voltage. However, due to the attackers inability to match the checksum
due to not having the historical values, the SCADA alarm immediately catches
the attack and triggers the alarm.
Figure 32. Time History of FDI Attack 1 on Bus 702
This can also be seen visually in the SCADA system. When the data is passed
to the control center, the hash check in Figure 33 clearly shows that the values have
been altered before being sent to the control center. The control center contains
a basic comparison of the two hash checks to verify that the data is consistent at
both points.
In the second FDI attack, the attacker is assumed to have access to both the
current data readings and the historical hash values. As such, the attacker can
recreate the blockchain completely assuming the attacker has the computational
power to run a SHA-256 algorithm while operating as a man-in-the-middle. It’s
76
Figure 33. SCADA Display of the System State Under FDI Attack
worthwhile to note, that all three of these capabilities (persistence, memory space
and computational resources) expand the attackers footprint on the infected ma-
chine and could make it easier for the intrusion detection system to uncover the
vulnerability. In this case, the attacker would be able to go undetected until the
attacker stops the attack and terminates the connection. At this point in time,
the blockchain would once again be broken and the SCADA system would trigger
an alarm. The implementation of this FDI attack in the Typhoon HIL is shown
in Figure 34
Figure 35 shows the attacker begin to alter the meter data at 1.5 seconds and
stops modifying the data at the about the 4.5 second mark. The middle plot shows
the SCADA alarm system does not recognize the FDI attack due to the attacker
having full access to the historical data. This enables the attacker to recreate
77
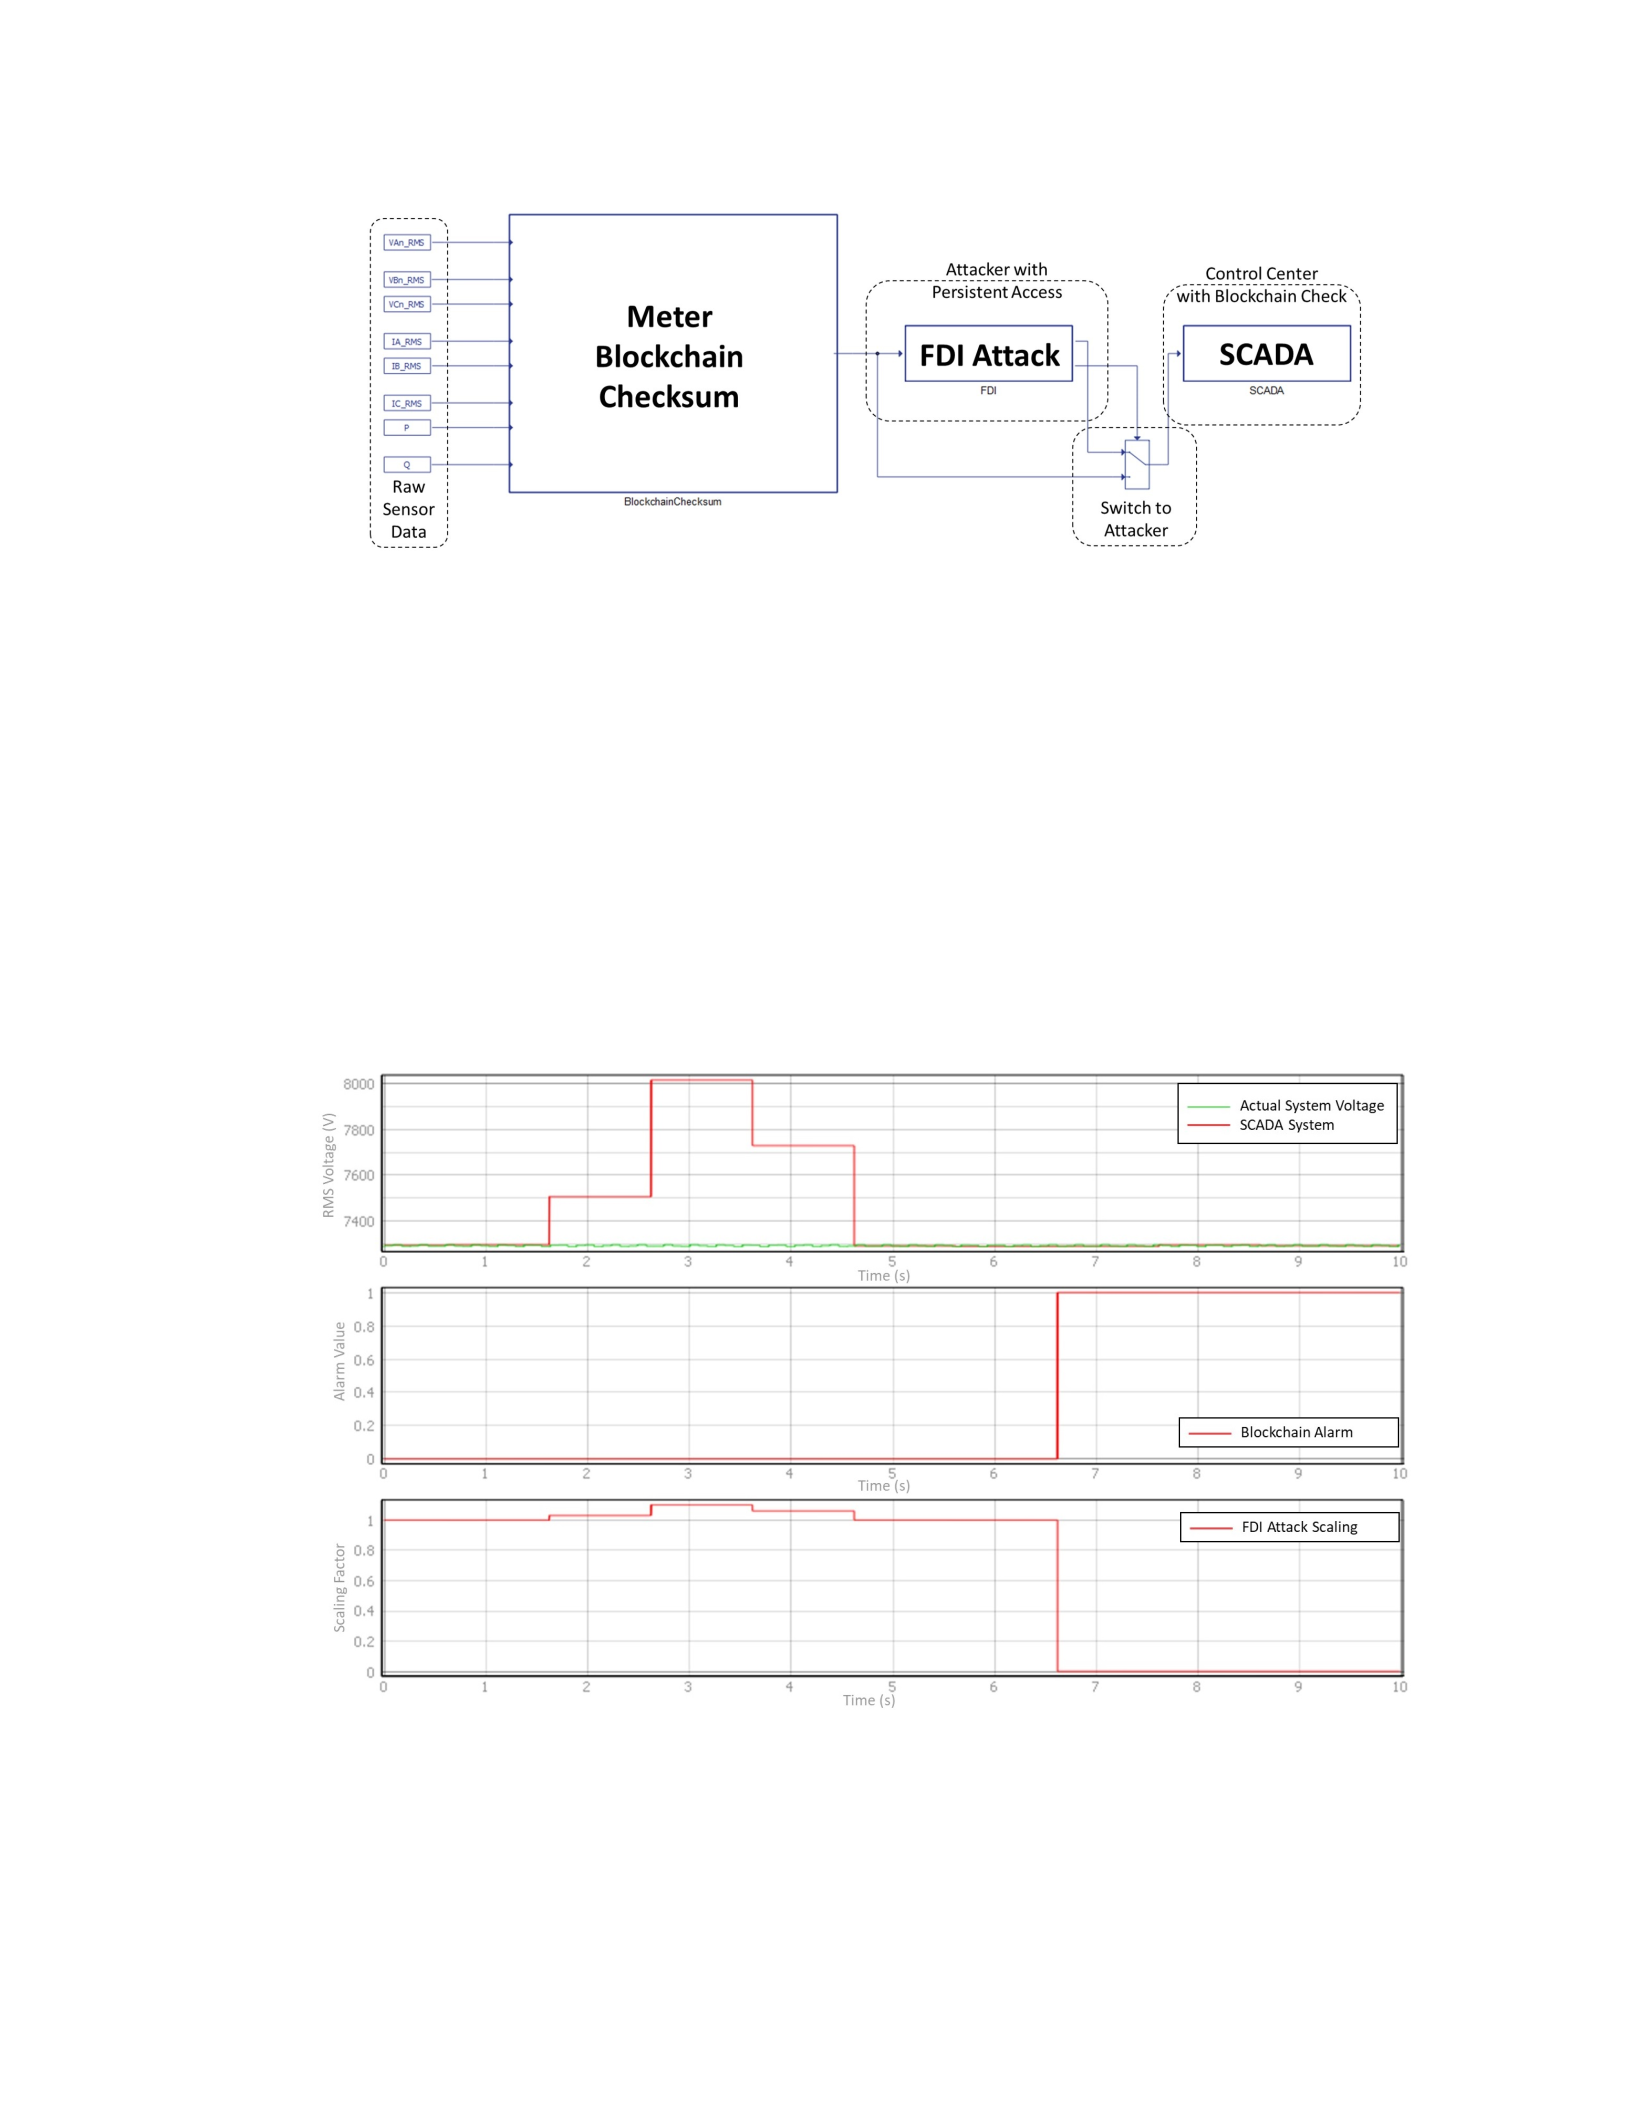
Figure 34. FDI Attack Implemented in the Typhoon HIL
the correct blockchain hash when spoofing the data. However, when the attacker
loses persistence, either through lost network access or terminating the attack,
the alarm is triggered because the true meter data does not match the blockchain
stored in the SCADA system. This is due to the meter independently calculating
the Blockchain with the correct sensor readings not the values altered by the false
data injection.
Figure 35. Time History of FDI Attack 2 on Bus 702
While you would like to catch the attacker during, or before, the attack, there
78

is still value in know that you have been compromised. For example, the vulnera-
bility can be evaluated to prevent future intrusions or if the attackers connection
drops during the attack the Blockchain would indicate the data inconsistencies.
5.5 Chapter Summary
The blockchain-based checksum provides an additional layer of security to
traditionally insecure communications. By linking the checksum to the previous
data entries, the attacker would be required to have access to the historical data
readings. This expands the attackers footprint in the network and increases the
likelihood of detection by the IDS. The blockchain checksum was able to detect
the FDI attack when the attacker does not have the historical sensor values and
was still able to provide some value when the attacker has full knowledge of the
system. The blockchain implementation shows promise to create a data verification
technique that doesn’t require significant overhead for the remote sensor or the
SCADA system. More sophisticated hash algorithms or cryptographic techniques
could also be used to increase the security of the checksum by increasing the
difficulty for the malicious attacker.
79

CHAPTER 6
Cyber-Physical Testbed Development and Real-time Implementation
6.1 Chapter Overview
To explore Digital Twin technology it is imperative to have a physical system
or high fidelity surrogate to act as the “physical twin”. The proposed work is to
look into applying digital twin technology to the Smart Grid so a power system
would be required to develop the digital twin. However, using a real power system
for this type of research would be very expensive and possibly dangerous. To over-
come the aforementioned limitations of physical systems, a high fidelity hardware
in the loop (HIL) simulator is used to act as the surrogate for the physical power
system. Using a HIL to simulate the power system has a number of benefits:
1. The system runs in real time and can simulate the full power system dynamics
along with the cyber connected sensors and monitoring devices.
2. Real hardware controllers and Intelligent Electronic Devices (IEDs) can be
connected to the HIL to create accurate real-time responses to events.
3. No need to transmit real power so the simulations are significantly safer than
using a real power system.
4. No risk of damaging devices during testing.
The Smart Grid Research Lab at the University of Rhode Island is uniquely
positioned to assist with this effort. The Smart Grid Research Lab is designed
from the ground up to emulate a smart grid control center. The lab is equipped
with two Hardware-in-the-Loop (HIL) simulators, multiple power system control
devices, a high powered deep learning server, and a range of networking devices.
80

The HIL simulators create a flexible modeling environment that are capable of
simulating a wide range of systems in real-time. The focus of the HIL simulators
is on the modeling of cyber physical power systems including all required com-
munications. Attached to the HIL system are commercial and industrial grade
power control hardware that function as cyber physical devices. The relays and
controllers monitor and control elements of the smart grid running on the HIL
simulator. The deep learning server contains eight state-of-the-art GPUs that al-
low for the training of very large neural networks as well as real-time inference of
trained models. The smart grid components are linked together by a cyber net-
work testbed that contains managed and unmanaged network switches as well as
multiple software defined network (SDN) switches. The cyber testbed allows for
the modeling and simulation of attack and defense scenarios on the cyber layer of
the system to evaluate the resiliency of a power system to a cyber attack. The
dedicated hardware-in-the-loop simulators allow for the real-time simulation of
complex power system dynamics without loss of fidelity. This allows for more ac-
curate and in-depth studies that would not be possible with conventional hardware.
The hardware-in-the-loop environment also allows for the easy transition between
benchmark test systems with limited downtime resulting in a thorough evaluation
of the developed approaches. In addition to my contributions, Dr. Gabriel dePace
played a key role in the research and implementation of the cyber physical testbed.
Additionally, Dr. Zhenhua Wang, Stephanie Murphy, and Zach deWardener also
contributed to various aspects in the research of the Smart Grid Research lab.
6.2 Smart Grid Research Lab Capabilities for Real-Time Hardware-
in-the-loop Experiment and Evaluation
Using the Smart Grid Research Laboratory at the Fascitelli Center for Ad-
vanced Engineering, some benchmarks models have been created to evaluate the
81

proposed research methods. The dedicated hardware-in-the-loop simulators allow
for the real-time simulation of complex power system dynamics without loss of
fidelity. This allows for more accurate and in-depth studies that would not be
possible with conventional hardware. The hardware-in-the-loop environment also
allows for the easy transition between benchmark test systems with limited down-
time resulting in a thorough evaluation of the developed approaches Figure 36.
Figure 36. Test Coverage with Different Modeling and Simulation Techniques [7]
In order to support cyber-physical research, the devices in Smart Grid Re-
search lab are connected on two planes, the physical and the cyber networking,
shown in Figure 37. The real time hardware in the loop (HIL) simulators and
and Intelligent Electronic devices communicate over the lab based Operational
Technology (OT) network to the control station running the SCADA system and
Digital Twin framework. The HILs and IEDs use industry standard communi-
cation protocols, such as DNP3 (Distributed Network Protocol 3) and IEC6150,
82
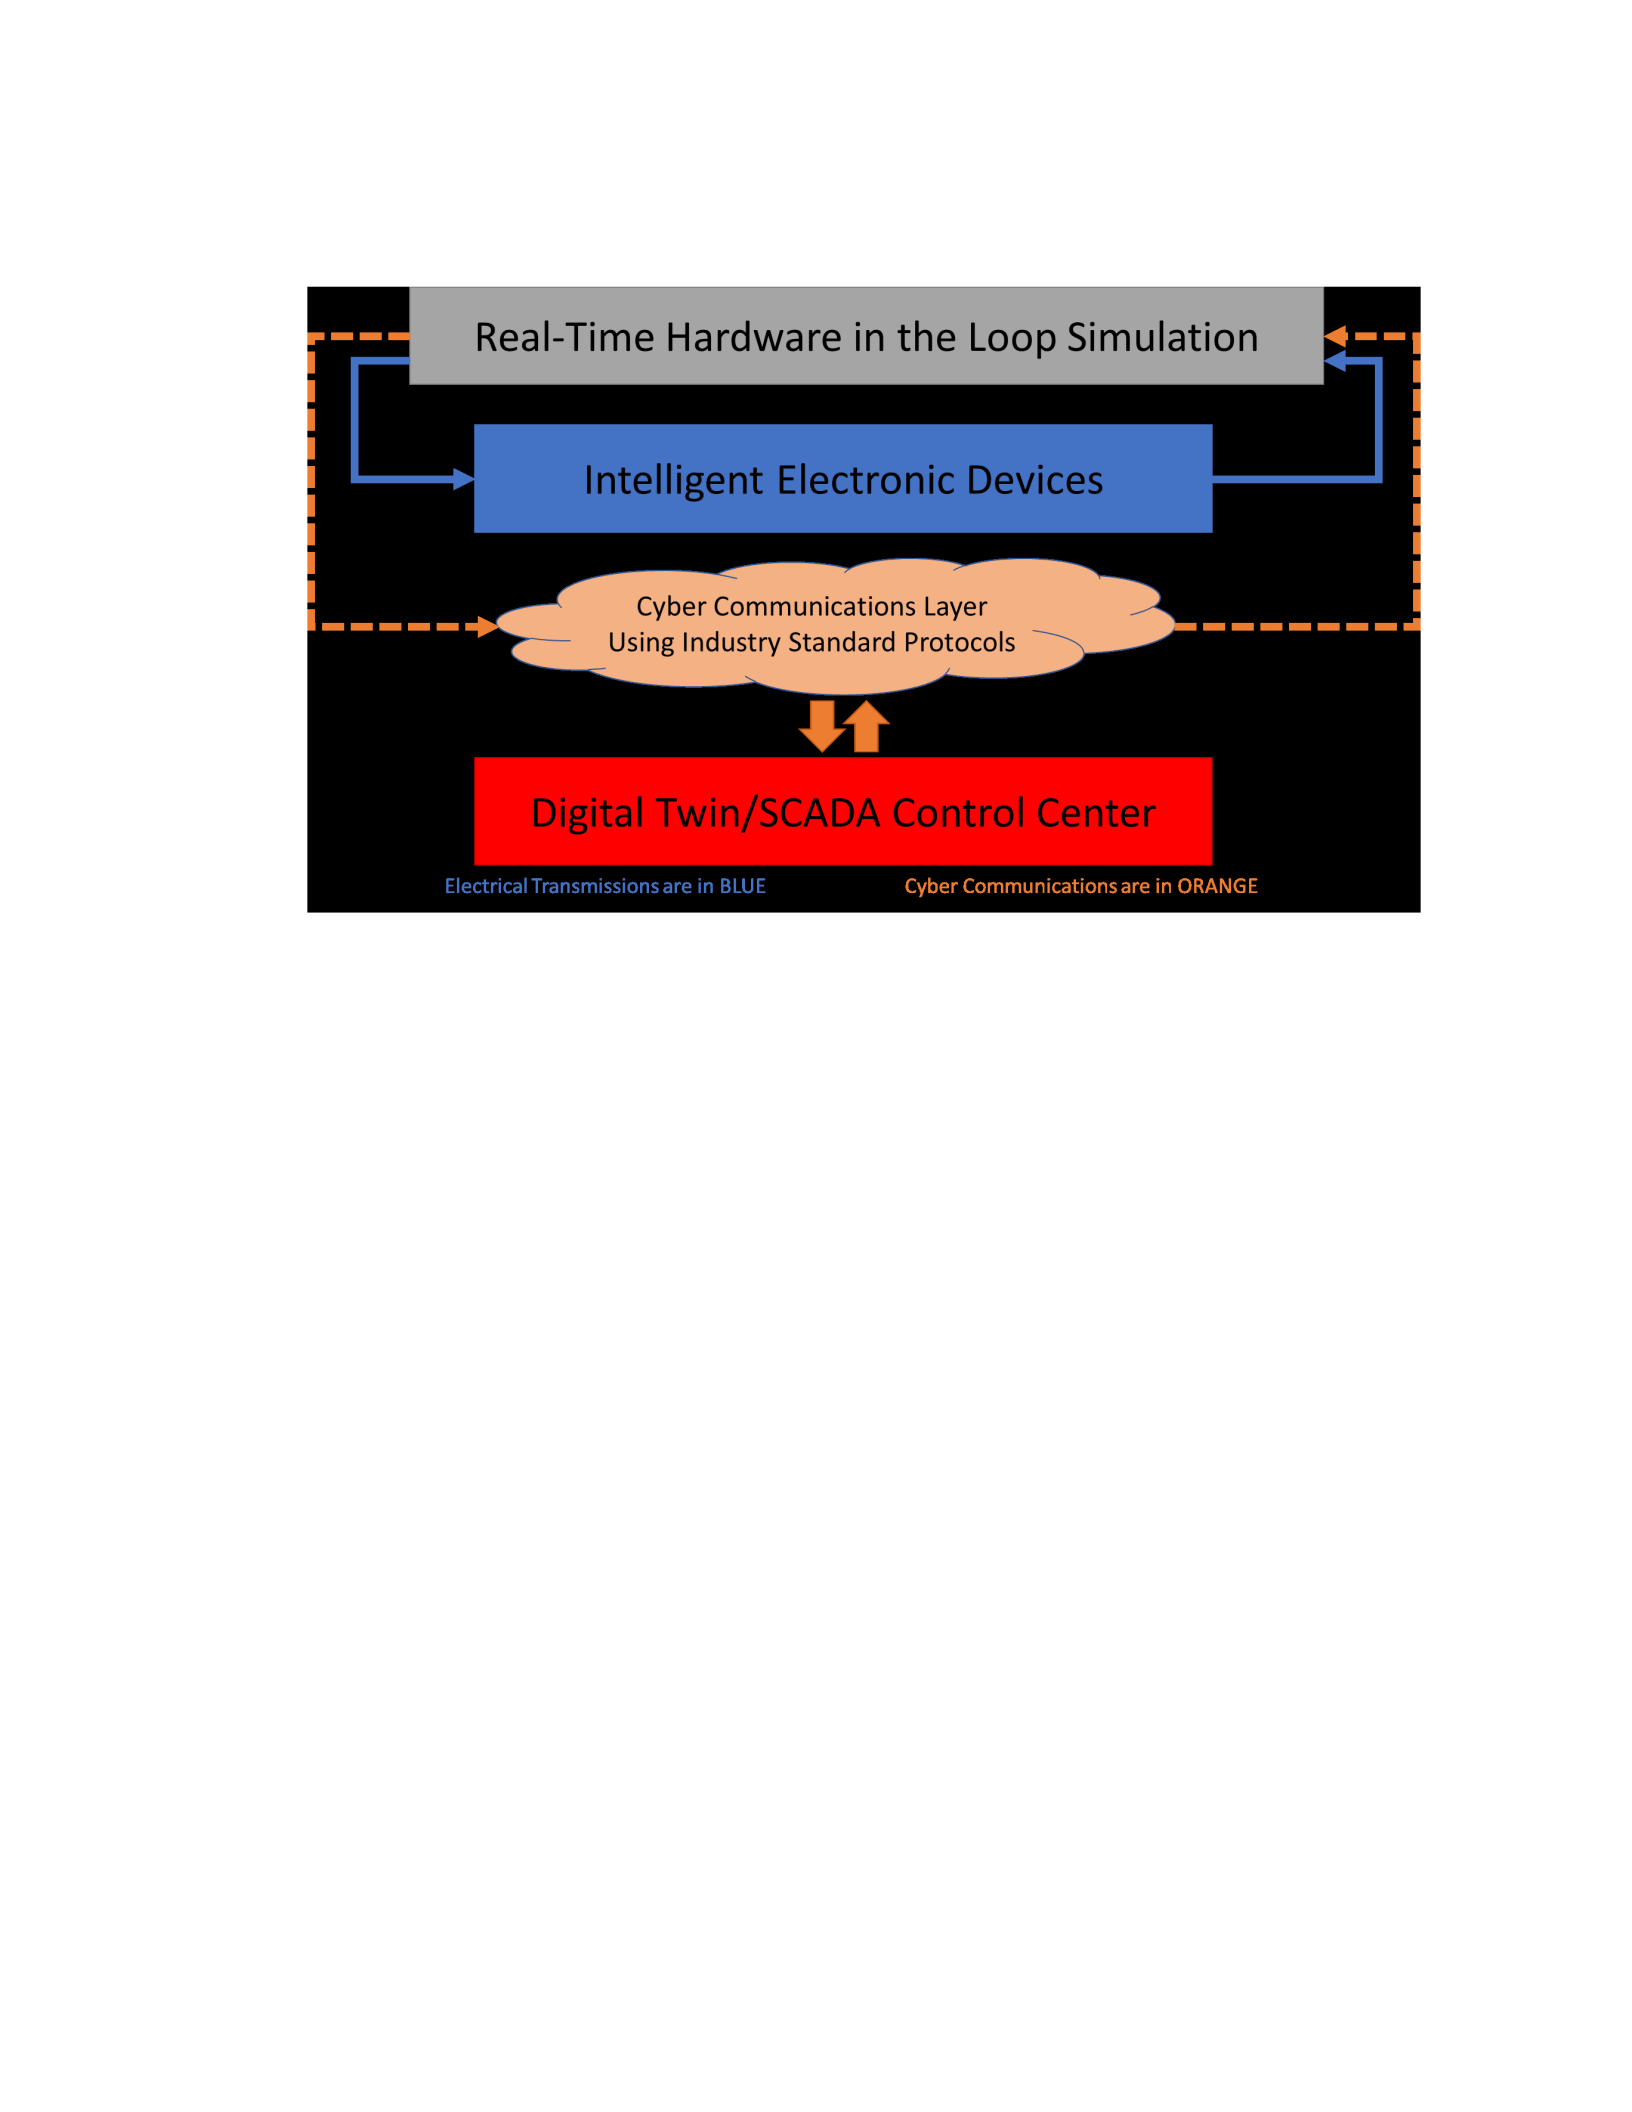
which allows for more accurate and meaningful research.
Figure 37. Smart Grid Research Laboratory Connection Schematic
6.3 Research Equipment and Resources
6.3.1 OPAL-rt Real-Time Digital Simulator OP5700
Located in the Smart Grid Research Lab, the OPAL-rt OP5700, shown in Fig-
ure 38, is the large-scale hardware in the loop simulator used by the team for power
system research. Using the HYPERSIM simulation software, the OP5700 is capa-
ble of modeling large scale power systems in real time and integrating real power
control and protection equipment into the real time simulation. The OP5700 also
incorporates real power system communications into the simulation environment,
such as IEC 61850 GOOSE and Modbus protocols. The OP5700 also incorpo-
rates a Xilinx Virtex7 FPGA to capture high frequency events, such as inverter
switching.
83
Figure 38. OPAL-rt OP5700 Real Time Digital Simulator
6.3.2 Typhoon HIL602+ Ultra-High Fidelity Simulator
Located in the Smart Grid Research Lab, the pair of Typhoon HIL602+,
shown in Figure 39, are configured into a microgrid testbed for the testing of smaller
scale power systems and power electronics where capturing of high frequency events
in high resolution is increasingly important. The Typhoon system uses custom
built FPGAs to run the ultra-high fidelity power simulations at a timestep as
small as 500ns. The Typhoon system integrates SEL protection relays, Woodward
generator control, and EPC Power solar and battery controllers into the Hardware-
84
in-the-Loop (HIL) microgrid in real time. The Typhoon system also supports a
number on power system communication protocols allowing for the modeling of
both the cyber and physical layers of the power grid. The Typhoon microgrid
testbed allows for comprehensive testing and validation of advanced primary and
secondary control algorithms in real-time.
Figure 39. Typhoon HIL602+ Real Time Digital Simulator
6.3.3 Controls Center and High Performance Computing Server
To emulate the look and feel of a Power System control room, the Smart
Grid Research lab is arranged with the primary computing hardware co-located
in the server racks. Each of the machines is connected to a workstation as well
as both the university network and the lab-based operational technology (OT)
85

network which is used to run the cyber-physical infrastructure. In addition to the
control center computers, the Smart Grid Research Lab contains a high powered
computing resource called the Bizon Z9000, shown in Figure 40. The Bizon 9000
is a high-powered machine optimized for deep learning applications. The liquid
cooled deep learning server boasts dual 20-core Intel Xeon processors. Leveraging
eight (8) Nvidia Titan RTX GPUs, the Bizon machine allows for fast training
of deep learning models and real-time inference of deep neural networks. The
computing power, and associated reduction in training time, offered by the deep
learning server vastly expands the problems that can be addressed using state-of-
the-art deep learning and deep reinforcement learning algorithms developed in the
lab.
6.3.4 SEL Relay and Power Quality Meters and SEL Software-Defined
Network Switches
Located in the Smart Grid Research Lab along with the hardware in the loop
(HIL) simulators are seven Intelligent Electronic Devices (IED) and four Software
Defined Network Switches (SDN), shown in Figure 41, to allow for the accurate
modeling of both the cyber and physical elements of real world power systems
in the lab environment. The relays and power meters are able to connect and
actively control the power system simulations in the both the Typhoon and OPAL-
rt HIL simulators in real time. The sensor readings and control actions of the
IED items are also broadcast to the lab Supervisory control and data acquisition
(SCADA) system using the laboratory test network. The lab test network consists
of the four SDNs, in addition to a few standard network routers, that support a
number of different network configurations for accurate and realistic cyber physical
simulations of smart power systems ranging from transmission to distribution to
microgrid applications. The accurate modeling of the cyber and physical layers of
86
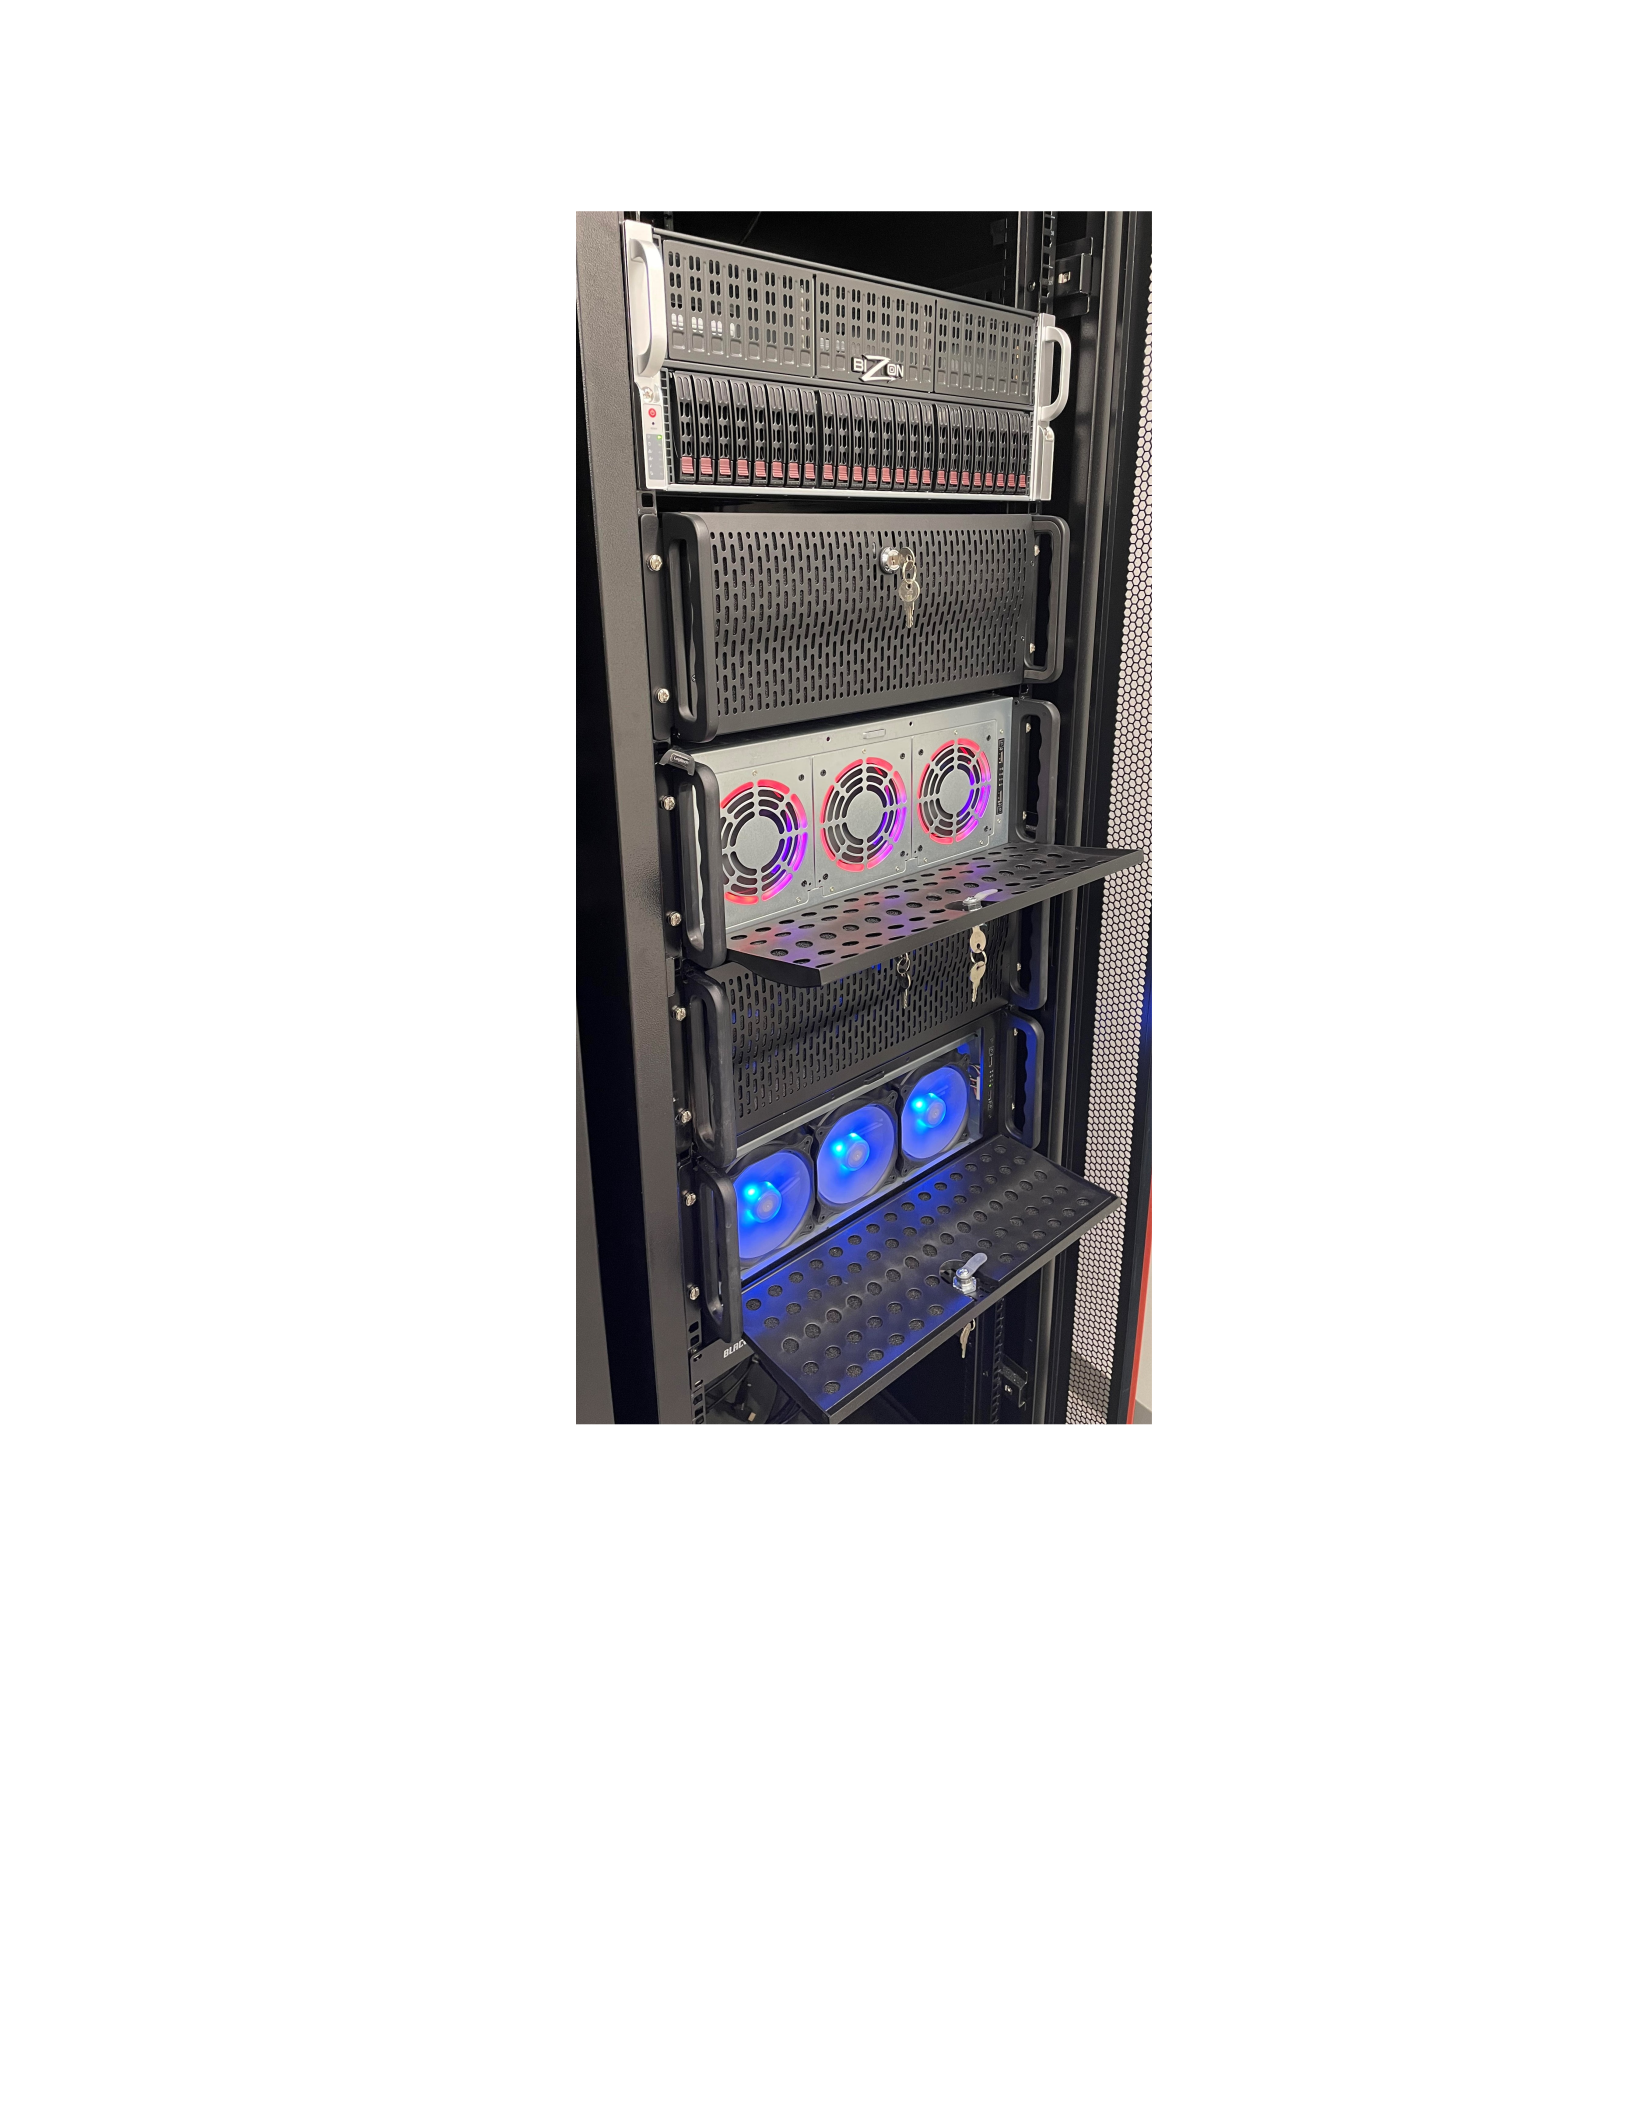
Figure 40. Deep Learning Computational Server at the Smart Grid Research Lab
the power system creates a laboratory environment that is able to support the test
and evaluation of the impacts of cyber attacks to the power grid.
87
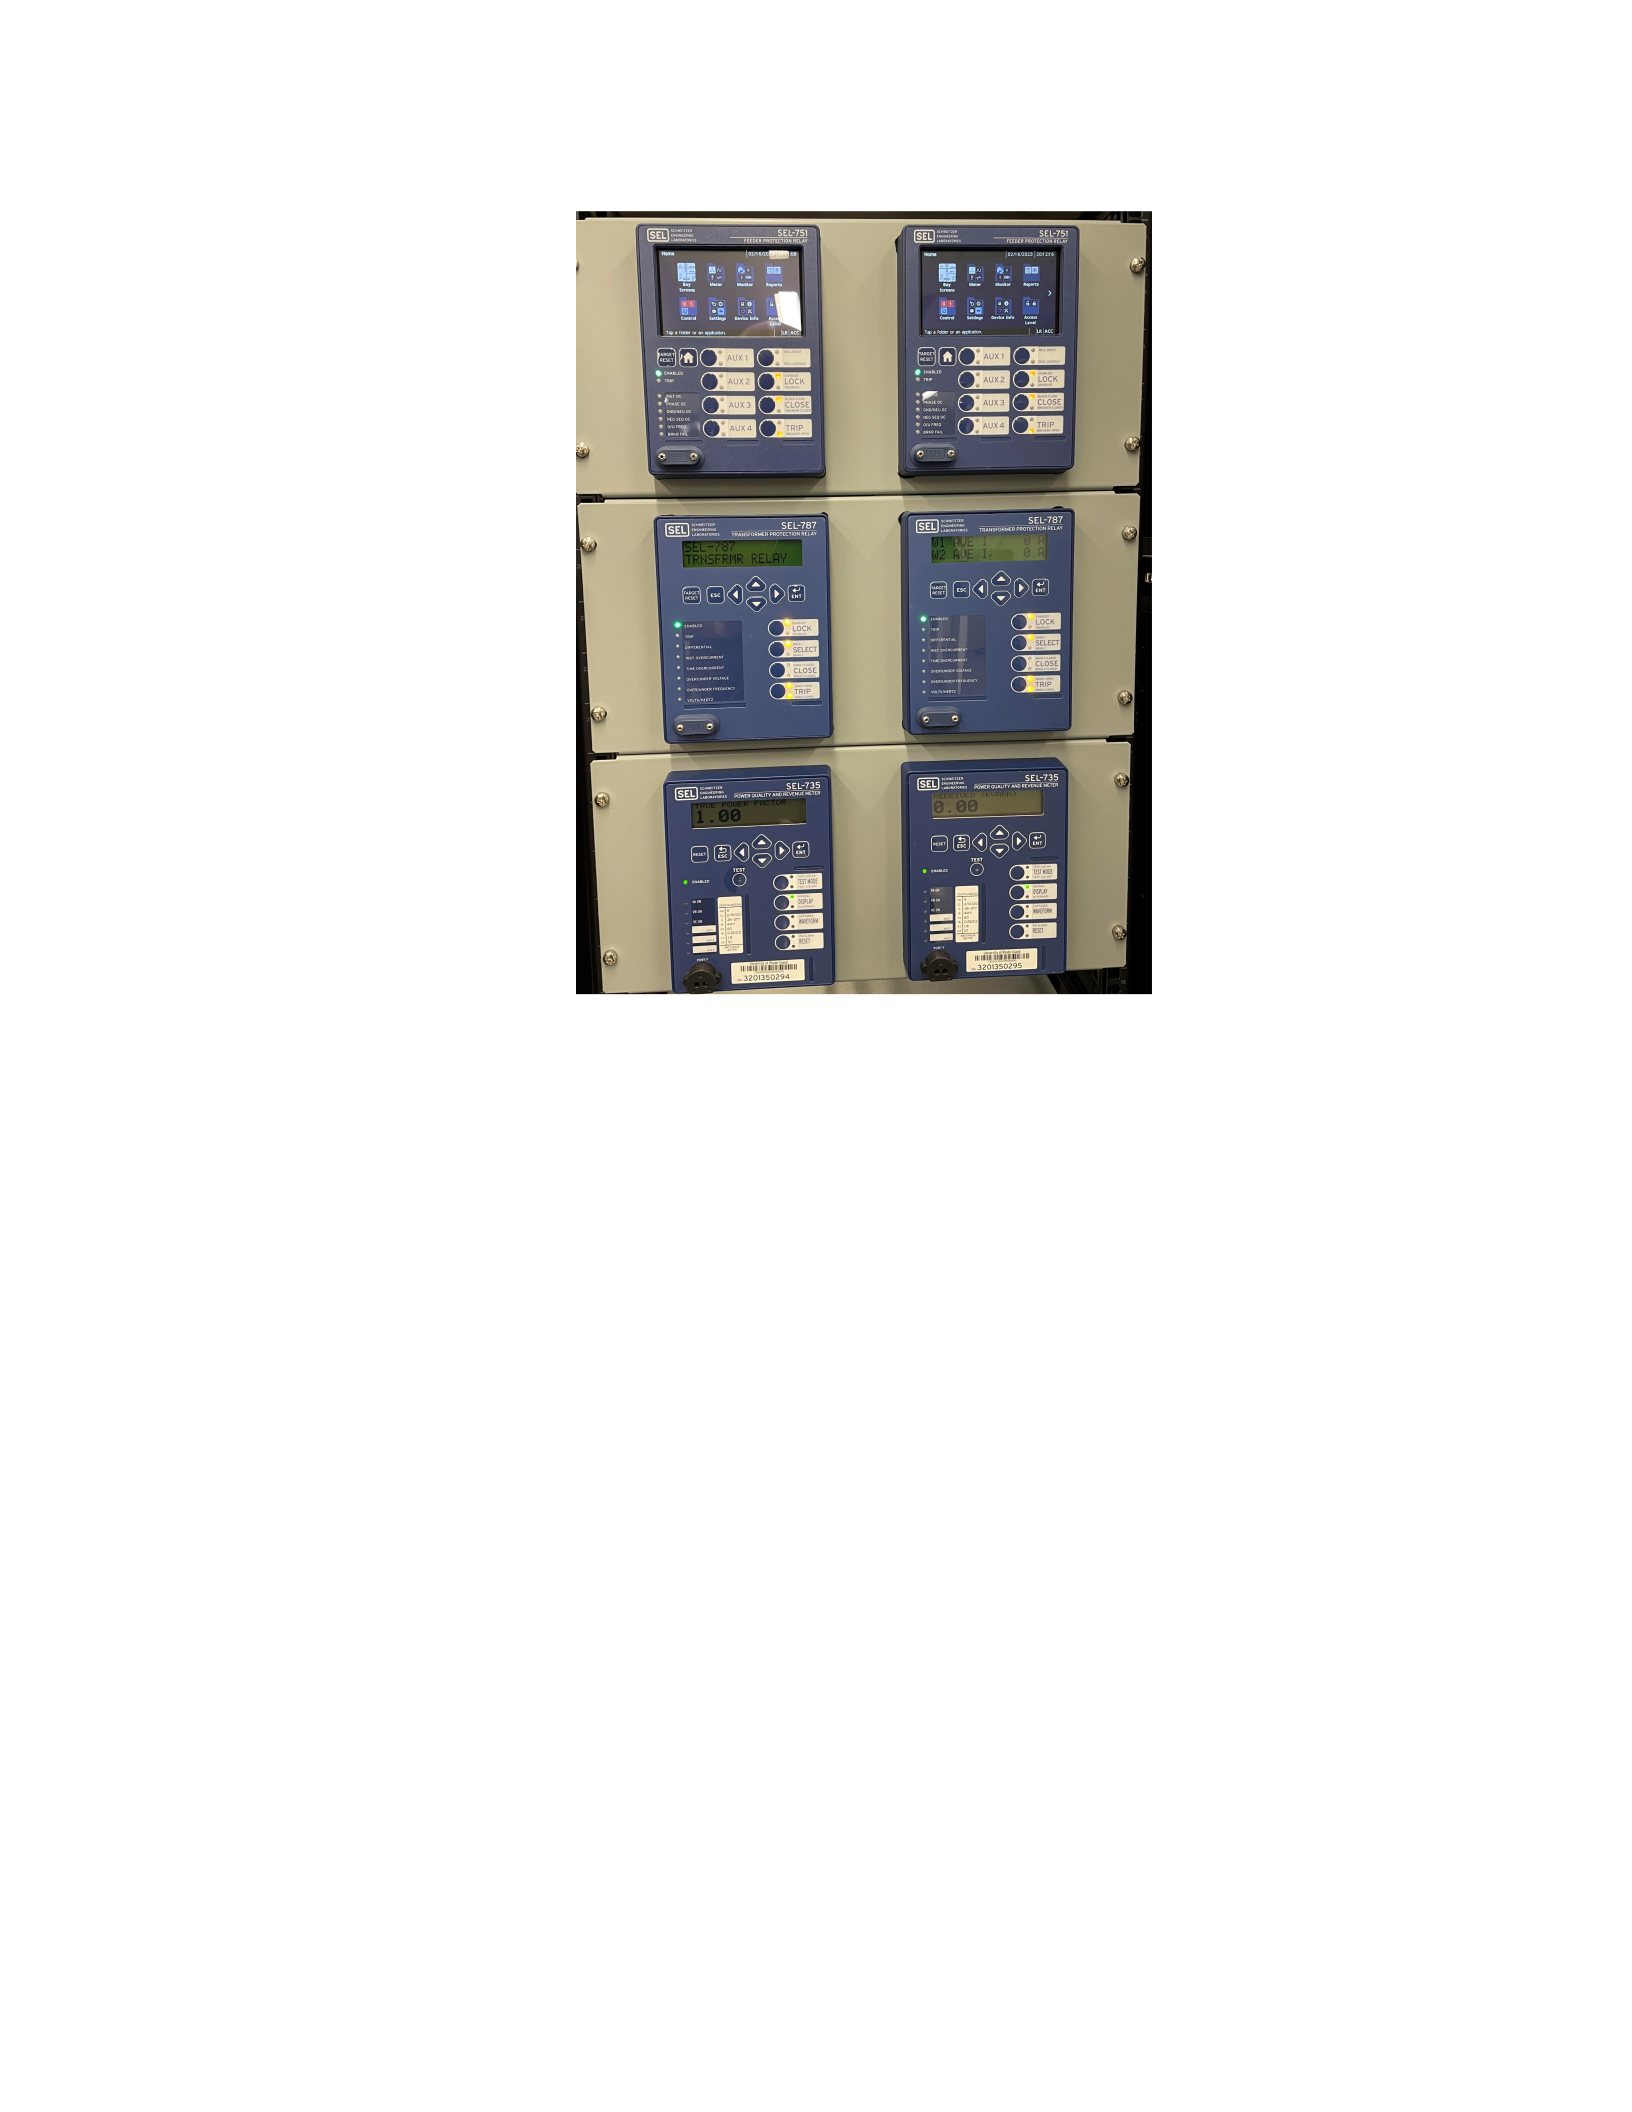
Figure 41. SEL Relays Installed at the Smart Grid Research Lab
6.3.5 Laboratory Supervisory control and data acquisition (SCADA)
environment
The Smart Grid Research Lab also features a control room setting to emulate
the SCADA system used by many power systems. The SCADA environment uses
four custom built control center computers and a 260-inch laser projection video
wall to give the look and feel of a real control room environment, Figure 42. Each
control center location has complete access to all four control center computers
as well as the power system sensor outputs and the deep learning supercomputer.
This setup allows for the testing and demonstration of complex attack and defense
scenarios in the laboratory environment.
In order to support the middleware communications between the remote sen-
sors a real lab-based SCADA system was required to be built. One of the important
objectives of the Smart Grid Research lab was to develop the core capability for
88
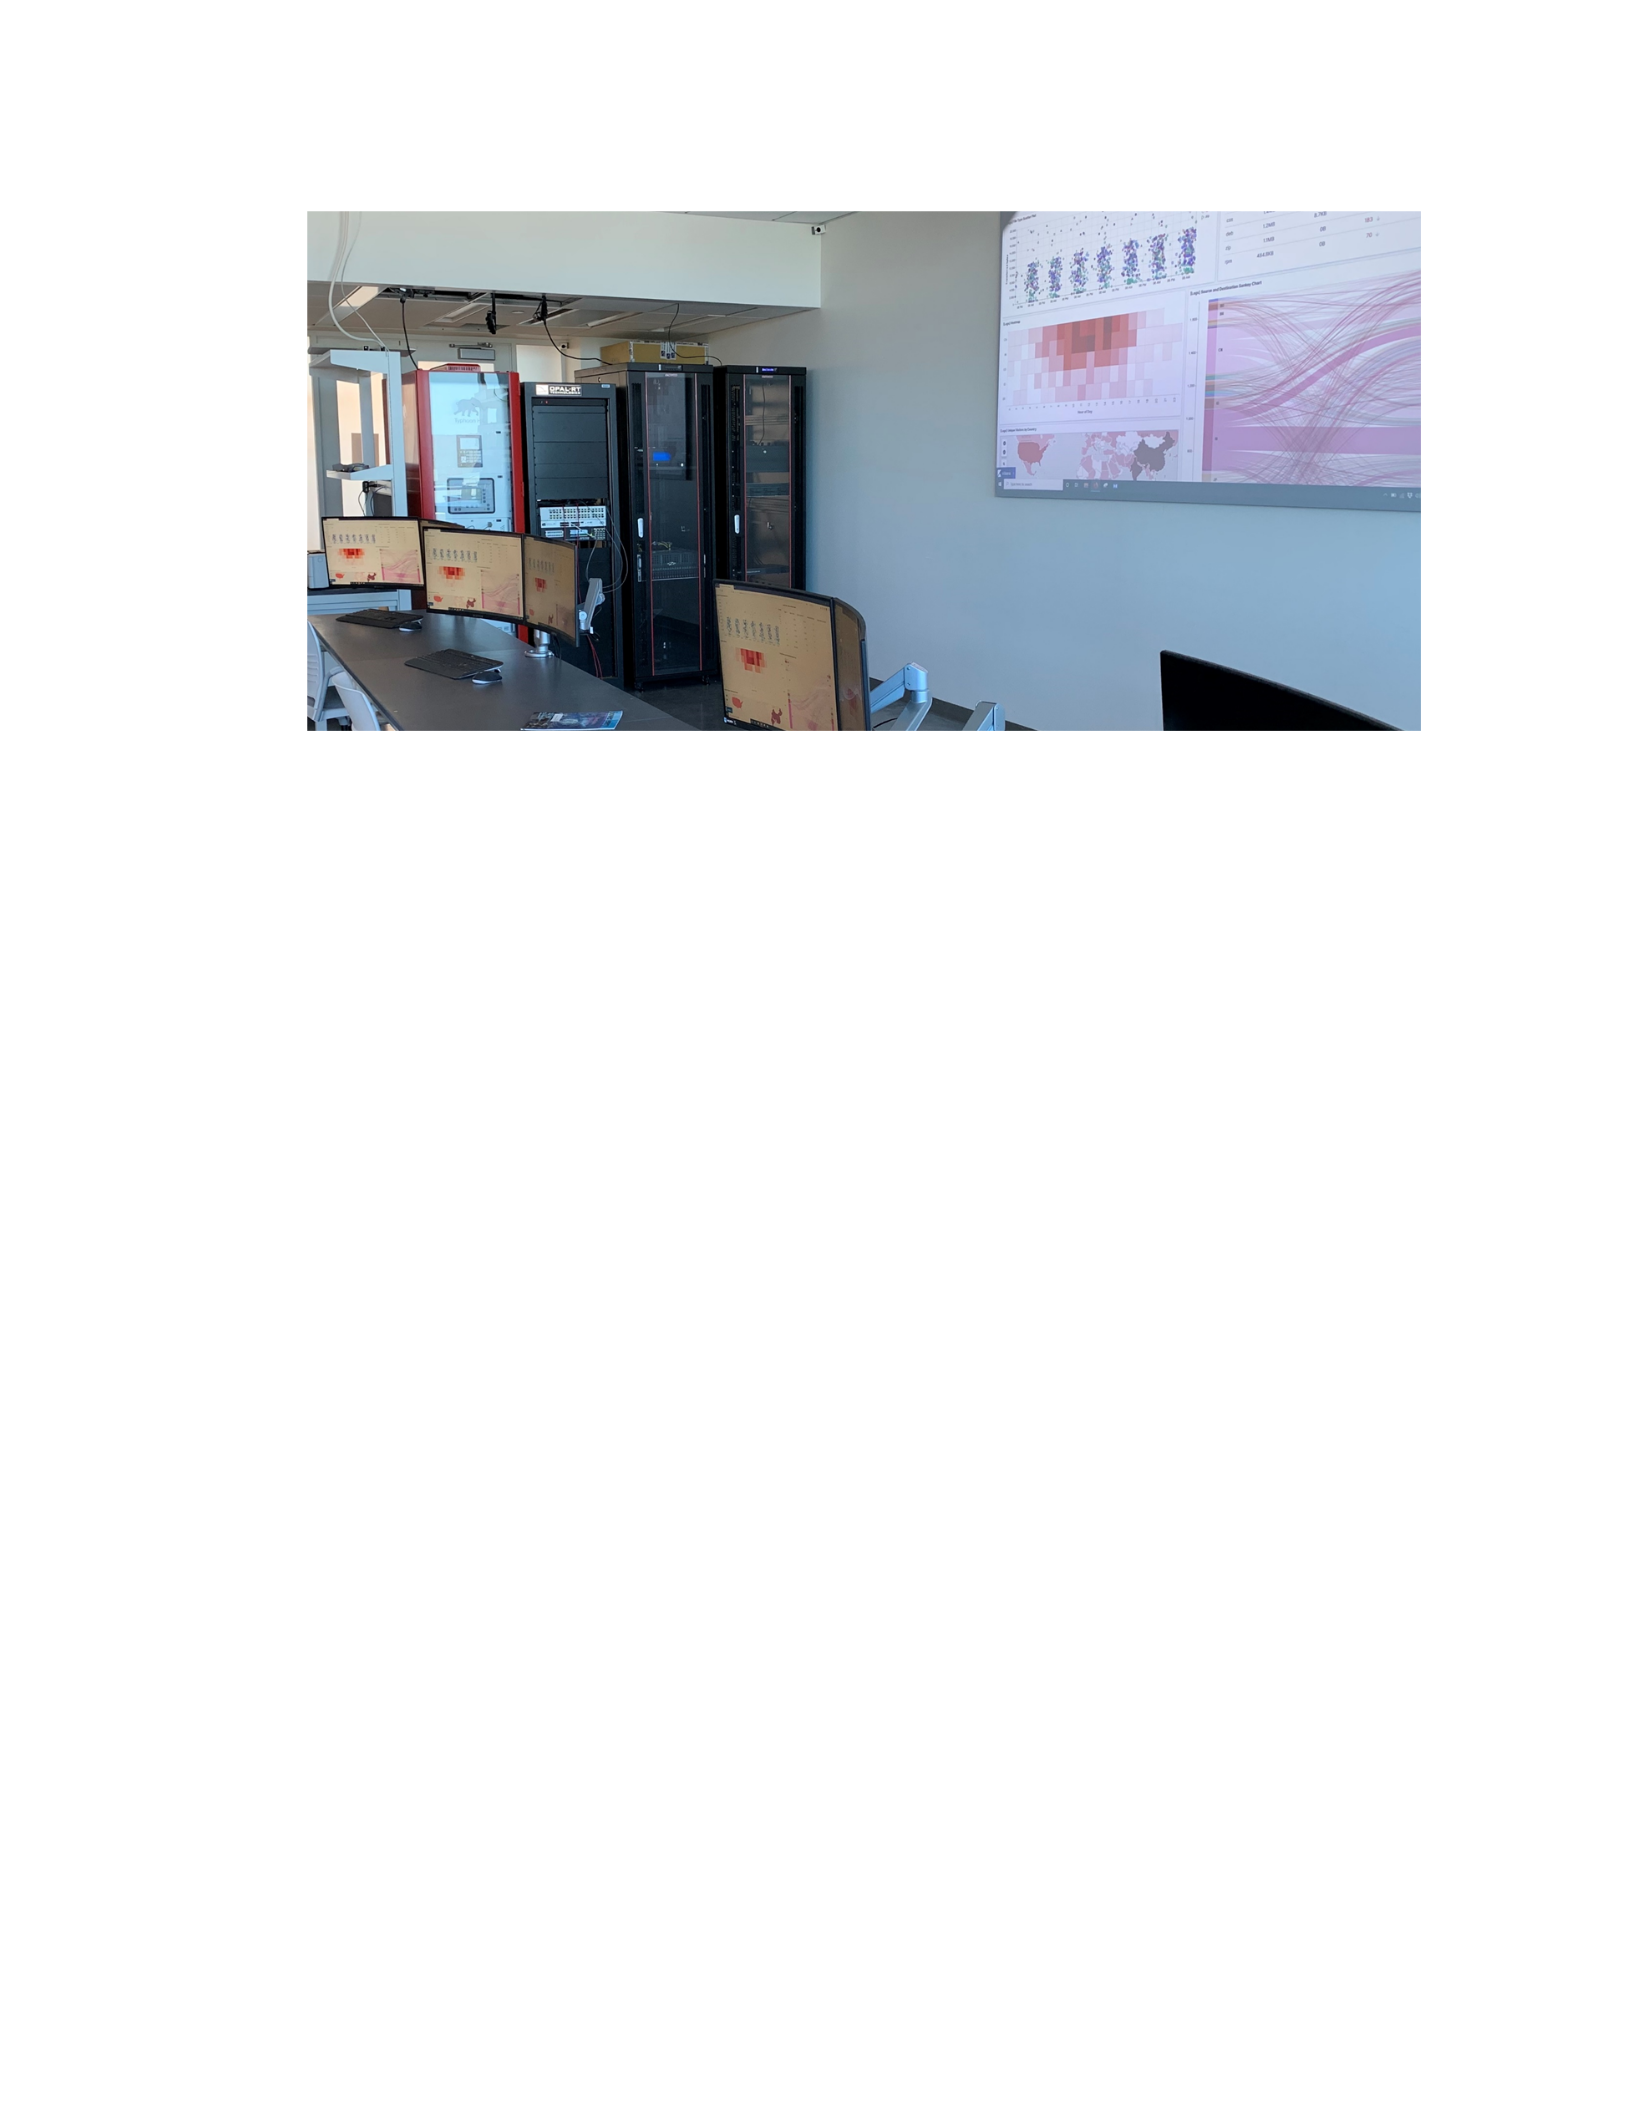
Figure 42. Control Center at the Smart Grid Research Lab
fundamental research in Cyber Physical System with a focus on the Smart Grid.
While it would have been possible to create a nominal SCADA control center to
query the remote assets, a commercial SCADA system was implemented to improve
the value of the research and potentially allow for future implementation. With the
assistance of Zach deWardener, the Smart Grid Research Lab SCADA system was
created using the Ignition SCADA system developed by Inductive Automation.
The industrial SCADA system developed for the IEEE 39-bus model is shown
in Figure 43. The interactive SCADA system was developed to communicate to
the remote sensors running in the hardware in the loop simulator. The SCADA
system acts as the control center and requests updates from the sensors using the
lab-based communication network.
6.4 Research Benchmark Models and Configurations
The Smart Grid Research lab has been built in a module concept to allow for
the testing of any power system of interest with little modification required.
89
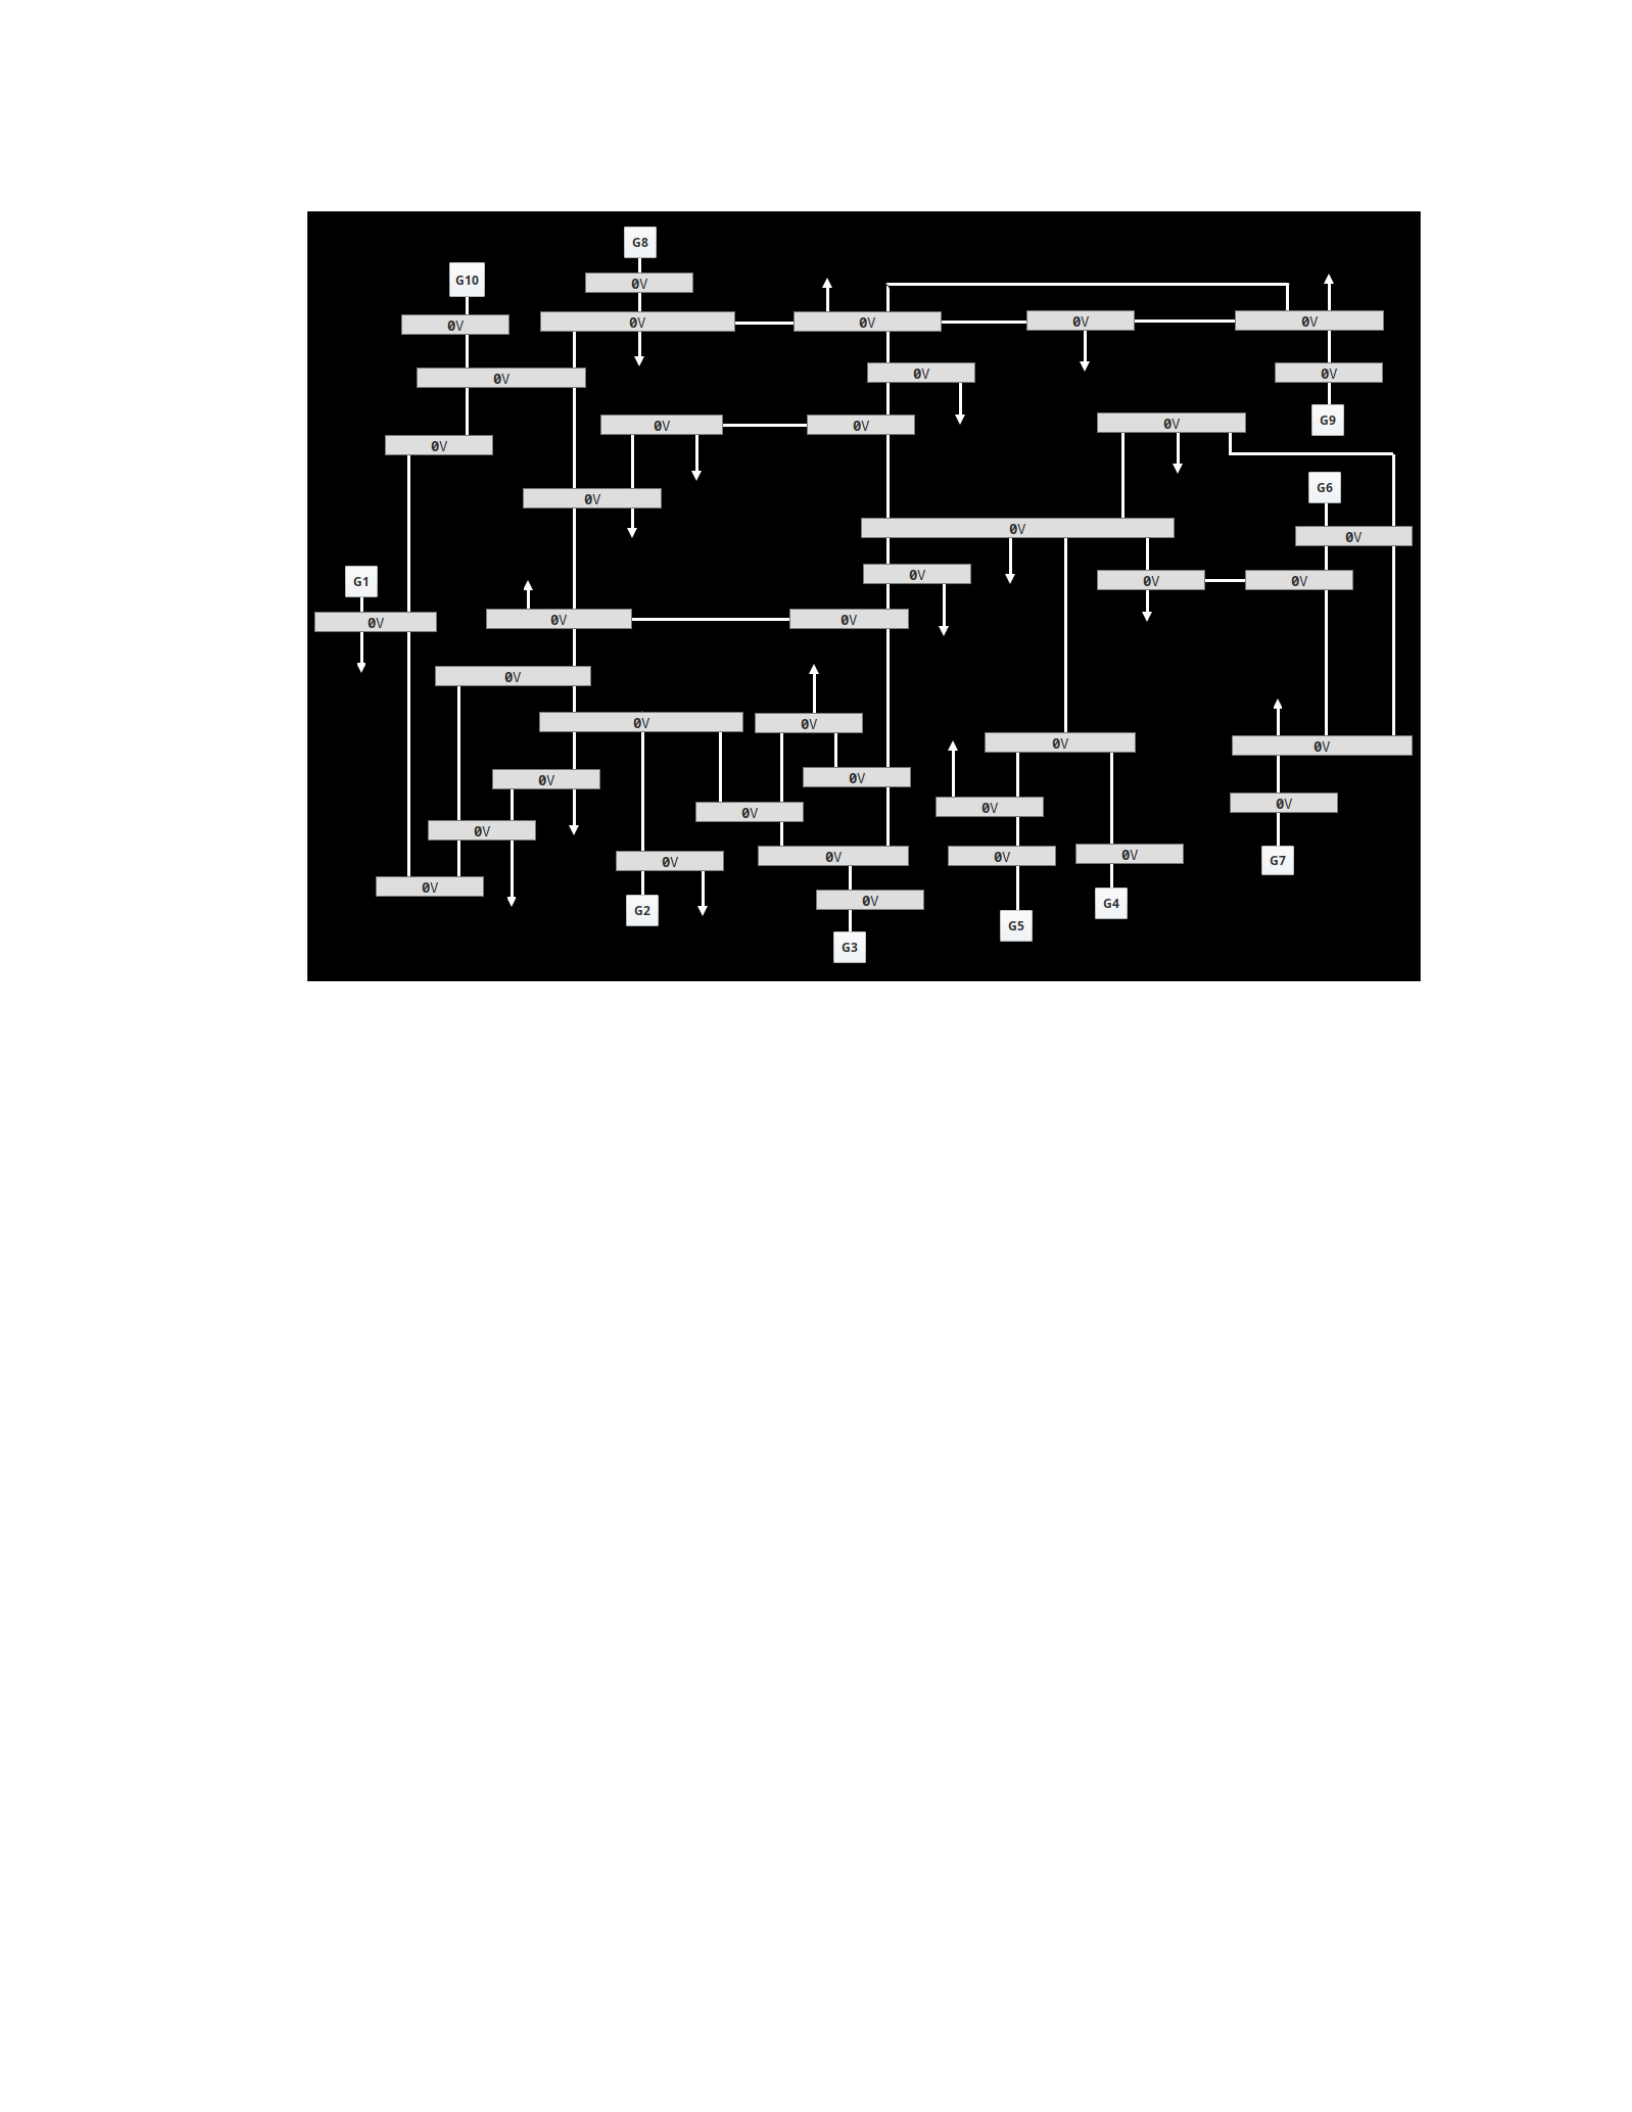
Figure 43. Industrial SCADA system for IEEE 39-Bus System
6.4.1 IEEE 9-bus Model
The IEEE 9-bus benchmark model is also known as the Western System Co-
ordinating Council (WSCC) test case. The system represents a simplified model
of the WSCC reducing the system to nine buses, and three generation units. The
one line diagram of the IEEE 9-bus model is shown in Figure 44.
In the Smart Grid Research lab, the IEEE 9-bus model is used as a simple
benchmark to test algorithms and control strategies. The IEEE 9-bus model used
in the lab, originally developed by OPAL-rt [120], has been modified to be a cyber-
physical system. The model used in the Smart Grid Research lab includes a full
cyber layer adn PMU sensors on each bus allowing the data to be monitored from
by control center computers. The model is also designed to support fault analysis
studies and is equipped with remotely activated three-phase faults on each bus.
90
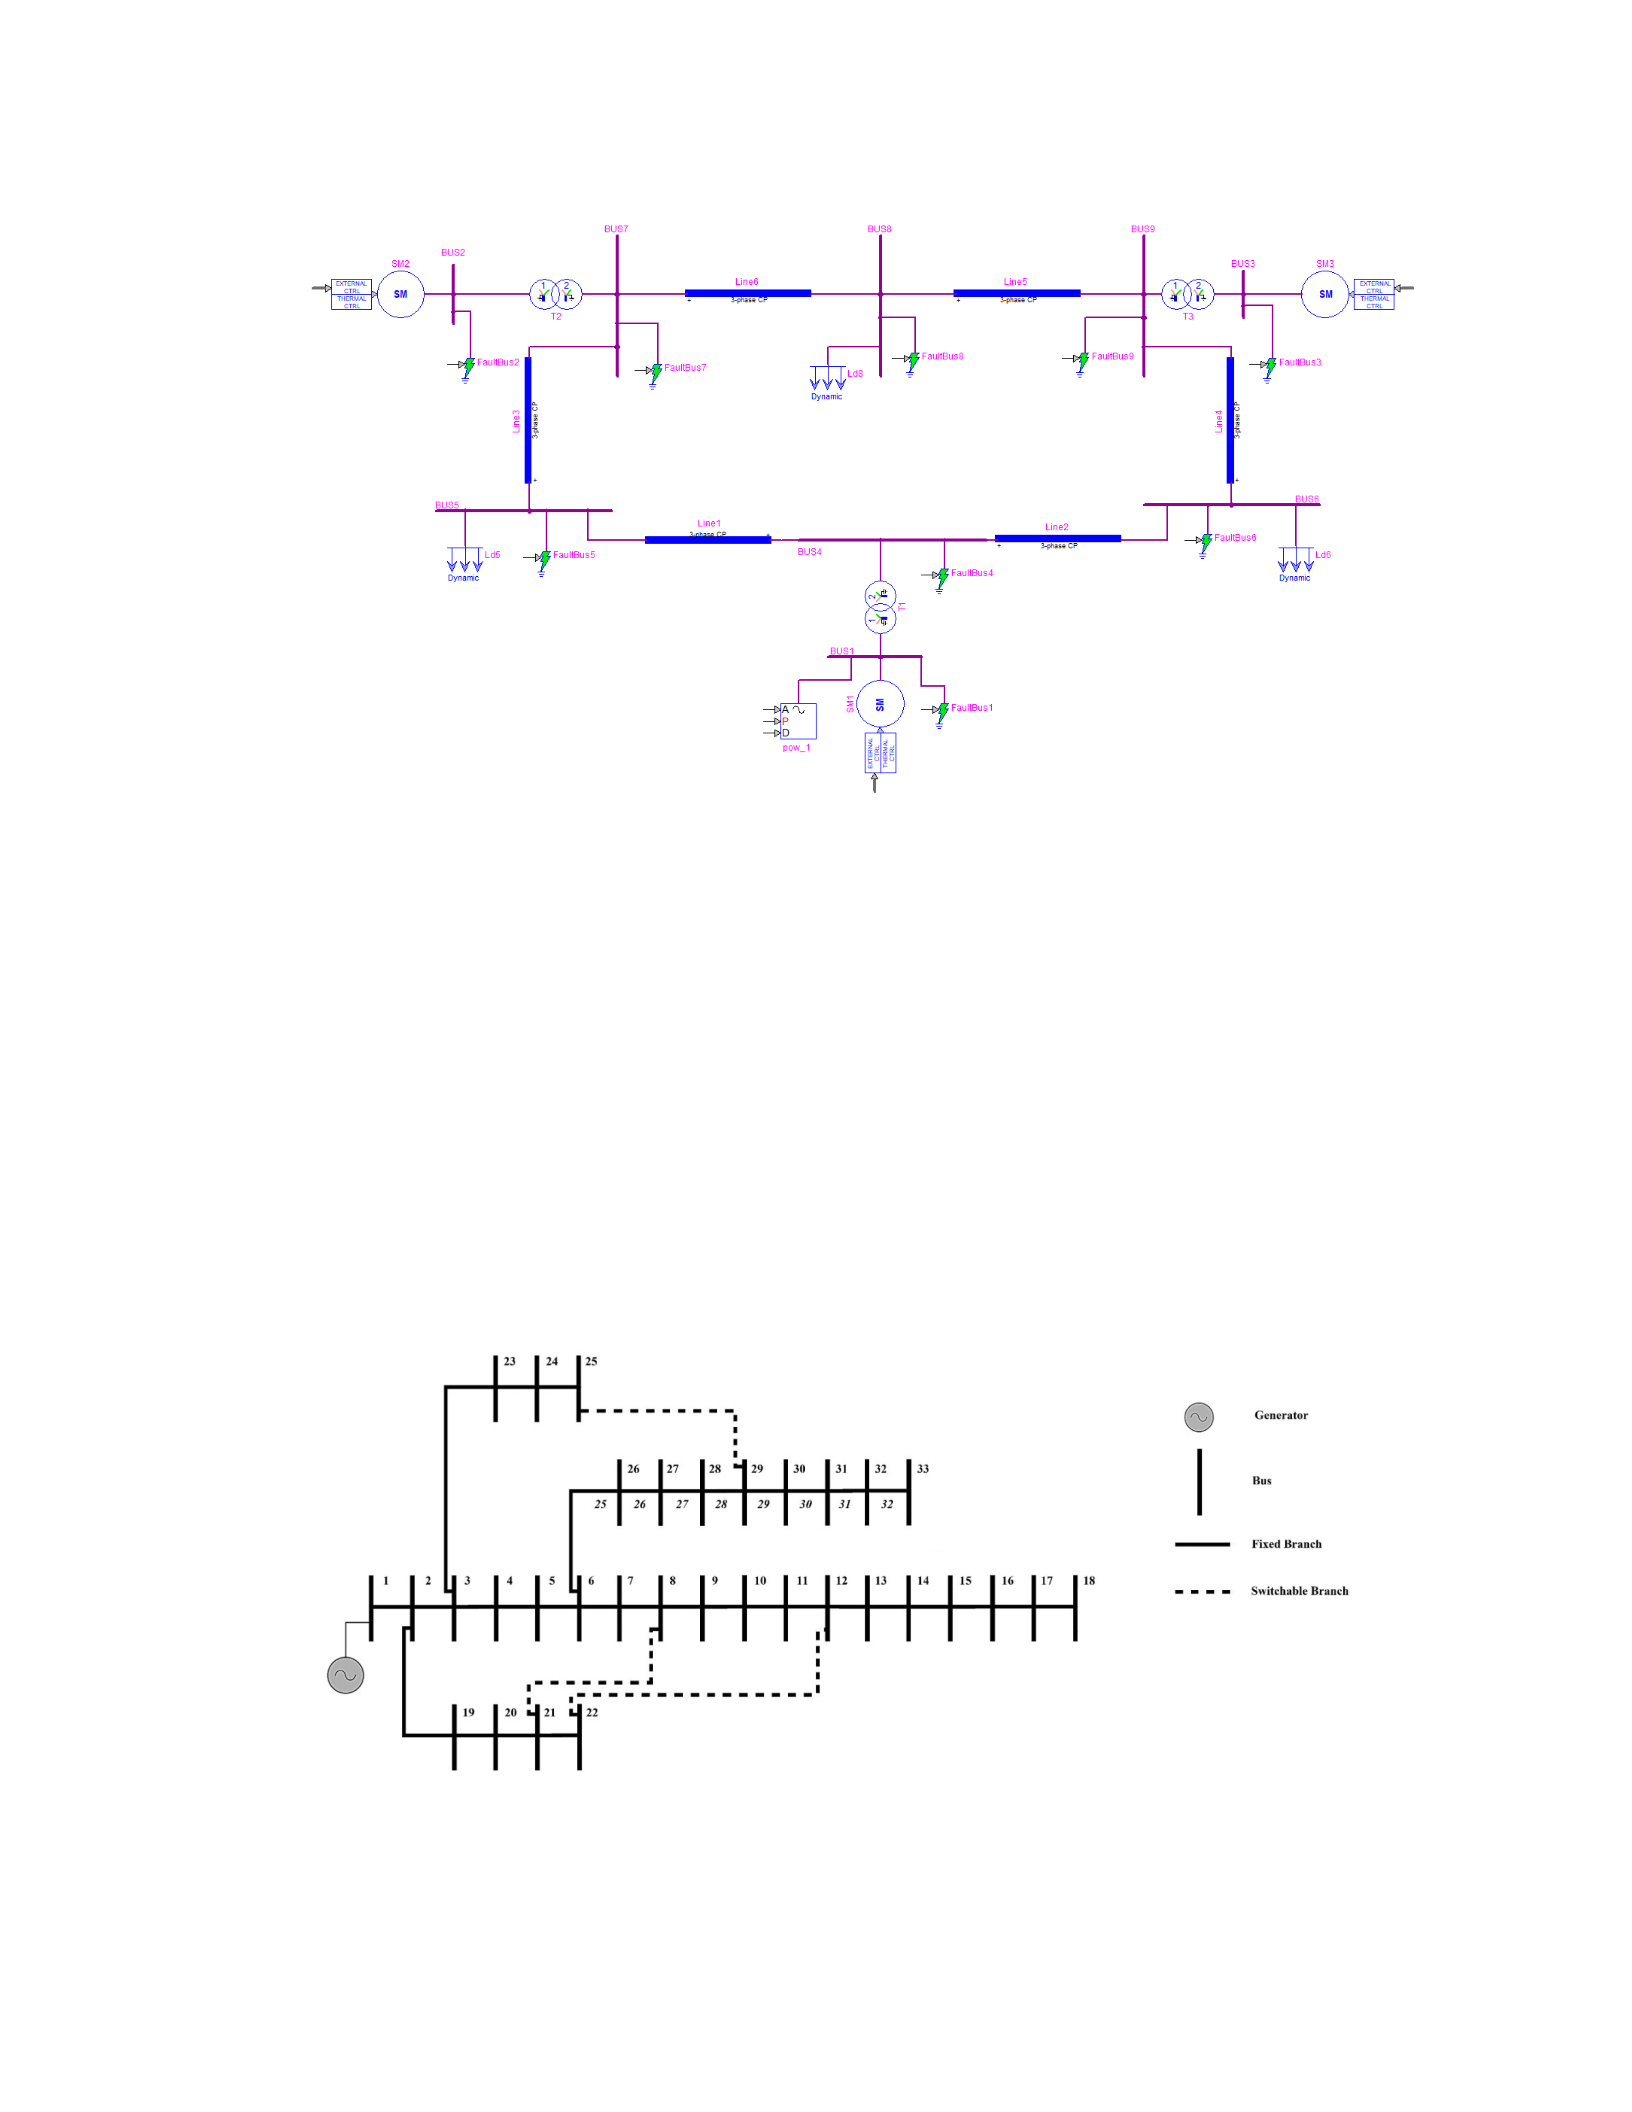
Figure 44. Modified IEEE 9-Bus Benchmark Model One Line Diagram [8]
6.4.2 IEEE 33-bus Model
The IEEE 33-bus benchmark system is a radial distribution system originally
presented in the 1989 paper by Baran & Wu [118]. The test system is a contains
a signal generation unit, 33 buses and 32 lines in the system. The system is also
equipped with three switchable tie lines that can be disabled if not required. The
one line diagram for the IEEE 33-bus model is shown in Figure 45.
Figure 45. IEEE 33-Bus Benchmark Model One Line Diagram [9]
91

This distribution system is modeled in the Typhoon HIL simulator. The sys-
tem is equipped with a local SCADA system and is the testbed for the Blockchain
checksum presented in [6] and expanded on in Chapter 6 of this dissertation. In
both of these works, the real time implementation was critical in showing that the
algorithm was able to run in real time without significant computational overhead.
6.4.3 IEEE 39-bus Model
The IEEE 39-bus benchmark model is also known as the New England 10-
Machine Power System. The benchmark model is a transmission level model and
contains ten machines, 39 buses and 19 loads. The system is a simplified represen-
tation of the New England power grid in the 1970s. The one line diagram for the
IEEE 39-bus system is shown in Figure 46.
The IEEE 39-bus model has been implemented in the OPAL-rt HyperSim
software and real-time simulator. The model has been modified to include a PMU
on each bus to communicate to the SCADA system running on the Control Center
Computers in the lab. The PMU data is transmitted using the Distributed Network
Protocol 3 (DNP3) communication protocol. The model has also been modified to
include physical faults that can be activated on each bus.
6.4.4 Grid Hardware Open Source Testbed (GHOST) Microgrid
The GHOST microgrid was developed by National Renewable Energy Lab-
oratory (NREL) and Massachusetts Institute of Technology Lincoln Laboratories
for the Microgrid and Distributed Energy Controller Symposium in 2017 [7]. The
GHOST model is a three zone, islanding microgrid with three feeders, four gener-
ation units, and 18 loads. The model also includes circuit breakers and protective
relays for microgrid control testing. The one line diagram for the IEEE 39-bus
system is shown in Figure 47.
92
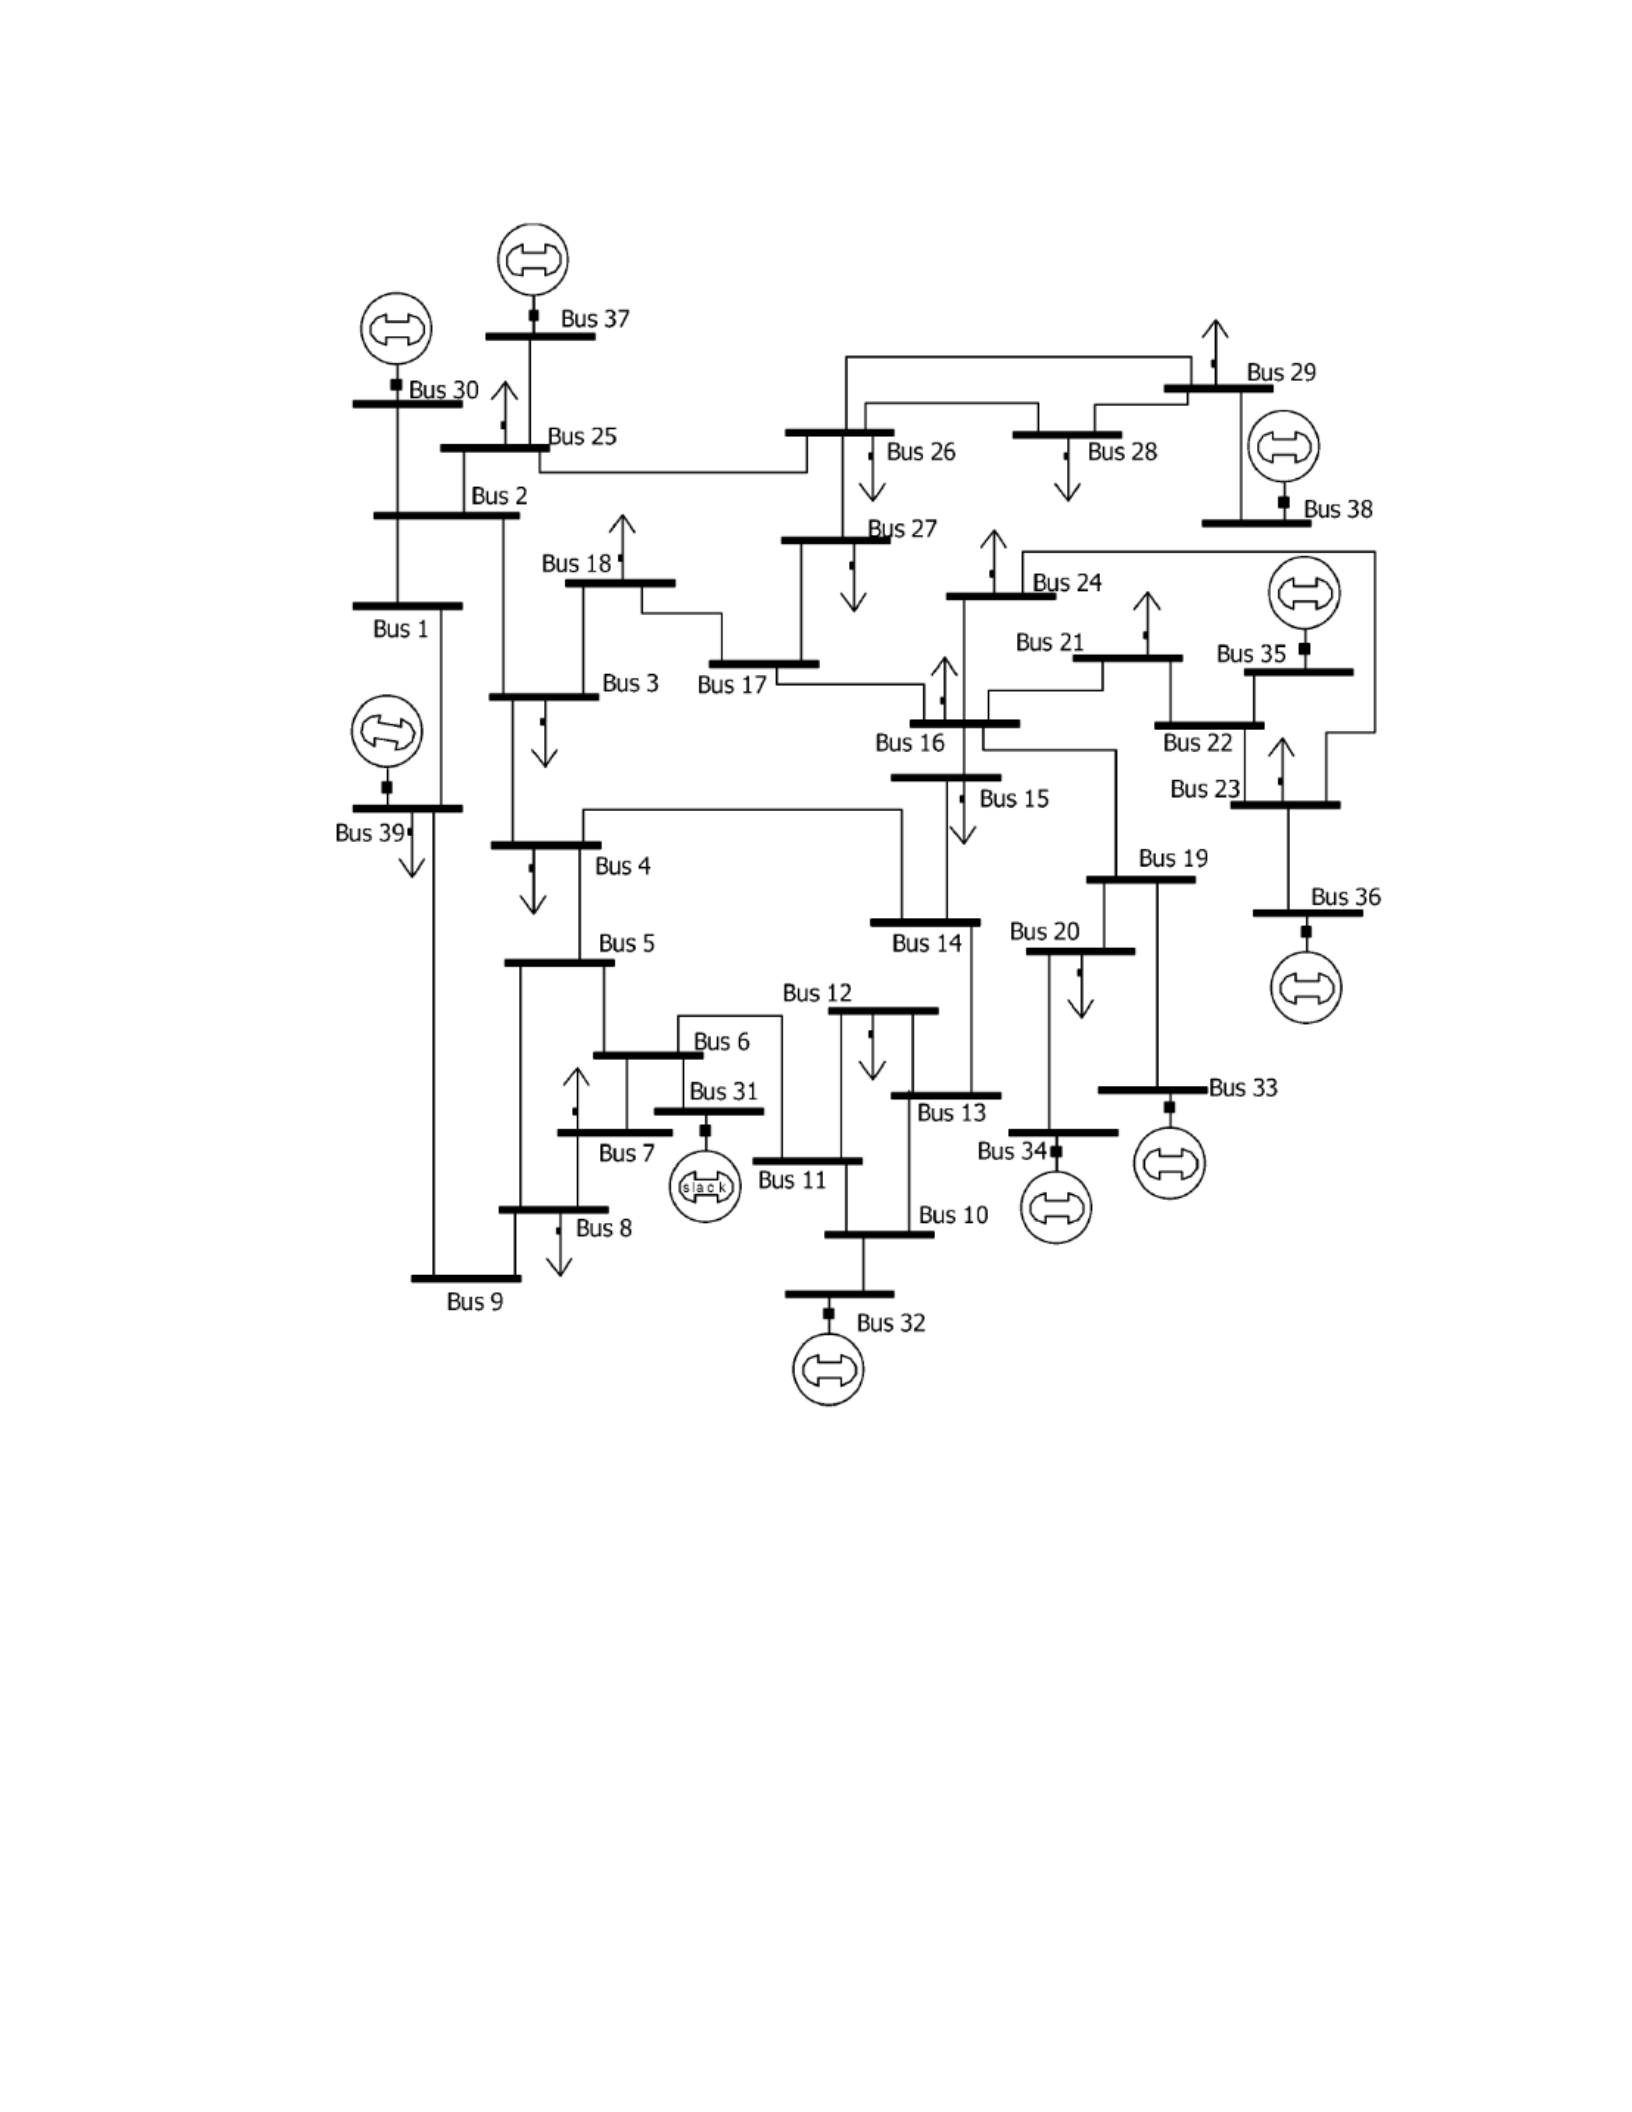
Figure 46. IEEE 39-Bus Benchmark Model One Line Diagram [10]
The GHOST model is based on a real-world distribution system that services a
small industrial complex. The model is designed to accurately model the challenges
of small microgrids and the complexities of microgrid monitoring and control.
93
Figure 47. GHOST Microgrid Model One Line Diagram [7]
6.5 Chapter Summary
The Smart Grid Research lab enables state-of-the-art research into Cyber
Physical Systems that is often unavailable in a university setting. The ability to
not only model but to execute a fully functioning cyber layer alongside a hardware-
in-the-loop simulator allows for cutting-edge research that is as closely aligned with
it’s real world counterpart. The benefits of this are two-fold:
1. The high fidelity cyber physical benchmark systems are realistic and therefore
applicable to industry partners, as well as, the overall research community.
2. By creating a real cyber layer with real communication packets, commercial
and open source cyber tools can be used to monitor and analyze the network
traffic. This allows research into the interaction of the cyber and physical
layers without obscuring either domain.
While the Smart Grid Research lab has primarily focused on power systems
and microgrids, the lab infrastructure can also be used in many different applica-
tions. For example, the HIL simulators can be used to model an smart car and
the cyber layer can carry the Controller Area Network (CAN) bus, which is a ve-
94

hicle bus standard, to the central controller. This enables the lab to have future
flexibility to any type of cyber physical research.
95

CHAPTER 7
Conclusion and Future Work
In this dissertation, the ANGEL Digital Twin framework is presented to im-
prove the resiliency of cyber physical systems and applied to benchmark systems
that represent modern microgrids and the future smart grid. Using the Smart
Grid research lab, as detailed in Chapter 6, the digital twin framework is imple-
mented alongside real-time Hardware-in-the-loop simulations and fully functional
communication systems that are deployed on a configurable cyber network. These
components have allowed the research presented in this dissertation to investigate
the use of digital twin technology for anomaly detection using real-time data from
a high-fidelity and realistic sources.
The ANGEL framework is configurable and modular in nature. In this disser-
tation, there have been a number of modules that have been researched to leverage
the power of the digital twin technology. Using state-of-the-art machine learning
such a Graph Convolutional Neural Networks (GCN) and cross-domain applica-
tions of Convolutional Neural Networks (CNN) algorithms that are well established
in other industries, two anomaly detection algorithms were presented that are able
to detect physical anomalies and locate the faults within a highly connected power
system.
Digital twin technology relies on real-time transmission of accurate sensor data
from the physical system. In transmission and distribution systems, this data is
often from the phasor measurement units (PMU) that are placed throughout the
system. Protecting this data using the proposed blockchain checksum, proposed
in Chapter 5 would provide a low overhead method to ensuring the authenticity
of the real-time sensor data.
96
As the digital twin technology is continued to be researched and pushed to
the more advanced levels of maturity, as presented in Figure 3 in Chapter 1, there
are many additional important research directions that can be expanded on in the
future. A few areas of expanded research are:
Fundamental research of using digital twin features as an augmented state
input in machine learning (ML) and artificial intelligence (AI) algorithms.
Using the additional information that can be provided by physics based mod-
eling, the resulting ML and AI algorithms can provide additional insight into
the underlying system and improve the overall results of the decision engine.
For example:
In the power system, there are many unknown system states both on
the generation side, a problem that is becoming increasing complex with
distributed generation units such as wind and solar, and the loads that are
put on the grid by both residential and industrial uses. The loads on the
system are expected to grow as the adoption of electric vehicles increases.
However, a multi-domain physics-based modeling approach can help balance
the system through dynamic and predictive modeling. For example, using
real-time weather data and a digital twin power system model, a smart home
can predict excess power generation from solar or wind generators without a
physical signal from the generation side.
Adaption of the proposed Digital Twin framework for other CPS systems
and domains outside of the power and energy field. While digital twins have
been applied in manufacturing plants, perhaps the addition of a cyber-layer
monitoring system would yield increased resiliency to cyber events.
Comparison and assessment of the advantage and limitations of digital twin
97

compared to other state-of-the-art methodologies in the field of power and
energy.
The landscape of the digital twin environment is a rich research field that has
many potential avenues for future exploration. The ANGEL digital twin framework
offers a basis for future researcher to continue to push the state-of-the-art and move
the world towards a more resilient and economical power grid.
98

