


Strategies for Securing Users Personal Data against
Security Threats in MCC Networks
Section 1: Foundation of the Study
The purpose of this qualitative pragmatic inquiry was to explore strategies used by
information security managers to secure their user’s personal data against security threats
in Mobile Cloud Computing (MCC) networks. In recent years, mobile devices have
become more important to people as the most effective and convenient communication
tool they have ever had by providing their users with easy access to news, entertainment,
health, business, and social networks (He et al., 2018; Somula & Sasikala, 2018). This
dependence has resulted in high demand for high-quality mobile devices and mobile
services. However, the major limitation of mobile devices are the limited resources such
as battery life, processing power, and storage capacity. On the other hand, cloud
computing provides extensive computing resources and services, such as substantial
computational power, large storage capacity, etc., which are provided at low costs to its
users (Somula & Sasikala, 2018). To break through the limitation in mobile devices,
cloud computing was introduced into the mobile environment to augment the capabilities
of mobile device resources, providing a robust technology called Mobile Cloud
Computing (MCC).
Combining the services of cloud computing services with mobile computing
helped to solve mobile device limitations. This integration allows mobile device users to
upload their applications, data, and other services onto cloud servers that are shared.

Mobile devices can now utilize the large storage capacities and high-computing resources
of cloud computing when running intensive applications and remote data storage
processes that usually use up the battery life and resources of mobile devices. Although
MCC has numerous advantages for its users, it still suffers from security and privacy
issues (Annane & Ghazali, 2019), which is a significant concern for both organizations
and individual users. Therefore, information security managers are challenged to provide
the most secure environments for their mobile cloud users and develop effective security
strategies to secure their user’s personal data from security threats in their MCC
networks.
Background of the Problem
Mobile cloud computing (MCC) is a fast-growing technology that allows mobile
device users to access cloud services from their mobile devices. Larger storage, greater
bandwidth, and longer battery life have improved the overall MCC capability, allowing
mobile device users to perform activities such as data mining, data storage, and
multimedia projects from nearly any location they choose. However, the major hurdles
for both organizations and individuals in implementing MCC are its security issues. He et
al. (2018) stated that the MCC environment is more likely to be attacked by hackers than
the traditional cloud computing environment. As a result, some organizations are
reluctant to embrace MCC.
Thus far, IT leaders have not addressed the security challenges in MCC (Sarode &
Bhalla, 2019), which has resulted in its low implementation. Findings from this study
may be used to provide mitigation strategies against MCC security threats by addressing

the challenges of protecting MCC networks in the field. When information security
managers have the proper knowledge to protect their users’ personal data against security
threats in MCC, they may cut down on the overall financial losses acquired by
organizations due to security breaches.
Information Technology Problem Focus and Project Purpose
The lack of privacy and data protection in mobile cloud computing (MCC)
networks poses enormous risks to mobile cloud users (Alnajrani et al., 2020). A survey
predicted that 98% of mobile traffic will originate from smart devices and would
consume over 30.6 exabytes per month in 2020, enabling the mobile market to grow from
USD $1.18 billion in 2015 to USD $3.26 billion in 2020 (Vishal et al., 2018). This
extremely high demand for smartphones and tablets will continue to grow in the coming
years, which may result in an equivalent need for increased security in user data
protection in MCC. The general IT problem was that users’ personal data in Mobile
Cloud Computing (MCC) networks are vulnerable to security threats. The specific IT
problem is that some information security managers lack security strategies to secure
users’ personal data against security threats in MCC networks.
The purpose of this qualitative pragmatic inquiry study was to identify strategies
necessary to secure users’ personal data against security threats in MCC networks. The
target population is information security managers located in the United States who are
implementing various strategies to secure their users’ personal data against security
threats in their MCC networks. In the findings of the study, I identified strategies that
other information security managers may apply to effectively secure their users’ personal

data against security threats in their MCC networks. The implications for positive social
change include increased security of MCC networks and protection of MCC user’s
personal data, reduced security breaches, thereby cutting down the overall financial losses
acquired by organizations from security breaches, and protection of consumers from
high-risk and cost of identity theft, which can be caused by confidential information
breaches.
Nature of the Study
To address the research question in this qualitative study, the specific research
design was a pragmatic inquiry design. According to Bleiker et al. (2019), a qualitative
methodology enables the researcher to gain a rich, detailed, and deep understanding of a
process. Because my primary focus was to investigate and uncover strategies used by
information security managers to protect their mobile cloud computing networks, a
qualitative study was the most appropriate research method. A quantitative research
method would have been appropriate if I intended to acquire statistical data to test a
hypothesis (Zyphur & Pierides, 2019). A quantitative study was not a suitable choice
because I did not test any hypothesis in this study and did not study the relationship
between variables. A mixed-method approach combines qualitative and quantitative
methods to answer complex questions (Stoecker & Avila, 2020). Because this study does
not combine numerical testing with participants’ experiences, I did not utilize the
mixedmethod approach.
The ethnographic design is used when the researcher intends to immerse themself
in the culture of the sample to observe patterns and experiences (Thomas, 2017). I did not

use the ethnographic research design because I did not intend to observe the cultures of
information security managers. A phenomenological design was also not chosen for this
study because the phenomenological design is focused on understanding the life
experiences of a sample population (Thomas, 2017). I did not choose this design because
I did not observe the perceptions of the lived experiences of information security
managers. In a narrative design, the researcher’s primary focus is on studying the lived
experiences of participants through storytelling (Rahiem et al., 2021). I did not choose the
narrative design because this research was not focused on the history and biographies of
information security managers.
I chose the pragmatic inquiry design for this research because it focuses on
individual decision-making within real-world situations (Frey, 2022). It was useful to
better understand and solve the needs of complex problems. My aim was to examine the
experiences of information security managers on real-world strategies to secure their
users’ personal data in MCC networks; therefore, the pragmatic inquiry design was the
most appropriate design. The pragmatic study was an effective study for investigating and
taking an in-depth look at a contemporary phenomenon using participants in realworld
environments (Frey, 2022). Using a pragmatic inquiry design allowed me to develop in-
depth insight into each organization’s experience, and specific strategies used by their
information security managers for securing their user’s personal data from security
threats in their MCC networks.

Research Question(s)
This study was guided by the following research question: What strategies do
information security managers use to secure their users’ personal data against security
threats in MCC networks?
Interview Questions
1. What successful strategies do you use to protect your user’s personal data in your
MCC network from security threats?
2. How can threats from within and outside your organization compromise your
MCC networks?
3. How do you evaluate the strategies of your organization for protecting users’
personal data from security threat?
4. What technical strategies have you implemented to secure your MCC networks
from security threats?
5. What applications do you utilize to protect your MCC networks from security
vulnerabilities?
6. What strategies were not successful in protecting users’ personal data in MCC
networks from security breaches?
7. What are some of the challenges you encountered when handling/dealing with the
security threats social engineers and cybercrimals pose to your MCC networks?
8. What steps do you take to mitigate risk in a personal data security compromise?
9. How does your experience contribute to the security of MCC in terms of failure to
implement technical and non-technical controls?

10. What roadblocks did you encounter in executing strategies to secure users’
personal data from security threats?
11. How did you overcome these barriers that hindered the successful application of
strategies for protecting users’ personal data from security threats?
12. What additional information would you like to include in regards to protecting
users’ personal data in MCC networks that you have omitted and would want to
discuss?
Conceptual Framework
The concept that grounded this study was the integrated system theory (IST) of
information security management. Hong et al. (2003) introduced the integrated system
theory (IST) to serve as a foundation for understanding the various strategies and
challenges surrounding information security management and examining its
effectiveness. Hong et al. (2003) developed the IST by combining information policies,
risk management, audit control, management, and contingency theories. IST suggests that
the theories be implemented together as implementing any of these theories individually
will be inadequate in addressing the confidentiality, availability, and integrity of
information. The IST is based on managing eventualities; hence it combines all the
theories in a certain way to meet the information security objectives of organizations by
creating and establishing information security strategies suited for the organizations. The
IST architecture also covers mitigation strategies for organizations should a security
breach occur.

Information security policy theory is used to determine what information assets
are useful or not useful in securing an organization. It covers the human element in
information security, which means it emphasizes the roles and responsibilities of
employees to secure the information and technological resources of the organization.
(Karim et al., 2021). Organizations that do not have a well-structured information
security policy could be exposed to risks such as loss of financial resources, employees,
reputation, and other tangible and intangible assets. Employees are the weakest link in
information security, and they cause half of the security breaches that occur in
organizations (Chin & Chua, 2021). Therefore, it is paramount that organizations have a
well-designed information security policy, and that individuals within organizations are
motivated to understand and comply with the information security policies created by the
organizations.
The risk management theory of IST suggests that a risk assessment must be
performed on an organization to determine the information security threats and
vulnerabilities of the organization. This theory helps to bring risk down to an acceptable
level (Hong et al., 2003) by using a comprehensive risk assessment and implementing
controls. Risk acceptability levels vary from organization to organization, which is a
major factor when making organizational decisions (Zhang et al., 2019). Therefore,
acceptable risks are determined by the organization implementing the risk management
theory.
Control and auditing theory states that organizations should have an information
security control system for measuring the prevention, detection, and correction of unusual

security events (Casola et al., 2019). Standards such as the ISO 27001 are used to
measure the audit and control performance within organizations; so, organizations that
comply with the ISO 27001 standard are presumed to have followed the recommended
standard for controlling the risks within their organization.
Management system theory suggests that organizations should have a
welldocumented information security management system (ISMS) for protecting the
organization’s information assets. The ISMS should contain information such as the
definition of the policy, the definition of the scope of the ISMS, when and how to
perform and manage a risk assessment, choosing the control objective, and documenting
a statement on how to apply the ISMS (Hong et al, 2003). Organizations must, therefore,
include the above steps when creating a solid and effective ISMS for their organizations.
Contingency theory refers to the documented plans and actions organizations
should take should a disaster or disruption of service occur (Carbaugh et al., 2019). With
a well-prepared contingency plan, organizations will be able to respond to any
information security issues that arise. Contingency theory is a part of contingency
management that concerns prevention, detection, and reaction to threats and
vulnerabilities in and outside the organization (Hong et al., 2003). Having a contingency
plan in place is also an essential part of risk management because it helps to ensure that
organizations have a backup plan when things go wrong or unexpected. Without a
properly documented contingency plan, organizations could face issues such as complete
data loss, business interruption, loss of clients, damage to reputation, and business failure.
Therefore, a contingency plan is necessary for the survival of every organization.

The IST serves as a guiding tool to promote a complete understanding of
information security. It provides invaluable information for security strategies, theories,
and procedures for researchers, information security decision-makers, and users to better
understand information security from an all-around perspective (Hong et al., 2003). With
an all-around knowledge of information security, organizations will be better prepared to
defend and secure the confidential information of their users. Within organizations,
security managers utilize security policies to secure their organizations. They set
expectations and rules for computer users and utilize internal control for preventing and
detecting fraud. They also implement contingency management plans to identify
vulnerabilities and provide countermeasures to prevent their occurrence (Hong et al.,
2003). Such rules and expectations help increase the overall security posture of
organizations.
Definition of Terms
Cloud computing: Cloud computing is a mechanism that gives its users the ability
to store, retrieve, and process information from various servers around the world with the
use of any internet-connected device on an on-demand basis (Sharma & Sehrawat, 2020).
Cybercriminals: Cybercriminals are people who use communication via the
internet and information systems to target networks and spread malware. The purpose is
to gain unauthorized access to users’ computers and steal sensitive information or corrupt
network systems (Stancu, 2020).

Data mining: Data mining provides users with the ability to extract massive data
sets, find patterns in the data sets, and generate helpful knowledge from the data by using
machine learning, statistics, and database systems (Ferri-García et al., 2019).
Data protection: Data protection is the process of safeguarding information from
loss, corruption, compromise, etc., and providing a way for the data to be restored should
anything occur that makes the data inaccessible or unusable (Omotubora & Basu, 2020).
Data storage: Data storage is the technology that securely records and preserves
digital information for ongoing operations in magnetic, optical, or mechanical media and
makes it readily available anytime it is needed (Mariani et al., 2021).
Insider threat: Insider threat refers to when former or current contractors,
employees, clients, business partners, or vendors misuse the privileges and access they
have to the corporate networks. Instead of using their privileges to serve the organization
positively, they use their network access to steal and damage the organization’s system
and network infrastructure (Schwab, 2021).
Mobile Cloud Computing (MCC): This technology empowers mobile devices
users to use the resources of cloud computing to overcome the limitations in the
technology of mobile devices. (Somula & Sasikala, 2018).
Personal data: Personal data is any data that directly or indirectly identify a living
individual (Tsui & Hargreaves, 2019).
Security breaches: Security breaches refer to the unauthorized manipulation or
disclosure of confidential data intentionally or unintentionally by human error, system
error, or criminal activity (Wang et al., 2022).

Security strategies: Security strategies refer to protective measures and actions
that can be used to prevent unauthorized access to confidential information. Such
measures include the use of firewalls, antivirus, active system monitoring and updates,
employee security training, security policies, etc., (Tan & Yu, 2018).
Security threats: Security threats refer to any action that threatens to harm any
valuable human and organizational system and values of societies and countries that
require protection and defense (Rogozińska, 2021).
Social engineers: Social engineers are individuals who exploit human
vulnerabilities through social interactions such as manipulation, deception, influence, and
persuasion. Their aim is to break through security goals such as confidentiality, integrity,
availability, auditability, and controllability of elements of the Internet, such as user, data,
resources, operation, and infrastructure (Wang et al., 2021).
Mobile Cloud: This is the concept where mobile devices offload high
resourceconsuming processes and data of huge sizes (such as videos) into the cloud,
which has large storage and computational power (Somula & Sasikala, 2018).
Assumptions and Limitations
This section summarizes this qualitative study’s assumptions, limitations, and
delimitations. Assumptions refer to perceptions and statements by the investigator that
some elements of the research are known to be true, and influence the viewpoint of the
investigator (Poucher et al., 2019). Limitations are weaknesses and limits that the
investigator cannot control (Theofanidis & Fountouki, 2018). Delimitations refer to
restrictions imposed by the investigator to accomplish the objectives of the study

(Theofanidis & Fountouki, 2018).
Assumptions
Assumptions are factors that the researcher may take for granted and assume are
true and widely accepted (Theofanidis & Fountouki, 2018). There are several
assumptions that I had during this research. The first one is that I assumed that all
participants of this research were knowledgeable enough to answer the interview
questions. Researchers in qualitative studies usually believe that their participants are
experts and have exposure or experience in the proposed area of study (Rutberg &
Bouikidis, 2018). The second assumption was that each interviewee in the research would
provide honest responses, and as such, the data that would be collected reflect the
strategies used for securing users’ personal data against security threats in MCC
environments. The third assumption was that the research method I used was the most
appropriate and will yield the information needed to answer the questions of the research
study. The final assumption was the outcome of the research would not be affected by
any form of bias from either the researcher or participant.
Limitations
Limitations are potential gaps that are beyond the control of the researcher and
could hinder the achievement of the study’s objectives (Theofanidis & Fountouki, 2018).
Some of the limitations of this study include limits on the data collected based on the
availability of the participants, unknown factors from the participant’s jobs may add some
biases to their responses, and the participants may not have the complete and allaround
knowledge to make informed responses. Fourthly, the study may not address all the

security challenges related to the security of users’ personal data in the MCC network.
Lastly, the study was limited to two financial technology companies in the fintech
industry in Northeast Massachusetts.
Delimitations
Delimitations are conscious restrictions imposed by the researcher (Theofanidis &
Fountouki, 2018). They are limits the researcher sets so that the goals of the research do
not become unattainable. The first delimitation of this study was that the research was
limited to security managers with at least 5 years of working experience in IT security
and who were at least 21 old or older. The second delimitation was that the study was
confined only to eligible interviewees who are qualified based on a specific set of criteria.
The third delimitation was that the study will be limited to the private sector of the IT
industry and not the government or educational sector. Lastly, the geographical area of
the research would be confined to Northeastern Massachusetts.
Significance of the Study
This study was significant because it may elicit an understanding of mitigation
strategies against security threats by addressing the challenges of protecting MCC
networks in the field. When information security managers have the proper knowledge to
protect personal data against security threats in MCC, this maycut down the overall
financial losses acquired by organizations due to security breaches. Data from this
research may also protect consumers from the high risk and cost of identity theft, which
personal information breaches can cause.

Contribution to Information Technology Practice
The results from this research may contian new knowlwdge regarding mitigation
strategies utilized by information security managers to protect their MCC networks from
security threats. Today, information security managers face the constant threat of
information security breaches, and wireless networks are vulnerable to various attacks in
transmitting users’ sensitive data (Mo et al., 2019). To secure personal data against
security threats in MCC networks, information security managers may utilize results and
conclusions from this research to enhance their information security knowledge and
improve their current information security practices. The result may help retain
customers’ and business partners’ confidence and cut down lost time, and the financial
losses organizations acquire when they fall victim to information security breaches
(Tayaksi et al., 2021). Information from this study may also help customers protect
themselves from identity theft costs, which results from breaches of users’ confidential
information.
Implications for Social Change
This study may impact social change because information security managers are
proactive in finding ways to mitigate information security breaches in MCC networks.
This research could provide information security managers with modern strategies to
protect personal data against security threats and advance organizational objectives,
which will be beneficial to information security managers in both small and large
business organizations.

Furthermore, the advantages of personal data security are apparent when there are
minimal security flaws; there is evidence of record-low numbers of cases where users’
confidential data are lost to cyber criminals (Sanchez Rubio et al., 2022). These benefits
may minimize the issue of unauthorized access to users’ personal information in MCC
networks due to poor security strategies (Fellah et al., 2020). Information security
strategies may help in cutting down the number of cases of stolen data. It may also help
information security leaders speed up on adopting technical and non-technical strategies
for securing their MCC network against security threats. This study may be used to build
an information security system that could expand to various geographical boundaries and
cultures, creating awareness for the right and safe ways to handle users’ personal data in
MCC networks.
Section 2: Literature Review
A Review of the Professional and Academic Literature A literature
review refers to the review, synthesis, and evaluation of various literature on the topic in
such a way that new frameworks, perspectives, and awareness are generated on the topic
(Duesbery & Twyman, 2020). There are various categories of literature review elements.
Authors such as Salkind (2010) and Cooper (1988) stated that literature elements are
categorized into focus, goals, perspective, organization, method of synthesis, coverage,
and audience. There are other scholars such as Torraco who believed that literature
elements are divided into three categories; these categories include literature review,
research methods, and theories (Torraco, 2016). A literature review, therefore, contains
key sources on a topic, and those sources are discussed in detail. It covers current

knowledge, relevant theories, methods, and gaps in the research. It also provides new
perspectives on a topic and offers critiques to help resolve inconsistencies in the
literature.
In this literature review, I examined various themes in the field of MCC networks.
There are ten themes in this literature review. They include (a) an overview of MCC, (b)
integrated system theory, (c) the opportunities and challenges in MCC, (d) security and
privacy, (e) encryption and cryptography, (f) access policies and access control (g) data
security (h) latency and reliability (i) countermeasures for security breaches within the
cloud, and (j) cyber-attacks in the cloud. I selected these themes to highlight the risks and
effects on both individuals and organizations of not correctly securing users’ personal
data in MCC networks. I also discussed some supporting and contrasting theories to the
integrated system theory of information security management and why it was appropriate
for my study.
I searched, reviewed, and utilized various peer-reviewed articles found in the
Walden Library, using terms such as mobile cloud computing, cybercriminals, data
mining, data protection, data storage, insider threat, cloud computing, personal data,
security breaches, security strategies, security threats, and social engineers. I also utilized
the Google scholar search engine to find related articles to the literature review. The
Walden University librarians also played an important role in helping me find various
articles that helped develop the literature review.
Most of the electronic and database resources used were limited to articles
published in 2018 and beyond. I utilized articles that contained information relating to

security, personal data, risk management, reliability, and mobile cloud security
challenges. This literature review contains 185 scholarly sources. Of these scholarly
sources, 148 (80%) were peer-reviewed via Ulrich, and 167 (90%) were within 5 years of
the chief academic officer’s (CAO’s) approval date.
Information Security Management Themes and Practices
Overview of MCC
Today, mobile devices provide their users with greater connectivity and ease of
access to multiple applications and services. However, mobile devices suffer several
limitations such as poor computational resources, low disk capacity, low memory size,
and small battery life (Alnajrani et al., 2020). Cloud computing utilizes a robust approach
in its delivery of services and has overcome the challenges in mobile devices. Cloud
computing services are also offered at a low cost and are easy to scale. To overcome the
challenges in mobile devices, they were combined with cloud computing to allow mobile
terminals have access to cloud-based services and resources, which led to the birth of
mobile cloud computing (MCC).
MCC is considered a fast-growing technology in the IT industry, as it combines
cloud computing services with mobile devices through wireless technology to overcome
the challenges of limited resources in mobile devices (Annane & Ghazali, 2019). MCC
users are now able to upload large amounts of data, applications, and services onto shared
cloud servers by leveraging the high computational power and large storage capacities
that were absent in mobile devices. Mobile users are also now able to process complex
and crucial applications that contain sensitive data and high multimedia content such as

texts, images, audio, and videos. Some of these resource-consuming processes include
banking applications, health applications, transportation applications, high-definition
games, online shopping, etc. However, the moving of users’ confidential information
from their mobile devices to the cloud raises many security concerns because the data is
in various distributed locations (Annane & Ghazali, 2019). As a result, security is a major
challenge in the MCC environment because MCC users give up control and the security
of their personal data to cloud providers, trusting them to safely store and manage their
confidential data.
Since MCC erupted from cloud computing, researchers believe that it inherited
the security challenges in cloud computing. Still, it is more critical in MCC because MCC
lacks the CPU capacity to run high-demanding software that secures personal computers
from losing sensitive data to malware attacks.
Figure 1
A Diagrammatic Illustration of the Overview of MCC
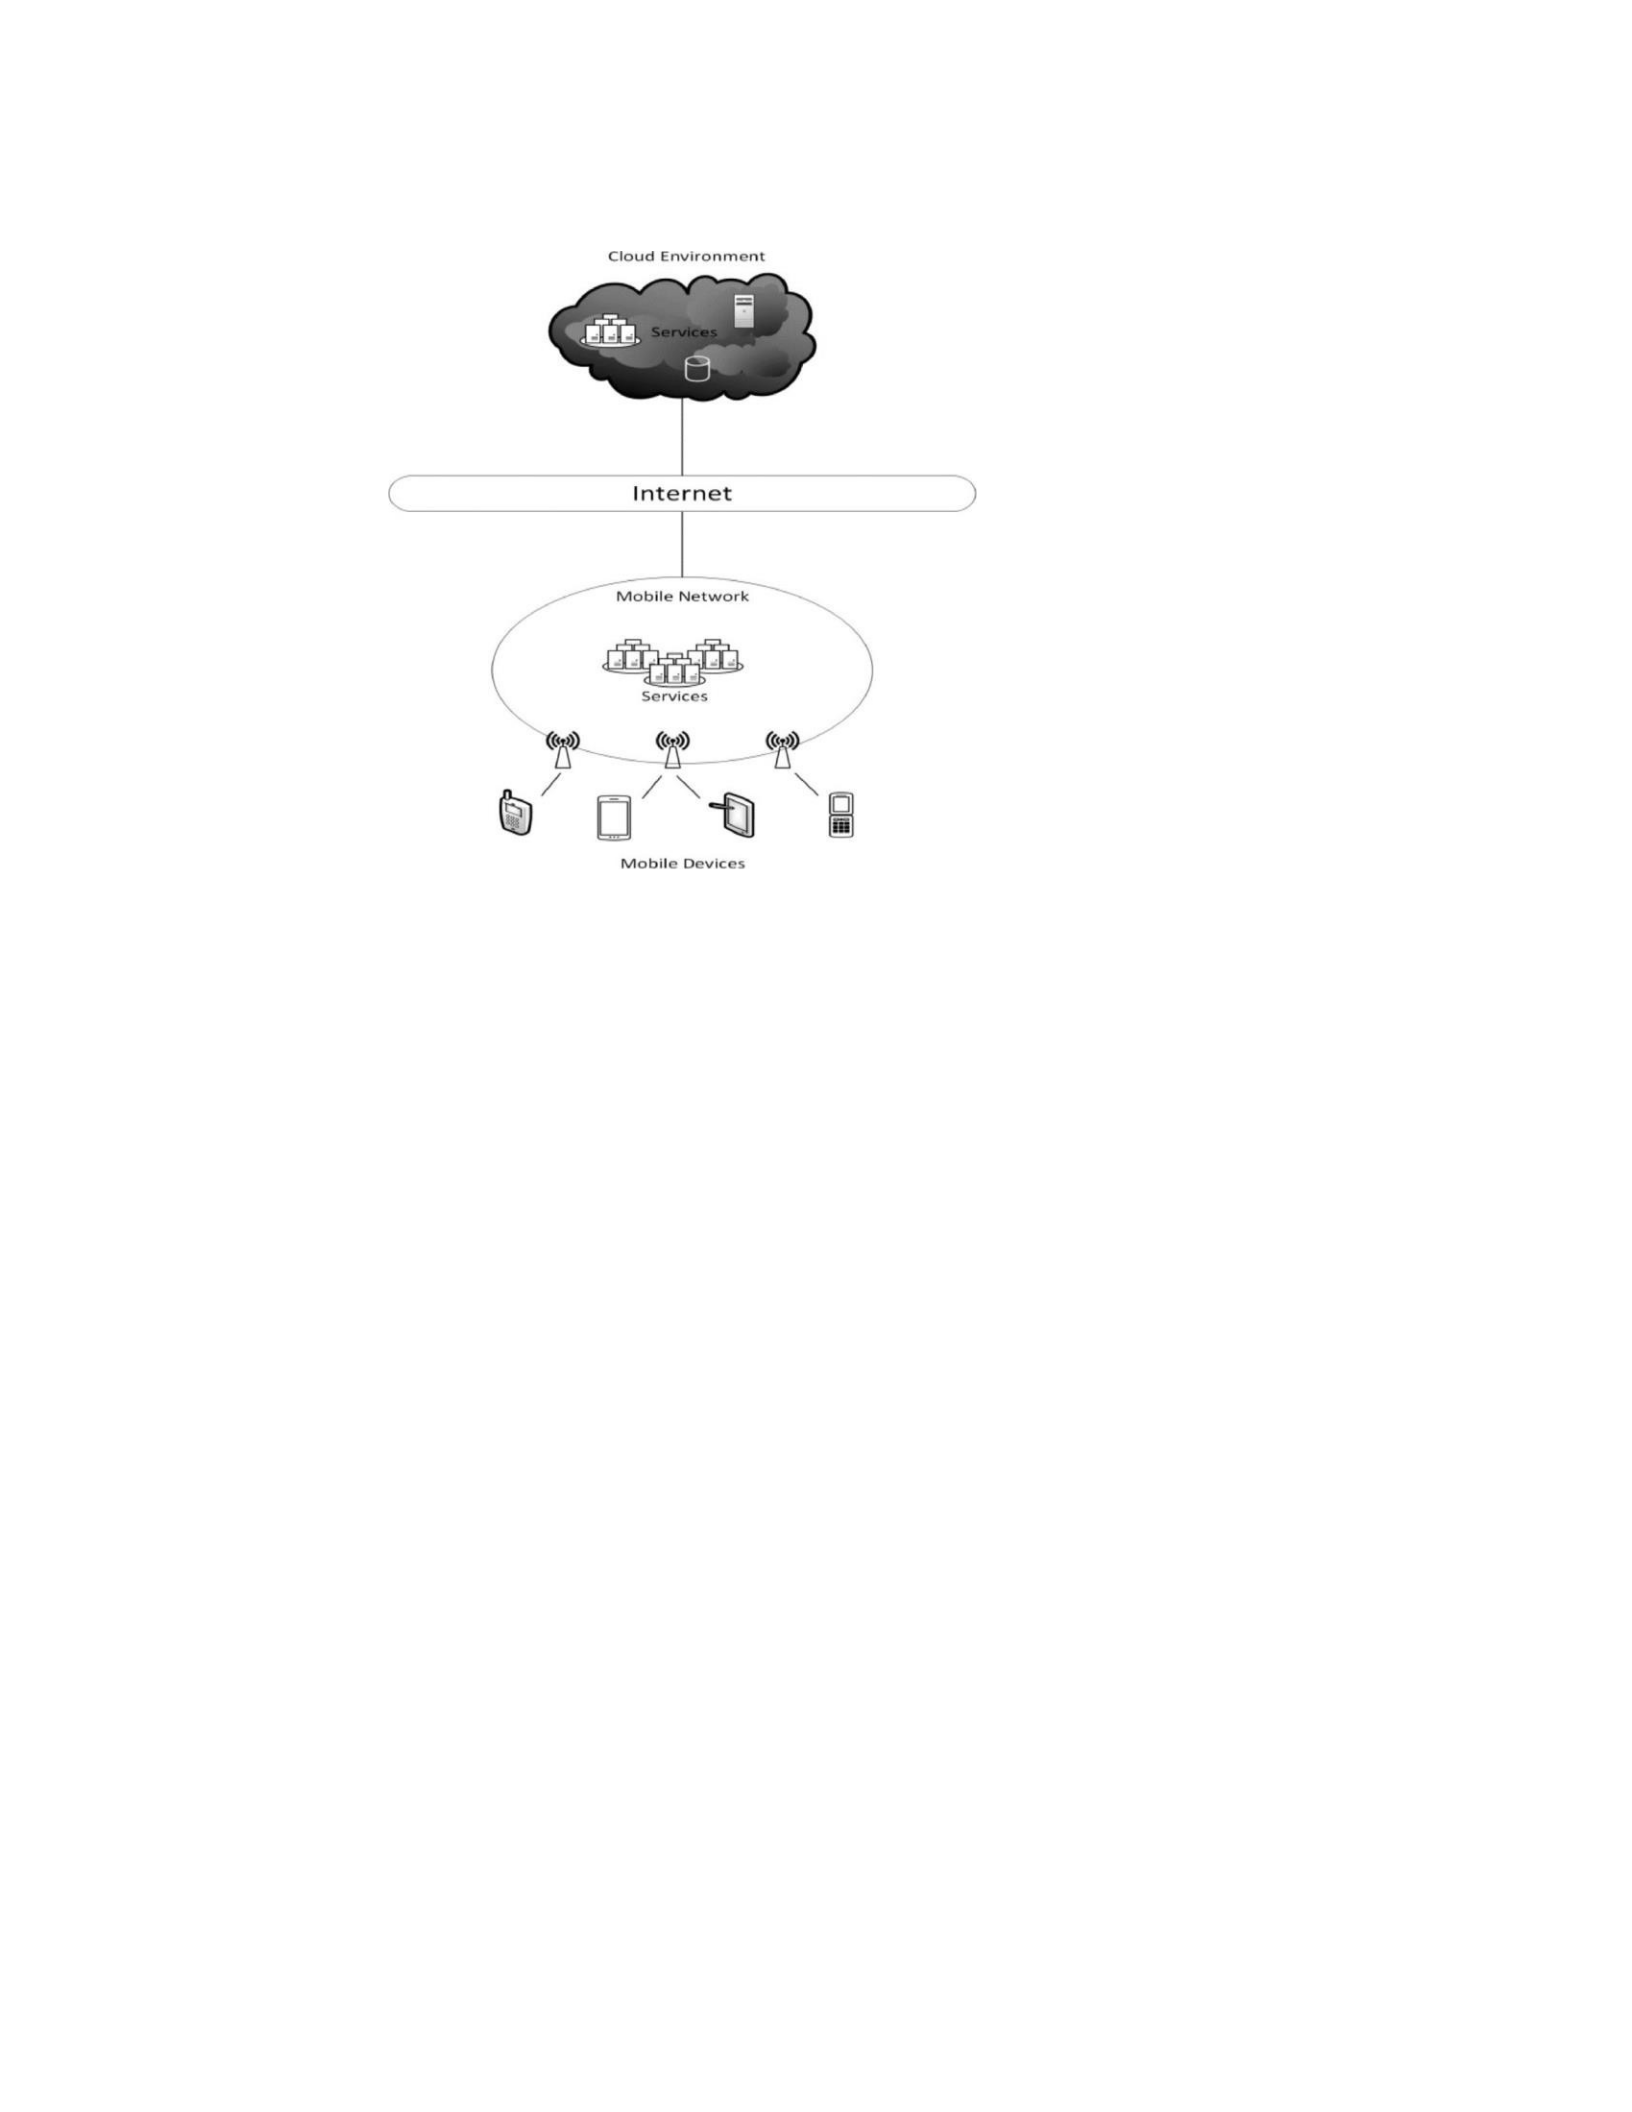
Note. This article was published in the “Journal of Information Security and
Applications, by Shamshirband, et al. (2020), Computational intelligence intrusion
detection techniques in mobile cloud computing environments: Review, taxonomy, and
open research issues, 55, 102582, https://doi.org/10.1016/j.jisa.2020.102582, Copyright
Elsevier (2020).” Reprinted with permission.
Integrated Systems Theory of Information Security Management
The theory or concept that grounds this research was the integrated system theory
(IST) of information security management. Hong et al. (2003) initiated IST to serve as a
foundation for understanding the various strategies and challenges surrounding
information security management and examining its effectiveness. Hong et al. (2003)
created the IST by combining information policies, risk management, audit control,
management, and contingency theories. A theory has the capability of accurately
predicting and defining ideas using various variables (Yang et al., 2016). The information
system theory (IST) was useful, comprehensive, practical, and vital for this study.
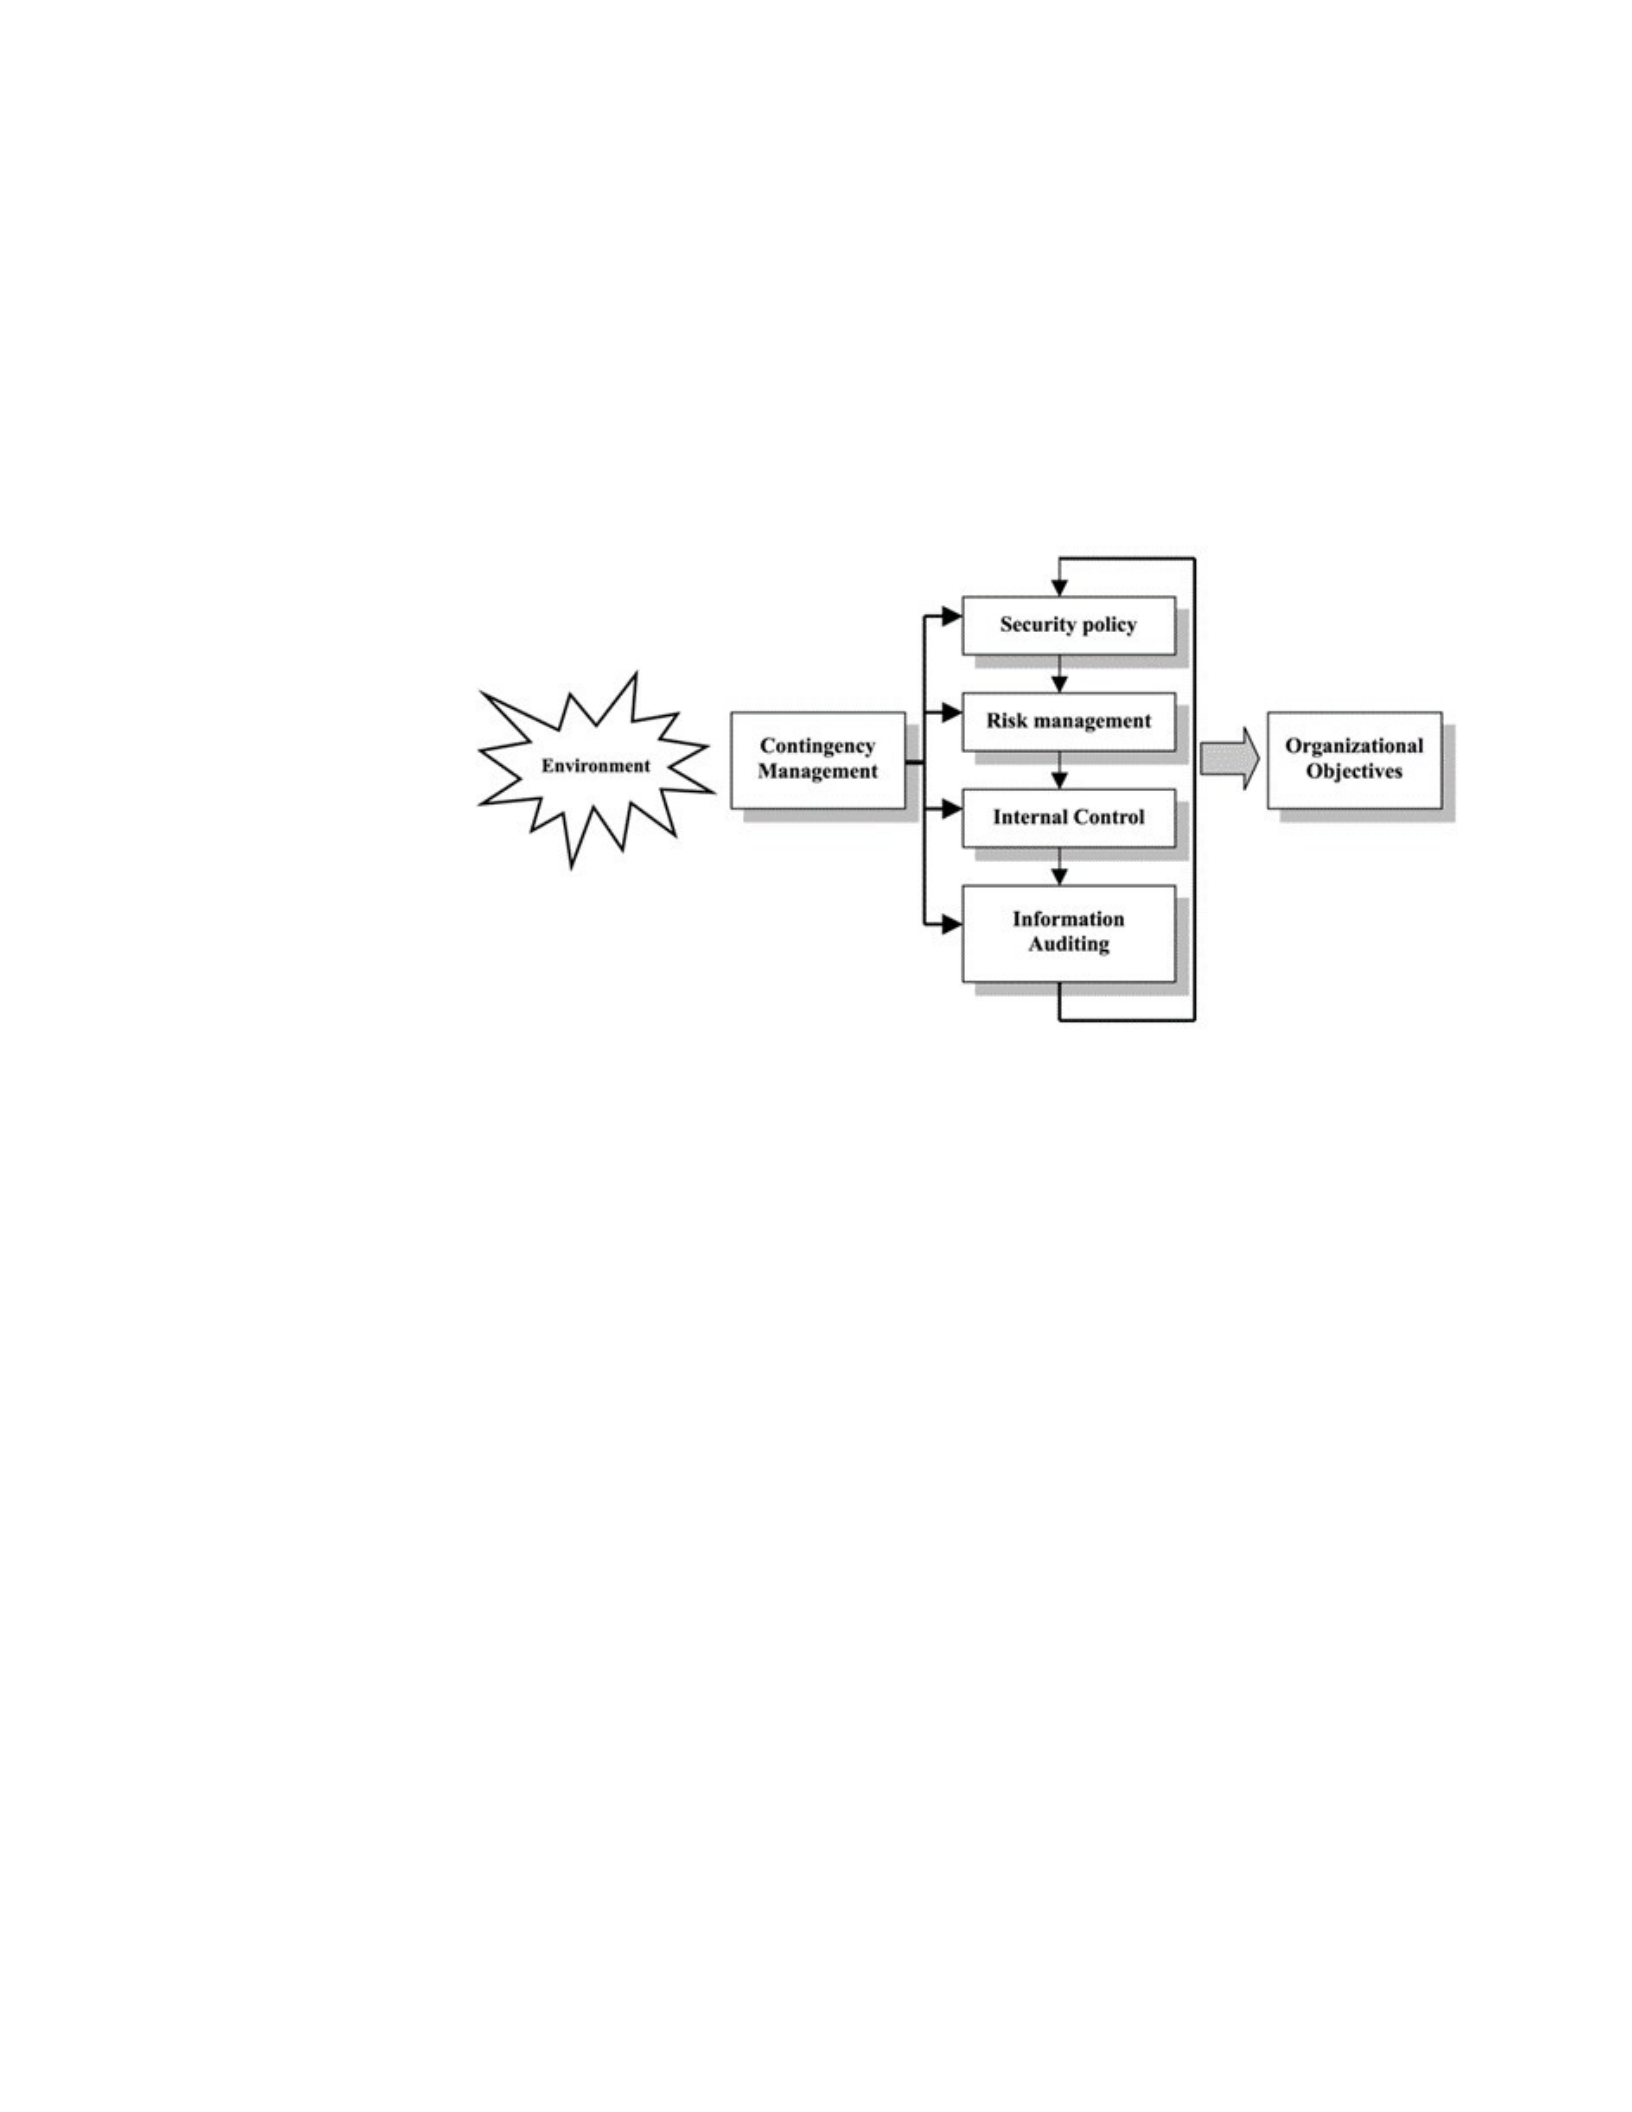
Figure 2
Integrated System Theory
Note. Adapted from “An Integrated System Theory of Information Security
Management,” by Hong, K. S., Chi, Y. P., Chao, L. R., and Tang, J. H. 2003,
Information Management & Computer Security,11, p. 247. Copyright 2003 by Emerald
Publishing Limited. Reprinted with permission.
The IST provides valuable information security strategies, theories, and
procedures for users, investigators, and decision makers of information security to have a
clearer understanding from a broad perspective (Hong et al., 2003). For example,
supervisors inside organizations utilize security policies to secure their companies by
defining expectations and proper regulations for computer users, utilizing internal control
for preventing and detecting fraud, and implementing contingency management for the
identification of loopholes and ways to avert their occurrence (Hong et al., 2003).

Therefore, the appropriate time to use the IST model was now because investigators are
seeking ways of identifying and recognizing security flaws in MCC and developing
effective plans for managing security threats.
Various authors have utilized IST as their framework for exploring factors of
information security management within organizations. As a result of the preceding
limitations and the present-day difficulties companies face, investigators became
stimulated to find solutions to the challenges of information security management and
figure out a way to secure users’ sensitive information to ensure the continuity of
business. Dzazali et al. (2009) investigated and noticed that for information security
management to be effective, its focus should be on processes, business goals, people, and
technology. They demonstrated that middle-level and top-level management group
perceptions of security greatly influence how they implement the security strategies in the
organization. The two levels of management are liable in one way or another for securing
their company’s information assets. Therefore, the conclusion of the authors confirmed
that IST’s risk management and the environment of the organization play huge roles in
their information security.
The use of the information policy theory of IST was to identify the information
security requirements of a company and create those policies to fit into the security
requirements. This policy noted that information security managers must clearly define
what the company allows and does not allow when using their organization’s information
assets (Karim et al., 2021). Information security policies must also stay current and be
regularly maintained/updated to make sure that the data of the organization is secure.

Information security policies also consider the people in information security; therefore,
the approach lists out the duties, guidance, and rules for employees to safeguard
information and technological resources that have to do with the organization’s
intellectual capital (Karim et al., 2021.) The policy provides users with the knowledge
and purpose for securing ICT assets and electronic information and ensuring information
is secured and available only to authorized users. The information security policy also
helps to protect information relating to confidentiality, integrity, and availability.
The addition of more security layers makes it difficult for attackers to breach a
system. Therefore, it is necessary to have multiple security layers in place for better
security (Ismail et al., 2014). With an added assurance layer, system administrators or
security managers are notified immediately when a breach occurs. This helps to prevent
an intrusion or mitigate it quickly should it occur (Ismail et al., 2014). The assurance
layer helps to boost the cloud security of organizations, and this framework helps
information security managers to have effective strategies for security in addressing data
breaches and loss of sensitive information in the cloud. Information security managers
must also review how information is shared within the organization and determine what
information is confidential. To make sure that the requirements for information security
are followed, there are four major goals of organizational security based on the four main
components of IST: risk management theory, control and auditing theory, contingency
theory and management system theory.
The risk management theory of IST states that one must analyze the current risks
within a company to pinpoint and estimate that organization’s information security

threats and vulnerabilities. The risk management theory suggests that information
security managers must perform risk assessments on organizations and use the result to
determine the information security risk control measures to implement (Jones &
Ashenden, 2005). The primary goal of risk management theory is to implement rules that
would bring risks low enough to a level that is tolerable (Hong et al., 2003). The
objectives of the risk assessment theory are achieved through a comprehensive risk
assessment and implementation of controls that would minimize risks within the
organization to a certain level acceptable by the theory of risk management. The level of
tolerable risks differs from one organization to another, as it is the level of risk an
organization may tolerate in order to achieve the goals of the organization. It is also
known as organization risk appetite, and it is considered an important factor when making
organizational decisions (Zhang et al., 2019). In summary, the risk management theory
of IST indicates that only organizations can determine which risks they can tolerate and
which risks they would not accept because it differs from one organization to another.
Control and auditing theory suggests that companies must have in place an
information security control system, and the system should be audited from time to time
to measure the control performance. Control covers areas such as preventing, detecting,
and correcting abnormal/unauthorized events. Control and auditing theory helps to ensure
that there are procedures and processes in place to track the performance of the various
controls available within the organization (Casola et al., 2019). Some organizations
utilize the control and auditing theory for achieving the information security objectives of
their organizations in areas such as confidentiality, integrity, and availability. The ISO

27001 standard, for example, defines 133 controls with eleven security domains and
thirty-nine control objectives. Organizations that comply with the ISO 27001 are
presumed to have followed the recommended and approved standards for mitigating
security risks within their organization. Hong et al. (2003) also referenced the Control
Objectives for Information and Related Technologies (COBIT) as an IT model for
organizations that wants to implement, monitor, manage and improve their IT
management practices, and balance information security risks control measures with
technical issues and business risks. For organizations to be secure, they must implement
information security standards and information security strategies, and regularly monitor
their control systems.
Management system theory posits that organizations should put in place, and
maintain, a well-documented information security management system (ISMS), for the
protection and control of the information assets of the organization. Hong et al., (2003)
laid out six steps for ISMS. They include defining the policy, defining the scope of ISMS,
performing a risk assessment, managing the risk, choosing the control and control
objective to be executed, and putting in place a statement for its application (Hong et al.,
2003). The management system theory must also take into consideration the information
security management system and the business strategy for the organization in which it
will be implemented. Organizations must therefore carry out processes such as inspection
of the organizational environment, scope definition, risk assessment, and control to
develop and information security management system that is robust and functional.

Contingency theory states that information security is partly contingency
management that has to do with prevention, detection, and reaction to the vulnerabilities,
threats, and impacts within and outside the organization (Hong et al., 2003).
Organizations usually combine mutiple measures of information security such as risk
management measures, security policy measures, control and auditing measures, or
system management measures to ensure the security of information within the
organization. Failure to adhere to information security measures can result in disaster or
disruption of service or both. Contingency planning contains the set of activities or
actions organizations should take in case there is a disaster or any disruption of service to
the organization (Carbaugh, et al., 2019). With a contingency plan, organizations stay
prepared to respond to any situational or information security issue to ensure business
continuity.
Mobile Cloud Computing (MCC) is a growing technology that gives mobile users
the ability to utilize cloud computing services using their mobile devices (He et al., 2018;
Somula & Sasikala, 2018). When organizations adopt Mobile Cloud Computing, they
give up their data security and data privacy to the cloud provider (Annane & Ghazali,
2019), making them lose control over the security and privacy of their data. Therefore,
IST would serve as a lens to help IT security managers identify specific strategies for
securing personal data in cloud computing networks. By combining and utilizing all the
theories within IST, organizations would be able to meet their information security
objectives and be well prepared in case of an attack. IT security managers lack these
strategies and knowledge, they would be unable to secure their MCC networks

effectively, thereby losing reputation and resources, and preventing more organizations
from accepting and implementing MCC.
Opportunities and Challenges for MCC
In our society today, most organizations and individuals are seeking more privacy
and security for their confidential information than ever before. Many organizations are
refraining from utilizing MCC due to privacy, trust, and security concerns with cloud
providers and their customers (Jawad, 2018). This is a result of the existing trust/privacy
concerns that exist in both cloud-computing and MCC environments. The security and
privacy concerns in both cloud-computing and mobile cloud computing are similar.
Shamshirband, et al. (2020) stated that attacks such as ARP spoofing, DDoS, flooding, IP
spoofing, DNS poisoning, and DoS are possible attacks in cloud computing and MCC
environments. The possibility of such attacks occurring in the MCC environment is what
makes organizations refrain from implementing MCC in their environment.
One of the significant factors that determine the success of an IT infrastructure is
the security of its customers’ data. Trust, security, and privacy are some of the significant
issues in MCC (Somula & Sasikala, 2018). Mobile devices are vulnerable to attacks and
have higher chances of data being stolen from them because they are unprotected. Some
security issues associated with mobile devices include data loss from lost or stolen
mobile devices, information stolen through mobile malware, data leakage via untrusted
third-party applications, insecure network access, use of access points that are not
reliable, vulnerabilities within the device operating system and design, and susceptible to
Near field communication (NFC) proximity hacking (Somula & Sasikala, 2018). It is this

ease of attack and data loss in mobile devices that keep individuals and organizations
from implementing MCC.
Privacy and Security
Security breaches occur when unauthorized users gain access to the confidential
data of other users without using the appropriate user permission. Many organizations
treat their data as one of the most valuable assets of their companies, so it is crucial that
such data are secure. Some mobile applications utilize hired storage for saving their
personal data in the cloud. These third-party storage companies then share their users’
sensitive data with government agencies without explicit permission from their users
(Somula & Sasikala, 2018). Another reason for the hesitation of organizations to use
MCC is that some of these third-party organizations can be targeted and hacked, which
will put confidential data of both individuals and organizations in the hands of bad actors,
and would result in issues such as financial losses, loss of reputation, blackmails, etc.
Privacy is another major area of concern when discussing Mobile cloud
computing. Privacy covers everything that has to do with managing the data stored,
shared, and disclosed in the cloud. Privacy also encompasses managing who accesses
such data (Gai, et al., 2021). One of the privacy concerns is the transmission of a large
amount of unencrypted data via mobile devices. This concern can result in the leakage of
confidential data because texts in plain format can be captured easily by hackers through
various techniques such as spoofing, jamming, monitoring, etc. (Gai et al., 2021). As a
result, attaining user data privacy is a massive hurdle for adopting MCC for
generalpurpose applications (Saharan, et al., 2021).

The privacy of images being shared with external servers is also paramount.
Cloud servers can implement image segmentation on the photos of users such as style of
clothing, restaurants, tourist locations, social events participation, etc., and putting all
these images together helps to characterize a user’s personal life (Saharan et al., 2021).
Some of this information is sought after by advertisers, and exposure or leakage of such
private information can result in huge consequences, such as identity theft. It is, therefor,e
necessary that the privacy of users’ data during communication on social networks and
mobile devices be guaranteed by cloud providers and information security managers.
Encryption and Cryptography
Encryption and cryptography are very crucial in the sharing and storing of data.
Encryption provides data security and prevents the leakage of confidential information
(Thomchick & San Nicolas-Rocca, 2018; Zhou, et al., 2019). Encryption mechanisms
help to guarantee that confidential information is safe and secure while in transmission to
be stored on any media that has a tendency to be accessed without authorization.
Cryptography is critical anywhere there is communication over untrusted transmission
systems (Zaru & Khan, 2018). When communicating via any public transmission system,
it is necessary to secure the data being transmitted to prevent the data from going into the
hands of bad actors. Cryptography is a significant sector in information system security,
and it works both in browsing the internet and for phone calls. As a result, the need for
cryptography and its enhancement has never stopped increasing (Pradhan, et al., 2020).
Organizations and individuals need their personal data to be secure when transmitting

them over public networks (such as the Internet), and cryptography is an effective way to
achieve that.
In Cryptography, encryption is the process of encoding information by converting
plaintext into ciphertext and can only be decrypted by an authorized party with the right
key (Masud, et al., 2022). Without the correct decryption keys, the ciphertext cannot be
converted back into plaintext, making the data unusable for unauthorized users.
Cryptography consists of various techniques for encrypting and decrypting data. One of
the early leading cryptographic techniques is the RSA (Rivest–Shamir–Adleman)
technique (Bosnjak, Sres & Brumen, 2018). The RSA technique uses an asymmetric
cryptography algorithm to generate two separate keys, public and private keys. The two
individual keys are different but mathematically linked. The public key is shared publicly,
while the private key must be kept secret and not shared with anyone. The RSA technique
is prevalent because it guarantees high safety/security. It could take several months for a
computer to compute the factors of very huge prime numbers, even if the computer is
modern with very high processor speed. The RSA technique is also resistant to brute
force attacks (Bosnjak et al., 2018). Another very popular and effective key cryptosystem
is the DES (Data Encryption Standard) technique. However, its short key length of 56 bits
makes it not secure enough for modern-day applications. The DES was mainly designed
to function in hardware systems, although it works slowly on software systems (Shahid,
et al., 2005). It uses simple logical operations to encrypt and decrypt data with the use of
a block cipher. The DES has weaker cryptographic capabilities than RSA. The DES keys

can be cracked in 1040 days by using a DES cracker. They can also be cracked using
brute force attacks when combined with computers on the internet
(Shahid et al, 2005). Therefore, it is not used widely by most organizations.
Another technique called the Triple DES is a cryptosystem which is the updated
version of DES (Rachmawati, et al., 2018). The triple DES was developed from the DES
technique. The triple DES technique requires three keys with a length of 56 bits each to
perform the encryption and decryption process. The message to be encrypted must also
have the extension *.txt (Rachmawati et al., 2018). The larger the message, the longer it
takes for the encryption to complete. Overall, the triple DES is more secure and difficult
to crack than the DES.
The AES cryptosystem is another technique that supersedes most of the other
cryptosystems. It is an algorithm-based symmetric key that encrypts and decreases data at
great speed (Laad & Sawant, 2021). The Advanced Encryption System (AES) technique
was created by the researchers Belges Daemen and Rijmen to overcome the weaknesses
in DES. Today, the AES technique is the encryption algorithm that is mainly used
(Boussif, 2022). It is also much more flexible and safer than the DES technique. The AES
technique is utilized in transferring sensitive messages over unsecured channels.
Encryption and decryption are performed using the same private key in this technique.
The sender and receiver share a secret which is the private key (Boussif, 2022). The data
in the AES technique processed in 128 bits which generates texts that are clear and
encrypted. The secret is also 128 bits, which is where the name AES-128 was generated.

Other variant keys of AES include 192 and 256 bits. This makes the AES technique
more secure and flexible to use.
Despite the numerous advantages of MCC, there are still numerous challenges in
securing users’ personal data during communications in MCC networks. One of the
challenges is the unencrypted transmission of personal information due to its large
volume (Gai et al., 2021). Some mobile applications are unable to manage the encryption
of large volumes of data before transmitting them to another device or the cloud. As a
result, many mobile applications abandon the use of cipher texts in the transmission of
data in mobile cloud networks. This phenomenon results in the leakage and loss of users’
personal data because plain texts are easy for hackers and cybercriminals to capture using
several ways, such as spoofing, eavesdropping, monitoring, jamming, etc.
Many authors have tried to resolve the issue of data encryption in MCC networks
using several techniques. Gai et al. (2021) tackled this issue using the Dynamic Data
Encryption Strategy (D2ES) model. This model uses two techniques, (i) classifies data
according to privacy levels and (ii) determines if the data can be encrypted under a
specific time. This technique focuses on encrypting big data considering the time
constraints on encryption. Huang, Zhang, and Yang (2021), proposed a
privacypreserving multi-dimensional media-sharing scheme called SMACD in MCC.
This technique is for preserving media files in the cloud. In this technique, Access-Based
Encryption (ABE) is used to encrypt every file through access-based policy, which
assures the confidentiality of the media as well as controls who accesses the media data in
the cloud (Huang, et al., 2021).

When media creators, YouTubers, and vloggers create video content, they want a
guarantee to share their videos securely and restrict access to unauthorized users. Media
services provide the ability for media owners/distributors to grant or deny access to
subscribers and authorized users; however, the media owners/distributors may not
completely trust the media center not to leak their media contents as well as their
identities to unauthorized consumers (Huang et al., 2021). Some media owners and
distributors may not want their media content to be viewed by the entire public. They
may create content for specific groups of people, and they may not want to share their
identity with their consumers. They may decide to remain anonymous after the media
contents are distributed, which is a serious concern to most media owners and
distributors.
Once media files are posted to media cloud centers, the owners lose control over
who can access the media content (Huang, et al., 2018). The media center has full access
to the media content and may share the content with unauthorized users. The current
techniques for preserving media privacy are identity-based encryption (Zhao, et al., 2012)
and broadcast encryption (Beato, et al., 2016); however, they may not be appropriate for
very large-scale media sharing. The media owners/distributors usually manage access to
their media content using social or subscription relationships. Huang et al. (2021)
suggested a way to solve this challenge using Attribute-Based Encryption (ABE) because
ABE uses one-to-many access control to protect media privacy. Although this technique
is effective, it incurs some computation and communication costs.

The Modular Encryption Standard (MES) is another technique used for
requirement-oriented health information security in the MCC environment (Shabbir, et
al., 2021). Health information security is crucial because most of our health information
is being stored in the cloud today. MCC offers several benefits to the healthcare domain,
such as remote access monitoring of health information, remote access to patient
information, modernization of healthcare applications, quick and easy access to big data
storage and data sharing, and easy collaboration between teams (Shabbir et al., 2021).
However, without proper security of health information, all these benefits will be useless.
MES is a modular symmetric cryptographic algorithm that provides modular security of
health records in the cloud. With the MES technique, cloud service providers cannot
access Health information records, so health information is protected from both
unauthorized inside and outside access. However, some limitations of this technique are
that it is only intended for encryption and decryption of textual data and no other data
formats such as images, and it greatly reduces system efficiency, hence not adaptable for
smart and mobile devices.
Combining multiple data encryption techniques has also been explored to provide
better security for MCC networks. Sarode and Bhalla (2019) proposed an encryption
security model which combines the AES technique, RSA technique, and QR code. The
AES technique, also known as the Rijndael algorithm, is used for securing information in
the cloud. AES is a block cipher algorithm with a packet length of 128-bit. It has three
optional key lengths, 128-bit, 192-bit, and 256-bit (Zhang, et al., 2020). When a user
saves data in the cloud, the data is encrypted from plaintext to ciphertext using the AES

algorithm. When the user wants to access the same data, they are decrypted and sent back
to the user. The RSA technique is an asymmetric cryptographic algorithm. It uses
different keys for encryption and decryption (Bajpai, et al., 2020; Zhang et al., 2020). The
public key is used for encryption and is known to all users, but the private key, used for
the decryption of the data is known only to the owner of the data. RSA uses 1024 and
2048 keys, with the latter being more secure as it has 112 bits of symmetric key length
which are more difficult to crack (Sarode & Bhalla, 2019). The RSA algorithm can also
be used to check and confirm that only those who are authorized can access the
application stored in the mobile cloud.
QR code stands for Quick Response Code. It was created by Denso Corporation in
1994 in Japan (Yue Liu, et al., 2008). The QR code is a two-dimensional barcode that
allows information to be coded in two directions: horizontally and vertically. As a result
of its two-dimension, it can store up to 100 times more data than a barcode, and it allows
decoding at high speed with any smart device, including mobile devices and smart
cameras (Mittal, et al., 2021). A QR code can contain up to 7089 characters, whereas a
barcode can only contain up to 20 digits. QR code also uses symmetric keys, meaning
that the same key can be used for both encryption and decryption, and the QR code can
be generated either from a sentence or a series of non-meaningful characters (Sarode &
Bhalla, 2019). QR codes can, therefore, be used as a means of securing information.
In this encryption process, the AES algorithm will be used to convert plain text
into cipher text. The cipher text generated by the AES algorithm will then be stored in the
database. For more security, the cipher text will then be encrypted using the RSA

algorithm. Finally, the encrypted text will be converted to a QR code, which is a
lightweight application used by mobile devices (Sarode & Bhalla, 2019). There are
several issues with securing data in the MCC environment, and combining multiple
encryption techniques solved some of its security issues. In this model, Sarode and
Bhalla, 2019 combined two cryptographic algorithms instead of using one and used QR
code as a lightweight application that can be used by mobile users. The challenge,
however, is that the process is a little cumbersome and will create some delays when
transferring or retrieving data to and from the cloud. The data first must be encrypted by
AES algorithm and then encrypted again using RSA, and finally converted into QR code.
The data also must go through the same process when retrieving data from the cloud.
Access Policies and Access Control
Data outsourcing services in the cloud have seen an uptick from many
organizations for their data-sharing solutions. MCC was introduced to allow users of
mobile devices to process and store data in the cloud anywhere and at any time (Dinh, et
al., 2011). Mobile cloud users can perform various actions on their smartphones and
tablets such as sharing, manipulating, retrieving, viewing, and storing data. However,
these devices still have limited computing resources, such as processing power and
storage capacity (Fugkeaw, 2021). With the help of MCC, users can offload highly
sophisticated tasks to cloud servers for processing and storage while they deal with
lesscomputing tasks on their mobile devices.
The need for mobile business processing while on the go has also increased with
the continuous use of tablets and mobile phones. Storage services in the cloud, such as

Microsoft, Google, Baidu, Alibaba, etc., provide some of their storage services for free.
However, users may rely on these cloud storage providers to securely share their business
files with others (Ren, et al., 2016). For example, once a user creates a file in the cloud,
other users who have access to the file can edit the file and re-share the file without the
control of the original creator. As a result, the need for fine-grained access policies and
access control over stored files in the cloud has become eminent.
Currently, distributed users have a level of access control that the mobile storage
cloud services provide to them. The mobile storage cloud providers assume that
distributed users share almost equal privileges as the original owners of the file (Ren et
al., 2016) because this helps them to simplify logistics at the cloud level. However, this is
a high risk for mobile users because the files can be leaked or damaged. Access control
should not be determined by the cloud server administrators. Still, it should be made easy
and simple so ordinary mobile cloud users can understand and define access to the files in
a straightforward and easy way.
Various mobile cloud applications allow owners of files to upload videos, photos,
movies, etc., to the cloud and distribute them to other users. The users can then retrieve
and open the files on their mobile phones or Personal computers. However, some of these
files may contain sensitive information, and the file owner may only want to share the
data with a minimal group of users. That means they may not want the cloud service
providers (CSP) to access the files. CSPs may be honest, but they may decide to probe or
explore the contents of the data in their cloud servers (Fugkeaw, 2021). Therefore, access
control policies for protecting data privacy in the cloud are crucial for MCC users.

If the data stored in the cloud is not encrypted, it could be leaked. Attribute-Based
encryption (ABE) was introduced as a solution to this issue. ABE is a method of
cryptography that permits the use of both access control and confidentiality. (Li, et al.,
2015; Thushara & Bhanu, 2021; Yin, et al., 2020).
ABE schemes are very effective encryption systems. The ciphertext in ABE
relates to access structure, while the user’s secret keys relate to attribute sets (Shao, Zhu
& Ji, 2017; Voundi Koe & Lin, 2019). This means that when data is encrypted, it can
only be decrypted after two layers of verification are completed by the users; the
certificate authority (CA) and the attribute authority (AA). The CA helps to identify who
the user is. Once the user’s identity has been verified, the CA will grant them a
certificate. The AA helps to store and verify the dynamic attributes of the user. Once the
attributes are verified and stored, the AA will assign partial keys to the user based on the
credentials they provided (Jamal et al., 2019). However, the drawback of this technique is
that it uses a single CA with numerous disjointed AAs for validating the user’s identity,
thus leading to a single point of failure. To address this challenge, Jamal et al. (2019)
introduced a backup node to store the state of the authority so that each time a failure
occurs, the state of the authority will be retrieved from the backup node.
Currently, the topic of access control policies has gotten lots of attention from
various scholars. Fugkeaw (2021) developed a scheme to allow access control policies to
be shared and used by users who have write privileges for data encryption. Encryption of
sensitive data in the cloud may be possible but using mobile devices to access and
decrypt those data is not practical as mobile devices have very limited computing and

processing resources when handling massive cryptographic operations. Fugkeaw (2021)
proposed a Lightweight Collaborative Ciphertext Policy Attribute Role-Based Encryption
(LW-C-CP-ARBE) scheme, which can be used in mobile cloud environments to provide
lightweight access control. He utilized the Ciphertext Policy Attribute Base Encryption
(CP-ABE) technique for cryptographic access control and Proxy Re-Encryption (PRE)
protocol. He used this technique to reduce the cost of re-encrypting and decrypting data
for mobile users. According to the author, this scheme also helps to reduce storage and
maintenance costs for the data owners.
Another access control technique that has been explored is Attribute Based Access
Control (ABAC). This model uses the attributes of entities in a system to give access to
users. It uses characteristics like user attributes, object attributes, conditions of the
environment, etc., and some authorization rules (Karimi et al., 2022). This technique is
effective for situations where the data is to be used by users in a group (Masoud et al.,
2022). For example, industrial cloud computing service users could include
manufacturing, sales, consulting, legal, logistics, and scientific research organizations
(Gupta et al., 2022; Song et al., 2019). For such circumstances, attribute-based access
control may be the best solution because the only users who can access the data will be
users who meet a specified set of access policies.
Data Security
Data security in MCC refers to safeguarding data from corruption and from
unapproved users. Some ways in which data can be protected in the cloud include data
encryption, tokenization, management of distributed systems, etc. (Prakash et al., 2022).

Data security is very essential in MCC to safeguard both individuals’ and organizations’
sensitive data. Many organizations are skeptical about migrating their sensitive data to the
cloud due to several security issues in MCC. Chief Technology Officers (CTO) and
security managers continue to worry about matters of privacy and security of data in the
mobile cloud (Muhseen & Elameer, 2018). For more organizations to adopt MCC, cloud
providers must lay out a tested and verified cryptography scheme for storage sharing and
data security. They must also provide a user access protocol that is trusted to ensure that
unauthorized users do not gain access to sensitive data, and a scheduled, reliable, and
secure backup of data and media (Prakash et al., 2022). If all these security issues are
addressed, there will be more adoption of MCC by organizations.
For users’ data to be secured, cloud providers must also design a system that
threats from external sources and fault tolerance cannot threaten. Other factors in MCC
must be addressed, such as mobile cloud-based data exchange privacy. Privacy in MCC
refers not only to information hiding but having legitimate control over your users’
sensitive data and following specific laws for access to such information (such as income
tax, etc.). Numerous security and privacy laws must be imposed in MCC to collect,
maintain, use, and disclose personal information by mobile cloud providers (Alnajrani et
al., 2020). Manufacturers of mobile phones and software developers must also establish
security protocols that would secure sensitive information on mobile phones (Hu, Kumar
& Popa, 2020). Such measures would aid the protection of mobile devices from external
threats. Mobile devices could also be easily stolen, allowing access to highly sensitive
and personal information (Arumugam et al., 2021). Mobile cloud providers must,

therefore, establish security measures to address such challenges to increase the adoption
of MCC.
To protect the data in MCC, mobile software developers and security managers
must first identify the possible threat and challenges in MCC that needs to be addressed.
Some of these threats include data replication, unavailability of cloud resources,
unreliability, and trust, among others (Muhseen & Elameer, 2018). The appropriate
countermeasures to these issues must be thought of while designing a secure system in
MCC. For safety in MCC, three major kinds of assets must be protected: data, software,
and hardware resources. The issue of security in MCC can also be classified into mobile
threats and cloud threats (Muhseen & Elameer, 2018). By addressing the security issues
in both the mobile and cloud threats, we would have a more secure MCC environment
which would lead to more adoption of MCC by organizations.
Latency and Reliability
Latency and reliability are issues of great concern in Mobile Cloud Computing
when offloading heavy computational tasks to the cloud. Due to the limited resources in
mobile devices, such as limited CPU processing capabilities and limited storage, mobile
users can offload heavy tasks to cloud servers for processing and storage (Annane &
Ghazali, 2019). However, some of these tasks are offloaded to distant cloud servers
leading to high latency, low bandwidth, real-timeand low performance (Akki &
Vijayarajan, 2021). Mobile users may try to utilize their mobile applications to access
health care information, road traffic measurements, smart education, geographic location,
multimedia files, etc. If these users are in locations with low Wi-Fi signal strength, they

may not be able to access this information in real-time, or they have a very high response
time. One solution to this challenge is the use of Cloudlet. Akki and Vijayarajan (2021)
stated that a cloudlet is a mini cloud server attached to a local network access point for
the purpose of providing high-speed code execution to devices. Normally, a cloudlet has
less computation abilities when compared to remote cloud servers but provides a quick
connection to devices.
Due to mobile device users moving from one location to another, allocating
resources to complete users’ requests is a major challenge. Also, Wi-Fi signal strengths
vary from access point to access point from time to time (Akki & Vijayarajan, 2021; He
et al., 2018). Since mobile device users are changing locations frequently, their
connection is unstable. Unlike wired connection which is fast and reliable because it
requires the user to be in one spot, Mobile device users can have access to their resources
to complete tasks while on the go. Wireless channels suffer from fluctuations in signal,
hence leading to poor response from cloud services. There are several reasons for signal
fluctuations. they include path loss, multi-path fading, and shadowing effect (Akki &
Vijayarajan, 2021). Radio fluctuation is also another reason for poor connectivity. Once
all these factors are considered, mobile device users may be able to have better
connectivity while on the move.
Mobility plays an important role in MCC. Mobile device users always move from
one location to another while trying to access cloud resources or offload tasks to cloud
servers. This sometimes results in the failure of mobile user requests, long response time,
and affects the correctness of the data (Akki & Vijayarajan, 2021; Fakhfakh, 2019).

Therefore, reliability is a very important factor when discussing MCC because its users
are not limited to being in one location. They change location constantly. Since MCC
architecture is dynamic in nature, it is necessary that users be assigned to the correct
access points in order to have continuous connectivity (Akki & Vijayarajan, 2021;
Khorramnejad et al., 2018). By having users connect to the right access point, they will
not only experience better internet connectivity on their mobile devices but will also have
minimal disconnection rates, short response time, and correct data.
Strategies to Control Security Breaches in Mobile Cloud Computing
While mobile cloud computing provides lots of advantages to both individuals and
organizations, they also increase the chances of intentional or unintentional data security
breaches. As a result, security budgets must include mobile devices and cloud computing.
One of the biggest concerns with mobile devices that have access to company networks is
that they can be easily lost or stolen due to their small and portable size (Controller
report, 2011). Therefore, organizations must budget for the use of strong passwords and
data encryption solutions. Also, they must set up a system that would allow them to
remotely wipe the data on the mobile devices issued by organizations.
Some organizations require employees to register any device they want to use for
work on the company’s network. Then they install applications that give the organization
some control over the device and can wipe the data from the device should it get lost or
stolen. Other organizations only allow employees to connect company-provided devices
to the network to access company data. Some organizations also set up applications to
monitor or manage what the company policy allows on the devices (Controller report,

2011). For example, companies might set up programs to block downloads of certain
applications, while other programs can separate corporate information from personal
information, so it would be easy only to wipe corporate information in case it gets stolen
or lost. Some of the applications can also track where the device is located. This will
allow them to find the device if it gets missing or stolen.
Some mobile users access the services of mobile-based systems via the cloud
through an internet connection. This makes them vulnerable to attackers. Attackers may
employ various ways to attack mobile users, such as blocking data access from mobile
devices to the cloud and inserting infected codes into mobile applications to gain access
to mobile users’ sensitive information (El-Sofany & Abou El-Seoud, 2019a). Some of
these attacks are possible due to the weaknesses in mobile device designs and the usage
of mobile devices. Other weaknesses in mobile devices include failure in the
authentication of username/password, outdated operating systems in mobile devices due
to bandwidth issues or weak internet connection to continuously update the software
versions in the mobile devices, etc. (Tekade & Shelke, 2014). If these weaknesses are
addressed, mobile devices will be much less vulnerable.
There are some major factors that must be in place to ensure that communication
between mobile devices and cloud servers is secure. They include authentication,
accountability, confidentiality, integrity, availability, and portability. Mobile users want
fast and undistributed internet connectivity when navigating from one URL to another.
This is one of the motivations attackers bank on to perform attacks on mobile devices

(Talukder et al., 2018). They look for ways to disrupt/obstruct the communication
between the cloud servers and the mobile devices and then launch their attacks.
Attacks in the Cloud Environment
There are divers cyber-attacks carried out by hackers. They include the following:
Distributed Denial of Service (DDoS). Attacks such as Distributed Denial of
Service (DDoS) are destructive and can cause significant challenges to the security of
mobile cloud computing (El-Sofany & Abou El-Seoud, 2019a). DDoS attacks primarily
attack and infect wireless device resources (such as wireless networks, software
applications, etc.) and make them inaccessible to their users with authorization. During
DDoS attacks, the hacker attempts to make the Mobile-based service overloaded with
traffic so that authorized users cannot access the requested service. They do this by
disrupting the web service or network access (Tang et al., 2019). The attacker usually
launches the DDoS attack using numerous machines with the intention of overloading
both the mobile device Central Processing Unit (CPU) and the wireless network. Such
attacks has gained lots of success because there exists the absence of a sound mechanism
or technique to defend against such attacks on mobile devices (El-Sofany & Abou
ElSeoud, 2019b). This issue motivated many researchers to continuously study and seek
ways to protect devices against such attacks. There are several pieces of research about
automatically detecting DDoS attacks, but most of them have low detection rates and
high false positives (Cheng et al., 2018; Idhammad et al., 2018). To defend against the
DDoS attack, security managers must impose DDoS attack detectors and strict
authentication on all communication exchanged between mobile devices and their IP

agent (Cheng et al., 2018; Zhang et al., 2019). This will provide better security in MCC
and make mobile device communications inaccessible to hackers.
Redirection Attacks. A redirection attack is an attack whereby the hacker
redirects the traffic meant for a mobile device and sends fabricated traffic to the device
instead (Anssari et al., 2021; Talukder et al., 2018). Such attacks deprive the mobile
device of getting the data it needs and are common with IP addresses like file servers,
DNS servers, etc. To defend mobile devices against redirection attacks, security managers
must ensure that the IP addresses of the nodes used for communication are changed
frequently (Anssari et al., 2021; Talukder et al., 2018). Another solution is for the
corresponding node to always authenticate and verify the binding update before sending
data to the mobile device (Talukder et al., 2018). This would help to confirm that the data
is coming from the right source. Although this is a security measure to mitigate this
attack, it may slow down the connectivity between the mobile nodes.
Bombing Attacks. A bombing attack is an attack in which an attacker redirects
huge number of unwanted data traffic to a victim’s node to exhaust the bandwidth of the
node and significantly degrade its performance (Talukder et al., 2018). Real-time
streaming servers are usually targeted by hackers for this type of attack. To defend
against bombing attacks, the servers should send hello packets to the new location of the
mobile device and wait for an acknowledgment. Once acknowledgment is received, it can
send the requested data to the mobile device (Talukder et al., 2018). This extra step of
acknowledgement will help to prevent bombing attacks and confirm that data is being
sent to the right device.

Replay Attacks. A replay attack is an attack where the hacker takes advantage of
a binding update (a message which notifies a home router of a mobile device’s location)
that was recorded previously and replays it when the mobile device user moves to a new
location (Talukder et al., 2018). This, therefore, disrupts communication between the
mobile device and the genuine node it should be connected to. To protect mobile devices
from replay attack, the corresponding node should make sure that the binding update is
authenticated before updating it. Nonetheless, it could be that the attacker already has the
authenticated binding update; therefore, we should utilize the sequence number for
authentication instead (Dizaj et al., 2011; Talukder et al., 2018). The corresponding node
should ensure that it authenticates the binding update and does not allow a repeat of
sequence numbers to prevent replay attacks.
Information Security Management Internal Controls
Organizations utilize internal controls and audit mechanisms to secure their data
and manage information security (Bozkus Kahyaoglu & Caliyurt, 2018). However, the
organization’s information security policies must be properly defined to have an effective
internal control mechanism. Standards like ISO 27001 is effective in the designing and
creation of internal control policies. Also, executive management corporate decisions on
handling information assets to ensure they are safe and secure are captured through
policies (Bozkus Kahyaoglu & Caliyurt, 2018). Policies dictate and regulate what is and
what is not acceptable and what controls are necessary to be compliant (Niemimaa &
Niemimaa, 2017). Internal control helps to monitor and make sure that the policies are
compliant, while policies are effective in addressing the existing information security

risks in organizations. There is a relationship between audit theory, internal control, and
security policy theory because the theories function together to ensure that the
information security system is effective within organizations. Factors such as culture,
applications, and technology influence security policies in organizations. These policies
sometimes change with changing technologies or cultures, but with an effective internal
control system, such changes will still be in compliance with existing security standards.
Internal control also ensures that the organization complies with its security policies by
making the policies available and easily accessible to employees. Communication of
policies and procedures and compliance with these policies is one of the key objectives of
internal control functions (Bauer et al., 2017; Humaidi & Abdallah Alghazo, 2022).
Policy communication can occur in several ways, such as security awareness campaigns,
training, etc.. Such actions aid organizations in meeting the information security
requirements needed to keep their data secure.
Analysis of Supporting Theories
Socio-technical Theory
The socio-technical systems (STS) theory is relevant in information security
management. It was introduced by Emery and Trist (1965) to analyze how combining
social and technical factors explains innovation in and transformation of organizations.
This theory suggests that organizations must invest time and resources, and focus on their
social and technical structure in order to be successful (Münch et al., 2022). The STS
theory put into consideration several aspects of the organization, including people,
processes, culture, and technology (Zhang & Williamson, 2021). The social aspect relates

to people, relationships, organizations, performance measures, and culture, and the
technical aspect relates to technology, innovation, knowledge, and processes (Emery &
Trist, 1965).
The application of the STS theory helps organizations to consider both the social
and technical aspects when developing security strategies to be implemented in the
organization. STS led to the re-design of the workplace, which increased the employees’
productivity, motivation, and well-being (Sony & Naik, 2020). It was initially divided
into four dimensions that are interrelated; task, people, structure, and technology (Leavitt,
1965). It was later modified and turned into a six-dimension system consisting of
technology, people, processes, goals, infrastructure and culture (Sony & Naik, 2020). The
STS is systemic, and it takes both the technical and social factors into consideration when
implementing new technology within the organization. Therefore, making changes to one
part without considering the effect on the other part will result in complications in the
workplace (Sony & Naik, 2020). The STS theory aligns with the IST theory because
when considering the information security policy theory, risk management theory, and
contingency theory, they are designed around technology, the environment, and people.
The IST was the most appropriate for this study because it provides a clear path
and simplified procedures to manage information security in organizations. While STS
merely lists all the security areas to be covered, IST completely covers all areas where
information risks are concerned. Li, Trutnevyte and Strachan (2015) also listed the
difficulties in implementing STS, such as lack of method and detailed structure for
implementation, etc., which is a drawback for applying STS in organizations. Another

limitation of the STS is that it does not completely cover the issue of monitoring the
theory for effectiveness. All these limitations are provided by the IST, and IST monitors
its effectiveness through its control and auditing policies. Organizations may, however,
utilize STS by combining it with other theories or using it on an ad hoc basis. Therefore,
the STS theory would not be sufficient in exploring the strategies for securing users’
personal data in MCC networks.
Activity Theory
Activity theory was formed in the 1920s and 1930s. Vygotsky (1978), a Russian
psychologist, stated that human beings do not interact directly with their environment but
via mediating artifacts (Chen et al., 2007). Another great Activity Theorician, Engeström
(1987) contributed greatly to this theory making it a powerful tool for analyzing social
systems.
Activity theory states that the activities humans engage in produces results because
they do so with artifacts and other resources. The fundamental rules of Activity theory
include that activity is the root of analysis, has a development process and history, and
uses mediatory artifacts (Gupta & Sharman, 2009). An activity is made up of various
elements including, objects, subjects, community, rules, tools, and division of labor. All
of these elements form a complete human activity. The primary purpose of human
activities are to bring about specific artifacts and convert them to certain outcomes or
results. Kuutti (1995) opined that in order for human activity to transform into outcomes,
a group of subjects must share the artifacts amongst themselves with the primary aim of
achieving the set objectives. These activities are conciliated with the instruments, tools,

and laws of the environment, which sets the boundaries for the performance of the
activities.
Activity Theory has also caught the research community’s attention for system
designs and development in organizations. This is because it furnishes a foundation for
analyzing the computer-mediated activities of an organization (Chen et al., 2007). This
Theory is also valuable for information security. Show (2017) used it in a payroll
processing system. He set payment issuance as an object, stakeholders, employees, and
other staff as objects, and information systems and payroll software as procedures for
accounting and mediating artifacts (Gupta & Sharman, 2009). In the above study, Show
(2017) expressed that the subjects of the activity used a division of labor style to perform
their functions based on certain rules and organizational policies in the community.
Activity theory was also used by Gupta and Sharman (2009) in designing secure Role
Based Access Control (RBAC) and engineering processes. He used the theory to
investigate how engineering processes are structured and their limitations.
Information security management also applies Activity theory to investigate why
employees are not compliant with security requirements and the causes of security
breaches within organizations (Jingguo, Gupta & Rao, 2015). Activity theory, therefore,
assesses the entire information security system and its various elements and relationships
with other systems. It operates with the assumption that there are rules that guide the
interaction of all the components in an activity (Razak et al., 2018). Activity theory is
somewhat similar to IST; however, it does not state what the nature of the rules will be.
Instead, it assumes the rules will be created by the culture and interactions the system

already has in place. IST takes a different approach. It suggests that standards will
determine the rules through IST’s management system theory. Through the requirements
of risk management theory, IST also captures how actors behave in a system and uses
those behaviors to develop rules and policies. However, Activity theory does not regulate
the practices of application. Therefore, the IST theory suits this study more than the
Activity Theory.
Distributed Cognition Theory
Distribution cognition theory (DCT) is utilized in the exploration of topics relating
to information security management. This theory focuses on studying humans and their
interactions with the computer. The DCT was created by Edwin Hutchins in the middle of
the 1980s (Jones, 2010) and he stated that cognition is a distributed phenomenon. DCT
theory suggests that all areas of the cognitive system are necessary for the understanding
of a system. This theory contrasts with the traditional cognitive phenomena, which
explain the processing of information at individual levels. The DCT theory proposes that
we should approach cognition as a distributed phenomenon (Rogers,
1997). In studying a cognitive system, one must consider the individual, their social
networks, and their related environment (McNeese & Hall, 2017). Therefore, DCT is the
study of the interactions of people, their functional relationships, resources, and materials
when they are present in systems. The DCT theory assumes that the personal cognitive
property of an individual is completely different from the cognitive properties of two or
more individuals (Rogers, 1997). Therefore, if a group of individuals collaborate and

work towards achieving a common goal, the result or outcome will be much more
effective than an individual effort.
The DCT theory is being applied to information security management as well. It
argues that information security management is related to human cognition and behavior.
Since information is highly disseminated in a virtual environment and employees are
responsible for most security breaches due to their contradiction of the security policies
of the organization, the theory argues that the approach should be in a distributed fashion
and not from an individual perspective. The solution is to create a distributed awareness,
or corporate awareness in order to build solid threat recognition and awareness among the
people in the organization (Banks et al., 2018). With everyone being aware and trained on
the security threats faced by the organization, they can all work collectively to mitigate
security breaches. D’Angelo and Rampone, (2018), views this theory as a network of
information among individuals in the organization. With this theory, people can interact
with themselves and with technology in a distributed and interconnected manner without
compromising the availability, confidentiality, and integrity of information assets in the
organization.
The interconnection of people and technology is in alignment with IST because
IST supports the interconnectivity and distribution of information in a computing
environment. Both principles consider the cognitive system, people, and technology to be
able to develop the appropriate security needed to secure information in organizations.
The DCT theory supports the STS theory because it combines social and technical
systems and connects people with technology. The DCT contradicts the IST because,

from a process view, the IST supports a holistic coverage of information security, while
the DCT, just like STS, views information security from a subject and object lens (Li et
al., 2015). The process view of IST uses multiple theories to ensure all the elements of
information security are covered which makes it a better theory for this study than the
DCT and STS theories.
Analysis of Contrasting Theories
General Deterrence Theory
General deterrence theory (GDT) was adopted from the discipline of criminology.
It aims primarily to discourage or deter criminal acts (Cohen & Nagin, 1978). This theory
states that having information security countermeasures and palns in place can discourage
people who commit computer security crimes from committing them. Lee (2017) states
that penalties must be critical and dire to discourage computer crimes. Deterrence often
occurs when people become afraid of committing crimes because of the harsh
consequences they will bring on them if caught (Bhattacherjee & Shrivastava, 2018;
Chen et al., 2018). Having sanctions and disincentives in place are effective in
discouraging computer criminal activities. The disincentives can be divided into two
parts, the certainty of the sanctions and the severity of the sanctions (Cohen & Nagin,
1978). This means that when computer security abusers think of the risk and harshness of
the punishment, they would change their minds about committing computer crimes.
GDT is of great importance and usefulness to Information security management
and research. Straub and Welke (1998) stated that GDT is fit for establishing security
policies, accessing the effectiveness of the policies, and the risks involved. Although

some computer violations may be unintentional, and some employees’ behavior might not
be motivated by malicious intents, however, such behaviors might compromise computer
systems and lead to data breaches. Information security managers are very concerned
because employee negligence and intentional/unintentional insider breaches pose
significant threats to the organization. Information security standards such as ISO
27001:2013 describes the requirements for discipline that sanctions non-compliant
behavior. Also, ISO 27002:2013 code of practice defines a process for monitoring
employee behavior (Trang & Brendel, 2019). The GDT is therefore important to
information security managers for mitigating computer criminal behaviors.
The GDT contrasts with the IST because it only focuses on the irrational
behaviors of computer users, unlike IST, which focuses on both the rational and irrational
behaviors of computer users. The GDT also focuses only on the subject and objects
involved in the technological tools of information systems. Alternatively, IST centers on
objects, subjects, processes, and technologies, making it a more comprehensive
framework for this study and for dealing with the issues of information security. IST also
makes provisions in situations where violations are unintentional by using its contingency
theory (Ismail et al., 2014). IST also stresses that no individual theory can be used to deal
with security issues; instead, one must combine multiple theories to provide a holistic
resolution to information security issues.
GDT deals with human psychology and compliance to deter information security
violators. IST makes provisions for worst-case scenarios even when irrational behaviors
are noticed in the organization (Onwudiwe, Odo & Onyeozili, 2005). GDT is very

effective in providing compliance standards that employees or subjects must comply with
in order to prevent severe penalties. This is also a part of IST. Lee (2017) stated that
subjects must understand the expected standards in-depth for GDT to support information
security. IST has theories such as risk management theory and contingency theory to take
care of situations where a non-understanding of standards is present. This proves that IST
would thrive where GDT fails.
The risk management theory in IST certifies that risk issues, including
nonunderstanding information security standards, are provided for when designing IT
security strategies and solutions. This means that IST provides a better plan and
foundation to manage information security. However, one can still consider GDT as an
applicable theory because people cause a huge number of losses due to intentional and
unintentional behavior leading to security breaches. Creating a quick and definite
retribution for wrong behaviors that threatens information security will mitigate breaches,
however, is a better theory because it has a broader foundation and contains plans and
mitigation steps for situations where security breaches occur.
Securitization Theory
This theory started from the works of the Copenhagen school, by Buzan, Wæver,
and de Wilde (1998), as stated by Gaidaev (2022). They suggested that security does not
only concern itself with the object (function of what makes up a risk) or the subject
(function of what is viewed to be a risk); rather, it is what the securitizing actor claims to
be a risk (Gearon, 2017). A securitization speech is one that would propel survival and
emergency response when a situation is labeled as a risk (Harrison, Ahn & Adolphs,

2015). Therefore, if an issue is securitized, it becomes an issue of high importance and in
need of a swift resolution. This means that by simply mentioning the word “security”
something or action gets done. When something is labeled a security issue, then it
becomes a security issue. When one states and proves that the existence of an object is
threatened, an actor of security takes a position to make sure that the object is protected
(Gearon, 2017). This moves the issue from the sphere of a normal issue to an emergency
issue where it is handled swiftly without following the normal procedures, rules, and
regulations of making policies.
Taureck (2006) stated that to prevent everything from becoming a security issue,
securitization should consist of three factors: (i) identification of existential threats (ii) the
need for emergency action (iii) the effects of inter-unit relations as a result of the
exoneration from rules. Therefore, any issue or situation that has all three factors should
be securitized and should not be securitized if any of the above factors are not present.
Buzan et al. (1998) focused more on the first factor, which is the identification of
existential threats. He stated that for a situation to be securitized, it must pose an
existential threat. If it poses an existential threat, then it must be tackled immediately, else
all they do are irrelevant because we may not be alive or free to take care of the issue next
time.
Securitization theory contrasts with the IST theory because the IST theory
considers risks from an all-around perspective. Securitization theory is useful in
cybercrime prevention because it labels cybercrime events as dangerous, and as a result,
it leads to proactive preventative and mitigative efforts. Just like IST, it also supports the

objective of risk management. Attributing risks using the securitization speech is similar
to the activities involved in risk management in IST. In comparing both theories, the
securitization theory seems inappropriate and inadequate for this study because it lacks
the depth to uncover all the risks involved in efficiently securing information systems.
While securitization theory uses securitization speech to address risks, the IST theory
employs a formal process of risk management that provides for and manages all aspects
of risks in an information system. Also, securitization theory may not provide allinclusive
protection for information systems because the risks it considers are the risks determined
by a few select groups of people.
The securitization theory, just like other theories discussed earlier is object and
subject dependent. This means that labels of insecurity are affected by the elements or
subjects involved (Wan Rosli, Kamaruddin, Mohamad, Mohd Saufi & Hamin, 2021). The
IST, on the other hand, defines processes and functions to achieve security goals. IST sets
standards and processes to mitigate risks and makes security provisions for both objects
and subjects present in the information ecosystem, and the ones to come (Ismail et al.,
2014). The IST also encompasses the contingency theory for managing risks should a
breach occur. It also assumes that no individual theory can address all threats, and that is
why it combines several theories for the holistic management of information security
(Dimase et al., 2015). IST, therefore, provides comprehensive coverage of information
security in organizations because it encompasses people, processes, and technology.

Transition and Summary
The integrated system theory (IST) of information security management by Hong
et al. (2003) was the framework used to develop this research. The approach offered
various information security strategies, methods, and procedures that researchers can
utilize to comprehend different vulnerabilities that could lead to the loss or leak of users’
sensitive information. It provided insights regarding security challenges, threats, and risks
faced by organizations and individuals within the mobile cloud computing system.
Weaknesses within mobile cloud computing networks could allow cybercriminals and
hackers to infiltrate information systems. Loopholes within mobile applications may also
result in severe harm to information assurance within MCC. It is paramount that
information security managers asses MCC faults and vulnerabilities and determine how
such issues might lead to information breaches and loss of confidential information. The
IST model uses strategies such as security policies to set rules and regulations to handle
internal and external threats, internal control to ensure MCC is safe and secure to transmit
users’ confidential information, and contingency management to teach and coach
employees on how to defend the MCC network against cyber threats. Additionally, risk
analysis is an important aspect of information security. By identifying, exposing, and
categorizing MCC risks, information security managers might provide relevant fixes and
implement the appropriate measures to secure users’ sensitive data in MCC networks.
In section 1, I discussed the importance of information security managers to
follow best practices when implementing policies to secure personal data in the mobile
cloud computing (MCC) environment. I provided a list of definitions used in the research

to help readers understand the specific meaning of the different terminologies used. I also
included the background of the study, the problem and purpose statements, the nature of
the study, research questions, conceptual framework, assumptions, limitations,
delimitations, and significance of the study that would contribute to the implications of
social change.
Section 2 describes how I conducted the study. It includes an overview of the
project, purpose statement, and discussion of the role of the researcher, participants, the
research method and design, population and sampling, ethical research, data collection
instruments and techniques, data organization techniques, data analysis, and the reliability
and validity of the study. Section 3 includes a presentation of (a) study findings, (b)
implications for social change, (c) recommendations for action and future research, (d) a
reflection of the experiences encountered conducting this study, and (e) my research
conclusions.
Section 3: The Project
The purpose of this qualitative pragmatic inquiry study was to identify strategies
necessary to secure users’ personal data against security threats in MCC networks. The
target population is information security managers in the United States who are
implementing various strategies to secure their users’ personal data against security
threats in their MCC networks. In the findings of the study, I identified strategies that
other information security managers applied to effectively secure their users’ personal
data against security threats in their MCC networks. The implications for positive social

change included increased security of MCC networks and protection of MCC user’s
personal data, reduced security breaches, thereby cutting down the overall financial losses
acquired by organizations from security breaches, and protection of consumers from
high-risk and cost of identity theft, which could be caused by confidential information
breaches.
Project Ethics
As the primary instrument for data collection in this study, I recruited participants
who met the study’s eligibility criteria, developed interview questions, conducted
interviews, rereviewed the documents from selected organizations, engaged participants
in member checking, analyzed the data collected, and interpreted the findings of the study
including reporting results. Another role I played as the researcher was to make sure that
there were no forms of bias during the study that would affect the overall outcome of the
study. I also made sure that the questions asked to all participants were consistent. Van
De Wiel (2017) stated that accurate and useful data can be obtained from participants
when they sincerely answer the interview questions asked in a study. By using interview
protocols, I made certain that all participants answered the same set of interview
questions. Interview protocols also enabled me to stay focused on the objectives of the
study and helped me make good use of my time and that of the participants during the
interview.
I used open-ended questions to extract rich and comprehensive details from the
participants’ responses, which led to further follow-up questions and open discussions.
As part of the data collection process, I took down notes, recorded the interviews, and

made thorough observations during the interview. Additional data were sourced from
organizational records, archival records, policies, information security reports, and data
available to the public. The other sources helped in verifying the information collected
during the interview. I also complied with the Belmont Report protocol regarding the
guidelines and principles to be followed during interviews, informed consent, risk
assessment and benefits, and participant selection. For every interview I conducted, I
ensured that the environment was safe for the participants, which complied with the
requirements for respecting humans in the Belmont Report (U.S. Department of Health
and Human Services, 1979). As a researcher, one must highly consider the safety,
personal dignity and autonomy of each participant during the research. The Belmont
Report also covers the beneficence principle, which means that the researcher must
protect the interview participants from any harm. It also includes reducing or eliminating
any risks that would damage the research or disrupt the fair distribution of the research’s
benefits.
Additionally, I implemented member checking which was a method of affirming
collected information with the participants to help validate and ensure the accuracy of the
interview data collected (Motulsky, 2021). With the method of member checking, I went
back to the participants and asked them to review the responses and summaries gathered
from the interview to ensure that the data reflected the responses, experiences, and ideas
they shared. Member checking provided an avenue for the interview participants to
validate their responses and make corrections where necessary.

Finally, as the researcher, I tried to minimize any form of bias. To accomplish
this, I used the technique called bracketing. Bracketing is a research technique used to
suspend the beliefs, prejudices, assumptions, or any previous experience of the researcher
related to the study or phenomenon (Gearing, 2004). I made sure to exempt any previous
personal views and opinions about the phenomenon under investigation from the
interview process.
Ethical defence and precautions are very crucial in every study because they are
put in place to protect participants. In this research, before the data collection process, I
obtained IRB approval from Walden University. Once received, I started the process of
data collection. I reached out to participants and sent them the consent form via email.
The content of the email included important details of the research, such as the research
topic, the purpose of the study, ethical concerns, and potential dangers. It also included
the voluntary nature of participation in the research, the right to decline or pull out from
the research at any point, and instructions to follow if they wanted to participate in the
study.
Informed consent includes the rights of participants, details of the research, and
instructions to indicate that one has accepted to contribute to the study (Xu et al., 2020). I
communicated with the participants the purpose of the study, the risks and benefits of the
study, and the duration of the study. One of the primary goals of ethical standards is to
protect participants from risk and harm during the research (Ross et al., 2018), so I made
this a priority during the entire period of the research. I also ensured that ethical issues
toward the participants were addressed. One such issue includes confidentiality. I ensured

that the information chosen by the participant to be confidential stayed confidential. Such
actions strengthened the trust between the interviewee and the interviewer, thereby
reducing concerns on the part of the participants regarding any harm that could result
from the study (DeRenzo et al., 2020).
The ethical protection of interviewees was an important part of the research.
Participants were informed that they were free to stop the interview and opt out of the
research study at any time. This was stated clearly in the letter of consent. Also, I
included that if they wished to withdraw from the research, all they needed to do was
send me an email informing me of their decision to withdraw. There are several reasons
why a participant may choose to withdraw from a study, and according to the Belmont
report, they can leave the research at any time during the research period. I also took
deliberate steps to ensure ethical principles were upheld during the study. Steps included
ensuring the participants’ identities and their organizations were protected and
represented with codes (such as participant 1, company X, etc.). I also stated clearly that
their confidential information will not be disclosed, divulged, or treated in any way that
would expose either the individuals or their organizations. I also ensured that the consent
was completely voluntary and that participants exercised their freedom of choice. No
intimidation, force, pressure, or deception was involved in the recruitment process in any
way.
In research from Bible et al., (2020), interviewers may offer financial incentives to
entice interviewees to participate in research studies. In this study, I clearly informed the
participants that there were no incentive or financial benefits when participating in this

study. Other investigators believe that creating trust is a better way of communicating and
retrieving information from participants than offering any form of reward (VandeVusse et
al., 2021). I made sure to build relationships with the interviewees so they were
comfortable during the interviews and provided all the knowledge and strategies they
have for securing MCC networks from security threats.
In this research, I ensured that the rights, privacy, and integrity of every person
and institution involved were respected. Privacy refers to when the identity of participants
in a research study is protected (Molitorisz et al., 2021). I coded the participants’
information, such as names, employment roles, names of their organizations, etc., to
ensure integrity is observed. Using codes to protect participants is encouraged as a tested
and trusted way to ensure confidentiality (Kennedy et al., 2021). I protected all the
information I collected from both organizations and participants in a separate file and
stored them separately from the main research using multi-factor authentication. I secured
all hard copies of the research study and research materials from organizations, which
were kept in a secure drawer in a private room in our house. I also made sure that all
documents relating to this research will be destroyed after 5 years. When the time arrives
to destroy the documents and files of this study, I will delete and empty the trash of my
online drive. I will also shred every paper document related to the research.
Nature of the Study
I used the qualitative multiple case study method for this research. According to
Bleiker et al. (2019), a qualitative methodology enables the researcher to gain a rich,
detailed, and deep understanding of a process. Because my primary focus was to

investigate and uncover strategies used by information security managers to protect their
mobile cloud computing networks, a qualitative study was the most appropriate research
method. A quantitative research method would have been appropriate if I intended to
acquire statistical data to test a hypothesis (Zyphur & Pierides, 2019). Quantitative
researchers use experimental methods, quasi-experimental designs, and nonexperimental
correlation designs to investigate cause-and-effect relationships among variables (King et
al., 2019). Researchers who make use of quantitative methods emphasize more on
numerical measurements using structured questionnaires or experiments. Quantitative
methods are more useful when used to compare data systematically and may relate to
analysis or comparison between groups. A quantitative study was not a suitable choice
because I did not test any hypothesis in this study and did not study the relationship
between variables.
A mixed-method approach is a combination of qualitative and quantitative
methods to answer complex questions (Stoecker & Avila, 2020). In mixed methods, the
researcher utilizes the techniques and components of qualitative and quantitative
research. In this method, there are multiple processes for collecting data, and researchers
using this method may engage in both inductive and deductive reasoning to support the
research findings. The mixed method is very complex and requires extended time for
researchers to complete because they have to manipulate the data between qualitative and
quantitative methodologies. Because this study did not combine numerical testing with
the experiences of participants, I did not utilize the mixed-method approach.

Research Design
I chose the pragmatic inquiry design for this research because it focuses on
individual decision-making within real-world situations (Frey, 2022). The pragmatic
inquiry design is useful for better understanding and solving the needs of complex
problems. My aim was to examine the experiences of information security managers on
real-world strategies to secure their users’ personal data in MCC networks; therefore, the
pragmatic inquiry design was the most appropriate design. The pragmatic study is an
effective study for investigating and taking an in-depth look at a contemporary
phenomenon using participants in real-world environments (Frey, 2022). Using a
pragmatic inquiry design allowed me to develop in-depth insight into each organization’s
experience and specific strategies used by their information security managers for
securing their user’s personal data from security threats in their MCC networks.
The ethnographic design is used when the researcher intends to immerse
themselves in the culture of the sample to observe patterns, language, ideologies, and
experiences (Thomas, 2017). I did not use the ethnographic research design because I did
not intend to observe the cultures of information security managers, and this research
design will prolong the research process. A phenomenological design was also not chosen
for this study because the phenomenological design is focused on understanding the life
experiences of a sample population (Thomas, 2017). The phenomenological design would
have been useful if my intention was to understand the lived experiences of participants
and if I sought to describe the essence and importance of their experiences (Faronbi et al.,

2019). I did not choose this design because I did not observe the perceptions of the lived
experiences of information security managers.
In a narrative design, the researcher’s primary focus is on studying the lived
experiences of participants through storytelling (Rahiem et al., 2021). I did not choose the
narrative design because this research did not be focus on the history and biographies of
information security managers. A narrative design captures individuals’ stories, including
requesting for participants to provide stories about their personal lives and interaction
with people, family, friends, strangers, co-workers, and life in general. (Merriam &
Grenier, 2019). The narrative design may be useful for exploring the experiences of a
group and investigating how the social, cultural, and physical environment impacts their
practices (Haydon et al., 2018). The narrative approach digs into people’s personal
experiences. In this approach, the participants tell stories of how they experience the
world in which they live. This approach has some downfalls because the stories, frames
of orientation, etc., could change. Because this research did not be focus on the history
and biographies of information security managers, I did not choose this design.
Additionally, saturation is also another crucial aspect of research. One of the
important elements of qualitative research is for the research to reach saturation.
Saturation is the point where reviewing more data will not provide any additional or new
data related to the research question (Lowe et al., 2018). Data saturation usually happens
when the investigator cannot discover any new data, themes, or codings. I made myself
acquainted with the data from the interview and match the responses from the
interviewees with the documents collected from organizations.

I chose four participants for the interviews after receiving their consent. During
the interview, I spent 30 minutes with each participant and continued to record the data
they provided until they could no longer provide any new information. When it got to the
point when the data became repetitive, I stopped the interview because the data had been
saturated. After the initial rounds of interviews, I then performed member checking with
the participants. Member checking helped the interviewees clarify and validate the
research analysis or elaborate on the study’s interpretation. Member-checking allowed
interviewees to review and approve the investigator’s interpretation of the data collected
and determine if they were valid from the interviewee’s perspective (Iivari, 2018). The
overall purpose of member-checking is to increase a research’s authenticity and
reliability. I also conducted several meetings with the interviewees to increase the
accuracy of the research. I performed member-checking interviews with participants
twice and ensured that they no longer had new information to offer. This also confirmed
that data saturation was reached.
Population, Sampling, and Participants
The participants were selected based on their level of skill, experience, and age. I
limited the study to participants who were information security managers, who had at
least 5 years of Information security experience, and who were at least 21 years of age.
Information security managers are people whose specialty is in protecting the computer
systems, networks, and databases of organizations from security breaches and
cyberthreats. They also ensure that their teams are monitoring and addressing the
information safety needs of their organizations. The criteria I used for the selection

include (a) successful implementation of strategies used by information security
managers to protect users’ personal data from security threats, (b) information security
managers with the responsibility of securing mobile cloud computing networks, and (c)
information security managers located in Northeastern Massachusetts.
An extensive screening process was conducted to ensure that the right participants
were selected for this research. Conducting a rigorous screening process would ensure
that the participants are fit for a multiple case study (Yin, 2016). I selected the candidates
based on the accomplishments they had achieved in terms of implementing security
strategies for protecting users’ personal data against security threats in MCC
environments. To ensure that the interviewees satisfied all the criteria for this study, I
reached out to the executive leadership of two financial technology organizations within
Northeastern Massachusetts. I elaborated on the purpose and objectives of the study to the
executive leadership to obtain their consent to participate in the study. I also sent the
summary of my proposal through email and explained what the research study is about.
In the email, I asked if they could provide me with the email addresses of managers in
their organization who would be willing to participate in the study. I identified potential
participants from the list of potential participants that the executive team from the
organization provided. Then I sent invitation letters to the potential participants via email
stating the objectives and goals of the study. I also included the consent form. Openended
questions was used to gather data during the interview. I also reviewed organizational
documents from the organizations.

To obtain participants for this research, I contacted the leaders of two financial
technology organizations to grant me permission to interview some of their employees in
the research study. Communicating and establishing contact with research participants
and requesting permission for them to participate in a study is a rigorous and
timeconsuming process (Monahan & Fisher, 2015). Once Walden University’s IRB gave
me approval for data collection, I enlisted participants with security managerial positions.
Then, I emailed each enlisted participant the information for the study and requested their
participation in the study. This communication helped build trust and establish a working
relationship. The organizations were very responsive, transparent, and courteous. During
the interview, I avoided using any identifying information about the participants. I
ensured privacy techniques were observed by encrypting all data, interview materials, and
participants’ email addresses. I avoided all forms of ethical violations during the course
of the research and followed all the necessary research standards to safeguard the
confidentiality of the participants’ confidentiality.
I ensured that the population selected matched the study’s purpose. I selected the
participants from two financial technology companies in Northeastern Massachusetts. I
chose four information security managers from two financial technology organizations
with current knowledge of the security strategies utilized by information security
managers to secure user’s personal information from security threats in MCC networks. I
ensured that the security managers chosen were able to provide valuable information for
this study.

I used the snowball sampling method as a method of sampling for this study. In
this method, a participant chosen by the researcher would help the researcher pick out
other participants from a target population that would be valuable to the research (Ellis,
2021). With snowball sampling, participants can help identify other participants who
would provide valuable information for the research (Perry, et al., 2017). I contacted
information security leaders of two financial technology companies in Northeastern
Massachusetts, who provided me with the contact information of other information
security managers in their respective organizations. Once I identify these participants, I
requested their help to locate other participants with common interests and goals. The
participants included experts and professionals in information security managers who
were tasked with providing and implementing security strategies for protecting users’
personal data from security threats and breaches within the organization. Information
security managers include individuals who provide information security training and
awareness, engage in creating and managing security strategies, and overseeing audits of
information security. They are also in charge of configuring and overseeing physical
security disaster recovery and managing data backups. They are also responsible for the
communication of information security goals with the organization. I used criteria such as
participants’ age, skill, and experience from those who have successfully implemented
security strategies for protecting users’ personal information from security threats. This
research was limited to participants who were information security managers and are at
least 21 years old.

I evaluated potential interviewees and continued to interview participants until I
reached the desired sample size. Okine, Dako-Gyeke, Baiden, and Mort (2020) stated that
using snowball sampling helps and drives interviewees to give the contact information of
other potential interviewees for a study. The more participants we are able to recruit for
the research, the richer the research would be. Sampling size often requires that the
researcher continues to collect and analyze data until the point where no new concepts are
found (Van Rijnsoever, 2017). The snowball sampling method met the objectives of this
research and was appropriate for this study.
With the use of data saturation, I was able to ascertain the sample size. The limit
of a sample is usually dependent on when the study reaches data saturation, which means
a point where no further new information emerges. Aldiabat and Le Navenec (2018)
opined that data saturation occurs when collecting more and more data does not result in
the collection of new data or the point where no new information erupts from the
collection of more data. Data saturation is also useful for validating the study’s outcome.
In qualitative research, specific sample size is usually not needed to produce accurate
results, rather, they vary greatly based on the individual requirements of each study.
Although it is important to know the sample size for your research for planning purposes,
I continued to evaluate it throughout my research period. I compared new information
and observations with previous data to identify differences and similarities.
Researchers who utilize qualitative research method continues to collect and
observe data until they reach data saturation, and no new data is derived from more
investigation (Guha et al., 2021). When an investigator does not receive any other new

information from interviewees, it is said that data saturation has been achieved (Pope &
Mays, 2020). When data saturation occurs, there will be no need for more participants
because data saturation signifies that the researcher has enough information for data
analysis (Zilber & Meyer, 2022). I continued to carry out interview sessions with
interviewees until I reached data saturation. Once data saturation was reached, there was
no need to conduct further interviews and spend hours of observation on data that only
confirmed what I already knew. I also ensured I reached back out to interviewees using
member-checking interviews to ensure that no new information emerged.
Data Collection Activities
Data collection is an important part of every research study. It is a method used by
researchers to collect information relating to concepts, ideas, and phenomena to answer a
research question (Ehrmin & Pierce, 2021). In data collection, various instruments and
methods are utilized for collecting information about the subject of study. The research
question was the foundation for selecting the research method and design. The qualitative
multiple-case method was used for this study. I believe this was the most appropriate
method because this method helped in exploring the strategies used by information
security managers in Northeastern Massachusetts for protecting users’ personal data in
MCC networks. Data was gathered from financial technology industries by examining
documents from organizations and semi-structured face-to-face interviews with
participants. This helped get an in-depth understanding of strategies information security
managers used to protect users’ personal data against security threats in MCC networks.

The data collection technique I used for this qualitative study included face-toface
interviews, organizational document reviews, and publicly available data. The primary
data was collected via interviews, and the secondary data was collected via organizational
documents and publicly available data. Researchers are usually the main data collection
instruments (Clark & Vealé, 2018). As I was the main instrument for data collection, I
ensured I paid close attention to any assumptions that could hinder or influence the
outcome of the research study in any way. Before starting the data collection process, I
sent out emails to potential interviewees at the two financial technology organizations.
Once I received their emails about them volunteering to participate in the research, I sent
out the consent forms to them. The consent form contains an explanation of the study’s
purpose and the option for participants to partake in the research or opt-out. Participants
who participated in the research chose their venue, date, and time for the interviews.
I interviewed the participants via Zoom and ensured the room was quiet and
reserved to prevent distractions and ensure privacy. I assured them of the confidentiality
of the research and the time frame for the interview (which was a 30-minute session). I
also built rapport with the participants to make them comfortable and answer the
questions naturally. I also obtained their permission before taking notes and recording
the interview. There were twelve questions for each participant. I used the recorder as the
primary tool to collect the data so I could be attentive and concentrate on the verbal, and
non-verbal, and physical behaviors of the participants during the study and use notetaking
can as a secondary tool. If the participants provided short answers to any question, I
asked them to elaborate on their responses or share more details on their answers.

In summary, I gave participants a chance to provide recommendations or share
any opinions they have about the research study. Researchers employ face-to-face
interviews so that through the experiences of the subject, they can take a different look at
the work around them (McGrath et al., 2018). By creating meaning from people’s stories,
they would be able to provide better and more accurate results in their study. Katz-
Buonincontro (2022) mentioned that through face-to-face interviews, researchers could
obtain more knowledge from the participant’s points of view and have a better
understanding of their lived experiences. Once each interview was completed, I reviewed
the notes and listened to the recording from the interview. This allowed for easy and
accurate transcription of the data collected and addressed any unclear information.
I also worked with the participants to perform member checking. This process
allowed them to certify, edit, and double-check if the data collected at the interview
session was accurate. Iivari (2018) stated that member checking helps the participants to
review and confirm the outcome of a research. After the member-checking process was
complete, I scheduled an interview to follow up with the participants and share a
summary of the information I got from the interview. I also included any terminologies
that were unclear for them to verify if my interpretation of the data collected was
accurate. Brear (2018) confirmed that researchers reach out to participants during
member checking to clarify, correct, amend, rephrase, or validate findings from the
research. This process helps to make the research study more truthful and reliable.
I utilized the document review protocol to have a clear understanding of the
strategies the fintech organizations use to secure their users’ personal data from security

threats. The primary aim of the document review protocol is to lead the process of how
secondary data is collected. With the document review protocol, I clarified to the
participants the type of documents I needed and that would be of value to the research. I
collected documents such as security policies, educational and training manuals, access
control documents, and documents guiding the use of the internet and electronic mail.
Organizational documents helped me point out key elements and reoccurring themes that
were beneficial to find the strategies that security managers use to protect their users’
personal data from security threats. Sharing corporate documents provided some of these
strategies. Once the documents were collected and member checking had been
completed, I imported the results collected into NVivo software for analysis of the data.
Interview/Survey Questions
Each interview/survey question must contribute knowledge related to the research
question(s). Avoid questions with yes/no answers.
Data Organization and Analysis Techniques
By creating, securing, organizing, and storing data effectively, we make the
process of data manipulation, access, and control, and regulation easier. There are various
methods for organizing research data. Some of them include reflective journals, file
naming, research logs, etc. This process of organization helps for easy tracking and
management of research documents/ data (Gupta et al., 2019). The availability of
research journals allows for knowledge to be readily available and shared/accessed easily.
The reflective journals will contain experiences and events when conducting face-to-face

interviews and obtaining documents for investigation and analysis. Cathro, O’Kane, and
Gilbertson (2017) stated that organizing collected data into research logs, journals,
themes, and labels helps the documents to be easily searchable and accessible. Reflective
journals will include information such as feelings, personal views, opinions, or sentiments
that may impact the study results.
I organized the research documents and labeled them according to the participants
and the organizations I investigated for easy searchability. I encrypted the soft copies of
the obtained documents, semi-structured interview recordings, and member-checking
scripts using NVivo software. Once encrypted, I stored them in a Google Drive account
for safekeeping and easy retrieval. Hard copies, such as organizational documents, were
kept in my private room and locked on a shelf. I categorized and labeled the documents in
a way that would make them easily retrievable. I backed up the documents by encrypting
them and storing them in a pen drive. All documents, including soft and hard copies, will
only be kept for five years, after which they will be destroyed and disposed
of.
Investigators who engage in qualitative studies ask questions that are open-ended
to participants for them to go deeper and explain their experiences, giving the researcher
the opportunity to have a more meaningful study. It is, therefore, crucial that a researcher
pay careful attention when analyzing, collecting, interpreting and organizing data in
research. I used the interview protocol and then performed the data analysis. The process
of data analysis will included (a) obtain and complipe the data, (b) disassemble the data,
(c) reassemble the data, and (d) interprete the data (Yin, 2014). Mattimoe, Hayden,

Murphy, and Ballantine (2021) stated that one could enhance the analyzed data through
one or more analytical procedures. For this study, I used methodical triangulation for my
data analysis. The benefit of methodical triangulation is that by combining multiple
sources of data, one might overcome the weakness obtained from using just one data
source and neutralize any biases to ensure validity and confidence in the results (Yarney
et al., 2021).
For this study, the Methodical triangulation was the most appropriate technique
for data analysis because this method increased the assurance that the study was valid and
enhanced the understanding of the research results. I extracted and obtained the right
explanation applicable to the collected data through carefully reviewing and analyzing the
transcripts from the interview and the organizational documents. Abdalla, Oliveira,
Azevedo and Gonzalez (2018) opined that methodical triangulation refers to utilizing
various sources of data to enhance or increase the collection of data that are valuable and
beneficial to the research. The use of methodical triangulation in multiple case studies
helps to improve the data collection and data analysis process (Jarlby et al., 2018). I
gathered documents such as security policies, educational and training manuals, access
control documents, and electronic mail from the organizations I researched.
The data analysis method involves analyzing various themes found in the data
collected. In analyzing qualitative data, one must be sure of the validity and reliability of
the data and ensure that it provides reasonable explanations for the findings (Yin, 2016).
The data analysis process involves reviewing and analyzing the raw data and extracting
valuable concepts from them. To perform the data analysis successfully, I must have a

comprehension of the collected data. I reviewed the interview scripts and performed
member checking to have a broad understanding of the raw data collected. I also
categorized the collected data during face-to-face interviews using code names and
arranged the documents by subject.
Once the interviews were transcribed, I compared the various responses gathered
during the interviews. I checked for themes and similarities, spotted patterns and ideas,
and grouped them into categories that were easy to understand using the NVivo software.
NVivo 14 is a software for qualitative data analysis that helps to cut down manual tasks
on the side of the researcher and gives them time to extract themes and draw conclusions
from a study (Atkins et al., 2016; Dalkin et al., 2020). Researchers such as Salahudin,
Nurmandi, and Loilatu (2020) utilized NVivo for processing their interview transcripts to
understand policy-making practices, including bribery, lobbying, and corruption in
politics in Indonesia. By organizing and analyzing ideas and concepts, one would identify
relevant themes, ideas, and patterns.
Thematic analysis is used for identifying themes and patterns in a dataset while
describing the phenomenon in a research study. In thematic analysis, one must become
familiar with raw data, generation of codes, theme searching, theme reviewing, definition
and naming of themes, and production of reports (Wheeler & Mcelvaney, 2018).
Thematic analysis was very useful for me in this research because of its multiple benefits.
Thematic analysis is also very suitable for analyzing qualitative data and identifying
themes (Heselton et al., 2022). I reviewed the data collected during the research and

extracted meanings and patterns to become familiar with the dataset. By reviewing
interview transcripts multiple times, I was able to identify patterns and issues that were
repeating.
Coding was done by labeling important words, sentences, and phrases in the
study. I used coding to create similar patterns and themes for data analysis. There are
various methods for inspecting and investigating the data collected in multiple case study
designs in qualitative studies. Yin (2014) stated that the data should be analyzed at
various levels, from general to specific. This includes transcribing the interview recording
into a text format for better data organization of the raw data. This process also includes
searching for information that complements or contradicts the research theme. I organized
relevant codes into themes. The themes had names that buttressed their importance and
meaning. After the initial coding, I carried out the axial coding. Axial coding refers to
linking data, organizing them, breaking them into categories and subcategories, and
assigning codes to various segments of review documents and interviews (Mende, 2022).
Once I received the organizational documents, I performed axial coding on them,
arranged them into categories and sub-categories and searched for similar themes and
patterns.
Furthermore, by analyzing the data from this research, I was able to generate
reports that revealed important themes that were related to the literature review and
conceptual framework. The conceptual framework that grounded this study was the
integrated system theory of information security management developed by Hong et al.
(2003). This approach was useful for organizations interested in increasing their

organizational security posture. The NVivo software was also the primary tool for sorting
out the themes, sub-themes, and patterns in generating the final report.
Study Validity
Reliability and validity are vital requirements in qualitative research. It is crucial
to document data truthfully, as this directly affects how credible the qualitative study will
be (Marshall & Rossman, 2016). In a qualitative study, if the data is documented
truthfully, it would be said that the qualitative study is credible, and vice versa. Spiers,
Morse, Olson, Mayan, and Barrett (2018) stated that reliability means when research
results are easily repeatable, while validity refers to data accuracy. Reliability can also
mean how valid the study’s results can be recreated, and validity determines if the
conclusions of the research are appropriate to the study. Four major areas are concerned
with reliability and validity, (a) dependability, (b) credibility, (c) transferability, and (d)
confirmability (Coleman, 2021; Elo et al., 2014). Reliability and validity were indeed
essential in this qualitative study to confirm that the data was valid, correct, accurate, and
appropriately applied.
Reliability
Reliability in qualitative studies refers to documenting and following detailed
steps in a way that other investigators can replicate and get similar results or come to
similar conclusions (Rose & Johnson, 2020). Reliability is a necessity in qualitative
research, and it expresses the accuracy and correctness of research results without biases.
Reliability shows how the research was conducted and decisions arrived at so that the
reader can perform an audit trail and get an understanding of the researchers’ thoughts

and actions (Coleman, 2021). It helps to prove that the research results are valid and can
be replicated. For a researcher to demonstrate that his/her research is reliable, they must
record the entire process of the research from the beginning of the research to the end. To
demonstrate reliability and credibility in this research, I carefully documented every step
I took in this research and carefully recorded the research findings accurately without
including my personal opinion in the results. An accurate recording of research results is
crucial to determine how credible a study is.
Marshall and Rossman (2016) stated that the steps to have reliable research
includes (a) use a case study protocol, (b) carefully record and correctly transcribe the
research results, (c) document/record the techniques for data analysis, (d) reveal all the
processes and plans utilized in the research. I ensured that the process for collecting data
was reliable by adhering to the interview protocols and using the same interview
questions for all the interviewees. I also utilized other approaches, such as feedback from
participants, methodical triangulation, member checking, etc. By gathering data from
various sources, I was able to accurately answer the research question.
Validity
In qualitative research, validity helps to check and certify that the findings of a
study are truthful and correct (Coleman, 2021). It confirms the truthfulness, correctness,
and how credible research results are. Validity does not directly question if the responses
provided by the participants are credible; instead, it investigates the aspect of determining
if the conclusions made by the researcher are the exact representation of the participants’
ideas (FitzPatrick, 2019). It helps to determine that whatever ideas the participants

convey to the researcher, those ideas should mean the same thing in the summary/results
provided by the researcher. Huttunen and Kakkori (2020) stated that qualitative
researchers use credibility, confirmability, dependability, and transferability to ensure that
a research finding is complete and accurate.
Dependability.
Dependability refers to how stable data is over time. It preserves the realistic
aspect of reliability (Coleman, 2021; Huttunen & Kakkori, 2020). Qualitative researchers
utilize several measures to record activities to ensure that a research study is consistent
and reliable (Rose & Johnson, 2020). Following each criterion in the selection of
participants helps to ensure that the research is dependable. To ensure that my research
study is dependable, I made sure that the transcription of the data collected during the
research was accurately and carefully analyzed. I also ensured that participants have the
opportunity to evaluate the research findings, review my interview
summaries/interpretations, and share their recommendations. I also performed member
checking with interviewees to ensure that the research summary matches the data they
shared and that the results were accurate and dependable.
Credibility.
Credibility refers to the level of trustworthiness and accuracy in the
documentation of research findings correctly (Marshall & Rossman, 2016). Research data
is said to be credible if the results from the research are recorded very carefully and
correctly. To prove/demonstrate credibility, researchers utilize triangulation to confirm
the completeness and integrity of the instruments used for data collection (Huttunen &

Kakkori, 2020). Documenting research results is very vital in every research study. In this
study, I compared and contrasted the responses from the various interviewees and made
note of the areas where the data sources and themes of the research were either similar or
different. I utilized methodical triangulation for collecting supporting documents from the
data gathered via semi-structured interviews and organizational document review. This
would help prove that data was collected from multiple sources, which helped answer the
research question.
Transferability.
Transferability is a crucial part of reliability in qualitative studies. Transferability
involves collecting dependable results that can be transferred to other settings (Marshall
& Rossman, 2016). It preserves the realistic aspect of validity, and it involves the level to
which the findings from study can be easily transferred to another context (Elo et al.,
2014; Huttunen & Kakkori, 2020). I carefully recorded observations from the research,
including assumptions noticed during the study. I explained in detail the methodology
used in the research, such as how I selected my participants, how the data obtained from
the research was interpreted, and how I reported the results/findings. By detailing the
research methodology, other investigators may be able to determine the transferability of
the research results and possibly use the results for future research studies. According to
Patino and Ferreira (2018), accurate documentation of research results could be
transferred to other groups. It is, therefore, important to record results accurately.
Confirmability.

Confirmability refers to how much information an investigator provides so that it
will be easy for other investigators to transfer the research results or findings. It shows
that analyses are supported by data (Rose & Johnson, 2020). It is the degree to which
other researchers and investigators are able to understand and interpret the research
results (Patino & Ferreira, 2018). The results from the research study must therefore
reflect the responses from the participants. I utilized methodical triangulation in
comparing and contrasting the results from the research to confirm the accuracy and
completeness of the research findings.
Transition and Summary
The purpose of this qualitative multiple case study was to explore strategies used
by security managers to secure their mobile cloud computing environment from security
threats. The data collection process would included two parts. A semi-structured
interview and organizational document review. The approach and method I used for this
study were suitable for achieving the purpose of this research because I was able to
interview participants 1-on-1 and review documents from their organizations on the
research topic. In section 3, I expanded on areas such as the overview of the study,
presented the research findings, expanded on application to the professional practice, and
stated the implications for social change. Furthermore, I included recommendations for
actions and suggestions for further research. Lastly, I provided reflections and
conclusions of the study.

Section 4: Application to Professional Practice and Implications for Change
The focus of this qualitative pragmatic inquiry study was to identify strategies
necessary to secure users’ personal data against security threats in MCC networks. The
target population consisted of information security managers from two financial
technology organizations in Northeastern Massachusetts implementing various strategies
to secure their users’ personal data against security threats in their MCC networks. This
section includes (a) presentation of findings, (b) application to professional practice, (c)
implication for social change, (d) recommendation for action, (e) recommendation for
further research, (f) reflections, and (g) summary and study conclusions.
The study was focused on identifying the strategies information security managers
use to secure their users’ personal data against security threats in MCC networks. I
conducted four semi-structured interviews with information security managers from two
financial technology organizations in Northeastern Massachusetts. The participants were
information security managers who were at least 21 years old and had worked in the field
of information security for at least 5 years. I recorded the interviews, transcribed them,
and coded the results. I used NVivo 14 software to identify themes in the collected data.
In addition to the semi-structured interviews, I reviewed publicly available data and
recently published documents for this study. The publicly available data allowed me to
validate the information obtained from participants’ interviews. I conducted the
interviews in a distraction-free room via Zoom, and each interview lasted for 30 minutes.

Presentation of the Findings
For this study, the research question was, “What strategies do information security
managers use to secure their users’ personal data against security threats in MCC
networks?” I recruited 4 participants who are information security managers from two
financial technology institutions to participate in this study. I utilized semi-structured
interviews and reviewed publicly available data for this research study. All participants
consented to participate in the interview before they were interviewed. Each participant
was asked 12 interview questions. Two men and two women participated in the
interviews. Gender did not pose any risks or bias to the interview because the interview
questions were not gender sensitive. I identified the participants using Participants 001,
002, 003, and 004. I identified the organizational documents as documents 00A, 00B,
00C, 00D, and 00E.
At the end of the interviews, I transcribed each interview session with the
participants. Once the transcription was completed, I performed member checking by
asking the participants to verify the transcripts. After member-checking, I imported the
interview transcripts, organizational data, and publicly available documents into NVivo
14 software. NVivo 14 software assisted in identifying emergent themes. Data saturation
occurred after the fourth interview. Reviewing organizational data and publicly available
data helped triangulate and validate the data obtained from the interviews. The themes
include (a) strong authentication and authorization controls, (b) encryption, (c) user
awareness and education, and (d) following the industry standard of information security.
Each theme is summarized below:

Theme 1: Strong Authentication and Authorization Controls
One of the themes that emerged from the interviews and supporting documents
was strong authentication and authorization controls. Strong authentication and
authorization controls include the implementation of long passwords, multifactor
authentication, and proper security policies. Strong authentication and authorization also
help to define who gets access to what information and IT resources. This theme
synchronizes with the internal controls within the IST standards and privacy and security
within the literature review. Configuring strong authentication and authorization controls
in mobile cloud computing is critical because if the mobile cloud is compromised, it
could put an entire organization’s resources at risk (Ahmad et al., 2018; Shamshirband et
al., 2020). The management of strong authentication and authorization controls is a
significant concern identified and addressed by the participants. Authentication is a
process where an individual or entity attempting to access a secured resource is examined
by utilizing the appropriate credentials. Authenticating an individual using a password is
still the most common and preferred information security method for cloud security
(Rajamanickam et al., 2020). Only authorized users are allowed access to certain
resources using the authentication method, and unauthorized users are denied access.
Authentication is therefore implemented when trying to increase the level of security to
resources (Kaur & Mustafa, 2019). One of the most effective ways of choosing a
password is by using phrases or sentences. This way, the passwords are too
complex/difficult to guess or crack. This strategy is in line with current literature and was
also confirmed by participants during the interviews.

While performing my research, I found out that MCC inherited the security
challenges of cloud computing. This was confirmed during my interview with the
participants. Three out of four participants stated that some of the security challenges in
MCC also exist in cloud computing. Some similarities include that when logging into a
cloud service, you must use a strong password, whether logging in from your mobile
device or from a computer, and these passwords must be changed periodically. This is a
crucial step in authentication and authorization because it immediately separates
authorized users from unauthorized users. Using strong passwords on one’s mobile
device acts as the first barrier against data breaches. If a user provides the correct
password, they are authorized to access the asset or resource and immediately denied
access if the password is incorrect. When strong authentication and authorization controls
are enforced, it aims to protect assets from any form of unauthorized security threat.
Verifying users’ identity using strong authentication and authorization controls
aligns well with the components for identifying users in the literature review. Users must
provide certain pieces of information, such as their usernames and passwords, to identify
who they are; however, the use of a weak password could become a passage for hackers
into the organization. Attackers could use various brute-forcing techniques or try
guessing the passwords using dictionary words, house addresses, names, dates of birth, or
maiden names. During my research, I found out that the best passwords are the use of
sentences or phrases, and include numbers, upper case, lower case, and special characters
in the combination. The longer passwords are, the more difficult they are to brute force or
guess. During my interview, three participants indicated that some users find it difficult

to remember passwords, so they prefer to use short and easy-to-remember passwords.
They all agreed that this is a bad idea because as the password is easy for the user to
remember, it will also be easy for an attacker to guess. They also said that some users,
due to the complexity of the passwords they choose, they write them on sticky notes and
place them close to their computers, so they can retrieve them anytime they need them.
They also said this is another bad idea, as anyone who searches through your workspace
can find your sticky note with the password and use that to unlock your computer. Two
participants suggested the use of password management applications like 1-password to
solve this problem. With the use of a password management application, the users do not
need to remember their passwords as the password manager is always available and
periodically changes the passwords. One participant stated that it is okay to forget your
password. He said that once you forget your password, just reset it to another sentence or
phrase. He said it is better to always reset your password than to have it compromised by
an attacker.
Prior literature also supports the use of strong passwords instead of weak
passwords. Hong et al. (2003) suggested that in the integrated system theory of
information security management, it is believed that using proper security measures to
protect systems is crucial for protecting resources against security threats. Strong
passwords are one of such security measures. A strong password must be a sentence or a
phrase and must include an upper case, a lower case, numbers, and special characters.
Passwords must also be changed periodically to nullify shoulder-surfing attacks or
password-learning techniques used to guess passwords.

Current literature also confirms that long passwords with a combination of
numbers, upper case letters, lower case letters, and special characters are effective and
difficult to crack. The use of weak passwords is a threat to an organization’s security, and
users must be educated on password combinations to increase the strength of their
passwords (Guo & Zhang, 2018). One weak password from a user is enough to
compromise an entire organization, so information security leaders must ensure that users
are using the right password combination and password length. If a weak password is
used by a user, it could result in data breaches, and opportunities for attackers to gain
access to organization confidential information (Galdi et al., 2018). This is in line with
my findings from the interview with participants. Information security managers must
also set up security policies to ask users to update their passwords periodically so the
same passwords are not used for too long.
The use of strong authentication and authorization methods was a common theme
among the participants. A strong authentication and authorization theme was also found
in the secondary data collected for this research. Statements from the participants and
data from secondary data confirmed that having strong authentication and authorization
controls strengthens security.
Below are what each participant said about the use of passwords for
authentication and authorization. Participant 001 stated that passwords are effective for
providing access to important resources, and that on a personal user basis, users should
divide their passwords into hierarchies. The first hierarchy is a simple password that can
be used for all news, newsletters, etc. The second hierarchy is a little complex password,

which should be used for subscriptions. The third hierarchy is a more complex password
for services such as Comcast, phone bills, utilities, etc. The fourth and highest hierarchy
should have the most complex passwords for securing email systems such as personal and
work email accounts, financial systems such as bank logins, brokerage and investment
credentials, etc.
Participant 001 also stated that when choosing a password, it should be a phrase
from a book you read, a movie, and so on. The longer the password, the more difficult it
is to hack. When you forget the password, you can always reset it. Participant 001 also
mentioned that organizations should implement tools like 1-password to generate
multiple strong/complex passwords and manage them all in one location. This method
gives the user peace of mind. Participant 002 stated that a user is identified by entering a
username and password, therefore granting access to resources based on their roles.
Therefore, using a unique and long password is necessary.
Participant 003 specified that entering a username and password helps to
determine which user is requesting access to what information so the security team can
tell, through their monitoring activities, any impersonation, impossible logins or
suspicious activities. Meanwhile, participant 004 suggested that strong password
authentication protects sensitive information stored on the mobile devices, which secures
both the user’s personal data and company information on the device. Participant 004 also
stated that one way of managing mobile devices is using mobile device manager (MDM).
This application helps to force users to use strong passwords on their mobile devices even
before accessing any mobile cloud resources.

Participants 001 and 003 stressed on the fact that when setting up your MCC
network, all users should be denied access or restricted at the very start, and then access is
given on a needed basis. So, the first configuration step should be “deny all” for all users.
This way, information security managers can manage the data users have access to and
provide only minimal data that users need to do their jobs. This strategy is also helpful in
case of an impersonation attack, which refers to when an attacker steas the password of
an authorized user and logs into the network as the user.When this occurs, the attacker
would only have access to the minimal data allowed for that user.
Multifactor Authentication (MFA)
MFA is a security strategy that all participants highlighted. Participant 001
expressed that security managers must implement MFA across all users and all accounts.
MFA provides a second layer of security. It refers to the combination of different
authentication methods, such as the use of passwords, pins, and codes for verification
(Al‐Ahmad et al., 2021). Once users log in using their usernames and passwords, they are
prompted to confirm their identity on something else they have, such as a mobile phone,
email or a token. Participant 002 acknowledged that MFA is now an industry standard
that information security managers must implement to secure their organizations’
resources. Participant 003 expressed that MFA provides an additional layer of security
against attacks. If a hacker can guess, crack, or steal the user’s password, they will face
another roadblock once they try to log in. This extra step completely blocks the intruder
from accessing sensitive information or buys time for the monitoring systems to detect
the suspicious activity.

Archival Document Analysis on Multifactor Authentication.
00A stated that MFA provides at least two methods of authentication to access
essential resources instead of just a username and password. This extra layer increases
security and adds multiple roadblocks before accessing a resource. Therefore, MFA helps
prevent anyone with a stolen password from gaining access to sensitive data. 00B and
00C stated that MFA is necessary for securing financial information. It is the standard
best practice for identity and account management.
Other secondary data and publicly available documents also confirm that MFA is
necessary for validating users and providing authorized access to resources and sensitive
information in mobile cloud computing. This was also confirmed by the participants in
the interviews. They stated that one effective way to provide multiple barriers and reduce
data breaches in the cloud is by using MFA.
When using passwords as a form of authentication, a mixture of uppercase,
lowercase, numbers, symbols, or special characters is encouraged. Also, information such
as birthdates, addresses, names, and phone numbers should be avoided when creating
passwords. One technique suggested by Participant 001 is to use phrases from books or
movies. They are easy to remember and can be reset if forgotten.
Strong authentication and authorization control stood out as an important strategy
among the participants, the secondary data, and publicly available data. The use of strong
authentication and authorization aligns properly with the conceptual framework of this
research. Hong et al. (2003) suggested that IST assisted in the identification of gaps in
information security risks. Once security managers are able to implement the proper

authentication and authorization controls, the risk of a data breach will be significantly
reduced.
Various literature has also supported the motion that strong authentication and
authorization controls are necessary to reduce data breaches. Some organizations
continue to educate their employees about the importance of strong authentication
passwords and MFA use, while others have yet to implement MFA in their setup
(AlAhmad et al., 2021). Some others believe that authentication combined with
cryptography is the right approach (Pradhan et al., 2020). MCC requires security
mechanisms that actively monitor activities and detect attempted breaches or suspicious
activities within the mobile cloud. This statement aligns well with the information
provided by Participant 003. She stated that organizations should have a central system
for managing all the mobile devices and their locations in the mobile computing space.
Today, some mobile device users still underestimate the importance and risks of choosing
a password in the MCC network. However, some users still hesitate to choose a strong
and secure password.
During my research, I uncovered that the addition of more security layers makes it
difficult for hackers to breach a system. Therefore, multiple security layers equal better
security (Ismail et al., 2014). This strategy is consistent with prior literature and was
confirmed by all four participants. They all agreed that multifactor authentication is a
security strategy to create additional barriers for attackers. They said that using a strong
password and hardware token such as a keyfob or a code from another device and/or
using a fingerprint or face scan makes it harder for hackers to access IT resources. With
these multiple barriers in place, the chances of attackers gaining access to systems are
significantly reduced.
Data collected from participants during the interview and publicly available data
shows that strong authentication and authorization control are critical, supporting this
study’s conceptual framework. Adding an extra layer of security or barrier is crucial
when accessing digital resources in MCC networks. Anakath, Rajakumar, and Ambika
(2019) stated that MFA serves as a control mechanism for centralized access and
information security in the cloud. MFA also helps to prevent insider and outsider threats
(Shamshirband et al., 2020). Users remain the most vulnerable and weakest link when it
comes to achieving security goals. Most users of MCC networks tend to use short and
easy-to-guess passwords, which are highly easy for cybercriminals to hack. Participants
in the interview suggested that organizations and users should use a password
management tool such as 1-password to generate and efficiently manage strong and
complex passwords.
Table 1
Strong Authentication and Authorization Controls (Frequency)
Source of Data Data Collected From Total Number of References
Participants 4 7
Secondary data 2 6
Theme 2: Encryption
Mobile Cloud Computing (MCC) is a fast-growing technology that allows users to
use their mobile devices to access cloud computing services. As a result, mobile devices
now have access to larger storage, greater bandwidth, and longer battery life, which were

formerly the limitations of mobile devices (He et al., 2018; Somula & Sasikala, 2018).
MCC nests many resources as well as private information, making it a valuable target for
cybercriminals. It is therefore paramount that when using, sharing, or storing users’
sensitive information such as tax documents, financial information, personal health
information, social security numbers, etc., information security managers must encrypt
the data while in use, in transit, and at rest (Suguma & Raja, 2018).
Encryption helps to hide data and prevent it from falling into the hands of bad actors.
Encryption was another common theme among all the participants during the
interview. 100% of the participants and 80% of secondary data sources collected shared
the importance of encryption in MCC networks. Many large organizations have reported
data breaches and sensitive information disclosure due to stolen or lost assets. On this
theme, Participants 001, 002, 003, and 004 stated that data must be encrypted while in
use, encrypted when being shared or transferred, and encrypted while at rest. By
encrypting data in transit, information stolen while sharing data with third-party vendors
will be unreadable to cybercriminals, therefore making encryption highly
recommendable.
In my literature review, I uncovered that the addition of more security layers
makes it difficult for hackers to breach a system. Therefore, multiple security layers equal
better security (Ismail et al., 2014). This strategy was confirmed by all four participants.
In encryption, plaintext is converted to ciphertext, and can only be decrypted to plaintext
using the correct keys. Prior and current literature confirms that encryption keeps
sensitive information from data leakage. Thomchick and San Nicolas-Rocca (2018)

stated that encryption is one of the strategies for preventing hackers from gaining access
to sensitive information. This was also confirmed during my interviews with the
participants.
The participants did not go further into explaining the types of encryption, the
strongest forms of encryption, or which encryption is better than the other; however, they
all agreed that weak encryption is a target for attackers, as weak encryption has
vulnerabilities that could be exploited by cybercriminals. Prior literature explored the
need for encryption and explained that encryption with short key-length keys could be
easily hacked by hackers. Without the use of proper encryption, sensitive data could be
exposed (Dai et al., 2016). There are various forms of encryption to protect data at rest, in
transit, and in use. To be able to decrypt encrypted data, the user must have the correct set
of keys; otherwise, the data will be unusable.
Current literature also confirms that encryptions provide another layer of security
for protecting data from data leakage. It is a mechanism that ensures that intercepted data
by cybercriminals becomes unusable once stolen. It is, therefore, necessary to encrypt
data in transit, including data transferred via mobile devices. All participants agreed that
all confidential information must be encrypted, and this is in line with prior and current
literature. Two participants mentioned that organizations must have the necessary tools to
encrypt sensitive data before transferring them to other users, whether they are
employees, contractors, vendors, etc. They also stated that users must be educated on how
to encrypt data, or else they would not utilize the tools and only realize the data was not

encrypted after sending the data. The strategy of encryption concurs with the suggestions
of the participants and what was found in the secondary data and literature review.
Archival Document Analysis on Encryption
Organizational document 00B mentioned that multiple organizations experience
data breaches as a result of stolen or lost assets. Encryption is when data is converted into
unreadable text to prevent unauthorized access. Therefore, Information security managers
use encryption to mitigate the risk of disclosing sensitive information in case the asset is
lost or stolen. The document also showed that information security leaders encrypt the
data with customers’ and vendors’ information while it is in transit (for example, with the
use of VPNs). If the data in transit is encrypted, in the event of an eavesdropping attack
while in transit, the cybercriminal will be unable to use the data because it is encrypted.
While the data is at rest in the cloud servers, it is also encrypted using various encryption
techniques. Document 00C also uncovers that financial information of any kind, customer
information, and any sensitive information must be encrypted whether in use, in
transit, or at rest.
Participant 003 stated that encryption is divided into three parts. Data should be
encrypted when it is stored somewhere, when it is going from one place to another (from
a source to a destination), and when in use. Participant 003 also implied that three
techniques should be considered and documented when setting up MCC networks; the
first is prevention. Ensure that the data given to users is as minimal as possible. Only
provide whatever information is needed by users. This helps to prevent data loss, data
leaks, etc. The second is to protect data in use through encryption. Tools like VPNs,

ZScalers private access, Zscaler internet access, etc., should be implemented to encrypt
the data in transit. Third is recovery or remediation in case of a data loss or breach. Once
a data loss or breach occurs, one has to make sure they minimize the damage as much as
possible.
Participants 001, 002, and 004 highlighted the importance of implementing both
MFA and encryption. They stated that when encryption occurs, a decryption key is shared
with the recipient. MFA is, therefore, necessary for the added security for the
management of the decryption key as it is transferred from one server to another.
Participant 003 stressed that data at rest must be encrypted. It should utilize the cloud and
third-party full-volume encryption of data stored in the cloud to protect it from
cybercriminals.
Participant 003 also highlighted that data in transit in MCC networks could be
transferred via unsecured or public networks, so it must be encrypted. Information
security managers must set up TLS (Transport Layer Security) and IP SEC (Internet
Protocol Security) tunnels where traffic can flow safely from one cloud server to another.
Participant 003 mentioned that tools like VPNs, ZScalers private access, Zscaler internet
access, etc., can be used to provide SSL (Secure Socket Layer) encryption while the data
is in transit. These tools help protect the data so that when a data leak occurs,
unauthorized users cannot read or use the leaked data.
The data in organizational and publicly available documents proves that
Information security leaders confirm that encryption is a necessity because it is a tested
and trusted form of securing data in use, in transit, and at rest. Participants 001, 002, 003,

and 004 agreed that encryption protects files and sensitive information while sharing
them with users/vendors and mitigates the risk of data loss or leakage.
Mobile cloud computing (MCC) is a fast-growing technology that many
organizations have implemented. However, many organizations are still reluctant to
implement MCC on their networks due to its numerous security challenges. Some
organizations believe that MCC is more likely to be attacked than traditional cloud
computing (He et al., 2018). Therefore, it is paramount that data in use, in transit, and in
the cloud servers be encrypted so sensitive information will not be disclosed when there
is an accidental or intentional data breach. Mobile cloud users should also be encouraged
to encrypt data before uploading them onto cloud servers. Other publicly available data
also confirms that encryption helps prevent data disclosure in the event that a data leak or
loss occurs (Thomchick & San Nicolas-Rocca, 2018). So, if information security leaders
and users properly encrypt their data, they will reduce the rate of data breaches. Zhou et
al. (2019) stated that encryption is a mechanism that helps sensitive information remain
secure while in transit or being stored on any media that unauthorized users can access.
Therefore, encryption is one of the confirmed and proven strategies for securing data in
MCC networks.
Data privacy in MCC networks is also a challenge for information security leaders
and stakeholders who utilize cloud computing (David & Dhillon, 2019). Data transmitted
over the cloud must be encrypted and decrypted seamlessly to achieve data security and
privacy. This was confirmed by the participants. There are several encryption techniques
available today that information security managers can employ to secure their data (Kaur

& Kaur, 2018). Information security managers must, therefore, choose an encryption
technique that works for their organization based on how they are set up. Data security is
one of the most important factors in MCC networks because organizations (especially
financial institutions) cannot safely and securely transfer their confidential information
within the cloud without proper data encryption.
I uncovered during my research that Encryption is crucial in the sharing and
storing of data in MCC networks. Encryption prevents against confidential data leakage
(Zhou et al., 2019). While data is in transit or being stored, it is necessary to have such
data encrypted so that if it falls into the hands of bad actors, they will be unable to
decrypt and use the leaked data. Data at rest and data in use must also be encrypted.
Although the participants did not go into the specificity of what encryption technique is
better, all agreed that encryption is necessary in today’s world for sharing, using, and
storing data. Encrypting data means that the data is converted from plain text to
cyphertext. The encrypted data can only be decrypted by an authorized party using the
right key.
Encryption was not only common among participants, but it also aligned well with
IST in the area of auditing and control. For effective auditing and control of which users
have access to what resources, Hong et al. (2003) suggested that organizations must set
up information security controls correctly to actively manage which users have access to
what resources within the organization. Encryption is, therefore, in alignment with
information security management. Ismail et al. (2014) mentioned that security policies
must be handled with great importance for compliance with security practices to be
enforced within the organization. IST provides the platform for the research framework
of information security and lays out the importance of combining various security
components within the organization to ensure that information is correctly secured and
classified. Encryption can, therefore, be used to protect users’ and organizations’
confidential information. The findings from the participants, organizational documents,
and publicly available data confirm that it is a strategy for defending against data leakage.
Table 2
Encryption (Frequency)
Source of Data Data Collected From Total Number of References
Participants 4 4
Secondary data 2 19
Theme 3: User Awareness and Education
The third major theme that emerged from the interviews and analysis of secondary
data and publicly available data is User Awareness and Education. Breitinger, Tully‐
Doyle, and Hassenfeldt (2020) stated that user awareness and education are the first line
of defense and one of the most critical subjects in information security. All participants
(100%) and all secondary documents pointed to the lack of training and user education as
one of the biggest threats to information security. Humans are the weakest link in
information security, so information security leaders must adequately educate them with
the latest and up-to-date information about security issues and how to protect their
sensitive information and that of their organizations. This information is in line with what
I found during my research in the literature review and was also confirmed by 100% of
the participants. Employees are the weakest link in information security, and they

cause half of the security breaches that occur in organizations (Chin & Chua, 2021). This
is also in line with the conceptual framework for this study. The IST of information
technology strongly supports that users get the proper training they need and adhere to the
information security policies created by the organizations.
The findings from my interviews and organizational documents showed that
information security leaders must provide consistent training for constantly building the
security knowledge of users and showing them the critical role they play in securing the
confidential information of both themselves and their organizations. By not equipping
users with the proper awareness and education, organizations can be exposed to various
security risks, which will pose a massive threat to the organization’s revenue and
reputation. Chaudhary, Gkioulos, and Katsikas (2023) stated that user awareness and
training are critical countermeasures for fighting against data breaches. Organizations
should educate their employees on the latest cyber threats and technologies and keep
them updated on the organizational policies and security etiquette of their jobs. Increasing
employee user awareness and training levels will also secure, promote, and develop a
sense of security regarding information security management, which is consistent with
the Integrated System of Technology of information management systems.
Employees must be educated on the potential cyber risks they may come across,
their responsibilities as employees, and the organizational policies and procedures they
must follow to keep the organizations’ confidential data safe (Chaudhary et al., 2023).
Empowering employees with such information will enable them to make informed
security decisions and act to protect the organization’s data. The strategy of user

awareness and education will, therefore, lessen human errors leading to security breaches,
negligences, and vulnerabilities caused by other human factors, thereby improving the
overall cybersecurity posture of organizations.
Effective User education and training would also eliminate threats posed by
insiders and external users. Insider threat may occur when an employee or contractor
intentionally or unintentionally ignores the organization’s security policies and performs
actions that could harm the organization’s information systems. External threats are
caused by viruses, trojan horses, worms, etc., or other attacks such as DDoS,
eavesdropping, ransomware, phishing, etc. Both internal and external threats were
subjects that came up during the interview with all participants. Three participants stated
that social engineering attacks are frequent with financial technology organizations, and
proper education and user awareness would help prevent users from falling victim to such
attacks. Organizational documents highlighted the risks posed by internal and external
threats and how users can overcome such threats.
A comprehensive User Education and Awareness program would address issues
such as abusing privileged accounts, login durations, inappropriate sharing of passwords,
access to critical information, how to report suspicious behaviors and activities, etc.
These findings align correctly with the security strategies in the literature review. Since
internal users already know the location of specific critical resources such as databases,
they must be trained on when and how to access such data and how to log into such
resources safely. If not properly trained, they would pose a severe threat to the
organization. All participants echoed that there should always be an auditing system to

track who accesses what resource and when. That way, everyone can be held accountable
if anything goes wrong. All four participants agreed that mobile devices can be used to
introduce viruses and worms into the corporate network if users are not appropriately
educated on the safe use of mobile devices. Users must be trained on how to use public
WiFi on their corporate mobile devices. If they are not cautious when using public WiFi,
an attacker may eavesdrop on the traffic they are sending or receiving, leading to
information disclosure or worse outcomes.
During my research, I discovered that information security managers use specific
security policies and controls to secure their organizations by properly defining the roles
of computer users, their access to resources, preventing and detecting fraud, and
contingency management in case of a breach. While interviewing the participants, two of
four participants stated that the use of security policies and control plays a vital role in the
MCC network. They stated that without the proper access control, mobile users could
access resources they were not supposed to, which could lead to information disclosure,
but more importantly, if they were hacked, the hacker could use their profile to access
more sensitive information and more access to other resources enabling them to cause
more damage. So proper security policies must be set up correctly, and users must be
educated on how to request access if they need access to certain resources and not try to
bypass the security configurations put in place.
The proper management of risk is crucial in information security. The risk
management theory of IST suggests that information security managers must perform a
risk assessment on organizations to determine the information security threats and

vulnerabilities of the organization. Once these risk assessments are performed, they must
use this information to create a training program for employees to expose the areas for
potential attacks and how to overcome them. This theory by Hong et al. (2003) reduces
risk to an acceptable level by using a comprehensive risk assessment and implementing
controls. Risk acceptability levels vary from organization to organization, which is a
major factor when making organizational decisions (Zhang et al., 2019). Participant 001
confirmed this during our interview. He stated that information security leaders must
perform proper due diligence on their vendors. They must categorize their vendors into
low-risk vendors, medium-risk, and high-risk vendors in case any of them get hacked. He
said they have to determine what business processes, what level of access, and what type
of information the vendors have access to in case they get hacked. For example, payroll
systems, finance systems, etc. are high-risk vendors. So, they have to categorize the
vendors down to low, medium, and high risks. Then, based on these categories, they
would determine what the impacts on the business, data, customers, employees, and
finances will be, and then educate their users on what type of information to share with
these vendors.
Below are what each participant had to say about User Education and Awareness.
Participant 001 stated that educating employees and users against phishing attacks and
how to avoid falling victim to them is an effective security strategy. Information security
managers should also train employees to report suspicious activity once they notice it.
Participant 001 continued that users and employees should be educated on all the possible
ways they could be compromised, whether via the network or the data. Participant 001 said,

“The bad actors only need to get it right once.” Cybercriminals only need to gain access to
an organization once, and from there, they can cause massive damage to an organization
that could cost them a heavy ransom and their reputation or worse.
Participant 002 stated that a lack of user awareness and training makes them
perform some actions that might lead to data leakage or loss. For example, an employee
might not know the company policies around working with company data. They may
want to work from home, but they cannot access the file they need to work with. So they
end up emailing the file to their personal email account, but in the process, they mistype
the email and send it to someone else instead of themselves. Another example is that they
do not necessarily take the correct precautions when working with company files. They
may want to send a file to John Smith but end up sending it to Jim Smith. Therefore, we
must educate employees to take the necessary precautions when transferring files.
Participant 002 continued that information security leaders must ensure that their
employees have access to their network and the data they need to work with and must be
properly trained to recognize phishing attempts. They must also be trained on the tools to
report suspicious activities or emails when they see one. Information security managers
must also make sure that employees have the appropriate access to the tools and resources
they need to do their job. Information security managers must ensure that users cannot
escalate their access without permission and have appropriate access controls in place.
They must also ensure that users do not have access to more resources than they need to
because if they get compromised in any way, whether from phishing attacks or if their

laptop gets infected, they have to ensure that the attacker only has access to as minimal
data as possible.
Participant 002 continued that when building a network or a security program, the
first thing information security leaders should do is educate the people about security
risks and make sure that they have the tools and techniques to report anything suspicious.
They should know how to detect it and how to report it. Users would know if their
computers are behaving in an unusual manner. They are going to notice strange emails if
they get infected, said Participant 002. All the tools that organizations use, such as
antivirus software, Malwarebytes, etc., usually miss something. Also, these tools typically
identify known viruses and worms, but users can tell if they are seeing strange activities
like their computers getting unlocked without them entering their passwords, they start
seeing new emails and files they do not recognize on their computers. This is a sign that
their computers may have been compromised, and they must report it immediately.
Information security managers should make sure employees have VPN, antivirus, the
correct authentication, and encryption in place, as these are industry standards. However,
they should be focused on securing their people at all times.
Participant 002 concluded that information security leaders should not put too
many controls and securities in place designed to get their users into trouble. They should
make things easy so that employees can do their jobs and the security team can protect
them effectively. One should not make their systems too invasive and too controlling, to
the extent that users would have to jump through 50 hoops and automatically violate
policy just to get their jobs done.

Participant 003 stated that “human beings are the weakest link in any
environment, and that is a rule of thumb in security.” We consider humans the weakest
link, meaning they need the most protection. So sometimes, we need to train people
multiple times and schedule mandatory training annually so people can stay alert. So
multiple trainings could be a strategy to reduce being hacked. Participant 003 continued
that users must be able to identify real threats. If users cannot identify a real threat when
one comes in, then that is a problematic strategy that needs to be fixed. Organizations
should conduct more training and education to identify threats. Also, the escalation
matrix should always be updated, so if someone sees a threat, they should know exactly
where to go and who they should reach out to. If they cannot reach out to the security
folks, they should be able to contact the CISO directly. He/she should be easily
accessible.
Participant 004 implied that user awareness and training are crucial because you
can spend all the money in the world to put various security controls in place, but if your
users do something that they are not supposed to, such as clicking on a phishing link, they
could break all the security controls you put in place. Also, because users have their
mobile devices on them all the time, they have a higher tendency to be targeted, hence the
reason for more training when it comes to MCC users. An example would be an
employee working from their mobile phone in a coffee shop. If they are not being careful
of their environment, someone can easily piggyback on them and breach information
confidentiality.

Participant 004 highlighted that the information security team of organizations
should send fake emails periodically using a phishing program to see how many users
will fail the test and click on the phishing links. User training is critical because it trains
the users in identifying phishing emails. It helps them look carefully at the sender’s email
address to see if it is the correct email/domain or a legitimate source. Also, user
awareness and training educate users on hovering their mice over a link to see if it is a
valid URL or if it redirects to some other websites. The user has to press and hold the link
for mobile devices to see the URL. That way, the users can determine if a link on their
mobile devices is legitimate or phishing.
Archival Document Analysis on User Awareness and Education
00A explained that creating awareness and educating users of MCC networks is
critical. Information security leaders must educate MCC developers and engineers to use
the security development life cycle when building systems and applications. Security in
applications and programs must be built from the ground up. The developers and
engineers must always consider information security when building
applications/programs. Document 00D stated that Information security leaders must set
up workshops and seminars for their developers and engineers to train them on how to
always put security first when developing applications. Once these trainings are
completed, they should be tested for understanding.
Data extracted from secondary documents and publicly available data proves that
user awareness and education are crucial strategies in information security from breaches
because they educate and reveal the risks, threats, and prevention mechanisms when

dealing with information in MCC networks. The interviews with the participants also
confirm this strategy to secure personal data from security threats. All participants
highlighted that user awareness and education help to prevent and reduce the possibility
of a security breach.
User awareness and education are related to the IST of information technology
and this study’s literature review. User awareness and education mean training
information security leaders with clear and thoroughly detailed security policies. This
training must also include setting clear expectations, setting up workplace user behavior
guidelines, and defining employee responsibilities (Hong et al., 2003). IST focuses on the
importance of effective security guidelines and policies because users must be trained and
educated on their organization’s security policies to increase their security posture and
minimize breaches. Alruwaili (2019) stated that information security awareness and
training are crucial parts of any information security program, both for individuals and
organizations. Training users and employees with the correct security information
empowers them to stop security breaches from occurring.
The issue of privacy also erupted during the interview with participants. During
my research, I found out that Privacy is a major area of concern when discussing Moblie
Cloud Computing (MCC). Privacy includes everything that has to do with managing
stored data, shared data, disclosed data in the cloud, and access to such data (Gai et al.,
2021). One concern is the transmission of unencrypted large amounts of data via mobile
devices. This can be easily hacked using techniques such as spoofing, jamming, or
monitoring. As a result of this hurdle, organizations are refraining from using MCC for

general-purpose applications. During the interview, participants noted that users share a
lot of unencrypted information with their peers via their mobile devices. They can take
photos of their driver’s license, for example, and distribute them to their friends via
public Wi-Fi or upload them onto social media platforms. This could result in the
disclosure of their personal information. On the organizational side, organizations install
Mobile Device Manager (MDM) on their employees’ personal mobile devices. This
prevents the user from copying any files from the organization’s system, such as emails
or other information, into their personal mobile devices. When MDM is installed on a
mobile device, it acts like a container and separates the organization’s data from the
user’s personal data on the same mobile device. Another advantage of the MDM is that if
the device gets stolen or lost, the organization can wipe all the organization’s data from
the device remotely. Once an employee leaves an organization, the organization also does
the same thing, deleting every company information on the mobile device without
deleting the individual’s data.
The integrated system theory of information security management, which is the
conceptual framework of this study, highlights the importance of User education and
Awareness but does not cover, in detail, the specific types of training users need. With
proper user education and training, users would be aware of certain changes to security
controls or download certain applications that would trigger various security alarms,
hence setting the right boundaries for them. The findings from this study support the IST
of information management and its security strategies as security policies, controls,
education, and awareness all tie together to provide a secure information security fortress
for information security leaders and their users. It is, therefore, critical that information
security leaders provide a comprehensive training and awareness program for users and
perform the training regularly to help users stay active and avoid falling victim to security
threats.
Table 3
User Awareness and Education (Frequency)
Source of Data Data Collected From Total Number of References
Participants 4 21
Secondary data 4 8
Theme 4: Following the Industry Information Security Standards
The fourth theme deduced from my data analysis was the importance of following
the industry information security standards. By accurately following the industry
information security standards and regulations, organizations could mitigate or minimize
the risk of being hacked. This is because various experts in the industry come together
periodically, perform detailed analyses of the security issues in the information security
industry, and propose best practices for organizations to follow to minimize their risk of
being compromised. All four Participants agreed that organizations can have a better
security posture by accurately following the regulations and standards set by the industry
experts. Two organizational documents also addressed this theme.
Participant 001 stated that some security managers do not put the proper
safeguards or safety measures in place when setting up or configuring their network or
devices for the first time. He said that by using the default settings that came with a
device, for example, an organization might be setting itself up to be hacked. This is

because some of these hackers study these default settings online and understand how the
default settings work. Then, they try out these default configurations on the
organizations’ devices and try to exploit them. If they are not set up correctly or were set
up using the default settings, the attacker may succeed in gaining access to that device.
Participants 001 and 003 confirmed that the industry standard when setting up a network
is to always deny all access to all users by default. Then, only allow access for individual
users or services as needed.
Two participants also stated that another technique is to only allow temporary
access to certain critical resources, so no one person has unlimited access to all resources.
For specific resources like critical databases, organizations should only give temporal
access to users. So, every time they need access to the database, for example, they would
have to request temporal access, which would go through an approval process. Once the
task is completed, the access should be restricted. By using this technique, when an
attacker gains access to a network, they are unable to have direct access to the database.
This step provides another barrier that would hinder attackers from gaining access to
critical information.
Participant 002 stated that when setting up the security systems and networks
within organizations, information security leaders must adhere to the best practices of
what the experts in the information security industry has published. He stated that there
are a lot of guidance and regulations from security bodies such as the National Institute of
Standards and Technology (NIST), the Health Insurance Portability and Accountability

Act (HIPAA), the National Cybersecurity Alliance (NCA), the Cybersecurity and
Infrastructure Security Agency (CISA), etc. So, as an information security leader, he
stated that he constantly reads and reviews what the industry has proposed and what has
worked and applies them effectively.
Participants 003 and 004 stated that there are industry standards to follow when
setting up mobile devices for work use. They said that when setting up mobile devices
such as mobile phones for work purposes, information security managers must implement
containers in these devices, which helps separate the company’s data from the user’s
personal data on the mobile phone. They stated that the reasoning behind this is that in a
situation where the mobile phone gets lost or stolen, the organization can remotely wipe
all the data in the container containing the organizational data. Abu Othman et al. (2021)
stated that by performing appropriate assessments and controlling the security perimeter,
information security leaders may be able to prevent misconfigurations in mobile devices
that could affect the organizations’ security.
Another industry standard includes constantly installing patches and updates
regularly on mobile devices. By staying consistent with installing the latest updates and
patches in mobile devices, organizations may be able to prevent hackers from utilizing
old bugs to gain access to organizations’ networks. Participants 001 and 004 mentioned
that organizations can always stay ahead by constantly updating their applications and
installing the latest patches, as this would minimize the possibility of being hacked. Two
organizational documents echoed the dangers of not updating applications and installing
the latest patches.

Another industry standard that the participants highlighted was setting up
effective and efficient monitoring alerts. Setting up effective and efficient monitoring
alerts would enable information security managers to be alerted when suspicious
activities or abnormal behaviors from users are noticed. This is of enormous importance
to organizations. Participant 002 stated that antivirus, VPNs, Malwarebytes, and all other
technologies organizations use must be configured effectively to remove noise and only
send essential alerts. This would prevent information security managers from missing
important alerts when they are sent out. If the alerts are not set up correctly, one would
receive too many noises and hence ignore all the alerts altogether, making them miss the
critical alerts. Participant 003 stated that Service Level Agreements are usually set by
organizations, which are then used to create these alerts. Once the threshold goes below
certain marks, an alert or alerts are automatically sent out to inform the information
security leader on which application or service needs attention. The participants
mentioned tools like Security Information and Event Management (SIEM), Rapid 7,
Sentinel, etc., are well-known monitoring tools for setting up and monitoring alerts within
organizations.
Taking regular backups was also discussed as an industry standard. All
Participants mentioned that backups are helpful if data gets lost or stolen; they can be
quickly recovered. They also stated that backups are crucial if organizations get attacked
by ransomware and the hackers ask for hefty ransomware. If the organization has its
backups up to date, they can just restore their files from their latest backups and avoid
that heavy payment. Taking regular backups is an industry standard that all organizations

should follow. Incase there is a data loss, one can always restore the data from a backup.
Yi & Wen (2023) stated that to prevent the loss of sensitive information, organizations
must perform regular backups.
Prior literature demonstrated that poor configuration, use of outdated applications,
and poor alerting systems could lead to information loss or compromise. Cybercriminals
develop trojans, viruses, and malware every day, making it difficult to eradicate all
threats in the MCC environment completely (Lee & Kwak, 2016). Some cybercriminals
are ahead of information security leaders and have various methods of disguise for
compromising networks. For example, cybercriminals could hide malware in legitimate
applications and convince users to download and install the applications. Once the users
install the applications, the malware will infect the mobile device and provide access to
the cybercriminal (Kim et al., 2015). This is a challenge for information security leaders.
Current literature argues that mobile devices have become a critical target for
cyber criminals (Abu Othman et al., 2021). The majority of attacks are launched on
information systems for financial benefits. The evolution of mobile devices and mobile
cloud computing has created more opportunities for cybercriminals to exploit and create
new sophisticated attacks daily. Malware is one of the most fearful security threats
because it can be disguised and programmed to avoid detection (Gandotra et al., 2017).
Such attacks are used to target mobile devices. Two participants mentioned that bugs
from outdated applications and misconfigurations could be a gateway for such malware to
gain access to the network through such loopholes. Therefore, organizations must stay on
top of installing regular updates and patches for all their computers and mobile devices.

Archival Document Analysis on Following the Industry Standards for Information
Security.
00B stated that adhering to the industry standards for information security is
necessary. It stated that the organization monitors the network, mobile devices, emails,
etc., constantly for suspicious activities. The document also encouraged users always to
install updates once they get alerted by the information security team of new updates or
patches. For the use of security applications such as VPNs, antiviruses, Malwarebytes,
etc., such applications had non-negotiable clauses to be on at all times. 00B stated that
users must not turn off these security applications at any time and ask for help by
submitting a ticket to their information security team if they need to perform any action
that required these apps to be turned off. 00E indicated that users must constantly back
up organizational projects using remote locations created by the organization. This helps
them to ensure the stored data is encrypted and also gives them control over where
information related to the organization is stored.
Information collected during my interviews with the participants and review of
documents 00B and 00E is consistent with my findings regarding following the industry
standards for information security. Malware, viruses, and trojans are used by cyber
criminals to attack organizations constantly (Makridis & Dean, 2018); hence, information
security managers must follow the industry standards for monitoring, tracking,
preventing, and remediating malware, viruses, and trojans by security infrastructures. The
document highlighted the use of antivirus, IDS, firewalls, and VPNs to fight off threats
and secure the network.

The integrated system theory of information security management is in line with
this theme because it provides vital information for installing updates and patches,
security networks with the use of VPNs, firewalls, antiviruses, etc., and backing up
organizational data. This theme is in agreement with the framework of this study. The
findings support that participants would follow the industry standards to secure their
network if they had clear directions from their information security managers. This
positively impacts the attitude of information security leaders because once they publish
these policies and standards, organizations adhere to them and utilize them to safeguard
their users and critical data (Hong et al., 2003). By carefully implementing strategies and
policies published by information security bodies, organizations may experience reduced
information security breaches, which is consistent with my findings from participants.
This validates the use of constantly updating and patching applications, utilizing VPNs,
firewalls, and antivirus, and taking regular backups. Organizational documents also
stressed the importance of adhering to these measures.
In summary, organizations face several challenges from cybercriminals constantly
seeking ways to penetrate the organizations’ networks. By using the industry standards
for information security as a foundation and building on top of what has been proposed
by industry experts, organizations could stand a better chance of minimizing the
possibilities and risks of data loss and disclosure. Such measures, such as active
monitoring of the organizations’ network and mobile devices, frequent installation of
updates and patches, active use of VPNs, firewalls, antivirus, taking regular backups, etc.,
could minimize and mitigate the loss of critical information to cyber attackers which
could lead to the increase in adoption of MCC by organizations and more prosperity for
the information technology industry.
Table 4
Accurately Following the Industry Standards for Information Security (Frequency)
Source of Data Data Collected From Total Number of References
Participants 4 18
Secondary data 5 10
How the Framework Applied to My Study
The concept that grounded this study was the integrated system theory (IST) of
information security management. Hong et al. (2003) developed this theory to understand
the challenges and strategies facing information security management. It serves as a
guiding tool for information security decision-makers to have a complete and all-round
understanding of information security. The themes that evolved from the interview
sessions and secondary data showed that the Integrated system theory of information
security management framework applied well to my study. The IST of the information
security management framework combines information policies, risk management, audit
control, management, contingency theories, and mitigation strategies (Hong et al., 2003).
The first theme uncovered during my research was Strong Authentication and
Authorization Controls. This theme synchronized well with the internal controls within
the IST privacy and security standards. Configuring strong authentication and
authorization controls in Mobile Cloud Computing is critical because if the mobile cloud
is compromised, it could put an entire organization’s resources at risk (Ahmad et al.,
2018; Shamshirband et al., 2020). Verifying users’ identity using strong authentication

and authorization controls aligns well with the components for identifying users in the
IST framework. Information security policy theory in IST emphasizes employees’ roles
and responsibilities to secure the organization’s information assets and resources (Karim
et al., 2021), and one way to do this is through strong authentication and authorization
controls. The use of strong authentication and authorization aligns properly with the
conceptual framework of this research. Hong et al. (2003) suggested that IST assisted in
the identification of gaps in information security risks. Data collected from participants
during the interview and publicly available data shows that strong authentication and
authorization control are critical, supporting this study’s conceptual framework. Adding
an extra layer of security is beneficial when accessing digital resources in MCC networks.
The second theme uncovered during my research was Encryption. Encryption
helps to hide data and make it unreadable in case it falls into the hands of unauthorized
users. In my literature review, I uncovered that adding more security layers makes it
difficult for hackers to breach a system. Therefore, multiple security layers equal better
security (Ismail et al., 2014). Encryptions provide another layer of security for protecting
data from data leakage. It is a mechanism that ensures that intercepted data by
cybercriminals becomes unusable once stolen. It is, therefore, necessary to encrypt data in
transit, including data transferred via mobile devices. Organizations must have the right
tools to encrypt data and educate their users on how to encrypt data, else Encryption
would have no impact to the organization.
Thomchick and San Nicolas-Rocca (2018) confirmed that encryption helps
prevent data disclosure in the event that a data leak or loss occurs. This mechanism

aligned well with IST of information system in the area of auditing and control. For
effective auditing and control of which users have access to what resources, Hong et al.
(2003) suggested that organizations must set up information security controls correctly to
actively manage which users have access to what resources within the organization.
Encryption is, therefore, in alignment with the IST of information system because it
supports the activities for measuring the prevention, detection, and correction of unusual
security events (Casola et al., 2019). IST provides the platform for the research
framework of information security and lays out the importance of securing information
within the organization.
The third theme uncovered during my research was User Awareness and
Education. This theme applied well to the conceptual framework of this study. Employees
are the weakest link in information security, and they cause half of the security breaches
that occur in organizations (Chin & Chua, 2021). This is also in line with the conceptual
framework for this study. The IST of information technology strongly supports that users
get the proper training they need and adhere to the information security policies created
by the organizations. The Management system theory of IST suggests that organizations
should have a well-documented information security management system (ISMS) for
protecting the organization’s information assets.
By not equipping users with the proper awareness and education, organizations could be
exposed to various security risks, which would pose a massive threat to the organization’s
revenue and reputation. Chaudhary, Gkioulos, and Katsikas (2023) stated that user
awareness and training are critical countermeasures for fighting against data breaches,

which is the primary goal of the IST. Hong et al. (2003) suggested that proper
documentation of policies, scopes, security control objectives, and applications would
help mitigate security breaches, and educating users is a significant factor in ensuring
information safety.
Without the proper access control, mobile users could access resources they were
not supposed to, which could lead to information disclosure and access to sensitive
information, which could cause damage to the organization. The risk management theory
of IST suggests that information security managers must perform a risk assessment on
organizations to determine the organization’s information security threats and
vulnerabilities. These risk assessments would then create a training program for
employees to expose the areas for potential attacks and how to overcome them. This
theory by Hong et al. (2003) aligns with this theme because it reduces risk to an
acceptable level by using a comprehensive risk assessment and implementing controls.
Zhang, Paraskevas, and Altinay (2019) mentioned that risk acceptability levels vary from
organization to organization, which is a major factor when making organizational
decisions. Therefore, this theme aligns well with the risk management theory of the IST
of information systems.
The fourth theme uncovered during my research was following the Industry
Information Security Standards. This theme aligns appropriately with the Information
security policy theory of IST because organizations implement policies that enable them
to manage users’ mobile devices. For example, if a mobile phone gets lost or stolen, the
organization can remotely wipe all the data in the container containing the organizational

data. Abu Othman et al. (2021) stated that by performing appropriate assessments and
controlling the security perimeter, information security leaders may be able to prevent
misconfigurations in mobile devices that could affect the organizations’ security. Karim,
Kaur, and Khalib (2021) mentioned that the Information security policy theory
emphasizes employees’ roles and responsibilities to secure the organization’s information
and technological resources. Therefore, organizations must have a well-designed
information security policy to help secure the organization and its resources.
The integrated system theory of information security management is in line with
this theme because it provides vital information for installing updates and patches,
security networks using VPNs, firewalls, antiviruses, etc., and backing up organizational
data. This theme is in agreement with the framework of this study because, based on the
Contingency theory of IST, Carbaugh, Antonio, Lynch, and Nelsen (2019) stated that
organizations must have documented plans and actions they should take should a disaster
or disruption of service occur. Taking regular backups aligns with the contingency theory
because if data is lost, organizations can restore that data from their last backup. Once
such policies and standards are published within the organization, users would adhere to
them and utilize them to safeguard their assets and critical data (Hong et al., 2003). This
theme, therefore, aligns well with the conceptual framework of this study.
Information Technology Contributions and Recommendations
for Professional Practice
The challenges for the security of users’ personal data against security threats in
MCC networks continue to increase over the years. As a result, information security

leaders are continuously seeking better security strategies to secure their systems from
hackers and cybercriminals. The findings from this study may help information security
leaders with various security strategies for securing their users’ personal data against data
breaches in the MCC networks. Information security managers are continuously
searching for the best security strategies to keep the confidential data of their users safe
and secure in the mobile cloud. The various themes uncovered from this research study
may be helpful for organizations and individuals to improve their security practices when
securing their sensitive data.
Another significant contribution of this study may be the potential to cut down
confidential information security breaches in MCC to a deficient number. Once
confidential information security breaches in MCC networks are minimized, there will be
an increase in profitability, performance, and MCC adoption. Without proper security
strategies such as authentication, encryption, and user education in MCC networks,
information security breaches within the mobile cloud will continue to cause severe harm
to organizations and individuals. The findings from this study will be valuable to
information security managers, organization leaders, IT professionals, and users of
mobile devices. The findings may help them develop better security strategies and
defense mechanisms for securing sensitive data within the mobile cloud.
When confidential data is lost or stolen from organizations, it damages their
reputation, leads to the loss of huge amounts of money, and causes the loss of customer
trust. With the rapid growth of MCC, strong authentication, encryption, and user
education are a necessity in information security to reduce the occurrence of data

breaches. The findings from this study may cut down the overall cost information security
leaders incur in efforts to manage data breaches in the mobile cloud when they occur. By
applying the security strategies from this research, organizations may be able to adopt
MCC with confidence and sustain their business reputation and profitability.
Findings from this study may also assist IT professionals in aligning Mobile cloud
computing with their business models and strategies to combat security breaches and
cybercriminals (Jóia & Marchisotti, 2020). A more secure MCC environment will lead to
more adoption from large organizations, leading to the investment of more resources in
the MCC industry. Security and privacy are important elements in cloud computing
(Varsha et al., 2022); hence, the themes identified in this study, such as strong
authentication and authorization controls, encryption and user awareness and education,
are essential strategies that may assist organizations in minimizing data breaches in their
MCC networks.
MCC is an evolving technology with numerous advantages for its users; however,
it still suffers from security and privacy issues (Annane & Ghazali, 2019), which is a
significant concern for organizations and individual users. The findings from this
research may provide additional resources that information security leaders may utilize to
secure their MCC networks. Government and private organizations can also utilize the
best practices from this study to set up prevention and remediation strategies against data
breaches in their MCC environment. Data breaches are among the most significant
challenges for stakeholders and information security leaders (Zou & Schaub, 2019). Data
breaches are a major threat in cloud computing; hence, information security leaders

should implement proven strategies for keeping users’ and organizations’ confidential
data safe and secure. This study may be used as a guide for setting up systems and
strategies to help ensure confidential data is kept safe within the MCC network.
Data is a critical asset that must always be secured against breaches. One
challenge in MCC network is to gain the trust of consumers by securing their sensitive
data in the cloud at all times from data breaches. However, information security leaders
cannot guarantee 100% that there will not be a data breach in the cloud. This study’s
findings may help information security managers mitigate the various risks and
vulnerabilities in the MCC environment.
A good number of organizations have adopted MCC and have their data stored in
the cloud. Alam, Muqeem and Suhel (2018) stated that many large organizations already
have some form of data in the cloud. It is, therefore, necessary that this data is protected
against security threats. Data protection involves creating defense mechanisms and
countermeasures against data breaches. If an organization’s sensitive data is leaked or
stolen, it could lose its reputation, money, and trust (Ali et al., 2020). This study’s
findings may assist organizations in building and keeping their reputation, money, and
confidence by utilizing the best practices listed in this study for securing their MCC
networks.
One outcome of this study is laying emphasis on the importance of data security
in MCC networks and strategies information security managers can utilize to prevent data
breaches. Results from this study may also assist information security leaders in detecting

and preventing future data breaches by proactively improving their systems and educating
their users on how to detect internal and external threats and report suspicious activities.
Implications for Social Change
The implication of this research was to search for. This study aims to find
effective security strategies that could be used to secure users’ personal data from
security threats in MCC networks. With more organizations migrating to the cloud, cyber
crimes and data breaches have increased (Alruwaili, 2019). Consumer data is considered
a very valuable asset and, hence, must be protected at all costs. Customers have to trust
and confidence that organizations will keep their data safe in the cloud, and they can
utilize MCC in their daily lives without fearing losing their data to cyber criminals. The
implication of this study for social change is that the findings from this study will help
build confidence between consumers and organizations. If an organization prevents any
form of data breach, it will be trusted by the public and have a long-standing reputation.
Furthermore, findings from the study will help organizations adopting MCC set
up their environment the right way, building data security at the core of their
implementation. This way, sensitive data will be secure, and customers will be happy
knowing their data is secure. With a secure MCC environment, information security
leaders will be able to migrate their organizations to MCC without the fear of losing their
data to cybercriminals. A well-secure MCC network will lead to an increase in MCC
usage and customer satisfaction.

Information security managers may use security strategies obtained from this
study to protect their customers’ Personal Identifiable Information (PII). By following the
strategies listed in this study effectively, information security managers will not handle
PII inappropriately, provide the proper access control to PII, properly destroy any unused
PII, allow only as minimal data as possible in case of a data breach, and recover a quickly
as possible from any data breaches.
The volume of data in the cloud continues to grow exponentially, and so are the
number of data breaches. As a result, prevention of data breaches, detection, and
remediation are among the pressing needs and concerns for information security leaders
and organizations. Studies have also shown that security breaches are very costly for
government organizations, private organizations, and individuals (Carre, Curtis & Jones,
2018). Data breaches lead to the loss of vast amounts of money in ransom and fines,
massive downtimes for the organizations, and loss of customer trust and loyalty. This
study’s findings can positively impact how businesses, organizations, and individuals
manage their data on their mobile devices. Although the advancement and development
of MCC is becoming increasingly common, only a handful of researchers have explained
its impact on people’s social lives. Findings from this study may contribute to positive
social change by encouraging information security leaders to implement safer MCC
networks capable of safeguarding users’ confidential data.
Recommendation for Action
This research study was aimed at providing security strategies to information
security leaders to help them secure their MCC networks and protect their users’ personal

data against security threats in their MCC environments. The purpose of this study was to
explore strategies used to protect MCC networks from security threats. Since
organizations are adopting MCC more and more, information security leaders must
access and evaluate their current strategies against the effective strategies listed in this
study, to see if they need to be updated. Based on the results of the research, I recommend
that the following actions be taken:
•Information security leaders should make training mandatory for all employees
and conduct it at least twice yearly to increase users’ security knowledge and
awareness.
•Information security leaders should only store data they need and immediately
properly discard any data they do not need. Most organizations do not know why
they are still keeping some confidential information they no longer need. As a
result, they do not do a good job securing that data. Only important data should be
stored and locked down from unauthorized access.
•Information security managers should train all employees to detect, identify, and
report any suspicious activities. They must have the tools readily available to
report any phishing and social engineering attempts they spot, both internal and
external.
•Information security leaders should set up MFA for all systems and applications.
Establishing strong authentication and authorization controls would make it
difficult for cybercriminals to access an organization’s network.

•Information security leaders should stay on top of security updates and patches for
all their systems, including mobile devices.
•Information security leaders should periodically assess their authentication
methods and keep them updated.
Once the research is completed, I will distribute the results to all participants and
other individuals and organizations interested in the information provided. Users’
confidential information is an expensive asset and must be secured at all times.
Organizations and individuals must understand the repercussions of not properly
safeguarding customers sensitive information. Once they understand the consequences of
data leaks, which could lead to fraud, identity theft, or worse, they will invest more time
and resources to secure such data correctly. Information security leaders may utilize the
findings from this research to design and plan the best practices for securing their users’
personal data against security threats in their MCC networks. Once this study is
approved, I will ensure that a version of the research is available in ProQuest journal to
assist other researchers in information technology.
Recommendations for Further Research
This research’s limitations include the participants’ workplace, limiting the
research to only two organizations in the financial technology industry in Northeastern
Massachusetts, and participants being from a limited geographical area. All participants
were interviewed, and the results of the research were a collection of all the strategies
suggested by participants as security strategies they use to secure their users’ data against
security threats in MCC networks. The design for this study was also appropriate because

the study focused on a small population of information security managers and a small
geographical area. This study needs to be expanded using a bigger sample size and a
wider geographical area.
Future researchers may consider using a larger sample size, a much larger
geographical area, and different industries. Another limitation is that the participants
might not have all the knowledge and experience to answer the research questions.
Further research may involve more experienced information security managers with
varying experiences and backgrounds to ensure the research results are reliable and
wellrounded.
The study results also revealed that information security managers must always
positively promote data security. Users must be involved in their data security, and
information security leaders must lead this motion. Information security leaders must also
align their organization’s culture around information security. Once the policies and
procedures of the organization are in line with promoting information security, there will
be an increase in performance, revenue, and customer satisfaction.
Future researchers may conduct multiple case studies for larger geographical
areas, revealing more diverse security strategies to secure MCC networks from threats.
Future researchers could also research the types of frameworks government and private
organizations use outside financial technology to secure their MCC environments. For
organizations to be profitable, they have to have their MCC networks adequately
protected from security threats, and this can be achieved by studying the results of this
research.

I recommend that future researchers first conduct introductory research on the
participants and their organizations. Doing so would help reduce any form of bias during
the study and increase the validity and accuracy of the results. Other factors such as age,
gender, race, and number of years of experience are areas future researchers might
consider evaluating. Future researchers should not limit their study to only a few
organizations in one industry. They should seek out participants from diverse
organizations in different geographical areas because every industry and location may be
experiencing different types of attacks, and cyber attacks common in one industry may
differ from cyber attacks in another. Cybercriminals have different motivations. While
they could be seeking personal health records from the healthcare industry, they could be
seeking a ransom from the casino industry.
Reflections
Utilizing a qualitative multiple case study for my research allowed me to explore
the strategies the information security managers used to secure their users’ personal data
in MCC networks. Throughout the research process, I discovered that the strategies used
by organizations in the financial technology space are similar. Each participant
introduced themselves, their current and former job roles, and how they currently secure
their MCC networks against security threats. They revealed their strategies, their
planning, the types and frequency of the cybersecurity training they conduct, and the
steps they take to remediate a data breach. A common theme was user education and
awareness. They all agreed that users are the weakest links in the information security
framework.

The interviews I conducted, and the secondary data and publicly available data in
reviewed enlightend my understanding and brought to my knowledge the criticality and
importance of data security within and outside my organization. The knowledge gained
while interviewing participant will enable me manage my personal data more securely
and educate other people on how to secure their personal data from security threats. I
utilized open-ended questions during the interview which allowed the participants to go
in-depth when answering the research questions.
I was made aware of various security breaches that have occurred recently within
the United States. Some were reported publicly, and others were not. This knowledge
revealed to me what organizations do when they are compromised and the next course of
action they take to remediate the breach. The knowledge about data security I have been
equipped with now is much higher than the data security knowledge I had before starting
this research.
The most challenging part of my research was looking for participants to
participate in the study. I searched LinkedIn, and utilized my former work colleague
contact list to get participants. Afer putting together a list of potential participants, I sent
out emails asking if they would like to participte in the research stdudy. Many potential
participants said yes, sure. When my study finally got approved to start collecting data,
only 10% of the participants responded to my email. I started reaching out to new
potential participants. Once I received their informed consent form, setting up interviews
was straightforward. Although I received multiple interviews cancellations, I could

reschedule the interview meetings without issues. After the third interview, I reached data
saturation. Overall, the information collected and the experience were all worth it.
Conclusions
This qualitative multiple case study explored strategies that information security
managers use to secure their users’ personal data against security threats in their MCC
networks. The study focused on organizations located in the Northeastern part of
Massachusetts. By utilizing open-ended questions and organizational documents and
reviewing the data available publicly, the researcher collected, analyzed, coded, and
triangulated the data to answer the research question for the study. From transcribing the
data collected from the interview and reviewing the secondary and publicly available
data, the researcher found three major themes: (a) strong authentication and authorization
controls, (b) encryption, (c) user awareness and education, and (d) following the industry
standard of information security. From the research results, the most successful breaches
have occurred due to human errors, so users must be trained and educated multiple times
annually to stay alert for security threats and remain current with security trends.

