


Solutions to Mitigate Information Security Breaches and
Protect Personally Identifiable Information in a Public-Sector
Cloud Computing Environment
Chapter 1: Introduction to the Study
Unintentional computer viruses have caused global privacy concerns about
unprotected personal data in a cloud computing environment (Akinola et al., 2017). Many
organizations no longer resist cloud computing, which has become part of everyday
conversation around most work environments as the latest trend in the technology industry.
However, previous studies about cloud risk and risk assessment have neglected to analyze
the robust nature of cloud technology and the effects of risks in cloud computing. The
purpose of this generic qualitative study was to explore viable solutions that information
technology project managers (ITPMs) may use to mitigate frequent occurrences of
information security breaches and to address security issues relating to computer threats and
network concerns associated with protecting personally identifiable information (PII) in the
event of a network breach.
In Chapter 1, I provided an overview of the topic of cloud computing. Since the advent
of the public cloud, enterprise leaders have worried about potential security risks associated
with it, and that has not changed. More enterprises are relying on training and certification of
their information technology (IT) staff to provide a solution to protect PII as time passes.
Background of the Study
The foundation for this research study originated in multiple security issues identified
with unprotected data being stored using cloud computing network services. The importance

of the study resides in its potential to identify information security’s main concern in
reducing the number of network challenges and strengthening data protection capability for
computer users accessing a public-facing cloud computing environment. This study focused
on public cloud computing security issues and how security issues are increasing due to
failure to secure personal data in a public-facing cloud environment.
Several researchers have investigated this issue, but the topic had not been explored in
this way. There may be no viable solutions available for protecting PII in a public cloud
computing environment. The IT industry has adopted cloud services despite security concerns;
however, security challenges are on the horizon due to the possibility that ITPMs lack viable
solutions to mitigate frequent occurrences of information security breaches (Akinola et al.,
2017). Those in the IT industry have an understanding of cloud technology and how the cloud
delivers IT services to users, although there are increased cybersecurity concerns associated
with the delivery of cloud computing services that exist in many cloud data storage
environments (Akinola et al., 2017).
Cloud storage is a core service of cloud computing and has non substitutable
characteristics in the big data era. Many challenging issues influence the data security and
quality of cloud systems. Zong et al. (2016) listed the main threats, vulnerabilities, and risks in
the cloud environment according to a cloud computing system’s locality.
Cloud Provider Side
The essential security issue with cloud computing is that the user sacrifices physical
control of data. Organizations that outsource storage reduce the cost of storage infrastructure

and daily maintenance. Many organizational leaders understand that outsourcing storage may
not be an effective way to authenticate the trustworthiness of a cloud service provider (CSP).
Compromised CSPs read, write, and execute remote data without authority by the data owner
(Ateniese et al., 2011).
Multiple tenant issues arise when users share a virtual environment in a data center
using different resources stored on the same physical machine. Attackers can exploit the
coresidence issue to launch a flooding attack with the aim of blocking the traffic between
server and client by consuming all available communication bandwidth. An attacker can
overwhelm all available ports on a CSP by generating a massive number of connection request
packets, causing broken availability of the cloud service of the CSP (Zunnurhain, 2012).
Big data generates huge operating costs and redundancy for fault tolerance. An
untrustworthy CSP could omit these replication procedures, causing segmentation faults or
unrecoverable mistakes. Clients may have no technical means of verifying the availability of
files.
Network Communication
In a traditional cloud service by a public network, an unprotected network connection
can be threatened by a man-in-the-middle attack (Bhushan et al., 2017). Such an attack
interferes with network connections and creates fake network communications. An attacker
may eavesdrop on sensitive data or reroute traffic to the attacker’s destination. Attackers can
silently observe traffic intercepted in route to its intended source once recorded or edited and
detecting a threat can be difficult to exploit for PMs.

A service level agreement (SLA) is a contract that is an essential part of a cloud system
to ensure the availability of services to the customer is agreed upon between the customer and
the provider (Emeakaroha et al., 2012). When an SLA violation occurs, the provider is required
to pay penalties due to the unsatisfactory quality of service. An SLA is a contract between a
service provider and a customer defining the types and standards of services to be offered.
A denial-of-service (DoS) an attack that is typically launched by flooding the targeted
resource with requests to overload systems and block legitimate requests from being fulfilled.
DoS attacks can cost an organization both time and money while its resources and services are
inaccessible (Bisson, 2016). CSPs are vulnerable to fraudulent resource consumption attacks. A
fraudulent resource consumption attack is a more subtle attack that exploits the utility pricing
model by extending usage time or consuming more data centers. By fraudulently consuming
web resources in superfluous volume, an attacker can incur significant fraudulent charges to
the cloud consumer (Idziorek et al., 2012).
Cloud Consumer Side
Due to the user outsourcing data to an uncontrollable or untrusted third party, data
encryption on the cloud consumer side (CCS) is a general solution to mitigate data
confidentiality concerns. The overhead of traditional symmetrical encryption requests
enormous computing resources and hard-to-achieve data sharing among multiple users (Carroll
et al., 2014). As for asymmetrical encryption, the number of key-pair generations will increase
with the participating users and the data-sharing group. Both symmetrical and asymmetrical
encryption have key management concerns. Managing the keys on the CCS limits the
convenience, availability, and reliability of cloud storage. As for access control, with those
masses of software on the CCS, the attacker’s face on the user’s side is more prominent than
the data center with professional maintenance. Access control mechanisms could be more
vulnerable at the local machine (Sabt et al., 2015).
Crypto.com
Cryptocurrency is a lucrative business that was impacted by a serious cybersecurity
incident that impacted the company operation. The incident occurred on January 17, 2022, that
impacted nearly 500 individuals’ cryptocurrency wallets (Jennings, 2022). Despite the
blockchain being a relatively secure transaction method, the thieves used a particular process to
execute their malicious intent. The cyber thieves bypassed the site’s two-factor authentication
and removed several items without permission in lieu of $18 million of Bitcoin and $15 million
of Ethereum (Jennings, 2022).
Microsoft
Microsoft was impacted by a cyber incident called Lapsus$. The group posted an
announcement online to indicate that they attempted a successful attack on Microsoft and, in
the process, hacked Cortana, Bing, and several other companies (Jennings, 2022). The cyber
thieves had access to several products produced by Microsoft. Microsoft publicly announced
that only one account was compromised due to recognizing and shutting down the hacking
attempt promptly (Jennings, 2022).
News Corp
News Corp is a company that confirmed they encountered several server breaches. Due
to News Corp being one of the biggest news organizations in the world, hackers are eager to
penetrate its security system (Jennings, 2022). News Corp announced that no customer data

was stolen during the breach, and that the company’s everyday work was not hindered. Instead,
News Corp uncovered evidence that company emails were stolen from their journalists. The
cyber thieves have not been identified, but News Corp servers hold a large amount of sensitive
information (Jennings, 2022).
Red Cross
Red Cross and a third-party contractor saw more than half a million records
compromised during an attack in January 2022. An attack was made on the documents that the
Red Cross classified as “highly vulnerable” (Jennings, 2022). Thousands of individuals had
their sensitive data stolen, and most of the people are currently listed as missing or vulnerable.
The Red Cross took their servers offline to stop the attack to investigate this seemingly political
breach, and the cyber thieves have not been identified (Jennings, 2022).
Ronin
Ronin is a blockchain gaming platform that relies on cryptocurrency where a
cyberattack impacted the organization. Ronin’s Axie Infinity game enables players to earn
digital currency and nonfungible tokens, and the increasing popularity saw the firm dial back
security protocols so its servers could handle a growing audience (Jennings, 2022). That helped
Axie Infinity deal with the number of people who wanted to play, but it also let criminals in,
and they stole $600 million of cryptocurrencies. Ronin’s parent company has worked with
authorities to identify the root cause and recover funds, but it has become a lesson learned
whenever a business unknowingly compromises their security standards (Jennings, 2022).

FlexBooker
FlexBooker is an appointment management business that was impacted by a cyberattack
that affected up to 3 million of their users (Jennings, 2022). PII data including emails, ID
information, driver’s licenses, and passwords were stolen by these bad actors, and then the
hackers began to offer the stolen PII for sale on social media message boards; because of the
breach, many users have decided to leave FlexBooker (Jennings, 2022). The incident was
caused by a group of bad actors called the Uawrongteam, and the group had unauthorized
access to FlexBooker’s Amazon Web Service (AWS) server and installed malware to
manipulate the firm’s systems (Jennings, 2022).
GiveSendGo
Cyber hacks were motivated by politics rather than pure financial gain in the
GiveSendGo security impact (Jennings, 2022). Canadian truckers performed an act of protest
against COVID rules due to GiveSendGo being a Christian fundraising site favored by
Canadian Truck drivers (Jennings, 2022). Cyber bad actors stole and then published the
information of 90,000 people who had donated money to the protesters, and then redirected the
fundraising page to another site that spoke unfairly about the truckers, a classic DoS attack
(Jennings, 2022). Some data were also sent to a group that published leaked data that usually
comes from a group of individuals with a history of violence. Companies need stronger security
measures to stop political attacks because all breaches are not driven by financial gain
(Jennings, 2022).
Cash App
Block is known as a popular mobile payment tool, and the firm acknowledged that a
former member of the staff had penetrated the service’s servers (Banks, 2022). The impact
involved customer names, stock trading information, account numbers, emails, and portfolio
values alongside other sensitive financial information (Jennings, 2022). The firm has not
confirmed how many people were affected by the breach, but Block has contacted more than 8
million customers to tell them about the incident (Jennings, 2022). The hackers stole account
information, but it was unclear during the attack whether the hackers stole only a limited
amount of identifiable information (Jennings, 2022). These significant challenges and security
issues profoundly influence cloud storage security, as shown in Table 1.
Table 1
Summary of Cloud Storage Challenges/Vulnerability
Locality Challenges/vulnerability
Cloud provider side Lack of physical data control
Multitenant VM co-residence
Uncontrollable service quality
Network communication Man-in-the-middle attack, DoS attack.
Service-level agreement violation
Fraudulent resource consumption
Cloud consumer side Cryptographical overhead
Data sharing access control
Untrusted CCS environment
Note. From “The Summary of Cloud Storage Challenges / Vulnerability” by Zong et al. (2016).
Security concerns are relevant with many internet service providers, and trend
technology is constantly developing innovative solutions that promote security control in data
centers environments; however, cloud data centers that offer multitenancy and virtualization

services are needed to create secured storage facilities that provide stronger security measures
and provide added reliability to secure client information in a cloud computing environment.
This study is significant in that it may reveal that ITPMs lack viable solutions to mitigate the
frequent occurrences of information security data breaches (Akinola et al., 2017). There are
many identified security issues relating to computer threats and network concerns associated
with the security of cloud computing. Placing this data in the cloud has its advantages but has
also created major concerns for several organizations. Many organizations have adopted cloud
computing but may lack the knowledge to ensure that they and their employees are using it
securely; however, security challenges may become serious threats in the 21st century due to
ITPMs lacking viable solutions to mitigate the frequent occurrences of information security
breaches.
Akinola et al. (2017) claimed that previous studies about cloud risk and risk
assessments failed to analyze the robust nature of cloud technology and the effects of supply
chain risks in cloud computing. A gap was identified in the literature that revealed that
industries are leveraging cloud-based solutions to increase efficiencies and improve supply
chain relationships (Akinola et al., 2017; Huynh, 2010; Tiwari, 2017). Cloud computing
provides greater flexibility and allows users to access software applications in the form of
mobile cloud computing. Major research is underway to reduce security issues, but much work
remains to be done to create a secure mobile cloud computing environment (Tiwari, 2017). For
instance, cloud platforms are susceptible to attack due to the high intensity of information
resources provided for user access (Tiwari, 2017). The primary goal of an attacker is to
interrupt service to cloud users by creating a means for users to access the cloud platform

(Tiwari, 2017). Therefore, an attack can come from an external source of cloud computing IT
users or within the cloud computing environment that consists of whomever may mistakenly
prevent users from accessing cloud services (Tiwari, 2017).
Patala et al. (2018) suggested that most students were ready to adopt cloud
cybersecurity, but the results suggested there is a lack of physical control of data or educational
knowledge about data protection prior to adopting cloud cybersecurity. There may be no viable
solutions available for protecting PII data in a public cloud computing environment. This study
may fill a research gap in public cloud computing, identify security challenges, and reveal a
lack of accountability in securing, monitoring, and managing PII data that impacts the end
user’s trust in a public cloud environment (Jaatun et al., 2018). The current study was needed to
initiate a demand for global awareness as an implication for positive social change to
encourage an increase for a society with a greater discerning of knowledge.
Problem Statement
The general problem was IT professionals may lack viable solutions to reduce frequent
security breaches. The specific problem was there may be no viable solution available for
protecting PII in a public cloud computing environment (see Devi et al., 2020). A gap was
identified in the literature regarding minimal cloud supply chain investigations performed by
the year 2017 (Akinola et al., 2017). Cloud platforms are susceptible to attack due to the high
volume of information resources provided for user access (Tiwari, 2017). The primary goal of
an attacker is to interrupt service to cloud users and create a means to pull down the cloud
platform (Tiwari, 2017). An attack can come from an external source of cloud computing IT

users or within the cloud computing environment that consists of staff and administrators who
may accidentally prevent users from accessing cloud services (Tiwari, 2017).
With the current shift to remote work, internet of thing (IoT) security has become a
more pressing issue for businesses. IoT security is frequently overlooked or minimized in
cybersecurity plans (CrowdStrike, 2021). As customers increasingly rely on their home
network and personal devices to conduct business duties, digital adversaries use weak security
measures at the endpoint level to conduct attacks. Inadequate IoT protocols, rules, and
processes can pose a severe danger to enterprises because any device might be a gateway to the
broader network (CrowdStrike, 2021).
Purpose of the Study
The purpose of this generic qualitative study was to understand how ITPMs may
implement viable solutions to mitigate the frequent occurrences of information security
breaches in a public cloud computing environment (see Patala et al., 2018). This study may
find that ITPMs may lack viable solutions to mitigate the frequent occurrences of information
security breaches. The study may find that there are no viable solutions available for protecting
PII in a public cloud computing environment.
Research Questions
RQ1: What are the most common security problems with protecting public data in a
cloud computing environment?
RQ2: What strategies are available to help information technology professionals
determine the desirability of a viable solution that may provide the necessary protection for
personally identifiable information (PII) data in a public cloud computing environment?

RQ3: What is the importance of a viable solution that may provide the necessary
protection for PII data in a public cloud computing environment?
The data was collected through a questionnaire/survey method until a determination of
data saturation was reached. Each RQ was associated with the research problem and was
functionally decomposed to create questionnaires. The data analysis determined a set of
requirements that included categories, groups, and themes.
Conceptual Framework
Consumers expect the products or services they use to meet practical standards for
safety, functionality, durability, and other important traits that are managed by the National
Institute of Standards and Technology (NIST, 2022). Some organizations have their IT systems
and data compromised regularly (Newman, 2017). Corporations such as Amazon, AIG
Insurance, and Home Depot have had their IT infrastructure compromised (Manworren et al.,
2016). In every situation, data that contains clients’ sensitive information was obtained (Kess et
al., 2017). The theft of this information was discovered months after hackers accessed what
they wanted. The NIST created the Cyber Security Framework (CSF) as a voluntary
framework to provide organizations with guidance on how to prevent, detect, and respond to
cyberattacks. NIST continuously develops cybersecurity standards, guidelines, security best
practices, and other resources to meet the needs of U.S. industry, federal agencies, and the
broader public. The NIST activities range from producing specific information that
organizations can put into practice immediately that anticipates advances in technologies and
future challenges.

Some NIST (2022) cybersecurity assignments are defined by federal statutes, execution
order, and policies. The Office of Management and Budget mandates that all federal agencies
implement NIST cybersecurity standards and guidance for nonnational security systems (NIST,
2022). The NIST cybersecurity activities are driven by the needs of the U.S. industry and the
broader public (NIST, 2022).
NIST (2022) engages with stakeholders to set priorities, to support organizations in
better identifying and protecting individuals’ privacy, to provide cybersecurity safety, and to
ensure resources that address key issues that security professionals face. NIST also advances
understanding and improves the management of privacy risks, some of which relate to
cybersecurity. The NIST CSF adoption continues to accelerate as many IT security
professionals recognize the framework as a pathway to maintain compliance with regulatory
standards, similar to the Payment Card Industry Data Security Standard (NIST, 2022).
Personal data include information about individuals such as addresses, Social Security
numbers, date of birth, and phone numbers that a company might gather and use in the normal
course of business (NIST, 2022). Because the data can be used to identify the people who
provide them, an organization must take action to ensure their employees’ information is not
misused in a way that could embarrass, endanger, or compromise the customer (NIST, 2022).
NIST (2022) helps organizations identify the privacy outcomes they want to achieve and then
prioritize the action needed to do so.
The goal of the current study was to collect and analyze data about critical determinants
that may identify a breach in public IT infrastructure to the cloud after a user transition to cloud
computing technology. This vital component of the study consisted of the essential area in

information security and the lack of control that IT professionals must possess to eliminate the
frequent occurrences of information security breaches. Chaudhry et al. (2012) identified threats
to information systems in four dimensions, which aligned with the conceptual framework for
this study:
1. Resources are inconsistent with outdated security procedures.
2. Perpetuators are either human or nonhuman that can originate from employees’ lack
of awareness or lack of consideration to conform with security guidelines form
internal or external sources.
3. Intent is either accidental or intentional and can originate from a human or
nonhuman perpetrator that may be influenced by internal or external sources.
4. Consequences include disclosure, modification, destruction, or denial of use and the
result of either accidental or unintentional intent, which originates from access
control management.
The concept of risk includes the possibility that an event may occur that involves one of
the four major issues that are common in the security industry. The researcher observed that
ITPMs primary issues were inconsistency, outdated security procedures, perpetuators or lack of
employee awareness, leadership backing needed to better manage the situation, and tighten
access control management. Chaudhry et al. (2012) identified a conceptual framework based
on these four issues that includes relevant security challenges with enterprise information
systems. In comparison, Pettigrew et al. (2001) noticed that for the field of information
security, one of the challenges that is often omitted from managing information systems is the
inclusion of clear instructions on specific types of development for IT systems. Researchers
have claimed that few security frameworks provide technical guidance on modernizing system
design (Pettigrew et al., 2001).
Researchers have analyzed how IT systems enhance end users’ knowledge and
accommodate computer user needs (Pettigrew et al., 2001). This conceptual framework related
to the current study’s approach and research questions as well as the instrument development
(e.g., participants, survey questions, and collected artifacts) and data analysis where
appropriate. The NIST framework includes a categorization approach whereby an organization
can choose to introduce information security procedures, manage future expectations about
security policies, and provide security guidance for identity credentialing and access control
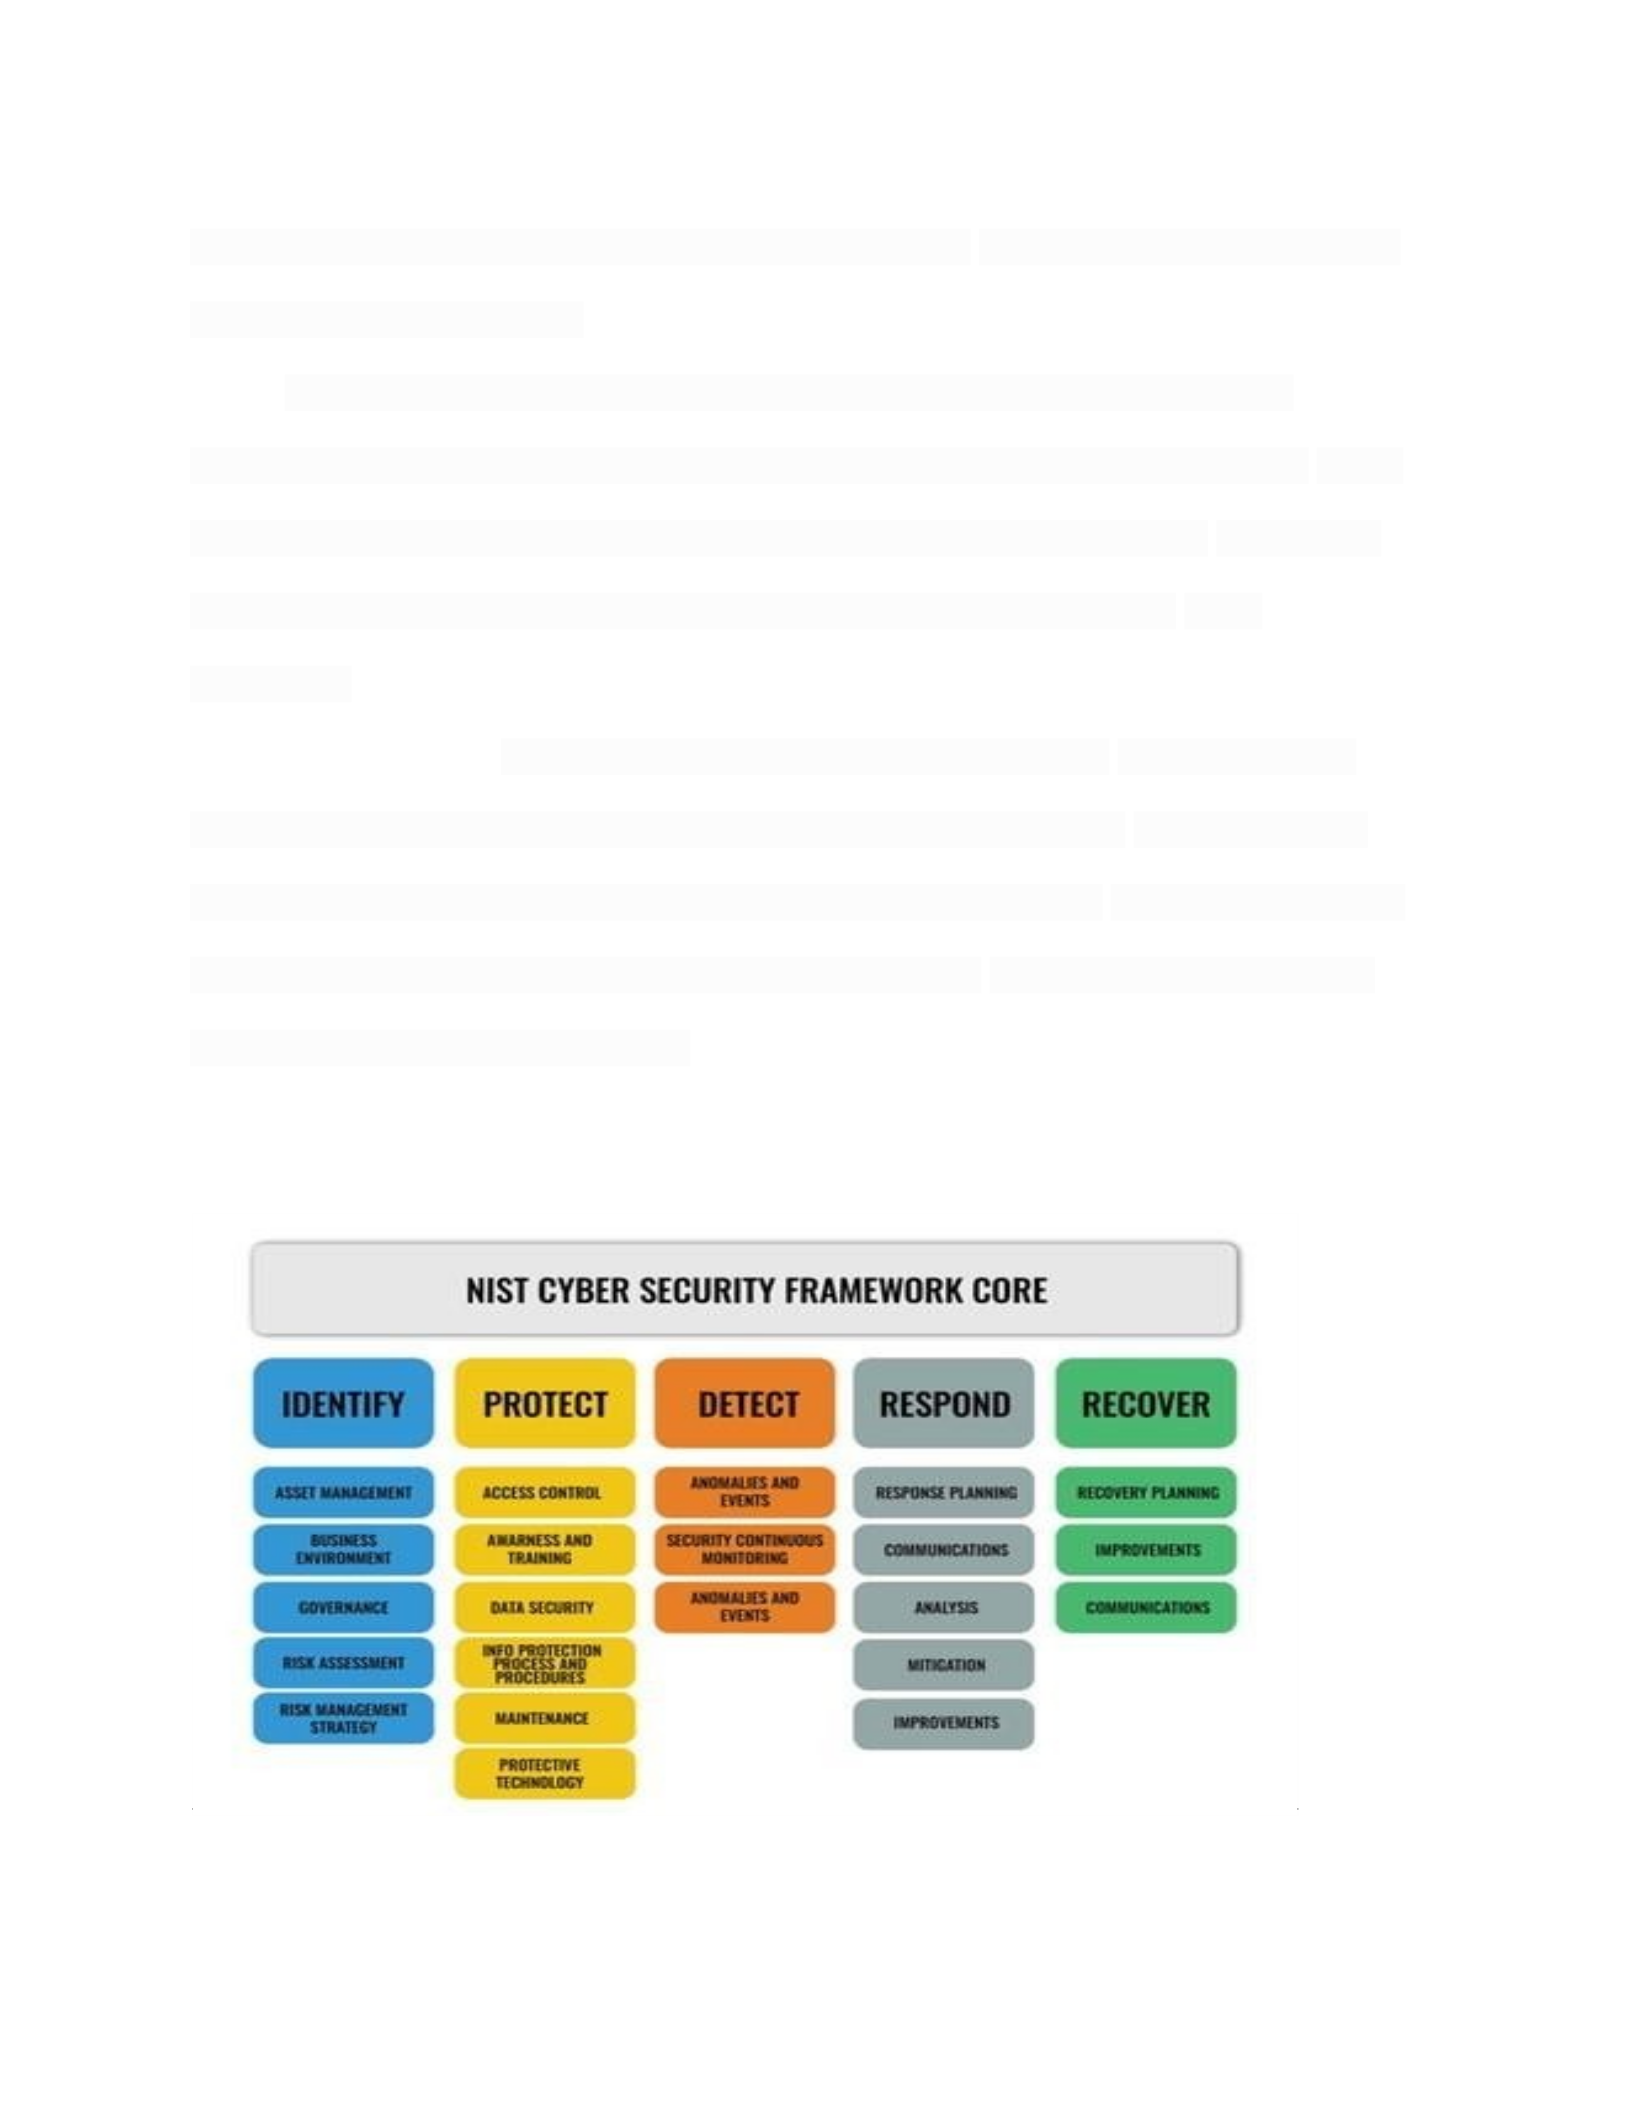
management in a cloud computing environment. This NIST framework has influenced security
policies and changed identity credentialing and access control management in a public cloud
computing environment (see Figure 1).
Figure 1
NIST Cyber security Framework

Note. From “NIST Cybersecurity Framework Guide 2022 Core Implementation and Profile.”
Nature of the Study
Five quantitative designs were considered and deemed inappropriate for the current
study. The quasi-experimental design is like the true experimental design except that it does not
use randomized sample groups (Jovancic, 2020; McCombes, 2020). Experimental design is the
most common way for quantitative researchers to gather data. Whether it is a field experiment,
a controlled experiment, or a quasi-experiment, this is one of the research designs that
establishes a cause-and-effect relationship between two variables or among group variables.
The independent variable is manipulated to observe the effect on the depended variable
(Jovancic, 2020; McCombes, 2020).
The correlational design seeks to discover whether two variables are associated or
related in some way, using statistical analysis while observing the variable. The descriptive
design is a theory-based design in which the researcher is interested in describing the topic that
is the subject of the research. The descriptive design was applied to the generic qualitative
studies, naturalistic observations, and survey types. This method includes data collection,
analysis, and presentation. The descriptive design allows the researcher to present the problem
statement so others can understand the need for this kind of research. Without a clear problem
statement, the researcher is conducting exploratory rather than descriptive research (Jovancic,
2020; McCombes, 2020). The observational design allows the researcher to gather data on
behaviors and phenomena without having to rely on the honesty and accuracy of respondents.
This method is often used by psychological, social, and market researcher to understand how

people act in real-life situations (Jovancic, 2020; McCombes, 2020). These five quantitative
designs were not suitable for my research study.
There are five primary qualitative designs. A historical study is the ideal choice for
studies that involve extensive examination of the past including people, events, and documents.
The purpose of a historical study is to draw conclusions about the present and future based on
research conducted in the past (Hoover, 2021). Phenomenology is a wideranging form of study
in which the researcher seeks to gather information that explains how individuals experience a
phenomenon and how they feel about it. This design recognizes that there is no single objective
reality; instead, everyone experiences things differently (Hoover, 2021). The purpose of
grounded theory is to develop a theory regarding a social issue. This design seeks not only to
identify problems in social scenes but also to define how people deal with those problems.
Grounded theory is unique among qualitative designs because it depends solely on the data
developed through the research process (Hoover, 2021).
Ethnography is the study of a specific group within a culture. Researchers using this
design immerse themselves in the culture they are researching. The qualitative data are
gathered through direct observation of and interaction with participants who belong to that
culture. The information is then presented through the researcher’s perspective. Ultimately, this
design aims at understanding group culture (Research Rundowns, 2021). This type of study is
one of the most common qualitative designs, and is used to examine a person, group,
community, or institution. Researchers often use a bounded theory approach that confines the
study in terms of time or space. To conduct the study, the researcher may draw upon multiple
sources of data, such as observations, surveys, and documents. All participants chosen must

share a unifying factor, which means they all must have a direct or indirect connection to the
research questions, or the subject being studied. After collecting the data, the researcher
analyzes the collected data to identify prominent themes
(Research Rundowns, 2021).
I chose a generic qualitative study to explore the topic regarding IT Security challenges
associated with protecting PII data. There are several approaches to analyzing qualitative data,
with that said, I used an exploratory qualitative data analysis to identify and interpret patterns
and themes until the data reached a saturation point to provide answers for my research
questions.
I created an online questionnaire using the SurveyMonkey platform as the data
collection technique to capture data from 33 cloud computing information security subject
matter experts. These subject matter experts provided their unanimous responses to the best of
their ability towards protecting public data in the cloud computing environment. I selected a
generic qualitative study for the research design which involved searching across several a data
sets of several online questionnaires and analyzed a range of text to find repeated patterns
related to the problem (see Ahmad and Waheed, 2015).
Exploratory research was conducted to investigate the phenomenon of ongoing
problems that were not clearly defined. This method of data analysis was flexible, compatible
and the right approach for this type of qualitative research study because it was used to
determine specific themes and patterns (Ahmad and Waheed, 2015). Data used in this research
study was collected through SurveyMonkey platform from subject matter experts working in

cyber security management positions because they are frequently involved with data protection
issues related to cloud computing (Ahmad & Waheed, 2015).
The initial data collected started the analysis which was gathered from the
SurveyMonkey’s platform. As each subsequent participant’s data was collected and analyzed,
they were compared to the previously analyzed data. The analysis moved back and forth
between data that had been coded and clustered into patterns. These patterns and themes
changed and developed as the analysis continued throughout the process until the data collected
reached a saturation point (see Ahmad & Waheed, 2015).
For my generic qualitative study, I was the primary instrument to initiate the data
collection process and then analyzed the data (see Pezalla et al., 2012). An initial
announcement was posted to recruit individuals from the Walden University participant pool to
find individuals willing to participate in my study. After two weeks of waiting for inquiries, I
made the decision to cancel the announcement and move on to my next option. I contacted
SurveyMonkey and began building my survey using their platform to find participants for my
research study. SurveyMonkey reviewed the questionnaire to make sure the announcement
followed their guidelines. SurveyMonkey approved the initial announcement as well as
guaranteed they could provide participants in the information security field to respond to my
initial request, review my preliminary questionnaire for clarification as well as review the
informed consent form. The researcher reviewed the test questions prior to the engagement
with the participants. Each volunteer was asked to read the criterion questions prior to
advancing to the informed consent form.

The primary data source included 5–10 participants. As each subsequent participant’s
data was collected and analyzed, I compared them to the previously analyzed data. The
analysis moved back and forth between current data and previous data that had been coded and
clustered into patterns and themes. These patterns and themes changed and developed. The
analysis continued throughout the process until the data collected reached a saturation point
(see Ahmad and Waheed., 2015). There was a logical connection between the qualitative
methodology, qualitative design, exploratory data analysis, and the nature of the study. There
may be no viable solutions available for protecting PII in a public cloud computing
environment (Akinola et al., 2017; Devi et al., 2020; Patala et al., 2018).
Definitions of Terms
Throughout this study, the following terms were used to describe the problem or clarify
the research effort (see Felton, 2021). Included are terns associated with small businesses and
the technologies that support them (see Felton, 2021). These terms are not exclusive to public
small businesses.
Bit technology: A bit (short for binary digit) is the smallest unit of data in a computer. A
bit has a single binary value, either 0 or 1. Although computers usually provide instructions
that can test and manipulate bits, computers generally are designed to store data and execute
instruction in bit multiples called bytes. In most computer systems, there are eight bits in a byte
to allow a computer to function properly with enough power (Stack Exchange.com, 2022).
Business continuity: Processes and procedures an organization leader uses to keep
business operations running during and after a synthetic or natural disaster (Long, 2017).

Cloud computing: A service offered by vendors that provides data storage, software
development platforms, application hosting, and other services over the Internet (Knorr, 2018).
Cloud provider service: A company that offers some component of cloud computing;
typically, when a person searches the internet, a cloud service is defined as infrastructure as a
service (IaaS), software as a service (SaaS), or platform as a service (PaaS) to other businesses
or individuals (Ateniese et al., 2011).
Cyber event: Any occurrence in a computer system/network in which unauthorized
access could result in data compromise, corruption, or destruction (Law Insider, n.d.).
Cyber resilience: The ability of an organization to detect, respond to, and recover from
an attack on its IT infrastructure with minimal damage to the business reputation and
competitive advantage (Wilding, 2016).
Cyberattack: Any attempt to disrupt, steal, or modify data, or to disable or gain
unauthorized access to a computer system, network, or network-enabled device (Colter et al.,
2022).
Cybersecurity: A security mode that features preventive measures designed to protect
data from attack, loss, theft, or compromise (Billingsley, 2019).
Cybersecurity policy compliance: Fundamentals across existing theories that are tested
and analyzed by the preliminary empirical support for the methodology (Moody et al., 2018).
Data breach: An incident in which data are accessed or corrupted by an unauthorized
person or persons (Wilding, 2016).

Data security: Also known as information security, the process of securing digital
information from unauthorized access and corruption using methods such as data encryption
while retaining full access for use by the organization (Bonderud, 2019).
Dialectical system theory (DST): A theory that addresses the lack of holism, which
considers all viewpoints in other systems theories (Zenko et al., 2012).
Extensible mark-up language: An encryption that requires the improvement in deciding
which part is sensitive using an automated process (Khan et al., 2019).
General systems theory (GST): A theory that indicates that certain general principles
apply to all systems regardless of their properties (Von Bertalanffy, 1972).
Information and communication technology (ICT): is the use of computing and
telecommunication technologies, systems and tools to facilitate the way information is created,
collected, processed, transmitted and stored. (Rouse, 2023).
Information security: A set of practices designed to protect the print, electronic, and
other private, sensitive, and personal data from unauthorized persons. Information security is
used to protect data from being misused, disclosed, destroyed, modified, or disrupted (Andress,
2014).
Information technology (IT): The application of technology both hardware and
software, to solve business and organizational problems (Sylvester, 2019).
Malware: Software that is written for the purpose of gaining access to a user’s computer
to harm the data contained within it or damage the computer system without the user knowing
(Palmer, 2017).
Model of PC utilization: The degree of ease associated with the use of the system

(Venkatesh et al., 2003).
Operating Expenses: A pay as-you-use system (Armbrust et al., 2010; Dillon et al.,
2010).
Payment card industry data security standard: A compliance standard that defines data
security requirements relating to the processing, storage, or transmission of cardholder data
(Bolton, 2016).
Perceived ease of use (PEOU): The degree to which an information security
professional believes that an information security system will be easy to learn and simple to use
(Davis, 1989).
Personally identifiable information (PII): Any information that permits the identity of an
individual to be directly or indirectly inferred, including any information that is linked or
linkable to that individual (Lever, 2022).
Perceived mobility value: An external variable to the adoption of mobile learning
management support (Saroia & Gao, 2019).
Perceived usefulness (PU): The level at which an IT manager believes that
implementing new technology could improve their ability to protect PII from phishing attacks
(Davis, 1989).
Phishing: A cyberattack method that uses email to gain entry into computer systems
(Fruhlinger, 2020).
Professional group on information theory: A group of information technology
professionals that discuss the transmission, processing, extraction, and utilization of
information (Lei et al., 2017).

Ransomware: A type of Trojan horse that is installed on a user’s system usually by the
user unknowingly clicking a link contained in a socially engineered email or by visiting an
infected website where the malicious software is downloaded to the user’s system (Kaspersky,
n.d.).
Service level agreement (SLA): A level of service stipulated in the contractual
agreements between service providers and the clients (Emeakaroha et al., 2012).
Simple object access protocol: A nonproprietary protocol used in cloud computing
(Khan et al., 2019).
Small business: An independently owned and operated business that is limited in the
number of employees. What constitutes a small business is determined by the Small Business
Administration, which is usually based on either a company’s number of employees or a
company’s annual revenue (Small Business Administration, 2019).
Social cognitive theory: One of the eight conceptual models (Venkatesh et al., 2003).
Software composition analysis: The examination of major security interests that need to
be inspected from a new point of view (Pathak, 2022).
Stakeholder: A person or entity that has an interest (stake) in the product or service an
organization or person provides (Castillo, 2020).
Technology acceptance model (TAM): A model that refers to the likelihood of a person
accepting new technology based on ease of use and perceived usefulness (Davis, 1989).
Technology acceptance use model: The consideration of organizational standards and
guidelines with the type of task performed to advocate using a system (Ajibade, 2018).

The institute of radio engineers (IRE): An institute that began to publish articles on
research work in a journal meant to focus on information theory and developed a discussion
setting called the Professional Group on Information Theory (Lei et al., 2017).
Theory of planned behavior (TPB): A theory that expands the theory of reasoned action
by considering an individual as having perceived behavioral control, attitude toward conduct,
and subjective norms for predicting their intent to engage in a behavior (Hill et al., 1977).
Theory of reasoned action (TRA): A theory that purports that a person’s behavior is
determined by their drive to do a certain thing (Hill et al., 1977).
Two-factor authentication: An additional security process that requires two types of
credentials to allow access to data or a system (Rosenblatt and Cipriani, 2015).
Unified theory of acceptance and use of technology (UTAUT): A theory that helps
explain users’ technology acceptance in an organizational context (Ajibade, 2018).
University management support: External variables to the adoption of m-LMS (Saroia
& Gao, 2019).
Web Services Description Language: A platform that encourages support for legacy
applications and integration of various types of systems (Khan et al., 2019).
Workgroup Information Security Effectiveness: An event that is achieved through
workgroup collective efficacy and security knowledge coordination using TAM as a theoretical
lens (Yoo et al., 2020).
Assumptions
I assumed that most developed countries have similar laws concerning the protection of
data. U.S. law imposes specific privacy and security restrictions on data transferred into the

cloud (Sen, 2013). A limitation of the current study was that the study included only U.S. cloud
computing environments. Another assumption in the study regarding the reluctance to adopt
cloud computing was that the participants were familiar with the cloud computing
environment, including virtualization, standard cloud business productivity solutions, email
systems, and online backup and storage processes (see Das & Dayal, 2016). I assumed that the
participants were subject matter experts in decision making, selection, recommendation, and
analysis in the security industry as influential leaders at the information system security
professional level (see Das & Dayal, 2016). From a research methodology perspective, the
study involved using a generic qualitative study approach. By using this research method, the
subject matter experts had the qualifications required and their responses would be limited to
the experience and knowledge of the participants (see Das & Dayal, 2016).
Scope and Delimitations
The scope of the study was based on the cybersecurity challenges encountered when
protecting personal data in a public cloud computing environment. The study covered the
ongoing inefficiencies of the security professionals and the effects of unprotected data when
users access a public cloud computing environment. The study included recommended actions
of security professionals to protect personal data in a public cloud computing environment. The
study also covered the effects of data loss and consequences of data breaches due to the
damage of customer information. The study included the risk factors associated with access
management and exposed customer information that the individual wanted to keep private. The
study also included the possibility of emotional damage that a customer would experience
because of a data breach.

As the researcher, I focused on informing computer users on cyberattacks and providing
users with several methods to consider for protecting personal data. The study was focused on
analyzing collected data by a SurveyMonkey questionnaire from subject matter experts in the
security field. The study focused on organizations that neglected some of the cloud security
flaws due to outdated security documentation.
The study was limited to the public facing cloud computing environment and not on
other non-public-facing cloud computing environments. The study did not cover on the crisis
of the IT security issues of the government or educational environments. The study was also
limited to the security industry due to the nature of the topic focusing on IT security
professionals who may lack the knowledge to eliminate recurring cybersecurity issues prior to
identifying a cyberattack on the network. The study did not include any bias characteristics,
influential perspectives, or suggestions made by me.
The integration of cloud services has many unresolved security challenges involving
data protection issues. Limitations, challenges, and barriers in information security benefits
outweigh the problems in most security risk assessment due to implementing stricter security
policies. There is a possibility of researcher bias influencing the study’s outcomes. The
researcher must monitor and mitigate all bias tendencies while conducting the research (Tiwari,
2017). Researchers must also develop the competence to implement the specialized skill
correctly (Tiwari, 2017). Competence and skill are required at all the following points: (a)
explaining the study without bias by using the ability to effectively communicate, (b) seeking
participants for the study, (c) making appropriate observations, (d) handling and collecting
data, (e) analyzing and interpreting the data per the design, (f) developing the artifacts, and (g)

presenting the findings (Tiwari, 2017). The key factor in the research is reducing personal
information damage. The researcher must understand that collected information must be
protected and managed with proper control. Researchers are required to seek the institutional
review board (IRB) approval prior to conducting the study. The IRB is designed to protect
research participants’ data, including their privacy and their confidentiality interests. Obtaining
IRB 05-19-24-0488449 approval is a requirement for researchers to protect participants’
personal data and follow strict guidelines and other methods of protecting and storing
participants’ data.
Security subject matter experts’ limitations and difficulties included the following:
•Encryption schemes have limitations and cannot be used in large-scale cloud
computing environments due to security requirements for large-scale cloud
computing (Khan et al., 2019).
•XML encryption requires the improvement in deciding which part is sensitive using
and automated process (Khan et al., 2019).
•The intrusion detection system and intrusion prevention systems need to monitor
each node simultaneously to detect malicious activities and health of the overall
system (Khan et al., 2019).
•The dynamic nature of adding and removing nodes from the cloud platform makes
it difficult to monitor each network packet. An efficient and intelligent mechanism
is required to analyze network traffic that does not compromise the application’s
performance (Khan et al., 2019).

•Signature-based detection is no longer a feasible detection mechanism.
Behaviorbased detection techniques require further research to minimize the risk of
false positives to validate legitimate traffic (Khan et al., 2019).
•Attribute-based and stateless authentication of users are among the current research
areas of access control and identity management in the cloud, but they require
improvements in maintaining attribute privacy and collusion resistance (Khan et al.,
2019).
•Logical isolation in multitenant databases requires improvement because it poses a
greater risk of exposing users’ data by malicious insiders such as administrators and
software testers. Depending on the level of access, an insider might have full access
to the data if given proper rights (Khan et al., 2019).
•Issues with insiders having access to and exposure to clients’ sensitive data such as
developers and testers are currently prevented by complex and time-consuming
procedures such as replicating database and falsifying data obfuscation. These
measures introduce large overhead costs (Khan et al., 2019). Using the
memoryprivacy-protection scheme prevents virtual machine escape and hopping
attacks to ensure tenant isolation. The problem is that it reuses many built-in
functions of Xen, which are not available on other hypervisors (Khan et al., 2019).
The significance of the current study is that cybercrimes continue to emerge, with new
threats surfacing every year. Every business, regardless of its size, is a potential target of
cyberattack. Cybersecurity in today’s connected world is a key component of any

establishment. Amidst known security threats in a virtual environment, side-channel attacks
target most impressionable data and computations. Software composition analysis is examining
major security interests that need to be inspected from a new point of view. As a part of
cybersecurity aspects, secured implementation of virtualization infrastructure is essential to
ensure the overall security of the cloud computing environment. Security professionals require
the most effective tools for threat detection, response, and reporting to safeguard business and
customers from cyberattacks. The objective was to explore virtual aspects of cybersecurity
threats and solutions in the cloud computing environment (Pathak, 2022).
Cryptography can be defined as a technique of securing private messages by using
codes so that only those for whom the message is destined can read and process it.
Cryptography converts ordinary plain text into impenetrable text. The concept of cryptography
has been widely used to secure communication in computer networks. Current cryptographic
techniques may be easily defeated by increasing computing power, which is not likely to be
more secure (Pathak, 2022).
Quantum cryptography is gaining importance among IT security practitioners. The
theory of quantum cryptography is becoming mature, and its practical implementations are also
emerging. The concept of quantum cryptography is formed on the basic principles of quantum
mechanics. Quantum cryptography has the capability to make a remarkable contribution to
personal, business, and e-commerce security. Quantum cryptography has the strength to
provide security among government organizations (Pathak, 2022). Over the past 3 years,
cybercrimes have been increasing and have become one of the most compelling threats across
the world. Cybercrimes can disrupt and damage business operations, result in commercial

losses, and compromise a well-established reputation. Cyberattacks evolve every day as
attackers are becoming more inventive (Pathak, 2022). Not only is the number of security
violations increasing, but violations are increasing in asperity, leading to massive losses to
businesses and organizations (Pathak, 2022).
Significance of the Study
The reason this study is significant is that it may reveal that ITPMs may lack viable
solutions to mitigate the frequent occurrences of information security breaches. There are many
identified security issues relating to computer threats and network concerns associated with the
security of cloud computing (Akinola et al., 2017). The IT industry has adopted cloud services
despite the security concerns; however, security challenges are increasing in the 21st century
due to ITPMs lacking the knowledge to create a viable solution to mitigate the frequent
occurrences of information security breaches (Patala et al., 2018). The collection and analysis
of data in the current study were intended to answer each research question, and conclusions
were drawn regarding the problem statement.
Significance to Practice
There remains a gap in the industry that is unable to eliminate the frequent occurrences
of information security breaches. The importance of this study is the potential for its findings to
contribute to the IT security industry to increase the awareness of the various security issues
and guide in the decision to mitigate cyberattacks in the public cloud computing environment.
This study may provide an increased benefit to other cloud computing services that may
encounter cyber-attacks.

Significance to Theory
The generic qualitative study design, the conceptual framework, and the exploratory
data analysis were aligned with the problem. I collected data from 5–10 subject matter experts
to explore the problem, establish a foundation for future research on the subject, and fill a gap
in the literature. The use of encryption is necessary to protect all types of PII documentation,
but the focus should be applied to develop tougher security standards and measure privacy
protection (Ahmad & Waheed, 2015). The significance to theory includes the fact that the case
study may advance the IT industry.
Significance to Social Change
The study may capture important data in the security industry and identify a significant
industry gap to further explore and mitigate issues related to public cloud computing, and
information security challenges. The study may identify that there may be a failure of securing
personal data in a public cloud environment that generates an overarching demand for global
situational awareness as an implication for positive social change. The study has the potential
to affect the security industry to encourage positive social change.
Summary and Transition
Researchers have investigated this issue, but there were no viable solutions for
protecting PII data in a public cloud computing environment. Chapter 1 included the
introduction and the background of the study on public cloud computing and managing
security. To explore this problem further, I conducted qualitative data analysis to understand
the problem, the diverse aspects, and to employ a wide range of analytical techniques (see
Glaser and Strauss, 1967; King and Brooks, 2018; Stubbs, 2019). The study included 5–10 IT

participants who participated in my SurveyMonkey questionnaire approach. I provided a
review of the peer-reviewed literature that included findings on public cloud computing and the
conceptual framework of the study. Chapter 2 includes a review of the literature review
strategy and provides a detailed review of cloud computing risks and the management issues
that security constantly encounters. This study may identify a lack of IT subject matter expert
knowledge and conclude that there may be no viable solution available for protecting PII in a
public cloud computing environment.
Chapter 2: Literature Review
Chapter 2 includes a review of the current literature that establishes the relevance of the
research problem. The literature review process has four phases: planning, selection, extraction,
and execution (Ahmad & Waheed, 2015). Those phases helped me position the current study
within the dominant paradigms of the field of information security. This chapter includes four
sections: the literature search strategy used to initiate the research, the conceptual framework, a
statement of the NIST cybersecurity framework, and a literature review related to
IT security. The research problem was there may be no viable solutions available for protecting
PII in a public cloud computing environment (see Devi et al., 2020).
Literature Search Strategy
The search strategy used for collecting documentation for this literature review included
scholarly publications common to all information systems in terms of data security,
cybersecurity, information management procedures, and information management policies. A
variety of search tools were used to support the review. The literature search was performed
electronically using the following business, technology, cloud computing, and information

security databases: Google Scholar, SAGE Knowledge -Encyclopedias and Handbooks,
Walden University-Dissertation Databases-Publications. Dissertation and peer-reviewed
literature consisted of a combination of studies conducted within the past 5 years. An iterative
search process was used in each database to identify the selected articles related to this study.
The following keywords were searched: cloud computing and cyber security theory,
general theory of security and theory of development, information security theory or
communication networks, cyber security challenges and network and defense, hackers, and
attacks. Additional search terms included breach, protection, phishing, ransomware, and
malware (see Felton, 2021). The search parameters were not the entire range of search
combinations used (Felton, 2021). The direction of the study evolved because of the search
parameters that were used. Resources used for these information searches were a combination
of Google Scholar, Walden University Library databases, and ProQuest. The use of these
databases guided my search patterns to literature related to this study.
The focus of the review included business and IT industry publications referenced to
address personal data protection and security resilience related to recovering from a breach that
may happen in a cloud environment. These publications provided the current security data from
businesses that did not have enough security measures in place as part of a cybersecurity
strategy (see Felton, 2021). These publications also addressed the resulting consequences
business faces when they neglect to implement a strict security resilience plan (see Felton,
2021).

Conceptual Framework
The percentage of small businesses being targeted by hackers (Brown, 2016; Carias et
al., 2020) and the increasing number of small businesses closing after a serious network breach
(Walker, 2019) illustrate a common problem among many small businesses (Felton, 2021).
Many small businesses have not implemented security protection after hearing that a cyber
incident caused major damage to larger companies (Felton, 2021). These companies have lost
millions of dollars because of network breach incidents but have usually expended the
resources necessary to recover, albeit at an increasing price (CSI.com, 2022). Most small
businesses do not have the resources to recover from a serious security incident (Carias et al.,
2020; Johnson, 2019). Most small businesses that suffer a serious cyber incident do not last
longer than 6 months (Liwer, 2018). Given the number of small businesses that are in the
United States, small business owners do not operate in a vacuum; that is, they have access to
news, media outlets, and social/technical media platforms where reports and discussions about
cyberattacks are published and broadcasted to make the general public aware of what
companies have been breached and the disposition of the companies’ data storage, if that
information is known and has been released to the public. Given what security industry
information is known, there appears to be a valid reason that small businesses are more
susceptible to cyberattacks that make them a prime target of cybercrimes (Knox, 2015).
There is a lack of awareness of the potential damage a cyberattack can have on a
business; businesses do not believe they are in any danger of being targeted by hackers because
of their company size (Jacques, 2015). Evidence indicated that is not the case, yet many small
business owners operate with the possibility of losing their business because of a cyberattack

(Gustke, 2016). If more business owners were made aware of a series of actions that could
lessen the effects of a cyberattack on their business when accessing the cloud environment, the
small business owner may take actions to accrue more expense and hire security matter experts
to protect employee data.
Chaudhry et al. (2012) identified a conceptual framework based on four issues that are
relevant security challenges with enterprise information systems: inconsistent and outdated
security procedures, lack of employee awareness, leadership backing and support, and identity
credentialling and access control management. A conceptual framework was established for
analyzing and categorizing uncertain employee activities with certain characteristics relating to
organizational topics involving information security best practices (Alfawaz et al., 2010). The
conceptual framework focused on understanding the traditional human behavior and the typical
social work environment by observing individual influences, knowledge, and skills that impact
cybersecurity practices managed by IT professionals (see Alfawaz et al., 2010). In my current
work environment, there were recognizable signs that indicate that recurring security issues
were increasing, which prompted me to research the matter. The classification of concepts and
features in the framework developed from an article that supported theoretical models and
provided a detailed explanation about each unique feature. Khan et al. (2019) revealed that an
intrusion detection system and intrusion prevention systems need to monitor each node
simultaneously to detect malicious activities and overall health of the system.
In comparison, Carroll et al. (2014) introduced a conceptual framework at the
Australian Conference on Information Systems and recommended a conceptual framework
with an emphasis on not only the accidental intent and deliberate intent (i.e., the behavior

and/or action that causes threats by an individual). The first category was insider threats are
considered as an unintentional act due to carelessness not meant to cause damage, as opposed
to a technical expert with a motive to cause damage perceived by a cyber security professional
who constantly looks for cyber threats. The second category was insider behavior is considered
an intentional act due to negative conduct and\or hate. A skilled tech expert eager to perform
the act is recognized as malicious and intentional. Carroll et al. (2014) explained that insider
threats are grouped into following different categories: (a) deliberate damages, (b) harmful or
misuse, (c) unsafe tampering, (d) unconscious mistakes, (e) attentive mistakes; however,
Carroll et al. (2014) found that an individual’s good intentions caused harm to an enterprise
network environment.
In contrast, Canner (2020) revealed that 50% of IT professionals who participated in the
survey used security applications to detect network attacks, and less than 50% of IT
professionals use electronic encryption collaboration tools; however, with insider threats and
other unknown risks, most IT security professionals do not use the existing technology.
Thompson (2020) recognized in a comprehensive and systematic review of several
types of security-related issues and breaches that influence organizational decisions that work
to mature their current preventive strategies. Organizations search for new techniques or
strategic approaches that will identify and detect network traffic threats faster than their
existing cyber solutions. Thompson (2020) claimed that human participation combined with
the affiliation of authoritative access is the primary cause of insider threats within an
organization. A report provided by Law Insider (n.d.) claimed that the number of internal
security issues has increased globally, creating an impact on organizational expenditures to

increase by 47% during that same period, and over $11 million dollars was devoted to security
prevention.
Epstein (2020) stated that many organizations assume insider threat detection can be
controlled with their existing solutions, when implementing a better overall management
approach may strengthen, and decrease the number of endless security issues. The overall
strategy may help internal employees realize the importance of protecting information,
understand the daily impact, and gain visibility to a network environment (Epstein, 2020).
Creating a lesson learned for employees and contractors to consider better alternatives or
suggest additional employee training is needed to emphasize the importance of protecting
information due to an incident (Epstein, 2020). Several researchers have investigated this issue,
but the topic has not been explored in this way. There may be no viable solutions available for
protecting PII in a public cloud computing environment. The IT industry demand has adopted
cloud services despite the security concerns; however, security challenges are on the horizon
due to ITPMs may lack viable solutions to mitigate the frequent occurrences of information
security breaches (Devi et al., 2020, March). The IT industry has a greater understanding about
cloud technology and how the Cloud delivers IT services to user; although there are increased
cyber security concerns associated with the delivery of cloud computing services that exist in
many cloud supply chain environments (Akinola et al., 2017). The observation part of this
study is of an exploratory nature. The conceptual framework has been applied by previous
researchers and adapted in their studies. This study benefits from understanding the specific
capabilities in the framework, summarized in (see Figure 1).

In comparison, Dupuis & Khadeer (2016) recognized that the growing numbers of
cyber outbreaks occur because of a weakened enterprise protection barriers plus an influx of
individuals who have elevated privilege (EP) with remote access to the organization’s network,
server machines and internal data (Dhillon et al., 2007). Dhillon et al. (2007) claimed that
internal employees in addition to external factors are the primary reason why unfortunate
computer incidents are a constant uphill battle for security professionals (Dhillon et al., 2007).
The concept aims to identify individual computer protection against employee’s uncooperative
consistent computer behavior (Dhillon et al., 2007).
In contrast, insider threats as accidental acts or deliberate acts performed by an
individual that may use their privileges to cause harm in a network environment. Security
incidents generally happen when employees and/or network administrators perform routine
tasks which lead to carelessness. An insider incident may occur when procedures are not
followed properly due to performing the same execution may seem mundane or repetitive for a
tech expert due to the person’s skill level may be highly developed and has developed a strong
understanding about the system.
Security professionals understand that insider threats may also happen when an
individual misplaces a technical device and discovers there is no locking mechanism on the
device (H. Li et al., 2020). Employees that refuse to adhere to organizational password policies
may result in losing their network privileges and may find themselves facing disciplinary
action by security professionals. Insider data breaches occur due to passwords are easily
refabricated making the system venerable. Security training constantly advises employees to
not write down their passwords or give their password to someone working on their computer

and/or share their password with colleagues and/or use the same password multiple times to
access several systems.
The National cyber security center claimed the insider threats are the result of
employees that use common words for their password. The word password and/or their unique
name is a common password used by many employees, and generally that same password is
reused multiple times across for different types of account access on related online services.
Even though a security professional may encourage users to frequently change their password,
knowingly users will create multiple variations of the same password that are easy to
remember.
Epstein (2020) claimed that many security professionals take an active role in
managing network threats inadequately by only tracking data movement; however, failing to
realize individuals are capable of moving data to different locations. Security professionals
primarily focus on tracking several individuals simultaneously to monitor daily activity and
data movement to provide better clues an identify where the threat may have occurred on the
network (Epstein, 2020). The security team will begin using this method to mitigate the time it
takes to investigate the incident and reduce exhausting the costs allocated for prevention to stop
future insider incidents (Epstein, 2020).
In contrast, Thompson recognized that the terminology used in the research literature
revealed inconsistent classifications of cyber security threats and how they are identified. In
addition, earlier research performed by Pettigrew et al. (2001) found that the security industry
encounters increased challenges due to the omission of clear systems documentation to
properly manage security issues due to the development of IT systems. Thompson (2020)

claimed that consistent terminology is the primary first step towards achieving a cohesive
understanding of terms. It is a critical success factor (CSF) for the security field to attain
control in the use and misuse of information systems and granting human access in an
organizational network environment (Thompson, 2020). Thompson (2020) recognized there are
discrepancies in the cybersecurity classification of insider threats. The security industry needs a
unified comprehensive framework to attain a universal understanding of common terminology
for best practices in the information security field (Thompson, 2020). The logical connections
between the framework presented and my study approach include Moody et al. (2018) theory
that was developed and built around behavioral research had produced different models to
explain cyber security strategy and strict standards. This proposes a unified model, called the
combined approaches of cyber security policy compliance (CACSPC), that joins certain
fundamental across these existing theories that are tested and analyzed by the preliminary
empirical support for the methodology. The existing insider threat classification provides the
different intents, offers a common unified language, improves the understanding of different
types of threats, and will help to develop stronger prevention and data protection policies in the
security industry.
Technology Acceptance Model
Several information security researchers examined information security using TAM.
The seminal origin of the technology acceptance model (TAM) began with Davis (1989) who
theorized the acceptance of technology is based on these factors perceived ease of use,
perceived usefulness, and user attitudes towards new systems (Davis, 1989). Davis (1989)
developed TAM to offer a general explanation for the influences that motivate users to adopt

new technologies. TAM originated from the theory of reasoned action (TRA) and the theory of
planned behavior (TPB) (Hill et al., 1977). The goal of TRA was to explain how a person’s
thoughts and feelings influence their intention to engage in a behavior (Hill et al., 1977). TPB
expands TRA by considering an individual as having perceived behavioral control, attitude
towards conduct, and subjective norms for predicting their intent to engage in a specific
behavior. This theory continues to evolve in the industry (extended) primarily in the security
field as it relates to updating resource material, employees accepting new application services,
and educational awareness. The theory of reasoned action (TRA) (Hill et al., 1977) allows the
research to investigate the likelihood of expected behavior by users when deciding to either use
a system or application service or not based on intentions and attitude (Felton Jr, 2021).
The TRA is a theory that focuses on the behavioral aspects and the circumstances or
environmental factors that affect one’s behavior (Hill et al., 1977). More specifically, they
focus on the attitudes and the subjective norms or influence others have on a person’s behavior
to perform/do a certain action or not (Hill et al., 1977). As the impetus for Davis (1989) TAM,
the two theories tie in well with this study when viewed through the lens of a small business
owner who appears to be slow to react to the reports and accounts of large companies being
hacked and incurring large amounts of damage to their data, their IT infrastructure, and their
reputation. The following literature review seeks to establish the conceptual foundation
evolving in the security industry and reveals the ongoing challenges that the security industry
has faced and continue to deal with upon which the research study is based.
TAM goes further by combining both theories and adding PU and PEOU to explain the
behavioral aspects of user’s technology usage intentions. In the context of this study, PU refers

to the level at which an IT manager believes that implementing new technology could improve
their ability to protect PII from phishing attacks. PEOU refers to the degree to which an
information security professional believes that an information security system will be easy to
learn and simple to use (Banks, 2022).
TAM provides researchers in the information security and IT field a framework for
determining the probability of user’s acceptance and usage of new technology (Sengkhyavong
(2019). User feedback regarding the PU and PEOU of a system can help system designers
create a valuable and accepted product. Researchers have applied the TAM to various
technologies and user populations, including cloud computing, education, business, and
banking. Sengkhyavong (2019) applied TAM to identify the factors related to IT manger’s
decision to adopt cloud computing. Sengkhyavong (2019) found that PEOU, PU, and perceived
benefits of cloud computing were significant factors in IT manager’s decisions to adopt cloud
computing. Pereira (2022) discovered a significant positive relationship between PU, security,
regulatory, environment, and IT manager’s choice to adopt cloud computing. At the same time,
Pruitt (2019) stated that authentication security, data protection security, physical security, PU,
and PEOU influenced IT managers to adopt cloud computing. Sondakh (2017) applied the
TAM to predict taxpayer’s interest in using electronic tax returns and found that PEOU had a
significant positive effect on PU and user’s attitude toward electronic tax services. Ramadania
and Braridwan (2019) applied the TAM to measure the influence of PU, PEOU, attitude,
selfefficacy, and subjective norms are directly proportional to the level of intent to use online
shopping. The results of these studies with Saroia & Gao (2019) claimed, if users develop a
positive relationship with an information system, they are more likely to use it.

Unified Theory of Acceptance and Use of Technology
The UTAUT is an extension of TAM. While TAM measures user acceptance of
technology at the individual level, UTAUT helps explain user’s technology acceptance in an
organizational context (Ajibade, 2018). UTAUT combines eight conceptual models commonly
used to describe the individual acceptance of technology (Venkatesh et al., 2003). The eight
conceptual models are the TRA, the TAM, the motivational model (MM), the TPB, Combined
TAM and TPB (C-TAM-TPB), the model of PC utilization (MPCU), the innovation diffusion
theory (IDT), and the social cognitive theory (SCT); (Venkatesh et al., 2003). UTAUT consists
of four components: EE, PE, SI, and FC (Puriwat & Tripopsakul, 2021). SI refers to how other
IT managers view the usefulness of the new technology. In the context of the study, EE
describes the system’s ease of use. FC refers to IT manager’s belief that appropriate support
infrastructure exists for the new system. PE refers to how IT managers believe that new
technology will help improve their job performance (Venkatesh et al., 2003).
UTAUT offers researchers a framework for investigating the implementation of new IT
system at an institutional level (Garone et al., 2019). UTAUT addresses TAM’s 40% variation
in predicting user’s intention to use technology (Garone et al., (2019). According to Garone et
al., (2019), UTAUT explains 70% of the variation in predicting user’s intention to accept and
use new information systems and technologies. Researchers have applied UTAUT to studies
concerning social media, e-commerce, and digital advertising platforms (Puriwat &
Tripopsakul, 2021; Reyes-Mercado & Barajas-Portas, 2020; Susanty et al., 2020). Puriwat &
Tripopsakul (2021) applied UTAUT to their investigation of social media adoption in small
businesses. Puriwat & Tripopsakul (2021) discovered that SI, effort, and PE greatly influenced

the behavioral inclination to implement social media for business purposes. These findings
align with those of Rozmi et al., (2019). Rozmi et al., (2019) investigated the intention of
owners of small and medium -sized enterprises (SMEs) to adopt information and
communication technology (ICT) and found the EE, SI, and FC influenced SME owner’s
intention to adopt ICT. The results of these studies support Varma’s (2018) assertion that EE,
PE, and SI are motivating factors in entrepreneur’s decision to adopt innovative technologies.
Applicability of the Technology Acceptance Model to the Study
Implementing an information security program was based on IT managers and users’
willingness to accept and adopt technologies and policies to protect data. Davis (1989) TAM
offers a general explanation for the influences that motivate users to adopt new technologies.
Budgetary constraints and user expertise are examples of individual results, while
organizational and legal standards represent environmental effects. Information security
policies must balance business requirements with ecological considerations, such as law and
industry regulations, to secure information and avoid data breaches. TAM aligned well with
this study because small business IT managers judge the PEOU and PU of implementing
strategies for protecting data, which aligns with the casual processes in the TAM.
Extensions of TAM
TAM is not without limitations. Davis (1989) acknowledged that PU and PEOU might
not be the only intermediaries between attitude and system acceptance and adoption. Davis
(1989) also wrote that TAM is a foundational model that future researchers can build upon and
extend to explore a wide range of phenomena. Ajibade (2018) agreed that TAM has
laminations. Ajibade (2018) argued that TAM was appropriate for describing individual

acceptance and use of technology, but not explaining the reasons for accepting and using
technology in a business environment. Ajibade (2018) introduced the technology acceptance
and use model (TAUM) to explain IT adoption and use by small and medium-sized businesses.
Ajibade’s TAUM involved consideration of organizational standards and guidelines with the
type of task performed to advocate using a system.
To overcome limitations of TAM, many researchers extended TAM to include a vast
range of internal and external variables that apply to various technologies and contexts. Saroia
and Gao (2019) used and extended TAM to investigate the impact of personal privacy on the
acceptance of mobile phone technology in small and medium-sized enterprises. Saroia & Gao
(2019) added personal privacy to TAM to determine the impact that personal privacy had on
SME’s acceptance and usage of mobile phones. Saroia & Gao (2019) found that personal
privacy affected the PU of mobile phones, but it did not influence the behavioral intentions to
use them. When employees felt that their privacy was safe, they were more inclined to use
mobile phones. Saroia & Gao (2019) also used and extended TAM to examine college
student’s intention to use mobile learning management systems (m-LMS). Saroia & Gao
(2019) extended TAM to include academic relevance (AR), perceived mobile value
(PMV), and university management support (UMS) as external variables to the adoption of m-
LMS. PMS represents the student’s judgement regarding the advantage of using m-LMS. AR
refers to the school’s PU judgement regarding the relevance of m-LMS for their studies. UMS
refers to the school’s commitment to ensuring that the m-LMS operates as intended. Saroia &
Gao (2019) found that UMS exhibited a strong relationship with PEOU. At the same time,
PEOU directly influenced attitude towards usage.

Saroia & Gao (2019) contended that TAM’s various external factors play a role in a
system’s PU and PEOU. Saroia & Gao (2019) extended TAM to include the external factors
content quality (CQ) and motivation (Mo) to explore the factors influencing student’s
acceptance and usage of a web-based social media application to improve academically. Saroia
& Gao (2019) found that high CQ was a reliable predictor of students PU and PEOU. This
result aligns with Razmak & Bélanger (2018) study that showed the ability of a system to
address user’s needs is related to PU. Razmak & Bélanger (2018) also extended TAM to study
the acceptance of electronic personal health records (PHR). Razmak & Bélanger expanded
TAM to include compatibility a communicativeness to consider variations in user’s behaviors
and needs when using new technology.
Wang et al. (2020) discovered the PU and PEOU are affected by the external TAM
variables computer self-efficacy, individual innovativeness, computer anxiety, perceived
enjoyment, social norm, content, and system quality experience and facilitating conditions.
Results from Wang et al. (2020) study of external TAM variables in e-learning and virtual
reality applications revealed that external variables affect PU and PEOU differently. The
authors also found that self-efficacy was the strongest predictor of PEOU with experience and
perceived enjoyment as secondary influences. At the same time, PEOU had a significant
impact on PU and sensed pleasure, system, and content quality. Wang et al. (2020) also
considered personal innovativeness in exploring consumer’s intention to use ridesharing
services. Wang et al. (2020) extended TAM to include external variables such as personal
innovativeness (PI), environmental awareness (EA), and perceived risk (PR). Wang et al.

(2020) found that PU, value, and convenience were the main motivations to use
ridesharing. All in all, both internal and external factors contribute to user’s PU and PEOU of
new technology and environment to which they are applied. Although TAM is famous in the
information security and technology field, researchers have extended and will continue to
expand it to apply it to a broad range of technologies and industries.
TAM was appropriate for this study because it evaluates the influences that motivate IT
managers to accept or reject security systems that protect PII. IT managers can use the TAM
model to improve information security adoption in small businesses. Understanding the
principles of the TAM is crucial in exploring the strategies that some small business IT
managers use to protect PII. To better understand IT manger’s acceptance of information
security systems and policies, I examined several conceptual and theoretical models. However,
I decided to use the TAM as the conceptual framework because IT managers can apply the
constructs behind user’s behavior in information security compliance to improve their
protection of PII.
Alternate Theories
General Systems Theory
General systems theory (GST) indicates that certain general principles apply to all
systems regardless of their properties (Von Bertalanffy, 1972). Systems are naturally hierarchal
and the procedure itself exists on the macro level, while the system’s microlevel includes its
components. The relationship between systems level is causal, while the system’s relationship
with the environment is horizontal (Hofkirchner, 2019). According to GST, systems are either
open or closed. Available systems elements interact with each other and the environment, while
secure systems are isolated from their environments (Hofkirchner, 2019). Hofkirchner (2019)
wrote that GST is a theory of goal driven behavior and further suggests that goals are
considered the cause of a system’s behavior. Individuals adjust their behavior to achieve
specific system goals (Hofkirchner, 2019). GST is appropriate for examining aspects of
information security, such as adaptation, communication, control, and self-organization (Dube
& Flowerday, 2018). However, GST is driven by behavior adaptation for goal achievement and
was not appropriate for this study.
Dialectical System Theory
Dialectical system theory (DST) addresses the lack of holism, which considers all
viewpoints in other systems theories (Zenko et al., 2012). According to Zenko et al. (2012),
DST achieves holism through interdisciplinary cooperation. DST supports decision-making in
that the manager is presented with information from various sides of the issue, thus giving
them a complete picture of the problem (Čančer & Mulej, 2010). DST also takes human
behavior into account as part of holistic systems thinking (Zenko et al., 2012). Zenko et al.
(2012) used DST to investigate knowledge management and discovered that interdependence
and responsibility are necessary for holistic, socially responsible decision making. DST did not
apply to this study because it is concerned with cooperation between opposing parties to attain
a goal.
Soft Systems Methodology
Checkland (2012) developed soft systems methodology (SSM) for research in various
fields, including business, engineering, and social sciences. SSM helps researchers understand
complex issues that involve multiple systems and stakeholders (Checkland, 2012). Research

indicates that SSM’s primary focus is investigating complex problems that require action to
remedy them. SSM helps in explaining how system stakeholders interact to address
problematic situations (Saroia & Gao, 2019). Saroia & Gao (2019) argued that SSM is suitable
for investigating complex problems with multifaceted social and human elements Saroia &
Gao (2019) used SSM to examine incentive policies and technological innovations in the
electricity sector. SSM allowed the authors to create a multicriteria decision support model to
help decision makers develop policies that encourage technical innovation in the electricity
sector (Saroia & Gao, 2019). Sutoyo & Sensuse (2018) researched gamification of information
systems using SSM. The researchers used SSM to visualize the problem and identify which
tools were needed to implement gamification. SSM helps in remembering specific actions
required to solve a problem; thus, SSM did not apply to this study.
Contrasting Theories
Grey systems theory is an opposing theory of TAM. The grey systems theory was
developed to solve economic, engineering, and social science problems (Nowak et al., 2020).
Grey systems theory helps investigate issues with limited available information that is difficult
to measure and is subjective (Nowak et al., 2020). Rao & Liu (2017) also argued that the grey
systems theory is appropriate for researching topics with small data samples and a degree of
uncertainty. Jalali & Heidari (2020) agreed that the grey systems theory helps make predictions
with small pieces and limited information. Rao & Liu (2017) suggested that grey systems
theory involves creating and extracting data from partially known and unknown data to support
decision-making and solve problems. Grey system theory deals with problems solving with
little to no information; therefore, grey systems theory does not apply to this study.

Related Studies
Self-efficacy refers to one’s belief in accomplishing a goal and is a central TAM factor.
An extension of self-efficacy is collective efficacy, which refers to the collaboration and
coordination between group members to achieve the collective goals (Chul et al., 2020).
Information security is a group effort that requires every member’s cooperation with an
organization to be effective. Chul et al. (2020) applied the collective agency concept to their
information security effectiveness study. The authors found that a workgroup’s sense of
collective efficacy directly influenced the group’s ability to detect, respond, and recover from
information security threats. Alshaikh et al. (2018) used TAM to explore the influence of
information security monitoring on employee’s security assurance behavior. The authors found
that employees are more likely to engage in appropriate security behavior when monitored.
Alshaikh et al. (2018) suggested that information security policies and organizational standards
create company culture that influences employee’s opinions and affects their information
security behaviors. Alshaikh et al. (2018) used TAM to understand the relationship between
employee’s noncompliance with information security policies and environmental factors. The
authors discovered that the frequency of security education, training, awareness training, policy
awareness, and knowledge of policy violation consequences positively influence employee’s
information security behavior. According to Alshaikh et al. (2018) when employees are aware
of security policies and the penalties for violating them, they are more likely to comply with
them.
Using TAM as a theoretical lens, Adhikar & Panda (2018) analyzed the relationships
between user’s privacy concerns and their likelihood of engaging in privacy protection

behaviors when using social networks. The researchers evaluated whether user’s perceived risk
and perceived vulnerability of personal data influence their social network’s security behaviors.
The researchers found that users who are confident in their ability to identify and respond to
security threats were likely to engage in security conscience behaviors. This finding supports
Nguyen and Kim (2017) assertion that when users have knowledge and skills to protect
information and information systems, they are likely to engage in appropriate security
behavior. Additionally, users who were not confident in their ability to identify and respond to
security threats were less concerned about data security in social networks. Adhikar & Panda
(2018) also observed that the perceived consequences of data loss, theft, or compromise
influenced user’s security behavior in social networks, which aligns with the outcome
expectation component of TAM. This observation aligns with Alshaikh et al. (2018) findings
that outcome expectation influenced user’s willingness to share health information in social
networks (Alshaikh et al., 2018). Adhikar & Panda (2018) studied underscored the need for
social network companies to inform users of their service’s information security implications.
When users are aware of information security threats and how to mitigate them, they are likely
to engage in appropriate security behavior.
Information Theory
Shannon & Weaver (1949) presented how information could be quantified with
absolute precision and demonstrated the essential unity of all information media (Knox, 2015).
The concept was formalized by Shannon who proposed the idea of information theory, which
established a solid foundation for the rapid development of modern communication (Lei et al.,
2017). Shannon has been called the father of the Information Age because he asserted this
unity and revealed how this new way of thinking can transfer all communication into bits of
decodable information. Shannon & Weaver (1949) revealed that understanding this concept
can trigger an influential perspective that can change the world (Knox, 2015). Shannon’s
research study contained four major concepts that shaped the impact of Information Theory.
Shannon’s research explained how bit technology is used to compress information, combined
with the speed limits of accurate data transmission, and the effect of “entropy” or unexpected
data, in the transmission of information (Strawn, 2014).
Shannon’s ideas provided an initial understanding about how to use a roadmap to
propose where technology could go. Strawn (2014) noted that Information Theory “has
strongly influenced not only the development of wireless systems, CDs, and data storage, but
also computer networks, satellites, optical communication systems, mobile phones, MP3s,
JPEGs, and the Internet” (p. 23). The field’s implications for modern disciplines and
technologies are apparent, but Shannon’s initial ideas helped many individuals understand the
transferability of information. A message, a piece of entertainment, or any data could be
transferred as 1s and 0s regardless of its original medium. It is almost hard to conceive of a
world where this was not readily understood, and this perhaps contributes to the difficulty in
understanding the importance of Shannon’s ideas (Knox, 2015). Since that time, Shannon
information theory structured and pioneered the establishment of an Internet security model
(Lei et al., 2017). The intent is to guide, control and strengthen cyber security and all other
security work. This general security theory is a set of security theory concepts structured
specifically for management. The theory fits this study because it aims to combine the security
branches and establish a unified theory across the security industry which is like the current

research study. According to Glaser & Strauss (1967), generally, this type of theory allows
concepts to emerge from research literature. Lei et al. (2017) claimed that security issues, such
as copy-move forgery (J. Li et al., 2015), ordinal regression (Gu et al., 2018), and cloud
computing security (Xia et al., 2016) have accelerated a demand for protecting information
across the technology industry. Many researchers have suggested different types of structures
to control network access threats to help secure and protect user data.
Pan et al. (2015) proposed a technique to resolve and protect video coding breaches.
Shen et al. (2017) proposed a data sharing framework to resolve cloud computing security
issues. Yuan et al. (2017) offered a viable solution during a technology conference that protects
sensitive stenography data that is sent across network channels. Yuan et al. (2016) proposed
fingerprint liveness detection to solve security and privacy problems. Yang et al. (2016)
research study investigated several security issues such as the meridian-collateral and the
security confrontation systematically that revived the outdated concept of security. Ren et al.
(2010) proposed a scheme to resolve security issues in wireless technology involving sensor
networks. Shen et al. (2016) proposed a minor multi-layer authentication protocol. Kong et al.
(2016) offered a viable solution during a technology conference that revealed a solution to
resolve task distribution problems in an open and dynamic cloud-based environment. Lei et al.
(2017) proposed a solution to protect privacy issues in social media environments that involve
data sharing across networks.
Shannon & Weaver (1949) began a vast circulation and propagation of ideas that
identified key factors that transformed a single research paper into a flourishing field, requires
an investigation into the activities that occurred soon after Shannon introduced his theory (Lei

et al., 2017). Initially, there was an eagerness of excitement to investigate the new concept.
Soon after, an explosion occurred, and Universities began to offer seminars which help develop
into classes. The Institute of Radio Engineers (IRE) began to publish articles on research work
in a journal meant to focus primarily on Information Theory, and immediately developed a
discussion setting called the Professional Group on Information Theory (PGIT). In addition,
symposiums were organized to present the information and to allow forum discussion
opportunities to occur (Lei et al., 2017).
Lei et al. (2017) claimed that this approach lacks comprehensive and systematical
theoretical guidance, as well as developed a cultivation for increased vulnerabilities and
security issues. Several experts have raised the question about the uncontrolled security issues
and identified that information security professional may lack the comprehensive theoretical
guidance dedicated to providing information security protection to secure personal data in a
network or cloud computing environment (Lei et al., 2017).
The selected theories such as information theory and the general security theory
absolutely related to the present study because they have identified in their research study that
information security professionals are the primary concern for increased security issues in the
past and the primary reason for constant network vulnerabilities creeping onto the network
(Palmer, 2017). I have built upon the issue to identify the primary concern about increased
security issues in the past and develop better solutions to mitigate constant network
vulnerabilities creeping onto the network. Security issues are still ongoing today. This research
identifies the research problem in my study and will answer the following research questions:
What are the most common security issues with protecting public data in a cloud computing

environment? What strategies are available to help IT Professionals in determining the
desirability of a viable solution that may provide the necessary protection for PII in a public
cloud computing environment? What are the feasible solutions that may provide the necessary
protection for PII data in a public cloud computing environment? What is the importance of a
viable solution that may provide the necessary protection for PII data in a public cloud
computing environment? These research questions relate to the challenges by revealing a gap
in the industry and help convey my conclusions by building upon existing theory.
Ganesan (2018) conducted a quantitative study to investigate the influence of senior
management and workplace norms on employee’s information security attitudes and
selfefficacy. Overall, 338 employees of a law enforcement agency participated in the study.
The researchers found that managerial support of information security significantly influenced
worker’s attitude towards information security. This finding aligns with Saroia & Gao (2019)
finding that administrative support has a strong relationship with PEOU, which influences
usage intention. Yoo et al. (2020) research information security in workgroups to examine how
workgroup information security effectiveness (WISE) is achieved through workgroup
collective efficacy and security knowledge coordination using TAM as a theoretical lens. Yoo
et al. (2020) also surveyed a law enforcement agency’s employee to assess the relationships
between collective workgroup efficacy, security knowledge coordination, individual
selfefficacy, and workgroup information security effectiveness. Yoo et al. (2020) examined
whether information security at the workgroup level relates to information security personally.
The strength of security at the lowest levels forms the basis for security at higher levels. Yoo et
al. (2020) found that individual self-efficacy, an external factor of TAM, is a vital WISE

element. Yoo et al. (2020) discovered that the effect of self-efficacy mediated through the
group mechanisms of workgroup collective efficacy and security knowledge coordination;
individuals equipped with their security efficacy require coordination for the workgroup to
achieve its information security goals. Ganesan (2018) also found that workplace norms
directly influenced employee’s feelings about information security and the compliant security
behavior of other’s positively influenced employee’s information security self-efficacy.
Ramadania & Braridwan (2019) found that user’s PU, PEOU, attitude, self-efficacy,
and subjective norms are in direct proportion to the level of intent to use online shopping.
Ganesan (2018) research revealed that the human element of information security is an
essential consideration in protecting data. Policies alone are not enough to motivate employees
to engage in compliant behavior. Positive role models and security-compliant colleagues
significantly influence employees’ view and self-efficacy about information security.
Enhancing the human element of cybersecurity is necessary for preventing cyberattacks.
Encouraging employees to adopt appropriate security behavior and improving their confidence
in doing so supports the external variable of self-efficacy in the TAM. While it is impossible to
prevent all cyber threats, small businesses can make themselves less susceptible by following
cybersecurity best practices and guidelines, including enhancing employee’s confidence in
adopting and implementing appropriate security behavior.

Application to the Applied Information Technology Problem
The study’s applied IT problem was that IT security managers and small businesses
may lack efficient strategies to protect their customer’s PII against phishing attacks, in a cloud
computing environment.
Security Policies
Information security policies are one element of an information security strategy that
ideally encompasses human factors, technical processes, policies, and data governance (Brown
(2016). Brown (2016) described information security policies as the directives, rules, and
practices that regulate how an organization handles, distributes, and protects data. Information
security policy implementation is challenging for many small businesses. Brown (2016)
concluded that information security policies are needed to protect the information, educate
employees, and provide supporting documentation for incident investigations. Brown (2016)
wrote that a robust implementation foundation is necessary to support information security
policies. According to Brown (2016), secure data controls, compliance, security budget
considerations, risk management, and security evaluation formulate the basis for adequate
information security policies.
Several researchers have reported that some employees lack an understanding of the
importance of information security and often fail to comply with information security practices
and policies (Brown, 2016). Information security guidelines can be confusing for non-IT
personnel, leaving them unsure about their responsibilities for protecting data (Brown, 2016).

Brown (2016) found that many organizations did not have clearly defined security
policies. Ensuring employees understand and comply with information security procedures
requires written policies, well-defined roles and responsibilities, and consistent enforcement.
According to Alshaikh et al. (2018), small businesses are often vulnerable to information
security attacks, risks, and threats due to inadequate security policy practices. Alshaikh et al.
(2018) wrote that many small businesses are susceptible to cybersecurity attacks due to a lack
of knowledge, resources, and time to devote to security efforts. Alshaikh et al. (2018) explored
information security policies and awareness in small businesses and found that employees were
often unaware of their organization’s information security policies and best practices.
Failure to enforce information security policies also presents a threat to data. Recent
evidence suggested that many organizations have information security policies in place;
however, they do not actively enforce them, like not having a policy (Alshaikh et al., 2018).
Small businesses should ensure all information security policies are disseminated to employees
during the onboarding process and subsequently made readily available. There should also be a
system to reinforce the company’s stance on information security best practices to remain
vigilant in protecting data. Alshaikh et al. (2018) argued that information security policies are
needed to protect information, which is increasingly becoming one of the most valuable
business assets. According to the researchers, the importance of some aspects of the
information security policy varied among different business sectors. For instance, financial
service organizations were more concerned with internal processes than the IT sector, wherein
web services management was of higher importance. Financial service organizations are
subject to numerous industries, governmental regulations, and laws, which may explain why

internal processes are more valuable that information security elements, such as executive
summaries and contacts (Alshaikh et al., 2018). Organizations that are heavily regulated may
require more security controls than companies that handle limited amounts of PII or financial
information. In sum, the findings of Alshaikh et al. (2018) indicated that the business sector,
data type, and information value impact the structure of security policies.
Adomavicius et al. (2008) conducted a case study of information security management
in small organizations and observed that many small businesses do not have formal information
security policies. The researcher’s results indicated that participating organizations often lacked
role-based access control of data. Everyone has access to everything, and that limited financial,
and personnel resources made implementing adequate information security control difficult.
Adomavicius et al. (2008) also found that access control, user privileges, and security policy
implementation are challenging for small businesses. Adomavicius et al. (2008) found that
companies do not fully implement access control policies, and employees do not always
comply with them.
Additionally, Adomavicius et al. (2008) observed that implementing information
security policies was complicated for small businesses and reported that participants felt their
organization’s security policies were too long and confusing. Alshaikh et al. (2018) observed
that many managers felt that their businesses were too small to worry about information
security, so they allowed everyone to access everything. The researchers also found that other
managers believed that being overly restrictive was easier than implementing appropriate
security controls for protecting sensitive data.

Alshaikh et al. (2018) concluded that user’s lack of awareness of information security
policies and leadership’s failure to disseminate policies could contribute to security policy
implementation challenges. Alternatively, Alshaikh et al. (2018) concluded that small
businesses should adopt specific guidelines, methods, and approaches to improve their security
posture. Implementing information security standards and procedures ensures that data
protection methods are consistent across the organization. Alshaikh et al. (2018) asserted that
organizations should develop a process for measuring information security control
effectiveness to identify areas requiring improvement. Raising awareness of information
security requires wide dissemination of concise and easily understood information security
policies.
Dombora (2019) studied information security management systems (ISMS) to
understand why the guidelines and policies of some ISMS are unenforceable. The researcher
created ISMSs quality parameters and development approaches to evaluate their enforceability.
Dombora (2019) Surveyed stakeholders first year, after they implemented the parameters and
guidelines regarding their experiences. Dombora (2019) results indicated that ISMS contained
inappropriate or cumbersome rules that created unnecessary expenditures and security gaps;
ISMS should comply with industry and legal standard, be written with well-defined roles and
responsibilities, and balance risks with resources (Dombora, 2019). Additionally, the research
results demonstrated that the overall quality of ISMS helps small business reduce costs and
maintain compliance with applicable legal and industrial regulations.
Zohrabi (2013) also ascertained that some organizations had information security
policies in place, but security managers did not articulate procedures to carry them out

properly. Managers also did not enforce information security controls, and the effectiveness of
the information security management system was not evaluated and not documented clearly.
Zohrabi (2013) studied Information Security Management (ISM) to identify and verify ISM
factors: IS policy, IS procedures, and employees. The authors found that IS policies must
clearly define IS roles, responsibilities, and objectives (Zohrabi, 2013). Zohrabi (2013)
research demonstrated needed periodic reviews of information security policies to make sure
policies are relevant to the current information security environment.
Similarly, Dombora (2019) conducted a literature review to identify the challenges and
explore current trends in information security policy compliance, which is essential to ensure
users adhere to security standards for protecting organizational assets. Dombora (2019)
examined articles on information security policy compliance, influencing compliance with
information security policies, behavioral intentions, and compliance measurements. Findings
revealed there was not enough information to identify the factors influencing the individual
choice to comply with information security policies. Dombora (2019) recommended further
research to determine the factors that influence individual-level information security policy
compliance. Dombora (2019) also discovered that employees are often unaware of information
security policies’ importance until their company experienced a data breach. Additionally,
information security policies should be reviewed and updated consistently to ensure they
address current threats (Dombora, 2019). Measurement tools can help organizations improve
information security compliance and measure the effectiveness of existing policies.

Awareness and Training Strategies
Scenario-based training with practical exercises allows users to experience real threat
with the chance to apply their newly acquired skills to their responses. Presenting users with
real phishing emails to improve information security and awareness training is the strategy
Slonka & Shrift (2016) used to evaluate the level to which phishing attacks impacted an
organization’s network.
Conversely, Slonka & Shrift (2016) argued that information security training should be
audience-specific because senior executives face different threats than junior level employees.
CSI (2022) contended that implementing strict access controls, password policies, and
employee awareness training mitigates the risk of unauthorized access to systems and phishing
campaigns.
An informal approach to training, such as a focus group or workshop setting, allows
learners to exchange ideas and learn from one another. Alshaikh et al. (2018) conducted an
information security workshop to increase cybersecurity awareness among nontechnical
employees and found that participants learned with and from one another by sharing
experiences and asking questions. When workshop attendees return to their organizations, they
can share their knowledge with colleagues, thus increasing the PU of cybersecurity awareness.
Everyone learns differently. For example, some learners prefer classroom instructions
to interact with the instructor and classmates, while others learn best through hands-on
exercises. With that in mind, CSI (2022) developed a mixed-method information security
training program to increase awareness of phishing emails. Training consisted of a combination
of instructor-led classroom training, videos, games, and text-based handouts. Although

research participants had an IT background, the variety of training approaches successfully
reduced phishing susceptibility while also increasing confidence in the ability to detect
phishing e-mails.
Another training approach involves presenting a security policy to a user, explaining the
policy’s purpose, and testing their policy knowledge through a hands-on exercise. During their
research on information security training effectiveness, Menard et al. (2017) informed users
about a security policy, then tested their knowledge using a scenario-based approach. Menard
et al. (2017) learned that when users understand a security policy’s purpose, they are more
likely to comply. Likewise, Menard et al. (2017) wrote that understanding the severity of a
threat and the likelihood of it occurring may positively influence user’s compliance behavior.
User Security Education
Small businesses are often the target of cyberattacks; however, it is possible to reduce
the risk of cyberattacks through information security awareness training and education. Phillips
and Tanner (2019) observed that some small businesses use information security awareness
and information security education synonymously, although they hold different meanings.
According to Wood (2024) a report published by the cybersecurity firm Zscaler (2024) stated
that ransomware threats are growing fastest in the healthcare industry and the educational
sectors. The number of ransomware victims whose data was listed on leak sites grew by 58%.
The report also revealed a rise in voice phishing, or vishing attacks, along with the availability
of ransomware-as-a-service, a canned product that enables would-be cybercriminals with
minimal technical skills to carry out attacks. Phillips & Tanner (2019) noted that information
awareness training centers on specific types of attacks, while information security education

focuses on policies and general concepts such as phishing. The authors also suggested that
information security awareness training be a continual process in that it is updated regularly as
new threats are constantly being found and identified. However, information security education
is not updated often and is sometimes an occasional activity.
North American Electric Reliability Corporation (NERC), a non-profit organization
created in 2006, released the Critical Infrastructure Protection (CIP) standard which provides
regulations for risk reduction and security of the power grid in North America (Halima, Islam,
& Mohammad, 2018; NERC, n.d.). The standards protect cybersecurity components of and
minimize risks associated with bulk electric systems (Halima, Islam, & Mohammad, 2018),
thus security awareness programming is required (NERC, 2020). The standard requires
quarterly training for high- and medium-impact bulk electric systems which comprise the large
transmission lines within North America (NERC, 2020). The education is designed to be
informal and includes emails, posters, computer-based delivery, presentations, and meetings
(NERC, 2020).
Cloud Computing
History of Cloud Computing
Cloud computing has developed step by step through a variety of phases which
incorporates grid computing, utility computing, application service provision, and software as a
service, etc. The Cloud computing marketplace is forecasted to exceed $241 Billion (Naik,
2023). But how did the cloud get here and where did all this started is the history of cloud
computing? Cloud computing is tied directly to the improvement of the internet and business

technology since cloud computing is the solution to the matter of how the Internet can help
improve business technology (Naik, 2023).
Phillips & Tanner (2019) suggested during a speech at MIT that computing can be sold
like a utility, just like electricity or water. It was a superb idea, but like all brilliant ideas, it was
ahead of its time, as for the next few decades, despite interest within the model, the technology
simply wasn’t ready for it (Phillips & Tanner, 2019). On the primary milestone of cloud
technology, Salesforce.com engraved the name of cloud technology. The cloud pioneered the
technique of delivering enterprise applications via a simple website. The cloud provided both
specialist and mainstream software firms to consider the use over the internet. The next
development by Amazon’s Web Service (AWS) provided cloud-oriented services inclusive of
storage, computing power and human intelligence through Amazon Mechanical Turk. Amazon
launches their EC2 (Elastic Compute Cloud), a commercial web service that allows small
organizations and sole proprietors to rent computers on which they run their computer
applications (W3schools, 2019).
EC2/S3 became the first accessible cloud technology infrastructure service. Google
Apps also launched their platform to provide cloud computing enterprise applications. Google
and others started to offer browser-based applications via Google apps and other app services`.
Then came Microsoft’s Azure, both Microsoft and Google deliver services in a way that is
reliable and easy to consume (W3schools, 2019).
Overview of Cloud Computing
According to Mell & Grance (2011) of the NIST, cloud computing is an evolving
paradigm. Vaquero et al. (2008) also claimed that cloud computing is still being developed into

the following trends like grid computing. Many opportunities and challenges have been cited
regarding the technology as companies have slowly adopted the idea of whether to transition
their technology functions to the cloud (Armbrust et al., 2010). Justifying the decision to invest
in IT is of high strategic importance for many businesses in the 21st century has become more
complex because of constant innovations in the IT landscape (Adomavicius et al., 2008).
According to Durkee (2010), cloud computing is positioned to become the next time
sharing delivering shared infrastructure service to enterprises. Durkee (2010) argued that high
computing infrastructure costs and specialized skills needed to sustain the IT operations within
the business were the primary forces driving timesharing initiatives 30 years ago. He also
claimed that these same forces are propelling the increased demand for cloud computing in the
21st century. According to Durkee (2010), the major attributes of cloud computing that are
satisfying the needs of businesses include on-demand access, elasticity, pay-per-use,
connectivity, resource pooling, abstracted infrastructure, and little or no upfront financial
commitment.
Several articulations of cloud computing as commoditization of hardware, software and
business processes have been made (Armbrust et al., 2010; Bardhan et al., 2010; Greenberg et
al., 2011). Bardhan et al. (2010) as well as Brynjolfsson et al. (2010) viewed computing-
asutility as a business model. They compared cloud computing with other utilities such as
electrical grids and water supply. Though the utility model has a great analogy and clarity on
the business paradigm supporting a shift to service orientation, there is an urgent need to
understand the real opportunities and challenges of cloud computing (Brynjolfsson et al.). This
study will seek to identify SLA attributes for cloud computing that will impact the behavioral

intention to accept cloud computing services. What follows in this review will present
definitions of cloud computing, describe the benefits of cloud computing, briefly describe
SLAs in relation to the cloud, and highlight some concerns that may not be able to provide the
proper protection to secure personal data in the event of a breach in a cloud computing
environment.
Definitions of Cloud Computing
In the search for an all-encompassing definition of cloud computing, several
technologies were reviewed for similarities and relationship to cloud computing.
Serviceoriented computing, utility computing and grid computing are three primary
technologies that are compared with cloud computing (Armbrust et al., 2010). Technology has
similar goals that are worth noting, cloud computing seems to be taking on definitions of its
own. Bundled with these definitions, is the fact that the elaborated benefits proclaimed by
many publications are accompanied by major concerns that could avert the acceptance of cloud
computing on a wide scale.
In 2008, Vaquero et al. declared that cloud computing continues to develop but its
definition remains unclear. Over the last five years, however, several definitions of cloud
computing have surfaced (Armbrust et al., 2010). Mell & Grance (2011) provided a
comprehensive definition of cloud computing for the NIST. They stated that: Cloud computing
is a model for enabling ubiquitous, convenient, on-demand network access to a shared pool of
configurable computing resources (e.g., networks, servers, storage, applications, and services)
that can be rapidly provisioned and released with minimal management effort or service

provider interaction. This cloud model promotes availability and is composed of five essential
characteristics, three service models, and four deployment models. (p. 2)
The essential features defined in the NIST definition included on-demand self-service,
broad network access, resource pooling, rapid elasticity, and measured service. SaaS, PaaS, and
IaaS are the three service models identified in this definition. The deployment models include
private, community, public, and hybrid clouds. Dillon et al. (2010) used this same definition
proposed by the NIST but also included an additional deployment model called data storage as
a service (Cloudthat.com, 2021).
Vaquero et al. (2008) also sought to give an all-inclusive definition of cloud computing
which also considers many of the core features of the definition put forward by Mell & Grance
(2011). Vaquero et al. outlined that: Clouds are a large pool of easily usable and accessible
virtualized resources (such as hardware, development platforms and/or services). These
resources can be dynamically reconfigured to adjust to a variable load (scale), allowing also for
optimum resource utilization. This pool of resources is typically exploited by a pay-per-use
model in which guarantees are offered by the Infrastructure Provider by means of customized
SLAs. (p. 51)
While Vaquero et al. (2008) implicitly included some of the primary features of cloud
computing highlighted by Mell & Grance (2011), they also looked at the cloud in relation to
grid computing. Armbrust et al. (2010), Dillon et al. (2010), as well as Vaquero et al. (2008)
argued that cloud computing and grid computing are two different concepts, though they share
similar objectives to provide technology services at lower costs and ensure availability of
services through the utilization of excess capacity in existing data centers. Vaquero et al.

(2008) further argued that virtualization forms the basis of cloud computing as it provides the
capability for OnDemand sharing of resources and security by isolation.
Another essential feature of the definition by Vaquero et al. (2008) is the inclusion of
SLAs. Vaquero et al. (2008) asserted that SLAs are critical to cloud computing as this enables
enforcement to meet the quality and level of service stipulated in the contractual agreements
between service providers and clients. Armbrust et al. (2010) argued that “cloud computing
refers to both the applications delivered as services over the Internet and the hardware and
systems software in the data centers that provide those services” (p. 50). Mell and Grance
(2011) as well as Vaquero et al. (2008) emphasized the service models SaaS, IaaS, and PaaS as
being important considerations when defining cloud computing.
Armbrust et al. (2010) however, believed that SaaS and utility computing are the core
for the definition of cloud computing. Armbrust et al. (2010) argued that the data center
hardware and software define the cloud. Armbrust et al. (2010) believed that the size of the
data center matters when determining a cloud. Armbrust et al. (2010) disagreed that some
private clouds meet the requirements of cloud computing.
Public clouds are those that offer a pay-as-you-go service to the general public while
private clouds are operated by businesses and are usually internal data centers providing
computing facilities to the entity (Armbrust et al., 2010). According to Armbrust et al. (2010)
cloud computing does not include small or medium sized data centers that are operated
privately. The data centers must be large enough to benefit from the economies of scale that the
cloud paradigm is projecting. Armbrust et al. (2010) therefore, did not include private clouds in

the definition of cloud computing because they believed private clouds are not large enough to
be classified as such.
Leavitt (2009) claimed that cloud computing is relatively new but argued that it will
change at a rapid pace as it advances, and larger companies begin to exploit and adopt cloud
services for critical applications. With that in mind, the evolution may help determine the
features of cloud computing and further refine the definition of the cloud.
Benefits of Cloud Computing
Cloud computing is rapidly becoming a revolutionary technological innovation (Dillon
et al., 2010). Some of the benefits that are being used to promote the cloud include elasticity,
risks transfer, and conversion of capital expenditure (CapEx) to operating expenses (OpEx) on
a payas-you-use basis (Armbrust et al., 2010; Dillon et al., 2010).
The ability of cloud services to provide short-term usage on demand through what is
called elasticity is one of the merits highlighted by Armbrust et al. (2010). Armbrust et al.
(2010) argued that consumers of cloud services can scale up or down the demand for
computing resources. This makes the cloud elastic due to the possible on-demand resizing that
can be self-provisioned (Armbrust et al., 2010); Mell & Grance, 2011). This type of resizing,
according to Armbrust et al. (2010) transfers the risk of under or over utilization of technology.
Armbrust et al. (2010) highlighted this as one of the economic benefits of using the cloud.
Cloud vendors market the technology as OpEx instead of CapEx (Armbrust et al.,
2010). There are no upfront costs in some instances. The consumer only needs to pay as they
use the service. This according to Leavitt (2009) should result in cost savings to the consumer
and is included as another benefit of cloud computing. Leavitt (2009) claimed that availability,

application integration, helpdesk support, and flexibility are other testimonies of the benefits of
cloud computing.
Leavitt (2009) argued that the cloud is operated by large service providers with several
huge equipment and many levels of redundancies which will provide high availability for cloud
customers. In addition, with nonproprietary protocols such as simple object access protocol
(SOAP), Web services description language (WSDL), and extensible mark-up language
(XML), the cloud provides a platform that encourages support for legacy applications and
integration of various types of systems. Leavitt (2009) also claimed that some cloud vendors
provide flexibility to users through modest or no contracts that give the user the added
advantage of obtaining more resources when required (Khan et al., 2019).
Concerns With Cloud Computing
Amongst the benefits, there are several concerns with cloud computing (Armbrust et al.,
2010). Armbrust et al. (2010) as well as the “NIST Cloud Computing Program” have been very
explicit in their views about the issues that could impact the adoption of this innovation.
Some of the issues highlighted by prior research include data security, reliability, definition of
SLAs, cloud lock-in, cost of communication, regulatory audit requirements, software licensing,
portability, interoperability, and access control (Armbrust et al., 2010;). The Information
Systems Audit and Control Association (ISACA) and IT Governance Institute (ITGI) in their
2015 Global Status Report on Governance of Enterprise IT (GEIT) disclosed that information
security concerns are the primary reasons cited by enterprises for not using cloud computing
(ISACA and ITGI, 2015). Edwards (2009) also outlined that while companies will realize

useful benefits from cloud applications, there are still major issues with information security
that must be addressed.
Information security in the cloud is one of the most publicized concerns affecting higher
acceptance of the cloud computing paradigm (Dillon et al., 2010). According to Dillon et al.
(2010) the nature of the cloud increases the issues with information security, such as trust
management and policy integration, secure service management, privacy, and data protection.
Dillon et al. (2010) argued that for cloud computing to be successful, the information security
issues must be resolved. Dillon et al. (2010) argued that third parties managing the security of
data and applications in the cloud may create further challenges with information security.
With that in mind, Dillon et al. (2010) emphasized that due to the multi-tenancy nature of the
cloud, the sharing of physical resources in this environment is also viewed as a risk to the
services hosted in the cloud.
Dillon et al. (2010) expressed concerns about the confidentiality, privacy of data, and
information that will be processed or stored in the clouds (Armbrust et al., 2010; Dillon et al.,
2010; Hayes, 2008; Leavitt, 2009). These concerns include malicious attacks on the cloud,
release of data due to a third party being subpoenaed thus creating confidentiality and privacy
issues, multi-tenancy approach, data loss, and lack of control over the infrastructure that hosts
the data and systems. Dillon et al. (2010), Hayes (2008) as well as Leavitt (2009) also
highlighted the concern about reliability. Dillon et al. (2010), Hayes (2008), & Leavitt (2009)
also claimed that because the cloud is solely dependent on Internet technologies, there could be
reliability, performance, and latency problems. Armbrust et al. (2010) believed there could be
availability and business continuity issues. Dillon et al. (2010), Hayes (2008), & Leavitt (2009)

argued that though the cloud itself may have some amount of internal redundancy, the CSP
may still be a single point of failure. The SLA in this regard is expected to set the minimum
level of service the cloud user is expected to receive from the CSP. With that in mind, SLAs
developed for cloud computing seemed to have been lacking components that would make
them more appropriate (Durkee, 2010). Dillon et al. (2010) claimed that business users of the
cloud may not adopt cloud computing services if privacy and security guarantees are not
provided by the CSPs and enforced stated in the cloud SLAs.
Armbrust et al. (2010) & Smith (2009) also argued that there are questions about
confidentiality and audit requirements for information and systems hosted in the clouds. Kant
(2009) claimed that one of the considerations when thinking about hosting enterprise
applications in the cloud is data management and IT regulatory compliance obligations. Kant
(2009) declared how some countries prohibited businesses from using the cloud to store several
categories of data. Regional legislation must be considered in some cases when considering
cloud computing. Hoberman (2010) also claimed that the cloud does not make data
management easier, and that cloud computing will not resolve data governance and
management issues. Hoberman (2010) suggested that cloud computing is not for everyone.
Smith (2009) argued that there are many companies that are not willing to host their
internal data external to their own company. Smith (2009) theory may be partly due to the
concern that data may end up being cohosted with other companies‟ applications. For many
companies this is not allowed, especially when it is either not clear or known what processes
are being executed by the cohosted applications. This detail is usually not specified in the

SLAs or other documents provided to the user. Dillon et al. (2010) also supports the view that
the coexistence of data generates greater information security risks to companies using cloud
services. He outlined that one of the attributes of the cloud is that several customers‟ data and
applications may coexist. According to Dillon et al. (2010) who claimed, if one company is a
subject of virus or hack attacks, this will compromise the integrity and availability of data for
other companies in the same environment.
Dillon et al. (2010) argued that the cloud user has little control over how the provider
secures the infrastructure. He argued that the user will only need to assess the data security
controls based on what the provider will disclose about its procedures. This creates some
uncertainty about what is being delivered. Dillon et al. (2010) said developers may need to
implement additional measures to guard against users of the same cloud infrastructure
intercepting transmissions within the network.
An important observation made by Dillon et al. (2010) is that companies still seemed to
be keeping their core systems in-house. Dillon et al. (2010) claimed the main functions that are
being migrated to the cloud include basic IT management and personal applications. Dillon et
al. (2010) also argued that storage and collaborative applications are expected to be the
principal users of the cloud, in the near future. Smith (2009) emphasized that there are still
bugs in cloud computing that still need to be resolved. Dillon et al. (2010) claimed there have
been instances when an entire cloud is made unavailable for hours or days which put the client
in an unfortunate position. Amazon S3 and Google services were unavailable for several hours
which was unexpected placing their clients in a helpless position (Yan, 2010). Yan also agreed

that other security issues relating to data transfer bottlenecks and legal jurisdiction exists which
could create problems for cloud computing.
Brynjolfsson et al. (2010) claimed that shared infrastructure such as cloud computing
comes with its own risk and concerns (Brynjolfsson et al., 2010). Cloud computing allows
limited control over the data and the management of information security to the client
(Brynjolfsson et al., 2010). Smith (2009) professed that companies are concerned about the
physical location of their data being stored in the cloud. Brynjolfsson et al. (2010) argued that
cloud computing will reduce control for the users and will present new information security
risks not experienced by countertypes of cloud computing models. Cloud computing customer
data, trade secrets, and classified government information are usually subject to rigorous
requirements and auditing standards for regulatory and law enforcement purposes.
Cloud computing has been one of the most important developments in IT since the past
60 years. Brynjolfsson et al. (2010) claimed that relinquishing control of critical information
assets to CSPs creates considerable legal issues. This includes access, availability, and
performance; customization and integration with existing technologies; compliance with
regulatory agreements; security of the information; and switching from one CSP to another.
Dillon et al. (2010) argued that public clouds provide very little negotiating power relating to
specific provisions such as limitations to the location of the data or the use of subcontractors.
Dillon et al. (2010) argued that data will be subject to the laws of the environment where the
data is located which may not necessarily be what the clients require.
Communication cost is another concern highlighted (Dillon et al., 2010; Leavitt, 2009).
Leavitt (2009) argued that due to the intensive reliance on the internet for access to the cloud,

increased bandwidth may be required which could significantly drive up the cost of
communication (Leavitt, 2009). This is especially so in cases where there are large databases to
access through the clouds (Leavitt, 2009). It was also argued that bottlenecks could be created
due to low-speed connections to the cloud and high traffic in some instances (Armbrust et al.,
2010). Initial uploads could also be a serious problem as huge volumes of data are expected to
be migrated to cloud computing infrastructures. This could result in increased transaction costs
for cloud computing. When this happens, the intent to adopt cloud computing may be adversely
impacted. Several researchers have investigated this issue in the past twenty years, but this
research topic has not been explored in this way. There may be no viable solutions available for
protecting PII in a public cloud computing environment. The IT industry demand has adopted
cloud services despite the security concerns; however, security challenges are on the horizon
due to ITPMs may lack viable solutions to mitigate the frequent occurrences of information
security breaches (Devi et al., 2020, March). The IT industry has a greater understanding about
cloud technology and how the Cloud delivers IT services to user; although there are increased
cyber security concerns associated with the delivery of cloud computing services that exist in
many cloud supply chain environments (Akinola et al., 2017). Information
Theory is one of the few scientific fields fortunate enough to have an identifiable beginning
(Strawn, 2014). The story of the evolution and how the development from a single idea
influenced the perspective about the vast possibilities to expand communication in the industry,
and how it helped change everyone’s life is an interesting story (Strawn, 2014).

Summary and Conclusion
Akinola et al. (2017) claimed that previous studies about cloud risk and risk
assessments failed to analyze the robust nature of cloud technology and the effects of supply
chain risks in cloud computing. A gap was identified in the literature that revealed a lack of
consideration for cloud supply chain investigations (Akinola et al., 2017). The lack of
accountability for monitoring and managing data in a cloud computing environment is an
essential concern, which impacts the end user’s trust (Jaatun et al., 2018). The intent of Chapter
2 revealed how the research has clearly explored the issues relating to protecting end user
personal data, and it has raised a global awareness about the issues involved with managing
increased security challenges in a cloud computing environment. The summary and
conclusions have concisely summarized major themes in literature. I summarized what was
known as well as what was not known in the discipline related to the topic of the study. I also
provided transitional material to connect the gap in the literature described in Chapter 2.
Chapter 3 reveals consistency with the Research Methodology, strategy and includes a
detailed roadmap that identifies the Research design and rationale involving the data collection
methodology. The examination of this study may identify a lack of IT subject matter expert
knowledge is needed and concludes that there may be no viable solution available for
protecting PII in a public facing cloud computing environment? The present study reveals how
public facing cloud computing environment fails to properly protect PII data as well as affects
other data and places data in risky situations.
Chapter 3: Research Method

Chapter 3 consists of the research tradition and the rationale for the chosen tradition.
The strategy for the role of the researcher consists of defining and explaining my role as the
observer, participant, or observer-participant. The strategy I used for the methodology
consisted of describing details in sufficient depth so that other researchers could replicate the
study. Despite decreased cost, reduced resources, and advances in performance when migrating
to the cloud solution, the question that remains for organizational leaders considering a cloud
solution will be how to protect personal data and sensitive information and mitigate loss of
control when migrating to the cloud (Das & Dayal, 2016). The primary issue around data
shared with the CSP is the method for protecting shared data and developing a cloud
computing security framework (Das & Dayal, 2016).
Research Design and Rationale
The purpose of this generic qualitative study was used to explore how 33 participants
who are IT security matter experts perceive the desirability, feasibility, and importance of
determining a viable solution that may provide protection for PII in a public cloud computing
environment (see Patala et al., 2018). The study may find that there are no viable solutions
available for protecting PII in a public cloud computing environment. ITPMs may lack viable
solutions to mitigate the frequent occurrences of information security data breaches. I explored
security issues relating to computer breaches and network concerns associated with the security
of cloud computing (see Akinola et al., 2017). The IT industry has adopted cloud services
despite the security concerns; however, security challenges are consistently increasing in the
21st century due to ITPMs lacking the knowledge to create a viable solution to mitigate the
frequent occurrences of information security breaches (Patala et al., 2018).

As the researcher, I conducted the initial field test, as a subject matter expert, to review
the appropriateness of the content for the survey questions that I intended to use in the study.
After my review, I launched the survey instrument to receive responses to my study. The
survey captured SME in the security field who volunteered to participate in the study. I
collected the subject matter experts’ perspectives which established a foundation for future
research by exposing a gap in the field. There was a logical connection between the qualitative
approach, the conceptual framework, and the exploratory research design that aligned with the
problem. The use of encryption is necessary to protect and secure all types of PII data. The
focus was on identifying the problem, solicit participation, observe the data collection method,
and reveal the findings as a result of the repeated issues in the security industry (see Ahmad
and Waheed, 2015; Nayak et al., 2017; Patala et al., 2018).
Role of the Researcher
The central concept of the study revealed that the selected theories such as information
theory and general security theory are related to the present study because they identified that
information security professionals are the primary concern for increased security issues and the
primary reason for constant network vulnerabilities creeping onto the network (Tiwari, 2017).
The rationale for the chosen tradition revealed why I chose this method and how it relates to
the primary concerns of the study. The following research questions were the basis for the
study:
RQ1: What are the most common security issues with protecting public data in a cloud
computing environment?

RQ2: What strategies are available to help information technology professionals
determine the desirability of a viable solution that may provide the necessary protection for
personally identifiable information (PII) data in a public cloud computing environment?
RQ3: What is the importance of a viable solution that may provide the necessary
protection for PII data in a public-sector cloud computing environment?
Data was collected via a SurveyMonkey questionnaire until data saturation was
reached. Data from each RQ were analyzed to identify categories and themes. The role of the
qualitative researcher was to maintain credibility, dependability, and data transferability that
reflects the perspectives of the participants (Bahrami et al., 2016). Researchers can make
mistakes that may threaten the validity, reliability, or integrity of the study (Bahrami et al.,
2016). As the researcher, I remained mindful to not develop an influential behavior or mindset
of altering the data (Clarkson University, 2024). The researcher must monitor and mitigate all
bias tendencies while conducting the research (Bahrami et al., 2016). Researchers must develop
the competence to implement the specialized skill correctly (Bahrami et al., 2016). A
researcher must recognize biased conduct that may occur and be prepared to address an issue
immediately by communicating with the research participant to mitigate and solve the issue, if
possible. By utilizing the SurveyMonkey questionnaire approach, and knowing the data
gathered from each participant would be unanimous, the researcher had to mitigate all bias
tendencies.
There is a possibility of a biased nature that can influence the study’s outcome.
Competence and skill are required at all the following stages: explaining the study without bias
by using the ability to effectively communicate, seeking participants for the study, making

appropriate choices to select the right platform for the field observation, handling and
collecting data, analyzing and interpreting the data per the design, developing the artifacts, and
presenting the findings (Bahrami et al., 2016). Researchers must recognize limitations and bias
tendencies that develop in the study to protect the credibility of the data and maintain the
integrity of the results. A biased nature can be avoided by the researcher when analyzing the
study’s results, if the interpretation does not appear to be realistic. The researcher must remain
trustworthy during the data collection process while handling participant data to avoid biased
activity. These concerns were important when conducting a self-evaluation on the role as the
researcher in various elements within the qualitative study (Bahrami et al., 2016).
Methodology
Exploratory Qualitative Analysis
Exploratory qualitative data analysis is a process used when investigating a problem
that is not clearly defined. The data analysis method offers a technique that is flexible and
compatible with many approaches to qualitative research, and a generic qualitative analysis
(Ahmad and Waheed, 2015). The subject matter expert is an information security professional
hired to manage and prevent network attacks and enforce communication security control to
the user community. The sample size will be from 05 to 10 participants. I collected data from
the population of public cloud computing users in the IT industry. Participants were expected
to be initiated from a a particular designated participant pool that would meet a specific
criterion to be eligible to participate in the study. Each participant would have to confirm the
following information: currently working in the security industry, be employed in a security
position for at least 3 years, be considered as a subject matter expert (SMEs), not be a

contractor, and be willing to answer personal identifiable demographic questions related to age,
gender, job title, and education level. When a participant clicks my online survey link to
participate in my study, the very first thing that they have to answer is five screening questions.
These questions are tied to my inclusion criteria, so the participants need to answer “yes”, to
indicate that they fit my inclusion criteria and are part of my target population before they can
move on to the informed consent form.
Each volunteer cannot participate in the study if they were affiliated with a government
agency or the same work location or government agency that I personally work for which may
create a conflict of interest or power differentials. An announcement was posted on the
participant pool communication board, prepared by the IRB. l provided an introduction
statement about my research study when I ask for their participation and include a statement
about the informed consent form and the terms that apply to preserving their private
information. I made it clear in the announcement that there will be no forced intentions,
personal relationships, or other possible related risks to eliminate, and prevent a bias
relationship. I was prepared to collect the data until the relationship between saturation and
sample size reaches a recognizable saturation point. There were no plans to offer incentives to
research participants for their involvement in the study. In similarity, Thompson (2020) used a
qualitative data analysis in his study to observe prior studies of other researchers that classified
insider data breaches based on many problems and different factors such as intent, motive,
technical expertise, or a combination. The qualitative data analysis used in this study was a
generic approach to analyzing data protection problems, people’s opinions, and reports that
came from many individual interpretations (Ahmad & Waheed, 2015).

Phase 1: Mapping the Selected Data Sources
Reviewed and familiarized myself with the data collected from the first participant
questionnaires). After reviewing the data gathered from each participant, I highlight intuitively
any sentences, phrases, or paragraphs that appear to be meaningful (Ahmad & Waheed, 2015).
The second task involved mapping the spectrum of multidisciplinary literature regarding the
phenomenon in question. This process included identifying text types and other sources:
ensuring the data was carried over correctly, such as existing empirical data and practices. The
main idea about the data collection process should be comprehensive and ensure data validity
(International Journal of Qualitative Methods, 2009; Morse et al., 2002).
Phase 2: Extensive Reading and Categorizing of the Selected Data
The aim in the second phase was to read the selected data and categorize the data by
discipline and organize the data by the scale of importance and power within each discipline.
This process maximized effectiveness and ensured the effective representation of each
discipline. I reviewed the highlighted data and used the research question to decide if the
highlighted data was related to the question. During the data collection process some
information in the questionnaire was not related to the questions, with that in mind, the
researcher must be mindful not become bias during this stage in the process (Braun et al.,
2019).
Phase 3: Identifying and Naming Concepts
The aim in the third phase was to read and reread the selected data and discover
concepts (Glaser and Strauss, 1967; Stubbs, 2019). The findings list numerous competing and
sometimes contradictory concepts. Generally, this method allows concepts to emerge from

literature. Morse et al. (2002) suggested that “qualitative inquiry that commences with the
concept, rather than the phenomenon itself, is subject to violating the tenet of induction, thus is
exposed to particular threats of invalidity” (Morse et al., 2002, p. 68-73). I eliminated all
highlighted data that was not related to the question; but all unrelated data will be kept for
historical purposes to create a data repository such that I may come back and reevaluate the
data in the future (Braun et al., 2019).
Phase 4: Deconstructing and Categorizing the Concepts
The aim of the fourth phase was to deconstruct each concept by taking each set of data
and code or name the data (Braun et al., 2019, p. 86) and identify the main attributes,
characteristics, assumptions, and role; and, subsequently, to organize and categorize the
concepts according to their features and ontological, epistemological, and methodological role.
The result of this phase is a table that includes four columns. The first column includes the
names of the concepts; the second column includes a description of each concept; the third
column categorizes each concept according to its ontological, epistemological, or
methodological role; and the fourth column presents the references for each concept.
Phase 5: Integrating Concepts
The aim in the fifth phase was to integrate and group together concepts that have
similarities. I clustered the sets of data that were related or connected and then started
developing patterns (Braun et al., 2019). This phase reduces the number of concepts drastically
and allowed the researcher to reduce the groups into a reasonable number of concepts.

Phase 6: Synthesis, Resynthesis, and Making It All Make Sense
The aim in the sixth phase was to synthesize concepts into a conceptual framework. The
researcher must be open, tolerant, and flexible with the theorization process and the emerging
new theory. This iterative process includes repetitive synthesis and resynthesis until the
researcher recognizes a general conceptual framework that makes sense. To complete this
process for the first participant’s data. I coded and clustered the first participants data and as
each subsequent participant’s data was analyzed, they were compared to the previously
analyzed data. Throughout this process, each participant’s data was reviewed and analyzed, and
the researcher compared the data being analyzed with the data that has been previously
collected in the study. The comparison emerged from the analysis (Braun et al., 2019).
Researchers should know how to build their conceptual frameworks. As Braun et al. (2019)
suggested, researchers who use qualitative methods “need to know how they are constructing
‘theory’ as the analysis proceeds, because that construction will inevitably influence and
constrain data collection, data reduction, and the drawing and verification of conclusions” (p.
434).
Phase 7: Confirming the Conceptual Framework
The aim in the seventh phase was to validate the conceptual framework. Throughout
this entire process, data that corresponds to a specific pattern was identified and placed with the
corresponding patterns and direct quotes were taken from the data (Braun et al., 2019).
Does the proposed framework and its concepts make sense not only to the researcher but also
to other scholars and practitioners? Does the framework present a reasonable theory for
scholars studying the phenomenon from different disciplines? A conceptual framework process

starts with the researcher, who then seeks confirmation among “outsiders”. Presenting an
evolving theory at a conference, a seminar, or some other type of academic framework
provides an excellent opportunity for researchers to discuss and receive feedback (International
Journal of Qualitative Methods, 2009).
Phase 8: Rethinking the Conceptual Framework
Throughout the process, I took all patterns and looked for the emergence of overarching
themes. This process involved combining and clustering the related patterns into themes
(Braun et al., 2019).
Phase 9: Analyze and Group Data into Patterns
Patterns and themes may tend to shift and change throughout the process of analysis
(Braun et al., 2019).
Phase 10: Arrange the Themes to Support the Patterns
After all the data has been analyzed, I arranged the themes to correspond with the
supporting patterns. The patterns were used to elucidate the themes (Braun et al., 2019).
Phase 11: Provide Detailed Analysis of the Scope and Substance of Each Theme
For each theme, I prepared a detailed analysis describing the scope and substance of
each theme (Braun et al., 2019).
Phase 12: Describe and Provide Clarification Quotes That Support Each Pattern
Each pattern should be described and elucidated by supporting quotes from the data
(Braun et al., 2019).

Phase 13: Combine Data and Summarize Questions Under Review
The data was synthesized together to form composite synthesis of the question under
inquiry (Braun et al., 2019). A theory or a conceptual framework representing a
multidisciplinary phenomenon was dynamic and may be revised according to new insights,
comments, and literature. Conceptual frameworks provide understanding, in addition to, the
theory should make sense for those disciplines and enlarge their theoretical perspective on the
specific phenomenon in question (Braun et al., 2019).
The theories and/or concepts that ground this study include Nayak et al. (2017) theory
of development, focusing on compliance, specifically on the concepts of encryption and
decryption algorithm are highly necessary to protect and secure all types of PII documentation,
but the focus should be applied to develop tougher security standards and measure privacy
protection.
The logical connections between the framework presented and my study approach
include Moody et al., (2018) theory that was developed and built around behavioral research
had produced different models to explain cyber security strategy and strict standards. This
proposes a unified model, called the combined approaches of cyber security policy compliance
(CACSPC), that joins certain fundamentals across these existing theories that were tested and
analyzed by the preliminary empirical support for the methodology.
For my planned research design, I created an online questionnaire through
SurveyMonkey’s platform, as the data collection tool to capture the data from 5 to 10 cloud
computing information security subject matter experts. The research questions were developed
from several known issues that I recognized occurred in the security industry. My involvement

with the industry has provided me with the questions that will be analyzed and responded to
from the research questions. These subject matter experts will reveal their opinions towards a
viable solution for the future that provides the necessary protection for public data in the cloud
computing environment. The planned research design provided a data analysis using a known
design technique as the exploratory qualitative data analysis. The development of the research
questions came about from a series of recognized network issues that occurred on the network
in my place of employment. My involvement with the IT industry provided firsthand
information about the issues and initiated the research questions that I analyzed from each
participant. The qualitative data analysis involved searching across a data set coordinated
between several SurveyMonkey questionnaires and/or a range of text to find repeated patterns
and themes (Braun et al., 2019). My data collection instrument and source consisted of a
combination of methods used to gather the participants and collect data: such as, an observation
sheet to use for the data cleanup, a method used to code the list of participants, survey artifacts,
archived data, and other kinds of data collection methods such as a word clouds, word trees,
etc. were used to collect data from the research participants (Pezalla et al., 2012).
The research design is a process used to conduct an analysis of qualitative data. It offers
a method of data analysis that is flexible and compatible with many approaches to qualitative
research and mix methodology, in a particular generic qualitative analysis (Braun et al., 2019).
Exploratory qualitative data analysis is a general approach to analyzing problems,
people’s opinions, and reports that may form the basis for many kinds of qualitative
interpretation (Braun et al., 2019).

The research design used was an exploratory qualitative data analysis of the essential
elements in qualitative research and when correctly applied can enable the readers of
qualitative work to judge it as respectable research. The initial data collected started the
analysis. Each subsequent participant’s data was collected and analyzed, then compared to the
previously analyzed data. The analysis moved back and forth between current data that had
been coded and clusters into patterns. These patterns/ themes changed and developed as the
analysis continued throughout the process until the data collected reached a saturation point
that followed the below guidelines, step by step (Braun et al., 2019).
Participant Selection Logic
The participants involved in this qualitative research study included cybersecurity
specialists of all levels who may have either architected, engineered, built or maintained a
secured public cloud computing environment. Each participant who volunteered through the
SurveyMonkey approach was considered as a unanimous individual. Once the participant
agreed to be a part of the research study, the questionnaire was precoordinated and prearranged
through the SurveyMonkey platform. The researcher used a SurveyMonkey questionnaire
approach to meet a specific criterion to be eligible to participate in the study. The data
collection process continued until the relationship between saturation and sample size reached
a recognizable saturation point. The researcher made sure that each participant completed the
inclusion criteria before moving forward to begin the survey.
Instrumentation
In a qualitative research study, the researcher is the instrument (Pezalla et al., 2012).

One of the primary issues in a qualitative research study is confirming the researcher as an
instrument of data collection. As the researcher, it’s important to ensure each citation receives
proper credit even though the information may be slightly reworded to eliminate plagiarism
and allow the researcher to use the information in the study. If the researcher does not have
enough validity in the data collection process, the results of the study will also not be cited
(Bahrami et al., 2016).
Field Test
A field test was conducted by requesting three technical cloud subject matter experts in
the field of information security to review the draft surveys and questionnaires. The reason for
using a survey style technique was to collect information about a specific group of individuals
by asking them questions and analyze the results. Each subject matter expert was contacted
through the SurveyMonkey online questionnaire platform to review the draft questionnaires
and determine specifically if the questions were understood by the industry expert participant.
A valid field test provided evidence by allowing each subject matter expert to verify, provide
comments for possible changes to the questionnaire which validated the initiation of data
collection.
Procedures for Recruitment, Participant and Data Collection
The initial research involved collecting three technical cloud subject matter experts in
the field of information security to review the draft SurveyMonkey questionnaire. Each
participant response was received through the SurveyMonkey platform. An initial attempt was
made to recruit other participants from the Walden University participant pool of student
volunteers posted through an internal announcement. After two weeks, the announcement was

removed due to student participation not being received. The data collected from the
SurveyMonkey platform produced thirty-three IT security participants that I used for this study.
The data collected was reviewed several times and analyzed until the data reached a saturation
point. The study did not include any foreign locations, as international locations were a
potential limitation of the study. The estimated sample size came from 33 U.S. based cloud
security experts and experienced IT managers who adopted and were involved with cloud
services. Saturation occurred when responses to the questions became repetitive, and when
variation between the rounds for the ranked issues among the experts became minimal.
The study involved using purposeful sampling to provide an appropriate sample for the study.
Participant Selection
The selected knowledgeable individuals came from the SurveyMonkey’s platform
which provided several unanimous cloud computing IT experts (expert IT managers who had
adopted cloud computing and cloud computing providers) who responded to a series of
questions, with the initial rounds consisting of open-ended questions. The field test
confirmation of 3 participants that were also IT subject matter experts who adopted cloud
computing experience reviewed the questions to determine if the questions were clear to
understand. The final examination resulted in 5 to 10 participants that were IT Professionals
who determined, the study was trusted. Each participant responded to the questions with trusted
responses that were used for this study.
The first round of the research involved identifying problems and aggregating data for
subsequent rounds (Zohrabi, 2013). The second round of the research study consisted of
identifying data collected from 5 to 10 experts (expert IT managers who had adopted cloud

computing and cloud computing providers) by individually ranking the order of perceived
importance of the security issues identified in the first round. The third and subsequent round
consisted of subject matter experts reranking the problems identified in the aggregated
response, with the process ending when the variation between the rounds for the ranked issues
was minimal.
Recruitment of the participants involved the following steps:
1. The initial approach started with the idea of recruiting participants from the Walden
university student participant pool with an internal posted announcement. This
method was not useful in attracting participants in the study, so the announcement
was cancelled after two weeks due to no student responses being received during
that time period. The announcement explained the nature of the study and the use of
the informed consent form, but the announcement did not attract any participants.
2. The recruitment effort was transitioned to the SurveyMonkey platform, that
provided the needed participation using the SurveyMonkey online questionnaire
approach.
3. Contacting each IT security expert via email who adopted cloud services about
participating in the study was not necessary because of the SurveyMonkey platform
that provided the online questionnaire approach. E-mail communication would have
included the researcher’s contact information and explained the nature of the study
and the use of the informed concept form, if I had used this approach.
4. Contacting each subject matter expert via email who worked for major CSPs to
discuss the study was not necessary because of the SurveyMonkey questionnaire

approach. E-mail communication would have included the researcher’s contact
information and explained the nature of the study and the use of the informed
concept form, if I had used this approach.
5. Experts who worked for major CSPs and IT security managers who adopted cloud
computing services and had interest in the study and may had questions regarding
raw data retention and dataset confidentiality as well as logging of all recruitment,
data collection, and data management steps. If the participants require copies of the
originally submitted IRB materials, they may request them from the Institutional
Review Board.
6. Participants were provided through the SurveyMonkey platform. an informed
consent form from the researcher to screen all potential participants for eligibility
(i.e., to ensure they worked for CSPs or were experienced IT managers who had
adopted cloud computing services and were in the United States). The researcher
built an exit criterion into the SurveyMonkey questionnaire for the participants to
answer to advance forward to answer the survey questions. If the participant had an
interest in joining the study, they were guided to advance to the survey questions. If
the participants did not agree to participate in the survey, the screening question
would guide the participant to end the survey. The informed consent form had a
button to click on for the electronic signatures before the survey began; If potential
participants did not agree, the process would terminate, and the survey would thank
them for their time. The method of screening each individual repeated until all

participants had agreed to volunteer in the study or disagreed to participate in the
study.
Protection of Participants
The researcher extracted the responses from each questionnaire received from each
participant from the rounds of the research study and stored them in a secure location to protect
the privacy and confidentiality of the participants. The process involves making a single master
copy of the responses and storing them with the original copy. The study involved making
multiple working copies of the responses, during the analysis process, each integration was
stored with the original and kept secured by using a secured passwords to access the data. All
survey questionnaires were shared with the dissertation committee members and other
university research reviewers upon their request.
Data Collection
Data collected through a questionnaire was the method used in this research study. The
questionnaire consisted of several questions that were typed in a definite order. The
questionnaire designed through the SurveyMonkey platform helped recruit several IT
professionals who currently work in the security industry and held an active role as a security
subject matter expert. The SurveyMonkey platform was designed to determine if the SME were
a part of the target market. The subject matter experts were expected to read the questionnaire
and then select a radio button to advance to the informed consent form. The respondents
answered each survey question on their own and then submitted the questionnaire at the end of
the survey.

Participants in the study were reminded in the informed consent form that each
individual has the right to withdraw from participating in the study at any time. These
individuals on the initial list of knowledgeable cloud computing IT experts (including expert
security professionals who have adopted cloud computing and or who work for the cloud
computing providers) will respond to a series of open-ended questions in the initial round of
this research study.
The purpose of the first-round aggregated information for subsequent rounds of the
study. The first round was created to establish the researcher’s credibility, which was crucial to
reducing participant attrition (Stewart, 2020). In the second round, each subject matter expert
was individually ranked in the order of the perceived importance of the issues identified in the
first round. The third and subsequent round consisted of the reranking of the issues identified
by the subject matter experts in the aggregated responses. The ranking and categorizing process
ended when the variation between the rounds for the ranked issues was minimal and the data
reached a saturation point.
Data Analysis Plan
I conducted a generic qualitative research study to explore the following research
questions.
RQ1: What are the factors that information technology professionals may include in
determining the desirability of a viable solution that may provide the necessary protection for
personally identifiable information (PII) data in a public cloud computing environment?
RQ2: What are the feasible solutions that may provide the necessary protection for PII
data in a public cloud computing environment?

RQ3: What is the importance of a viable solution that may provide the necessary
protection for PII data in a public cloud computing environment?
The primary goal of the study was to identify the issues and gain an understanding and
then document the specific strategies needed by cybersecurity professionals to correct decisions
to enable the proper protection for computer users in a public cloud computing environment
from future recurring cyber-attacks seeping into network stored PII.
Survey Questions
Survey Question 1: What types of phishing attacks against customers’ PII has your
business experienced? Survey question 1 derives from RQ 2.
Survey Question 2: How do you protect your customers’ PII against phishing attacks?
Survey question 2 derives from RQ 1.
Survey Question 3: What are the considerations involved when developing strategies
for protecting your customer’s PII against phishing attacks? Survey question 3 derives from
RQ 1.
Survey Question 4: What techniques have you found most effective in protecting your
customers’ PII against phishing attacks? Survey question 4 derives from RQ 1.
Survey Question 5: What are the challenges relative to the strategies used in protecting
your customers’ PII phishing attacks? Survey question 5 derives from RQ 1.
Survey Question 6: What types of training are offered to customers to protect their PII
against phishing attacks? Survey question 6 derives from RQ 2.

Survey Question 7: What additional information about your experiences protecting your
customers’ PII against phishing attacks would you like to share? Survey question 7 derives
from RQ 3.
Survey Question 8: Briefly describe what you know about computer user issues when
storing PII data in a public cloud computing environment? Survey question 8 derives from RQ
2.
Survey Question 9: What are the strategies that cybersecurity professionals need to
build to correct decisions to enable data protection for computer users in a cloud environment?
Survey question 9 derives from RQ 1.
Survey Question 10: What are the most significant strategies that cybersecurity
professionals need to build to correct decisions to enable data protection for computer users
accessing a public cloud environment? Survey question 10 derives from RQ 1.
Survey Question 11: What are the least significant strategies that cybersecurity
professionals need to build to correct decisions to enable data protection for computer users
accessing a public cloud environment? Survey question 11 derives from RQ 1.
Survey Question 12: What strategies must be changed in the future to build correct
decisions to enable proper data protection for computer users accessing a public cloud
computing environment? Survey question 12 derives from RQ 2.
Survey Question 13: What strategies, specific to attacks, risks, threats, and
vulnerabilities must be addressed to build correct decisions for training computer users
accessing a public cloud computing environment? Survey question 13 derives from RQ 2.

Survey Question 14: What strategies, specific to cloud service models (IaaS, PaaS,
SaaS) must be addressed to build correct decisions for computer users accessing a public cloud
computing environment? Survey question 14 derives from RQ 3.
Survey Question 15: What strategies, specific to cloud deployments model (public,
private, hybrid, community) must be addressed to build correct decisions for computer users
accessing a public cloud computing environment? Survey question 15 derives from RQ 3.
Survey Question 16: What strategies, specific to confidentiality, integrity, and
availability, must be addressed to build correct decisions for computer users accessing a public
cloud computing environment? Survey question 16 derives from RQ 1.
Data Point Questions Used for the Study
1. What are the security measures for protecting PII data in Cloud data centers (c,
2018)?
2. What level of technical support and security measures are included in a Cloud SLA
(Lawton, 2018)?
3. What software is used to secure the transferability of data and provides enough
security for a public cloud environment (Lawton, 2018)?
4. Explain how data is secured and stored in a cloud environment (Lawton, 2018)?
5. Explain how data is stored in a data center and who generally has access to
customers stored data in that location (Lawton, 2018)?
6. What format is data returned in when sent to virtual machines stored in the cloud
(Lawton, 2018)?

7. Generally, computer users do not control their own data. Do you see this rule
changing in the future? If so, explain how security would allow data to flow
between the cloud to the organization (Lawton, 2018)?
8. How are organizations able to achieve data flexibility and maintain regulatory
security compliance to protect Data. (Lawton, 2018)?
9. Which Cloud providers offer the best services and can be trusted (Lawton, 2018)?
10. Explain how a suspected security violation is handled in the cloud (Lawton, 2018?
The study provided an opportunity to find a relationship between the research questions,
the data collected and determine the appropriate evaluation method to analyze the data
collection process. The initial coding and procedure provided specific guidance that I intended
to follow after I analyzed the collected data. The intention was to use a Microsoft Excel
spreadsheet to initiate the coding procedure and then move forward to an inductive coding
technique to analyze my data. There was no set codebook to use for this study. I started from
scratch and created codes based on the qualitative data that I received from the survey
responses, in the study.
Issues of Trustworthiness
One of the primary issues in a qualitative research study was the issue of
trustworthiness and honesty of the researcher with respect to the data collection process. As the
researcher, I ensured that I made no attempt to discredit the data or myself while performing
the data analysis. If the researcher is not honest with the data collection methodology, the
results of the study will be misguided and biased (Bahrami et al., 2016). The researcher used it
as a data collection tool and an information flow medium when conducting an investigation

(Braun et al., 2019). The researcher perceived as the primary person who collects the data,
describes the information, and gives the importance of the findings (Thompson, 2020).
The strategy used by the researcher established trustworthiness, credibility,
transferability, dependability, and confirmability. The easiest way for the researcher to
establish trustworthiness in a research study was to use the following four tenets of
trustworthiness (credibility, transferability, dependability, and confirmability) that was
proposed in 1985 by Lincoln and Guba. Since then, many researchers have used the four tenets
as a framework for trustworthiness (Lincoln and Guba, 1985).
Credibility
To establish creditability, the goal for the researcher was perceived as believable or
trustworthy. Fogg and Tseng (1999) found that in their research believability was a good
symptom for creditability. The intension to quickly establish credibility with each participant
allows them to feel confident knowing their electronic files/data were stored in a safe location,
and on the researcher’s password-protected computer.
Transferability
To establish transferability, the goal for the researcher was to create a reflexive journal,
a research log to record thoughts about the research. A spreadsheet was the strategy used by the
researcher to capture ideas, any preconceptions, bias nature, and anything that may impact
objectivity of the research. The primary goal was to allow the researcher to keep all the
incoming data organized as it is received from each participant. Researchers should minimize
bias tendencies during the data collection process and ensure that a personal bias nature do not

adversely influence the work in the study (Fusch and Ness, 2015) by making every attempt in
the research to be objective, honest, and straight forward as much as possible (Zohrabi, 2013).
This study will not be transferable because of a small and nonrandom sample. The transferability does not
involve broad claims but invites readers of research to make connections between elements in the study and
compare it within their own experience.
Dependability
To establish dependability, the primary goal for the researcher was to provide explicit
details about the methodology which helped to establish dependability of the chapter. The more
consistent the researcher proved to be during the research process, the more dependable and
believable are the results or findings gathered from the examination. This is done to allow
future researchers to follow along with all the decisions made that were related to the research
study. As the researcher, using this type of technique allowed the researcher to provide an
explanation that clarifies why a particular decision, or decisions were made relating to the
study. If the researcher does not maintain any kind of audit trail, the dependability cannot be
assessed, and dependability and trustworthiness of the study are diminished (Williams, 2011).
The strategy of the researcher was to establish dependability for auditing purposes, created an
audit trail with the data collection process, and analyze the data until a saturation point was
recognized, reflexivity, as well as ensure that all participants worked in the security industry.
Confirmability
To establish confirmability, which is the last criteria of trustworthiness, the goal for the
researcher was to conduct the research with a level of confidence that the study’s findings were
based on the participants narratives or actual words rather that potential research biases

(Williams, 2011). The goal of the researcher was to verify that the findings were determined
from the data that was collected from the participants rather than the findings being determined
by the researcher. The primary strategy was to thoroughly explain the decisions that were being
made in the research process.
Ethical Procedures
The participants in the study will be volunteers and will not be promised any type of
compensation for their participation. Participant in the study will not be from any protected
group such as children, prisoners, or the handicapped. The goal was to follow the Belmont
Report guidance the guidance to protect the rights and identities of each participant (HHS.gov,
1979).
Participants in the study had the right to refuse participation at any given time, in
writing. Prior to starting the data collection process, each participant was presented with an
informed consent form provided by the online SurveyMonkey platform, documenting their
willingness to participate in the study, as a willing participant. No personal information was
solicited at any point during the collaboration process (Felton Jr, 2021). Nor was sensitive
information such as passwords were not solicited during the engagement. Each participant data
was associated with a code so that no association was made to link a participant with their data
directly or indirectly (Felton Jr, 2021).
The primary goal was to collect the data from each participant using an online
SurveyMonkey link to keep the information confidential and then destroy the information
received from each participant after a period has passed that is greater than five years (Felton
Jr, 2021). A copy of this study may be made available to each participant upon written request.

The initial goal was to receive the approval from the Walden University Institutional Review
Board (IRB) before the data collection process began.
Summary
The main points of Chapter 3 justified the choices of the generic qualitative study
research design as the methodological approach to the research. A generic qualitative study
approach was appropriate because the research topic has not yet been explored. The purpose of
this generic qualitative study was to align how 5 to 10 participants that were IT SME experts
may perceive the desirability, feasibility, and the importance of determining a viable solution
that someday may provide the proper protection for PII in a public cloud computing
environment (Patala et al., 2018). The research design and rational for the study were based on
security theories found to be related to the study because IT security professionals are a
primary concern for increased security issues in the past and may be the primary reason for
increased network vulnerabilities in the future (Tiwari, 2017). The role of the researcher was a
critical key aspect in the study and must work with the participants and develop competence to
implement the specialized skill without having a bias nature interfering in the data collection
analysis process. The qualitative methodology will include the design of an exploratory
qualitative data analysis. The exploratory analysis was the process used to conduct an analysis
of qualitative data. It offered a method of data analysis that was flexible and compatible with
many approaches to qualitative research and provided a generic qualitative analysis (Braun et
al., 2019). In this generic qualitative study, the researcher was the instrument (Pezalla et al.,
2012). The researcher was responsible for making sure there was validity in the data collection;
by properly citing information performed by the researcher and understanding how important it

is to the study was a critical aspect of being a research instrument (Pezalla et al., 2012). This
chapter presented the instrument used in the study along with strategies for achieving validity
and reliability, and the process of data collection, data analysis plan, and the ethical
consideration were included. A data analysis plan was used to connect data to a specific
research question, organize and track data coding elements related to the participants. The
researcher was the primary person who collected the data so establishing trustworthiness was
the key determining factor for success. Data evaluation implemented leveraging a
computerized methodology, which provided results in evolving patterns and themes that
represented the findings of the research. Chapter 4 includes an analysis of the collected data
and reveals a report of the research findings.
Chapter 4: Results
Background
Chapter 4 represents the results of the exploratory generic qualitative study specified in
the preceding chapters. The generic qualitative study technique was used to gather the thoughts
from the target population of IT security professionals who have worked in the security
industry in various roles and were responsible for managing users and had experience in cyber
security problems in a public cloud computing environment. For years, IT professionals have
witnessed hackers constantly causing harm to end user PII data by seeping into secured
network environments. This chapter presents the results of the study, identifying the industry’s
primary problem of not properly protecting personal information based on the data collected
from the survey questionnaires (Creswell and Creswell, 2018). The research adheres to the
processes presented in the methodology map in Appendix C.

This technique allowed the researcher to gather pertinent information, initiate data
coding methods, identify themes and stimulate a greater awareness to better implement
stronger security measures and develop improved end-user training techniques that will
safeguard PII data. The primary goal identified what possible strategies IT professionals have
implemented to mitigate the frequent occurrences of providing secured protection to eliminate
information security breaches in a public cloud computing environment (see Patala et al.,
2018). Overall research findings will be explained, and the interpretations of the research
questions will be examined.
Research Collaboration Process
Before conducting a research study, the Institutional Review Board (IRB) at Walden
University reviewed the proposed research study to make sure the research topic was compliant
before issuing an approval to proceed to conduct the research. The process to obtain IRB
approval is a key factor to ensure no harm comes to human participation in research
(Faveraetto, De Clerq, Gaab and Elger, 2020). Researchers must receive a signed informed
consent from participants is an essential part of the process when requesting volunteers to
participate in a research study (Faveraetto, De Clerq, Gaab and Elger, 2020).
Prior to conducting the research study, a solicitation announcement was posted on
Walden’s University intranet to attract experienced volunteers for the study. The research
participant pool is a virtual bulletin board that connects researchers to participants. After two
weeks and several views by many students, no IT professionals inquired about the posting and
there were no volunteers who wanted to participate in the research study.

Survey Development
For this general qualitative research study, the researcher used the SurveyMonkey
platform, which allowed flexibility in the development of the question types used and
information gathered. The survey consisted of textboxes for open-ended questions, radio
buttons for Yes/No questions, and multiple-choice buttons for questions with multiple
answers. A textbox was provided to obtain additional information, feedback, and comments
for some of the survey questions.
Round 1
Prior to Round 1, the researcher tested the qualitative data analysis method to ensure
its viability for this research. The research study for Round 1 consisted of 14 questions. The
first page consisted of the qualifying questions to determine the correct target market inclusive
with an exit criterion presented in Appendix D. Page 2 consisted of the informed consent form
presented in Appendix D. The third page consisted of fourteen survey questions and ten
openended survey questions from SQ5 to SQ14, which are presented in Appendix E. The final
page consisted of a custom page that was created to thank the volunteers for their participation
in the study.
The thematic analysis approach was used to review the raw survey results (Braun and
Clark, 2006; Saldaña, 2016; Terry, Hayfield, Clarke, and Braun, 2017). This method is
depicted in Figure 2.
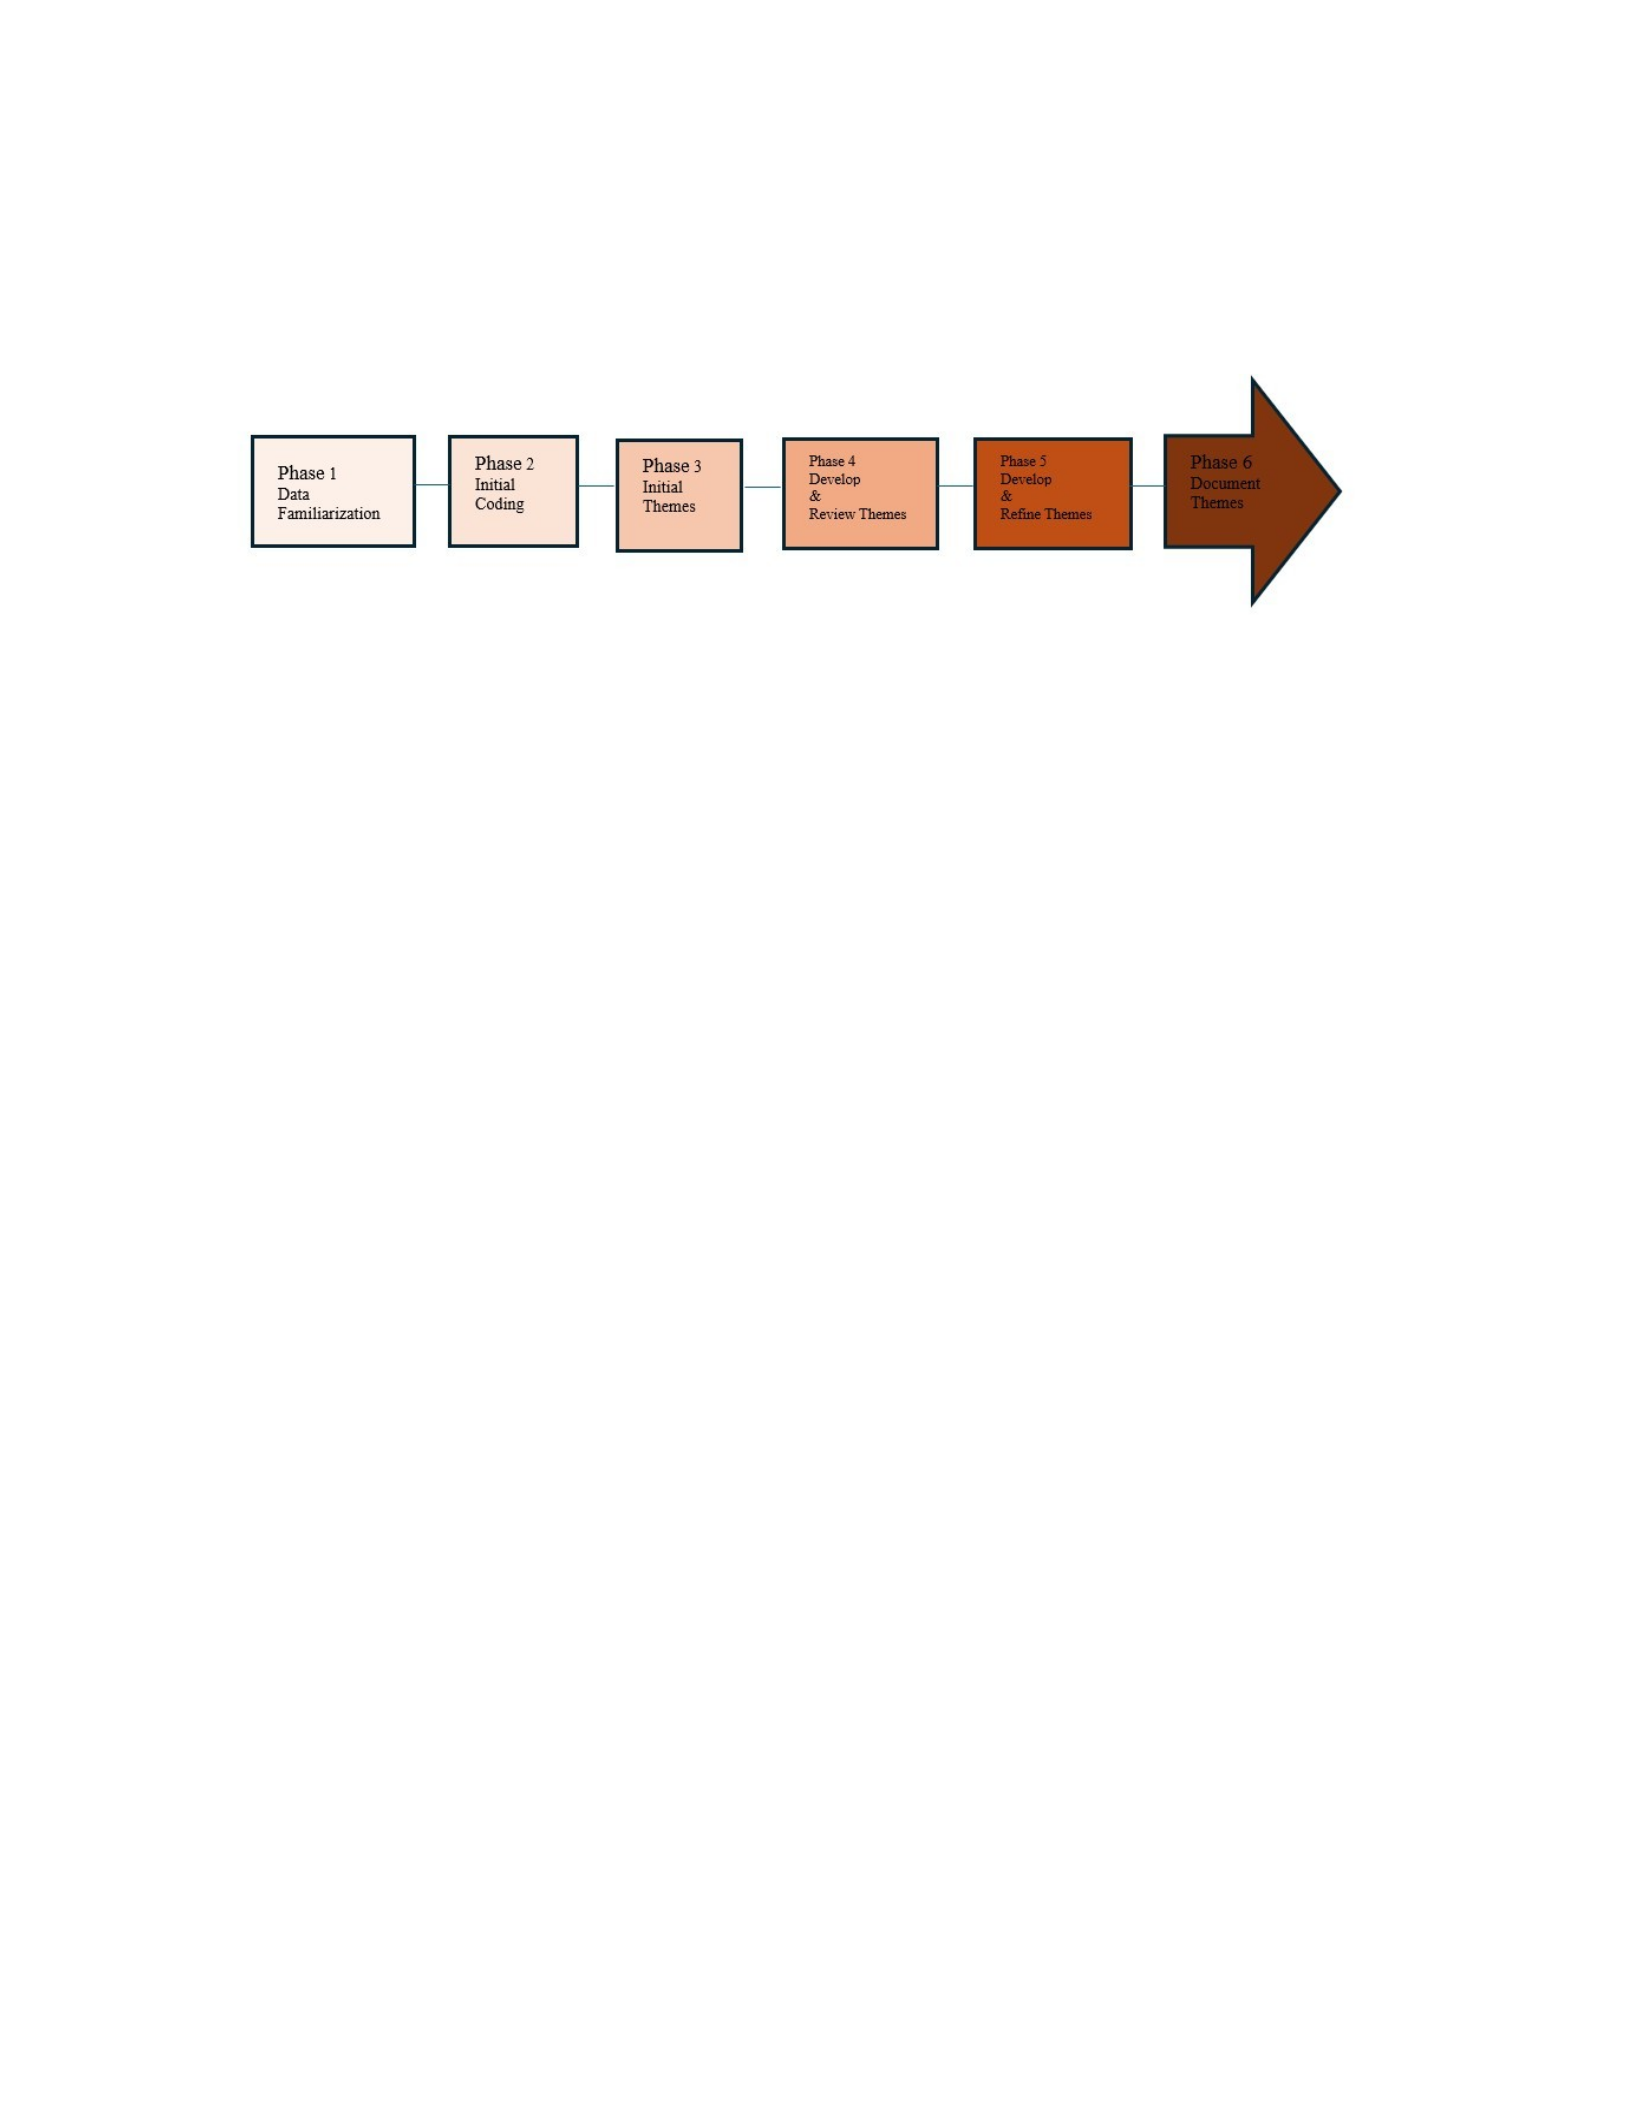
Figure 2
Thematic Analysis Process
Figure 2. Thematic Analysis Process derived from Braun & Clark, 2006; Saldaña, 2016;
Terry, Hayfield, Clarke, & Braun, 2017.
This chapter provided the responses to the research questions used to address the
research problem: how information technology project managers (ITPMs) may implement
viable solutions to mitigate the frequent occurrences of information security breaches in a
public cloud computing environment. The specific problem identified how there may be no
viable solutions available for protecting PII in a public cloud computing environment (Devi et
al., 2020). The survey protocol consisted of 14 questions. 05 to 10 SurveyMonkey participants
shared their experiences in the security field revealing common security issues, offering viable
solutions, and providing their experience about PII protection.
The findings addressed the gap in the literature, in Chapter 1, which was the perceptions
and experiences of the end-user trust in cloud data storage (Jaatun et al., 2018). ITPMs in the
security field may lack the ability to protect and secure personal data in the cloud to eliminate
security issues and subsequent data exposure from reoccurring (Wilson, 2018). Researchers
have never explored the issues relating to protecting end-user personal data in a cloud
computing environment. The lack of security has inflated serious issues as well as created

subsequent data exposure (Stewart, 2020). Previous researchers found different cloud security
issues such as cloud adoption and knowledge management security (Benjelloun & Lahcen,
n.d.); in addition to, cloud systematic identification threats (Hong et al., 2019). Enduser
perceptions, experiences, and challenges regarding PII protection within a public cloud
computing environment has not been investigated (Mohapatra et al., 2015).
Data Collection
Based on the study criteria, the researcher captured the data through SurveyMonkey’s
platform. The participants were SME who adopted cloud computing services and were familiar
with cloud computing providers. I had the participants review the questions that were
perceived to be valid questions to determine if they met the target market. As the researcher, I
reviewed the information obtained from the SME during the data collection process and
performed a comparison analysis related to the tested criteria questions concerning the security
industry to determine if they were (a) IT project managers (b) had worked a minimum of 3
months with the current organization or on a contract, and (c) lived in the United States. The
SurveyMonkey online questionnaire continued until all thirty-three participants had completed
the survey process which ended after reaching the last question.
Table 2
Survey Participation Summary
Data Analysis
After gathering, reviewing, and assembling all the data. The data was imported into
NVivo 14 from the SurveyMonkey questionnaires which allowed me to code the responses
from the IT subject matter experts in the security industry who were (a) IT project managers
(b) had worked a minimum of 3 months with the current organization or on a contract, and (c)
lived in the United States. , I used NVivo 14 software to identify themes in the collected data.
Round 2
Based on the responses received from the survey results of Round1 Survey prompted
Round 2. Three topics were used in Round 3: 1) Lack of outdated security training material is
needed and frequent security awareness training on risk attempts, quarterly 2) IT subject matter
experts install firewalls and implement System upgrades with reliable security applications,
Round 1 Round 2 Round 3
33
# SME Participants 33
# Unusable Records in Survey 10
N/A N/A
# Partial Blank Records in Survey
15 15
# Completed Surveys 9 9
and 3) major concerns about a lack of protection for PII information, such as SSN, etc. The
ability to enter additional questions was removed to ensure the consensus of expert opinion.
Table 3
Data Gathered from Participants
Respondent ID Q1 Q2 Q3 Q4 Q5 Q6 Q7 Q8 Q9 Q10 Q11 Q12 Q13 Q14
#Row 1 RID955 YES YES YES AGREE GPAR KTS RISK SBEA HS RT NM PACD ? SSSNI
#Row 2 RID937 YES YES YES AGREE GSSN FW FW N/A HFW QU DK DK N/A N/A
#Row 3 RID058 YES NO YES AGREE EXPE TU KC EDUC SP VFEB N/A N/A N/A N/A
#Row 4 RID292 YES YES YES AGREE EMLP SEI DOUE DSE KUA CTIA LCDS KSU FW WAT
#Row 5 RID422 YES YES NO AGREE N/A E FISHY DK NS US US US US US
#Row 6 RID628 YES YES YES AGREE SECL N/A NONE N/A N/A N/A N/A N/A N/A NS
#Row 7 RID828 YES YES YES AGREE IDENI FW N/A BSFW PFUS NC DWIL NC NC NIAT
#Row 8 RID099 YES YES YES AGREE N/A SF AFF ADT FG DYY ET ETT N/A ADG
#Row 9 RID802 YES YES YES AGREE CLNK APPS APPS APPS APPS CLASSES NS NS N/A APPS
________________________________________________________________________________________________________________
Codes were vital because they indicated trends in the questionnaire responses or were
related to key topics indicated in the literature (see O’Leary, 2017). I performed the qualitative
content analysis by coding the data generated from the questionnaires. I also employed a
bottom-up qualitative coding procedure (see Auerbach and Silverstein, 2003), conducting three
rounds of this synthesizing technique. The initial process started with the line-by-line coding of
all data generated from the cases using NVivo 14, resulting in 33 unique codes. For the second
round, I used Microsoft Excel to group similar or related words or statements, resulting in 24

codes. For the third round, I used Microsoft Excel to group similar or related words or
statements. Using the thematic analysis method prompted the results of the findings. From that
point, I used the codes to develop themes.
Theme Development
Theme development occurred in the third and final round. I used Microsoft Word to
create labels and form clusters for each theme before transferring the data back into NVivo 14.
Second codes were compared across all significant information to understand higher level
concepts. I systematically and iteratively group related or repeated codes into clusters. This
process resulted in three themes. Developing themes using qualitative methods (Merriam and
Tisdell, 2016) is like developing affinity diagrams (Holtzblatt, 2016) to make sense of a large
volume of data or to cluster information in an organized manner (Nyre-Yu et al., 2019).
Round 3
The outcomes of the qualitative data analysis included three themes grouped around
various aspects of security incidence and challenges (see Table 2). Each of the subject matter
experts’ statements were ranked by the volume of codes subsumed under them, with the
number of codes included. I used the codes to identify categories and locate themes. The data
analysis addressed the perceptions and experiences of security challenges in providing proper
protection for PII data in a cloud computing environment. Three themes were identified
challenges in cybersecurity: industry trends and standards, IT Security actions, and experiences
with data breach prevention.
Table 4
Theme Development from the Questionnaires
Rank
Theme Code
1 Industry Trend and IT Security Standards 3
2 IT Security Action/ Protection 3
3 Prevention 3
Once I was done coding all of the questionnaire data, the codes were reviewed and
analyzed to find common words shown in Table 5.
Table 5
Common Words
List of words Word count Percentage
Attacks 15 4.95%
Challenge 11 3.63%
Cloud 10 3.30%
Environment 9 2.97%
Firewall 8 2.64%
PII 15 4.95%
Training 10 3.3%
Total 78 26.74%
Evidence of Trustworthiness
One of the primary issues in a qualitative study is the trustworthiness and honesty of the
researcher with respect to the data collection process. As the researcher, I made sure that I

made no attempt to discredit the data or myself while performing the data analysis. If the
researcher is not honest with the data collection methodology, the results of the study will be
misguided and biased (Bahrami et al., 2016). The strategy was to establish trustworthiness,
credibility, reliability, confirmability, transferability, and dependability for auditing purposes
by creating an audit trail and triangulation, prolonged contact, member checks, saturation,
reflexivity, peer review, and making sure that all participants did not work for the same
company. The researcher is a data collection tool and an information flow medium when
investigating (Lincoln and Guba, 1985). The researcher is the primary person who collects
data, describes the information, and gives importance of the findings (Lincoln & Guba, 1985).
The easiest way for the researcher to establish trustworthiness in a qualitative study is to use
the following four tenets of trustworthiness: credibility, dependability, transferability, and
confirmability (Lincoln & Guba, 1985). Since then, many researchers have used the four tenets
as a framework for trustworthiness (Lincoln & Guba, 1985).
The researcher established creditability, the goal for the researcher is to be perceived as
believable or trustworthy. Fogg & Tseng (1999) found that in their research believability is a
good symptom for creditability. The researcher’s intension was to quickly establish credibility
once the participant shared the consent form with each participant so they would understand
the rules of engagement and know their data would be stored in a safe location.
The researcher established transferability, the goal for the researcher was to create a
reflexive journal or a research log to record thoughts about the research. The researcher used a
spreadsheet to capture any ideas, preconceptions, biases, and anything that may impact
objectivity of the research. The primary goal was to keep all of the incoming data organized as

it is received from each participant questionnaire. Researchers should be mindful to minimize
bias during data collection and ensure that personal biases do not adversely influence their
work (Fusch & Ness, 2015) by making every attempt in their research to be objective, honest,
and straight forward as possible (Zohrabi, 2013).
The researcher established dependability, the goal for the researcher was to provide
explicit details about the methodology helped to establish dependability amongst the
participant. The more consistent the researcher is with the research process, the more
dependable the results will be. This is done to allow future researchers to follow along with all
the decisions made that are related to the research study. As the researcher, using this type of
technique allowed the researcher to provide an explanation that clarifies why a particular
decision, or decisions were made relating to the study. If the researcher does not maintain any
kind of audit trail, the dependability cannot be assessed, and dependability and trustworthiness
of the study are diminished (Williams, 2011). The researcher’s strategy established
dependability for auditing purposes, creating an audit trail in field notes, and triangulation,
prolonged contact, member checks, saturation, reflexivity, and peer review, as well as making
sure that all participants did not work at the same company.
The researcher established confirmability, which is the last criteria of trustworthiness,
the goal for the researcher was to conduct the research with a level of confidence that the
study’s findings were based on the participants responses or actual words rather that potential
research biases. The goal was to verify that the findings were shaped by the participants rather
than the findings being shaped by the researcher. The primary strategy was to thoroughly
explain the decisions that are being made in the research process.

Results
The researcher coded all the questionnaires; the codes were reviewed to see what kind
of themes the codes align with to find common themes or patterns shown up in the data
gathered. The initial codes listed in NVivo 14 easily visualized across all the questionnaires.
The researcher used the code to conceptualize the data. The questionnaires were uploaded into
NVivo 14, which allowed the researcher to start coding the questionnaires. Codes were a
phenomenon the researcher considered vital because it repeatedly showed up in the unanimous
participant responses, was related to a research question or was related to a scholarly article.
Three themes were identified with IT security challenges: industry trend and standards, IT
security actions and prevention.
The data for the study came from the 33 participants who used SurveyMonkey’s online
questionnaire platform. The data collected from the open-ended questionnaire asked during the
survey provided each participant with an open awareness about the research study called: A
Qualitative Study of Management in Cloud Computing Security Challenges and concerns based
on each participants perspective. The fourteen open-ended questions were field-tested by the
researcher prior to releasing them to the volunteers who cloud computing experts were (IT
managers who had adopted cloud computing and cloud computing providers) to verify the
questions to ensure they were clear and perceived to be valid questions (Nyre-Yu et al., 2019).
The era of data breaches is here and multiplying by thousands each day. Protecting an
organization’s infrastructure is a vital concern of cyber security. Over recent years, cloud data
storage has become part of an organization’s day to day business processes to protect PII data
after the implementation of cloud data storage for their end users (Nyre-Yu et al., 2019).

Shared awareness has often been identified as a key component of effective cyber
defense operations Gutzwiller et al., 2019; The data confirmed and identified several factors
that contribute to shared awareness, moving the need in cybersecurity operations towards new
ways to facilitate information sharing or the process of shared awareness is not a one-way
information flow but rather a cycle that needs to include a genuine feedback flow oftentimes
lacking in the cyber security industry (Nyre-Yu et al., 2019). Feedback ensures the information
was received and understood, it can also be a communication channel for new input from
stakeholders and end-users (Nyre-Yu et al., 2019). For this to be effective, the feedback must
be genuine (Nyre-Yu et al., 2019). Feedback can further establish incident decision making and
enable learning between research and analysis (Nyre-Yu et al., 2019).
Summary
The researcher coded all the questionnaires received from SurveyMonkey. The codes
were reviewed to see what kind of themes and codes aligned with to find common themes or
patterns shown up in the data collected. The initial codes listed in NVivo 14 easily visualized
across all the questionnaires. The researcher used the codes to conceptualize the data. The
questionnaires were uploaded into NVivo14, which allowed the researcher to start coding the
questionnaires. Codes were a phenomenon the researcher considered vital because it was
repeatedly showing up in the unanimous participant responses, was related to a research
question or was related to a scholarly article. Included in Chapter 4 are study outcomes,
findings, data analysis, major and prominent themes that relate to the secure cloud computing
strategies needed by cybersecurity specialists for building the correct decisions for protecting
PII into a public cloud computing environment. The researcher used the saturated data from the

SurveyMonkey questionnaires to argue the results of this study.
Chapter 5 is the final chapter in this study and presents an overview of chapters 1
through 4. Chapter 5 includes a summary of the findings and recommendations in relation to
the research questions and problem statement. The limitations in the study will be reviewed and
discussed. The findings and interpretations will also be revealed. Recommendations for further
development and future research will be presented, and a summary will close out the final
chapter in this research study.
Chapter 5: Findings, Implications, Recommendations, and Conclusion
In this generic qualitative study, Chapter 5 provides a discussion of the findings that are
grounded in the iterations of a survey (Creswell & Guetterman, 2019). The technique provided
the structure for the survey prompts and the demand for data collection (Creswell and
Guetterman, 2019). The data analysis in the previous chapter further supports the findings of
this research which are grounded in the themes developed through experts on IT security
challenges associated with protecting PII data. A generic qualitative study research approach
(see Bhushan et al., 2017) was used to explore the strategies that IT security professionals need
to protect personal data in a cloud computing environment.
The purpose of this generic qualitative study was to understand how ITPMs may
implement viable solutions to mitigate the frequent occurrences of information security
breaches in a public cloud computing environment (see Patala et al., 2018). The study aimed to
identify critical cloud computing security challenges, threats and risks that hinder ITPMs
implementing viable solutions to mitigate the frequent occurrences of information security
breaches to properly protect public PII data in a cloud environment.

This study was important because it would provide ITPMs with insights into security
challenges, threat and risks and offer information in unknown areas where cloud computing
services need to improve in their cloud computing platform to address limitations associated
with their systems (Alworafi et al., 2016; Zhan & Huo, 2012). The primary objective of cloud
service offerings was to design cloud systems with robust security features aligned with the
information security needs of target client applications.
The general problem is IT professionals may lack viable solutions to reduce frequent
security breaches. ITPM’s generally rely on software programs that have inadequate strategies
to protect their customers’ PII from cyber threats. ITPM’s are generally reactive to current
security issues instead of being proactive to eliminate a future security breach. Spending time
to examine security issues could reduce data breaches (Barosy, 2019).
ITPMs fail to recognize persistent threats that could be eliminated to identify an attack
(Aldawood & Skinner, 2019; Alruwaili, 2019; Brisson & Savoie, 2018; Eling & Schnell,
2016). The specific problem is there may be no viable solution available for protecting PII in a
public cloud computing environment (see Devi et al., 2020). Focusing on continual threats will
benefit the cloud environment by reducing the likelihood of risk.
The finding indicated that cyber risks and threats in cloud computing exposed business
organizations to data breaches and data loss through human error and neglect. The results show
that loss of vital data through a data breach or the conduct of malicious actors within and
outside of an organization are major threats in cloud computing that uncover leaks to sensitive
data. Mischievous insiders exposed business organizations to vulnerabilities, which contributed
to an increase in hacking or cyber-attack attempts by external bad actors. The vulnerabilities

are often caused by cyber risks and the following key factors such as having weak password
policies, which made it easier for mischievous actors to break through security firewalls.
Vulnerable security systems and weak security practices have exposed organizations to data
breaches and data loss through gaps on the part of security providers in establishing stronger
security measures. As per the participants, cloud computing environments could be better if
stronger security measures were implemented correctly to eliminate making business
organizations highly vulnerable, particularly when cloud security settings are incorrectly
configured by IT security managers. PII data confidentiality, data privacy threats, and
cyberattacks in cloud computing are continuous which have raised a global awareness of cloud
computing weaknesses in large and small businesses in this country. The research findings
indicated that increased threats of cyber-attacks constrained leadership to move towards cloud
computing because business leaders fear the process of data transfer to the cloud is not secure,
fear of transferring PII data is risky and still very costly, and primarily the fear of losing their
organizations’ data. Additionally, participants revealed that the fear of data breaches and loss
made leadership decide to lockdown the network environment to analyze the frequent
occurrences to prevent additional PII data loss connected with cloud computing. The
volunteered participants also offered their perspective on the protection of PII data
confidentiality, data privacy threats, and cyber-attacks in cloud computing, which indicated
there was the availability of feasible, effective security solutions considered as high
requirements to ensure service and resources availability and sustainability are continuous
(Abdel Hakeem, Hussein, & Kim, 2022). Many participants revealed their perspective on
security solutions used to aid and protect PII data confidentiality, data privacy threats, and

attacks in cloud computing include install current upgrades and patch security systems
regularly when bug fixes are needed or security software is out of compliance, remove
erroneous data in networks environments and decommission unnecessary assets or equipment
improves security posture, employee training on cybersecurity standards, introducing zero trust
implementation to restrict data accessibility, enforce strong password policies, investigate
stronger anti-malware software to protect data.
User awareness programs and increased security countermeasures minimize the
exposure of cyber threats associated with IS misuse. Organizational practices were recognized
that may deter IS misuse: user awareness of security policies, security education, training, and
awareness (SETA) programs; and computer monitoring (D’Arcy, Hovav, & Galletta, 2009) the
likelihood that information systems are insufficiently protected against certain kinds of
damage or loss is known as “systems risk” as information systems that are constantly at risk,
security systems cannot be fully secured with technology alone (Straub & Welke, 1998).
Investigation and identification of additional security awareness techniques targeted to
eliminate threats will benefit organizations by reducing the risks associated with cyber threats.
Qualitative research methodology was adopted in this study. Thirty-three IT
professionals from the security industry played a significant role in the study to uncover
security strategies. The study also provided an opportunity to use the Walden University
participant pool to collect data. The SurveyMonkey questionnaire was designed to provide
open-ended questions, allowing participants to share their experiences, insights, and
perceptions regarding data protection planning. Data was collected using the questionnaire
identified in Appendix C.

The findings of this research are grounded in the use of thematic analysis. The findings
of this research will help IT professionals plan for future enhancements that will align with
security best practices, implement stronger security standards and focus on zero trust access
techniques to implement in a network environment.
SurveyMonkey online questionnaires were used to collect data from a sample of 33
information technology security participants to identify what they have experienced and
consider security best practices in their organization to improve a viable solution and the
implementation of cloud computing in the security industry. The participants used for the
study were drawn from a SurveyMonkey’s pool of unanimous volunteers who currently work
in the information security industry. A random sampling technique was used to gather the
necessary sample amount (Etikan & Bala, 2017). Boddy (2016) indicated that a smaller sample
size would be the most suitable for the study. The collected data was analyzed using the
thematic analysis process derived from Braun & Clark, 2006; Saldaña, 2016; & Terry,
Hayfield, & Clarke, & Braun, 2017. The six phases include data familiarization, initial coding,
initial themes, develop and review themes, develop and redefine themes, and document themes.
Limitations of the Findings
The limitations provided options to find different types of possibilities throughout the
qualitative research project (Stewart, 2020). The primary limitation was that the small group of
participants were unanimous and willing to volunteer without receiving any compensation and
work in IT security industry, and not be coerced by the researcher to participate in the study. A
practical understanding about the limitation in qualitative research was the findings would not
be generalizable from the sample to the population of interest (Merriam & Tisdell, 2016). As

an alternative, transferability of information and settings must be assessed by the reader
(Drisko, 2024). Another practical understanding about limitations in all qualitative studies was
that researcher bias may influence the findings (Merriam & Tisdell, 2016). To allow the reader
to verify that the influence of researcher bias on the findings had been minimal, descriptors of
the findings were provided when the results were reported (Boampong, 2024). This generic
qualitative research study was limited to the cybersecurity industry in the United States, who
were experienced IT security professionals who were exposed to cyber-security threats and
risks related to cloud computing. This study was limited to a small sample size because small
sample sizes are common in qualitative research, where data collection and analysis are time-
and resource-intensive (Merriam & Tisdell, 2016). The threat of limited transferability was
mitigated using data saturation to determine when the sample size in this study is sufficient to
achieve a comprehensive description of the phenomenon of interest, as recommended by Fusch
& Ness (2015). Chapter 5 includes the implications, recommendations for practice,
recommendations for future research, and the conclusion.
Implication of Research Questions
The problem is the protection of data in the cloud is questionable (Bhardwaj et al.,
2016), which created and perpetuated distrust among Leadership, end users (Oliveira, 2018).
The general problem was IT professionals may lack viable solutions to reduce the frequent
attacks of security breaches. The specific problem was there may be no viable solutions
available for protecting PII in a public cloud computing environment (Devi et al., 2020). The
study provided greater awareness of the perpetuated distrust of end-user data protection,
stronger focus on public cloud computing security issues, and how security issues are

increasing due to a lack of IT security professionals securing personal data in a public-facing
cloud environment.
The generic qualitative study was guided by the following research questions:
Research Question 1
What are the most common security problems with protecting public data in a
cloud computing environment?
In pursuit of finding an answer to the primary research question provided relevant
information for organizations implementing industry best practices for security awareness
insight. Two of the themes recommended to identify security problems were industry best
practices and IT security standards to enforce policies with non-compliant employees accessing
vulnerable security systems.
The execution of security policies already in place or the implementation of
new policies to comply with security standards is directed by the CISO (Smit, van Yperen
Hagedoorn, Versteeg, & Ravesteijn, 2021). Organizational policies determine what is
acceptable and unacceptable regarding user behavior associated with security guidance
(Mishra, Yehia, Gill, & Memoona, 2022). The literature review initiated a security culture to
include businesses and IT industry publications referenced to address personal data
protection challenges and focus on security resilience related to recovering from a breach
that may happen in a cloud environment. These publications provided the current security
data from businesses that did not have enough security measures in place as part of a
cybersecurity strategy (see Felton, 2021).

Research Question 2
What strategies are available to help IT professionals determine the desirability of
a viable solution that may provide the necessary protection for personally
identifiable information (PII) data in a public cloud computing environment?
Recognizing the current circumstances that generate security challenges are the
primary concern of the organization and prevention is the secondary force behind eliminating cyber-
attacks in any small or large organization. In addition to the two security issues currently identified in
participants responses from surveyed questions provided an awareness to research security trends,
implement stronger security standards, and encourage protection techniques for quarterly virtual training
of cloud security programs and the process of security vetting/training for onboarding new employees.
IT professionals generally provide specific programs that guide all new hires and or certain role-based
training opportunities the security comprehension that is needed for network access (Huang & Pearlson,
2019; NIST, 2020). The foundation set during initial, or onboarding training must be built upon with
quarterly, annual or continuous reminders to make the intention of the security process effective
(Campbell, 2019; Huang & Pearlson, 2019).
NIST 800-50 and NERC CIP recommend using different types of media for
security literacy (NERC, 2020, Wilson & Nash, 2003). In addition, the healthcare industry and
NIST 800-66, emails, newsletters, meetings, and computer-based training are all recommended
for users as cloud training techniques (Scholl et al., 2008).
Cloud computing is an organization’s primary barrier and ITPMs have been
working together to find security solutions to mitigate problems but something else needs to
be done to create a way forward. Volunteer participants provide their perspectives to address

questions that will improve existing security protection, prevention and training to strengthen
the culture and enforce an understanding about cloud computing issues throughout the
organization. There are security attacks that can occur when using cloud-based applications
and services. Users that attend security awareness training should understand that account
hijacking and protecting their passwords and other confidential information are vital to a
cyber-attack. Users should also understand that a security attack can restrict cloud users from
accessing hosted applications. The attack has constantly forced the cloud service providers to
use up system resources after an intruder enters the cloud environment. There barriers
identified by ITPMs that limit accessing cloud computing include replay attacks, man-in the
middle attacks, sniffing and spoofing of information. Cloud computing is very vulnerable to
security threats because of the way it is distributed. When critical data is transferred to a
thirdparty cloud receiver there can be security issues that require monitoring. Whenever an
organization decides to adopt cloud services, the organization must understand the risks
involved and follow security guidelines and security regulations to implement and comply
with industry standards. Network connections that have bad internet service providers, weak
or unreliable may prevent access to information or cloud applications. As a result of the study,
cloud service provider offers SLA that require customers to pay for what they use but hidden
costs for service can add up. ITPMs may lack the expertise needed which can create unknown
security issues and preventable spending. Constant training, updated training materials for
ITPMs that can offer increased certifications to encourage cyber pay can help ITPMs take
ownership more seriously. Any one of these organizational barriers can assist by executing
these research findings.

Research Question 3
What is the importance of a viable solution that may provide the necessary
protection for PII data in a public cloud computing environment?
The importance of a viable solution to protect data while accessing the cloud is
highly critical because the cloud enables organizations and their end users to access stored
essential data, applications, from any location. With the help of an internet connection
cloud customers constantly rely on cloud services leading to increased productivity,
flexibility, reduced expenses over time, and secured accessibility which includes improved
data recovery techniques. It is safe to say the cloud is nothing more than the internet itself
which allows users to operate more efficiently and competitively in the industry we live
in.
It is imperative that ITPMs develop continuous programs for enhancing security
programs to mitigate frequent occurrences to provide proper security protection based
on industry standards and the SME opinions of the volunteer participants.
As a result of this research study, the theme based around security prevention and
frequent occurrence replicates existing industry regulations. FISMA (2002) recommends
training annually. The survey results regarding the federal government recommended
annually and monthly. ISO/IEC 27001 (2020) recommends training
“periodically.” NERC CIP (2020) mandates quarterly training. The majority of NIST
regulations suggest having the organization define the frequency (Scholl et al., 2008;

NIST, 2020). Financial Technology and Managed Security Service Provider
(MSSP)/Information Technology (IT)/Information Security sectors
recommend continuously.
Recommendations
The generic qualitative study design was to study the end user experience in a cloud
computing environment. I recommend further research to explore end-user perceptions and
experiences of small businesses in the IT security industry. Due to the recruitment process used
in this generic qualitative study, the initial recruitment of participants was limited to the
Walden University participant pool and then transitioned to a SurveyMonkey platform
questionnaire approach. I used SurveyMonkey to recruit participants to obtain the data needed
for the study. Although the participants of this generic qualitative study were limited, the data
was consistent.
The themes and categories presented are a narrative rich in expert opinion (Salkind,
2017). Generalizability of qualitative research is limited (Salkind, 2017). Due to the diversity
of industries in the results, this research can be applied to any organization through
generalizations (Sridharan, 2020). This research is reporting the findings and providing themes;
applying recommendations summarized in this section is strictly up to the organization
(Sridharan, 2021). To mitigate an uprise of cyber-attacks the cloud should implement stronger
security standards and increase security countermeasures for situational awareness depicted
throughout this research for an improved protection program.
The results of this qualitative research study, recommend that all organizations

moving towards a cloud-based infrastructure will eventually have to increase their security
awareness program, seek initial approval from their senior level executive, chief financial
officers, and IT security management for enforcement of organizational policies with
employees eager to access the cloud computing environment. All users not willing to conform
with mandatory training guidelines or deadlines will require user access to be restored to access
the organizations network. Creating better role-based training with options like mandatory
virtual training for course credit, brown bag sessions, and strict security awareness training that
are new, interactive, and mind stimulating.
Security training techniques will improve an organizational security awareness
culture and offer cloud computer training that is stimulating, engaging, and interactive
(Boampong, 2024). Quarterly online security awareness training program or impromptu
security training will help influence user awareness. New employees during their onboarding
process are required to complete security awareness training and obtain a security certificate
with a score of 80% or better that can be provided as proof of completion.
Application software team will periodically announce the upcoming release dates
and times that are scheduled to install in support of improving cyber security hygiene. Users
are notified for situational awareness about the upcoming software installations schedule in the
attempt to build a security awareness culture at work to promote better cyber hygiene.
Organizations that set up cloud test environments use specific security tools to
provide visibility into monitoring, detecting, and protecting assets that are in the cloud test
environment. Another recommendation would be to have ITPMs show how hackers design
phishing emails and use them to try to compromise accounts and systems. Additionally, ITPMs

should create a webinar demonstration showing how hackers can gain unauthorized access to a
system by exploiting a vulnerability. It is the responsibility of the ITPMs to promote key
behaviors to improve cyber hygiene, promote users to stay safe online and encourage ITPMs to
research security best practices and implement security standards.
The conceptual framework used for this research was the National Institute of
Standards and Technology (NIST, 2022). This research recommends meeting practical security
standards for safety, functionality, durability, and other important traits that are managed by the
cybersecurity Maturity Model Certification. CMMC builds upon NIST 800171 through a
maturity model (House, 2021; Sharkov, 2020). The CMMC was created for systems within the
Defense Industrial Base (DIB) but can be applied to all small and large organizations (House,
2021; Sharkov, 2020). The primary reason for the CMMC is to protect the DIB from cyber
threats (House, 2021; Sharkov, 2020). Additional research recommendations are that CMMC
advises organizations to increase their defense strategy against cyber-attacks, help mitigate data
breaches in cloud environments, and review how the new guidance applies to security
awareness.
Recommendations for Future Research
This researcher recommends performing interviews to seek more study
participants or working with a large organization to arrange interviews to support potential
research. This research study achieved the required small sample size based on
recommendations from prior research, revealed final themes, and provided answers to the
research questions. Another means of participation could have provided deeper insight,
outcome and additional guidance. Security managers may be more engaged through

conversation versus as opposed to taking an online survey. The recommendation for future
research studies would be to interview volunteer participants to gather the data instead of using
a questionnaire approach.
The Chief Information Security Officers (CISO) is designated by the CIO to serve
as the principal advisor on information security matters. The CISO reports directly to the CIO
on the security of information systems and oversees implementation of information security
awareness programs for an organization. Other security practitioners or support staff are
recommended to interview for future research.
A consensus was reached in this generic qualitative research study based on SME
opinion on the frequency of cyber-security challenges in the cloud, industry trends, and PII
protection. Ransomware is the largest emerging cyber threat to organizations (Palmer, 2021).
Research concerning ransomware will prepare an organization to strengthen their security
standards to combat cyber-attacks. Future research should be performed to further evaluate the
frequency of cyber-attacks. The researcher recommends that future research will uncover
additional techniques that will mitigate frequent security breaches in a cloud computing
environment.

Conclusion
The purpose of this generic qualitative research study was to examine how ITPMs
may implement viable solutions to mitigate the frequent occurrences of information
security breaches in a public cloud computing environment (see Patala et al., 2018). This
study revealed that ITPMs lack viable solutions to mitigate the frequent occurrences of
information security breaches. However, the study may find that there are no viable
solutions available for protecting PII in a public cloud computing environment. Due to
increased security vulnerabilities, threats and network breaches in cloud computing
continue to allow bad actors to damage important data in business organizations through
data breaches and data loss.
The current research aimed to identify critical cloud computing security threats and
risks that hinder its adoption by small and large businesses. The importance of this study
was to provide an understanding of cloud computing security threats and risks that hinder
the adoption of cloud computing services in modern organizations. From the study
findings, we can learn that ITPMS must continue to improve security awareness programs
by following updated security policies, regulations and implementing security standards.
Security vulnerabilities and threats due to data breaches and data loss in cloud computing
begin with human error being the primary barrier of mitigating cyber-attacks. Insider
threat also expose organizations to network weaknesses, that aid to increase hacking or
cyber-attack from outside malicious bad actors.

Organizations that experience cyber-attacks in cloud computing increase their
protection to prevent security threats however, ITPMs are unable to eliminate the vicious
attacks by modern day hackers. The research study has provided an awareness into
security solutions offered idea to prevent damage to PII data, confidentiality information,
PII privacy, and unstoppable cyber-attacks in cloud computing, including employee
training on cybersecurity, restricting data accessibility, security software with frequent
updates for software systems, and encourage users to create strong passwords per security
policies can help serve as solutions to eliminate cyber threats in public facing cloud
computing environments.
Organizations should focus on training employees about cloud computing and
threats to data security. Further research can be conducted by focusing on additional
programs, preventive ideas that can provide solutions and change the culture to strengthen
cloud computing will protect PII data from getting to unauthorized individuals.
The focus of the research study was to foster awareness of ongoing security
challenges by collecting industry best practices from industry volunteer participants’
perceptions. This qualitative approach gathered the opinions of security SME from
questionnaires using a survey monkey approach, followed by a thematic analysis to
reveal the findings which can be used by researchers as a starting point to help understand
how ITPMs should create solutions that may prevent future cyber attempts.
A comprehensive literature review of security awareness was provided in
Chapter 2. Scholarly articles, journals, conference literature, and dissertations were

examined to provide context on the topic of cybersecurity education and the current state
of these training programs. NIST compliance guidance was presented to explore
techniques, identify barriers, and the importance and primary focus of frequent release of
updated security materials. As a result of the literature review, the researcher identified
differences among suggested presentation methods, topics, and frequency of security
awareness training based on industry best practices.
A gap was identified in the literature that revealed that industries are leveraging
cloud-based solutions to increase efficiencies and improve supply chain relationships
(Akinola et al., 2017; Huynh, 2010; Tiwari, 2017). Cloud computing provides greater
flexibility and allows users to access software applications in the form of mobile cloud
computing. Major research is underway to reduce security issues, but much work remains
to be done to create a secure mobile cloud computing environment (Tiwari, 2017). For
instance, cloud platforms are susceptible to attack due to the high intensity of information
resources provided for user access (Tiwari, 2017). The primary goal of an attacker is to
interrupt service to cloud users by creating a means for users to access the cloud platform
(Tiwari, 2017). Therefore, an attack can come from an external source of cloud computing
IT users or within the cloud computing environment that consists of whomever may
mistakenly prevent users from accessing cloud services (Tiwari, 2017).
The literature review identified research gap in public cloud computing, identify
security challenges, and reveal a lack of accountability in securing, monitoring, and

managing PII data that impacts the end user’s trust in a public cloud environment (Jaatun
et al., 2018). The current study revealed the standards and laws against the maturity model
chosen as the framework for this manuscript. The gaps prove there is a need to initiate a
demand for global awareness as an implication for positive social change to encourage an
increase for stronger security measures in the cloud and help to discover additional
security methods in the future.
Chapter 3 outlined the research method and technique used for this generic
qualitative research study. As the researcher, I collected the subject matter experts’
perspectives which established a foundation for future research by exposing a gap in the
field. There was a logical connection between the qualitative approach, the conceptual
framework, and the exploratory research design that aligned with the problem. The use of
encryption is necessary to protect and secure all types of PII data. The focus was on
identifying the problem, solicit participation, observe the data collection method, and
revealing the findings because the repeated and frequent issues in the security industry
remain unresolved (see Ahmad and Waheed, 2015; Nayak et al., 2017; Patala et al., 2018).
Chapter 4 presents the field study, which tested and validated the data collection
instrument that was discussed. The results of this exploratory qualitative research field
study were used to gather the thoughts from the target population of IT security
professionals who worked in the security industry in various roles and were responsible
for managing users and had experience in cyber security problems in a public cloud

computing environment. The field study resulted in necessary modification needed to
finalize the survey for the research study. The responses to the survey prompts were
presented and a consensus from the participants were finalized, when completed. The
research followed the six-step thematic analysis process to provide ample data for this
research study. Each theme was associated with an initial research question and
conceptual framework. All findings were documented, and demographics were revealed
and given an explanation.
Chapter 5 presents the findings, limitations, Implications, recommendations and
the conclusion of this dissertation. All sections in this chapter pertaining to this research
topic were further discussed. The findings and interpretations were examined. This
dissertation concluded with recommendations for future research to explore what
techniques ITPMs plan to implement improved transferability methods to eliminate
frequent occurrences of security attacks that damage PII data in cloud computing
environments.

