


Introduction the global commercial
Today, the global commercial fleet with 99,800 vessels of 100 gross tons and
above (United Nations Conference on Trade and Development [UNCTAD],
2021) that carry around 90 percent of the world’s merchant trade volume in
tons (Ma, 2021) are equipped with modern technologies such as industry 4.0,
which are vulnerable to a range of hacking incidents(Kidd, 2019). Most of
maritime network system operating nowadays, including the communication
system, navigation system and monitoring systems are poorly mature when it
comes to cyber security.
Cyber safety and security is an increasingly important issue for the shipping
industry both onboard and shore due to rapid digital transformation such as
automation or maritime big data and with that comes new threats and regulatory
requirements. One of the major classification DNV (2022) which is
endeavoring to improve cyber safety on board noticed that hundreds of new
cyber threats are emerging every day as hackers become faster and more
creative.
However, the increasing cyber safety and security issue is generally not
only just coming from cyber-attacks from the world wide web, but also coming
from the information system failures caused by intentional or un-intentional
incorrect operations or data breaches. This article will analysis the
uncertainties and challenges from above three aspects in related to cyber safety
and security in maritime industry and provide some constructive and
innovation suggestions so that the issue of maritime cyber safety and security
are fully recognized and emphasized in the maritime industry.
Based on the questionnaire, the authors will give short, medium and long
term measures to minimize threats to maritime cybersecurity, in addition to
complying with the guidelines of Cyber Security 4.0 on board.
1.1 Background
The world is under cyber threat all the time as the information technology been
invented, the world wide web(WWW) and millions of local area network(LAN) are
suffering cyberattack by second.
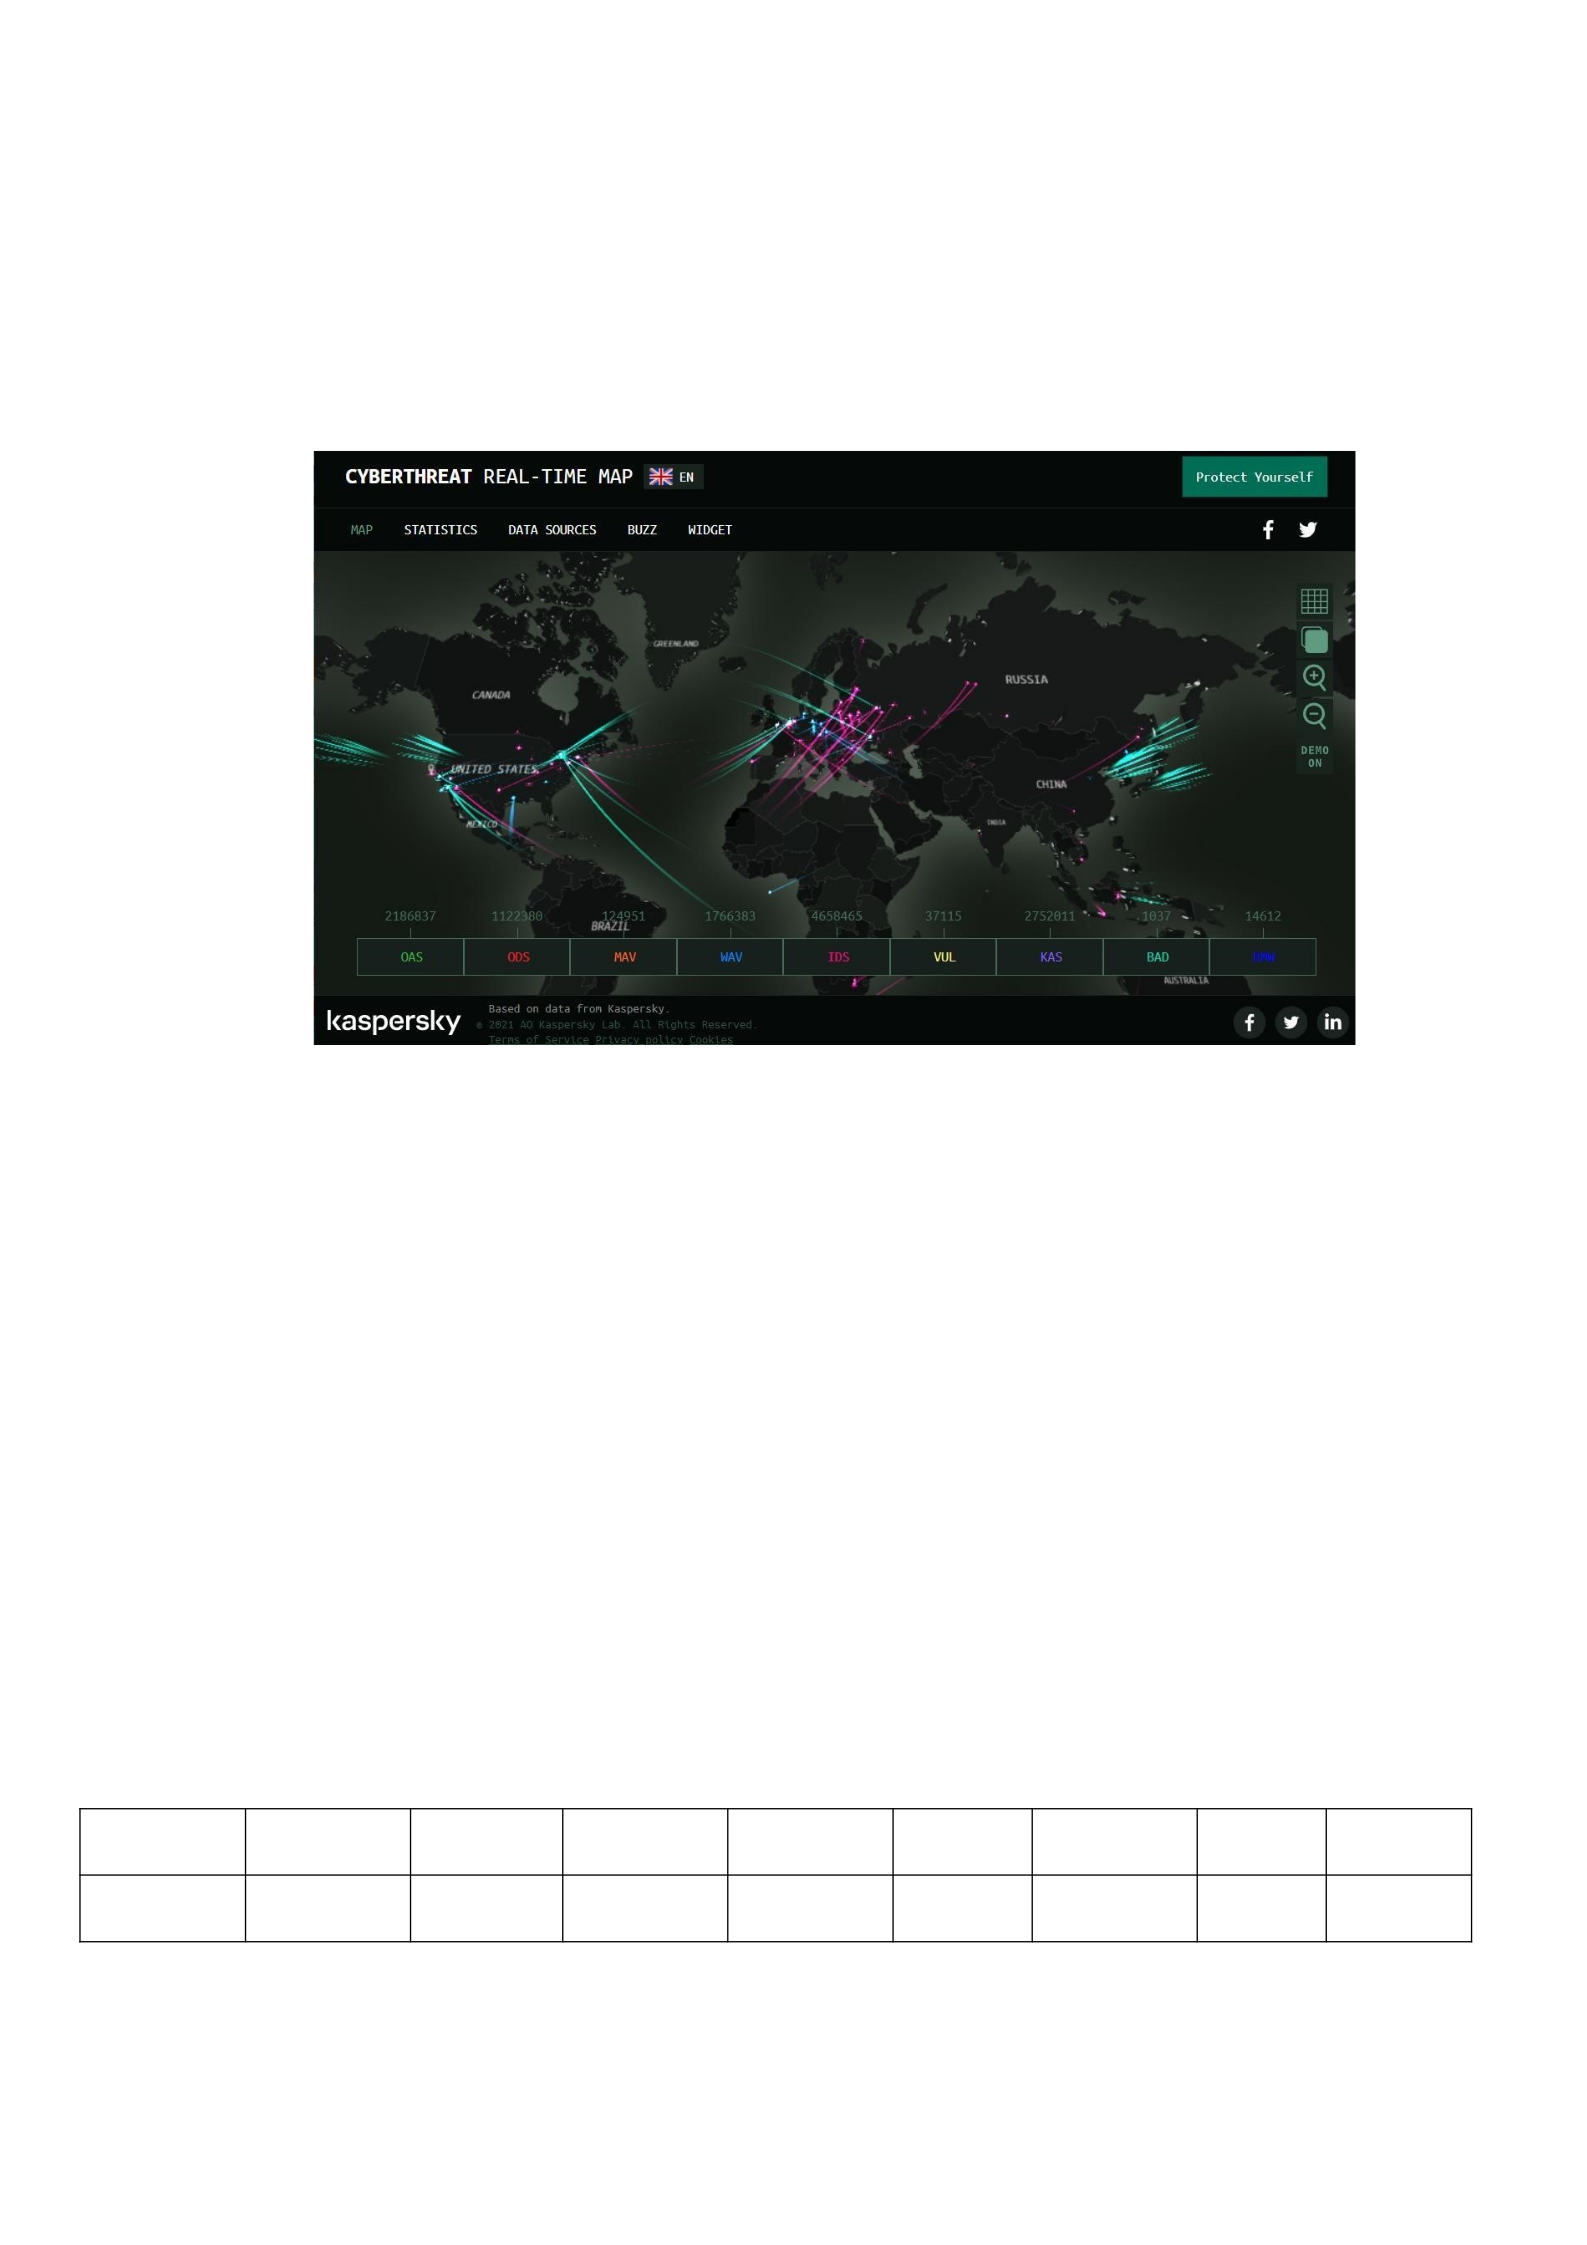
Figure 1 World real-time cyber-attacks (00:00-0636 1st Feb,2022)
Source: https://cybermap.kaspersky.com/stats (Kaspersky, 2022)
As shown in figure 1, we conclude table 1 in related to the world daily
cyberattacks in 9 different aspects based on data from Kaspersky real time map(2022),
the worldwide network system suffered a total 12663791 cyber threats within 6 hours
36 minutes on 1st Feb,2022 and which equals to 533 times cyber threats per second,
and these data was just collected by one of the most famous anti-virus company only.
As shown in figure 2, the most common cyber issue to the world network system is
intrusion detection scan (IDS) reaches to 200 times per second comparing with the
other cyber issues such as OAS, WAV etc. which almost contributes a 50% of normal
cyber threat to the world.
Table 1 Numbers of world real-time cyberattacks
OAS ODS MAV WAV IDS VUL KAS BAD RMW
2186837 1122380 124951 1766383 4658465 37115 2752011 1037 14612
Source: https://cybermap.kaspersky.com/stats (Kaspersky, 2022)
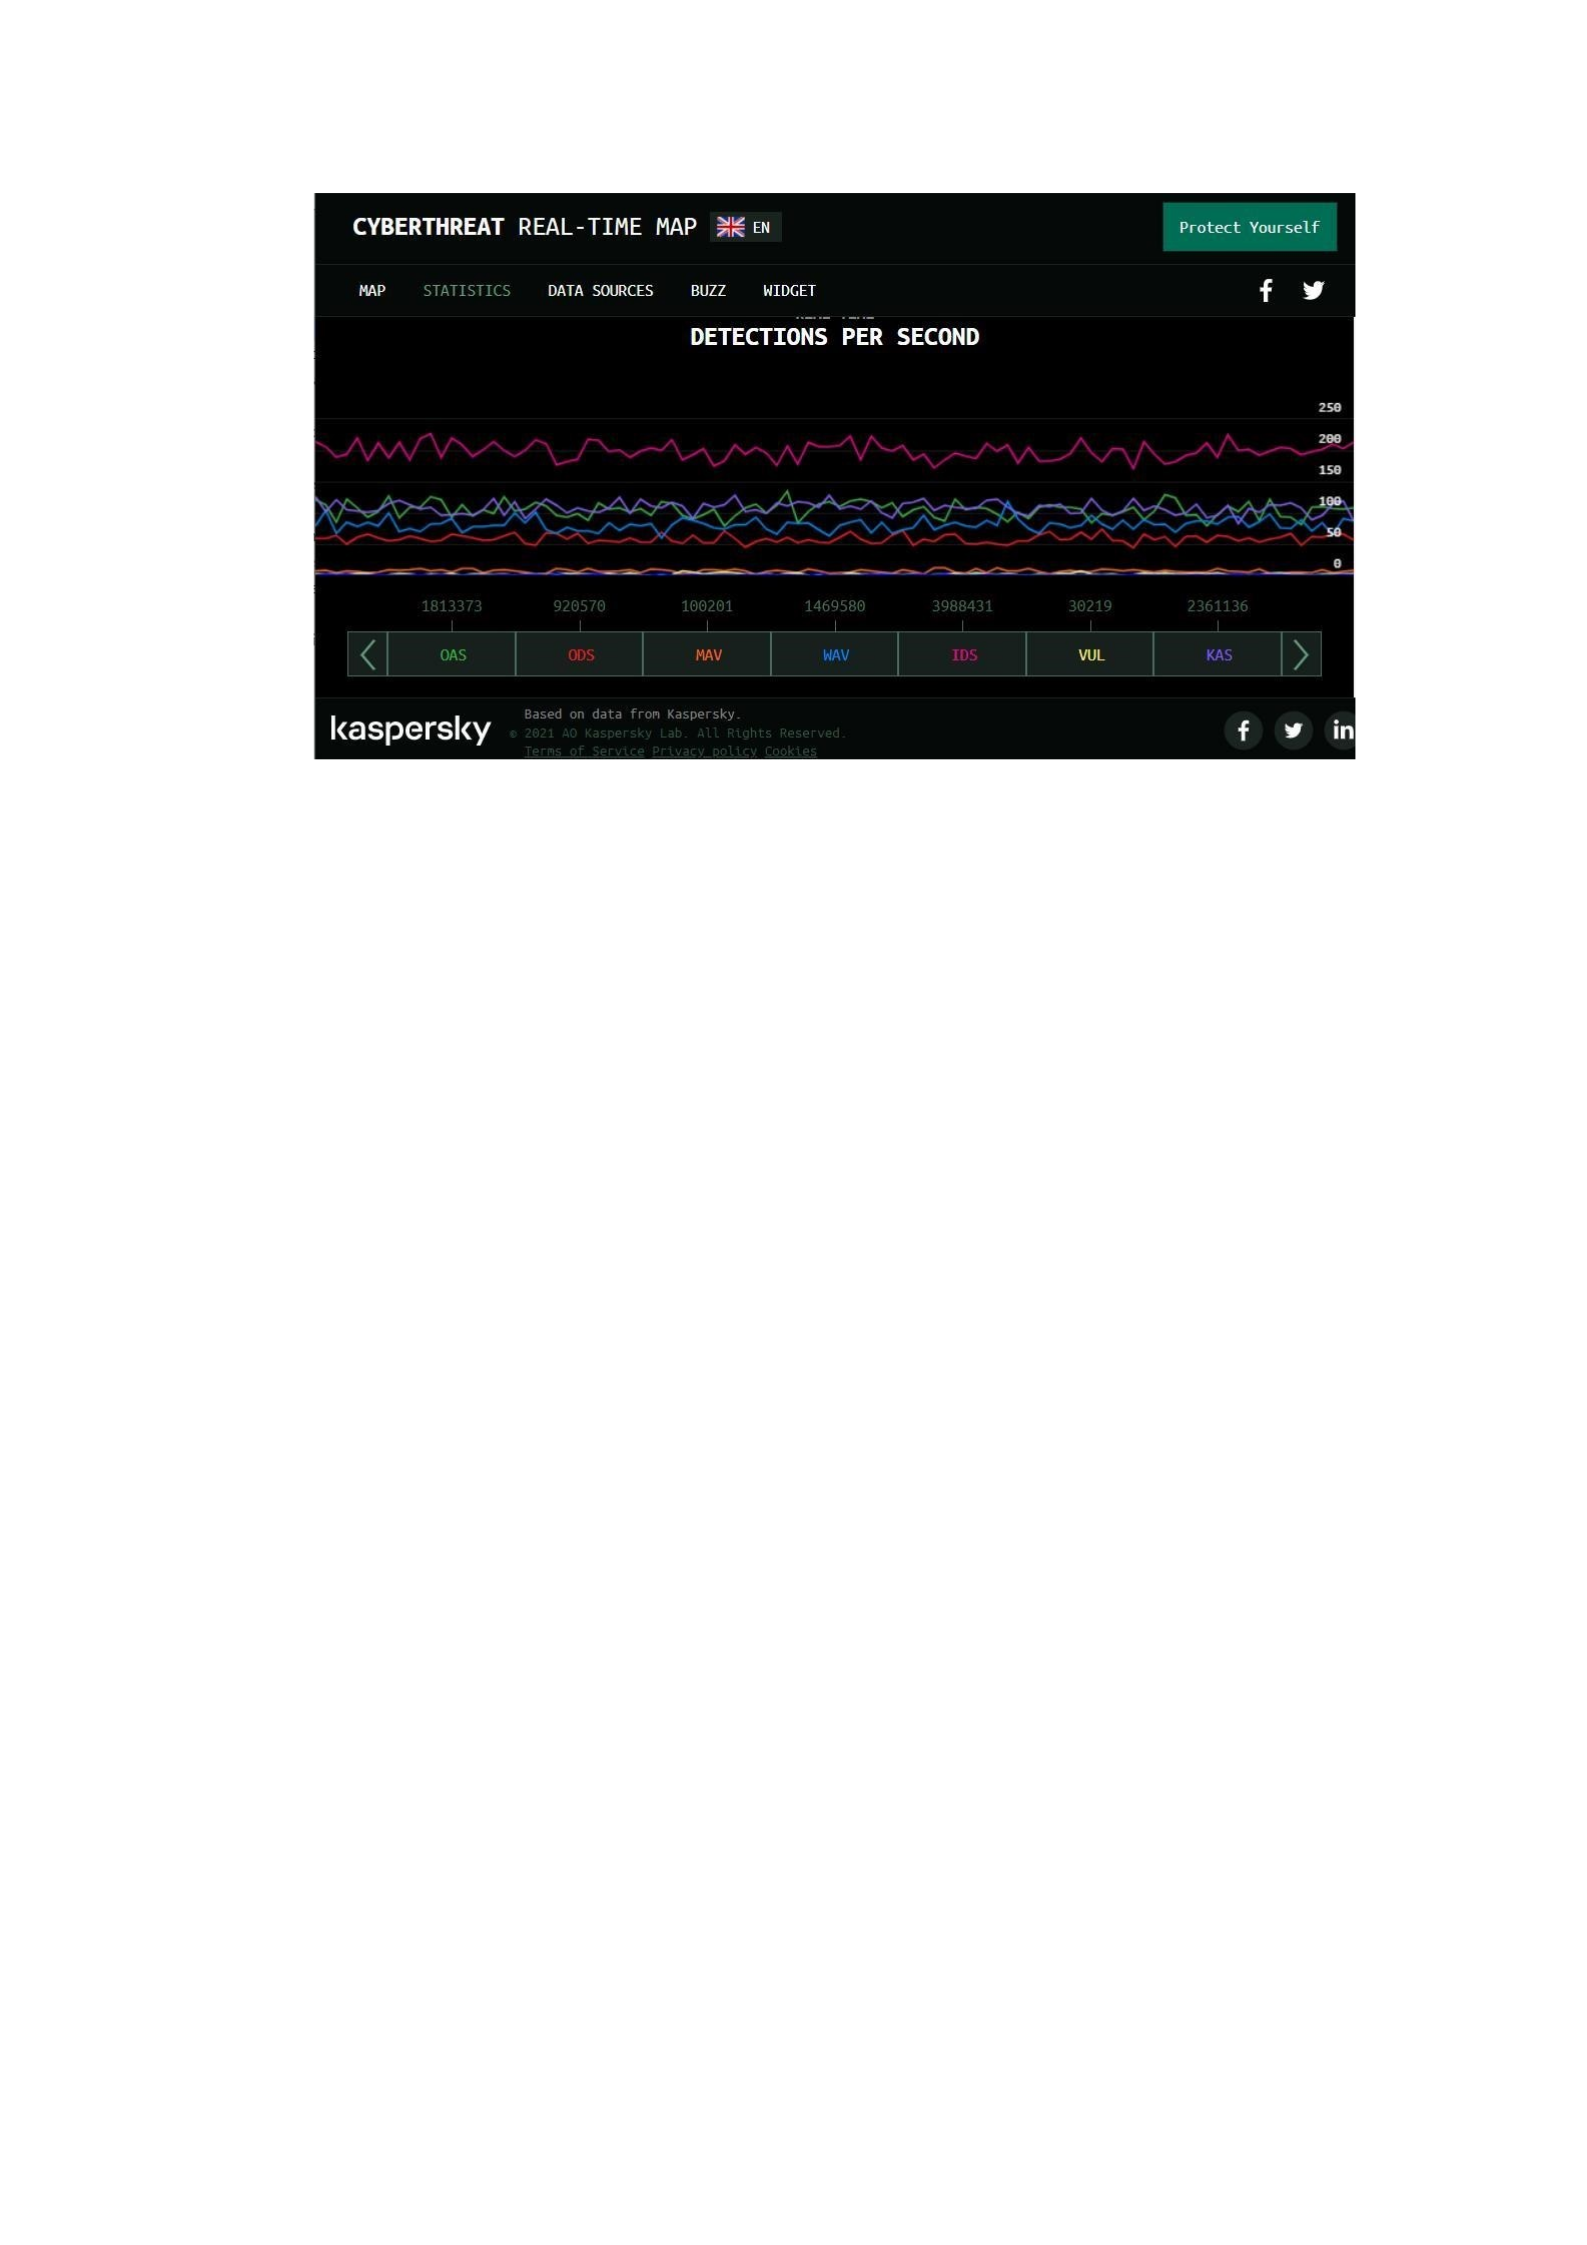
Figure 2 Cyber threat real-time map: detections per second
Source: https://cybermap.kaspersky.com/stats (Kaspersky, 2022)
According to the UNCTAD (2021), 90% of world trade volume in tons was
transported by ships, meanwhile the increasing relay on information communication
technology in international trade has attracted more concerns on cyber security to the
maritime industry. For example, one of the world largest container shipping company
Maersk was suffered cyberattack by a ransomware attack in 2017 which shut down
Maersk`s network system caused about 200-300million US dollars lost, and a COSCO
terminal at Port of Long Beach has also experienced cyber attacked by ransomware in
Jul 2018 and took 5 days to recover, the GPS systems of 20 vessels showed inaccurate
locations off the coast of Russia, South Korea has reported a GPS attack, in which
around 280 vessels were affected as well. These are only a few examples of maritime
cyber-attacks that have been carried out and reported in the media (Cyberonboard,
2021).
With the increasing cyber safety and security threat on the shipping industry,
International Maritime Organization (Hereafter refers to IMO) and Baltic and
International Maritime Council (Hereafter refers to BIMCO),European Union Agency
for Cybersecurity (Hereafter refers to ENISA), International Union of Marine
Insurance(Hereafter refers to IUMI) and some other international organizations related

to shipping industry and regional organizations have published several maritime cyber
safety and security guidelines recently.
IMO proposed a cybersecurity guideline (MSC-FAL.1/Circ.3) in 2017; BIMCO
published a first version of guidelines for shipboard cybersecurity in 2016; the ENISA
issue a guideline for cybersecurity in the maritime sector: Cyber risk management for
ports in 2020(ENISA, 2020). These guideline refers to National Institute of Standards
and Technology (Hereafter refers to NIST) and ISO/IEC 27001 as a source of
additional guidance and standard (Nettitude, 2019). Although there are gradually
increasing maritime cyber incidents and several maritime cyber security guidelines
published by international organizations, the researches that addressed on maritime
cybersecurity risk control is still at the beginning stage and is ten to twenty years
behind other computer-based industries such as automotive industry.(Caponi, Steven
L; Belmont, 2018).
1.2 Research aim and objectives
Based on the above mentioned background, and the fact of limited researches of
addressing the cyber safety and security in maritime industry nowadays, the issue of
cyber safety and security both onboard ship and ashore shall be identified and draw
more attention to the public. The situation of selective ignorance on maritime cyber
safety and security by relevant parties must be changed in near future. Whether on
shore based parties or shipboard activities and whether on management level or
operational level, the substantive actions and steps for cyber safety and security need
to be applied to the maritime industry.
Target the high level of maritime cyber security cannot be achieved just by the
endeavor of any single part of the shipping industry or by just updating the software or
strengthening the system firewall. The article will try to give the advices and
suggestions against the maritime cyber security based a systematic literature review, a
series of interviews and surveys.
In order to facilitate the research on maritime cybersecurity, this article aims to
carry out full survey regarding to maritime cybersecurity from management level to

operational level in different main maritime sectors: IMO and other legislation bodies,
shipboard, ship`s owner& managers; cargo owner & charterers, ports& terminal
operators, ship yards and other stakeholders, target to figure out the uncertainties and
challenges of cyber-security in maritime industry.
The objective of this dissertation is to inform the maritime policy and
management in the world by identifying barriers to maritime cyber security and
improved cyber resilience for maritime cyber infrastructure.
1.3 Significance of the research
In the face of rapid technological developments, maritime practitioners are under
increasing pressure to respond to the complex demands of the industry sector. As a
prime example, the uncertainties and challenges of maritime cyber safety and security
will continue to exist and evolve. Cyber safety and security engineering is a systemic
project and it is impossible to achieve goals through unilateral efforts.
Research on maritime cyber security is still at the beginning stage, and cyber
security risk assessment research in the maritime industry is limited as well. A
modelbased framework for maritime cyber risk assessment was published on the
Engineering & Technology Reference (Jones et al., 2016), but this framework does not
involve risk control options. This article will systematically review the cyber risk of
maritime industry. A series of risk control measures will be provided, furthermore, the
maritime practitioners are given the cyber safety and security awareness of how
serious is the cyber situation they are facing right now and how to realize the
inadequacy of their activities on emerging technology on board and shore.
2 Literature review
2.1 Definition of maritime cyber security
As per CISCO (2022), a leading global networking solutions provider,
cybersecurity is the general practice of protecting IT systems, networks, and programs
from external and internal cyberattacks. The different kinds of cyberattacks are

usually aimed at accessing, changing, or destroying sensitive information; extorting
money from users; or interrupting normal business processes.
In front of these directly cyber-attacks, the author think the general cyber safety
and security issues usually consist of three aspects, the first one is definitely
cyberattacks, the second one we defined as cyber information system failure and the
last one is data breaches(WTO, 2021).
The network system has blurred the concept of geographical and spatial
boundaries, making online conflicts and confrontations more insidious, and cyber
problem often occur without warning. The three aspects of cyber security can occur
independently or often in combination.
2.1.1 Cyber attacks
When it comes to cyber safety and security, cyber-attacks are often considered to
be the only cyber security problem as the fact that successful cyber-attacks are
constantly reported in the different media outlets.
A cyber-attack usually means any intentional attempt to obtain unauthorized
access to a computer, computing system or computer network with the intent to cause
damage. Intentional cyber-attacks target to disconnect, disrupt or control computer
systems or to modify, block, delete, manipulate or steal the data held within these
systems(Mary K., 2021). Cyber-attacks are the most basic cyber safety and security
concern that has been raised by public, which usually lead to cyber damages, such as
financial loss, communication breakdown, system malfunction etc. A cyber-attack is
usually an external attack on a network, where the cyber-criminal aims to gain some
benefit or achieves some goals by attacking the network thru various techniques.
In April 2020, the World Health Organization (WHO) issued a statement
claiming that the number of cyber-attacks had increased dramatically during the
epidemic and that the email addresses and passwords of approximately 450 WHO and
thousands of related staff had been compromised. According to foreign media reports,
and the WHO data leaked together with the NIH, the CDC, the Gates Foundation and
other agencies, a total of nearly 25,000 pairs of mailboxes and passwords(Sohu,
2020). The latest news as per Checkpoint`s 2022 cyber security report, cyberattacks
against corporate networks increased by 50% in 2021 compared to 2020(Checkpoint
Rreseach, 2022).
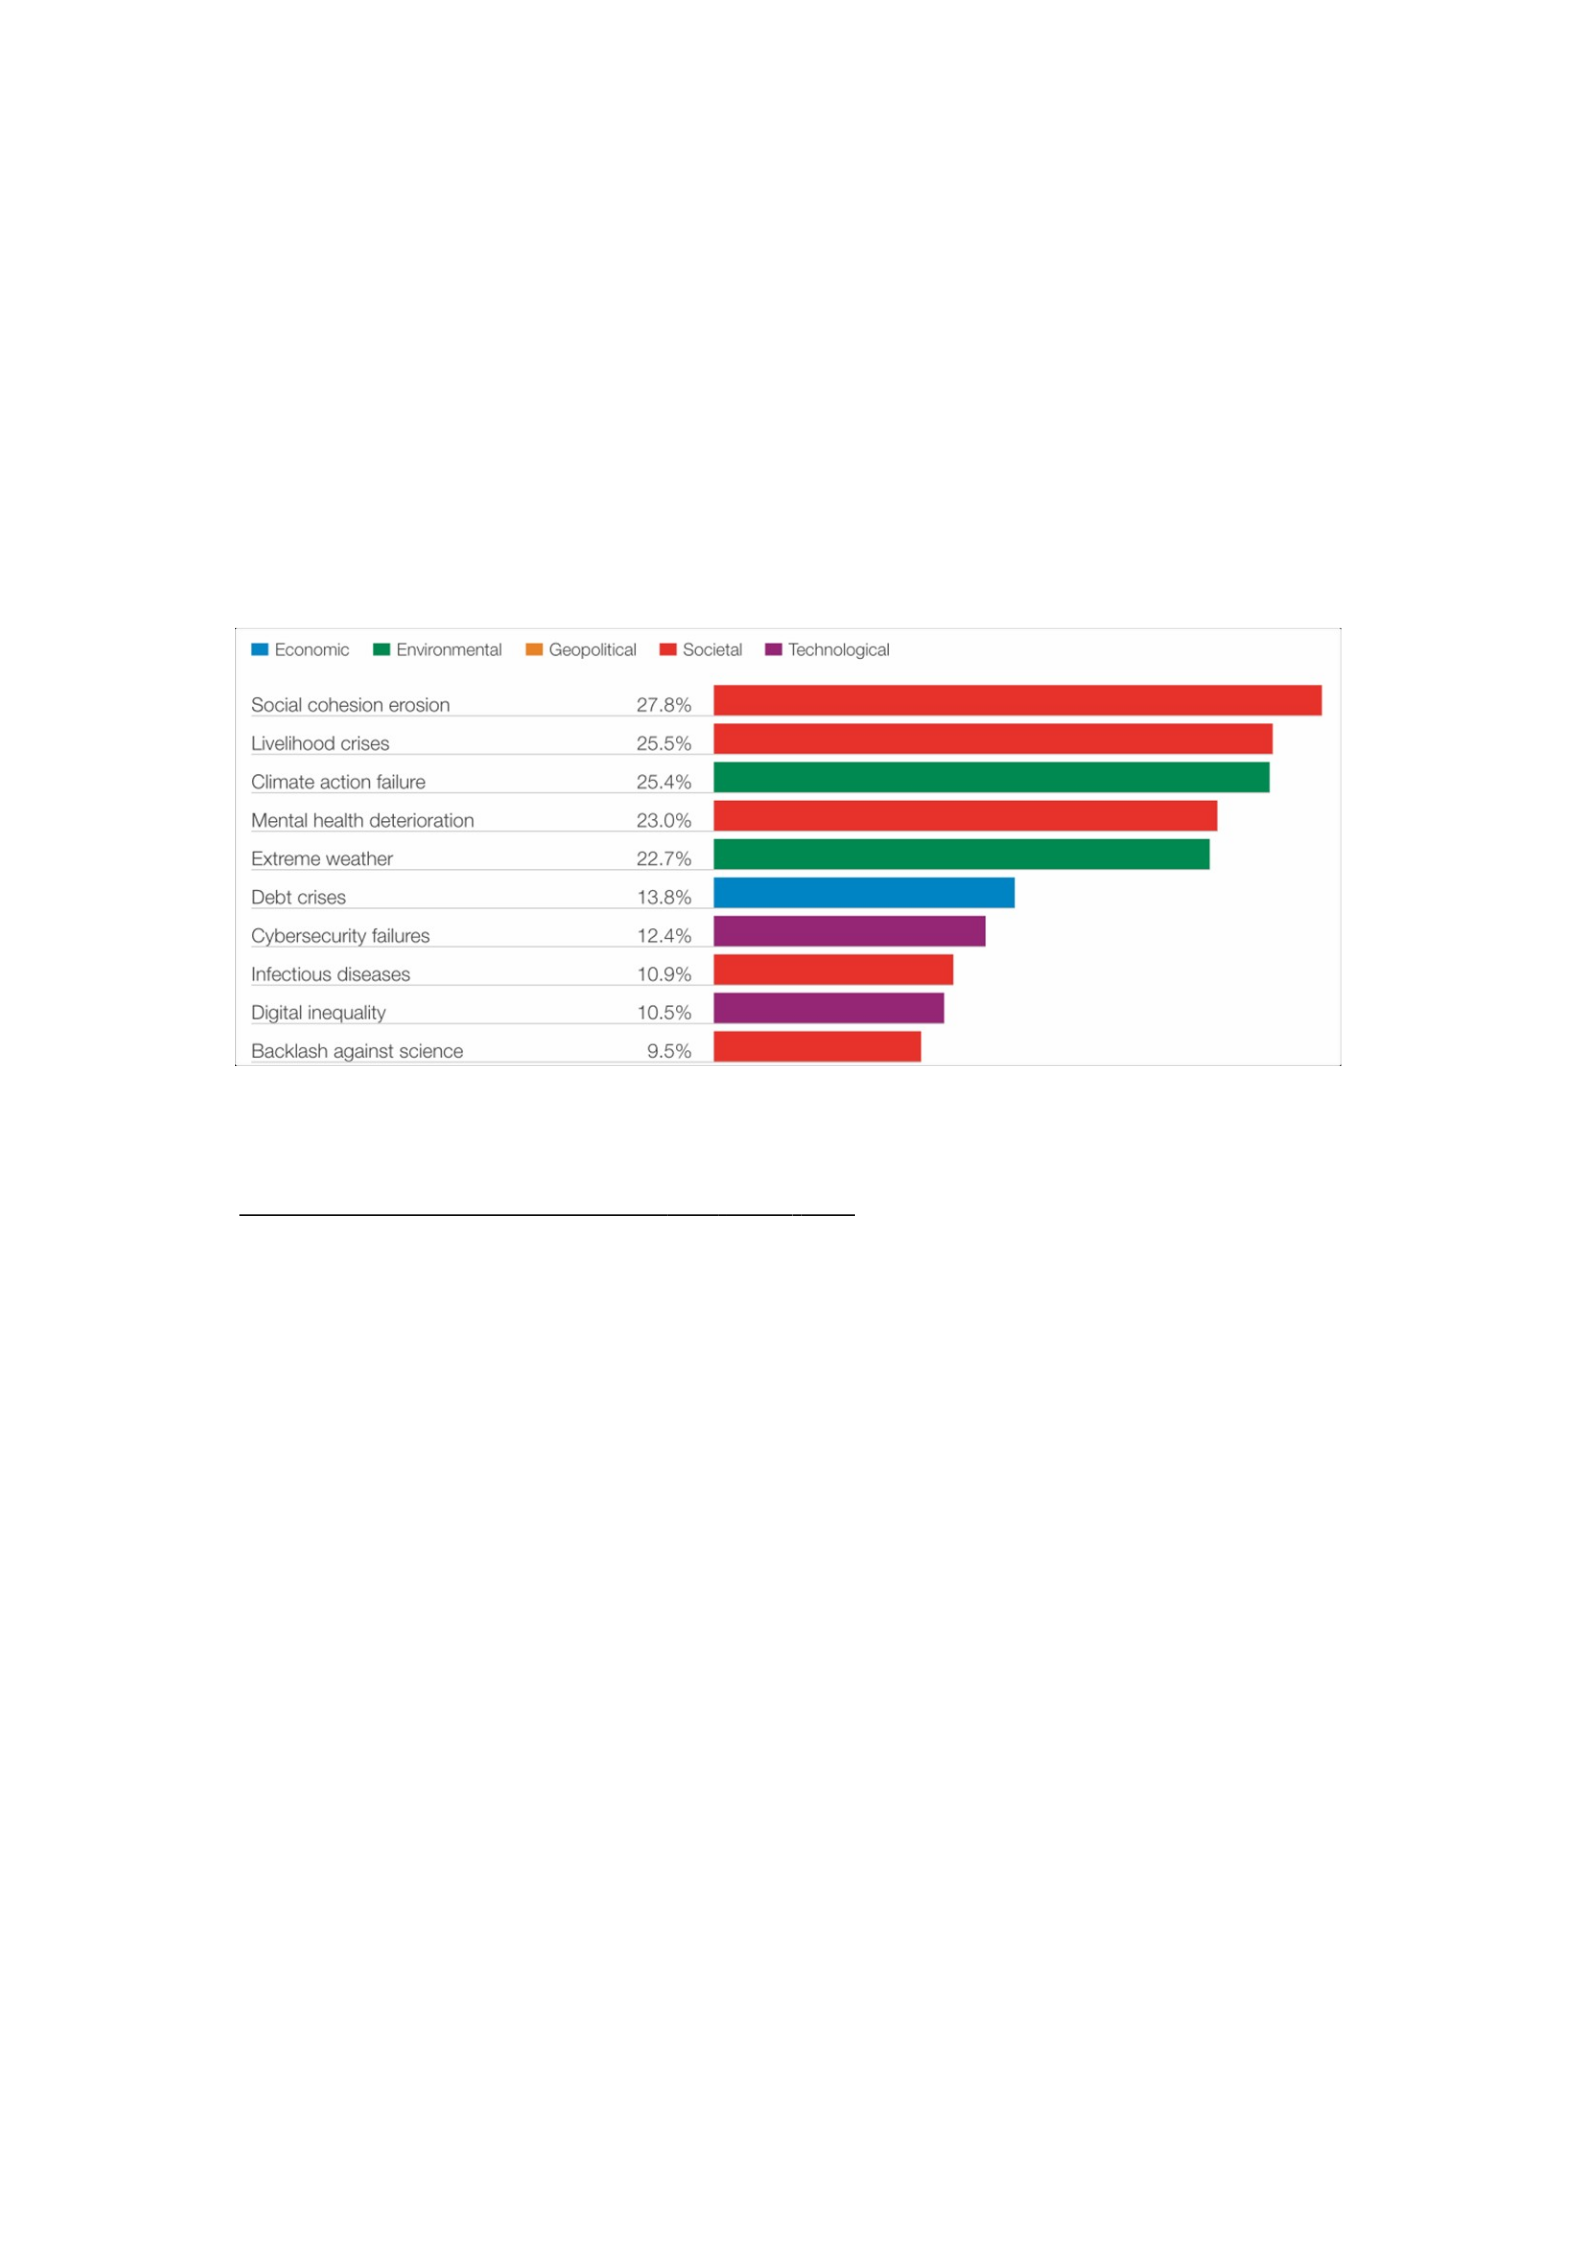
According to the latest global risk report by world Economic forum, cyber
security has become one of top 10 global risks which will carry cascading physical
consequences across societies, while prevention will inevitably entail higher costs.
(World Economic Forum, 2022).
Figure 3 World Economic Forum: world top 10 risks in 2021
Source: the global risks report 2022 17th edition insight report,
https://www.weforum.org/reports/global risks - report - 2022 (World Economic Forum, 2022)
2.1.2 Cyber information system failure
Cyber information system failure is one of the most common cyber safety and
security problem, which usually been ignored by those involved. Cyber information
system failures cover all aspects of the cyber issues, even the cyber-attack can lead to
the information system failure. However, the cyber information system failure may be
caused by both external and internal factors.
Unlike cyber-attacks, which usually result in direct cyber damage such as
financial losses and communication breakdown, cyber information system failures
may cause minor harm to the maritime industry and these system failures may be
easily recovered through the basic computer knowledge and computer skills of
personnel. These minor cyber incidents maybe sorted out by updating the software,
restart the network system or cooling down the circulation etc. (Oruc & Flinstone,
2019).
2.1.3 Data breaches
A data breach exposes sensitive or confidential information to unauthorized
people, or the files in data breaches are accessed or shared without permission.
Anyone could be in risk condition in the face of a data breach, from government to
enterprise and individuals. Whether you are offline or online, data breaches may
happen through the internet access, mobile information, Bluetooth sharing, text
messages etc. As long as people don't realize the widespread nature of data breaches,
they will not give it enough attention.
The cost of a data breach per year is on the rise and a significant percentage of
data loss comes from stolen or lost company laptops and portable hard drive
(Winnicki et al., 2017). In the era of big data, data safety is critical to the government,
enterprise and individuals, on the top of the operational costs there is the un-
quantifiable cost of data breaches.
Table 2 Top 10 breaches victims based on number of record stolen
No. Date Organization Industry Number of records
Stolen
1 Between 2013&
2014
Yahoo Email service
provider
3,000,000,000
2 October 2016 Adult Friend Finder Adult website 412,200,000
3 May 2016 MySpace Social media
website
360,000,000
4 Between 2007 &
February 2013
Experian Credit bureau 200,000,000
5 2012 LinkedIn Social media
website
165,000,000
6 February 2018 UnderArmour/
MyFitnessPal
Fitness
mobile
app
150,000,000
7 Between May &
July 2017
Equifax Information
solutions
company
145,500,000
8 May 2014 eBay Online auction
website
145,000,000
9 March 2008 Heartland Payment
Systems
Credit and debit
processor
134,000,000
10 December 2013 Target Retailer 110,000,000
Source: Trend Micro. https://www.trendmicro.com/vinfo/us/security/definition/databreach
(TrendMicro, 2020)
In the maritime industry, the importance of data has not yet been taken or valued
seriously, especially shipboard information data such as the static and dynamic
information from AIS, vessel`s movement data, cargo information etc. With data
breaches of these unprotected and open information, ships can easily be targeted by
hackers or terrorists or others stakeholders and turned into tools for terrorist attacks or
illegal benefits.
Figure 4 Breach methods observed across industries
Source: https://www.trendmicro.com/vinfo/us/security/definition/data-breach
2.2 Status of maritime cyber security
2.2.1 Legislation of Maritime cyber security
New information technology facilitates the management of shipping companies
and the safe operation of ships, however, while enjoying the benefits of new
information technology, maritime cybercrime threats that may affect the safety and
security of maritime industry which we need to assess and evaluate.

At present, the maritime industry is slow to act on these threats compared with
other industries. As a highly concerning hot topic, hackers and other illegal individuals
can easily exploit cyber security vulnerabilities to monitor ship activities and gain
access to compromised information.(Karahalios, 2020).
According to MSC.428(98), cyber risks should be appropriately addressed in the
Safety Management Systems (SMS) no later than the first annual verification of the
Document of Compliance (DOC) after January 1st, 2021. The Guidelines on maritime
cyber risk management laid down in MSC-FAL.1/Circ.3 and MSC.1/Circ.1526, both
of them annexed, contain recommendations for maritime cyber risk management and
should be taken into account when developing appropriate safeguards against cyber
threats and vulnerabilities. Ship owners, ship managers, ship operators, masters,
classification societies are advised to act accordingly(IMO, 2017b).
In response to above mentioned IMO cyber security documents, a number of
shipping associations and classification societies have launched guidelines describing
the methodology for maritime cyber risk assessment and making recommendations on
the developing, implementing and improving management systems to assist the
maritime industry dealing with ever-growing cyber threat, e.g. the China
Classification Society has published the guidelines on maritime cyber risk assessment
and cyber safety management system( 2019); the ENISA issued a guideline for
cybersecurity in the maritime sector: Cyber risk management for ports in 2020; the
DNV issued the recommendation practice of cyber security resilience management for
ships and mobile offshore units in operation (2021).
However, cybersecurity is not just a particular issue within the maritime sector, it
is a global crisis which is definitely not able to be sorted out by maritime related
stakeholder only. In the actual of fact, there has been limited discussion on how
shipping companies can educate or train their employee against existing cyber threat.
In this paper, therefore, we will use a risk-based methodology to identify
maritime cyber threats; evaluate the severity of each potential risk; and give
immediate actions and corrective actions for short and midterm period.

2.2.2 Maritime cybersecurity status
According to IBM`s security researchers and the cyber security intelligence
index, 95 percent of successful hacking attacks or cyber incidents were because of
some type of human error(2014). The maritime industry's high reliance on advanced
information and communication technologies exposes the vulnerable maritime cyber
safety and security in the age of intelligent today. As more and more maritime related
cyber security are being reported to the public, attention is being drawn to this
previous overlooked area. Cyber threat has been highlighted on the reviewed of
maritime transport version 2020 and 2021 by UNCTAD (2022). The facts that
maritime industry is increasingly structured around automated system and integrated
into information technology networks make the cybersecurity measures become an
essential priority.
In the maritime industry, both on the shore-based and on the shipboard
themselves, the issue of cyber security is currently highly dependent on the efforts of
the shipping companies and management enterprises themselves, and the international
organizations of the industry have not shown any creative and strong measures to deal
with the global issue of cyber security.
Although we have seen some efforts and attempts by many international
organizations, particularly the IMO, these efforts are merely the guidelines or
recommendations, and it is obvious that only relying on maritime experts who are
non- IT background will not make a substantive step, this is because that cyber safety
and security is evolving into a global critical issue that affects all industries of the
world including the maritime industry.
Cyber-attacks in the maritime industry have become exacerbated over the last
couple of decades due to limited ability to protect against cyber threats (Trump, 2020).
Another issue is the limited number of maritime cyber incidents that are reported due
to the concerns about protecting the company's reputation, however, the numerical
underreporting of cybersecurity incidents is becoming a major weakness in the
maritime industry`s response to cyber security issues (Safety4sea, 2019).

2.2.3 Typical shore based maritime cyber security issues
Maritime shore based cybersecurity incidents are similar with the most common
cyber incidents as the shore based maritime network are linked to common network
system, with three main aspects: i) cyberattacks from various sources, ii) cyber
incidents due to operational errors, and iii) data breaches due to lack of security
awareness.
The most typical cyber-attacks in maritime industry recently years was the
shipping company MAERSK cyber incident in 2017, the container giant faced the
cyber-attack of a ransomware, caused its commercial and logistic operation
breakdown, not only damaging the company`s reservation system and losing vessel`s
tracking, but also causing congestion in almost 76 ports around the world operated by
its subsidiary, APM terminal (Jensen, 2017).
The maritime related critical infrastructures such as port operator, maritime
administrative agency, government information system etc. are also the easy targets
for illegal cyber activities as the maritime industry is much slower to develop in terms
of emerging information technology than other industrial chains.
Last year, on May 7, 2021, the hack used a single compromised password to take
down the largest fuel pipeline in the U.S. and cause shortage across the East
Coast(William & Kartikay, 2021). Major oil terminals in some of western Europe`s
biggest ports have fallen victim to a cyberattacks on Feb 4, 2022, caused some
terminals disrupted (Safety4sea, 2022a).
2.2.4 Typical shipboard cyber security issues
Shipboard cyber security is complicated, the interconnection of ship`s computer
systems has exposed to increasingly cyber threats while obtaining convenience.
Cyberattacks against ships can target any network vulnerability in the system to
achieve their objectives(Elisa et al., 2020).
The most common cyber risks on board vessel nowadays is the traditional
electrical navigational system such as RADAR, GPS, ECDIS, AIS etc. which are
usually not the easiest targets for hackers, but they are the most vulnerable devices in
the ship's network information system (Svilicic, Rudan, Jugović, et al., 2019). The
prevails integrated navigational system consolidate information from all independent
navigation system such as RADAR, GPS, AIS, ECDIS, Engine telegraph, echo
sounder etc. and even the latest integrated navigational system can update the real
time information through the internet.
Take AIS as example, the AIS was setup with the intention of assisting vessels in
situational awareness by providing them with information about the traffic situation
beyond their visual capabilities and traditional radar capabilities. As the AIS
information transmission, lots of the message can be received by anyone in the
vicinity who wants to know about the ship, which may include people with illegal
intentions such as pirates, terrorists or other criminals. This interoperability of
information within a specific range was the original design of AIS, but this kind of
data breaches is nothing compared to the internet websites that broadcast the location
of thousands of vessels around the world, such as Shipxy, FindShip, MarineTraffic,
VesselFinder, Vesseltracker, etc.(Bothur et al., 2020). And the research have shown
that fabrication of ship`s AIS information is possible, this will bring another risks on
shore based traffic monitor system and navigation problem.(Ray et al., 2015).
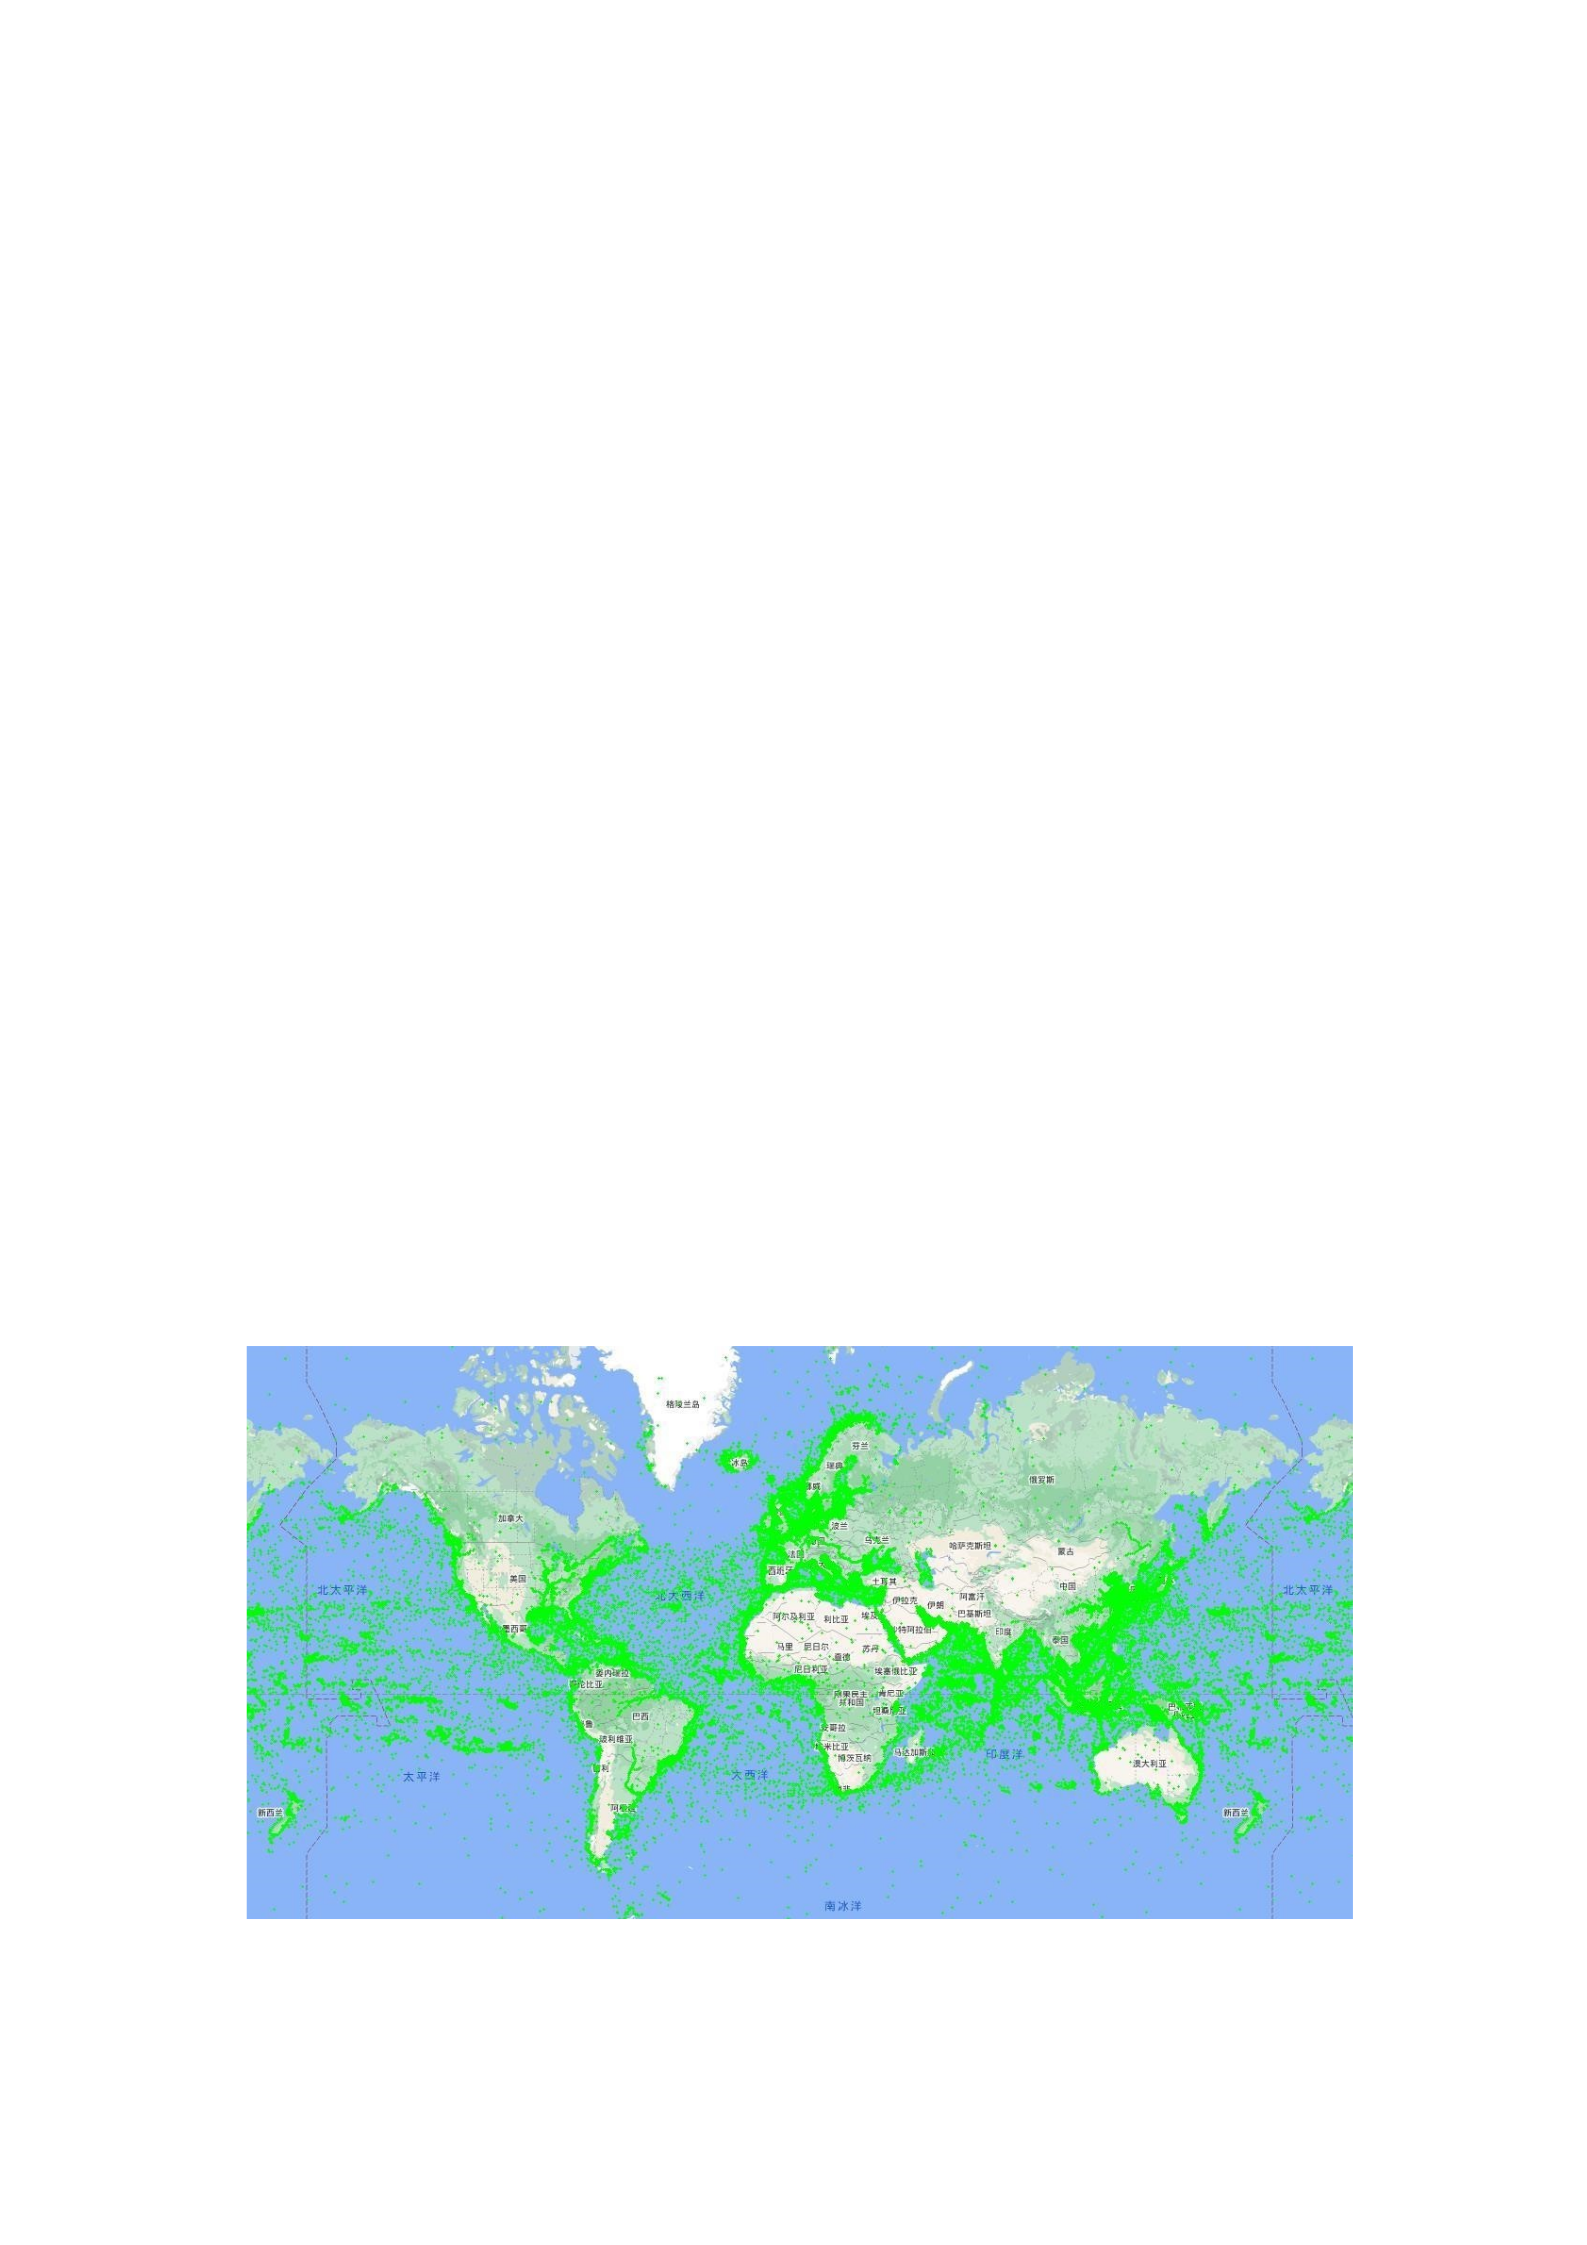
Figure 5 Shipxy AIS information on Feb 07,2022 1606(GMT+8)

Source : Shipxy website:http://www.shipxy.com/(Shipxy, 2022)
The ECDIS is another very important equipment onboard in safe navigation by
providing integrated real time information and significantly reducing the workload,
the ECDIS is generally a software running on a computer system that could be
comprised of the third party components, however the research shows that even the
type approved ECDIS with proper software and operating system updated could be a
source of a vulnerable cyber threat (Svilicic, Rudan, Frančić, et al., 2019).
Shipboard cyber threat was initially highlighted by the shipping company due to
the ship shore email system breakdown which cause the vessel losing control and
surveillance from the shore based management level (ICS, 2020). When it comes to
cyber security on board, all shipboard computer based systems have been escalated as
a source of security threat. In the first few years of the shipboard cybersecurity issue
been raised up, the USB interface was considered to be the only way to threaten the
ship`s network and was well managed and controlled when I was a mate onboard
ships.
The other important issue which may be the critical viewpoint that the
crewmember lack of general knowledge in the network field of shipboard
cybersecurity. There is no specific computer knowledge and skill requirement on
officer and crew education and training requirements as per STCW(IMO, 2017b).
Seafarer are one of the lowest barrier professions, especially the ratings, with no
specific educational requirements and only some mandatory trainings required to join
a ship, where these mandatory training program even does not include basic computer
skills, let alone maritime cyber security (IAMU, 2019).
The regulatory hierarchy tacitly assumes that all crew members have some basic
computer cyber information skills that are competent for the shipboard cyber
environment, however, this viewpoint is obvious outdated and incorrect in today`s
world where shipboard cyber information technology is evolving with the times.
From this perspective, the maritime regulator should be held inescapably responsible
for the occurrence of shipboard cyber security incidents at least. It is already a

mandatory requirement under the ISM code although maritime cyber security is not
specifically mentioned (IAMU, 2019), but these simplified requirement are far from
adequate in light of the threats facing the maritime industry.
3 General cyber threats in the maritime industry
3.1 Traditional cyber threats in the maritime industry
Cyber security is now recognized as one of the major challenges for the global
risks, including the maritime industry. There are numerous maritime cyber
information systems, whether onboard ships or ashore, built with international
standard components. Maritime cyber infrastructure and shipboard navigational
systems are considered to be systems whose operation and management are critical to
the safety and security of the maritime industry (Canepa et al., 2021).
Intentional shipboard cyber-attacks are often launched in regular steps, initiating
with scanning for weakness point of the network system, and then executing the attack
by disabling the computer system or stealing the confidential data or both. Compared
with intentional cyber-attacks, un-intentional cyber security incidents are usually
caused by human error. And the below figure 6 shows the common types of maritime
cyber-attacks.
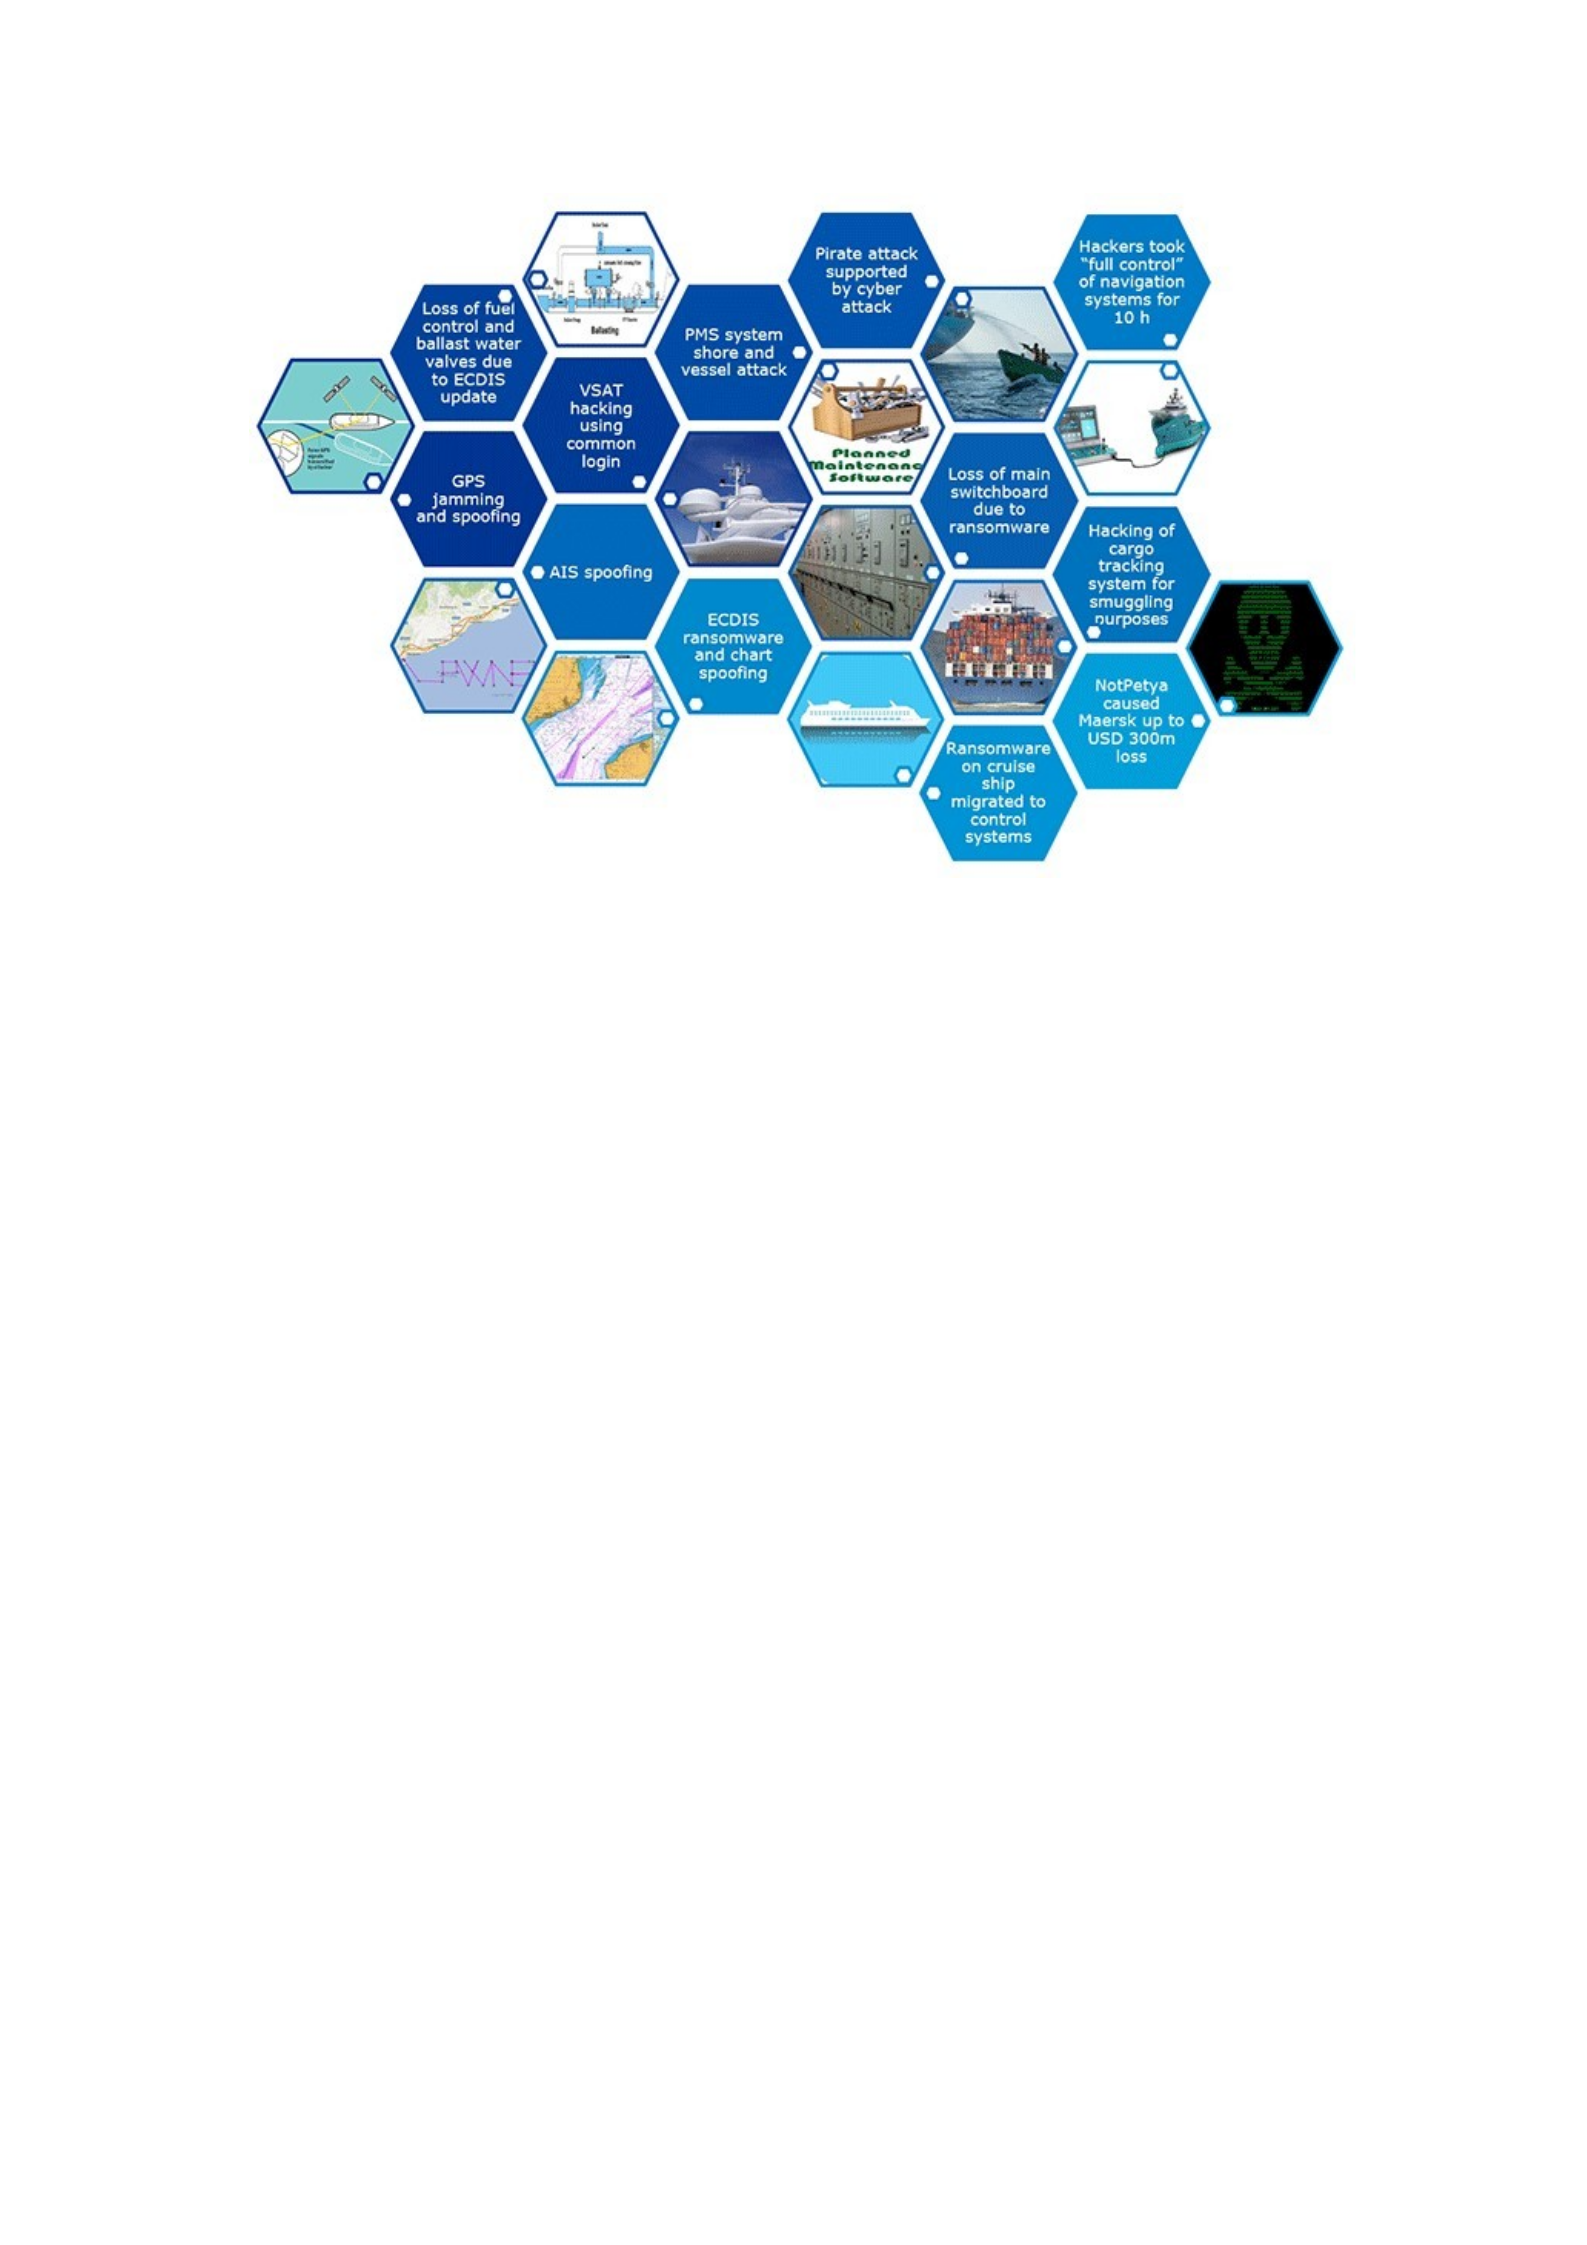
Figure 6 General cyber issue on board
Source: https://www.dnv.com/maritime/insights/topics/maritime-cyber-security/index.html
3.1.1 Human error
According to IBM security researchers and the cyber security intelligence index,
95 present of successful hack attacks or cyber incidents were because of some type of
human error (2014). In general, cyber incident both on board ship and ashore happen
due to weakness on user`s behavior.
Human error can be divided into two sections, one is lack of knowledge on
information technology, we call skill-based error, such as computer skills. And the
other one is cyber security awareness, we call awareness-based error, such as not
having enough information about the specific circumstance. Both lack of IT
knowledge and cyber security awareness could lead severely cyber incident.
Although we start this paragraph with a frightening statistic, we can look at this
statistic in a different way. If 95% of vulnerabilities are caused by human error, then
taking even the smallest steps to reduce human error can create huge benefits in terms
of cyber security (Ahola, 2019).

3.1.2 Malware
Malware is a catch-all term for any type of malicious software designed to harm
or exploit any programmable device, service or network. It is often used by
cybercriminals to extract data for financial gain. In the maritime industry, these data
include port rotation information, ship arrival and departure details, charterers`
financial data, shipboard official and personal emails and passwords—the possibilities
of what information can be compromised have become endless(McAfee, 2022).
Malware combines all types of malicious software, including viruses, ransomware,
scareware, worms, spyware, Trojans, adware, file-less malware etc.
One of the most profitable and popular types of malware amongst cybercriminals
is ransomware. This malware usually installs itself onto a target’s network device, and
then encrypts their documents and files, afterward the cybercriminals ask for the
ransom.
In general, the most common signs that cyber system been affected malware are
the following: i) the computer system become slow; ii) your web browser redirects the
sites you visit; iii) infection warnings with solicitations to register or buy something to
fix; iv) software breakdown or system restart; v) continuous pup-up ads.
3.1.3 Phishing
Phishing is a general approach of cybercrime in which someone posing as a
legitimate organisation contacts a target via email, phone or SMS to trick individuals
into providing confidential data such as financial data, password, personal
identification information, bank account details etc.
The shipboard cyber-attacks are usually suffering from the phishing emails with
the feature of attachments, urgency message and hyperlinks. The figure 5 is a great
internet resource that outlines 22 social engineering red flags commonly seen in
phishing emails (2017), these infographics will show us what to watch out for in
emails during daily works.
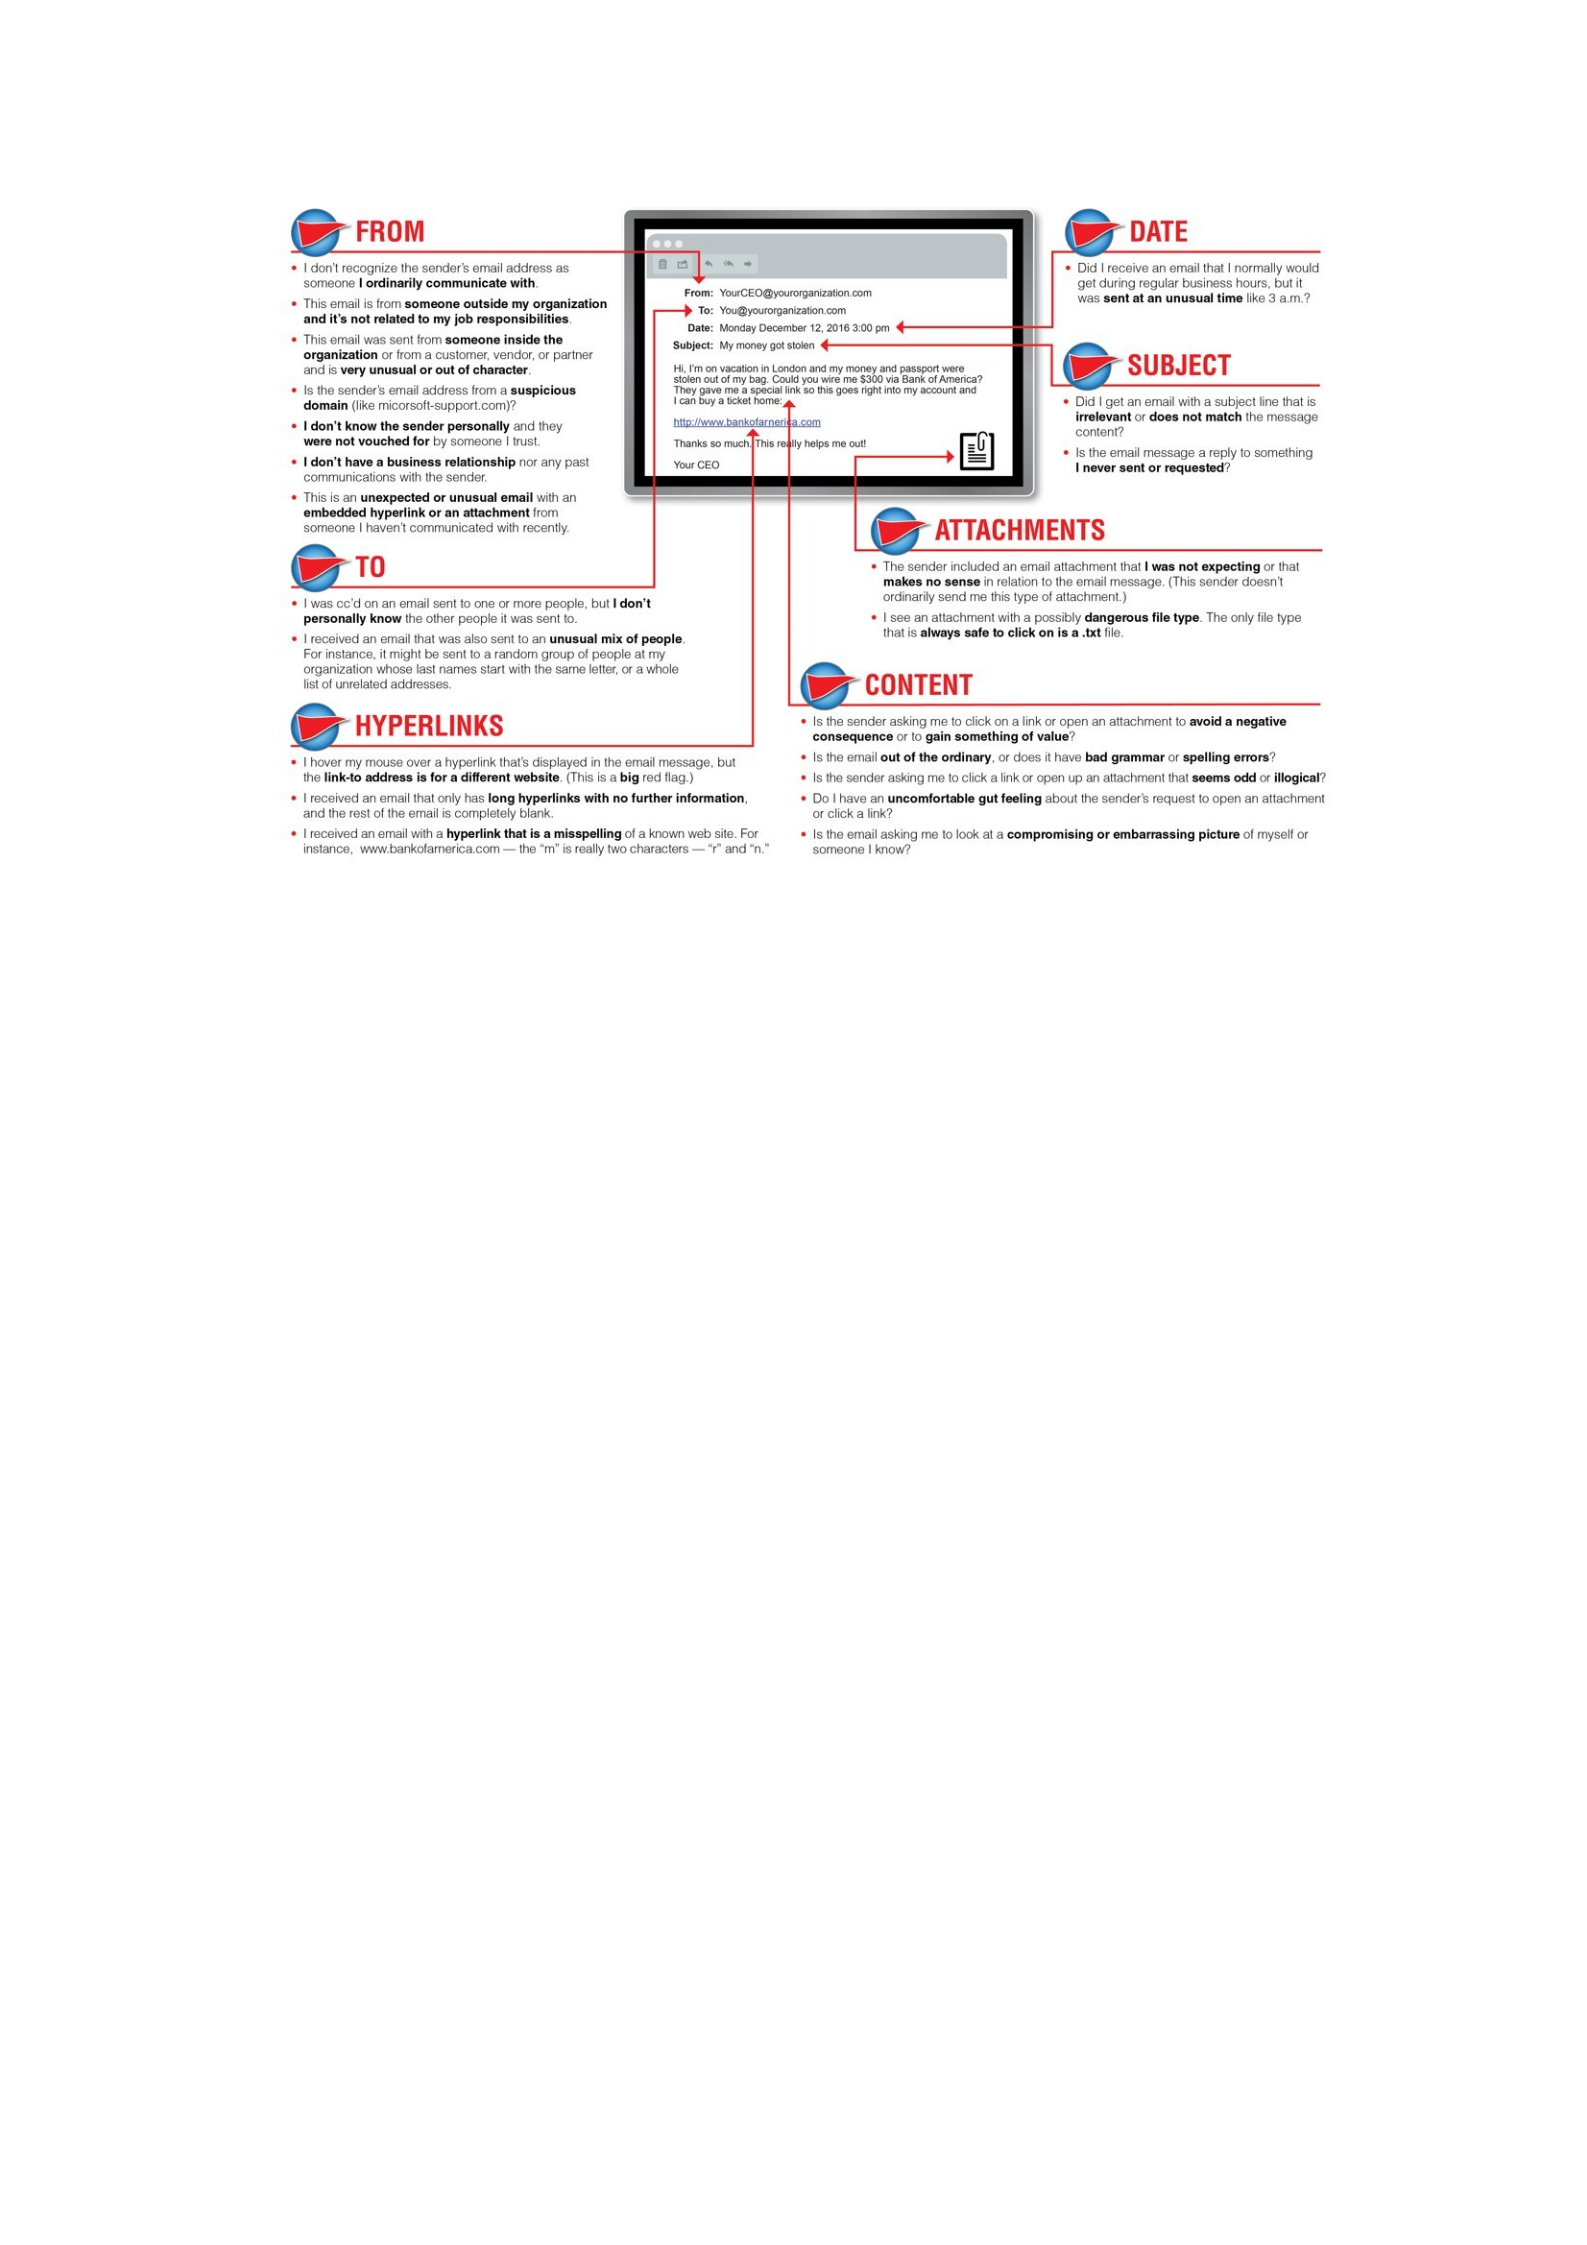
Figure 7 Example of phishing email
Source: Knowbe4. https://www.knowbe4.com/hubfs/22RedFlags.pdf?hsLang=en (Knowbe4, 2017)
3.1.4 DoS and DDoS attacks
Denial of service (DoS) attacks and distributed denial of service (DDoS) attacks
aim to overload the target resource with requests to exhaust the bandwidth, attempt to
bring down a target server, service or infrastructure. A DDoS attack is able to leverage
multiple compromised devices to bombard the target with traffic. Amazon Web
Services experienced an DoS attack with a peak volume of 2.3 terabits per second in
February 2020 (BBC News, 2020).
There are many different types of DoS and DDoS attacks; the most typical are
TCP SYN flood attack, teardrop attack, smurf attack, ping-of-death attack and botnets
(Melnick, 2018). Shipboard computers and critical equipment network systems are
usually old and slow to be updated, making it difficult to have effective protection
against DoS and DDoS attack.
3.1.5 Man in the middle attacks(MITM)
A man in the middle attack is a traditional type of cyberattack, but it is still one of
the most popular cyber-attack approach in today`s world. The cybercriminals often
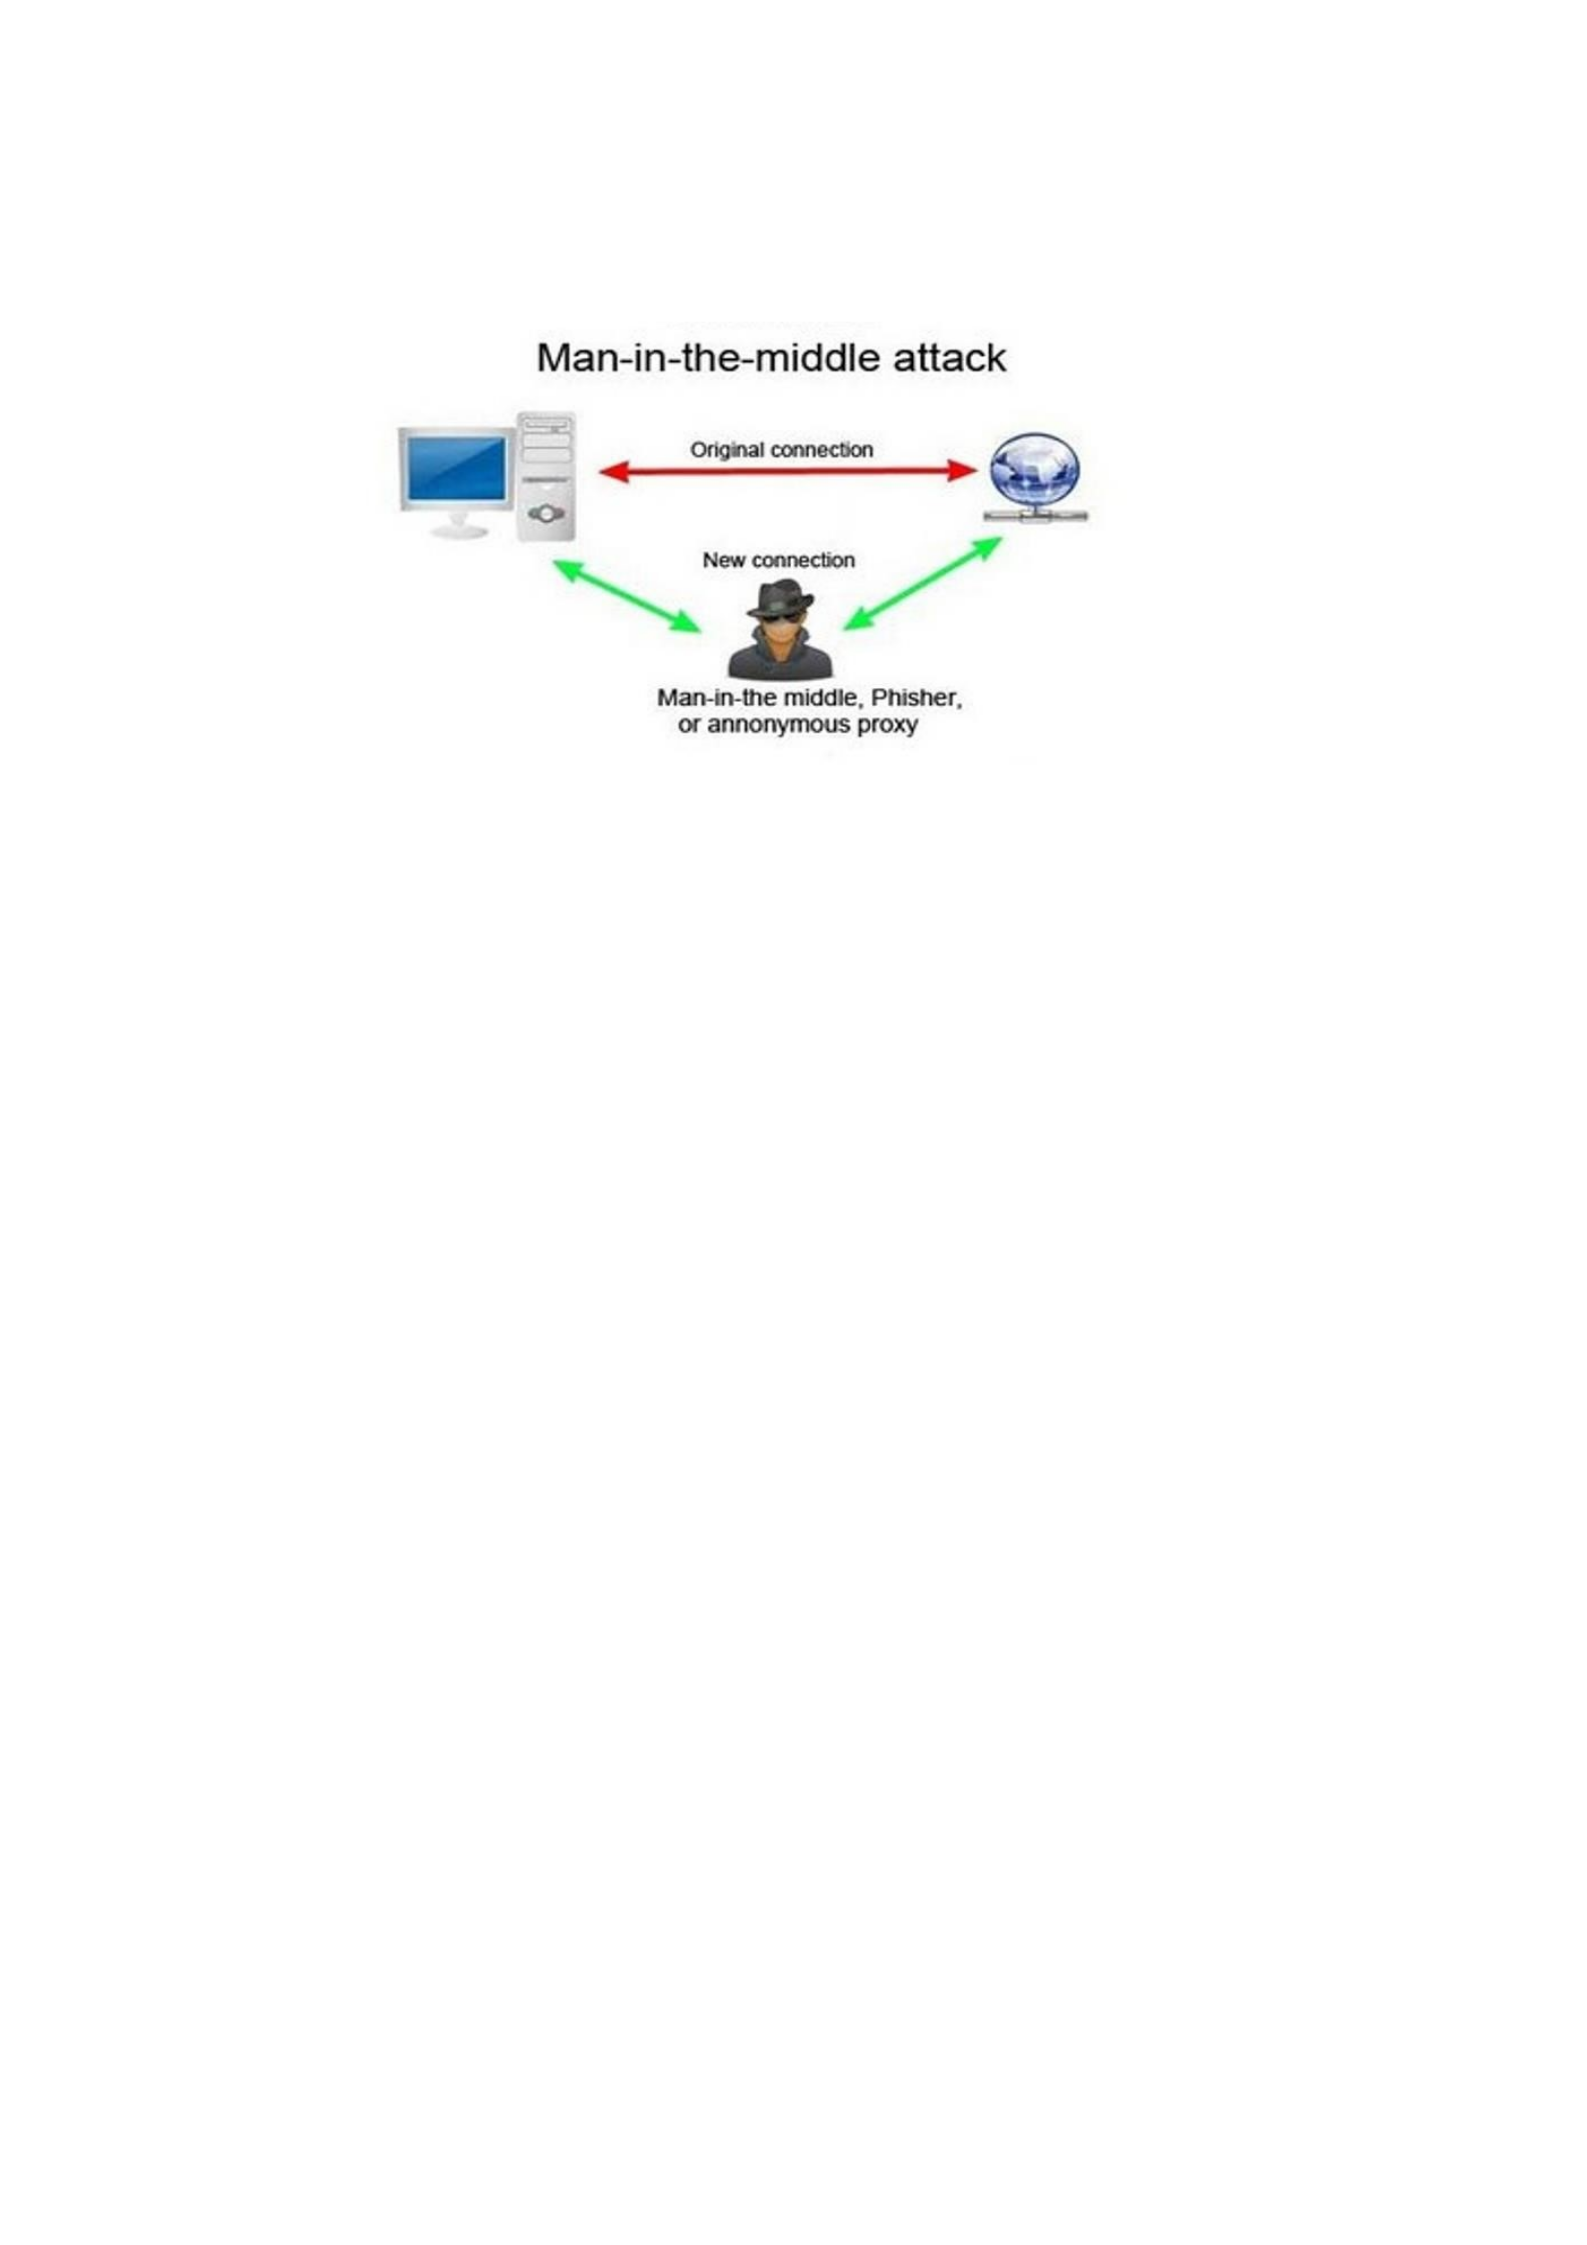
spy on victims and steal personal information or credentials, and tamper with data by
intercepting normal network communication data.
Figure 8 Man in the middle attack
Source: Baike.Baidu. (Baike Baidu, n.d.)
Today, while most email and chat systems use end-to-end encryption to prevent
third parties from tampering with data being transmitted over the network, there is still
a wide scope of MITM, with attacks such as session hijacking and DNS spoofing etc.
3.1.6 Expired/outdated IT system
In maritime sector, the shore based systems are connected to the global internet
system and are also able to ensure updates and effective antivirus. Shipboard
computers and critical equipment network systems are usually old and slow to be
updated, making it vulnerable to common cyber security threat, and therefore the
shipboard IT systems are in the worse situation compared with the shore-based cyber
systems due to the specific cyber environment onboard(ISO/IEC, 2019).
Expired software and outdated hardware system are the main source of threat to
shipboard cyber system, which directly contributes to shipboard cyber security being a
major cybersecurity concern for the maritime industry and a prominent weakness in
maritime cybersecurity that has attracted attention from publics.
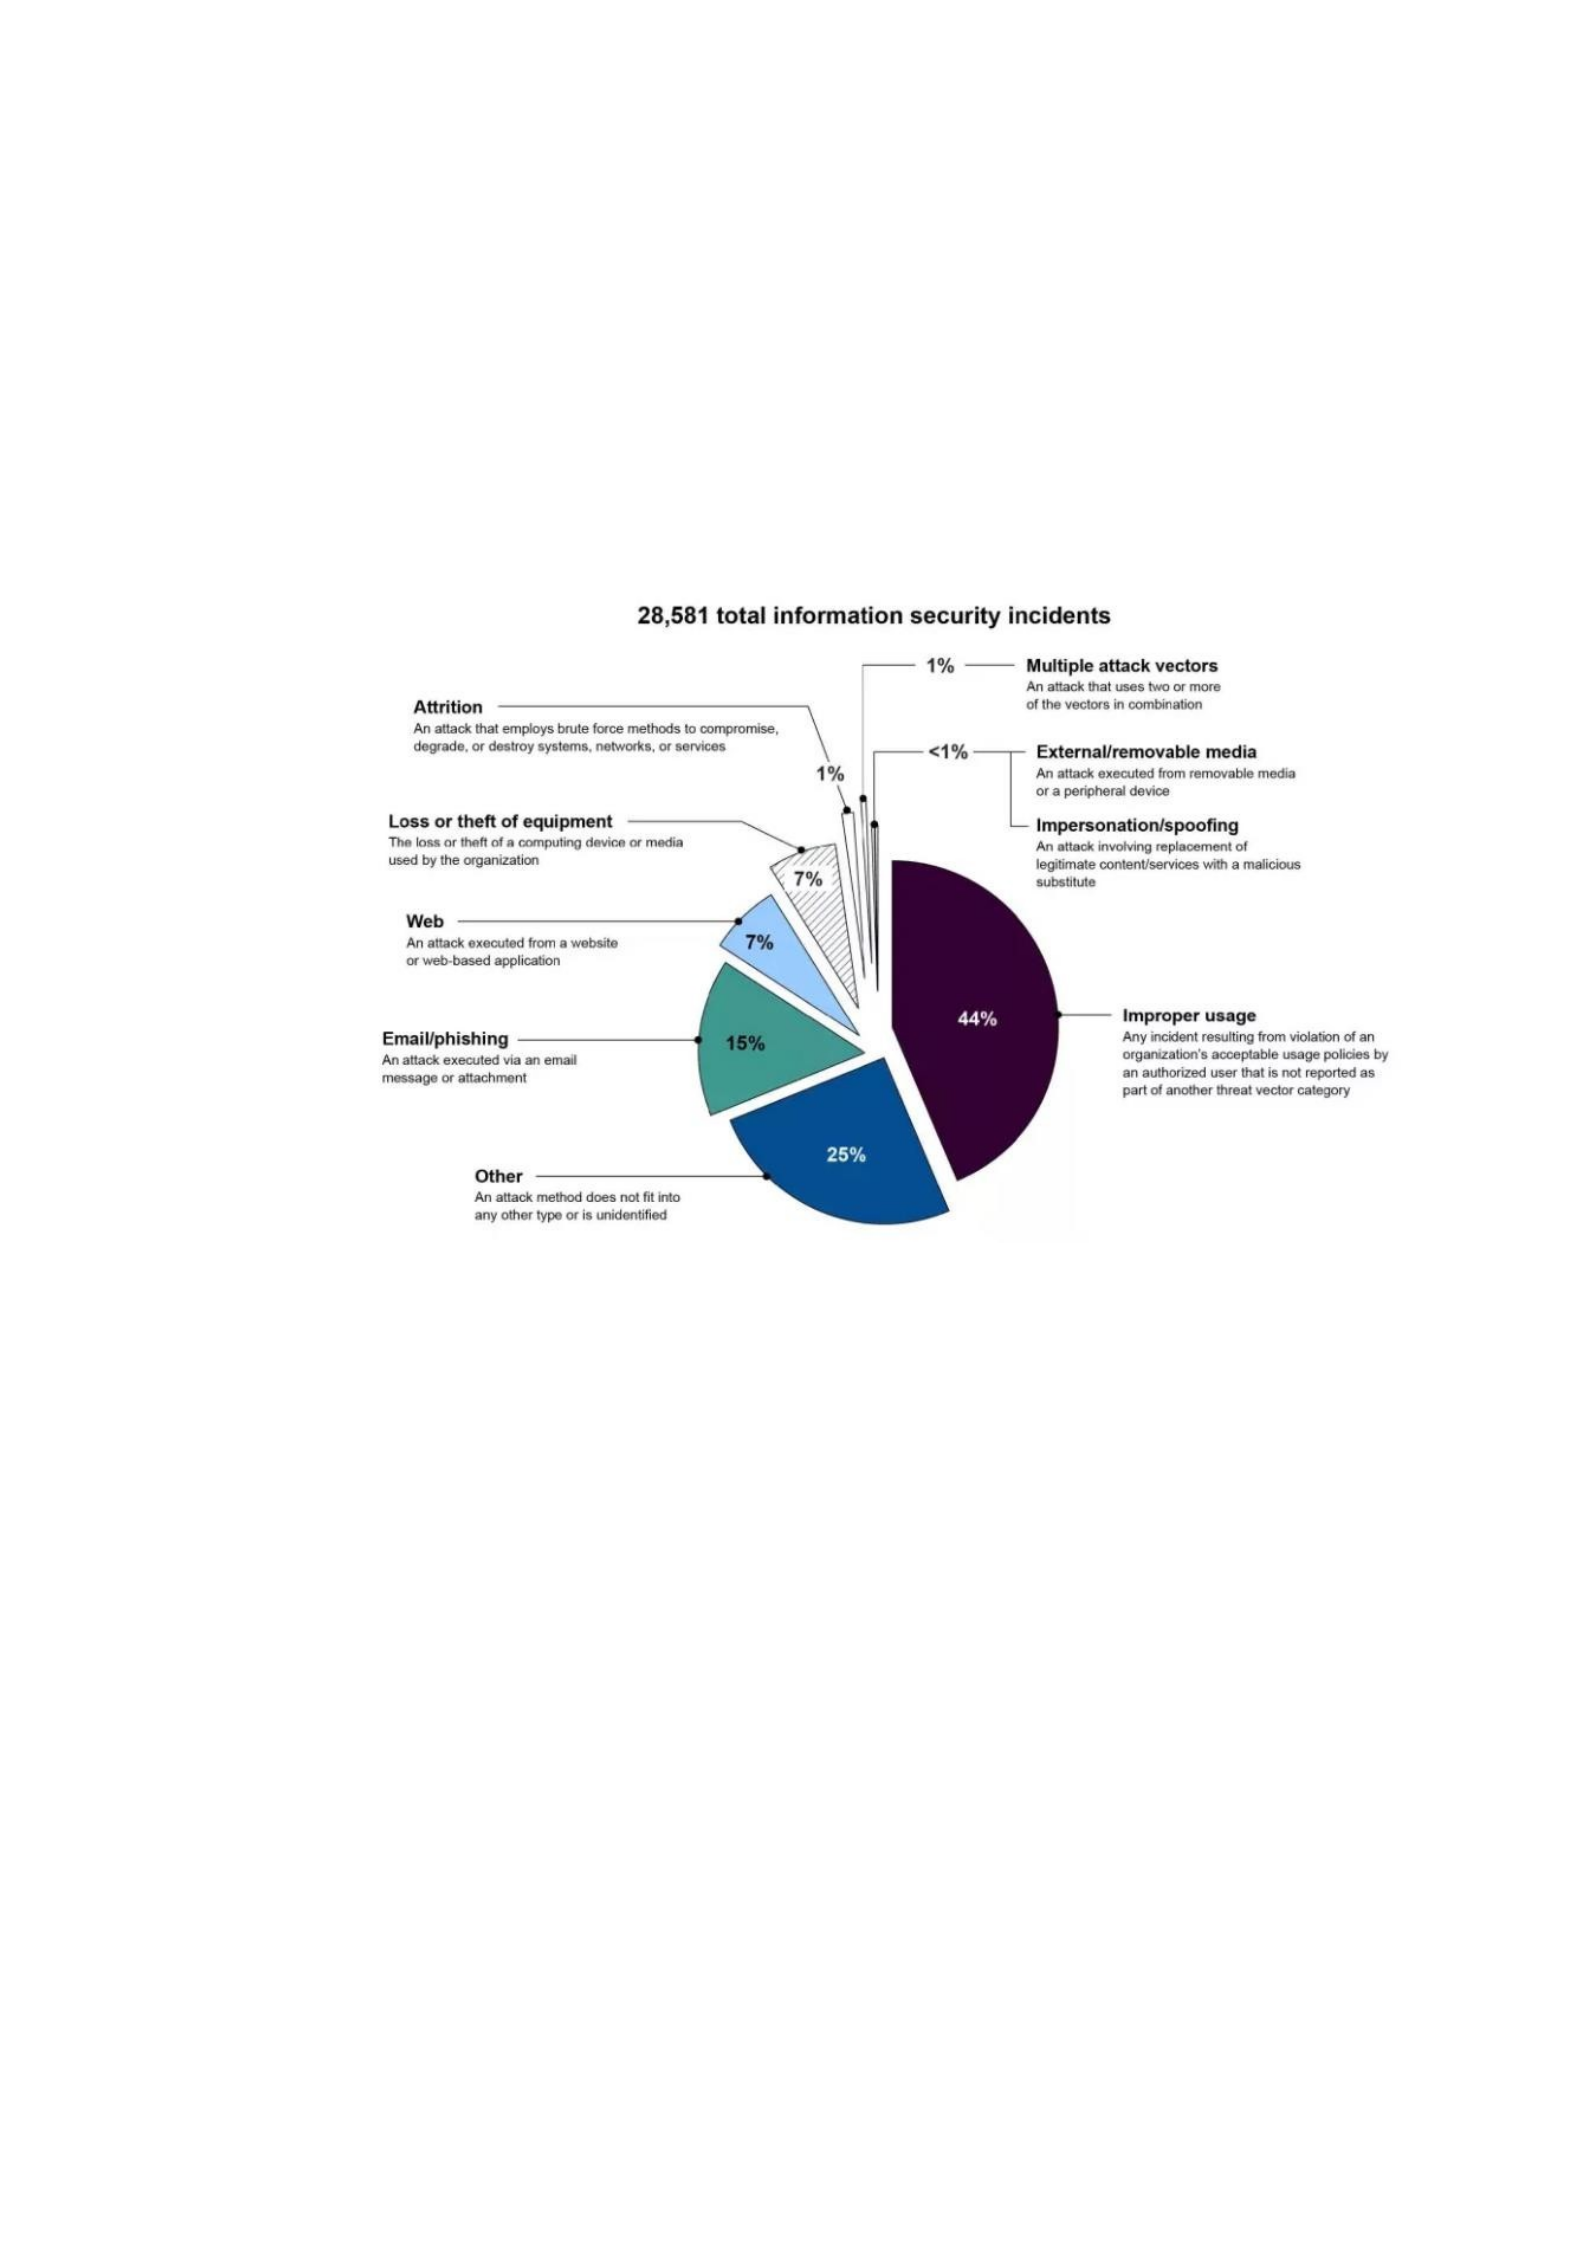
The above examples listed from 2.3.1 to 2.3.5 regarding to the maritime cyber
security threats are not exhaustive, the BIMCO guideline on cyber security onboard
ships give another 11 general types of cyber-threats(BIMCO et al., 2021), we could
even list thousands of cyber threats affect maritime industry as shown in figure 9. As
information technology continues to evolve, cyber security issues continue to grow in
number and complexity.
Figure 9 Distribute of 28581 total cyber incidents
Source: GAO analysis of united states computer emergency readiness team and office of management
and budget data for fiscal year2019. (U.S. GAO, 2019)
3.2 The latest DIT in maritime industry and threats
3.2.1 Digital information technology
Global industrial civilization has gone through four eras that today into the
electronic age which used to recognize that the age started in 1940 after the first
computer was invented (Techwithtech, 2022). When it comes to emerging information
technology nowadays, people used to think about the computer, smart phone, internet,
laptop etc.
Information technology (IT) is the utilization of any system from painting to
books that can be used to store, retrieve and transmit information; Digital information
technology(DIT)can best be defined as using computers to create, process, store,
and secure electronic data. As per Fenil Savani, digital information technology
concentrates on converting data into information and then vice versa. In addition,
digital information technology is used to transfer data and information in the form of
images, texts, sounds, and videos (2021).
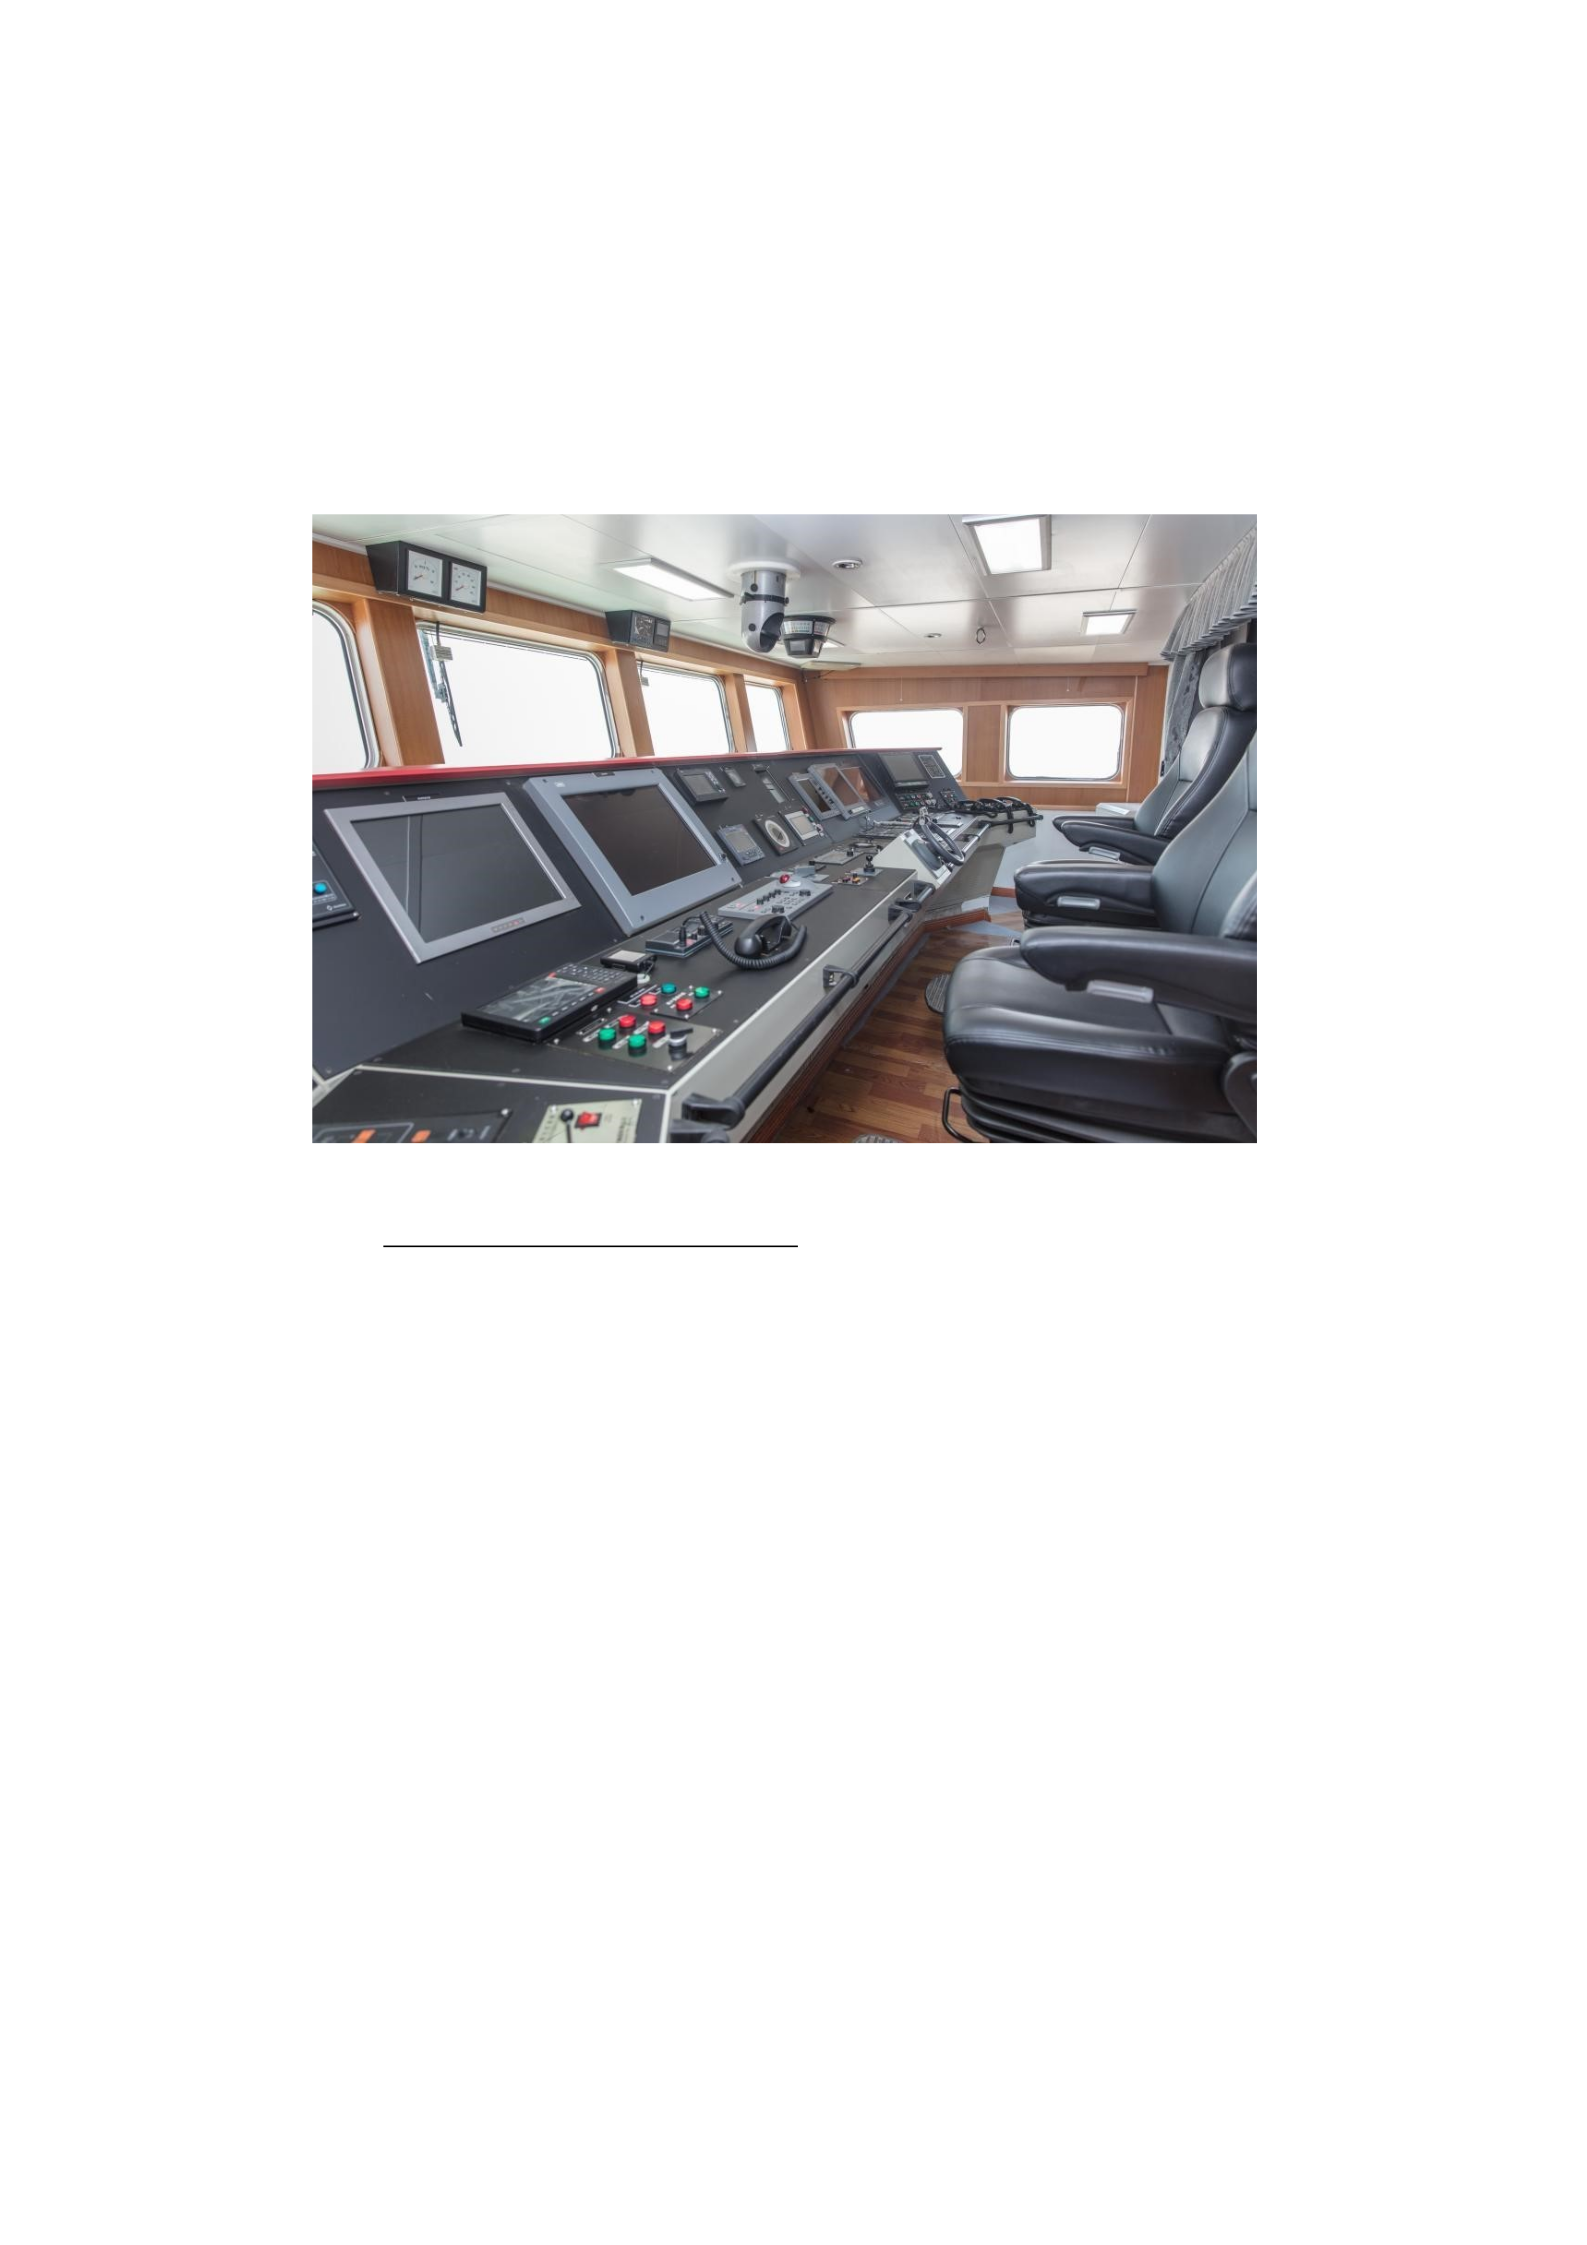
Figure 10 Integrated bridge system: highly dependent on DIT
Source: http://cbgl.zjou.edu.cn/zyk2jj/cbss.htm
At a time when digital information technology is widely used in all aspects of
human life, most people downplay the essence of the sophisticated field of digital
information technology. Especially in the maritime industry, it is easy to overlook the
cyber security threats associated with digital information technology while enjoying
the convenience it brings.
The digital information technology in maritime industry include all modern
electronic equipment fitted onboard ship and ashore, such as LRIT, GMDSS
shipboard stations and shores based station, EPIRB ship unit and shore based stations,
VDR,
ECDIS, AIS, GPS system, machinery monitoring system etc. As one of the major
game changer nowadays, the digital information technology is having an increasingly
profound impact in the maritime industry in combining with the Big Data, Cloud

computing, Internet of Things, Block chain, Artificial Intelligence etc. There is no
doubt that firms and organizations that priorities the adoption of emerging digital
information technology will gain a definite competitive advantage in the near future.
3.2.2 Big data
Big data is recognized as the current buzz word in almost all industry in the last
five years. As the Oxford dictionary defines Big Data as “sets of information that are
too large or too complex to handle, analyze or use with standard methods” (2022).
As a maritime practitioner, we are not breaking a new field when we are taking
about maritime big data, just because the maritime industry has responded positively
to the word of big data, even though the maritime sector is generally slow to response
to the new technology.
In the actual of fact, big data has involved almost all industries such as banking,
finances, healthcare, education, telecom etc. but it is not prominent in the maritime
industry and especially contribute less to the general operations on board ships.
However, we are still enjoying the benefit it brings, for example, the website of
maritime traffic which is available for all AIS data. The challenge is obvious that
comes to my topic that the cyber safety and security is not guaranteed in the big data
era today (Container-xchange, 2020).
While every single information been brought to the cloud platform, lack of
supervision and intruding by unauthorized users could lead the entire bodies subject to
severe losses which was happened as an example mentioned in chapter 2.2.3 the US
colonial-pipeline company.
Figure 11 Big data and ships at sea
Source: https://image.baidu.com/
3.2.3 Cloud computing
Instead of storing the data to the computer or other personnel hardware, cloud
based storage has become a popular option for people at works while internet is
available. Cloud computing was created together with big data, while a massive
quantities of data been collected at an exceptional rate and stored with very low cost,
the company with interests in maritime industry have unparalleled opportunities to
gain new strategies insights(IHS Markit, 2022).
The transformation of those data to valuable information is challenging. Cloud
computing is the delivery of various information services via internet through remote
server to make the cloud data been effective used. These information service we called
cloud computing include data storage, networking, databases, servers, and software
etc.(Frankenfield, 2020).
As cloud computing is highly relying on the internet speed, shore based maritime
industry may make greater use of this emerging technology, and cloud computing on
board will depend on the shipping company`s internet service. While the big data and
cloud computing help the shipping company eliminate intuition and promote better
decision, the concerns of cloud computing security or, more simply, cloud security are
usually categorized in two directions: the safety and security grade of cloud provider
and the user itself.
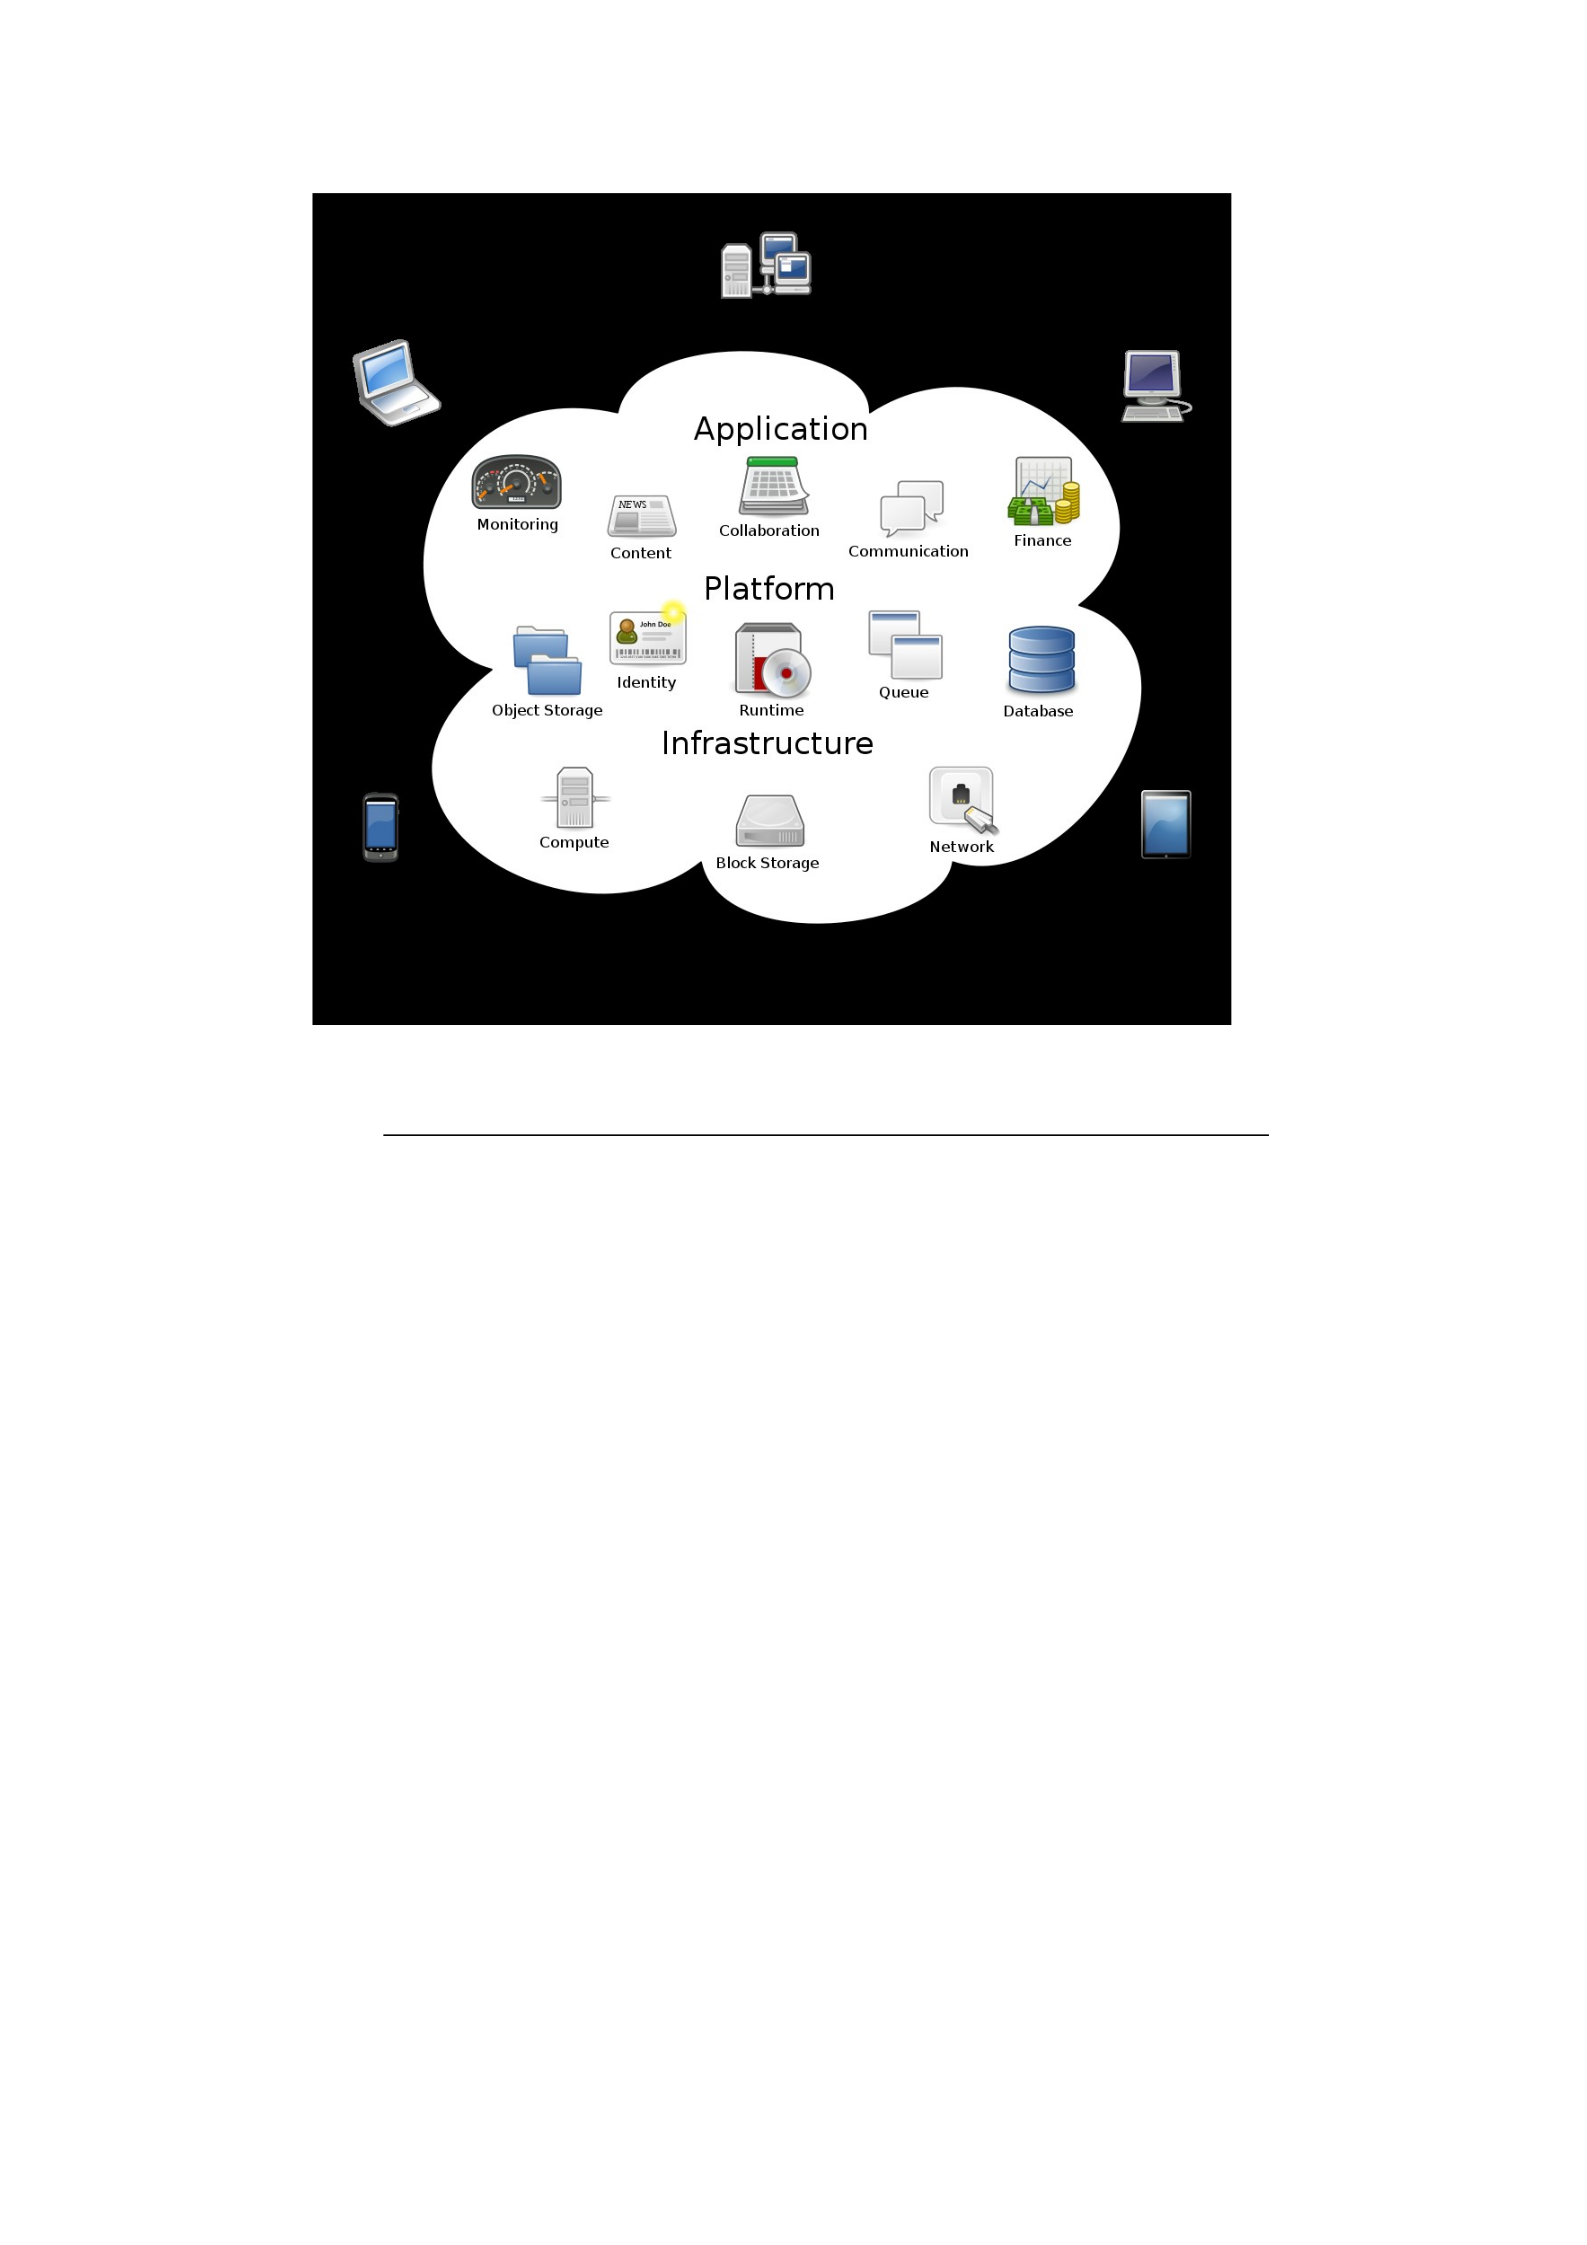
Figure 12 Cloud computing
Source: https://en.wikipedia.org/wiki/Cloud_computing#/media/File:Cloud_computing.svg
Note: Cloud computing metaphor: the group of networked elements providing services need not
be individually addressed or managed by users; instead, the entire provider-managed suite of
hardware and software can be thought of as an amorphous cloud(Wikipedia, 2019).
3.2.4 Internet of things
The Internet of things (IoT) is one of the growing trends in many industries
including maritime industry(Shipware, 2021). In short, the Internet of Things(IoT)
is the idea of connecting any physical “things” to the Internet through the various
different types of sensors. The IoT is considered as a huge network of connected
things and people - all of which collect and share data about the way they are used and
about the environment around them (Clark, 2016).
Figure 13 The internet of things (IoT)
Source: https://zhuanlan.zhihu.com/p/367257739
The ship/shore communication revolution has catapulted internet of things to the
shipping industry (Hannemann, 2019). For the manager of shipping company, they
can make data-driven business decisions and optimize operations at different levels
with increasing IoT connectivity. IoT enable the ship owners or fleet managers
monitor the ship`s movement condition at all times to figure out operational issues and
avoid potential loss.
For the shipping industry, IoT enables the real time tracking and monitoring the
ships status which is disrupting the traditional shipping management. In order to
achieve the greater efficiencies and competitive advantage, many of the shipping
companies are willing to apply the new technologies such as IoT, block chain, AI etc.
However the uncertainties and challenge with any digital information technology
is that it can introduce new chances for abuse and data crimes if not architected
correctly and managed with a robust governance (Loftus, 2019). The shipping
industry, as one of the most vulnerable aspects of modern industry in facing of cyber
threats, requires multifaceted attention and more effective countermeasures.
3.2.5 Block chain
Block chain was firstly introduced in 2008 as part of a proposal for a virtual
currency system known as bitcoin which is the first application of block chain
technology(Marco Iansiti & Lakhani, 2017). Whether you recognize it or not, block
chain technology has been successfully utilized in the maritime industry especially for
operational level in shore sector.
As per Marine insight news network, block chain technology is hitting the
maritime industry in a major way, as many shipping companies are looking forward to
making the information process more smoothly between business segments, and
making trade-related processes faster and more efficient ( 2021). The world's first
shipping transaction on the ethereum block chain was successfully completed on 15
March 2018 with the first trial of its smart contract deployed on the ethereum block
chain (Marineinsight, 2018).
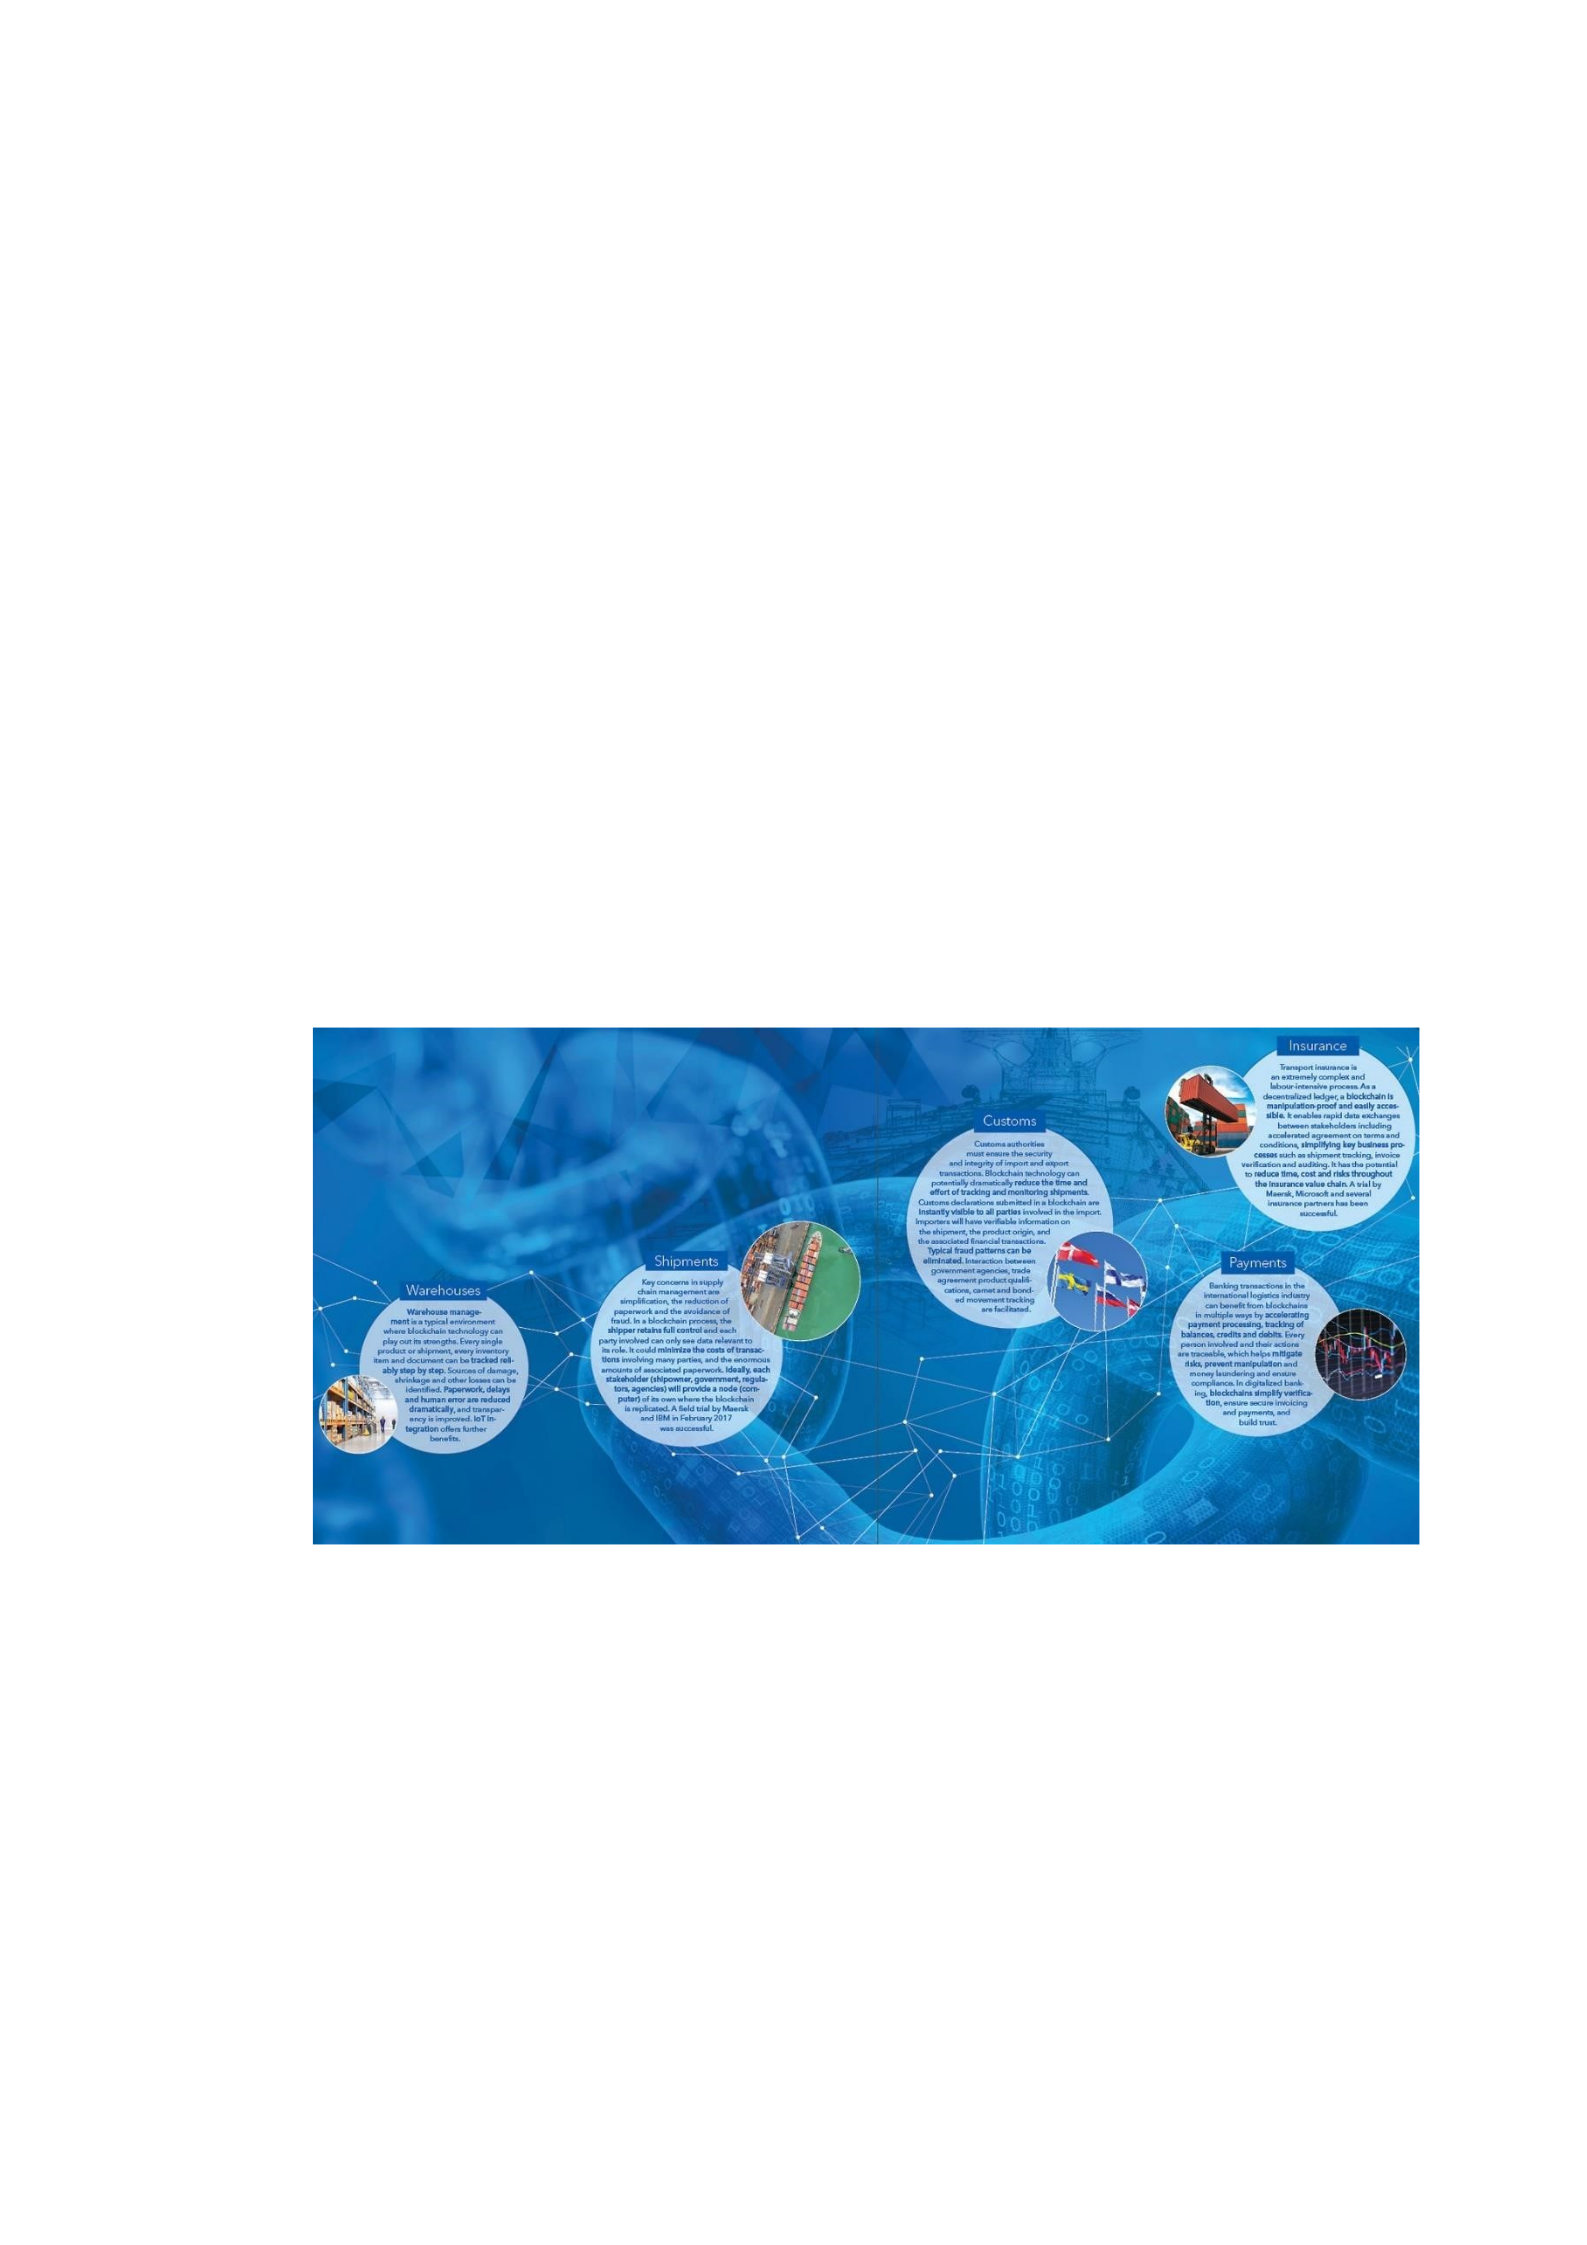
Figure 14 Block chain can be used in any business transaction
Source: DNV. https://www.dnv.com/expert-story/maritime-impact/Blockchains-in-the-
shippingworld.html
The ability to reduce trade documentation, transaction costs, delays, data
manipulation, fraud and human error via non-compromising intelligent contracts
makes block chain technology attractive to the maritime industry(Einarsson, 2018).
However, before wide range implementation of block chain technology in the

maritime industry, there are lots of uncertainties and challenges need to be addressed,
for example the cyber safety and security issues(Green et al., 2020).
3.2.6 Artificial intelligence technology
Before driving into artificial intelligence technology in maritime industry, I bring
a news regarding to a Japanese domestic coastal container ship named Mikage which
autonomously sailed from Tsuruga Port to Sakai Port on 24-25 January 2022 which is
the first autonomous containership sails in Japan, and Information on ships and
obstacles on the route was gathered by the Furuno Electric-developed autonomous
surrounding information integration system (Berrill, 2022). And also according to Yara
News, on 18 November 2021,Yara Birkeland, an autonomous ship which would be the
world`s first fully electric and autonomous container ship with zero emission took first
trip(2021).
Artificial intelligence technology is usually being considered as a simulation of
human intelligence processes by machines, especially computer system, AI
technology is an area of computer science that emphasizes the creation of intelligent
machines that work and reacts like human.
The current application of artificial intelligence technology in the maritime
industry is autonomous ships, but there are more interesting applications being
developed in other areas of reality, such as Alpha Go, as the best example of AI
technology application, which is the first computer program to defeat a professional
human Go player (DeenMind, 2017).
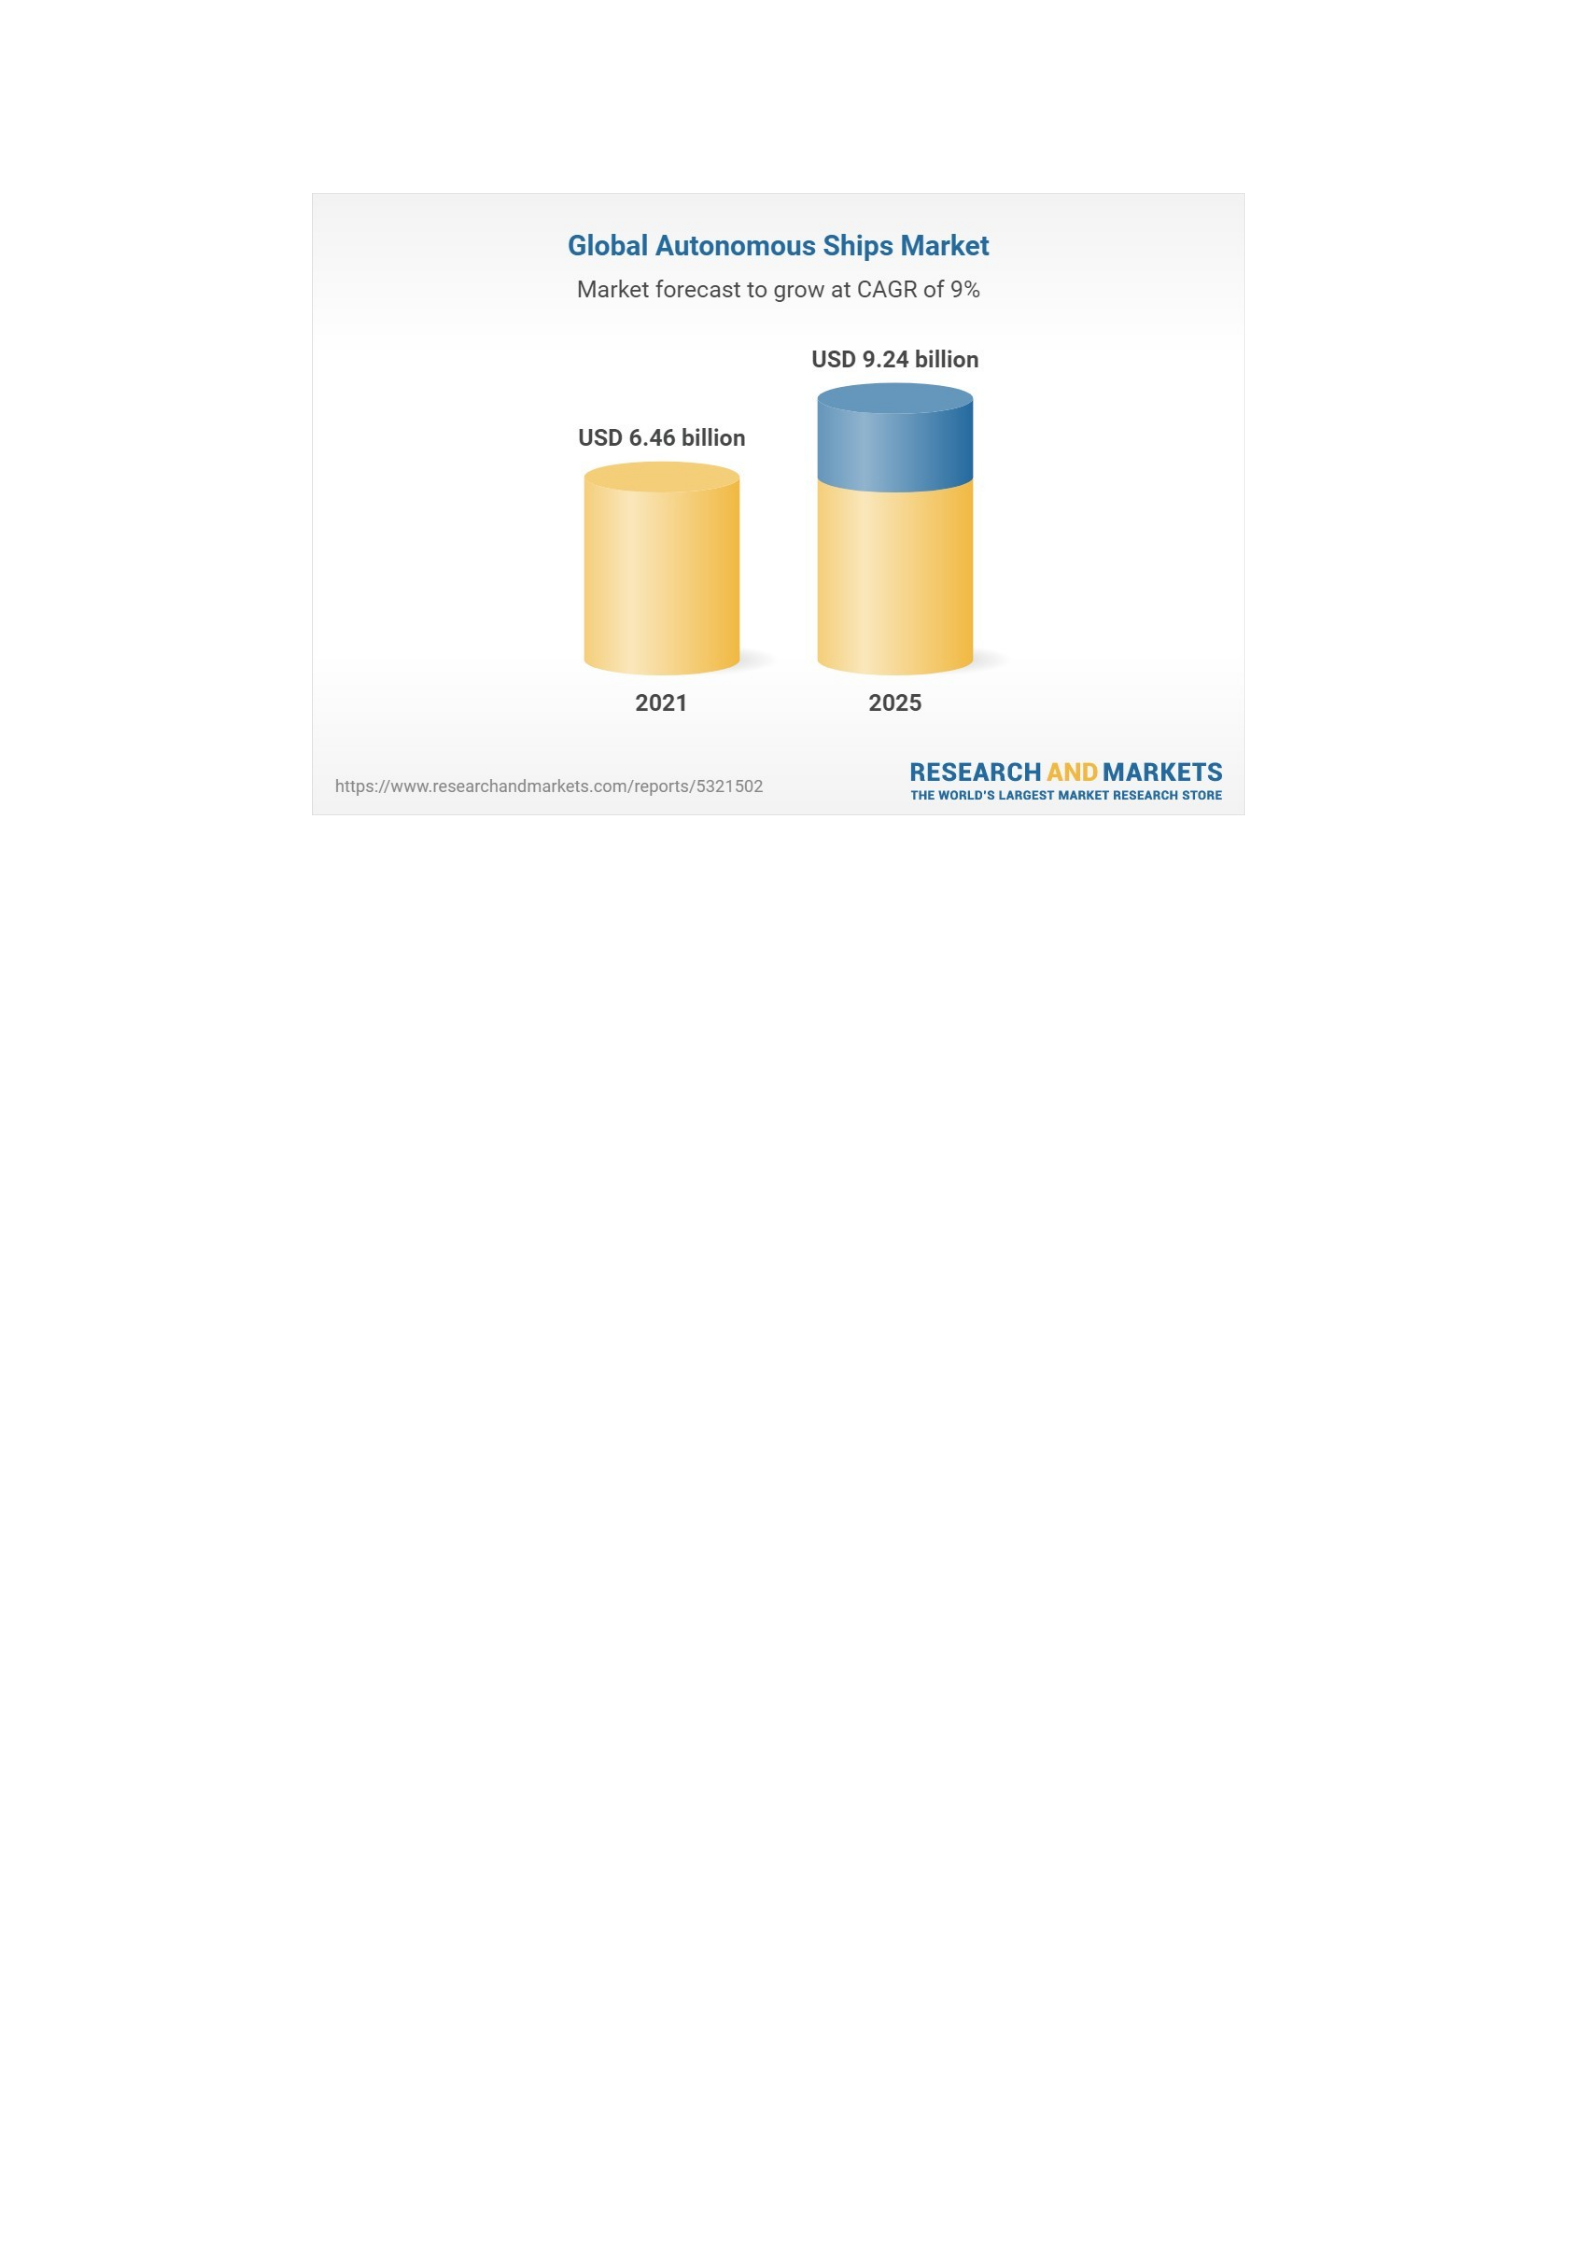
Figure 15 Global autonomous ships market forecast
Source: Research and Markets.
https://www.researchandmarkets.com/reports/5321502/autonomous-ships-global- market-
report2021-covid
The AI technology application is increasing in most industries especially the
logistics. As shown in figure 14, a study by Research and markets shows that the
global market for autonomous ships is expected to grow at a GAGR of 9% to reach
9.24 billion USD in 2025. There is a clear indication that autonomous ship will be the
next revolution in the maritime industry, and the combination of AI and big data being
used in shipping industries is an inevitable technological development (Jim, 2021).
Outside of the academy, it is easy to see how artificial intelligence technology is
driving innovation in the maritime industry. New technologies such as Maritime
Autonomous Surface Ships (MASS) and the increasing wireless coverage of ships at
sea are relying on the utilization of artificial intelligence technology to continue to
innovate and ensure the competition of the industry (Foster, 2021).
However, a detailed risk assessment of cyber risk landscape of the maritime
industry will be necessary in order to identifying and mitigating the ever-growing
vulnerabilities. The existing risk assessment for autonomous cars ashore do not
adequately standing for the unique characteristics of cyber-threats for autonomous
vessels in maritime industry(Tam & Jones, 2018).
3.3 Identify vulnerable cyber system in maritime industry
3.3.1 General shipboard cyber system
The dependence of the maritime industry on cyberspace has increased
significantly, and therefore also generates unexpected vulnerabilities to cyber safety
and security. According to IMO (2017a), vulnerable cyber systems on board ships
could include the following 8 different cyber systems as shown in the table 3.
Table 3 Onboard vulnerable cyber system
No. Vulnerable systems onboard
1 Bridge systems
2 Cargo handling and management systems
3 Propulsion and machinery management and power control systems
4 Access control systems
5 Passenger servicing and management systems
6 Passenger facing public networks
7 Administrative and crew welfare systems
8 Communication systems
Source: IMO MSC-FAL.1/Circ.3 Guidelines on maritime cyber risk management
With the approval of the IMO resolution MSC.428(98) maritime cyber risk
management in safety management systems, the responsibility for establishing the
cyber security management system has mainly transferred to the shipping companies,
resulting in an onboard cyber security framework that is currently different for each
company (Kapalidis, 2020). This has led to a diversity of cyber security management
systems and different standards. To address the cyber security on board, we have to
identify the vulnerability of each single related equipment according to MSC-FAL 1-
Circ 3. The detailed cyber equipment may include the following items listed in table 4.
Table 4 Identify the detailed cyber equipment on board
No. Vulnerable systems Equipment
1 Bridge systems ECDIS, VDR&SVDR, AIS, GPS&DGPS,
GMDSS-Radio communication system,
VHF, MF/HF, Integrate bridge system,
Satellite communication system, Radar&
ARPA system, Steering control and Auto
pilot system, Rudder angle indicating
system, Fire detection system, Echo sounder
and Doppler system, Speed log, Course
recorder, Weather fax receiver, CCTV,
Master clock system, Thruster control
system, Engine telegraph control system,
Bridge watch alarm system, LRIT, SSAS
system etc. Alarm control system, Gyro
compass system, Public address and talkback
system, Internal network station etc.
2 Cargo handling
management systems
and Cargo handling system, Ballast water
management system, Oil discharging
monitoring system, Tank radar system,
Ballast water tank gas detection system,
Remote valve and draft gauging system, Gas
detection system, Vapor emission control
system, Internal network station etc.
3 Propulsion and machinery
management and power
control systems
Engine control system, Auxiliaries control
system, Remote firefighting system, Oily
water separation system, Remote fire damper
system, Air conditioning system, Low
insulation monitoring system, Fixed
firefighting control system, refrigerant
monitoring system, engine room alarm
system, Power distribution and monitoring
system, various switch board system,
emergency maneuvering system, Internal
network station etc.
4 Access control systems Lighting control system, Low location
lighting system, Evacuation indicating
system, CCVT, shipboard security alarm
system, Boarding system, Electronic
personnel positioning system,
5 Passenger servicing and
management systems
3G/4G network ,VoIP automatic telephone
system, CCTV, Passenger boarding system
and access control system etc.
6 Passenger facing public
networks
Wi-Fi networks system, Cabin LAN system,
Guest entertainment systems, Cabin digital
entertainment system etc.
7 Administrative and crew
welfare systems
Internal network station, Onboard computer
network system etc. Planning maintenance
system , Crew welfare system, ship`s crew
email system etc.
8 Communication systems Satellite communication system, Wi-Fi
network system etc.
In short, any equipment and systems associated with digital technology can be a
vector for cyber security issues, not just those that we normally think of as being
connected to the Internet.
3.3.2 Identify shore based digital and information system
Maritime industry and all related activities are more relying on information
technology platforms. The maritime industry, consisting of shipping, port operations,
critical infrastructure and digital economic transactions, is highly structured around
information cyber systems(Jacq et al., 2019). The relative vulnerability of ship
cybersecurity has led to a selective concentration on the ships and crew only when
developing the associated cyber security counter measures. From MSC-FAL 1-Circ 3
and MSC. 428(98) ,we can see that the IMO more focuses on the ship or shipping
company itself than the whole industry. However, it seems to me that the shore based
IT systems in maritime industry are the primary cause of ship`s cyber security
problem on board ships, both at the management level and at the technical or
operational level.

For example, shipboard cyber systems do not usually generate viruses, and most of
viruses on board come from e-mail or attached files sent ashore.
Typically, shore based cyber security issue in maritime industry is recognized to
be same as the public cyber security issue mentioned in chapter 3.1. It often comes
under attacks by hackers due to the high automation and computerization of ports and
shore-based facilities(Avanesova et al., 2021). As shown in Table 2, there are many
cyber-attacks been reported every year, most of them were the case occurred in the
shipping companies, such as cyber-attacks were unleashed on servers of the container
giants Maersk and COSCO, blocking cargo terminal systems in 2017 and 2018.
Comparing with the situation on board, too much is being done ashore to
improve the cyber safety. Cyber security in ports and terminals can be integrated into
national cyber security response systems. Maritime administration ashore could have
enough facilities to response quickly while experiencing the cyber-attacks and they
also can keep the cyber system in real time updated to deal with the potential cyber
risk. In contrast, shipping companies, especially smaller ones, may need to pay more
attention to cyber security issues as most cyber security attacks are concentrated on
them.
The article identifies the risks and vulnerabilities of the maritime industry both
onboard and ashore in related to cybersecurity and seek potential international
cooperation to enhance cyber resilience in the maritime. The next chapter will conduct
3 main questionnaires which are covering all the people involving maritime industry
and try to figure out the challenges and uncertainties of the cyber security in maritime
industry.
4 Maritime cybersecurity survey
4.1 Maritime cyber risk survey and questionnaires design
This questionnaire is to reveal the current cyber security situation in maritime
industry. The respondents could have background covered a significant sample field
that would allow me to achieve a reliable answer of the knowledge on cybersecurity at
a general level.
In addition, while receiving the questionnaire showed a lack of knowledge or
cyber security awareness, the maritime practitioners were reluctant to show their
personnel weak point. To maximum the reliability, the question shall be objective and
directly as much as possible.
The questionnaires consisted of three sessions to cover all aspect of people
involving maritime industry, the first part was aimed at those people involved in
maritime industry ashore; the second part was aimed at the seafarers working onboard
or those who have experienced working on board ships; the last session was setup for
students undertaking maritime education or training.
4.1.1 Questionnaires design for maritime personnel ashore
The following table 5 shows question setting for maritime personnel ashore, the
basic idea is trying to covering all aspects of maritime industry.
This questionnaire is consisting in 16 questions, where the knowledge in
cybersecurity and the general practices of the respondents were highlighted.
Table 5 Cyber security questionnaires for maritime personnel ashore
employee
B, Maritime official personnel (MSA,
Classification, surveyor etc.) People engaged in maritime industry ashore
C, Marine service personnel (Agent, supplier, consist various aspects including listed from
chandler etc.) A to F
D, Maritime education and training faculty
E, Maritime-related personnel (Shipyard
employee, Port and terminal personnel,
insurance etc.)
F, Others
Are there any qualified third parties involving
2 the cyber security in your work platform such as
working computer, system server etc.?
This is to ensure that the computers and
work platforms obtain vulnerability test by
1 What aspects of the maritime industry are
involved in your job title?
A, Shipping company or management company
professional third parties, which is essential
A, Yes
B, No
C, Not sure
to recognize the scope of cyber security in
the working environment and to identify
weaknesses in order to minimize the
possibility of cyber -attacks.
Is there any formal cyber safety and security
3 framework in place?
A cyber safety and security framework first
and foremost reflects the cyber safety and
security awareness by decision makers and
A, Yes
B, No
C, Not sure
enables the entity to maintain certain cyber
protection capabilities. In general, the
framework should include risk
identification, risk assessment, control
measures, and contingency p lan etc.
Is there a formal procedure to control the access
4 to your work platform? This process is used to verify who has access
to your system. Failure of logical access is
A, Yes
B, No
one of the most critical reasons for cyber
incidents.
Has your vender applied the principle of least
5 privilege and multi-factor remote access
authorization?
Access rights based on the nature of the
work to determine which employees the data
types are open to are effective. With the
continuous impact of COVID 19 outbreak,
ensuring that
A, Yes
B, No
remote access requires multi-factor
authentication is an effective means of
securing the network.
6 How is data delivered in your daily work? It is extremely important that the media of
data transmission and that the data are
A, Authorized email service providers protected from unauthorized access. This is a B, Private
email service providers
C, Social apps. (WeChat, Facebook, Twitter matter of personal working behavior in relation to
cyber security and can easily etc.) reflect a personal cyber security awareness.
D, Others
All users of work systems should be trained
Have you been involved in cybersecurity in basic cyber security awareness to reduce
7 training throughout your career? Or was cyber human error in cyber security incidents. 95
security included in your induction training?
percent of successful hack attacks or cyber
incidents were because of some type of
A, Yes
B, No
human error. How to reduce human error is
the primary means of protecting cyber safety
and security.
How often do you update your antivirus
8 software? All antivirus shall keep up to date to ensure
the maximum protection from the cyber
threat. Outdated antivirus software can put
your working station at risk.
A, It is done automatically
B, At least once a week
C, Occasionally, when I remember
D, Never
9 How often do you use Windows Update?
Windows updates include the system
updates for security, bugs, new features etc.
Most computers have the recommended
setting as
“install updates automatically”, The purpose
of this question is to check that if the
participants are aware of the terminology.
A, It is set to update automatically
B, At least once a week C,
At least once a month
D, I don’t know what Windows Update is
Do you use firewall software on your computer
10
(not anti-virus software)? Without a firewall, you may allow yourself
to accept every connection that enters your
network, without any way to detect
incoming threats.
A, Yes
B, No
C, I don’t know what firewall software is
What do you do if your working platform
11 crashed down?
A, Call company IT technician The objective of this question is to figure out
B, Ask help for computer geek in your office respondents' cyber security awareness the
C, Seek assistance from your network service answer B and D are not what the questioner vendor or
equipment supplier want to see.
D, Do It Yourself
E, Report to your superiors
Where did you obtain your computer skills and
12 knowledge of the internet?
Computer technology as a basic skill should
be studied systematically as part of the basic
curriculum and both middle and high
schools should strengthen the content of
cyber security, maritime cyber security
education and training should be highlighted
in maritime education.
A, Academic Education
B, Vocational training C,
Self-learning online
D, Colleagues sharing
Do you know how Big data, IoT, Block chain
13 or Cloud computing works?
A, Yes
B, A little
C, No
D, I don’t know what they are
This question 13 and 14 were setup to check
whether the respondents were
knowledgeable about the new computer
technology.
Do you know how cloud computing, block
14 chain, big data and artificial intelligence are
affecting the maritime industry? This question 13 and 14 were setup to check
whether the respondents were
knowledgeable about the new computer
technology and how much they knew about
it.
A, Yes
B, A little C,
Not sure
D, I don’t know how they work
What security topic(s) are you most familiar
15 with or interested in? (Select all that apply)
This question is reflective of the
respondents' understanding of cyber security
and all options should be covered.
A, User`s end data protection and encryption
B, Network security
C, Cyber incident contingency plan
D, Approved cyber security service
E, Cyber security training and education
F, Other (please specify) ______
Is it possible to provide your email address to
16 send the final survey report to you?
Email address for sending final survey report
A, Yes
B, No
(if Yes, please specify)_______
4.1.2 Questionnaires design for seafarers
The following questions are used to determine the state of maritime cyber security
awareness among seafarers. This questionnaire is consisting of 16 questions as same as
first one, where the cybersecurity awareness and the general practices of seafarers were
highlighted. And the answers will reflect to the scope of cyber security management of
ship owner or management companies as well.
Table 6 Cyber security questionnaires for seafarers
1 What is your job title on board ship? From the position of the seafarers
A, Deck officers
B, Engineers
C, Ratings
crewmember have more cyber-security
awareness, and although it is likely that the
answer is unique, but I still want to see a
difference.
Is there any official cyber safety and security
2 framework in place?
IMO recommended all administrations to
ensure that cyber risks are appropriately
addressed in safety management systems no
later than the first annual verification of the
company's Document of Compliance after 1
A, Yes
B, No
C, Not sure
January 2021. A cyber safety and security
plan first and foremost reflects the cyber
safety and security awareness by ship`s
owner and managers, and enables the ship to
maintain certain cyber protection capabilities.
How often do you have a cyber-security drill
3 or trainings during you are staying at sea? The answer of this question will show the
reliability of last answer and determine how a
company implements resolution
MSC.428(98).
A, Monthly
B, 3 monthly
C, 6 monthly
D, Never
Is there a qualified third party provide cyber
4 security service to your vessels?
This is to ensure that the onboard cyber
system
we will be able to figure out which group of
obtain vulnerability test by a professional
A, Yes
B, No
C, Not sure
third party, which is essential to recognize the
scope of cyber security in your ship, and to
identify weaknesses in order to minimize the
possibility of cyber incidents.
Is there a password protection to your work platform,
such as cargo monitoring system,
5
communication system, ship`s computer This process is used to verify who has access
system server etc.? to your system. Failure of logical access is one
A, Yes, all password protected
B, Yes, but partially protected C,
Yes,
of the most critical reasons for cyber
incidents.
When you receive ECDIS weekly update Designated USB device for specific purpose files
by mail, which portable USB do you use such as ECDIS updates, cargo monitoring
6 to transfer the data from the public mail record keeping, OWS recording etc. is a good computer to
the ECDIS system? (For deck practice can minimize the computer virus officer only)
spreading out. However, the general practice
A, Personnel working USB device is using their own personal USB stick for such B, Ship`s
public USB device data transferring, as the nature of the officer's
C, Not required, automatically updated work is such that they always do the similar because
of Integrate bridge system connected work for long periods of time.
to internet
D, any USB device whenever it is available on
bridge
7 How is data delivered in your daily work? It is extremely important that the media of
data transmission and that the data are
protected from unauthorized access. This is a
matter of personal working behavior in
relation to cyber security and can easily
reflect a personal cyber security awareness.
A. Authorized email service providers
B. Private email service providers
C. Social apps. (WeChat, Facebook, Twitter
etc.)
D. Others
Have you been involved in cybersecurity
training before you join the ship? Or was
8 cyber security included in your induction training?
Most of shipping companies and
management companies used to assign a
crewmember to ship before all paper work
ready to meet the criteria of SMS inspection,
such paper work consists of the induction
training which may
11
A, Yes
B, Yes, but just to sign the paper only
C, No
include cyber safety and security issue.
However, due to the vessel’s time schedule
and port rotation, crewmember may not able
to receive the effective training as
documented been signed
How often do you update your antivirus
software or cleanup junk files on your
ECDIS
9 computer or main engine performance computer?
It is of utmost importance that antivirus
software is kept up to date at all times. This is
a personal work behavior matter relating to
A. It is done automatically
B. At least once a week
C. Occasionally, when I remember
D. Not required, there is no cyber risk
because they are highly stand-alone system.
E, Never
cyber security reflecting personal awareness
of cyber security. Shipboard operational
cyber system is often a neglected segment
due to the long period and uninterrupted
running in a single function.
Can you transfer your favorite music or This is to verify the reliability of the answers
10 movies to the ship's public entertainment of previous questions and check the general computer
system? practice of onboard cyber security process.
A, Yes, by portable hard drive B, Yes, by copying
from personal laptop via ship designated hard drive
C, Yes, authorized by captain or person in charge first
D, No, I cannot transfer those to ship`s public
entertainment computer system. E, No, never done it
before because the USB ports been locked
Can you install your favorite software to ship`s
public cyber system? A, Yes, I can install any
software in my working station
B, Yes, I can install my favorite software once I get
authorization from my superiors
C, Yes, I can install my favorite software once I get
authorization from company D, No, I can`t install my
favorite software because it is not allowed
E, No, I can`t install my favorite software because it
is not allowed
Same with the question No.10, this is to verify the
reliability of the answers of previous questions and
check the general practice of onboard cyber security
process.
What do you do if your working platform
12 crashed down?
The objective of this question is to figure out
respondents' cyber security awareness and
the answer B and D are not what we want to
see.
A, Call company IT technician
B, Ask help for computer geek on board ship
C, Seek assistance from electrician officer
D, Do It Yourself
E, Report to your superiors
Where did you obtain your computer skills
13 and knowledge of the internet?
Computer technology as a basic skill should
be studied systematically as part of the basic
curriculum and both middle and high schools
should strengthen the content of cyber
security, maritime cyber security education
and training should be highlighted in
maritime education.
A, Academic Education
B, Vocational training
C, Self-learning online
D, Colleagues sharing
Do you know how cloud computing, block
14 chain, big data and artificial intelligence are
affecting the maritime industry?
The answer for this question could be
various, seafarers may not able to have the
chance to get in touch with the new term,
even though
4.1.3 Questionnaires design for students
The following question is designed for students undertaking maritime education or
trainings, targeting to obtain the cyber security awareness of the new generation and
the answer will imply the status of current maritime cyber security education level in
China.
Table 7 Cyber security questionnaires for maritime background students
A, Yes
B, A little
C, Not sure
D, I don’t know how they work
they have been engaged these
new technology.
What security topic(s) are you most familiar
15 with or interested in? (Select all that apply)
This question is reflective of the seafarers`
understanding of maritime cyber security and
all options should be covered.
A, User`s end data protection and encryption
B, Network security
C, Cyber incident contingency plan
D, Approved cyber security service
E, Cyber security training and education
F, other (please specify) ______
What types of cyber security issues have you
16 experienced?
This is try to find out the most significant
cyber security case.
A, Hacking or malware
B, Phishing
C, Dos and DDos attacks
D, Man in the middle attacks
E, Physical loss
F, Unintended disclosure
G, Stationary device loss
H, Payment card fraud
I, Others (please specific) ____
Is it possible to provide your email address to
17 send the final survey report to you?
Email address for sending final survey report
A, Yes
B, No
(if Yes, please specify)_______
1 What is your major??
The student survey will cover all
maritime related majors as much as
possible
A,Maritime technology
B,Maritime engineering
C,Marine electrician D,Maritime
economic
E,Maritime law
F,Others
Do you have cyber safety or security as a subject in
2 your courses under the current education and training
system? This question will reveal the
curriculum for maritime cyber
security education.
A, Yes
B, No
Did the professor give you a lecture on cyber security
3 in relation to maritime industry?
the question will reveal the
curriculum of cyber security
education in schools and indicate the
cyber security awareness of the
instructors
A, Yes
B, No
What would you do if you suspected a virus or Trojan
4 horse on your computer? The objective of this question is to
figure out respondents' cyber
security awareness and the answer A
and C are preferred
A, Call IT technician
B, Ask help from computer geek in your class
C, Seek assistance from equipment provider D,
Do It Yourself
5 I usually use the same password for:
Using the same password for
different accounts increases the
cyber risk and should be avoided.
A, All of my online accounts
B, Most of my online accounts
C, Some of my online accounts
D, I never use the same password on my online
accounts
6 My passwords contains Passwords containing personal
A, Personal information information are very insecure, the
B, Dictionary words or phrases recommended security password
C, The same information as my other passwords, should contain upper case letters,
D, Just in a different sequence lower case letters, numbers and
E, Randomized sequence of numbers, letters, and special symbols symbols
10
A, I click on the link or download the document
immediately
B, I verify the sender's email domain to ensure I
recognize it
C, I examine the link before clicking to identify any
suspicious words and misspellings
usually suffering from the
phishing emails with the feature
of attachments, urgency message
and hyperlinks, Cyber security
awareness training in this area
should start with students
D, I verify and examine (second and third answers)
What types of cyber security issues have you
experienced?
A, Hacking or malware
B, Phishing
C, Dos and DDos attacks
D, Man in the middle attacks
E, Physical loss
F, Unintended disclosure
This is a multiple choice question
to find out how well students
know about the types of cyber
security
issues
G, Stationary device loss
H, Payment card fraud
I, Others (please specific) ____
Is it possible to provide your email address to send the
11 final survey report to you?
Email address for sending final
survey report
A, Yes
B, No
(if Yes, please specify)_______
7 I save my password in a web browser: Automatic saving passwords on
websites increases the risk of
personal information leakage
A, Always
B, Sometimes
C, Never
I use the following type(s) of two-factor authentication
8 when logging into my…
Multi-Factor Authentication is an
electronic authentication method in
which a user is granted access to a
website or application only after two
A, Smart card, RSA key, phone, or RFID badge
B, Password, PIN number, or a security question
C, Biometric authentication like a fingerprint scan or facial
recognition
D, what is two-factor authentication?
or more pieces of evidence (or
factors) have been successfully
provided to the user. it protects user
data from being accessed by
unauthorized third parties
(Wikipedia, 2022)
When I receive an email with a link or document
9 attached: The shipboard cyber-attacks are

4.2 Methodology and Statistical data of questionnaires
4.2.1 Sample
The participants of this survey were people working in the maritime industry
as well as in the field of networking and communications in China. The
respondents include seafarers from both Chinese shipping companies and foreigner
shipping companies, such as COSCO shipping, Hafnia tanker, Evergreen, OOCL
etc. Students receiving maritime education and trainings from DMU, various
training centers, maritime education and training personnel in China, cyber security
engineers, project workers engaged ship building, shipping company employees,
maritime bureau officials, etc.
We will use stratified random sampling method and which was selected in two
stages. In the first stage, the three questionnaires were set up separately according
to the professional characteristics of the participants. And the questionnaires were
randomly distributed through different WeChat App. Groups and by emailing.
The second stage of the sample was a selective face-to-face interview using
the same questionnaires. The survey respondents were picked out in a
representative manner. Interviews were conducted with wide range including a
number of small shipping companies, no matter how small it was, even if this
company managed only one ship, they were reached.
All sample surveys are subject to possible sampling error; At a 95%
confidence level, the sampling error rate for the entire questionnaire is +/- 2.5%.
This means that 95 out of 100 samples of this size will obtain results that fall within
plus or minus 2.5% points, which would have been obtained if everyone had been
interviewed. Other nonsampling errors may also cause overall investigation
error(Bear Team, 2017).
4.2.2 Questionnaire and Interviewing
The questionnaire used in the survey was prepared by myself in conjunction with
an internet source and other experts within the maritime industry. The draft of three
questionnaires were pretested, and amendments were made in terms of description and
length during the pretesting process.
During the survey, I conducted the internet survey and face-to-face interviews.
The average length of the interviews was about 10 minutes. Information received
from the online survey and interviews were collected and categorized by
WenJuanXing at all stages to ensure ensuring both accuracy and reliability.
4.2.3 Data Analysis
The survey data obtained via the above mentioned methods can basically
reflect the development of cyber security in maritime industry of China. Through
statistical weighting of the collected information, these data can be used to analyze
the cyber security issues in the global maritime industry.
4.2.4 Statistical data of questionnaires
Finally, the maritime cyber security survey consists 3 questionnaires reflect all
responses 849 people in maritime industry, and the majority of the respondents
(47%) are students from different maritime universities and training centers, the
second largest group (21%) is seafarers. The other respondents (32%) consist with
different background of shore personnel working along with maritime industry. The
percentage of types of respondents shows in the figure 16.
%21
%47
9%
3%
2%
6%
10% %2
Respondants type
Seafarers
Students
Shipping company or management company employee
Maritime official personnel
Marine service personnel
Maritime education and training faculty
Maritime industry-related personnel
others
Figure 16 Respondents type in percentage.
Source: WenJuanXing.
The answers for which there was clear evidence, such as contradictory answers
in contextual, would be considered as invalided questionnaires. In the analysis of
all 849 answers, a total of 55 answers been considered as invalid for the
questionnaire. Finally, the number of effective questionnaire is 794 with a valid
response rate of approximately 93%. In table 8 we can see the effective answer rate
of each group.
Table 8 Statistical data of questionnaires
Total answer Effective
answer
Rate of effective
answer
First questionnaire 271 261 96.3%
Second questionnaire 178 161 90.4%
Third questionnaire 400 372 93.0%
Total 849 794 93.5%
Source: WenJuanXing.
A large percentage of students were invited into the survey, but from the
position of the students themselves, it was mainly able to reflect the current status
of maritime cyber security education and the students` cyber security knowledge,
not directly related to the current situation of maritime cybersecurity, so it was wise
to set up a separate questionnaire for students, as seafarers did.
The limitations of my survey were time limit and lack of international
participants due to the COVID 19 pandemic and the platform of international
relationship in which situation that did not allow me to make sure the
comprehensiveness and reliability of the answer. And also it did not allow me to
cover a wide range of respondents involving different sectors of the maritime
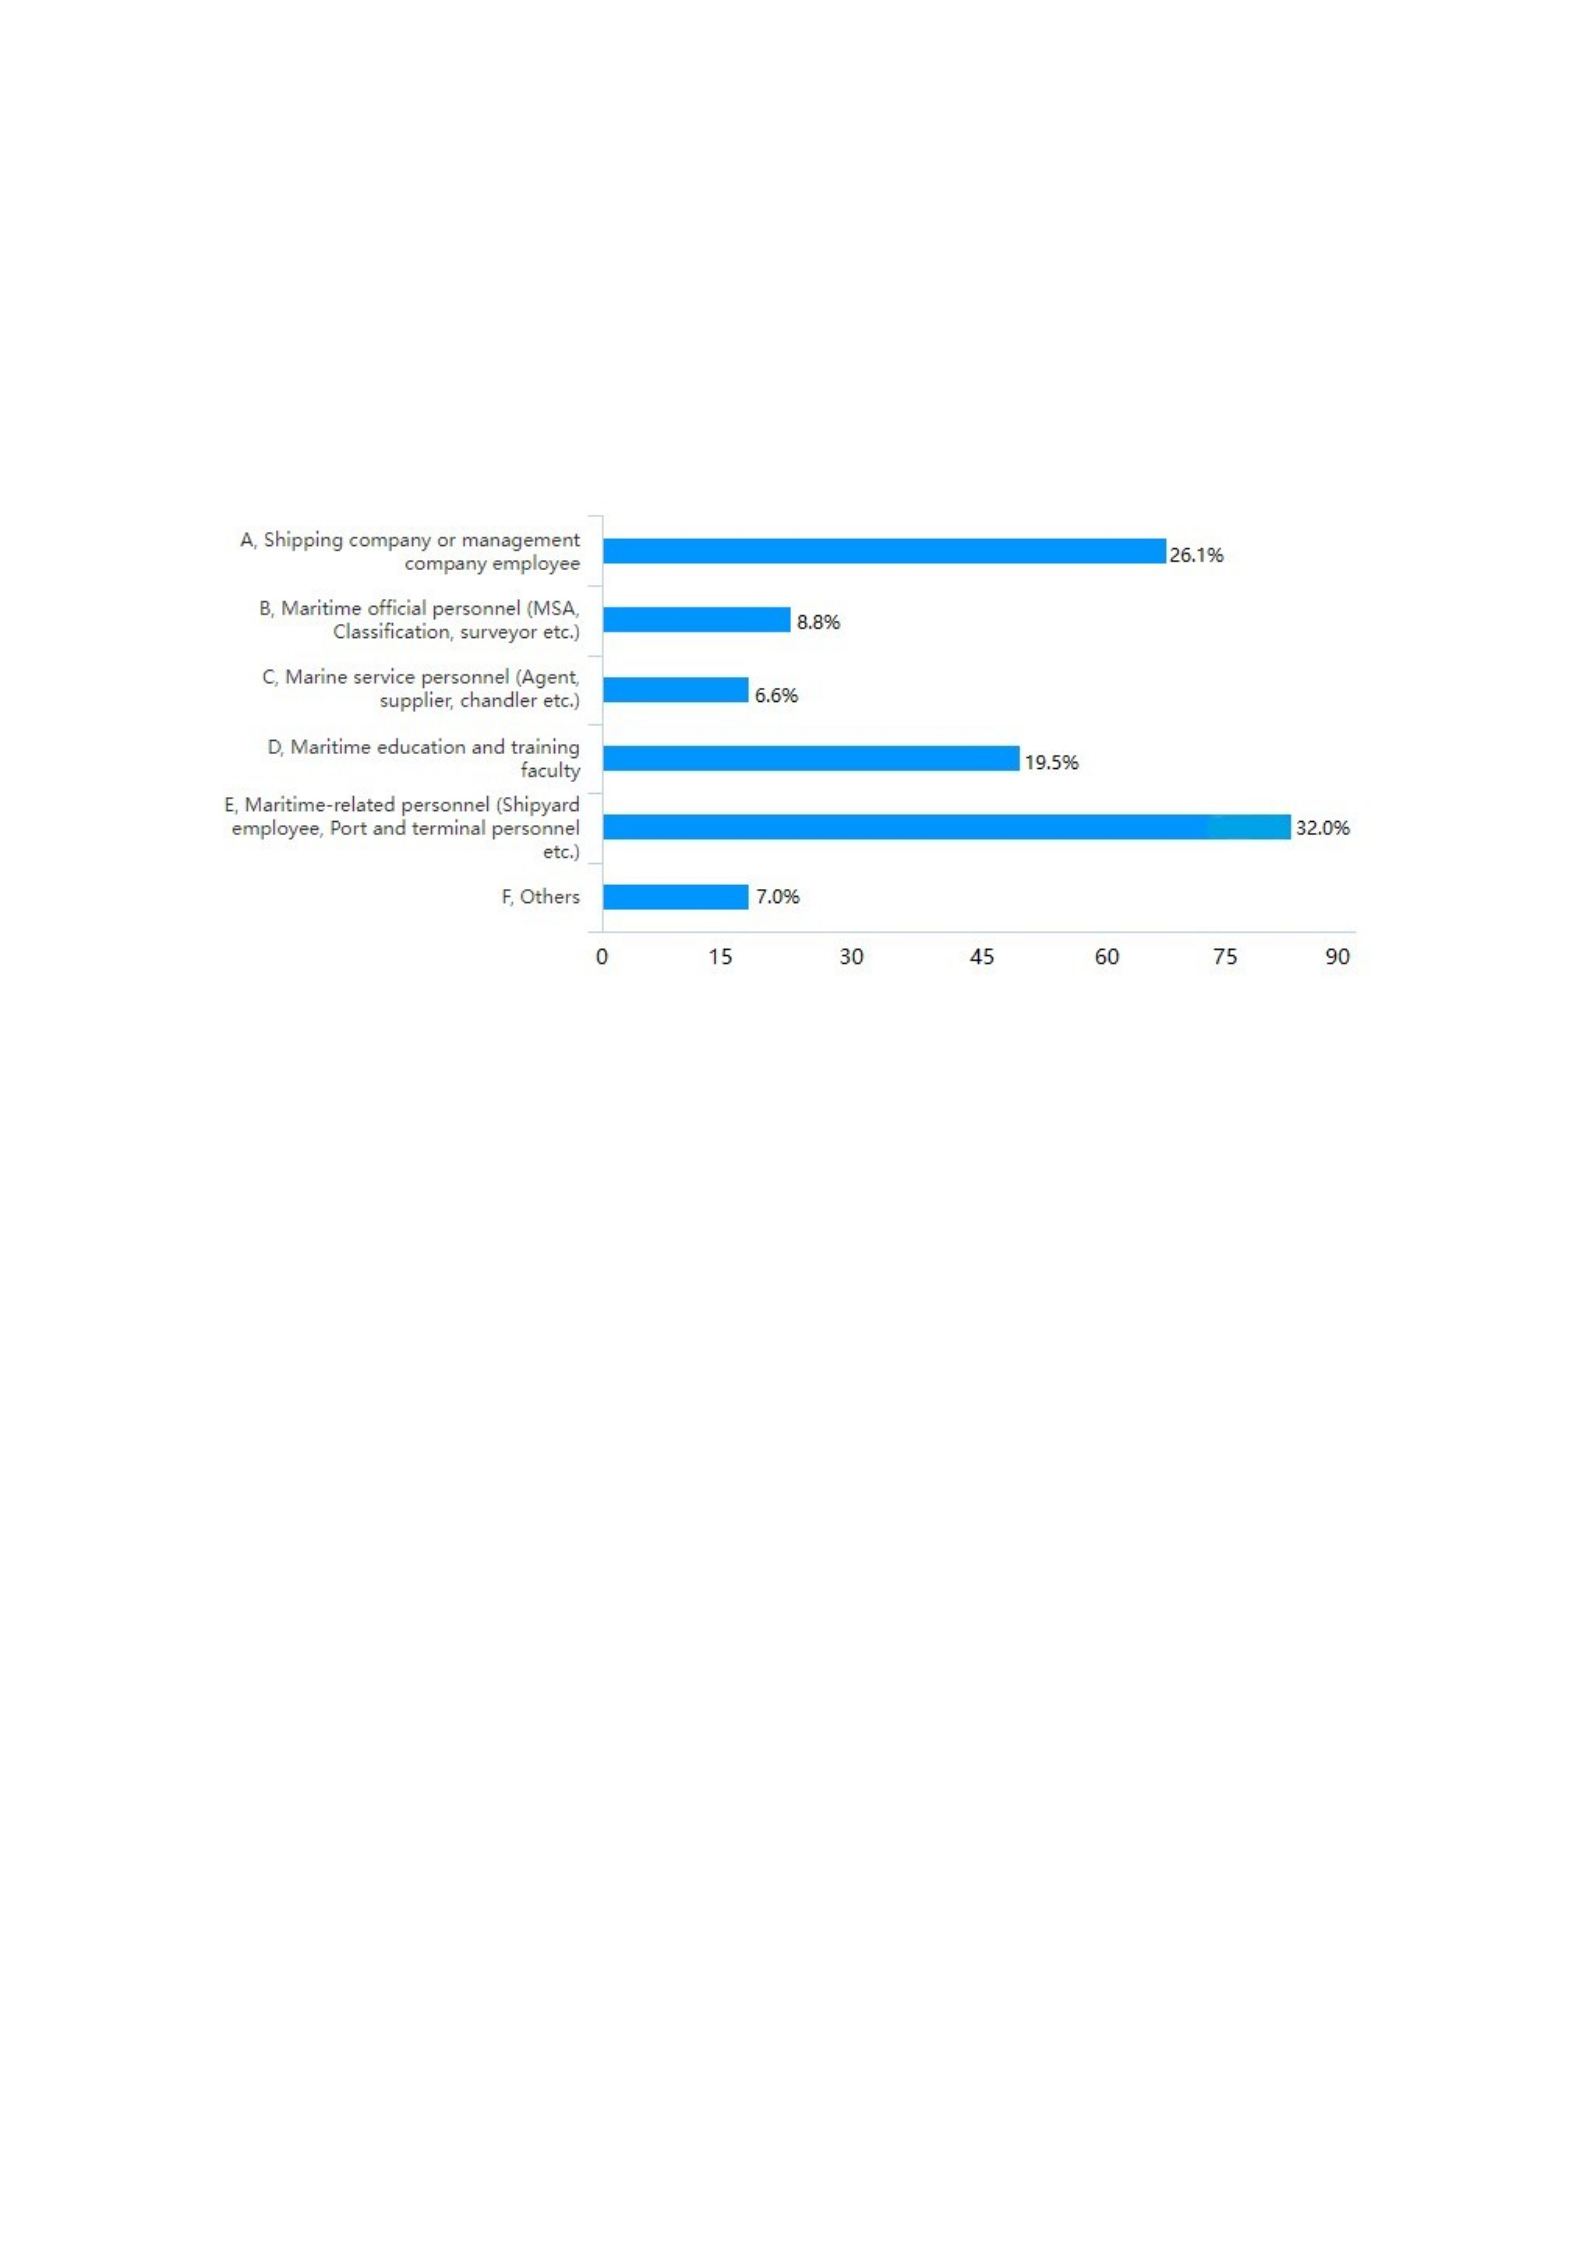
industry. This is particularly true for the seafarers’ background participants who
work on board ships without effective internet connection.
4. 3 Questionnaire findings
4.3.1 Respondents related to maritime industry ashore
Figure 17 Type of respondents related to maritime industry ashore
Source: WenJuanXing.
Total number of respondents of shore personnel was 271, the distribution
shows on the figure 17. There are about 56% participates were from shipping
companies, port& terminal and shipyard etc. and 19.4% respondents were involved
maritime education and training, which are the most typical categories of workers
in maritime ashore.
Looking at the answer to the question 1,2 and 3, an average 53% respondents
gave a positive response to qualified third parties and company cyber security
frame works, mainly from the official entities, port and terminal, large shipping
companies. However, the maritime service personnel such as manning agency,
ship`s chandler, supplier and terminal workers contributed opposite answer up to
48%. Question 4 and 5 give a nearly same number of 65% “Yes” and 35% “No”.
with regard to the question 6, a clear picture will give in figure 18.
Figure 18 General data transferring method.
Source: WenJuanXing.
Refers to the new technology associated with question 13&14, there are only
15% of respondents giving the answer “Yes”, with majority answering “No” or “Not
Sure”.
It was shown that most of shore based companies have cyber security response
plan in place with the formal procedures and frame works, however, it is
embarrassing that many of respondents (20%) form these company only give the
answer “No” or “Not Sure” while analyzing the results of question 2&3. The facts
show that the most significant cyber security issue ashore is policy compliance,
with the poor implementation of their cyber security policies and failure to consider
technical upgrades and basic training.
Automatically updating of antivirus software and windows system is a basic
setting to avoid the working station exposed to cyber risk, however, this percentage
are quite low (30% only), the reason could be reflecting to the internet jamming
due the limited speed and complex settings as well as network interference due to
40%
12%
36%
12%
How is data been delivered in your daily work?
A, Authorized email service providers
B, Private email service providers
C, Social apps. (WeChat, Facebook,
Twitter etc.)
D, Others
push notifications of ads associated with antivirus software (Demchak & Thomas,
2021).
Table 9 Percentage distribution of effective answer for question 3.
Q3: Is there any formal cyber safety and security framework in place?
Total Percentage
A, Yes 136 52.1%
B, No 76 29.1%
C, Not sure 49 18.8%
261
Source: WenJuanXing.
From the face to face interviewing, it is a good sign that the respondents tend
to be more aware of maritime cyber security issues. From the answers of question
15, we can see that most of employees are willing to strength their abilities digital
information technology from different aspects of cyber technology. As a multiple
choice question, a total of 261 effective respondents contributed 731 answers in this
mutable selection.
Table 10 Percentage distribution of effective answer for question 15.
Q15: What security topic(s) are you most familiar with or interested in? (Select all that
apply)
Total Percentage
A, User`s end data protection and encryption 136 52.1%
B, Network security 169 64.8%
C, Cyber incident contingency plan 142 54.4%
D, Approved cyber security service 138 52.9%
E, Cyber security training and education 146 55.9%
F, Other (please specify) 0 0%
731
Source: WenJuanXing.
However, there are still lots of challenges on the cyber security issue ashore, for
example, the willing of cyber security budgets of shipping company is slim overall.
They are more interested in enhancing the cyber security behavior of their
employees and raising the awareness through internal training as the effects of
human error is being emphasized throughout the whole society. Investment in
ship`s cyber infrastructure is not considered to be the optimal choice.
4.3.2 Seafarer
There are total number 178 respondents including 17 invalided answers, and
the 161 effective questionnaires (Deck officers:55, Engineers:72, Ratings:34) were
completed by 89 seafarers onboard 32 vessels, and 72 seafarers at home. The range
scale covered by different level of crewmembers from both Chinese shipping
companies and foreigner shipping companies.
Table 11 Percentage distribution of valid answers to question 2
Q2: Is there any official cyber safety and security framework on board your
ship or your last ship?
Total Percentage
A, Yes 109 67.8%
B, No 18 11.1%
C, Not sure 34 21.1%
161
Source: WenJuanXing.
The question 2 was designed to determine whether the shipping company
establish an effective cyber-security framework, the survey gave us a negative
answer, as shown in the table 11, with a large number of crew giving a “No”
(11.1%) or “Not sure” (21.1%) answer, despite the majority of respondents (67.8%)
indicating that a formal cyber security framework was in place on board. And the
question 3 also gave clear evidence showed a 11.9% crewmember did not
experience any cyber security training or drills as shown figure 19. Monthly and
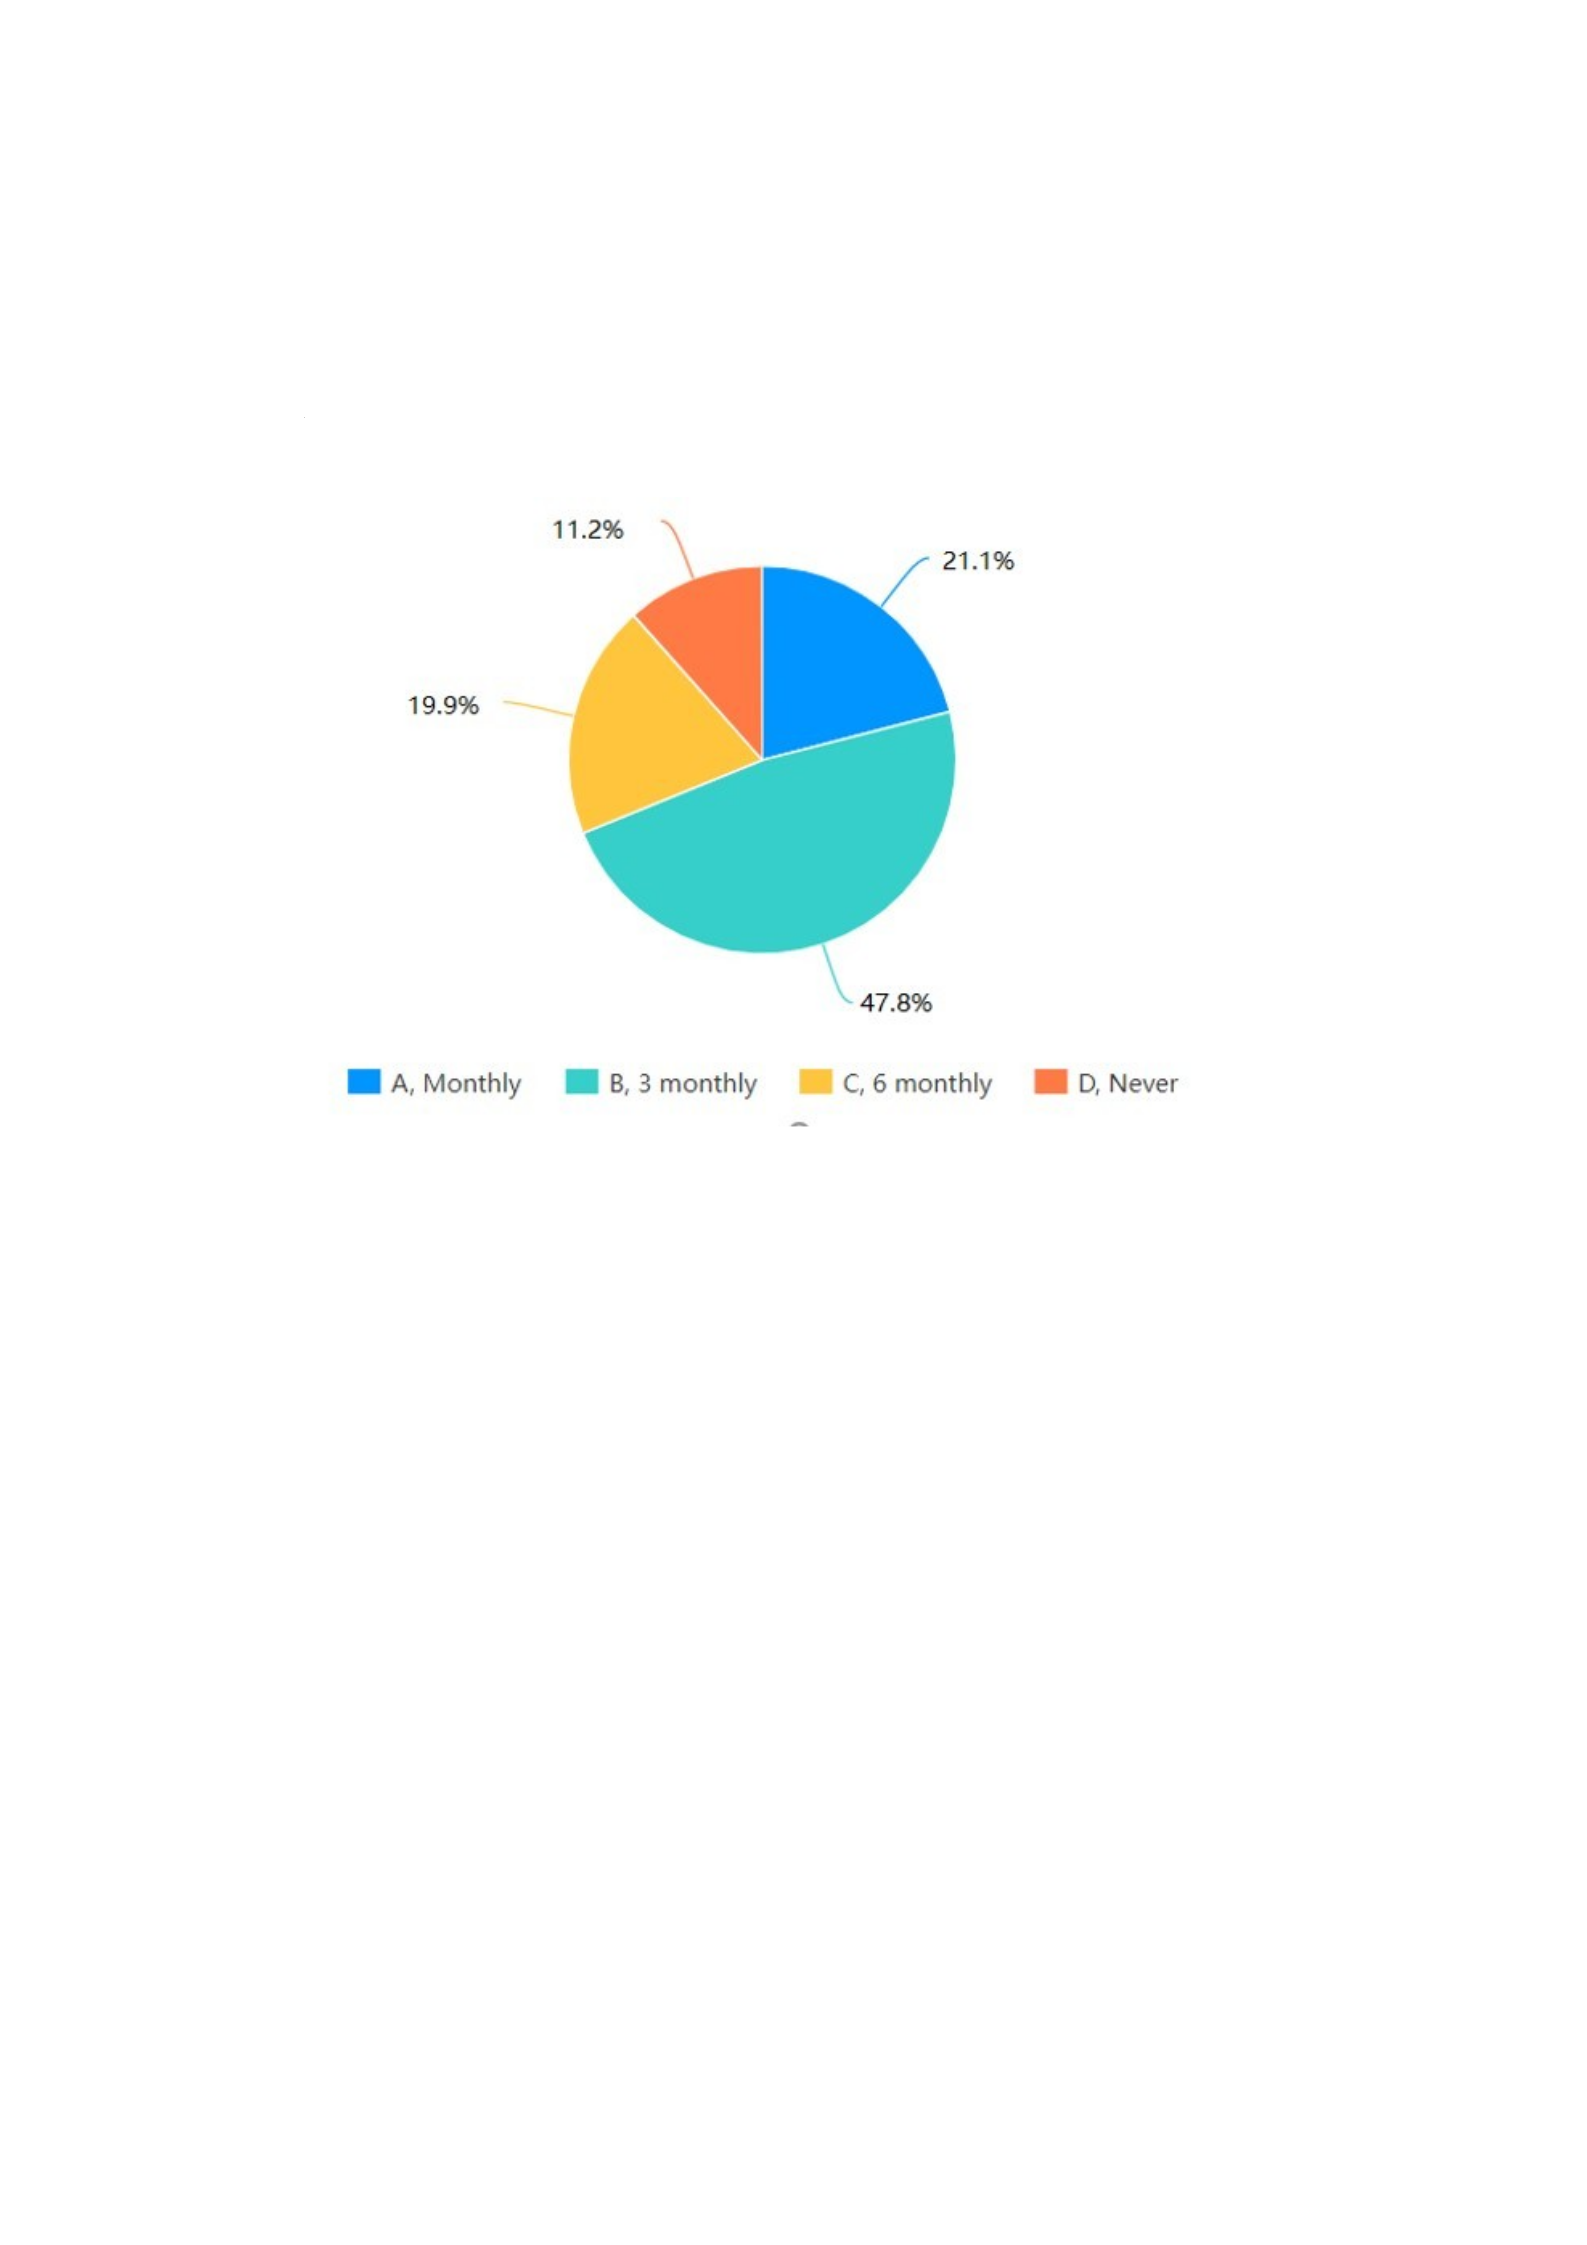
three monthly cyber security drill and training is reasonable for vessel`s drill
&training matrix. The duration of 6 monthly could be too long to achieve the
effectiveness of training objectives.
Figure 19 Percentage distribution of valid answers to question 3
Source: WenJuanXing.
Respondents were asked to verify that the availability of qualified third party
services, and only one third (31.1%) showed affirmative, and four in ten (41.0%)
selected answer “No” and three in ten (27.9%) showed “Not Sure”.
It is a common sense for shipping company that the investment on maritime
cyber security issue is still not yet been highlighted today`s world. As the IMO
guidelines giving recommendation of addressing the cyber security to safety
management system, the actually measures will be in papers first. And how far the
shipping companies and other entities involving the maritime industry would like to
go forward is highly depending on how serious cyber incidents they had
experienced.
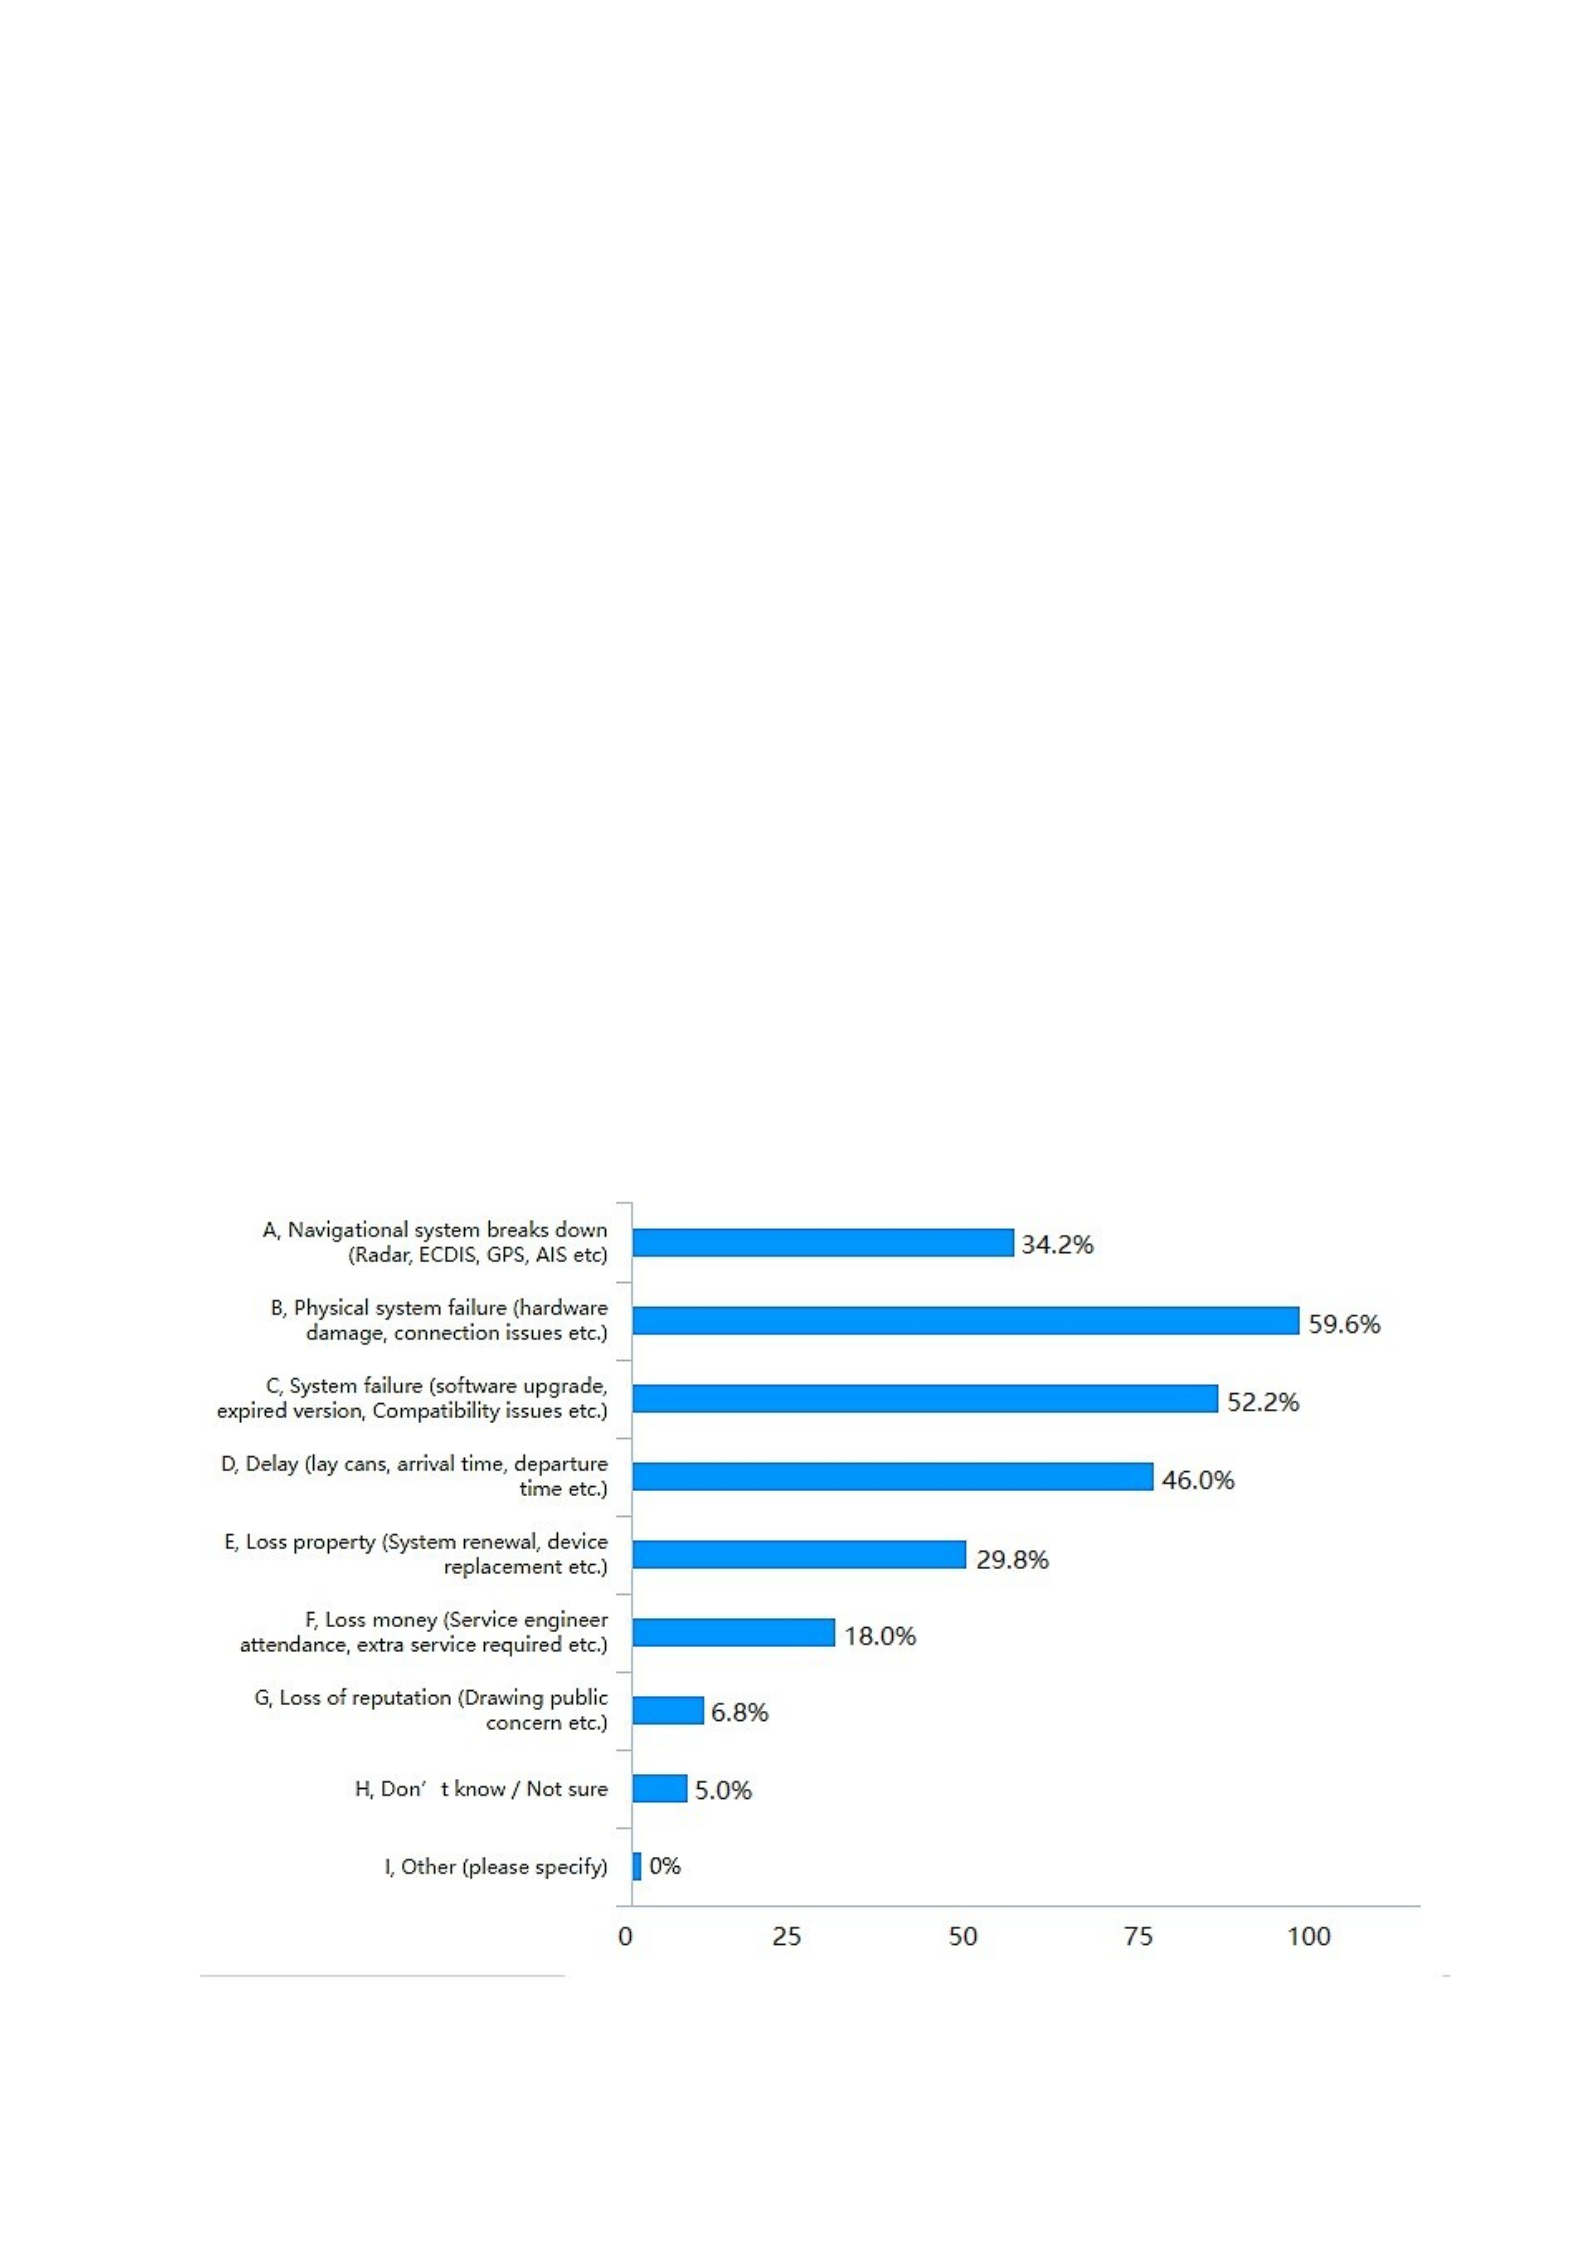
I also asked the respondents a number of questions about personnel behaviors.
For example, the use of personal devices, such as personal laptop to carry out
routine work activities, and personal USB to insert in shipboard working station,
were more common among entertainment, data transferring and group works both
onboard and ashore.
For seafarers, a majority of respondents reported the most common cyber
safety and security incident typically involved system failure. In particular, the
types of cyber system failure reported include physical system failure (59.6% of
respondents), and software failure (52.2% of respondents), navigational system
break down (34.2%), system delay (46.0%), property damage (29.8%).
As a result, ship owners and employers need to pay more attention to cyber
security awareness training for crew members, emphasis the implementation
shipboard cyber risk assessment and mitigation, and upgrade or replace outdated
software where possible.
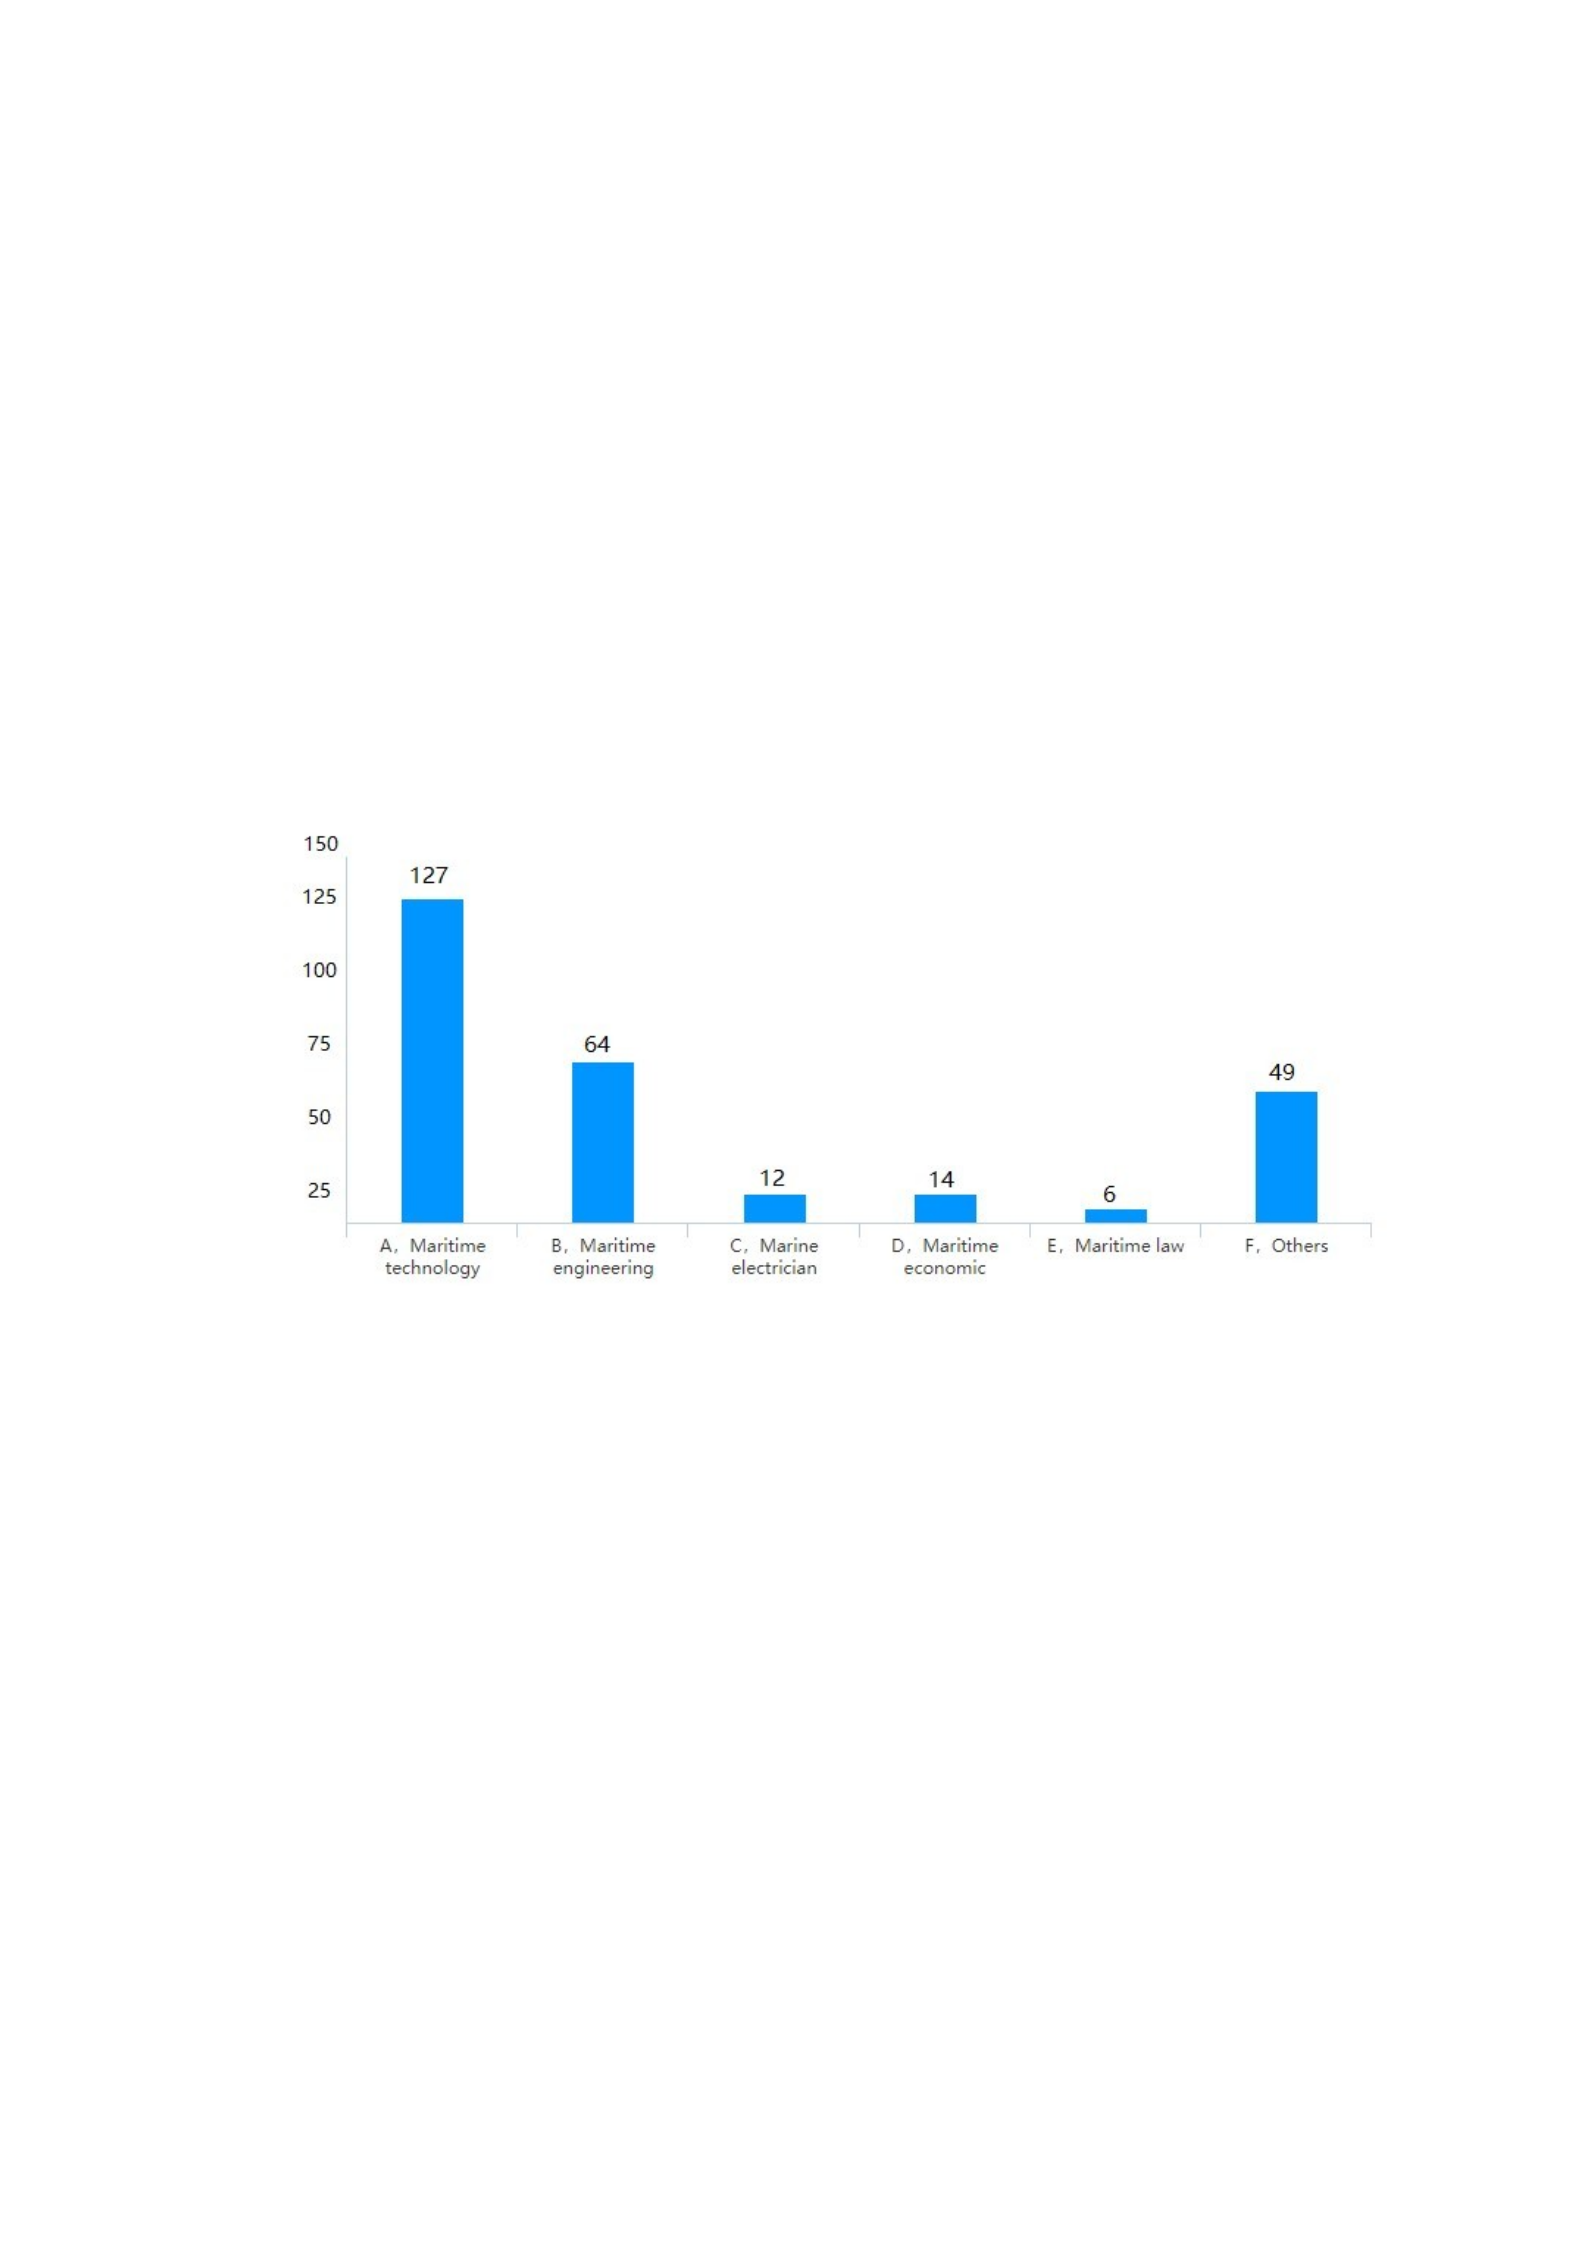
Figure 20 Types of significant cyber safety and security incident
Source: WenJuanXing.
4.3.3 Students receiving maritime education and trainings
The questionnaire for maritime students was targeting to obtain the cyber security
awareness of the young generation and addressing the status of current maritime cyber
security education in China. The majority of effective respondents were from the major
of maritime technology (total 127), marine engineering (total 64) and others major (total
49) like MSEM students, PhD students etc.
Figure 21 Major distribution of students respondents
Source: WenJuanXing.
Beyond the survey we found that all students from primary schools to
university were undertaking computer technology courses in varying degrees and
although the maritime cyber security as a new field has not yet been incorporated
into maritime education, about 261 respondents (70.2%) reported their professor
had covered maritime cyber security during classes as shown in figure 22. The
investigation showed that students were doing better than seafarers and maritime
staff ashore on the personnel online behaviors and cyber security awareness.
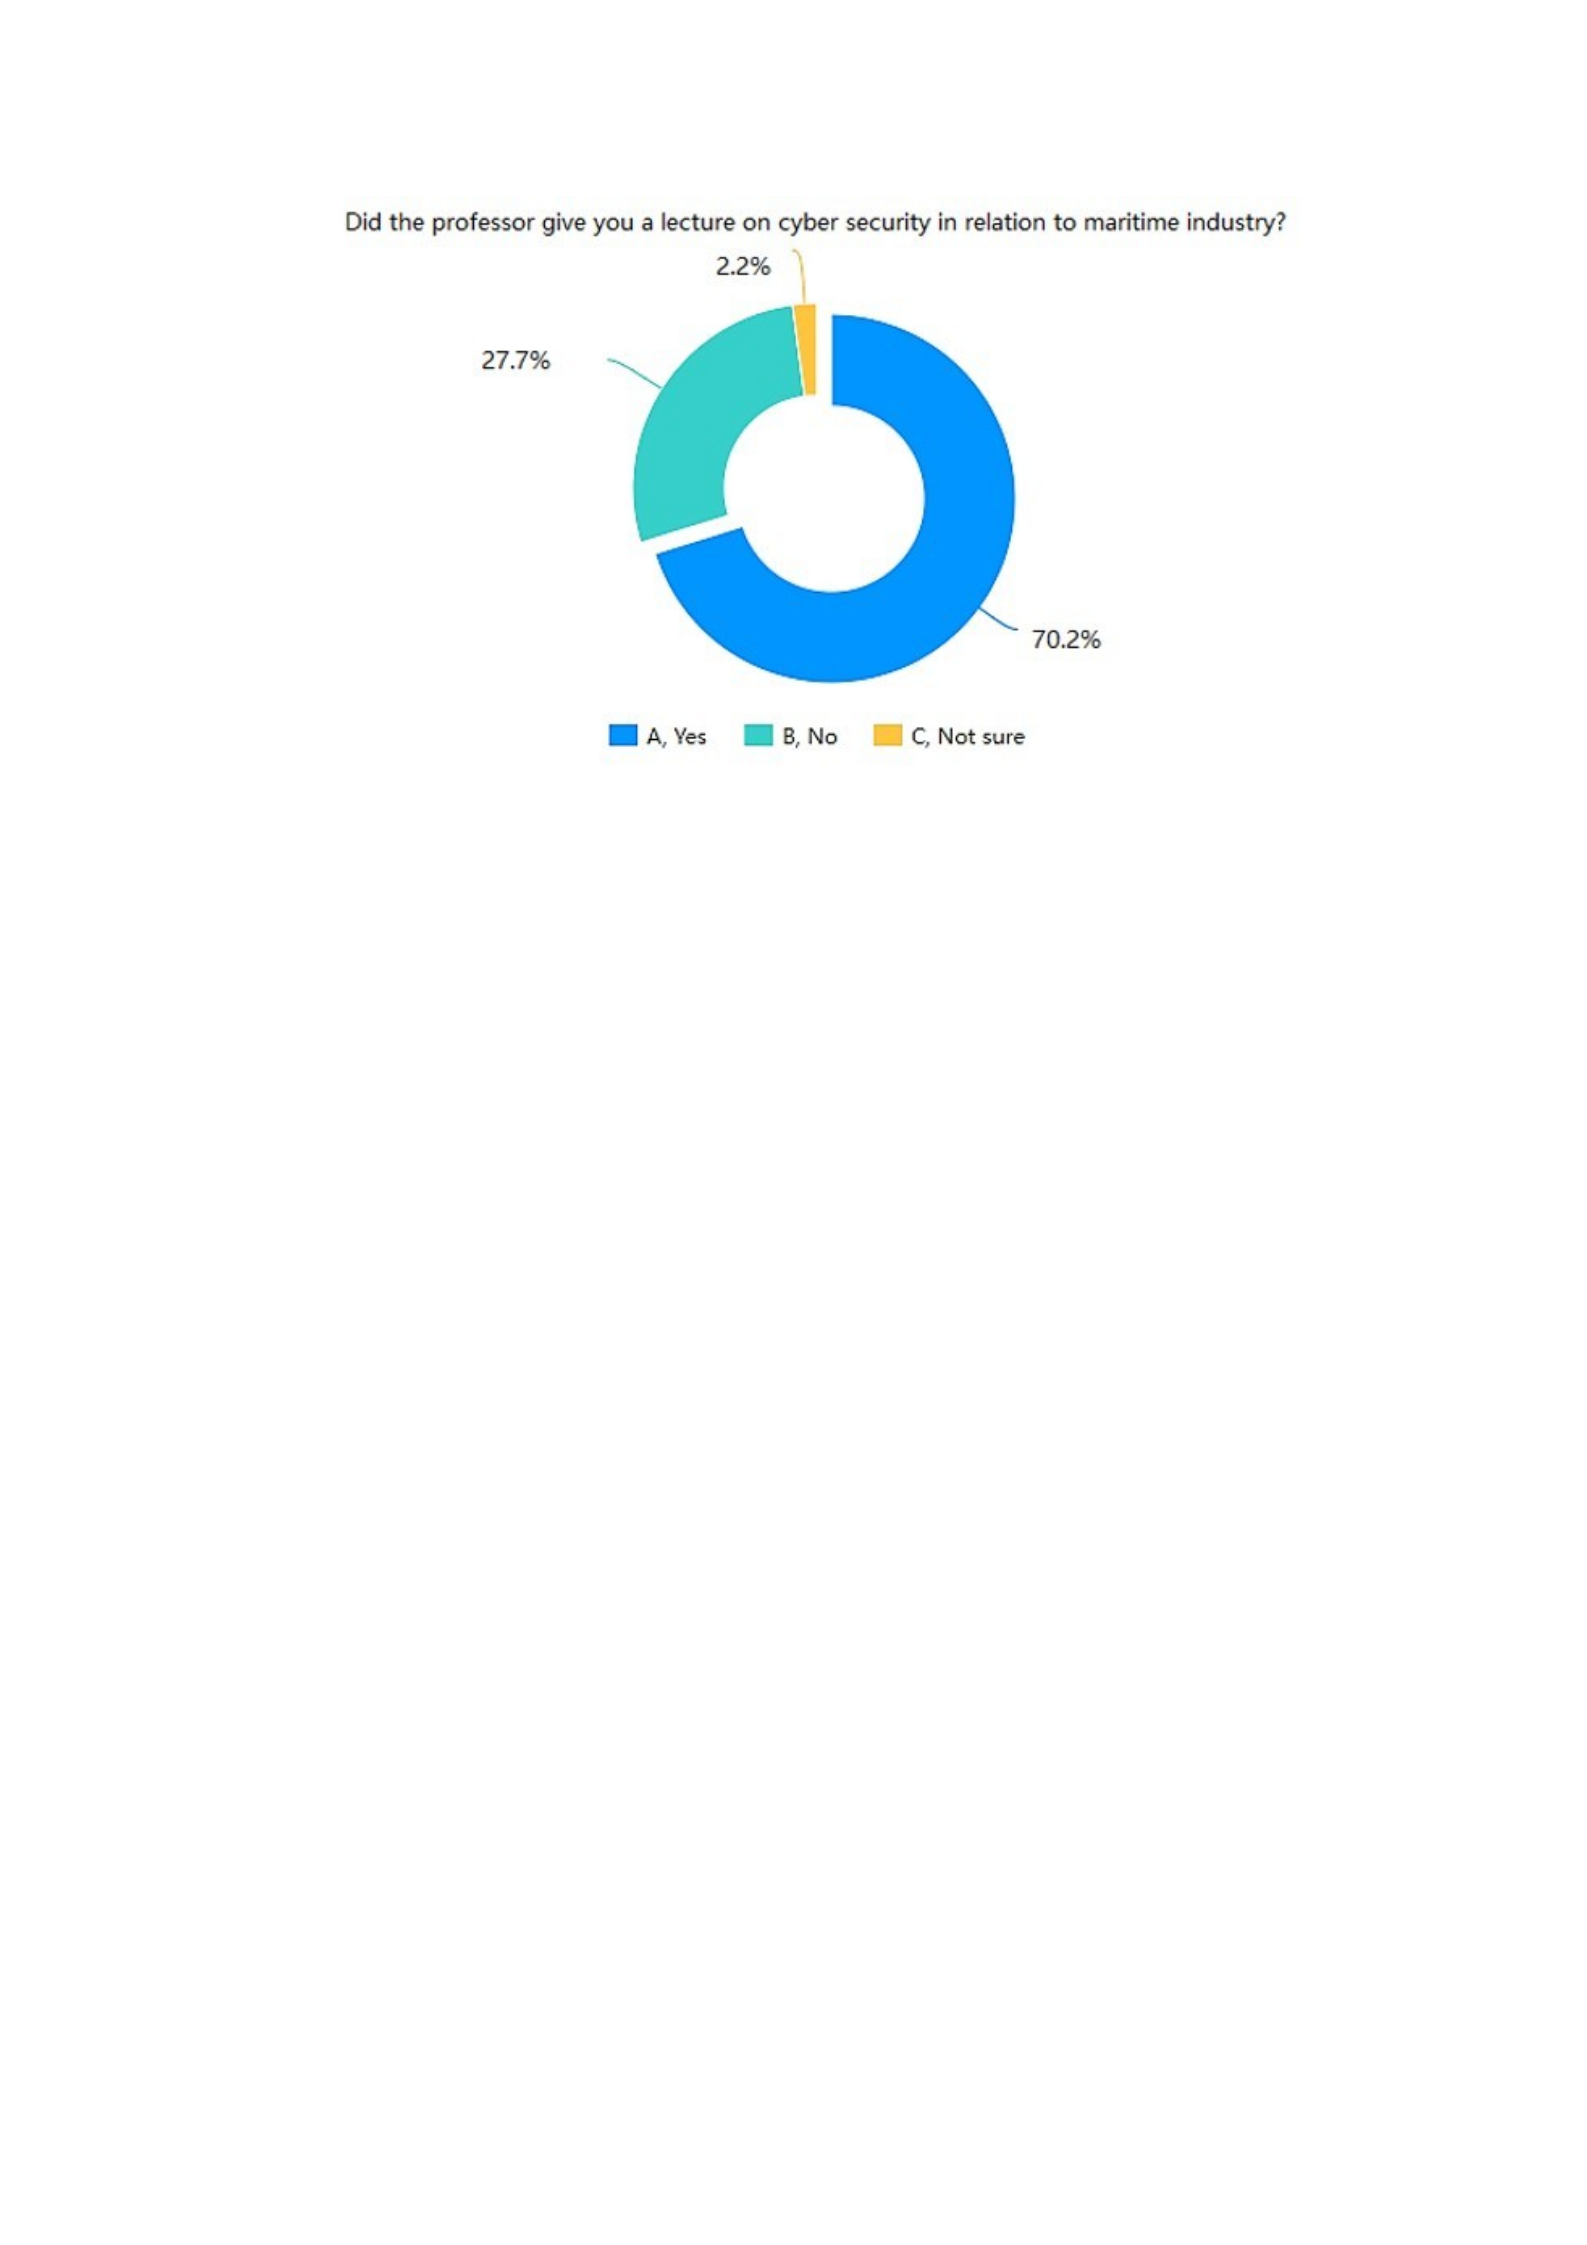
Figure 22 Percentage distribution of question 3
Source: WenJuanXing.
4.4 Summary of maritime cybersecurity survey
The questionnaires and surveys indicate that the most common cyber
incidents on board and ashore are system failures and malware attacks. There are
varying deficiencies in cyber security awareness, shipboard cyber risk assessment
and mitigation, and implementation of cyber security plans on board and ashore.
Maritime cyber security issues are complexity and diversity, and the following
five aspects of challenges and uncertainties are perhaps the one require to draw
attention and urgent resolution.
4.4.1 Human error is always the priority
95% of successful hack attacks or cyber incidents were because of some type
of human error as we mentioned in chapter 2.2.2. Human error to be considered as
the biggest challenge and uncertainness of maritime cyber security in this article,
with lack of cyber security awareness or poor operational behaviors being the main
findings of the questionnaires.

4.4.2 Policy compliance issue
Policy compliance is another challenge and uncertainty in maritime cyber
security issue, whether it is outdated policies and procedures or increasingly
cumbersome and granular policies and procedures, where strictly compliance with
policies and procedures can be difficult. Where there are numerous exceptions to
the implementation of policies and procedures, or where policies and procedures
are often applied and implemented inconsistently, the security posture of the
maritime industry can be significantly weakened.
4.4.3 Legacy system on board
Legacy technology is another significant security challenge and uncertainness.
Especially for shipboard operation system such as engine monitoring system which
are no longer supported by the manufacturer and safety patches and other upgrades
are unavailable (Nabiha, 2020). For example, the windows XP operation system is
still in use on board ship at many computer-based systems which was no longer
updated for long time. One reason for this is that there is less interest from ship-
owners in updating legacy technology, and another is that many legacy
technologies are still applicable.
4.4.4 Budget/ cost
Cost is an unavoidable challenge on maritime cyber security for many
shipping companies and entities. Dealing with cyber security issue currently results
in many shipping companies having to pick and choose what to maintain, upgrade
or purchase. Normally, better cyber security state requires more financial support
(HIMSS, 2021). But it is absolutely unfair to pass on the cost of addressing cyber
security to shipowners and employers.
4.4.5 Maritime cyber security education
Basis on the result of third questionnaire, the analysis shows that students
understand some basic cyber security knowledge, but lack systematic maritime
cyber security knowledge, therefore, it is necessary to improve the typical maritime

cyber security education and training. The most effective and economic measure
could be enhancing the cyber security education at college level.
However, as far as the existing maritime education system is concerned, it is a
great challenge to address the cyber knowledge system of the teachers in the
maritime education industry, and it is clear that the majority of maritime
practitioners engaged in education and training have a very poor understanding of
ship cyber security.
5 Maritime cybersecurity risk control management
Currently, the maritime industry does not have an effective mechanism to
rigorously assess and manage cyber risks, particularly on board ships. Although
cyber risk assessment, mitigation and cyber incident response measures on board
ships and maritime cyber insurance are implemented to varying degrees, they are
generally inadequate (Tonn et al., 2019. Limited data and rapid technological
developments have also inhibited the accurate modelling of maritime cyber risk
(Sahay et al., 2019).
Although a number of prominent maritime organizations such as IMO, ICS,
Classification Societies, IACS, BIMCO, OCIMF and Intercargo have developed
various initiatives and provided guidance on maritime cyber security, none of these
approaches have established a common standard that can be accepted by all, and
the complexity of fragmentation by industry organizations has made it difficult to
address maritime cyber security issues.
Considering the above challenges and uncertainties obtained through the
survey, in this chapter, the author will present a set of short, medium and long term
approaches to address the pressing issues of maritime cyber security.

5.1 Short-term approaches
5.1.1 Highlight cyber security awareness
To raise up cyber security awareness in maritime industry is a global challenge
that requires the effective cooperation and endeavors of IMO, maritime
associations, member states, shipping companies, maritime education and training
entities and other relevant parties (Ignacio, 2021).
IMO, as the leading body for maritime industry, could announce the ‘Cyber
security awareness months” every year to the whole industry or different parts of
industry such as shipboard or ashore to raise awareness about the importance of
maritime cyber security across the industry, ensuring that all maritime personnel
have sufficiently alert to cyber security.
In view of the current vulnerability of cyber security on ships, to alert shipping
industry and raise awareness of ship cyber security, we can organize cyber security
drill or exercise by remotely intruding into ship control systems and managing to
remotely control the ship movements.
5.1.2 Establish internal and external training schedule
From the questionnaire, poor cyber behavior is another factor of challenge and
uncertainties of maritime cyber security, training is not an easy step in the
procedure of transforming personnel cyber behaviors in maritime industry
especially in the shipboard sector (Kavallieratos & Katsikas, 2020).
Unlike cyber security awareness training, personal behavior change training is
one of the best ways to mitigate cyber risks because it means they know what to do
when they experience a cyber-threat. In terms of education and training, external
training provided by qualified third parties is probably the best solution to provide
new ideas and knowledge to existing employees on board and ashore.
Due to maritime cyber security has not yet been incorporated into maritime
education and training system under STCW, currently the relevant education and
trainings are mainly being conducted by well-known organizations. The famous

Elearning on the maritime cyber security program includes DNV maritime cyber
security course(DNV, 2021b), maritime cyber security (basic) training program(SP,
2022), Ondemand cyber security training(RINA, 2022), Maritime cyber awareness
for seafarers the nautical institute(NI Academy, 2022), Training on maritime cyber
security awareness by LR(LR, 2022) etc.
5.1.3 Antivirus / Firewalls software etc.
As we discuss in chapter 3.3.1, the onboard digital information equipment are
various in 8 vulnerable cyber systems as listed in table 3, the IT and OT system
need to be alerted on the effectiveness of antivirus and firewall. Limitation to
internet connection does not mean safe at all in cyber security. Expired/outdated
soft wares in the computer based system will affect the system`s compatibility
(Kessler, 2021).
The common computer skills such as software update, malware protection
software installation, firewall update, web and email content filtering and proxy
server scanning, patch and vulnerability management etc. shall be considered as a
common practice to be implemented into shipboard IT and OT system in the short
future(USCG, 2020).
5.3.4 Engaging RO and establishing maritime cyber audit scheme
A cybersecurity enterprise that focuses on maritime industry, providing advice
on potential cybersecurity threat and focusing on responding to future attacks will
be great help to address the maritime cyber security in short time(Susumu OTA,
2017). However, the cost and revenue to engaging the RO could be a consideration
for maritime enterprise.
5.2 Mid-term approaches
5.2.1 Buildup company cyber safety and security culture
To establish a positive cyber-security culture and raise the awareness of
maritime cyber security among all employees is not a simple task; it requires a

great deal of cost, time and energy, as well as tangible tools like information
bulletins and posters, or games and competitions between ship and shore, or
different departments etc. shipping companies should target to create an approach
that is both entertaining and educative way of encouraging people to take charge of
their own cyber knowledge and awareness in the med-term.(Safety4sea, 2022b).
5.2.2 Establish and implement effective cyber security response plan
In accordance with the IMO MSC.428(98) and MSC-FAL.1-Circ.3-Rev.1, the
cyber risk management needs to be taken into account in the safety management.
For shipping company(CCS, 2020), fully recognition and emphasis on the maritime
cyber risk and put it incorporate into safety management system are vital in current
stage.
Establish a cyber-security response plan generally been considered as a
shortterm approach, however an effective and practical cyber security response plan
requires significant research and study which is not generally been done by a single
shipping company(IACS, 2016).
A systematic cyber security plan requires a massive collaboration between the
various stakeholders and to keep up to date with the state of the cyber technology
and regular updates.
Figure 23 Cyber Incident Response Plan template
Source: Cyber Management Alliance. https://www.cm-alliance.com/cyber-incident-response-plan-template?
hsCtaTracking=0edbe2ea-03c3-4f6f-b253-458a6c407c8e%7C6f079989-2786-445c-8d51-d67d31ce8c2e
5.2.3 Upgrade/replace legacy system
Legacy systems are outdated systems because they are based on older
technology but they are usually critical to daily operation on board ships (Androjna
et al., 2020). shipboard cyber vulnerabilities are in no way limited to GPS, AIS or
ECDIS(USCG, 2017), and the general shipboard IT and OT systems are usually old
and slow to be updated, which make it difficult to have effective protection against
cyber-attack.

With most things, making the transition is easier said than done. Upgrade
/replace shipboard legacy system is an effective measure to address maritime cyber
security, but it is also facing many challenges as well.
The first challenge to Upgrade/replace the legacy system for a company is
budget, and the other unavoidable challenge is a future-ready workforce for
transformation (UNCTAD, 2021a). However, the collaborative innovation in the
maritime industry is a trend of shipping industry, the legacy system must be
replaced in near future.
5.2.4 Setting up maritime cyber insurance system
Maritime cyber insurance could be an important risk management measure to
allow maritime information infrastructure systems to recover effectively from
cyberattacks(Tonn et al., 2019). At present there are not many specific cyber
exclusions in standard P&I cover. To establish a regulated insurance system will
help to address the maritime cyber security issue.
5.3 Long-term approaches
5.3.1 Establishing multi-sector collaboration mechanisms
Future innovation in technology will change the way collaboration works, but
also will affect the way the maritime industry, drive performance improvements
and create opportunities for maritime businesses to take better decisions(GOV UK,
2019). To address the maritime cyber security, multi-sector collaboration
mechanisms shall be established by relevant stakeholders.
One of the most important target of the multi-sector collaboration mechanisms
is to achieve the information sharing between the stakeholder of relevant industry,
such as share cybersecurity threat intelligence with cleared maritime industry
stakeholders (Herr et al., 2020).
A multi-sector collaboration mechanism can promote robust, real-time,
maritimecyber information sharing between maritime stakeholders, and between

those stakeholders and the government (and vice versa), when appropriate, which is
critically important.
5.3.2 Maritime cyber security education
Familiarity with basic computer skills is widely recognized as general practice
in developed countries, however, there are a large percentage of existing
employees, especially seafarers, have not receive a systematic computer education
(Hopcraft, 2021). Their computer skills which were obtained by self-learning and
colleague sharing are far from adequate for the modern maritime industry under
industry 4.0. It is a big challenge for existing seafarers and also a significant
uncertainty for the cyber safety and security of maritime industry.
The challenge of IT education and training for maritime industry is the conflict
between the limited courses setting and the wide range of IT knowledge. Maritime
cyber security education and training could be a huge project need cooperated with
all relevant parties, including IMO member states, flag states, port control states,
shipping companies, maritime insurances etc.
The maritime cyber security training and education shall be integrated into the
STCW maritime education system. Under the IMO framework, a series of
endeavors should be reviewed and implemented in accordance with the latest
development of maritime digital information technology, such as AI, bid data, cloud
computing, chain block, IoT, autonomous ship, etc.(NI Academy, 2022). It will take
time to achieve the effective maritime cyber security education, however it will be
the best solution as a mid-term approach to address maritime cyber security with
contribution of all member states.
5.3.3 Utilizing and alerting the latest DIT
Technological advances offer opportunities but also present some of the
greatest security challenges (IACS, 2020). Unmanned ships such as remotely
controlled boats and autonomous vessels become operational by global internet
connectivity, satellite positioning systems, cloud computing, chain block and

internet of thing, and AI technology etc., marking a technological revolution for the
maritime industry (Silverajan et al., 2018), as these emerging DIT technology been
drawn into maritime industry, their exposure to cyber security risk s will also
increase.
Ports as one of the most important roles in the maritime industry are more
exposure to the cyber threat (Alcaide & Llave, 2020), other maritime industry
stakeholder such as shipping companies, associate organizations suffered many
cyber-attacks in the past years as well. Be vigilant to maritime cyber threat by new
technology while increasing the investment on smart maritime technology is
crucial.
6 Future developments of maritime DIT
Sułkowski et al. (2021,p.16) stated that “The future is today, just somewhat
further”, which is a relevant perspective for maritime industry. In the race of
achieving greater efficiency and competitive advantage, the majority of maritime
companies and stakeholders are actively pursuing the use of high technologies such
as big data, cloud computing, the Internet of Things, block chain and artificial
intelligence. Digital information technology has become a driving force in the
digitization transformation of many sections of the maritime industry(Lai et al.,
2021), especially the shore based sectors, such as the widespread availability of
modern communication technologies, the growth of the Internet of Things for cargo
and passengers, and the continuous development of new logistics innovations.
As the maritime industry continues its processing of digitization
transformation, in the short term, the integration of ship-to-shore networks has
become the trend and will be realized in the next decade; in the medium to long
term, artificial intelligence and big data should be at the forefront as the
stakeholders strive to streamline efficiency and remain competitive(Foster, 2021).

7 Summary and conclusion
This article focuses on the challenges and uncertainties of international
maritime cyber security. This article focuses on the challenges and uncertainties of
international maritime cyber security. The author try to provide an overview of the
structures of maritime cyber information , the current situation of maritime cyber
security state and the international legislation of cyber security, mainly shaped by
the International Maritime Organization.
The questionnaires were successful, a wide range of respondents covering all
aspect of maritime industry, provided mass of valuable information regarding to
maritime cyber security. By analyzing the surveys, the author has identified many
challenges and uncertainties we were never aware of before.
While future vessels may reduce the number of crew, but it is obvious sure that
crewmember will not be completely removed from the ships in short time (Tam &
Jones, 2019). The article forecasts with a great prospect, and addresses the maritime
cyber security measures, and analyses the impact on autonomy and unmanned ships
in the era of big data and cloud computing.
Maritime industry is facing the big challenge on the cyber safety and security
currently (Daum, 2019), maritime technicians especially the onboard engineers
may not be able to sort out the complex cyber security problem without multi-
sector collaborating with real IT technician in short time period.
It will be a trend where qualified RO involves in managing the maritime cyber
security matters, rather than the current maritime technician as many of them are not
professional in the field of internet and emerging information technology due to their
education background.
The current maritime education and training curriculum lags far behind the
development of the maritime digital information technology. Maritime education
and training is probably the best solution to sort put the problem, but considering
the different developments of IMO member states, it will be take a long time to get

effect. The traditional maritime technology need to be handed down, but the
maritime education need a completely evolution to catch up with the development
in information technology of today and tomorrow.

