ISE 620 Module 5 Lab
Carlos Delapaz
SNHU
September 14,2019
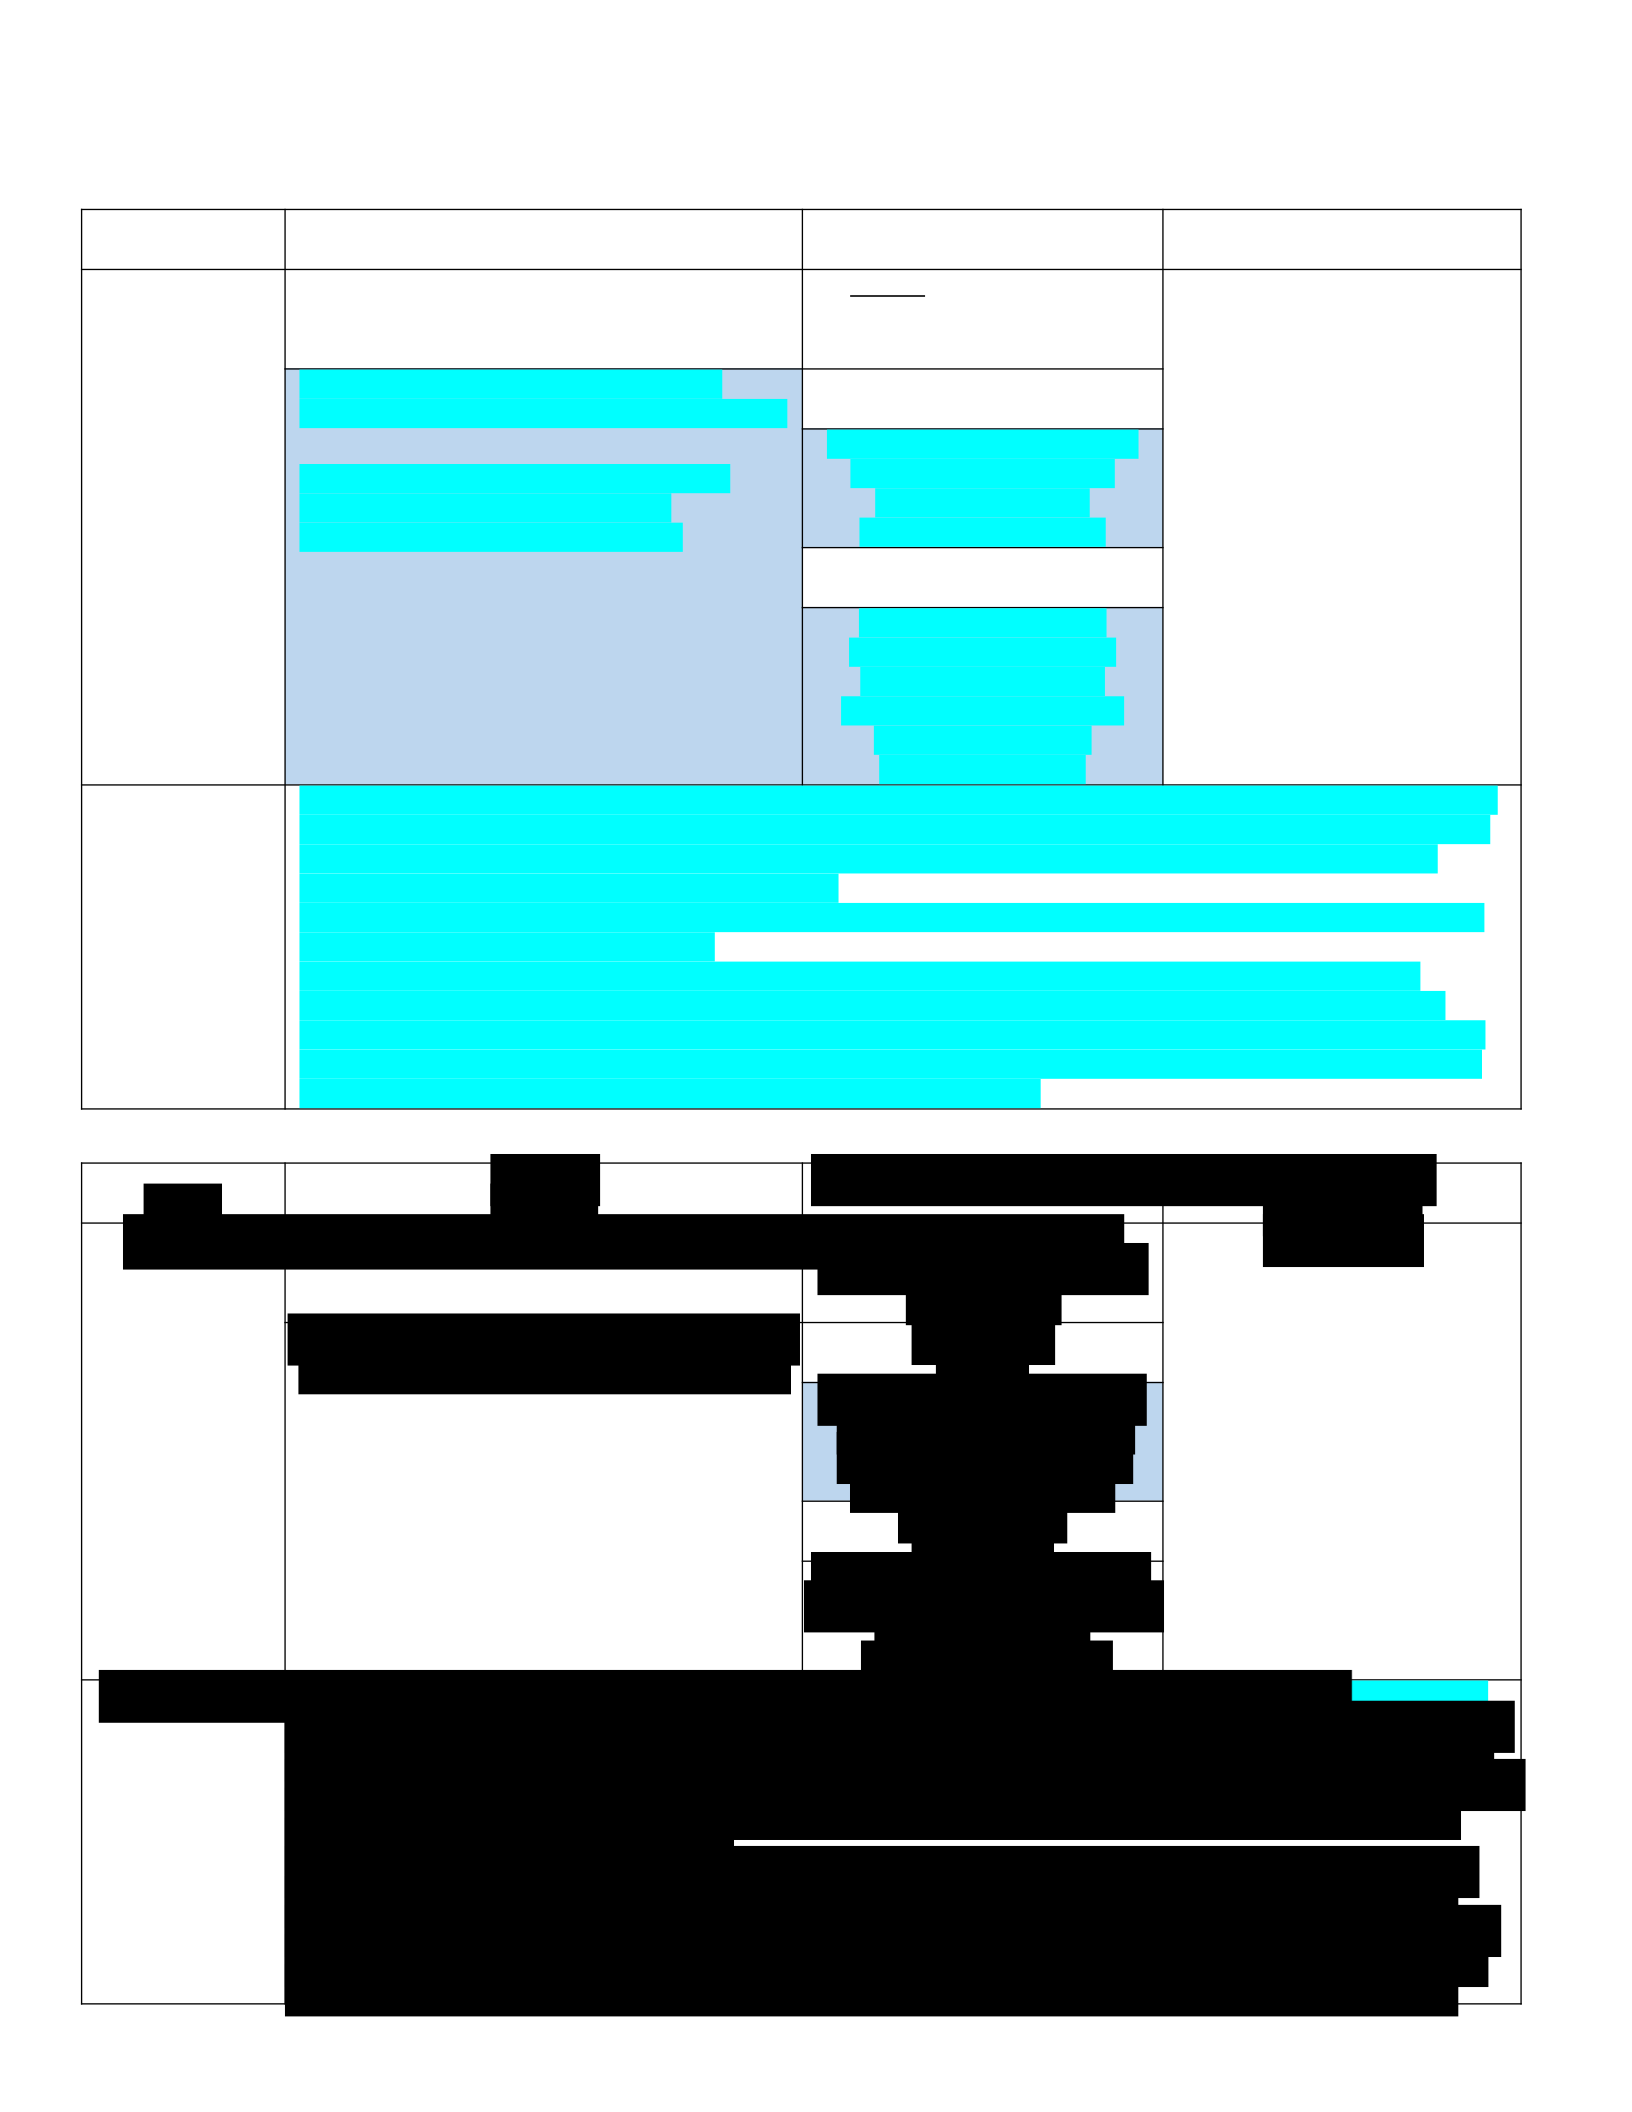
Unauthorized Activities: Courses of Action
ATTACK
STEP
ATTACK
ACTION
DEFENSIVE COUNTERMEASURE DEFENSIVE STEP
(IR PROCESS)
Targeting Objective: Decide who to attack Identify suspicious external
connections to a public-facing
Microsoft Windows server.
Identification
To utilize a scanning tool for the purpose of
scanning a network for open ports on the firewall.
To conduct the scanning of the public-facing
Microsoft Windows servers to identify
vulnerabilities like possible host victims.
DETECTION
POINT
The firewall connection logs will
disclose the connections to
suspicious/ unknown/
anonymous IP addresses.
INDICATOR(S)
OF ATTACK
The connections to the IP
addresses which have been
reported to be abused or
malicious on any reliable and
reputed database, like
www.abuseipdb.com
ANNOTATION Vulnerability scanners are extremely vital tools which are available for security practitioners as well as online hackers. They
are often used for achieving important goals for both parties. The security practitioners make use of vulnerability scanners
so that they can locate open vulnerabilities in their systems or network. The results help them to patch the identified
vulnerabilities and make suitable changes as necessary.
Cyber hackers use vulnerability scanning tools to locate the victims that they intend to attack and identify the key exploits
they these victims might be susceptible to.
Numerous modern firewalls and security appliances like advanced Security Incident and Event Management (SIEM)
platforms have the ability to monitor network traffic, detect vulnerabilities and other suspicious connections. Security
practitioners can establish rules in modern firewalls so that they can drop the connection when malicious connections are
detected. But it is necessary to evaluate every event, even if the connection has been dropped. The collected information
can help by giving detailed insight into redesigning future security decisions.
ATTACK