


Running Head: SNHU
1
SNHU
ISE 510 Security Risk Analysis & Plan
Security Breach Analysis and Recommendations
Milestone 3: Incident Response Plan
SNHU
2
2
Incident Response Plan
I) Identify the Purpose of an Incident Response Plan.
In Limetree, a robust Incident Response Plan needs to be introduced in place so that the
security posture of the business undertaking can be maintained. The fundamental purpose of
designing the plan is to help the firm minimize the risks that arise in the cyber setting. It
encompasses a number of guidelines so that the plan would help the research and development
organization to detect, analyze, prioritize, and handle security incidents. It would offer a solid
framework so that the IT team could implement suitable processes and protocols to be prepared
to face cybersecurity issues.
The Incident Response Plan has been specifically made for Limetree by taking into
account the It ecosystem and the activities that it carries out on the online platform. The plan
would guide the IT department of the undertaking to take proper measures so that it could be
prepared to deal with cyber attackers and online criminals. f
II) Identify the Roles and Responsibilities of the Incident Response Plan
A number of individuals would play certain roles and have responsibilities so that the
security posture of the firm could be strengthened. The key roles of the Incident Response Plan
include Incident Response Coordinator, IT Manager, Chief Executive Officer, and Chief
Network Administrator.
Incident Response Coordinator (IRC) or Team Leader –
The IRC would be responsible to collect data on the security incident, intimating the
necessary parties and ensuring that a robust communication model is established throughout and
SNHU
3
3
after the investigation process. He would drive and coordinate the incident response team
activities so that the damage could be minimized.
IT Manager –
He would have to respond to the It security incident and give authority to each of the
team members with coordination with the IRC.
Communications Manager –
He would lead the effort to communicate for all the audience inside as well as outside the
business firm.
Network Administrator –
He would have to take an active part in the investigation process. In addition to this, he
would document all activities relating to investigation, discovery and recovery tasks ((Cichonski
et al., 2012).
It is necessary to involve law enforcement such as local police and state law enforcement
agencies as well that are responsible to present warrants for disclosure of information.
III) Provide 5-Examples of Incidents at Limetree
a) Give the definition (in your own words) of an IT security ‘incident’ and differentiate
between IT security ‘event’
An IT security ‘incident’ can be defined as a warning that there might exist some form of
threat to the security posture of the undertaking. This warning could also mean that the thread
has already taken place in the IT setting of the organization. Thus, a computer security incident
SNHU
4
4
could mean that there is a threat to policies that are related to the firm’s computer security SEI
(n.d.).
There exist numerous differences between an IT security ‘incident’ and an IT security
‘event’. NIST has defined an IT security incident as an occurrence which potentially or actually
threatens the confidentiality, availability or integrity of an Information System (IS) or the
processes (Kral, 2011). An IT security event can be defined as any alteration in the day to day
operations of a network or Information technology services which indicates that a security policy
might have been violated or a security measure might have failed (Valentin, 2013). Security
events are minor in nature which could arise frequently. When these events produce
repercussions, they are considered to be security incidents (Kral, 2011).
b) Provide exactly 5 examples from Limetree. f
• Official documents containing confidential information were left for anyone to see.
Anyone could make their copies and use the information to adversely affect the
organization.
• A number of computer terminals were left unlocked. So anyone could access the
systems and retrieve sensitive data and information.
• Employees used weak passwords and there was no policy to strengthen this security
measure. Additionally, employees at Limetree changed passwords annually.
• Even though the file cabinets were locked, their keys were kept in plain sight. So
anyone could use them to open these cabinets and steal confidential papers.
• Documents containing confidential business information were not properly disposed of.
Instead of shredding them they were simply put in the trash bin.
SNHU
5
5
IV) Current Incident Response Plan at Limetree
The existing Incident Response Plan at Limetree is very ineffective and weak. I case any
security incidents arise, the system administrators are notified of the same and they escalate the
issue to the IT Manager. He is then responsible to report the incident to the Security Manager if
it is considered to be an actual incident. Currently, there exists no documentation process so
there is no record of previous security incidents (Cichonski et al., 2012).
V) Incident Response Plan & Process
a) Proposed (NEW) Incident Response Plan at Limetree:
A new Incident Response Plan has been proposed that could be introduced at Limetree to
upgrade its security posture. The process has been designed so that the Incident Response Team
could take necessary measures to deal with the security issue and make sure that the extent of the
damage can be curbed to the best possible extent. The main phases that would be involved in the
plan have been highlighted below:
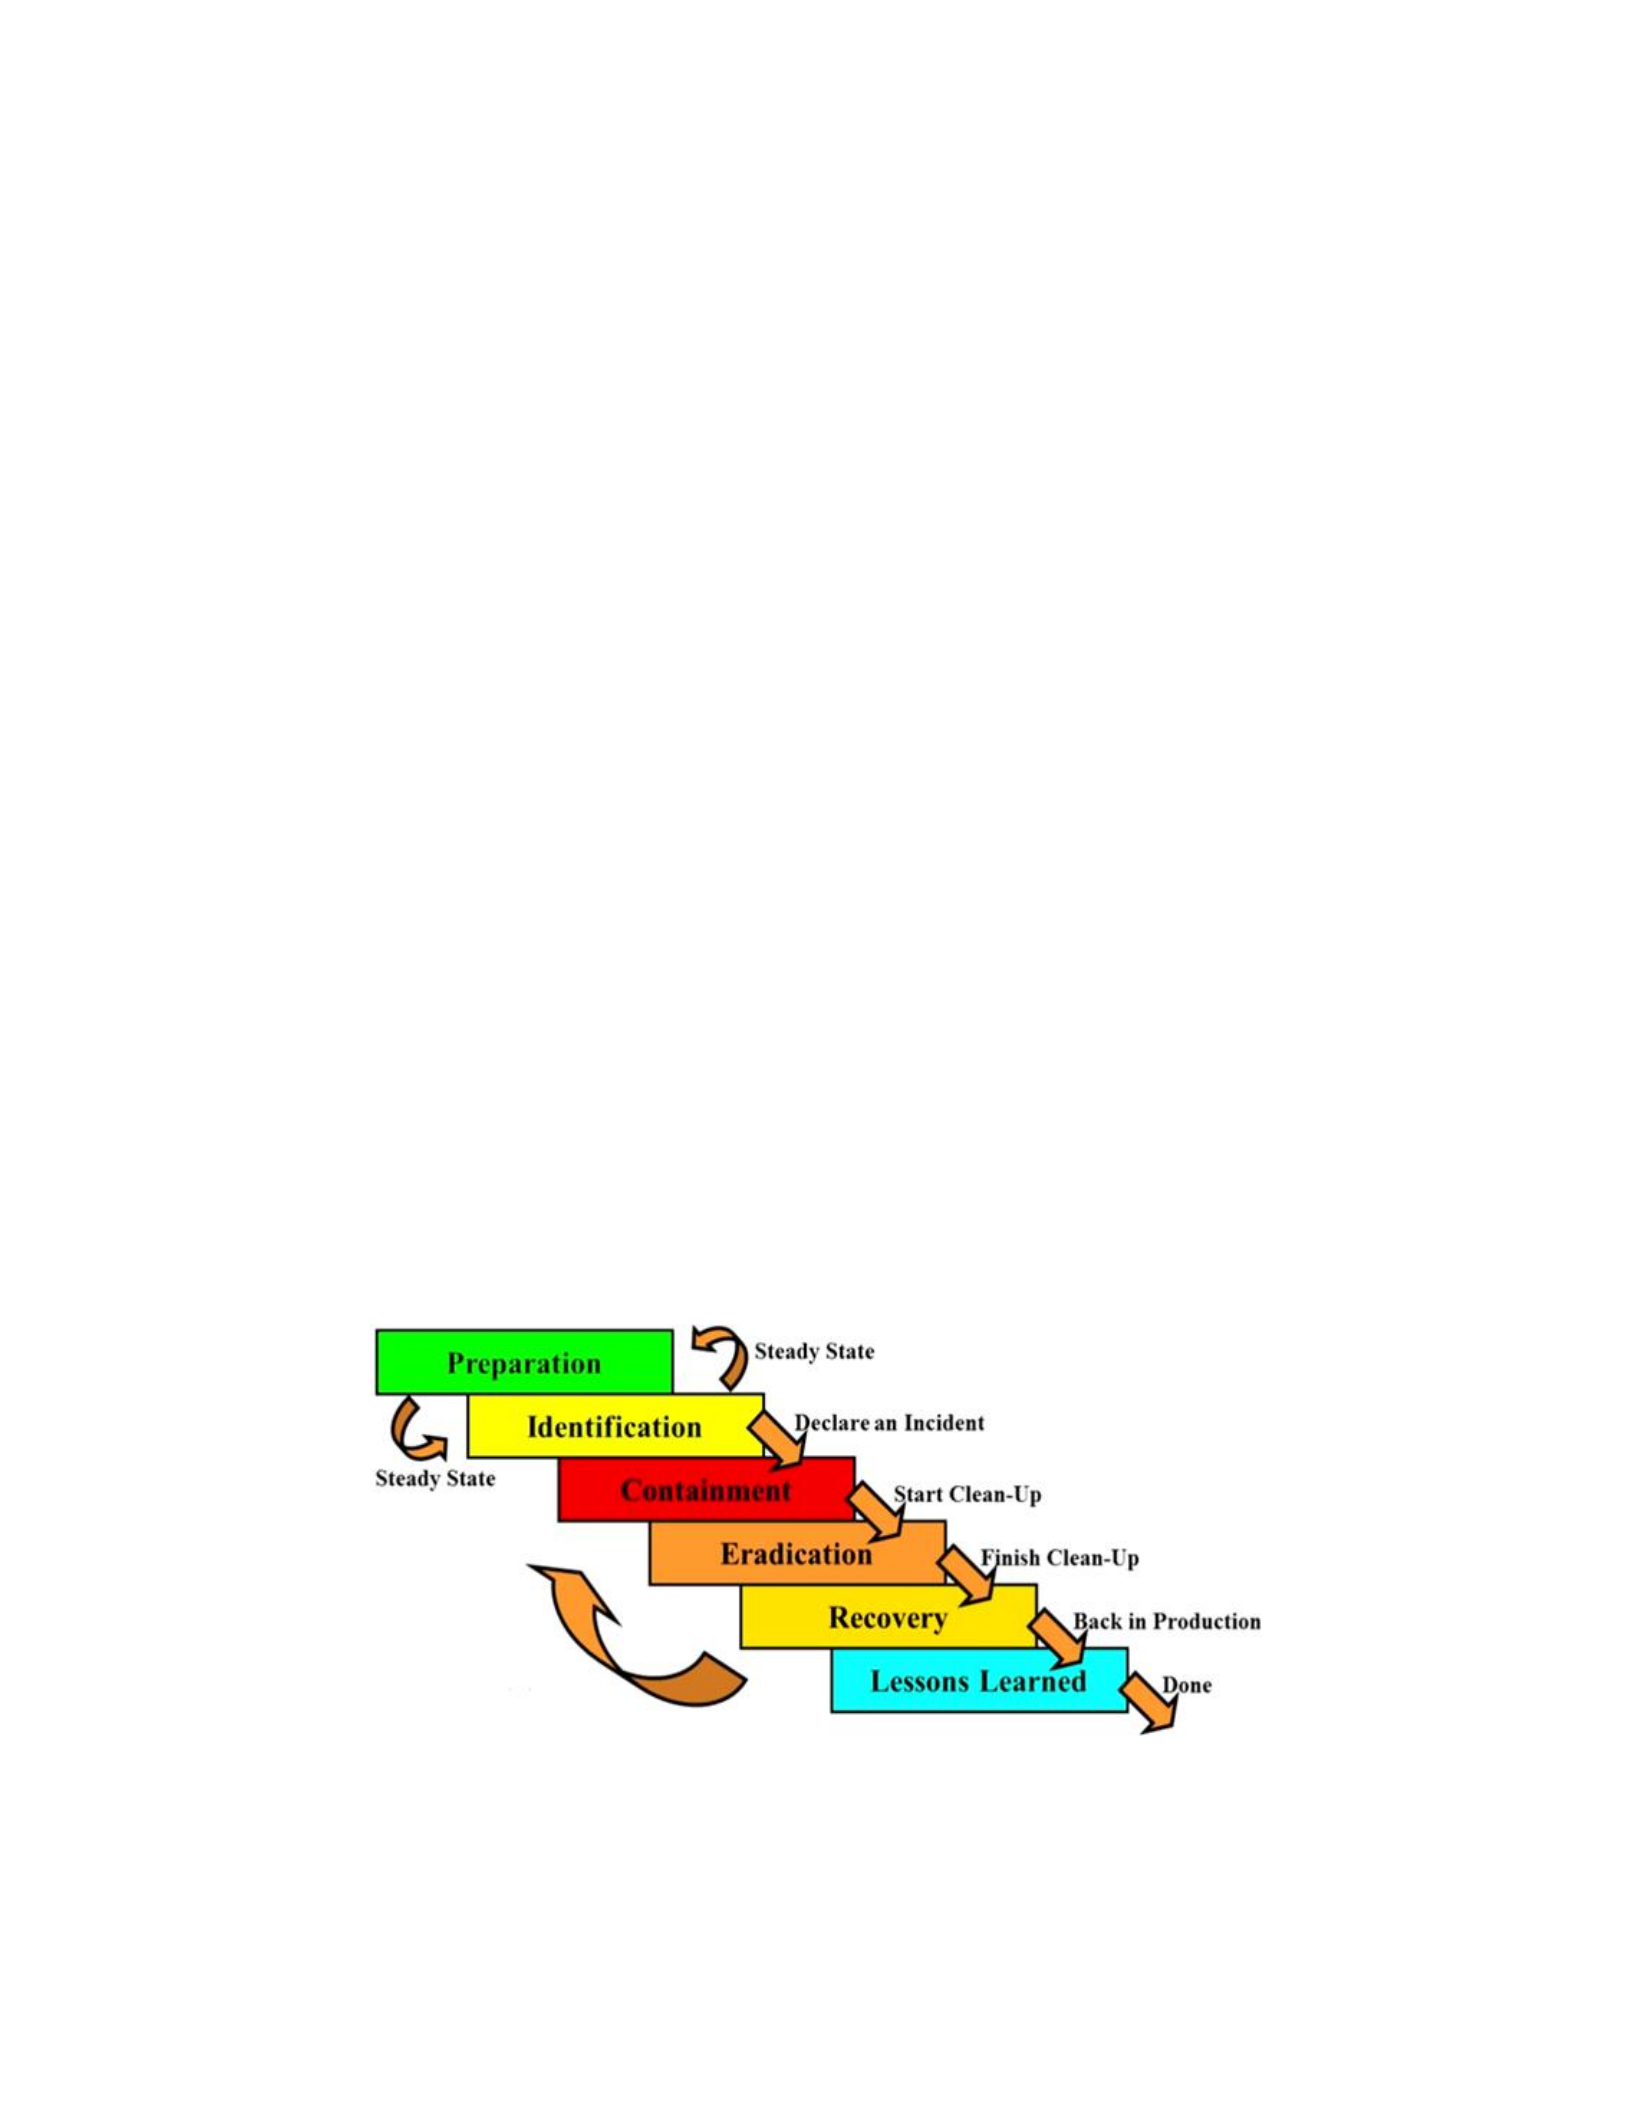
1) Preparation -
In the preparation stage, Limetree must make sure to develop suitable capabilities so that
security incidents could be prevented in the future. So the research and development
organization must ensure highly-functional and effective networks, systems, hardware, and
applications are employed. f
2) Identification –
Limetree has to confirm, categorize, determine the scope and prioritize various kinds of
risks that could arise in the IT ecosystem. Such an approach would enable the business to get a
better insight into the threats and risks that could affect the business in the cyber setting.

SNHU
6
6
3) Containment –
Necessary steps have to be in place so that the damage can be minimized or mitigated to
a possible extent. Limetree has to ensure the affected devices are disconnected from the internet
so that the spreading of the breach could be restricted (Kral, 2011).
4) Eradication –
In order to eliminate the cybersecurity threat, Limetree has to ensure that the root cause
of the issue is dealt with. So, all malicious elements have to be securely removed and the system
would have to be hardened and patched(Valentin, 2013).
5) Recovery –
Limetree has to assess the incident to get a detailed insight into the procedural and policy
implementations (Kral, 2011). At this stage, the business undertaking would have to restore the
affected systems so that they could be restored and brought back into the business environment.
The firm must ensure to document each and every process so that in the new future it could
prepare itself in case similar security breach incident arises (Cichonski et al., 2012).
6) Lessons Learned –
After the in-depth investigation relating to the cybersecurity incident has been completed, a
post-action meeting must be conducted by the Incident Response team at Limetree. All the
members would get the opportunity to discuss the learning from the data breach incident. This
meeting would allow them to assess and document every little aspect relating to the security
incident. Some of the main questions that need to be addressed have been highlighted below:
• What are the changes that can be introduced in the security model to strengthen the
security posture of Limetree?
SNHU
7
7
• How the employees of the firm need to be trained so that their security awareness can
be improved?
• What weaknesses and vulnerabilities had been exploited by cyber attackers?
• What steps will you take to avoid such a security breach incident in the future?
b) The Incident Response Process:
The new Incident Response Process that would be implemented at Limetree encompasses
a number of procedures that will help to minimize the impact the security incident and make a
solid recovery. The figure that has been highlighted below shows that a number of processes of
the response plan would be carried out interchangeably so that proper measures could be
introduced to deal with the security issue. After a security incident has been identified and
corrective actions have been taken, the recovery procedure must be initiated. As highlighted in
the figure, in case fresh malicious elements have been identified, the team can go back to the
containment stage so that suitable measures can be deployed to contain the extent of damage that
might be caused by the IT security breach incident. f f f
Source: (Valentin, 2013)

SNHU
8
8
The team would have to actively assess the Information Technology ecosystem of
Limetree so that it could be able to identify any kind of malicious behavior in its network or
system. All the phases of the Incident Recovery Plan must be followed in a disciplined manner.
The logging records must be critically analyzed to identify any potential security incident. IT
would help to classify the incident that could arise before the research and development entity
and compromise its security posture.
The IT staff members and personnel would be playing an active role throughout the
cybersecurity incident in the organizational setting of Limetree so that all traces of malicious
elements could be effectively identified and suitable actions could be taken against them.
Throughout the process, the roles of communication among the team members would be of
paramount importance. Such an approach would make sure that proper flow of information and
details takes place among the organizational personnel on a real-time basis. The knowledge of
the professionals on the latest cybersecurity incidents must be upgraded on a regular basis so that
they could play an active role throughout the incident response process within Limetree.
SNHU
9
9
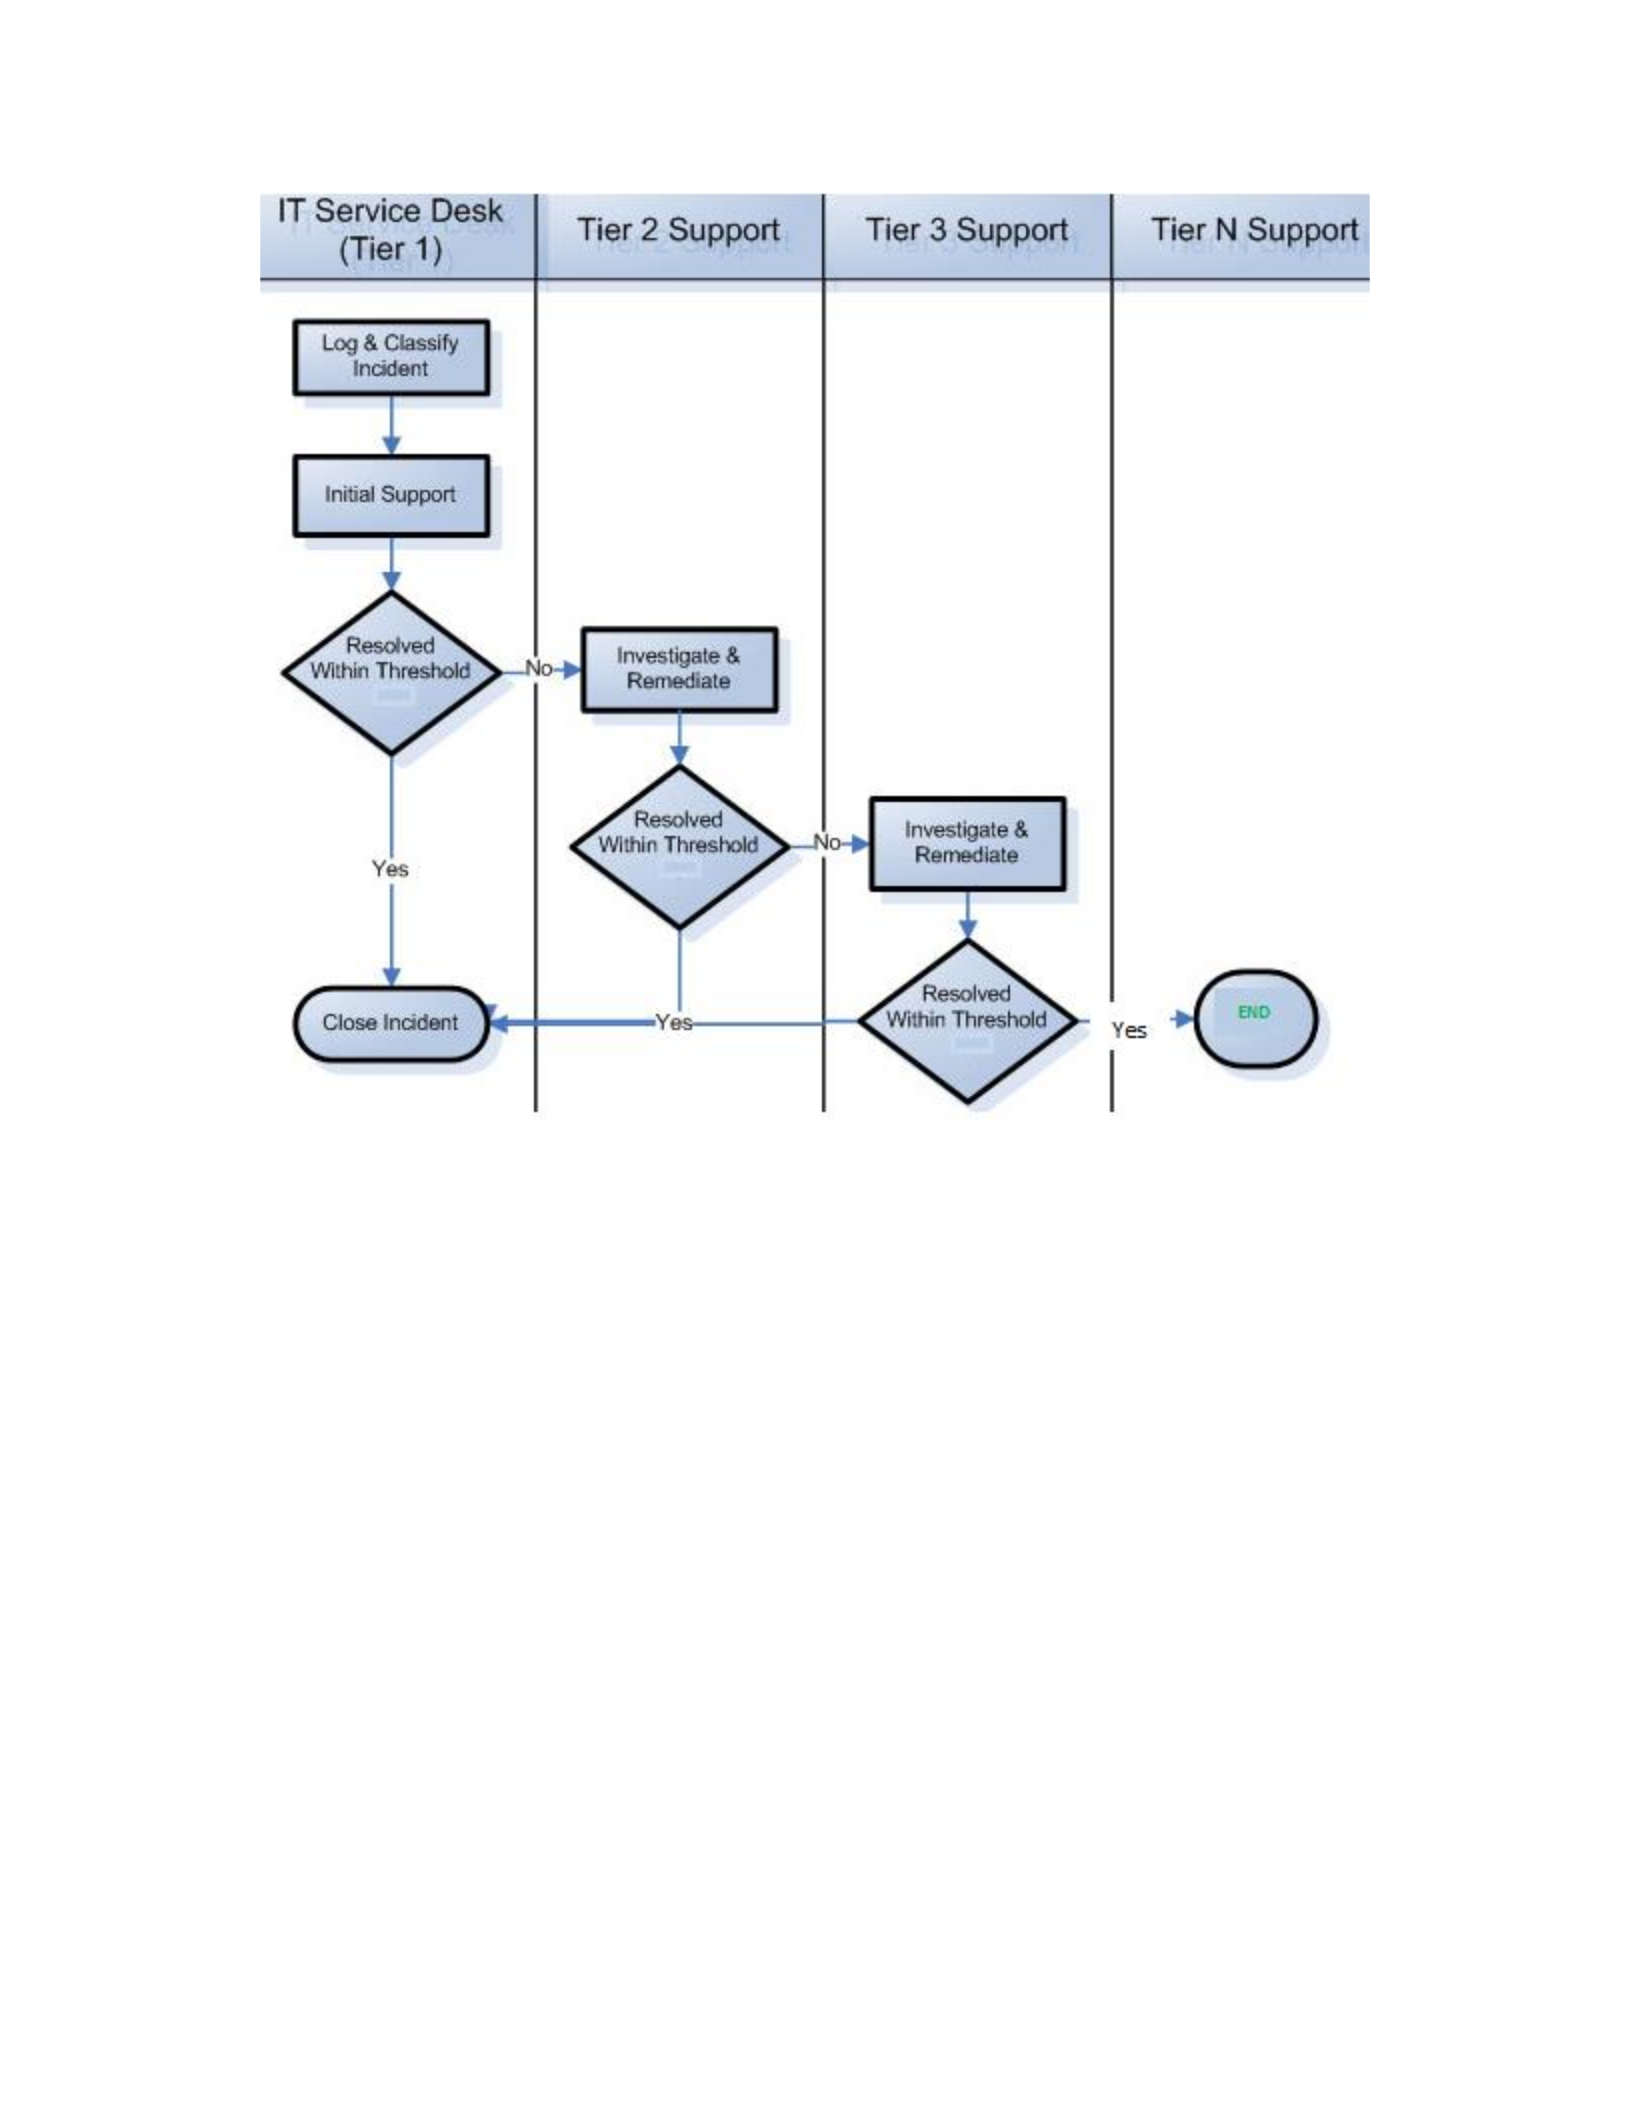
f f f f f f f f f f f f f f f f f f f f Figure 1: Business Recovery Process Flow Diagram f
SNHU
10
10
References
Cichonski, P., Millar, T., Grance, T., &; Scarfone, K. (2012). Computer Security Incident
Handling Guide Recommendations of
the National Institute of Standards and Technology (rev 2). Retrieved from
http://nvlpubs.nist.gov/nistpubs/SpecialPublications/NIST.SP.800-61r2.pdf
Kral P. (2011). Incident handler's handbook. Retrieved from https://www.sans.org/reading-
room/whitepapers/incident/incident-
handlers-handbook-33901
Valentin, J. (2013). Building an incident response team and IR process. Retrieved from
http://resources.infosecinstitute.com/building-an-incident-response-team-and-ir-process/
SEI (n.d.) CSIRT Frequently asked Questions (FAQ). Retrieved from
https://resources.sei.cmu.edu/asset_files/WhitePaper/2017_019_001_485654.pdf
SNHU
11
11
What is Security Incident? - Definition from Techopedia. (2019). Techopedia.com. Retrieved 28
September 2019, from https://www.techopedia.com/definition/15957/security-incident
The list of references must be on a new page at the end of your text. The word “References”
should be centered at the top of the page. Do not underline, bold, enlarge or use quotes for the
word References. The reference list must include all references cited in the text of your paper.
The only exceptions to this rule are personal communications and classical works; they are
cited in text only and are not included in the Reference list.
Margins - 1 inch all sides, including top, bottom, left and right f
Font preference and size - The preferred font is 12-pt Times New Roman. f
SNHU
12
12
Line Spacing - Regular APA is Double spacing, but I prefer using single spacing; especially
tables
Quotations Do not use quotations
Video
Purdue OWL (2012). Purdue OWL: APA Formatting: Reference List Basics. Retrieved from
https://youtu.be/HpAOi8-WUY4

