


Running Head: ISE 510
1
SNHU
ISE 510 Security Risk Analysis & Plan
Week 3 HW 3-1 Video Game: Agent Surefire: InfoSec
=====================================

ISE 510 ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad
ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad 2
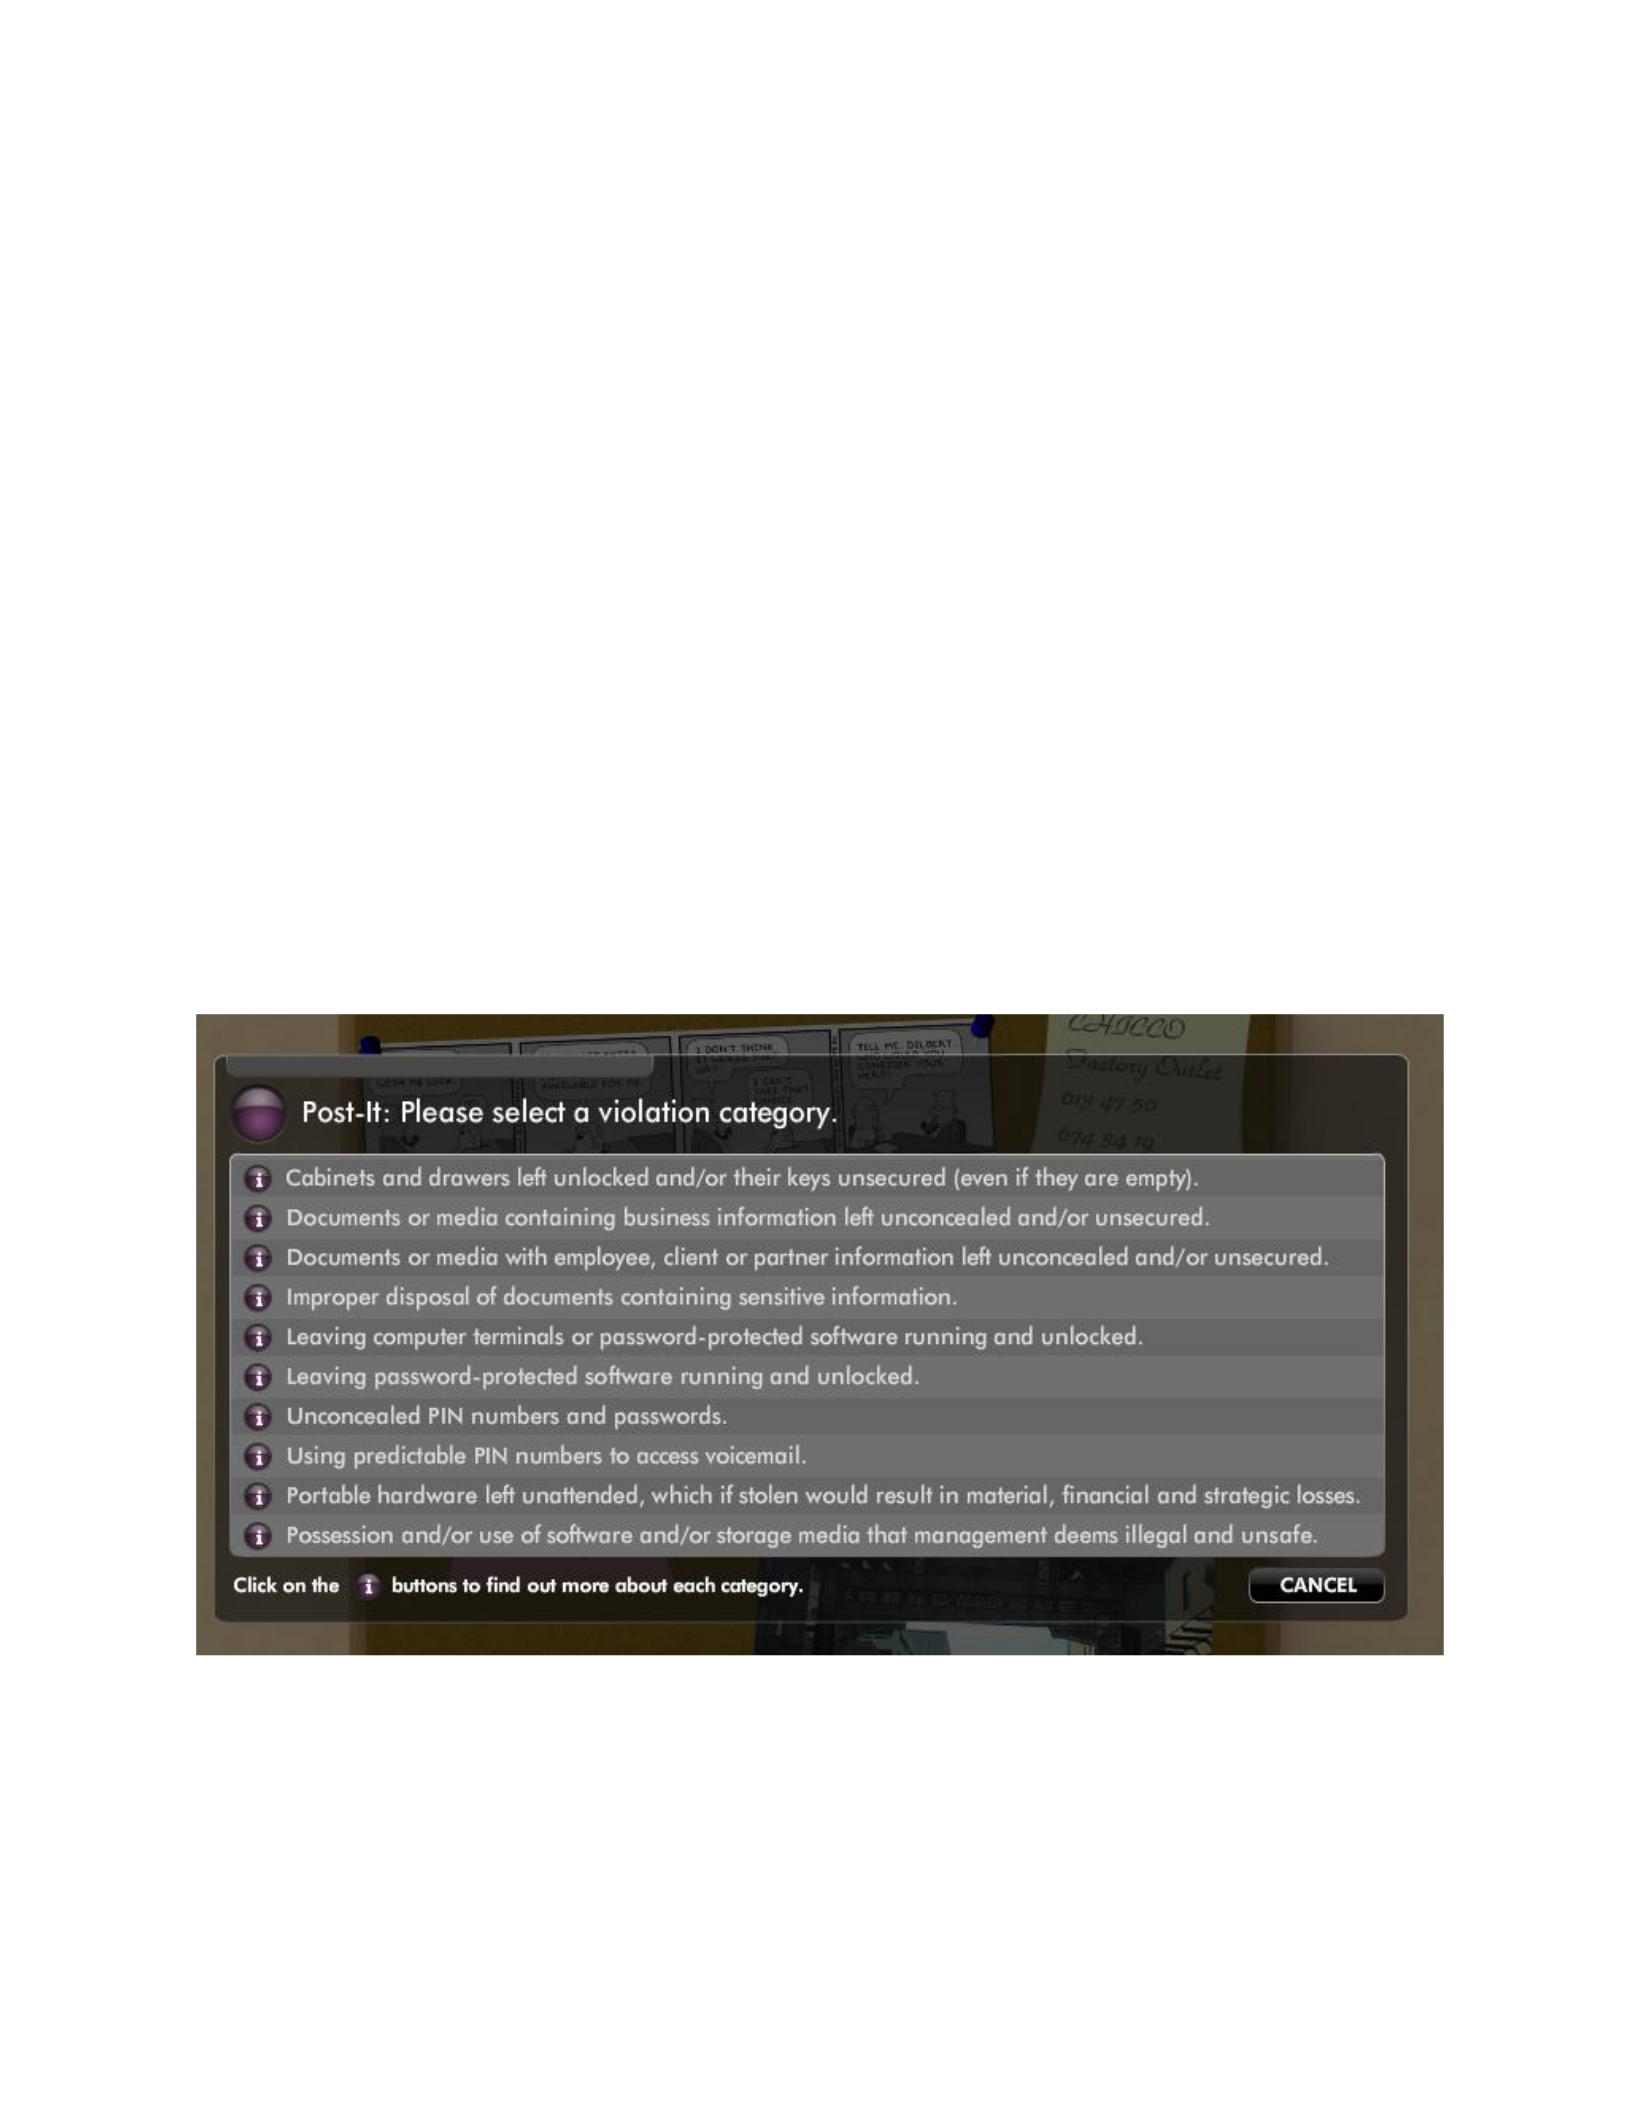
1) (vulnerability category #1). Cabinet and drawers left unlocked and/or their keys
unsecured (even if they are empty). What example of this vulnerability category did you
find?
The cabinet and drawers are supposed to be locked after the office or non-
working hours. The keys to such places must be kept in a secured manner so that it
cannot be accessed by any unauthorized party. In the game, the cabinets were not
locked. In addition to this, numerous keys had been hidden in potted plants (Liang,
Sankar & Kosut, 2015).
2) (vulnerability category #2). Documents and media containing business information left
unconcealed and/or unsecured.
What example of this vulnerability category did you find?
Any information relating to the business whether it is confidential or not must be
kept in a secure manner so that it will not be exposed to outsiders. In the game, there
were multiple areas where documents were carelessly kept. These documents contained
information relating to the clients, employees or partners of the organization.
Additionally, there were certain business documents that were lying on the conference
table.
3) (Mandatory - vulnerability category #3). Documents or media with employee,
client or partner information left unconcealed and unsecured.
What example of this vulnerability category did you find?

ISE 510 ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad
ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad 3
Give details: Which workstation did you find it? Can you identify the person the
desk belongs to? What could be done to prevent this?
Information relating to the company must be securely kept so that it cannot be
accessed by unauthorized individuals. In case the sensitive information is available to
outsiders they can cause severe damage to the business entity. Sensitive information
relating to the employees was kept in a cabinet under the cork board where a post-it
containing safety deposit pin number was attached.
4) (vulnerability category #4). Improper disposal of documents containing sensitive
information.
What example of this vulnerability category did you find?
Documents which contain confidential information of the company such as the
minutes of the meeting, marketing or financial data and business charts must be shredded
in case they have to be disposed of. In the office, the trash bins contained documents
with sensitive business information. It could be easily accessed by an outsider and used
against the company (Liang, Sankar & Kosut, 2015).
5) (vulnerability category #5). Leaving the computer terminals or password-protected
software running and unlocked.
What example of this vulnerability category did you find?
In case computer terminals or password-protected software are kept running and
unlocked, any outsider can gain access into the system containing confidential business

ISE 510 ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad
ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad 4
information. In the office, a couple of workstations were kept unlocked so anyone would
use these systems to steal confidential information about the business undertaking.
7) (Mandatory - vulnerability category #7). Unconcealed PIN numbers and
passwords
What example of this vulnerability category did you find?
Give details: Which workstation did you find it? Can you identify the person the
desk belongs to? What could be done to prevent this?
Passwords are highly case sensitive in nature and thus they must not be written
down where anyone can view them or they must not be left unattended. In case
passwords are written, they must be secured in a safe place so that no one can gain
access to them. There was a post-it on the cork board just above the printer which had
Pin or password written on it.
9) (Mandatory - vulnerability category #9). Portable hardware left unattended,
which if stolen would result in material, financial and strategic losses
What example of this vulnerability category did you find?
Give details: Which workstation did you find it? Can you identify the person the
desk belongs to? What could be done to prevent this?
The loss of a portable hardware can cause significant damage to a business
undertaking both financially, and strategically. It can also adversely impact the reputation
of the business. The data stored in such devices must be encrypted so that in case they
ISE 510 ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad
ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad ad 5
are stolen, the unauthorized individuals cannot gain access to the data. In the office, a
laptop and a personal digital assistant (PDA) were left unattended on the work desks.
Reference:
Liang, J., Sankar, L., & Kosut, O. (2015). Vulnerability analysis and consequences of
false data injection attack on power system state estimation. IEEE Transactions on
Power Systems, 31(5), 3864-3872.
Appendix ad - Violation Category from the InfoSec Game

