


To Explore and Understand the Factors Influencing the Addition of Artificial Intelligence (AI) Skills to
the U.S. Cybersecurity Workforce
Chapter 1: Introduction
Background
AI’s Emergence
AI has come a long way in solving real-world problems compared to earlier days. The
growth of AI has faced challenges as opposed to being uniform, predictable, and consistent.
Leusin et al. (2021) refer to at least two instances of past AI research peaking and stalling.
However, AI research and applications have bounced back and continued to become more
complex, mature, innovative, transformational, mission-critical, and pervasive across multiple
industries (NIST AI, 2021; Leusin et al., 2021; Samoli et al., 2020; NIST AIO, 2017; Arrieta et
al., 2020). According to Leusin et al. (2021), AI research has increased rapidly in recent years
based on their study of international patents from 1974 to 2018. They point out that 80. 6 % of
the total AI patents they identified for research were between 2004 and 2018. Their study also
shows that AI has expanded from computer science to diverse healthcare, manufacturing, and
agriculture applications.
The consistent growth of affordable and powerful computer systems and vast amounts of
readily available data on the internet, combined with continued AI research, results in newer
learning algorithms and transformative and generative AI models and sustain the momentum of
AI. The ongoing AI research topics include explainable and trustworthy AI, general AI
techniques applicable across multiple problem domains, the narrow AI applicable in specialized

situations, and the definition and taxonomy of AI. For example, Arrieta et al. (2020) specify that
the capability to explain a solution derived from an AI technique is an essential attribute of a
"responsible" AI solution. They further point out that the current data-driven AI techniques, such as
neural networks, behave like a black-box solution and cannot be explained easily compared to the
earlier symbolic AI techniques.
AI’s Growth
AI researchers organized as a panel by Stanford University in 2021 discussed the next 100
years of AI. They predicted its significant growth impacting nearly all aspects of our future
economy and society (Littman et al., 2021). Zeadally et al. (2020) mention that an increasing
number of AI-based systems are being built and deployed in many industries. They attribute this
trend to the decreasing cost of high-powered computer hardware and software combined with the
newer AI paradigms, algorithms, and tools. AI techniques are transformational due to their ability
to process large volumes of data faster and more consistently than humans (NIST AI, 2021).
According to NIST AI (2017), AI with machine learning (ML) is changing our nation's way of
addressing economic and security challenges and opportunities.
Furthermore, Littman et al. (2021, p. 12), based on discussions among AI researchers,
present that in the last five years before their panel meeting, AI has made significant progress in
its standard domains, including vision, speech recognition, and generation, natural language
processing (understanding and generation), image and video generation, multi-agent systems,
planning, decision-making, and integration of vision and motor control for robotics. In addition,
they also mention breakthrough applications in other domains, including games, medical
diagnosis, logistics systems, autonomous driving, language translation, and interactive personal
assistance.

AI’s Penetration
Researchers analyze AI-related job advertisements to understand their growth and
penetration across economic sectors. This technique was adopted by Squicciarini and Nachtigall
(2021) to study AI’s progress. The Organization for Economic Co-operation and Development
(OECD), an intergovernmental organization with 38 member countries, sponsored this study by
Squicciarini and Nachtigall (2021). Squicciarini and Nachtigall (2021, p. 46) measured AI jobs
by industry sectors to understand the penetration of AI across economic sectors and labor
markets. Their study shows (pp. 46-48) that AI jobs have grown across all industry sectors they
investigated in the four countries they studied- the United States, the UK, Singapore, and
Canada.
AI-Related Global Patents
Patents reflect inventions within a technical field. Researchers use global patents that
refer to AI techniques to study the emergence of AI and understand its growth. The upward
trends in AI-related patents indicate the potential for sustained growth in AI and healthy demand
for AI in the future. For example, Qiu et al. (2021) analyzed 25,000 AI-related global patents in
their study. The keywords they used to search through the patents include popular AI techniques
of deep learning, deep neural networks, and convolutional neural networks (Qiu et al., 2021, p.
131). Based on the data included in their study, they report that the total number of global AI
patents grew from 4,000 in 2017 to 8,000 in 2018 and subsequently to 14,000 by 2019 (Qiu et
al., 2021, p. 132). Furthermore, they conclude that the number of AI-related patents in signal
devices, telecommunication, and medical technology is significantly higher than in other fields
(Qiu et al., 2021, p. 139).

AI-Related Jobs
Researchers analyze AI-related job advertisements to study the emergence of AI and
understand its growth. This method was used by Squicciarini and Nachtigall (2021) to study the
growth of AI. They used online job advertisements in the UK, United States, Singapore, and
Canada to present the demand for AI skills. Their method has many interesting attributes: (a)
identified job advertisements for generic AI skills, using keywords such as "artificial
intelligence" and "machine learning." (b) identified job advertisements for specific AI solution
categories, using keywords such as "Bayes," "decision trees," "deep learning," "evolutionary
computation," "neural network," "random forest" and "supervised learning.", (c) identified job
advertisements for specific AI application types, use keywords such as . "autonomous systems,"
"computer vision," "image recognition," "intelligent agent," "natural language processing,"
"robotics" and "text mining.", and (d) identified job advertisements for specific AI software tool
kits, use keywords such as “Keras," “ND4J”, “Spark," and TensorFlow.
Many of their findings indicate the future growth of AI, and these are (a) According to
Squicciarini and Nachtigall (2021, p. 29), the total number of AI job advertisements in the
United States grew from 271,562 in 2012 to 908,815 in 2018, (b) Squicciarini and Nachtigall
(2021, p. 30) present using a figure that the total AI-related job advertisements have grown from
2012 to 2018 in all four countries they studied- the United States, UK, Singapore, and Canada,
(c) Squicciarini and Nachtigall (2021, p. 31) present using a figure that the “AI software-related
job advertisements have grown from 2012 to 2018 in all four countries they studied- the United
States, UK, Singapore, and Canada, (d) Squicciarini and Nachtigall (2021, p. 31) present using a
figure that the AI-related job advertisements spike frequently, and they refer to it as "bursts.", (e)
Squicciarini and Nachtigall (2021, p. 46) measure and represent AI jobs by industry sectors to
understand the penetration of AI across economic sectors and labor markets. Their analysis

shows (pp. 46-48) that AI jobs have grown across all industry sectors they investigated in the
four countries they studied- the United States, the UK, Singapore, and Canada, (f) Squicciarini
and Nachtigall (2021, p. 50) summarize that the group of industry sectors "Information and
Communication," "Financial and Insurance Activities," and “Professional, Scientific and
Technical Activities” have the most growth in terms of AI jobs in all countries considered.
AI’s Definition
Despite AI’s growth, a consistent definition of AI that has been accepted by academics,
governments, and commercial organizations continues to be elusive (Kelly et al., 2022).
However, the definition of AI from the High-level Expert Group on AI by the European
Commission is compared with other definitions and described by Sheikh et al. (2023) as precise
enough to include the AI’s current capabilities and broad enough to include AI’s future
capabilities. This definition states that AI systems display intelligent behavior by analyzing their
environment and acting autonomously to achieve specific goals.
Competitive AI Strategies
Potential-driven AI Initiatives. The potential to transform economies, societies, and
national security has triggered fiercely competitive national strategies for researching and
developing AI applications. Littman et al. (2021) state that over 60 countries have initiated AI
strategy since 2015. Furthermore, Bareis and Katzenbach (2021) present that national AI
narratives and strategies are being shaped globally, with risks, uncertainties, opportunities,
flexibility, regulations, and leadership included in the debate topics. In the United States, due to
the National AI Initiative of 2020 (NAII), a National Artificial Intelligence Advisory Committee
(NAIAC) has been established to advise the President on advancing AI.

Comparison of National Strategies. AI-based applications continue to grow and are
increasingly entrenched in competitive organizational capabilities. They are considered
breakthrough technology with the potential to redefine and revolutionize mainstream functions
across multiple industries. According to Bareis and Katzenbach (2021), national AI narratives
and strategies are being shaped globally, with risks, uncertainties, opportunities, flexibility,
regulations, and leadership included in the debate topics. They analyze national AI strategies of
the United States, China, France, and Germany through a study of policy descriptions and the
underlying discourses (pp. 4-7) and mention the standard building blocks for AI strategies among
the four countries included in their study: (a) Between Rupture and Legacy, (b) The Inevitability
of AI, International Competitiveness and the Interdependence of Technology and Societal Good,
and (c) The Necessity of AI, and Uncertainty and Leadership: Articulating Hopes and Fears of
Technological Advancement (pp. 9-10).
In addition, Bareis and Katzenbach (2021, p.17) emphasize that even with similarities in
the building blocks of strategy, the countries differ in their discourses, structure, and media for AI
strategy according to their culture, political, and economic differences. They describe the
variations in AI strategy among the nations they studied: (a) Germany’s AI strategy revolves
around the manufacturing industry and includes ethical aspects such as freedom, participation,
and self-determination of its citizens; (b) France defines its AI strategy towards the betterment of
its citizens by specifically mentioning AI applications for medicine, zero-emission, and urban
mobility, (c) China's AI strategy blends AI applications with high-tech initiatives such as
smartcity, industry 4.0, and intelligent robotics and states social governance and social stability
as its key objectives, and (d) The U.S. AI strategy declares a free-market approach to combine
the strengths of government, industry, and academia. It aims to empower the U.S. worker and
drive growth in the U.S. industry.

The Chinese AI Strategy. Nations formulate AI strategies tailored to their cultural, social,
and economic conditions. For example, the Chinese AI strategy was shaped differently from that
of leading nations like the United States and Germany. The Chinese strategy aimed at AI
leadership by 2030 started with a new generation Artificial Intelligence Development Plan
(AIDP) released in July 2017 by their state council (Roberts et al., 2020). Though the central
government sets an ambitious strategy, the actual innovation and transformation will be driven by
the private sector and local governments (p. 61).
Furthermore, Roberts et al. (2020) describe other vital features of the Chinese AI strategies.
The central government's AI strategy was to reduce the risk and incentivize local governments
and the private sector to use AI technologies. The central government went a step further and
designated a select few Chinese private companies as 'AI national champions' to focus on the
specific areas of AI technology. For example, the company Baidu was to lead the development of
AI-based autonomous driving, and another company, Alibaba, was to lead the AI-driven smart
cities initiative; yet another Chinese company, Tencent, was to lead in the computer vision for
medical applications (Jing & Dai, 2017; as cited in Roberts et al., 2020). These designated
national champions were already internationally successful yet would receive preferential
treatment from the government for using AI.
In parallel to designating national AI champions, the Chinese strategy continued to support
smaller AI companies and startups with financial incentives and left out a few areas of AI for
open competition. The strength of the Chinese financial incentive for AI can be seen through $5
billion in funding for AI in Tianjin (Mozur, 2017; as cited in Roberts et al., 2020). Another
interesting feature of the Chinese AI strategy is the integrated, explicit, and emphatic reference to
the leadership in AI to catch up and gain an advantage over the U.S. military. According to
Roberts et al. (2020), the Chinese strategy considers AI to be a breakthrough technology and that

focused expenditure on AI can provide an advantage to their military over the United States
without having to outspend it on conventional technologies. Like other nations, the Chinese AI
strategy includes AI for strengthening social services and improving people's lives. They
conclude by noting that China is a leader in the development and governance of AI, and its
policies need to be understood from a Chinese perspective.
Strategies to Grow AI-Talent. Talent is essential in developing and deploying AI
technologies (Schmidt et al., 2021, p. 32). Hence, nations formulate AI strategies, including
initiatives and funds for growing AI talent. For example, China and India, the two rapidly
developing economies with large educational systems, have changed their educational policies to
grow AI talent. Jain (2020) compares the steps these two nations took as part of their AI strategy
to grow AI talent. According to him, India initiated its AI strategy with a discussion paper in June
2018 that included healthcare, agriculture, and education as areas for AI applications. India
followed that up in July 2020 by including AI as a focus area in its national education policy; on
the contrary, the Chinese AI development plan initiated in 2017 directly references the inclusion
of AI in its post-secondary education (p. 4).
While India's AI-related talent and education plan is broad, the Chinese plan is more
competitive and includes specific, measurable objectives. For example, the Chinse plan targets
(a) 100 interdisciplinary courses in AI, (b) the publication of 50 world-class undergraduate and
graduate textbooks on AI, (c) the establishment of 50 AI schools, and (d) the launch of 50
national-level AI online courses (Jain, 2020, p. 5). In addition, Jain (2020) points out that the
Chinese strategy is more effective as they have published six times more research papers than
India (p. 13). He concludes by mentioning the challenges faced by India and China in growing
their AI talent (p. 22). India's challenges include (a) a shortage of faculty and (b) outdated

teaching methods. The challenges faced by the Chinese include (a) restrictions on the free flow
of ideas and (b) the digital surveillance of educational institutions.
Ecosystem for AI. Researchers describing AI strategy for a nation or a region refer to an
ecosystem that comprises a collaborative environment to discuss, determine, and achieve
strategic goals. The AI strategy and the associated recommendations vary according to cultural,
social, and economic conditions. For example, Harhoff et al. (2018) elaborate on such an
ecosystem tailored to German conditions in describing the AI strategy for Germany. According to
them, Germany lags leading nations on AI and needs political measures at various levels to
facilitate collaboration between scientists, commercial entities, and society (p. 1). Furthermore,
they observe that AI innovation will be enabled through close exchanges between researchers,
software developers, academic institutions, established companies, investors, and startups (p. 1).
They present the build blocks for an effective ecosystem aiming for Germany’s leadership
in AI (pp. 9-26) and those are (a) Enhance AI research through increased funding, adopting
emerging trends, attracting worldwide talent, and creating benchmarks to measure effectiveness,
(b) Establish AI competencies across society by including AI topics in computer science and
engineering, natural science, and applied science programs, (c) Ensure readily available high-
quality anonymized data pools that will become the foundation of deep learning AI algorithms
for German industries, (d) Provide, in the near and long term, affordable highpowered computing
infrastructure for AI research and development, (e) Expedite AI applications in the German
economy through state-funded AI laboratories for small and medium-sized companies, public-
funded venture capital, and AI investment incentives, (f) Encourage discussions about ethics and
regulatory requirements of AI within the German society so that all stakeholders are
knowledgeable and comfortable with AI technologies, and (g) Envision the German AI strategy
in the context of international competition and join European Union-wide AI

initiatives.
They add that the German AI strategy should include means to identify and measure how
the strategy evolves and the associated ecosystem develops. Finally, they conclude by
mentioning the indicators of an effective AI strategy and growing ecosystem in Germany: (a)
The attractiveness of German institutions for leading AI researchers, (b) Quality and quantity of
German AI patents, (c) German publishers at AI conferences, (d) Venture capital investments in
German AI startups, and (e) Growth of German AI companies.
Adoption Challenges
While researchers indicate that AI is increasingly used to solve mainstream problems,
they also describe the factors that impede the adoption of AI and recommend enhanced
governance of AI as it emerges to support mainstream functions (Schwartz et al., 2021, p. 35;
Littman et al., 2021, pp. 29-37). The key factors that impede the broader adoption of AI include a
lack of trust in AI, biases introduced through the big data behind machine learning algorithms,
and a lack of explanations when AI algorithms behave like black-box solutions.
Specifically, Littman et al. (2021, p. 33) describe growing concerns among researchers,
policymakers, and governments about establishing and securing public trust in AI. Ryll et al.
(2020, p. 115) mention impediments to the adoption of AI in the financial industry as (a) data, (b)
talent, (c) trust, and (d) regulations. Arnaz et al. (2020, p. 110804-12), while elaborating on the
emergence of AI in the manufacturing industry, mentions that further research is required on data
quality and trust in AI. In addition, Arrieta et al. (2020, p. 82) point out that even impressively
popular and successful AI algorithms such as deep neural networks and deep learning are data-
driven empirical techniques and lack causal links to explain outcomes to their human users and
subject matter experts. According to them, this inability to explain the datadriven AI technique's

performance in a human-comprehensible manner is a barrier to the broader adoption of AI
techniques (p. 108).
Researchers call for further studies on the building blocks of AI's adoption challenges.
For example, on behalf of the NIST, Schwartz et al. (2021) propose techniques to manage bias
within AI. They refer to accuracy, explainable algorithms, interoperability, privacy, robustness,
safety, resilience, and mitigation of harmful bias as building blocks of trustworthy AI that need
further studies. Furthermore, the International Standards Organization ISO (2017) has a
dedicated working group on trustworthiness regarding AI standards. However, research on these
building blocks of AI's adoption is still early; hence, these impediments to AI's adoption are not
readily quantifiable.
Risks, Governance, and Regulations
Leading researchers emphasize the need for better control and governance of AI (Littman et
al., 2021). They list several AI's potentially harmful influences on society. These are (a) The
temptation to apply AI decision-making to all societal problems could negatively impact complex
special social issues, (b) Dangers of adopting a statistical perspective on justice and automating
decisions that may produce skewed results, replicating and amplifying existing biases in the data,
(c) When AI systems do not generalize beyond their training data, discrimination, and risk in
medical applications, and (d) AI systems that replace human workers as opposed to augmenting
the workforce.
Other researchers also mention the risks of AI and refer to strategies that include
governance for the safe, ethical, and legal use of AI with minimal economic and social
disruption. For example, Parker (2018), in describing the U.S. National AI Strategic Plan 2016,
refers to governance-related research and development priorities. These include (a)
understanding and addressing ethical, legal, and social implications, (b) ensuring the safety and

security of AI systems, and (c) enabling AI-human collaboration as opposed to replacing humans
with AI.
Multilateral groups of nations are creating governance structures in AI strategies. For
example, the European Union (EU) has regulated automated decision systems and formulated the
framework of ethical aspects of AI robotics and related technologies, which recommends the
creation of national supervisory bodies (Littman et al., 2021, p. 39). In addition, Canada has
initiated AI governance for automated decisions. Furthermore, Jelinek et al. (2020) propose an
international committee for the governance of AI and to mitigate its risks while the collaborating
nations compete with their own AI strategies.
AI for Cybersecurity
Opportunities to Enhance Cybersecurity
Researchers analyze and present the potential of AI to strengthen cybersecurity. Samtani
et al. (2020) state that securing cyberspace has become a major societal challenge in the 21st
century. Significant research is in progress on applying AI techniques to improve cybersecurity.
Chen et al. (2020) predict that AI-based learning techniques will help cybersecurity in the face of
rapidly emerging and complex threats to computer systems. Lazic (2019) emphasizes using a
quote from another research report that strengthening cybersecurity with AI is paramount to
organizations. He further points out that the same research report mentions the belief in using AI
techniques by hackers. Finally, Samtani et al. (2020, p. 16) summarize that AI techniques can
enhance cybersecurity significantly, but it is still in the early stages of development.
According to Bresniker et al. (2019), for cybersecurity to advance, AI techniques such as
machine learning must automate the mundane tasks of cybersecurity professionals, enabling
them to investigate more events in a shorter period. They further predict that AI can detect threats
when applied effectively and recommend timely remediation steps to cybersecurity professionals.

In addition, they conclude that when AI applications for cybersecurity become more advanced,
they will detect earlier and help deter denial of service attacks, data leakages, and network
penetrations.
The increased sophistication of cyber-attacks necessitates using AI to strengthen
cybersecurity (Capgemini 2019, as cited in Lasisi et al., 2022). Furthermore, the utilization of AI
technology for strengthening cybersecurity is spreading globally (Abbas et al., 2019, as cited in
Lasisi et al., 2022). Therefore, to protect critical computer systems from increasing AI-based
cyber-attacks, Lasisi et al. (2022) emphasize that AI techniques, including machine learning,
deep learning, multi-agent systems, game theory, and neural networks, should be included in
cybersecurity education.
Cary (2021), in a study sponsored by a think tank Center for Security and Emerging
Technology (CSET) based at Georgetown University's School of Foreign Service, reports on the
need for the U.S. to bolster cyber/AI skills in response to an increasing number of Chinese
universities implementing programs with AI and cybersecurity. He concludes that the U.S. is well
positioned and better organized, in the long run, to standardize cybersecurity education by
including AI topics.
As data-driven AI algorithms such as machine learning and deep learning become more
advanced and the available data for cybersecurity analysis increases, AI-based cybersecurity
detection techniques are also evolving rapidly (Zeadally et al., 2020). Artificial Intelligence (AI)
based applications enable efficient and effective processing of large volumes of complex
cybersecurity data, increasing the potential for enhancing cybersecurity tasks, such as asset
identification, vulnerability management, emerging threats detection, and control deployment
(Samtani et al., 2020).

According to Chen et al. (2020), AI-based learning techniques will strengthen
cybersecurity in the face of emerging threats to critical computer systems. Lazic (2019)
emphasizes using a quote from another research report that strengthening cybersecurity with AI
is paramount to organizations as hackers already use AI to enhance their attack tools. Finally,
Dhir et al. (2021) describes the prospects of AI-enabled cybersecurity elements such as network
security, security planning, and penetration testing that could soon lead to automated cyber
defense.
Barriers to Fully Harnessing AI
While researchers analyze and describe AI’s growing potential to strengthen
cybersecurity, they also study the barriers to harnessing AI for cybersecurity (Schwartz et al.,
2021). For example, Alsheiabni et al. (2019) mention the lack of skills to build AI solutions for
cybersecurity as a significant barrier, and Zhang et al. (2020) point out that cybersecurity skills
with AI knowledge are short in supply. Furthermore, Gupta et al. (2020) mention the shortfall of
AI skills in the cybersecurity workforce and recommend educational courses as a solution.
Finally, lack of top management support, lack of AI skills, and employee fear of change are
mentioned as organizational barriers based on a survey of 207 industries in Australia (Alsheiabni
et al., 2019).
Rawindaran et al. (2021), using a survey of small and medium enterprises in the UK to
study the adoption of AI for cybersecurity, report that 30% of the cybersecurity professionals
needed to be made aware of the AI capabilities available in their cybersecurity software tools.
Davidson and Filkins (2019) surveyed cybersecurity professionals working or actively interested in
using AI to improve their organization's security posture. Their study identified barriers to adopting AI
for better cybersecurity and reported that 27% of the participants identified a lack of AI skills in
cybersecurity teams as a significant barrier, with 35% pointing to a lack of AI maturity for

cybersecurity. Lasisi et al. (2022) refer to the benefits of preparing cybersecurity professionals with AI
skills and recommend including AI courses in cybersecurity undergraduate programs. According to
Cary (2021), China has eight universities integrating AI into cybersecurity programs compared to a
single university in the United States doing the same. He recommends the United States act
expeditiously to enable an AI-skilled cybersecurity workforce. Problem of Study
General Problem
A shortage of AI skills in the U.S. cybersecurity workforce is one of the leading barriers
to fully harnessing the potential of AI to strengthen U.S. cybersecurity. The research findings
leading to the selection of this general problem include (a) demonstrated benefits of AI
techniques such as machine learning to strengthen cybersecurity (Samtani et al., 2020; Zeadally
et al., 2020), (b) an increase in the utilization of AI techniques by malicious actors to breach the
cyber defenses of mission-critical information systems, which requires an AI-based cybersecurity
response (Lazic, 2019; Lasisi et al., 2022) and (c) lack of AI skills among cybersecurity
professionals to develop, deploy, and utilize AI-based cybersecurity applications and tools
(Davidson & Filkins, 2019).
The adoption of AI is impeded by additional attributes such as lack of trust, algorithm
results that cannot be explained, and bias in the data behind algorithms; when combined with low
executive awareness, shortage of skills, and weak business justification, they result in significant
challenges to develop AI-based solutions and to harness the potential of AI fully. The selection
of shortage of AI skills from the many challenges AI faces for this study narrows down the
general problem.

Specific Problem
Current studies have established the importance of AI skills for the cybersecurity
workforce and its shortage as a barrier to AI’s adoption (Alsheiabni et al., 2019; Zhang et al.,
2020; Gupta et al., 2020; Lasisi et al., 2022; Cary, 2021; Davidson & Filkins, 2019). The
proposed study will further explore the factors influencing adding AI skills to the U.S.
cybersecurity workforce. A systematic study to understand the supporting factors and
impediments to adding AI skills to the U.S. cybersecurity workforce will augment the ongoing
efforts to harness the potential of AI for better cybersecurity.
Purpose of Study
This study aims to explore, identify, and understand the factors impacting adding AI skills
to the U.S. cybersecurity workforce. In addition, the study is designed to provide insights into the
positive factors that aid the addition of AI skills to the workforce and the negative factors that
impede it. It is directed toward generating potential theories grounded on the views of U.S.
cybersecurity professionals who comprise the workforce. In theorizing, this study will analyze
the nature, meaning, origins, and perceptions of the impacting factors and the extent to which
they impact the addition of AI skills. The outcomes of this study could help increase the AI skills
of the U.S. cybersecurity workforce and expedite AI-based tools and techniques for more robust
cybersecurity.
Conceptual Framework
The study is approached through the philosophical lens of interpretivism, in which the
meanings of reality are understood by social actors (Moerman, 2016e). In other words, the
factors that impede or enable the addition of AI skills, as perceived, experienced, explained, and
described by the professionals who make up the U.S. cybersecurity workforce and to be

interpreted by the researcher, will lead to a better understanding of the phenomenon and help
answer the research question.
Studies have described (a) AI’s impact on multiple industries, (b) the utilization of AI for
malicious attacks on critical information systems, (c) AI’s potential to strengthen cybersecurity,
(d) an urgency to strengthen cybersecurity with AI, (e) a need for blended AI and cybersecurity
skills, (f) general shortage of AI skills to develop AI-based solutions, and (g) additional AI’s
adoption challenges such as lack of trust, bias in the data used, and the inability to explain the
solutions.
Furthermore, researchers also point out the specific shortage of AI skills in the
cybersecurity workforce as a leading barrier to fully realizing AI's potential for cybersecurity.
Therefore, researchers analyzing the need for AI skills for cybersecurity recommend, as a
longerterm solution, including AI topics in cybersecurity academic programs for a future AI-
enabled cybersecurity workforce. However, the U.S. cybersecurity workforce is estimated to be
over a million strong (International Information System Security Certification Consortium, 2021,
p. 5). Therefore, while the studies emphasizing the inclusion of AI topics in the U.S.
cybersecurity academic programs continue, adding AI skills to the current U.S. cybersecurity
workforce needs to be studied and understood to enable and expedite AI technologies for
strengthening U.S. cybersecurity practices.
The factors that impede or enable the addition of AI skills, as perceived, experienced,
explained, and described by the cybersecurity professionals and interpreted by the researcher,
will lead to a better understanding of the phenomenon and help answer the research question.
The study focuses on adding AI skills to the U.S. cybersecurity workforce. Since prior
researchers have studied adding AI topics to the cybersecurity academic curriculum, the
proposed study will exclude the U.S. academic course contents. In addition, limiting the study to

cybersecurity professionals within the United States narrows the environmental factors and
makes the research question precise.
Significance of Study
The proposed study could potentially enhance and expedite the harnessing of AI to
strengthen cybersecurity in the United States. The objective is to understand the factors that
positively and negatively impact adding AI to the cybersecurity workforce. The significance of
the study is directly proportional to the importance of cybersecurity to the U.S. economy, its
national security, and AI's value in strengthening cybersecurity. According to Lewis et al. (2020;
as cited in Ciuriak, 2021, p. 4), the annual global cost of cybercrime is one trillion dollars.
Zeadally et al. (2020) elaborate on harnessing AI techniques to fend off cybercriminals and
minimize data breaches.
Cybercriminals are using AI techniques to lower the cost and improve the effectiveness of
attack tools, and hence, cybersecurity needs to evolve faster using the same (Zeadally et al.,
2020). Understanding the factors that influence the AI skills of U.S. cybersecurity professionals
will help in initiatives to blend AI and cybersecurity skills. Researchers, including Gupta et al.
(2020) and Johnson et al. (2021), elaborate on the value of such a blend of skills. In addition,
public sector and commercial entities that support U.S. cybersecurity professionals with technical
standards, professional development programs, software tools, and certifications will potentially
use the study's findings to better target AI skills for cybersecurity professionals.
Research Questions
The research questions that are the basis of this study are: (a) What factors influence
adding AI skills to the U.S. cybersecurity workforce? and (b) What are the recommendations
once these factors are identified?


Chapter 2: Literature Review
Objectives
As a part of this dissertation, research studies were searched, selected, and reviewed with
multiple objectives: (a) Obtain foundational AI knowledge: taxonomy, machine learning, deep
learning algorithms, generative AI models, penetration into industries, prospects, the U.S.
national AI initiatives, global competition, governance, laws, regulations, trustworthiness,
explainability, risks, and risk management framework; (b) Obtain basic knowledge of U.S.
cybersecurity's past, current, and future states; (c) Understand the potential of AI for
strengthening cybersecurity; (d) Assess the importance and shortage of AI skills for cybersecurity
professionals and the adoption challenges AI faces; and (e) Analyze research methodologies to
select an appropriate one for this dissertation's research problem.
Themes for Searching and Selection
The themes in selecting the AI-related research papers were skills, growth, trends,
predictions for the future, strategies, impediments, enablers, and impact on industries,
cybersecurity, and society. The research studies were searched using phrases that included (a) AI
for cybersecurity, (b) AI skills, (c) AI algorithms, (d) AI techniques, (e) AI technologies, (f)
machine learning, (g) big-data-driven AI, (h) AI for industry sectors such as medicine,
transportation, economics, finance, and manufacturing; (i) patents related to AI; (j) job
advertisements related to AI; (k) AI’s future; (l) AI’s adoption challenges; (m) AI regulations;
(n) AI’s global impact; (o) global competition for AI leadership; and (p) AI initiatives of the
United States government.
Sources for Current Studies
The key portals used to search for research papers included (a) The Journal of Artificial
Intelligence Research (JAIR), published by AI Access Foundation, a non-profit organization
whose purpose is to facilitate the dissemination of scientific results in artificial intelligence;
https://www.jair.org/index.php/jair, (b) Special Interest Group on AI of the Association for
Computing Machines; https://sigai.acm.org/, (c) IEEE Transactions on artificial intelligence;
https://cis.ieee.org/publications/ieee - transactions - on - artificial - intelligence , (d) MDPI is a pioneer
in scholarly open-access publishing and has supported academic communities since 1996;
mdpi.com, (e) Scholar.google.com, (f) JSTOR, a not-for-profit organization helping the academic
community use digital technologies to preserve the scholarly record and to advance research and
teaching in sustainable ways; jstor.org, and (g) Youtube videos.
Growing Reach of AI
AI for Economics and Finance
A growing number of applications in the economic and financial sectors are harnessing
data-driven AI techniques such as machine learning and deep learning. Relatively newly
established technology-enabled financial service providers referred to as "Fin-Tech," which have
often emerged outside the traditional financial services industry, provide innovative AI
applications. Established financial companies called "incumbents," primarily offering traditional
products and services, are also warming up to AI techniques. Research findings predict an
AIdriven "smart" economy, finance, and society.
For beginners, Prof. Arman Eshraghi from Cardiff University, UK, discusses the rapid
growth of technology-driven financial companies (Eshraghi, 2019). He presents interesting
statistics about the phenomenon of technology-driven growth, though not limited to AI
techniques, in the financial sector. The first is global investment in technology-enabled financial
services companies, which grew to 40 billion dollars in 2018. The second one is that there were
40 technology-enabled financial services companies in 2019 with a valuation exceeding one
billion dollars.

He concludes that the promise of rapid wealth accumulation through technology-enabled
financial services should be cautiously approached.
Another example with in-depth research and details is from Ryll et al. (2020). They
present their research findings as a 128-page report on AI for financial services based on a survey
of 151 respondents from 33 countries. This research represents one of the most extensive global
surveys about AI for financial services. The United States, China, and the UK are the major
markets covered by this survey. The survey also includes, in nearly equal numbers, the emerging
technology-enabled service providers and the traditional financial service institutions. The
respondents were classified according to their offerings within financial services: Deposits and
Lending, Investment Management, Payments, Market Infrastructure and Professional
Services, Capital Markets, and Insurance.
Ryll et al. (2020) highlight the "amazing opportunity ahead of us in Financial Services for
using artificial intelligence and machine learning to benefit our customers and our organizations”
(p. 8). There are numerous findings from this study, indicating AI's future demands, and these are
(a) According to 77% of the survey respondents, AI will become a factor of high to very high
importance within two years; (b) Only 16% of the respondents use AI for supporting essential
functions, and about 64% anticipate harnessing AI for critical business functions in the coming
years; (c) Risk management followed by AI-enabled products for revenue generation are the
essential functions presently benefitting; (d) AI is expected to become a key driver for
investment returns, credit analytics, customer service, and risk management; (e)
Technologyenabled service providers use AI techniques for new products and services, including
autonomous decision-making applications, while traditional financial service providers use it to
improve existing ones; (f) Technology-enabled service providers offer their AI-enabled products
as services; (g) The leaders using AI within the financial industry incorporate dedicated AI

resources primarily for data analytics within their current information technology departments;
(h) As the key to their successful AI applications, about 60% of the respondents use alternate data
from non-traditional sources such as social media, geo-locations, and payment providers; (i) The
Technology-enabled service providers anticipate an increase of over 37,000 jobs due to their use
of AI technologies, while the traditional financial service providers expect a net reduction of
337,000 jobs; (j) All respondents consider access to high-quality data and the availability of
AIqualified professionals as the primary challenges for implementing AI; (k) About 40% of the
respondents mention regulations as impediments to implementing AI applications, while 30%
refer to the same as an enabler; (l) Respondents anticipate broader use of AI to increase
marketwide risks and biases; about 20% feel they are not ready to manage those risks; (m)
Though most respondents plan to use deep learning-driven AI capabilities such as computer
vision and natural language processing within two years, well-established and proven machine
learning algorithms are mainly used instead of complex ones; (n) About 50% of the respondents
describe the entry into financial services by leading social media and search engine companies
(Big Techs) with powerful AI capabilities as their major competitive threat; (o) Organizational
return of investment in AI indicates more than linear payoffs; hence, it has reached 10% of the
research and development expenditure.
Ryll et al. (2020, p. 115) summarize the potential impediments to the rapid
implementation of AI in the financial industry as data, talent, trust, and regulations. They
conclude by emphasizing the uncertainty of the competitive environment in financial services
due to the impact of AI implementations (p. 116).
However, in another example with in-depth details, Cao (2020) composed keywords
using commonly known AI terms such as machine learning, data science, neural networks, and
data analytics and analyzed the monthly search trend in Google for them. In his review of AI in

finance, he mentions that the interest in AI for economics and finance in recent years has grown
about four to five times compared to before 2015 (p. 2). According to him, AI techniques have
strengthened the efficiency, cost-effectiveness, customer experience, risk mitigation, regulation,
and security of existing economic-financial systems and services (p. 2).
Moreover, at a high-level AI can address economic and financial objectives such as (a)
economic-financial simulations, (b) economic-financial modeling, (c) economic-financial
representations, (d) economic-financial computing, (e) economic-financial analysis and
forecasting, (f) economic-financial learning and prediction, (g) economic-financial anomaly
detection, (h) economic-financial event analysis, (i) economic-financial behavior insight, (j)
economic-financial planning, (k) economic-financial optimization, (l) economic-financial
recommendation and intervention, (m) economic-financial intelligent systems, (n)
economicfinancial intelligent services, (o) economic-financial visualization, (p) economic-
financial security assurance, (q) economic-financial compliance and risk management, (r)
economicfinancial ethics assurance, and (s) economic-financial innovations (p. 3). In addition, he
provides
30 examples of low-level AI application types to address narrow business problems in economics
and finance (p. 4). Finally, he concludes that the new generation of AI techniques, particularly
data science, machine learning, and deep learning, creates intelligence-driven economics and
finance (p. 29).
Another researcher presents a study titled "AI-Empowered Financial Businesses and
Challenges" (Cao, 2021). In this, he describes the aspects of the financial industry that could
benefit from AI, including (a) Stock and services, (b) Derivative and services, (c) Commodities
and services, (d) Index and services, (e) Currency, cryptocurrency, and services, (f) Banking and
services, (g) Insurance and services, (h) Wealth and services, (i) Surveillance and compliance. He

predicts a new era of AI-driven paradigm shift from conventional economy and finance to a new
era that uses deep data analysis and data-driven evidence discovery and combines datadriven
discovery and machine learning theories with economic and finance theories.
Another researcher, Mhlanga (2020), discusses the value of AI in enabling people at the
lower levels of the financial pyramid to become more financially savvy and active. According to
Mhlanga (2020), technology-driven financial services companies are developing AI applications
that enable low-income earners, people with low incomes, women, youths, and small businesses
to participate in and benefit from the mainstream financial market. Regarding the pace of AI
adoption in the financial services industry, Lynn et al. (2019, p. 181) mention conservatism and
regulatory requirements as significant challenges for innovation. Zetzsche et al. (2020, p. 4)
mention that AI in finance is progressing while calling for human responsibility in using AI in
this sector.
AI for Medicine
The future demand for AI applications in medicine is quite promising based on the recent
trends described in research papers. For example, Bica et al. (2020, p. 87) refer to data
availability in an electronic health record that could be used for machine learning applications.
They mention that such data has been harnessed successfully in machine-learning applications
for modeling disease progression, predicting disease deterioration and risk factors, and predicting
treatment responses (p. 88). They further point out that machine-learning techniques have yet to
harness the full potential of observational data for clinical decision support (p. 97). Through their
research, Choy et al. (2018) present that machine learning holds promise for diagnostic imaging
now and in the future. According to them, machine learning applied to medical imaging could
automate the detection and interpretation of diagnostics findings (p. 321). They further add that
as more imaging data are becoming available, with the help of machine learning, considerable

progress has been made in postprocessing tasks such as image registration, segmentation, and
quantification (p. 322). They quote from a study that the convolutional neural network technique
for medical image classification provides accuracy higher than 96% in organ mapping and organ-
specific radiation dose estimation (p. 323). They conclude that machine learning can personalize
health care further and enhance the precision of medicine (p. 326).
Handelman et al. (2018) describe machine learning as the future of biomedical research,
personalized medicine, and computer-aided diagnosis. They refer to radiology within medical
disciplines as the one ripe for machine learning (p. 608). According to them, the pattern
recognition capabilities of machine learning are ideally suited to automate and enhance radiology
tasks (p. 608). They emphasize that machine learning is the next wave in advancing modern
health care and even recommend that physicians become more familiar with the basic concepts
and metrics of machine learning (p. 617).
In addition, researchers focus on machine learning algorithms, an essential AI technique
that is increasingly used to diagnose and treat diseases. For example, Luz et al. (2020) researched
the application of machine-learning techniques for treating bacterial and fungal infections by
analyzing hospital patient records from 2014 to 2019. Based on 42 studies, they found the use of
35 different machine learning algorithms (p. 1291). They attribute large volumes of electronic
health records to enhance machine learning for infection management, though the health records
need to be completed and structured (p. 1292). In addition, they provide deeper analysis and
point out that the supervised learning category of machine learning instead of unsupervised
learning is mainly in use (p. 1295). However, some challenges persist in the use of AI for
infection management. For example, Luz et al. (p. 1296) mention further research on perceptions,
interpretations, and trust in machine learning for infection management with potential users such

as physicians, patients, and healthcare workers. Furthermore, they emphasize the need for
explainable machine learning algorithms that would enhance the
‘algorithm literacy’ of clinicians (p. 1296).
The Coronavirus pandemic of 2020 (COVID-19) poses unprecedented healthcare and
economic challenges. Some researchers refer to this phenomenon to explain their findings on AI
for medicine. For example, Korsunska and Fajgenbaum (2021) present their research on using AI
techniques to repurpose drugs as newer diseases emerge during the COVID-19 pandemic (p.
464). According to them, cutting-edge machine-learning techniques could be applied to data
pools to predict potential treatment approaches (p. 464). Furthermore, they forecast that the
machine learning techniques for therapeutics will advance beyond the pandemic since the need to
collect, share, and access treatment data has taken deeper roots (p. 465). They conclude by
elaborating on the importance of collecting data in the future across the various disease steps for
the effective use of data-driven AI techniques (p. 465).
Presently, drug discovery is another area of medicine where AI techniques play a critical
role. Researchers present findings on harnessing machine learning algorithms for the various
stages of drug discovery. They predict significant growth in such a utilization. For example,
Vatansever et al. (2020) explain the suitability of machine learning algorithms for drug
discovery, primarily focusing on the drugs for central nervous system disorders. According to
them, technological advances such as high‐throughput screening (HTS) and chemical synthesis
have dramatically increased available data on drug and disease-related chemical activity (p. 2).
They elaborate on machine learning techniques for the steps involved in drug discovery using
such complex data (p. 7). The adoption of AI techniques for drug discovery is still in the early
stages, as per their findings, and they envision a more prominent role for AI in future drug
discovery, enabling personalized medicine (p. 28).

AI for Transportation
Researchers describe AI applications to address an impressive array of transportation
problems and enable the future smart cities for which energy-efficient transportation will be a
critical requirement. AI will potentially impact transportation problems with several drivers:
ridesharing to limit pollution and reduce resource consumption, large-scale delivery of packages
using drones over transit networks, root cause analysis of fatalities in road accidents to enhance
traffic safety, manage better emergencies or incidents in the transportation network, make
transportation more accessible to older adults and those with disabilities, influence individual
behavior and reduce the transportation energy expenditure of a city, detection of hard-to-find
bottom-up cracks on roads to expedite repairs, and predict traffic jams based on the analysis of
transportation system data.
This researcher will elaborate on two survey findings on AI for transportation. The U.S.
Department of Transportation Intelligent Transportation Systems Joint Program Office sponsors
the first survey by Vasudevan et al. (2020). They provide a comprehensive list of potential and
operational AI applications for supporting various aspects of transportation (pp. 1-92). In
addition, they describe the AI applications for transportation under 11 broad categories (pp. 510):
(a) Advanced Driver Assistance Systems and Automated Driving Systems- This includes AI
applications to enable vehicle automation, including advanced driver assistance systems (ADAS)
and Automated Driving Systems (ADS); (b) Cybersecurity- This includes applications that use
AI to provide the security of cyber technologies used in transportation for communications and
control, positioning, tracking, navigation, and operations and management; (c) Accessible
Transportation- This includes applications that use AI specifically for accessible transportation,
supporting independent travel for all travelers, including people with disabilities and older adults;
(d) Traveler Decision Support tools- This includes applications that make use of AI for the

provision of static, dynamic, and other information about the transportation network, such as
route and mode travel times, transit status, mobility services, flight arrivals, weather conditions,
pricing information, and incentive-based data; (e) Transportation Systems Management and
Operations (TSMO)- This includes applications that make use of AI to optimize the performance
of a multimodal infrastructure through the implementation of real-time and dynamic systems,
services, and management strategies to preserve capacity, advance efficiency, and productivity,
and improve the security, safety, and reliability of our transportation system; (f) Commercial
Vehicle and Freight Operations- This includes AI applications to manage the efficiency, safety,
and operation of commercial vehicle fleets and freight movement; (g) Transit Operations and
Management- This includes applications that use AI to address the management, operations,
maintenance, and security of public transportation and mobility services to enable them to
provide services that meet the demands of users and operate an efficient and integrated mobility
system; (h) Emergency Management- This includes applications that use AI to address the
management of emergencies or incidents in the transportation network by public safety agencies,
including those relating to hazardous materials through the transportation network; (i) Air Traffic
Management- This includes AI applications for safe and efficient air traffic management and
operations that can be adapted for intelligent transportation systems (ITS); (j) Remote sensing
includes AI applications for intelligent remote sensing, such as drones and crewless aerial
vehicles (UAV) for traffic monitoring, pavement monitoring, bridge inspections, and aerial
mapping; and (k) Asset Management and Roadway Construction and Maintenance- This category
includes AI applications to address the strategic and systematic operation, maintaining and
improving physical assets, focusing on engineering and economic analysis.

They further describe AI-enabled applications under the above categories, with their
objective, the supported transportation functions, and the AI techniques used. They further refer
to each application’s maturity level by selecting from (a) concept stage, (b) research and
development, (c) prototype, and (d) production (pp. 14-91). Finally, they summarize the potential
of AI and conclude by enumerating risks and barriers to using AI common across all the 11
application categories they identified (pp. 90-91).
Another survey about AI for transportation is from Yuan et al. (2019). They focus
on the machine learning components of AI technology and their use for the next generation of
intelligent transportation systems (pp. 9-22). According to Yuan et al. (2019), plenty of data is
available from multilayer intelligent transportation systems. Hence, data-driven machine learning
algorithms are suitable for finding valuable knowledge (p. 9). They breakdown machine learning
further into multiple algorithms for use in transportation as CNN- Convolutional neural
networks, RNN- Recurrent neural networks, FNN- Fully-connected neural networks, DBN- Deep
belief network, RF- Random forest, SVM- support vector machines, LSTM- Long shortterm
memory method, BRT- Boosted regression trees, KNN- K-nearest neighbors method, Kmeans- A
popular unsupervised machine learning classification method, AdaBoost- Adaptive boosting, and
ELM- Extreme learning machine.
In addition, Yuan et al. (2019) discuss the suitability of identified algorithms for specific
transportation functions and match the algorithms against perception, prediction, and functional
management groups in an intelligent transportation system (pp. 11-22).
It is important to mention a few additional research papers on AI for transportation since they
reinforce AI’s potential impact on nearly all future intelligent transportation systems segments.

For example, Zahid et al. (2020) compare machine learning algorithms for driver risk
assessment through a case study of traffic violations in a city of over 1 million people with an
area of 12,246 square kilometers (p. 3). They apply the AI learning algorithms (a) K nearest
neighbors, (b) support vector machines, and (c) CN2 rule inducer on a year’s worth of traffic
violation data (pp. 5-6). They found that the K nearest neighbors learning algorithm predicted
traffic violations with an accuracy of 99% (p. 12). They conclude that their findings could help
improve road safety (p. 12).
Praticò et al. (2020) apply machine learning algorithms to their experiment to identify hardto-
detect bottom-up cracks and maintain roads better. They collected data from acoustic responses
indicative of bottom-up cracks as cars passed on the road and applied machine learning
algorithms to that data (pp. 3–5). According to them, the support vector machine learning
algorithm could predict bottom-up road cracks with an accuracy of 99.1% (p. 13).
Peng et al. (2020) describe big data and machine-learning methods to address low-carbon
emissions in intelligent transportation systems. They analyze and present AI algorithms for
dynamic, intelligent navigation of vehicles on the road to reduce fuel consumption and vehicle
exhaust emissions (p. 2). They combine the AI genetic algorithm techniques and particle swarm
optimization to implement a support vector regression model (p. 6). Unlike traditional navigation
systems, based mostly on static urban road networks with little real-time analysis of changes in
traffic networks to reduce the traveling time or distance, their method harnesses big data-based
AI technologies. It focuses on reducing carbon emissions (p. 16).
To understand fatalities resulting from road accidents and create an AI-based prediction
model, Ghandour et al. (2020) used a database containing 8482 road accidents spanning four
years (p. 2). They tried out five learning algorithms and determined that Sequential minimal
optimization and random forest AI learning algorithms produced the best results for their model

(p. 6). Furthermore, their predictive AI model identifies key fatal injury-contributing factors that
help in preventive countermeasures (p. 9).
To predict traffic speed in urban areas, Bratsas et al. (2020) use probe data from the road
network and compare the prediction accuracy of the AI algorithms (a) Random forests; (b)
Support vector regression; (c) Multilayer perceptron neural networks; and (d) Multiple linear
regressions (p. 2). Their experiment shows that neural network-based models are more accurate
during more considerable traffic flow changes, while the support vector regression models
perform better during more minor changes.
AI for Manufacturing
The world has seen many industrial revolutions resulting in significant improvements in
the manufacturing sector of the global economy. Ladani (2021, p. 3) refers to the first three
industrial revolutions characterized by mechanization, steam power, mass production, assembly
line, automation, and electronics. The fourth one, referred to as Industry 4.0, originated in 2011
from a project in the high-tech strategy of the German government; it advances the concept of
cyber-physical systems into cyber-physical production systems, and smart factory is one of its
key initiatives (Xu et al., 2021, p. 530). Therefore, AI technologies are a crucial driver behind
Industry 4.0 and the ongoing improvements in the manufacturing sector (Ladani, 2021, p. 3).
Multiple research papers describe the growth of and potential AI in manufacturing from
different perspectives. For example, Arinez et al. (2020, p. 110804-5) predict that with the
advancement of the industrial Internet of Things (IoT), AI, and specifically machine learning, we
benefit the entire manufacturing system, resulting in reduced cycle time and scrap, improved
quality and improved resource utilization. According to them, machines, ambient sensors,
controllers, and labor records produce vast amounts of continuously generated data. AI can
transform large amounts of complex manufacturing data into actionable and insightful

information (p. 110804-2). They also refer to the growing number of scientific publications on AI
in manufacturing, from 750 in 2015 to 2200 in 2020.
Furthermore, their research details match the manufacturing process requirements against
the capabilities of AI techniques, such as machine learning, deep learning, random forest, and
support vector machines. Finally, they list the benefits of AI for manufacturing aspects such as
system optimization, applications of human-robot collaboration, process monitoring, diagnostics,
prognostics, and process control. They summarize by listing the topics for further research on AI
for manufacturing, which includes data quality and trust in AI (p. 110804-12).
Another example of research that explains the value of AI for manufacturing is from
Beldiceanu et al. (2021). They examine the benefits of the manufacturing process from a
combination of AI and digital twins that create virtual copies of processes and physical assets.
Accurate real-time data from digital twins for the development of AI in the manufacturing
industry is the basis for their research. Their project, 'ASSISTANT,' aims to create intelligent
digital twins by combining machine learning (ML), optimization, simulation, and domain
models. Integrating human and machine intelligence for sustainable learning targets a significant
increase in flexibility and reactivity, product and process quality, and the robustness of
manufacturing systems (p. 641). A blend of data-driven modeling, the Internet of Things (IoT),
and machine learning technologies will create the next revolution in the manufacturing industry
(p. 642).
Beldiceanu et al. (2021) also describe four AI-based intelligent data-driven digital twins
that would improve the various components of a manufacturing process (p. 643): (a) The process
planning twin will make the factory re-configurable for future demands; (b) The production
planning twin will make the factory agile in managing uncertainties such as demand variations,
production defects, and process durations; (c) The scheduling twin will assign the operations to

the optimal resources at the right moment; and (d) The real-time control twin will execute the
production plans and provide feedback to other twins based on deviations from the plans.
Another researcher surveys the various AI technologies in a factory environment (Fahle et al.,
2020). In their analysis (pp. 413-414), they list the AI technologies as machine learning, deep
learning, neural networks, convolutional neural networks, support vector machine, K-nearest
neighbor, random forest, multilayer perceptron, and gradient-boosted trees.
They describe the current use of AI technologies for manufacturing process components such
as (a) process planning, (b) quality control, (c) predictive maintenance, (d) robotics, (e) process
control and optimization, and (f) logistics (p. 414). They conclude that during the past five years,
neural networks and decision tree algorithms have been widely used in manufacturing and
factory applications; supervised methods are the most used machine learning algorithms, with
reinforced learning gaining momentum in the last three years.
With the ever-increasing global population, the food industry will remain an essential
segment of the global manufacturing sector, and AI contributes to this segment. Kakani et al.
(2020) discuss the value of AI for manufacturing by focusing on the food industry. They report
that AI techniques and computer vision significantly influence the food industry's methods, tools,
and machinery (p. 6). According to them, crop farming, cultivation, production, and processing
have improved significantly by introducing AI-driven methods and machines into the agriculture
and food industry (p. 6). They refer to an agriculture start-up applying machine learning
algorithms on the data collected from farms, irrigation, soil characteristics, meteorological data
recommendations, and machine learning methods to double the overall yield (p. 9).
AI for The Military and National Defense
As AI impacts the global economic sectors such as medicine, finance, and transportation,
its importance to the military is firmly established. An act formally established the National

Artificial Intelligence Initiative in the United States on January 1, 2021 (NAIIA, 2021). Though
not exclusively for military purposes, it refers to the Department of Defense (DOD) as one of the
critical agencies that contribute to the research and development of AI. In addition, the U.S.
Congress created a National Security Commission on Artificial Intelligence in 2019, entrusted to
make recommendations to the U.S. Congress and the president to develop AI technologies
exclusively for national security and defense. This commission comprised 15 experts, including
technologists, business executives, academic leaders, and national security professionals.
After research and analysis, they submitted a 756-page final report in March 2021
(Schmidt et al., 2021). They describe their report as “an integrated national strategy to reorganize
the government, reorient the nation, and rally our closest allies and partners to defend and
compete in the coming era of AI-accelerated competition and conflict.” (p. 8). They also refer to
two critical convictions in their executive summary: (a) The rapidly emerging AI technologies
are world-altering and will be the source of enormous power for the countries that harness them,
(b) AI is diminishing the technological leadership of the United States and increasing the
vulnerability of our economic and military capabilities.
Furthermore, Schmidt et al. (2021) divide their AI strategy into two parts (p. 20). The first
part describes the AI-related threats from state and non-state actors and recommends actions for
the U.S. government to protect the people and national interests. The second part describes AI's
broader economic impacts and recommends actions for the U.S. to nurture AI innovations for
competitive advantages. Next, they explain their AI strategy through a series of (a) topics of
interest, (b) followed by explanation and forecast, and (c) strategy recommendations specific to
the topic.
Another study by Schirmer and Léveillé (2021), in a project sponsored by the RAND

Corporation, describes their implementation of AI tools for measuring U.S. military readiness.
According to them, the AI algorithms, including deep neural networks, work well for evaluating
the metrics relating to the readiness of various elements of the U.S. military (pp. 1-7).
Furthermore, they report that their AI-based model interpreted natural language descriptions and
measured the readiness of the U.S. military's personnel, equipment, and training factors (p. 29).
They conclude that their model uses AI to process unstructured information to predict the
readiness of the U.S. military units.
AI for Other Sectors
AI for Education. Technical advancements such as computers and communication have
impacted education, and AI is a recent addition to such technologies. Zhai et al. (2021) present
their findings on AI's impact on education based on a systematic literature survey of 100 papers
from 2010 to 2020 (p. 1). According to them, AI contributes to education as a development tool
to create an intelligent learning environment that includes deep learning techniques for learners
and teachers (pp. 7-10); as a knowledge extraction tool to provide learners feedback, reasoning,
and adaptive learning; and as an integration tool to combine multiple educational techniques
resulting in capabilities such as role-playing, immersive learning, and gamification.
Finally, based on their analysis of research papers, they report the positive effects of AI
techniques on education (p. 13). However, they also refer to the challenges AI faces in the field
of education that include (a) a lack of metrics to justify the extra cost, (b) an inability to support
domain-specific education, and (c) the potential for over-reliance on AI on the part of teachers
and students (p. 13).
AI for Law Enforcement. Researchers have published that AI-based techniques are
increasingly used for law enforcement and crime prevention. For example, Vasyukov (2021)
elaborates on the Republic of Singapore’s use of AI for crime control. According to him, in

collaboration with financial institutions and technology providers that are both foreign and
domestic, the Singapore government uses AI for crime-fighting as part of its larger goal of a
digital economy for dynamic social-economic progress (p. 1). He lists many uses of AI
techniques for law enforcement and crime prevention in Singapore: AI-based drones that monitor
the streets for criminal activity, AI-based biometric screening and facial recognition systems at
the nation’s border, AI-based detection of fraud, illegal assets, and money laundering, AI-based
credit scoring and risk identification to protect against cybercrime and fraudulent transactions,
and AI-based malware detection to protect computer systems from cybercriminals. Vasyukov
(2021) concludes that the Republic of Singapore's many uses of AI prove its potential for law
enforcement and crime prevention.
AI for Politics. Data-driven AI technologies are also making inroads into the data-rich
democratic political process. However, similar to AI's impact on other fields, its growing use in
the political process is highlighted by researchers with words of caution. For example, Schippers
(2020, p. 33), while praising AI-based communication platforms for facilitating the core
democratic principles of debate, connections between people, and information exchange, also
cautions that AI could damage democratic politics. He mentions five AI-driven activities that
have taken place in the recent elections that could damage our democratic political process (pp.
33-34): (a) Fake images, voices, or the contents of public discourse contradicting facts, (b)
Machine-generated decisions undermine human accountability and responsibility, (c) The
blackbox nature of AI decisions humans accept without explanations impacts marginalized
individuals and communities, (d) AI-driven state surveillance encourages abuse of power, and (e)
AI-driven collaboration between public and private sectors in sensitive activities such as law
enforcement and security creates conflicts of interest. He concludes that AI needs constant

scrutiny due to its rapid pace of development and calls for democratic governance of AI to
prevent potential damage to the democratic political process (p. 35).
AI for Pollution Control. Bhardwaj and Pruthi (2020) propose an AI-based model to
predict air pollutants. They target pollutants of size 2.5 microns or less since they cause the most
damage to pulmonary and nervous systems. Representing pollution as time-series data for 2015
to 2018 to train their model, they present a machine learning adaptive neuro-fuzzy inference
system (ANFIS), a combination of artificial neural network and fuzzy inference system (pp.
1874-1877). They compare different machine learning algorithms and select a hybrid of
algorithms that predicts pollution with the highest accuracy (p. 1879).
AI for Climate and Weather Modeling. According to Chantry et al. (2021), current
weather predictions are built on models that use numerical computation of dynamic equations of
meteorology. However, researchers are exploring data-driven AI techniques for models that
compete with the current ones with the emergence of deep neural networks. Their paper
summarizes a workshop conducted in 2019 to discuss the application of machine learning
techniques to enhance weather and climate prediction. To explain the AI-related findings from
that workshop, Chantry et al. (2021, p. 2) categorize weather and climate predictions: predictions
with a forecast lead time of a few hours are called now-casting, predictions with a forecast lead
time of a day or two are short-range, predictions with a forecast lead time of a few days to a few
weeks are referred to as medium-range, predictions with a forecast lead-time of two weeks to a
season is called sub-seasonal, and predictions in the timescales of decades and longer are called
climate change.
They further categorize the use of AI techniques for climate and weather predictions as
follows (p. 2): Hard AI is where AI-based machine learning techniques can replace current
equation-based models; Medium AI, where AI-based machine learning techniques can enhance

current equation-based models; and Soft AI, where AI-based machine learning techniques can
improve the computational efficiency of the current equation-based models.
Key findings of AI for climate and weather predictions, based on an analysis of the
researcher discussions of the workshop they studied, are presented by Chantry et al. (2021, pp.
34), and these are (a) Now-casting AI prediction models could replace conventional models, so
hard-AI is feasible. I.e., AI models could replace the current models, (b) For short-term and
medium-term forecasting, AI prediction models lack sufficient training data; hence, only medium
and soft AI is feasible. I.e., AI models can only enhance current model predictions and improve
their computational efficiency, (c) AI prediction models could replace conventional models for
sub-seasonal forecasting, making hard AI feasible. I.e., AI models could replace the current
models, and (d) For climate-change predictions, the AI models face the challenge of limited data;
hence, hard AI is not feasible. For example, further research on AI models' climate change
predictions is required.
AI for Travel and Tourism. An editorial for a special issue on AI and machine learning
mentions that the travel industry needs to adopt AI technologies faster (Vinod, 2021). However,
he also mentions that the opportunity for AI over other analytics used in travel is very high and
refers to cases of AI techniques for specialized areas of the travel industry, which include (a)
machine learning algorithms for modeling market size and share for airlines; (b) Bayesian
machine learning algorithms for forecasting travel demands; and (c) deep-learning algorithms to
model price elasticity (p. 211). Specifically, Fararni et al. (2021) suggest a system that would
recommend tourists based on big-data-driven AI techniques for trip and travel service selection
from the many available destinations, attractions, and activities. They describe their hybrid
system as an AI-driven combination of many prevalent travel recommendation techniques (p.

49). Furthermore, they explain their AI recommender application with these three sub-systems:
(a) A user profiler uses machine learning algorithms to learn user preferences instead of merely
capturing user input, (b) A machine learning model to predict users' interest in an item and use
that for filtering recommendations, and (c) A trip planner that uses operational research
techniques to formulate the itinerary. They conclude by emphasizing that their AI application
would be implemented using big-data-based machine learning algorithms and the Internet of
Things (p. 53).
AI for Strategic Management
To achieve long-term goals, leaders of commercial organizations, with an eye on their
future, make knowledge-based strategic decisions with uncertainties in their external operating
environment. Researchers have identified the role of AI in supporting and improving the strategic
management process. For example, Keding (2020) presented their findings on AI for strategic
management based on their analysis of research over four decades. A knowledge base is a critical
success factor for strategic management decisions, and artificial intelligence techniques have
outperformed senior managers in various decision-making situations (p. 92). However, according
to Keding (2020), the AI technology component and its approach to supporting strategic
management decisions have changed over the decades. For example, Carlsson and Walden (1997;
as cited in Keding, 2020, p. 94) mention the top-down approach of AI's rulebased expert systems
supporting strategic management decisions from 1979 to 2005. On the contrary, Davenport and
Ronanki (2018; as cited in Keding, 2020, p.94) refer to the bottom-up approach of AI’s data-
driven machine learning algorithms supporting management decisions during 2015-2019.
Furthermore, Keding (2020) lists the prerequisites for AI to support management decisions (pp.
100-103): (a) Availability of sufficient high-quality data, data-driven workflows, and streamlined
processes to extract knowledge from data within the organization; (b) Organizational structure,

management willingness, trust, and acceptance of AI techniques for creating and enhancing
products and processes; and (c) Proven organizational capabilities in solving narrow business
problems through AI before harnessing it for more significant strategic decisions.
He also lists the consequences of AI’s supporting management decisions (pp. 103-106):
(a) AI algorithms help organizations address data overload and increase decision-relevant data
when based on data without bias; (b) AI algorithms replace managerial tasks that are objective
and codifiable and enable managers to focus on tasks requiring implicit knowledge, creativity,
flexibility, and judgment; and (c) AI enhances human-machine collaboration, augments strategic
decision-making, and helps redirect resources toward executing strategies.
Keding (2020, pp. 108-109) concludes by stating that the organizational rewards of using
AI for strategic management depend on (a) reducing the impacts of biased data, hidden
imprecisions, and ethical issues and (b) realigning structure and culture, and processes to adapt to
AI-augmented intelligent management.
Studies on AI’s Significance for Cybersecurity
Current studies present the value and potential of AI techniques to strengthen
cybersecurity and emphasize the need to deploy AI-based applications to augment cybersecurity
as a necessity for emerging threats against critical computing infrastructures. For example,
Zeadally et al. (2020) elaborate on harnessing AI techniques for improving cybersecurity in their
study. First, they describe the current cybersecurity practice that uses legacy tools, the types of
attacks, their sources, the goals, the resulting exposure of data, the computer system components
impacted, the adverse outcomes, and the techniques for detection; they follow that by mapping
the AI techniques such as machine learning, decision trees, k-nearest neighbors, support vector
machines, self-organizing maps, natural language processing, deep neural networks, and
generative adversarial network, in improving specific aspects of cybersecurity practice.

Zeadally et al. (2020) further extend their findings and recommend AI techniques and
AIbased agents to protect against threats to the Internet connection, application layer, Internet of
things, network layer, privacy, cyber-physical systems, and critical infrastructure. Furthermore,
they conclude that as the speed and sophistication of malicious attacks increase, AI has become
indispensable for improving cybersecurity.
Another study by Zhang et al. (2020) mentions the significant value of AI skills for
improving cybersecurity and points out the lack of AI skills among cybersecurity professionals.
They propose using cybersecurity competitions to identify the AI skills of cybersecurity
professionals.
Chen et al. (2020) mention in their editorial on AI in cybersecurity that AI-based
adaptable solutions are expected to solve cybersecurity challenges such as intrusion detection,
privacy protection, proactive controls, anomalous behavior, and advanced threat detection. They
quote from multiple researchers on applying AI algorithms to cyber security: Lee et al. (2020)
describe machine learning for ransomware detection; D’hooge et al. (2020) study supervised
machine learning methods using 20 years of intrusion detection data; Malaiya et al. (2020)
present deep learning for network anomaly detection; Xiao et al. (2020) propose a Recurrent
Neural Network-based anomaly detection for crewless aerial vehicles; and Liu et al. (2020)
propose an AI learning-based adaptive network immune mechanism to prevent eavesdropping
attacks.
Davidson and Filkins (2019) discuss the barriers holding back the broader adoption of AI
for cybersecurity. They present the results of a survey conducted by SANS Institute, a private

U.S. company specializing in cybersecurity training. The survey was directed at members of the
U.S. cybersecurity workforce who were involved or interested in using AI for better
cybersecurity in their organizations. According to the survey results from Davidson and Filkins
(2019), (a) Of the responders, 85% view cybersecurity as an enabler of more robust
cybersecurity, (b) Legacy cybersecurity tools were expected by 67% to remain in use, and (c)
AI’s maturity for cybersecurity was trusted by 46%. When it came to AI-based techniques for
cybersecurity, (a) predictive analysis was mentioned by 76%, (b) deep learning algorithm by
74%, and (c) machine learning by 73%.
Furthermore, when it came to the specific areas of cybersecurity expected to be improved
by AI-based solutions, Davidson and Filkins (2019) mention that (a) cyber defense was referred
to by 75% of the responders, (b) malware prevention by 71%, and (c) advanced threat detection
by 69%. Another key finding of the survey was about the barriers to implementing AI-based
solutions to cybersecurity; 35% of the survey responders said lack of AI maturity was the main
barrier, and 27% said lack of AI skills in cybersecurity was the main barrier.
Study on AI and U.S. Cybersecurity Workforce
A study by the International Information System Security Certification Consortium
(International Information System Security Certification Consortium, 2021) provides details
about the U.S. cybersecurity workforce; their study mentions 1,142,462 working professionals in
the U.S. workforce as of 2021, and it is an increase of 30% from the previous year. The study
finds cybersecurity professionals in information technology, financial services, government,
manufacturing, consulting, healthcare, retail/wholesale, and telecommunications. When it comes
to skill development, the study participants expressed their priority on multiple topics: (a) Cloud
security is preferred by 40%; (b) Risk assessment by 26%; (c) Artificial Intelligence and machine
learning by 25%; (d) Governance, risk management, and compliance by 24%; and (e) Threat
intelligence by 22%. In addition, the study also mentions that 17% of the participants mentioned
AI-based automation as a solution to address the cybersecurity skill shortage. The global
cybersecurity workforce estimates presented by this study are in Table 1.
Table 1 The Cybersecurity Workforce Around the World
Country 2019 2020 2021
North America
United States 804,700 879,157 1,142,462
Canada 84,000 101,963 123,696
Latin America
Mexico 341,000 421,750 515,527
Brazil 486,000 626,650 581,349
Europe
United
Kingdom
289,000 365,823 300,087
France 121,000 118,302 146,808
Germany 133,000 175,159 464,782
Ireland N/A* 14,212 15,028
Spain N/A* 122,284 124,336
Netherland N/A* 34,406 35,106
Asia Pacific
Australia 107,000 108,950 134,690
Japan 193,000 226,269 276,556
Singapore 43,000 57,765 92,744
South Korea 201,000 232,281 239,085
Global 2,802,700 3,484,971 4,192,255
Note. From (ISC)2 Cybersecurity Workforce Study, 2021
N/A* Not available for the year
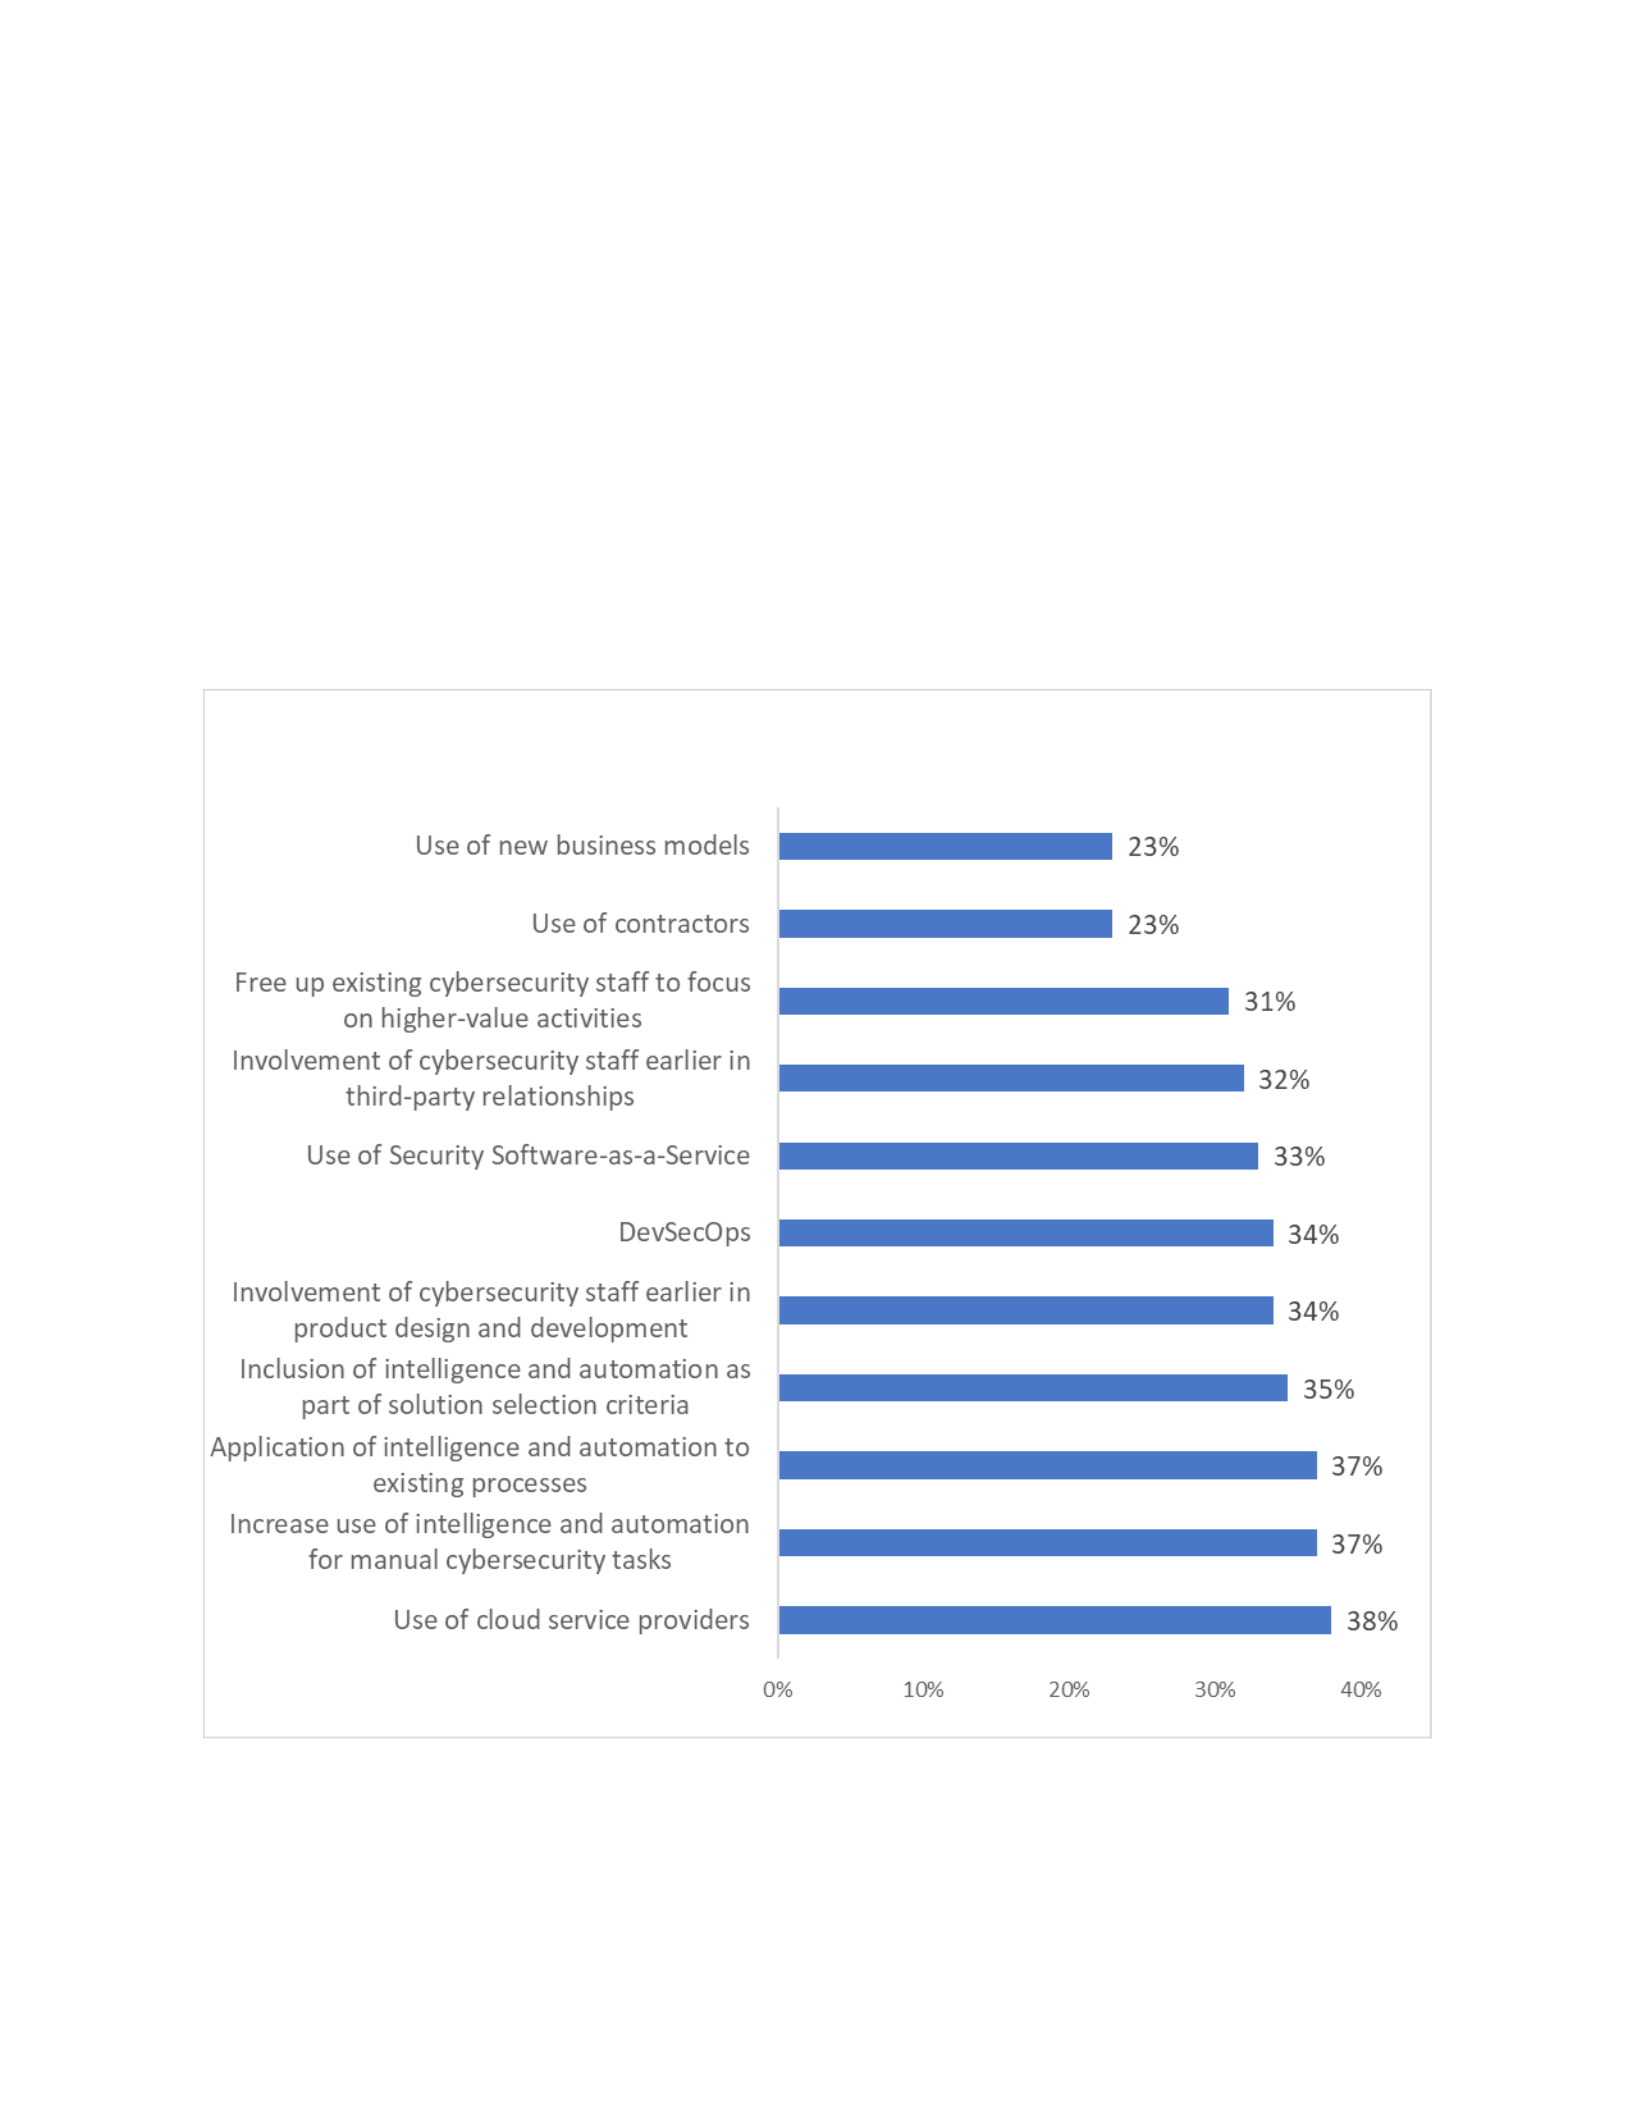
Furthermore, the study by the International Information System Security Certification
Consortium (International Information System Security Certification Consortium, 2021) presents
technologies to address cybersecurity workforce gaps, including inclusion, application, and
increased use of intelligence. Figure 1 is a schematic of their findings on addressing
cybersecurity workforce gaps.
Figure 1 Top Technology Investments to Overcome Cybersecurity Workforce Gap
Note. From (ISC)2 Cybersecurity Workforce Study (2021).

AI Initiatives of the United States Government
National AI Initiative Act
As the importance of AI for economic and social advancement and national security is
being realized, and the global competition for AI leadership keeps growing, the U.S. federal
government has launched its approach to advance AI research, utilize AI-related opportunities,
and identify and minimize AI risks. The National Artificial Intelligence Initiative Act (NAII
ACT), legislated in 2020 by the U.S. Congress, provides the authority, directives, structure,
guidance, and funding for the activities of a National Artificial Intelligence Initiative Office
(NAIIO) located with the Office of science and technology policy (OSTP) of the U.S. President
(NAII-ACT, 2020).
The NAII ACT (2020) lists the purpose of the U.S. AI initiative. Those are (a) To enable
and sustain U.S. leadership in artificial intelligence research and development; (b) To provide
global leadership in developing and using trustworthy artificial intelligence systems in the public
and private sectors; (c) To prepare the U.S. workforce to utilize artificial intelligence systems
across all sectors of the economy and society; and (d) To coordinate ongoing artificial
intelligence research, development, information sharing, and demonstration activities among the
U.S. civilian agencies, the Department of Defense, and the intelligence community.
Furthermore, the NAII ACT (2020) tasks the NAIIO to provide technical and
administrative support to the AI initiative committees, ensure interagency coordination, facilitate
the technical and programmatic information exchange on the AI initiative across U.S. federal
departments and agencies, industry, academia, nonprofit organizations, professional societies,
state and tribal governments, and others; reach out periodically to diverse stakeholders on
AIrelated issues; and enable access to technologies, innovations, best practices, and expertise
from the AI Initiative for agency missions and systems across the U.S. Federal government.

In addition, the NAII ACT (2020) directs the task force within NAIIO to consult with
multiple U.S. entities from public and private sectors: The National Science Foundation; The
Office of Science and Technology Policy; The National Academies of Sciences, Engineering, and
Medicine; The National Institute of Standards and Technology; The Director of National
Intelligence; The Department of Energy; The Department of Defense; The General Services
Administration; The Department of Justice; The Department of Homeland Security; The
Department of Health and Human Services; Private industries; Institutions of higher education;
and Civil and disability rights organizations.
The NAII ACT (2020) also assigns specific critical responsibilities to the National
Science Foundation (NSF), the National Institute of Standards and Technology (NIST), the
Department of Energy (DOE), and the National Oceanic and Atmospheric Administration
(NOAA). NSF is directed to finance the establishment and operation of national AI research
institutes. NIST is directed to (a) advance collaborative frameworks, standards, guidelines, and
associated methods and techniques for artificial intelligence, (b) support the development of
technical standards and guidelines that promote trustworthy artificial intelligence systems, (c)
support the development of technical standards and guidelines by which to test for bias in
artificial intelligence training data and applications, and (d) develop a risk management
framework for AI applications. NOAA is directed to facilitate scientific efforts related to artificial
intelligence across its organization, expand external partnerships, and build workforce
proficiency to effectively transition artificial intelligence research and applications to operations.
DOE is directed to conduct cross-cutting research and development to advance artificial
intelligence tools, systems, capabilities, and workforce needs and to improve the reliability of
artificial intelligence methods and solutions relevant to its mission.

AI Bill of Rights
The National Artificial Intelligence Initiative Act (NAII-ACT, 2020) established the
National Artificial Intelligence Initiative Office (NAIIO) within the U.S. President’s Office of
Science and Technology Policy (OSTP). The OSTP advises the U.S. President on all issues
related to science and technology, including AI. When balancing the risks of AI against its
benefits, the OSTP states that the progress of economic, social, industrial, and national security
through AI should not negatively impact the civil rights or democratic values of U.S. citizens
(The White House, 2022). As a result, OSTP implemented a policy of listening to the U.S.
people on the impacts of AI, compiled risks and likely threats from it, and drafted a blueprint for
an AI bill of rights. OSTP intends the AI Bill of Rights to be used as a guide for any society to
protect its citizens from the threats posed by AI while still harnessing AI’s benefits (The White
House, 2022).
To understand AI’s threats and risks and manage and mitigate them, OSTP invited
responses from diverse U.S. stakeholders. The stakeholders included (a) communities, (b)
industries, (c) AI technology developers, (d) experts from multiple AI-impacted disciplines, and
(e) policymakers from the U.S. federal government. OSTP, as a part of its outreach, conducted
panel discussions, public listening sessions, private meetings, formal requests for information on
the use of biometrics in AI algorithms, and responses from the public. They used many activities
for gathering information on the risks and threats of using AI: (a) A panel focused on consumer
rights and protections and explored and identified the opportunities and challenges for individual
consumers and communities in the context of rapidly growing AI applications; (b) A panel
focused on the criminal justice system. It explored the impact of AI applications on the criminal
justice system and identified how AI advances or undermines public safety, justice, and
democratic values; (c) A panel focused on equal opportunities and civil justice and explored the

impact of AI on equity of opportunity in employment, education, and housing; (d) A panel
focused on democratic values and examined the AI applications for non-discriminatory
algorithms, explainable algorithmic results, human-computer interaction designed for community
participation, and privacy awareness; (e ) A panel focused on social welfare and development and
identified the benefits of AI applications for social welfare systems, social development
programs, and other systems that can impact life chances; (f) A panel focused on the healthcare
system and explored the pros and cons of using AI for healthcare practices and related consumer
products; (g) Information was gathered from the general public on their experiences using
datadriven AI applications by soliciting it through a widely publicized email address; and
Following a formal request for information, they collected and analyzed responses from 130
organizations on the use and governance of AI algorithms based on biometrics technologies.
OSTP composed its blueprint for the AI Bill of Rights based on its analysis of the
information from U.S. stakeholders about the risks and threats resulting from AI. The blueprint
contains many critical elements: (a) Safety and Effectiveness- AI applications must be deployed
safely and effectively by monitoring their intended use, identifying unsafe outcomes, and
removing them if needed; (b) Protections from Algorithmic Discriminations- AI application
designers, developers, and operators must ensure in the use of data-driven algorithms, that people
are protected from discrimination based on their race, color, ethnicity, gender, religion, age,
disability, medical conditions, national origin, veteran status, other genetic information, or any
other classification protected by law; (c) Data Privacy- Designers, developers, and operators
must protect privacy by default while deploying data-driven AI algorithms. They must seek
permission and respect decisions regarding collecting, using, accessing, transferring, and deleting
people’s data; (d) Notice and Explanation- People should be notified when AI-driven automation
impacts them about the extent, reasons behind, and explanation of the automation contributing to

the outcomes; and (e) Human Alternatives, Consideration, and Fallback- People using AI
applications should have the means to opt out of using AI, where appropriate, and seek the
assistance of a human alternative capable of solving their problems. The appropriateness should
be determined based on reasonable expectations in a given situation and to protect the public
from harmful impacts.
AI Theme-based Research Institutes
The NAII ACT (NAII ACT, 2020) directs NSF, an independent U.S. federal agency
supporting science and engineering in all 50 states and U.S. territories, to finance and help
operate AI research institutions in the United States and to collaborate on AI-related issues with
like-minded global partners. NSF established the foundation for its AI mission in 2020 by
starting seven AI research institutions with the stated objective of extending the boundaries of
AI’s capabilities. Their first set of research institutions vary in their specialties: AI Institute for
Research on Trustworthy AI in Weather, Climate, and Coastal Oceanography; AI Institute for
Foundations of Machine Learning; AI Institute for Student-AI Teaming; AI Institute for
Molecular Discovery, Synthetic Strategy, and Manufacturing; AI Institute for Artificial
Intelligence and Fundamental Interactions; AI Institute for Next Generation Food Systems; and
AI Institute for Future Agricultural Resilience, Management, and Sustainability.
In 2021, NSF, collaborating with academic, U.S. Federal, and public sector organizations,
started 11 more institutes, focused on the themes of (a) Human-AI Interaction and Collaboration,
(b) AI for Advances in Optimization, (c) AI and Advanced Cyberinfrastructure, (d) AI in
Computer and Network Systems, (e) AI in Dynamic Systems, (f) AI-Augmented Learning, and
(g) AI-Driven Innovation in Agriculture and the Food System. These institutions cover many
objectives: (a) AI Institute for Collaborative Assistance and Responsive Interaction for
Networked Groups; (b) AI Institute for Advances in Optimization; (c) AI Institute for Learning-
Enabled Optimization at Scale; (d) AI Institute for Intelligent Cyberinfrastructure with
Computational Learning in the Environment; (e) AI Institute for Future Edge Networks and
Distributed Intelligence; (f) AI Institute for Edge Computing Leveraging Next-generation
Networks; (g) AI Institute for Dynamic Systems; (h) AI Institute for Engaged Learning; (i) AI
Institute for Adult Learning and Online Education; (j) USDA-NIFA Institute for Agricultural AI
for Transforming Workforce and Decision Support; and (k) AI Institute for Resilient Agriculture.
In 2023, NSF added seven more institutes based on six themes. The following table
describes the themes and the related institutes:
Table 2 Theme-Based AI Research Institutions
Theme Institutes
Trustworthy AI NSF Institute for Trustworthy AI in Law & Society (TRAILS)
Led by the University of Maryland, TRAILS aims to transform
the practice of AI driven primarily by technological innovation to be
driven by attention to ethics, human rights, and support for communities
whose voices have been marginalized into mainstream AI. TRAILS will
be the first institute to integrate participatory design, technology, and
governance of AI systems and technologies and will focus on
Theme Institutes
investigating what trust in AI looks like, whether current technical
solutions for AI can be trusted, and which policy models can effectively
sustain AI trustworthiness. A partnership between NSF and NIST funds
TRAILS.
Intelligent Agents for
Next-Generation
Cybersecurity
AI Institute for Agent-based Cyber Threat Intelligence and
Operation (ACTION)
Led by the University of California, Santa Barbara, this institute
will develop novel approaches that leverage AI to anticipate and take
corrective actions against cyber threats that target the security and
privacy of computer networks and their users. The team of researchers
will work with experts in security operations to develop a revolutionary
approach to cybersecurity, in which AI-enabled intelligent security
agents cooperate with humans across the cyber defense life cycle to
jointly improve the resilience of the security of computer systems over
time. A partnership between NSF, DHS S&T, and IBM funds ACTION.
Climate Smart
Agriculture and
Forestry
AI Institute for Climate-Land Interactions, Mitigation,
Adaptation, Tradeoffs and Economy (AI-CLIMATE)
Led by the University of Minnesota Twin Cities, this institute
aims to advance foundational AI by incorporating knowledge from
agriculture and forestry sciences and leveraging these unique, new AI
Theme Institutes
methods to curb climate effects while lifting rural economies. By creating
a new scientific discipline and innovation ecosystem intersecting AI and
climate-smart agriculture and forestry, our researchers and practitioners
will discover and invent compelling AI-powered knowledge and
solutions. Examples include AI-enhanced estimation methods of
greenhouse gases and specialized field-to-market decision support tools.
A key goal is to improve accounting for carbon in farms and forests to
empower carbon markets and inform decision-making. The institute will
also expand and diversify rural and urban AI workforces. USDA-NIFA
funds AI-CLIMATE.
Neural and Cognitive
Foundations of
Artificial Intelligence
AI Institute for Artificial and Natural Intelligence (ARNI)
Led by Columbia University, this institute will draw together top
researchers across the country to focus on a national priority: connecting
the significant progress made in AI systems to the revolution in our
understanding of the brain. ARNI will meet the urgent need for new
interdisciplinary research paradigms between neuroscience, cognitive
science, and AI and, as a result, will accelerate progress in all three fields
and broaden the transformative impact on society in the next decade. A
partnership between NSF and DoD OUSD R&E funds ARNI.
Theme Institutes
AI for Decision
Making
AI Institute for Societal Decision Making (AI-SDM)
This institute, led by Carnegie Mellon University, seeks to create
human-centric AI for decision-making to bolster effective responses in
uncertain, dynamic, and resource-constrained scenarios like disaster
management and public health. By bringing together an interdisciplinary
team of AI and social science researchers, AI-SDM will enable
emergency managers, public health officials, first responders, community
workers, and the public to make data-driven, robust, agile,
resourceefficient, and trustworthy decisions. The institute's vision will be
realized via the development of AI theory and methods, translational
research, training, and outreach, enabled by partnerships with diverse
universities, government organizations, corporate partners, community
colleges, public libraries, and high schools.
AI-Augmented
Learning to Expand
Education
Opportunities and
Improve Outcomes
AI Institute for Inclusive Intelligent Technologies for Education
(INVITE)
Led by the University of Illinois Urbana-Champaign, this institute
seeks to fundamentally reframe how educational technologies interact
with learners by developing AI tools and approaches to support three
Theme Institutes
crucial noncognitive skills known to underlie effective learning:
persistence, academic resilience, and collaboration. The institute's
useinspired research will focus on how children communicate STEM
content, how they learn to persist through challenging work, and how
teachers support and promote noncognitive skill development. The
resultant AI-based tools will be integrated into classrooms to empower
teachers to appropriately support learners developmentally.
AI Institute for Exceptional Education (AI4ExceptionalEd)
Led by the University at Buffalo, this institute will work toward
universal speech and language screening for children. The framework, the
AI screener, will analyze video and audio streams of children during
classroom interactions and assess the need for evidence-based
interventions tailored to students' needs. The institute will serve children
needing ability-based speech and language services, advance foundational
AI technologies, and enhance understanding of childhood speech and
language development. The AI Institute for Exceptional Education was
previously announced in January 2023—a partnership between NSF and
ED-IES funds the INVITE and AI4ExceptionalEd
institutes.
Note. From NSF-AI, 2023.

AI Risk Management Framework
The National Institute of Standards and Technology (NIST) is a part of the U.S.
Department of Commerce, aiming to advance science, standards, and technology to promote U.S.
innovation and industrial competitiveness. The NAII ACT (NAII ACT, 2020) legislated for the
U.S. leadership in AI, directs NIST to (a) advance collaborative frameworks, standards,
guidelines, and associated methods and techniques for artificial intelligence, (b) support the
development of technical standards and guidelines that promote trustworthy artificial intelligence
systems, (c) support the development of technical standards and guidelines by which to test for
bias in artificial intelligence training data and applications, and (d) develop a risk management
framework for AI applications.
According to NIST (NIST-AI-RMF, 2023), AI presents significant opportunities yet poses
risks and threats, particularly careless design and use cases. Furthermore, NIST states that AI
systems without controls can increase, perpetuate, or worsen inequitable or undesirable outcomes
for individuals and communities. It also considers AI risk management a key component of
responsible development and use of AI systems. Data-driven AI algorithms are likely to be socio-
technical. Societal dynamics and human behavior influence them, and the risks of using them
need to be identified and managed (NIST-AI-RMF, 2023). Hence, NIST drafted an AI Risk
Management Framework (AI-RMF) to guide organizations in designing, developing, deploying,
or operating AI systems to minimize AI's many risks and promote trustworthy and responsible AI
systems. The AI-RMF is also intended to be voluntary, rights-preserving, nonsector-specific, and
use-case agnostic, providing flexibility for all organizations to implement the framework's
principles.
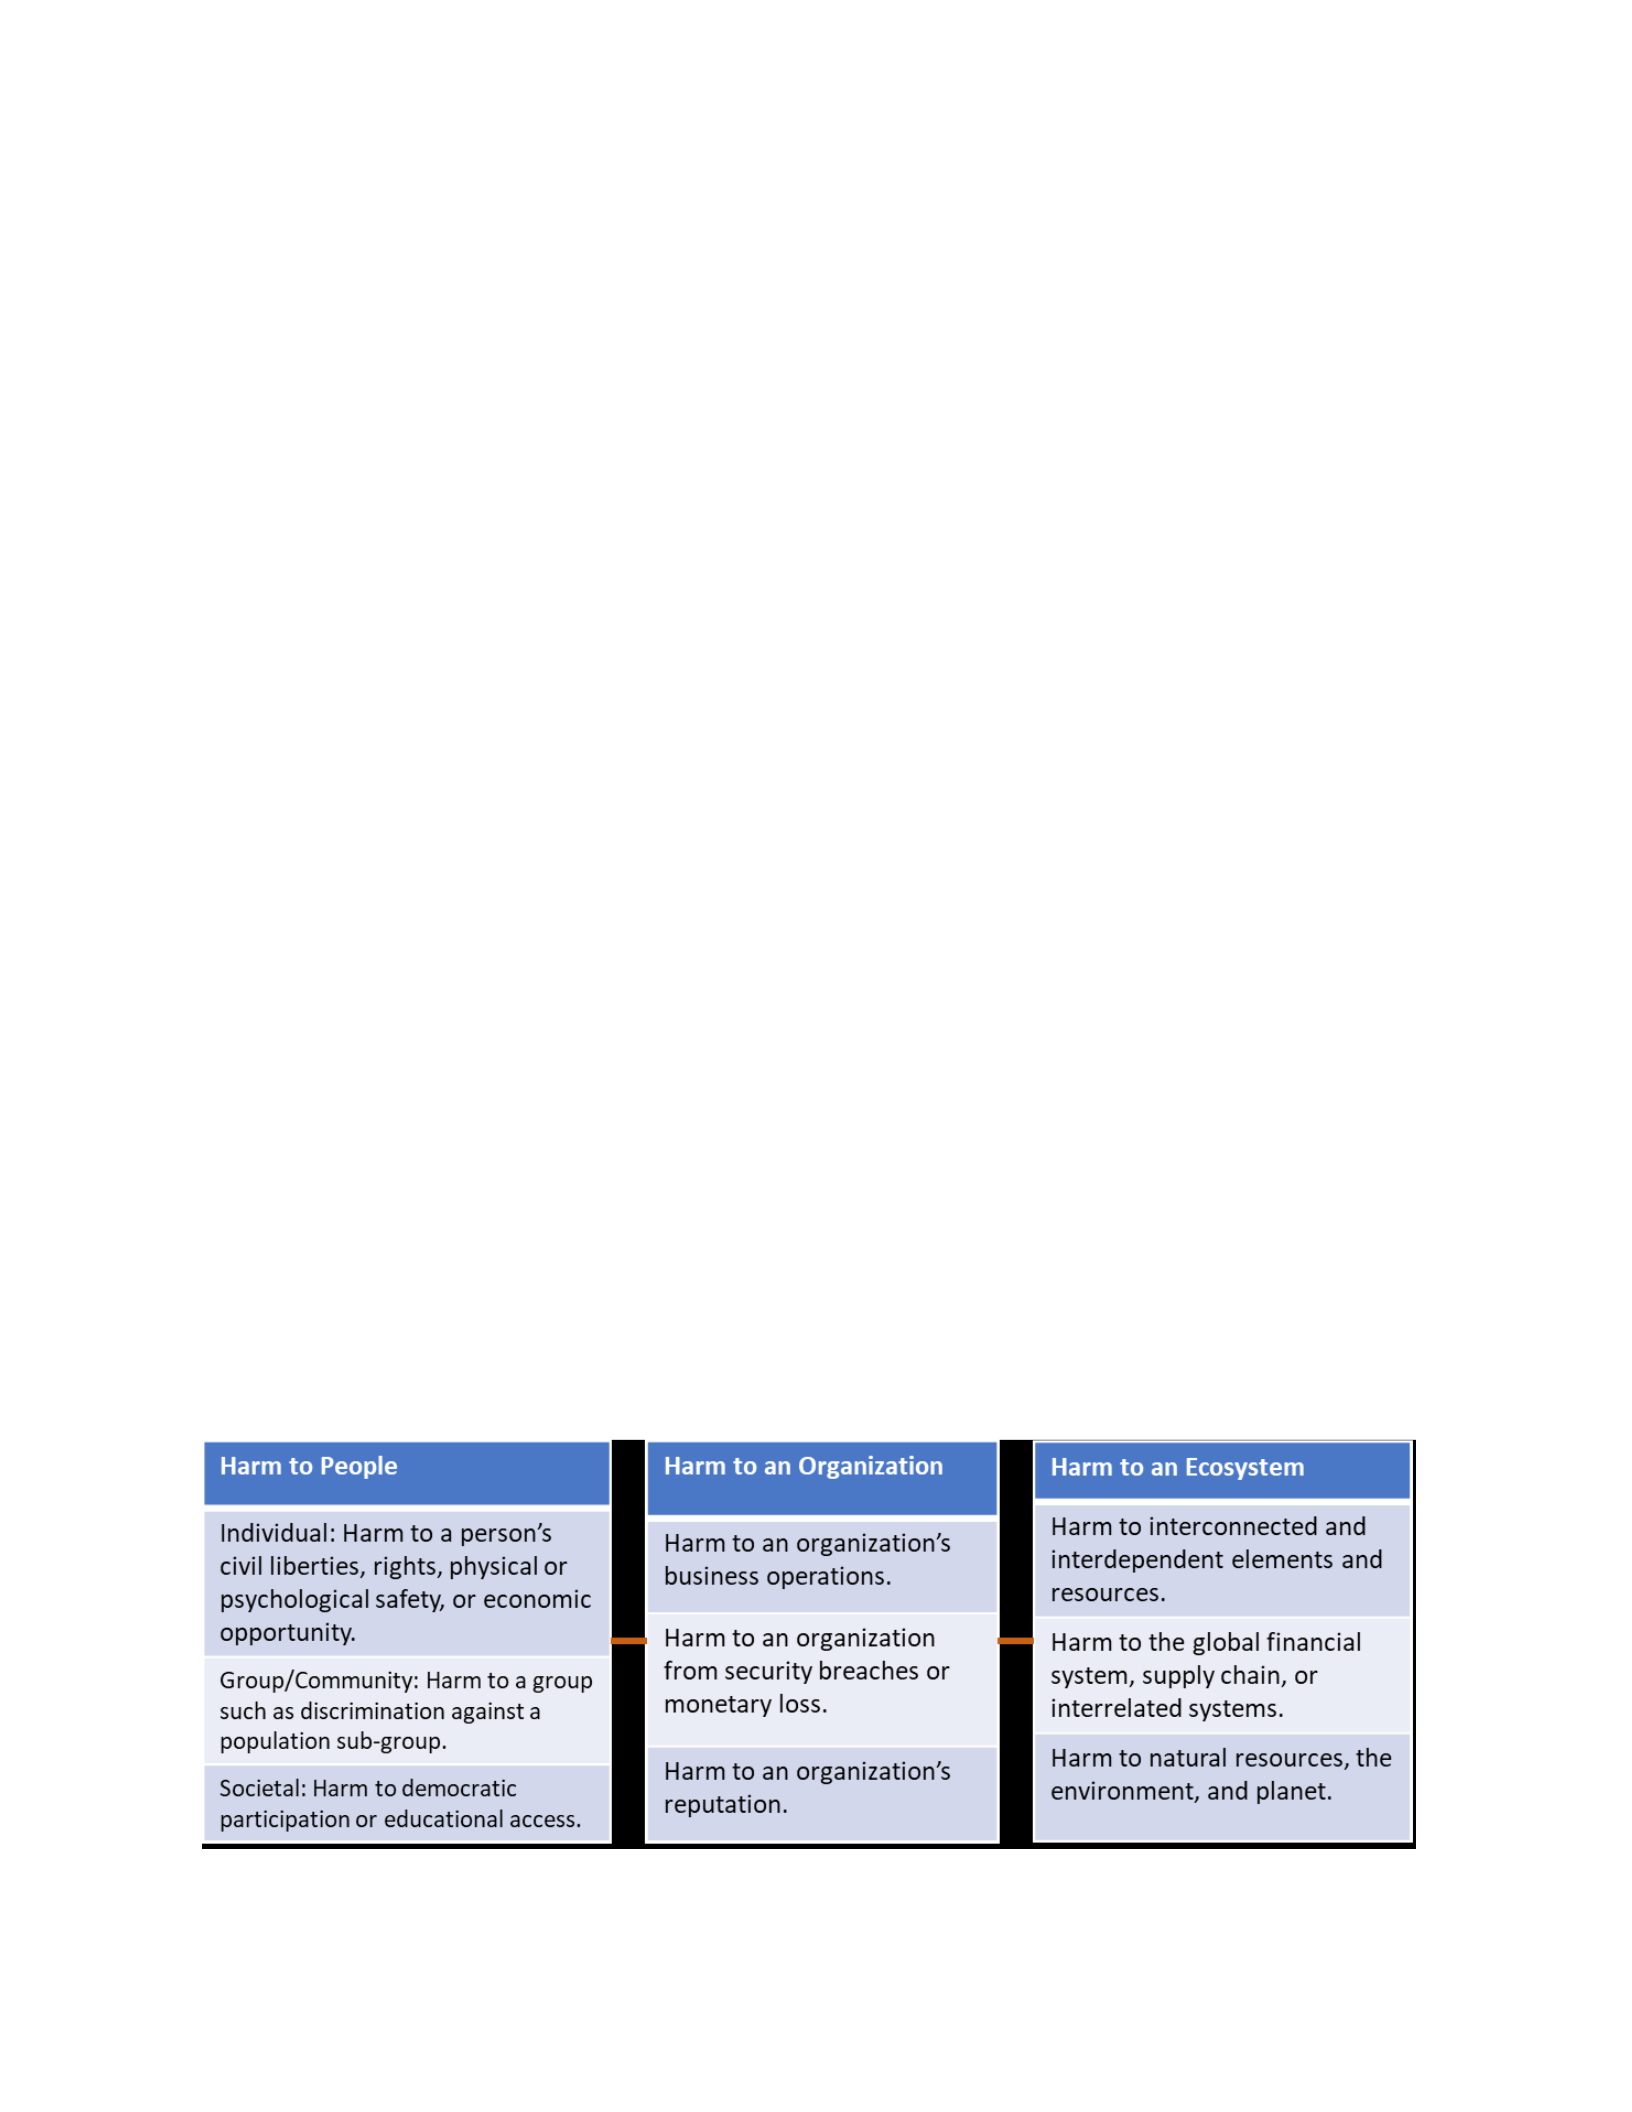
The first part of the AI-RMF describes the foundations of AI’s impacts, risks, and
potential harms and addresses the challenges in AI risk management. The second part describes
the core principles of the AI-RMF framework. The framework also explains the differences
between the risks of AI applications and traditional software systems. In establishing the
foundations of AI risks, the framework mentions examples of AI’s potential harms to (a) people,
(b) organizations, and (c) ecosystems. The framework further breaks down people as (a)
individuals, (b) communities, and (c) society. In the discussion of AI’s impact on organizations,
the framework mentions potential harms to (a) business operations, (b) security posture, (c)
monetary status, and (e) reputation. For AI's impacts on the ecosystem, the framework includes
potential harms to (a) the global supply chain, (b) financial systems, (c) the environment, and (d)
natural resources. The following figure provides examples of potential harms as described in the
AI-RMF framework:
Figure 2 Examples of Potential Harms from AI

Note. Recreated from NIST-AI-RMF, 2023, p. 5.
In analyzing and explaining AI's risks, the AI-RMF utilizes an AI life cycle approach,
identifies the socio-technical parameters impacted by AI, and maps the dimensions against the
life-cycle stages. The framework lists the AI application life cycle stages as (a) plan and design,
(b) collect and process data, (c) build and use, (d) verify and validate, (e) deploy and use, and (f)
operate and monitor. In addition, it also identifies the AI-impacted socio-technical dimensions as
(a) application context, (b) data and input, (c) AI model, (d) task and output, and (e) people and
planet (NIST-AI-RMF, 2023, p. 10). The following figure represents the AI life cycle stages and
impacted socio-technical dimensions as described in the AI-RMF framework:
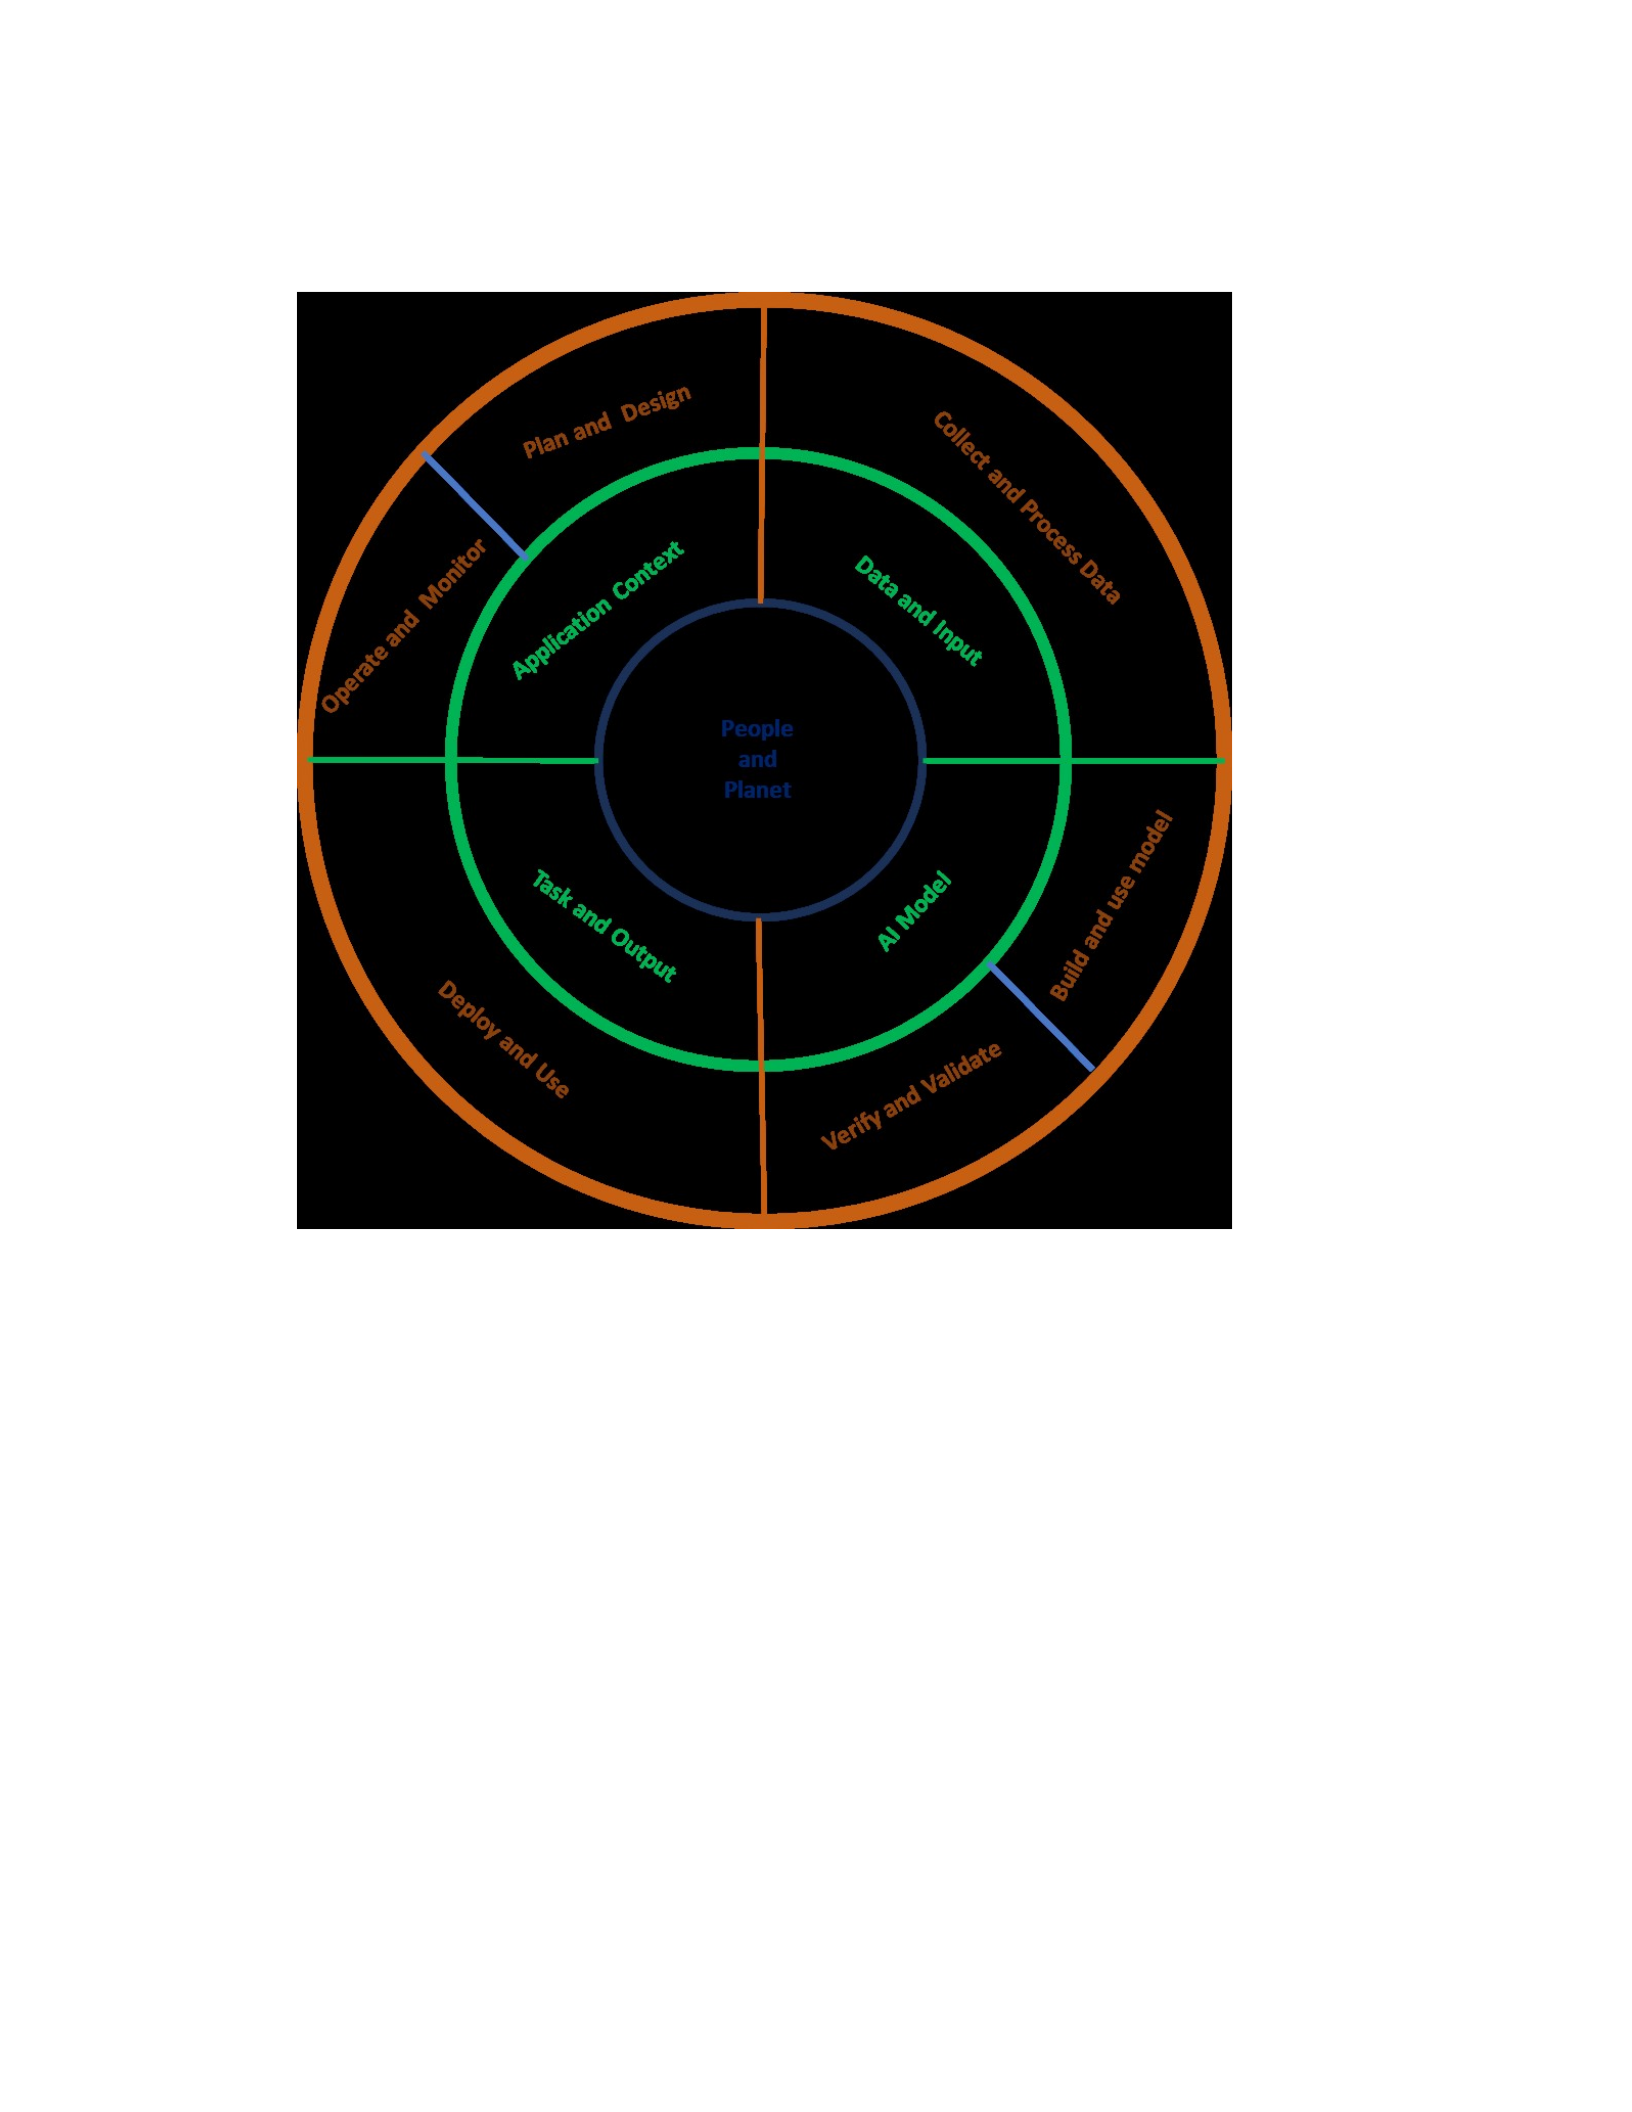
Figure 3 Lifecycle and Key Dimensions of AI System
Note. Recreated from NIST-AI-RMF, 2023, p. 10.
According to AI-RMF, risk management is the collective responsibility of the actors
participating in an AI application's life cycle. Hence, in addition to the description of
AIapplication life cycle stages and the related socio-technical dimensions, the AI-RMF also
identifies the AI actors and their responsibilities during the AI-application life cycle stages. The
framework identifies a list of AI application actors that includes Advocacy Groups, Application
Developers, Civil Society Organizations, C-suite Executives, Data Engineers, Data Scientists,
Domain Experts, End Users, Environmental Groups, Experts on Legal, Ethical, and Regulatory
Requirements, Experts on Socio-cultural issues within the application context, General Public,
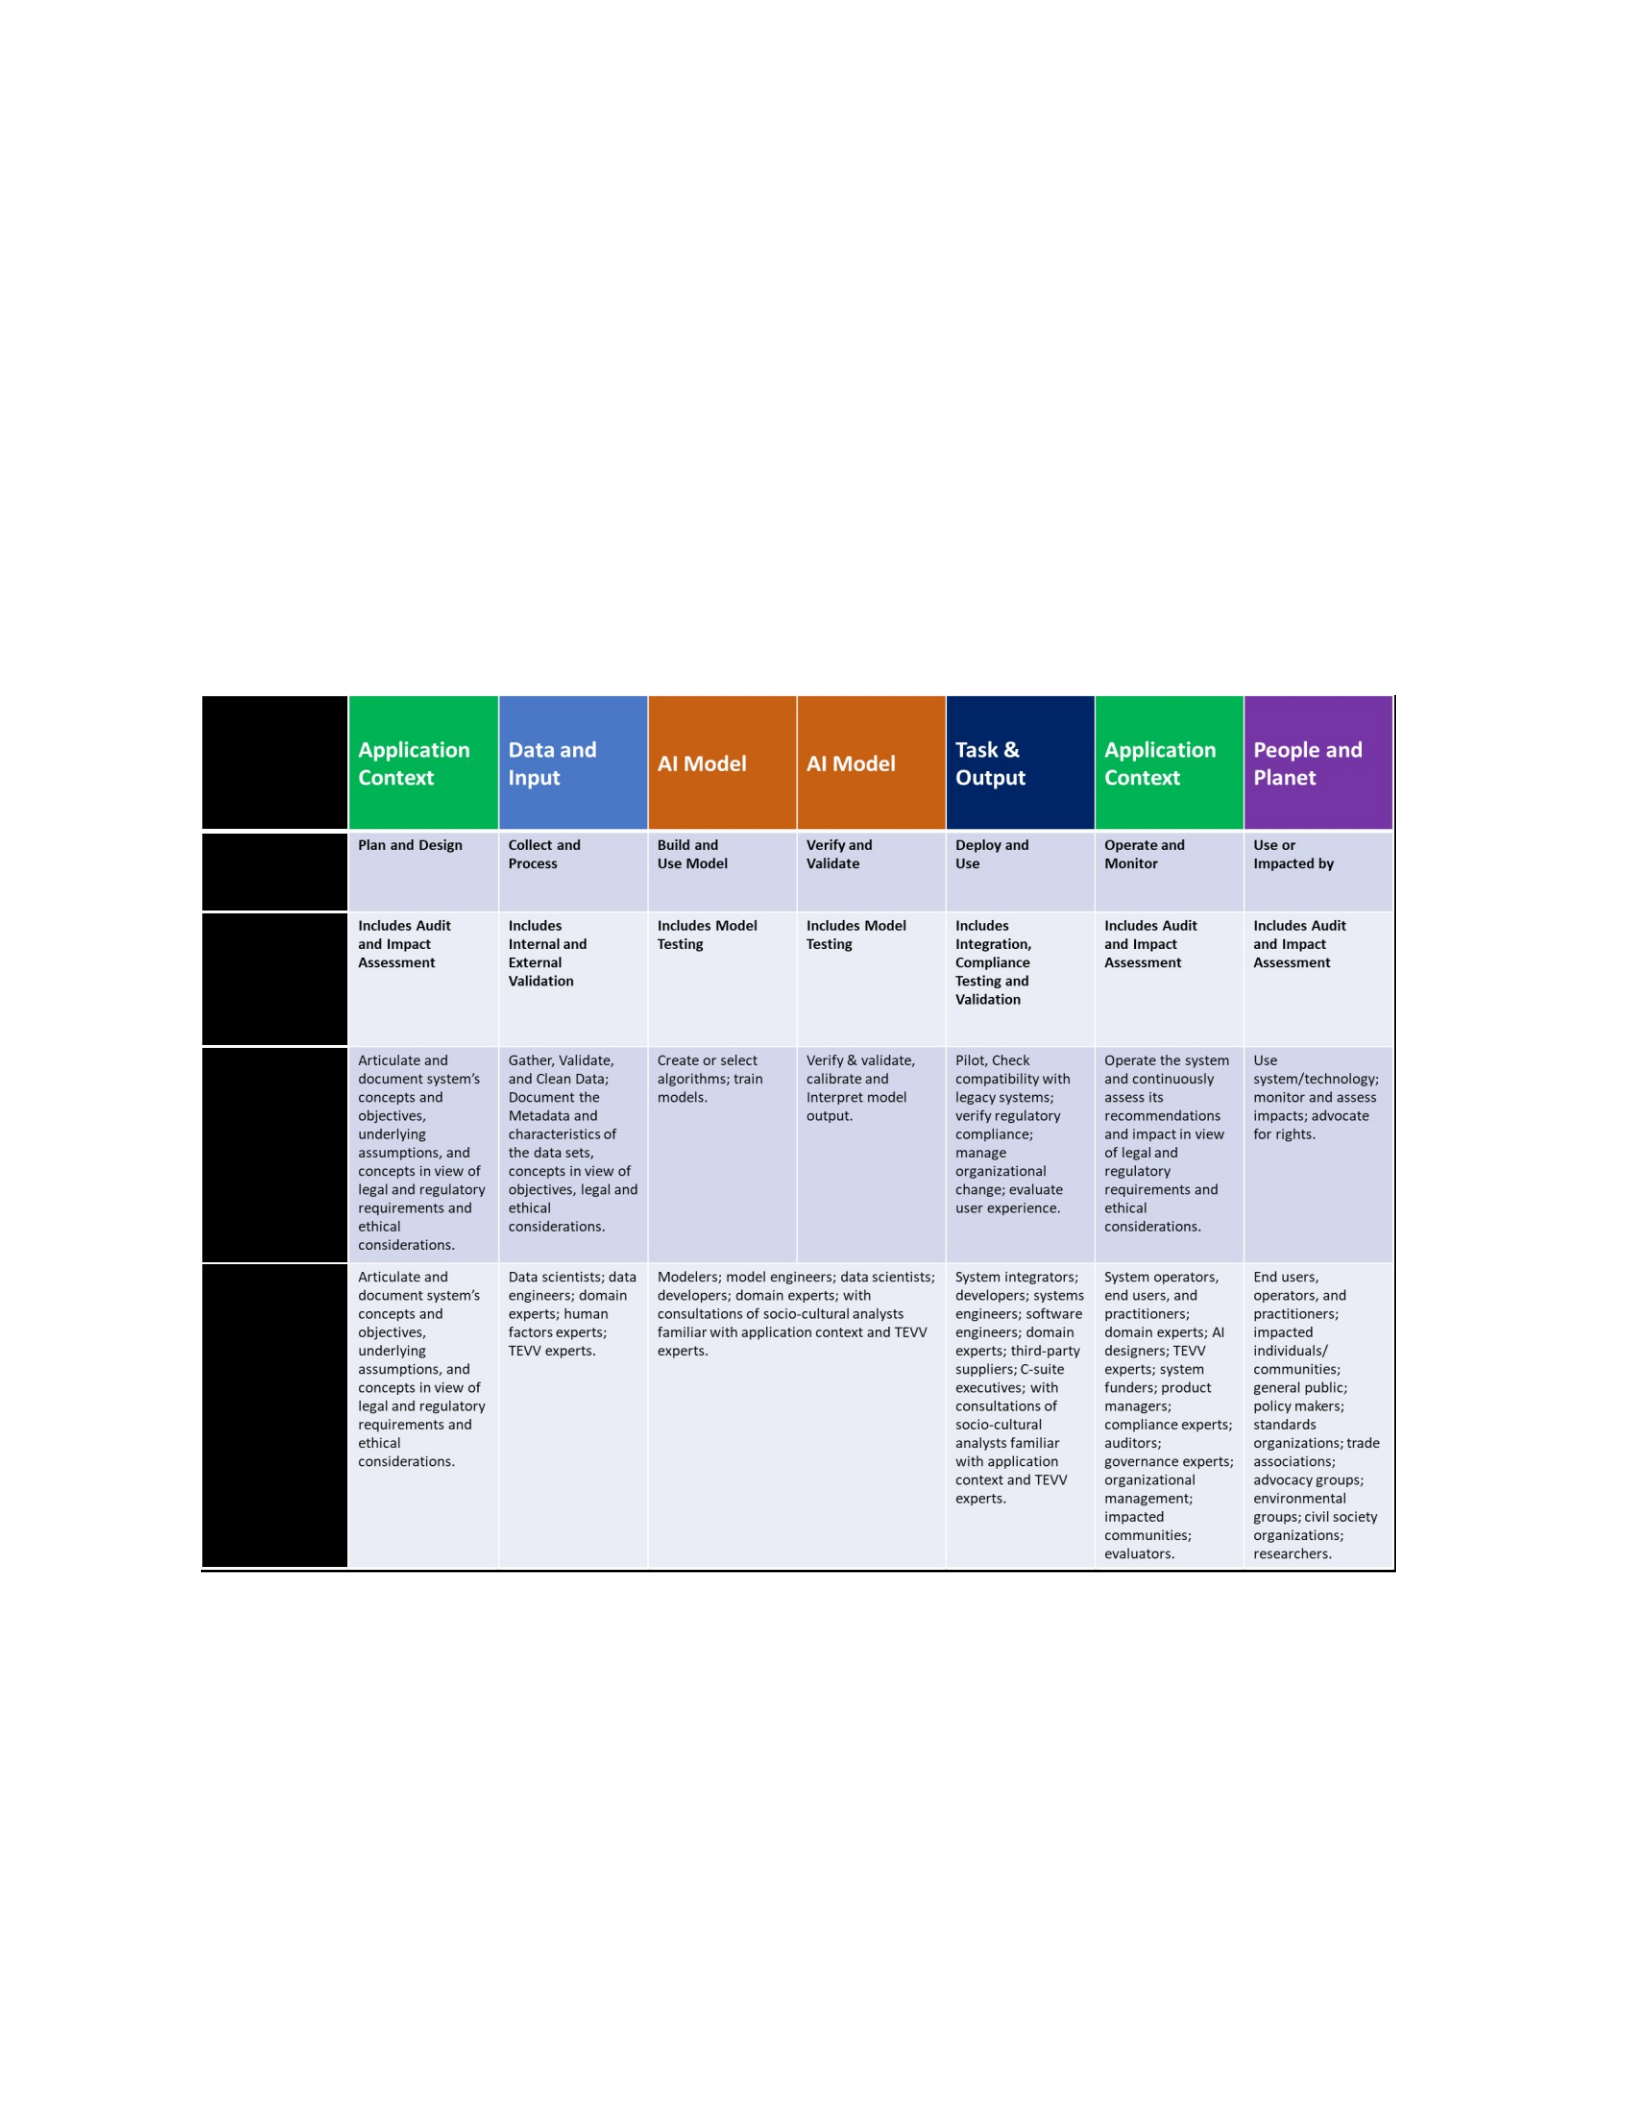
Human Factors Experts, Impacted Individuals and Communities, Model Engineers, Modelers,
Operators, Policy Makers, Practitioners, Researchers, Software Engineers, Standards
Organizations, System Integrators, Systems Engineers, Test, Evaluation, Verification, and
Validation Experts, Third-party Suppliers and Trade Associations (NIST-AI-RMF, 2023, p. 11).
The following figure represents the AI life cycle stages and the responsibilities of the actors
involved, as described by the AI-RMF framework:
Figure 4 AI Lifecycle, Actors, and Responsibilities
Note. Recreated from NIST-AI-RMF, 2023, p. 11.
Furthermore, the AI-RMF discusses the attributes of a trustworthy AI application and
mentions trustworthiness as a requirement to minimize AI risks. According to AI-RMF, AI's
trustworthiness depends on addressing multiple criteria, some specific to the context of use.
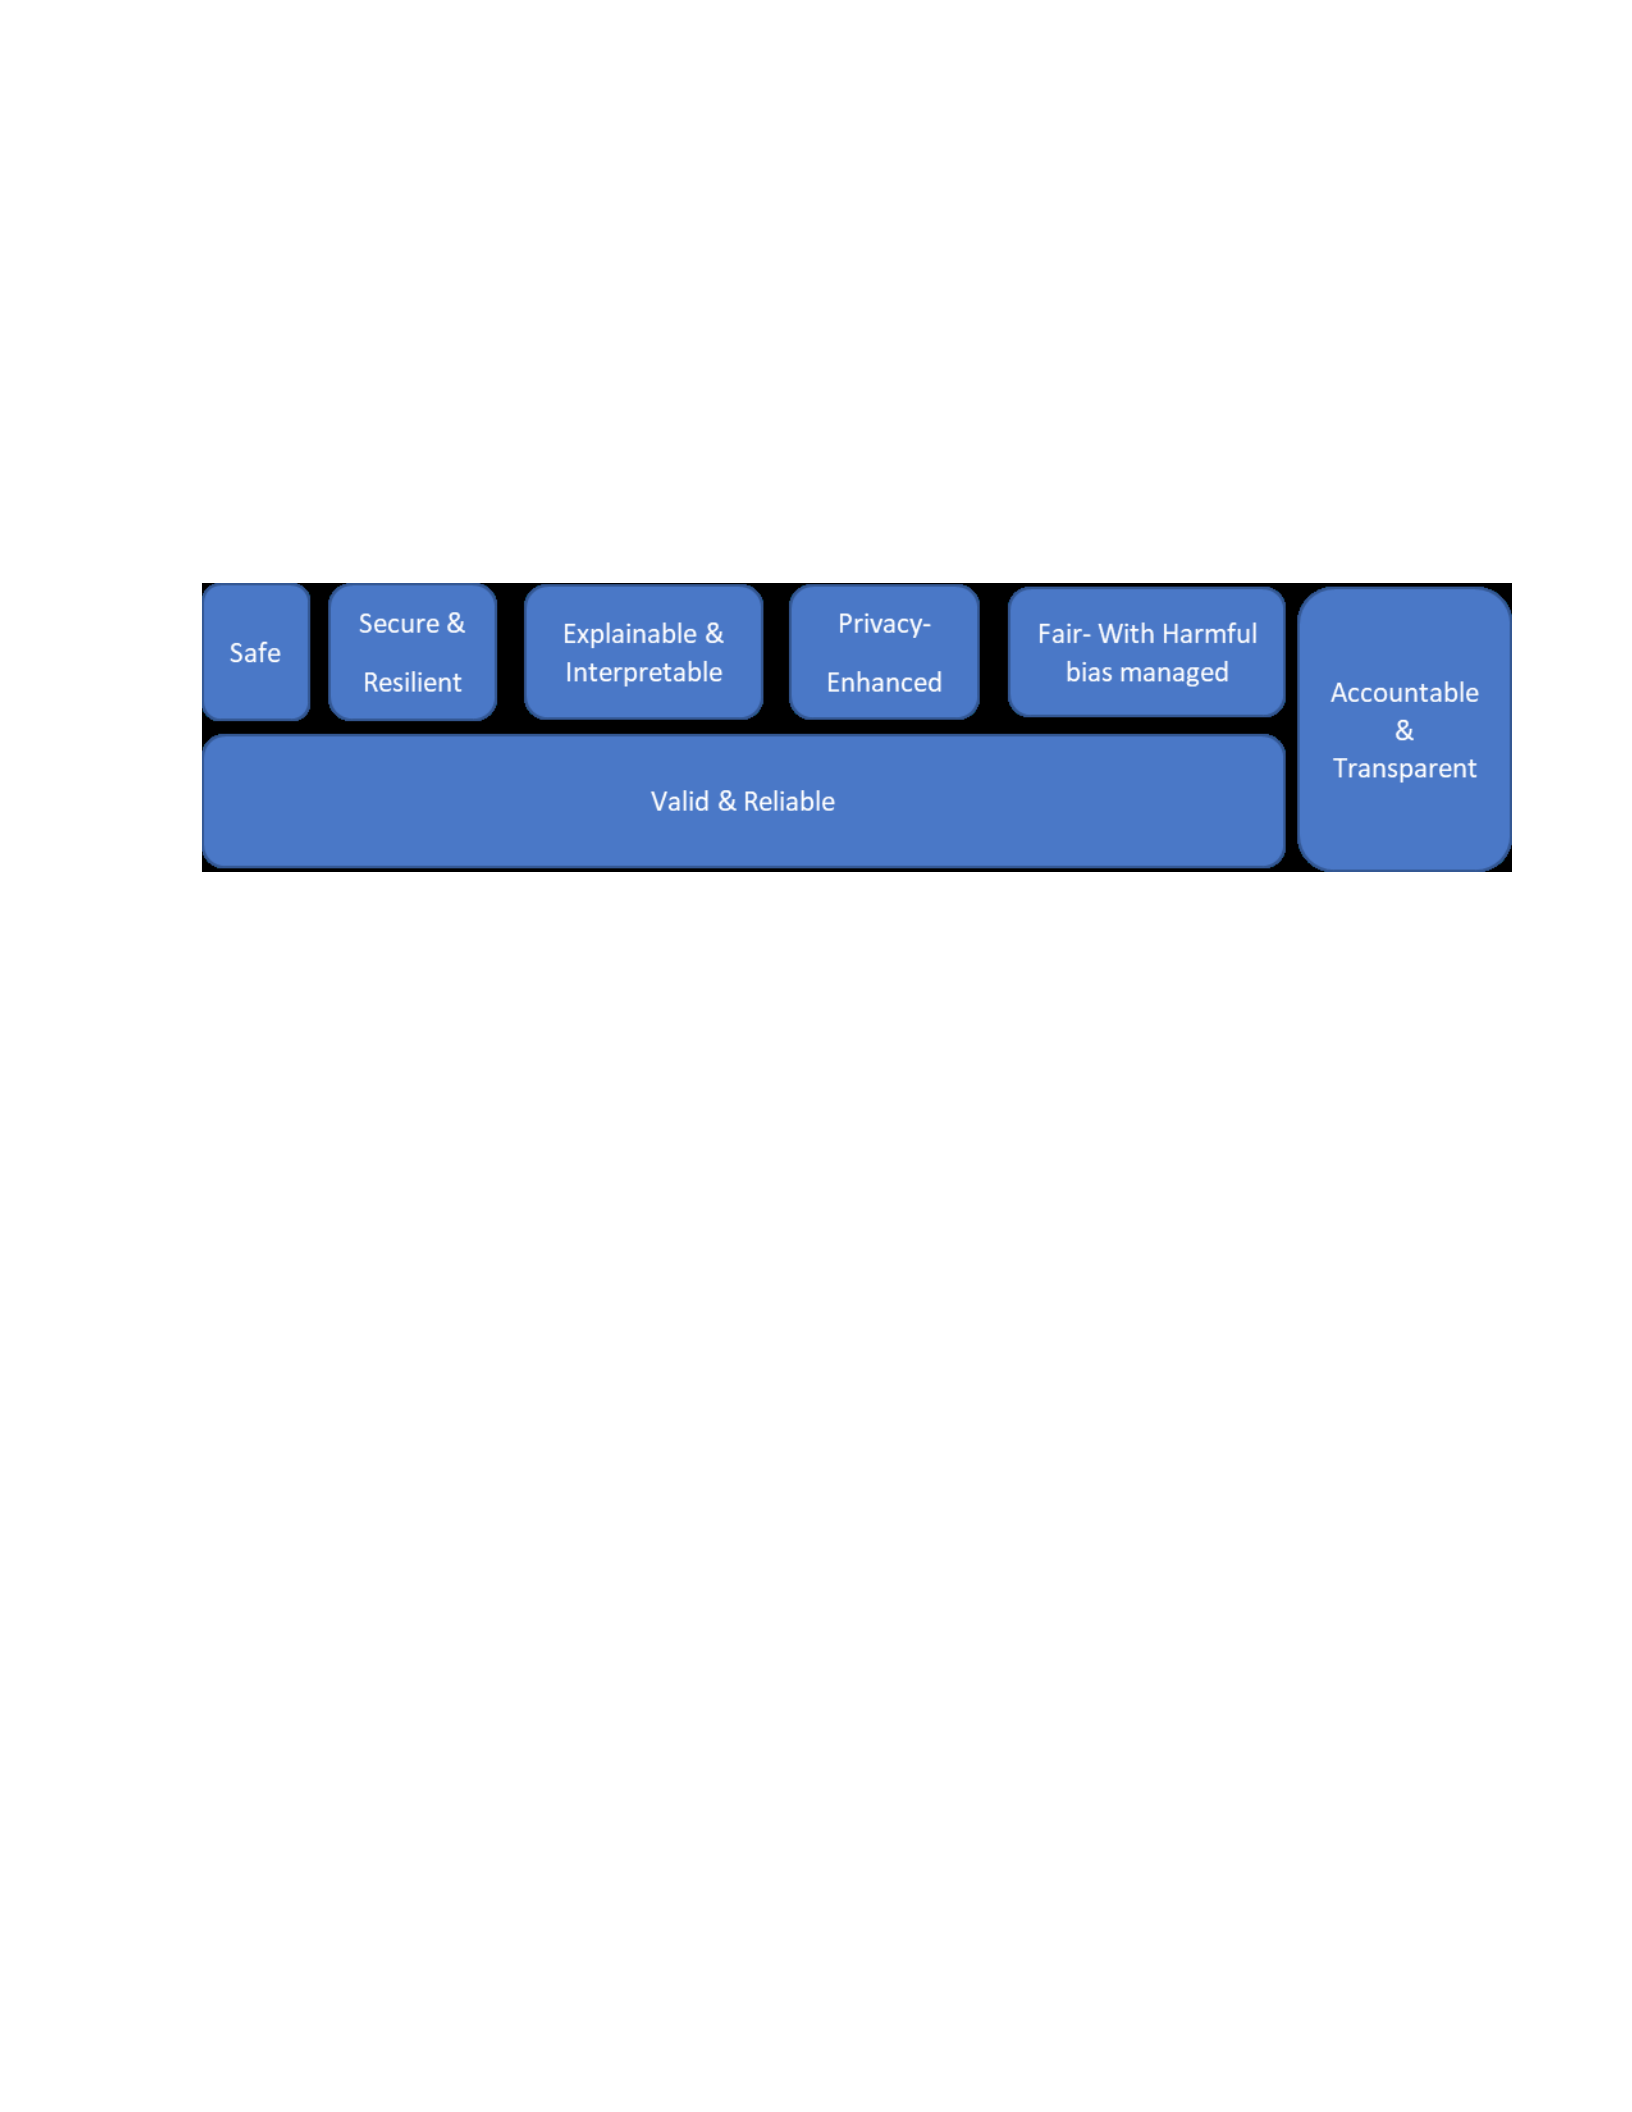
AIRMF describes the attributes of a trustworthy AI to be "valid and reliable, safe, secure and
resilient, accountable and transparent, explainable and interpretable, privacy-enhanced, and fair
with harmful bias managed” (NIST-AI-RMF, 2023, p. 12). The following figure represents the
attributes of trustworthiness as described in the AI-RMF framework:
Figure 5 Characteristics of Trustworthy AI Systems
Note. Recreated from NIST-AI-RMF, 2023, p. 12.
The second part of the AI-RMF is referred to as AI-RMF Core, and it describes four main
functions, broken down further into categories, sub-categories, and actions, with the intended
outcomes, all aimed at minimizing AI risks. The four core functions of the framework are (a)
Govern, (b) Map, (c) Measure, and (d) Manage. AI-RMF’s govern function influences the other
three functions, and its main objective is to implement risk management across all AI life cycle
stages and AI actors. The map function of AI-RMF, depending on the contextual details of the AI
application under analysis, aims to identify the negative impacts of its intended use and the risks
beyond the intended use. The other functions of the AI-RMF Core use the output from the map
function. The measure function uses qualitative, quantitative, and mixed methods to assess and
analyze AI's negative impacts and risks. Measuring AI's risks includes tracking its
trustworthiness attributes and recording management decisions to accept risks in return for
benefits. The management function of AI-RMF is designed to monitor, prioritize, and minimize
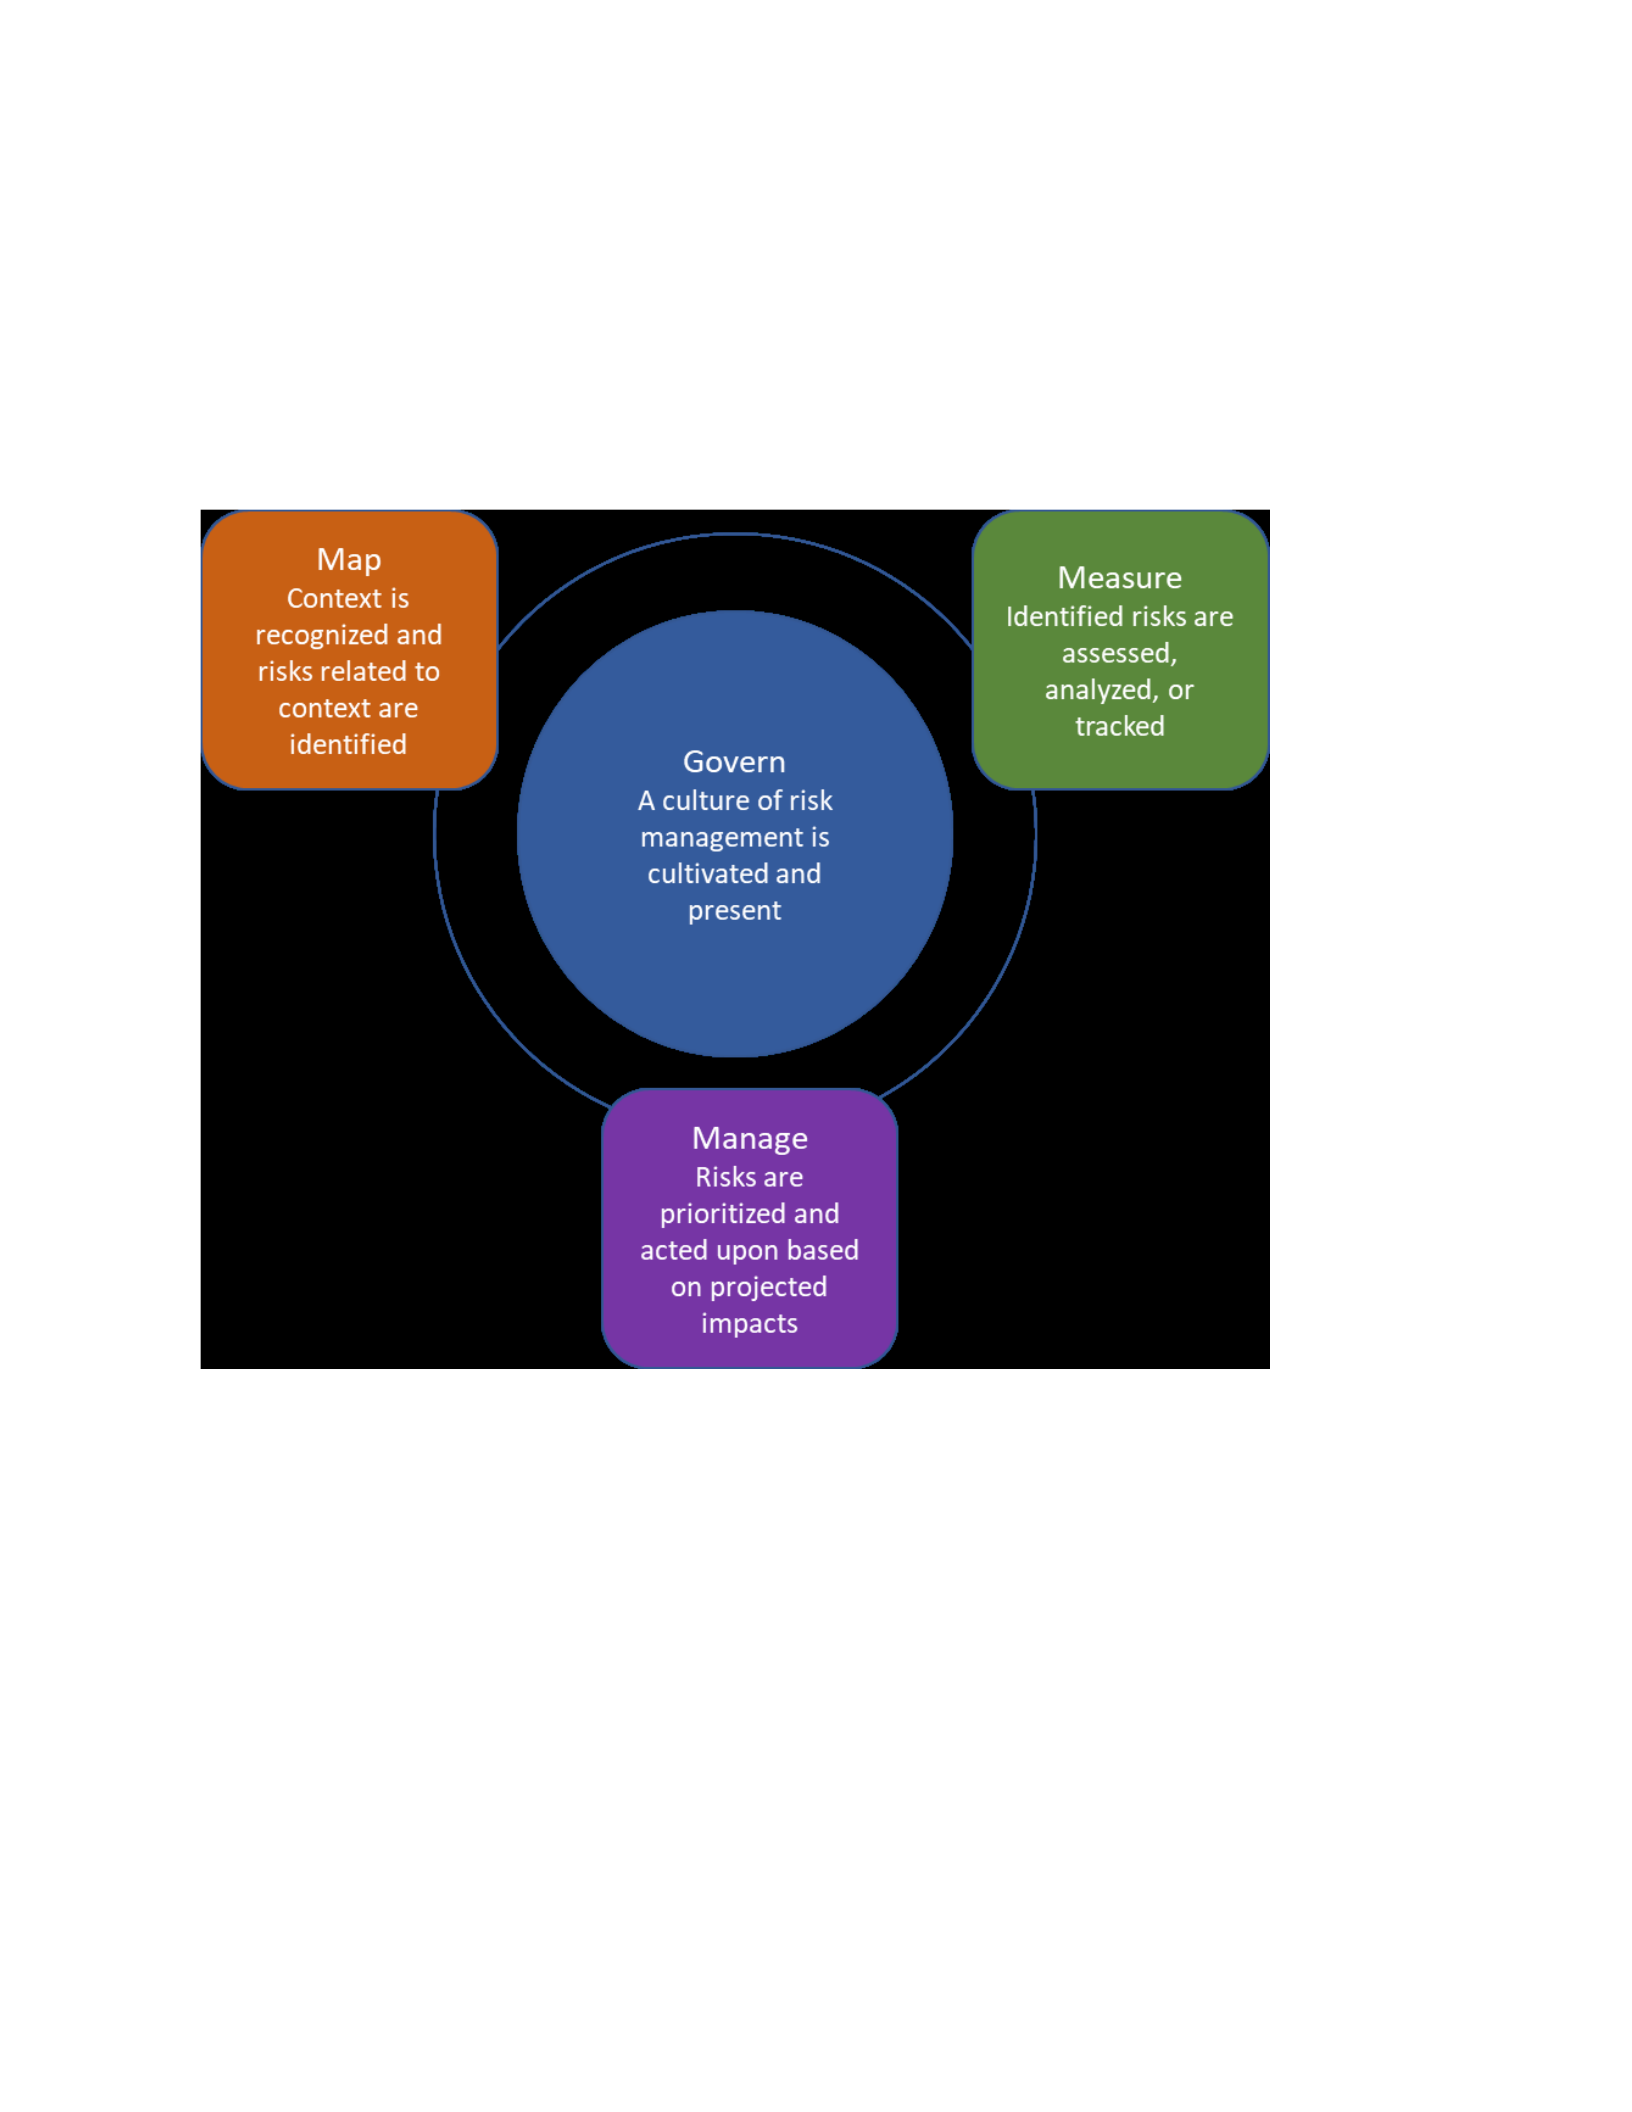
risks continuously, as guided by the governance function. The figure below represents the four
main functions of AI-RMF Core:
Figure 6 Functions of AI Risk Management Framework
Note. Recreated from NIST-AI-RMF, 2023, p. 20.
According to AI-RMF, AI algorithms and applications tend to have unique attributes with
potential negative impacts that differentiate them from the risks of traditional software systems.
Hence, it lists several key differences in the risks of data-driven AI algorithms when compared to the
risks from traditional software algorithms: The data used to train and build AI algorithms may not be
accurate enough to reflect its context, creating less reliable results; The data used for decision-support
AI algorithms may contain biased decisions of the past years, resulting in perpetuating the bias in AI

applications; When used without controls, the data behind AI algorithms could lead to privacy
violations; The outcomes of AI algorithms are not readily explainable and hence not easily
reproducible; More frequent maintenance of AI models may be required if the model drifts over time
due to newer trends in input data; and Insufficient training data tends to create unreliable AI
algorithms.
Studies on Generative AI
The Fundamentals
Recursive neural networks used for machine learning-based natural language processing
were replaced with a new attention mechanism in 2017 that enabled highly efficient parallel
processing of input strings (Vaswani et al., 2017). Though the proposed transformer architecture
was focused on text strings as inputs, Vaswani et al. (2017) concluded the discussion of their
approach with plans to apply their transformer architecture for inputs other than text. According
to Raschka (2023), the year 2023 has been one of rapid growth and popularity for AI;
furthermore, the most impactful AI papers of the year 2023 analyzed variations of AI
transformer-based language processing models referred to as large language models (LLMs).
Taxonomy of Generative AI
Based on AI Transformers and pre-trained unsupervised deep learning models, another
class of AI technology, large generative AI models (LGAIM), has emerged with the capabilities
to produce novel outputs not seen earlier (Hacker et al., 2023). The large language models
(LLMs) are a version of the generative AI model applied to texts. Gozalo-Brizuela and
GarridoMerchan (2023, p. 3) present a taxonomy of the generative AI models released since 2021 and
identify them under nine categories based on their capabilities. They are text-to-image, text-tothree-
dimensional views, image-to-text, text-to-video, text-to-audio, text-to-text, text-to-code, text-to-
science, and image-to-text.
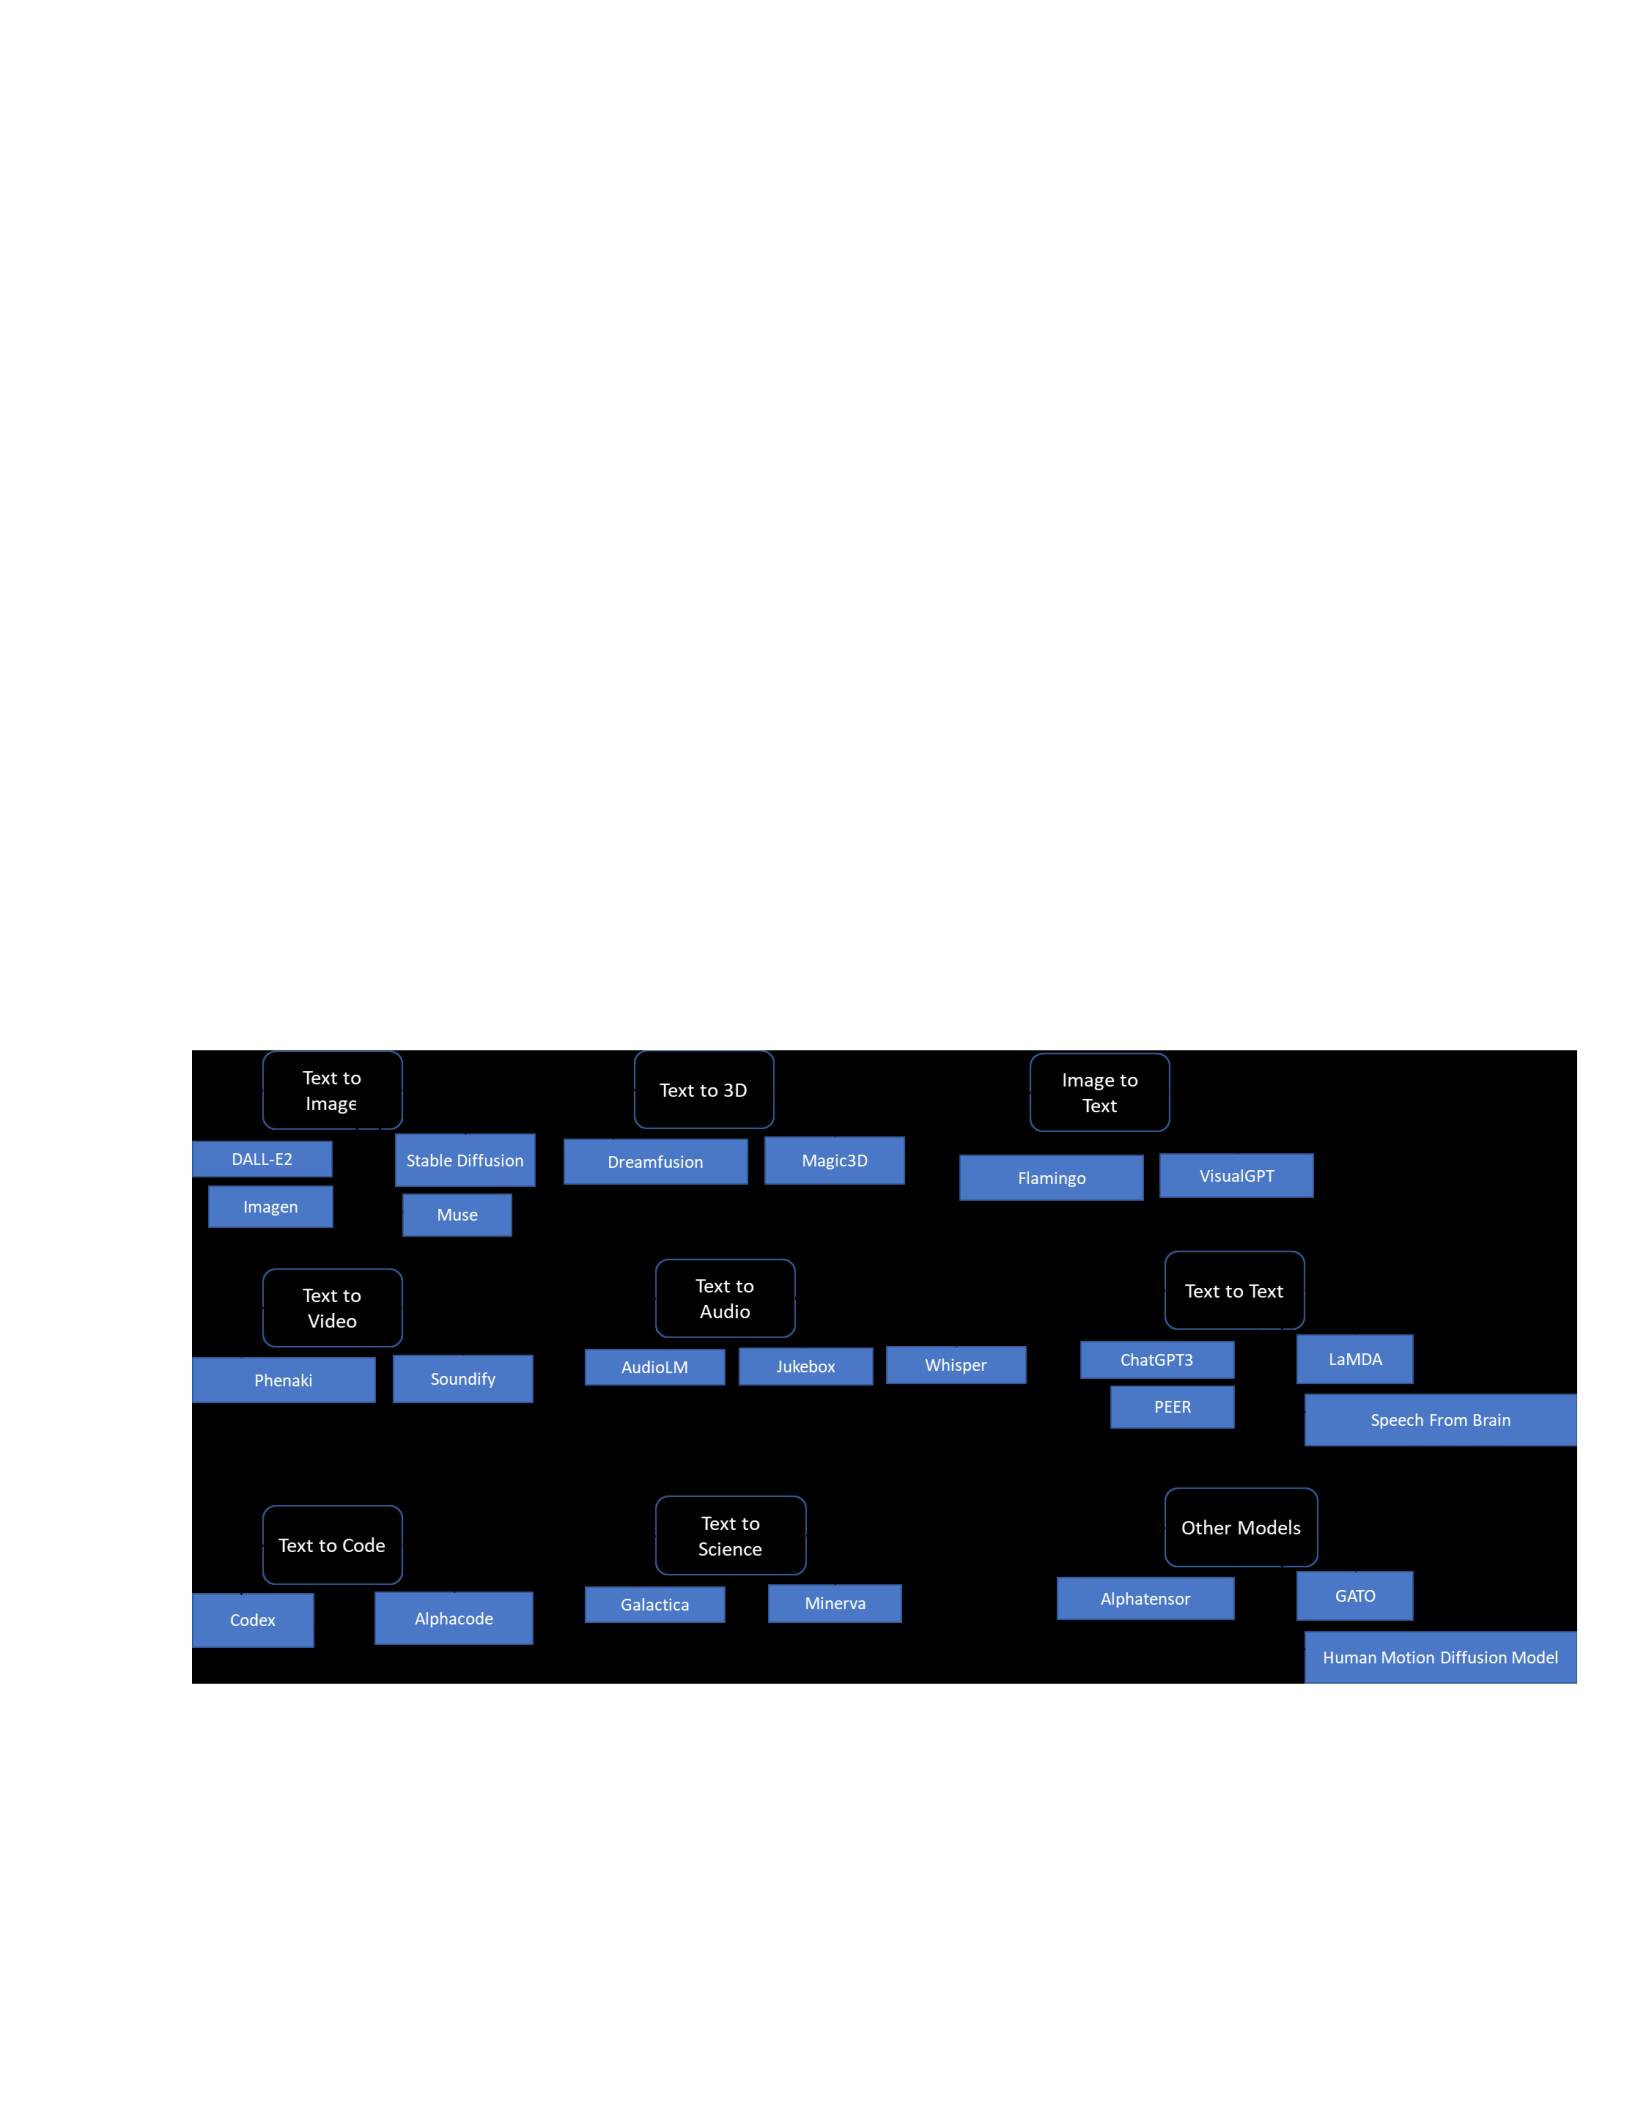
Furthermore, according to Gozalo-Brizuela and Garrido-Merchan (2023), earlier AI
machine learning models are trained to identify and classify patterns in data provided to them as
inputs, while the more recent generative AI models are unique in using unsupervised or
semisupervised or supervised learning techniques on extensive input data to generate novel
outputs. As a result, the generative AI models can be used both as a general question-and-answer
system or as an artistic content-creating system. Consequently, the generative AI tools released in
the market significantly impact multiple aspects of the economy and society. The taxonomy of
generative AI presented by Gozalo-Brizuela and Garrido-Merchan (2023) is shown in the figure
below:
Figure 7 Taxonomy of Generative AI
Note. Recreated from Gozalo-Brizuela and Garrido-Merchan (2023).
Furthermore, Gozalo-Brizuela and Garrido-Merchan (2023) also discuss the timeline of
the generative AI tools released for general use and point out that though the earliest tool was
available in 2021, most were released in 2022. The figure below shows the timeline of the
generative AI tools released:
Figure 8 Timeline of Generative AI Tools
Note. Recreated from Gozalo-Brizuela and Garrido-Merchan (2023).
Impact on Cybersecurity
Generative AI tools have made a significant impact on the AI community and the users of
AI across many fields, such as education, arts, and law. They are considered the latest frontier of
the AI technology landscape (Gupta et al., 2023). In addition, researchers mention multiple
instances where generative AI tools, such as ChastGPT, have been used for both cyber defense
and cyber-attacks. Gupta et al. (2023) describe that generative AI models could be exploited for
cyber defense and cyber-attacks and list their potential impact under multiple categories: Attacks
on the generative AI models themselves and damaging the integrity of the large data volumes that
drive them; Cyber-attacks that use the generative AI models for activities such as social
engineering, phishing emails, automated hacking, attack payload generation, malware code
generation, and polymorphic malware generation; Cyber security that uses the generative AI
models for tasks such as cyber defense automation, cybersecurity reporting, threat intelligence,
secure code generation and detection, identification of cyber-attacks, development of ethical
guidelines, and incident response; The Impact of generative AI on social, legal, and ethical issues
involves the models' pervasive role, unauthorized access to conversations, personal information
misuse, data ownership concerns, misuse by organizations and employees, and hallucinations.
The following figure represents the impact of generative AI, as presented by Gupta et al.
(2023), on analyzing the commercially available tool ChatGPT on cybersecurity and privacy:
Figure 9 Impact of Generative AI on Cybersecurity and Privacy
Note. Recreated from Gupta et al. (2023).
Risks and Governance
While the generative AI models present great potential to sectors of society such as
education, research, and arts, they also pose significant risks (Hacker et al., 2023). Despite

widespread benefits, the generative AI models have been found to have limitations, such as
generating erroneous answers and presenting fictitious text as real ones (BaiXdoo-Anu & Ansah,
2023, p. 58). The generative AI tools offer new features not offered by the earlier AI technologies
and present unique risks in addition to those in the previous AI technologies. For example,
Elgesem (2023) reviews the AI Act of 2021, formulated to regulate AI technologies by the
European Commission, and finds it to address only the risks posed by data-driven AI algorithms
to individuals. Elgesem (2023) observes that generative AI tools could be used to publish
credible-looking fake content that could strengthen extremist views resulting in radicalization
and recommends amendments to the AI Act to regulate the potential societal damage that
generative AI could cause.
Since generative AI models use publicly available news articles, academic papers, social
media posts, photos, and even chatbot chats as their training data, Lucchi (2023) argues that these
tools pose legal issues concerning the ownership of the generated contents, copyright, and the fair
use of the training data. Hayes (2023) discusses the potential copyright infringements by
generative AI when they use publicly available content for training the models and suggests
measures that are not burdensome on the development of AI.
As additional AI technology, such as generative AI, is added to the suite of AI
technologies, the U.S. Government continues to track and provide guidance and mandates to
benefit from the new opportunities and to manage the emerging risks better. For example, on
October 30, 2023, the U.S. President issued an executive order titled “Safe, Secure, and
Trustworthy Development and Use of Artificial Intelligence” that included several mandates to
manage the risks of rapidly growing generative AI models and also to track and protect against
the use of U.S. Computing infrastructure for training AI models with malicious intent, such as
cybercrimes (The White House, 2023b). There are two critical directives from this executive

order. The first is that within 270 days of this executive order, the National Institute of Standards
and Technology (NIST) under the U.S. Department of Commerce must develop a risk
management framework for generative AI models. This framework will be a companion resource
to the prior framework covering the other AI models. The second one is that within 90 days of
this executive order, the U.S. Department of Commerce secretary must propose a regulation
through which the U.S. providers of high-end computing infrastructure can be directed to report
periodically on foreign clients building AI technologies for suspected malicious cyber activities.
Studies on AI and Cybersecurity Trends
Studies that describe the current and future states of AI and cybersecurity were reviewed
and analyzed to establish the context and understand the current research environment for
exploring the main research question of this dissertation. Current researchers are exploring a
wide range of topics related to AI and cybersecurity, such as the future of AI, the demand for AI
and cybersecurity skills, the global competition for leadership in AI, the strategies for AI in the
commercial and public sector, the impact of AI on economies, militaries, and societies, the
challenges faced by cybersecurity, adoption challenges of AI that persist, the need for governance
and regulations for AI, the risks of attacks on critical computing infrastructure, the trend of
hackers using AI for sophisticated cyberattacks, the potential of AI to improve cybersecurity, and
the barriers to harnessing AI for better cybersecurity.
For example, AI researchers participated in a Stanford University panel in 2021 to
discuss, question, and describe the next 100 years of AI. An earlier AI researcher panel that met
in 2016 focused on the North American context and omitted AI's impact on defense and the
military. However, the 2021 panel of AI researchers, referred to as Littman et al. (2021), widened
their scope, composed key AI-related questions, and arrived at responses. They predict the
significant global growth of AI impacting nearly all aspects of future economies and societies.

They also emphasize the need for better control and governance of AI's potentially harmful
influence on societies.
Furthermore, according to Littman et al. (2021), (a) since 2016, AI has grown
significantly in all of its application sub-domains, such as vision, speech recognition, voice
synthesis, natural language processing, image and video generation, multi-agent systems,
planning, decision-making, and robotics, (b) breakthrough AI applications have emerged in
medicine, autonomous driving, games, natural language translation, and personal assistance, (c)
the core AI technologies behind its growth are deep learning and reinforced learning, enabled by
the availability of large scale data and computing resources, (d) the U.S. public awareness on AI
has broadened, (e) the U.S. government, in response to global competition, has initiated measures
towards leadership in AI, and (f) the governance and regulation of AI-based applications to
minimize the risks are also under research, discussions, and implementations.
Another example is Anderson et al. (2018), who, in their survey on artificial intelligence
and the future of humans, provide quotes from thought leaders in AI. They quote from Judith
Donath, author of "The Social Machine, Designs for Living Online" and faculty fellow at
Harvard University's Berkman Klein Center for Internet & Society, "By 2030, most social
situations will be facilitated by bots – intelligent-seeming programs that interact with us in
human-like ways" (p. 5). Using a quote from Amy Webb, the founder of the Future Today
Institute and professor of strategic foresight at New York University, they further add that every
single industry will become more deeply entrenched with AI systems (pp. 6-7).
A study focusing on AI skills for the U.S. federal workforce is from D. Gilbert (2021),
which elaborates on the steps needed for the United States to implement AI in U.S. federal

agencies. The shortage of AI skills in the U.S. federal workforce "not only leaves our country
functioning below potential but also puts U.S. cybersecurity at risk” (D. Gilbert, 2021, p. 3).
According to D. Gilbert (2021), implementing AI can improve the workforce's productivity by up
to 40% and result in savings of 41.1 billion dollars to U.S. federal agencies. In addition,
professionals in many fields have started combining the skills specific to their field with AI
skills, referring to that blend as "bilingual talent" (D. Gilbert, 2021, p. 16). D. Gilbert (2021)
further recommends that for AI skills, the U.S. federal government must institute fellowships and
apprenticeships, partner with non-profit organizations for skills-based hiring, and consider an AI
ethics officer for each agency to address the risks associated with AI.
Studies on AI’s Impact on Cybersecurity Practice Areas and Managing Breaches
A study by Lazic (2019) provides insight into the current and future trends in using AI for
cybersecurity. According to Lazic (2019), in 2016, of the funding for 279 cybersecurity startups,
the companies with AI applications for cybersecurity attracted the most investments. Referring to
a survey of 850 information system executives from 10 different countries by Capgemini
Research Institute, Lazic (2019) mentions that 75% of those surveyed responded that AI enables
faster response to data breaches, and 65% responded that AI is essential to protect against
cyberattacks; furthermore, the survey shows that organizations report a reduction in both the time
to detect and to remediate a data breach.
Lazic (2019) also refers to Siemens Cyber Defense Center (CDC) developing an
AIenabled automated platform to evaluate over 60,000 threats per second, using less than a
dozen cybersecurity professionals. AI lowers the cost of detecting and responding to breaches,
saving an average of 12% over other techniques (Lazic, 2019, p. 7). He summarizes that AI
applications can enhance cybersecurity with the proper training, systems, and resources while
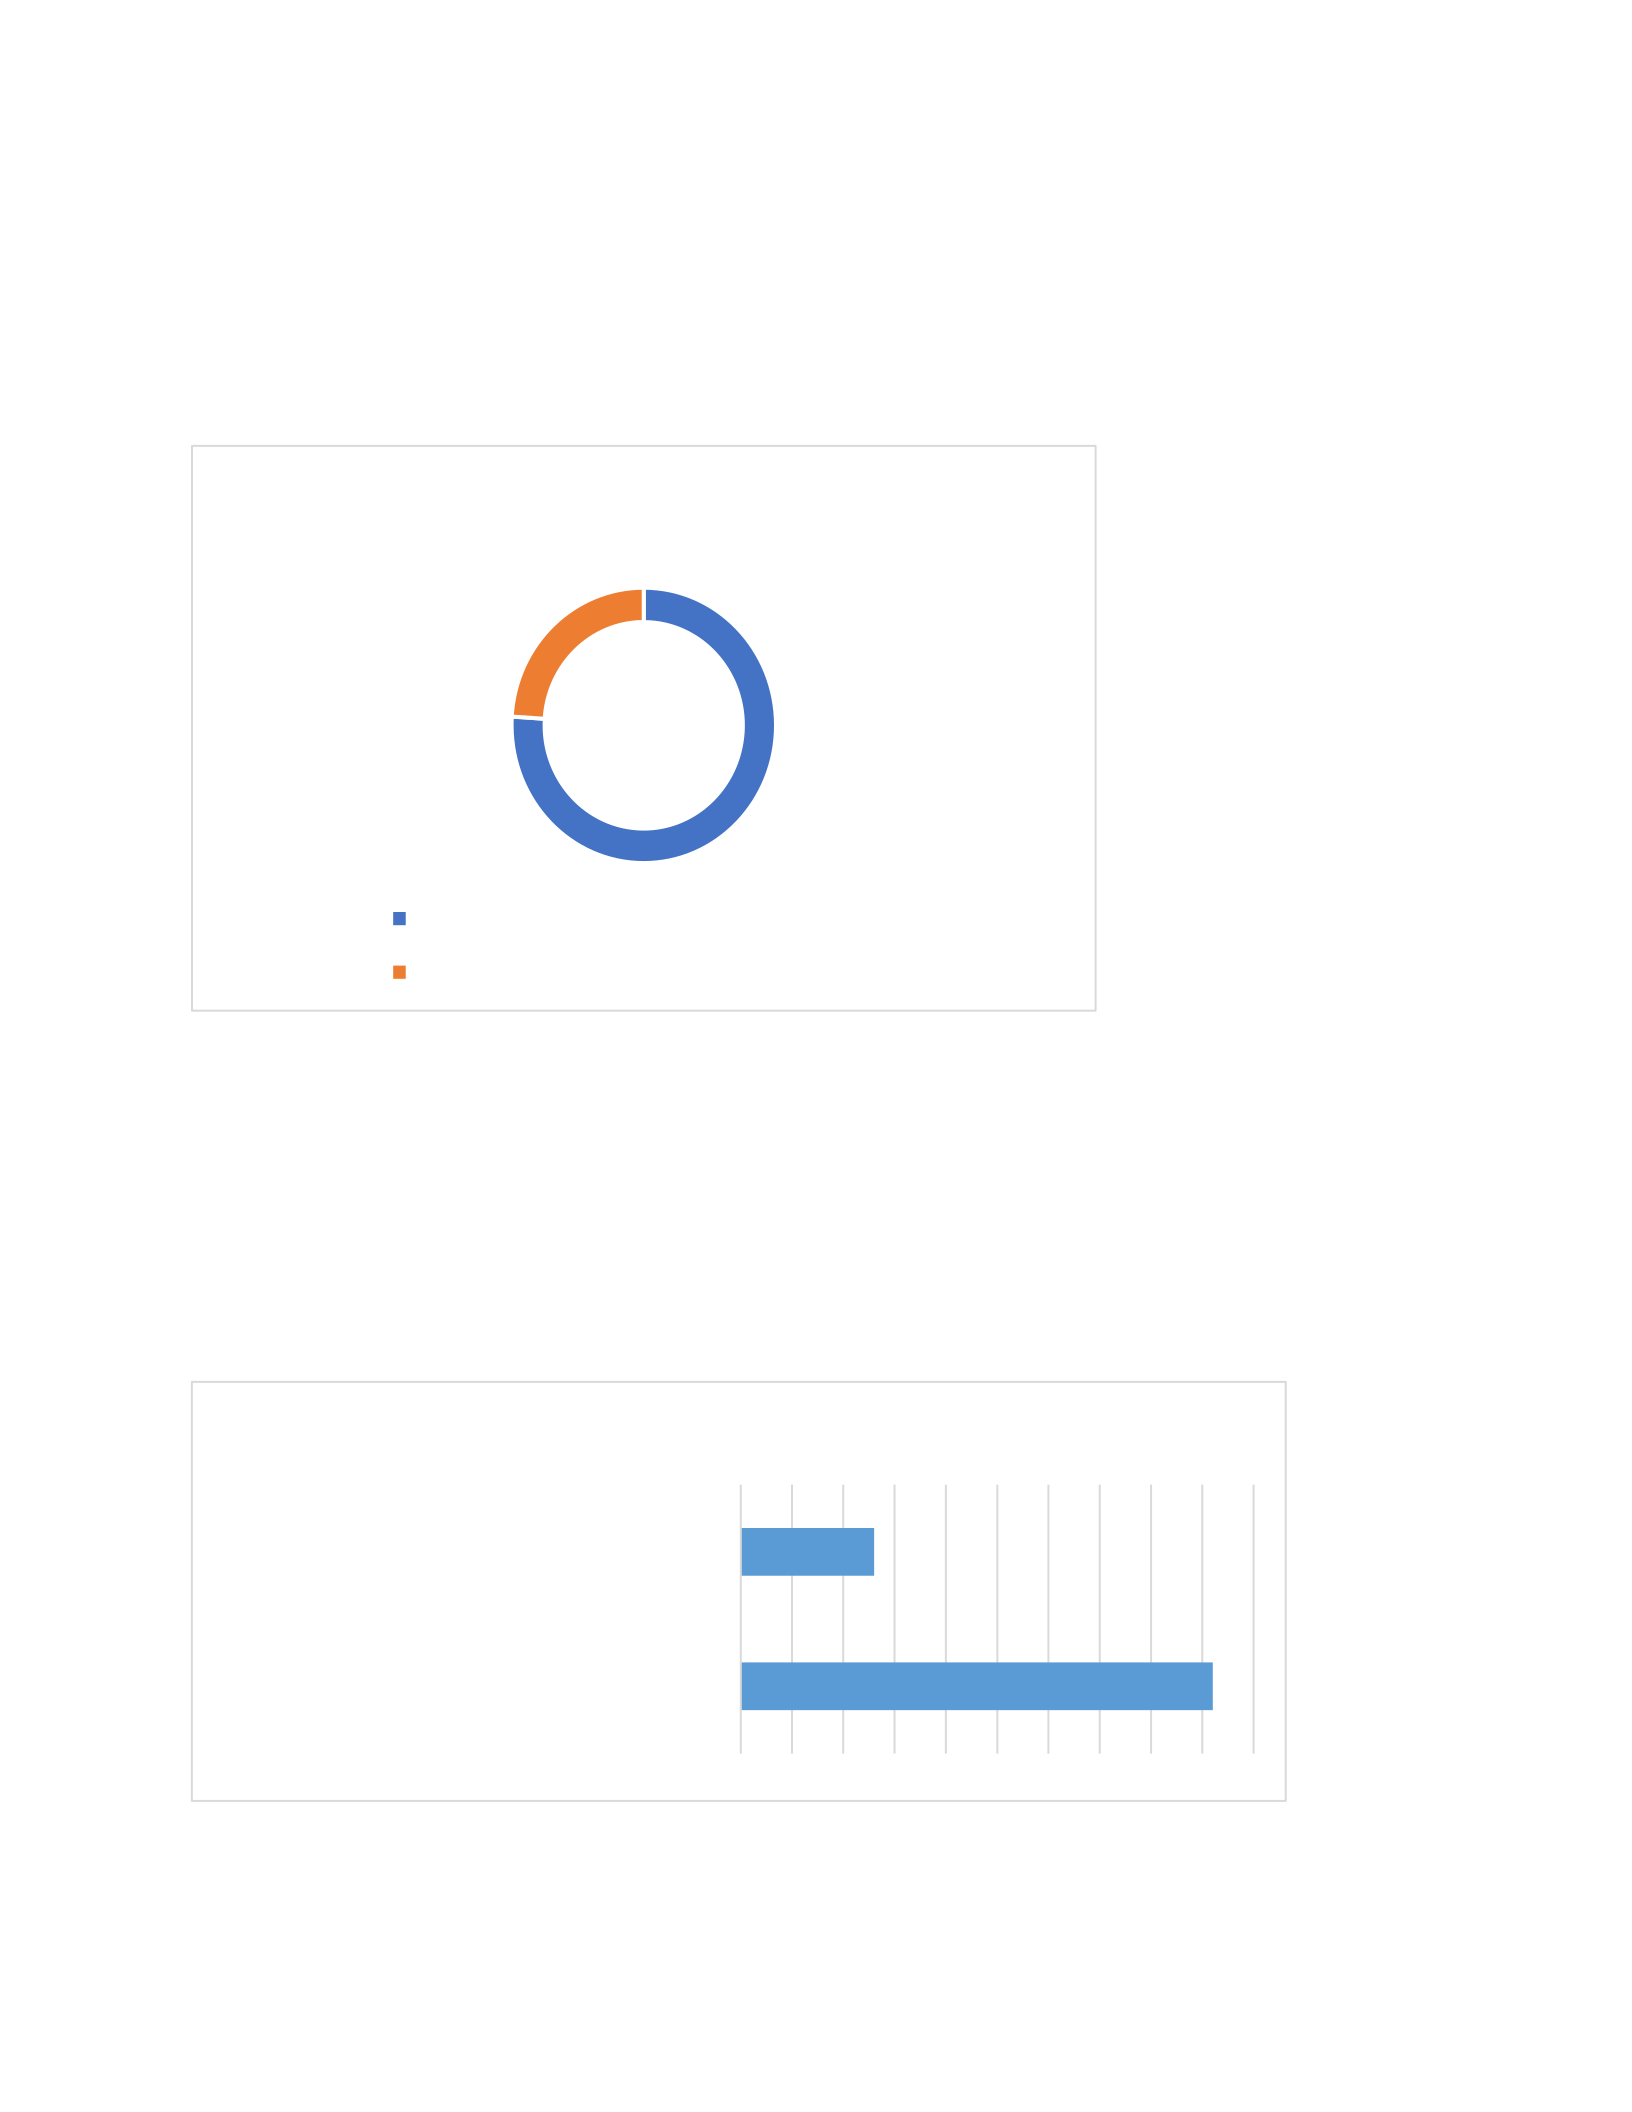
minimizing the risks of dependency on AI algorithms and automation. Figure 10 shows the
survey results from Lazic (2019) on AI-driven faster response to data breaches.
Figure 10 Survey of AI-Driven Faster Response to Breaches
Note. Recreated from Lazic (2019, p. 7).
Figure 11 shows the survey results from Lazic (2019) on AI-driven faster detection of data
breaches.
Figure 11 Survey of AI-Driven Faster Detection of Breaches
3 out of 4 Executives say AI enables faster
response to breaches
AI enables faster response to breaches
AI is NOT enabling response to breaches
46
13
0 5 10 15 20 25 30 35 40 45 50
Time reduced by 1 to 15 % to DETECT a
breach
Time reduced by more than 15% to DETECT a
breach
Organizations Reporing AI Reducing Time to Detect a Breach
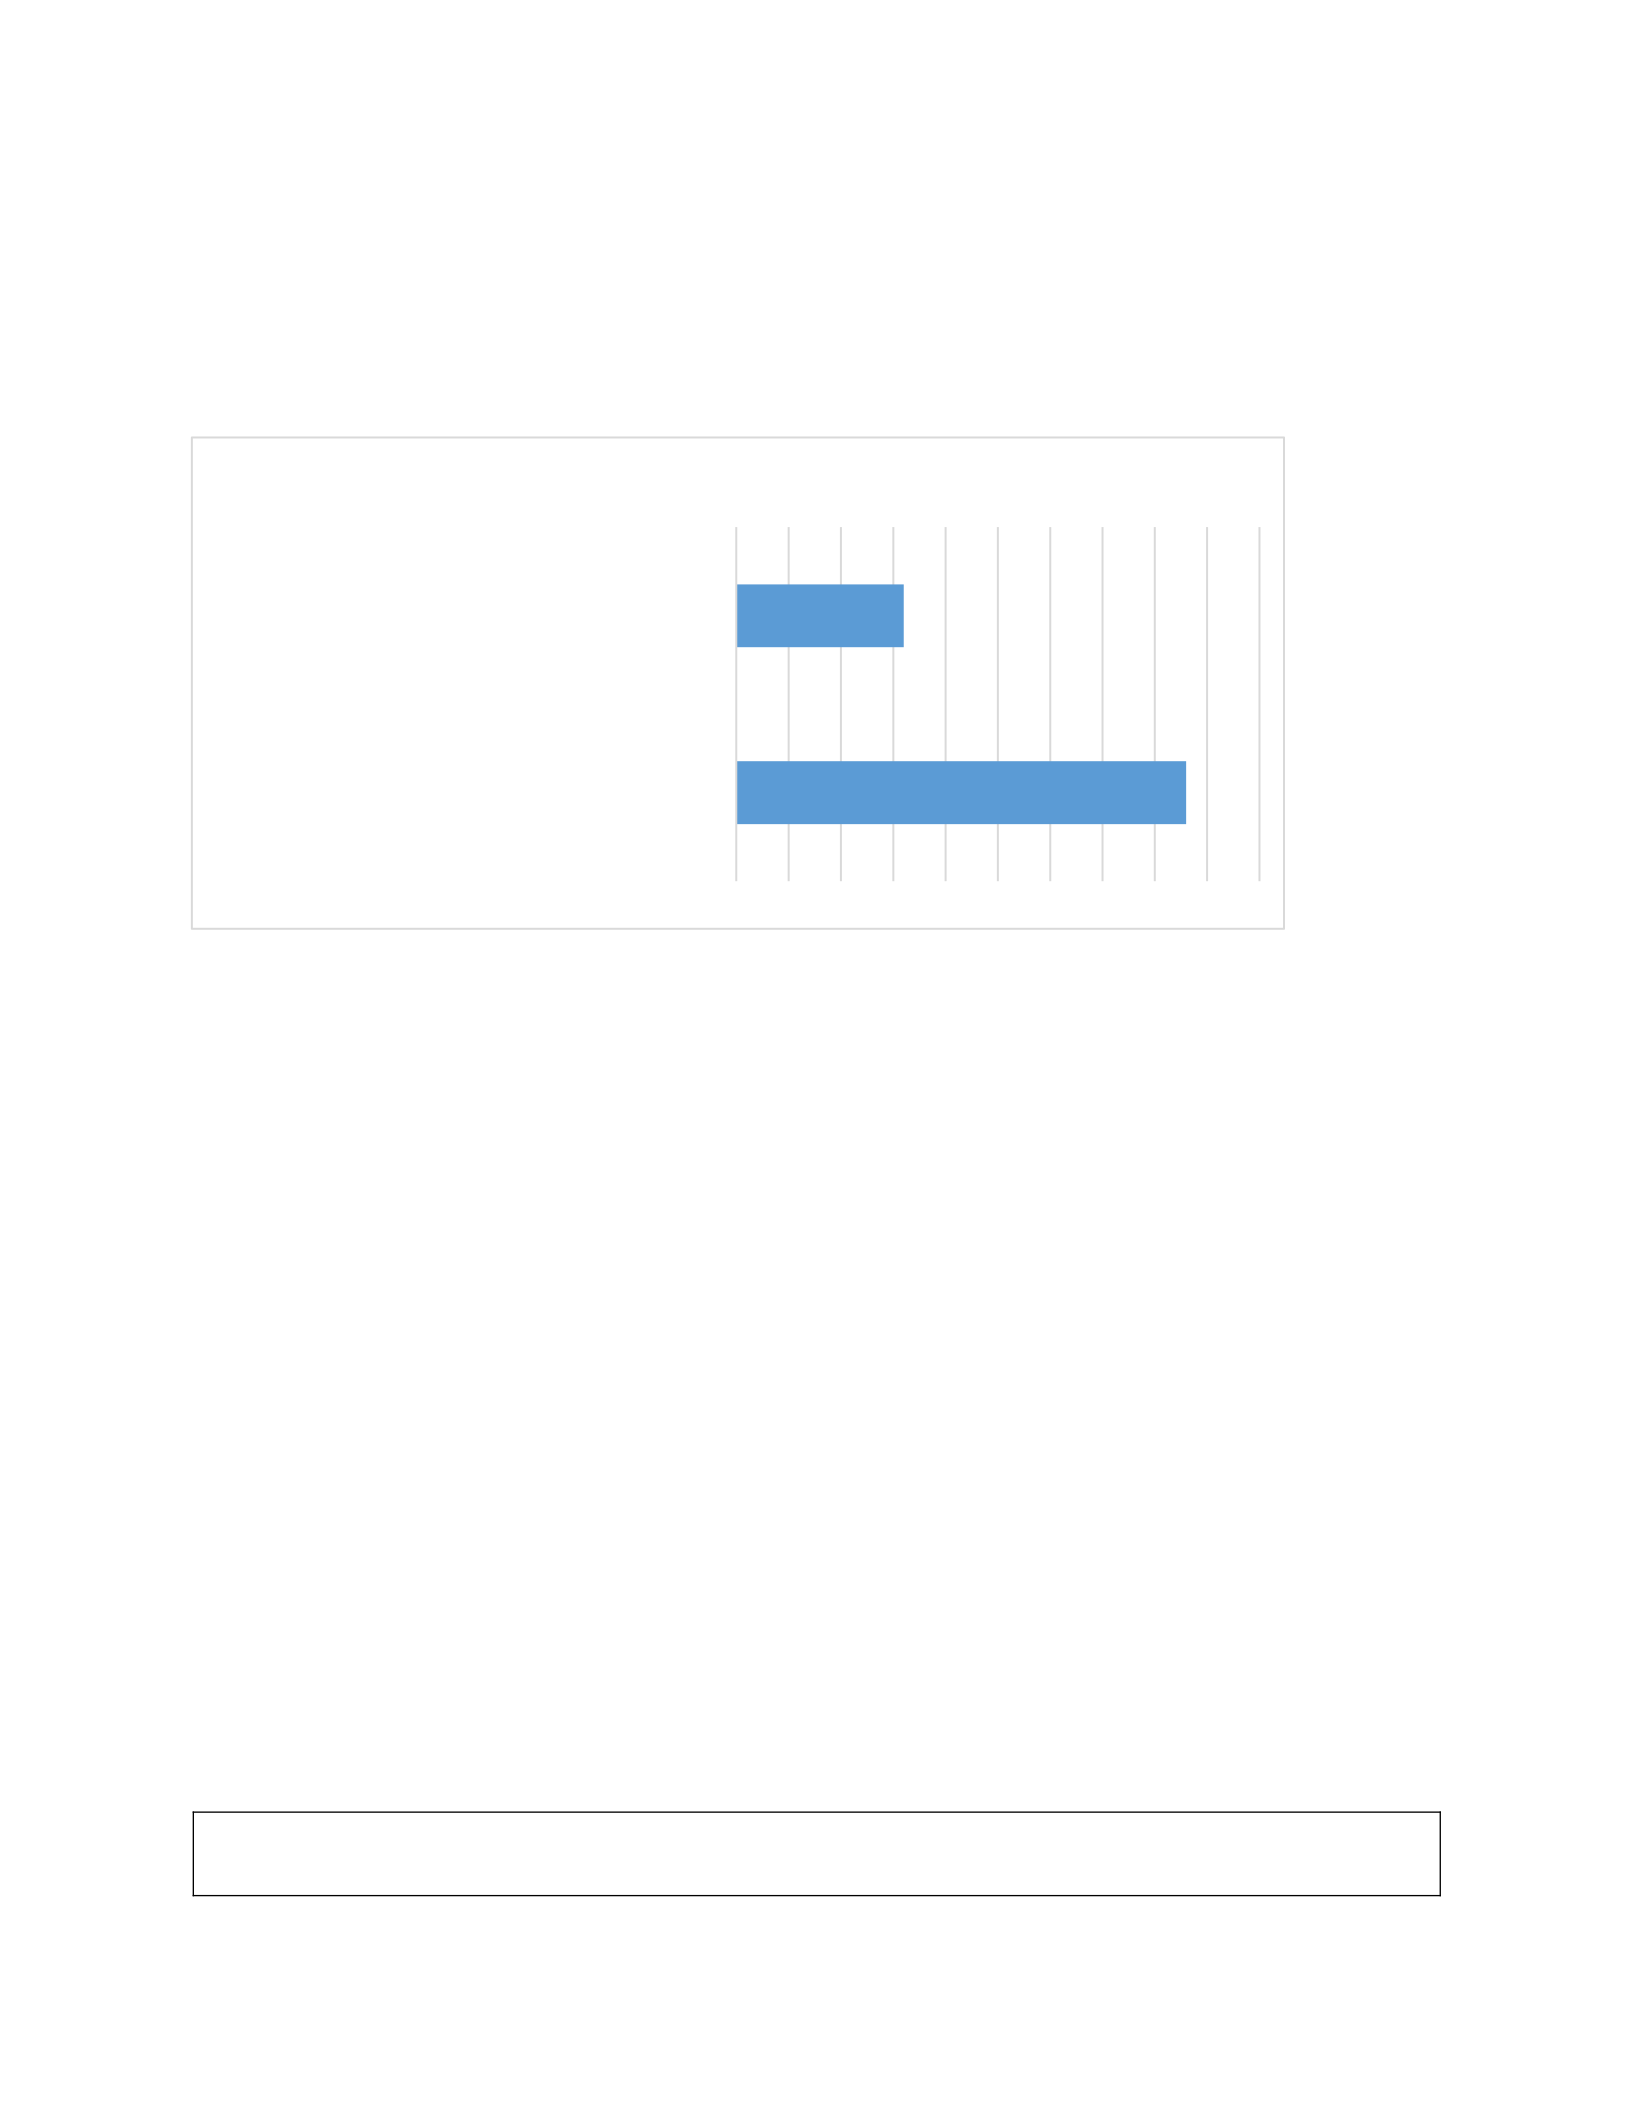
Figure 12 shows the survey results from Lazic (2019) on AI-driven faster remediation of
data breaches.
Figure 12 Survey of AI-Driven Faster Remediation of Breaches
Note. Recreated from Lazic (2019, p. 7).
Researchers have also studied machine learning algorithms, strengthening parts of
cybersecurity, such as spam email, intrusion, and malware detection. Studies also discuss how AI
techniques, such as natural language processing, machine learning, reinforced learning, deep
learning, and generative adversarial networks, can be applied to strengthen broad cybersecurity
topics such as prevention tasks, detection tasks, recovery and response tasks, and active cyber
defense.
Musser and Garriott (2021) discuss the timeline of machine learning's development for
spam, intrusion, and malware detection, referring to the periods (a) the pre-1990s, (b) the 1990s,
(c) the 2000s, and (d) the 2010s. Table 3 elaborates further on their findings.
Table 3 Timeline of Machine Learning Developments for Major Cybersecurity Tasks
Cybersecurity
task
Pre-1990s 1990s 2000s 2010s
43
16
0 5 10 15 20 25 30 35 40 45 50
Time reduced by 1 to 15 % to REMEDIATE a
breach
Time reduced by more than 15% to
REMEDIATE a breach
Organizations Reporting AI Reduced Time to Remediate a Breach
SPAM
detection
1978: First spam
email
Spam continues
to worsen due to
the growth in
email 1996:
First spam
blockers
2002: Machine
learning
methods first
proposed for
spam detection
2003: First
attempts to
regulate spam in
the
United States
Machine
learning spam
detection
widely
embedded in
email services
Emergence of
deep learning-
based classifiers
Intrusion
detection
1980: First
intrusion
detection systems
1986: Anomaly
detection systems
combine expert
rules and
statistical
analysis
Early 1990s:
Neural
networks for
anomaly
detection first
proposed
1999: DARPA
creates datasets
to study
intrusion
detection
systems
Machine
learning further
studied as a
possible tool for
misuse-based
and anomaly-
based intrusion
detection
Late 2010s:
Emergence
of large-scale,
cloud-based
intrusion
detection
systems Deep
learning
studied for
intrusion
detection
Malware
detection
Early 1980s: First
viruses found "in
the
wild"
Late 1980s: First
antivirus companies
founded
Early 1990s:
First
polymorphic
viruses
1996: IBM
begins studying
machine
learning for
malware
detection
Early 2000s:
First
metamorphic
viruses
A wide number
of traditional
machine learning
methods studied
to detect
malware
Rise of
"nextgen"
antivirus
detection
Emergence of
ML-focused
antivirus
companies
Note. From Machine Learning and Cybersecurity Hype and Reality Musser and Garriott (2021).
Furthermore, Musser and Garriott (2021) discuss their machine learning research for
cybersecurity, using a four-stage model for cybersecurity practice that includes (a) prevention, (b)
detection, (c) response and recovery, and (d) active defense. They identify the underlying

cybersecurity tasks for each stage and map each task against machine learning techniques such as
deep learning, reinforcement learning, natural language processing, traditional machine learning,
and generative adversarial networks. In addition to mapping, they also present the significance of
the AI technique and its transformative potential on the cybersecurity task.
Musser and Garriott (2021) break the prevention stage of their cybersecurity practice
model into the tasks of (a) fuzzing, (b) penetration testing, (c) bug triage and classification, and
(d) vulnerability severity assessment and match them against the AI techniques of (a) Deep
Learning, (b) Reinforcement Learning, (c) Natural Language Processing, and (d) Traditional
Machine Learning Methods. Figure 13 represents this.
Figure 13 AI Applications for Prevention
Note. Recreated from Machine Learning and Cybersecurity Hype and Reality Musser and
Garriott (2021).
Musser and Garriott (2021) break the detection stage of their cybersecurity practice
model into the tasks of (a) accurate detection, (b) alert prioritization, and (c) adversarial
hardening of detection systems and match them against the AI techniques of (a) deep learning,
and (b) generative adversarial networks. Figure 14 represents this.
CYBERSECURITY TASK UNDERLYING
TECHNOLOGY OF NEW
AI APPLICATIONS
SIGNIFICANCE OF TASK TRANSFORMATIVE
POTENTIAL OF NEW AI
Fuzzing Deep Learning High Medium-High
Penetration Testing
TASK
Reinforcement
Learning
High Medium-High
Bug Triage and
Classification
Natural Language
Processing, Traditional
Machine Learning
Methods
Medium Medium
Vulnerability Severity
Assessment
Natural Language
Processing, Traditional
Machine Learning
Methods
Medium Medium-Low
P D
R
R
A
D
Figure 14 AI Applications for Detection
Note. Recreated from Machine Learning and Cybersecurity Hype and Reality Musser and
Garriott (2021).
Musser and Garriott (2021) break the recovery and response stage of their cybersecurity
practice model into the tasks of (a) accurate detection, (b) alert prioritization, and (c) adversarial
hardening of detection systems and match them against the AI technique of reinforcement
learning. Figure 15 represents this.
CYBERSECURITY TASK UNDERLYING
TECHNOLOGY OF NEW
AI APPLICATIONS
SIGNIFICANCE OF TASK TRANSFORMATIVE
POTENTIAL OF NEW AI
Accurate Detection Deep Learning High Low
Alert Prioritization
TASK
Deep Learning Medium-High Medium
Adversarial Hardening
of Detection Systems
Generative Adversarial
Networks
Medium-High Medium-Low
P D
R
R
A
D
Figure 15 AI Applications for Recovery and Response
Note. Recreated from Machine Learning and Cybersecurity Hype and Reality Musser and
Garriott (2021).
Musser and Garriott (2021) break the active defense stage of their cybersecurity practice
model into the tasks of (a) deceptive document generation, (b) dynamic honey potting, (c)
automated phishing response, (d) dark web threat intelligence, (e) attack clustering for
attribution, and (f) code de-anonymization and match them against the AI techniques of (a)
natural language processing, (b) generative adversarial networks, (c) reinforcement learning, and
(d) traditional machine learning methods. Figure 16 represents this.
CYBERSECURITY TASK UNDERLYING
TECHNOLOGY OF NEW
AI APPLICATIONS
SIGNIFICANCE OF TASK TRANSFORMATIVE
POTENTIAL OF NEW AI
Adversary Engagement Reinforcement
Learning
High Medium-High
Moving Target Defense Reinforcement
Learning
High Medium-High
P D
R
R
A
D
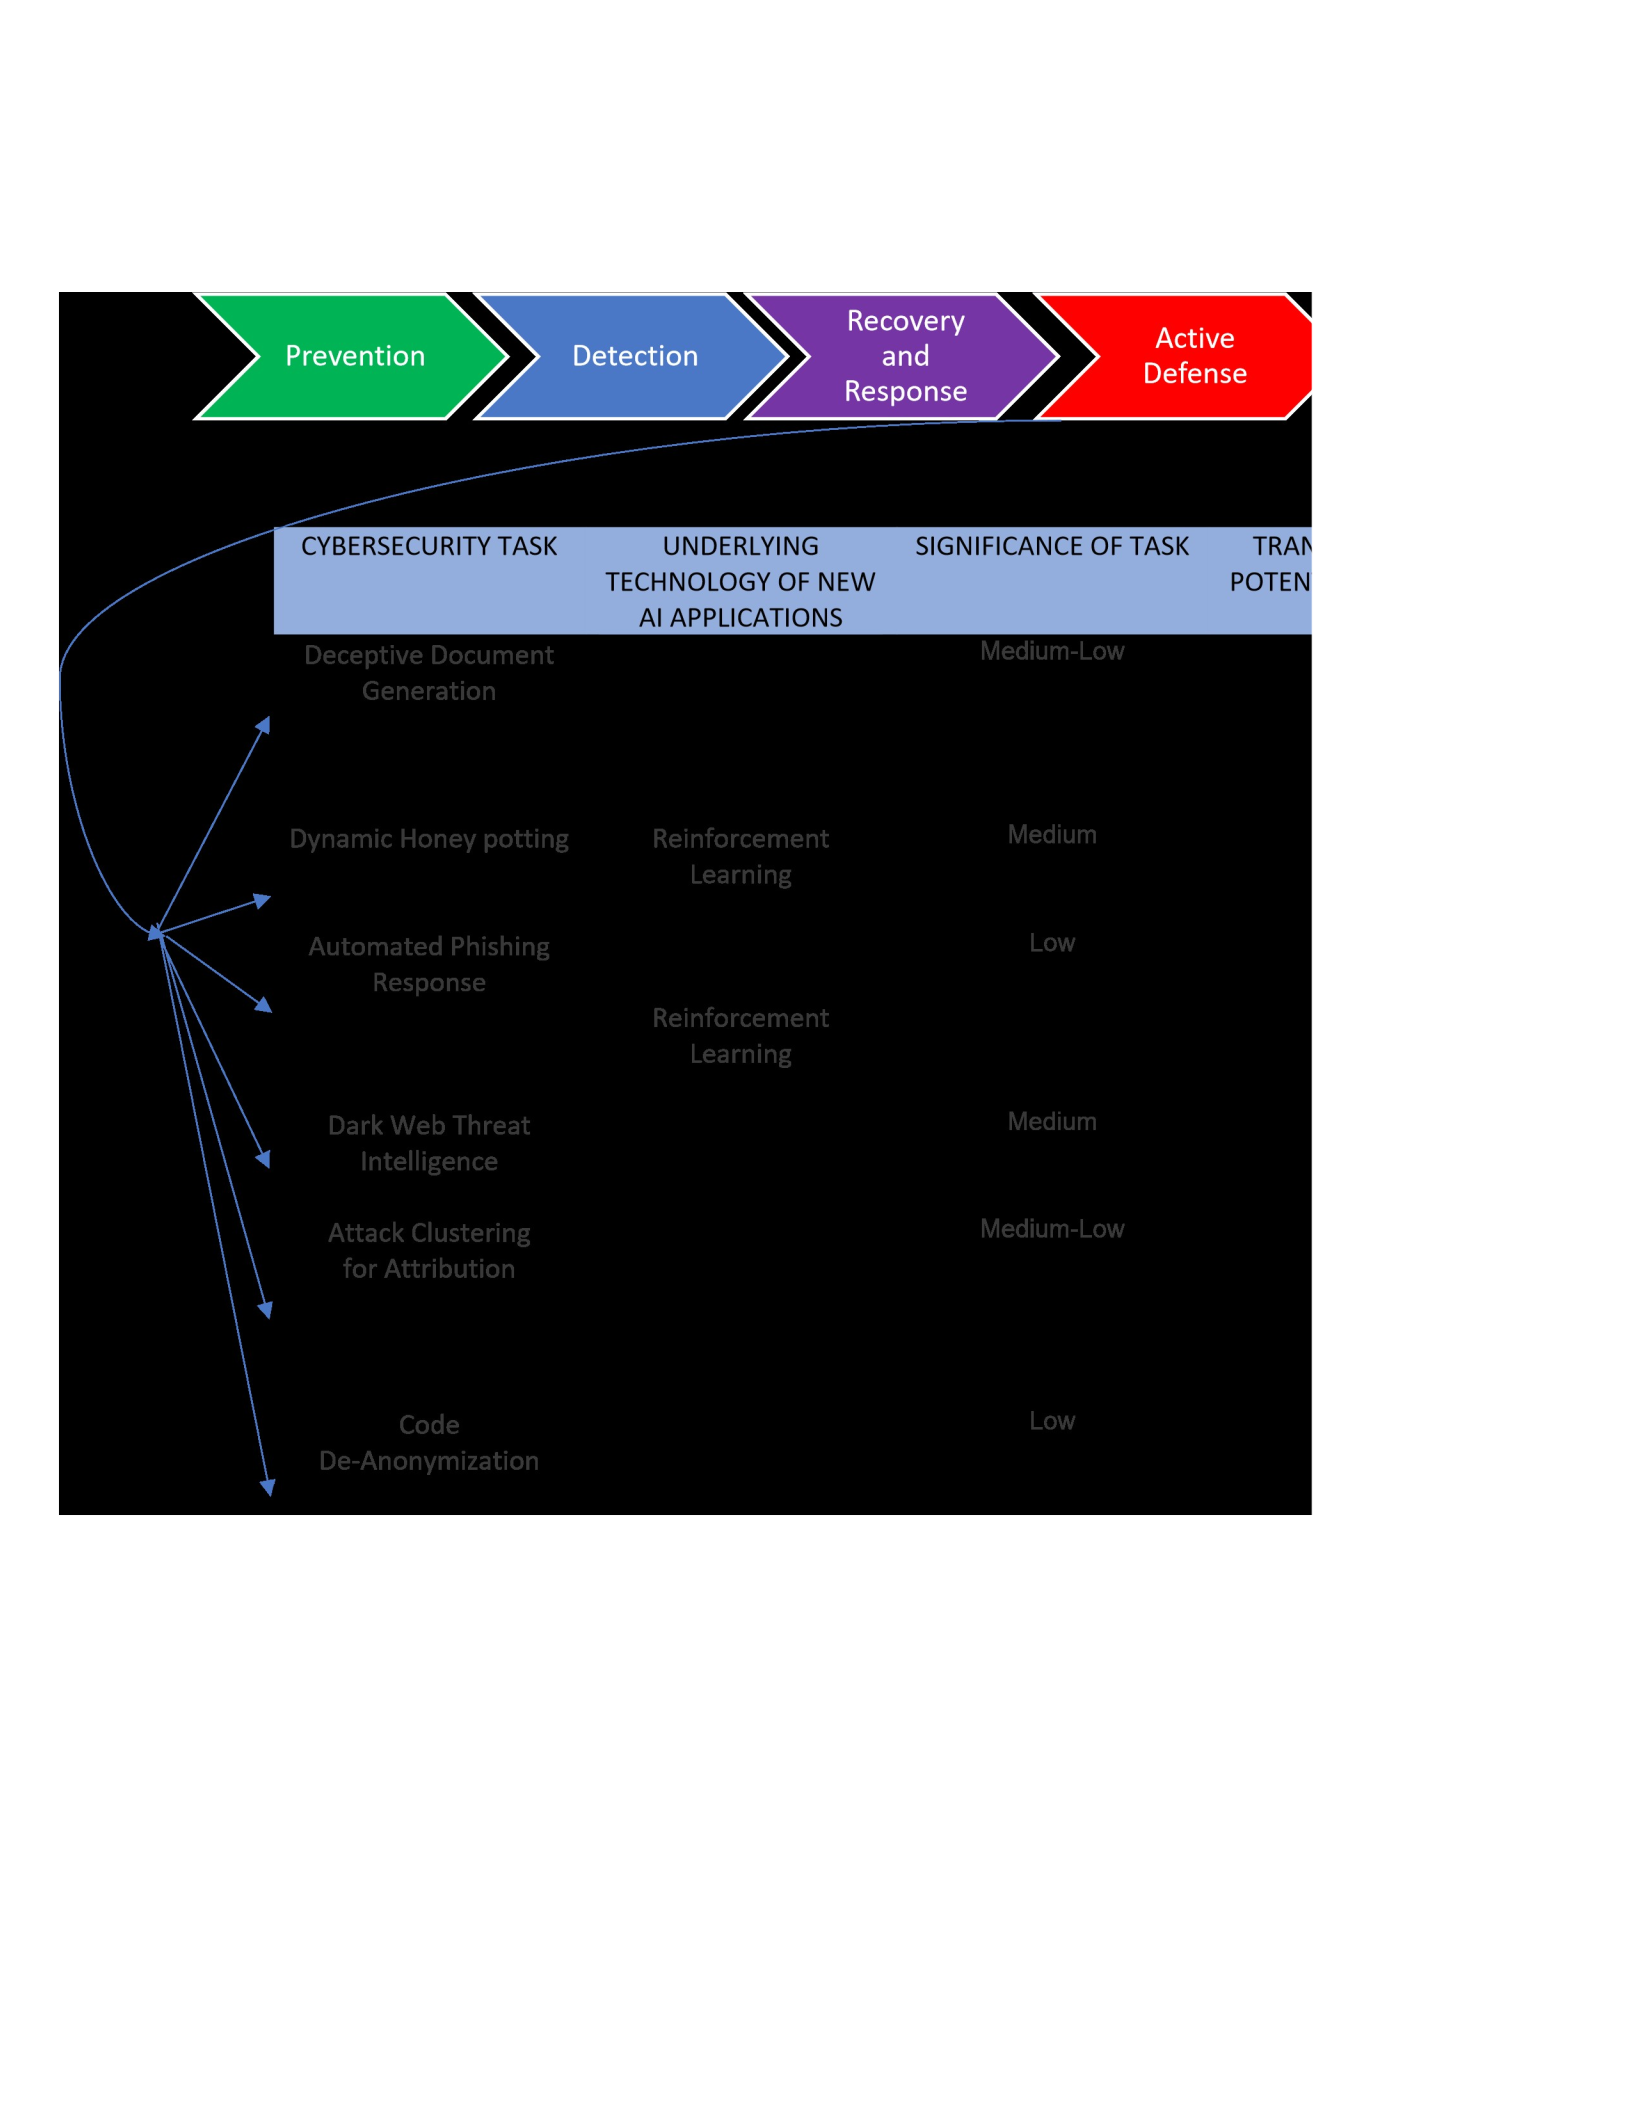
Figure 16 AI Applications for Active Defense
Note. Recreated from Machine Learning and Cybersecurity Hype and Reality Musser and
Garriott (2021).
Studies on Research Design and Methodologies
Explanations and studies related to research methodologies and methods were reviewed
to select an appropriate method for this dissertation. Creswell's "Educational Research: Planning,
conducting and Evaluating Quantitative and Qualitative Research" provides comprehensive
guidelines and explanations on problem selection, literature review, quantitative method,
qualitative method, data collection, analysis, interpretation, evaluation, and reporting (Creswell,
2018).
Curry's videos provide fundamentals of the qualitative method and explain its
components, such as developing questions, interviews, surveys, focus groups, and steps for
ensuring scientific rigor (Curry, 2015; Curry, 2018a; Curry, 2018b; Curry, 2018c; Curry, 2018d;
Curry, 2019). In addition, Kriukow’s videos explain the details of qualitative research methods,
including negative case analysis, ensuring validity and credibility, sampling, audit trails, and the
differences between grounded theory and phenomenology (Kriukow, 2019; Kriukow, 2021;
Kriukow, 2022a; Kriukow, 2022b).
Moerman defines ontology and epistemology and explains the fundamentals of grounded
theory and its multiple versions (Moerman, 2016a; Moerman, 2016b; Moerman, 2016c;
Moerman, 2016d; Moerman, 2016e; Moerman, 2016f). Tomaszewski et al. (2020) provide new
researcher definitions and elaborations on qualitative research, narrative, ethnography,
phenomenology, case studies, and methodological comparisons. Table 4 depicts the explanations
of Tomaszewski et al. (2020).
Table 4 Comparison of Qualitative Research Approaches
Case Study Ethnography Narrative Phenomenology
Goals
Describe
cases/cases to
develop an indepth
understanding of the
context of specific
cases/ cases.
Describe a
specific group of
people's shared
and learned
cultural practices
(culture).
Describe the
stories people tell
about their lives
and lived
experiences.
Describe the
meaning of the
lived experiences
of a phenomenon
by the people who
lived it.
Formulating
Research
Questions
What are the
qualities/
characteristics of
the unique/
representative case?
What are the
shared practices
of the culture?
What is the story
of the lived
experience?
What is the
essence of the
phenomenon of
interest?
Sampling
People with roles
within the case's
boundaries/criteria/
context.
People who
participate in or
experience the
culture of
interest.
People who
contribute to the
story of the
experience.
People who have
lived the
phenomenon of
interest.
Data Collection
One-on-one
Interviews or Focus
groups in which
participants
describe the case.
Observations of
participants in the
context of the case
being studied.
Observations of the
setting(s) where the
case(s) occur.
Documents
(physical or
One-on-one
Interviews or
Focus groups in
which
participants
describe the
culture.
Observations of
participants in the
context of their
culture.
Observations of
the cultural
setting.
Documents
(physical or
digital) that are
One-on-one
Interviews in
which
participants tell
a story about
their experience.
Observations of
participants
during
storytelling or
enactment of the
story.
Documents
(physical or
digital) that are
One-on-one
Interviews or
Focus Groups in
which participants
describe the
experience
Observations of
the phenomena of
interest.
Documents
(physical or
Case Study Ethnography Narrative Phenomenology
digital) represent the
case(s).
representative of
the culture.
representative of
the narrative.
digital) that are
representative of
the phenomena.
Data Analysis
Constant
comparative;
Thematic.
Constant
comparative;
Thematic.
Narrative
analysis.
Phenomenological
analysis.
Note. Extracted from Planning qualitative research: Design and decision making for new
researchers by Tomaszewski et al. (2020, p. 2).

Chapter 3: Research Method
Research Design
Analysis
The literature review of this research shows that (a) AI techniques such as machine
learning, deep learning, and neural networks continue to grow in scale and capabilities; (b)
Increasingly, AI applications are penetrating the functions of government, military, and
industries; and (c) there is a global competition in progress for leadership in AI. In addition, the
literature review also shows that AI techniques, when fully harnessed, can strengthen
cybersecurity and that the availability of cybersecurity expertise with AI skills can expedite that
process. According to Cresswell (2018), "Qualitative research is best suited to addressing a
research problem in which you do not know the variables and need to explore" (p. 16). Cresswell
(2018) further adds that qualitative research literature review identifies the need to study the
research problem rather than providing primary research directions, and the research is about
learning from the participants.
Qualitative Method
The primary objective of this research is to explore and identify the factors that influence
adding AI skills to the U.S. cybersecurity workforce. It will provide insights for the U.S.
cybersecurity workforce to be equipped with AI skills, resulting in more robust cybersecurity.
Due to the explorative nature of the research, the research design will use qualitative methods to
understand the phenomenon from the participants- practicing U.S. cybersecurity professionals.
In-depth one-on-one interviews with the participants will primarily collect data about the
phenomenon of interest (Cresswell, 2018; Curry, 2018c; Kriukow, 2022b). Semi-structured
questions about the phenomenon of interest will be used to initiate the one-on-one interviews.
Questions that imply a directive or judgments will be avoided to minimize researcher bias.
Grounded Theory
Researchers refer to multiple qualitative methodologies. For example, Kriukow (2021a)
mentions (a) Phenomenology, (b) Narrative, (c) Ethnography, (d) Grounded Theory, and (e) Case
study as the five key qualitative research methodologies. Elaborating further on the
methodologies, Kirukow (2021a) lists them with key attributes: (a) Phenomenology- The
researcher selects a group of people who have experienced a particular phenomenon and gathers
details of their experience; (b) Narratives- The researcher, believing that knowledge is embedded
in stories, interacts with a few participants, and gathers stories about a single event or their whole
life; (c) Ethnography- The researcher is often fully immersed in the culture of those studied and
studies people in their natural settings through observations and open-ended interviews; (d)
Grounded Theory- The researcher explores an under-researched phenomenon and derives
detailed explanations from the collected data. It has similarities to Phenomenology through
typically using a larger sample size, and (e) Case Study- The researcher gathers details about a
single case to address a specific problem of interest.
Researchers compare Grounded Theory with Phenomenology. For example (Burns et al.
(2022) compare grounded theory with phenomenology based on the attributes of (a) Ontology,
(b) Epistemology, (c) Nature of research questions, (d) Data analysis techniques used, (e) Type of
findings; and (f) Limitations. Table 5 depicts the details of this comparison.
Table 5 Comparison of Methodologies- Grounded Theory and Phenomenology
Methodology
Grounded Theory Phenomenology
Ontology Truth is comprised of multiple realities.
Epistemology
Subjective value-relative and value mediated.
Researchers seek inter-subjectivity, shared subjective
awareness, and understanding within research
relationships. Knowledge is co-constructed and
constantly revised.
Research Questions
Focus on social processes, such
as how individuals cope,
navigate, and adapt to
phenomena.
Focus on meanings of
lived experiences of
phenomena.
Data Analysis
Coding, constant comparison,
memos, theoretical sampling.
Explore what lies
beneath this
experience, enhancing
our understanding of
the participant's being
in the world.
Findings Substantive Theory Narrative Life-worlds
Strengths
Multiple realities allow for
holistic view
Enhanced appreciation for the
multiple possible meanings of
experience
Good for exploratory study
Supports individualized care
Shared meanings constructed in
natural environments—
contextspecific
Enhanced appreciation
for the multiple
possible meanings of
Experience. Supports
individualized care.
The narrative is a call
to action for positive
change.
Methodology
Grounded Theory Phenomenology
Limitations
The middle-range theory offers
some explanatory power that is
context-specific.
Multiple meanings.
Descriptive.
May need to go beyond to test the
theory.
Context-specific Does
not provide specific,
standardized
recommendations for
practice.
Note. Extracted from Constructivist Grounded Theory or Interpretive Phenomenology?
Methodological Choices Within Specific Study Contexts by Burns et al. (2022).
According to Charmaz (2017), grounded theory shaped the development of qualitative
research and could result mainly in inductive findings emerging from the data analysis. In
addition, Charmaz (2017) also mentions that in a few exceptional cases, abductive deductions
that are probabilistic findings are also likely. Kriukow (2020c) describes grounded theory as a
suitable methodology for under-studied phenomena of interest when limited information is
available from prior studies. He adds that findings emerge from data in grounded theory without
prior hypotheses, theorems, and metrics.
The phenomenon of interest for this research is the factors that influence adding AI skills
to the U.S. cybersecurity workforce. This phenomenon has not been thoroughly researched, and
pre-existing hypotheses and metrics are unavailable. Hence, this research design will use a
qualitative grounded theory methodology to deeply understand the phenomenon, grounded on the
data collected from the study participants. A purposeful sampling of participants of practicing
professionals of the U.S. cybersecurity workforce will be selected and interviewed to collect
data.
Qualitative Grounded Theory Approach
Current research findings on the factors that influence adding AI skills to the U.S.

cybersecurity workforce are limited, and theories and attributes about this phenomenon are
absent. Therefore, there is a need to explore and identify the phenomenon's attributes, and a
qualitative study where the researcher learns from the participants is better suited for such a
situation (Creswell, 2018, p. 16). Furthermore, due to the lack of current theories, hypotheses,
and structures related to the proposed research problem, top-down and deductive research
methods are less suitable than qualitative inductive ones.
Using in-depth interviews, focus groups, observation, and document review is appropriate
for qualitative study designs (Curry, 2018c). In addition, the grounded theory approach, as
applied to qualitative methods, potentially generates a broad theory about the qualitative
phenomenon of research (Creswell, 2018, p. 422; Gramenz, 2017; Moerman, 2016a). This study
will explore adding AI skills without pre-existing theories, potentially aiming to inductively build
concepts and theories grounded in the researcher's interpretations of the participants' views.
During the interviews, the terms from published AI taxonomy will refer to the components of AI
consistently. For example, Samoli et al. (2020) propose an AI taxonomy to help researchers and
industrial computer system developers categorize their AI-related activities. It includes AI
terminologies related to its scientific, technical, ethical, and philosophical aspects and is
presented in Table 6.
Table 6
Computer vision
Perception
Audio processing
Multi-agent systems
Robotics and Automation
Integration and Interaction
Transversal
AI Ethics
AI Taxonomy - Terminologies for Interviews
AI Taxonomy
AI domain AI subdomain
Core
Reasoning
Knowledge representation
Automated reasoning
Common sense reasoning
Planning
Planning and Scheduling
Searching
Optimization
Learning Machine learning
Communication Natural language processing
Connected and Automated
vehicles
Services AI Services
Ethics and Philosophy
Philosophy of AI
Note: Recreated from AI Watch Defining Artificial Intelligence Samoli et al. (2020).
Data Collection and Analysis
Based on the nature of the phenomenon of interest and the attributes of qualitative study
design options, this study will utilize in-depth interviews to collect rich data and the grounded
theory approach to that data. The open-ended and non-directional primary research question will
initiate the in-depth interviews. Furthermore, the study will use the qualitative practices and
guidelines described by other researchers and professors ( Creswell, 2018; Gramenz, 2017;
Curry, 2019; Curry, 2018a; Curry, 2018c; Curry, 2018b; Curry, 2018d; Moerman, 2016a):
Individual cybersecurity professionals living and working in the United States who are members
of the U.S. cybersecurity workforce will be the unit of analysis; Participant selection will be
purposeful; the objective would be to identify professionals with rich information close to the
phenomenon of interest; The study participants would be employed U.S. professionals with over
six years of cybersecurity experience and recognized cybersecurity certifications; Data collection
and analysis will be concurrent, through constant comparisons, and iterative. The analysis will
involve coding and consolidating codes into concepts and themes. When deviant data, also called
outliers, are identified, they will be analyzed to strengthen the finding; justification will be
provided for rejected ones; Validations will be through checking recorded views with the
participants who provided them (member checking); triangulation will be used only as a second
validation technique; Questions during the one-on-one interviews will be general and
nondirectional to obtain in-depth information, views, experiences, and perceptions; Interviews
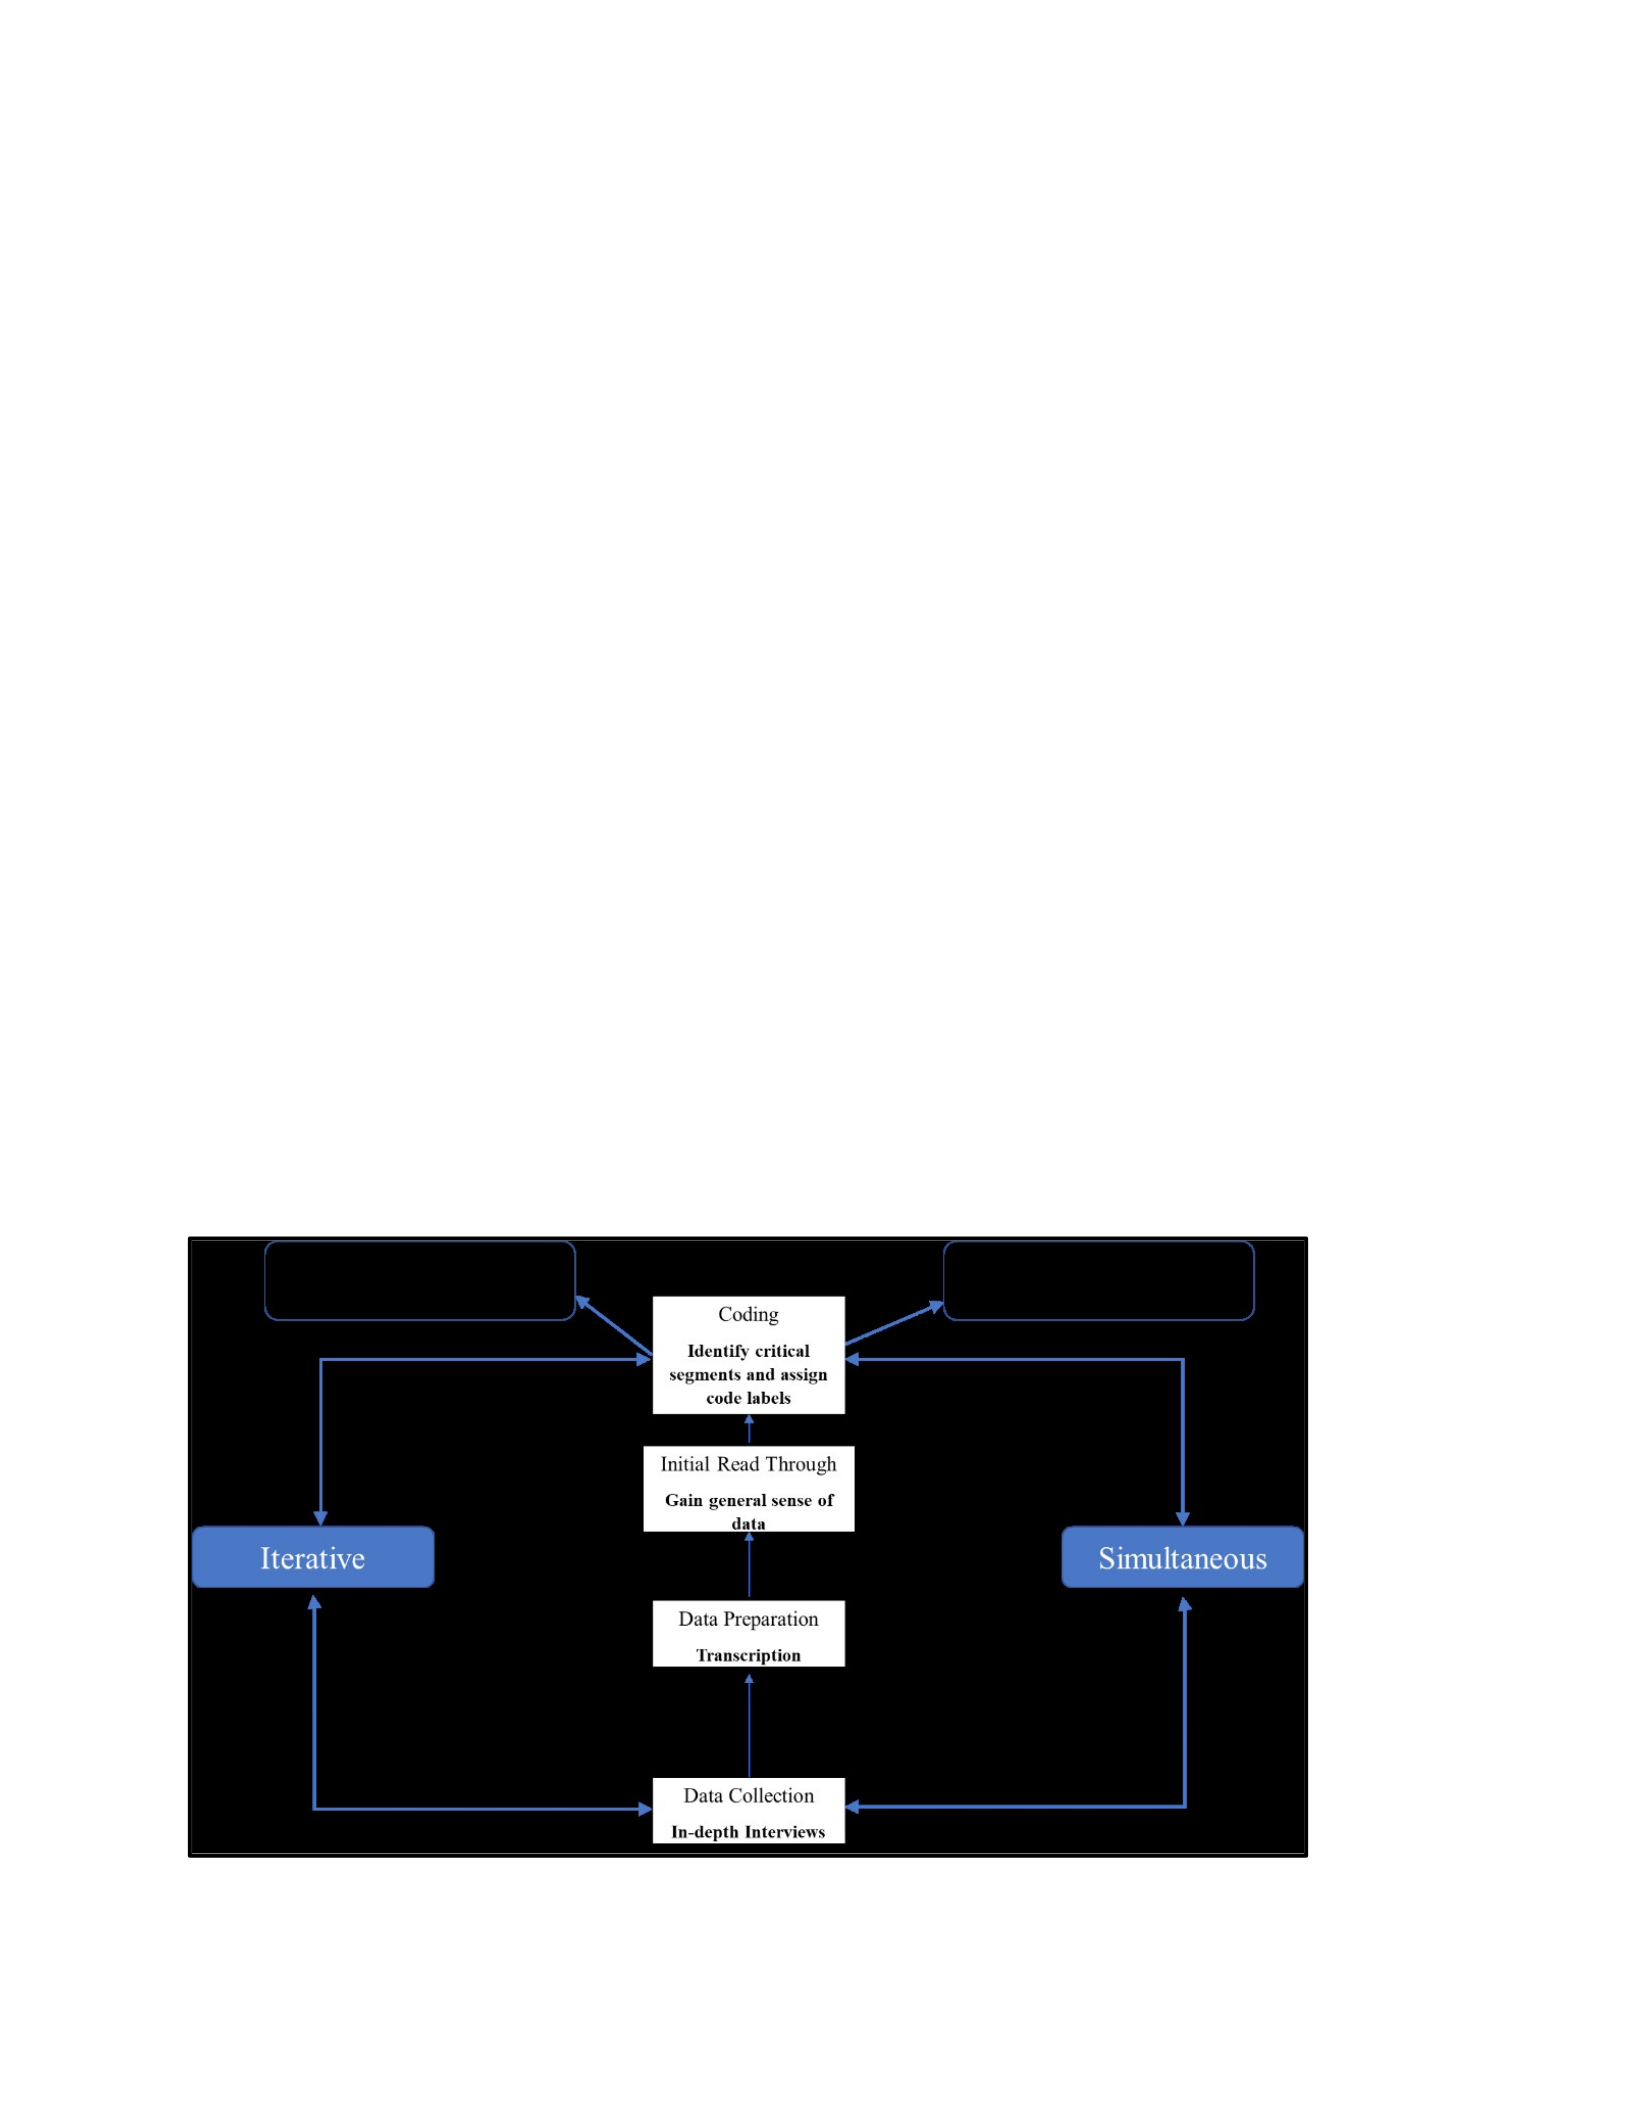
will be conducted in a natural, non-work setting comfortable for the participants; The identity of
the participants will be strictly confidential. The interviewer will reinforce this at the start of each
interview. The study will begin with an initial set of questions for the first round of in-depth
oneon-one interviews; the subsequent questions will be based on analyzing the participant
responses from the earlier rounds, and The depth of the interviewer's questions will be limited to
clarify a participant's response or obtain richer information from a response.
The proposed qualitative study would refer to the presently available guidelines on the
grounded theory approach. For example, Gramenz (2017) describes a qualitative grounded
theory approach involving in-depth interviews resulting in interview transcripts, assigning codes
to represent prominent and essential segments of the transcripts, and an iterative process to
compare codes from multiple transcripts for consistency coding. In parallel with this iterative
process, the codes are also categorized following the primary research question. Figure 17
depicts the process described by Gramenz (2017).
Figure 17 A Process Schematic for Grounded Theory Approach
Note.
Recreated from the work of Gramenz (2017).

Stages of Coding
When using grounded theory methodology, with in-depth interviews as the data collection
method, the codes that denote and summarize critical elements of the resulting interview
transcripts are inductively built from the data without deduction from an initial set (Delve, 2021).
Coding is an essential practice in grounded theory research, and it arises from the researcher’s
interaction with the data. According to Charmaz (2011; as cited in Mohajan &
Mohajan, 2022b), codes are shorthand labels and phrases that define the meaning of a piece of
data. Researchers recommend three phases of coding in grounded theory research that consist of
(a) initial or open coding, (b) focused or axial coding, and (c) selective or theoretical coding
(Strauss & Corbin, 1998; Charmaz, 2006, 2014; Saldaña, 2016; as cited in Mohajan & Mohajan,
2022b).
The first stage of coding, open coding, is where the researcher identifies significant
concepts in the data, assigns labels to specific pieces of data, and assigns preliminary categories
to these labels based on the attributes of the datum. In this stage, the researcher makes initial
connections with categories (Creswell, 2007; as cited in Mohajan & Mohajan, 2022b).
During the second axial coding stage, the researcher investigates the relationships
between concepts and categories identified in the open coding process (Strauss & Corbin, 1990;
as cited in Mohajan & Mohajan, 2022b). Axial coding is constructing data relationships between
and within categories (Creswell, 2007; as cited in Mohajan & Mohajan, 2022b). During this
stage, the data is organized into hierarchical categories and sub-categories (Noble & Mitchell,
2016; as cited in Mohajan & Mohajan, 2022b).
In the third stage of coding, termed selective coding, a dominant core thematic category is
selected, and its relationship to other categories is developed during the axial coding (Linneberg
& Korsgaard, 2019; as cited in Mohajan & Mohajan, 2022b). According to Strauss and Corbin,
the creators of grounded theory, selective coding is “the process of integrating and refining
categories” (Strauss & Corbin, 1998; as cited in Mohajan & Mohajan, 2022b, p. 14).
A simplified linear schematic of grounded theory with its three stages of coding is shown
in Figure 18.
Figure 18 Linear Flowchart of Qualitative Grounded Theory Research
Note. Recreated from Williams & Moser (2019; as cited in Mohajan & Mohajan, 2022b, p. 15).
This research will use the three stages of coding recommended and explained by multiple
researchers on grounded theory (Strauss & Corbin, 1998; Charmaz, 2006, 2014; Saldaña, 2016;
as cited in Mohajan & Mohajan, 2022b ). In addition, it will implement the stages of coding
using Microsoft Word as the primary tool of choice. Kriukow (2020a) describes the specifics of
coding using Microsoft Word as the primary tool of choice and defines a process for (a) code
creation from interview transcripts, (b) code comparison and iterative refinement, and (c) code
categorization into hierarchical categories and sub-categories. Figures 19 and 20 show two
sample interview transcripts with codes. Figure 21 shows a sample comparison of codes from
two interview transcripts, and Figure 22 shows the iterative code refinement process described by
Kriukow (2020a). Figure 23 shows an example of stage three coding described by Kriukow
(2020b). Q Research – Interview transcript and coding
D
C
Analysis
S 1:
O Coding
S 2:
A Coding
S 3:
S
C
T
D
C a
G
T
Figure 19 Sample Transcript-1 Qualitative Research Coding using MS-WORD
E of an Int T ; ID: 3-29-C1 Candida :
#1
L : Gaithersbur , M , Public library
F : In-person
D method: audio re and written notes
D a Time: March 29, 2023, 10:00 AM t 11:30 AM US EST
Example of Codes
ID: 3-29-C1
Created: 3/29/2023
Revised: 3/30/2023
AI- cyber requir compet rela t data. I
year , science beco an inter field using scientific
to e knowledge and insigh from . T demand f
- abilities points to the need f AI- cyber
to comb thro va amounts o collected d t help identify
o persi thr .
I re year , Artificial Intelligence (AI) has been g a central s
influencing the discussions o cybersecurity pol and prof .
H , term ma hav d m while widely used, as no
accepted defi of AI e . Hence, it poses a chall to es
rol in cybersec .
"Abilities in data
science" enables
cybersecurity
professionals to
utilize AI better.
“Availability of big
data” for
cybersecurity helps
insights from data.
"The lack of a
universally
acceptable
definition of AI
challenges AI's role
in cybersecurity.
Note. Created from Kriukow (2020a).
Figure 20 Sample Transcript-2 Qualitative Research Coding using MS-WORD
E o an Interview T ; ID: 4-2-C2
C : #2
L : T Corner, V , Office con r
Example of
Codes
ID: 4-2-C2
F : In-person
D method: audio re and written notes
D a Time: April 2, 2023, 2:00 PM to 3:30 PM US EST
Created:
4/2/2023
Revised:
4/4/2023
S rela to pro languages such as C++, J Script,
JAVA, P are when applying AI techniques (or building AI-
tools) to task . Furthermore, when applying AI e
cyber ta , compet tend to be gr around softwar
technology, well as sy administr and support.
A
skill group also emerg around s tools, co ,
risk mitig ; the mos fr skills f AI cybersecurity,
languages, rela to mach learning, science,
processing, neur networks,
/mining/visualiz .
C data sk can enable semi-aut AI-enab
proc for cybersecurity, as web scraping, audit log
, e judgment, a te mining.
“Skills in
machine
learning, data
science,
natural
language
processing” are
vital for
applying AI in
cybersecurity.
“Big-data skills
needed for
semiautomated
AI analysis for
cybersecurity.”
Note. Created from Kriukow (2020a).
Figure 21 Sample Qualitative Research Comparing Codes Using MS-WORD
C of Codes
Codes
ID: 3-29-C1
Codes ID:
4-2-C2
Created: 3/29/2023
Revised: 3/30/2023
Created:
4/2/2023
Revised:
4/4/2023
"Abilities in data
science" enables
cybersecurity
professionals to
utilize AI better.
“Availability of big
data” for
cybersecurity helps
insights from data.
"The lack of a
universally
acceptable
definition of AI
challenges AI's role
in cybersecurity.
“Skills in
machine
learning, data
science,
natural
language
processing” are
vital for
applying AI in
cybersecurity.
“Big-data skills
needed for
semiautomated
AI analysis for
cybersecurity.”
Note. Created from qualitative coding and thematic analysis in Microsoft Word (Kriukow,
2020a).
Figure 22 Qualitative Research Constant Comparison and Refinement of Codes
Note. Created from qualitative coding and thematic analysis in Microsoft Word (Kriukow,
2020a).
Figure 23 Sample Stage 3 Coding
Example
Stage 3: Selective Coding- Categorizing Codes
Factors that
influence the
addition of AI skills
to the U.S.
Cybersecurity
workforce.
Enhancers Strong
Factor 1
Factor 22
Factor 19
Mentioned 12
times
Mentioned
three times
Mentioned
seven times
Example
Stage 3: Selective Coding- Categorizing Codes
Moderate Factor 2
Mentioned 16
times
Factor 7
Factor 19
Mentioned
four times
Mentioned
seven times
Weak Factor 5 Mentioned
once
Other Factor 26 Mentioned
two times
Impediments
Strong
Moderate
Weak
Other
Note. Created from qualitative coding and thematic analysis in Microsoft Word Part II (Kriukow,
2020b).
Practices for Validity and Credibility
The study will involve in-depth interviews with 20 to 25 participants. Additional
interviews will only be conducted for clarification if needed. Its scientific rigor, credibility, and
transparency will be maintained by following best practices in qualitative grounded theory
research ( Creswell, 2018; Gramenz, 2017; Curry, 2019; Curry, 2018a; Curry, 2018c; Curry,
2018b; Curry, 2018d; Moerman, 2016a) and also by creating and maintaining study artifacts: (a)
An audit trail of all events related to the study; (b) Transcripts of the interviews; (c) An interview
guide to describe the rules of engagement used by the interviewer in the in-depth interviews; and
(d) Codes and code structure.
The potential outcomes from the study on the factors influencing the addition of AI skills
to the U.S. cybersecurity workforce are many: (a) Recurrent themes or hypotheses on the

phenomenon; (b) Identify a unit of measure for future surveys on this topic; (c) Taxonomy—
identify essential properties of the phenomenon; (d) Conceptual models or theories on the topic.
Based on the nature of the phenomenon of interest and the attributes of qualitative study
design options, this study will utilize interviews to collect rich data and apply the grounded
theory approach to that data. The open-ended and non-directional primary research question,
structured to be precise and clear, will be used to initiate in-depth interviews with U.S.
cybersecurity professionals at the management and operational levels. Subsequent interviews
will be based on the responses from the initial round of interviews. The proposed study will
utilize the core elements of grounded theory qualitative research methods such as iterative
process, concurrent data collection and analysis, constant comparisons, identification of concepts
from data, categorization of concepts, coding based on transcript analysis, avoidance of
researcher bias, transparency, and maintenance of audit logs (Moerman, 2016a; Moerman, 2016f;
Charmaz, 2017).
According to Moerman (2016f), the key versions of grounded theory are (a) the
Straussian version, which is highly prescriptive, formal, and procedural, (b) the Glaserian
version, in which all forms of data are allowed with less focus is on formality and procedures,
and (c) the Charmaz version in which the researcher, though without bias, is a co-constructor of
meanings, interpreting through interactions with the participants, with a focus on descriptions,
and potentially multiple theories. This study will be aligned more with the Charmaz version of
grounded theory in its approach to research method, which is influenced by the interpretive
worldview.
Member Checking
Validity is the process a researcher follows to gather evidence for their findings to be
accurate (Guion et al., 2011; Jordan, 2018; as cited in McKim, 2023). Researchers also refer to

validity using credibility, trustworthiness, and authenticity (Whittemore et al., 2001; as cited in
McKim, 2023). Member-checking is a valuable tool in ensuring the validity of qualitative
research. It will be implemented in this research by providing interview transcripts to each
participant after they have been interviewed and obtaining their feedback. This process will
identify and correct errors and omissions in interview transcripts. In addition to sharing draft
interview transcripts specific to each interviewee, McKim (2023) recommends sharing a draft
version of the findings with a few selected participants to obtain feedback that includes (a)
general thoughts, (b) accuracy of the finding in reflecting the participant responses, (c) items to
be added or removed from the draft findings with reasons. Since the participants are recognized
as experts on the phenomenon of interest in this research, a draft version of the final findings will
be shared with a few select participants, and their feedback will be analyzed and used to refine
the findings further.
Use of Memos
In grounded theory research, writing memos is an essential step of data analysis (Glaser
& Strauss, 1967; Charmaz, 2006; as cited in Mohajan & Mohajan, 2022). These reflective
interpretive audit trails document ideas, events, and the thought processes inherent in the
research process (Glaser, 1978; as cited in Mohajan & Mohajan, 2022). Memo writing helps with
analytical tasks and increases researcher productivity (Charmaz, 2006; as cited in Mohajan &
Mohajan, 2022). A memo containing the date, time, and cross-references to other artifacts,
priorities, codes, categories, themes, challenges, decisions, assumptions, events, ideas,
reflections, and thoughts will be maintained throughout this research. The memo will also track
questions, answers, and problems that need resolution.

Interview Guide
An interview guide will ensure that the interviews effectively learn from the participants
about the phenomenon of interest without introducing researcher bias. Key elements of the
interview guide used (Curry, 2018c) will be (a) Start with an understanding of the participant’s
work; (b) Explain the research objectives briefly; (c) Provide assurance about the confidentiality
of the information shared; (d) Ensure that questions are non-leading and non-judgmental; (e)
Explain questions when the respondent requests further clarity, (f) Allow time for the participants
to pause, reflect and respond, (g) Maintain focus on the phenomenon of interest without
interrupting the participants and (h) Pose probing non-leading questions only when responses
lack clarity or need further explanations.
Chapter 4: Results
Candidate Selection
This qualitative grounded theory study aimed to explore, identify, and understand the
factors impacting adding AI skills to the U.S. cybersecurity workforce. More specifically, the
study was to derive insights into the positive factors enabling adding AI skills to the workforce
and the negative factors that impede it. The National Capital Region (NCR) chapter of the
International Information System Security Certification Consortium (ISC2) in Washington, DC,
facilitated this study. The chapter manager sent the email composed by this researcher to the
chapter members. Subsequently, the study identified candidates with a minimum of 8 years of
cybersecurity professional experience with a basic understanding of AI and obtained informed
consent. The qualified candidates were added to the list of participants as soon as they sent a
signed informed consent, which amounts to a random selection without other considerations.

Thus, the study participants represented a purposeful sampling of practicing professionals in the
U.S. cybersecurity workforce. The responses from the participants represented a sampling of the
views and expertise on the research question from the U.S. cybersecurity workforce.
Pilot Study
Several qualified candidates consented, contingent on approvals from their employers,
that could have delayed their participation by a few weeks to a few months or could have
resulted in their withdrawal from the study. Hence in the interest of viability of the research, and
to ensure enough study participants, a single pilot study was decided. From the list of qualified
cybersecurity professional volunteers, one with multiple professional certifications, cybersecurity
program management responsibilities, more than eight years of work experience, and a basic
knowledge of AI techniques was selected randomly for a pilot study and upon receiving the
signed informed consent, sent the primary research question and the additional probing questions
to the pilot study participant as a part of a sixty-minute interview request. The interview was
conducted remotely based on the participant's preference.
The interview used the collaborative tool Microsoft Teams, which supported audio, video,
and screen-sharing features. Though only planned for 60 minutes the interview lasted 80 minutes
due to the learning curve in the use of recording feature. The interview was recorded, resulting in
a digital media container format MP4 that the collaboration tool supported. The MP4 file was
further converted to interview transcript text in Microsoft Word format using the dictatetranscribe
feature of Microsoft Word.
The pilot study helped to verify the ease of use and effectiveness of the collaborative tool
to schedule, conduct, and record interviews. The size of the MP4 files that resulted from the
recording depended on the duration of the interview. The number of steps involved in converting
the MP4 files into interview transcript texts was directly proportional to the size of the MP4 files.

When the MP4 files exceeded a specific size, the transcription failed. In such cases, a single MP4
file had to be broken into smaller ones, resulting in multiple transcription-to-text steps. In
addition, a free, open-source qualitative data analysis tool called "Taguette" was used and
verified to meet the requirements for analyzing and coding the interview transcripts.
Furthermore, the pilot study participant validated the clarity of the primary research
question and the relevance of the additional interview questions. The participant feedback, which
took the topic's complexity and the questions' scope into account, also helped to decide in favor
of multiple interviews of 60 minutes or less over a single extended interview. The capability of
the open-source data analysis tool to support open coding and axial coding was also verified
during the pilot study.
Interviews
A total of 35 cybersecurity professionals responded to the request for study participation.
A request for informed consent was sent to all of them, and 21 first responders were selected for
interviews, including one for the pilot study. The interview for the pilot study on June 26, 2023,
was the first to be conducted, and it lasted 60 minutes. The recording of the pilot study interview,
its transcription to text, and the analysis and coding of the transcribed text were completed by the
first week of July 2023. The remaining 20 interviews were scheduled and conducted between
July 2023 and November 2023. Each interview started with a brief discussion and understanding
of the participants' professional experience, roles, and responsibilities at the time of the interview
and their general awareness of AI techniques.
The interviewed study participants included cybersecurity professionals in executive
management, project and program management, subject matter experts, and security operational
roles. In addition, the participants were found to be employed at U.S. federal, U.S. Department of
Defense, or commercial organizations. All the participants had multiple worked at multiple
organizations during their careers. They also expressed a general awareness of AI techniques'
current state and progress and their applicability for strengthening cybersecurity. Only one of the
participants was a female. The gender and job roles of the participants were not considered for
the study. At the start of each interview, the participants were informed to skip any interview
questions they were uncomfortable answering, yet none skipped any questions. All participants
had at least one active cybersecurity certification to their credit. Table 7 summarizes the
professional profiles of the study participants.
Table 7 Professional Profiles of Study Participants
Identifier Job role
Type of
organization
employed at
Awareness of AI
techniques
Years of
cybersecurity
professional
experience
Participant 1
Program
manager;
Subject matter
expert
U.S. federal
civilian agency Yes 18
Participant 2
Program
manager;
Subject matter
expert
U.S. Department
of Defense Yes 15
Participant 3
Program
manager;
Subject matter
expert
U.S. commercial
organization Yes 16
Participant 4
Executive;
Subject matter
expert
U.S. federal
civilian agency Yes 12
Participant 5
Executive;
Subject matter
expert
U.S. commercial
organization Yes 20
Participant 6
Risk
management and
subject matter
expertise
U.S. commercial
organization Yes 14
Participant 7 Risk U.S. commercial Yes 14
management and
subject matter
expertise
organization
Participant 8
Risk
management and
subject matter
expertise
U.S. commercial
organization Yes 10
Participant 9
Risk
management and
subject matter
expertise
U.S. commercial
organization Yes 15
Identifier Job role
Type of
organization
employed at
Awareness of AI
techniques
Years of
cybersecurity
professional
experience
Participant 10
Risk
management and
subject matter
expertise
U.S. federal
civilian agency Yes 18
Participant 11
Risk
management and
subject matter
expertise
U.S. federal
civilian agency Yes 20
Participant 12
Risk
management and
subject matter
expertise
U.S. federal
civilian agency Yes 14
Participant 13
Risk
management and
subject matter
expertise
U.S. federal
civilian agency Yes 12
Participant 14
Risk
management and
subject matter
expertise
U.S. federal
civilian agency Yes 9
Participant 15
Risk
management and
subject matter
expertise
U.S. federal
civilian agency Yes 11
Participant16
Risk
management and
subject matter
expertise
U.S. federal
civilian agency Yes 12
Participant 17
Risk
management and
subject matter
expertise
U.S. federal
civilian agency Yes 12
Participant 18
Risk
management and
subject matter
expertise
U.S. federal
civilian agency Yes 11
Participant 19
Risk
management and
subject matter
expertise
U.S. Department
of Defense Yes 12
Identifier Job role
Type of
organization
employed at
Awareness of AI
techniques
Years of
cybersecurity
professional
experience
Participant 20
Risk
management and
subject matter
expertise
U.S. Department
of Defense Yes 16
Interview Transcript Analysis and Coding
The study scheduled the interviews based exclusively on the availability of the
participants and not on any order of the participants. The participants used cybersecurity,
information assurance, and system security as synonyms. Each interview recording was
converted to a textual format, resulting in an interview transcript. Once completed, the
transcribed text file was uploaded into the tagging tool, and tags were assigned to significant
phrases in the transcription from the perspective of the purpose of this study. As more interviews
were completed, the additional transcribed files were uploaded into the tagging tool, codes from
prior interviews were repurposed, or new codes were assigned.
The 14th interview needed only one new open code to tag its interview transcript. The
subsequent six interviews were completed, and their transcripts were tagged, repurposing the

codes from the previous interviews without any new code. Hence, saturation for this study was
observed at the end of 14 interviews.
In addition to the interviews, eleven additional discussions were held with a select few
participants to verify, obtain more information, or clarify statements considered outliers. After
completing the 20 interviews and merging codes where the phrases with the same meaning had
more than a single code, the open coding resulted in 212 codes. After the initial round of open
coding, the next round of axial coding was performed.
An analysis was conducted on the identified open codes to explore the logical connection
between them from the perspective of the purposes of this study. When codes and the semantics
behind them were found to belong to a logical group, they were grouped into a code category and
assigned a category ID. For example, the three initial rounds of codes that represented (a)
hackers using AI for phishing attacks, (b) hackers using AI for vulnerability identification, and
(c) hackers using AI for identity spoofing were categorized into “Hackers using AI for
cyberattacks.”
The code categories from the second coding round were further compared and grouped to
identify sub-themes and themes. This process was iterative, and multiple reviews and revisions
were conducted before sub-themes and themes were finalized. From the initial 212 codes from
the open coding round, logical categories were formed, resulting in 53 code categories during the
axial coding round. They were further grouped, resulting in 16 sub-themes and six themes.
Figure 24 represents the stages of coding and the emergence of sub-themes and themes of this
study.
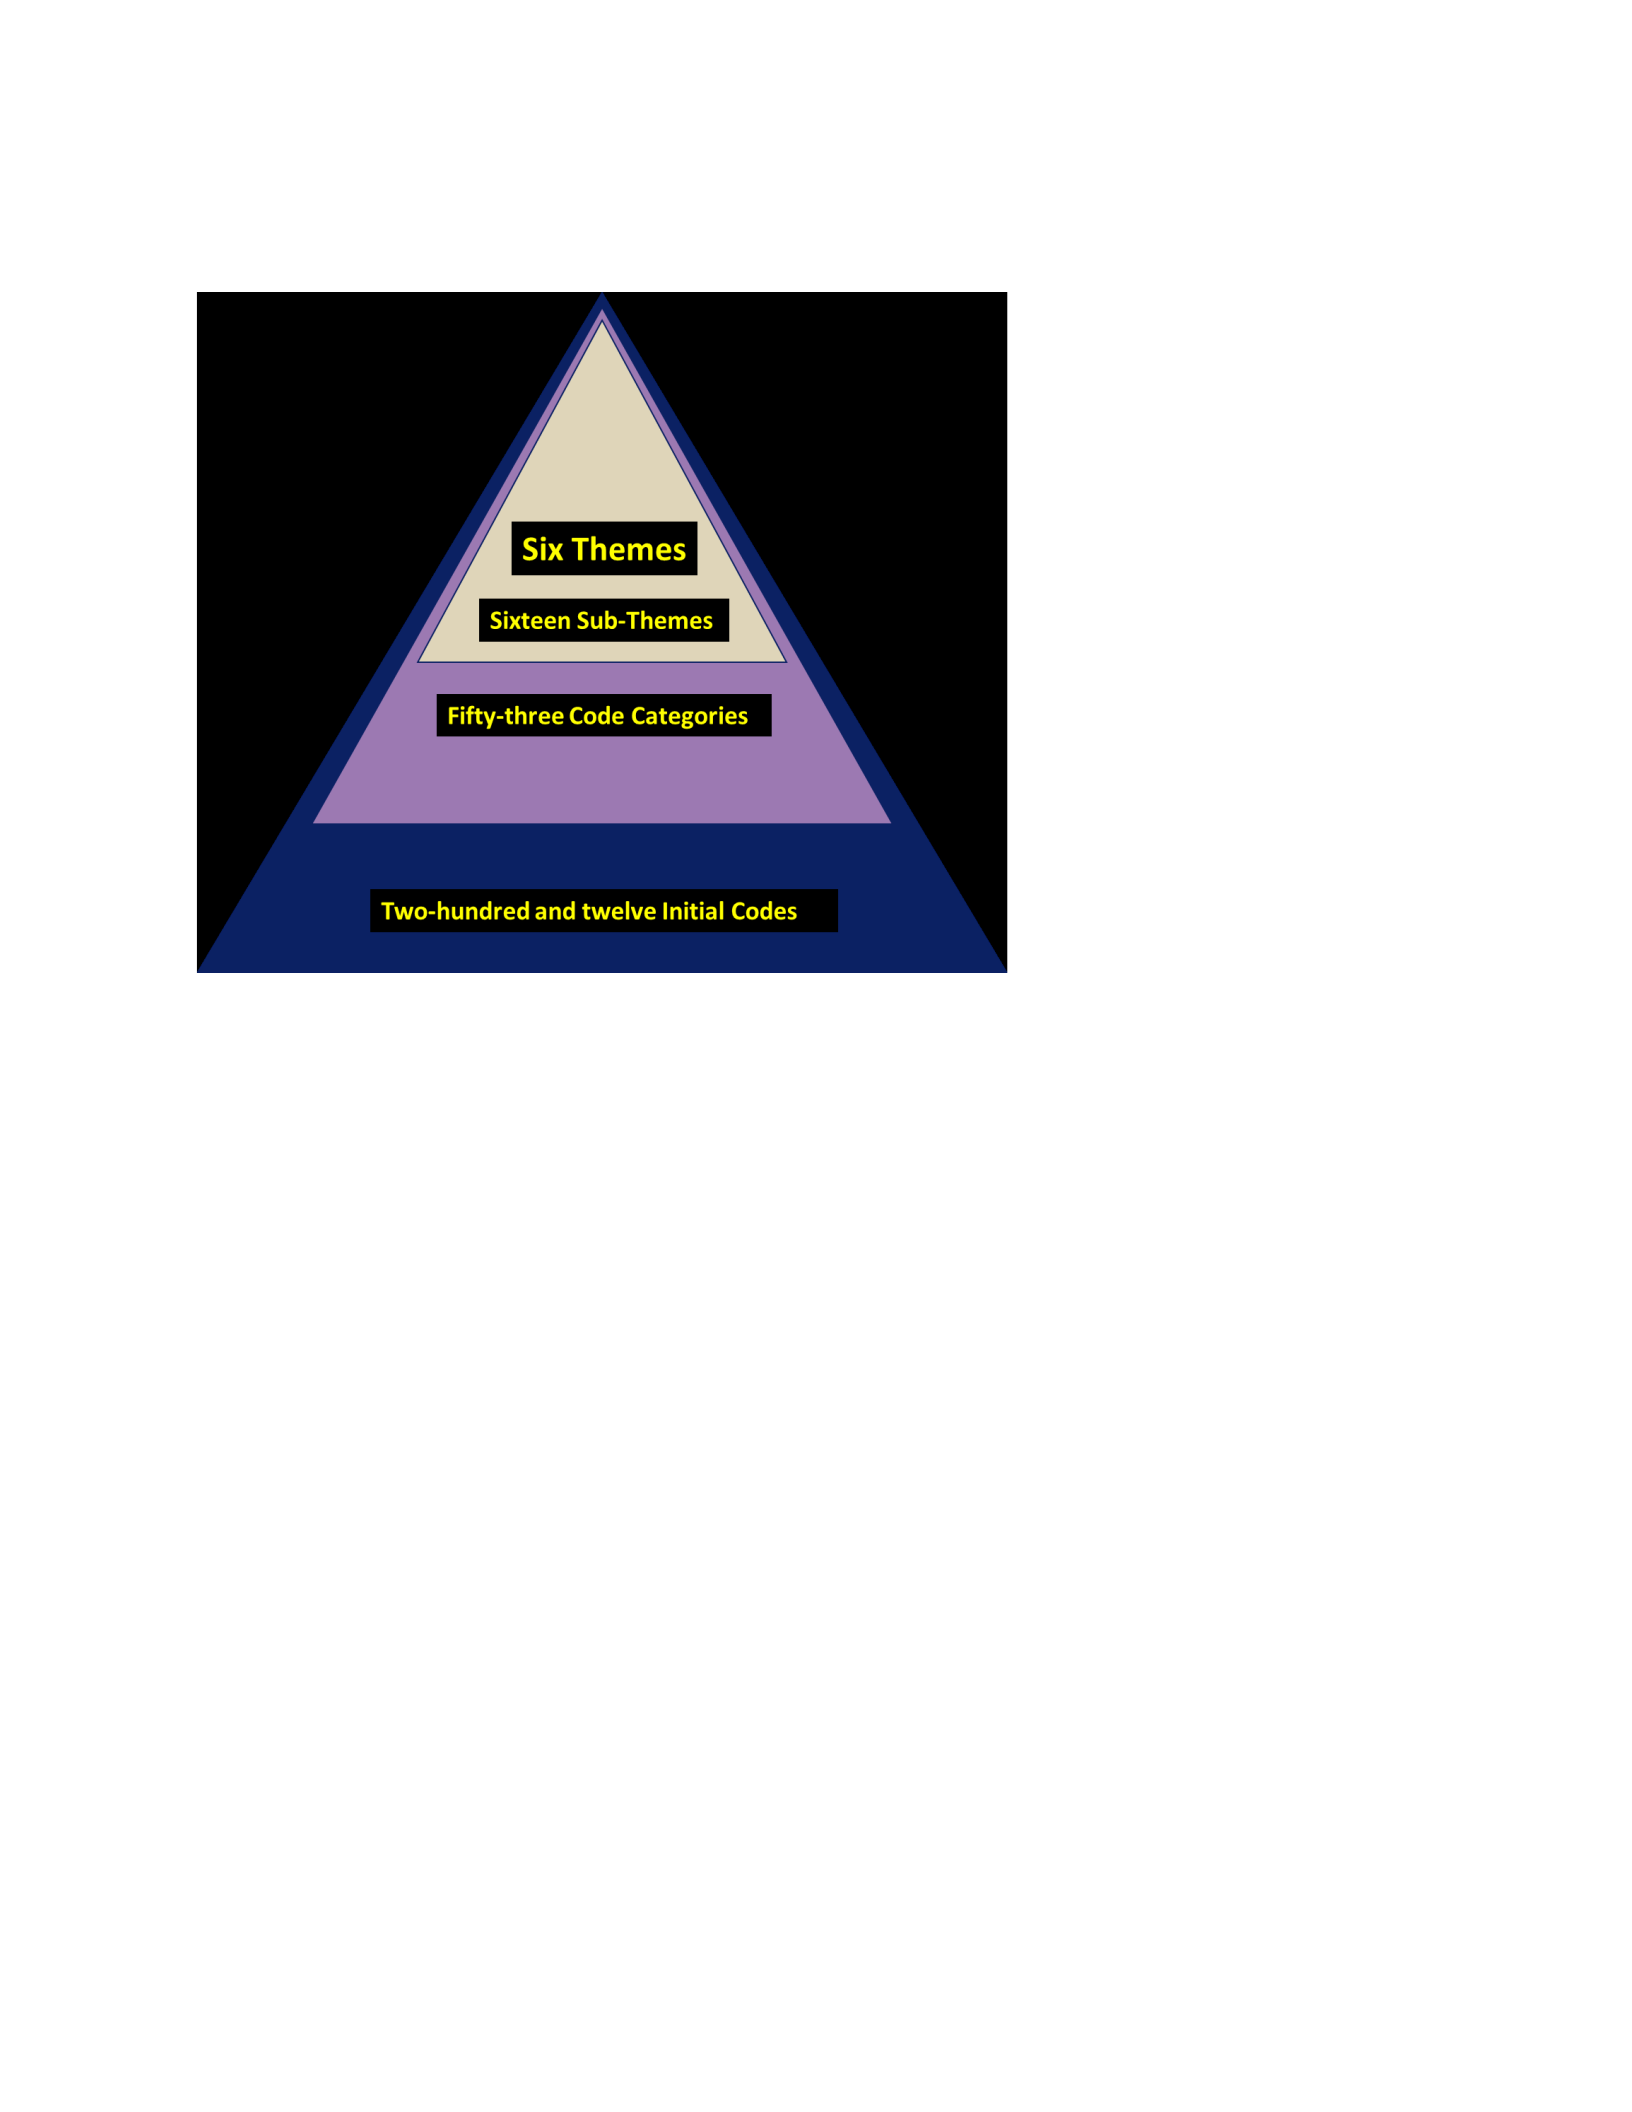
Figure 24 Derivation of Themes and Sub-Themes from Coding
Themes
Theme One- AI Information Through Familiar and Trusted Channels
This study aims to identify the factors influencing AI skills for U.S. cybersecurity
professionals. Responding to the primary research question and the additional probing questions,
the study participants explained with details and examples the sources through which they
gathered, analyzed, and understood the information about AI technologies that could enhance
cybersecurity. In their explanations, they also included opinions about conflicting messages,
confusing concepts, questionable predictions, intimidatingly complex AI algorithms, and
promotional material to sell software services and tools in AI information for cybersecurity.
Fourteen participants mentioned a lack of clarity and consistency in the AI information they
receive for aiding cybersecurity tasks. Five added that the information needed to be more specific

and tailored to the cybersecurity requirements of the industries they supported, such as finance
and healthcare.
Furthermore, for AI information for cybersecurity, the participants mentioned the use of
websites, white papers from commercial vendors of services and tools, webinars, podcasts,
online resources referenced in social media, conference publications, emails from professional
associates, training sessions from professional certification consortiums (ISC2), publications
from standards organizations (NIST, ISO), and documents from the U.S. national AI initiatives,
articles published in public journals. They added that the information was overwhelming,
contradictory, complex, confusing, rapidly changing, lacking verifiable facts and clarity, and
threatening cybersecurity jobs.
The open codes were categorized into (a) Conflicting AI information, (b) Too many
sources, (c) Trusted sources, (d) Familiar sources, (e) Industry-specific AI details, (f) Too
complex and intimidating, (g) Lack of specifics, (h) Suitability, (i) AI risks, (j) Limitations of AI,
(k) Match AI techniques to cybersecurity tasks, and (l) AI references in social media and
interpreted to derive the first theme of 'AI Information Through Familiar and Trusted Channels.'
In addition, three sub-themes with additional attributes under the first theme of ‘AI
Information Through Familiar and Trusted Channels’ were identified based on the interpretations
of the participants' responses. The first sub-theme was the need for information on AI techniques
to be explicitly mapped to cybersecurity tasks instead of being too general. An example of this
sub-theme would be the information about AI's supervised machine learning algorithms
successfully identifying cybersecurity vulnerabilities from event logs.
The second sub-theme was the importance of simple, clear, and precise AI information
introduced to cybersecurity professionals with educational explanations recognizing the newness
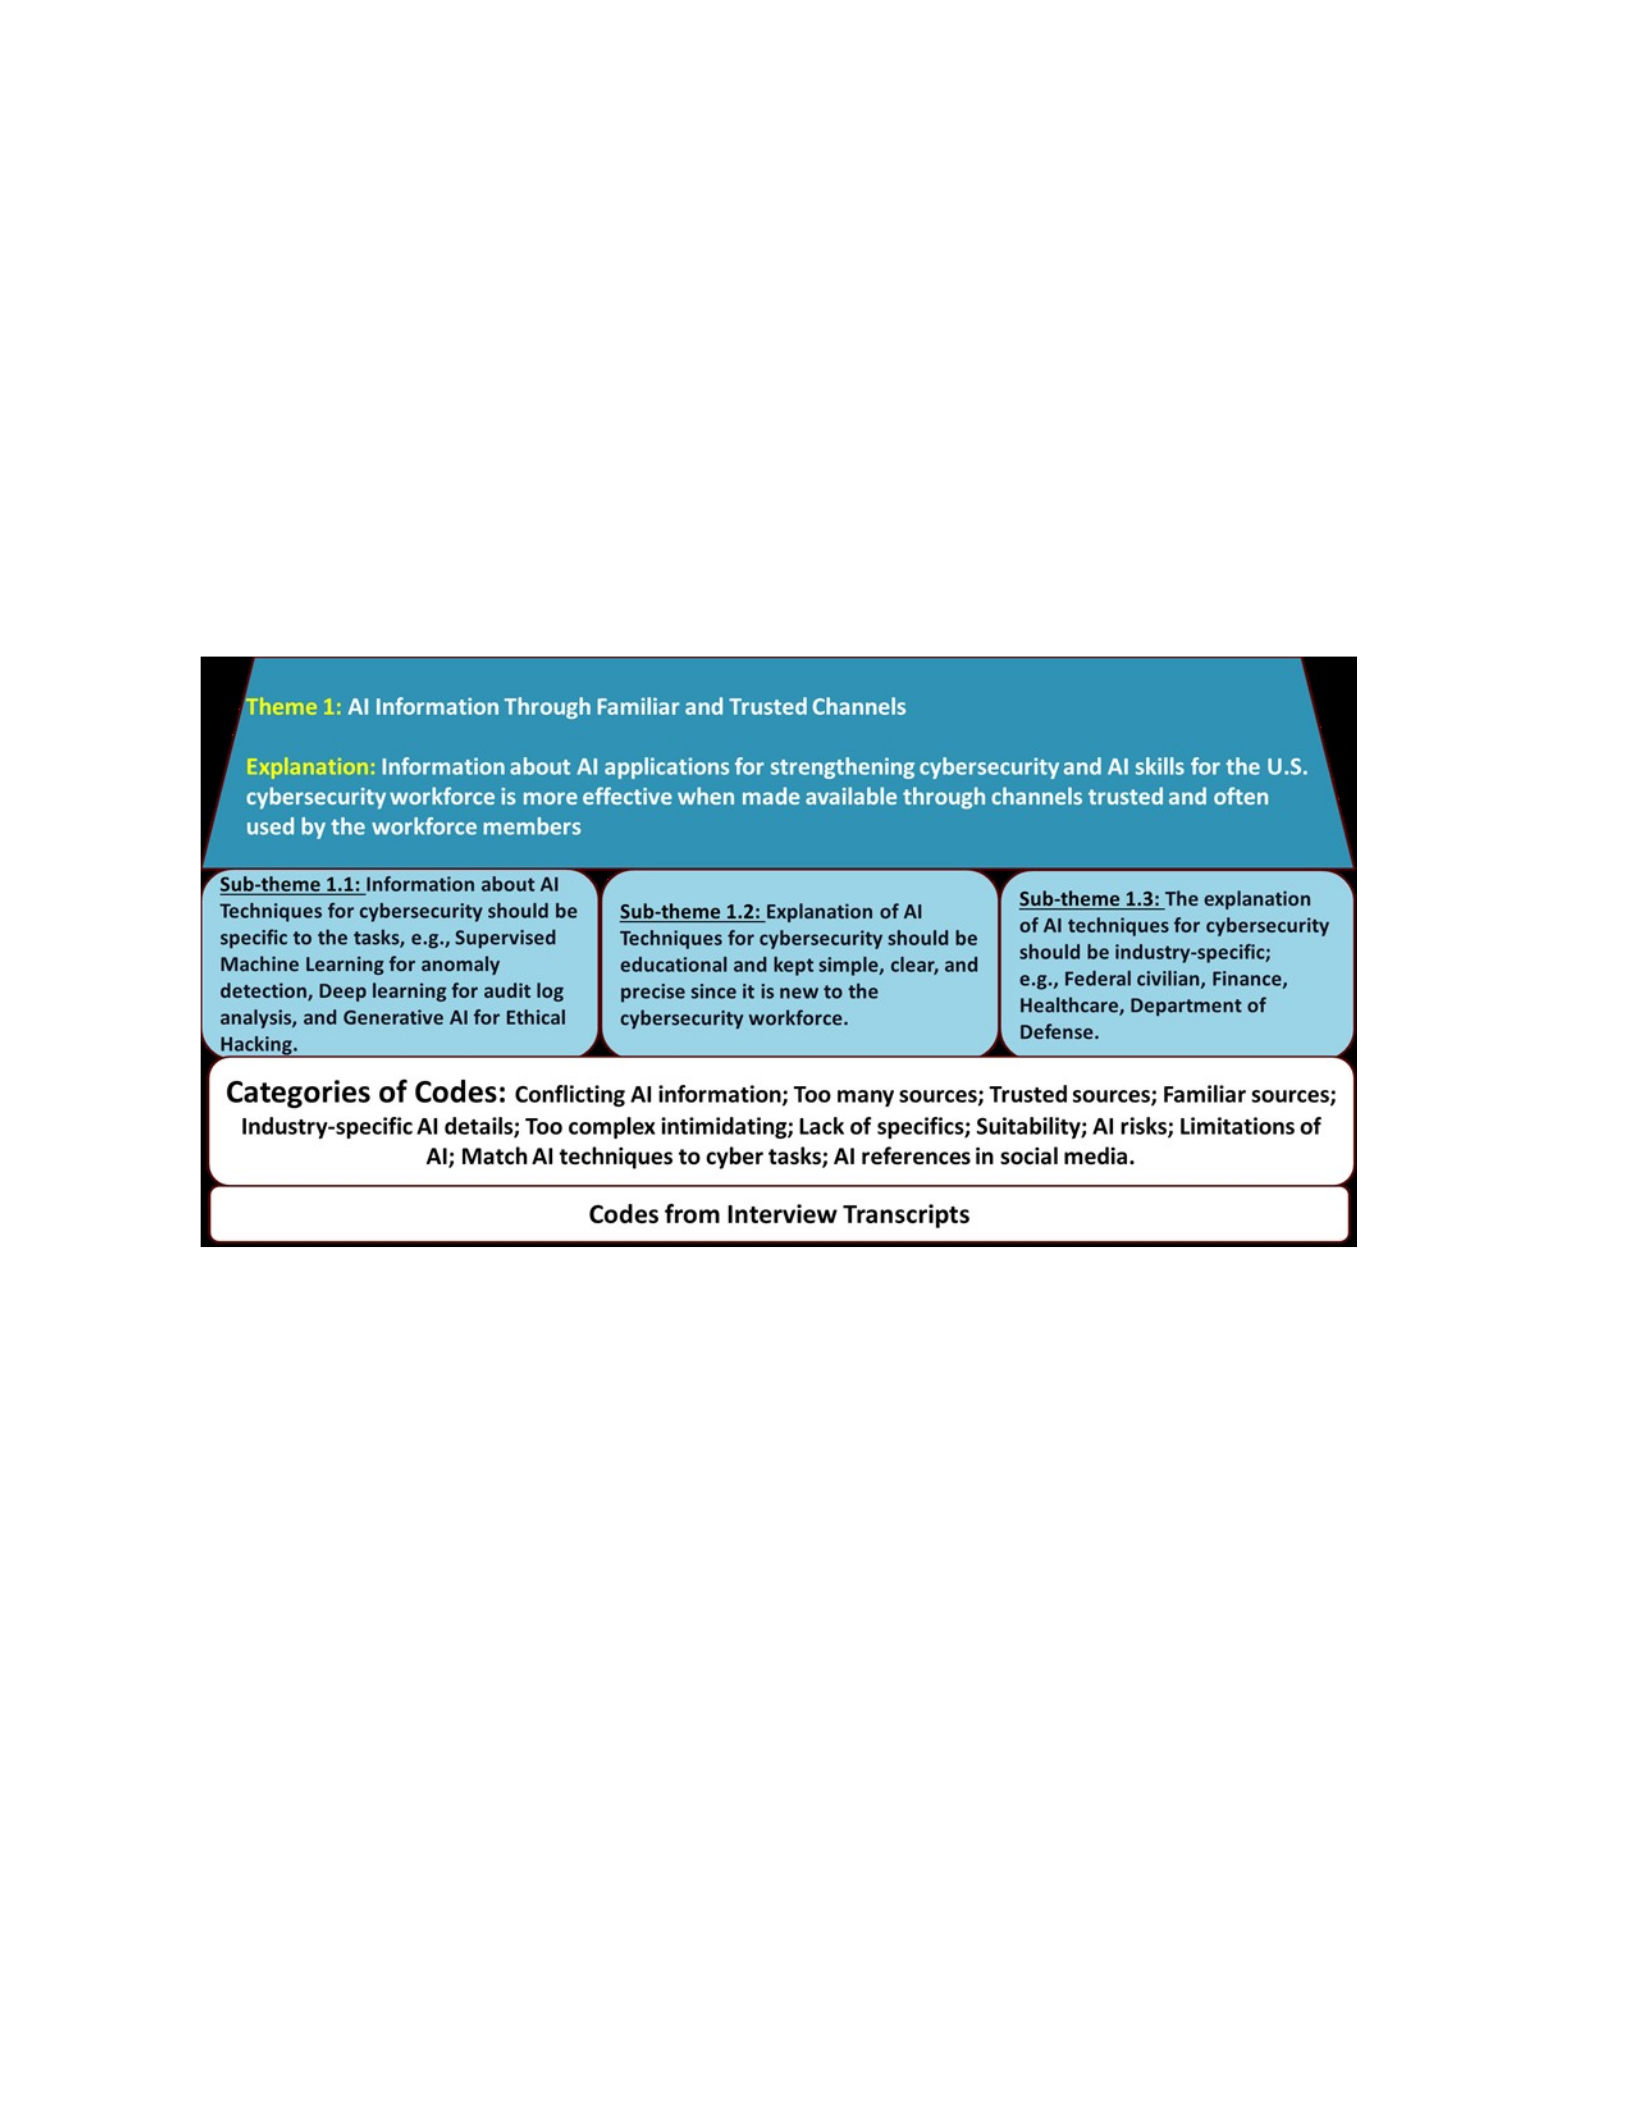
of the topic. The third sub-theme was that the AI information directed to cybersecurity
professionals should be tailored to their industry-specific nuances, standards, and terminology.
For example, since cybersecurity differs for federal civilian, finance, health care, and defense
sectors, AI information should be customized and directed to the professionals in those sectors to
enhance comprehension. Figure 25 represents the structure of the first theme.
Figure 25 Theme One and Sub-Themes
Theme Two- AI Topics in Compliance and Regulatory Cybersecurity Requirements
The study participants were cybersecurity professionals from diverse U.S. organization
types, including federal civilian, Department of Defense, healthcare, and finance. In responding
to the questions about the factors behind AI skills for the U.S. cybersecurity workforce, they also
referred to the U.S. national initiatives on AI, among other issues. One of the participants pointed
out that the U.S. AI initiatives and associated governance and risk management frameworks were
more focused on fairness, ethics, trustworthiness, privacy, and data security in the development

and operation of AI applications and less on the guidance for using AI to strengthen cyber
defenses.
Multiple participants referred to their employer's need to meet cybersecurity requirements
dictated by laws and regulations. Furthermore, they expected the national initiatives to mature
and prioritize AI applications for strengthening cybersecurity. According to them, including AI in
compliance-based cybersecurity requirements would positively influence the adoption of AI
applications and be a significant enabler of AI skills for U.S. cybersecurity professionals. They
quoted the laws and regulations with which they were most familiar. Thirteen participants
referenced the compliance-based cybersecurity requirements and the prospects of AI topics. The
cybersecurity requirements mandated by (a) the Federal Information Security Management Act
of 2002, (b) the Federal Information Security Modernization Act of 2014 (FISMA), (c) The
Sarbanes-Oxley Act of 2002 (SOX), (d) Health Insurance Portability and Accountability Act of
1996 (HIPAA), and (e) The Payment Card Industry Data Security Standard of 2004 (PCI DSS)
were referred to by the participants in their explanations.
The theme ‘AI Topics in Compliance and Regulatory Cybersecurity Requirements’
emerged from analyzing the responses that recommend AI for cybersecurity to be included in
compliance and regulations. Researchers have discussed in-depth the security requirements
resulting from laws, compliances, and regulations and how AI could impact them (Akhtar, 2023;
Moore & Frye, 2019; Disterer, 2013; Williams & Adamson, 2022), yet it is beyond the scope of
this study to discuss them.
The open codes were categorized into (a) National AI policy, (b) Compliance and
regulatory requirements, (c) Budget, (d) Procurement processes, (e) AI for HIPAA, (f) PCI DSS
AI, (g) ISO AI, (h) SOX contains security, (i) Integration into policies and procedures, (j) AI in

professional certification courses, and (k) AI in mandatory cybersecurity training and interpreted
to derive the theme of ‘AI Topics in Compliance and Regulatory Cybersecurity Requirements’.
Furthermore, the participants' responses identified three sub-themes that refer to the
benefits under the central theme of 'AI Topics in Compliance and Regulatory Cybersecurity
Requirements.' The first sub-theme indicates a benefit of the theme as the integration of AI
applications for cybersecurity into organizational policies and procedures. For example, suppose
guidance for using AI applications is introduced into the technical standards driving the
healthcare cybersecurity requirements. In that case, it expedites including AI techniques for
cybersecurity tasks into the organization's cybersecurity program objectives. The second
subtheme refers to the higher chances for the introduction of AI topics into professional
cybersecurity certifications, such as Certified Information Systems Security Professional
(CISSP), Certified Information Systems Auditor (CISA), and Certified Ethical Hacker (CEH).
The second sub-theme also applies to technical standards such as the ISO/IEC 27001 that
provide organizations from all sectors of activity with guidance for establishing, implementing,
maintaining, and continually improving an information security management system.
A third sub-theme indicates that AI in compliance and regulation-driven cybersecurity
requirements will influence organizational budgeting and procurement processes to support AI
techniques and AI skills for the workforce. Figure 26 is a visual representation of theme two and
its sub-themes.
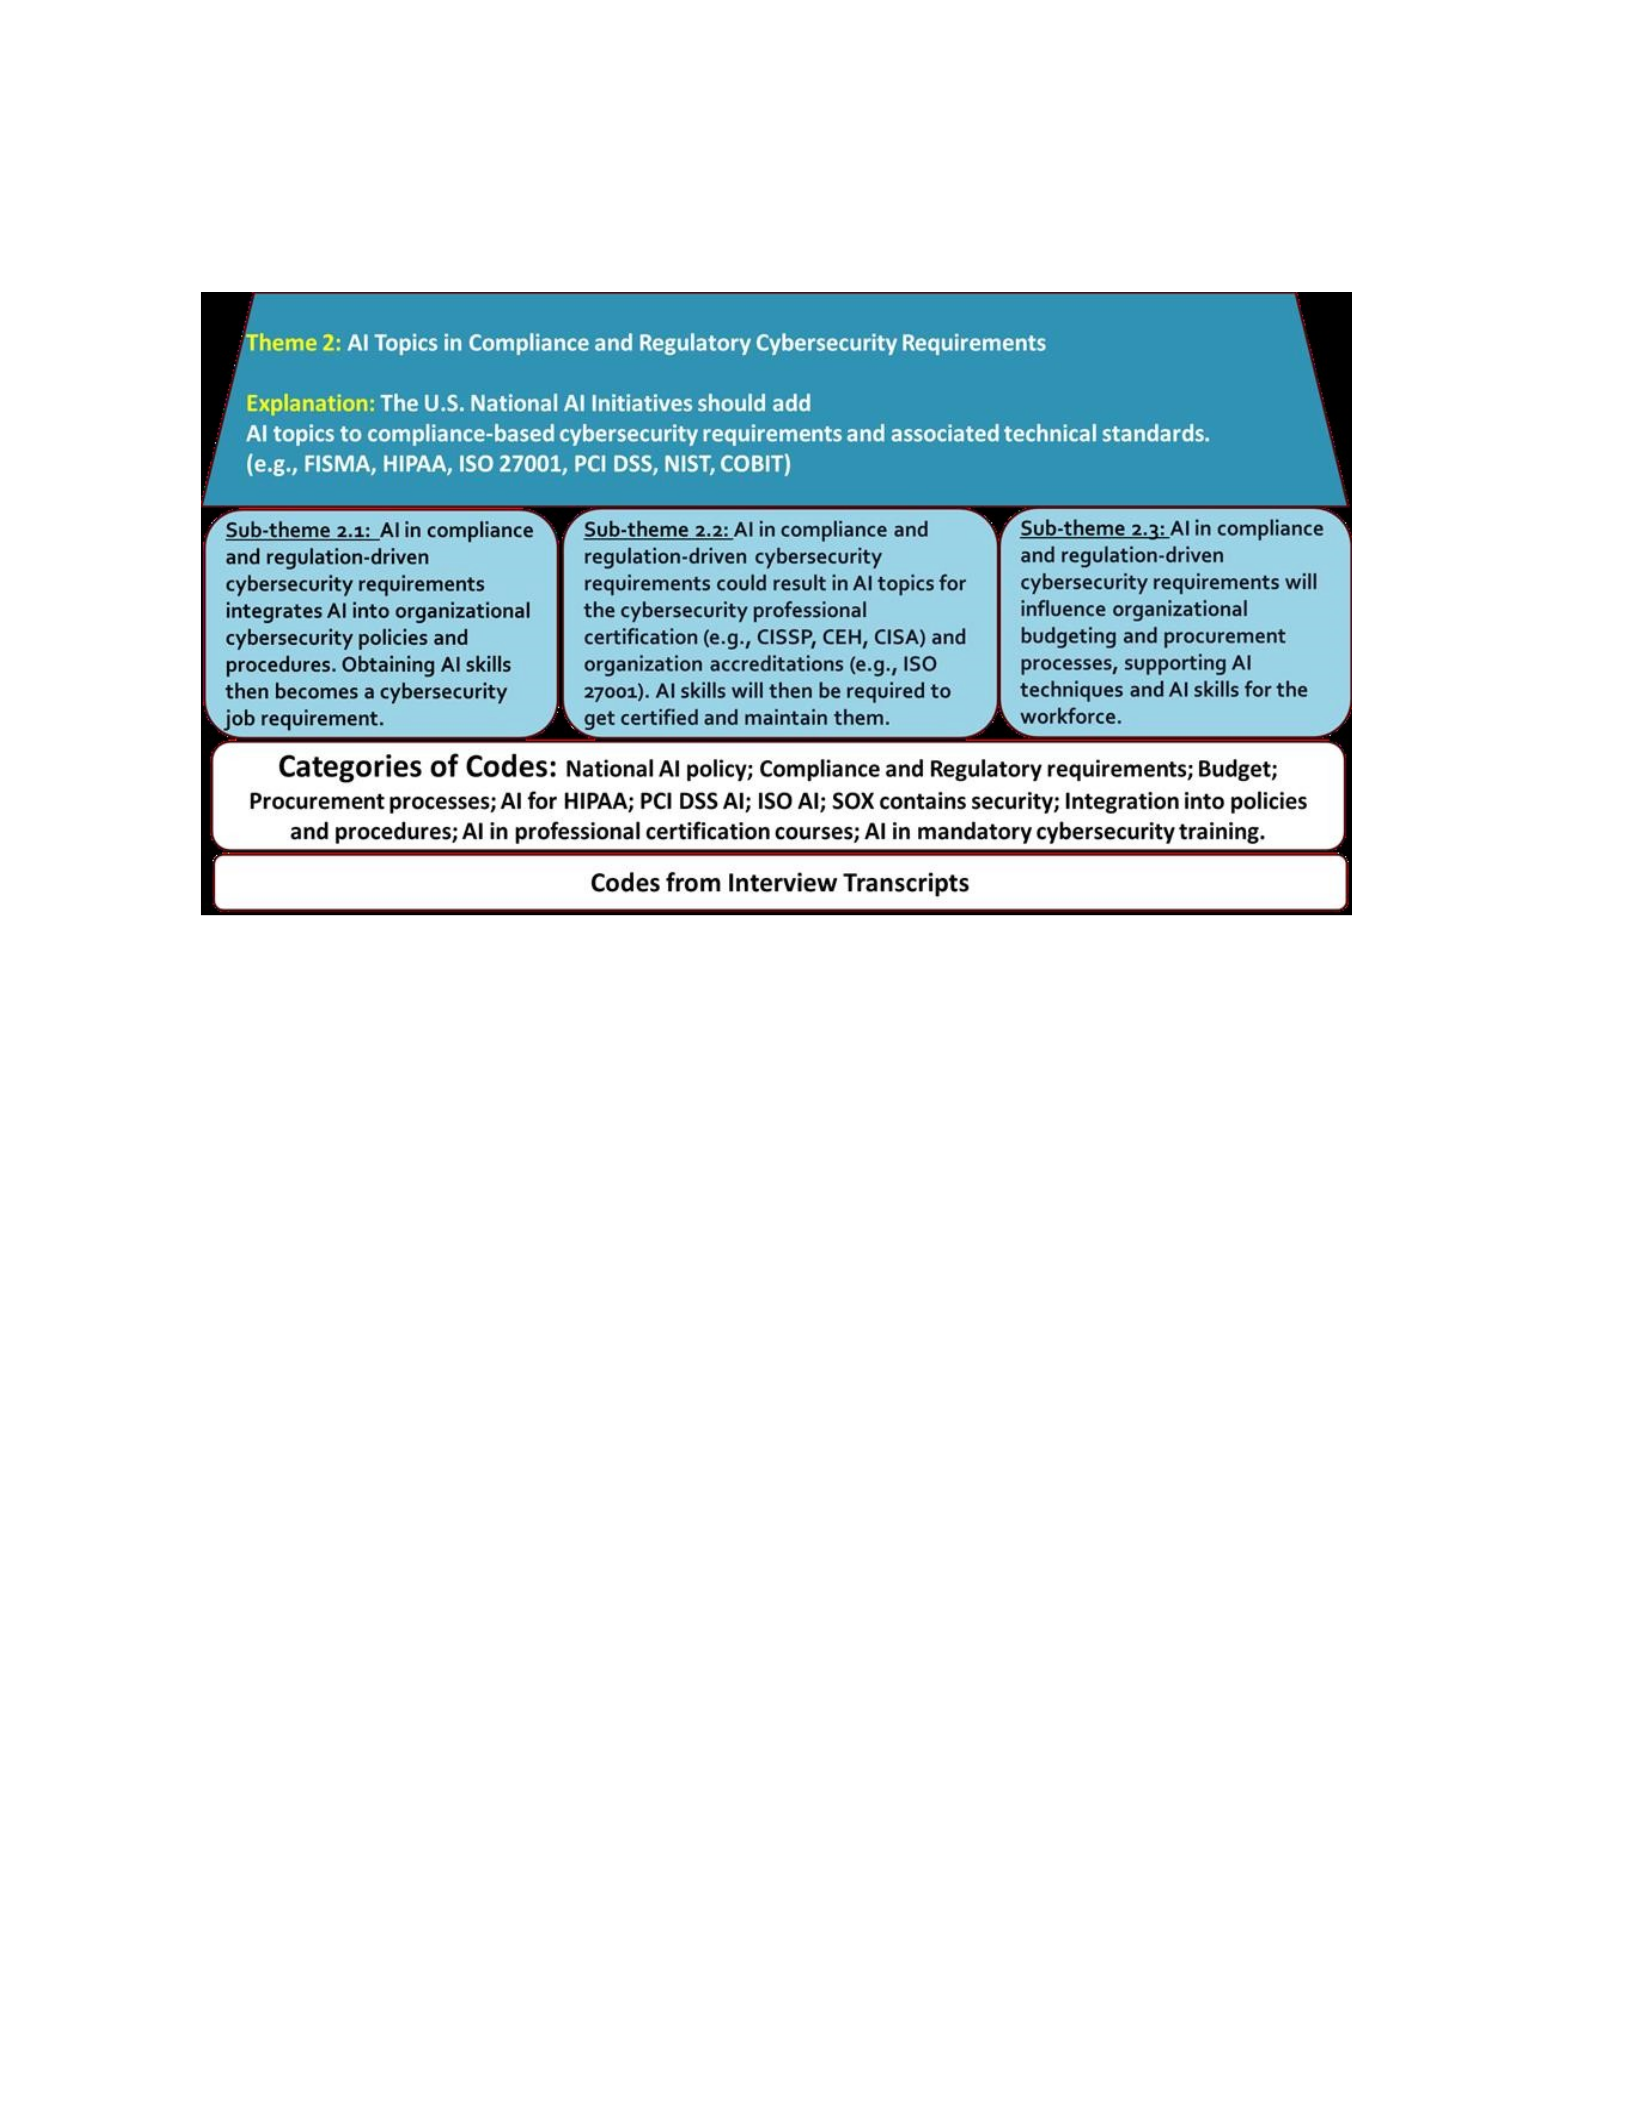
Figure 26 Theme Two and Sub-Themes
Theme Three - AI Techniques Integrated into Cybersecurity Tools
When discussing the issue of validating and verifying AI techniques before using them
for cybersecurity tasks, the participants highlighted the risk-averse nature of cybersecurity
professionals. The participants explained the approach to thoroughly test the AI applications for
cybersecurity combined with the need for risk mitigation. The need to validate and verify the AI
techniques before using them for the U.S. cybersecurity practice areas was discussed by 13
participants, with risk mitigation included in their explanations. Participants mentioned the
thorough testing of any new tool at their organizations, referring to one or more of (a) proof-
ofconcept, (b) vetting-process, and (c) a trial period. According to them, integrating AI
techniques as extensions to the current cybersecurity tools would expedite the verification and
validation of the AI techniques for cybersecurity and simplify the adoption, installation, training,
and maintenance. The responses also included the potential for adding rapidly emerging AI
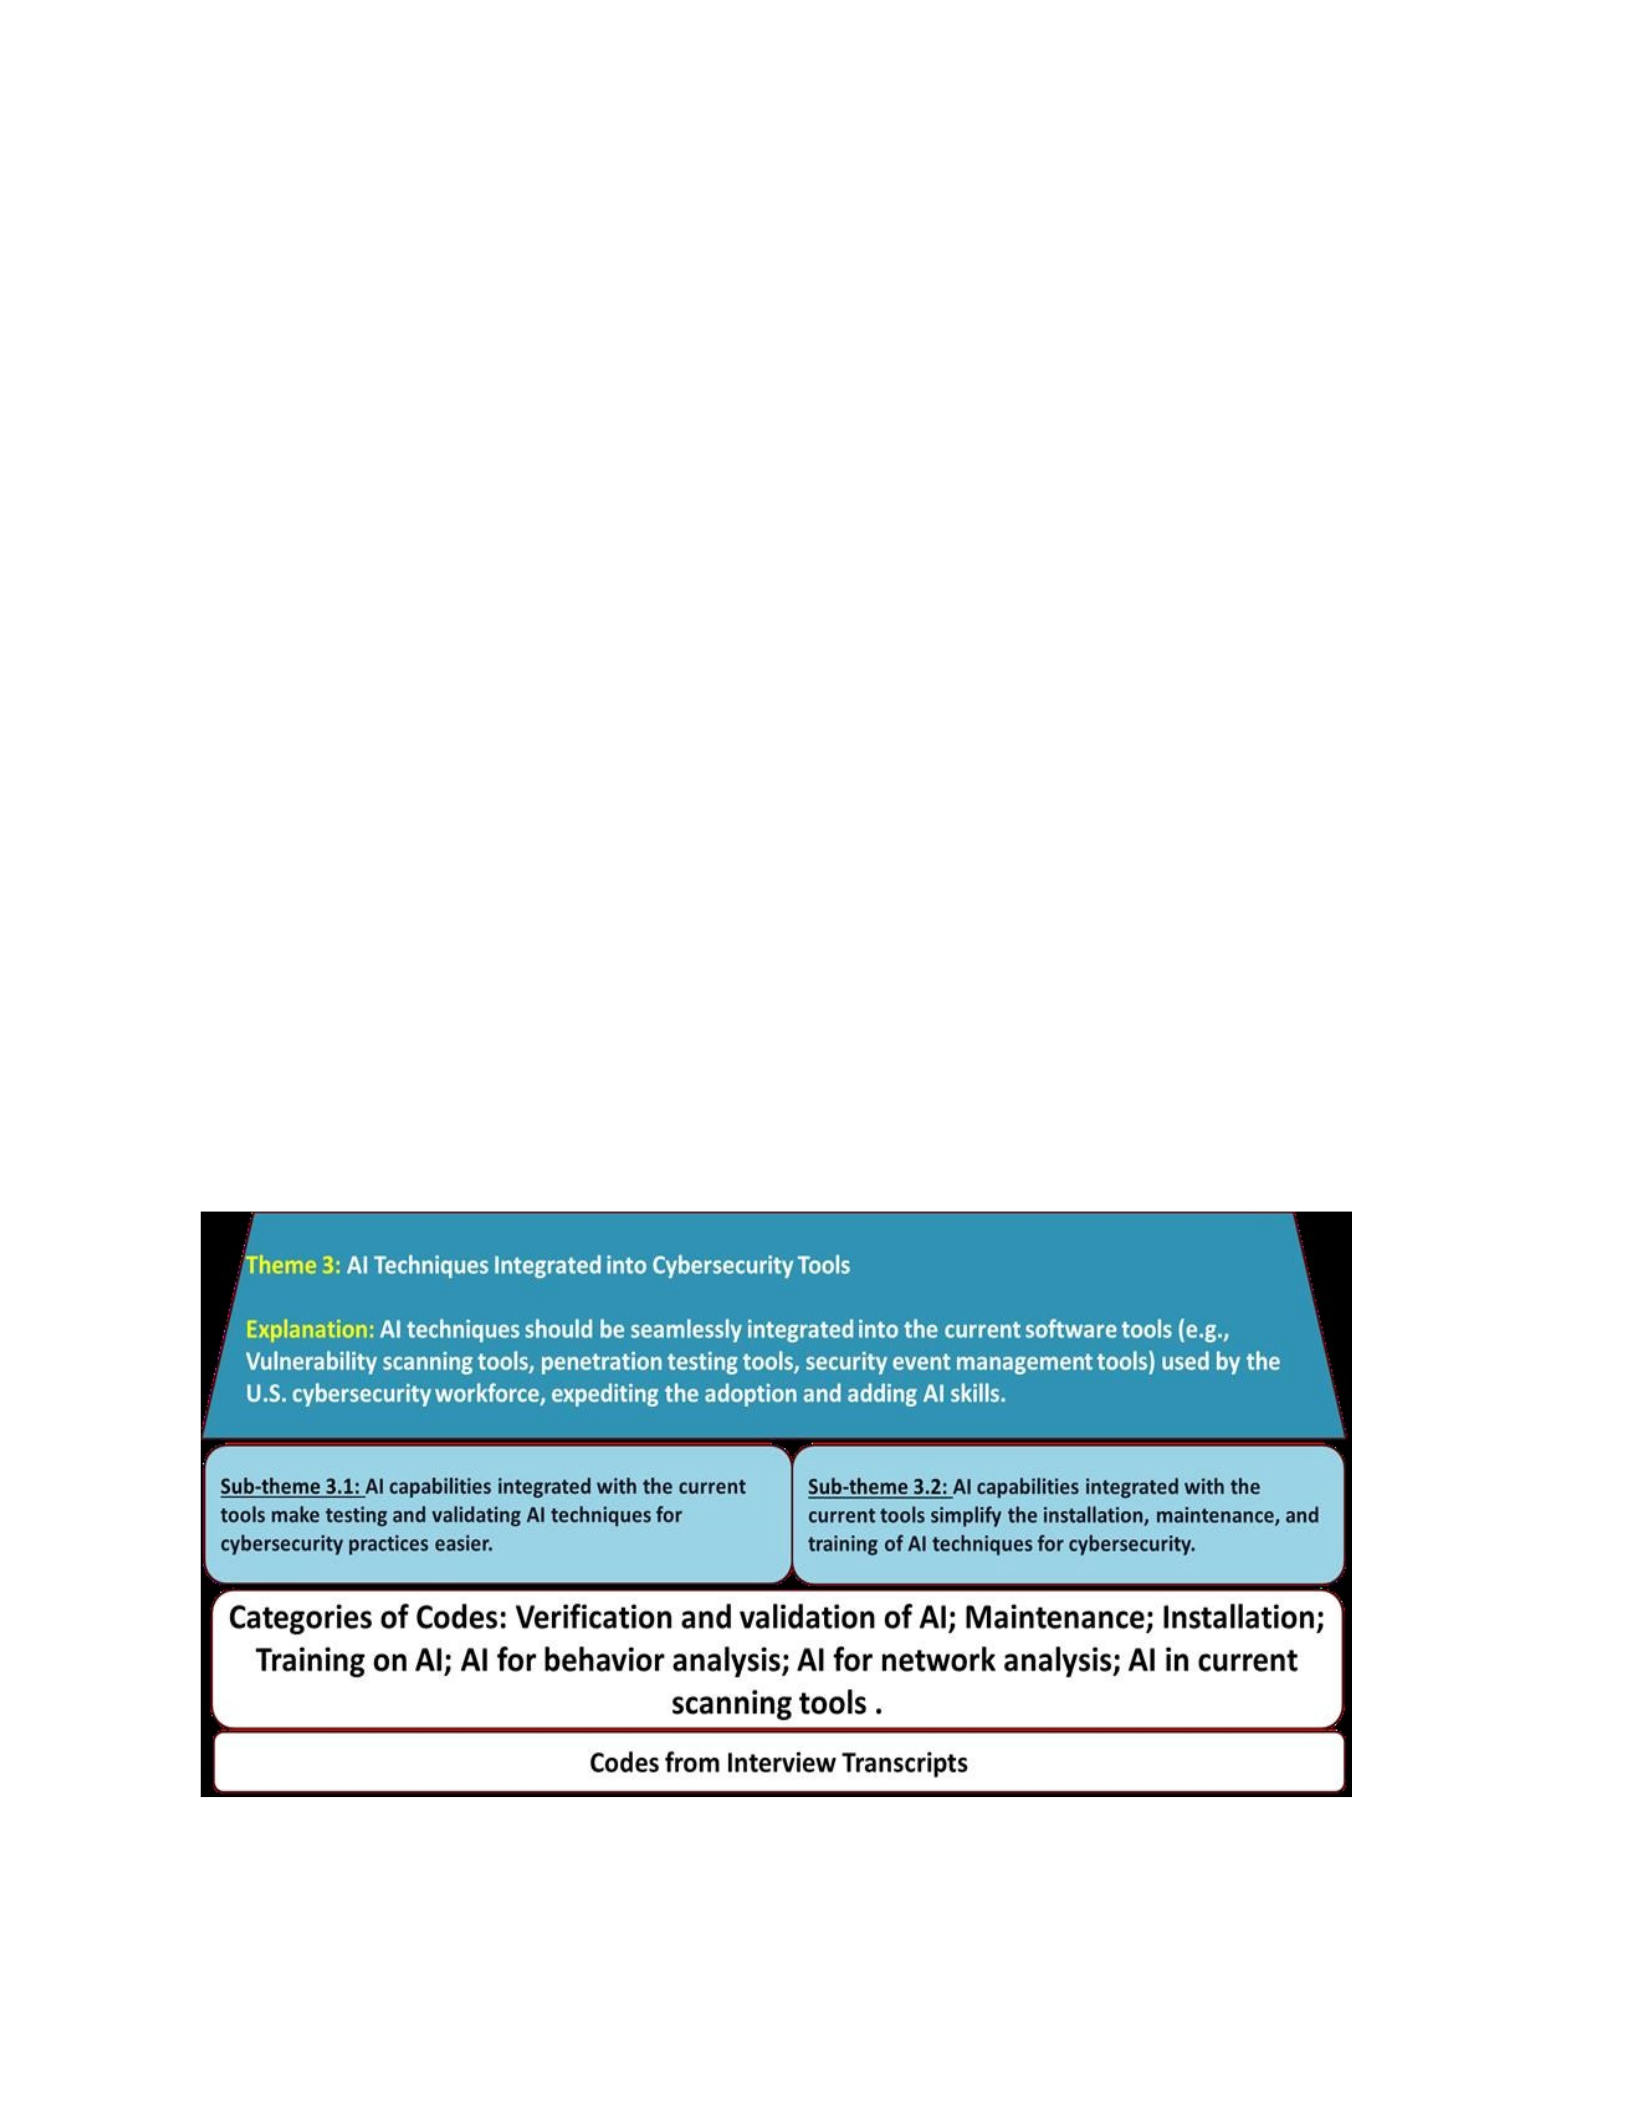
algorithms through the maintenance process for upgrading cybersecurity tools. The theme ‘AI
Techniques Integrated into Cybersecurity Tools’ was derived from the responses around the need
for a risk-minimized introduction of AI applications for cybersecurity tasks.
The code categories (a) Verification and validation of AI, (b) Maintenance, (c)
Installation, (d) Training on AI, (e) AI for behavior analysis, (f) AI for network analysis, and (g)
AI in current scanning tool, helped derive the theme ‘AI Techniques Integrated into
Cybersecurity Tools’.
In addition, two sub-themes with additional attributes were identified under the main
theme of ‘AI Techniques Integrated into Cybersecurity Tools.' The first sub-theme mentions that
AI capabilities integrated into cybersecurity tools make testing easier. The second one refers to
simplifying installation, maintenance, and training. Figure 27 is a visual representation of the
third theme and its sub-themes.
Figure 27 Theme Three and Sub-Themes

Theme Four - AI Education for Cybersecurity Roles and General Awareness for Others
When responding to the need to educate the U.S. cybersecurity workforce on AI
techniques for cybersecurity tasks, the data-driven supervised and unsupervised machine learning
algorithms were widely quoted for analyzing large volumes of event logs and identifying
potential threats and security incidents. Participants used their cybersecurity tasks, which
required close coordination and collaboration with their fellow technical and nontechnical staff,
as examples and preferred similar teamwork for adopting AI techniques for cybersecurity tasks.
The prioritization of organizational AI resources for cybersecurity, the need for data collection to
support the AI algorithms, and the impact of the learning curve during the adoption of AI
techniques were a few key issues mentioned during the interviews. The theme ‘AI Education for
Cybersecurity Roles and Awareness for Broader Organization’ was derived from the responses
around the need for AI education and training for the cybersecurity workforce. The code
categories (a) AI for all IT staff, (b) AI for managers, (c) Data for AI algorithms, (d) Basic
AI for all staff, (e) Teamwork, (f) Risks in AI application, (g) Explain AI findings, and (h)
Priorities in using AI, helped derive the theme ‘AI Education for Cybersecurity Roles and
Awareness for Broader Organization’.
Three sub-themes, with additional attributes, under the main theme of ‘AI Education for
Cybersecurity Roles and Awareness for Broader Organization’ were identified based on the
participants’ responses. The first sub-theme relates to better expectations management when AI is
applied to cybersecurity tasks. The second sub-theme refers to the faster collection of data for AI
algorithms. The third sub-theme mentions prioritizing organizational AI resources, as they
emerge, for cybersecurity tasks. Figure 28 represents theme four and its sub-themes.
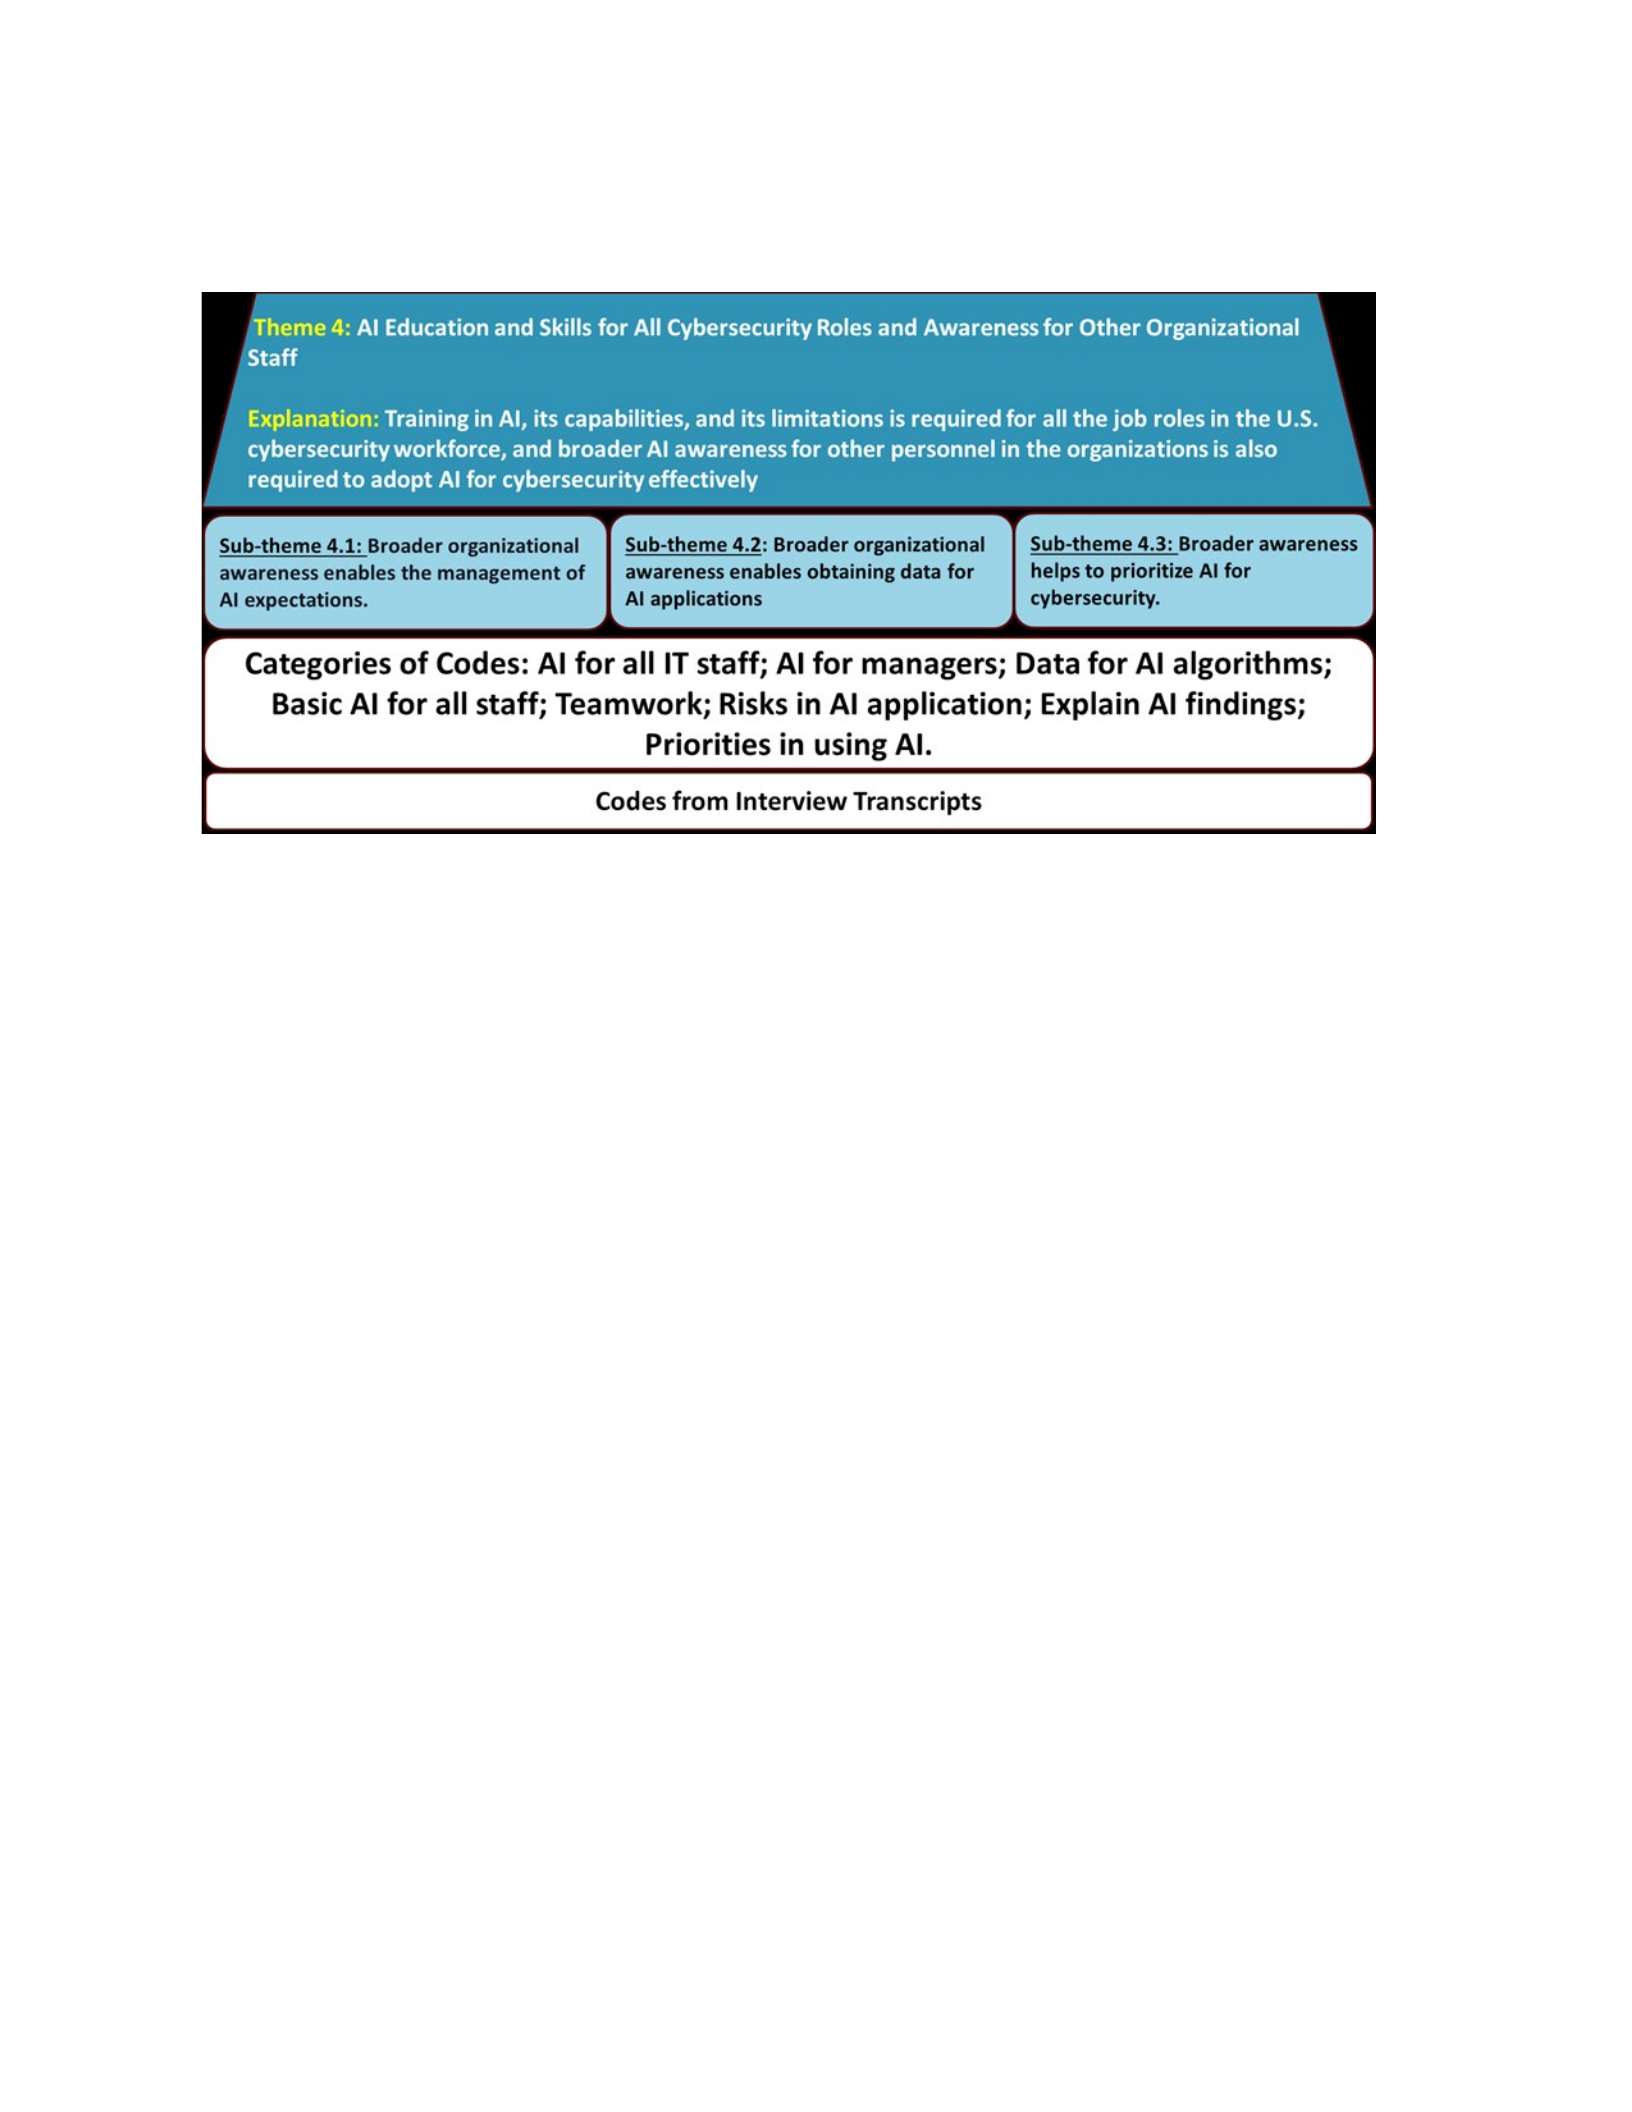
Figure 28 Theme Four and Sub-Themes
Theme Five - Communicate Cases of AI Used for Cyber-Attacks and Cyber-Defense
The study participants recognized, through the many information sources available, an
understanding of AI technology's potential for cybersecurity. Fifteen of the 20 participants quoted
AI techniques, including machine learning and generative AI, being used by hackers for cyber-
attacks and further added that cyber defense was lagging in using AI to counter the threat posed
by AI-based attacks. The recent popularity of generative AI-based tools such as ChatGPT was
mentioned by 10 participants as a tool with potential use for cyber defense and cyberattacks.
Nine participants discussed identity spoofing, phishing email generation, vulnerability detections,
and behavior analysis as AI-based cyber-attack tasks. A total of 14 participants referred to the
knowledge of verifiable and credible instances of AI's use for cyber-attacks and cyber defense as
valuable for cybersecurity professionals to adopt AI techniques and obtain AI skills
expeditiously. The code categories (a) Hackers use AI for data breaches, (b) Hackers use AI for
vulnerability detection, (c) Hackers are ahead in the use of AI, (d) Cybersecurity is lagging, (e)
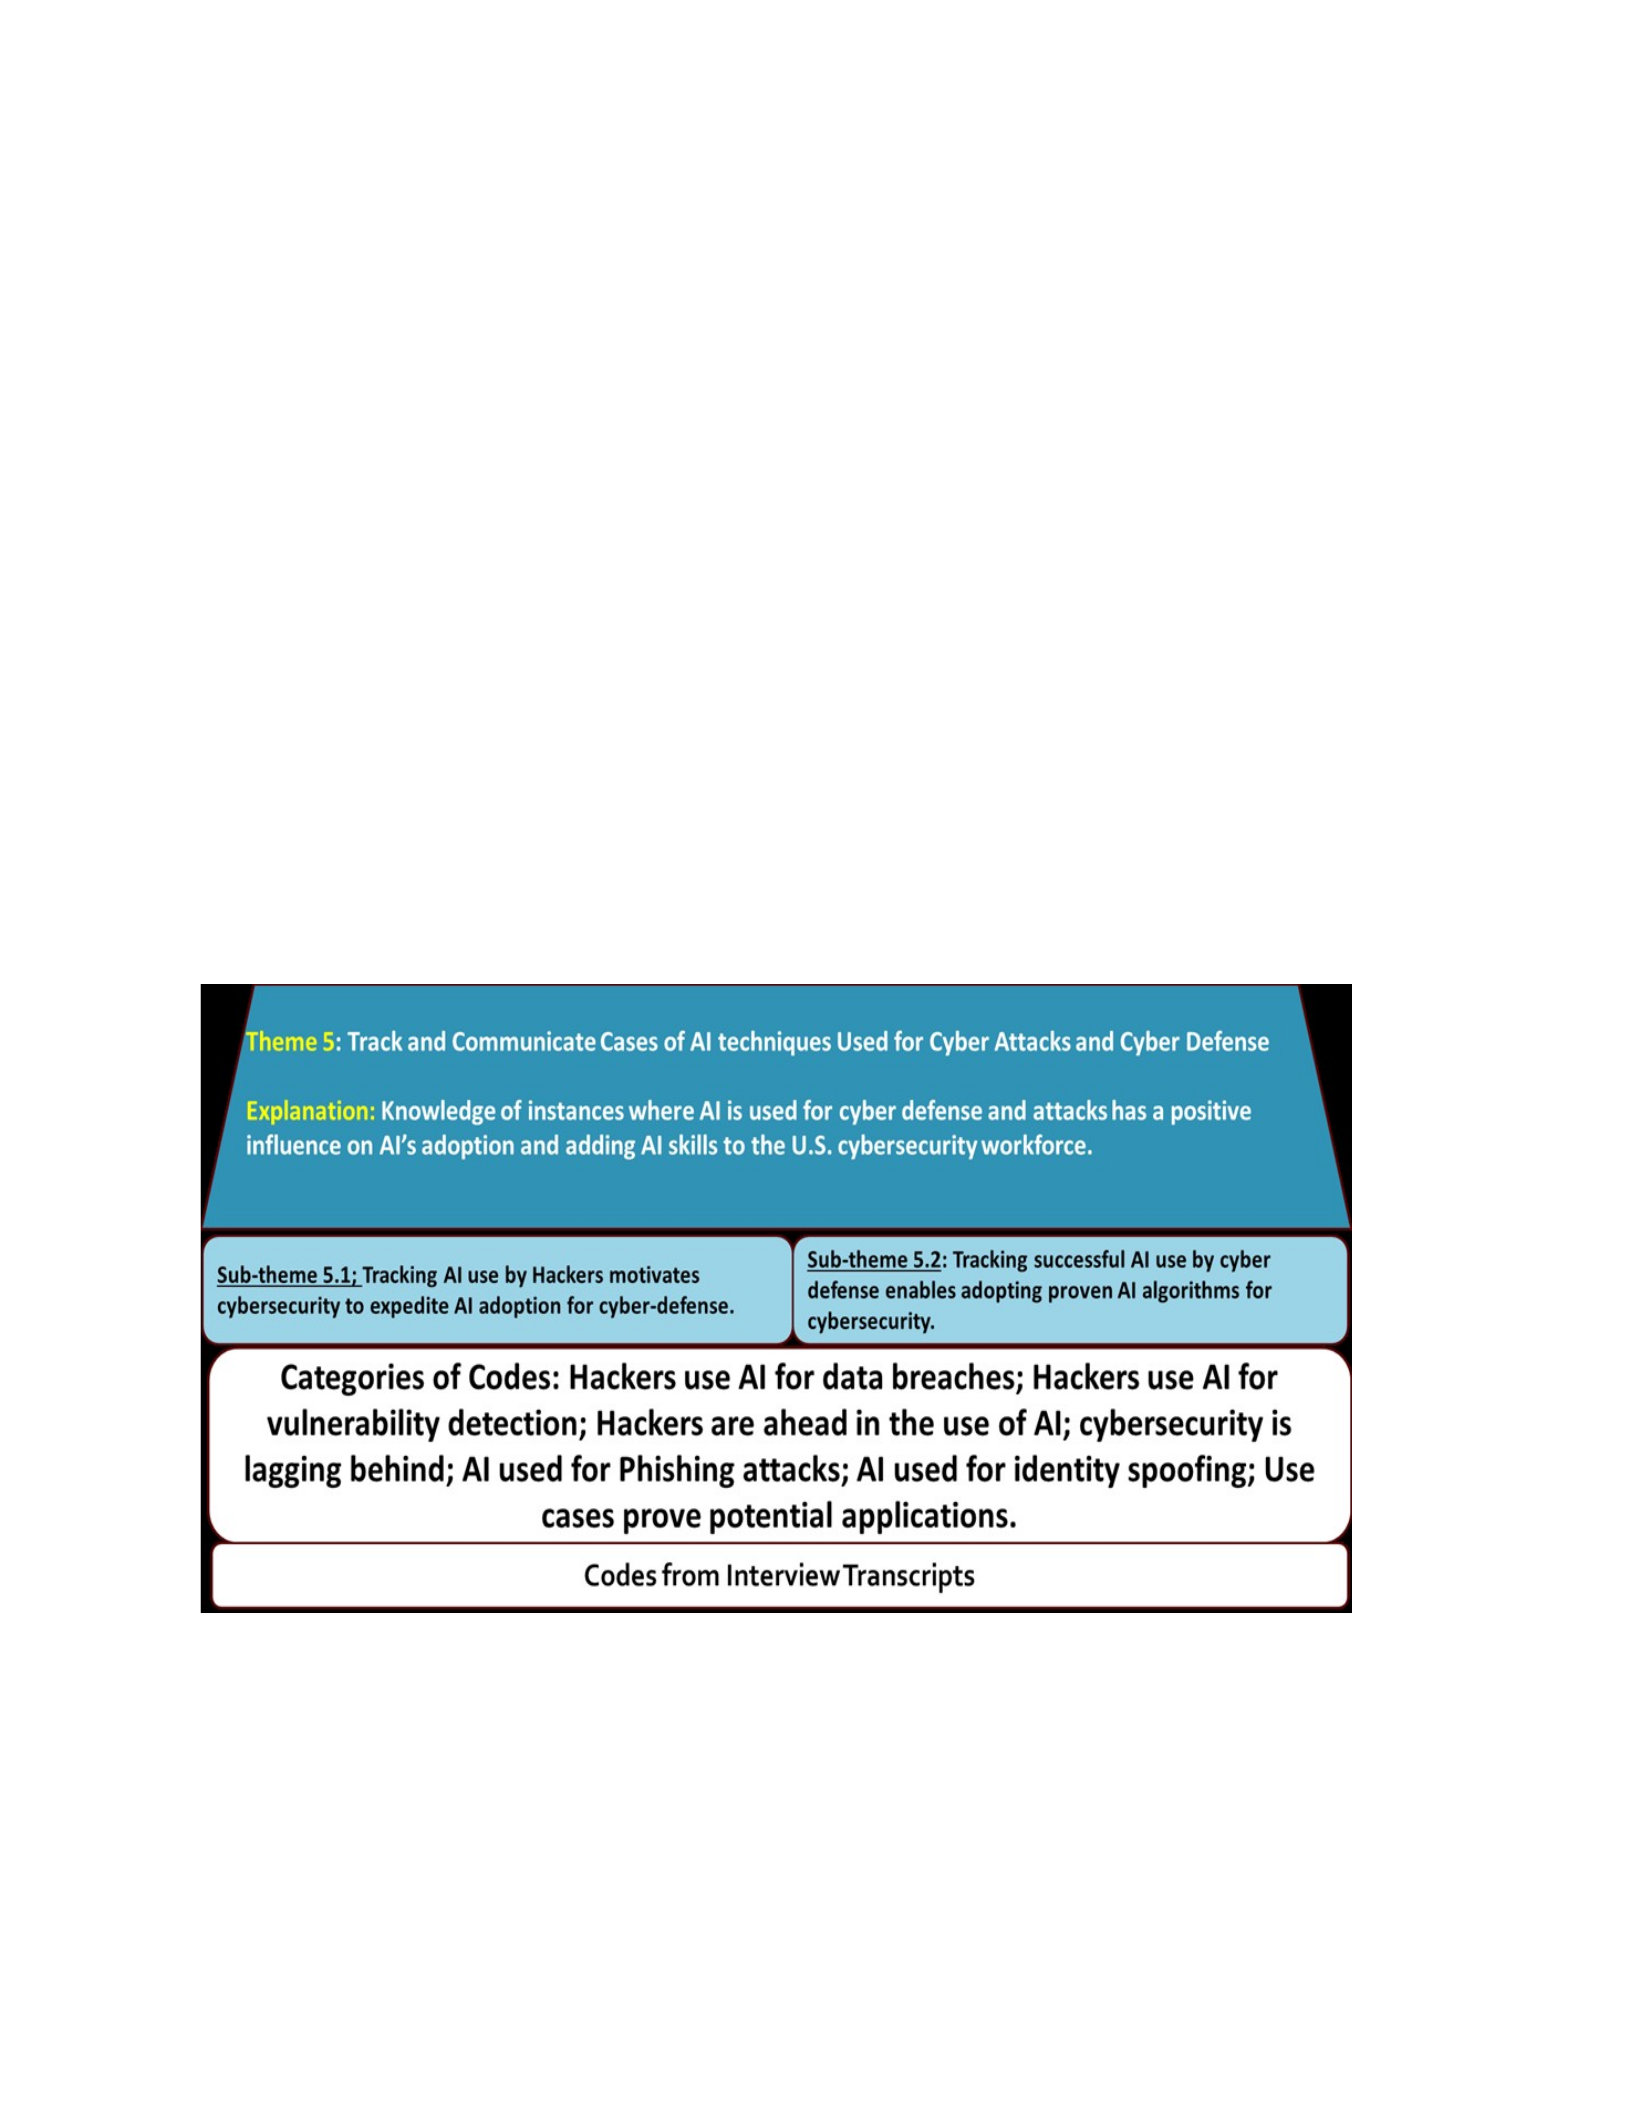
AI used for phishing attacks, (f) AI used for identity spoofing, and (g) Use cases prove potential
applications helped derive the theme ‘Communicate Cases of AI Used for Cyber-
Attacks and Cyber-Defense.’
Two sub-themes with additional attributes were also identified when deriving the fifth
theme. The first sub-theme is that credible information about the successful use of AI algorithms
for cyber defense motivates cybersecurity professionals and expedites AI skills for cybersecurity
professionals. The second sub-theme is that verifiable explanations of AI's use by hackers
increase the chances of cybersecurity professionals adopting AI to respond better to AI-based
cyber-attacks. Figure 29 represents theme five and its sub-themes.
Figure 29 Theme Five and Sub-Themes
Theme Six - Reliable, Explainable, and Risk-Free AI Applications for Cybersecurity
One of the topics discussed by the study participants was concerning the features that
would determine the operational readiness of AI applications for cybersecurity tasks. The
participants expressed awareness of the AI techniques, especially the machine learning

algorithms that could enhance cybersecurity practices by identifying patterns of threats and
security incidents in an overwhelming amount of event logs collected. They also pointed to the
ability of AI algorithms to learn from cybersecurity data, which reflects failed attempts to
recognize cyber threats. Furthermore, the participants preferred that the AI applications be built
with a few attributes that would prepare them for day-to-day cybersecurity operations.
According to the participants, the AI applications should be reliable in presenting their
findings clearly and concisely, with a confidence level attached, in cases where a finding could
not be fully confirmed. In addition, the AI applications are expected to explain their findings
instead of being an AI-based black-box tool. Furthermore, the participants would require the AI
applications to provide some guidance about the remediation of findings reported, much like the
current cybersecurity tools in use by U.S. cybersecurity professionals. Concerns were raised
about AI applications creating false alarms and posing a risk to the cybersecurity events logs fed
into the machine learning algorithms as inputs. Twelve participants contributed to the responses
used for this theme. Four more participants raised concerns about false alarms and data loss and
emphasized that they needed to be minimized for AI applications to be of reliable use for
cybersecurity tasks.
The code categories (a) Data-driven AI algorithms, (b) Cybersecurity is risk-averse, (c)
False alarms, (d) Data leaks, (e) Confidence levels in findings, (f) Need mitigations for findings,
(g) Explain findings, (h) AI as a black box, helped derive the theme ‘Reliable, Explainable, and
Risk-Free AI Applications for Cybersecurity.’
Three sub-themes were identified, with additional attributes, under the main theme of
‘Reliable, Explainable, and Risk-Free AI Applications for Cybersecurity’ to address the details of
the main theme. The first sub-theme refers to minimal false alarms when AI techniques are
applied to cybersecurity tasks. The second sub-theme emphasizes that AI techniques in reporting
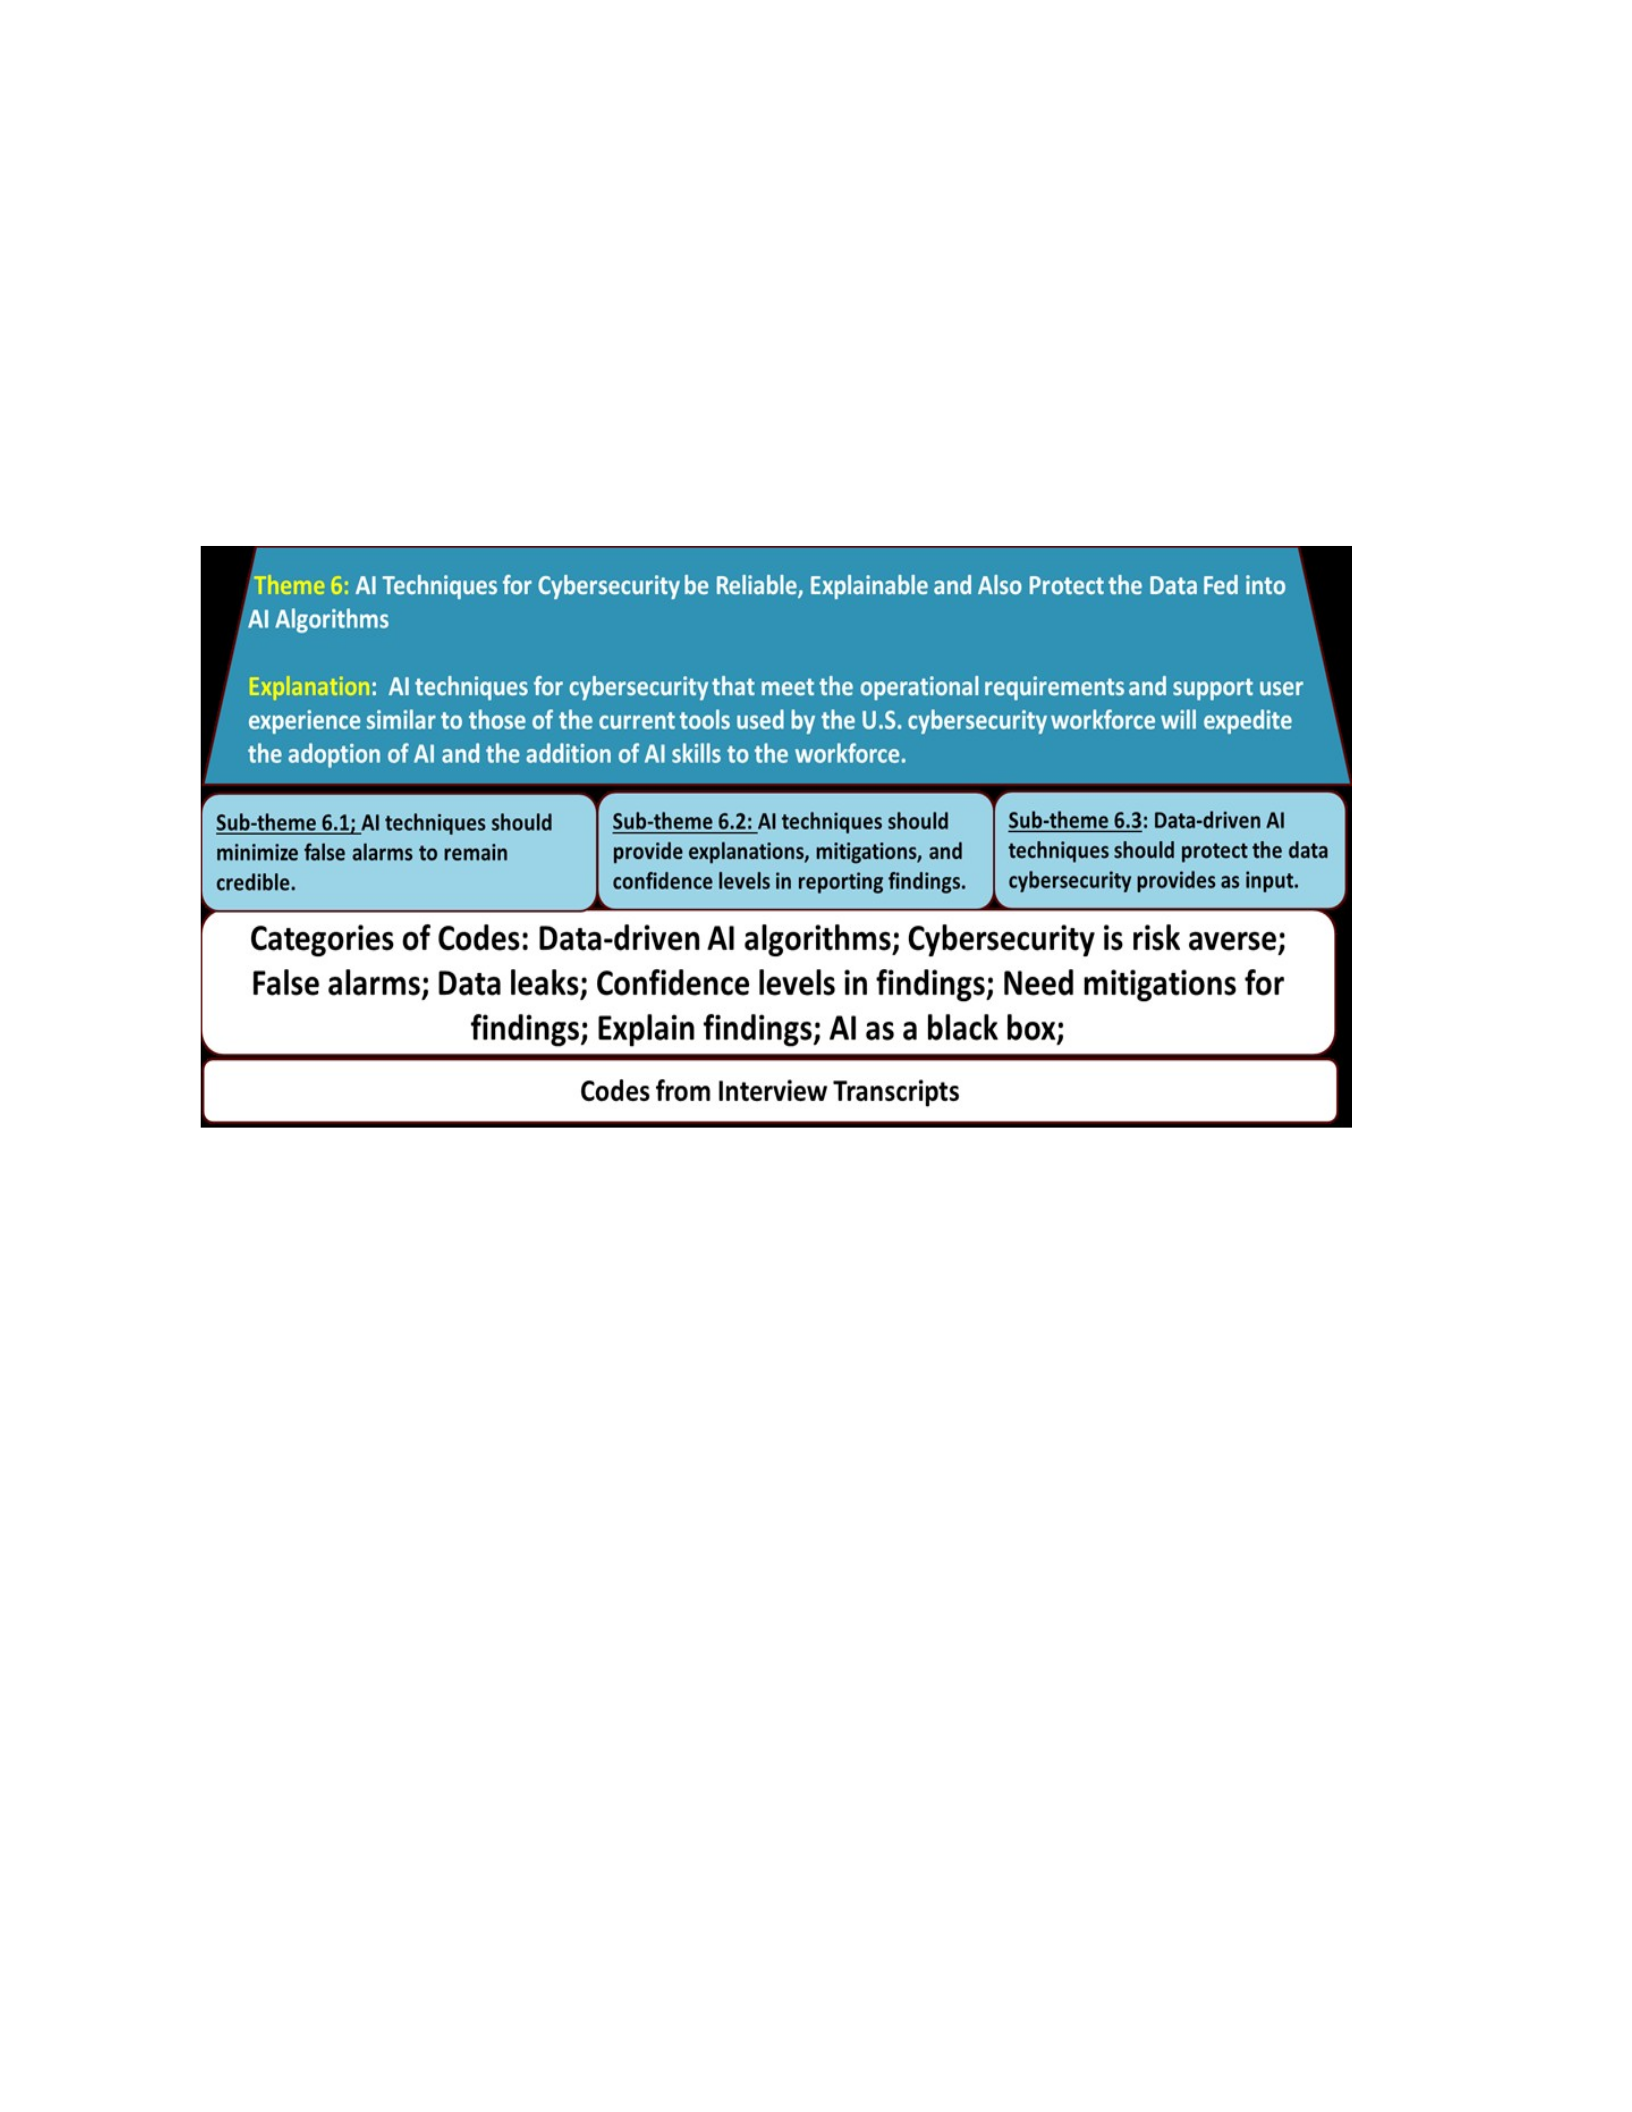
the findings to cybersecurity professionals should include explanations, mitigation steps, and
confidence levels. The third sub-theme concerns cybersecurity data protection the AI algorithms
use. Figure 30 is a visual representation of theme six and its sub-themes.
Figure 30 Theme Six and Sub-Themes
Chapter 5: Findings and Recommendations
About Themes, Findings, and Factors
This study aims to explore, identify, and understand the factors impacting the addition of
AI skills to the U.S. cybersecurity workforce and provide insights into the positive factors that
aid in adding AI skills and the negative factors that impede it. The findings presented from this
study are based on the themes that emerged from the qualitative grounded theory approach to the
analysis of the data collected as interview transcripts. Each theme, combined with its sub-themes,
led to a primary finding summarizing the theme, its impacts on the research objective, and
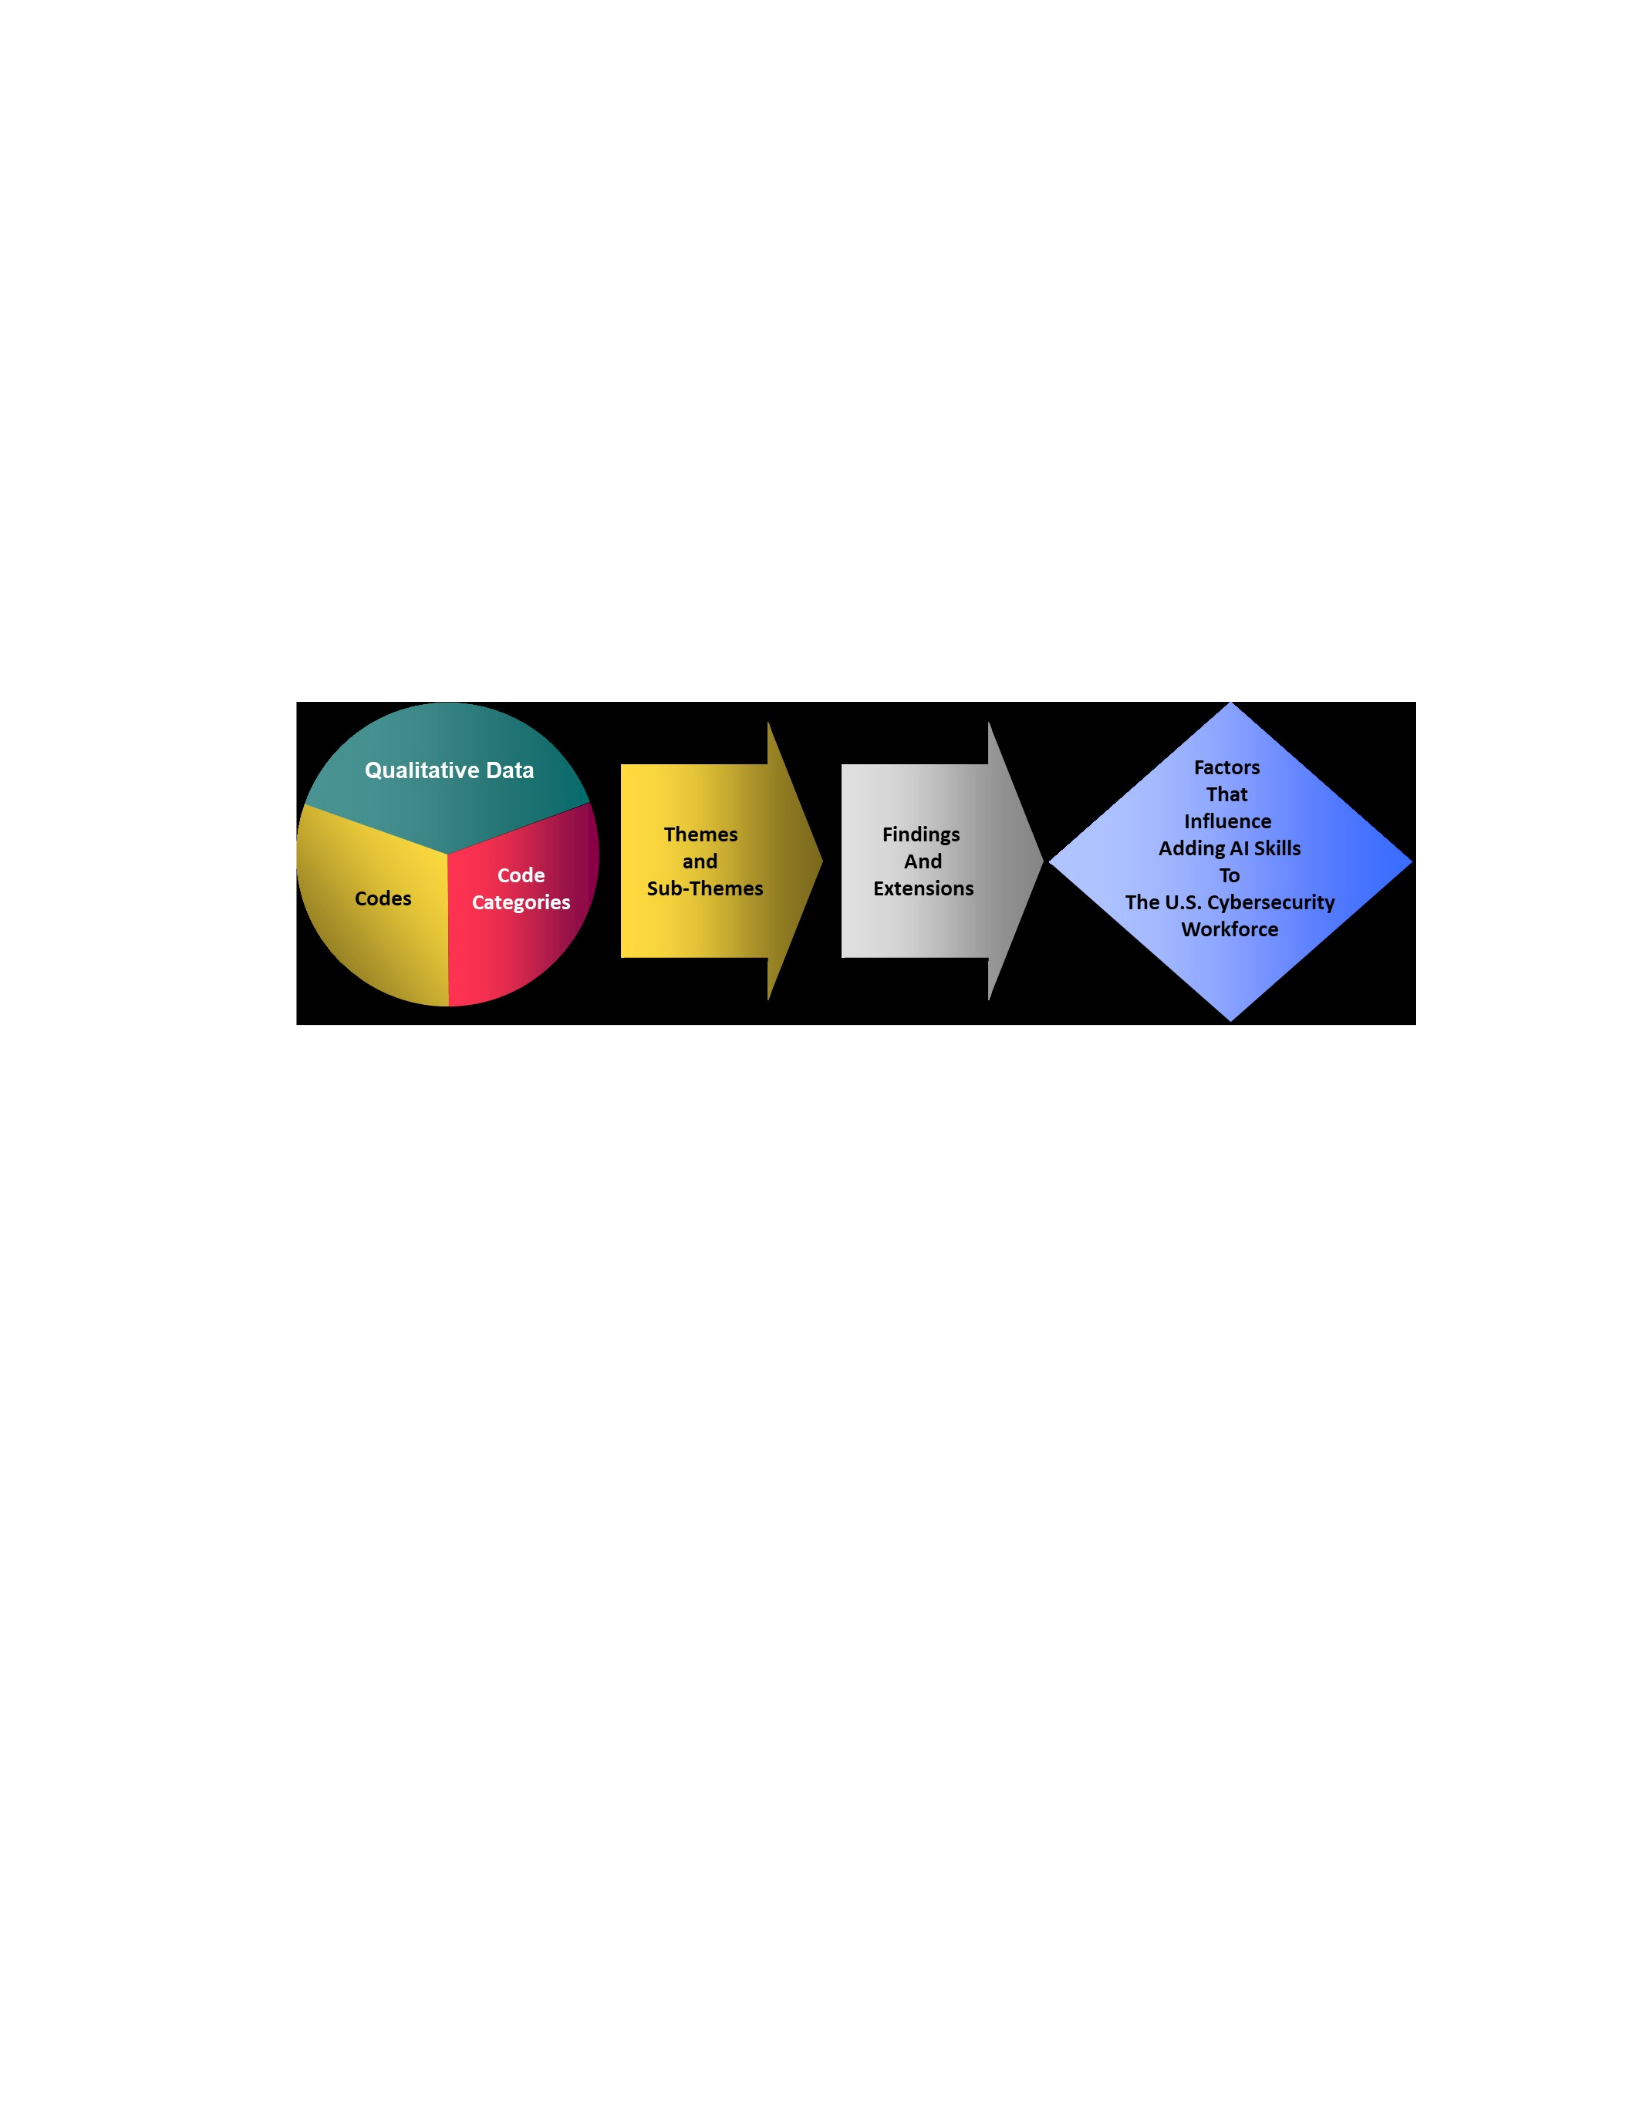
additional extensions to the finding. The extensions add further details to the finding. The
findings and extensions are interpreted, leading to the determination of positive and negative
factors. In summary, qualitative data have been used as the building blocks, through themes,
subthemes, findings, and extensions, to identify the factors behind adding AI skills to the U.S.
cybersecurity workforce. Figure 31 summarizes the progression from qualitative data to the
factors behind AI skills for the U.S. cybersecurity workforce.
Figure 31 Qualitative Data to Themes, Findings, and Factors Behind AI Skills
Findings and Factors Behind AI Skills
Channeling AI Information Through Trusted and Familiar Sources
Channeling AI information to the U.S. Cybersecurity workforce optimally increases the
chances of adding AI skills to the U.S. Cybersecurity workforce. Analyzing the participants'
opinions, preferences, and ongoing experiences led to the finding that the AI information directed
to the U.S. cybersecurity workforce through trusted and familiar channels is an enabler for
adding AI skills. Three extensions that add more details to this finding were also identified.
The first extension is that AI information tailored to the specific cybersecurity
requirements of the industry sector of a cybersecurity professional, such as healthcare and
finance, will improve and expedite the comprehension of AI's applicability to cybersecurity. An
example is the AI information elaboration that states how AI algorithms apply to the privacy and
security requirements of healthcare organizations mandated to comply with the Health Insurance

Portability and Accountability Act of 1996 (HIPAA).
The second extension is that AI information that matches specific AI algorithms
applicable to the cybersecurity practice areas improves comprehension. An example is the AI
information that states that the supervised machine learning algorithm applies to analyzing large
volumes of cybersecurity event logs and identifying potential threats.
The third extension is that AI information targeting the U.S. Cybersecurity workforce is
more effective when it is educational, clear, coherent, and concise, recognizing AI applications
for cybersecurity as relatively new.
This finding and its extensions are interpreted to derive the factors behind adding AI
skills to the U.S. Cybersecurity workforce. When AI information is directed to the U.S.
cybersecurity workforce through trusted and familiar channels to increase reliability and
credibility, it acts as a positive factor. Since AI information is new and still emerging, it needs to
be directed to the U.S. cybersecurity workforce as educational content in a clear, coherent, and
concise manner, and this would be another positive factor. When AI information in which
specific AI algorithms are matched against specific cybersecurity practice areas is directed to the
cybersecurity professionals, they enhance and expedite comprehension, which would be a third
positive factor from this finding. AI information tailored to the specific cybersecurity
requirements of the industry sector of cybersecurity professionals, such as federal civilians,
healthcare, and finance, also enables comprehension and increases the chances of AI’s adoption.
When AI information from numerous sources is directed to the U.S. cybersecurity
workforce and perceived as conflicting, overwhelming, and unverifiable, it reduces trust and
comprehension and impedes AI for cybersecurity.

Adding AI for Cybersecurity to U.S. Laws, Compliances, and Regulations
Cybersecurity requirements mandated by U.S. Laws, Compliances, and Regulations, and
the resulting technical standards, reporting requirements, and metrics to measure effectiveness,
play a significant role in U.S. Cybersecurity practices across all industry sectors. The U.S.
national AI initiatives focus more on secure, trustworthy, and fair AI applications and less on how
AI could benefit and strengthen cybersecurity. The study participants expressed the need for AI
topics to strengthen cybersecurity in U.S. Laws, Compliances, and Regulations. Including
guidelines, technical standards, and frameworks for applying AI techniques will seamlessly
merge into the critical role of U.S. Laws, Compliances, and Regulations in Cybersecurity
practices. Three extensions that explain the benefits behind this finding were also identified.
The first extension is that when guidelines, technical standards, and frameworks for
applying AI techniques for cybersecurity are introduced into U.S. Laws, Compliances, and
Regulations, obtaining AI skills becomes a cybersecurity job requirement and integrates AI
applications into organizational cybersecurity policies and procedures.
The second extension is that adding AI to compliance and regulation-driven cybersecurity
requirements could result in AI topics for the cybersecurity professional certification (e.g.,
CISSP, CEH, CISA) and organization accreditations (e.g., ISO 27001). AI skills applicable to
cybersecurity will then be required to be certified and maintained.
A third extension is that AI in compliance and regulation-driven cybersecurity
requirements will influence organizational budgeting and procurement processes, simplifying the
purchase of AI-related services and tools.
This finding and its extensions are interpreted as leading to additional factors behind AI
skills for the U.S. Cybersecurity workforce. AI’s inclusion in compliance- and regulation-driven

cybersecurity requirements integrate AI into organizational cybersecurity policies and procedures
and makes obtaining AI skills a cybersecurity job requirement; hence, it can be seen as a positive
factor. AI’s inclusion in cybersecurity certification course contents incentivizes AI skills for
professionals who pursue those certifications and becomes another positive factor. The same
applies when organizations pursue cybersecurity accreditations with AI content. AI’s inclusion in
regulation-driven cybersecurity requirements also simplifies procuring AI-related services and
tools for cybersecurity tasks, acting as another enabler.
Fewer cybersecurity professionals will obtain AI skills independently without AI
techniques being introduced into their job requirements. Hence, delays in introducing AI topics
in support of cybersecurity to U.S. Laws, Compliances, and Regulations can impede adding AI
skills.
Integrating AI capabilities into Cybersecurity Tools
While discussing the AI capabilities increasingly proven to support cybersecurity tasks,
such as machine learning for vulnerability identification using event logs, the study participants
referred to and explained the importance of AI capabilities integrated with the current
cybersecurity tools instead of being standalone AI tools. Cybersecurity professionals prefer to
harness AI capabilities added as extra features to their current cybersecurity tools. This
integration will smoothen the process of applying AI techniques for cybersecurity tasks, expedite
the adoption of AI, and add AI skills. Three extensions to this finding that explain the benefits
further were also identified.
The first extension to this finding concerns verifying and validating new techniques, such
as AI, before they are applied to cybersecurity tasks. The U.S. Cybersecurity professionals are
risk averse. Their job responsibilities are centered around risk management. They consider
integrating AI capabilities into their current cybersecurity tools as the fastest means to test the AI

techniques thoroughly and establish their reliability before the cybersecurity team could use them
routinely.
The second extension to this finding recognizes that AI capabilities are growing fast and
relates to the need to upgrade the AI capabilities for use by the cybersecurity team as newer and
better AI algorithms emerge. Cybersecurity professionals consider the processes in place to
upgrade their cybersecurity tools as mature and proven. They would repurpose them for adding
newer AI algorithms when AI capabilities are integrated with the cybersecurity tools.
The third extension to this finding concerns the installation and maintenance based on
vendor-supplied revisions, training, and the learning curve as newer techniques are introduced
for cybersecurity tasks. Cybersecurity professionals view integrating AI capabilities with the
current cybersecurity tools as the least burdensome path to adopt and maintain AI for
cybersecurity.
This finding and its extensions lead to additional factors behind AI skills for the U.S.
Cybersecurity workforce. AI techniques integrated into the current cybersecurity tools reduce the
learning curve and play a positive role in expediting the adoption of AI. In addition, integration
into the current cybersecurity tools expedites the installation, upgrades, maintenance, and
training required for applying AI to cybersecurity tasks and, hence, is an enabler of AI skills.
Integration is also a positive factor since it facilitates thorough testing and expedites the
validation and verification of AI techniques. On the contrary, standalone AI applications for
cybersecurity tasks considered another tool, will require separate installation, upgrades,
maintenance, and training, slowing down AI’s adoption.
Combining AI Training for Cybersecurity with Organizational Awareness
For AI techniques to be adopted for cybersecurity tasks, cybersecurity professionals must
understand AI's capabilities, limitations, and risks. In expressing this, the study participants

identified that teamwork within their organization is essential for AI to be successfully adopted
for cybersecurity. The participants preferred higher levels of AI awareness for the rest of the
organization for teamwork success. This finding concerns AI education and training for
cybersecurity professionals that should be combined with, at a minimum, general AI awareness
training for the rest of the organization.
Extensions to this finding that explain the benefits were also identified. Increased
organizational awareness of AI helps in the management of AI expectations. The cybersecurity
professionals and the organizational staff who team with them will better understand AI's risks,
capabilities, and limitations. In addition, it helps in obtaining data for the data-driven machine
learning AI algorithms. Furthermore, it helps prioritize the organization's AI resources to
strengthen cybersecurity.
The findings and their extensions lead to additional factors behind AI skills. AI training
for cybersecurity professionals, combined with increased organizational awareness of AI, is a
positive factor since it supports the essential requirements of AI’s adoption, such as teamwork,
managing expectations better, obtaining data for data-driven algorithms, and prioritizing AI
resources for cybersecurity. On the contrary, when a cybersecurity team starts adopting AI
applications without organizational awareness of AI, organizational support could be slowed
down, and organizational AI resources for cybersecurity could be more challenging to obtain.
Channeling Instances of AI in Cyber Defense and Cyber Attack
The study participants discussed cyber attackers using AI and cyber defenders lagging in
the use of AI. They expressed a need for credible and well-explained real-life instances of AI
techniques applied for cyber defenses and cyber-attacks. According to them, such use cases help
strengthen the role AI could play in cyber defense and demonstrate the urgency for adopting AI

to counter cyberattacks, which already use AI with malicious intent. The information they
considered valuable regarding the cases of AI for cyber defense was the AI techniques used to
counter the attacks, their effectiveness, and the lessons learned. The information they considered
valuable regarding the cases of AI for cyber-attacks were the AI techniques used by the attackers,
the vulnerabilities they exploited, and the impacts.
Two extensions describe the benefits in support of this finding. The first extension is that
tracking AI used by hackers and channeling the cases with the details of techniques used,
impacts, exploited vulnerabilities, attempted countermeasures, and lessons learned motivates
cybersecurity to expedite AI adoption for cyber-defense. The second extension is that tracking
successful AI use by cyber defense helps establish proven AI algorithms for countering AI-based
attacks and expedites AI adoption for cyber defense.
This finding and its extensions contribute to additional factors behind adding AI skills.
Analytical and hypothetical explanations of AI’s use for cyber defense and cyber-attacks, with
attackers leading the defenders in using AI to exploit vulnerabilities, were considered valuable by
the study participants. However, the participants expressed that credible, well-explained, reallife
instances of AI techniques applied for cyber defenses and cyber-attacks are a strong positive
factor in adopting AI and obtaining AI skills.
Operational Readiness of AI for Cybersecurity Practices
While recognizing the growing AI capabilities that could automate cybersecurity tasks,
help analyze the overwhelming amount of event log data collected by cybersecurity teams,
counter the cyber-attacks that already use AI, and even help in the ethical simulation of
cyberattacks, the participants discussed the operational readiness expectations from AI
techniques.

The cybersecurity professionals approached AI’s readiness by comparing the would-be AI
techniques against the attributes of their current cybersecurity tools.
Attributes of AI techniques cybersecurity professionals consider essential for adopting AI
as a dependable component of cybersecurity practices helped define this finding. This finding is
that to be of reliable and routine use for cybersecurity tasks; the AI techniques need to produce
understandable results that could be applied, in combination with human inputs and other tools,
to identify and resolve vulnerabilities and threats.
Three extensions were also identified along with this finding. The first extension is that
AI techniques, when applied to cybersecurity tasks, should minimize false alarms in identifying
vulnerabilities to remain credible. The second extension states that AI techniques should explain
their outcomes instead of being a black box, suggest mitigations, and report confidence levels of
identified vulnerabilities when reporting findings. The third extension is that data-driven AI
algorithms, such as machine learning, should protect the data that the cybersecurity team would
provide as input to them.
This finding and its three extensions also lead to factors behind AI skills for the
cybersecurity workforce. AI techniques that are operationally ready for cybersecurity tasks
through explainable and reliable findings while ensuring input data protection are considered
enablers of AI skills. On the contrary, AI applications for cybersecurity that act as black boxes
without explanation of their findings or cause data leaks are considered not ready for the day-
today operations of the cybersecurity team and are likely to be an impediment.
Summary of Factors Behind AI Skills
The six findings and their extensions have been interpreted as factors behind AI skills for
the U.S. Cybersecurity workforce. Table 8 summarizes these findings and the related factors.
Table 9 lists only the positive and negative factors.
Table 8 Findings and Factors Behind AI Skills
Finding and Extensions Finding and Extensions Interpreted as
Factors Behind AI Skills for the U.S. Cybersecurity Workforce
AI information directed
to the U.S. cybersecurity
workforce through
trusted and familiar
channels enables the
addition of AI skills.
Extensions: Should also
be (a) Educational, (b)
Industry Sector Specific,
and (c) Match AI
techniques to
cybersecurity practices.
Positive Factors:
1. AI information should be directed to the U.S. cybersecurity
workforce through trusted and familiar channels to increase trust
and credibility.
2. Since AI information is new and still emerging, it needs to be
directed to the U.S. cybersecurity workforce as educational
material in a clear, coherent, and concise manner.
3. AI algorithms matched to be valuable to specific cybersecurity
practice areas are easier to understand.
4. AI information addressing the specific cybersecurity requirements
of the industry segment of cybersecurity professionals, such as
federal civilians, the Department of Defense, healthcare, and
finance, will improve and expedite comprehension.
Finding and
Extensions
Finding and Extensions Interpreted as
Factors Behind AI Skills for the U.S. Cybersecurity Workforce
Negative Factor:
1. AI information from numerous sources directed to the U.S.
cybersecurity workforce and perceived as conflicting,
overwhelming, and unverifiable reduce trust and comprehension.
AI Topics in
Compliance and
Regulatory
Cybersecurity
Requirements is an
enabler of AI skills.
Extensions: AI skills then
(a) become a
cybersecurity job
requirement,
(b) are integrated into
organizational
cybersecurity
policies and
procedures, (c) are
added to
cybersecurity
professional
certifications (e.g.,
CISSP, CEH, CISA) and
organization
accreditations, and (d)
are integrated into
organizational budgeting
and procurement
processes.
Positive Factors:
1. AI’s inclusion in compliance and regulation-driven cybersecurity
requirements integrates AI into organizational cybersecurity
policies and procedures and makes obtaining AI skills a
cybersecurity job requirement.
2. AI’s inclusion in compliance and regulation-driven cybersecurity
requirements potentially will result in AI’s inclusion in
cybersecurity certifications, mandating AI skills for professionals
who require those certifications.
3. AI’s inclusion in compliance and regulation-driven cybersecurity
requirements will influence budgeting and procurement processes
to support AI techniques for cybersecurity tasks and AI skills for
the workforce.
Negative Factor:
1. Fewer cybersecurity professionals will obtain AI skills
independently without AI techniques being introduced into their
job requirements.
AI Techniques
Integrated into
Cybersecurity Tools is an
enabler of AI skills.
Extensions: AI techniques
integrated (a) Enables
verification and
validation, (b) adding
newer AI algorithms
easier, and (c) makes
maintenance,
Positive Factors:
1. AI techniques integrated into the current cybersecurity tools
expedite the adoption of AI applications for cybersecurity tasks.
2. AI techniques integrated into the current cybersecurity tools
expedite the installation, upgrades, maintenance, and training of
the AI applications for cybersecurity tasks.
3. AI techniques integrated into the current cybersecurity tools
expedite validating and verifying AI applications for cybersecurity
tasks.
Negative Factor:
Finding and Extensions Finding and Extensions Interpreted as
Factors Behind AI Skills for the U.S. Cybersecurity Workforce
installation, upgrades, and 1. Stand-alone AI applications for cybersecurity tasks, perceived as
learning simpler. another tool, will require separate installation, upgrades,
maintenance, and training, hence impede AI’s adoption.
When combined with
Awareness for Other
Organizational Staff, AI
Education and Training
for All Cybersecurity
Roles is an enabler of AI
skills.
Extensions: General AI
awareness helps (a)
teamwork and data
collection for machine
learning algorithms, (b)
better management of
expectations from AI, and
(c) prioritize AI resources
for cybersecurity.
Positive Factors:
1. When AI education for the U.S. cybersecurity staff is combined
with AI awareness training for the rest of their organization, it
improves the teamwork essential for adopting AI, and facilitates
data-collection for machine-learning algorithms.
2. Broader organizational awareness enables the better management
of expectations from AI applications since the cybersecurity
professionals and the organizational staff who team with them will
better understand AI's risks, capabilities, and limitations.
3. Broader organizational awareness helps prioritize organizations' AI
resources for more robust cybersecurity.
Negative Factor:
1. When a cybersecurity team starts adopting AI applications without
organizational awareness of AI, organizational support could be
slowed down, and organizational AI resources for cybersecurity
could be more challenging to obtain.
Track and communicate
cases of AI techniques
used in cyber defense and
attacks.
Extensions: AI-use cases
help (a) validation of AI
for cyber defense, (b)
expedited adoption of AI
for cyber defense, and
(c) identify AI
algorithms to counter
AI-based cyber-attacks.
Positive Factors:
1. When AI’s real-life uses for cyber defense and attacks are tracked
and directed with additional details to the U.S. Cybersecurity
workforce, it validates AI’s potential for strengthening
cybersecurity.
2. Tracking AI used by hackers and channeling the cases with the
details of techniques used, countermeasures, and lessons learned
motivates cybersecurity to expedite AI adoption for cyber-defense.
3. Tracking successful AI use by cyber defense increases the
reliability of AI, enables the adoption of proven AI algorithms for
cyber defense, and expedites AI skills for cybersecurity
professionals.
Negative Factor:
1. Information about AI’s potential to strengthen cyber defenses
without supporting pieces of evidence from real-life cases is
considered unverifiable by cybersecurity professionals.
AI Techniques for
Cybersecurity must be
reliable and explainable
and protect the data fed as
inputs to AI algorithms.
Positive Factors:
1. AI applications for cybersecurity tasks should be operationally
ready for use, with data protection, explainability, and reliability
features.
2. AI applications for cybersecurity tasks should minimize false
alarms in identifying vulnerabilities to remain credible.
Finding and Extensions Finding and Extensions Interpreted as
Factors Behind AI Skills for the U.S. Cybersecurity Workforce
Extensions: AI techniques
should (a) provide
explanations, confidence
levels, and recommend
mitigation steps, (b)
minimize false alarms,
and (c) protect the cyber-
security data fed as inputs
to AI algorithms.
3. AI applications for cybersecurity tasks should provide explanations
instead of being a black box, suggest mitigations, and report
confidence levels of identified vulnerabilities when reporting
findings.
4. AI applications that use data-driven machine learning algorithms
should protect the data that the cybersecurity team would provide
as input to the algorithms.
Negative Factor:
1. AI applications for cybersecurity that act as black boxes without
explanation of their findings or cause data leaks are considered not
ready for the day-to-day operations of the cybersecurity team.
Table 9 List of Positive and Negative Factors
Factors Behind AI Skills for the U.S. Cybersecurity Workforce
Positive Factors:
1. AI information should be directed to the U.S. cybersecurity workforce through trusted
and familiar channels to increase trust and credibility.
2. Since AI information is new and still emerging, it needs to be directed to the U.S.
cybersecurity workforce as educational material in a clear, coherent, and concise manner.
3. AI algorithms matched to be valuable to specific cybersecurity practice areas are easier
to understand.
4. AI information addressing the specific cybersecurity requirements of the industry
segment of cybersecurity professionals, such as federal civilians, the Department of
Defense, healthcare, and finance, will improve and expedite comprehension.
5. AI’s inclusion in compliance and regulation-driven cybersecurity requirements integrates
AI into organizational cybersecurity policies and procedures and makes obtaining AI
skills a cybersecurity job requirement.
6. AI’s inclusion in compliance and regulation-driven cybersecurity requirements
potentially will result in AI’s inclusion in cybersecurity certifications, mandating AI
skills for professionals who require those certifications.
Factors Behind AI Skills for the U.S. Cybersecurity Workforce
7. AI’s inclusion in compliance and regulation-driven cybersecurity requirements will
influence budgeting and procurement processes to support AI techniques for
cybersecurity tasks and AI skills for the workforce.
8. AI techniques integrated into the current cybersecurity tools expedite the adoption of AI
applications for cybersecurity tasks.
9. AI techniques integrated into the current cybersecurity tools expedite the installation,
upgrades, maintenance, and training of the AI applications for cybersecurity tasks.
10. AI techniques integrated into the current cybersecurity tools expedite validating and
verifying AI applications for cybersecurity tasks.
11. When AI education for the U.S. cybersecurity staff is combined with AI awareness
training for the rest of their organization, it improves the teamwork essential for adopting
AI and facilitates data collection for machine-learning algorithms.
12. Broader organizational awareness enables the better management of expectations from
AI applications since the cybersecurity professionals and the organizational staff who
team with them will better understand AI's risks, capabilities, and limitations.
13. Broader organizational awareness helps prioritize organizations' AI resources for more
robust cybersecurity.
14. When AI’s real-life uses for cyber defense and attacks are tracked and directed with
additional details to the U.S. Cybersecurity workforce, it validates AI’s potential for
strengthening cybersecurity.
15. Tracking AI used by hackers and channeling the cases with the details of techniques
used, countermeasures, and lessons learned motivates cybersecurity to expedite AI
adoption for cyber-defense.
16. Tracking successful AI use by cyber defense increases the reliability of AI, enables the
adoption of proven AI algorithms for cyber defense, and expedites AI skills for
cybersecurity professionals.
17. AI applications for cybersecurity tasks should be operationally ready for use, with data
protection, explainability, and reliability features.
18. AI applications for cybersecurity tasks should minimize false alarms in identifying
vulnerabilities to remain credible.
Factors Behind AI Skills for the U.S. Cybersecurity Workforce
19. AI applications for cybersecurity tasks should provide explanations instead of being a
black box, suggest mitigations, and report confidence levels of identified vulnerabilities
when reporting findings.
20. AI applications that use data-driven machine learning algorithms should protect the data
that the cybersecurity team would provide as input to the algorithms.
Negative Factors:
1. AI information from numerous sources directed to the U.S. cybersecurity workforce and
perceived as conflicting, overwhelming, and unverifiable reduce trust and
comprehension.
2. Fewer cybersecurity professionals will obtain AI skills independently without AI
techniques being introduced into their job requirements.
3. Stand-alone AI applications for cybersecurity tasks, perceived as another tool, will
require separate installation, upgrades, maintenance, and training, impeding AI’s
adoption.
4. When a cybersecurity team starts adopting AI applications without organizational
awareness of AI, organizational support could be slowed down, and organizational AI
resources for cybersecurity could be more challenging to obtain.
5. Information about AI’s potential to strengthen cyber defenses without supporting pieces
of evidence from real-life cases is considered unverifiable by cybersecurity
professionals.
6. AI applications for cybersecurity that act as black boxes without explanation of their
findings or cause data leaks are considered not ready for the day-to-day operations of the
cybersecurity team.

Recommended Actions for Adding AI Skills
The positive factors identified from each finding and its extensions have been further
treated as objectives, and a series of recommended actions have been composed to meet those
objectives. For example, for the first finding of directing AI information through familiar and
trusted channels and the positive factors from the finding considered as objectives, the initial
recommendation is to identify familiar and trustworthy sources the U.S. cybersecurity workforce
refers to for emerging technologies applicable to cyber defense. The source could vary based on
the type of organization they work for, e.g., U.S. federal civilian, department of defense, finance,
health care. Following that, entities targeting their AI information to the U.S. cybersecurity
workforce should channel it through these sources.
For the second finding of including AI topics in compliance and regulatory cybersecurity
requirements, the primary recommendation begins with the U.S. national initiatives on AI. At the
time of this study, the U.S. national initiative on AI was progressing on many fronts. Presently,
guidance for ethics, privacy, and risks in collecting the data, building, and operating AI
applications in a secure and trustworthy is under development. To expedite the adoption of AI
techniques for cybersecurity and to enable AI skills for the U.S. cybersecurity workforce, these
U.S. initiatives also need to prioritize AI applications for strengthening the U.S. cyber defense
and introduce AI framework, guidance, and standards into the compliance and regulation-related
cybersecurity requirements applicable across public and commercial sectors.
For the third finding of seamlessly integrating AI techniques into cybersecurity tools, the
recommended actions relate to the entities offering AI techniques to U.S. cybersecurity practices.
The U.S. software vendors are already adding AI techniques to many of their software tools. As
AI algorithms are enhanced further into supporting the U.S. cybersecurity practices, they should

become seamless extensions to the cybersecurity tools presently used by the U.S. cybersecurity
workforce and preferably should support similar user experience.
The fourth finding is about educating cybersecurity professionals of all roles on relevant
AI skills and, at the same time, raising the general awareness of AI for the rest of the
organization. The recommended actions from this finding relate to entities entrusted with AI
education and training for the U.S. cybersecurity workforce and others in their organizations.
Those in charge of U.S. organizational educational, talent management, and skills improvement
programs should provide AI courses for cybersecurity tasks, targeting all the cybersecurity
workforce's job roles and AI awareness courses for the rest of the organizational personnel.
External entities offering AI courses should similarly structure their offering for the cybersecurity
workforce and other organizational personnel.
The fifth theme is tracking and directing to the U.S. cybersecurity workforce real-life
cases of AI’s use in cyber defense and cyber-attacks, with sufficient details. The recommended
actions from this finding relate to entities entrusted with AI education and training for the U.S.
cybersecurity workforce. Units within an organization and external entities providing education,
talent management, skills improvement courses, and AI technical information for the U.S.
cybersecurity workforce should include credible and verifiable instances of AI techniques used
for cyber defense and cyber-attacks.
The sixth finding concerns the operational readiness of AI techniques for cybersecurity
practices and the need for AI applications to be reliable, explainable, and capable of protecting
the cybersecurity data fed into them. The recommended actions relate to the entities offering AI
techniques to the U.S. cybersecurity practices. AI applications for U.S. cybersecurity should have
features and user experiences similar to current software tools used by the U.S.
cybersecurity workforce; AI algorithms for cybersecurity should minimize false alarms, be
explainable when reporting findings as opposed to being a black box, recommend remediations,
associate a confidence level with findings, and protect the cybersecurity data fed into the
datadriven machine learning algorithms.
Table 10 summarizes the recommended actions based on the study findings.
Table 10 Recommended Actions by Findings
Finding
Recommendations to Enable Adding AI Skills to the
Applicable AI information should be
directed to the U.S. cybersecurity
workforce through trusted and familiar
channels.
U.S. Cybersecurity
Workforce Identify the familiar and
trustworthy sources the U.S.
cybersecurity workforce refers to for emerging
technologies applicable to cyber defense. The source could
vary based on the type of organization they work for, e.g.,
U.S. Federal Civilian, Department of Defense, Finance,
Health Care. Entities targeting their AI information to the
U.S. cybersecurity workforce should direct AI-related
information through these sources.
AI topics should be added to the laws,
compliances and regulations that
define cybersecurity requirements.
The U.S. national initiative on AI is progressing on
many fronts.
Presently, guidance for ethics, privacy, and risks in
collecting the data, building, and operating AI
applications in a secure and trustworthy is under
development.
These U.S. initiatives also need to prioritize AI
applications for strengthening the U.S. cyber defense
and introduce AI framework, guidance, and standards
into the compliance and regulation-related
cybersecurity requirements applicable across public
and commercial sectors.
AI techniques should be integrated into
cybersecurity tools.
The U.S. cybersecurity workforce uses software tools
to automate tasks and achieve efficiencies in their
practice areas. Some examples are software tools to
scan systems for vulnerabilities, secure configurations,
manage security events, and capture and analyze event
logs.
The U.S. software vendors are already adding AI
techniques to many of their software tools.
As AI algorithms are enhanced further into supporting
the U.S. cybersecurity workforce, they should become
seamless extensions to the cybersecurity tools
presently used by the U.S. cybersecurity workforce
and preferably should support similar use experience.
When AI capabilities become extensions, they could
potentially expedite AI’s adoption by the U.S.
cybersecurity workforce and enable the addition of AI
skills.
Finding Recommendations to Enable Adding AI Skills to the
U.S. Cybersecurity Workforce Those in
charge of U.S. organizational educational, talent
management, and skills improvement programs
should provide AI courses targeting all the
cybersecurity workforce's job roles and introductory
AI awareness courses for the rest of the organizational
Combine AI education and skills for personnel. External entities offering AI courses should
cybersecurity professionals with similarly structure their offering for the cybersecurity
awareness for others in the workforce and other organizational personnel. organization.
Including the cybersecurity workforce and others
will facilitate teamwork, collaboration, managing
expectations, and data gathering for AI algorithms,
which is essential for AI applications and adding AI
skills to the U.S. cybersecurity workforce. Units
within an organization and external entities providing
education, talent management, skills improvement
courses, and AI technical information for the U.S.
cybersecurity workforce should include
Track and communicate cases of AI credible and verifiable instances of AI techniques used
techniques used in cyber-attacks and for cyber defense and cyber-attacks. Furthermore, the
cyber defense. details about cyber-attacks, including the techniques used in the attacks, their
impacts, countermeasures, and lessons learned, will enhance AI’s adoption by cybersecurity
professionals.
AI techniques for cybersecurity
practices should be reliable,
explainable and protect the data fed
into AI algorithms.
AI applications for U.S. cybersecurity should have
features and user experiences like current software
tools used by the U.S. cybersecurity workforce; AI
algorithms for cybersecurity should minimize false
alarms, be explainable when reporting findings as
opposed to being a black box, recommend
remediations, associate a confidence level with
findings, and protect the cybersecurity data fed into
the data-driven machine learning algorithms.
Recommendations for Further Research
This study identified additional research questions while arriving at the themes, findings, and
factors behind AI skills for the U.S. cybersecurity workforce. These are recommended for further
research.

This study finds that routing AI information to cybersecurity professionals through trusted
and familiar channels will increase the chances of AI skills for the U.S. cybersecurity workforce.
A relevant follow-up study would be to identify the industry specific (E.g., Finance, Healthcare,
Federal Civilian, DOD) information sources (E.g., Websites, Webinars, BLOGS, Whitepapers,
social media, Online Educational Courses, Generative AI tools like ChatGPT) used often and
trusted by the cybersecurity professionals, for channeling AI skills and techniques to U.S.
cybersecurity workforce.
As this study finds that the introduction of AI topics in the Laws, compliances, and regulations
behind cybersecurity, and reporting on cases for cyber defense and cyber-attacks will increase
the chances of AI skills for the U.S. cybersecurity workforce, the research questions: (a)
What is the progression of AI-related topics in industry-specific compliance-related (E.g., FISMA,
ISO, HIPAA, PCI DSS) cybersecurity requirements and the associated technical standards? (b)
Are guidelines, frameworks, and standards specific to AI algorithms for cybersecurity challenges
emerging? Furthermore, (c) Are there requirements in development for tracking and reporting on
the adoption of AI for cyber defense and cyber-attacks? are recommended for further studies.
Based on the finding from this study that the seamless integration of AI techniques into the
current cybersecurity tools will expedite the adoption of AI for cybersecurity and adding AI skills,
the research questions: (a) What is the status of adding AI capabilities seamlessly to technical
tools (E.g., Vulnerability scanning, Intrusion detection, incident response, event management,
audit log analysis, threat intelligence.) used by the U.S. cybersecurity workforce?
(b) How many vendors offer standalone AI-based tools for the U.S. cybersecurity workforce? (c)
How many vendors have added AI techniques as extensions to current cybersecurity tools? (d) Which
cybersecurity tasks will be impacted by these AI-integrated cybersecurity tools? are recommended
for future studies.

Limitations of This Study
This qualitative grounded theory study collected data from semi-structured one-on-one
interviews with U.S. cybersecurity professionals. These participants had one or more professional
certifications to their credit from the International Information System Security
Certification Consortium (ISC2) and were members of the consortium’s Washington, D.C., chapter.
Qualified participants who responded were selected at random. Subsequently, the interviews were
conducted based on a participant’s availability and in no other order. The participants responded on
their own accord, demonstrating an awareness of the recent trends in artificial intelligence
technology. The participants answered all the interview questions, though they could skip any
uncomfortable questions.
All participants quoted current AI related information from more than one source and
expressed their views on how AI could help cybersecurity. Saturation was observed at the end of
the 14th interview. The remaining six interviews were completed. In addition to the 20 interviews,
11 additional one-on-one discussions were held with a select few participants to confirm and
clarify a few of their interview statements. The scientific rigor, credibility, and transparency were
maintained by following best practices in qualitative grounded theory research and by creating
and maintaining the study artifacts that included (a) an audit trail of the events related to the
study, (b) an audio recording with textual transcripts of the interviews, (c) an interview guide to
describe the rules of engagement used by the interviewer and (d) the codes used to tag significant
parts of the transcripts, and the code structure.
This study represents the best effort and expertise-based opinions of the randomly selected
U.S. cybersecurity professionals, excluding the views of others, such as information technology
professionals, senior executives, and subject matter experts. Furthermore, there were three deviant

cases where participants brought up issues without elaborations or background discussions, such
as (a) AI is already used widely by hackers, (b) Cybersecurity professionals must obtain AI skills
to stay relevant, and (c) Cybersecurity professionals will be soon replaced by AI technology.
Given these, the readers should interpret the findings as “highly likely” to influence the AI skills
of the U.S. cybersecurity workforce, as opposed to being at 100% confidence levels.
Inferences and Conclusions
Inferences
This study established its conceptual framework using (a) prior studies on the potentials
of AI techniques to strengthen cybersecurity, (b) research findings on AI's adoption challenges,
(c) published reports on the shortage of AI skills in the U.S. cybersecurity workforce, and (c) lack
of insights into the factors behind adding AI skills to the U.S. cybersecurity workforce. The study
used qualitative grounded theory methodology to systematically answer the research questions:
what factors influence adding AI skills to the U.S. cybersecurity workforce? and what are the
recommendations once these factors and their origins are identified?
The positive and negative factors, with explanations identified from the findings and
extensions, are described in Table 8, and it answers the first research question concerning the factors
that influence the addition of AI skills to the U.S. cybersecurity workforce. Furthermore, Table 10
lists the actionable recommendations to build on the identified factors and facilitate AI skills for the
workforce, answering the second research questions related to recommendations.
Hence, this researcher infers that this qualitative grounded theory research, through its
findings, when combined with the recommendations for the next steps and the suggested future
research questions, answers the stated research questions, meets the objectives of this study, and
offers valuable, actionable insights into positive and negative factors that influence the addition of
AKI skills to the U.S. cybersecurity workforce.
Conclusions
The goals, practices, and day-to-day operations of the U.S. cybersecurity workforce as
per the opinions of the study participants, under the context of adopting new technologies such as
AI, appear to be controlled and defined by critical elements such as (a) mandatory requirements
from laws, compliances and regulations, (b) trustworthy and often-used sources for technical
guidelines, and standards, (c) dependency on software tools for operations, and (d) organizational
governance, policies, procedures, education, training, skills improvement programs, professional
certification requirements, and teamwork. Figure 32 shows the elements that control and define
the U.S. cybersecurity workforce's goals, practices, and operations.
Figure 32 Elements that Control and Define the U.S. Cybersecurity’s Goals, Practices, and Operations
Mandatory Requirements from
Laws, Compliance, and Regulations
Dependency on Software tools for
operational tasks
Trustworthy Sources for current
and emerging Technical Standards
and Guidances
Organizational governance, policies,
procedures, education, trainings,
skills improvement programs,
professional certification
requirements, and teamwork
Goals, Practices, and
Day-to-Day Operational
Tasks of the U.S.
cybersecurity workforce

The factors influencing the addition of AI skills and the adoption of AI techniques are
related to how effectively the AI skills, techniques, and guidance are blended into these
controlling and defining elements. In other words, when AI skills, techniques, and guidance blend
in better, they are likely to become a positive factor, and when the blending has weaknesses, it is
likely to result in negative factors. This abstraction also explains the reasons behind the
influencing factors.
To summarize, AI needs to merge into the work environment of the U.S. cybersecurity
professionals in a non-disruptive, risk-free, easy-to-learn, explainable, trustworthy, and
nonburdensome manner for AI skills to be obtained and AI techniques to be adopted expeditiously.
The risk-averse cybersecurity workforce is likely to be slower in obtaining AI skills and adopting
AI techniques, if their work environment is redefined by the introduction of AI.
In conclusion, this study identifies the positive and negative factors that influence the
addition of AI skills for U.S. cybersecurity and describes a systematic qualitative grounded theory
research methodology used to arrive at those factors. Furthermore, this study identifies actionable
recommendations and topics for further research aimed at adding AI skills to the workforce and
expediting AI techniques for cybersecurity. As a result, the stakeholders, internal and external to
U.S. organizations, targeting AI skills to the cybersecurity workforce and AI techniques to the
cybersecurity practices, have a path forward to reduce the impediments, facilitate positive factors,
and better harness AI techniques for a more robust U.S. cybersecurity.

