


A Qualitative Exploratory Study of Cyber Threats to Financial Organizations
Introduction
Overview
The study investigated cyber threats to financial organizations. For the study, financial
organizations included banks, small and large for-profits, credit unions, and insurance
companies. Cybercrimes are prevalent in all business sectors, but financial organizations are
among the most targeted (Varga et al., 2021). Previous scholarly inquiries have explored the
array of preventative strategies organizations deploy to mitigate the risk of cyberattacks. These
strategies encompass restrictive measures on employee data access, the implementation of
firewalls, the establishment of robust data security policies, and the fortification of wireless
access points (Ghelani, 2022). Nonetheless, a limited body of research has focused on
investigating defensive strategies to counteract cyberattacks, including data monitoring, analysis
of network traffic, and behavioral assessments (Steingartner et al., 2021). The research
interviewed cybersecurity employees from various financial organizations, including banks,
small and large for-profits, credit unions, and insurance companies. The purpose was to examine
their views on the potential risks posed by deviations from their organization's cybersecurity
policies and their perspectives on the extent of support offered to staff in this context. Individuals
with cybersecurity experience within these financial organizations articulated their insights on
cybersecurity evaluations and their preparedness to address cyber threats.
The remainder of the study included four additional chapters that addressed various
aspects of the study. Chapter Two outlined a literature review of the current research and
literature on numerous topics about cyber security in financial organizations, including banks,
small and large for-profits, credit unions, and insurance companies. Chapter Three entailed the
methodology and procedures to provide details by discussing several aspects such as research

methods and design, population, sample, recruitment methods, data collection, and data analysis
procedures. Chapter Four examined the study’s findings through data analysis to answer the
research question. Chapter Five presented the study’s findings, the interpretation of the existing
literature, and the theoretical framework to guide the study.
Background and Problem Statement
Financial organizations, including banks, small and large for-profits, credit unions, and
insurance companies, are highly susceptible to cybercrime due to their sensitive financial assets
and personally identifiable information, such as social security numbers, which hackers can use
for identity theft (Kosutic & Pigni, 2022). Cybercrime remains a pervasive threat to various
sectors worldwide, with the banking industry experiencing the most attacks year after year
(Kosutic & Pigni, 2022). Financial organizations are the primary targets for cybercriminals due
to the vast repositories of sensitive financial data they manage and the potential for significant
financial gain from successful breaches (Kosutic & Pigni, 2022). According to Gulyás and Kiss
(2023), banks have reported increased cyberattacks from organized crime groups operating
globally, utilizing sophisticated cybercrime tools and services from illicit providers to orchestrate
targeted attacks against financial organizations.
Criminals often target banking institutions because these organizations provide them with
various ways to profit through extortion, fraud, and robbery (Stanikzai & Shah, 2021). Criminals
targeting financial organizations have an agenda; they aim to exploit vulnerabilities within these
organizations to illegally gain profits while using these profits to enhance their cyber capabilities.
The financial sector is a choice for these activities due to the potential for significant financial
rewards and the reliance on digital infrastructure and valuable data (Gulyás & Kiss, 2023).
Cyberattacks on financial organizations occur frequently and on a larger scale than other sectors,
highlighting cybercriminals' persistent pursuit of monetary gains worldwide. Recent studies

showed that financial organizations rank second after the technology sector regarding
cyberattack volume, comprising 22.4% of reported incidents (Kuzior et al., 2022). Cyberattack
incidents underscore the importance of strengthening cybersecurity measures in financial
organizations to mitigate cyber threats and protect the financial system’s integrity. Financial
organizations must adopt a proactive and adaptable approach to navigate the ever-changing
cybersecurity landscape and defend against sophisticated cyberattacks. The proactive approach
includes equipping themselves with advanced technologies, gaining access to threat intelligence,
and engaging in collaborative efforts.
Financial organizations, including banks, small and large for-profits, credit unions, and
insurance companies, invest the most money in the cybersecurity industry. They can spend
anywhere from six to ten percent of their IT budget on preventing cyberattacks annually (Kuzior
et al., 2022). Despite the devastating nature of financial cybercrime, Usman et al. (2023) noted
that implementing available cybersecurity protocols can prevent approximately 95% of
cyberattacks. Cyber Threat Intelligence (CTI) plays a pivotal role in cybersecurity strategies,
providing organizations, including those in the banking sector, with a structured framework to
strengthen their defenses against cyber threats (Kayode-Ajala, 2023). The CTI is a real-time alert
system that helps organizations anticipate, identify, and address cyber threats before they become
security breaches (Kayode-Ajala, 2023). By utilizing various data sources, such as open-source
intelligence monitoring and the internet, and collaborating with information-sharing partners,
CTI allows financial organizations, including banks, small and large for-profits, credit unions,
and insurance companies, to gain insights into the strategies used by cyber attackers. With this
knowledge, financial organizations can proactively enhance their security measures, implement
targeted responses, and reduce the risks of emerging cyber threats. Furthermore, CTI supports
decision-making and resource allocation by helping organizations prioritize security investments

and allocate resources effectively to the most vulnerable areas (Kayode-Ajala, 2023). By
integrating CTI into their cybersecurity strategy, financial organizations can establish a defense
to strengthen resilience against cyber threats and protect the integrity of their assets and customer
information in today’s increasingly challenging cyberspace.
Despite the potentially preventable nature of many cyberattacks, they are steadily rising
due to increased predation from attackers, the failure of corporations to create cybersecurity
defenses, and a lack of awareness about adhering to adequate cybersecurity policies (Walaza et
al., 2020). Cyberattacks and their intensity have become more common due to technology,
digitization, and globalization (Sharif & Mohammed, 2022). Cyber threats devastate and create
corporate risks, trade obstacles, and economic losses. As a result, corporations face costly
cleanups. Sharif and Mohammed (2022) project that cybercrimes cost the global economy $10.5
trillion annually, amounting to about $32,000 per individual in the United States. Recent years
have witnessed notable cybersecurity breaches, including those involving Colonial Pipeline and
Solar Winds breaches (Sharif & Mohammed, 2022). The cost of cybercrimes in financial
organizations like the banking sector bears 40% of the economic impact of cybercrimes relative
to other industries (Kuzior et al., 2022). The dissertation investigated the financial organization’s
adherence to security policies and potential coping mechanisms. Studies showed that
organizational factors, such as a lack of regular communication regarding the importance of
cybersecurity, significantly contribute to cybersecurity vulnerabilities within organizations
(Pollini et al., 2022). Human factors, including inadequate knowledge about cybersecurity threats
and a breach's potential consequences, are responsible for many cybersecurity flaws (Zwilling et
al., 2022). Other studies, such as the one by Nobles (2022), have noted that employee fatigue,
stress, and burnout have an increased impact on cybersecurity in organizations. These factors
lead to lower cognition, noncompliance, and low security awareness (Nobles, 2022). The human

factor is often considered the weakest link in the cybersecurity chain (Rahman et al., 2021). The
most frequent types of attacks include those dealing with human factors, such as social
engineering attacks and online fraud (Pollini et al., 2022). Incorrect employee actions were
among the most frequent types of attacks (Pollini et al., 2022). Organizations have embraced
monitoring and security technologies to protect their data and information system assets. There is
a possibility that although leaders in organizations may implement human-independent
technology, employees remain an essential element in the cyber defense of organizations (Pollini
et al., 2022).
Cybersecurity professionals and information system analysts were responsible for
educating employees about cyber risks and ensuring they were knowledgeable about the existing
risks and how to make informed decisions (Dash & Ansari, 2022). Regarding cybersecurity, the
effectiveness of security measures and systems depends on how easily individuals are
comfortable using the systems implemented in their organizations. Hadlington (2021) stated that
employees or other users could find some security protocols implemented in organizations
complicated. Enhancing compliance with cybersecurity measures and policies in organizations
necessitates simplifying the systems to positively influence employees' adoption and practice
behaviors (Hadlington, 2021). Studies such as the one by Alsharif et al. (2021) have emphasized
the role of elements in cybersecurity, underscoring that more than 39% of security threats
originate from human-related weaknesses. Notably, 95% of cyberattacks are due to human
factors, highlighting the urgent need to address vulnerabilities centered on people in
cybersecurity defenses (Alsharif et al., 2021). One primary concern is the need for more
awareness among organizations with many employees about the dangers posed by cyberattacks.
Given these insights, organizations must prioritize initiatives focused on educating users and
raising awareness as part of their cybersecurity approach. Creating a culture that values security

awareness and providing training programs can empower IT employees to identify and mitigate
cyber threats proactively.
Cybersecurity professionals' perceptions of cyber threats, assessment of those threats, and
motivation to address or prevent threats were of central importance. Many organizations use
cybersecurity awareness training to improve cybersecurity threat detection and evaluation
(Richardson et al., 2020). Information security practices among employees were the leading
source of cyber threats and vulnerabilities (Dash & Ansari, 2022). Comprehensive approaches to
cybersecurity policy may require additional defensive and reactive components. Defensive
components attempt to stop an attack before it occurs, and reactive components mitigate the
threats once they happen (Usman et al., 2023). This comprehensive approach can be achieved by
promptly improving cybersecurity professionals' ability to assess threats and their motivation to
address those (Usman et al., 2023). Further research was required to understand cybersecurity
professionals' perceptions of cyber threats to financial organizations, their threat assessment
methods, and the incentives that motivate them to manage or mitigate these threats.
Reactive and defensive approaches to cybersecurity have their pitfalls. These barriers
include false positives that lead to alert fatigue among users (Nobles, 2022). Alert, or
cybersecurity fatigue, is a form of work disengagement with cybersecurity. Cybersecurity fatigue
is an aversion to cybersecurity-related workplace behaviors resulting from overexposure to
cybersecurity-related work tasks or training (Reeves et al., 2021). Studies such as the one by
Reeves et al. (2021) have concluded that cybersecurity awareness training programs were often
ineffective. The lack of uptake and maintenance of defensive procedures in financial
organizations indicated that more research is needed to determine potential coping mechanisms
(Steingartner et al., 2021). Like many central aspects of cybersecurity, the problem is not
technical but human. The key to addressing this problem was bolstering users’ perceptions of,

assessments of, and motivations regarding cybersecurity without giving rise to alert fatigue,
excessive stress, or highly dangerous burnout (Nobles, 2022).
The financial industry is a prime target for cybercriminals due to the sensitive and
valuable information that financial organizations possess (Richardson et al., 2020). Cyberattacks
can cause significant financial losses, damage to reputation, and loss of customer trust (Nobles,
2022). In recent years, numerous high-profile cyberattacks have occurred on financial
organizations, such as the Equifax data breach, which affected over 140 million customers
(Alsharif et al., 2021). In light of these challenges, financial organizations have significantly
enhanced their cybersecurity protocols to safeguard their entities against cyberattacks (Alsharif et
al., 2021). Despite such advancements, the incidence and complexity of cyberattacks persistently
escalate (Alsharif et al., 2021). Consequently, financial organizations necessitate adept
cybersecurity personnel to identify and neutralize cyber threats (Reeves et al., 2021).
Nonetheless, ambiguity prevails regarding cybersecurity professionals' perspectives and
evaluative criteria towards cyber threats, along with the factors that incentivize their efforts
toward threat management and prevention (Alsharif et al., 2021; Richardson et al., 2020).
Purpose of the Study
This qualitative exploratory study focused on potential coping mechanisms and whether
security policies are adequately implemented. The study addressed how the critical constructs of
the Technology Threat Avoidance Theory (TTAT) explained vital aspects of financial
organizations’ cybersecurity risks. The study further addressed protecting financial organizations
against cybersecurity risks and ensuring adherence to cybersecurity protocols. The growing
threat of cyberattacks has become a primary concern for financial organizations worldwide,
resulting in significant financial losses, damage to reputation, and loss of customer trust (Reeves

et al., 2021; Varga et al., 2021). Responding to this, cybersecurity professionals were critical in
identifying and mitigating cyber threats (Richardson et al., 2020). However, further research was
required to understand how cybersecurity professionals perceive cyber threats, evaluate their
impact, and inspire their organizations to prevent them (Alsharif et al., 2021; Steingartner et al.,
2021).
The study addressed the knowledge gap by examining the perceptions of cybersecurity
professionals working in financial organizations. By understanding cybersecurity professionals’
perspectives, the study provided insights into the factors influencing their decision-making and
strategies to manage or prevent cyber threats. (Richardson et al., 2020). The study's findings
aimed to help financial organizations identify weak cybersecurity policies and determine if
policies were adequately adhered to mitigate the risk of cyberattacks and protect their
organizations.
Significance of the Study
This study's findings helped cybersecurity professionals in financial organizations identify weak
cybersecurity policies and adhere to better policies that improve their security. The study also
highlighted potential coping mechanisms and whether policies are adequately implemented. The
study results supported future investigations into the importance of adequately adhering to
security policies in financial organizations. Steingartner et al. (2021) argued that, despite a
decade of growing interest in information security, more studies should focus on defensive rather
than preventative information security methods. Financial organizations contain vast amounts of
personal information about clients and employees. Consequently, improving information
security among these organizations should be a priority (Usman et al., 2023). The findings in the
study helped financial organizations lessen the opportunity for information breaches and invest
in information security to safeguard financial and client data.

Conducting this qualitative exploratory study highlighted potential coping mechanisms
and whether security policies are adequately implemented. The study addressed a critical gap in
the existing literature by focusing on how cybersecurity professionals in financial organizations
perceive cyber threats, assess them, and motivate them to manage or prevent them. As
Steingartner et al. (2021) noted, there needs to be more research exploring proactive measures
such as data monitoring, traffic analysis, and behavioral analysis to thwart cyberattacks, making
the study particularly relevant and timely. Furthermore, the research explored why financial
organizations need help implementing cybersecurity measures. The study aimed to reveal the
fundamental causes behind gaps in security policies, providing valuable perspectives to enhance
strategies for tackling these challenges. Additionally, the study's research inquiries offered
perspectives from cybersecurity professionals on the risks associated with not following
cybersecurity policies and how supportive they felt in dealing with and preventing cyber threats.
The insights from the study could have helped leaders in financial organizations develop and
implement strategic approaches to address potential cybersecurity threats.
Research Questions
The qualitative exploratory research aimed to facilitate the development of robust
security protocols within financial organizations, thereby safeguarding sensitive corporate data
against insider threats. The design of the research questions aimed to fulfill its purpose. The
following research questions guided the study.
RQ1. How do cybersecurity professionals perceive deviation from their organization’s
cybersecurity policies as a risk to their organization?
RQ2. How do cybersecurity professionals perceive the active support they provide to
employees as helping them cope with and prevent cyber threats?

The study formulated two research questions to gather insights and experiences from
cybersecurity professionals. The questions provided information that aided in understanding how
these cybersecurity professionals perceived the threats faced by the organization because of
deviations from policies. The inquiries aimed to elicit insights from cybersecurity professionals
regarding their experiences supporting employees, thereby contributing to an understanding of
the organization's cybersecurity defense capabilities.
Theoretical Framework
The core of any research study lies in its theoretical foundation. The research question
guided this qualitative exploratory by exploring key theoretical constructs related to the study. In
qualitative exploratory research, this step is crucial as it often helps refine the primary question
and may even introduce new ones as a conceptual tool in the research process by guiding data
collection interviews (Daiberl, 2020). A well-suited theoretical framework and well-crafted
research questions were indispensable elements in any investigation, as they provided focus and
clarity to the research.
TTAT was the theoretical model for the study, which addressed insider threat avoidance
behavior. The theory highlighted how insiders assessed and perceived the threat of deviation
from security rules and the motivation to avoid the perceived threats through remedial options to
prevent or cope with this threat (Almansoori et al., 2023). TTAT posited that individuals’
perceptions of their risk of technological threats influenced their awareness of potential hazards
and, in turn, their behavior toward avoiding the perceived threats (Almansoori et al., 2023).
According to the theory, individuals who have experienced severe information technology (IT)
threats were more likely to be perceived as vulnerable. Individuals who have not experienced IT
threats are less likely to take evasive precautions and view them as threatening to themselves or
their businesses (Almansoori et al., 2023).

The TTAT included two interdependent facets that play a crucial role in individuals'
responses to potential threats: avoidance behaviors and coping strategies centered on emotions
(Almansoori et al., 2023). TTAT theory undertook a comprehensive exploration of this
connection, systematically quantified the probability of a threat materializing, and thoroughly
assessed the threat occurring to measure the probability of the cyber threat occurring and
effectively gauge the likelihood of a cyber-threat. TTAT also underlined the significance of users'
evaluations when assessing the danger posed by a potential threat. Three pivotal factors came
into play during this evaluation process. In the initial evaluation phase, individuals gauged the
effectiveness of protective strategies in diminishing the perceived threat. Also, it subsequently
addressed the costs associated with deploying these safeguarding measures. In the final stage of
the analysis, individuals appraised their capability to implement these protective strategies
successfully. Hence, the triad of considerations formed the basis for users' perceptions of the
potential danger, highlighting the multifaceted nature of the decision-making process in the face
of threats.
When viewed through the lens of TTAT, the rising incidences of cyberattacks in the
United States are likely to increase threat precautions and assessment among individuals at
financial organizations as more and more of these individuals experience cyberattacks (Alawida
et al., 2022). Individuals who have experienced cyberattacks in the past are more likely to
implement extraordinary defensive techniques to mitigate future threats than individuals who
have never experienced a cyberattack. From a qualitative perspective, the theory indicated that
individuals’ perceptions about their susceptibility to and the resulting severity of cyber threats
impacted their awareness and response to the threats, influencing their decision or motivation to
avoid them. As cyberattacks increase, financial organizations must strengthen their cybersecurity
protocols.

Limitations
A fundamental limitation of this qualitative exploratory study was limited
generalizability. However, the nature of qualitative exploratory research usually uses a small
sample size and underlines fastidiousness over the finding’s generalizability (Boumhand et al.,
2023). Merriam (2020) anticipated that the study would provide empirically and practically
valuable knowledge, enlightening decisions about how cybersecurity professionals in financial
companies perceive, assess, and find motivation to manage or prevent cyber threats.
Generalizability depends on a study’s reporting of descriptive data adequate to inform readers’
decisions about the transferability of results to other contexts (Merriam, 2020). Efforts to
mitigate this limitation entailed providing participants with detailed information related to their
demographic descriptions and integrating it into the study’s findings to inform readers’
judgments of transferability (Boumhand et al., 2023).
Another study limitation was that the interview partly relied on self-reported data.
Selfreported data were valuable for collecting participants’ experiences from their points of view
(Kosutic & Pigni, 2022). However, more emphasis on using self-reported data could lead to
participants misremembering a situation or purposefully misrepresenting it, which could
negatively affect the credibility of the findings (Merriam, 2020). Efforts to address this limitation
included ensuring each participant was comfortable sharing openings during the interview and
reminding them that deception is unethical research (Boumhand et al., 2023).
Another limitation of the study was that it included few participants because of its
qualitative nature. By ensuring data saturation in the collection, the study addressed this
limitation. Boumhand et al. (2023) stated that involving five to 25 participants was sufficient to
reach data saturation in a qualitative exploratory study. The sample recruited for the study
consisted of 25 participants working in financial organizations. According to Boumhand et al.

(2023), qualitative exploratory research focuses on exploring an issue or adding more depth to
quantitative data. Therefore, a qualitative descriptive study should involve a small sample
(Boumhand et al., 2023). The study continued data collection until saturation, ensuring sufficient
data collection. Identifying and acknowledging potential limitations is essential for honesty and
transparency in qualitative exploratory studies. Several aspects related to design and
methodology features limited the current study, potentially influencing the data collection,
interpretation, and presentation of the findings. Chapter Five further delineates the impact of the
limitations.
Assumptions
The study assumed the trustworthiness of the various data types collected through
interviews. Qualitative exploratory research, part of the constructivist research paradigm, was
based on the presumption that meaning is naturally constructed by interpreting individuals’
unique experiences (Kosutic & Pigni, 2022). The analysis of trustworthy data gathered through a
semi-structured interview format aimed to support participants in offering detailed descriptions
of the study.
The study assumed that participants openly and honestly shared their descriptions of the
explored phenomenon. To encourage open and honest responses, the consent process and
introduction to the interview assured confidentiality and described the use of pseudonyms in
transcripts and reporting. Also, one of the critical assumptions of the study was that adequate
security policies in financial organizations could prevent some cyberattacks. Sharif and
Mohammed (2022) supported this assumption with literature and stated that cybersecurity
protocols could stop approximately 95% of cyberattacks if policies are adequately implemented
and currently available. The study also assumed that participants would respond accurately to
interview questions, a necessary assumption since qualitative exploratory studies depend on

selfreported data. Self-reported data can threaten the study's credibility. An interview protocol
standardized the questions, and follow-up questions allowed for clarification and corroboration
of participants' responses. The study also assumed that participants understood insider threats and
their impact on the organization.
Definitions
To understand the current study, one must be familiar with the terms and definitions
provided in this section, which the study employed. In this research, it was imperative to
establish precise definitions of key terms. The definition section served the purpose of offering
explicit explanations of crucial keywords. These definitions are essential for a comprehensive
understanding of how cybersecurity professionals can enhance the implementation of potential
coping mechanisms and how cybersecurity policies are adequately implemented.
Computer security: Offensive and defensive security measures are designed to protect data stored
on information systems and computers (Kilani, 2020).
Cyberattack: Unauthorized access to computer systems activities, including information data and
software theft and information modification (Dhirani et al., 2021).
Cybersecurity: Protects computer systems from unauthorized access and intentional harm or
interruption (Kilani, 2020).
Cyber threat: Event impacting business operations through service disruption or denial of service
with malicious intent (Dhirani et al., 2021).
Data Breach: Data breaches occur daily, posing a significant threat to businesses that become
targets of internal and external attacks (Reddy, 2021). These breaches involve hackers
clandestinely infiltrating systems data to acquire personal and company data illicitly.

End-users: Individuals who use computing systems to generate and distribute knowledge to add
value to the business (Kilani, 2020).
Hackers construct or utilize computer programs to illegally access information systems and
obtain confidential business information (Dhirani et al., 2021).
Information technology: Using computer systems to send, store, and retrieve information
(Dhirani et al. (2021).
Information systems: Integrated components critical for collection, storing, processing data, and
providing operations for a company (Kilani, 2020).
Malware: Software designed to disrupt, damage, and gain unauthorized access to a computer
(Kilani, 2020).
Password authentication: Offensive and defensive security measures designed to protect data
stored on information systems and computers (Kilani, 2020).
Phishing: The method used to obtain confidential information from users impersonating a trusted
source (Dhirani et al. (2021).
Security breach: The attempt by attackers to gain unauthorized system access to an information
system (Kilani, 2020).
Secure computing practices: Procedures utilized to execute security processes to protect
corporations’ confidential data and business resources (Dhirani et al., 2021).
Spyware: Computer software used to collect information without the user’s knowledge (Dhirani
et al., 2021).
Trojan: Malware created by cybercriminals to impersonate legitimate software to cause
significant damage or obtain data (Kilani, 2020).
Unauthorized software: Software not authorized to install (Kilani, 2020).

Virus: A malicious program deployed by attackers that can self-replicate by copying itself to
other programs and taking over a computer system (Kilani, 2020).
Vulnerability: Flaws that allow an attacker to violate an information system to gain access to the
data (Kilani, 2020).
Summary
Chapter One included background information about the problem and discussed the
purpose of the study and its significance. It also consists of a research question that guided the
study, the theoretical framework, study limitations, assumptions, and the definitions of terms. In
summary, Chapter One provided the perceptions of cybersecurity professionals within the
financial sector regarding cyber threats, evaluative processes, and the motivational factors that
drive their preventive efforts. It underscored the critical need for comprehensive cybersecurity
policies that not only deter cyber threats but also foster a security-aware organizational culture,
thereby enhancing the resilience of financial organizations against the evolving landscape of
cyber risks. Chapter Two discussed the concepts introduced in this chapter in detail, focusing on
the Technology Threat Avoidance Theory (TTAT) approach in the literature review, which was
considered a significant danger to the global financial industry. Through the literature review, the
study identified gaps in the understanding of developing and utilizing modeling approaches to
cybersecurity risks faced by financial organizations.

Chapter Two
Review of Literature
Introduction
Global financial institutions have faced the threat of internal invasion through
technological means (Stanikzai & Shah, 2021). The fear of cyberattacks is prevalent in every
aspect of society for those who rely on technology for business. From hospitals to banking,
technology has become a primary means for information, communication, and daily business
practices (Bécue et al., 2021; Steingartner et al., 2021). Even small to medium-sized businesses
rely on technology for daily operations, making them vulnerable to cyberattacks. With this
knowledge, cyber-based terrorism has become increasingly concerning, with security
professionals constantly immersed in new methods to protect technological information. Leaders
in the banking sector concerned with economic and identity theft recognized a need to develop
defensive and preventative cybersecurity policies that would subvert cybercrimes successfully
(Usman et al., 2023).
Cybersecurity remains elusive despite its necessity in the current age. Information
security is paramount at a time when technology is quickly advancing. Users should understand
the need for information security to protect themselves from hackers. The knowledge gap is
widening, and users need more information to prevent internal and external attacks (Shipena &
Gamundani, 2024). This literature review focused on three fundamental aspects: efficient
policies that financial organizations employ to protect data and finances, the situation mitigation
process, and the challenges companies experience in mitigating cybersecurity breaches.
This qualitative exploratory study addressed how TTAT can help cybersecurity
professionals working in financial organizations perceive cyber threats, assess those threats, and
provide motivation to manage or prevent the threats. The review of existing literature aimed to

identify gaps and offer a comprehensive understanding of the current cybersecurity policies in
financial organizations. A thorough review revealed a need for more literature discussing cyber
protection. The review of existing literature also revealed limited information to address the
application of consistent and reliable anti-cyber security models that protect a company’s
sensitive data from insider threats (Shipena & Gamundani, 2024). The existing literature has
focused on topics including cyberattacks and threats, malware and security, cyber models,
methods for security protection, cybersecurity and defense, legalities with cybersecurity,
financial challenges to data protection, and cybersecurity efficient policies in financial
organizations. Therefore, there was ample reason to implement the current study due to the
absence of literature and the gap in exploring how much cybersecurity professionals working in
financial organizations perceive cyber threats, assess them, and motivate them to manage or
prevent them.
Literature Search Strategy
The literature search strategy for articles reviewed in this qualitative exploratory study
was obtained by searching academic databases. It searched these terms and phrases through the
following databases: ABI/INFORM, Business Source Complete, EconBiz, EconLit, Google
Scholar, International Financial Statistics, International Monetary Fund (IMF), Jurn, Research
Papers in Economics (RePEc), and Scopus the initial search produced over 6,500 scholarly
works. Table 1 shows the breakdown of resources by database. The literature search employed
the following keywords and phrases: cyber security policies, cyberattack, cybersecurity, cyber
threat, end-users, defensive risk management practices, security policies, hacking into financial
organizations, protecting IT, phishing, protecting data, protection methods for technology,
protecting systems and databases from emerging cyberattacks, risk management practices for
cyber security in the financial industry, security breach, secure computing practices, spyware,
Trojan, unauthorized software, virus, and technology vulnerability.
Table 1
Breakdown of Resources by Database
Database Number of Resources
ABI/INFORM
Business Source Complete
EconBiz
EconLit
Google Scholar
IMF
Jurn
RePEc
Scopus Total
675
122
985
904
2,112
76
195
847
620
6,536
Note: The table shows the resources on each platform where a search for the specific terms was
done. This table provides a breakdown of resources across various databases, indicating the total
count obtained from searches on specific terms. This distribution highlights the varying amounts
of information available across academic and research platforms.
The selection of articles suitable for review followed these inclusion criteria: (a)
peerreviewed, (b) relevant to the study’s topic, and (c) printed in English. More than 88% of the
selected articles were from the past five years. Duplicate resources were removed by assessing
each article based on resource titles, abstracts, and full content. The process resulted in
eliminating research sources that did not meet the standard. The final number of resources
utilized in the literature review was 148.
Conceptual Framework
The conceptual framework of the study relied on the theoretical model of TTAT. Liang
and Xue (2009) first developed the TTAT, which examined how and why individuals utilize

threat avoidance behaviors within the information technology industry. Liang and Xue
established this theory using previous research from multiple disciplines and industries,
including healthcare, risk management, psychology, and IT. Almansoori et al. (2023) reported
different ways to safeguard data by comparing and combining the knowledge used for
preventative methods. An individual must perceive the threat and be motivated to actively avoid
such danger by implementing safeguarding measures if they believe it can be avoided by
following the safeguarding action. Liang and Xue (2009) also showed that many individuals
would “passively avoid the threat through emotion-focused coping if they perceive the threat not
to be avoidable by any safeguarding measure available to them” (p. 71). Within the TTAT
framework, Almansoori et al. (2023) assessed the likelihood of cyber threats and their adverse
effects to determine emotion-focused coping and avoidance behaviors. Clients considered the
peril in light of defending viability, cost, and self-adequacy. The conceptual framework utilizing
TTAT indicated that a continual IT risk necessitates a risk management plan within an
organization. The elements were part of a continuous interlocked process, not a singular or
repetitive event, which suggested that risk influences management, as shown in Figure 1.
Figure 1
Risk Management Elements
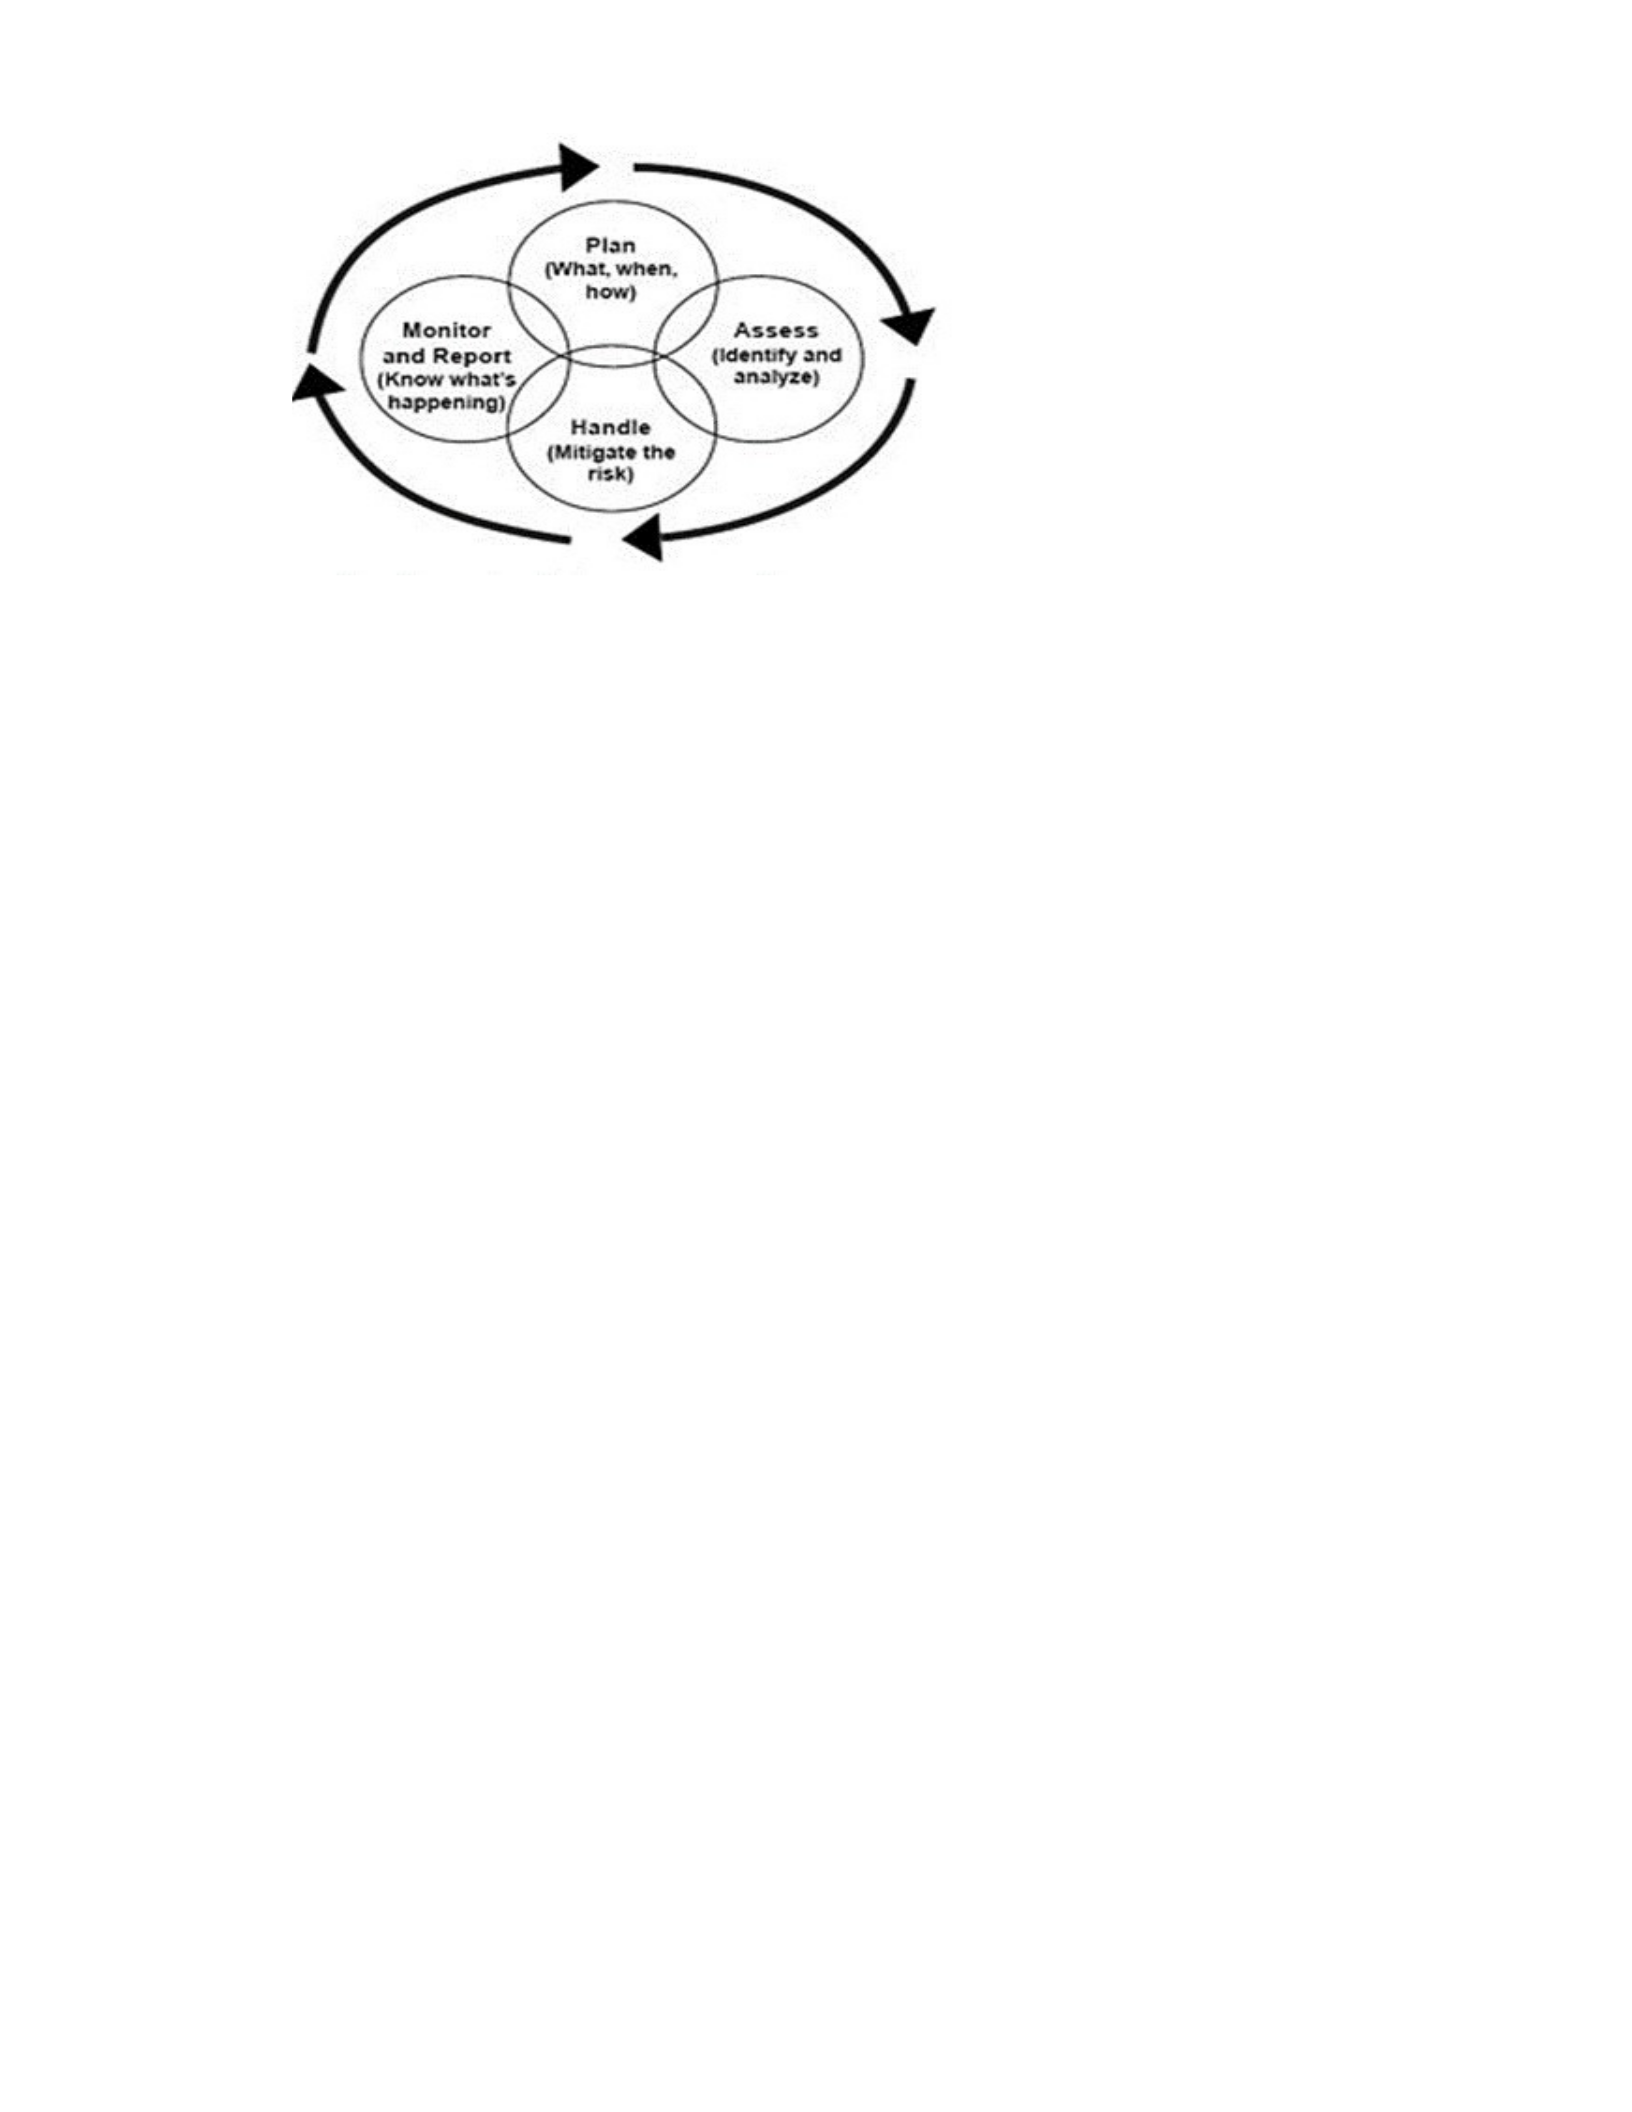
Note: The figure illustrated the continuous and interlocked process of IT risk management
elements, aligning with the TTAT conceptual framework. The diagram emphasizes that
managing IT risks is an ongoing process, not a one-time event. Adapted from Overview of ISMS
by M. Moghaddas, 2012, About Networks. https://ip.engineering/overview-of-isms/.
Therefore, continuous processes can impact a financial organization’s incorporation of
the prevention strategies necessary to protect it from cyberattacks. Deterring cyberattacks
through better policies emphasizes implementing prevention measures to mitigate intruders and
data theft (Sharif & Mohammed, 2022). Sharif and Mohammed (2022) noted that many banks
maintain programs to address cybersecurity issues and manage internal security through a shared
governance structure. This qualitative exploratory study used TTAT to examine how previous
research described prevention and protection methods against cyberattacks. This qualitative
exploratory study involved observing the descriptive design and analyzing cybersecurity policies
that failed to help establish more robust security methods. The research aimed to adhere to better
cybersecurity policies that reduce a financial organization’s risk, respond to external threats,
address findings, enhance cybersecurity capabilities, and protect sensitive data. The conceptual
model for the current study is shown in Figure 2.
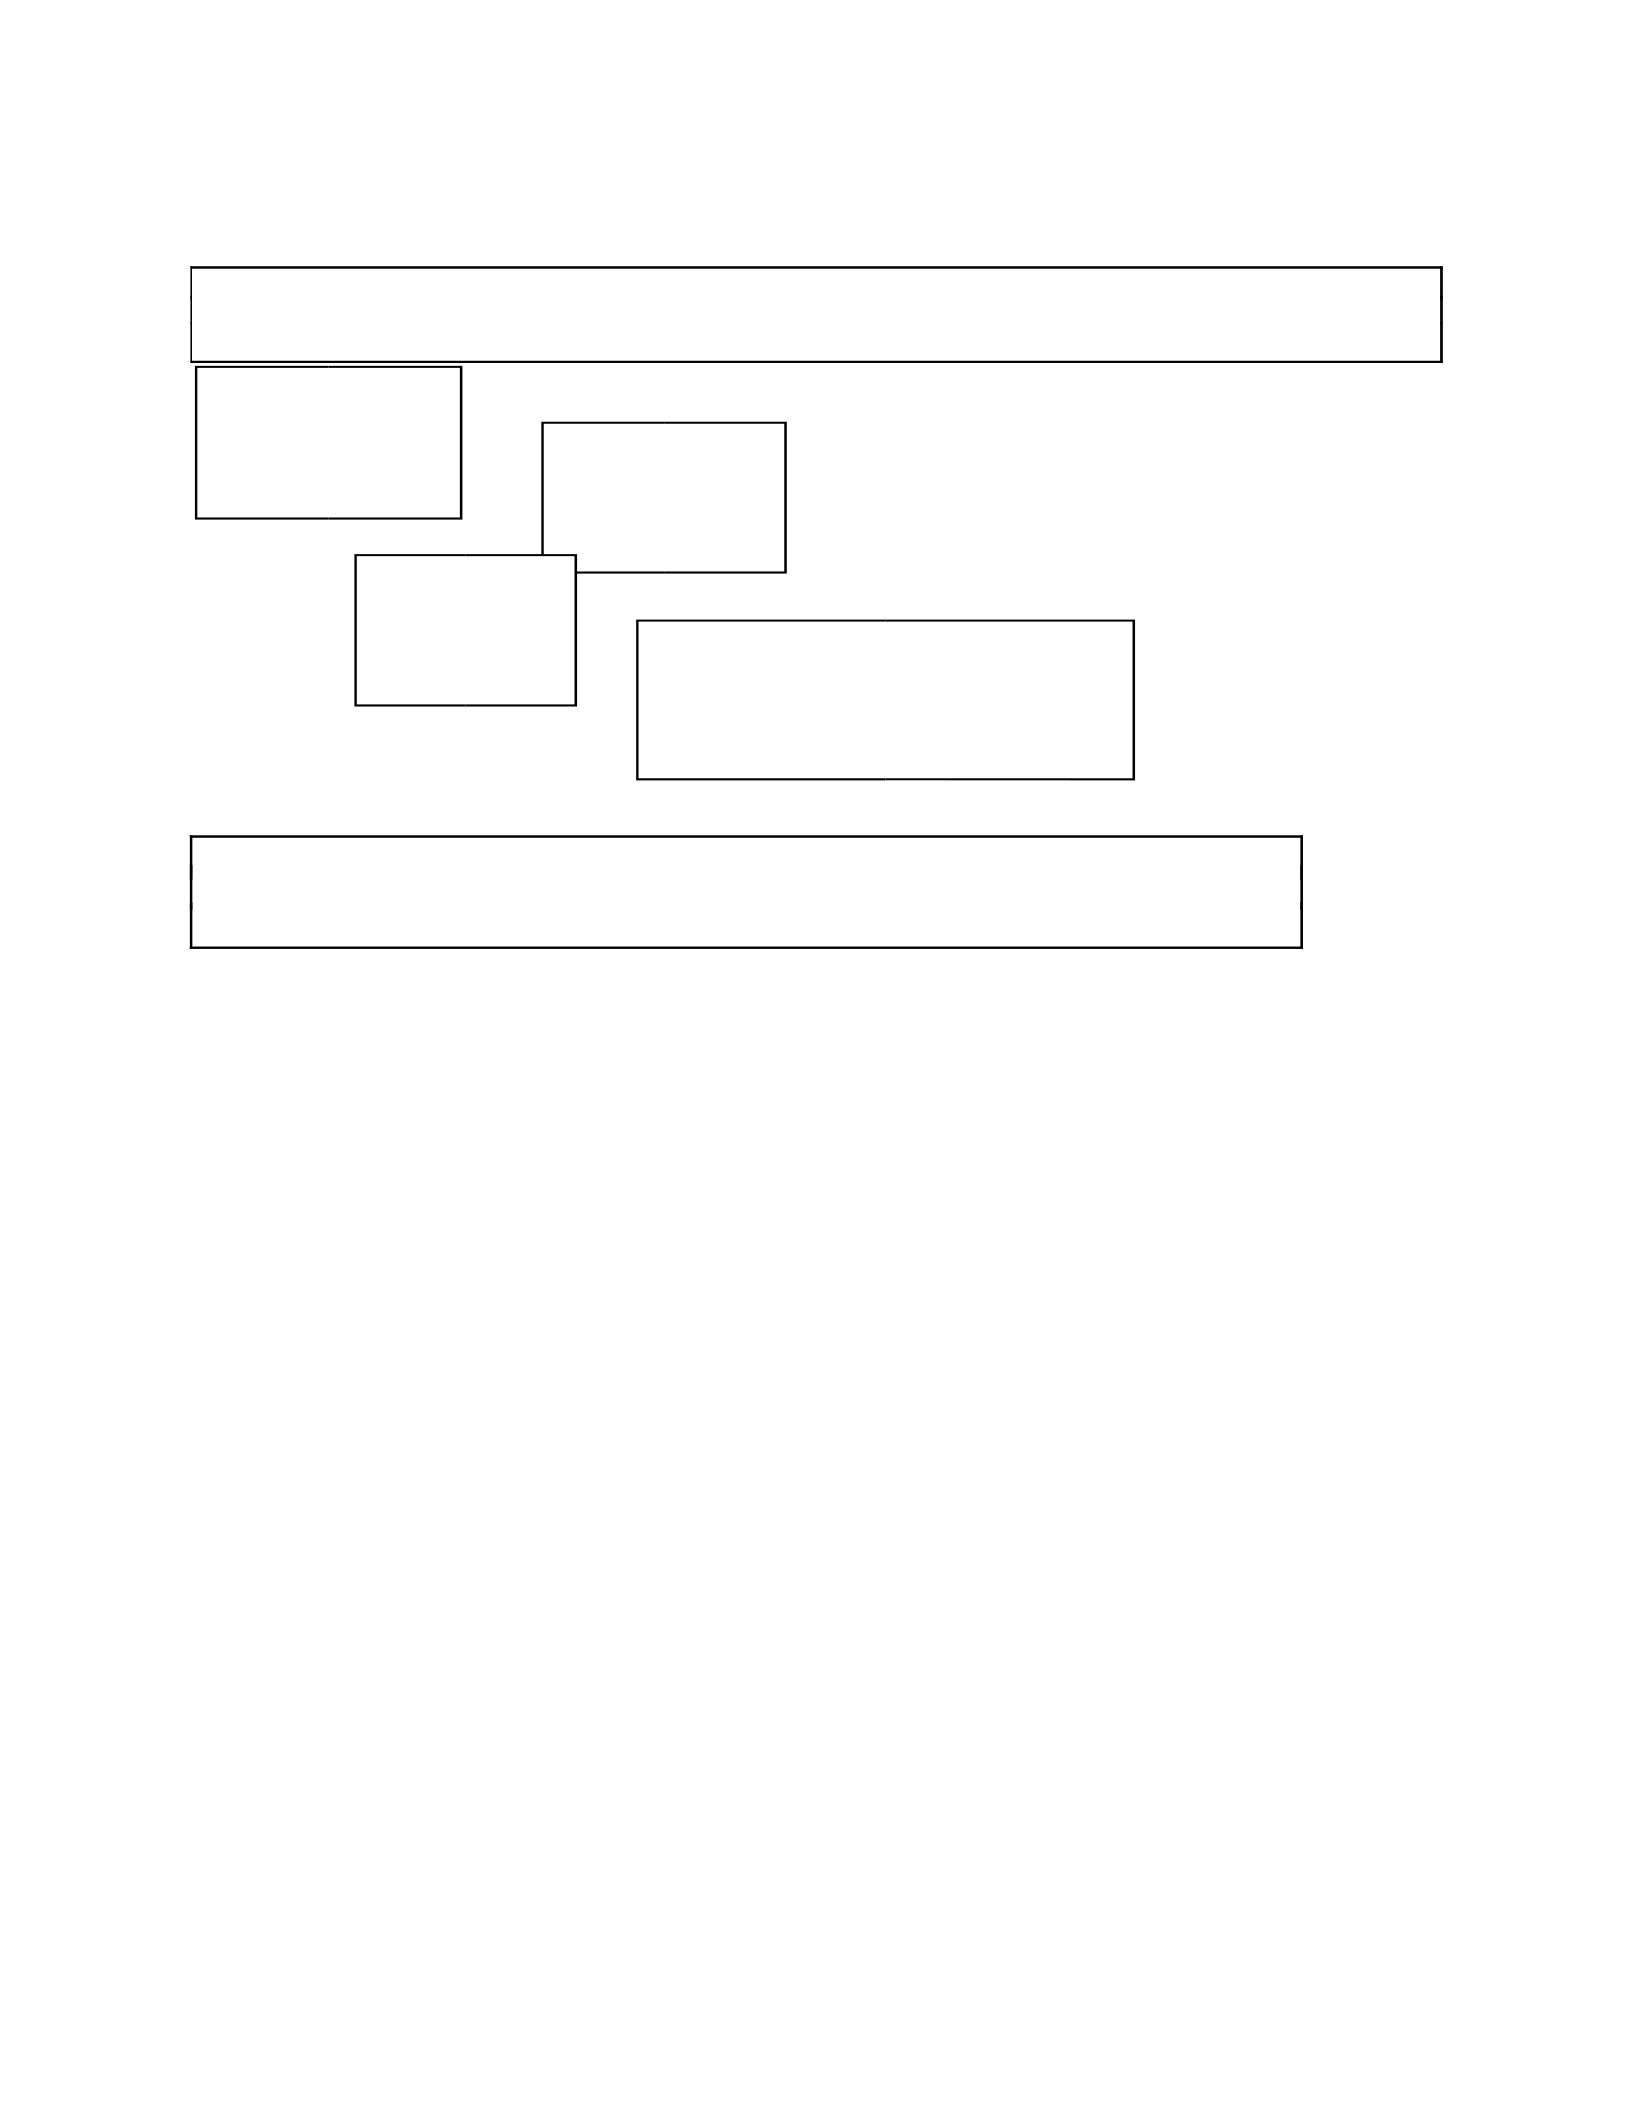
Figure 2
Conceptual Model
Environment
Cybersecurity Defense Model
Outcomes
Financial Data Protected
Note: The figure illustrates a conceptual model for analyzing the effectiveness of cybersecurity
defense models within a given environment. Adapted from Avoidance of Information
Technology Threats: A Theoretical Perspective (MIS Quarterly, 33(1), 71-90) by H. Liang and
Y. Xue, 2009, MIS Quarterly. 71–90. https://doi.org/10.2307/20650279. Copyright 2009 by
Huigang Liang and Yajiong Xue.
Existing Literature Review
Cybersecurity is a threat because it affects about 90% of organizations in the United
States and 75% in Europe (Hussain et al., 2020). Information systems professionals in
organizations must plan and prepare to handle threats regularly. The extant literature addressed
multiple facets of this phenomenon and how organizations were prepared to mitigate such
dangerous thefts while exploring new methods for protecting valuable information and data.
Input
Defensive strategi es
Past failures/successes
T hrea t Avoidance
The ory
Insider Threat
Avoidance Behavior
T hrea t Avoidance
The ory
Emotion -Focused
Cop ing
Influencing Factors ( Potential Barriers)
Effectiveness of the measure
C ost of the measure
S elf -efficacy in applying the measure

Most organizations in the financial sector have established a mature cybersecurity program,
which defined claims that the processes, tools, and people were aligned to work collaboratively
so that the program was successful at diminishing risk. A mature program with adequate security
policies obtained and accepted by those in leadership positions also impacts an entire
organization (Usman et al., 2023). Mature programs in an organization were frameworks that
were advanced in cybersecurity controls and technologies and demonstrated high degrees of
adaptability to respond to potential threats (Usman et al., 2023).
The TTAT holds significant importance in cybersecurity, offering insights into users'
perceptions and responses to technology threats, such as cyberattacks, malware, and data
breaches. Developed by Liang and Xue (2009), TTAT assumed that individuals tend to avoid
technology threats, and factors such as perceived susceptibility, perceived severity, perceived
effectiveness, perceived cost, and self-efficacy shape their avoidance behavior. Numerous studies
have applied TTAT in different cybersecurity contexts, from information sharing and cloud
computing to biometric authentication. Session and Muller (2022) found that the willingness of
cybersecurity professionals to share threat information hinged on their perceived threat,
indicating the need for additional incentives and support. Almansoori et al.'s (2023) systematic
review underscored TTAT's prevalence in explaining user awareness and motivation in
cybersecurity, emphasizing its consideration of coping elements, risk tolerance, and social
influence.
Marotta (2023) refined TTAT by introducing the concept of perceived benefits and
suggested that emphasizing positive outcomes could enhance users' motivation to avoid
technology threats. Their revised TTAT model included perceived benefits as a moderator
between perceived threat and avoidance motivation, revealing a significant positive effect on
users' motivation and intention to use security features. Marotta (2023) tested their model using a

survey of online banking users and found that perceived benefits positively affected avoidance
motivation and purpose to utilize security features.
The study by Al-Jarba and Al-Khathami (2021) provided a comprehensive review of the
existing biometrics-based authentication techniques for mobile devices, such as smartphones,
tablets, and wearable devices. Biometrics-based authentication techniques are categorized into
physiological, behavioral, and hybrid to explain and justify the need for biometrics-based
authentication techniques in the mobile ecosystem. Proponents of TTAT argue that applying
biometric authentication methods can enhance mobile device security and the user experience by
providing a more reliable and convenient way for user identity verification. The study revealed
that biometrics-based authentication techniques could motivate users to avoid technology threats
and adopt more secure and user-friendly mobile applications and services. Estrela et al. (2021)
aimed to improve the security and usability of mobile banking applications by proposing a
framework for continuous user authentication based on touch dynamics, biometrics, and location.
The framework, Biotouch, uses machine learning models to analyze users' behavioral patterns
when interacting with their devices' touchscreens, such as typing and sliding, and compare them
with their registered profiles. They applied TTAT to explain and evaluate the user’s behavior and
motivation regarding the continuous authentication framework.
TTAT was used to design and test the Biotouch framework and measure the user’s
satisfaction and acceptance (Estrela et al., 2021). They concluded that the Biotouch framework
could provide a secure and usable solution for continuous user authentication for mobile banking
applications. The TTAT offered a practical, theoretical framework for understanding and
predicting the user’s behavior and motivation regarding the framework. These studies showed
that TTAT, the theoretical framework for the study, was practical as it explored how
cybersecurity professionals perceived deviation from their organization’s cybersecurity policies

as a risk to their organization and how they were motivated to avoid or cope with this risk. TTAT
also helps identify the factors that influence behavior and intention, such as perceived threat,
perceived effectiveness, perceived cost, self-efficacy, perceived benefits, organizational support,
and peer influence. Effectively addressing this threat requires information systems professionals
to plan and prepare to handle cyber threats continually. The literature explored various facets of
cybersecurity and highlighted the importance of mature cybersecurity programs in mitigating
risks, particularly in financial organizations. Additionally, TTAT plays a significant role in
understanding users' perceptions and responses to technology threats. Developed by Almansoori
et al. (2023), TTAT emphasizes perceived susceptibility, severity, effectiveness, cost, and
selfefficacy in shaping avoidance behavior.
Marotta (2023) refined TTAT by introducing perceived benefits as a moderator and
showed that emphasizing positive outcomes can enhance users' motivation to avoid technology
threats. Studies by Al-Jarba and Al-Khathami (2021) and Estrela et al. (2021) applied TTAT to
biometrics-based authentication techniques for mobile devices, highlighting their potential to
enhance security and usability. Overall, TTAT provided a theoretical framework for
understanding and predicting user behavior and motivation in cybersecurity contexts, offering
insights for developing effective security measures and strategies.
Historical Context and Concern with Cyber Intrusions
Today, threats are increasingly likely to stem from information breaches, blurring the
boundaries between information privacy, security, invasive actions, and criminal behavior
Marotta (2023). Neiva et al. (2023) observed that numerous cybercriminals do not perceive cyber
intrusions as acts of theft. This perspective has contributed to expanding misappropriation to
encompass intangible assets like information, given the significant increase in cyber theft
incidents over the last decade. Investigations into misappropriation, its underlying causes, and
the traits of individuals involved in such acts must broaden their understanding of theft (Bécue et

al., 2021). Social media interactions, health records, phone logs, government records, and other
digital traces left by people were all prone to theft, leakage, and destruction (Neiva et al., 2023).
Kozyreva et al. (2021) further argued that notions of objectivity and accuracy often
proved illusory, as global datasets did not necessarily lead to improved information quality.
Moreover, they noted that public and private data were frequently removed from their original
context, significantly diminishing their meaning. The ethics of public versus confidential access
information were often abused and misconstrued, and the digital division based on permissible
accessibility caused a new digital divide in society. A shift in technological advancement and
open public information acts led to a breakdown in the community. Kozyreva et al. (2021)
asserted the necessity for societal comprehension of cybersecurity industry-recognized best
practices' role in molding global dynamics, mainly through their adoption by organizations. Such
ideas provided a new facet of society that was a frightening possibility, with the world simply
accessible to all (Kozyreva et al., 2021).
Technology, analysis, and mythology through Big Data triggered utopian and dystopian
rhetoric (Neiva et al., 2023). Such rhetoric offered benefits and changes along with information
theft, abuse, invasion, and control of society’s most private lives. Research led by IT specialists
observed insider dangers by assessing the effect of federal-state intrusions on community and
government organizations. Demertzi et al. (2023) further suggested that improving
comprehension of cyber threats and developing preventive measures to battle insider dangers
were required to control and alleviate hacker risk. These preventative methods exhibited a
security situation that favored a database administrator to commit malicious acts. Analysts then
discussed courses where the same problem could be relieved by utilizing the Insider Threat
Security Architecture model, copying the methodology but protecting other countries from
entering U.S. technology (Judijanto et al., 2023). Keeping malicious insiders from breaking into

U.S. systems and stealing private information at the database application level was necessary, but
determining the best method proved difficult.
The study highlighted that reviewing and assessing some archived national and state
intrusion risk cases helped distinguish the qualities and properties of terrorists who attempted to
steal private and federal security information (Choi et al., 2021). Choi et al. (2021) identified the
utility of forecasting patterns and revealing fundamental techniques malicious hackers employ.
Reviewing a portion of the archived hacker occurrences also helped to determine the hacker’s
thought processes and expectations for carrying out such violations. Such may be an appropriate
mechanism to recognize and utilize. The availability of remote access to an organization’s data
network further drives the ability of harmful hackers to commit breaches. Many information
thieves use the ability to access and break into outside networks remotely. They can use a
removable device such as a portable drive or SD Card to download classified data without
notice. In one such incident, a virus erased 10 billion records in the networks of a universal
budgetary administration organization (Kozyreva et al., 2021). The incident influenced over
1300 of the organization’s servers throughout the United States. The incident cost the company
$3 million to repair the damage. During the investigation, Kozyreva et al. (2021) determined that
a disgruntled team member, disappointed by his end-of-year bonus size, had planted the virus.
Scholars noted that a single team member could create chaos. Hackers with professional
experience and a background in such criminal activity would easily find such break-ins and, over
the last several decades, have innovated more methods for cyber theft (Kozyreva et al., 2021).
Information theft for business advantage was a class of insider danger that included
taking private business information by present or previous employees, business accomplices, or
contractual workers (Kozyreva et al., 2021). Cybercriminals could authorize access to the
network, taking confidential or sensitive business information from their company and using it

for business advantage. In this situation, Kozyreva et al. (2021) found that malicious insiders
aimed to use the data to secure a better position with a competitor, start a competing business, or
sell the information to competitors. These insiders held positions that provided them daily direct
contact with sensitive data and authorized access. Studies showed that such breaches caused
significant data loss to an organization and cost millions to investigate and repair the issues
(Kozyreva et al., 2021).
Importance of Information Security in Implementing Adequate Security Policies
Information security is paramount when protecting a customer’s sensitive information.
Moreover, they mitigate information risks. It safeguards data during transmission across various
networks and encompasses software and hardware. Information security employs several
mechanisms, including access control and data encryption, to thwart third parties and users'
unauthorized access. Security measures such as firewalls also play a crucial role in ensuring the
authentication of individuals using identification names and passwords (Mishra et al., 2022).
Key reasons highlighting the importance of information security include protecting
sensitive data. Information security prioritizes safeguarding sensitive data, including customers'
banking and personal information. Encryption prevents unauthorized access by converting data
into a format only a decryption key can read. The primary objective is to avoid identity theft
(Mishra et al., 2022). The second step is ensuring data integrity. Information security focuses on
maintaining data confidentiality, integrity, and availability. Data must be accurate and actively
operational to prevent security breaches. Mishra et al. (2022) stated that only authorized
individuals could access data or necessary tools due to confidentiality and availability. The third
step is minimizing risks. Information security helps organizations identify and mitigate
vulnerabilities and risks. Thus, mitigation includes regular data backups and encryption, team

member training, and keeping software and systems current. Strong password policies are also
crucial in information security (Yeng et al., 2021).
Practical strategies and objectives in information security include standards that establish
efficient information security management practices. Typical objectives include confidentiality,
availability, and integrity, aligning technology portfolios with broader risk mitigation goals (Yeng
et al., 2021). Information security protects sensitive data from unauthorized actions, ensuring the
protection and privacy of critical information. It helps organizations make informed business
decisions and manage risks effectively (Yeng et al., 2021). The Information Security department
grants or approves access to tools or networks based on roles and responsibilities. Yeng et al.
(2021) stated that the system monitors access attempts and limits access for juniorlevel
employees. Data is categorized and assigned sensitivity levels to avoid unnecessary pressure and
ensure data protection (Yeng et al., 2021).
Financial data should be backed up and encrypted using industry-standard protocols.
Information security monitoring is crucial for compliance and data protection (Ahmad et al.,
2019). Organizations must follow industry-specific security guidelines like the NIST framework.
Employees should be confident in adhering to information security practices (Ahmad et al.,
2019). Compliance frameworks are essential for protecting organizations and adhering to
security rules and regulations. Thus, the compliance framework included staying updated on
security tools and frameworks, planning, and testing (Ahmad et al., 2019). Information security
is critical for safeguarding sensitive data, ensuring data integrity, and minimizing risks and
vulnerabilities. Organizations should implement robust security measures and adhere to
industryspecific guidelines to protect customer and organizational data effectively.
Current Context
Using advanced technologies in businesses, government, and individual private homes
has become problematic as data and information security are continually breached (Burnes et al.,

2020; Harrell, 2019). Such an impact of technology theft has created a new array of legal
mandates and laws to protect such secure information. However, the financial burden, the legal
consequences, the reputational damage, and the overall impact on our society continue to present
challenges to legislation (Malgieri, 2020). Today, many entities invest significant funds into
security measures to keep electronic information safe (Burnes et al., 2020). This new age of
technological security systems has come with separate and more formidable issues.
Technological advancement has caused a modern era of policies, legalities, and laws to be
necessary. Burnes et al. (2020) and Malgieri (2020) highlighted the considerable challenges that
emerge from the progression of technology usage within society. The primary concern for future
consequences, if the study did not address this topic, would come from the knowledge that
hackers have the potential to hack and steal data stores in the cyber world. Such theft can create a
haze of effects for the financial industry, leading to problems when a hacker takes a customer’s
data to sensitive, compassionate combat plans not secured within the Security landscape
worldwide (Harrell, 2019; Malgieri, 2020).
Using advanced technologies in various sectors has led to ongoing challenges with data
security breaches (Burnes et al., 2020; Harrell, 2019). These advanced technologies have
necessitated new legal mandates and laws to protect sensitive information. However, the
financial burden, legal consequences, reputational damage, and societal impacts continue to pose
challenges for legislation (Malgieri, 2020). In response to security breaches, numerous
organizations are allocating substantial resources to protect electronic data (Burnes et al., 2020).
Concurrently, the evolution of technology introduces novel and more complex obstacles,
necessitating the development of contemporary policies and legal structures (Malgieri, 2020).
The substantial issues arising from society's escalating dependence on technology have been
recognized (Burnes et al., 2020; Malgieri, 2020). Failure to address these challenges could have

severe consequences, as hackers could potentially breach cyber data stores, leading to various
adverse effects, including disruptions in the healthcare industry and financial sector
vulnerabilities (Harrell, 2019; Malgieri, 2020).
Cyber Threats to Financial Organizations
Financial organizations, including banks, small and large for-profit, credit unions, and
insurance companies, heavily depend on technology to facilitate daily transactions, which is the
foundation of their operations (Varga et al., 2021). Thus, the absence of infrastructure would
significantly limit the sector's functionality. However, this reliance on technology exposes
organizations to cyber risks. Cyber responsibilities within these organizations are often spread
across departments, posing challenges in recognizing and prioritizing threats (Alahmari &
Duncan, 2020). Additionally, the division of cyber responsibilities can complicate the
development of strategies to address and resolve cyber threats effectively. Breaches into banking
systems raise concerns as they are among the most damaging cyberattacks, allowing attackers to
access sensitive financial information. The consequences of security breaches on banks were
diverse, including damaging their reputation, losing customer trust, and disrupting the financial
sector (Varga et al., 2021).
Previous Incidents in Financial Organizations
The banking industry has experienced data breaches over time, impacting consumers and
institutions significantly. One of the breaches occurred in Equifax, a leading credit reporting
agency, which disclosed a breach that compromised the information of around 147 million
individuals (Kost, 2023). This Equifax breach raised concerns about privacy and security,
involving details like social security numbers, birth dates, addresses, and driver's license
numbers. In the aftermath of the Equifax breach, it became evident that there were four security
flaws within the company's systems. Equifax's failure to quickly address a known vulnerability in

its Open-Source development framework highlighted weaknesses in its patch management
procedures. Inadequate segmentation within Equifax's network allowed attackers to move freely
across servers, worsening the scale and impact of the breach. Storing usernames and passwords
without encryption made it easy for cybercriminals to access systems and data. Overlooking the
renewal of an encryption certificate for a tool allowed attackers to extract data covertly for a
period, emphasizing the importance of timely certificate management in combating cyber threats
(Kost, 2023).
Data breaches at Equifax are a warning for banks by emphasizing the importance of
cybersecurity practices, staying alert to new risks, and safeguarding customer information at the
forefront in today's digital era. JP Morgan Chase & Co. also experienced a breach in its data
security that highlighted vulnerabilities in the cybersecurity defenses of financial organizations.
(Kost, 2023). This breach, executed by cybercriminals from Brazil, involved infiltrating over 90
JP Morgan servers by exploiting access to carry out their activities (Kost, 2023). Instead of
focusing on stealing financial information, the attackers chose to target customer contact details,
such as names, email addresses, and phone numbers. While this may seem harmful, it still has
far-reaching consequences.
Investigations following the breach revealed shortcomings in JP Morgan's security
measures and the failure to implement Multi-Factor Authentication (MFA) on one of its network
servers (Kost, 2023). MFA is a recommended security feature that adds a layer of protection by
requiring users to provide multiple forms of authentication before accessing sensitive systems or
data (Alkhalil et al., 2021). The absence of MFA left a vulnerability for exploitation, emphasizing
financial organizations' need to adopt comprehensive security protocols to effectively defend
against evolving cyber threats (Kost, 2023). The incident at JP Morgan indicated how persistent
and adaptable cyber threats can be, stressing the role robust cybersecurity practices and proactive

risk management play in safeguarding financial systems and securing customer data against
malicious entities.
The WannaCry ransomware incident is often cited as one of the most devastating
cyberattacks in recent memory, creating widespread turmoil globally. By leveraging a
vulnerability found in Microsoft Windows systems, WannaCry encrypted files on compromised
devices and demanded Bitcoin payments for decryption keys (Kafi & Akter, 2023). This attack
used the Eternal Blue exploit, believed to have links to the United States National Security
Agency (NSA), revealed by a group known as the Shadow Brokers. Exploiting a weakness in the
Server Message Block (SMB) protocol, WannaCry rapidly spread across the internet, infecting
computers in over 150 countries within days.
The impacts of the WannaCry assault were far-reaching and non-selective, causing havoc
across sectors and industries on a global scale. Noteworthy casualties included healthcare
facilities, government bodies, financial entities, and businesses of varying sizes (Sabharwal &
Sharma, 2020). The attack led to disruptions in services and operations, with healthcare
institutions struggling to retrieve records for treatment purposes while businesses encountered
substantial financial setbacks and operational disturbances. The attack hit prominent
organizations like the National Health Service (NHS) in the United Kingdom, Spanish
telecommunications giant Telefónica, and FedEx (Ambika, 2021). Victims received ransom
demands in Bitcoin currency, usually starting at $300 and escalating. The perpetrators threatened
to encrypt files if they did not receive the ransom within a specified period. Despite the incident's
repercussions, the relatively modest sum paid as ransom suggested that many affected entities
chose not to succumb to extortion pressures. Efforts to comply with the demands for payment
focused on limiting the ransomware's spread, recovering compromised systems from backups,
and enacting measures against future cyber threats.

Government entities, cybersecurity firms, and technology corporations cooperated in
response to the WannaCry cyberattack. Microsoft quickly issued emergency patches to fix the
vulnerability exploited by WannaCry, advising users to update their systems and enhance
security measures. Cybersecurity experts diligently studied the code, created decryption tools,
and disrupted the attacker's operations. While the identity of those for the WannaCry attack
remains uncertain, many cybersecurity specialists and government bodies suspect Korean
statebacked hackers like the Lazarus Group (Kafi & Akter, 2023). This incident highlighted the
ransomware threat and emphasized the importance of proactive cybersecurity practices such as
regular updates, patching software, backing up data, and educating employees on cybersecurity
protocols.
The finance industry has faced significant data breaches, notably the Equifax breach,
which compromised the data of around 147 million individuals and revealed critical security
flaws (Kost, 2023). This incident underscored the importance of timely patch management,
network segmentation, encryption, and certificate management in combating cyber threats (Kost,
2023). Similarly, JP Morgan Chase & Co. experienced a breach, revealing vulnerabilities in
cybersecurity defenses and the necessity for Multi-Factor Authentication (MFA) (Kost, 2023).
The WannaCry ransomware attack, leveraging a Microsoft Windows vulnerability, caused
widespread global disruption, emphasizing the need for proactive cybersecurity measures and
stakeholder collaboration (Kafi & Akter, 2023; Sabharwal & Sharma, 2020). Despite the
challenges, swift responses, including emergency patches and decryption tools, demonstrated the
importance of proactive cybersecurity practices (Kafi & Akter, 2023). These incidents highlight
the evolving nature of cyber threats and the critical role of robust cybersecurity practices in
safeguarding financial systems and customer data.

Cyber Attacks and Threats
In cybercrime, two categories cover a range of illegal activities, each bringing different
dangers to individuals, organizations, and society. The first category involves attacks on
computer networks or devices using technologies like malware, denial of service (DoS) attacks,
or viruses to cause harm or disruption (Stanikzai & Shah, 2021). Malware, which includes
various software types, can breach systems to steal essential data encrypted files for ransom
demands or control devices without detection for malicious purposes (Reshmi, 2021). DoS
attacks flood targeted networks or servers with traffic, making them inaccessible to legitimate
users and disrupting regular operations (Kumari & Mrunalini, 2022). Viruses infect systems.
Reproduce themselves, leading to damage to data and software (AL-Hawamleh, 2023).
The second type of cybercrime involves using networks or computers for deceptive and
exploitative purposes (Stanikzai & Shah, 2021). This category covers a range of actions,
including phishing schemes, identity theft, and information warfare. These activities take
advantage of the interconnected nature of systems to deceive and manipulate. Phishing scams
trick individuals into revealing information, like login details or financial data, through
misleading emails or fake websites posing as legitimate organizations (Wash, 2020). Identity
theft includes acquiring and misusing data to impersonate people for financial benefits or
unlawful deeds (Burnes et al., 2020). Information warfare is a cybercrime that spreads false
information to influence public opinions, erode trust in organizations, or create social unrest
(Taddeo, 2020).
Due to their underlying and implicit terroristic nature, the earliest national and state cyber
intrusions posed a considerable threat to the United States. With the continual advances in
technology, the increased propensity for cyberattacks has created concern about threats of
national and global disasters through information theft, data exchange, and system break-in (Jha

& Kumar, 2022). Such facets within contemporary situations or threatening acts against
organizations necessitate considerations for legal actions against the use of threatening
technology, cyber theft of data, and cyberattacks within businesses (Bécue et al., 2021; Jha &
Kumar, 2022). The continued threat of cyberterrorism and cyberwar has created a whole new
arena of legal issues, legislation, and security measures for the protection and safety of society.
As the danger of terrorism has increased significantly within multiple industries, so have cyber
protection methods.
Criminal systems assume they operate in a profit market from which alarmists and
cybercrimes acquire data (Bradshaw, 2021). Terroristic groups using federal-state intrusions were
highly involved in criminal activities, including weapons sales, smuggling, and illegal shipments
overseas. According to the head of UNODC, these unlawful arms fuel the brutality that
undermines security, improvement, and equity worldwide (Bradshaw, 2021). Hassanzadeh et al.
(2020) and Ho and Luong (2022) argued that cyberattacks were less chaotic, safer, and more
convenient for people who want to cause organizational harm than physical attacks. Moreover,
since an Internet connection does not have distance or geographical constraints, cyber attackers
can remotely carry out such attacks. Ho and Luong (2022) explained that this action occurs when
hackers turn to acts of revenge and cyberterrorism.
The danger of enhanced cyberattack methods has posed a massive challenge for financial
organizations to manage their respective data (Graves et al., 2019). Many companies learn of
data breaches after a long time when the data has leaked or the company has discovered financial
damages. Data breaches were a significant problem that affected most companies globally
(Dupont, 2019). However, companies have embarked on modern technological development to
counter the advanced methods of attack used by attackers within cyberspace (Bradshaw, 2021).
Achieving this may minimize many threats. Achieving this may also require massive financial

investments, which means this challenge may continue to affect smaller and medium financial
organizations. Various organizations have ensured a continued fight against institutional data
breaches and finances. Most companies continue implementing measures to secure their system
against violating the abovementioned standards. Because most targeted companies are small or
medium, they face many challenges that lead to loopholes that necessitate attacks from hackers
(Bécue et al., 2021).
Small to medium-sized businesses are also facing challenges with cybersecurity threats.
Attackers have begun to target these businesses because of their size and are easily targeted by
criminals (Chidukwani et al., 2022). Larger organizations invest considerable time and money in
their cybersecurity processes, whereas small to medium-sized businesses do not. Cybersecurity
challenges medium-sized businesses (SMBs) due to their limited resources and expertise.
According to Boletsis et al. (2021), a notable trend was the presence of several SMBs that either
lack an up-to-date cyber risk strategy or, more alarmingly, have no plan in place. This gap
exposes SMBs to obstacles when attempting to devise effective strategies to address cyber risks.
One significant internal barrier that SMBs encounter is a need for more awareness and
comprehension regarding the complexities of cyber threats and vulnerabilities. SMBs may need
to understand the evolving cyber landscape to assess the potential risks to their operations, data,
and reputation. This lack of awareness could hinder their capacity to prioritize cybersecurity
initiatives and allocate resources effectively.
Medium-sized businesses often need help to conduct thorough assessments of cyber risks
because they need more resources and expertise in cybersecurity. Compared to companies with
dedicated cybersecurity teams, SMBs may find it challenging to access the tools, methods, and
skilled personnel needed for comprehensive risk assessments (Alahmari & Duncan, 2020).
Furthermore, developing and implementing strategies to mitigate cyber risks can pose challenges
for SMBs due to capacity and competing organizational priorities (Chidukwani et al., 2022).

SMBs may need help investing time, effort, and money into cybersecurity initiatives, especially
if they view cybersecurity as a peripheral aspect of their operations. Additionally, they may need
more governance structures and processes to effectively handle cybersecurity risks across their
entire organization.
The changing landscape of cyber threats poses a continuous challenge for small and
medium-sized businesses (SMBs) as they struggle to keep up with new risks and vulnerabilities.
Lacking timely threat information and proactive monitoring tools, SMBs may be unprepared to
promptly identify and respond to cyberattacks, increasing the risk of financial losses and damage
to their reputation (Alahmari & Duncan, 2020). SMBs encounter obstacles when developing and
implementing strategies to mitigate cyber risks. Overcoming these hurdles necessitates raising
awareness about cybersecurity, strengthening organizational capabilities, and cultivating a
security-conscious culture within SMBs (Chidukwani et al., 2022). By giving importance to
cybersecurity measures and investing in resources and expertise, SMBs can enhance their
defense against cyber threats, ensuring the continuity and resilience of their business operations.
In the realm of cyber warfare, a notable and burgeoning technological tool for malicious
actors is artificial intelligence (AI). These actors have adeptly employed AI to orchestrate
targeted assaults with unprecedented velocity and magnitude, eluding conventional rule-based
detection systems by implementing offensive AI techniques (Guembe et al., 2022). These
AIdriven cyberattacks represent a pernicious exploitation of AI capabilities aimed at
compromising the digital fortifications of organizations (Guembe et al., 2022). However, the
utility of artificial intelligence extends beyond malevolent purposes; numerous entities have
embraced AI to fortify the security of Internet of Things (IoT) devices and networks (Abdullahi
et al., 2022). By leveraging AI algorithms, these financial organizations endeavor to bolster
defenses against emerging threats and enhance the resilience of interconnected systems in the

face of evolving cyber risks. The financial sector has increasingly turned to artificial intelligence
(AI) as a cornerstone for fortifying cyberdefense systems (Meduri et al., 2024). This strategic
shift reflects a recognition of AI's potential to bolster security measures and mitigate evolving
cyber threats.
AL-Dosari et al. (2024) delved into this trend by examining the ramifications of AI adoption on
cybersecurity within Qatari banks. Their qualitative analysis unearthed four overarching themes,
shedding light on the promises and challenges inherent in leveraging AI for cybersecurity in the
banking sector.
The study underscored AI's pivotal role in augmenting financial organization's
cybersecurity posture. By harnessing AI-driven algorithms and machine learning techniques,
financial organizations can enhance threat detection capabilities, identify anomalous activities,
and respond swiftly to security incidents, fortifying their defenses against cyberattacks. The
research also pointed out two aspects of AI and showed how the technology can be misused for
harmful purposes, posing a severe risk to banks. Criminals skilled in using AI-based tools can
carry out attacks, exploit weaknesses, and bypass traditional security methods. Using AI-based
tools highlights the need for banks to stay alert and adapt their defense tactics to combat new
threats effectively (Abdullahi et al., 2022).
Additionally, the study emphasized the difficulties banks face when utilizing AI to
enhance cybersecurity. Despite the benefits of AI-driven solutions, financial organizations need
help seamlessly incorporating AI technologies into their current systems, navigating through
regulatory obligations, and addressing issues related to data privacy and ethical considerations
(Abdullahi et al., 2022). Additionally, the study shed light on the vulnerabilities inherent in
banks' AI-based tools, which inadvertently exposed financial organizations to cyber threats.
Flaws in AI algorithms, data bias, and adversarial attacks pose significant risks, potentially

undermining the efficacy of AI-driven cybersecurity measures and necessitating robust
mitigation strategies.
A recent study by Guembe et al. (2022) explored how AI impacts the banking sector by
improving efficiencies and building customer trust. The study emphasized that AI enhances
risk management, streamlining processes, cutting costs, and enhancing the customer
experience. Banks can make better-informed decisions through AI-driven analytics and
automation, offer personalized services, and maintain transparency and accountability to
cultivate customer relationships. Incorporating AI into cybersecurity and operational
frameworks in the banking sector signifies a shift with far-ranging implications. While AI
presents opportunities to strengthen cybersecurity measures and improve banking services, it
also brings challenges and risks that require attention and proactive management strategies. By
navigating these complexities ethically, AI financial organizations can harness their potential
to safeguard their assets, drive innovation, and nurture lasting client relationships in an
increasingly digital world (Guembe et al., 2022). Thus, incorporating insights from the
comprehensive discussion on cybersecurity in financial organizations, this literature review
highlights the critical importance of robust cybersecurity protocols. Cyberattacks' escalating
prevalence and sophistication necessitate a proactive and dynamic approach to safeguarding
sensitive data. The shift towards employing advanced technologies, such as Artificial
Intelligence (AI), has emerged as a pivotal strategy in enhancing cybersecurity defenses. AI-
driven algorithms offer promising avenues for detecting and mitigating threats more efficiently
and precisely (Guembe et al., 2022).
Furthermore, the collaborative efforts among cybersecurity professionals, regulatory
bodies, and technological innovators play a crucial role in developing comprehensive
cybersecurity frameworks. These collaborative endeavors balance innovation with security,

ensuring the financial industry's resilience against evolving cyber threats. This synergy between
technological advancements and strategic collaborations underscores the imperative of a
multifaceted approach to cybersecurity, emphasizing the need for continuous adaptation and
vigilance in the face of an increasingly complex cyber threat landscape (Guembe et al., 2022).
Cyber intrusions threaten national and global security, particularly those with terroristic
implications. The evolving landscape of cyber threats necessitates legal actions, legislation, and
security measures to safeguard against information theft and cyberattacks (Bécue et al., 2021; Jha
& Kumar, 2022). Criminal organizations exploit cyberspace for profit, weapon trafficking, and
illegal shipments, contributing to global insecurity (Harviainen et al., 2023). Cyberattacks,
facilitated by technological advancements and the Internet's reach, pose substantial challenges to
financial organizations, necessitating robust cybersecurity measures and risk management
strategies (Bradshaw, 2021; Dupont, 2019; Graves et al., 2019). Small to medium-sized
businesses (SMBs) face particular challenges due to limited resources and expertise, hindering
their ability to address cyber risks effectively (Alahmari & Duncan, 2020). AI-driven
cyberattacks represent a growing threat, exploiting AI capabilities to compromise digital
defenses, necessitating proactive cybersecurity measures and adaptation strategies (Guembe et
al., 2022). Despite challenges, AI adoption offers opportunities to enhance cybersecurity,
improve operational efficiency, and build client trust, marking a transformative shift in the
banking sector (AL-Dosari et al., 2024). However, responsible AI deployment requires
addressing regulatory, ethical, and privacy considerations to mitigate risks effectively.
Malware and Security
Most contemporary cybersecurity attackers have developed means that enhance attacks
while erasing any trace that may lead to detection or an early response from the company. Many
attackers have developed sophisticated malware to launch the attacks (Beaman et al., 2021;

Meland et al., 2020). Malware contains several variants, such as ransomware, spyware, and
viruses. The threat landscape in cybersecurity has evolved along with the digital landscape, and
malware has transformed from its original traditional file-based malware to more sophisticated
and multifarious malware (Sudhakar & Kumar, 2020). Fileless malware can attack systems and
remain undetected through surveillance, persistence, data theft, or execution. This malware has
two significant advantages: financial organizations' lack of early detection and erasing any link
that can lead to detection. Designers of malicious software often make it enticing to spark
curiosity among targeted individuals. The allure of the information and the strategic development
of hyperlinks lead users to engage with links or advertisements, significantly damaging their data
and computer systems (Brundage et al., 2018; Samangouei et al., 2018).
Furthermore, vulnerabilities have been identified in emails, advertisements, and links
disseminated through malicious software, exposing devices to potential threats (Bécue et al.,
2021; Sudhakar & Kumar, 2020). While organizations may deploy software solutions to combat
cyber threats, these may not always cover the specific nuances required to thwart certain types of
attacks. Ransomware is one of the most prevalent and harmful forms of malware infiltrating
digital landscapes worldwide (Kara & Aydos, 2022). Ransomware operates through
cryptographic modules designed to render victims' data inaccessible or beyond reach. The
ransomware infection is twofold: either by encrypting critical files or effectively immobilizing
devices, thus impeding users' access to their data. Once ransomware infects a user's data, the
cyber assailant leaves victims with an ultimatum: either succumb to their demands by paying a
ransom or risk losing their data and facing a system lockdown (Reshmi, 2021). This form of
digital extortion impacts individuals, businesses, and even governmental entities by causing harm
to data integrity and operational continuity.

With each successful ransomware incursion, the cybercriminals behind these campaigns
create chaos and disruption and operate a lucrative underground economy through ransom
payments from victims (Reshmi, 2021). The ramifications of ransomware attacks extend beyond
the immediate financial toll victims experience. The loss of trust in digital systems, the
compromise of sensitive information, and the destabilization of critical infrastructure represent
just a fraction of the broader societal repercussions of ransomware (Kara & Aydos, 2022). As
such, combating intelligence added a multifaceted approach encompassing comprehensive
cybersecurity measures, proactive threat intelligence, and concerted international cooperation to
dismantle the underlying infrastructure supporting ransomware operations and hold perpetrators
accountable for their attacks.
Cybersecurity has been an elusive problem. Companies and financial organizations face
threats to their private data and finances. The cyberattack on Capital One serves as a significant
example of the cybersecurity threats faced by organizations today. In this incident, a data breach
exposed personal information belonging to over 100 million customers in the United States and 6
million in Canada (Novaes Neto et al., 2020). The breach was discovered by their Responsible
Disclosure Program rather than regular cybersecurity avenues. The criminal in this attack was a
single individual who created a scanning software tool that allowed them to identify servers
hosted by a specific cloud computing company that also had misconfigured firewalls. These
misconfigured firewalls allowed for the execution of outside commands to penetrate and access
the cloud computing servers. After the breach, an analysis showed that access to the server was
possible because of a Server-Side Request Forgery attack that was allowed because of a
configuration failure in the firewall solution used by Capital One. This event underscored the
vulnerability of financial organizations to such threats.

Similarly, cyberattacks have also identified insurance companies as prime targets. The
increasing dependence on technology in insurance systems and devices has pros and cons
because it offers connectivity and convenience. The connectivity and convenience also make
them vulnerable to cyberattacks. Cybercriminals target wireless-enabled insurance systems and
devices like insurance records, risking safety and data security (Sethuraman et al., 2020). Cyber
attackers commonly use threats like denial of service (DoS) attacks and phishing schemes against
financial infrastructure. DoS attacks can disrupt services using network resources or turn off
systems, potentially impacting insurance care. Phishing attacks trick insurance workers into
revealing information or installing malware through social engineering tactics, endangering
patient confidentiality and data protection.
Furthermore, as Spanakis et al. (2020) noted, many financial organizations must prepare
to deal with the growing cybersecurity threats associated with technology. Security protocols and
educational campaigns in the financial industry must be improved, making these organizations
vulnerable to cyber threats. Adding to these risks is reliance on outdated systems that lack
security measures and do not receive updates, perpetuating known vulnerabilities and raising the
chances of unauthorized access or data breaches. Additionally, the intricate nature of healthcare
settings, with their interconnected systems and various data sources, presents challenges in
reducing risks, ultimately increasing the susceptibility to cyberattacks. These instances
underscore the intricate nature of technological development in creating effective and efficient
attack methods that leave no trace. They also highlight the challenges organizations face in
mitigating these threats. The complexity of these attacks and the difficulty in tracing them back
to their source pose significant challenges to threat mitigation efforts.
Studies also highlighted complex malware attacks on companies whose employees were
unaware of the constant attack (Brundage et al., 2018; Sudhakar & Kumar, 2020). Traditionally,

companies have developed strategies to mitigate the effects of malware and attacks. Past research
showed they accomplished this mitigation by regularly checking their software and hardware
using antivirus and identification strategies. These checkups equipped employees with
knowledge of malware and other attacks on the company, establishing a more constricted
security strategy (Sudhakar & Kumar, 2020). The lack of equivalent development in the
countermeasures against enhanced attack patterns is another technological problem related to
financial organizations' challenges in mitigating company data breaches. Scholars claim that
thieves consistently stay one step ahead of law enforcement, as evidenced by the relationship
between attackers and companies (Beaman et al., 2021; Muzhanova et al., 2021).
The development of malware and attacks necessitated the development of
countermeasures within a company. Companies worked on manufacturing a virus and using the
properties of countermeasures to create an antivirus (Muzhanova et al., 2021). One related
problem is the lack of advanced technology equivalent to the threat to meet the mitigation
demand. Beaman et al. (2021) and Khan et al. (2020) observed numerous companies resorted to
fundamental, less effective security protection strategies. These challenges enabled employees’
inability to effectively detect, respond, and retrieve the breached data within the company. The
research showed how employees unknowingly initiated the attacks by downloading malware or
opening files that contained malware, which then led to the attack on the company’s data and
finances.
Computer and software technocrats constantly develop malware to infect people’s
computers and then sell antivirus to remove the malware. Samangouei et al. (2018) argued that
many people create a virus and its antivirus, a business venture many companies undertake
today. An analysis of some of the vulnerabilities of state-of-the-art techniques indicated that the
lack of continuous innovation and technological improvement gives hackers time to figure out

cloud computing techniques. McIntosh et al. (2021) argued that creators of some malware
programs designed them to mimic the original ones, making it difficult for users to distinguish
them or realize their computers had been infected with malware until it was too late. The
examination of instances where individuals used computers without recognizing that data theft or
financial siphoning often went unnoticed, leading to disastrous consequences (McIntosh et al.,
2021).
Symantec revealed that the rate of cyberattacks is about 69% in the general population
(McIntosh et al., 2021). Among those hacked, only 37% discovered the hacking in less than a
week, and only half knew how to regain control of their devices. The other half realized the
problems only when they got suspicious emails, requests, or information (McIntosh et al., 2021).
Other victims only discovered the cyberattack issues when they lost their money from banks.
These challenges grow in two fundamental ways: the development of complex malware that
attacks without detection or trace and the lack of equivalent growth in the countermeasure
technologies within many institutions (McIntosh et al., 2021). These challenges cut across all
financial organizations regardless of their level of operation or classification.
Most of the malware used by attackers, especially online users, targets the employees
who open the links or the information malware unsuspectingly. Malware often passes through the
computer’s defense system, engulfing existing applications rather than infiltrating the internet
(Nahmias et al., 2020). An unsuspecting team member would easily let the malware infest the
computer, triggering an attack. A team member would receive an email not from a person or a
compromised account of somebody known to them but from hackers. These emails come in the
form of Excel or Word documents, which, upon download, would trigger the opening of macros
responsible for running subsequent tasks on the computer (Van der Ham, 2021).

Disclosure issues may also cause cyberattacks. Jia et al. (2020) and Seh et al. (2020)
stated that some attacks on an organization happen when members are confronted with
confidential matters and coerced to act as the attacker demands. Individuals shared sensitive
information with attackers to protect themselves; attackers used the compromised individual for
information and sometimes planted malware in highly secured places. The type of malware and
the choice of an organization’s defensive mechanism were noted as crucial weapons for fighting
or losing and securing a company’s databases (Nahmias et al., 2020; Saeed, 2020). Nahmias et
al. (2020) and Saeed (2020) explained the types of malware, including viruses, Trojan horses, bot
executables, worms, and spyware, and that the nature of each infection was unique to each
malware.
Counter-malware software sometimes fails to protect computers efficiently, leading to
vulnerability even for those with some types of defensive models. Hassanzadeh et al. (2020)
asserted that data must be encrypted well when reporting the loss of devices, and immediate and
appropriate action must be in place to handle emergencies. Organizations with sensitive data
should hire people with computational logic skills to create sophisticated defensive techniques to
control data, the Internet, connectivity, and networking (Hassanzadeh et al., 2020). Companies
should restrict access to sensitive areas such as servers, security rooms, and central operating
systems and install a scheme that eases tracking of activities for monitoring and evaluation
(Hassanzadeh et al., 2020).
In contemporary cybersecurity, attackers have evolved sophisticated means to launch
attacks while covering their tracks, presenting challenges for detection and response (Beaman et
al., 2021; Meland et al., 2020). Malware, including ransomware, spyware, and viruses, has
become a prevalent tool for attackers to target individuals and organizations. (Sudhakar &
Kumar, 2020). Fileless malware, in particular, poses a significant threat by operating without

leaving traditional traces, enabling attacks like reconnaissance, persistence, and data theft to go
undetected (Sudhakar & Kumar, 2020). Attackers exploit human psychology and vulnerabilities
in emails, advertisements, and links to deceive users into clicking on malicious content, leading
to devastating consequences for data and systems (Brundage et al., 2018; Samangouei et al.,
2018).
Ransomware, a prominent form of malware, encrypts data or immobilizes devices,
demanding ransom payments from victims to regain access (Kara & Aydos, 2022). These attacks
disrupt operations, compromise data integrity, and erode trust in digital systems (Kara & Aydos,
2022). High-profile incidents like the Capital One breach highlight the vulnerability of financial
organizations to cyber threats, with attackers exploiting misconfigurations and vulnerabilities in
systems (Novaes Neto et al., 2020). Healthcare institutions are also prime targets, facing risks
from wireless-enabled systems vulnerable to DoS attacks and phishing schemes (Ghafur et al.,
2019; Sethuraman et al., 2020).
Malware in the Financial Sector
The rise in the availability of off-the-shelf software marks a significant change in
cybercrime, making advanced tools and tactics once exclusive to experienced hackers more
accessible to a broader range of individuals (Gulyás & Kiss, 2023). This shift has made it easier
for even beginners in activities to launch their unlawful operations with minimal effort. The easy
access to packaged malware often found for sale or download on underground platforms and
marketplaces offers aspiring cybercriminals a quick route to carrying out attacks without needing
extensive technical knowledge or resources (Zimba, 2022). Mobile devices have become targets
due to their widespread use in daily life and the increasing reliance on mobile apps for various
tasks. Expanding cloud services has also opened up possibilities for exploitation as criminals try
to breach sensitive data stored in the cloud or identify weaknesses in cloud infrastructure (Gulyás

& Kiss, 2023).
By exploiting weaknesses in payment networks and online transaction platforms,
cybercriminals take advantage of this environment. These trends provide cybercriminals with
various ways to launch attacks, from traditional malware infections and phishing scams to more
sophisticated methods like ransomware and supply chain attacks. Furthermore, the
interconnected structure of digital environments, as emphasized by Zimba (2022), magnifies the
potential consequences of vulnerabilities. A single security flaw in a mobile app could put the
personal information of millions of people at risk, paving the way for further exploitation.
Similarly, breaches in the infrastructure of cloud service providers could lead to large-scale data
breaches affecting organizations and individuals. Effectively combating these increasing cyber
risks requires a strategy. This strategy should involve technical solutions, strong cybersecurity
policies, thorough user education programs, and collaborative efforts among industry players and
law enforcement agencies. Since cybercriminals evolve their techniques, organizations and
individuals must stay alert, proactively protect their digital assets, and counter emerging threats
(Gulyás & Kiss, 2023).
The increase in readymade software availability has made cybercrime more accessible,
allowing even beginners to engage in activities easily, as discussed by Gulyás and Kiss (2023)
and Zimba (2022). Ready-to-use malicious software, found on various platforms, has made it
easier for new cybercriminals to enter the field without requiring technical knowledge. By
exploiting vulnerabilities in payment networks, online platforms, and cloud services,
cybercriminals carry out attacks ranging from malware infections to complex ransomware and
supply chain attacks. The interconnected nature of environments highlighted by Zimba (2022)
magnifies the impact of vulnerabilities posing risks to individuals and organizations.

Cyber Models, Systems, Protections, and Methods for Security
Tactical approaches to dealing with established and knowledgeable hackers require
organizations to use multiple defensive mechanisms. A company can use a set of fingerprints to
log in, followed by a password, and then decryption of data, which hinders an intruder from
successfully going through all the above procedures (Yaacoub et al., 2020). With the increased
use of technology, a constant adaptive market was established, with technological hardware and
software constantly being upgraded. Valette et al. (2023) and Yaacoub et al. (2020) documented
the effects of these transformations on cyberattacks across various sectors, highlighting
healthcare as the most extensively discussed industry in contemporary literature. Even so,
deeming security imperative for many organizations, scholars, experts, and organizational
leaders described the need to understand the complexity, variety, and variability of all cyber
protection models and methods available for public use (Valette et al., 2023; Yaacoub et al.,
2020).
The rapid expansion and increased connectivity of Internet users have been linked to a
heightened risk of cyberattacks, as indicated by Doan et al. (2020) and Y. Li & Liu (2021).
Technology's continuous evolution necessitated corresponding security measures updates to
address emerging vulnerabilities (Doan et al., 2020). Significant vulnerabilities within an
organization's computer systems require comprehensive protection across all technological
assets. The lack of security in a single device, such as a computer, tablet, or another piece of
technology, could jeopardize the integrity of the entire network (Cremer et al., 2022; Y. Li &
Liu, 2021). Furthermore, a sophisticated attacker exploiting a single vulnerable computer could
potentially gain access to and compromise other interconnected devices, leveraging any existing
gaps in connectivity to breach even well-secured technologies (Cremer et al., 2022).

Security frameworks help many organizations mitigate the risks and threats of
cyberattacks and are available for public organization purchase among these frameworks. While
many models are associated with these preventative methods, the literature typically discusses
the three most common and most successful: The National Institute of Standards and Technology
(NIST) framework, ISO 27000, and The Center for Internet Security (CIS) (Roy, 2020). Studies
examining these three methods showed how each method’s maturity specifically increased the
cybersecurity platform security when implemented based on the order of steps consistent with
the system reaching maturity (Roy, 2020).
The NIST framework primarily offered cybersecurity services based on identity,
detection of breaches, recovery of stolen data or information, response to data breaches, and
detection of any ongoing violations on the company (Snider et al., 2021). NIST is the most
adopted cybersecurity strategy to ensure the safety of an organization’s data. This model
followed five key phases to reach the maturity necessary for a cybersecurity management
program: identify, protect, detect, respond, and recover (Roy, 2020). In the first phase,
organizations established a business-wide approach to cybersecurity management, including
understanding the current risks to the network, what sensitive information lives throughout the
organization, and what critical business operations are needed to protect from cybersecurity
threats. Phase 2 entailed building program maturity and defining the defenses necessary to
protect the essential pieces of a security program. Phase 3 prompted an organization to act by
highlighting practical tools for monitoring cyber risks. The response phase increased program
maturity while tackling an organization’s known threats. The Response phase is more than just
patching a network; it incorporates the proper containment of malicious activity. The fifth phase
of recovery impacted the organization. It suggested that management processes schedule time to

recover and reflect on damages to allow for real program improvements and better future
network protection (Roy, 2020).
Studies showed how cyberspace teams provided concrete protection and policies against
data breaches and finances in a company (Dalal et al., 2021; Williams et al., 2020). The use of in-
depth security defense models established four fundamental layers. When implemented, the
organization (a) demonstrated comprehension of the networks, communication channels used by
the organization, and the technological infrastructure within the company; (b) prepared
comprehensive security policies, strategies, and protocols together with a complete
implementation plan within each respective financial organization; (c) conducted timely tests and
inspections of the entire security infrastructure within an organization, maintenance, and
upgrades in situational demands based on the shift in methods and nature of attacks over time;
and (d) undertook mitigative measures before the speculated incidences of attack on the data or
finances of the company (Dalal et al., 2021).
Nisha et al. (2023) suggested that organizations be aware of the fundamental layers of
security protection: perimeter defense, protection of the host, application security, and data
protection. Each layer builds upon the previous and establishes a concrete security platform.
Cybersecurity experts noted perimeter defense as the most fundamental layer of security
protection (Nisha et al., 2023). The perimeter defense layer entailed two essential elements:
connections and proxy connections. The study noted that 70% to 80% of data breaches originate
within an organization. The primary focus of the perimeter defense layer was to secure the data
from internal breaches or alterations. This layer formed the initial defense line, although it may
need more reliable protection for organizational data (Nisha et al., 2023).
The second layer is the protection of the host. With security concerns also stemming from
internal activities connected to the initial network, this second layer (a) protected from internal

attacks by maintaining a similar connection to one network and (b) secured stored data from
external intrusion through a firewall (Fonseca & van Wyk, 2021). This layer’s method has
several characteristics, including policies allowing users to access the intended data but
restricting access to other organizational data. The organization updates primary security
measures while recognizing the inability to retain spoiled hardware and software within the
organizational infrastructure (Fonseca & van Wyk, 2021).
The third layer protects an entire operating system with all related servers (Burnes et al.,
2020). This application security is ideally provisional upon applications within any given
operating system that utilizes different types of traffic. Suppose users of the applications or other
operating systems within the company compromise the network. In that case, it exposes the
network to external risks. This layer’s security hardening helps protect the data across the
internet (Burnes et al., 2020).
The fourth layer, data protection, entailed using an organization’s shared network to
secure all devices within the company (Harviainen et al., 2023). This layer comprises two
security elements: temporary data security and data encryption. The three elements cover the
data being used or requested on the operating system, the sensitive data within the operating
system, and data protection through encryption (Harviainen et al., 2023). The examination of the
four layers revealed that cyber resilience enables organizations to implement strategic
mechanisms for safeguarding various types of data, a practice deemed crucial for entities
involved in large-scale database management and information exchange (Harviainen et al.,
2023).
Other experts claimed that intrusion detection software was more affordable and provided
more robust security through sensing and reporting an outside attempt to access an organization’s
data. Mahamood et al. (2023) explained that an immediate alert notified companies using the

next-generation firewall whenever someone attempted an intrusion. The software used automatic
remedy procedures such as automatically shutting down or prompting users to sign in and give
their credentials, changing passwords, and entering other verification details. Alqahtani (2022)
explained that people who are not tech-savvy might ignore such prompts from one machine and
continue working with the old versions, which endangers data and devices connected to it.
Studies showed a threat-based defense model on a fundamental principle of
understanding the nature of the attacks and the techniques an attacker implements while carrying
out the breach (Steingartner et al., 2021). They maintained a threat-based defense that allowed
for a crucial method of detecting a future threat to an organization (Huang & Chiang, 2021;
Steingartner et al., 2021). Analysts detected an attack in its initial stages. Studies showed that to
achieve this, and most security measures exploited the indicators of a pending, ongoing, or past
attack to create strong mitigating preventive measures (Nejad, 2022). This kind of defense model
addressed two fundamental demands of the companies: working on the basic hygiene model and
the effectiveness of the classifications in safeguarding the data and finances from breaches
(Mahamood et al., 2023; Moustafa et al., 2021). A defense model often relies upon a metered
attack strategy in which the entire framework protects the company from data breaches and
finances (Shipena & Gamundani, 2024). The defense model worked on designing a phase and
product presentation displaying all the speculative attacks and techniques that the cybersecurity
attackers used. This model proposed facilitating neutrality between an organization and the
platform while offering a broad spectrum of defensive measures applicable at various stages of
organizational activity.
The model follows three basic procedures: (a) creating and recreating consistent
damaging patterns based on the reports that emanate from the investigation of situational
breaches of data and finances within an organization, (b) harmonizing the attacking patterns and

consequently formulating the defense technique at each stage of attack to mitigate a
cybersecurity attack; and (c) Detecting and identifying the protective measures against any
speculative attack that may occur at any activity phase within the organization (Conway et al.,
2020). In typical cases, there were many mitigative options for neutralizing an attack (Alhayani
et al., 2021; Mahamood et al., 2023). Proactive and adaptable cybersecurity measures, known as
defenses, are crucial for countering cyber threats in real time. Unlike defenses that follow set
rules and patterns, dynamic defenses utilize advanced technologies to monitor, analyze, and
respond to evolving threats constantly (Zheng et al., 2022). These strategies are agile and
responsive, capable of effectively handling unfamiliar risks. Examples of defenses include
behavioral analytics to detect unusual user behaviors, machine learning to adapt defenses based
on past incidents, adaptive access controls adjusting privileges according to the context, threat
intelligence integration enriching security analytics with live threat data automated response
systems streamlining incident handling procedures and continuous security monitoring &
scanning of network activities for signs of compromise.
By implementing dynamic defense mechanisms, organizations can improve their ability
to identify, address, and mitigate cyber threats while bolstering their cybersecurity posture. The
literature highlights the need for organizations to employ multiple defensive mechanisms to
combat cyber threats effectively. With the proliferation of technology and the rise of off-theshelf
software, even novice cybercriminals can quickly launch attacks, underscoring the importance of
robust cybersecurity measures (Valette et al., 2023; Yaacoub et al., 2020). The increasing
connectivity of Internet users exacerbates the risk of cyberattacks, necessitating continuous
advancements in security measures (Doan et al., 2020; Y. Li & Liu, 2021). Security paradigms,
such as NIST, ISO 27000, and CIS 20, provide organizations with extensive methodologies to

bolster their cybersecurity stance, emphasizing key stages, including identification, protection,
detection, response, and recovery (Roy, 2020).
Additionally, implementing in-depth security defense models with layers such as
perimeter defense, host protection, application security, and data protection is crucial for
safeguarding against internal and external threats (Burnes et al., 2020). Intrusion detection
software and next-generation firewalls provide additional layers of security, detecting and
responding to potential breaches in real-time (Alqahtani, 2022; Mahamood et al., 2023).
Moreover, adopting a threat-based defense model allows organizations to understand attackers'
techniques and implement proactive measures to mitigate future threats (Xiong et al., 2022).
Dynamic defense mechanisms, such as behavioral analytics, machine learning, adaptive access
controls, threat intelligence integration, automated response systems, and continuous security
monitoring, were essential to address evolving cyber threats in real time (Zheng et al., 2022).
Overall, proactive and adaptable cybersecurity measures are imperative for organizations to
counter emerging threats effectively and bolster their resilience against cyberattacks.
Cyber Security and Defense
Primary measures are fundamental in tackling simple threats such as ordinary antiviruses.
However, with the increased complexity of the developed malware, the primary security strategy
fails to detect, respond to, and retrieve the stolen data from the companies. Because of this
failure, organizations remain susceptible to agents of cybersecurity attackers at any time. The
systematic challenges of agencies are that they cannot build resilient and long-lasting defensive
mechanisms against cyberattacks due to an increase in the nature and types of malware that
endanger the data security of many organizations. Bunker (2020) and Liao et al. (2018) stated

that hackers use gaps left behind by computer users using old technology to infiltrate an
organization and access other connected machines (Bunker, 2020).
Safeguarding information in the industry is essential due to its critical nature. There are
ways for companies to enhance the security of their data and that of their clients. One effective
method is implementing access control measures designed to prevent access to financial systems
and protect sensitive data, as Kafi and Akter (2023) highlighted. By managing access rights,
organizations can create barriers that deter unauthorized entry attempts and strengthen the overall
security of their data infrastructure. By addressing known vulnerabilities, companies can add a
layer of defense, reducing the risk of exploitation by malicious individuals looking to breach
financial systems. This level of vigilance not only enhances resilience but also takes a proactive
approach to defending against evolving cyber threats, thereby enhancing the security posture of
financial organizations in today's digital era.
According to Javed et al. (2020), organizations developed a defensive mechanism that
provides backup and differentiates systems so an attack should not interfere with all systems.
Defensive models were only sometimes practical due to the ever-changing nature of different
and ever-growing types of cybersecurity. Javed et al. (2020) added that it was essential for any
organization to remain prepared to defend their data and systems against cyber threats and
educate themselves and their employees on such dangers to databases and how to protect them.
Hackers utilized these new technologies before organizations knew them to infiltrate their
systems, cause havoc, steal data, or interfere with operations. Such changes and loopholes have
exposed companies to cyber insecurity, leading to data loss, money, or clients (Javed et al.,
2020).
Information protection has many organizations in a panic to incorporate security systems
that are foolproof and fail-safe. This fear of losing the information necessary to keep their
respective organizations in business falls under the panic syndrome theory (PST). PST is a

continuance of neglectful actions against many organizations’ employees. Hernandez-Castro et
al. (2020) and Parn and Edwards (2019) used PST to present a theoretical analysis of insider
threats. The incentives introduced could be part of the reason for any insider threat that could
cause severe damage to a company’s electronic security system. The findings of
HernandezCastro et al. and Parn and Edwards included an explanation for the under-application
of the security tools used by companies. The study explained how organizations could mitigate
insider threats, reduce the impact of such threats, and understand the need for high-value
categories of information to trace through intelligent data. The insider threat risk influences
security revisions to protect sensitive information and an organization’s livelihood.
When incorporating trust in technology, businesses used strategic methods to initiate
managers’ and employees’ confidence in monitoring or surveillance of the respective work and
workers. Exploration of the Expectation Disconfirmation Theory (EDT) recommends
comprehending the strategic implications of technology usage and gaining insights into
managerial practices' influence on employee behaviors. Technology and the alignment of
expectations with those of employers significantly affect employees' intentions toward
trustworthy behavior, mediated by their satisfaction, performance, and disconfirmation
experiences (Alhayani et al., 2021; Parn & Edwards, 2019). They are implementing EDT through
a company’s management system of developing projects that provide implementation strategies
with technology trust-building processes to affect usage intent from employees
(Hernandez-Castro et al., 2020; Parn & Edwards, 2019).
Using trust-building methods from employer to team member gave an understanding that
such intent for trust is critical in the EDT process and in preventing technology or information
theft. The demonstration of benevolence via human actions for the best interest of the party with
which the first party works on the emotional interplay that only occurs through human

interactions (Hernandez-Castro et al., 2020). Emotions were not part of technology; they were
only part of those using technology. By reinforcing employees’ right to privacy, trust intent can
positively influence usage continuance intent, reducing the risk of insider threats such as
information theft, abuse, and disclosure (Hernandez-Castro et al., 2020; Parn & Edwards, 2019).
Cyber threat intelligence (CTI) is an element of cybersecurity strategies that offer
organizations valuable insights into emerging threats and potential vulnerabilities. CTI involves
gathering, analyzing, and sharing information about cyber threats, such as tactics, techniques,
procedures, and signs of compromise. This intelligence comes from monitoring open-source
data, exploring the dark web, analyzing malware, and collaborating with industry peers,
government entities, and cybersecurity vendors (Kayode-Ajala, 2023). Using CTI, organizations
can proactively evaluate cyber risks, prioritize security measures, and bolster their cybersecurity
defense. CTI helps organizations predict and address threats before they become security
breaches by reducing the chances of data breaches, financial harm, or damage to reputation (Sun
et al., 2023).
Moreover, CTI plays a role in responding to incidents by furnishing information to aid in
detecting and handling cyberattacks efficiently. By harnessing cyber threat intelligence
capabilities, organizations can outsmart cyber adversaries and safeguard their assets,
infrastructure, and sensitive data more effectively. In summary, with the continuous evolution of
cyber threats becoming complex and sophisticated, organizations face significant challenges in
protecting their data and systems. Conventional security methods often fall short in the face of
cyber threats, leaving organizations susceptible to potential attacks at any given time. Companies
must implement security strategies incorporating access control measures, proactive software
upkeep, and dynamic defense mechanisms to reduce risks effectively. Recognizing threats and
establishing trust-building initiatives within organizations are essential to strengthening

cybersecurity resilience. Additionally, cyber threat intelligence (CTI) plays a role in
cybersecurity strategies by providing valuable insights into emerging threats, enabling
organizations to anticipate, identify, and respond to cyberattacks more efficiently (Kayode-Ajala,
2023). By adopting security practices that foster a culture of cybersecurity awareness and
utilizing advanced technologies such as CTI, organizations can bolster their defenses against
cyber threats and protect their critical assets amidst today's digital landscape.
Legalities with Cyber Security
Government interference in the cyber world has created a new element of concern for
many U.S. private citizens and U.S. legislators. The government wants to protect its society.
Organizational leaders need to recognize the specific issues of cyber operations that have much
to do with cyber theft far beyond privacy concerns, owing to the responsibility of cybersecurity
professionals to ensure data safety (Malgieri, 2020). Applying the cyber protection law is part of
Homeland Security’s defenses. The government’s legal channels define cyber operations as using
computers to disrupt, deny, degrade, or destroy information resident in computers and computer
networks or the computers and networks themselves (Kilani, 2020). Cyber operations can be a
form of advanced force operations that prepare the objective for the main assault. Cyber
operations secure illegal access within crucial security systems, networks, and mapping network
systems (Muzhanova et al., 2021). Acquisition of information or intelligence with any possible
military application is a cyber-operation, albeit illegal. With the occurrence of given cyber access
based upon the above definition, the law of war suggested that these actions are punishable
through the U.S. government’s legal standings.
There are specific challenges that pertain to the use of technology for cyberattacks. The
evolution of cybercrime and theft through technology has introduced new legal issues that
present their challenges. These challenges stemmed from legality issues in collecting proof for

offenders acting against the United States in cyberterrorism (Harviainen et al., 2023). Critics
claim that gathering information through illegal Internet access into a government military
installation constitutes a criminal act. However, proving such action would likely require access
to a personal or private computer, which may prove difficult (Harviainen et al., 2023). Homeland
Security implemented specific defenses against cyber intrusion, cyber terrorism, and the
possibility of cyber war through legal channels. However, issues fall beyond insider intrusion or
inadequate security of information kept through electronic resources (Choi et al., 2021). Such
issues pertain to the differences in laws between nations and countries, which governments may
find problematic. According to Choi et al. (2021), the perspective on workplace practices for
monitoring usage and the legislation for privacy was comparatively different. It often caused
severe and significant issues for actionable recourse in case of invasion of private information.
The study also explained that the loss of the Fourth Amendment right for U.S. citizens when
dealing with a privacy breach on the European end of a given company was often argued and
caused much inconsistency in managing the legalities of security or rights to privacy (Harrell,
2019).
Gunduz and Das (2020) observed that despite the common assumption that a viable
solution would be unattainable without a global privacy protection policy, the U.S. Department
of Defense proactively implemented protective measures. These measures, grounded in legal
authority, reinforced defensive strategies, including data encryption and formulating security
policies. For the past ten years, Homeland Security has produced and implemented specific
techniques to protect legal systems to protect federal and state data. These strategic goals
included building and maintaining ready forces and capabilities to conduct cyberspace
operations, defend any information network and its respective data, and mitigate any risks to
Homeland Security and its missions (Gunduz & Das, 2020). The overriding purpose was to

build, implement, and maintain viable cyber options with plans to use such opportunities to
control a conflict and the potential escalation of a conflict that consisted of cyber threats. The
measures were also intended to work with international alliances, partnering to deter shared
incidences of terroristic and war-like threats, thereby increasing global security and stability
(Bécue et al., 2021; Gunduz & Das, 2020).
The interaction between government involvement and cybersecurity presents challenges
in today’s world. In the efforts to safeguard societies from cyber dangers, the enforcement of
cyber protection regulations is crucial (Malgieri, 2020). Homeland Security plays a role in
combating cyber intrusions and terrorism by using frameworks to define and tackle cyber
activities (Kilani, 2020). Moreover, different laws across nations complicate issues, invoking
worries about privacy rights and legal remedies (Choi et al., 2021; Harrell, 2019). Despite these
challenging initiatives, organizations like the U.S. Department of Defense and Homeland
Security strive to strengthen cybersecurity through planning, preparedness, and global
collaboration. These endeavors aim to improve security and reduce the risks associated with
cyber threats, ultimately promoting stability and resilience (Bécue et al., 2021; Gunduz & Das,
2020). In this changing landscape, governments, cybersecurity experts, and global allies must
work together to tackle the evolving challenges of cyber threats and safeguard a stable digital
tomorrow.
Financial Challenges to the Protection of Data
Companies and financial organizations are categorized as small, medium, and significant.
The existing difference in each category is the level at which each company operates. Small
financial organizations often work within a small regional space and with a small number of
finances. Most large companies operate globally and develop the landscape and strategies they
run on (Alkhalil et al., 2021). Many organizations search for less expensive methods to establish

security if they lack the finances to acquire efficient tools, software, and hardware to protect
secure data and finances (Hamoud & Aimeur, 2020). Most efficiently developed security
systems, such as Microsoft security products, antiviruses, and anti-phishing software, are costly
to acquire (Van der Ham, 2021). These products require monthly fees and lengthy and expensive
subscriptions. Therefore, the financial demands of many companies’ developed security
strategies minimize the acquisitions of their services to only significant companies worldwide.
Small and medium companies often remain unprotected, attracting hackers and cyber
attackers (Alkhalil et al., 2021; Van der Ham, 2021). These companies depend on unreliable
primary measures amid the enhanced technological practices that make it easy to attack these
financial organizations. A company’s security strategy requires many elements, including
employees and assets (Herath et al., 2018). Hamoud and Aimeur (2020) and Herath et al. (2018)
suggested training employees on the primary ways of detecting and responding to data breaches
within an organization. Major companies have developed security sectors that are usually
concerned with data protection, even if the employees within the company know of the breach
(Seh et al., 2020). These departments ensure that the entire company’s data is decentralized so
that no single attack can significantly impact the company’s other data. The departments ensure
an enhanced security structure that incorporates the employees while maintaining the
departments’ separate roles (Herath et al., 2018). Small companies establish such a high or
developed structure of security and protection within the company. These small-sized companies
remain the target of hackers and cybersecurity attacks that easily infiltrate their weak security
systems due to their inability to install sophisticated protection mechanisms.
The nature of transactions between big and small organizations provides a loophole in
which most minor financial organizations become a target of attackers. The study noted that
transactions were often different between small and big companies. While significant companies

operate on closed, non-wired transactions, many small and medium-sized companies operate on
open-end transactions (Voas et al., 2022). The nature of these two transactions defines the degree
of threats or risk of interference between them. Closed transactions are secure because of
irreversible codes that are impervious to hacking. Bitcoin transactions are the safest because
hackers cannot reverse their transactional regulations, thus maintaining a high-security discipline
across all their dealings.
Attacks are imminent for open-end transactions within small and medium companies, and
many security measures cannot be helpful based on the nature of the transactions. (Dupont, 2019;
Voas et al., 2022). This lack of protection leaves the companies more targeted. Further
examination of new financial ecosystems revealed a broad range of options available to small
and medium-sized businesses in the financial sector, focusing on the impact of transparent, open
banking on industry cybersecurity. Voas et al. (2022) noted that open banking was believed to
facilitate entry for new financial service providers into the business sector while highlighting
numerous security and privacy challenges. The disparity in resources and capabilities among
small, medium, and significant financial organizations underscores the challenges in securing
sensitive data and finances. While significant companies can afford sophisticated security
measures and dedicated departments to protect against cyber threats, small and medium-sized
enterprises often lack the financial means to acquire robust security systems (Alkhalil et al.,
2021; Van der Ham, 2021). Consequently, they relied on less reliable primary measures and were
more vulnerable to cyberattacks (Hamoud & Aimeur, 2020). Training employees on detecting
and responding to breaches is crucial for all organizations, but significant companies typically
have more developed security sectors to handle data protection (Herath et al., 2018; Seh et al.,
2020).

The nature of transactions further exacerbates the security challenges for smaller entities,
with open-end transactions posing more significant risks than closed transactions (Voas et al.,
2022). Despite efforts to address these challenges, such as exploring new financial ecosystems
like open banking, cybersecurity in the financial sector remains a pressing issue that requires
ongoing attention and innovative solutions (Dupont, 2019; Voas et al., 2022). As the digital
landscape continues to evolve, bridging the security gap between different-sized financial
organizations is essential to safeguarding against cyber threats and ensuring the integrity of
financial systems worldwide.
Cybersecurity Defense Model to Implement Adequate Policies in Financial Organizations
The Center for Internet Security has developed at least 170 strategies for mitigation,
referred to as the defense models. The models intended to safeguard, organize, and coordinate
the activities within a company. The security community has always cooperated to update the
defense system to meet the contemporary challenges raised within cyberspace (Kuzior et al.,
2022). The challenge lies within most companies that need to prioritize implementing each
respective strategy, which exposes their vulnerability to hackers. The Center for Internet Security
categorized three fundamental implementation strategies: confidentiality, integrity, availability,
and basic cyber hygiene (Richardson et al., 2020). Most companies adopt the CIS defense model,
which protects every company’s activity.
Financial Organizations use outdated processes and data protection strategies that
partially apply patches to protect the entire data. For financial organizations, all-around
monitoring of the organizations’ threats is fundamental because many of these threats can go
undetected (Usman et al., 2023). IT companies worldwide have worked together to develop
solutions to protect organizations' cyber information and services (Kuzior et al., 2022). Although
the speculative nature of data breaches in the future is slippery, most attackers would try to cover

up their intrusion to be persistent in the future. Initially, they would steal identity credentials
before launching an attack using a more developed and advanced mechanism (Van der Ham,
2021). The risk of data exposure grows immensely after the attack because it launches into other
parts or devices within a company. The attackers would create a back to remove or steal data
from targeted organizations slowly ions.
Adhering to adequate policies, many financial organizations and other organizations may
successfully safeguard their companies' data and finances (Pollini et al., 2022). Most of these
organizations attempt to counter many challenges through cybersecurity measures. Among these
measures were the ever-growing technological demands, lack of efficient and modern data
protection methods, lack of company policies and developed security strategies to detect and
respond to cybersecurity breaches, and lack of skilled employees knowledgeable on data security
and finances (Dash & Ansari, 2022). Creating adequate cybersecurity policies for financial
organizations is crucial to protecting sensitive financial data and maintaining the trust of clients
and stakeholders. Several key components were included in cybersecurity policies for financial
organizations:-
1. Risk Assessment and Management - Conduct a comprehensive risk assessment to
identify potential threats and vulnerabilities of an organization. Develop strategies to
mitigate these risks and regularly update them.
2. Data Classification - Classify data based on its sensitivity and importance. Ensure that
stricter security measures are in place for susceptible financial data.
3. Access Control - Implement robust access controls, including role-based access, strong
authentication mechanisms, and the principle of least privilege (granting users only the
minimum access required for their role).

4. Security Awareness Training—Provide cybersecurity training and awareness programs to
ensure employees know best practices and potential threats.
5. Incident Response Plan - Develop a detailed incident response plan outlining the steps to
take in case of a security breach. Test this plan regularly through simulated exercises.
6. Encryption - Use encryption for data in transit and at rest to protect sensitive financial
information from unauthorized access.
7. Patch Management - Keep all software and systems updated with the latest security
patches to address known vulnerabilities.
8. Network Security - Implement firewalls, intrusion detection/prevention systems, and
network segmentation to protect against external threats.
9. Vendor Management - Assess the cybersecurity practices of third-party vendors with
access to data and ensure they meet security standards.
10. Regular Audits and Monitoring - Conduct regular security audits and monitoring to
identify and respond to security incidents in real time.
11. Compliance - Ensure compliance with industry-specific regulations and standards such as
the Payment Card Industry Data Security Standard (PCI DSS) and GDPR (General et
al.).
12. Data Backup and Recovery - Conducting regular backups of financial data and
establishing a comprehensive data recovery strategy is imperative, thereby mitigating
downtime during cybersecurity incidents.
13. Mobile Device Management (MDM) - Implement MDM solutions to secure mobile
devices used by employees and enforce security policies on them
14. Team Member Exit Procedures - Establish clear procedures for revoking access to
systems and data when employees leave the organization.

15. Regular Security Testing - Conduct penetration testing and vulnerability assessments to
identify weaknesses in systems and applications.
16. Security Governance - Establish clear lines of responsibility for cybersecurity within the
organization, including appointing a Chief Information Security Officer (CISO) if
feasible.
17. User Behavior Analytics - Implement tools and techniques to monitor user behavior and
detect unusual or suspicious activities.
18. Secure Software Development - If an organization develops software, incorporate
security into the development process with secure coding practices and regular code
reviews.
19. Physical Security - Restrict and monitor physical access to data centers and sensitive
areas.
20. Continual Improvement - Cybersecurity is an evolving field. Regularly review and
update policies and practices to adapt to new threats and technologies (Dash & Ansari,
2022; Pollini et al., 2022).
The cybersecurity landscape for financial organizations continues to evolve with the ever-
increasing sophistication of cyber threats. The Center for Internet Security has provided essential
defense models and strategies to safeguard organizations against these threats, emphasizing the
importance of implementing fundamental cybersecurity measures such as confidentiality,
integrity, and availability (Richardson et al., 2020). However, many financial organizations must
rely on outdated processes and partial data protection strategies, leaving them vulnerable to
cyberattacks (Usman et al., 2023). Collaborative efforts among IT companies globally have
aimed to develop solutions to protect organizations' cyber information and services

(Kuzior et al., 2022). Nevertheless, the speculative nature of future data breaches poses
challenges, with attackers likely to persistently employ advanced techniques and cover their
tracks to target organizations (Van der Ham, 2021).
Financial organizations must prioritize implementing robust cybersecurity policies to
address these challenges. Critical components of such policies include comprehensive risk
assessment and management, data classification, access control, security awareness training,
incident response planning, encryption, patch management, network security, vendor
management, regular audits and monitoring, compliance with industry regulations, data backup
and recovery, mobile device management, team member exit procedures, security testing,
security governance, user behavior analytics, secure software development, physical security,
and continual improvement (Dash & Ansari, 2022; Pollini et al., 2022). By integrating these
components into their cybersecurity policies, financial organizations can better protect sensitive
financial data, maintain the trust of clients and stakeholders, and mitigate the risks posed by
cyber threats. However, organizations must remain vigilant, adapt to emerging threats, and
continuously update their cybersecurity practices to stay ahead of cybercriminals in today's
dynamic and evolving threat landscape.
Human Factors in Cybersecurity
Human factors in cybersecurity include human behavior, cognition, and emotions that
impact data information systems and data security. These factors serve as potential vulnerabilities
and sources of resilience in cybersecurity, depending on how individuals perceive, assess, and
respond to cyber threats (Kadena & Gupi, 2021; Zhang & Ghorbani, 2020). The human factor in
cybersecurity within organizations influences the effectiveness of any measures taken, the
likelihood that attacks can be successful, and the overall resilience of the organization’s security
posture (Pollini et al., 2022) while advances made in developing cyber security systems to

protect organizations from outside threats, the human factor is often the most detrimental. It
leads to the system’s complete failure (Grobler et al., 2021). Understanding human factors
becomes crucial in examining the implementation of robust security policies and their role in
safeguarding sensitive information within financial organizations from insider threats. Exploring
the perceptions and behaviors of cybersecurity professionals concerning cyber threats and
security policies can enhance financial organizations' protection against cybersecurity risks and
ensure adherence to established protocols.
Addressing cybersecurity demands a holistic approach that encompasses both
technological solutions and consideration of the human element assertion is underscored by the
findings of Jeong et al. (2019), who conducted a systematic literature review illuminating human
factors' nuanced and multifaceted role in cybersecurity. Their study unveiled a conspicuous
disparity, revealing a predominant emphasis on technological aspects at the expense of
understanding the profound influence exerted by human factors on cybersecurity. The research
by Jeong et al. (2019) underscores several critical shortcomings in current cybersecurity
paradigms. Firstly, there is a lack of concerted effort in consolidating the diverse array of human
factor attributes relevant to cybersecurity. This fragmentation impedes a comprehensive
understanding of the intricate interplay between human behavior and cybersecurity outcomes.
The absence of robust theoretical frameworks further exacerbates this issue, hindering the
development of cohesive strategies to integrate human-centric approaches into cybersecurity
protocols. Jeong et al. (2019) highlighted a need for qualitative studies exploring human factors
in cybersecurity. While qualitative methodologies were employed, more theoretical
underpinnings were needed to guide these investigations. This deficiency undermines the depth
and rigor of qualitative analyses, ultimately impeding the advancement of knowledge in this
crucial area. Contrary to some aspects of Jeong et al.'s findings, Rahman et al. (2021) conducted

a subsequent literature review that nuanced human-centric cybersecurity paradigms' discourse.
Their study revealed a predominant reliance on qualitative methodologies among computer
science scholars investigating human factors in cybersecurity. However, Rahman et al. (2021)
also identified limitations in the existing body of research, including a notable bias towards the
Western community in sample selection, which diminishes the generalizability of findings and
underscores the need for more diverse representation in cybersecurity research.
Moreover, Rahman et al. (2021) highlighted a critical gap in the availability of
standardized security-specific scales for measuring user cybersecurity perceptions. This deficit
impedes efforts to accurately gauge user perceptions and attitudes towards cybersecurity
measures, hampering the development of targeted interventions to enhance cyber resilience. The
insights gleaned from both Jeong et al. (2019) and Rahman et al. (2021) underscore the
imperative of integrating human factors into cybersecurity strategies. Achieving a robust
cybersecurity posture necessitates technological fortifications and a nuanced understanding of
human behavior and perceptions in the digital realm. Addressing these gaps demanded
interdisciplinary collaboration, theoretical rigor, and methodological innovation to usher in a
more holistic and practical approach to cybersecurity.
Various human factors, such as user awareness, training programs, decision-making
processes, behavioral aspects, and insider threats, contribute to the complexity and dynamism of
cybersecurity. User awareness encompasses how users perceive and respond to cyber threats,
influencing the probability and severity of security incidents. Negligent behavior by employees
can have detrimental effects on the organizations and increase the vulnerability to cyberattacks.
Effective education and awareness programs that account for user characteristics, context, and
threat type can augment user awareness (Rohan et al., 2021). The level of security awareness
training employees engage in can significantly influence the organization’s security posture.

Training programs are another means to enhance user awareness and cybersecurity measures by
imparting knowledge, skills, and attitudes toward cybersecurity to users. However, training
programs required customization to the target audience, current cyber threats, and best practices,
as well as addressing the challenges of user motivation and retention. (Hatzivasilis et al., 2020).
Decision-making processes influenced how users behaved and reacted to cyber threats,
often falling prey to human errors and cognitive biases like overconfidence, complacency, or
confirmation bias. These biases and error mistakes can result in security breaches, necessitating
effective security policies and interventions that comprehend the psychological factors that mold
decision-making processes (Johnson et al., 2021). Even though there has been an increase in the
focus on the role of individual behaviors in cyber security, there is still limited information on
how individuals differ in their awareness, knowledge, and cyber security behaviors when
confronted with a risk (Zwilling et al., 2022). Behavioral aspects denote how users comply or
deviate from security protocols and policies shaped by user personality, motivation, trust, and
convenience. Behavioral aspects demand monitoring and measurement, and feedback and
incentives demand provision to motivate and reinforce desirable security behaviors. A balance
between security and usability demands attainment, as too much or too little security can have
adverse consequences (Moustafa et al., 2021).
Time constraints, including cybersecurity, are essential in shaping people's behavior and
decision-making. Chowdhury et al. (2020) have emphasized the influence of time constraints on
the cybersecurity practices of both users and employees in environments. The rapid growth of
information and communication technologies (ICT) and the constant stream of interruptions
during the workday add to the pressure felt by employees. In today’s fast-paced world,
employees often deal with tight deadlines, constant alerts, and conflicting priorities, all
contributing to a sense of urgency. In these circumstances, individuals may prioritize completing

tasks quickly over following security protocols, inadvertently risking their organization's
cybersecurity (Chowdhury et al., 2020). Time pressure weakens the defense mechanisms within
organizations, making it harder for users to address security threats effectively and comply with
security measures. Sometimes, when individuals are under time constraints, their abilities can be
overwhelmed, leading to decision exhaustion, making it harder for them to evaluate risks
accurately and make sound cybersecurity choices. Employees might opt for insecure shortcuts to
meet deadlines or simplify workflow procedures while ignoring security protocols altogether,
making the organization vulnerable to security risk.
In their research, Hong and Furnell (2021) explored how college students develop habits
related to cybersecurity behavior, revealing the factors that impact how people approach
cybersecurity practices. They found a relationship between self-belief, understanding of
behaviors, and actual cybersecurity habits, highlighting the importance of individuals' confidence
in influencing their approach to security. The study showed that those who feel capable of
handling cybersecurity tasks were more inclined to take security measures, demonstrating the
empowering effect of self-confidence on safety practices. Hong and Furnell’s (2021) work
proved that cybersecurity habits were not inherent qualities but skills that can be learned and
honed over time. The research also stressed the role of support systems in shaping people's
cybersecurity behaviors, emphasizing how organizational support can promote a culture of cyber
awareness. Hong and Furnell (2021) recommended that organizations provide resources and
assistance, including access to cybersecurity experts who can offer guidance and support to
employees. By ensuring staff members can contact specialists for help with their cybersecurity
concerns and receive advice on handling security matters, companies can enable their employees
to make informed decisions and strengthen their security stance.

Several studies, like the one by Hong and Furnell (2021), have explored the connection
between behavior and cybersecurity. They have uncovered a range of factors that influence how
individuals approach cybersecurity, such as socio-demographics, perceptions of cybersecurity,
and patterns of IT usage. Kovačević et al. (2020) analyzed these determinants, highlighting
knowledge as a driver of cybersecurity awareness among people. To emphasize the importance
of education and awareness programs in helping individuals grasp cybersecurity risks and adopt
practices. Kovačević et al. (2020) delved deeper into this topic by examining how employees'
views, understanding, and knowledge of cybersecurity in settings were interconnected. Their
study emphasized the influence of culture and procedures on shaping employees' attitudes and
actions toward cybersecurity. Specifically, they observed employees' perceptions and awareness
regarding cybersecurity based on their familiarity with security protocols and their grasp of how
cybersecurity is implemented and prioritized within the company. This gap underscored the
importance of cultivating an organizational culture prioritizing cybersecurity awareness, where
security measures were communicated clearly, reinforced, and easily integrated into operations.
By synthesizing insights from the studies by Kovačević et al. (2020), a comprehensive
understanding of the human factors that influence cybersecurity behavior emerges. From the
critical role of knowledge and awareness in driving cybersecurity practices to the influence of
organizational culture and practices on employee attitudes, these studies underscore the complex
nature of cybersecurity behavior and the need for holistic approaches to cybersecurity education,
training, and organizational support.
Preventing social engineering attacks in organizations is a concern in today’s
cybersecurity discussions. A recent study by Momoh et al. (2023) explored the relationship
between human factors and cybersecurity in financial organizations, focusing on strategies to
detect and counter social manipulation threats. Their thorough examination highlighted how

human behavior shapes cybersecurity dynamics in finance and offers insights into risk mitigation
strategies. The research by Momoh et al. (2023) indicated several ways human actions impact
cybersecurity outcomes within settings. By uncovering patterns and vulnerabilities exploited by
manipulators, the study emphasized the need to understand human behavior when creating robust
defense mechanisms.
The results also emphasized incorporating people-centered approaches in cybersecurity
frameworks within firms to enhance resilience against social engineering threats. In addition, the
research provided suggestions to improve the detection and prevention of social engineering in
financial organizations. These suggestions involve strategies such as implementing layers of
authentication using strong email filters to detect and isolate suspicious messages, employing
intrusion detection systems to monitor and proactively address abnormal activities, and
conducting thorough training programs to educate employees and promote a security-conscious
environment. Financial organizations can strengthen their defenses against social engineering
attacks by combining solutions with human-focused approaches. Effectively reduce associated
risks. The findings from Momoh et al.’s (2023) study highlighted the significance of
understanding behavior in cybersecurity and stressed the need for steps to protect valuable
financial information. Financial firms could have enhanced their cybersecurity stance and
maintained trustworthiness in the digital domain by adopting an approach that considered
weaknesses and human elements.
Insider Threats
Insider threats are the intentional or unintentional actions of authorized users that
jeopardize an organization's security, and they are one of the most severe and prevalent
cybersecurity risks. An insider, as defined by Prabhu and Thompson (2022), encompasses
individuals who hold current or former roles as employees or contractors within an organization,

potentially retaining access to its data even after their official tenure concludes. The spectrum of
insider threats is multifaceted, comprising deliberate acts of fraud, subversive IT sabotage, and
inadvertent breaches stemming from employees' lack of malicious intent. Prabhu and Thompson
(2022) delineate distinct categories within insider threats, including malicious, mischievous,
negligent, and accidental. Malicious threats, as outlined by CERT (2018), entail deliberate
actions aimed at causing harm or heightening the organization's vulnerability driven by evil
intent. Such insiders harbor motives to inflict damage and consciously elect to pursue detrimental
courses of action. In contrast, mischievous threats transpire when employees exploit their
privileges intentionally, albeit without harboring malicious intent. This category of insider threat
often emerges as particularly pervasive, as individuals possess an awareness of security protocols
yet fail to adhere to established procedures (Prabhu & Thompson, 2022).
Negligent insiders represent a distinct category within insider threats, characterized by
their deliberate disregard for information security measures, albeit without harboring any
malicious intent or motive. Unlike malicious or mischievous insiders, negligent individuals do
not actively misuse their privileges; instead, they overlook or bypass organizational security
policies based on the perception that their actions pose minimal risk (Prabhu & Thompson,
2022). This insider threat is rooted in a lax attitude towards security protocols, often stemming
from believing their actions do not lead to adverse consequences. Conversely, accidental insiders
constitute another facet of insider threats, distinguished by their lack of malicious motives or
deliberate intent to breach security protocols. These individuals inadvertently engage in actions
that compromise security without any conscious decision to deviate from prescribed policies.
Unlike negligent insiders, accidental insiders neither actively ignore security measures nor
intentionally circumvent them; instead, their actions by oversight or lack of awareness regarding
the potential repercussions (Prabhu & Thompson, 2022). Despite lacking malicious intent, the

actions of accidental insiders can still result in significant security breaches and pose substantial
risks to organizational integrity and data confidentiality.
Insider threats demand prevention and detection, and appropriate responses and sanctions
demand implementation to deter and mitigate them. A global report conducted in 2020
highlighted that, on average, the global cost of insider threats rose by 31% in the previous two
years to $11.45 million (Saxena et al., 2020). The motives, behaviors, and warning signs of
insiders who may pose security risks demand understanding, such as disgruntlement, greed, or
negligence (Tsiostas et al., 2020). Harms et al. (2022) explored how personality traits influence
individuals’ likelihood to participate in insider threats within organizations. The study discussed
the importance of dark personality characteristics in determining behaviors and outcomes across
different areas. These traits were widely studied for their connection to workplace behaviors,
interpersonal relationships, and organizational results (Saxena et al., 2020). The research
highlighted the significance of these traits in comprehensively understanding insider
cybersecurity threats. Investigators can understand the factors behind insider threats by exploring
how these personality aspects interact with individuals’ motivations, attitudes, and actions in
cybersecurity settings. Harms et al. (2022) proposed that recognizing the role of dark personality
traits in influencing insider threat behaviors can lead to efficient prevention and mitigation
strategies.
Organizations invest heavily in strengthening their networks to deter outside malicious
attacks but often fail to deploy adequate protection against potential insider threats by malicious
insiders (Saxena et al., 2020). Human factors are pivotal to the success or failure of
cybersecurity, and they demand constant assessment and improvement through various methods
and strategies. To effectively mitigate insider threats, it is crucial to understand the motives and
goals of these attacks. Cybersecurity experts have categorized four types of insider threats in the

literature based on the motives and goals behind the attacks. These classifications cover insider
fraud, infrastructure sabotage, intellectual property (IP) theft, and unintentional breaches. Insider
fraud stands out as a form of insider threat acknowledged by companies as existing within their
organizational structures (Saxena et al., 2020). This type of threat involves insiders taking actions
to gain personally or undermine the organization's systems and processes. Infrastructure sabotage
is another category of insider threat often carried out by individuals with specific skills in roles
within the company. Saboteurs use their expertise to deploy software or other disruptive methods
to disrupt the organization's information systems and operations. Such attacks can cause damage
to infrastructure, resulting in service interruptions, data breaches, and financial harm.
Theft of property (IP) concerns companies where insiders illegally obtain and misuse
important proprietary information for personal benefit or to gain a competitive edge. This kind of
insider threat risks the organization's ability to innovate, compete, and maintain its position in the
market, as stolen IP addresses can be used by rivals or sold on markets. (Prabhu & Thompson,
2022). Unintentional insider threats involve actions taken by former employees without intent,
but they inadvertently cause harm to the organization’s resources or assets. These individuals
may unknowingly compromise security measures, mishandle sensitive data, or fall prey to social
manipulation tactics such as phishing attacks and other social engineering attacks, resulting in
outcomes like data breaches, system failures, or breaches of regulations (Prabhu & Thompson,
2022). Even though they do not have malicious intentions, the combined impact of insider threats
can be significant, underscoring the need for thorough security training and robust risk
management strategies in organizations.
Summary
The current emergence of technology in the workplace has created new and unique
problems for information security within multiple industries (Burnes et al., 2020; Harrell, 2019).

Companies and organizations today must invest large amounts of funds into security measures to
keep electronic information safe. With continual technological advances, the constant need for
increased security measures amounts to more money output. This output can create issues for
organizations that need the necessary finances. This new age of technological security systems
has come with separate and more formidable matters, and it has caused a new generation of
policies, legalities, and laws to be necessary (Harviainen et al., 2023; Ho & Luong, 2022;
Maimon & Louderback, 2019). Due to the technology used in most workplaces, there is an
everincreasing public question of who monitors whom in this new age of technological miasma.
From blurred boundaries of legal content and electronic records to employees’ privacy rights,
many cybersecurity experts recognized the distinct issues created by the advent of technology.
Organizational leaders recognized that models designed to prevent cyber threats in
organizations must be used to train their workers to avoid cybercrimes (Kadena & Gupi, 2021;
Zhang & Ghorbani, 2020). Cybersecurity experts recommended constant software updates to
obtain the latest and best security prevention. Before developing countermeasures, financial
organizations would have experienced massive data breaches and economic losses. The
challenge of achieving data security requires substantial financial investments, which means
smaller and medium financial organizations can continue to be affected by this challenge
(Alkhalil et al., 2021; Van der Ham, 2021). Organizations should continue to seek ways to
mitigate threats to fight against organizational data breaches and finances. Most companies
continue implementing measures to secure their system against violating the abovementioned
standards. Because most targeted companies are small or medium, they face many challenges
that lead to loopholes and cyberspace attacks.
The existing literature relayed concerns within many industries regarding cybersecurity
measures addressed the issues with cost, problems with team member training, and the deep

concern of privacy within data security (Herath et al., 2018; Walaza et al., 2020). Many studies
were focused on corrective measures for cybersecurity protection solutions (Usman et al., 2023).
The research needed to have a distinction in discussing specific industries and a gap in discussing
cybersecurity within the banking and financing industries. Chapter Three detailed the research
methodology, including the research design, participant selection criteria, data collection
methods (interviews, observations, and document analysis), procedures, and data analysis and
interpretation approaches, outlining how the study ensured its credibility and reliability.
Chapter Three
Procedures and Methodology
Introduction
This qualitative exploratory study focused on potential coping mechanisms and whether
financial organizations adequately implement security policies. The study addressed how the
critical constructs of the Technology Threat Avoidance Theory (TTAT) assisted in understanding
the vital aspects of financial organizations’ cybersecurity risks. The study further addressed
protecting financial organizations against cybersecurity risks and ensuring employees' adherence
to cybersecurity protocols. Previous scholarly inquiries have explored the array of preventative
strategies organizations deploy to mitigate the risk of cyberattacks. These strategies encompass
restrictive measures on employee data access, the implementation of firewalls, the establishment
of robust data security policies, and the fortification of wireless access points (Ghelani, 2022).
Chapter Three entailed the method and design selected for this research and how the study

answered the posed research questions. The chapter addressed the sampling and population, the
process for recruiting participants, and the criteria for such selection. The study used Chapter
Three to explain the procedure for data collection and describe the study's tools. The chapter also
highlighted the data analysis process and the means for determining the themes found within the
compiled data. The chapter ended with a discussion of the ethical considerations applied within
all functions of the research design. The study used the TTAT theoretical model.
The problem of the study focused on potential coping mechanisms and whether security
policies were adequately implemented. The study explored how applying the TTAT can help
cybersecurity professional experts understand and mitigate their cybersecurity risks. This
research was carried out by answering two central research questions. The first central research
question was how cybersecurity professionals perceive deviation from their organization’s
cybersecurity policies as a risk to their organization. The second research question was how do
cybersecurity professionals perceive the active support they provide to employees as helping
them cope with and prevent cyber threats? The study presented and discussed the literature
supporting the research problem and the associated theoretical framework. This chapter
addressed the methodology used to carry out the study.
The chapter began with a discussion of the research methodology, namely qualitative
exploratory research. The debate about the nature and appropriateness of the specific qualitative
research design, exploratory study, followed. It also discussed the population and sampling used
in the research and explained the data sources with interview questions. The chapter then
presented the data collection process and analysis. Toward the end, the chapter addressed the
trustworthiness of the research and ethical concerns. Chapter Three ends with a summary of the
key points in the chapter.

Research Method and Paradigmatic Perspective
The study used a qualitative exploratory method. This approach was characterized by its
descriptive and exploratory nature, as Merriam (2020) outlined. A qualitative exploratory
research method comprehensively explored a central phenomenon under investigation (Pollini et
al., 2022). This phenomenon is typically broad and open-ended in nature instead of narrowly
defined. Such open-endedness aligns with the open-ended nature of qualitative inquiry (Merriam,
2020). Open-ended questions were asked in qualitative studies to explore and understand the
experiences and perceptions of the study population (Pollini et al., 2022). Qualitative research is
also subjective, focusing on the experiences and perceptions of those with firsthand experience
vis-à-vis the central phenomenon (Merriam, 2020). A qualitative exploratory study was
contextual, seeking to understand the role of context in the phenomenon by examining that
phenomenon within its context rather than isolating it and studying it in the abstract (Pollini et
al., 2022).
The study focused on identifying potential coping mechanisms and assessing the extent to
which financial organizations adhere to security policies. This descriptive purpose also entailed
exploring critical ideas encoded in the qualitative research questions that focused on asking what
and how. The study was subjective in that it relied heavily on the individual experiences of the
population under investigation. The study also explored all replies within the population because
failing to do so would have led to an incomplete understanding of the strategies used. The
proposed research was contextual in that it is central to understanding how the specific context of
the financial sector influences cybersecurity decisions.
Quantitative analysis is relationship-oriented and numerical (Levitt, 2021). Rather than
exploring a central phenomenon, quantitative research focused on pre-determined and narrowly
defined variables (Levitt, 2021). Not only must the relevant variables be able to take on the

quantified form using existing and well-validated instrumentation, but their hypothesized
relationships must also be suggested by existing theory (Levitt, 2021). In exchange for its
closedended rigidness, the strength of a quantitative approach is that it can yield statistically
significant results by leveraging a large sample size (Levitt, 2021). The utility of those results
may need improvement because achieving them is only possible in a closed-ended context where
data collected from sufficiently large sample sizes is feasible (Levitt, 2021).
The study addressed a broad phenomenon rather than specific, narrowly defined
variables. The study had an exploratory focus, not a relational or numeric. The research questions
were open-ended and exploratory. Such research questions could not adequately be answered
using pre-defined quantitative outcomes, as crucial aspects of the research population’s
perspectives could be missed when using any list of presuppositions. Data collected from a large
sample would be impractical for such a study. With a sufficiently large sample size, the
quantitative methodology offered more. In addition, a mixed methods design combining
qualitative and quantitative approaches could be beneficial, but such a design would be too
resource-intensive to be practical for the present study (McKim, 2017).
Qualitative Exploratory Research Approach
Several specific qualitative research designs exist within qualitative research. The study’s
detailed qualitative research design was exploratory (Merriam, 2020). Though all qualitative
research designs inherit a contextual nature from the overall methodology, the exploratory study
was a primarily contextual approach to research (Boumhand et al., 2023). An exploratory study
focused on specific phenomena to understand essential characteristics more deeply (Merriam,
2020). The study should choose an exploratory topic because it was unusual or considered very
close to average or typical (Boumhand et al., 2023). An exploratory study design leveraged
multiple data sources to obtain a more comprehensive perspective regarding the central

phenomenon (Merriam, 2020). These data sources offer various views and a richer depiction of
the case, the context within which it exists, and the relationship between phenomenon and
context (Boumhand et al., 2023). In this regard, the exploratory study was ideal for exploring
context-dependent phenomena.
Qualitative Exploratory Study
The study considered other qualitative designs for the research but rejected them. A
phenomenological study examined the phenomenon through in-depth interviews with a few
participants and the lived experiences of those participants. A phenomenological design was not
appropriate for this study because, in this research, the focus was on the participants' knowledge
rather than their lived experiences. A grounded theory approach takes the results and builds a
new theory of the subject from the ground up using only those results. Such an approach could
be too extreme for this study, as the existing theory of TTAT provided a solid foundation. The
ethnographic study investigated the experiences of a cohesive ethnic or social group (Muzhanova
et al., 2021). Ethnography was inappropriate for this research because the study does not focus
on any ethnic or cultural group. Narrative inquiry involves an in-depth analysis of participants’
stories (Muzhanova et al., 2021). As with phenomenology, narrative inquiry was inappropriate
because the study focused on participants’ knowledge more than their stories.
The qualitative exploratory study design was the most appropriate of the available
qualitative research designs. The study focused on an exceptional exploratory study, namely, the
financial organization. Relative to the broader economy, the financial industry is online and
attractive to cybercriminals. The case was also contextual because the unique context of the
financial organization makes its cybersecurity practices different from those of other industries
and of particular importance. The exploratory study’s multiple data sources were also relevant to
this study, given the complexity of cybersecurity decision-making and the balance of different

interests and stakeholders. Hence, an exploratory study design was the most appropriate for the
research (Boumhand et al., 2023).
Trustworthiness
Trustworthiness refers to the veracity, genuineness, and reliability of the findings.
Typically, four essential criteria were employed to assess the validity of qualitative research.
They include credibility, transferability, dependability, and confirmability. These four
components correspond to the qualitative constructs of internal validity, external validity,
reliability, and objectivity (Doan et al., 2020). The section below discusses how each element of
trustworthiness was established in this research.
Credibility. Credibility is the internal validity of qualitative exploratory studies. It
focused on how congruent the findings are with reality (Amin et al., 2020). It measured the truth
value of qualitative exploratory research and was concerned with whether the findings were
accurate. The study utilized several strategies to establish credibility. One is member checking,
also known as respondent or participant validation (Doan et al., 2020). After gathering data from
the participants, they returned it to check for accuracy and resonance with their experiences.
Results were also returned to the participants to check for accuracy. This study collected data
through individual structured interviews and pre-interview questionnaires. The data from the two
sources were compared to ascertain areas of agreement and divergence.
The negative exploratory study was the third strategy to establish the study's credibility. It
was a technique for ensuring the validity of the interpretation of qualitative data by analyzing
outlier data (Johnson et al., 2021). The study identified data elements that disconfirmed emergent
findings by conducting a negative exploratory analysis. The study’s negative exploratory analysis
involved finding and discussing data that contradicted the explanations developed from the
research. Any new negative exploratory analysis necessitated refined data analysis, with this
revision proceeding until most of the data captured in the study could be explained. This

procedure helped in refining all the conclusions reached until they accounted for all the known
cases without exception.
Dependability. This component of trustworthiness was used to demonstrate or measure
the reliability and consistency of the results of a given research. It entailed the degree to which
the procedures in a study can be replicated in the same research context to get the same results
(Amin et al., 2020). This study established dependability so that if someone else wanted to
replicate it, they would have adequate information from the research report and obtain findings
like this research. Using interview questions protocols to guide data collection also contributed to
the replicability of the data collection procedures, further strengthening dependability.
Transferability. The second principle component of trustworthiness is transferability.
Transferability is the generalizability of inquiry (Amin et al., 2020). Data is transferable to the
extent that it holds settings and samples except those from which it was derived (Amin et al.,
2020). This study established transferability via the description of the participants, as follows. By
gathering data from participants through individual semi-structured interviews, the study
obtained detailed insights into how effective security policies were implemented to safeguard
their company's sensitive information from insider threats. Chapter Three described the inclusion
criteria to assist readers in assessing the transferability of the findings in this study to different
settings and samples, and all the recruited participants met those criteria. The analyses of the
research questions section of this chapter also described the findings in direct quotes from the
data. Direct quotes were a form of participants’ words that helped the study convey the contexts
and perspectives from which the participants were speaking.
Confirmability. Confirmability ensured that the findings were based on the participants'
responses and were not influenced by the motivations or biases of the investigators (Amin et al.,
2020). This study established credibility through an audit trail, highlighting all steps taken to

justify the decisions made in the data analysis process. The study followed six steps when
analyzing the data, consistent with the thematic analysis process described by Clarke et al.
(2015). The member-checking procedure employed in the study also contributed to
confirmability by allowing the participants to verify that interpretations of the data correctly
reflected their intentions in making their responses and not the investigator's biases.
Role of the Researcher
In this qualitative exploratory study, the researcher was the main instrument that
maintained high integrity during and after the study. To maintain the integrity and transparency
of the research, efforts were made to minimize errors and biases throughout the data collection
and analysis phases. Measures were taken to ensure participant comfort during interviews,
thereby facilitating the sharing of genuine experiences. I also functioned as the primary
instrument for data collection, which entailed direct interaction with participants. The researcher
handled the techniques of recording, documenting, managing the data, note-taking, audio
recording, and transcription. The other role of the study's individual was to analyze the gathered
data. A comprehensive and systematic approach to data analysis, namely, thematic analysis, was
utilized. To facilitate the data analysis process and enhance the transparency and quality of the
results, the qualitative software NVivo was used. Another responsibility was to present the data.
Also, responsible for communicating the study’s findings and implications to pertinent
audiences, including the public, owners of financial companies, and academic peers. The
following section of this chapter addressed the participants and research setting.
Researcher Positionality
Researcher positionality is an essential aspect of a study. The researcher's positionality
refers to the position the researcher has adopted in research and influences how the study and
results were conducted (Holmes, 2020). The study used Semi-structured interviews and

preinterview questionnaires to reduce any potential bias. Another important thing was
understanding how cybersecurity professionals have constructed their identities regarding their
position in their organization. In-depth knowledge of the topic introduced preconceived notions
about deviations from cyber-security policies in organizations and the effectiveness of adequate
policies in protecting a financial company's information.
Reflexivity and Bracketing
Reflexivity in qualitative exploratory studies requires the investigator to explicitly
acknowledge their biases, assumptions, and potential impact on the research. (Holmes, 2020).
Bracketing was when the study attempted to set aside preconceptions and judgments to focus on
the investigated phenomenon. (Holmes, 2020). Reflexivity and bracketing enhance the credibility
and validity of qualitative exploratory research. The study used bracketing to set aside biases and
allow the collected data to be interpreted. A reflexive journal was referred to before and after
each interview to enhance the study's credibility and reduce bias. The reflexive journal was used
to document biases that, during the study, acknowledged them and set them aside to analyze the
data without bias.
Sampling Procedures and Data Collection
This section presented the sampling procedures used to recruit participants. The
discussion also covered the sampling strategy used and how they recruited participants. The
datagathering sources were thoroughly detailed, and the tools devised for data collection were
also addressed. Furthermore, the methods employed to ensure the diversity and
representativeness of the sample were highlighted to provide a comprehensive view of the data
collection process.

Sampling Strategy
In qualitative exploratory studies, the focus extends beyond individual participants to
encompass broader issues, with individuals functioning as embedded units within the context of
interest (Boumhand et al., 2023). The study targeted cybersecurity professionals in financial
organizations, recognizing them as embedded units within this domain. The inclusion criteria
stipulated that participants must be currently employed at a financial organization, possess some
level of involvement in their organization's cybersecurity efforts, have a minimum of one year of
employment to ensure relevant experiences, and be at least 18 years of age.
The study utilized purposive sampling to recruit participants, selecting individuals based
on their ability to effectively address the research questions (Boumhand et al., 2023). Participants
were recruited from various channels such as professional associations, LinkedIn, and other
social media platforms, ensuring a diverse pool with relevant experiences in cybersecurity within
banks. This approach facilitated the selection of participants who could provide valuable insights
into the research questions that guided the study. In determining the sample size, the study
adhered to the guidance provided by Boumhand et al. (2023), who suggested that qualitative
studies typically involve a sample size ranging from five to 25 participants to achieve data
saturation. When new participants ceased contributing novel ideas or information, data saturation
was stopped, which is crucial in qualitative research as it indicates the depth and
comprehensiveness of the collected data.
As Boumhand et al. (2023) outlined, qualitative descriptive studies focused on exploring
issues in-depth or providing additional context to quantitative data. Consequently, a small sample
size was often preferred to facilitate a thorough examination of the phenomenon under
investigation. In this study, 25 participants aligned with the qualitative descriptive approach,
which enabled the study to delve deeply into the experiences and perspectives of cybersecurity

professionals in the financial organization. The study employed purposive sampling to recruit 25
cybersecurity professionals from financial organizations, ensuring they met specific inclusion
criteria. This approach facilitated the attainment of data saturation, a crucial aspect of qualitative
exploratory research, while also aligned with the study's qualitative descriptive nature. Through
this methodology, the study aimed to gain comprehensive insights into cybersecurity practices
and challenges within the financial organization.
Instrument Development
Boumhand et al. (2023) indicated that a qualitative exploratory study must use at least
three data sources. They also suggested that an exploratory study was unique among qualitative
methods in that it may draw upon quantitative interviews as a contextualizing data source. This
study’s data sources were qualitative semi-structured interviews and pre-interview
questionnaires. Qualitative semi-structured interviews are the backbone of qualitative inquiry. A
semi-structured interview was structured in that a preliminary set of questions and critical topics
guided it. An interview guide was developed with careful attention to answering the research
questions. The interview guide for this study is in Appendix E. In addition to being designed with
a thorough eye toward answering the research questions, the dissertation committee reviewed
and validated the interview guide to ensure it was appropriate. At the same time, semistructured
interviews were flexible because the study did not need to strictly adhere to the interview guide
(Kosutic & Pigni, 2022). A critical follow-up or probing questions were included if the
participant had more insight about a particular topic. A participant may also volunteer more
relevant information unprompted.
The data source was interviewed, which was developed following the distribution of the
interviews to be filled out and then collected back the answered interviews as per the
participants' opinions. The interviews aimed to assess the widespread use of the cybersecurity
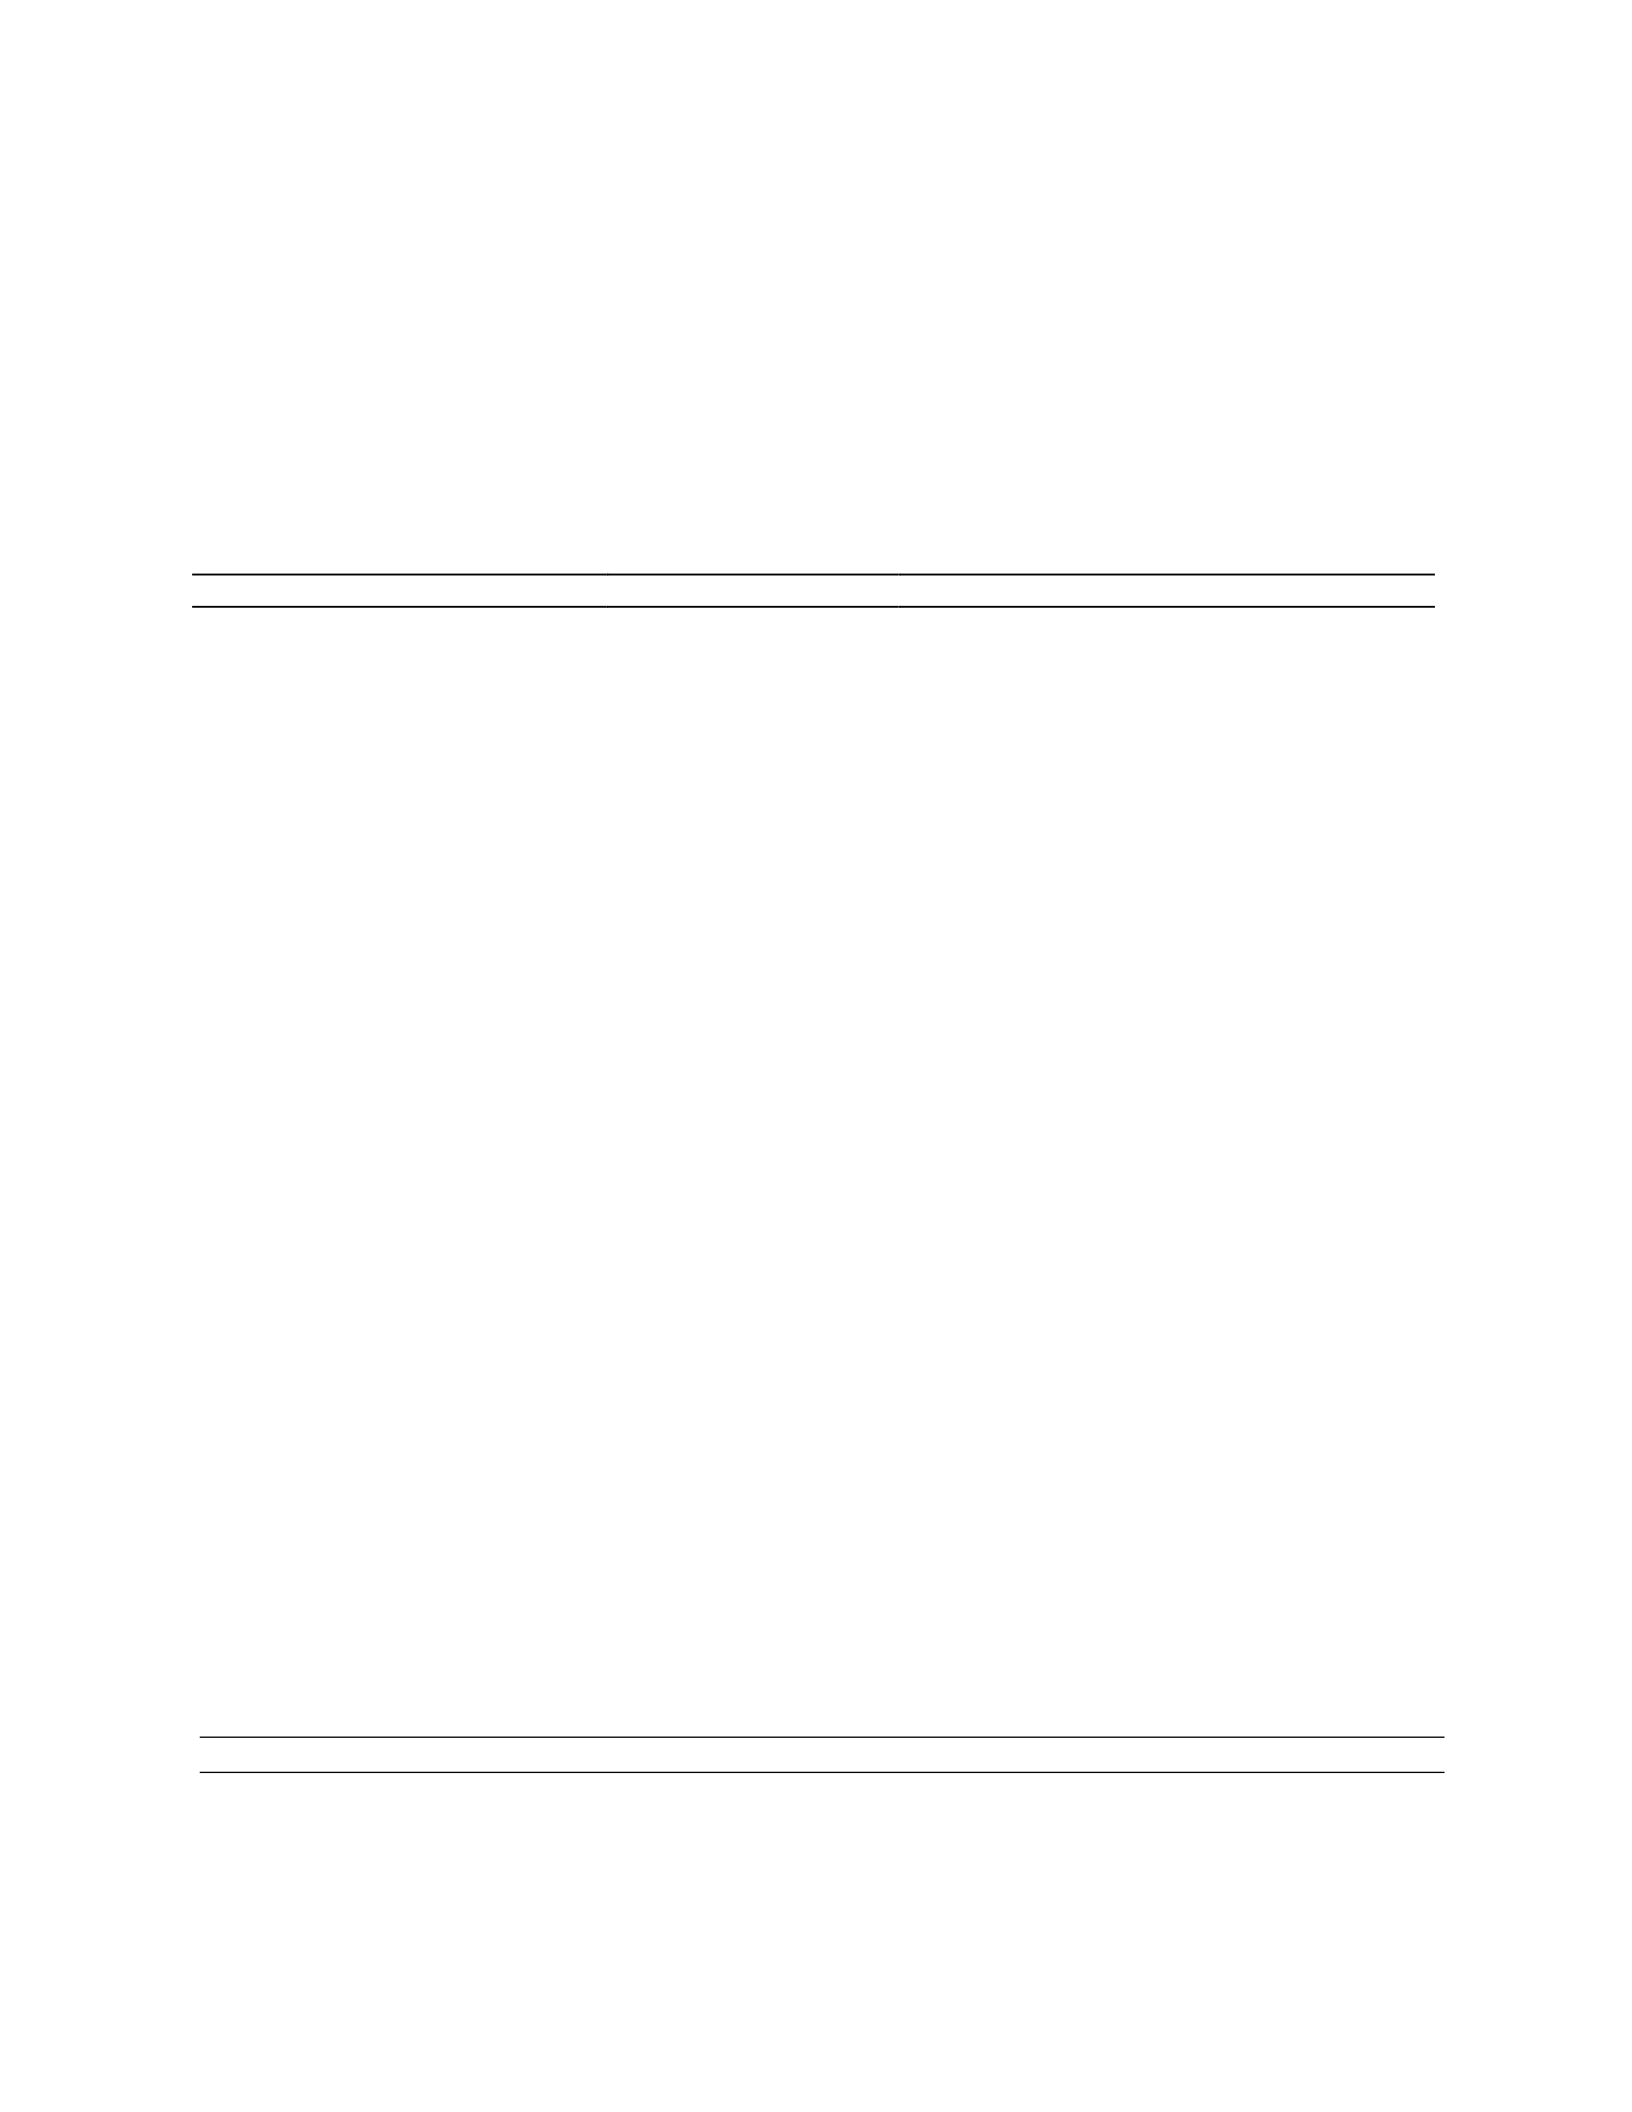
practices highlighted within them. The interviews included open-ended items. The participants
utilized the open-ended items to identify any further cybersecurity practices at their organization
that should have been included in the list of techniques and strategies compiled based on the
results of the interviews.
Table 2
Mapping of Interview Questions to Research Questions and Existing Literature
Q6: How do cybersecurity professionals assess the potential
response to cybersecurity challenges.
RQ1 Herath et al. (2018) highlighted the crucial role
of employees in maintaining cybersecurity
within an organization.
Interview Question Research Question Literature Base
risks of employees deviating from
cybersecurity policies?
Q7: What is your perception of
cybersecurity professionals'
RQ2 Studies by Choi et al. (2021) emphasized the
importance of team member participation in
cybersecurity coping appraisals.
Interview Question Research Question Literature Base
Q1: What is your perception as a
team member working in a
financial company regarding the
importance of participation in
cybersecurity threat appraisals
organized by their companies?
RQ1 (Harviainen et al., 2023) Concur that team
member' participation in cybersecurity coping
appraisals organized by their companies is
highly important.
Q2: How do cybersecurity
professionals define and perceive
threat appraisals in the context of
organizational cybersecurity
policies?
RQ1 The literature emphasized systematically
evaluating cybersecurity risks and
vulnerabilities and underscored the practical
implementation of threat appraisals to assess
an organization's potential risks and threats
(Malgieri, 2020).
Q3: What is your perception of
cybersecurity as a professional
working in financial companies
regarding the importance of
participation in cybersecurity
coping appraisals organized by
their companies?
RQ2 Cybersecurity professionals and information
system analysts are responsible for educating
employees about cyber risks, ensuring they are
knowledgeable about the existing risks and
how to make informed decisions (Dash &
Ansari, 2022).
What is your perceived experience
as a cybersecurity professional
working in financial companies
regarding emotion-focused coping
concerning cyber threats?
RQ2 The studies conducted by Alhayani et al.
(2021) and Hernandez-Castro et al. (2020)
both emphasize the need for more than relying
solely on emotion-focused coping to address
cyber threats.
What is your perceived experience
as a cybersecurity professional
working in financial companies
regarding problem-focused coping
concerning cyber threats?
RQ2 Conway et al. (2020) and Seh et al. (2020)
emphasized the importance of problemfocused
coping. This approach proactively addresses
the root causes of cyber threats, offering a
strategic and comprehensive
importance of participating in
cybersecurity coping appraisals
organized by their companies?
Q8: To what extent do
cybersecurity professionals believe
technology adoption and
advancements influence employees'
cyber threat readiness?
RQ2 Gunduz and Das (2020) and Alkhalil et al.
(2021) asserted that technology adoption and
advancements significantly impact employees’
readiness to cope with cyber threats.
Q9: What are the key indicators
cybersecurity professionals use to
measure employees' cybersecurity
preparedness?
RQ2 Key indicators utilized by cybersecurity
professionals to measure employees'
cybersecurity preparedness (Parn & Edwards,
2019) include participation in training and
awareness programs, usage of secure practices
like strong passwords, knowledge of and
adherence to policies and procedures, response
time, level of awareness of cyber threats,
ability to identify phishing emails, and
performance in simulated cyberattacks.
Q10: What cognitive and emotional
factors influence threat appraisals
among cybersecurity professionals
regarding team member deviations
from cybersecurity policies?
RQ1 Cognitive factors included cognitive biases,
perceived severity, knowledge and
understanding of the threat landscape, past
experiences with cybersecurity incidents, and
the ability to assess risks accurately
(Harviainen et al., 2023).
Q11: What strategies and practices
do cybersecurity professionals use
to mitigate threats arising from
team member deviations from
cybersecurity policies based on the
Technology Threat Avoidance
Theory?
RQ1 When viewed through the lens of TTAT, the
rising incidences of cyberattacks in the United
States are likely to increase threat precautions
and assessment among individuals at financial
organizations, as more and more of these
individuals are likely to have experienced
cyberattacks firsthand (Alawida et al., 2022).
Q12: What strategies do
cybersecurity professionals employ
to enhance employees' cyber threat
coping abilities and risk mitigation
behaviors?
RQ2 The findings from Bunker (2020), Choi et al.
(2021), and Van der Ham (2021) highlighted
the strategies employed by cybersecurity
professionals to enhance employees' cyber
threat coping abilities, including regular
training and awareness, simulated attacks,
strict cybersecurity policies, encouraging a
cybersecurity culture, and drills.
Note. Interview Questions to Research Questions and existing literature.
The table presented a structured analysis linking interview questions with specific
research inquiries and established literature on cybersecurity within financial organizations.
It covers the spectrum from team members' views on their role in cybersecurity evaluations
to professionals' strategies for enhancing cyber threat coping skills, referencing critical

studies to support these insights. This mapping highlights the critical interaction between
employee involvement, threat appraisal methodologies, and the broader implications for
organizational cybersecurity policy and practice.
Expert Review. The instruments developed for this study were reviewed by two
experts who were faculty members of the University of the Cumberlands. The expert review
included one faculty member who was a methodologist and one with content expertise in IT.
Each member was asked to review each instrument to ensure they aligned with the research
questions, study purpose, and theoretical framework. Their review focused on each
question's relevance, clarity, and suitability within the guide, aimed to align them with the
study's research goals and ensure methodological integrity. The expert review resulted in
feedback for the instruments, which was considered when revised. The reviewers concluded
that the interview questions were well-constructed but suggested minor modifications to
improve clarity around research questions. The recommended changes were integrated into
the final iteration of the interview guide, detailed in Appendix E.
Participant Recruitment
Upon receiving approval from the Institutional Review Board (IRB), the study
commenced data collection, with the approval details documented in Appendix C for
transparency and accountability. Given the necessity to recruit participants until data
saturation was achieved, the study strategically leveraged professional associations and
social media groups to facilitate recruitment. Identifying suitable professional associations
and social media groups was conducted through online searches, ensuring relevance to the
research focus on
cybersecurity professionals within the financial sector. Once identified, these platforms were
approached to disseminate recruitment materials to their members or followers.

Following the approval from the IRB, professional associations and social media
groups were contacted to draft and distribute recruitment posts and emails. These
communications outlined the purpose of the study participation requirements and included
contact information for any inquiries. The responsibility for sharing the recruitment
materials rested with the administrators of the respective professional associations and
LinkedIn sites. The inclusion criteria stipulated that participants must be currently employed
at a financial organization, possess some level of involvement in their organization's
cybersecurity efforts, have a minimum of one year of employment to ensure relevant
experiences, and be at least 18 years of age. Experienced association administrators utilized
their expertise to disseminate the recruitment email to cybersecurity professionals, ensuring
targeted outreach within their networks. Similarly, social media administrators posted
recruitment emails to reach a wider audience of potential participants.
Participants were given a two-week window to respond to the recruitment efforts
before additional recruitment measures were initiated. This timeframe allowed for adequate
consideration and response from interested individuals while ensuring efficient progress
toward data saturation. Given the iterative nature of qualitative exploratory research and the
pursuit of data saturation, new professional associations and social media groups were
recruited for participation after the initial two-week period. This approach ensured a
continuous influx of potential participants, maximizing the chances of capturing diverse
perspectives and experiences within the study population. The recruitment strategy employed
a systematic approach, utilizing professional associations and LinkedIn and Facebook
platforms to reach potential participants within the cybersecurity field. Through clear and
transparent communication of study objectives and requirements and strategic dissemination

by platform administrators, the recruitment process aimed to attract qualified participants and
facilitate data collection until saturation.
Data Collection
Once individuals expressed interest in participating in the study, they were instructed
to initiate contact for further details. Preliminary screening was conducted based on the
established inclusion criteria to ensure eligibility. Once eligibility was confirmed, interested
potential participants were provided with informed consent forms detailing the research
process comprehensively. These consent forms outlined the study's objectives, procedures,
possible risks and benefits, confidentiality measures, and the participant's rights. Digital
signatures were collected using DocuSign.
After receiving signed informed consent forms, interviews with participants were
scheduled at mutually convenient times. Each interview was scheduled to last between 30
and 60 minutes, allowing ample time for participants to share their experiences and
perspectives indepth. Due to the ongoing COVID-19 pandemic, interviews were conducted
remotely via video conferencing platforms like Microsoft Teams, which was deemed a
weakness of the study. Because body language could not be read, this impacted the
interpretation of the data. This virtual approach ensured the safety and well-being of
participants while maintaining the integrity of the data collection process. Participants'
responses were audio-recorded throughout the interviews to capture their insights accurately.
These audio recordings were transcribed verbatim within 24 hours by trained
transcriptionists, ensuring the timely availability of data for analysis.
After transcription, participants were allowed to review and correct their transcripts for accuracy
and return them. This feedback mechanism helped to ensure that participants' voices were
accurately represented in the final data analysis.

Data Saturation
Given the iterative nature of qualitative exploratory research and the goal of
achieving data saturation, a rolling analysis approach was employed. The approach entailed
an ongoing analysis of interview data concurrent with its collection, facilitating the
identification of themes, patterns, and insights as they emerged. This iterative method
allowed for the determination of saturation, marked by the juncture where subsequent
interviews ceased to yield new themes or insights. Once saturation was achieved, data
collection was concluded, and the focus shifted toward synthesizing findings and drawing
conclusions (Mishra and Dey, 2022).
Data Analysis
The study conducted a qualitative thematic analysis. All data analysis used NVivo, a
qualitative data analysis software. The study applied qualitative thematic analysis separately
to the interviews (Mishra and Dey, 2022). Thematic analysis is a six-step process for
reducing qualitative data to its key ideas.
Data Preparation
Before analyzing the interview data, several meticulous steps were undertaken to
prepare the data for thorough analysis. The initial step involved transcribing the interviews to
convert them into a suitable format for analysis. This transcription process ensured accurate
documentation of the spoken words for further examination. After transcribing the interviews,
an additional quality assurance step was implemented to maintain data integrity. Transcribed
interviews were meticulously compared to the original audio recordings to ensure the data's
consistency and accuracy. This comparison helped to identify any discrepancies or errors in
the transcription process, ensuring that the transcribed data correctly reflected the content of
the interviews.

After verifying the transcriptions, interviews were shared with the participants for
their review and feedback, adhering to transparency and participant validation principles
essential in qualitative exploratory research. Participants were allowed a 24-hour window to
review their transcribed interviews and were suggested any necessary corrections or
clarifications. This feedback phase offered a crucial opportunity to improve the transcribed
data's accuracy and credibility. The participants' input highlighted areas that needed
clarification or revision, ensuring the final dataset accurately represented their perspectives.
Upon receiving corrections or feedback from the participants, the revised transcribed
files were meticulously reviewed and integrated into the dataset. Necessary adjustments or
amendments were made to address the participants' feedback, ensuring that the transcribed
data accurately reflected their contributions. Subsequently, the finalized transcribed files were
imported into NVivo, a qualitative data analysis software, for systematic data analysis. NVivo
provided a robust platform for organizing, coding, and analyzing the transcribed interviews,
facilitating a rigorous and structured approach to data analysis (Mishra and Dey, 2022).
Coding and Theme Development
Mishra and Dey (2022) identified that the initial step in qualitative thematic analysis
was to establish familiarity with the data. To ensure the data analysis was based on the data,
this step involved the review of all transcripts. The transcripts were read several times to
ensure familiarity with the data, and preliminary notes were taken regarding initial thoughts
about the data and preliminary themes. The next step of thematic analysis was coding
(Mishra & Dey,
2022). Codes were critical units of meaning within the data. Descriptive labels were given to
data sets representing specific concepts and topics. A combination of an initial codebook of
expected codes based on the literature and emergent codes that arose during the analysis
formed the basis for identifying the codes in this study. Utilized both inductive and deductive

coding to ensure the codes accurately represented the data and related to the topic of the study
(See
Appendix F).
After completing the initial coding round, a review ensured that the labels assigned
to the codes were relevant to the data they contained. The labels assigned to the data
segments were then documented to describe their meaning. The codes were then refined with
similar or related codes grouped to create broader categories. The broad categories were then
analyzed to identify initial patterns and relationships between the codes. The broad codes
were then grouped thematically. The third step was identifying themes, which were complete
ideas that usually relate to the co-occurrence patterns of two or more codes across the
dataset. The grouped codes were analyzed to identify themes in the data and then labeled.
The name of each theme was related to the pattern identified in the codes. Multiple instances
of data also supported each theme. Themes were answers to research questions (Mishra &
Dey, 2022).
After identifying the themes, the fourth step was to validate the themes, including
both Major and Minor themes (Mishra & Dey, 2022). In this step, each interview was
carefully checked against the data to be sure it was present and could be supported. The
identified themes were reviewed and assessed for their relation to the research questions and
the purpose of the study. This step occurred twice to ensure the themes developed were
accurate according to the data. The pieces were further validated in the fifth step by assessing
their uniqueness and completeness (Mishra & Dey, 2022). Compare the themes against each
other to ensure they were similarly substantial and all different. Finally, the pieces were
compiled and recontextualized to ensure no duplicate content (Mishra & Dey, 2022). The
themes were then interpreted concerning the research questions and categorized to which

research question each theme addressed. This process is further detailed in Chapters Four and
Five. Exploratory studies often use thematic content analysis with document reviews and
complete coding and theme development at the case level for all participants before engaging
in group-level analysis. Trustworthiness is divided into credibility and transferability. These
concepts correspond to internal and external reality (Nadella, 2023).
Credibility is the internal coherence of research and the credibility of the results
(Merriam, 2020). The study used several key strategies to achieve credibility in this
research. One strategy the study used was closely aligning the critical components of the
study. The study developed and validated the interview guide with interest in its ability to
answer research questions. The research incorporated measures of credibility into its
analytical framework, with the preliminary phase of the study laying the foundation for all
subsequent data analysis. The study also established transferability, informing prospective
readers about the applicability of the findings (Merriam, 2020).
Summary
This chapter addressed the research methods and stated that the study involved
qualitative exploratory methodology. The study’s population of interest was broad,
comprising cybersecurity professionals at financial organizations. The study used a sample
of 25 participants for semi-structured interviews conducted via Teams for 30-60 minutes.
The study leveraged professional associations and social media groups to recruit the
participants. The study took stringent measures to ensure adherence to the trustworthiness
and ethical research practices.
Chapter Four presented the findings from the data collected and analyzed the research questions.

Chapter Four
Research Findings
Introduction
The cost of cybercrime worldwide is high, affecting organizations negatively. In the
United States alone, cybercrime led to a loss of between $57 and $109 billion in 2018 (The
Council of Economic Advisers, 2018). The problem of the study focused on potential
coping mechanisms and whether security policies are adequately implemented. To address
this problem, the purpose of this qualitative exploratory study was to enable financial
organizations to establish adequate cybersecurity policies to protect their company’s
sensitive information from insider threats. This purpose was achieved by addressing the
following two central research questions. The first central research question was how do
cybersecurity professionals perceive deviation from their organization’s cybersecurity
policies as a risk to their organization? The second research question was how do
cybersecurity professionals perceive the active support they provide to employees as
helping them cope with and prevent cyber threats?
The research project included defining the purpose of the study and the research
questions, selecting appropriate qualitative methods and approaches, choosing the proper
sampling strategy and criteria, and planning the procedures for collecting and analyzing the
data. The theoretical framework and the research questions guided the research design. The
following chapter describes the study's analysis procedures and explores the analyses
conducted to address the research questions. It also included participant responses and
research settings. The final section of this chapter is the summary section.
Participants and Research Setting
The study participants were cybersecurity professionals, IT employees, and managers
of financial organizations. The participants were recruited from their professional associations
and Facebook and LinkedIn platforms. No organizational or personal conditions influenced
the participants. In addition, no such conditions influenced their experience at the time of
study as there were no budget cuts, personnel changes, or other trauma. As such, the
interpretation of the study's results was not influenced by personal or organizational
conditions. A sample of 25 participants over 23 years were recruited, and data saturation was
reached after 15 interviews.
The participants were of diverse ethnicities and included both males and females.
Regarding the study's relevant characteristics, each participant had to work at a financial
organization, engage with their organization's cybersecurity efforts, and have at least one
year of employment. These traits were important because lacking these characteristics would
have meant that the participants could not provide the data needed for the study. The
participants’ real names were known to the individuals who conducted the study.
Nonetheless, since anonymity and confidentiality of participants were paramount in the
study, using pseudonyms was an important consideration. Each participant's pseudonym was
used instead of their name to protect privacy and confidentiality. All 15 participants were
willing and prepared to engage in the semistructured interviews that lasted 30 to 60 minutes.
Their demographic information is illustrated in Table 3.
Table 3
Participant Demographics
Participant
pseudonym
Gender Age Ethnicity Work for a financial
organization (yes/no)
Work in cybersecurity
department (yes/no)
Participant 1 M 30-39 White Yes No
Participant 2 F 40-49 White Yes Yes
Participant 3 M 20-29 Hispanic Yes Yes
Participant 4 M 30-39 Black Yes Yes
Participant 5 F 30-39 White Yes Yes
Participant 6 M 30-39 Asian Yes Yes
Participant 7 F 30-39 White Yes Yes
Participant 8 F 40-49 White Yes Yes
Participant 9 M 20-29 Asian Yes Yes
Participant 10 F 40-49 Black Yes Yes
Participant 11 M 20-29 White Yes Yes
Participant 12 F 30-39 White Yes Yes
Participant 13 F 50-59 Black Yes Yes
Participant 14 M 40-49 Hispanic Yes Yes
Participant 15 M 30-39 White Yes Yes
Note. Demographic information of the participants.
The table outlines the demographics and employment details of fifteen participants, all
employed in financial organizations, with the majority working in cybersecurity. It showcases
a variety of genders, age groups, and ethnic backgrounds, reflecting diversity. This data
highlights the focus on cybersecurity in the financial sector among a diverse workforce.
Study Analysis
The interview transcripts were analyzed using NVivo 12, a qualitative data analysis
software. Braun and Clarke et al. (2015) have stated six phases of thematic analysis, which
were as follows: (1) familiarization, (2) generation of initial codes, (3) grouping codes, (4)
reviewing themes, (5) defining final themes, and (6) producing results were used in the data
analysis process. The initial phase of the analysis entailed familiarization with the data.
Additionally, handwritten notes were made on points of potential analytical interest, such as
repeated phrases, ideas, and keywords, from which codes were developed in the next step of
the thematic analysis. In phase two of the study, they generated the initial codes. Various
excerpts from the interview transcripts were clustered into codes that encapsulated similar
meanings. Those codes generated were then labeled with descriptive phrases that indicated
the meaning of the data assigned to them. Participant 1 spoke about his perception regarding
employees’ deviation from their organization’s cybersecurity policies, “If they deviate from
the cybersecurity policies that the organization establishes, it could be the significant risk for
a threat to the organization.” Participant 2 also stated that deviating from policies can create
vulnerabilities. “They understand that deviating from those policies can create
vulnerabilities.” Both responses revealed that the participants felt that employees’ deviating
from their organization’s cybersecurity policies was a significant risk to the organization and
could increase vulnerabilities in the company’s systems, so both responses were assigned to
the same code, which was labeled “deviating is a significant risk to the organization and
increases vulnerabilities with the system.” In total, 627 response excerpts were assigned to
62 codes. Table 4 shows the initial codes and the number of response excerpts assigned to
each code frequency.
Table 4
Initial Code Frequencies
Initial code
Code frequency in
interviews
Consider type and frequency of deviation, access levels, data sensitivity, and past incidents,
and follow technical implementation guides
13
Use a combination of qualitative and quantitative methods 8
Assess risk through penetration testing, simulated attacks, and risk assessments 12
Deviating is a significant risk to the organization and will increase vulnerabilities 5
Deviating increases the threat vector or the landscape for a threat 6
Deviation can lead to a cyberattack 12
Effectiveness of security awareness and training programs based on the frequency of
training, the relevance of content, the overall culture of the organization, use of real-world
examples
17
The effectiveness of security awareness and training programs perceived based on a reduction
in the number of security incidents
9
Emotion-focused coping alone is insufficient to address cyber threats 13
Emotion-focused coping entails speaking to IT employees calmly, assuring them 13
Emotion-focused coping involves meditation, increasing positive thinking 19
Engage with IT employees in coping appraisal on an ongoing basis or periodically 12
Engage with IT employees regularly in coping appraisals concerning cyber threats 24
Feedback and improvement, awareness campaigns, collaboration 5
Gamified cybersecurity challenges, regular feedback, and open communication 9
Participation in coping appraisals fosters better understanding among IT employees 5
Participation in coping appraisals helps to assess the effectiveness of current strategies 7
Participation in coping appraisals helps to understand the organization's readiness 15
Participation in cybersecurity coping appraisals promotes continuous improvement 6
Policies in place for preventing and addressing risks or threats arising from deviation 20
Problem-focused coping involves addressing the problem directly 20
Problem-focused coping is more effective in dealing with cyber threats 18
Regular training and awareness, simulated attacks, strict cybersecurity policies 19
Security controls are put in place to prevent deviating 29
Awareness, training, technical controls, monitoring and detection, sanctions and rewards, and
policy reviews and enforcement
28
Perceived threat severity, perceived vulnerability, perceived efficacy of countermeasures, and
self-efficacy
16
threat perceived, avoidance response determined, avoidance response executed, and
feedback loop
8
Technology adoption and advancements can bolster defense mechanisms 8
Threat appraisal helps to understand the capabilities of threat actors 23
Training programs that are hands-on, regular, comprehensive, and simulate real-world 28
attacks are more effective
Note: This table demonstrates the initial codes and the number of response excerpts assigned to
each code.
This table outlines the frequency of specific codes identified during interviews
relating to cybersecurity practices and organizational perceptions. Key insights include the
highest frequency of codes concerning "Security controls are put in place to prevent
deviating" and "Training programs that are hands-on, regular, comprehensive, and simulate
real-world attacks are more effective," each cited 29 and 28 times, respectively, indicating a
strong emphasis on proactive security measures and comprehensive training. Additionally,
the table revealed a significant focus on emotional and problem-focused coping strategies,

highlighting the importance of cyber threats both technically and psychologically within the
organizational context.
The above table summarized critical themes from interviews on cybersecurity
practices, emphasizing proactive security measures and active employee involvement. It
showcases a strategic blend of technical controls, regular training, and emotional coping
mechanisms to address cyber threats. This comprehensive approach underscored the
importance of organizational policies and individual responses in cybersecurity management.
The third phase of the thematic analysis was grouping codes. Codes were grouped to
form themes. If unrelated, they indicated the same aspects related to the study questions and
grouped them into clusters to create themes. The three codes, ‘deviating is a significant risk
to the organization and increases vulnerabilities with the systems,’ ‘deviating is considered a
high risk as it increases the threat vector or the landscape for a threat,’ and ‘deviation can
lead to a cyberattack that can damage the company's reputation and lead to financial loss,’
were grouped into a theme because they all indicated that IT employees of financial
organizations perceive deviation as a high risk which can increase vulnerabilities within the
systems, increase threat vector, and can lead to a cyberattack that damages their company’s
reputation and result in financial loss. The 62 initial codes were clustered into six major
nomothetic themes.
The fourth phase of the thematic analysis was about reviewing the themes. The
themes were cross-checked against one another to ensure that the ideas they represented did
not overlap. Furthermore, the themes were compared to the original data to ensure they
indicated patterns in the participants' responses. In the fifth phase, the themes were named
and defined (Clarke et al., 2015). These definitions were in the analysis of the research
question section. The sixth data analysis phase entailed presenting the results by writing
Chapter Four of the dissertation (Clarke et al., 2015). As a preliminary overview of the
results, Table 5 below demonstrates how the initial codes were grouped to form the finalized
themes.
Table 5
Grouping of Codes into Finalized Themes
Theme
Initial code clustered to identify the theme
Theme
frequency in
interviews
Theme 1: A high risk that can increase system vulnerabilities and threat vectors and lead to
cyberattacks that damage the company’s reputation \and result in financial loss
23
Deviating is a significant risk to the firm and will increase system vulnerabilities.
Deviating is a high risk as it increases the threat vector or the landscape for a threat.
Deviation can lead to a cyberattack that can damage the company's reputation and lead to
financial loss.
Theme 2: Participation helps assess the effectiveness of strategies and develop new ones,
understand the organization’s readiness, highlight vulnerabilities, and identify areas of
strengths and weaknesses
22
Participating in appraisals helps assess current strategies' effectiveness and develop new
approaches to enhance cyber resilience.
Participation in appraisals helps to understand an organization's readiness, identify areas of
weakness and strength, highlight vulnerabilities, and help deal with cyber threats. Theme 3:
Ready and able to cope with cyber threats due to technologies, security awareness,
training, and simulations and drills
61
Regular training and awareness, simulated attacks, strict cybersecurity policies, and an
encouraging cybersecurity culture enhance employees' cyber threat coping abilities.
Security awareness and training programs are crucial in promoting threat avoidance among
employees.
Technologies enhance the ability to detect, prevent, and respond to cyber threats, thus
influencing employees' cyber threat readiness.
Simulating cyberattacks and conducting drills to test and improve response capabilities
Theme 4: Participation promotes continuous improvement, skill enhancement, compliance
and standardization, building confidence, and better employee understanding.
11
Participation in coping appraisals fosters better understanding among employees and
promotes a proactive cybersecurity culture.
Participation in coping appraisals helps with skill enhancement, keeping updated,
compliance and standardization, and building confidence.
Participation in cybersecurity coping appraisals promotes continuous improvement and
ensures everyone is on the same page regarding the company's cybersecurity policies.
Theme 5: Inadequate when used alone to address cyber threats as it does not solve actual
problems but helps manage stress and anxiety.
45
Emotion-focused coping alone is insufficient to address cyber threats and is less effective
than problem-focused coping.
Emotion-focused coping entails calmly speaking to employees, assuring them, and helping
them maintain a healthy mental state in the workplace.
Emotion-focused coping involves meditation, increasing positive thinking, and
seeking support from others to reduce anxiety and manage stress related to cyber threats.
Theme 6: Addresses root cause and solves problem directly and proactively
Problem-focused coping involves addressing the problem directly.
Problem-focused coping is a proactive way of managing and mitigating potential cyber risks.
54
Problem-focused coping is more effective in dealing with cyber threats as it addresses stress's
root cause.
Note. This table shows that the codes are grouped to form finalized themes.
A total of six major (MA) nomothetic themes and eight minor (MI) nomothetic
themes emerged from the analyzed data. The table organized various codes into six themes
related to cybersecurity, quantifying their frequency in interviews. Theme 1 discussed the
high risks associated with system vulnerabilities and the potential for cyberattacks leading
to financial loss and reputational damage, with a frequency of 23 mentioned. Meanwhile,
Theme 3, with 61 mentioned, emphasized the readiness and capability of coping with cyber
threats through technologies, security awareness, and training, highlighting the importance
of proactive measures in cybersecurity management.
Table 6 overviews the research questions and corresponding major nomothetic themes.
Table 6
Research Questions and Their Corresponding Themes
Research Question Theme
RQ1: How do cybersecurity professionals perceive
deviation from their organization’s cybersecurity
policies as a risk to their organization?
MA Theme 1: A high risk that can increase system
vulnerabilities threat vector and lead to cyberattacks
that damage the company’s reputation or result in
financial loss.
1a. What is the perception of employees working in
financial companies regarding the importance of
participation in cybersecurity threat appraisals
organized by their companies?
MA Theme 2: Participation helps assess the
effectiveness of strategies and develop new ones,
understand the organization’s readiness, highlight
vulnerabilities, and identify areas of strengths and
weaknesses.
RQ2: How do cybersecurity professionals perceive the
active support they provide to employees as helping
them cope with and prevent cyber threats?
MA Theme 3: Ready and able to cope with cyber
threats due to technologies, security awareness,
training, and simulations and drills.
2a. What is the perception of employees working in
financial companies regarding the importance of
participation in cybersecurity coping appraisals
organized by their companies?
MA Theme 4: Participation promotes continuous
improvement, skill enhancement, compliance and
standardization, building confidence, and better
employee understanding.
2b. What is the perceived experience of employees
working in financial companies regarding
emotionfocused coping with respect to cyber threats?
MA Theme 5: Inadequate when used alone to address
cyber threats as it does not solve actual problems but
helps manage stress and anxiety.
2c. What is the perceived experience of employees
working in financial companies regarding
problemfocused coping with respect to cyber threats?
MA Theme 6: Addressed root cause and solved the
problem directly and proactively.
Note. Research questions and themes were used to answer them.
This table outlines the connection between research questions and themes in the
context of cybersecurity within financial organizations, shedding light on how deviations
from cybersecurity policies and threat appraisals were perceived. RQ1 emphasizes the high
risks of policy deviations and the benefits of using threat appraisals to enhance
organizational security. RQ2 focused on cybersecurity professionals' support, the
significance of employee involvement in coping appraisals, and the effectiveness of different
coping strategies. The themes underscore the critical role of proactive engagement and
comprehensive support in mitigating cyber threats.
Evidence of Trustworthiness
Understanding trustworthiness involves acknowledging the truthfulness, authenticity,
and quality of findings. Four critical criteria were typically used to judge the soundness of
qualitative exploratory research: credibility, transferability, dependability, and confirmability.
The components mentioned in the study by Doan et al. (2020) corresponded to the qualitative
categories of internal validity, external validity, reliability, and objectivity. The following
section detailed how each element of trustworthiness was established in this research.
Credibility
Credibility focuses on how congruent the findings are with reality (Amin et al.,
2020). Moreover, it measured the truth value of qualitative exploratory research and was
concerned with whether the findings were accurate (Amin et al., 2020). The study employed
several strategies to establish credibility. One was member checking, also known as
respondent or participant validation (Doan et al., 2020). After gathering data from the
participants, the interview transcripts were returned to them to check for accuracy and

resonance with their experiences before actual data analysis. All 15 participants confirmed
that their data was accurate, and thus, credibility was established.
The second procedure used in the study to strengthen credibility was data
triangulation. Data triangulation is the process whereby the study compares data from at
least two sources to identify common points and discrepancies to develop a more robust
characterization of a phenomenon than a single data would allow (Johnson et al., 2021). The
study collected data through individual interviews. The data from those sources were
compared to identify areas of consistency and discrepancy. Negative case analysis was the
third strategy to establish the study's credibility. It was a technique for ensuring the validity
of the interpretation of qualitative data by analyzing outlier data (Johnson et al., 2021). By
conducting a negative case analysis, data elements that disconfirmed emergent findings
were identified and removed. The procedure was performed by establishing data that
contradicted results or needed to be completed. The revision continued until the study
explained most of the data captured in the study. This procedure helped in refining all the
conclusions reached until they accounted for all the known cases without exception.
Transferability
Transferability is the second main component of trustworthiness (Amin et al., 2020).
Data is transferable to the extent that it holds settings and samples except those from which
it was derived (Amin et al., 2020). For the study, transferability was established through the
participants' descriptions, which were as follows. The study participants were comprised of
cybersecurity professionals who knew their banks’ cybersecurity efforts and had a minimum
of 12 months of experience working in their current positions at the time of the study. Data
collected through semi-structured interviews allowed the study to gain an in-depth
understanding of how to establish the extent to which applying consistent and reliable anti-

cyber security models can protect their company’s sensitive information from insider
threats.
Additionally, Chapter Three provided descriptions of the inclusion criteria for the
study sample to assist readers in assessing the transferability of the study's findings to
different settings. All participants recruited met the inclusion criteria. Besides, the study
provided descriptions of the findings in the analysis of the research question section of this
chapter, which were in the form of direct quotes from the data, so that through the use of
participants’ own words, the contexts and perspectives from which they were speaking were
conveyed to the readers.
Dependability
This component of trustworthiness is used to assess the reliability and consistency of
the results of a given research. Dependability is the degree to which the procedures in a study
can be replicated in the same research context to get the same results Clarke et al. (2015). For
the study, dependability was established by providing detailed descriptions of the study
procedures in Chapter Three that the reader can use, if needed, to substantiate the integrity of
those procedures by replicating the study. The use of interview protocols to guide data
collection also contributed to the replicability of the data collection procedures, further
strengthening dependability.
Confirmability
Confirmability refers to the degree of neutrality in the findings of a study.
Confirmability ensured that the findings were based on the participants' responses and were
not influenced by the motivations or biases of the investigators (Amin et al., 2020).
Credibility was established in the study through an audit trail highlighting all steps taken in
the data analysis process to justify the decisions made. Six steps were consistent with the

thematic analysis process outlined by Clarke et al. (2015) for data analysis. The employment
of a member-checking procedure contributed to confirmability, as it enabled participants to
ensure that interpretations of the data accurately represented their intentions behind their
responses rather than being influenced by any external interpretations of their interview
data.
Analyses of Research Questions
The study addressed two central research questions. The first central research
question was how do cybersecurity professionals perceive deviation from their
organization’s cybersecurity policies as a risk to their organization? The second central
research question was how do cybersecurity professionals perceive the active support they
provide to employees as helping them cope with and prevent cyber threats? Several themes
emerged from the data to address the research questions. The study identified major and
minor nomothetic themes from the interviews. The themes were presented and discussed as
per the research question.
Research Question One
RQ1. How do cybersecurity professionals perceive deviation from their
organization’s cybersecurity policies as a risk to their organization?
RQ1a. What is the perception of employees working in financial companies
regarding the importance of participation in cybersecurity threat appraisals organized by
their companies?
RQ1b. How do cybersecurity professionals define and perceive threat appraisals in
the context of organizational cybersecurity policies?
RQ1c. How do cybersecurity professionals assess the potential risks associated with
employees deviating from cybersecurity policies?

RQ1d. What cognitive and emotional factors influence threat appraisals among
cybersecurity professionals regarding employee deviations from cybersecurity policies?
RQ1e. What strategies and practices do cybersecurity professionals use to mitigate
threats arising from employee deviations from cybersecurity policies based on the
Technology Threat Avoidance Theory?
One minor theme addressed this question. Two participants contributed to this
theme.
The theme was as follows:
Theme One: Deviation increases the landscape for threats. Based on this theme,
participants noted that the cybersecurity threat arises whenever the organization deviates from
cybersecurity policies. Two participants supported this theme. Participant 6 mentioned that
information, mainly financial data is always secured, and deviating from the company’s
cybersecurity policies heightens the threat landscape. He stated:
We perceive our information as everything that needs to be secured, especially when
dealing with financial data. Any lessening of security policies or security
implementation increases the landscape for a threat. So, consider it a very high risk if
it deviates from the required baseline security policies.
Likewise, Participant 2 mentioned that failure to comply with the organization’s cybersecurity
policies can adversely affect the company’s security posture and that everyone is responsible for
keeping data safe. Specifically, she noted:
It also realizes that not complying with these policies can harm the overall security
posture. Furthermore, we all have our own; what is it? We all have goals and
responsibilities to keep the data safe.
The following minor themes addressed this question:

Theme Two: Participation provides a snapshot of the risk landscape. Participants
indicated that participating in cybersecurity threat appraisals allows employees to understand risk
identification and management. Five participants contributed to this minor theme. Participant 1
mentioned that while cybersecurity professionals typically consider threat appraisals integral to
cybersecurity strategy, a good threat appraisal provides cybersecurity professionals with a clear
snapshot of the present risk landscape. This participant stated:
Perception-wise, cybersecurity professionals often view threat appraisals as a
foundational element in a cybersecurity strategy. An effective threat appraisal provides a
snapshot of the current risk landscape. It helps organizations move from a reactive stance to
a proactive, risk-informed approach, making them more resilient against cyber threats.
Similarly, Participant 4 remarked that threat appraisals allow cybersecurity professionals to
understand the severity and likelihood of a threat before determining how to handle it. He
stated: Threat appraisal in cybersecurity often refers to evaluating a perceived cyber threat's
potential harm or adverse impact. Cybersecurity professionals perceive threat appraisals in
the context of organizational policies as an essential precursor to risk management, seeking
to understand the severity and likelihood of a threat before deciding how to address it.
Theme Three: Participation guides proactive measures for risk mitigation.
Participants noted that participation in cybersecurity threat appraisals could help guide
proactive risk mitigation measures for this theme. Four participants contributed to this theme.
Participant 1 stated, “An effective threat appraisal guides proactive measures for risk
mitigation.”
Similarly, Participant 13 noted, “Assessing threats based on their likelihood to occur and their
possible impact on the organization enables companies to prioritize their cybersecurity
endeavors.” Similarly, participant 11 stated, “Cybersecurity professionals typically assess

threats based on their likelihood of occurring and the potential impact they might have to help
organizations prioritize their security resources and efforts.”
Research Question Two
RQ2. How do cybersecurity professionals perceive the active support they provide to
employees as helping them cope with and prevent cyber threats?
RQ2a. What is the perception of employees working in financial companies regarding
the importance of participation in cybersecurity coping appraisals organized by their
companies?
RQ2b. What is the perceived experience of employees working in financial
companies regarding emotion-focused coping with respect to cyber threats?
RQ2c. What is the perceived experience of employees working in financial companies
regarding problem-focused coping with respect to cyber threats?
RQ2d. To what extent do cybersecurity professionals believe technology adoption and
advancements influence employees' cyber threat readiness?
RQ2e. What are the key indicators cybersecurity professionals use to measure
employees' cybersecurity preparedness?
Theme Four: Participation fosters a proactive cyber security culture. Most
participants stated that participating in cybersecurity coping appraisals helps promote a
proactive cybersecurity culture in the organization. Participant 13 stated, “Most
cybersecurity professionals view participation in coping appraisals as crucial. These sessions
can promote a proactive security culture.” Similar views were shared by Participant 2, who
stated, “Participating in such appraisals not only helps enhance the organization's
cybersecurity posture but also reinforces the importance of cybersecurity to the employees.”
Participant 9 said, “Encouraging and promoting a culture of cybersecurity within the

organization where employees were encouraged to take cybersecurity seriously and actively
participate in training and awareness programs.” Theme Five: Participation ensures
everyone understands the company’s cybersecurity policies. Based on the interview data
analyzed, cybersecurity coping appraisals helped individuals identify areas of improvement
among the employees and provide the necessary training so that all the employees
throughout the organization could be conversant with the company's cybersecurity policies.
Data from five participants supported this theme. Participant 15 stated, “Participation in
cybersecurity coping appraisals organized by their companies is generally critical. These
appraisals can help identify potential improvement areas and ensure everyone is on the same
page regarding the company's cybersecurity policies and procedures”. Similarly, Participant
8 stated, “Most cybersecurity professionals perceive participation in coping appraisals as
vital. These appraisals provide valuable insights into employees' awareness levels and areas
of improvement and can also help tailor future training sessions.”
Theme Six: Emotion-focused coping is not as effective as problem-focused
coping. Based on this theme, emotion-focused coping can help deal with the stress and
anxiety associated with cyber threat incidents, but it is generally less productive than
problem-focused coping. Participant 11 stated, “Cybersecurity professionals often perceive
emotion-focused coping as less effective than problem-focused coping when dealing with
cyber threats.” Similar sentiments were shared by Participant 2, who said, “Cybersecurity
professionals often perceive emotion-focused coping as less effective than problem-
focused coping because it does not address the root cause of the threat.”
Theme Seven: Emotion-focused coping impairs judgment. Some participants
noted that emotion-focused coping can impair a person’s judgment. Participant 6 reported,
“While professionals need to manage the anxiety and stress that arise from potential cyber

threats, an excessive emotional response can impair judgment.” Likewise, Participant 15
reported that focusing too much on emotion could distract the individual from tackling the
issue effectively, adversely affecting their judgment. He said, “Too much focus on emotion
can potentially distract from addressing the problem.”
Theme Eight: Problem-focused coping is more effective in dealing with cyber
threats. Concerning this theme, some participants noted that problem-focused coping is
generally more appropriate for dealing with cyber threats. Participant 1 noted, “This
approach is considered more effective in dealing with cyber threats as it involves taking
concrete actions to mitigate the risks and prevent attacks.” Similarly, Participant 8 stated,
“Problem-focused coping entails “taking proactive measures to prevent cyberattacks,”
making it more effective in tackling cyber threats.
The study identified major nomothetic themes when at least eight of the 15
interview participants, or 53% of all participants, expressed indications of such themes.
Thus, major nomothetic themes in this study included those that were referred to by most
participants.
Conversely, minor nomothetic themes refer to those referred to by 47% or less of all
participants. A descriptive format was utilized to present these themes in the results. A total
of 14 themes emerged from the analyzed data, including six major nomothetic themes and
eight minor ones.
Supplementary Findings
The interview participants in the study referenced major nomothetic themes, and 15
participants verbalized the same thought. Table 7 lists the number of participants who
verbalized a particular MA nomothetic theme and the percentage of participants who

shared the theme. The table shows six major nomothetic themes, the frequency with which
the theme occurred in the data and the participants who contributed to the theme.
Table 7
Major Nomothetic Themes and Frequencies in the Data
Note. This table shows the major nomothetic themes and the overall frequency with which
they occurred.
The nomothetic themes addressed the research questions. As Haufe (2015) pointed
out, major nomothetic themes established collective laws supported by the majority of the
population. In the study, major nomothetic themes were identified by gathering the
responses from the participants and determining common participant responses, where a
minimum of 53% of the participants agreed. Participants were considered to have shared
thoughts when at least two shared the same ideas, as demonstrated by their responses to the
interview questions. There were major nomothetic themes for each of the research
questions.
The following table shows the major nomothetic themes that emerged from data analysis.
Themes P1 P2 P3 P4 P5 P6 P7 P8 P9 P10 P11 P12 P13 P14 P15 Percent
MA Theme 1 X X X X X X X X 53%
MA Theme 2 X X X X X X X X X X X X X X 93%
MA Theme 3 X X X X X X X X X X X X X X 93%
MA Theme 4 X X X X X X X X X X X 80%
MA Theme 5 X X X X X X X X X X X X X X X 100%
MA Theme 6 X X X X X X X X X X X X X X X 100%
Table 8
Major Nomothetic Themes
Theme
Number
Theme Description
MA Theme 1 A high risk that can increase system vulnerabilities threat vector and lead to
cyberattacks that damage the company’s reputation or result in financial loss
MA Theme 2 Participation helps assess the effectiveness of strategies and develop new ones,
understand the organization’s readiness, highlight vulnerabilities, and identify areas
of strengths and weaknesses.
MA Theme 3 Ready and able to cope with cyber threats due to technologies, security awareness,
training, and simulations and drills
MA Theme 4 Participation promotes continuous improvement, skill enhancement, compliance
and standardization, building confidence, and better employee understanding.
MA Theme 5 It is inadequate when used alone to address cyber threats as it does not solve actual
problems but helps manage stress and anxiety.
MA Theme 6 Addressed root causes and solves problems directly and proactively.
Note. This table shows the major nomothetic themes that addressed the research questions.
The table outlines major nomothetic themes addressing research questions,
highlighting risk assessment, the value of participation, and coping strategies for cyber
threats. Themes stress the importance of proactive measures, such as technology and
training, and the limitations of solely emotion-focused coping. The emphasis is on
continuous improvement, problem-solving, and the holistic involvement of employees in
enhancing cybersecurity resilience.
Central Research Question One (RQ1). How do cybersecurity professionals
perceive deviation from their organization’s cybersecurity policies as a risk to their
organization? One central nomothetic theme emerged from the analyzed data that
addressed RQ1. This was as follows: (a) deviation is a high risk, which can increase
vulnerabilities within the systems, increase threat vector, and lead to a cyberattack that
damages the company’s reputation or results in financial loss. Below are the themes.
MA Theme One: A High Risk Which Increases System Vulnerabilities, Threat

Vector, and Leads to Cyberattacks That Damage Company’s Reputation or Result in
Financial Loss. Eight interview participants contributed to this major theme. The contributing
participants indicated that employees working in financial companies viewed deviation from
their organization’s cybersecurity policies as a high risk that could increase vulnerabilities within
the organization’s systems, increase threat vector, and even lead to cyberattacks that may, in turn,
damage the reputation of the company and result in financial loss. Participant 1 mentioned
reputation damage and stated:
There may be some perceptions about it among employees. The first thing that comes to
mind is that uh, if, uh, um, reputation [of the] organization and you have many clients,
for example, as you can take my, um, case, which I told you earlier, like a denial of
services, right? Right. So, at that time, what will happen if, as an employee or on the
business side, they think, or what will happen initially? First, it is reputation damage
that people will experience in the next few days.
Participant 2 said, “They understand that deviating from the policies can create
vulnerabilities, right? Furthermore, it makes data breaches, malware, and unauthorized
access more acceptable, as well as other incidents.” Participant 4 mentioned:
They are usually aware that cybersecurity policies are implemented to protect sensitive
information, all systems, and the organization. Deviating from these policies increases
the likelihood of a successful cyberattack or compromise, which usually destabilizes
the business and the company's branding.
Furthermore, Participant 6 reported:
We perceive our information as everything that needs to be secured, especially when
dealing with financial data. Any lessening of security policies or implementation

increases the threat vector or the landscape for a threat. So, we consider it a very
high risk if we deviate from the required baseline security policies.
RQ1a. What is the perception of employees working in financial companies
regarding the importance of participation in cybersecurity threat appraisals
organized by their companies?
One major theme that answered this sub-question emerged from the analyzed data.
The theme was: (a) participation in cybersecurity threat appraisals helps to assess the
effectiveness of current strategies and develop new strategies to enhance cyber resilience,
helps to understand the organization’s readiness, highlights vulnerabilities, and identifies
strengths and weaknesses of employees and companies. The following paragraph will
discuss this theme.
MA Theme Two: Participation Helps Assess the Effectiveness of Strategies and
Develop New Ones, Understand the Organization’s Readiness, Highlight
Vulnerabilities, and Identify Areas of Strengths and Weaknesses. Fourteen out of the 15
interviewed participants contributed to this significant theme. The theme suggested that
according to the participants, employees who work in financial companies perceive
participation in cybersecurity threats appraisals as vital because it helps in assessing the
effectiveness of current strategies and developing new techniques, understanding the
organization’s readiness, highlighting vulnerabilities, and identifying areas of strengths and
weaknesses. According to Participant 12, “Cybersecurity professionals perceive
participation in cybersecurity coping appraisals as highly important. These appraisals help
identify potential areas of improvement, assess current strategies' effectiveness, and develop
new strategies to enhance cyber resilience.”

Similarly, Participant 14 mentioned, “It helps identify areas of weakness and strength
and develop strategies to enhance the organization's overall cybersecurity posture.” Participant
3 reported, “Most cybersecurity professionals perceive participation in cybersecurity coping
appraisals organized by their companies as extremely important. It helps identify potential
weaknesses in the existing cybersecurity infrastructure and develop better strategies to cope
with cyber threats.” Participant 11 indicated, “Cybersecurity professionals typically view
participation in cybersecurity coping appraisals as crucial. Such appraisals offer insights into
the organization's readiness to highlight vulnerabilities.” Similarly, Participant 13 noted, “Most
cybersecurity professionals view participation in coping appraisals as crucial. These sessions
can reveal vulnerabilities,” whereas Participant 14 stated, “These appraisals help assess and
improve the organization's readiness to face and manage cyber threats.”
Central Research Question Two (RQ2). How do cybersecurity professionals
perceive the active support they provide to employees as helping them cope with and prevent
cyber threats?
One major theme emerged from the analyzed data that answered RQ2. The theme
was: (a) employees have the readiness and capacity to cope with cyber threats due to
technologies, security awareness, regular and hands-on training, and simulations and drills,
which improve response capabilities. The following paragraph discusses this theme.
MA Theme Three: Ready and Able to Cope with Cyber Threats Due to
Technologies, Security Awareness, Training, and Simulations and Drills. Thirteen out
of the 15 interview participants contributed to this major theme. The theme showed that,
according to the participants, employees who work at financial companies had the
readiness and capacity to cope with cyber threats due to technology adoption and

advancements, security awareness, regular hands-on training, and simulations and drills,
which improved response capabilities.
Speaking about technology adoption and advancements, Participant 12 reported:
Cybersecurity professionals believe technology adoption and advancements significantly
influence employees' cyber threat readiness. Properly implemented advanced
technologies can enhance the ability to detect, prevent, and respond to cyber threats.
However, they also recognize that technology, while essential, requires complementation
through adequate employee training and awareness initiatives.
Similarly, Participant 9 stated:
Adopting advanced technologies, such as artificial intelligence and machine learning,
can help detect and prevent cyber threats more efficiently.
Participant 5 noted:
Cybersecurity professionals generally believe that while technology adoption and
advancements can bolster defenses and automate specific processes, they can also
introduce new vulnerabilities if not managed properly. The human element remains
vital; thus, employees' cyber threat readiness combines technology and awareness
training.
Participant 2 mentioned:
Cybersecurity professionals employ strategies to enhance employees' cyber threat
coping abilities and risk mitigation behaviors, such as regular training and awareness
programs. Consistent training sessions and awareness efforts educate staff about the
most recent cyber risks and the most effective methods to minimize their impact.
Similarly, Implementing and Enforcing Strong Cybersecurity Policies: Having well-defined
cybersecurity policies and procedures in place and ensuring all employees follow them.

Providing Tools and Resources: Ensuring employees have access to the necessary tools and
resources to cope with cyber threats, such as up-to-date security software and secure
communication channels. Likewise, Participant 3 stated:
Cybersecurity professionals employ various strategies to enhance employees' cyber
threat coping abilities and risk mitigation behaviors. This mitigation includes regular
training and awareness sessions and simulated cyberattacks to test employees
‘responses. They were encouraging adherence to best practices and company policies.
Similarly, Participant 11 stated, “Regular training and awareness sessions, real-time
simulations and drills, and incentivizing and rewarding cybersecurity best practices” as
strategies for enhancing employees’ cyber threat coping abilities and risk mitigation
behaviors. According to Participant 4,
Cybersecurity professionals generally perceive continuous and engaging security
awareness programs as more effective than one-off sessions. Programs that utilize
reallife scenarios, interactive sessions, and hands-on training are more beneficial.
He also mentioned frequent awareness training can help individuals stay updated on
the new cybersecurity impacts and laws.
2a. what is the perception of employees working in financial companies regarding the
importance of participation in cybersecurity coping appraisals organized by their
companies?
One major theme from the analyzed data was that it effectively addressed this
subquestion. The major theme was: (a) participation in cybersecurity coping appraisals
promotes continuous improvement, helps with skill enhancement, compliance, and
standardization, builds confidence, and fosters better employee understanding. The theme
discussed here is as follows:

MA Theme Four: Participation Promotes Continuous Improvement, Skill
Enhancement, Compliance and Standardization, Building Confidence, and Better
Understanding Among Employees. Eleven out of 15 participants in the semi-structured
interviews contributed to this significant theme. The theme indicated that, as per the
participants, employees who work in banks perceived participation in cybersecurity coping
appraisals as important. It promotes continuous improvement, helps with skill enhancement,
compliance, and standardization, builds confidence, and fosters better employee
understanding. According to Participant 10, “It helps develop a proactive approach to
cybersecurity and fosters a culture of continuous improvement.”
According to Participant 13, “Most cybersecurity professionals view participation in
coping appraisals as crucial. These sessions can foster better employee understanding and
promote a proactive security culture.” Participant 15 mentioned, “Participation in
cybersecurity coping appraisals organized by their companies is critical. These appraisals can
help ensure everyone is on the same page regarding the company's cybersecurity policies and
procedures.” According to Participant 4, “Most cybersecurity professionals perceive
participation in coping appraisals as essential. These sessions provide opportunities to
identify vulnerabilities, improve procedures, and refine the team's skills.”
Participant 7 reported, “Cybersecurity professionals generally perceive participation in
cybersecurity coping appraisals organized by their companies as highly important.”
As mentioned by Participant 7, some of the reasons were: Skill Enhancement: Regular
appraisals help assess and improve the skills and knowledge of the professionals, which is
crucial for keeping up with the ever-evolving landscape of cyber threats. Keeping Updated:
The world of cybersecurity is constantly changing. Regular appraisals ensure that
professionals have the latest threats and the best practices to counter them. Compliance and

Standardization: Regular appraisals help ensure the organization's cybersecurity practices
align with industry standards and legal requirements. Building Confidence: Being regularly
appraised and getting positive feedback builds confidence in one's skills and abilities. It also
helps develop a proactive approach to cybersecurity rather than a reactive one.
2b. What is the perceived experience of employees working in financial companies
regarding emotion-focused coping with cyber threats?
One major theme arose from the analyzed data that helped to answer this sub-
question. The theme was as follows: (a) emotion-focused coping alone is inadequate to
address cyber threats as it does not solve actual problems. However, it helps to manage stress
and reduce anxiety. The following paragraph discusses this theme.
MA Theme Five: Inadequate When Used Alone to Address Cyber Threats as it
Does Not Solve Actual Problem but Helps Manage Stress and Anxiety. All 15 interview
participants contributed to this theme. According to the participants, this theme suggested
that emotion-focused coping alone was insufficient to effectively address cyber threats
because it did not solve the problem. However, it is crucial in managing stress and reducing
anxiety. Participant
1 mentioned:
Emotion-focused coping involves managing the emotional response to a stressful
situation rather than addressing the problem. While managing stress and anxiety is
essential, especially in high-pressure situations like a cyberattack, emotion-focused
coping alone is not sufficient to address cyber threats. Cyber threats always need to
be complemented with problem-focused coping strategies.
According to Participant 12, “Cybersecurity professionals often perceive
emotionfocused coping as less effective than problem-focused coping when dealing with

cyber threats. Emotions like anxiety and fear can sometimes hinder the decision-making
process and response time during a cyber-attack.” Furthermore, Participant 13 reported:
Cybersecurity professionals recognize that emotion-focused coping can be a
doubleedged sword. While individuals must manage stress and anxiety related to
cyber threats, over-reliance on emotional coping can lead to complacency or
avoidance. While professionals may encourage healthy emotional coping
mechanisms, like seeking support or taking breaks, they also stress the importance
of problem-focused coping.
Likewise, Participant 3 indicated:
Cybersecurity professionals generally perceive emotion-focused coping as less
effective than problem-focused coping when dealing with cyber threats. Emotion-focused
coping, which involves managing emotional responses to a threat, is essential but can
sometimes be seen as a secondary response as it does not address the root cause of the cyber
threat. 2c. What is the perceived experience of employees working in financial companies
regarding problem-focused coping with respect to cyber threats?
One major theme that adequately addressed this sub-question emerged from the analyzed
data: (a) problem-focused coping, which addresses the root cause of the issue and solves it
proactively. The following paragraph discusses this theme.
MA Theme Six: Addressed Root Cause and Solves Problem Directly and
Proactively. Data supporting this major theme from all 15 individual interviews. The finding
indicated that, according to the participants, employees working in financial companies
believe that problem-focused coping addresses the root cause of the issue and solves the
problem proactively. Participant 10 stated:

Well, the perceived experience of cybersecurity professionals regarding problem-
focused coping to cyber threats is generally favorable. Problem-focused coping
involves addressing the problem or stressful situation directly, which, in the context
of cybersecurity, means identifying the threat, analyzing it, and taking necessary
actions to mitigate or eliminate it. This approach is generally perceived as more
effective because it addresses the problem's root cause and helps prevent future
attacks.
Similarly, Participant 11 indicated:
Problem-focused coping is at the core of a cybersecurity professional's toolkit. It
involves direct action to address the threat, such as enhancing security measures,
updating software, or deploying countermeasures. Their experience underscores the
importance of proactive measures, continuous learning, and immediate response to
threats. This type of coping is more direct and effective in managing cyber threats
than emotion-focused coping.
Participant 12 mentioned:
Cybersecurity professionals usually prefer problem-focused coping, which involves
addressing the problem, such as identifying the source of a cyber-attack, mitigating
its effects, and implementing measures to prevent similar attacks in the future. This
participant added, “This approach is perceived as more effective because it directly
deals with the threat and helps resolve it.
According to Participant 14:
Problem-focused coping involves tackling the problem head-on and taking
proactive steps to resolve it. Cybersecurity professionals often prefer problem-
focused coping strategies as trained to identify, assess, and respond to threats

directly. Their perceived experience may involve actively monitoring networks,
implementing security measures, and developing response plans to address cyber
threats.
Minor (MI) Nomothetic Themes
The interviewees mentioned Minimal Nomothetic (MI) motifs. These themes were
contributed to by less than half of the participants, or seven out of the 15 who were
questioned. Table 7 lists the number of participants who verbalized the MI nomothetic
themes and the percentage of participants who shared the theme. The table also depicts the
frequency of the theme in the data and the number of participants who contributed to each
theme.
Table 9
Minor Nomothetic Themes and Frequencies in the Data
Themes P1 P2 P3 P4 P5 P6 P7 P8 P9 P10 P11 P12 P13 P14 P15
Percent
MI Theme 1 X X 13%
MI Theme 2 X X X 20%
MI Theme 3 X X X X 27%
MI Theme 4 X X X X 80%
MI Theme 5 X X X X X X 40%
MI Theme 6 X X X X X X 33%
MI Theme 7 X X X X 27%
MI Theme 8 X X X X X X 47%
Note. This table shows the minor nomothetic themes and their overall frequency in the
data.
Table 9 maps minor nomothetic themes across participants, showing their varying
frequencies in the data. Themes like MI Theme 4, with an 80% occurrence, suggested a
widespread acknowledgment of certain cybersecurity attitudes or practices among the
group. The table highlights the diverse yet specific engagement with themes ranging from
risk awareness to coping strategies within the participant pool.
Minor nomothetic themes occur less frequently than major nomothetic themes. Haufe
(2015) reported that these themes were essentially the establishment of universal laws often
supported by a significant, but less than half, of the population. The study discovered such
minor nomothetic themes by determining themes supported by seven out of the 15 interview
participants, or 47% of all participants. Shared thoughts occurred when two or more
participant responses shared the same idea to the interview questions. The following table
shows the minor nomothetic themes that emerged from data analysis.
Table 10
Minor Nomothetic Themes
Theme
Number
Theme Description
MI Theme 1 Deviation increases the landscape for threats
MI Theme 2 Participation provides a snapshot of the risk landscape.
MI Theme 3 Participation guides proactive measures for the risk landscape.
MI Theme 4 Participation promotes a proactive cyber security culture.
MI Theme 5 Participation ensures that everybody understands the company’s cybersecurity
policies.
MI Theme 6 Emotion-focused coping is not as effective as problem-focused coping.
MI Theme 7 Emotion-focused coping impairs judgment.
MI Theme 8 Problem-focused coping is more effective in handling cyber threats.
Note. This table demonstrates the minor nomothetic themes.

Table 10 delineates minor nomothetic themes, emphasizing the impact of deviation
and participation on organizations' cybersecurity landscape and culture. It contrasts the
efficacy of emotion-focused versus problem-focused coping strategies in managing cyber
threats. The themes collectively advocate for a proactive, inclusive approach to
cybersecurity and highlight the superiority of problem-focused coping in threat mitigation.
Summary
The problems that were identified in the study were coping mechanisms and whether
the security policies that financial organizations have are adequately implemented. The
purpose of the qualitative exploratory study was to enable financial organizations to
establish how consistent and reliable anti-cyber security models can protect their company’s
sensitive information from insider threats. The study aimed to answer two central research
questions, which it has successfully addressed. Interview data from 15 employees,
cybersecurity professionals, and managers working at financial organizations were analyzed
through thematic analysis. There were six steps of analysis. These included familiarizing
with the data, generating initial codes, searching for themes, reviewing, defining, naming,
and reporting. NVivo 12 software was used in the analysis process.
Major nomothetic and minor themes emerged from the data analysis, with at least
eight of the 15 participants supporting the major themes and seven or fewer participants
supporting the minor themes. The first central research question was how cybersecurity
professionals perceive deviation from their organization’s cybersecurity policies as a risk to
their organization. The findings revealed that according to the participants, employees in
financial organizations felt that deviation was a high risk, which can increase
vulnerabilities within the systems, increase threat vector, and lead to a cyberattack that
damages the company’s reputation and results in financial loss, which was the first major

nomothetic theme. The minor nomothetic theme was that deviation increases threats for a
threat. The finding showed that, according to the participants, participation in cybersecurity
threat appraisals helped assess current strategies' effectiveness and develop new techniques,
understand the organization’s readiness, highlight vulnerabilities, and identify areas of
strengths and weaknesses, which was the second major theme. The minor themes were that
participation provides insights into the risk and guides proactive measures for risk
mitigation.
The second central research question was how cybersecurity professionals perceive
the active support they provide to employees as helping them cope with and prevent cyber
threats. The answer is that employees had the readiness and capacity to cope with cyber
threats due to technologies, security awareness, regular and hands-on training, and
simulations and drills, which improved response capabilities, which was the third major
theme. The findings demonstrated that the participants believed that participation in
cybersecurity coping appraisals promoted continuous improvement, helped with skill
enhancement, compliance, and standardization, built confidence, and fostered better
employee understanding, the fourth major theme. The minor themes were that participation
promotes a proactive cybersecurity culture and ensures everyone understands company
cybersecurity policies.
The findings revealed that the participants felt that emotion-focused coping alone was
inadequate to address cyber threats as it did not solve the problem. However, it helped to
manage stress and reduce anxiety, which was the fifth major theme. The minor themes were
that emotion-focused coping was less effective than problem-focused coping and impaired
judgment. Lastly, RQ2c was about the perceived experience of employees working in
financial companies regarding problem-focused dealing with cyber threats. The finding,

showed by the sixth major theme, indicated that, according to the participants, problem-
focused coping addressed the root cause and solved the problem directly and proactively. The
minor theme was that problemfocused coping is effective in handling cyber threats. Chapter
Five focused on the research summary, implications, conclusions, and study
recommendations based on these findings.
Chapter Five
Summary, Discussion, and Implications
Introduction
The study was on cyber threats to financial organizations, commencing with an
introductory chapter that addressed the problem of potential coping mechanisms and the
adequacy of security policy implementation. The rising tide of cyber threats underscored the
significance of this issue. The research questions were introduced, and the Technology
Threat Avoidance theory (TTAT) was presented as the study's theoretical framework.
Chapter Two provided an extensive examination of the current body of research on
cybersecurity in several financial organizations. The chapter focused on the legal and ethical
dimensions of cybersecurity, the involvement of the government, and the difficulties
enterprises face.
Chapter Three discussed a qualitative exploratory research methodology, specifically
an exploratory study design that justified this choice over other qualitative exploratory
designs. The chapter was also used to discuss the sampling procedures, data collection
sources, and data analysis methods and addressed the issue of trustworthiness through
credibility and transferability (Alkhalil et al., 2021; Gunduz & Das, 2020). Chapter Four
reported the study’s results and described the data collection and analysis process. The data
collected through interviews were analyzed using thematic analysis. The results were

presented in table format for clarity, setting the stage to discuss the findings in Chapter Five.
Chapter Five discussed the results that encapsulated the research findings, their implications
and conclusions, and suggested areas for future research.
Practical Assessment of Research Questions
A practical assessment of the study’s research questions required considering findings
within the context of prior research: the current study both reinforced and supplemented
previous literature. The study offered an essential contribution to research findings from the
study conducted on cyber threats to financial organizations. The problem focused on potential
coping mechanisms and whether security policies are adequately implemented. The data was
collected through individual interviews and analyzed using thematic analysis. The analysis
resulted in 14 themes that addressed the research questions.
Research Question One
The study’s first research question explored how cybersecurity professionals perceive
deviation from their organization’s cybersecurity policies as a risk to their organization. The
challenges related to inadequate security policies involved examining potential coping
strategies and the effectiveness of implementing security policies in addressing the problem.
The literature review also highlighted a lack of comprehensive information on deploying
consistent and dependable anti-cybersecurity frameworks that safeguard a company's
confidential data against internal threats (Shipena & Gamundani, 2024). Previous studies had
primarily concentrated on cyberattacks and threats, malware and security measures,
cybersecurity models, methods for ensuring security, cybersecurity strategies and defense,
legal aspects of cybersecurity, financial implications of data security, and effective

cybersecurity policies within financial organizations. Consequently, the need to conduct the
present study was evident, given the scarcity of research and the unexplored aspect of
understanding how cybersecurity professionals in financial organizations perceive, evaluate,
and are motivated to address or prevent cyber threats. The analysis in Chapter Four revealed
several themes that addressed the research question.
Theme One: Deviation is a High Risk That Can Increase Vulnerabilities within the
Systems, Increase Threat Vectors, and Lead to a Cyberattack That Damages the
Company’s Reputation and Results in Financial Loss. The findings suggested that
employees perceive deviation from cybersecurity policies as a high risk. Employees
expressed concerns about the potential consequences of such deviations, emphasizing the
increased vulnerabilities within the systems, expansion of the threat vector, and the
possibility of leading to a cyberattack. The findings aligned with Alkhalil et al. (2021) and
Gunduz and Das (2020), whose results underscored the importance of adhering to
cybersecurity policies to prevent vulnerabilities and potential cyberattacks that could damage
a company’s reputation and result in financial loss. The current study findings were similar to
those of Herath et al. (2018), who, similar to this study, underlined the crucial role of
employees in maintaining cybersecurity within an organization.
Sub-Theme One: Increased Vulnerabilities and Threat Vector Expansion. From
the study findings, employees reported a clear understanding that deviation introduced
vulnerabilities within the organizational systems, which was consistent with existing
literature that non-compliance widens the cybersecurity threats by providing opportunities
for malicious actors to exploit weaknesses (Alkhalil et al., 2021; Gunduz & Das, 2020). The
concept of an expanded threat vector aligned with the understanding that deviations create
entry points for potential cyber threats emphasized the need for a comprehensive

cybersecurity strategy to counteract this risk. Hence, it underscored the imperative for
organizations to foster a culture of adherence to cybersecurity protocols and continuous
education to mitigate the risks associated with these deviations.
Theme Two: Participation in Cybersecurity Threat Appraisals is Important as it
Helps to Assess the Effectiveness of Current Strategies and Develop New Strategies,
Understand the Organization’s Readiness, Highlight Vulnerabilities, and Identify Areas of
Strengths and Weaknesses. The analysis revealed that employees view participation in
cybersecurity threat appraisals as necessary, highlighting their role in assessing the effectiveness
of current strategies, developing new ones, understanding organizational readiness, and
identifying strengths and weaknesses. The appraisals helped determine the effectiveness of
current strategies and developed new ones, understand the organization’s readiness to handle
threats, highlight vulnerabilities, and identify areas of strengths and weaknesses. This appraisal
aligned with the literature’s recognition of the strategic value of threat assessments (Usman et al.,
2023). The findings extended this understanding by emphasizing employees' perspectives on the
practical significance of threat appraisals in the organizational context.
Sub-Theme Two: Consequences of Cyberattacks: Reputation Damage and
Financial Loss. The acknowledgment by employees that deviation led to a cyberattack,
which resulted in reputation damage and financial loss, is consistent with the literature's
recognition of the multifaceted impacts of cybersecurity breaches (Bunker, 2020;
Muzhanova et al., 2021). The linkage between deviation, cyberattacks, and tangible
consequences reinforces the literature's argument about the significance of employee
compliance in safeguarding organizational interests. This finding also aligned with the work
of Bunker and Muzhanova, who emphasized the importance of employee compliance in
safeguarding organizational interests (Bunker, 2020; Muzhanova et al., 2021).

Theme Three: Evaluations of Risks and Threats and their Potential Impacts on
an Organization. Cybersecurity professionals defined perceived threat appraisals as
evaluating risks and threats and their potential impacts on an organization. The impacts
aligned closely with the literature's emphasis on systematically assessing cybersecurity risks
and vulnerabilities (Malgieri, 2020). The findings underscored the practical implementation
of threat appraisals to evaluate an organization's potential risks and threats. Therefore, the
present study's importance was emphasized by the possible dangers and vulnerabilities,
considering the lack of extensive research and the unknown aspect of how cybersecurity
experts at financial institutions perceive, assess, and mitigate cyber threats.
Theme Four: Conduct Vulnerability and Risk Assessments, Penetration Testing,
Monitoring User Behavior, Simulated Attacks, Regular Audits, Scenario Analysis, and
Evaluating Potential Impact. Cybersecurity professionals employed a range of strategies
to assess the potential risks associated with employees deviating from cybersecurity
policies; they conducted vulnerability and risk assessments, penetration testing, monitoring
of user behavior, simulated attacks, regular audits, scenario analysis, and evaluated the
potential impact and likelihood of threats due to non-compliance. These strategies aligned
with the comprehensive risk assessment approaches advocated in the literature (Alkhalil et
al., 2021; Gunduz & Das, 2020). The findings provided practical insights into the diverse
methods employed by cybersecurity professionals to evaluate and mitigate the risks arising
from deviations.
Theme Five: Cognitive Factors Include Cognitive Biases, Perceived Severity,
Knowledge and Understanding of Threat Landscape, Past Experiences, Perceived Severity,
And Ability to Accurately Assess Risks, While Emotional Factors Comprise Anxiety,
Fear, Trust, Confidence, And Sense of Responsibility. The analysis highlighted that

cognitive and emotional factors influence threat appraisals among cybersecurity professionals
regarding employee deviations from cybersecurity policies. Cognitive factors included
cognitive biases, perceived severity, knowledge and understanding of the threat landscape, past
experiences with cybersecurity incidents, and the ability to assess risks accurately (Harviainen
et al., 2023).
Emotional factors included anxiety, fear, trust, confidence, and a sense of responsibility, as
highlighted by Hernandez-Castro et al. (2020) and Alhayani et al. (2021) in the literature. These
findings resonated with the literature's acknowledgment of the multifaceted nature of
decisionmaking in cybersecurity. The employees' perspectives provided practical insights into
the organizational context's interplay of cognitive and emotional factors.
Theme Six: Strategies and Practices Based on TTAT Include Training, Technical
Controls, Monitoring and Detection, Sanctions and Rewards, Policy Reviews and
Enforcements, and Clear Communication. Finally, the findings suggested that cybersecurity
professionals used various strategies and practices based on the Technology Threat Avoidance
Theory (TTAT) to mitigate threats arising from employee deviations from cybersecurity
policies. The findings aligned with Bécue et al. (2021), who discussed cyber options and
international alliances aligned with the TTAT principles. Gunduz and Das (2020)
highlighted Homeland Security's strategies, confirming the practical implementation of
TTAT principles in addressing threats from employee deviations. These studies aligned with
the findings of the studies under this theme. Both studies concur in their focus on essential
strategies and practices to combat cyber threats. These strategies include rigorous training
programs designed to educate employees on the latest cybersecurity trends and threats.
Training is crucial for fostering a culture of security awareness within organizations,
ensuring employees understand their role in maintaining cybersecurity (Alkhalil et al.,

2021; Van der Ham, 2021). Technical controls form another cornerstone of effective
cybersecurity, with these studies identifying their role in detecting and preventing
unauthorized access. These controls include firewalls, intrusion detection systems, and
encryption technologies, providing a robust line of defense against external and internal
threats.
Monitoring and detection are equally crucial, allowing organizations to identify
suspicious activities and respond promptly. By implementing continuous monitoring
systems, organizations can detect deviations from standard practices, reducing the risk of
internal threats. Sanctions and rewards serve as behavioral incentives, encouraging
adherence to security protocols. Studies by Al-Jarba and Al-Khathami (2021) and Estrela et
al. (2021) indicate that clear policies on sanctions for non-compliance, coupled with rewards
for adhering to security measures, contribute to a more secure organizational culture.
Policy reviews and enforcement ensure that cybersecurity policies remain relevant
and effective. Regular reviews allow organizations to adapt to evolving threats and adjust
their security measures accordingly. Enforcement, supported by a clear communication
strategy, ensures that all employees understand the consequences of security breaches and the
importance of compliance. The findings suggested that cybersecurity professionals utilized
strategies and practices based on the Technology Threat Avoidance Theory (TTAT) to
mitigate threats arising from employee deviations (Harviainen et al., 2023). These strategies
included training, technical controls, monitoring and detection, sanctions and rewards, policy
reviews and enforcement, and clear communication. Incorporating AI and machine learning
for predictive threat analysis and automated response mechanisms is also becoming an
increasingly pivotal aspect of their approach.

Research Question Two
The second research question was: how do cybersecurity professionals perceive the
active support they provide to employees as helping them cope with and prevent cyber
threats? Challenges stemming from insufficient security policies include assessing potential
coping mechanisms and the success of security policy implementation in resolving issues.
The literature review pointed out a significant gap in information regarding establishing
reliable and consistent anti-cybersecurity frameworks designed to protect a company's
sensitive information from internal risks (Shipena & Gamundani, 2024). Prior research had
mainly focused on topics such as cyberattacks and their associated threats, malware and
protective measures, cybersecurity frameworks, strategies for security assurance, defense
tactics in cybersecurity, legal issues surrounding cybersecurity, the financial aspects of data
protection, and the implementation of efficient cybersecurity policies in financial entities.
This gap highlighted the necessity of undertaking the current study, which investigated how
cybersecurity experts in financial organizations perceived, assessed, managed, or mitigated
cyber threats. The findings presented in
Chapter Four identified several key themes that addressed this research question.
Theme Seven: Employees have the Readiness and Capacity to Cope with Cyber
Threats Due to Technologies, Security Awareness, Regular Hands-on Training, and
Simulations and Drills that Improved Response Capabilities. The findings suggested that
employees in financial companies have the readiness and capacity to cope with cyber threats
(Alkhalil et al., 2021; Van der Ham, 2021). Technology adoption and advancements, security
awareness, regular hands-on training, and simulations contributed to this readiness by
enhancing response capabilities. Moreover, a continuous improvement and learning culture in
cybersecurity practices further solidifies their resilience against evolving digital threats.

Theme Eight: Participation in Cybersecurity Coping Appraisals Promoted
Continuous Improvement, Helped with Skill Enhancement, Compliance and
Standardization, Building Confidence, and Fosters Better Understanding among
Employees. The analysis also revealed that employees view participation in cybersecurity
coping appraisals as necessary. These appraisals promoted continuous improvement, helped
with skill enhancement, compliance, and standardization, built confidence, and fostered
better employee understanding. Studies by Choi et al. (2021) confirmed that Theme Eight
emphasized employee participation in cybersecurity coping appraisals.
Theme Nine: Emotion-focused coping alone was Inadequate for addressing cyber
Threats as it does not Solve Actual Problems, although it helped to Manage Stress and
Reduce Anxiety. While emotion-focused coping is valuable for managing stress, it is
considered inadequate on its own to address cyber threats, complemented with problem-
focused coping strategies. The studies conducted by Alhayani et al. (2021) and Hernandez-
Castro et al. (2020) both emphasized the inadequacy of relying solely on emotion-focused
coping to address cyber threats. While this approach is valuable for stress management, it
does not tackle the root problems of cybersecurity incidents. The studies affirmed the need for
complementing emotionfocused coping with problem-focused coping strategies.
Theme Ten: Problem-Focused Coping Addresses the Root Cause of the Issue
and Solves the Problem Directly and Proactively. Problem-focused coping, which
proactively and directly confronted the underlying causes of cyber threats, represented a
significant strategy. This finding aligned with the studies by Conway et al. (2020) and Seh et
al. (2020), which emphasized the importance of problem-focused coping. This approach
proactively addressed the root causes of cyber threats, offering a strategic and
comprehensive response to cybersecurity challenges. Problem-focused coping was a

proactive strategy that directly tackled the root causes of cyber threats, as highlighted by
Conway et al. (2020) and Seh et al. (2020), offered a strategic solution to cybersecurity
challenges.
Theme Eleven: Participation in Cybersecurity Coping Appraisals Organized by
Their Companies Is Highly Important and Crucial. Participation in cybersecurity coping
appraisals organized by their companies is considered crucial. Research by (Harviainen et al.,
2023) concluded that employee participation in cybersecurity coping appraisals organized by
their companies was significant. These appraisals helped identify potential improvement areas,
assessed current strategies' effectiveness, and ensured everyone was on the same page regarding
the company’s cybersecurity policies and procedures.
Theme Twelve: Technology Adoption and Advancements Significantly
Influenced Employees’ Cyber Threat Readiness. Technology adoption and advancements
significantly influenced employees’ cyber threat readiness. Gunduz and Das (2020) and
Alkhalil et al. (2021) asserted that technology adoption and advancements significantly
impact employees’ readiness to cope with cyber threats. However, these advancements
required continuous training and awareness to ensure employees can handle evolving
cybersecurity challenges. Moreover, such involvement empowered employees, making them
proactive stakeholders in their organization's cybersecurity defenses.
Theme Thirteen: Participation in Training, Use of Strong Passwords,
Knowledge of and Adherence to Policies, Response Time, Level of Awareness of Cyber
Threats, Ability to Identify Phishing Emails, And Performance in Simulated Cyber
Attacks. Key indicators utilized by cybersecurity professionals in measuring the
cybersecurity preparedness of employees. Parn & Edwards (2019) included participation in
training and awareness programs, using secure practices like strong passwords, knowledge

of and adherence to policies and procedures, response time, awareness of cyber threats,
ability to identify phishing emails, and performance in simulated cyberattacks. Furthermore,
employee engagement in regular cybersecurity updates and briefings can significantly
enhance their preparedness and resilience against evolving cyber threats.
Theme Fourteen: Regular Training and Awareness, Simulated Attacks, Strict
Cybersecurity Policies, Encouraging Cybersecurity Culture, And Drills. Finally, the
findings suggested that cybersecurity professionals use various strategies to enhance
employees’ cyber threat coping abilities and risk mitigation behaviors. The findings from
Bunker (2020), Choi et al. (2021), and Van der Ham (2021) aligned with the conclusions of
theme fourteen and highlighted the strategies employed by cybersecurity professionals to
enhance employees' cyber threat coping abilities. These strategies and practices included
regular training and awareness, simulated attacks, strict cybersecurity policies, encouraging
a cybersecurity culture, and drills. The analysis findings aligned closely with the literature
reviewed in Chapter Two, providing empirical evidence substantiating established
cybersecurity principles. Furthermore, the analysis findings validated and enriched Chapter
Two's theoretical understanding, reinforcing the importance of employee compliance and
strategic cybersecurity measures in organizational settings (Harviainen et al., 2023).
Limitations of the Study
The limitations provided insights into potential constraints that impacted the
interpretation and generalizability of the findings. Both design and implementation
encountered limitations. Below is a discussion of the design and implementation issues
encountered. Moreover, these limitations highlighted areas for future research and suggested
paths to refine methodologies and approaches in subsequent studies.

Design Issues
The study in question presented several limitations. Initially, the sample size of 15
participants was relatively modest and may not fully represent the range of experiences and
viewpoints among cybersecurity professionals in financial firms. This limitation could
potentially restrict the applicability of the study’s results to a broader demographic. Secondly, the
study relied on self-reported data gathered through interviews and pre-interview questionnaires.
This method could introduce bias or inaccuracies, as participants might have either
misremembered situations or portrayed information in a way they perceived as socially
acceptable.
Thirdly, the ongoing COVID-19 pandemic necessitated conducting the study
virtually. The virtually conducted study might have limited the depth of understanding and
rapport that cannot be established through in-person interactions, potentially affecting the
richness of the collected data. Lastly, the study adopted a qualitative exploratory study
design, which, while facilitating a deep dive into the subject matter, might limit the statistical
generalizability of the findings to a larger population and necessitates caution when applying
the results beyond the studied context.
Implementation Issues
Despite concerted efforts to recruit participants through professional associations and
social media groups like Facebook and LinkedIn, the study encountered difficulties achieving
a larger sample size. This relatively low sample size might affect the breadth and diversity of
perspectives represented in the study. The study’s reliance on participants’ subjective
perceptions and experiences introduced potential variability and subjectivity in the data,
which could impact the consistency and reliability of the findings. The study included
cybersecurity professionals working in financial organizations.

While this diversity enriched the data, it also introduced variability that could make it
challenging to draw definitive conclusions. Future research addressed these limitations by
employing a more extensive and diverse sample, using additional data collection methods, and
considering other research designs that allow for broader generalizability of the findings.
Despite these limitations, the study offered valuable insights into the perceptions and
experiences of cybersecurity professionals in financial companies, thereby contributing to the
existing body of knowledge in this field.
Implications for Future Study
The implications of this study extended across various levels, encompassing
participants, organizational communities, the cybersecurity field, and avenues for future
research. Findings suggested that organizations should prioritize ongoing training and
awareness programs to enhance employees’ understanding of cybersecurity threats and the
importance of policy adherence, contributing to a more vigilant and informed workforce. It
was also beneficial to encourage employees to adopt problem-focused alongside emotion-
focused coping strategies, which can foster a more resilient response to cyber threats,
potentially involving targeted interventions to enhance problem-solving capabilities (Shipena
& Gamundani, 2024).
Integrating Technology Threat Avoidance Theory (TTAT) principles into
cybersecurity frameworks can be considered at the level of organizational communities. This
initiative aligned training programs, policy reviews, and communication strategies with
TTAT principles for more effective threat mitigation. Fostering a cybersecurity culture
within organizations requires policy enforcement and the promotion of shared responsibility
among employees. Organizations should create an environment where employees feel
empowered to contribute to cybersecurity efforts actively (Shipena & Gamundani, 2024). In

cybersecurity, the findings highlighted the importance of comprehensive threat appraisals.
The development of standardized tools and methodologies for evaluating risks and threats,
considering cognitive and emotional factors, should be explored. Training programs should
continuously update as technology evolves to ensure employees can handle emerging cyber
threats. The training program involved collaboration between cybersecurity professionals
and training providers to create dynamic and relevant content
(Harviainen et al., 2023).
Future research could extend the study to different industries to assess the
generalizability of the findings. Comparing cybersecurity practices and perceptions across
sectors could provide valuable insights into sector-specific challenges and solutions.
Understanding the impact of various factors, including organizational culture, leadership
styles, or distinct aspects of the cybersecurity landscape across different regions, on threat
appraisals and coping strategies could provide valuable insights (Shipena & Gamundani,
2024). Longitudinal studies tracking the effectiveness of interventions over time could offer
insights into the sustainability of cybersecurity practices. Understanding how attitudes and
practices evolve could inform the development of more adaptive and resilient cybersecurity
strategies. Given the global nature of cyber threats, international collaboration in
cybersecurity research was crucial. Comparative studies across nations could uncover
cultural nuances in threat appraisals and coping strategies, contributing to a more globally
informed cybersecurity approach. Insights from this study informed the development of
international cybersecurity policy recommendations. Understanding common challenges and
effective strategies contributed to establishing best practices on a global scale (Harviainen et
al., 2023).

Summary
Chapter Five comprehensively analyzed the research findings, discussed the study's
limitations, and outlined implications for future research. The chapter began with a detailed
analysis of the findings, organized into 14 themes, and addressed two research questions.
The first question explored the implications of employee deviation from cybersecurity
policies in financial organizations. The analysis revealed that employees perceive deviation
as a high risk, and participation in cybersecurity threat appraisals was crucial for assessing
the effectiveness of current strategies and developing new ones. The second question
examined employees’ readiness and capacity to cope with cyber threats. The findings
suggested that cybersecurity professionals employ regular training, awareness programs, and
simulated attacks to enhance employees’ cyber threat coping abilities.
The chapter also discussed the study's limitations, including the modest sample size,
reliance on self-reported data, and the virtual nature of the study due to the COVID-19
pandemic. These limitations impacted the interpretation and generalizability of the findings.
The chapter concluded with implications for future research, suggested that studies could be
extended to different industries, explored additional variables influencing threat appraisals
and coping strategies, and conducted longitudinal studies tracking the effectiveness of
interventions over time. Given the global nature of cyber threats, the chapter emphasized the
importance of international collaboration in cybersecurity research. The research
highlighted the importance of ongoing training, awareness programs, and employee
involvement in cybersecurity threat appraisals to boost their readiness and ability to handle
cyber threats. Despite the limitations, the study provided valuable insights into the
perceptions and experiences of cybersecurity professionals in financial companies,
contributing to the existing body of knowledge in this field.


